Share
Embed
Transcript
42 slides
-
We Will Call Him aNgine or How and why we
made one more access control framework Oleg Broslavsky, Denis Kolegov, Nikita Oleksov, Positive Technologies -
You need access control if your app has: • different
users • different levels of access to resources or actions • …? M8, U Need It 3v3rywh3r3! -
Environment-specific: • django-access-control / flask-ACL • STAPL-DSL / FACPL (Java)
• Casbin (Golang) Oth3rs STUFF -
Environment-specific: • django-access-control / flask-ACL • STAPL-DSL / FACPL (Java)
• Casbin (Golang) + Lots of custom solutions for distinct applications Oth3rs STUFF -
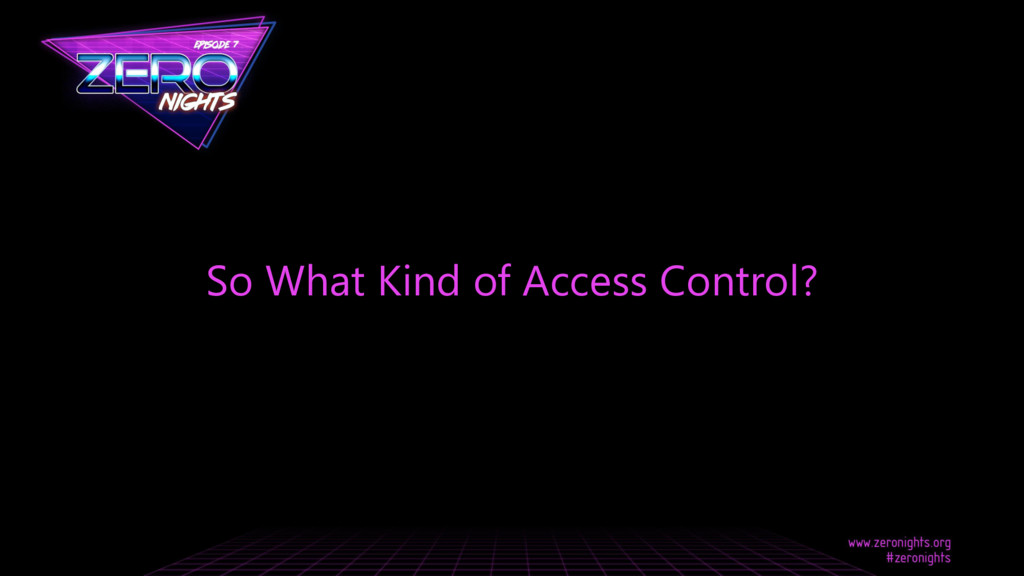
Environment-specific: • django-access-control / flask-ACL • STAPL-DSL / FACPL (Java)
• Casbin (Golang) + Lots of custom solutions for distinct applications Oth3rs STUFF © Standards (xkcd #927) -
ABAC Attribute-based access control • policies can use any type
of attributes • provides dynamic, context-aware and risk-intelligent access control • most strict and technically accurate description ABAC th3 b3st! Attractiveness: 10 Strength: 1 Intellect: >9000 -
XACML – "eXtensible Access Control Markup Language“ Intended to be
cross-platform standard XACML was not an 3scap3 -
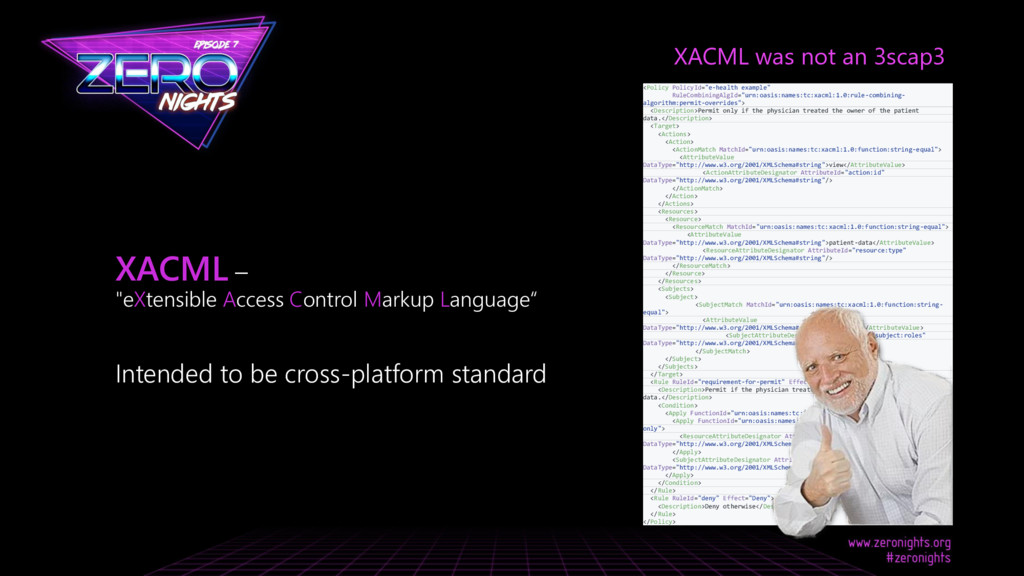
XACML was not an 3scap3 <Policy PolicyId="e-health example" RuleCombiningAlgId="urn:oasis:names:tc:xacml:1.0:rule-combining- algorithm:permit-overrides">
<Description>Permit only if the physician treated the owner of the patient data.</Description> <Target> <Actions> <Action> <ActionMatch MatchId="urn:oasis:names:tc:xacml:1.0:function:string-equal"> <AttributeValue DataType="http://www.w3.org/2001/XMLSchema#string">view</AttributeValue> <ActionAttributeDesignator AttributeId="action:id" DataType="http://www.w3.org/2001/XMLSchema#string"/> </ActionMatch> </Action> </Actions> <Resources> <Resource> <ResourceMatch MatchId="urn:oasis:names:tc:xacml:1.0:function:string-equal"> <AttributeValue DataType="http://www.w3.org/2001/XMLSchema#string">patient-data</AttributeValue> <ResourceAttributeDesignator AttributeId="resource:type" DataType="http://www.w3.org/2001/XMLSchema#string"/> </ResourceMatch> </Resource> </Resources> <Subjects> <Subject> <SubjectMatch MatchId="urn:oasis:names:tc:xacml:1.0:function:string- equal"> <AttributeValue DataType="http://www.w3.org/2001/XMLSchema#string">physician</AttributeValue> <SubjectAttributeDesignator AttributeId="subject:roles" DataType="http://www.w3.org/2001/XMLSchema#string"/> </SubjectMatch> </Subject> </Subjects> </Target> <Rule RuleId="requirement-for-permit" Effect="Permit"> <Description>Permit if the physician treated the owner of the patient data.</Description> <Condition> <Apply FunctionId="urn:oasis:names:tc:xacml:1.0:function:string-is-in"> <Apply FunctionId="urn:oasis:names:tc:xacml:1.0:function:string-one-and- only"> <ResourceAttributeDesignator AttributeId="resource:owner:id" DataType="http://www.w3.org/2001/XMLSchema#string"/> </Apply> <SubjectAttributeDesignator AttributeId="subject:treated" DataType="http://www.w3.org/2001/XMLSchema#string"/> </Apply> </Condition> </Rule> <Rule RuleId="deny" Effect="Deny"> <Description>Deny otherwise</Description> </Rule> </Policy> XACML – "eXtensible Access Control Markup Language“ Intended to be cross-platform standard -
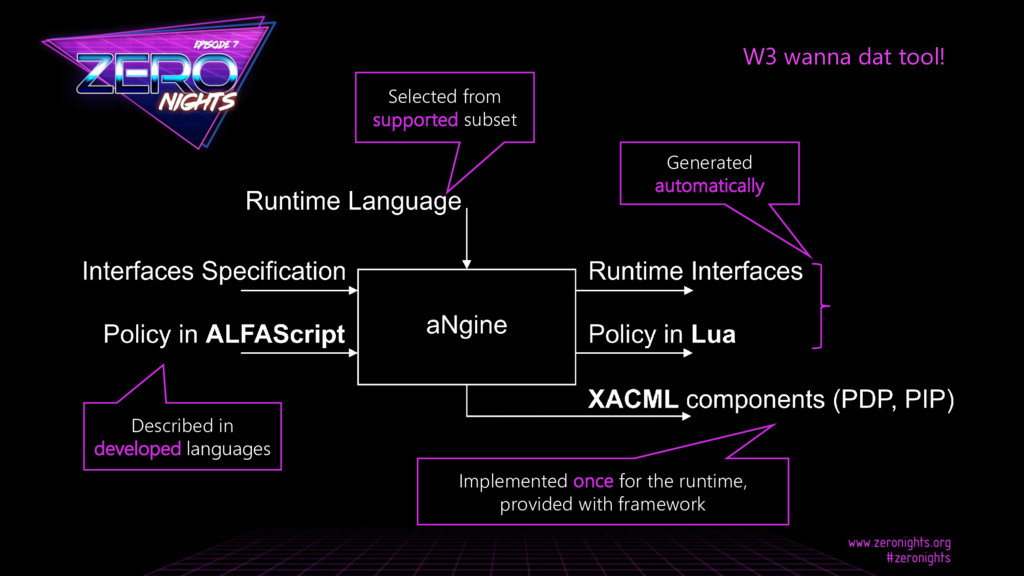
W3 wanna dat tool! Generated automatically Selected from supported subset
Described in developed languages Implemented once for the runtime, provided with framework -
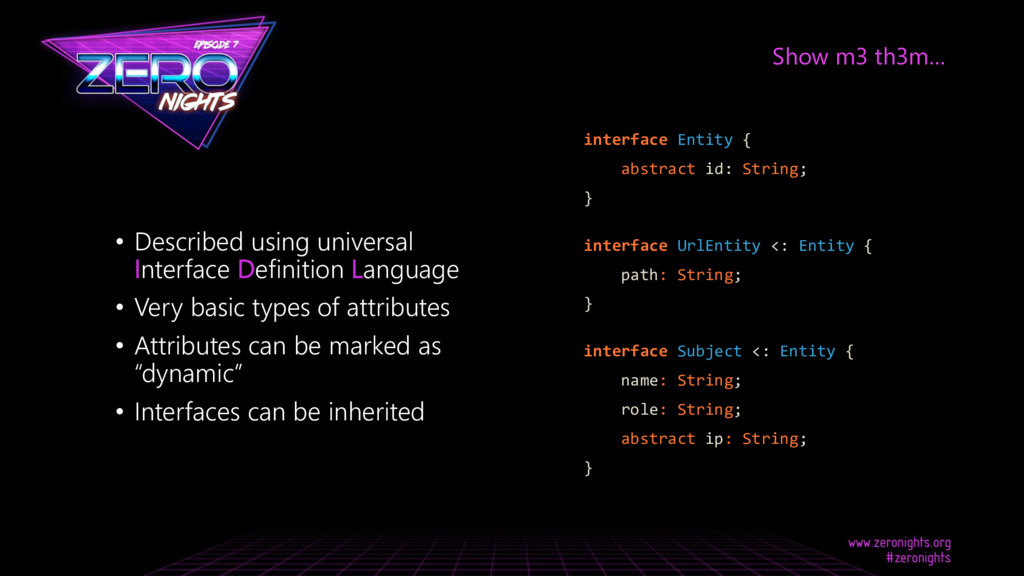
interface Entity { abstract id: String; } interface UrlEntity <:
Entity { path: String; } interface Subject <: Entity { name: String; role: String; abstract ip: String; } Show m3 th3m… • Described using universal Interface Definition Language • Very basic types of attributes • Attributes can be marked as “dynamic” • Interfaces can be inherited -
interface Subject <:Entity { level: Number; `ldap:"(&(uid={ID})(objectClass=user))"` roles: [String]; tags:
[String]; `json:"corporate_units"` } Looks lik3 Go? • PIP can be generated automatically • Uses previously defined interfaces and specified location of attributes • Struct tags could be used to specify attribute location -
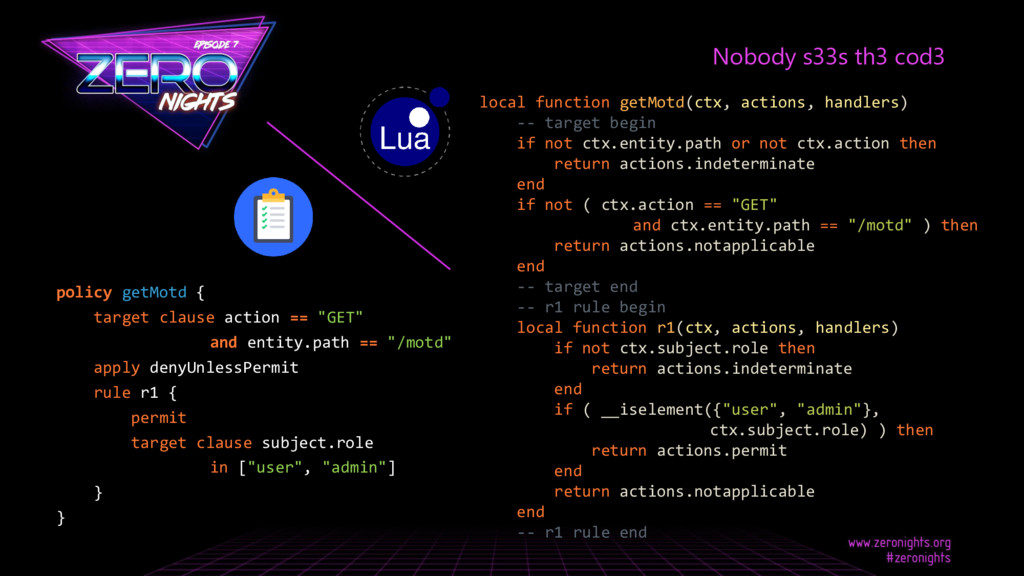
policy getMotd { target clause action == "GET" and entity.path
== "/motd" apply denyUnlessPermit rule r1 { permit target clause subject.role in ["user", "admin"] } } Mor3 acronyms! ALFA, the Abbreviated Language For Authorization (actually an extension of the ALFA language named ALFAScript) -
R3ally concr3t3 * CST contains all syntax-specific tokens and delimiters,
e.g. parentheses and quotes {"type": "Program", "body": [{ "type": "VariableDeclaration", "kind": "var", "declarations": [{ "type": "VariableDeclarator", "id": { "type": "Identifier", "name": "AST" }, "init": { "type": "Literal", "value": "is a tree" } }] ]} } var AST = “is a tree”; Keyword Identifier Equals String Literal Semicolon -
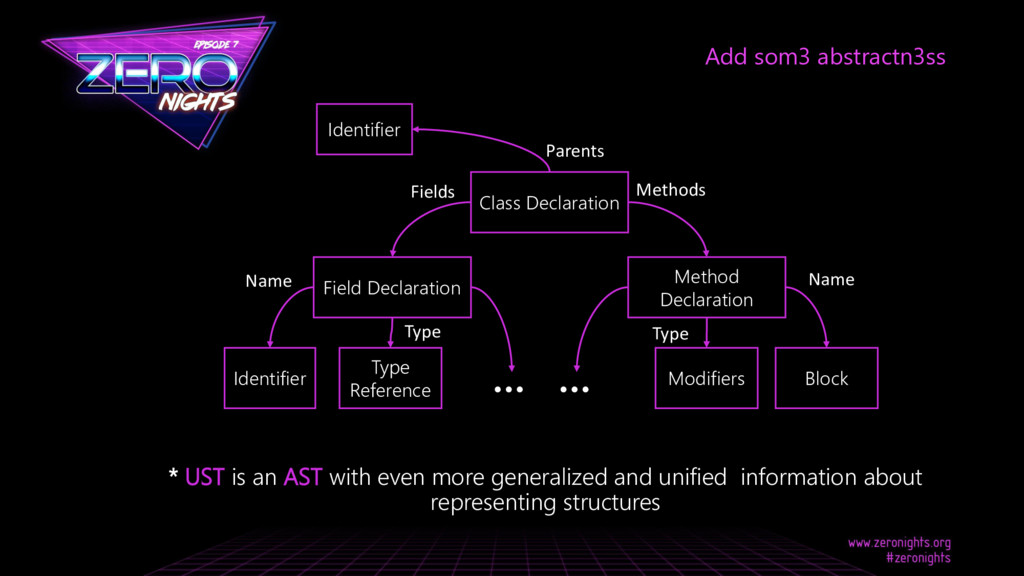
Add som3 abstractn3ss * UST is an AST with even
more generalized and unified information about representing structures Class Declaration Field Declaration Method Declaration Identifier Type Reference Identifier Block Modifiers … … Parents Fields Methods Name Type Type Name -
Kinda w3b {%- macro gen_class(class_) -%} class {{ class_|name }}(
{%- set comma = joiner(",") -%} {%- for cls in class_.parents -%} {{ comma() }}{{ cls|name }} {%- endfor -%} ): {% filter indent(4, True) -%} {{ gen_init(class_.constructor, class_) ~ '\n' }} {% for prop in class_.fields|select("abstract") -%} {{ gen_property(prop) ~ '\n'}} {% endfor %} {% for method in class_.methods -%} {{ gen_method(method) ~ '\n'}} {% endfor %} {% endfilter %} {%- endmacro -%} -
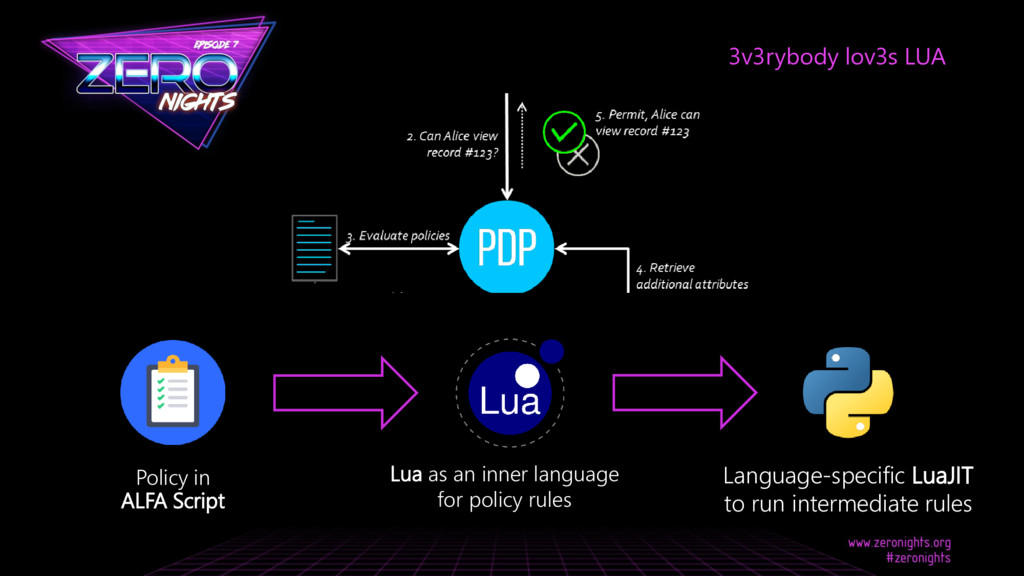
3v3rybody lov3s LUA Policy in ALFA Script Lua as an
inner language for policy rules Language-specific LuaJIT to run intermediate rules -
Nobody s33s th3 cod3 local function getMotd(ctx, actions, handlers) --
target begin if not ctx.entity.path or not ctx.action then return actions.indeterminate end if not ( ctx.action == "GET" and ctx.entity.path == "/motd" ) then return actions.notapplicable end -- target end -- r1 rule begin local function r1(ctx, actions, handlers) if not ctx.subject.role then return actions.indeterminate end if ( __iselement({"user", "admin"}, ctx.subject.role) ) then return actions.permit end return actions.notapplicable end -- r1 rule end policy getMotd { target clause action == "GET" and entity.path == "/motd" apply denyUnlessPermit rule r1 { permit target clause subject.role in ["user", "admin"] } } -
K3k, PEP • PEP translates the request from application logic
to formal interface • Use ANTLR for parsing requests • Provided parsers for the most common request (SQL, HTML, files) Interface Request { subject: Subject; entity: [Entity]; action: Action; env: Environment; } -
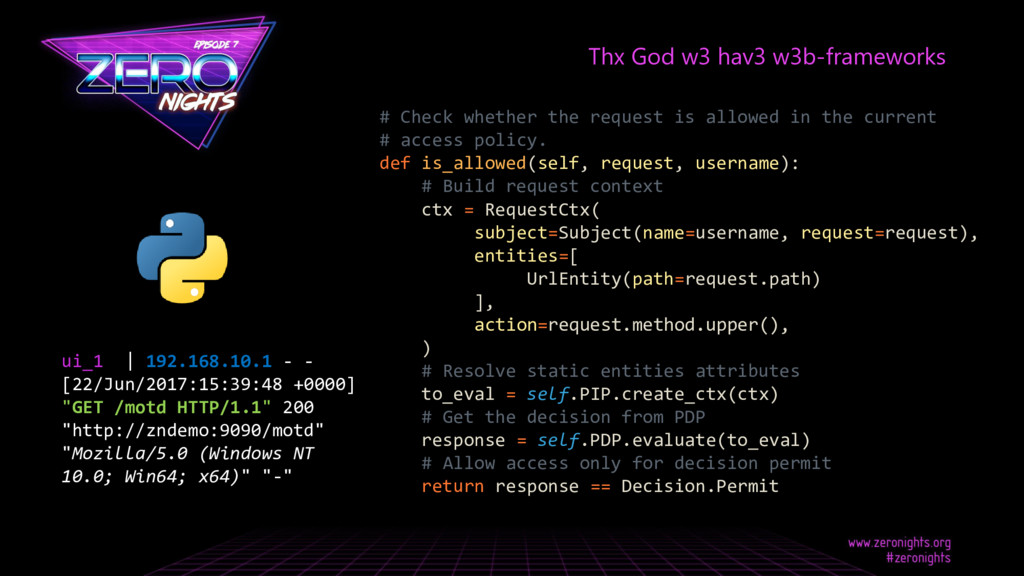
Thx God w3 hav3 w3b-frameworks # Check whether the request
is allowed in the current # access policy. def is_allowed(self, request, username): # Build request context ctx = RequestCtx( subject=Subject(name=username, request=request), entities=[ UrlEntity(path=request.path) ], action=request.method.upper(), ) # Resolve static entities attributes to_eval = self.PIP.create_ctx(ctx) # Get the decision from PDP response = self.PDP.evaluate(to_eval) # Allow access only for decision permit return response == Decision.Permit ui_1 | 192.168.10.1 - - [22/Jun/2017:15:39:48 +0000] "GET /motd HTTP/1.1" 200 "http://zndemo:9090/motd" "Mozilla/5.0 (Windows NT 10.0; Win64; x64)" "-" -
Final structur3 ALFA Write policy rules Adapt existing parsers Describe
entities Provide dynamic attributes if necessary -
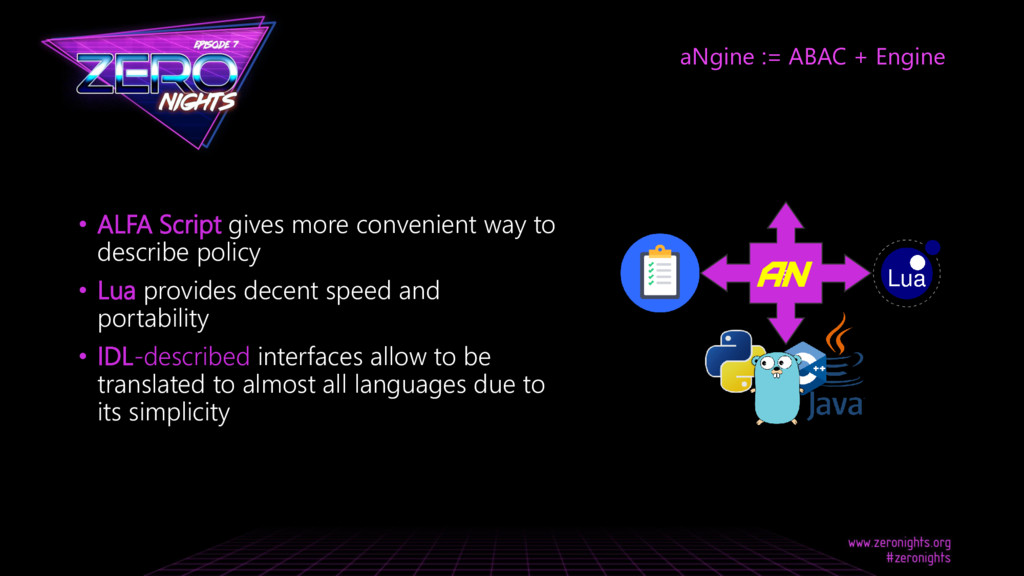
• ALFA Script gives more convenient way to describe policy
• Lua provides decent speed and portability • IDL-described interfaces allow to be translated to almost all languages due to its simplicity aNgine := ABAC + Engine s AN