current employer The most vulnerabilities were found and fixed during my work at F5 Networks Some new vulnerabilities have been reported to F5 Networks Platform Security Team Disclaimer
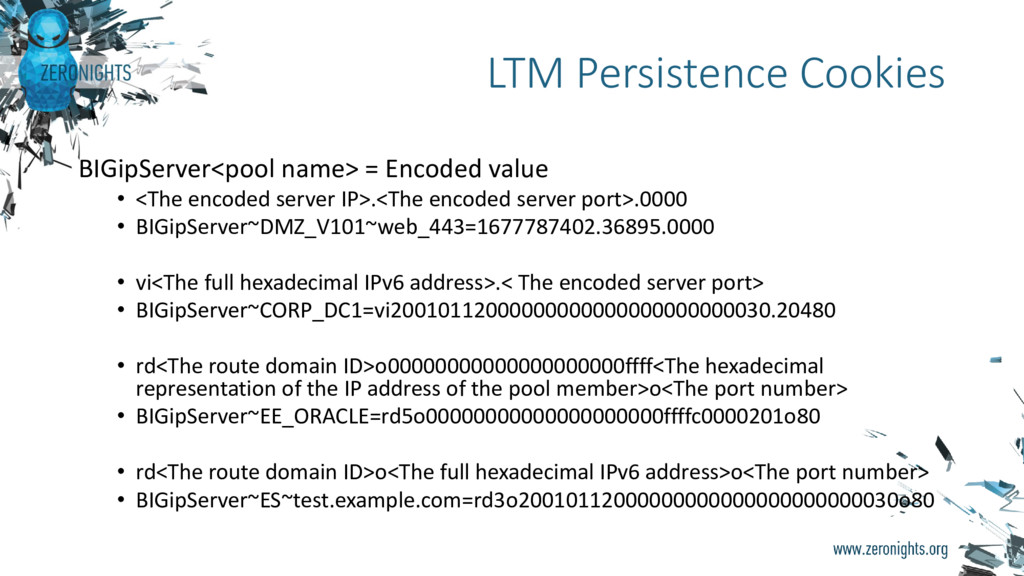
encoded server port>.0000 • BIGipServer~DMZ_V101~web_443=1677787402.36895.0000 • vi<The full hexadecimal IPv6 address>.< The encoded server port> • BIGipServer~CORP_DC1=vi20010112000000000000000000000030.20480 • rd<The route domain ID>o00000000000000000000ffff<The hexadecimal representation of the IP address of the pool member>o<The port number> • BIGipServer~EE_ORACLE=rd5o00000000000000000000ffffc0000201o80 • rd<The route domain ID>o<The full hexadecimal IPv6 address>o<The port number> • BIGipServer~ES~test.example.com=rd3o20010112000000000000000000000030o80 LTM Persistence Cookies
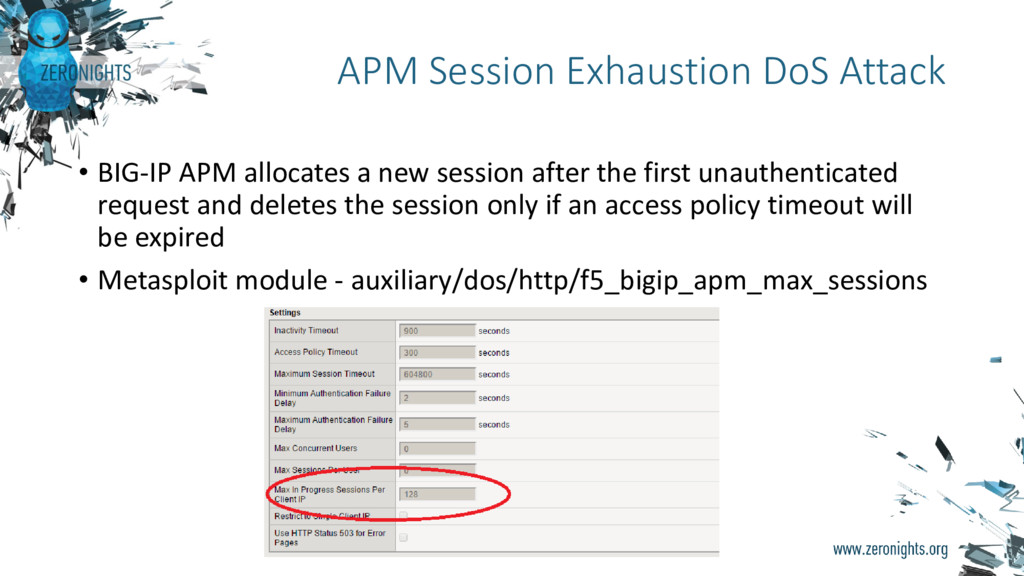
unauthenticated request and deletes the session only if an access policy timeout will be expired • Metasploit module - auxiliary/dos/http/f5_bigip_apm_max_sessions APM Session Exhaustion DoS Attack
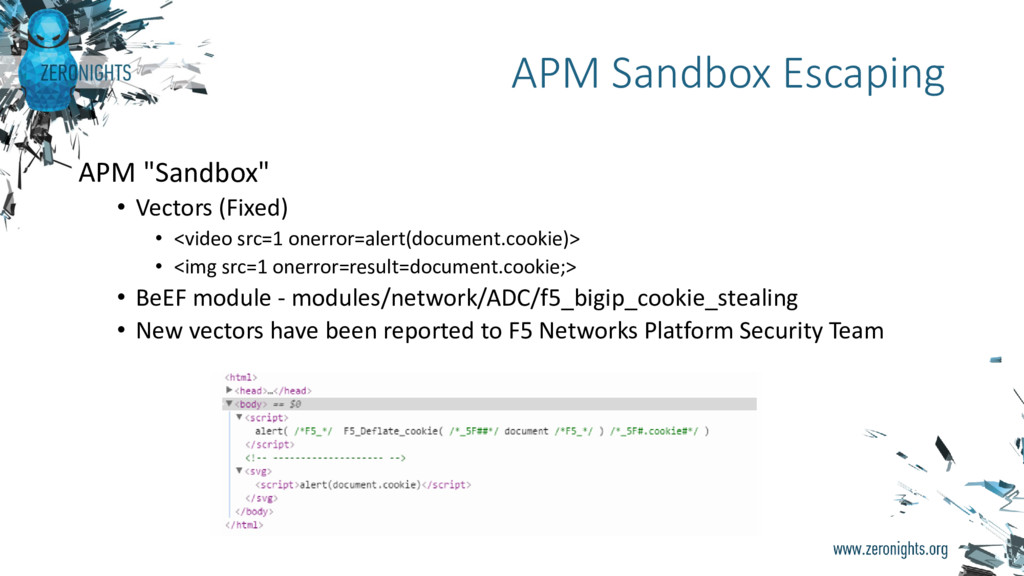
<img src=1 onerror=result=document.cookie;> • BeEF module - modules/network/ADC/f5_bigip_cookie_stealing • New vectors have been reported to F5 Networks Platform Security Team APM Sandbox Escaping
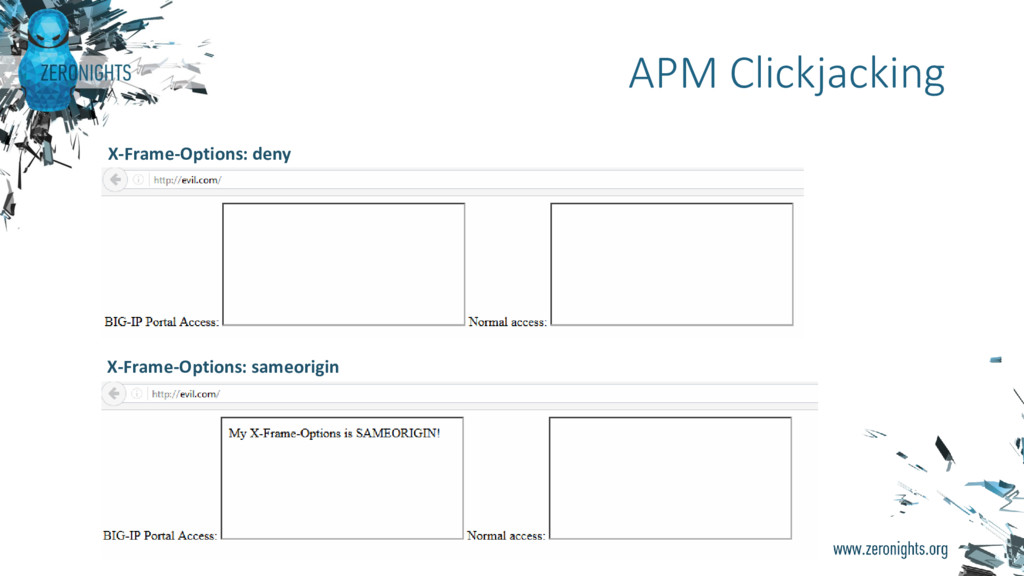
application’s original "X-Frame-Options: sameorigin" header, but accepts "X-Frame-Options: deny" To protect against classic Clickjacking attack it is necessary to configure LTM iRules Reproduced on BigIP 12.1.0 build 0.0.1434 APM Clickjacking
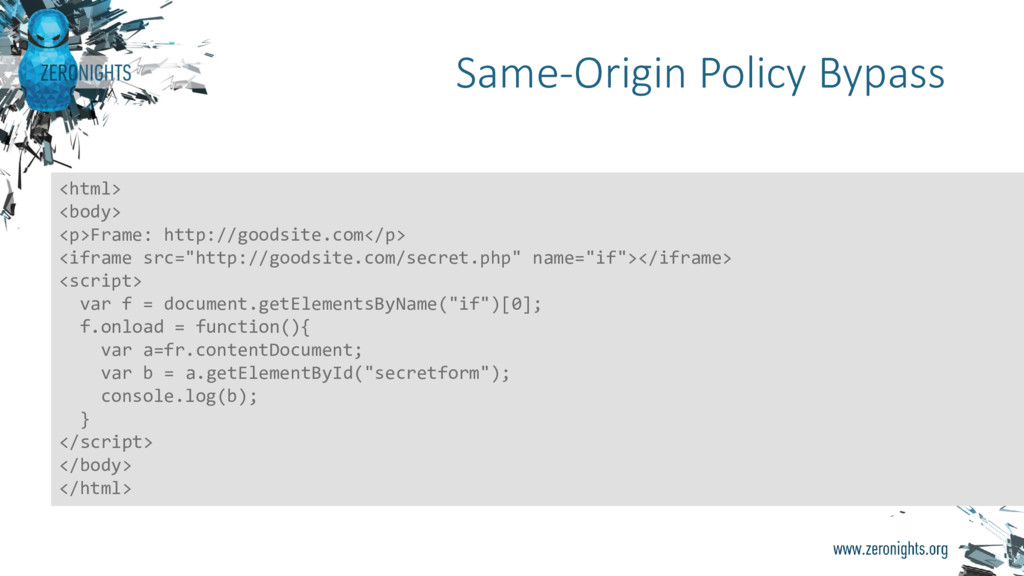
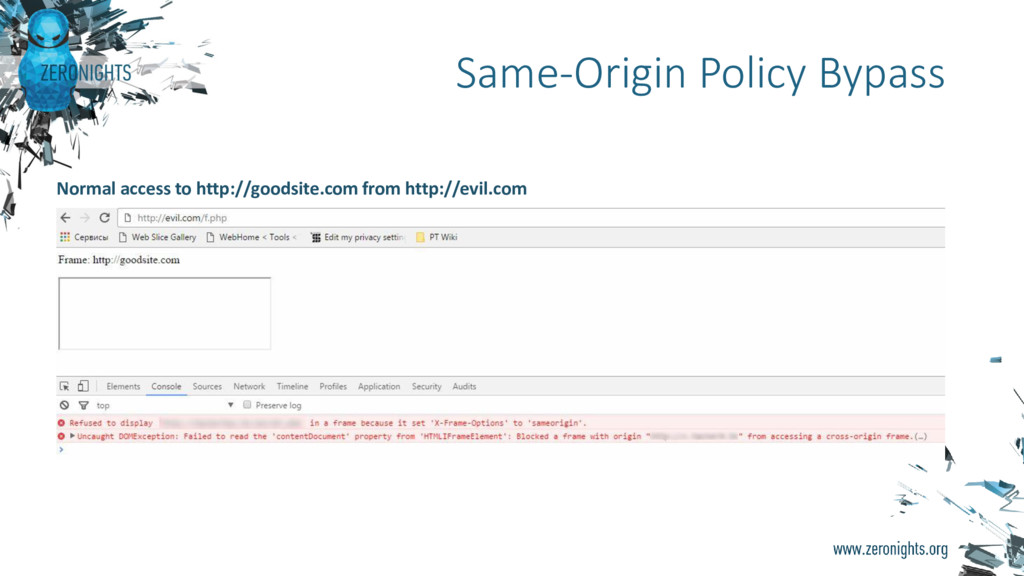
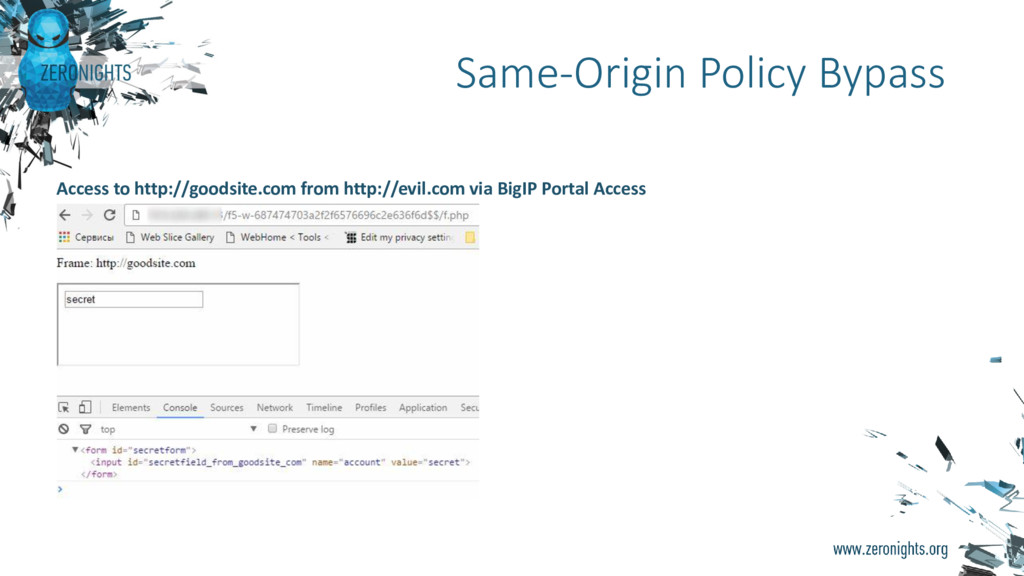
applications behind BIG-IP share the same origin http(s)://bigip:port/ All real applications origins are HEX-encoded and transmitted via URL path /f5-w-[HEX-encoded-origin]$$/path Secure configuration • Services Isolation • L4/L7 ACL Reproduced on BigIP 12.1.0 build 0.0.1434 Same-Origin Policy Bypass
<script> var f = document.getElementsByName("if")[0]; f.onload = function(){ var a=fr.contentDocument; var b = a.getElementById("secretform"); console.log(b); } </script> </body> </html>


 dnkolegov
 ldcn
 resolutionfoundation
 kogoro
 institutdelelevage
 godel
 mickey_0226
 analokmaus
 hirachan
 rabernat
 stephaniewalter
 chriscoyier
 dougneiner
 wayneb77
 vanstee
 stuffmc
 cargoodrich
 reverentgeek
 axbom
 sferik
 codingconduct