Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
AWSとTerraform初心者が やってみたこと
Search
masa-ita
December 21, 2019
Technology
540
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
AWSとTerraform初心者が やってみたこと
masa-ita
December 21, 2019
More Decks by masa-ita
See All by masa-ita
Ollamaを使ったLocal Language Model活用法
itagakim
1
250
Run Instant NeRF on Docker
itagakim
1
2.4k
3D Clustering and Metric Learning
itagakim
0
430
Cloud TPUの使い方〜BigBirdの日本語学習済みモデルを作る〜
itagakim
0
770
多言語学習済みモデルmT5とは?
itagakim
1
800
AWSのGPUを安く使って TensorFlowモデルを訓練する方法
itagakim
0
430
最近の自然言語処理モデルの動向
itagakim
1
610
ディープラーニングで芸術はできるか? 〜生成系ネットワークの進展〜
itagakim
0
390
IntroductionToTensorFlow2_0.pdf
itagakim
1
390
Other Decks in Technology
See All in Technology
3人で1000GPU超を統合運用する?マルチクラウド&オンプレを跨ぐ、構築と運用のリアル!
kazukun0716
2
810
20260930_Gemma4_Hands-on
tsho
0
210
『GOエコノミー 』(相乗りサービス) におけるスペック駆動開発
mot_techtalk
1
180
「とりあえず動く」の先へ。 AI時代のチーム開発と内部設計/2026-slsdays
slsops
0
110
10年欲しかった音楽管理アプリを、AIと一緒に作りはじめた
judau
1
200
雪かき部 #7 もう怖くない!SELECT文!
foursue
0
270
生成AIを使って「人が」考える技術 ― AI時代の人機共想と実践ノウハウ|UNITT AC2026
ishiirikie
0
520
私の推しは「聞いてから進む」AIです -AI-DLCに一人でアプリを作らせた話
yama3133
1
160
React Nativeでの OTA Updateって、 どう説明する?
ichiki1023
0
130
The kernel report
ennael
PRO
1
190
組み立てて楽しむ AWS Blocks 入門
kmiya84377
0
120
[2026-09-30]ロックンロールは鳴り止まないっ - 信頼性かまってちゃん - 「データ駆動を投げ捨ててまで。」追いかける信頼性改善に向けた取り組みの話
tosite
0
180
Featured
See All Featured
End of SEO as We Know It (SMX Advanced Version)
ipullrank
3
4.4k
Utilizing Notion as your number one productivity tool
mfonobong
4
610
A Tale of Four Properties
chriscoyier
163
24k
How to build an LLM SEO readiness audit: a practical framework
nmsamuel
2
930
The Success of Rails: Ensuring Growth for the Next 100 Years
eileencodes
47
8.4k
Future Trends and Review - Lecture 12 - Web Technologies (1019888BNR)
signer
PRO
0
3.8k
Deep Space Network (abreviated)
tonyrice
0
350
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
The MySQL Ecosystem @ GitHub 2015
samlambert
251
13k
Agile Actions for Facilitating Distributed Teams - ADO2019
mkilby
0
290
YesSQL, Process and Tooling at Scale
rocio
174
15k
The Curse of the Amulet
leimatthew05
3
15k
Transcript
AWSとTerraform初⼼者が やってみたこと 板垣 正敏@JAWS-UG Niigata 2019/12/21
⾃⼰紹介 • 板垣 正敏 • 県内IT企業の技術顧問(2020/3まで) • 中⼩企業診断⼠ • ⽇本Rubyの会
• 新潟オープンソース協会 • Python機械学習勉強会 in 新潟 • TensorFlow Users Group • @itagakim • https://github.com/masa-ita • AWS歴 2017年〜
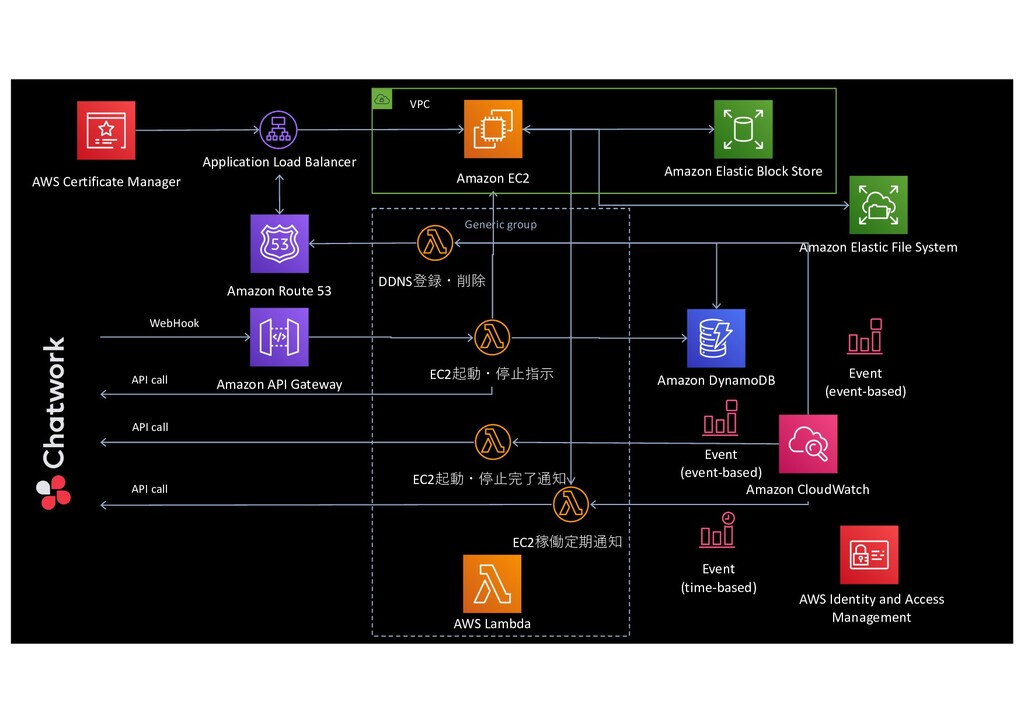
システムの全体像
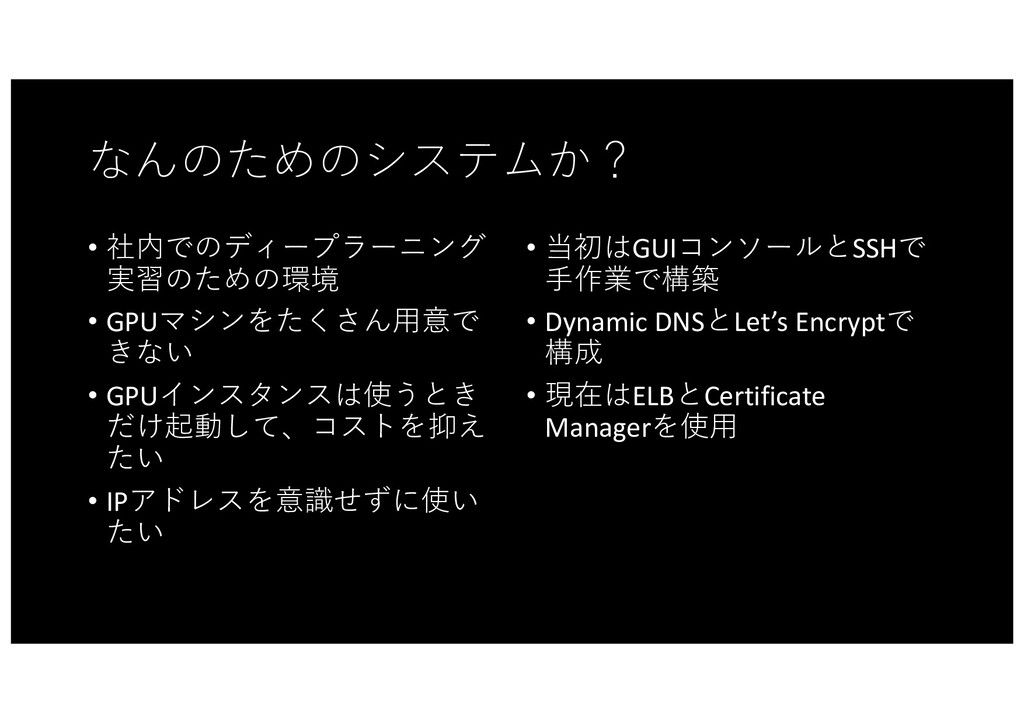
なんのためのシステムか? • 社内でのディープラーニング 実習のための環境 • GPUマシンをたくさん⽤意で きない • GPUインスタンスは使うとき だけ起動して、コストを抑え
たい • IPアドレスを意識せずに使い たい • 当初はGUIコンソールとSSHで ⼿作業で構築 • Dynamic DNSとLet’s Encryptで 構成 • 現在はELBとCertificate Managerを使⽤
AWS Lambda EC2起動・停⽌指⽰ Amazon API Gateway DDNS登録・削除 Amazon DynamoDB Amazon
EC2 Amazon Route 53 Application Load Balancer Amazon CloudWatch Amazon Elastic Block Store Amazon Elastic File System EC2起動・停⽌完了通知 EC2稼働定期通知 AWS Identity and Access Management Generic group Event (time-based) Event (event-based) Event (event-based) AWS Certificate Manager VPC WebHook API call API call API call
本題:Terraformとは?
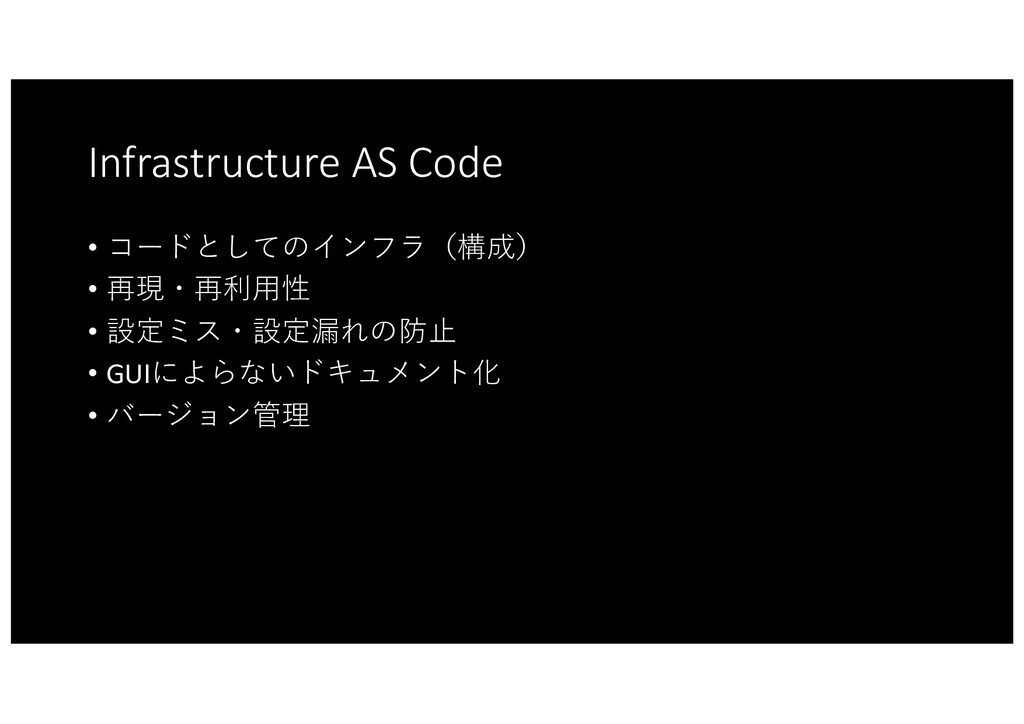
Infrastructure AS Code • コードとしてのインフラ(構成) • 再現・再利⽤性 • 設定ミス・設定漏れの防⽌ •
GUIによらないドキュメント化 • バージョン管理
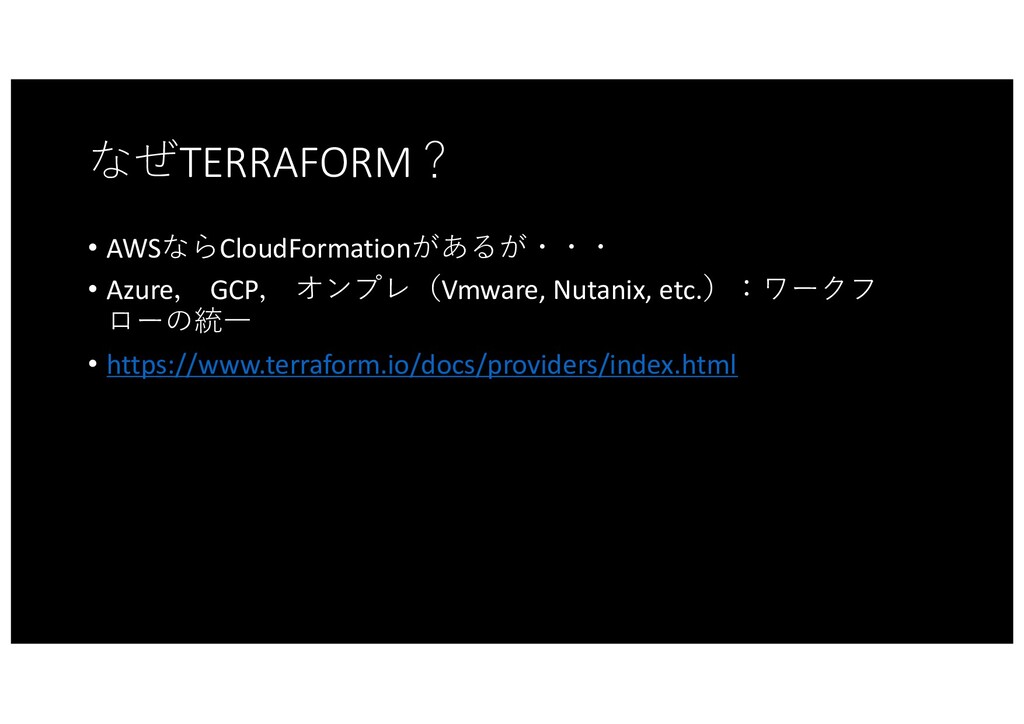
なぜTERRAFORM? • AWSならCloudFormationがあるが・・・ • Azure, GCP, オンプレ(Vmware, Nutanix, etc.):ワークフ ローの統⼀
• https://www.terraform.io/docs/providers/index.html
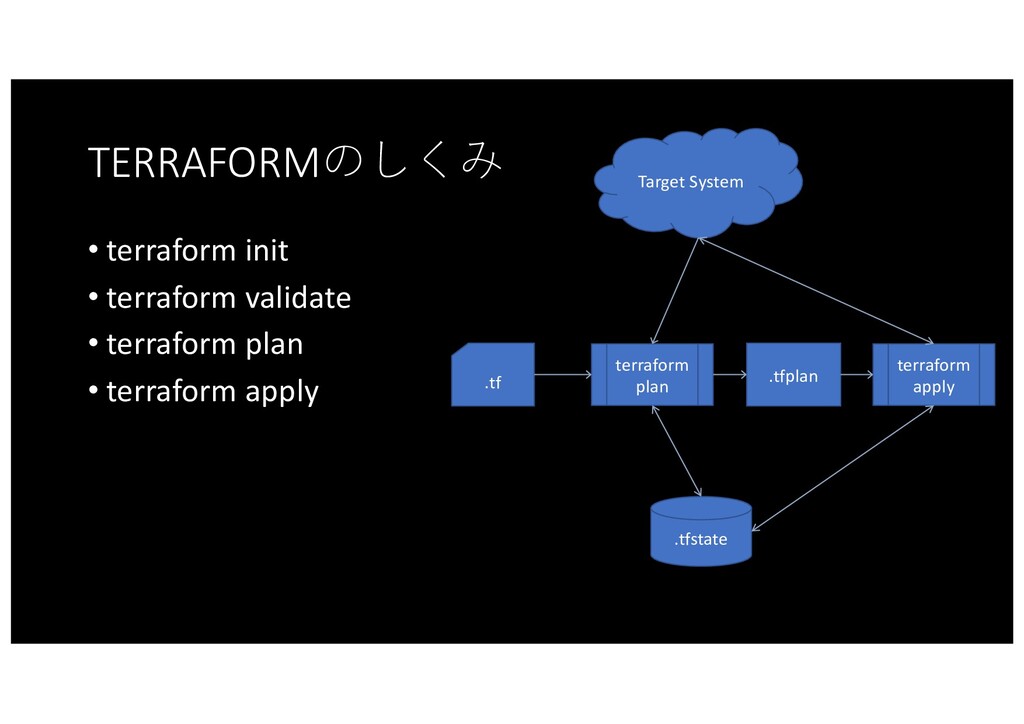
TERRAFORMのしくみ • terraform init • terraform validate • terraform plan
• terraform apply .tf .tfstate .tfplan Target System terraform plan terraform apply
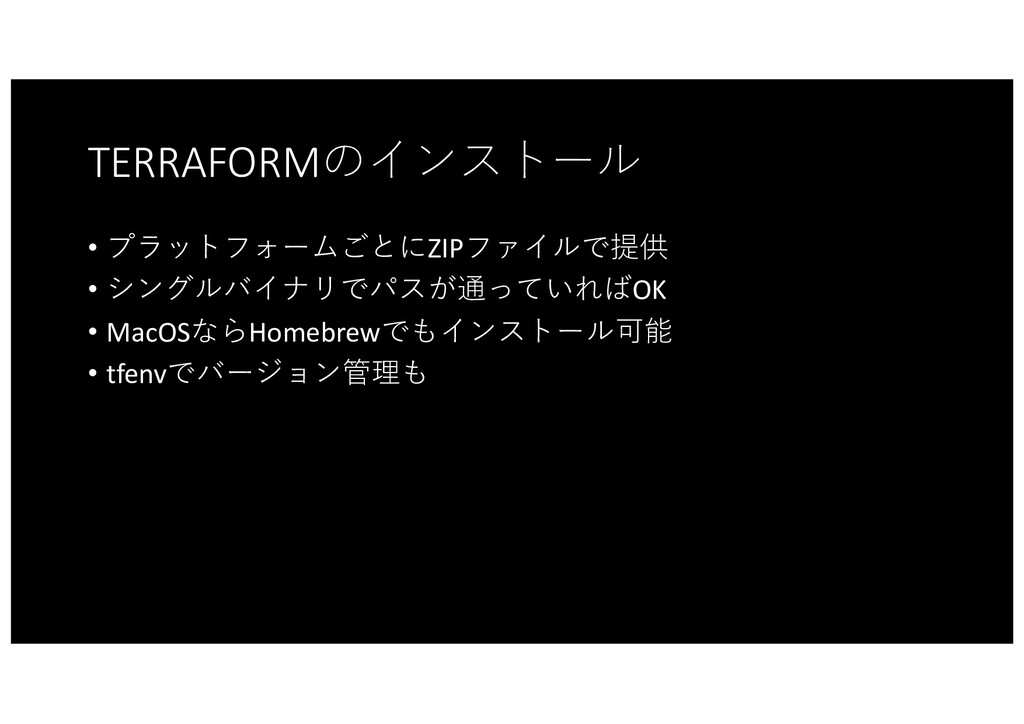
TERRAFORMのインストール • プラットフォームごとにZIPファイルで提供 • シングルバイナリでパスが通っていればOK • MacOSならHomebrewでもインストール可能 • tfenvでバージョン管理も
構成例 Labmdaを⽤いたDynamic DNSの部分のみを紹介
プロバイダ設定 • クレデンシャルは環境変数か awscliの設定ファイルに保存 すべき • バージョンアップでの⾮互換 を防ぐため、Terraformやプロ バイダのバージョン指定が有 効
• 右の例では、.tfstateファイル をS3バケットに保存している (共同作業やリモート参照の ため) terraform { required_version = "0.12.17” backend "s3" { bucket = "tfstate-terraform-demo” key = "network/terraform.tfstate” region = "ap-northeast-1” } } provider "aws" { version = "~> 2.41” region = "ap-northeast-1” }
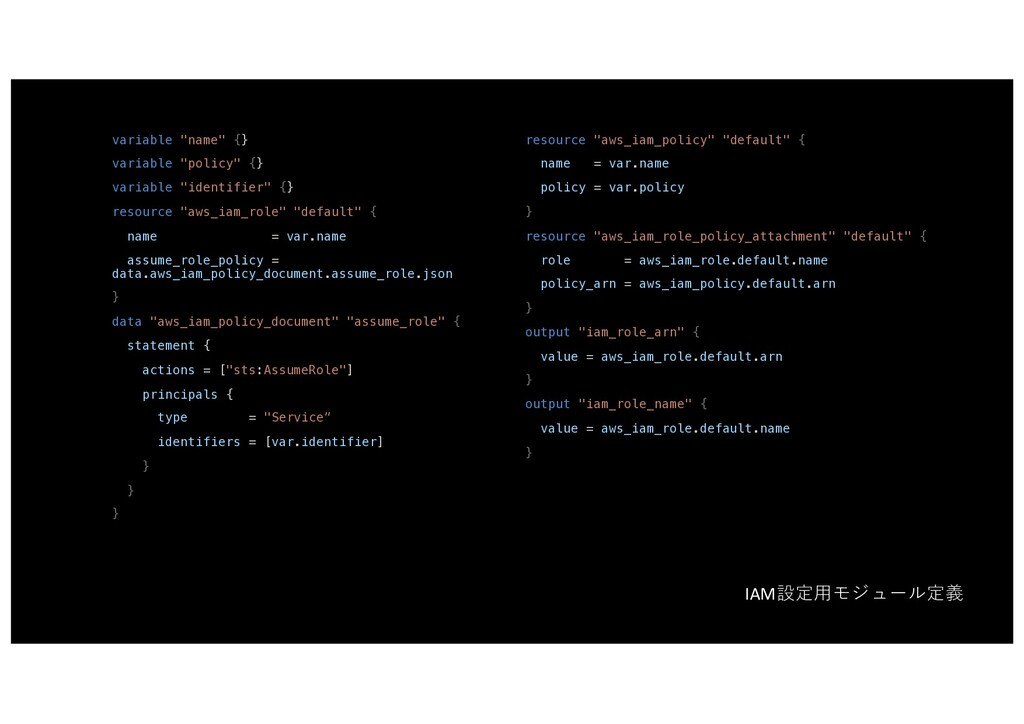
variable "name" {} variable "policy" {} variable "identifier" {} resource
"aws_iam_role" "default" { name = var.name assume_role_policy = data.aws_iam_policy_document.assume_role.json } data "aws_iam_policy_document" "assume_role" { statement { actions = ["sts:AssumeRole"] principals { type = "Service” identifiers = [var.identifier] } } } resource "aws_iam_policy" "default" { name = var.name policy = var.policy } resource "aws_iam_role_policy_attachment" "default" { role = aws_iam_role.default.name policy_arn = aws_iam_policy.default.arn } output "iam_role_arn" { value = aws_iam_role.default.arn } output "iam_role_name" { value = aws_iam_role.default.name } IAM設定⽤モジュール定義
data "aws_iam_policy_document" "for_ddns_lambda" { statement { effect = "Allow” actions
= ["ec2:Describe*"] resources = ["*"] } statement { effect = "Allow” actions = ["dynamodb:*"] resources = ["*"] } statement { effect = "Allow” actions = [ "logs:CreateLogGroup", "logs:CreateLogStream", "logs:PutLogEvents” ] resources = ["*"] } statement { effect = "Allow” actions = ["route53:*"] resources = ["*"] } } module "role_for_ddns_lambda" { source = "./iam_role” name = "role_for_ddns_lambda” identifier = "lambda.amazonaws.com” policy = data.aws_iam_policy_document.for_ddns_lambda.json } Lambda関数⽤IAM定義
data "archive_file" "lambda_function" { type = "zip” source_dir = "lambda/function”
output_path = "lambda/upload/lambda_function.zip” } resource "aws_lambda_function" "ddns_lambda" { filename = data.archive_file.lambda_function.output_path function_name = "ddns_lambda” role = module.role_for_ddns_lambda.iam_role_arn handler = "union.lambda_handler” source_code_hash = data.archive_file.lambda_function.output_base64sha256 runtime = "python2.7” memory_size = 128 timeout = 120 } resource "aws_lambda_permission" "allow_cloudwatch" { statement_id = "AllowExecutionFromCloudWatch” action = "lambda:InvokeFunction” function_name = aws_lambda_function.ddns_lambda.function_name principal = "events.amazonaws.com” source_arn = aws_cloudwatch_event_rule.ec2_lambda_ddns_rule.arn } Lambda関数定義
resource "aws_vpc" "main" { cidr_block = "10.0.0.0/16” enable_dns_support = true
enable_dns_hostnames = true tags = { Name = "main” } } resource "aws_subnet" "main" { vpc_id = aws_vpc.main.id cidr_block = "10.0.1.0/24” map_public_ip_on_launch = true availability_zone = "ap-northeast-1d” tags = { Name = "main” } } resource "aws_internet_gateway" "gw" { vpc_id = aws_vpc.main.id tags = { Name = "main” } } resource "aws_route_table" "public" { vpc_id = aws_vpc.main.id } resource "aws_route" "public" { route_table_id = aws_route_table.public.id gateway_id = aws_internet_gateway.gw.id destination_cidr_block = "0.0.0.0/0” } resource "aws_route_table_association" "public" { subnet_id = aws_subnet.main.id route_table_id = aws_route_table.public.id } resource "aws_vpc_dhcp_options" "aws_subdomain" { domain_name = "aws.rails.to” domain_name_servers = ["AmazonProvidedDNS"] tags = { Name = "aws_subdomain” } } output "vpc_id" { value = aws_vpc.main.id } output "main_subnet_id" { value = aws_subnet.main.id } VPC定義
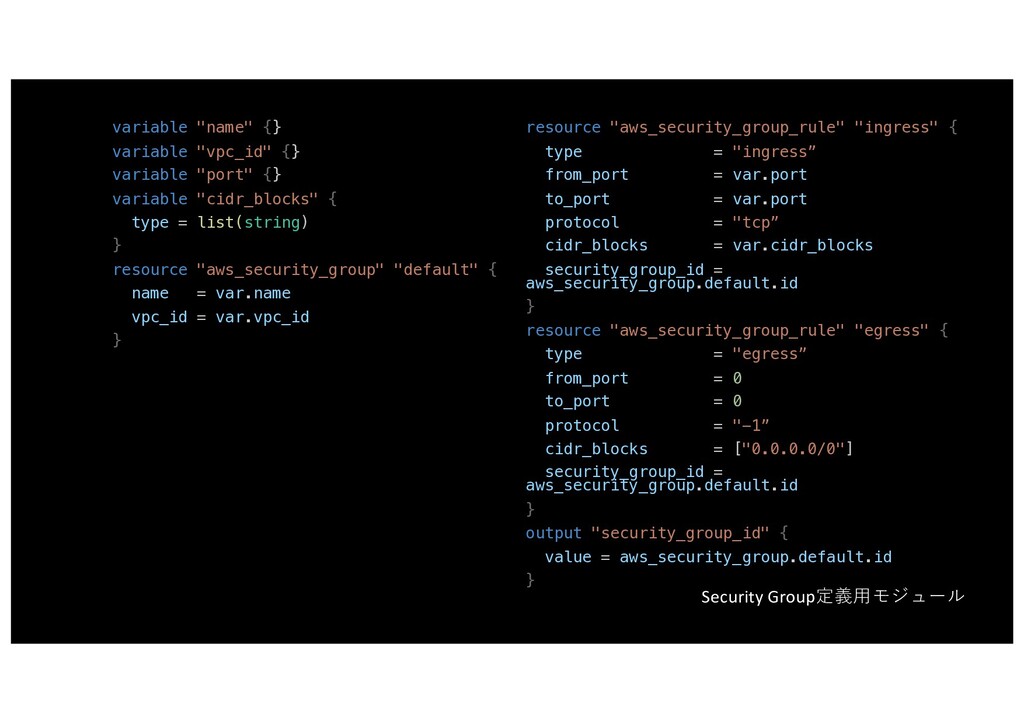
variable "name" {} variable "vpc_id" {} variable "port" {} variable
"cidr_blocks" { type = list(string) } resource "aws_security_group" "default" { name = var.name vpc_id = var.vpc_id } resource "aws_security_group_rule" "ingress" { type = "ingress” from_port = var.port to_port = var.port protocol = "tcp” cidr_blocks = var.cidr_blocks security_group_id = aws_security_group.default.id } resource "aws_security_group_rule" "egress" { type = "egress” from_port = 0 to_port = 0 protocol = "-1” cidr_blocks = ["0.0.0.0/0"] security_group_id = aws_security_group.default.id } output "security_group_id" { value = aws_security_group.default.id } Security Group定義⽤モジュール
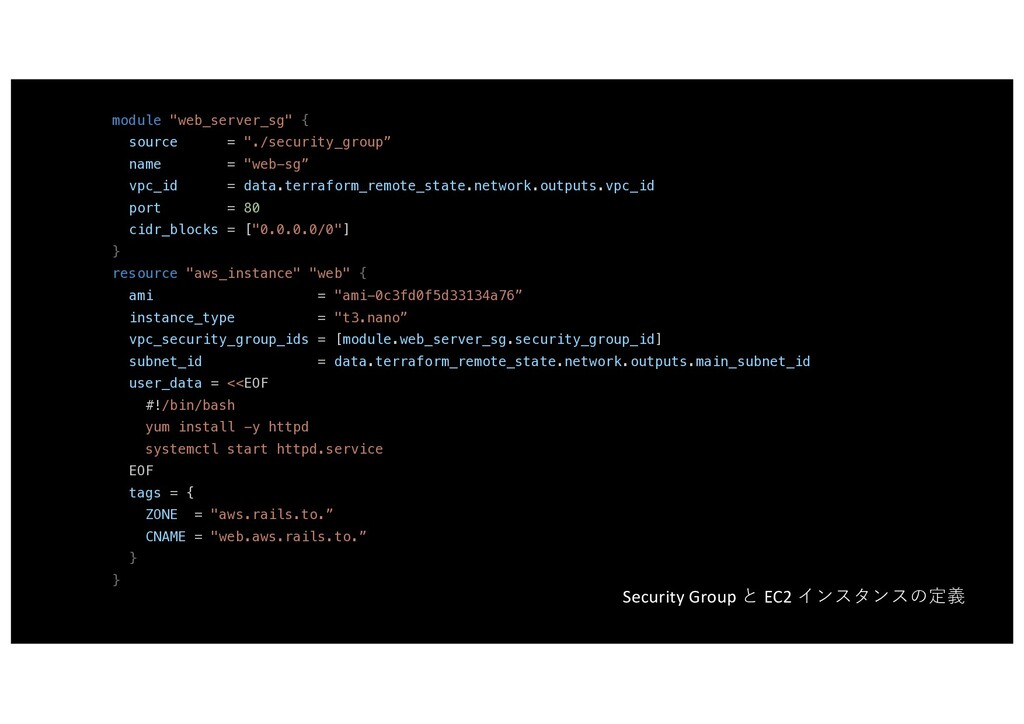
module "web_server_sg" { source = "./security_group” name = "web-sg” vpc_id
= data.terraform_remote_state.network.outputs.vpc_id port = 80 cidr_blocks = ["0.0.0.0/0"] } resource "aws_instance" "web" { ami = "ami-0c3fd0f5d33134a76” instance_type = "t3.nano” vpc_security_group_ids = [module.web_server_sg.security_group_id] subnet_id = data.terraform_remote_state.network.outputs.main_subnet_id user_data = <<EOF #!/bin/bash yum install -y httpd systemctl start httpd.service EOF tags = { ZONE = "aws.rails.to.” CNAME = "web.aws.rails.to.” } } Security Group と EC2 インスタンスの定義
まとめ
Terraform は強⼒なツール • 何よりも構成の再現性がありがたい • GUIが時々変わるクラウドには必須のツールか • プロビジョニングの機能はそれほど便利ではない(ファイル コピーとコマンド実⾏) •
モジュールの使い⽅(使いどころ)がよくわかってません • 最適なリソース分割やディレクトリ配置がまだわかってませ ん
参考図書 • 「実践Terraform」野村友規著 • オンデマンド / Kindle • https://www.amazon.co.jp/dp/4844378139
参照サイト • Terraform Documentation • https://www.terraform.io/docs/index.html • Lamdaを⽤いたDynamic DNSの参考事例 •
https://aws.amazon.com/jp/blogs/compute/building-a-dynamic-dns-for- route-53-using-cloudwatch-events-and-lambda/ • https://github.com/aws-samples/aws-lambda-ddns-function
おまけ: Python機械学習勉強会 in 新潟 Restart #10 やり ます • 2020年1⽉11⽇(⼟)
• 新潟市中央公⺠館(クロスパル) • 「(仮)ディープラーニングで芸術はできるか?〜⽣成系ネッ トワークの進展〜」(itagakim) • 「機械学習による動作認識」(Oh!No!さん) • 「産学連携セミナー報告とインフラWG設⽴の提案」 (haru_fujitaさん) • 「Deep Learningを⽤いた残存⻭の⾃動認識」(historoidさん)


 itagakim
 kazukun0716
 tsho
 mot_techtalk
 slsops
 judau
 foursue
 ishiirikie
 yama3133
 ichiki1023
 ennael
 kmiya84377
 tosite
 ipullrank
 mfonobong
 chriscoyier
 nmsamuel
 eileencodes
 signer
 tonyrice
 destraynor
 samlambert
 mkilby
 rocio
 leimatthew05