Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Fuzz Testing and go-fuzz
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Poga Po
April 18, 2017
Programming
420
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Fuzz Testing and go-fuzz
Poga Po
April 18, 2017
More Decks by Poga Po
See All by Poga Po
Spacer - iThome Serverless All-Star
poga
2
320
civic-notebook
poga
0
120
everything is log
poga
12
2k
g0v intro
poga
0
120
新聞產生器
poga
0
740
RESTful API @ Front-End Developers Taiwan 2014-04-23
poga
3
250
Dependency Management in Go
poga
4
690
Redis: based on real story
poga
16
1.4k
Other Decks in Programming
See All in Programming
作れるエンジニアから、価値を届けるエンジニアへ
ryunakayama
1
250
Zero-Tap Sign-In対応、結局何をすればいいの?
mitohato14
0
1.9k
Herb in Rails 8.2: Your ERB views, now HTML-aware @ Kaigi on Rails 2026, Tokyo, Japan
marcoroth
2
420
TS 7.0 で baseUrl が使えなくなった今、パスエイリアスをどうするか
bicstone
2
580
GraphQL の onError と Nullability のこれから
quramy
0
210
PumaからFalconに移行したRailsアプリケーションでの実践
falcon8823
0
370
作って学ぶSpring BootのAuto Configuration / JJUG Night Seminar 2026-10-19
rshindo
0
220
Distance field of Julia set
kinakomoti321
0
310
プロジェクトコードをキレイキレイしよう!暗黙的な参照を読み解く静的解析
ostk0069
0
210
AIがコードを書いてくれる時代、我々は何を確かめるのか
yosuke_furukawa
PRO
13
5.8k
Spec-Driven Development - Why Vaadin Is the Perfect Fit
simas
PRO
0
240
AI時代のシニアエンジニアとは
yosuke_furukawa
PRO
15
11k
Featured
See All Featured
How to Get Subject Matter Experts Bought In and Actively Contributing to SEO & PR Initiatives.
livdayseo
0
240
The Art of Delivering Value - GDevCon NA Keynote
reverentgeek
16
2.2k
How to Align SEO within the Product Triangle To Get Buy-In & Support - #RIMC
aleyda
2
1.9k
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
530
コードの90%をAIが書く世界で何が待っているのか / What awaits us in a world where 90% of the code is written by AI
rkaga
63
48k
Site-Speed That Sticks
csswizardry
13
1.6k
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.4k
SEO Brein meetup: CTRL+C is not how to scale international SEO
lindahogenes
2
3k
JAMstack: Web Apps at Ludicrous Speed - All Things Open 2022
reverentgeek
1
670
Efficient Content Optimization with Google Search Console & Apps Script
katarinadahlin
PRO
1
980
SERP Conf. Vienna - Web Accessibility: Optimizing for Inclusivity and SEO
sarafernandez
2
1.6k
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
Transcript
Fuzz Testing and go- fuzz
Testing • Unit Test • Integration Test
Hard-to-test • Combination • Uncontrolled Input • hard to define
"Corner cases"
Randomized Test?
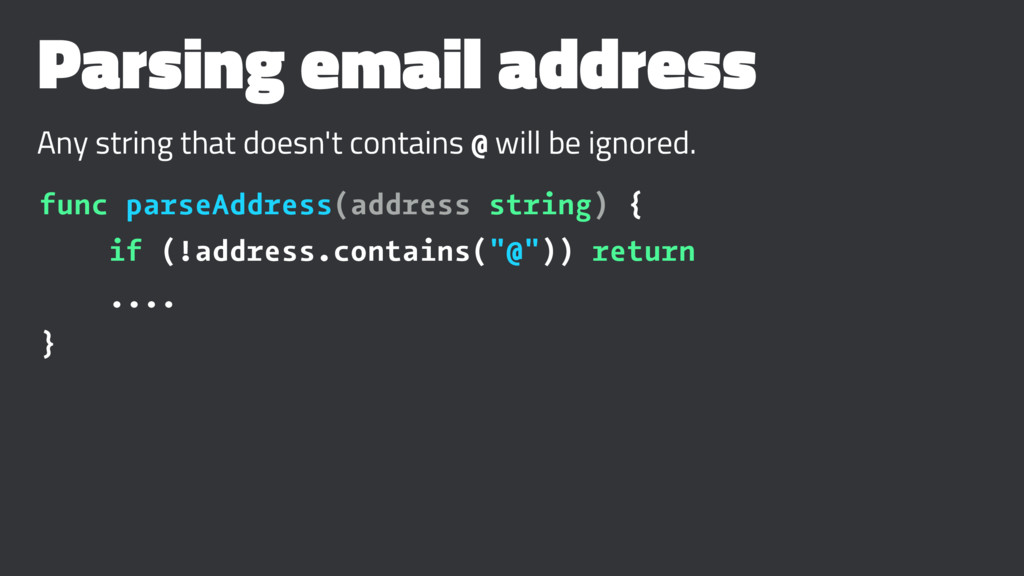
Parsing email address Any string that doesn't contains @ will
be ignored. func parseAddress(address string) { if (!address.contains("@")) return .... }
Fuzzing Feeding programs with automatically generated inputs to trigger unexpected
behaviour.
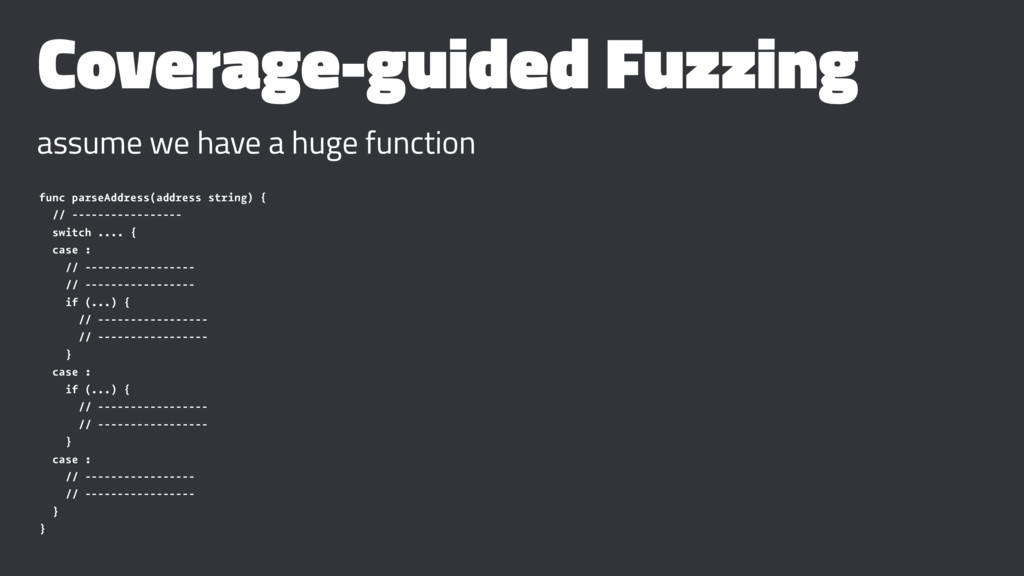
Coverage-guided Fuzzing assume we have a huge function func parseAddress(address
string) { // ----------------- switch .... { case : // ----------------- // ----------------- if (...) { // ----------------- // ----------------- } case : if (...) { // ----------------- // ----------------- } case : // ----------------- // ----------------- } }
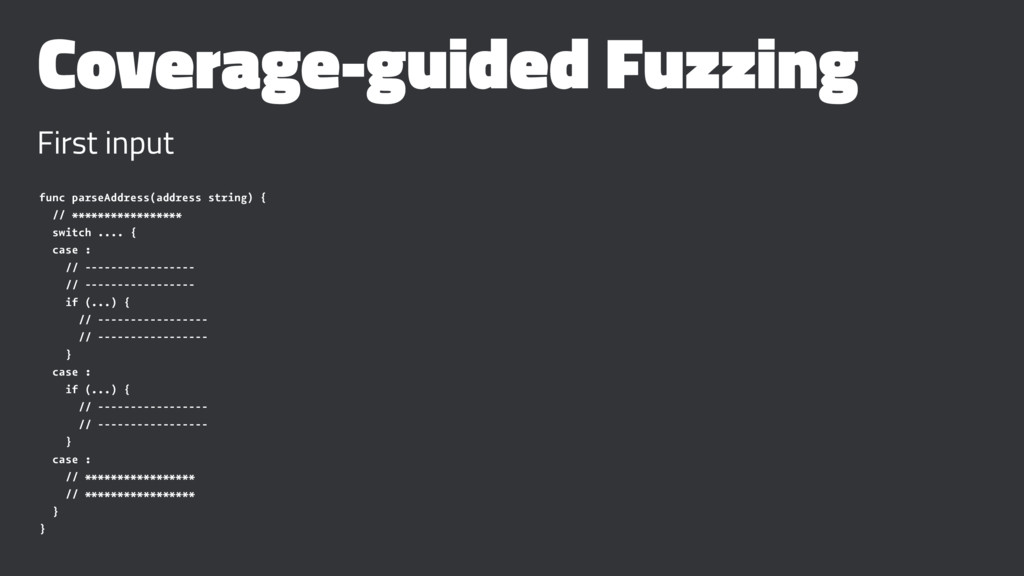
Coverage-guided Fuzzing First input func parseAddress(address string) { // *****************
switch .... { case : // ----------------- // ----------------- if (...) { // ----------------- // ----------------- } case : if (...) { // ----------------- // ----------------- } case : // ***************** // ***************** } }
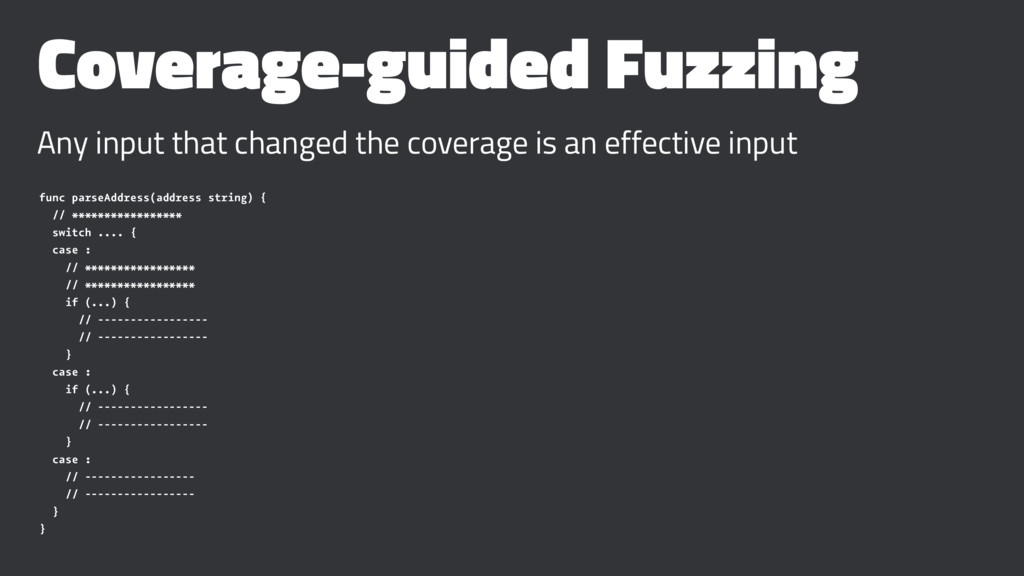
Coverage-guided Fuzzing Any input that changed the coverage is an
effective input func parseAddress(address string) { // ***************** switch .... { case : // ***************** // ***************** if (...) { // ----------------- // ----------------- } case : if (...) { // ----------------- // ----------------- } case : // ----------------- // ----------------- } }
American Fuzz Lop
American Fuzz Lop American Fuzzy Lop is a brute-force fuzzer
coupled with an exceedingly simple but rock-solid instrumentation-guided genetic algorithm. It uses a modified form of edge coverage to effortlessly pick up subtle, local-scale changes to program control flow.
go-fuzz
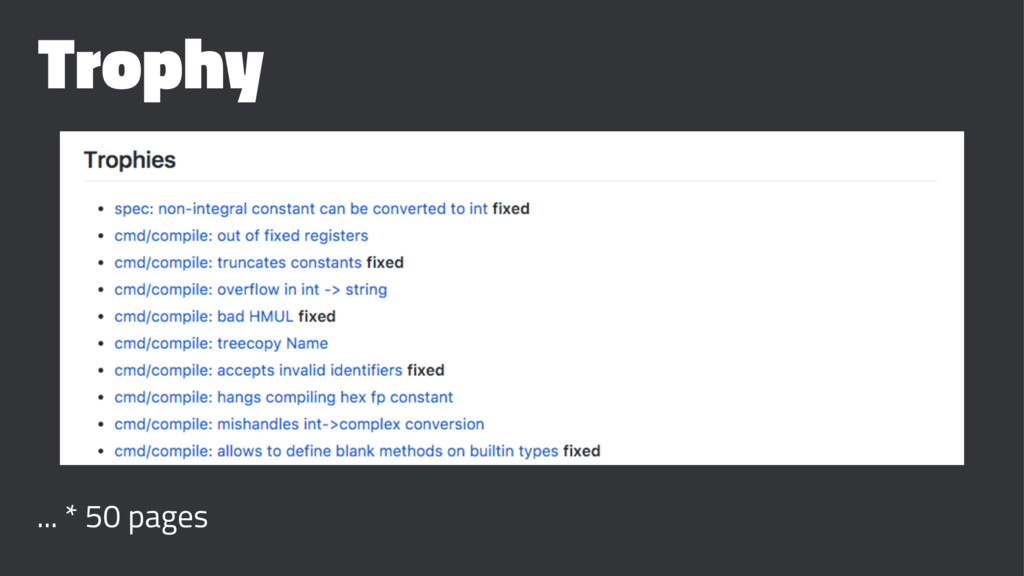
Trophy ... * 50 pages
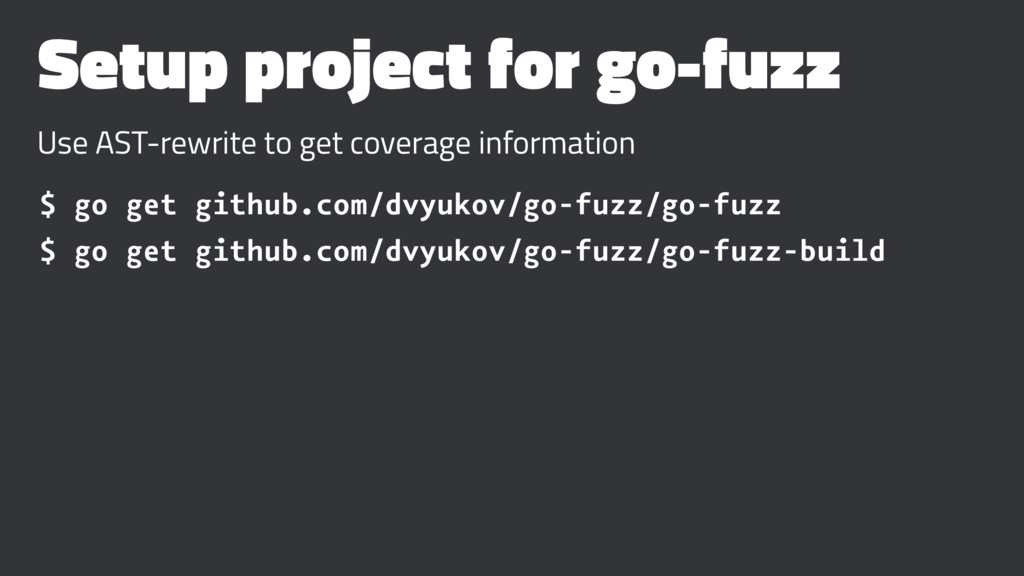
Setup project for go-fuzz Use AST-rewrite to get coverage information
$ go get github.com/dvyukov/go-fuzz/go-fuzz $ go get github.com/dvyukov/go-fuzz/go-fuzz-build
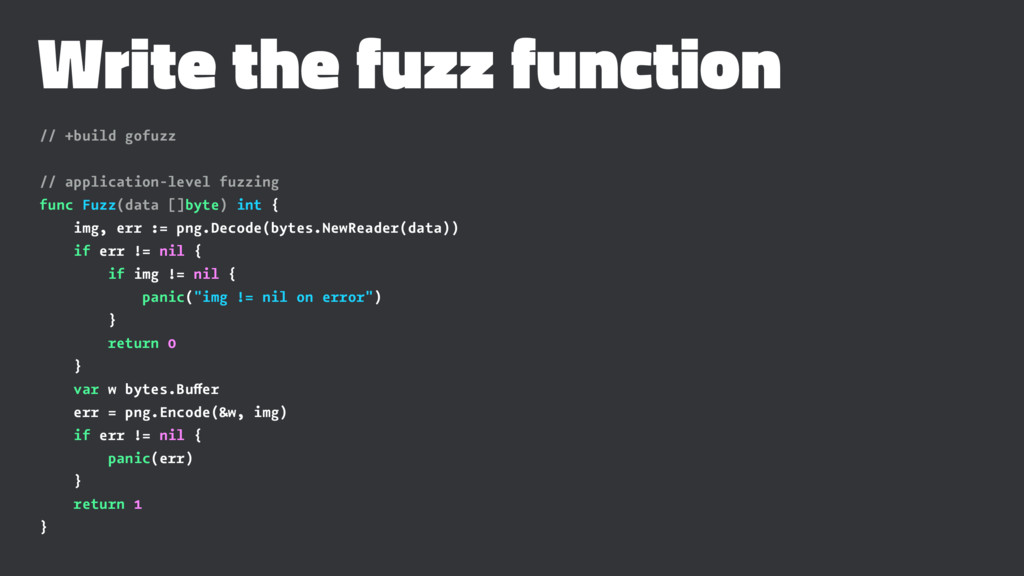
Write the fuzz function // +build gofuzz // application-level fuzzing
func Fuzz(data []byte) int { img, err := png.Decode(bytes.NewReader(data)) if err != nil { if img != nil { panic("img != nil on error") } return 0 } var w bytes.Buffer err = png.Encode(&w, img) if err != nil { panic(err) } return 1 }
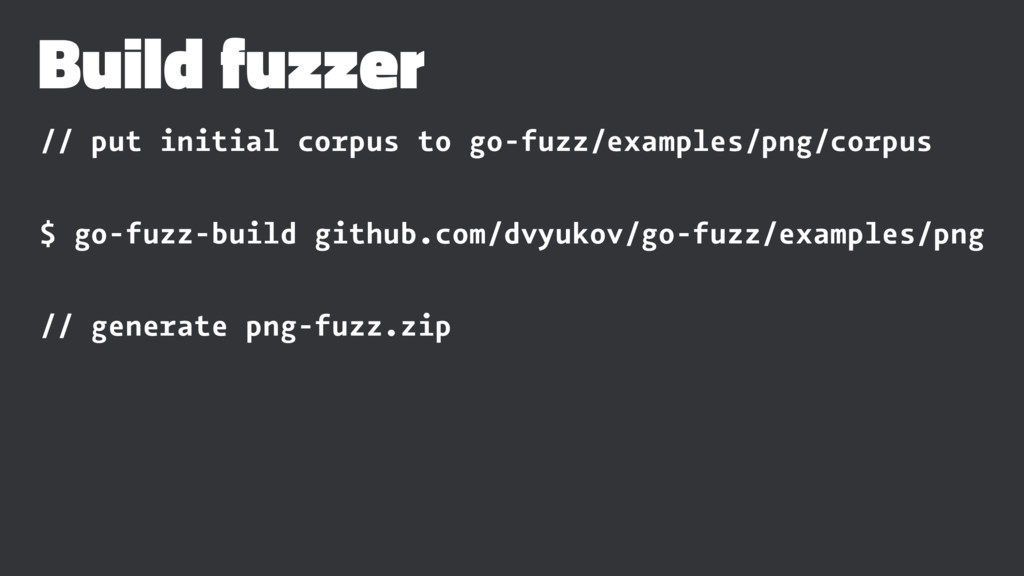
Build fuzzer // put initial corpus to go-fuzz/examples/png/corpus $ go-fuzz-build
github.com/dvyukov/go-fuzz/examples/png // generate png-fuzz.zip
Run the test $ go-fuzz -bin=./png-fuzz.zip -workdir=examples/png $ tree examples/png
examples/png/ !"" corpus # !"" 00184ecf083019781fa3cd954f07ae5f6f8996c5-4 # !"" 00694592b23b147b3ed48fdd58ad93190495c0e1-6 # !"" e1ffccce440e7d27f9f8f4f21b57e1092d5701bc-13 # !"" f1c9f52119ce4f4086ce39c50c84c88373284bb9-9 # !"" f4b5fde0975f447920100b63ca8faa811cd084e5-10 # !"" f4fcdc199b808050a943d900e04e5507d8ccc0f1-7 # $"" f84b0521ed4ee32fcc6f87f1af486efab81986cb-13 # $"" ... !"" crashers $"" suppressions
Examine the output [~/projects/fuzz-test] $ go-fuzz -bin=./png-fuzz.zip -workdir=examples/png 2017/04/17 00:10:44
slaves: 4, corpus: 19 (0s ago), crashers: 0, restarts: 1/0, execs: 0 (0/sec), cover: 0, uptime: 3s 2017/04/17 00:10:47 slaves: 4, corpus: 20 (2s ago), crashers: 0, restarts: 1/3370, execs: 10110 (1681/sec), cover: 173, uptime: 6s 2017/04/17 00:10:50 slaves: 4, corpus: 20 (5s ago), crashers: 0, restarts: 1/4501, execs: 54021 (5964/sec), cover: 173, uptime: 9s ... • slave: concurrent test count • corpus: generated corpus • crashers: corpus which crash the program • restarts: restart rate (due to crashes) • execs: total number of execution • cover: coverage bits
• When should I run fuzz test?: CI • Fuzz
test is only for security issue?: NO • How do I know which corpus crashed my program?: quoted input • Who should write Fuzz test?: You!
Thank you! @devpoga
[email protected]


 poga
 ryunakayama
 mitohato14
 marcoroth
 bicstone
 quramy
 falcon8823
 rshindo
 kinakomoti321
 ostk0069
 yosuke_furukawa
 simas
 livdayseo
 reverentgeek
 aleyda
 techseoconnect
 rkaga
 csswizardry
 tomoyanonymous
 lindahogenes
 katarinadahlin
 sarafernandez
 garrettdimon