Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
PHP 也有 Day #48:我是誰?我在哪?
Search
Star Rocket
October 01, 2019
Technology
95
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
PHP 也有 Day #48:我是誰?我在哪?
PHP 也有 Day #48:我是誰?我在哪?
Star Rocket
October 01, 2019
More Decks by Star Rocket
See All by Star Rocket
PHP 也有 Day #51:高效能框架的曙光 - 以 Laravel 經驗開發 Hyperf 應用
starrocket
1
370
PHP 也有 Day #50:處理前人的遺產—聊 legacy code
starrocket
0
100
PHP 也有 Day #49:邊緣人救星!用 Laravel 打造私人定製的聊天機器人
starrocket
0
460
PHP 也有 Day #48:我是誰?我在哪?
starrocket
0
100
API-整合測試
starrocket
0
160
How we talk about Engineering Culture at Phase
starrocket
0
55
PHP 也有 Day #47:打造好維護的 PHP 程式碼專案
starrocket
0
390
全端起手就用 Laravel+Vue.js 現場實作給你看
starrocket
0
230
PHP 也有 Day #45: VS Code 實戰料理 PHP 套件網站佐 Azure Pipelines
starrocket
0
150
Other Decks in Technology
See All in Technology
技術的負債から考える、AI時代のエンジニアリング投資 — ビズリーチの技術的負債と向き合った経験から、変更し続けられるソフトウェアを考える/ technical-debt-con2026
visional_engineering_and_design
3
3k
作品が生態系になった ─ Mini Tokyo 3D から世界へ
nagix
0
190
空間オーディオで過去の 自分(ゴースト)と競うランニング 〜HealthKitのルートを足音に変える実装〜
nao_randd
0
220
OpenTelemetryのメトリクスをCloudWatchに送ってPromQLで見てみた
ota1022
0
150
越境するなら専門用語を使うな高校校歌 / If you wanna cross border, you shouldn't use jargon
vtryo
0
140
AI時代、データエンジニアが一番おもろい
genshun9
0
600
synctest時代のhttptest Go 1.27で変わるHTTPサーバテストの裏側 / go conference2026 synctest and httptest
budougumi0617
1
3k
2026/09/10 Spring Bootから Jakarta EE/MicroProfileへの移行
megascus
0
370
AI 時代のスタートアップエコシステ厶から考究する技術的負債との向き合い方
m3m0r7
PRO
2
2.1k
品質と信頼性を地続きにする
grimoh
0
400
AIによるクリエイティブ生成を行う上での試行錯誤
plaidtech
PRO
0
150
日経電子版を支えていく Kasane Design System/fec_fukuoka
nikkei_engineer_recruiting
0
1.5k
Featured
See All Featured
Rebuilding a faster, lazier Slack
samanthasiow
85
9.6k
Bioeconomy Workshop: Dr. Julius Ecuru, Opportunities for a Bioeconomy in West Africa
akademiya2063
PRO
1
360
Practical Orchestrator
shlominoach
192
12k
Sharpening the Axe: The Primacy of Toolmaking
bcantrill
46
3k
A designer walks into a library…
pauljervisheath
211
25k
The Curse of the Amulet
leimatthew05
3
14k
Statistics for Hackers
jakevdp
799
230k
CSS Pre-Processors: Stylus, Less & Sass
bermonpainter
360
30k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
Building a Scalable Design System with Sketch
lauravandoore
464
34k
Kristin Tynski - Automating Marketing Tasks With AI
techseoconnect
PRO
0
520
How to Align SEO within the Product Triangle To Get Buy-In & Support - #RIMC
aleyda
2
1.8k
Transcript
我是誰︖我在哪︖ 聊聊 Web 的身分驗證
ABOUT MILES CURRENT Senior Developer @ 104 Corp. Volunteer @
DevOps Taiwan TAG PHP, Docker, DevOps
[email protected]
MilesChou
None
今天將會聊些什麼 Terminology Scenario Native App Security Topic
Terminology Authentication Entity Identifier
Server User
Server User Entity
Server User Identifier Entity
Server User Entity Identifier Miles Miles
Server User Entity Identifier Authentication Miles Miles
基本的安全問題 請求真的是該使⽤用者本身的意願所發出的請求嗎︖ 有沒有可能被竄改︖有沒有機會造假︖ 回應真的是伺服器的回應嗎︖ 有沒有可能被竄改︖有沒有機會造假︖
Scenario 從前從前,有個網站提供了很多服務
安安你好,第⼀一 一 次 來 來 嗎 ? 第⼀一 一 次
來 來 的 都 是 絕 緣 ⼈人 人 哦 ! 為了了讓你不再絕緣, 你先跟我講好,要怎麼驗證你是誰!
註冊的⽬目的 使⽤用者提供憑證資訊,如帳號、密碼、etc 伺服器提供 metadata
註冊的⽅方法 線上註冊 私訊註冊 線下註冊
User Login 身為⼀一個使⽤用者,我希望能使⽤用網站提供的服務
安安你好,第⼆二 二 次 來 來 嗎 ? 站著!⼝口 口 令
? 誰 ? 我知道你是麥爾斯了了,可是我⾦金金 金 金 ⿂魚 魚 腦 ! 24 分鐘內記得過來來刷新⼀一 一 下 !
User Login Challenge State Management Mechanism
實作 LaravelAuth Zend Authentication
Server-side Authentication 身為⼀一個伺服器,我希望能呼叫網站提供的 API
How about Authorization?
Server-side Authentication Trusted Server VPN、鎖 IP、發 token、etc. OAuth 2.0 Facebook、Google、GitHub、AWS、etc.
Terminology -OAuth2.0 Authorization Resource Owner Resource Server Client Authorization Server
Authorization Server Resource Owner Resource Server Client Authorization Request
Authorization Server Resource Owner Resource Server Client Authorization Grant
Authorization Server Resource Owner Resource Server Client Authorization Grant
Authorization Server Resource Owner Resource Server Client Access Token
Authorization Server Resource Owner Resource Server Client Access Token
Authorization Server Resource Owner Resource Server Client Protected Resource
微信偷連結 Facebook︖ 到底花⽣生省魔術︖請看 VCR!
微信偷連結 Facebook︖ Facebook 實作了 OAuth 2.0 微信 App 為 Client
授權範圍
Third-party Login 身為⼀一個外部網站,我希望能透過貴站做身分驗證
安安你好,你是麥爾斯的跟班嗎? 有刷過麥爾斯的臉就可以進場了了哦! 但過⼀一 一 回 兒 後 , 我還會再跟麥爾斯確認,你還是不是他的跟班
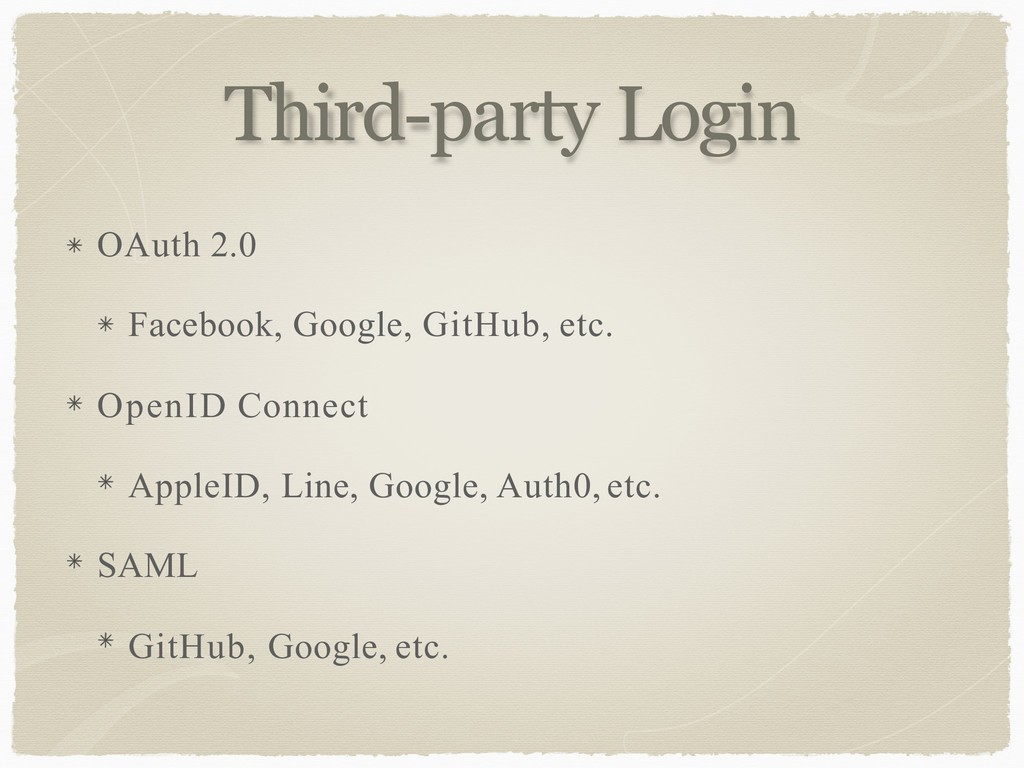
Third-party Login OAuth 2.0 Facebook, Google, GitHub, etc. OpenID Connect
AppleID, Line, Google, Auth0, etc. SAML GitHub, Google, etc.
Server User Provider Authentication Check
OpenID Connect
OpenID Connect Based-on OAuth 2.0 Use JWT on ID token
Discovery Dynamic Client Registration
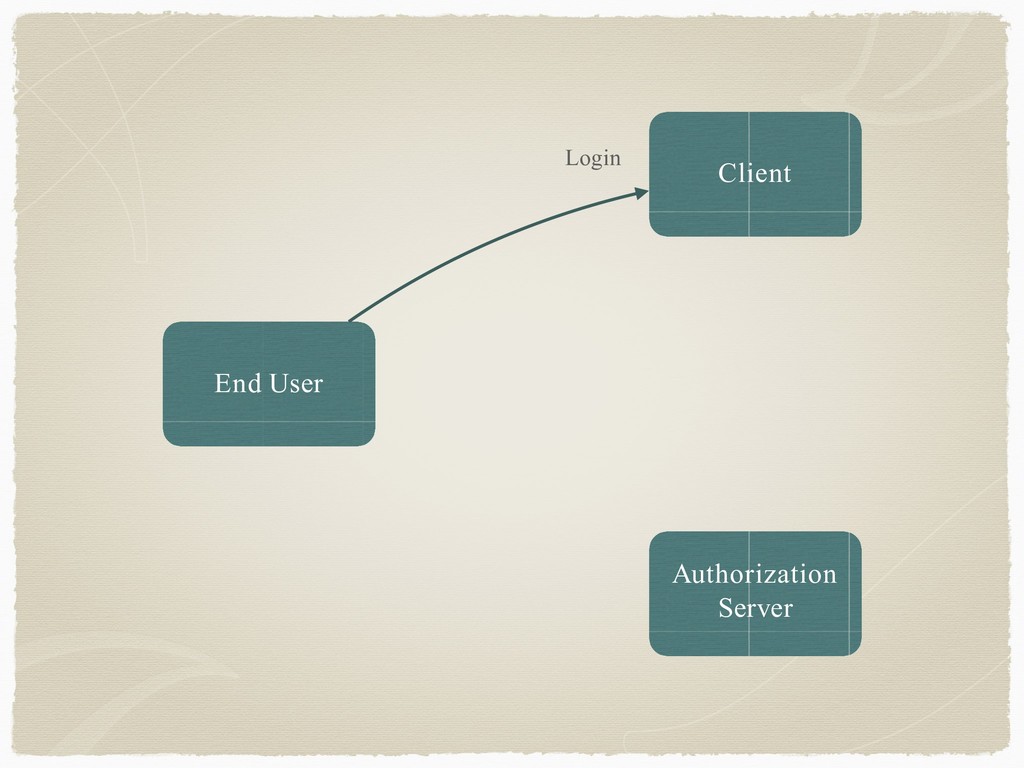
Authorization Server Client End User Login
Authorization Server Client End User Redirect to AuthorizationServer scope=openid
Authorization Server Client End User Authorization Request
GET / POST
Authorization Server Client End User Challenge
Client End User User Credentials Authorization Server
Authorization Server Client End User Authorization Request
Client End User Authorization Grant Authorization Server
Authorization Server Client End User Redirect to Client withCode
Authorization Server Client End User Use Code to get Access
Token ID Token
ID token
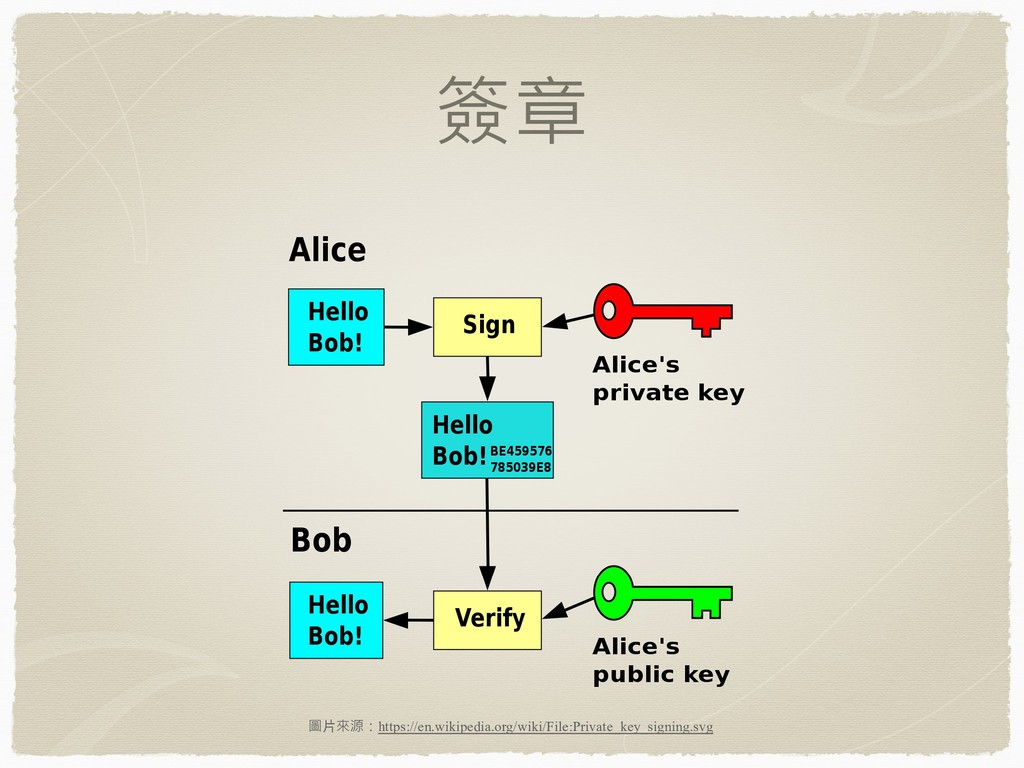
簽章 圖⽚來源:https://en.wikipedia.org/wiki/File:Private_key_signing.svg
簽章演算法 HS256 - HMVC using SHA-256 Line RS256 - RSASSA-PKCS1-v1_5
using SHA-256 AppleID, Google ES256 - ECDSA using P-256 and SHA-256 AppleID
Discovery AppleID Line Google
⽤用 用 講 的 不 就 很 會 ? 做⼀一
一 個 來 來 看 看 啊 !
Demo
Native App
先講結論 不要⽤用嵌入式 User Agent,即麻煩又危險 可使⽤用 PKCE 來解決這個問題
Chrome on Mobile 圖⽚來源:https://www.ory.sh/oauth2-for-mobile-app-spa-browser/
App on Mobile 圖⽚來源:https://www.ory.sh/oauth2-for-mobile-app-spa-browser/
Security Topic
基本 TLS CSRF XSS CSP Same-origin Policy
HTML 登入 無標準協定 網路釣⿂魚
Covert Redirect Redirect url 驗證
清除登入狀態 Token Revoke 的時機 OpenID Session Management Front-Channel Logout Back-Channel
Logout
Extra - Password 千萬不要存明碼 MD5 與 SHA1 已被認為是不安全的演算法 建議使⽤用 SHA256
Extra - Cookie 問題核⼼心在於過度依賴 Cookie 作為身分驗證的⼿手段 CSRF Session Hijacking Session
Fixation Weak Confidentiality Weak Integrity
Q & A


 starrocket
 visional_engineering_and_design
 nagix
 nao_randd
 ota1022
 vtryo
 genshun9
 budougumi0617
 megascus
 m3m0r7
 grimoh
 plaidtech
 nikkei_engineer_recruiting
 samanthasiow
 akademiya2063
 shlominoach
 bcantrill
 pauljervisheath
 leimatthew05
 jakevdp
 bermonpainter
 destraynor
 lauravandoore
 techseoconnect
 aleyda