Share
Embed
Meet the Keycloak Maintainer
Here are the slides of a Keycloak update the Keycloak Meetup Vienna
Alexander Schwartz PRO
November 05, 2026
Transcript
25 slides
-
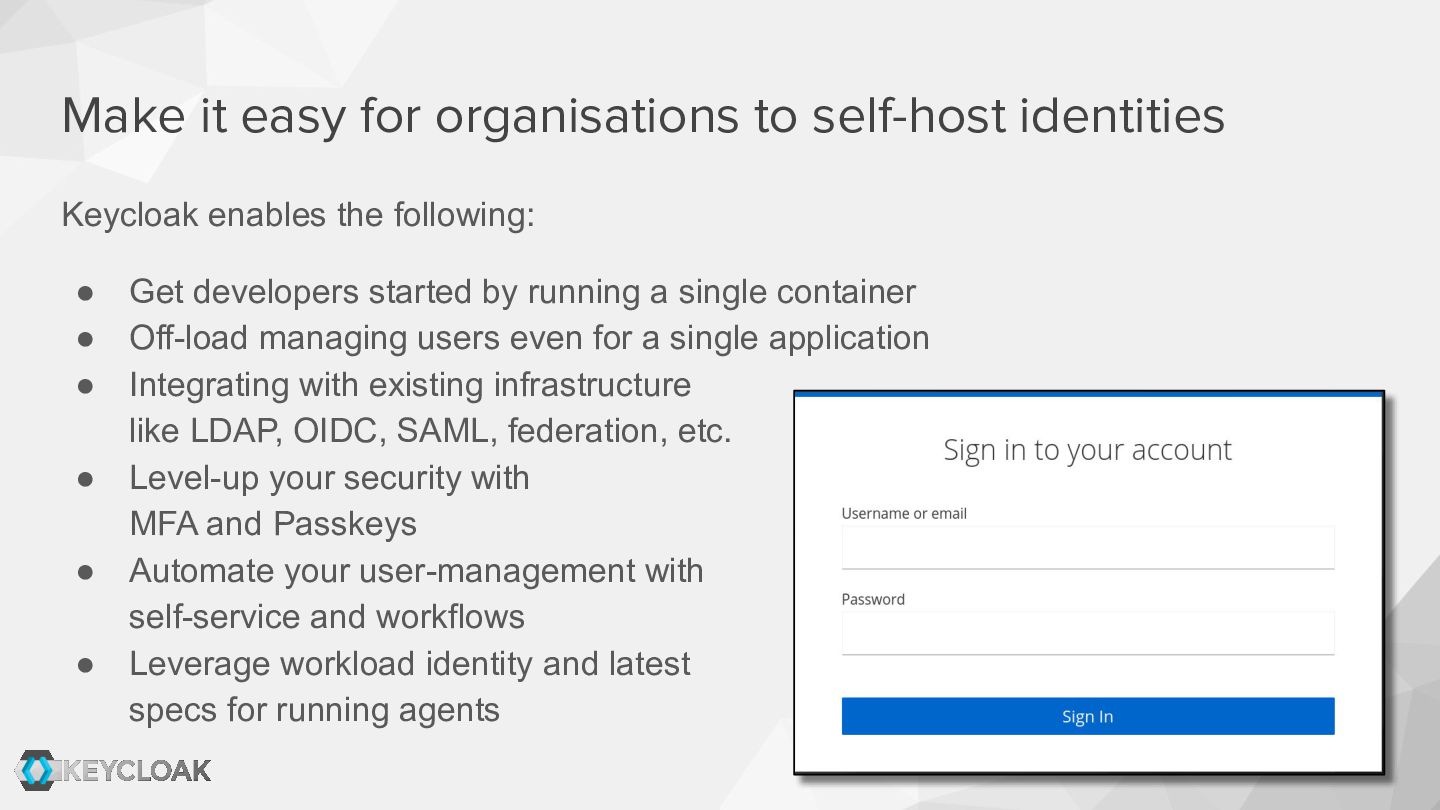
Make it easy for organisations to self-host identities Keycloak enables
the following: • Get developers started by running a single container • Off-load managing users even for a single application • Integrating with existing infrastructure like LDAP, OIDC, SAML, federation, etc. • Level-up your security with MFA and Passkeys • Automate your user-management with self-service and workflows • Leverage workload identity and latest specs for running agents -
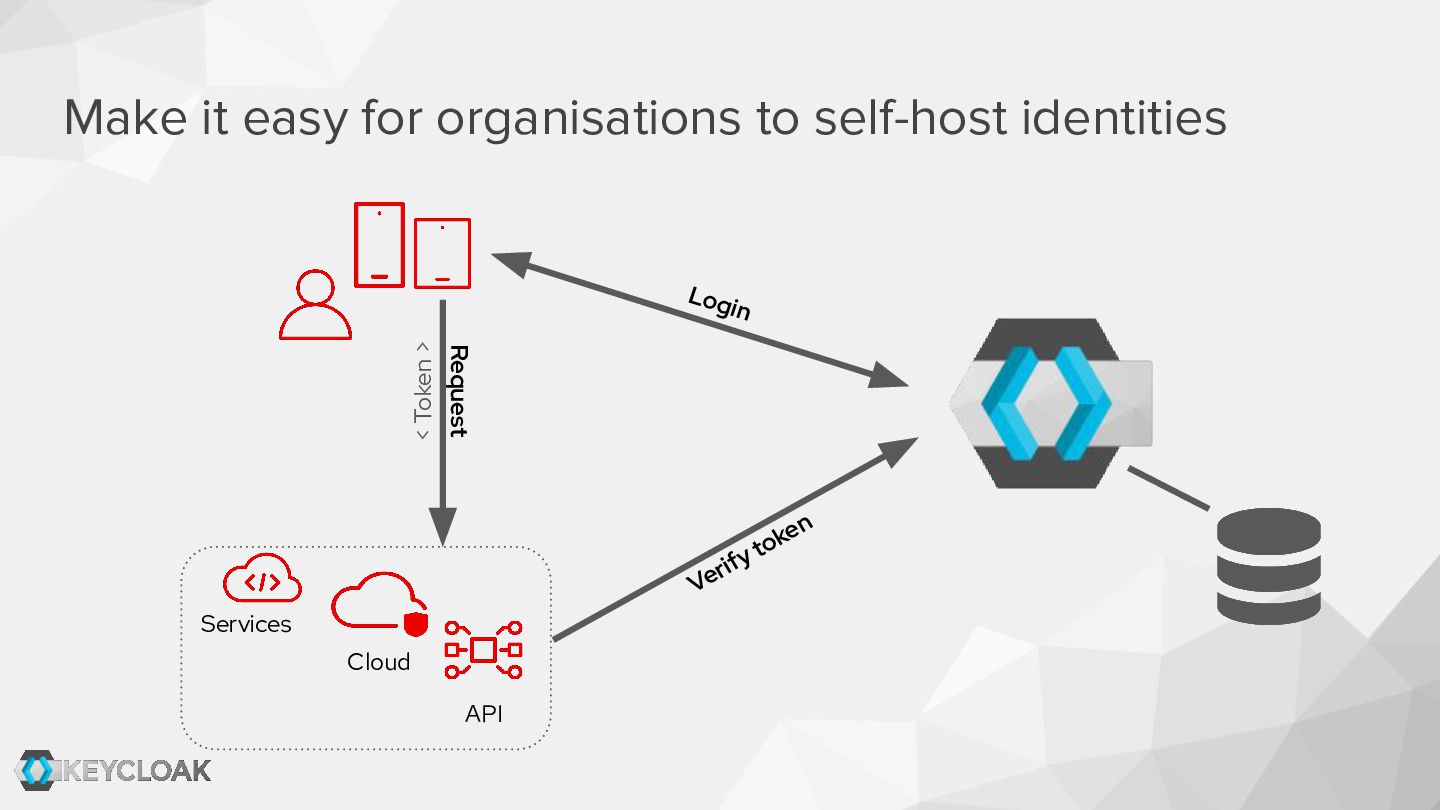
Make it easy for organisations to self-host identities Request <
Token > Log in f ri Ve Services Cloud API en ok t y -
Keycloak is an Open Source Identity und Access Management System
🎂 First Commit 2013-07-02 📜 Apache License, Version 2.0 ⭐ 37k GitHub stars -
Case Studies Hitachi Ltd. used Keycloak to make financial grade
security easier OpenTalk achieves versatile and compliant user authentication with Keycloak BRZ migrated the Austrian Business Service Portal with 2M+ users to Keycloak https://www.keycloak.org/case-studies -
Ask for feedback To shape Keycloak’s roadmap and help us
to improve: 1. Challenges that users and admins struggle with? 2. Features on the road map that are exciting and should be prioritized? 3. Features are already used, but should be promoted more? -
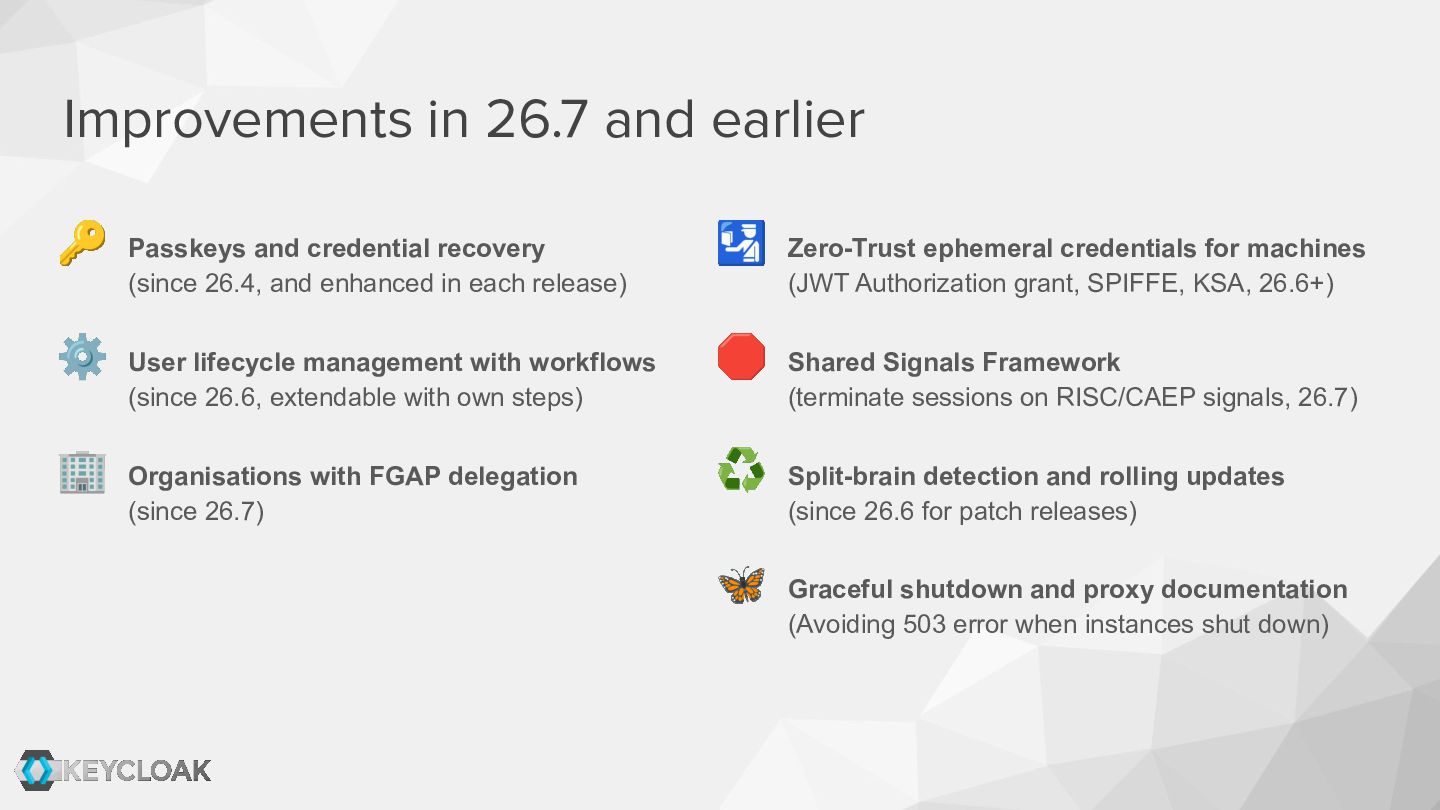
Improvements in 26.7 and earlier 🔑 Passkeys and credential recovery
(since 26.4, and enhanced in each release) ⚙ User lifecycle management with workflows (since 26.6, extendable with own steps) 🏢 Organisations with FGAP delegation (since 26.7) 🛂 Zero-Trust ephemeral credentials for machines (JWT Authorization grant, SPIFFE, KSA, 26.6+) 🛑 Shared Signals Framework (terminate sessions on RISC/CAEP signals, 26.7) ♻ Split-brain detection and rolling updates (since 26.6 for patch releases) 🦋 Graceful shutdown and proxy documentation (Avoiding 503 error when instances shut down) -
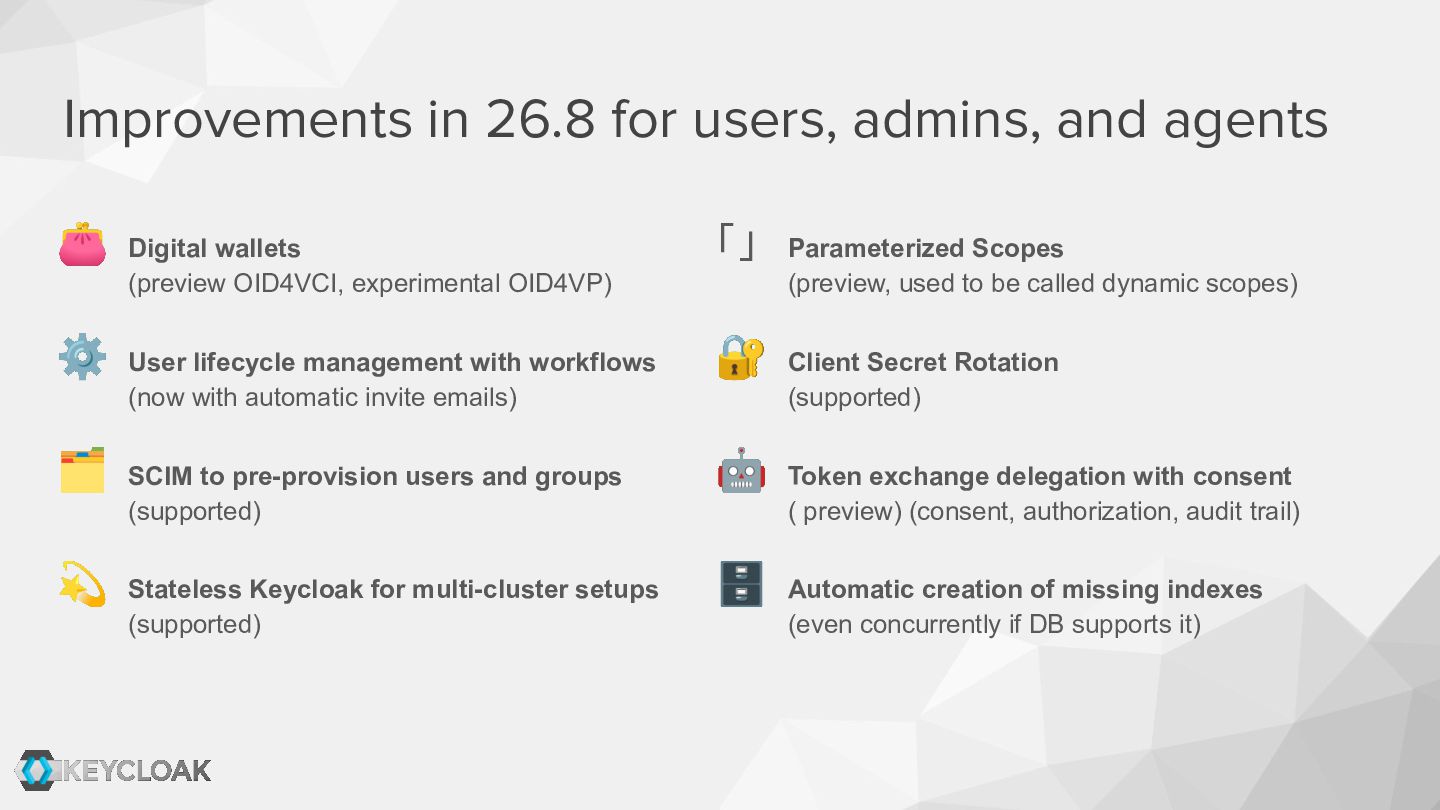
Improvements in 26.8 for users, admins, and agents 👛 Digital
wallets (preview OID4VCI, experimental OID4VP) ⚙ User lifecycle management with workflows (now with automatic invite emails) 🗂 SCIM to pre-provision users and groups (supported) 💫 Stateless Keycloak for multi-cluster setups (supported) 「」 Parameterized Scopes (preview, used to be called dynamic scopes) 🔐 Client Secret Rotation (supported) 🤖 Token exchange delegation with consent ( preview) (consent, authorization, audit trail) 🗄 Automatic creation of missing indexes (even concurrently if DB supports it) -
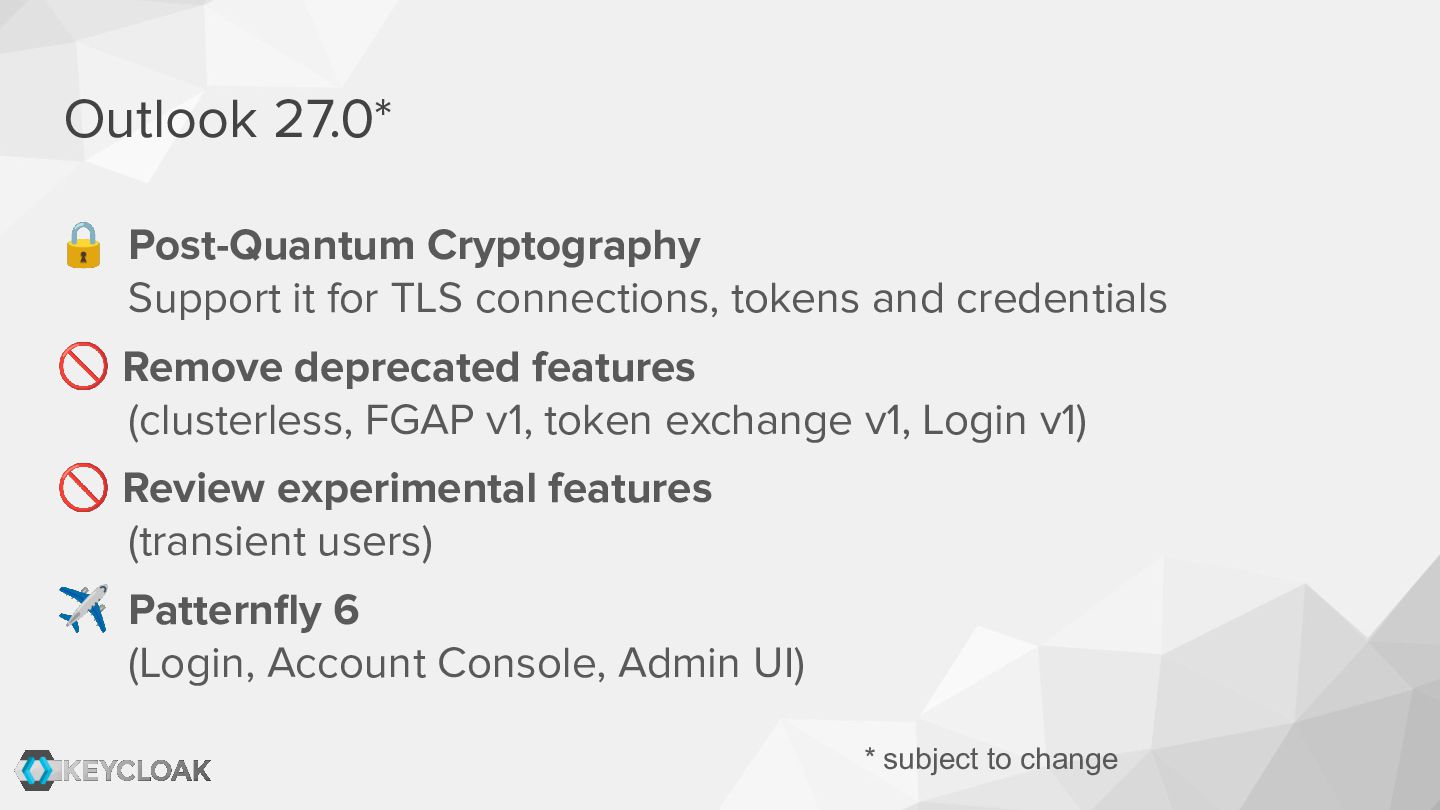
Outlook 27.0* 🔒 Post-Quantum Cryptography Support it for TLS connections,
tokens and credentials 🚫 Remove deprecated features (clusterless, FGAP v1, token exchange v1, Login v1) 🚫 Review experimental features (transient users) ✈ Patternfly 6 (Login, Account Console, Admin UI) * subject to change -
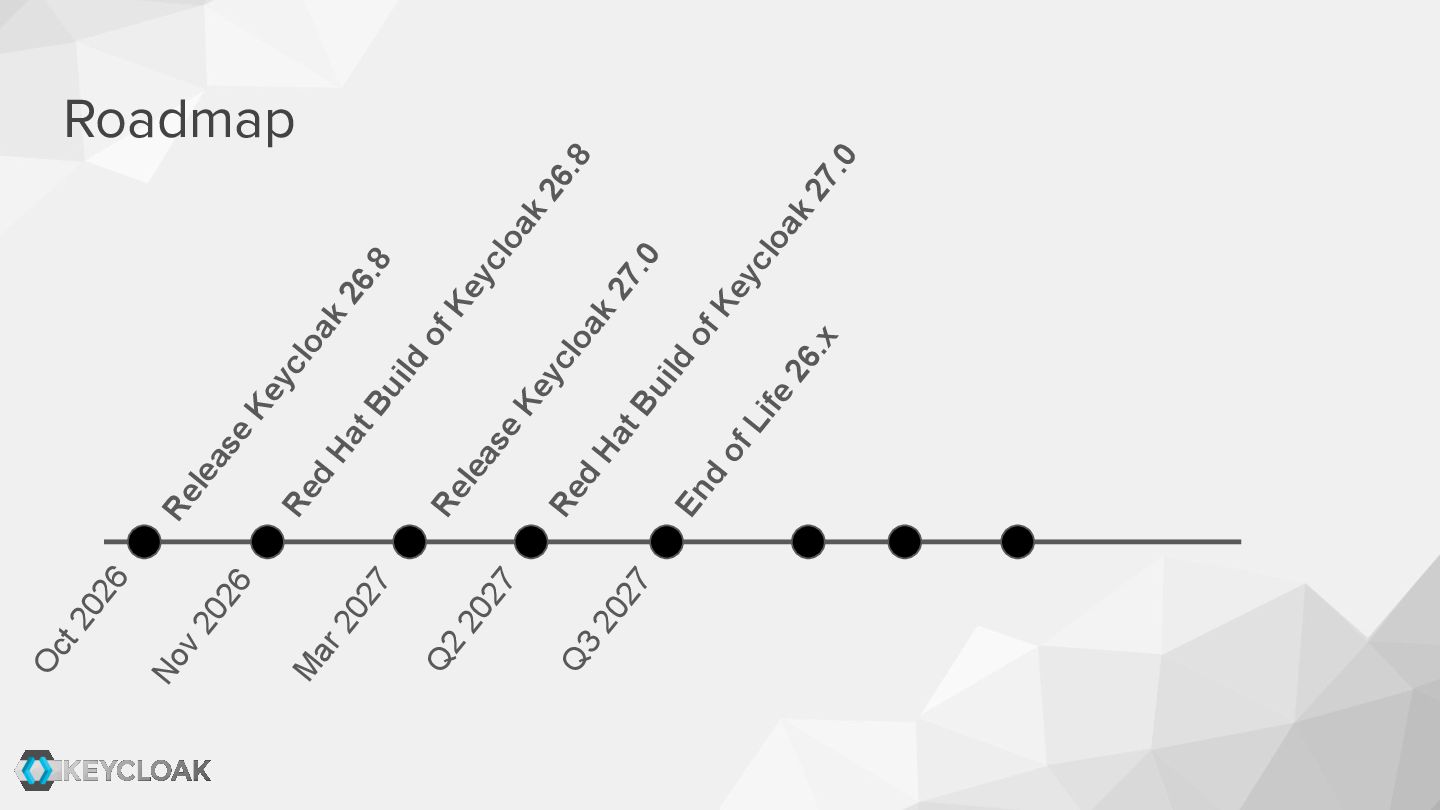
Q3 Q2 ar M No v 27 20 27 20
27 20 26 20 6 02 t2 Oc d En d Re se of of 26 cl oa k Ke y 27 .0 cl oa k .8 Ke y ak x 26 . ui ld Li fe of yc lo Ke tB Ha le a Re ui ld ak lo yc Ke tB Ha se ea d Re Re l .0 27 .8 26 Roadmap -
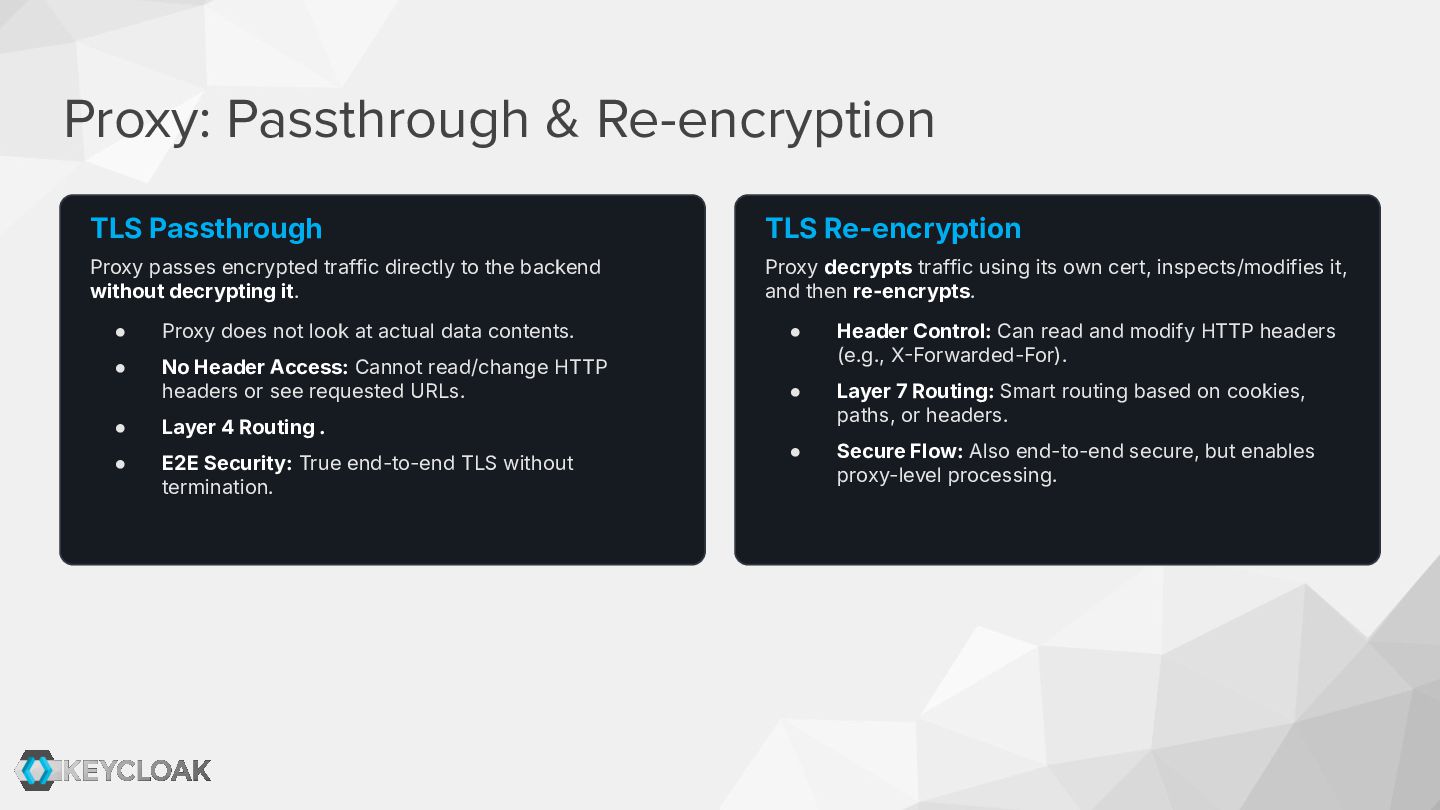
Proxy: Passthrough & Re-encryption TLS Passthrough TLS Re-encryption Proxy passes
encrypted traffic directly to the backend without decrypting it. Proxy decrypts traffic using its own cert, inspects/modifies it, and then re-encrypts. • Proxy does not look at actual data contents. • • No Header Access: Cannot read/change HTTP headers or see requested URLs. Header Control: Can read and modify HTTP headers (e.g., XForwarded-For). • Layer 7 Routing: Smart routing based on cookies, paths, or headers. • Secure Flow: Also end-to-end secure, but enables proxy-level processing. • Layer 4 Routing . • E2E Security: True end-to-end TLS without termination. -
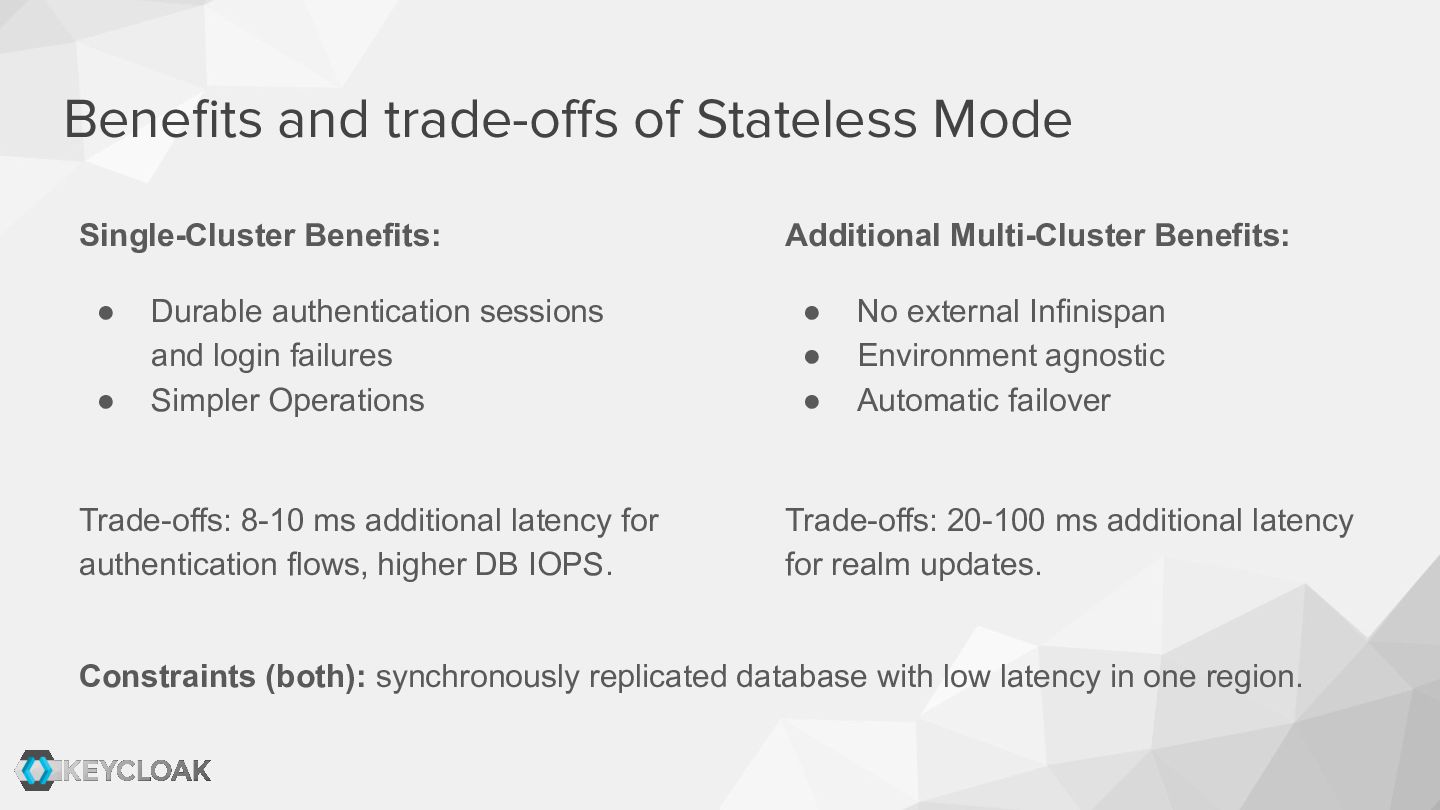
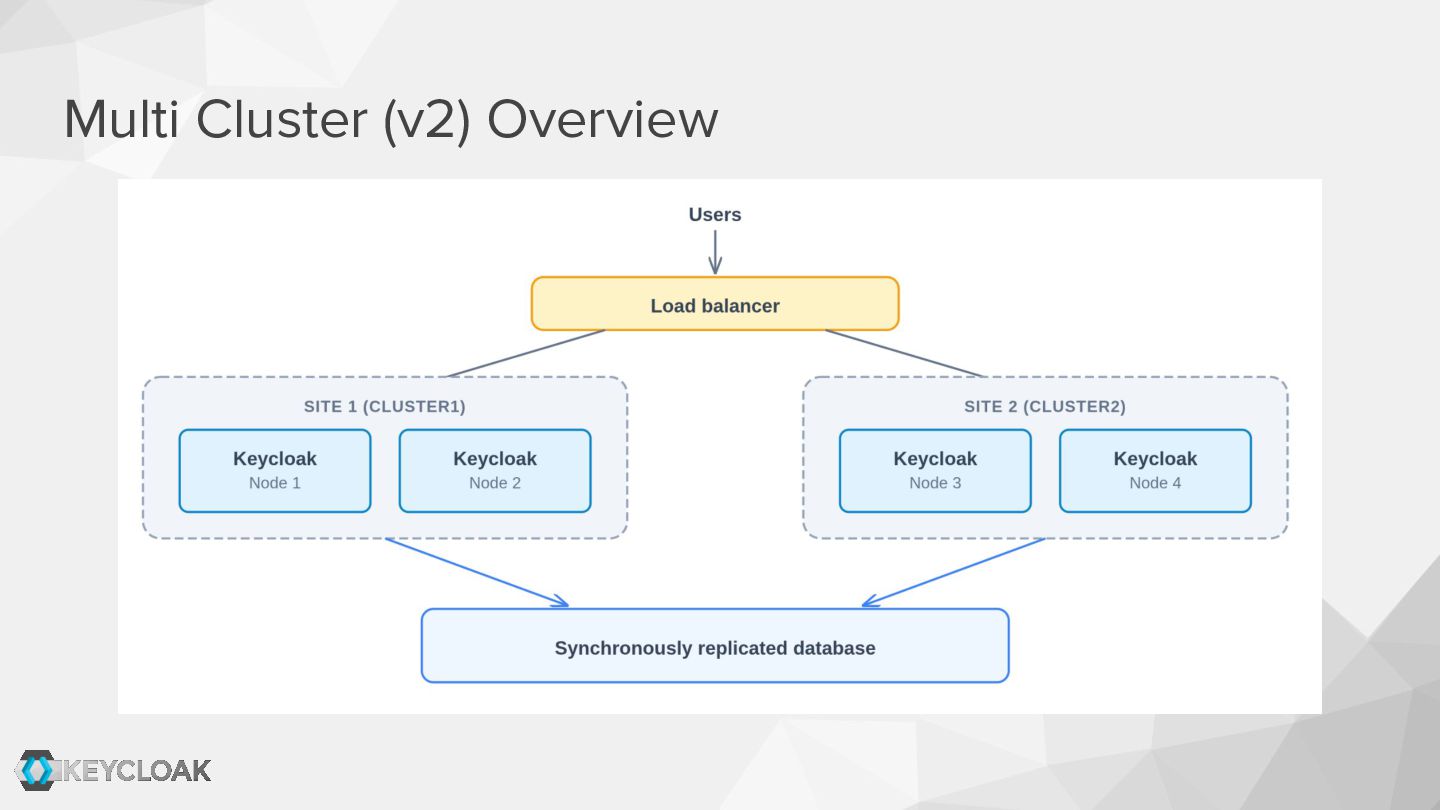
Benefits and trade-offs of Stateless Mode Single-Cluster Benefits: Additional Multi-Cluster
Benefits: • • • • • Durable authentication sessions and login failures Simpler Operations Trade-offs: 8-10 ms additional latency for authentication flows, higher DB IOPS. No external Infinispan Environment agnostic Automatic failover Trade-offs: 20-100 ms additional latency for realm updates. Constraints (both): synchronously replicated database with low latency in one region. -
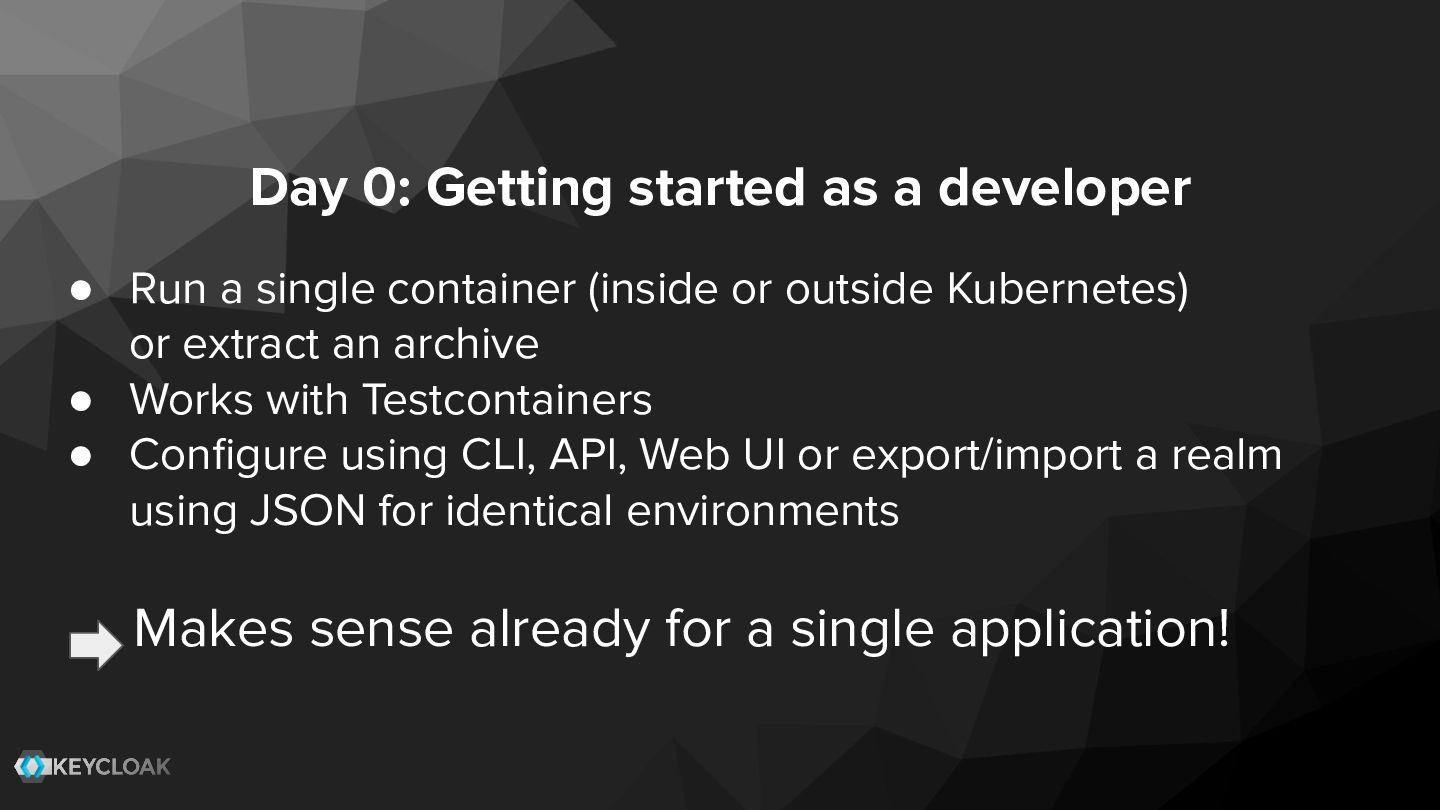
Day 0: Getting started as a developer • Run a
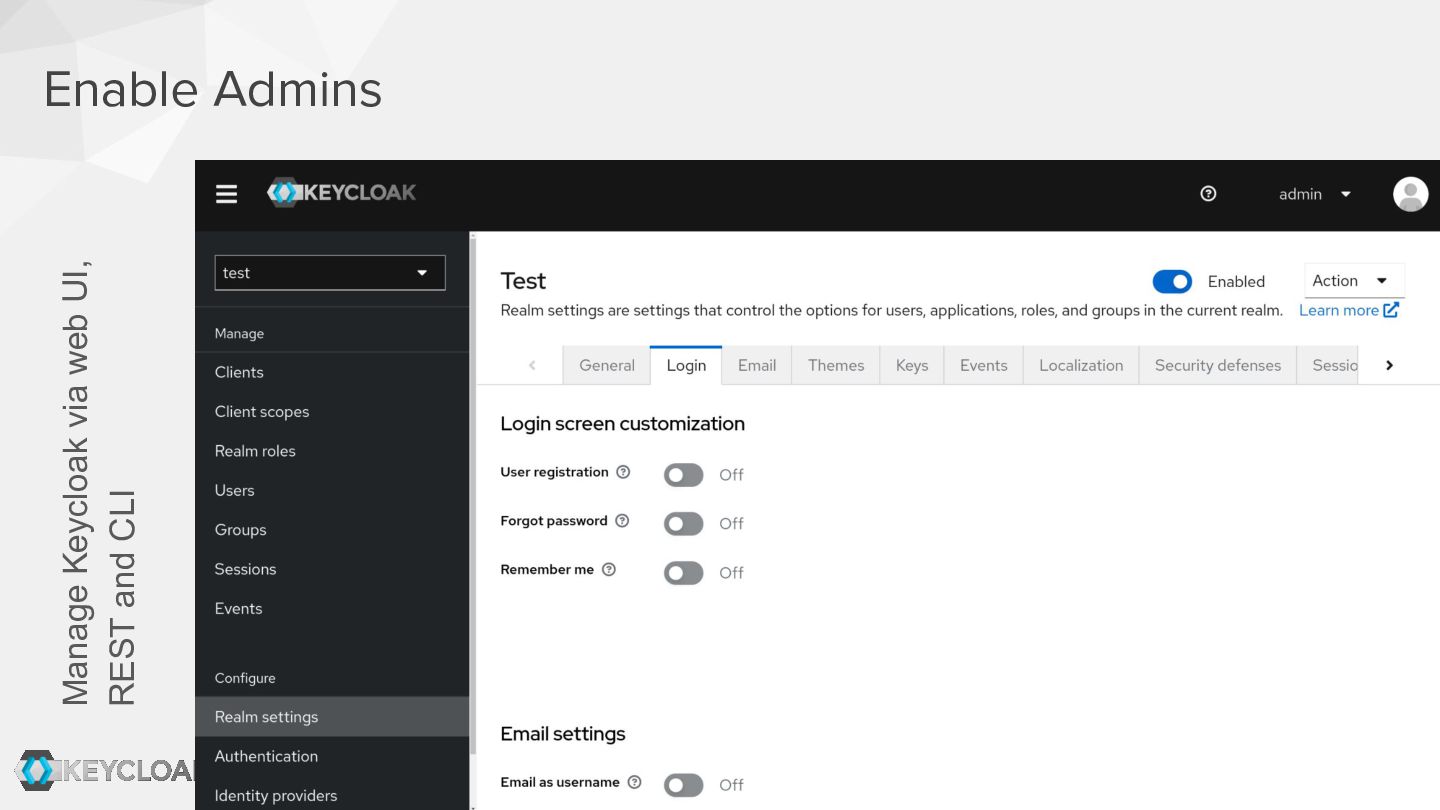
single container (inside or outside Kubernetes) or extract an archive • Works with Testcontainers • Configure using CLI, API, Web UI or export/import a realm using JSON for identical environments Makes sense already for a single application! -
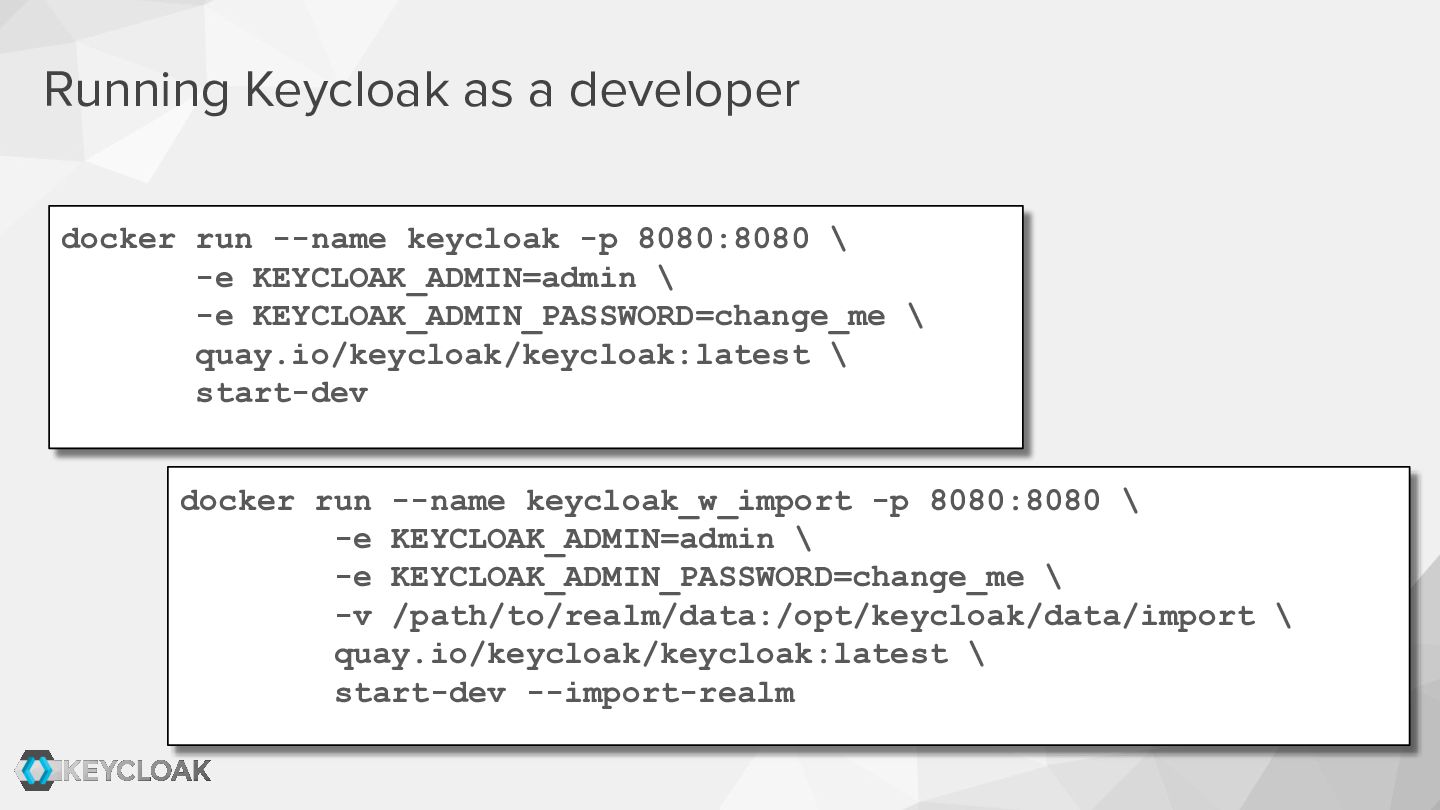
Running Keycloak as a developer docker run --name keycloak -p
8080:8080 \ -e KEYCLOAK_ADMIN=admin \ -e KEYCLOAK_ADMIN_PASSWORD=change_me \ quay.io/keycloak/keycloak:latest \ start-dev docker run --name keycloak_w_import -p 8080:8080 \ -e KEYCLOAK_ADMIN=admin \ -e KEYCLOAK_ADMIN_PASSWORD=change_me \ -v /path/to/realm/data:/opt/keycloak/data/import \ quay.io/keycloak/keycloak:latest \ start-dev --import-realm -
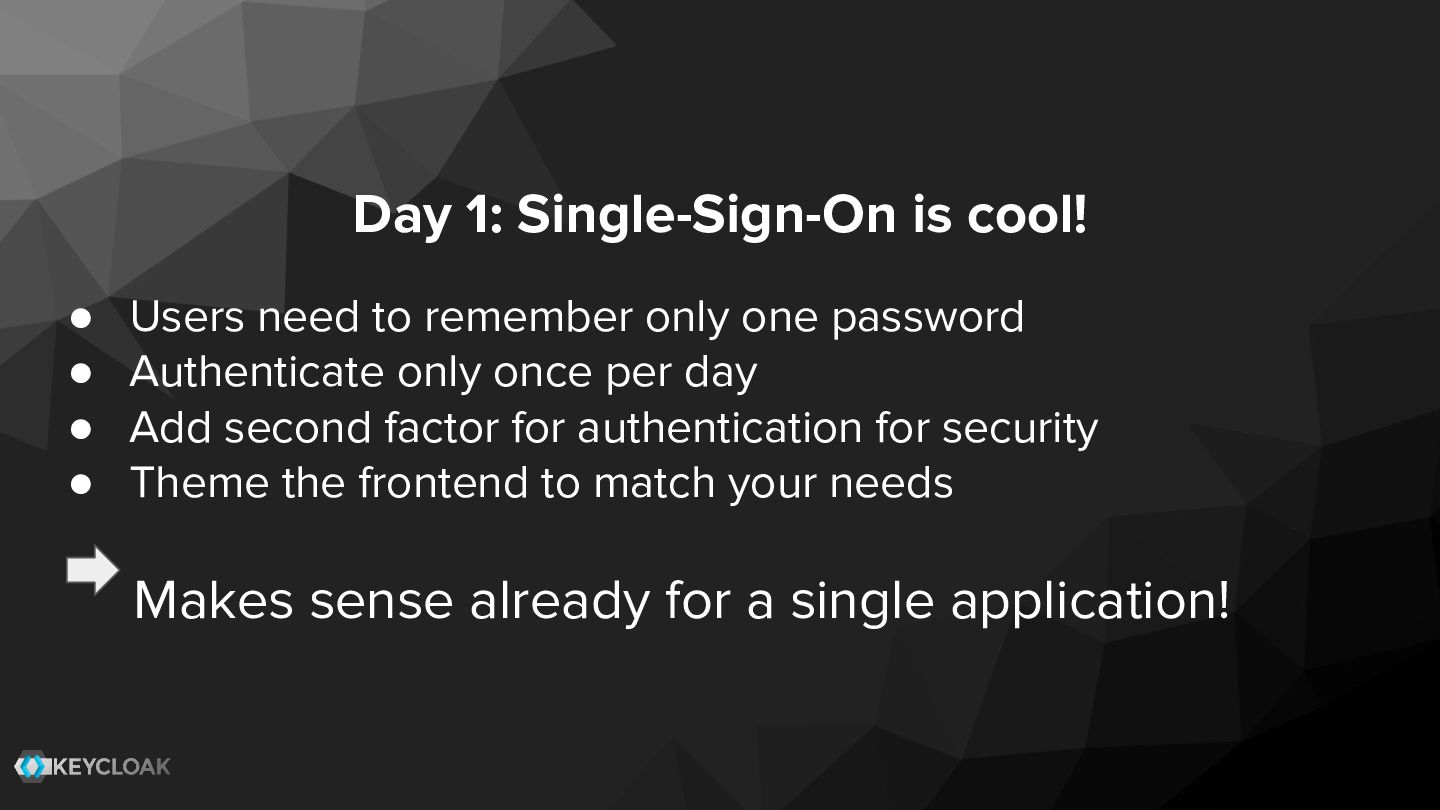
Day 1: Single-Sign-On is cool! • • • • Users
need to remember only one password Authenticate only once per day Add second factor for authentication for security Theme the frontend to match your needs Makes sense already for a single application! -
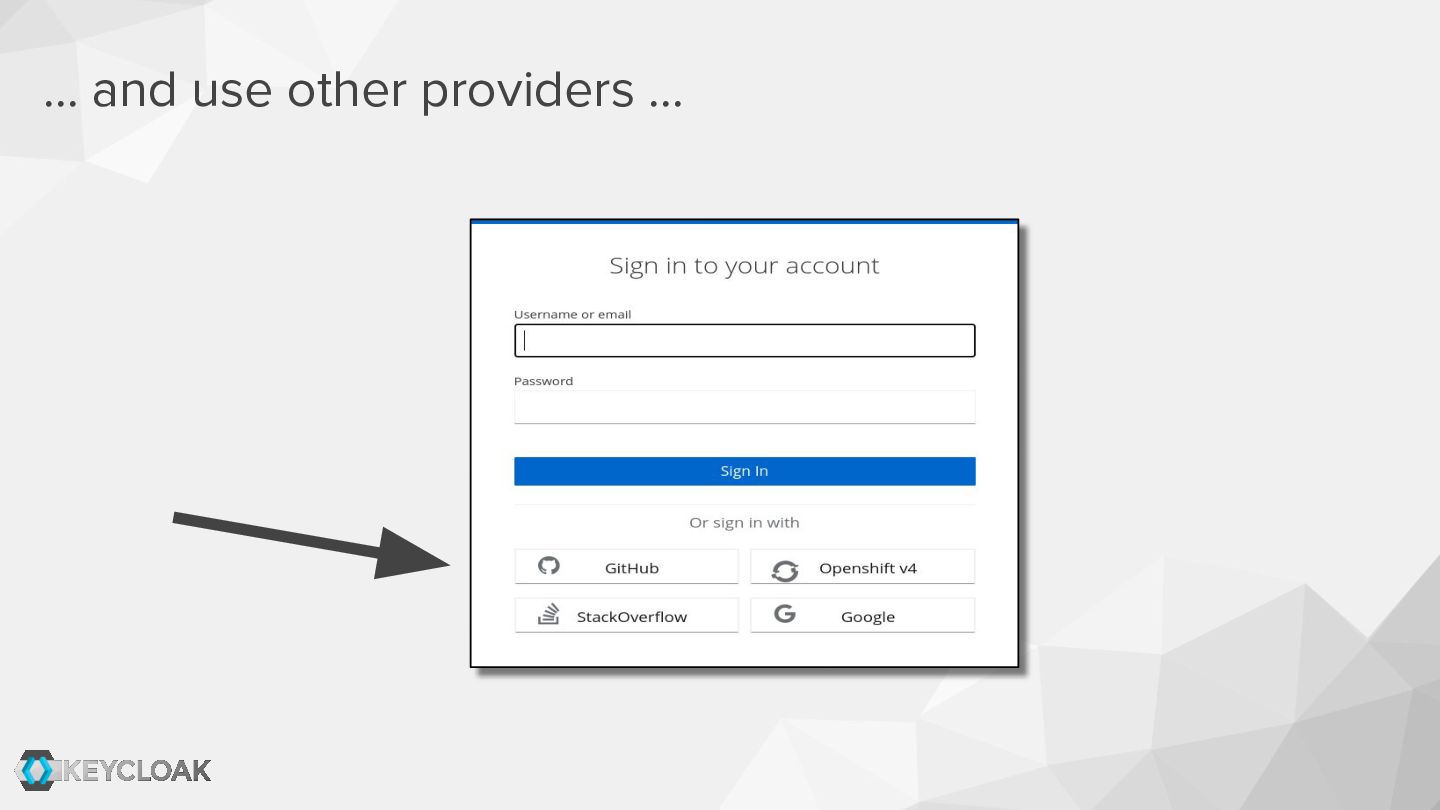
Day 2: Become flexible in your setup • • •
• Integrate LDAP and Kerberos Brokerage to existing SAML services Brokerage to existing OIDC services Integrate existing custom stores Reuse the existing user infrastructure! -
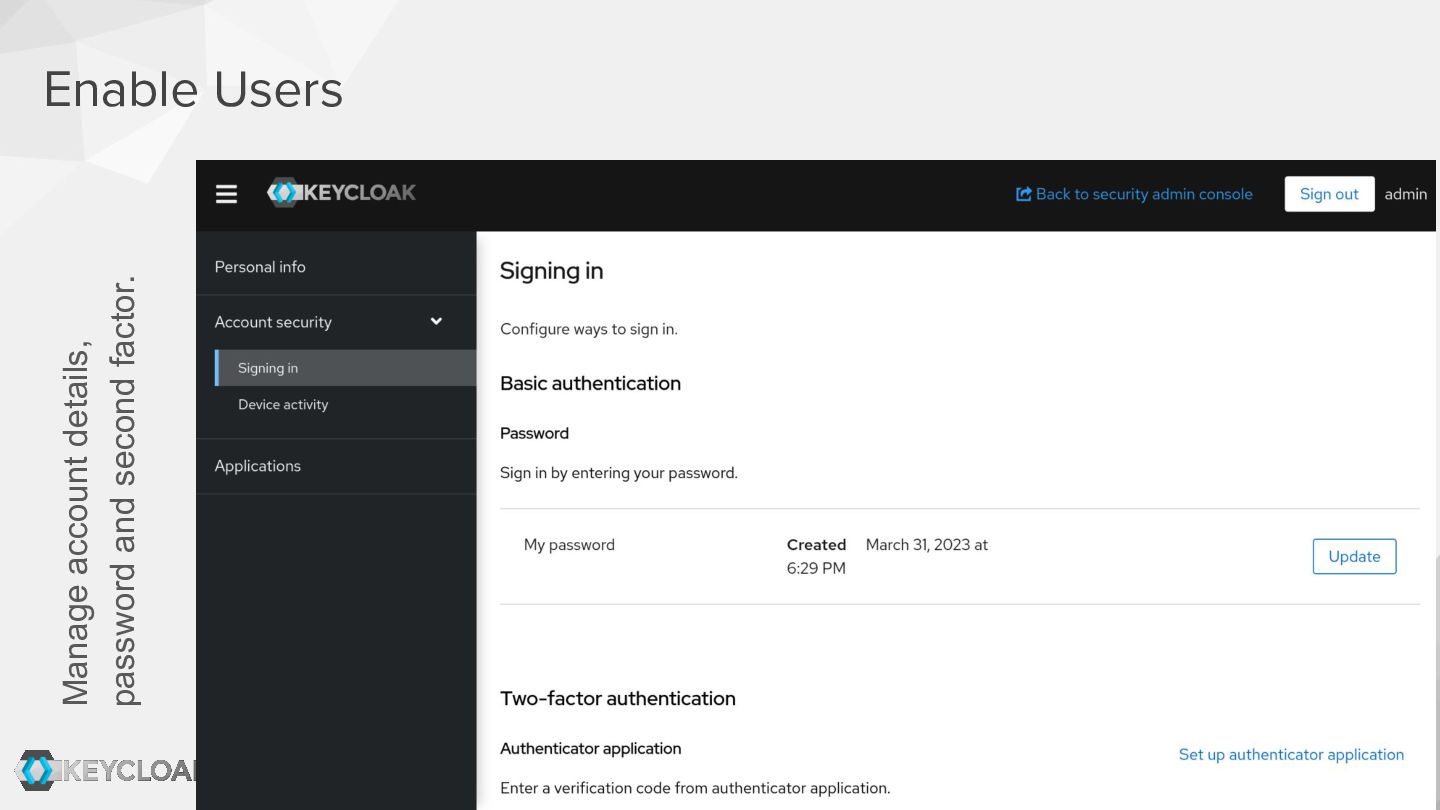
Day 3: Eliminate daily churn • • • • User
required actions User password recovery (even when using LDAP) Self-registration for users User data self-management Resolve the need for calls and tickets! -
Links • Slides: Keycloak https://www.keycloak.org/ https://www.keycloak.org/securing-apps/dpop • KeycloakCon @ KubeCon
EU / 15…18 Mar 2027 https://events.linuxfoundation.org/kubecon-cloudnativecon-europe/ • Keycloak DevDay / 8..9 Apr 2027 https://keycloak-day.dev/