Upgrade to Pro — share decks privately, control downloads, hide ads and more …

IBM TechXchange 2026 26–29 October Atlanta, GA

IBM TechXchange 2026 26–29 October Atlanta, GA

IBM TechXchange™ 2026 is the hands‑on conference where developers, engineers, scientists and researchers build real‑world skills across AI applications, data management, hybrid cloud management, infrastructure and security and governance. From hands‑on labs and workshops to technical certifications, roadmap previews and direct access to product experts, this is where practitioners come to advance their expertise.

Avatar for Amaury Borges Souza

Amaury Borges Souza

November 01, 2026

More Decks by Amaury Borges Souza

Other Decks in Technology

Transcript

  1. Hybrid Cloud Management, Security & Governance TLK-4021 - Secrets, Infrastructure

    and Trust: Securing AWS with Terraform and Vault Amaury Borges Souza CI&T, Cloud Security Engineer, Specialist Atlanta, GA October 26–29
  2. Agenda 01 The Credential Problem 02 Terraform & AWS Authentication

    03 Vault as the Trust Broker 04 Dynamic AWS Credentials 05 Secure Terraform at Scale 06 Demo & Key Takeaways IBM TechXchange | © 2026 IBM Corporation
  3. What you will learn in this session 01 The Risk

    of Long-Lived Credentials 02 Identity & Trust in AWS 03 Dinamic AWS Credentials with Vault 04 Securing Terraform Workflows 05 Scaling Trust with Guardrails IBM TechXchange | © 2026 IBM Corporation
  4. What if there were no longlived AWS credentials to steal?

    IBM TechXchange | © 2026 IBM Corporation 5
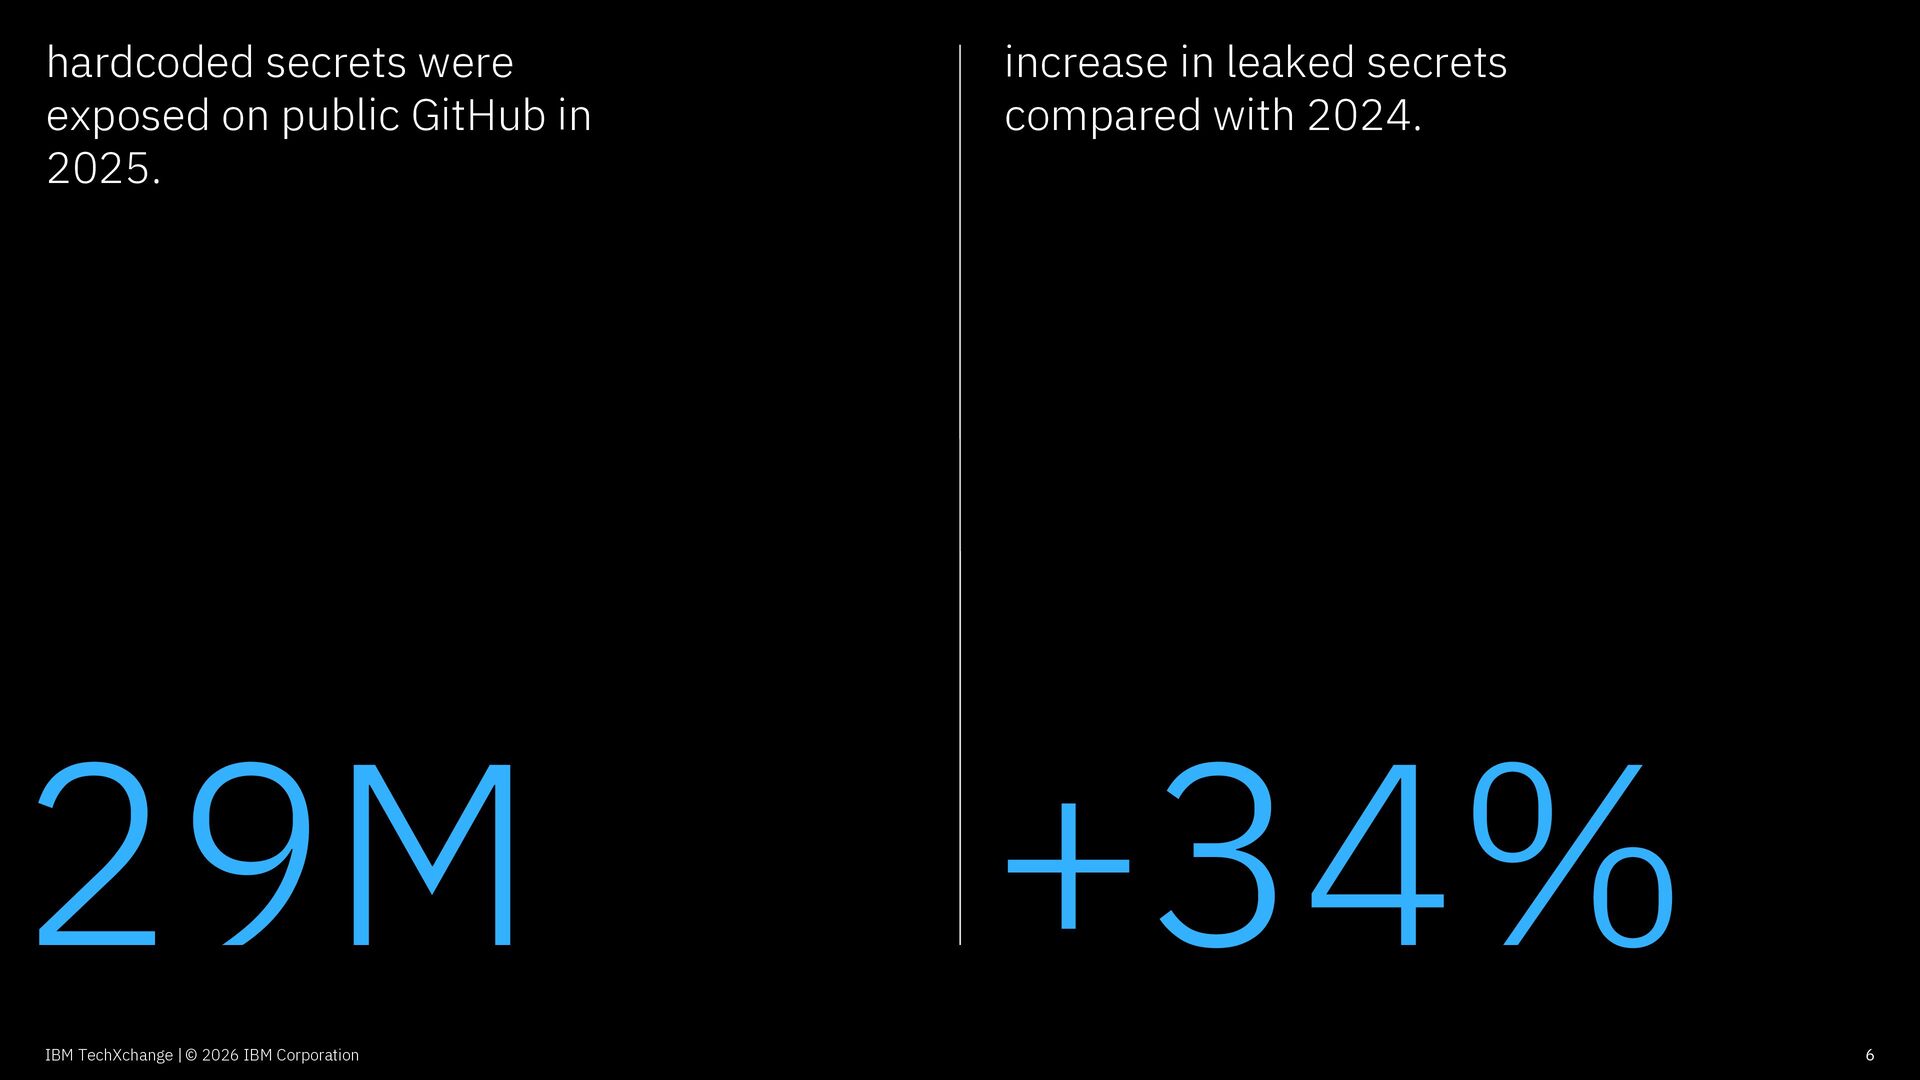
  5. hardcoded secrets were exposed on public GitHub in 2025. increase

    in leaked secrets compared with 2024. Source: 1. Lorem source name Source: 2. Lorem second source name IBM TechXchange | © 2026 IBM Corporation 6
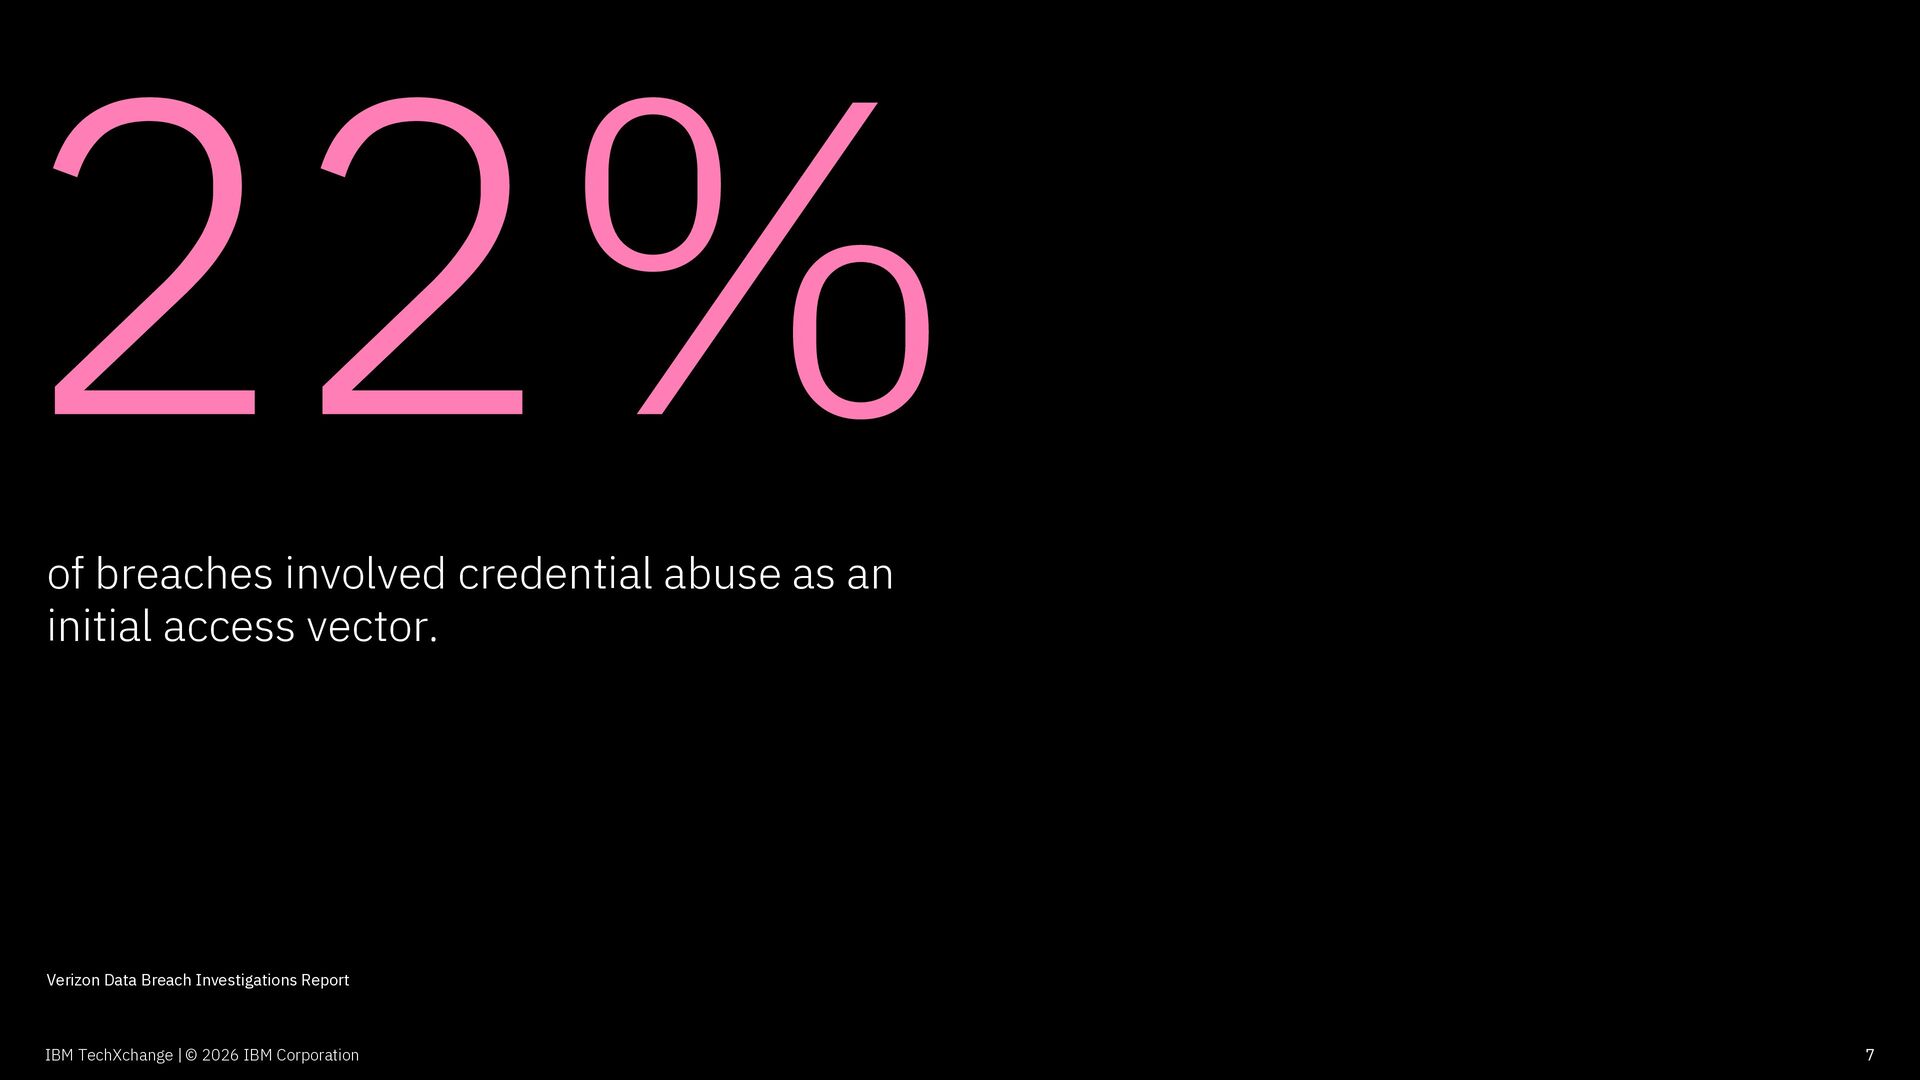
  6. of breaches involved credential abuse as an initial access vector.

    Verizon Data Breach Investigations Report IBM TechXchange | © 2026 IBM Corporation 7
  7. We automated everything. Except trust. Infrastructure is automated. Terraform provisions

    environments in minutes. Delivery is automated. CI/CD pipelines deploy applications continuously. But credentials are still static. Long-lived keys can remain valid for months or even years. IBM TechXchange | © 2026 IBM Corporation 8
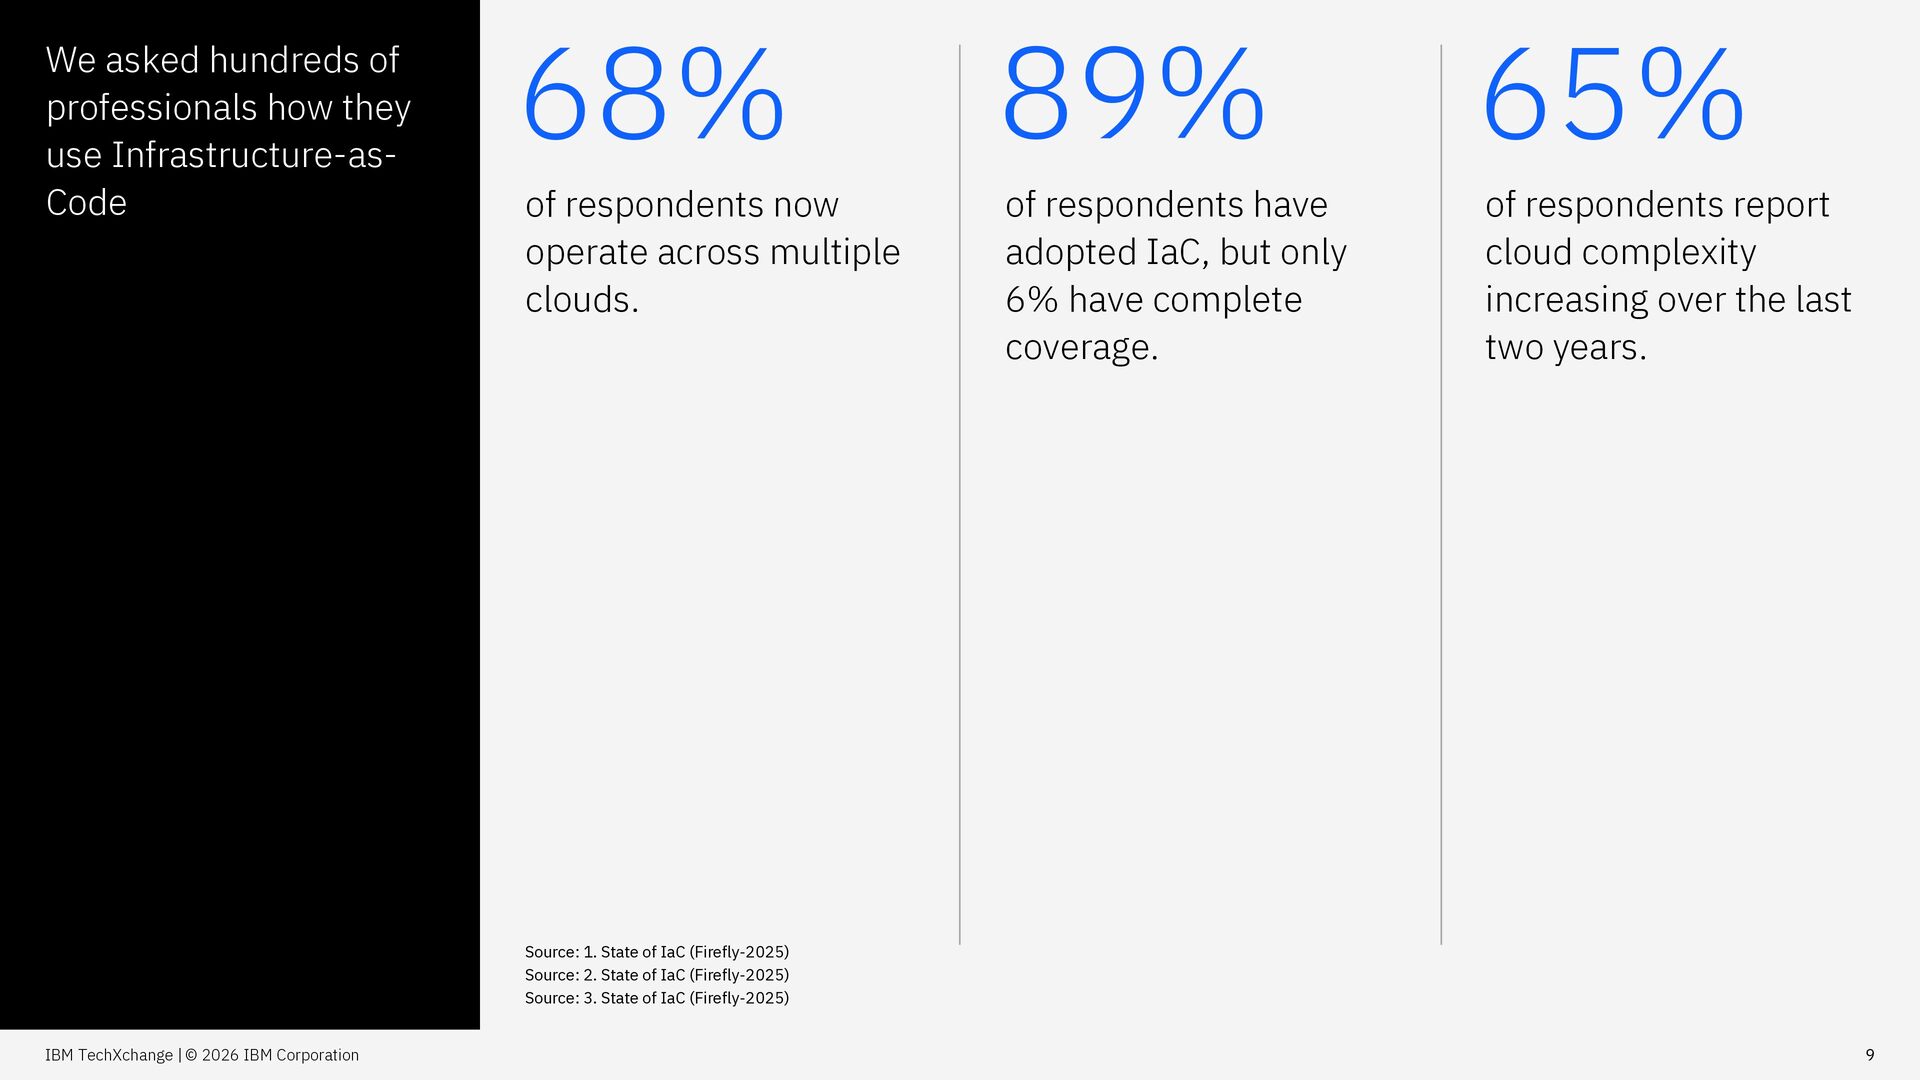
  8. We asked hundreds of professionals how they use Infrastructure-asCode 68%

    89% 65% of respondents now operate across multiple clouds. of respondents have adopted IaC, but only 6% have complete coverage. of respondents report cloud complexity increasing over the last two years. Source: 1. State of IaC (Firefly-2025) Source: 2. State of IaC (Firefly-2025) Source: 3. State of IaC (Firefly-2025) IBM TechXchange | © 2026 IBM Corporation 9
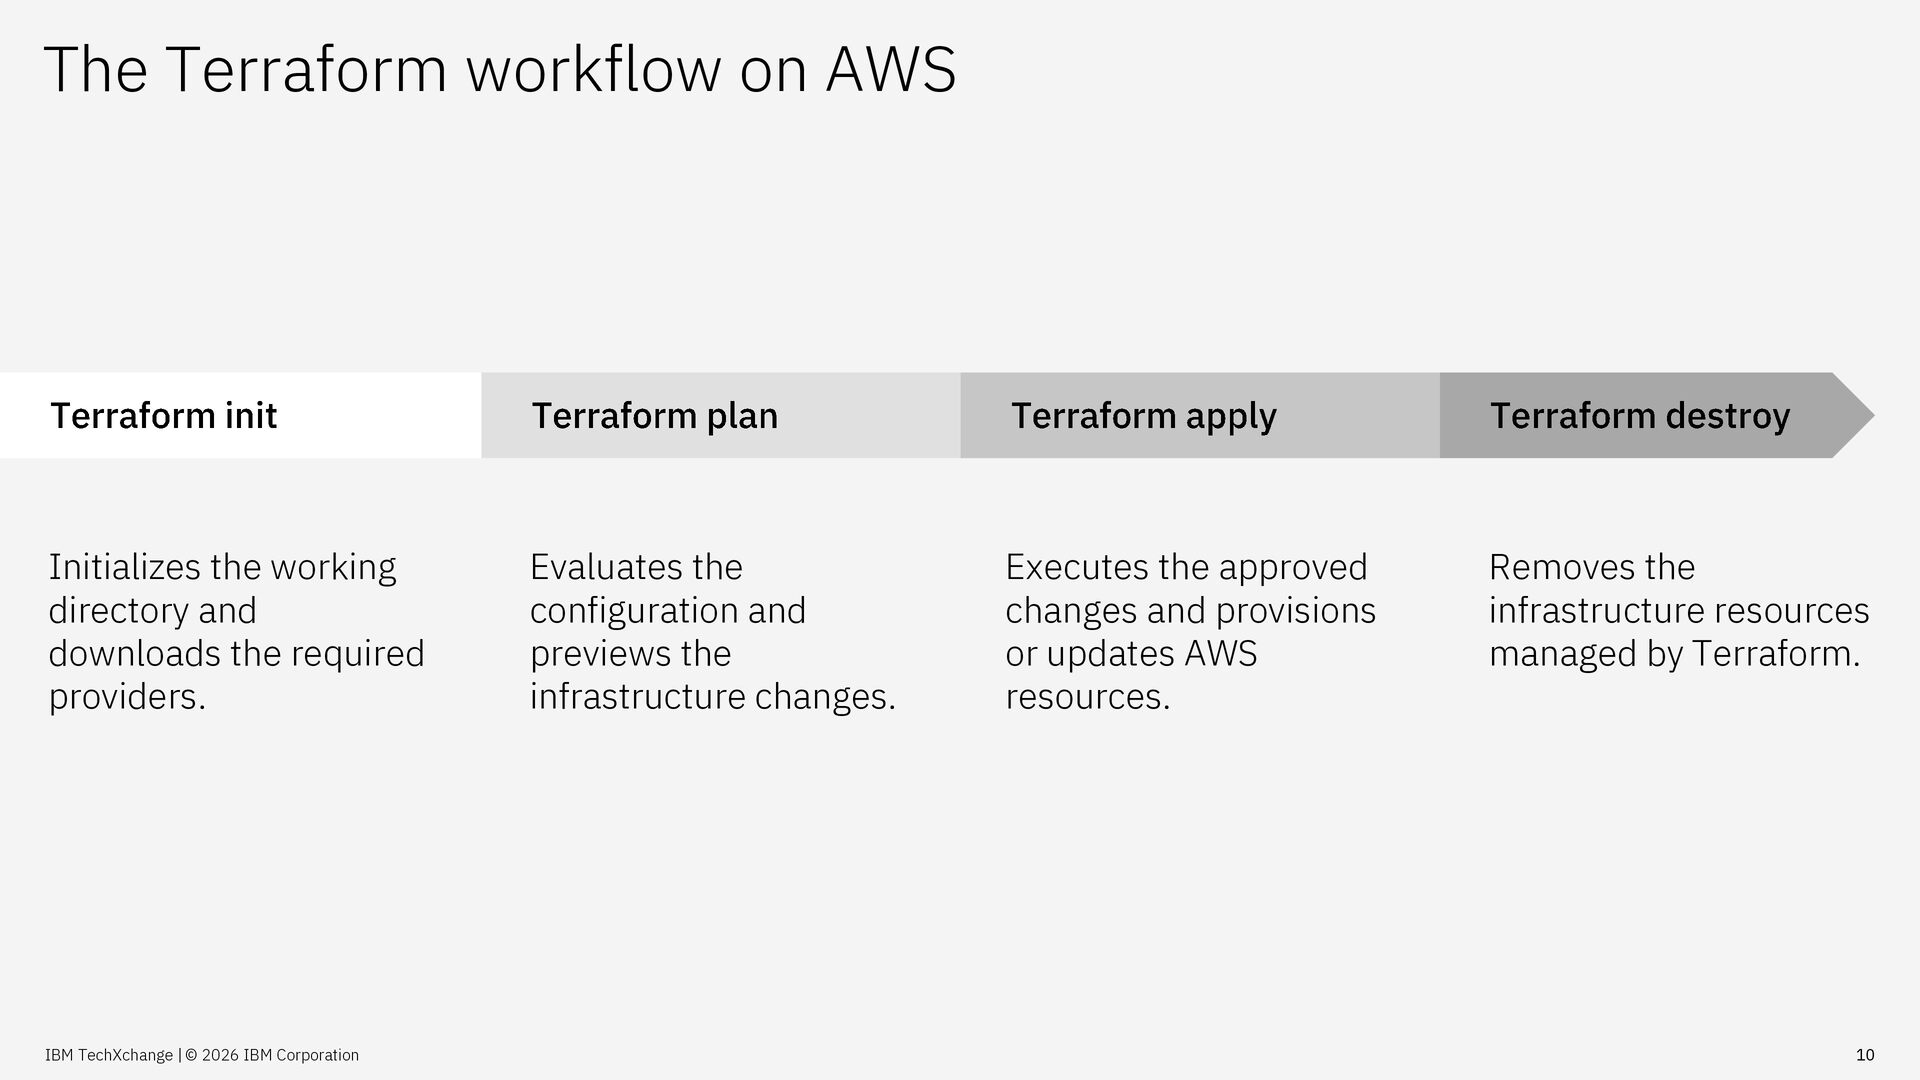
  9. The Terraform workflow on AWS Terraform init Terraform plan Terraform

    apply Terraform destroy Initializes the working directory and downloads the required providers. Evaluates the configuration and previews the infrastructure changes. Executes the approved changes and provisions or updates AWS resources. Removes the infrastructure resources managed by Terraform. IBM TechXchange | © 2026 IBM Corporation 10
  10. Terraform automates the infrastructure. But it still needs credentials to

    access AWS. IBM TechXchange | © 2026 IBM Corporation 11
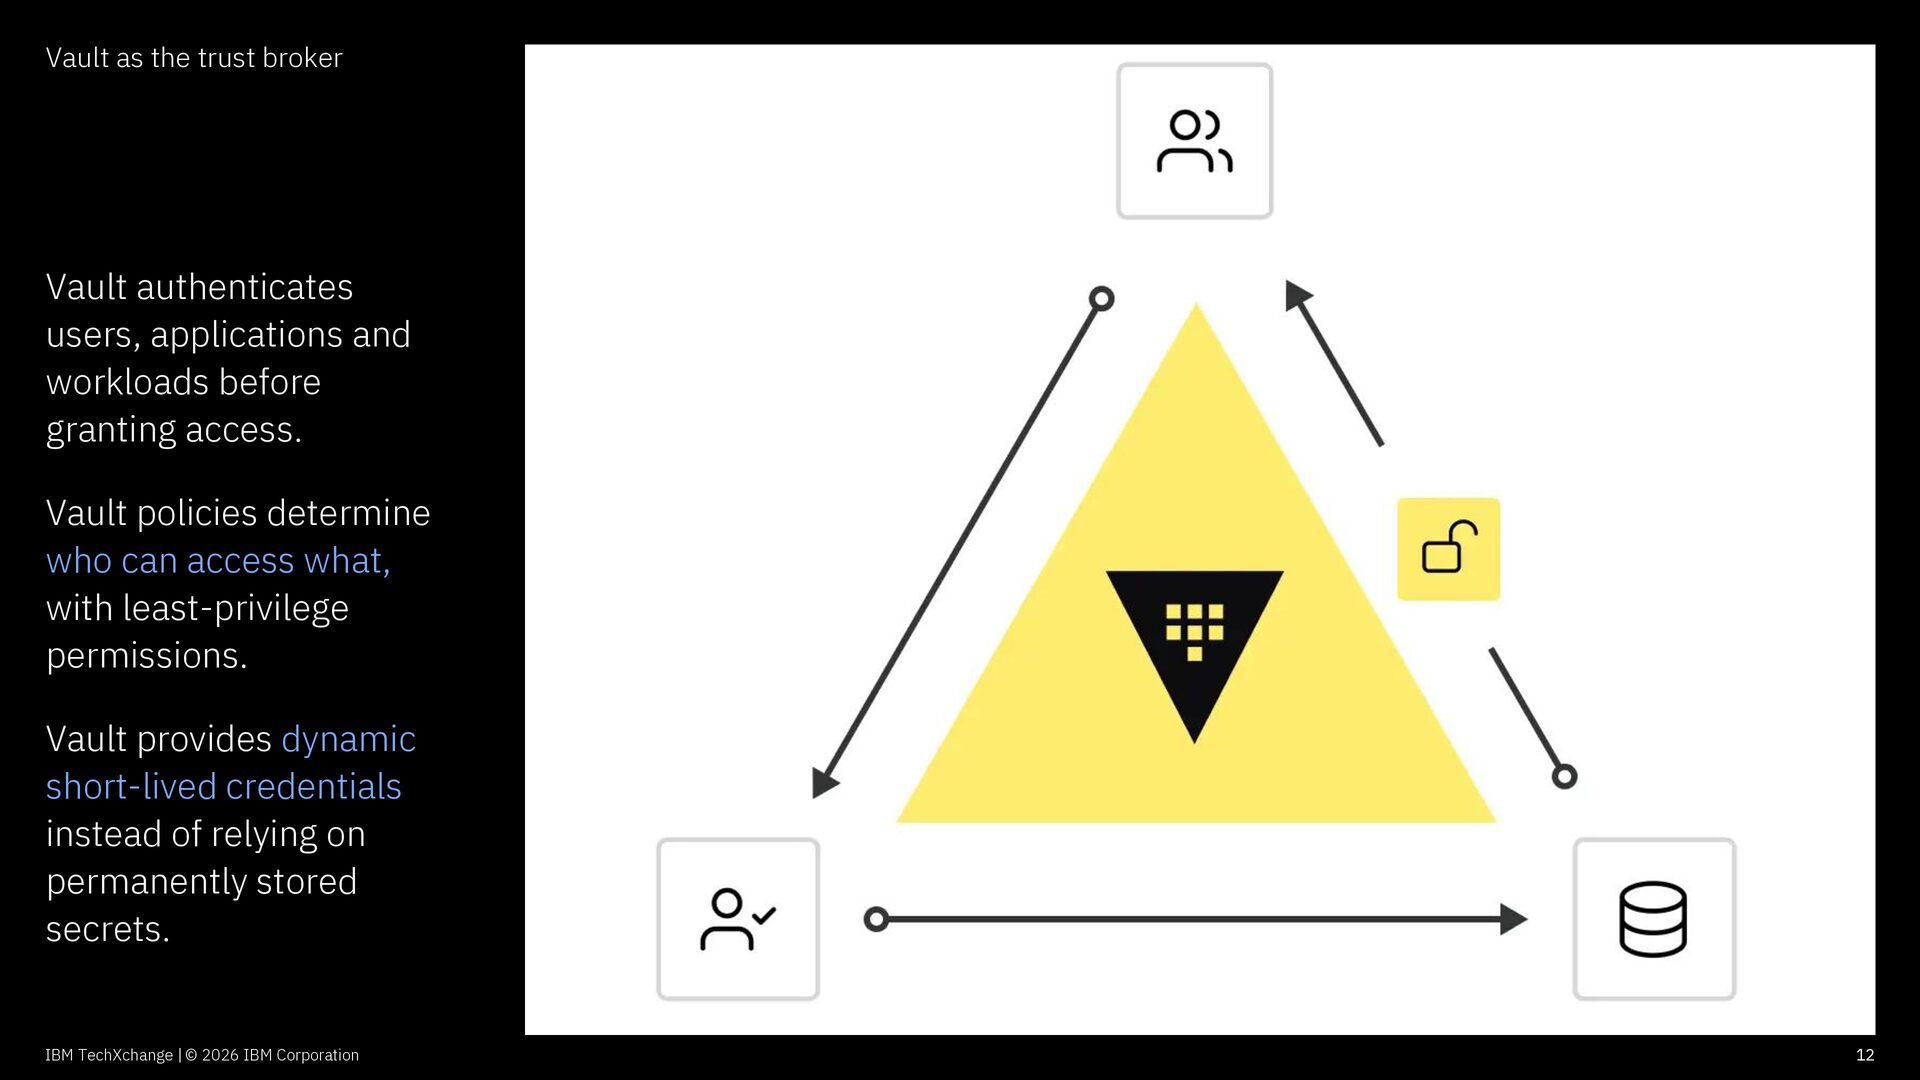
  11. Vault as the trust broker Vault authenticates users, applications and

    workloads before granting access. Vault policies determine who can access what, with least-privilege permissions. Vault provides dynamic short-lived credentials instead of relying on permanently stored secrets. IBM TechXchange | © 2026 IBM Corporation 12
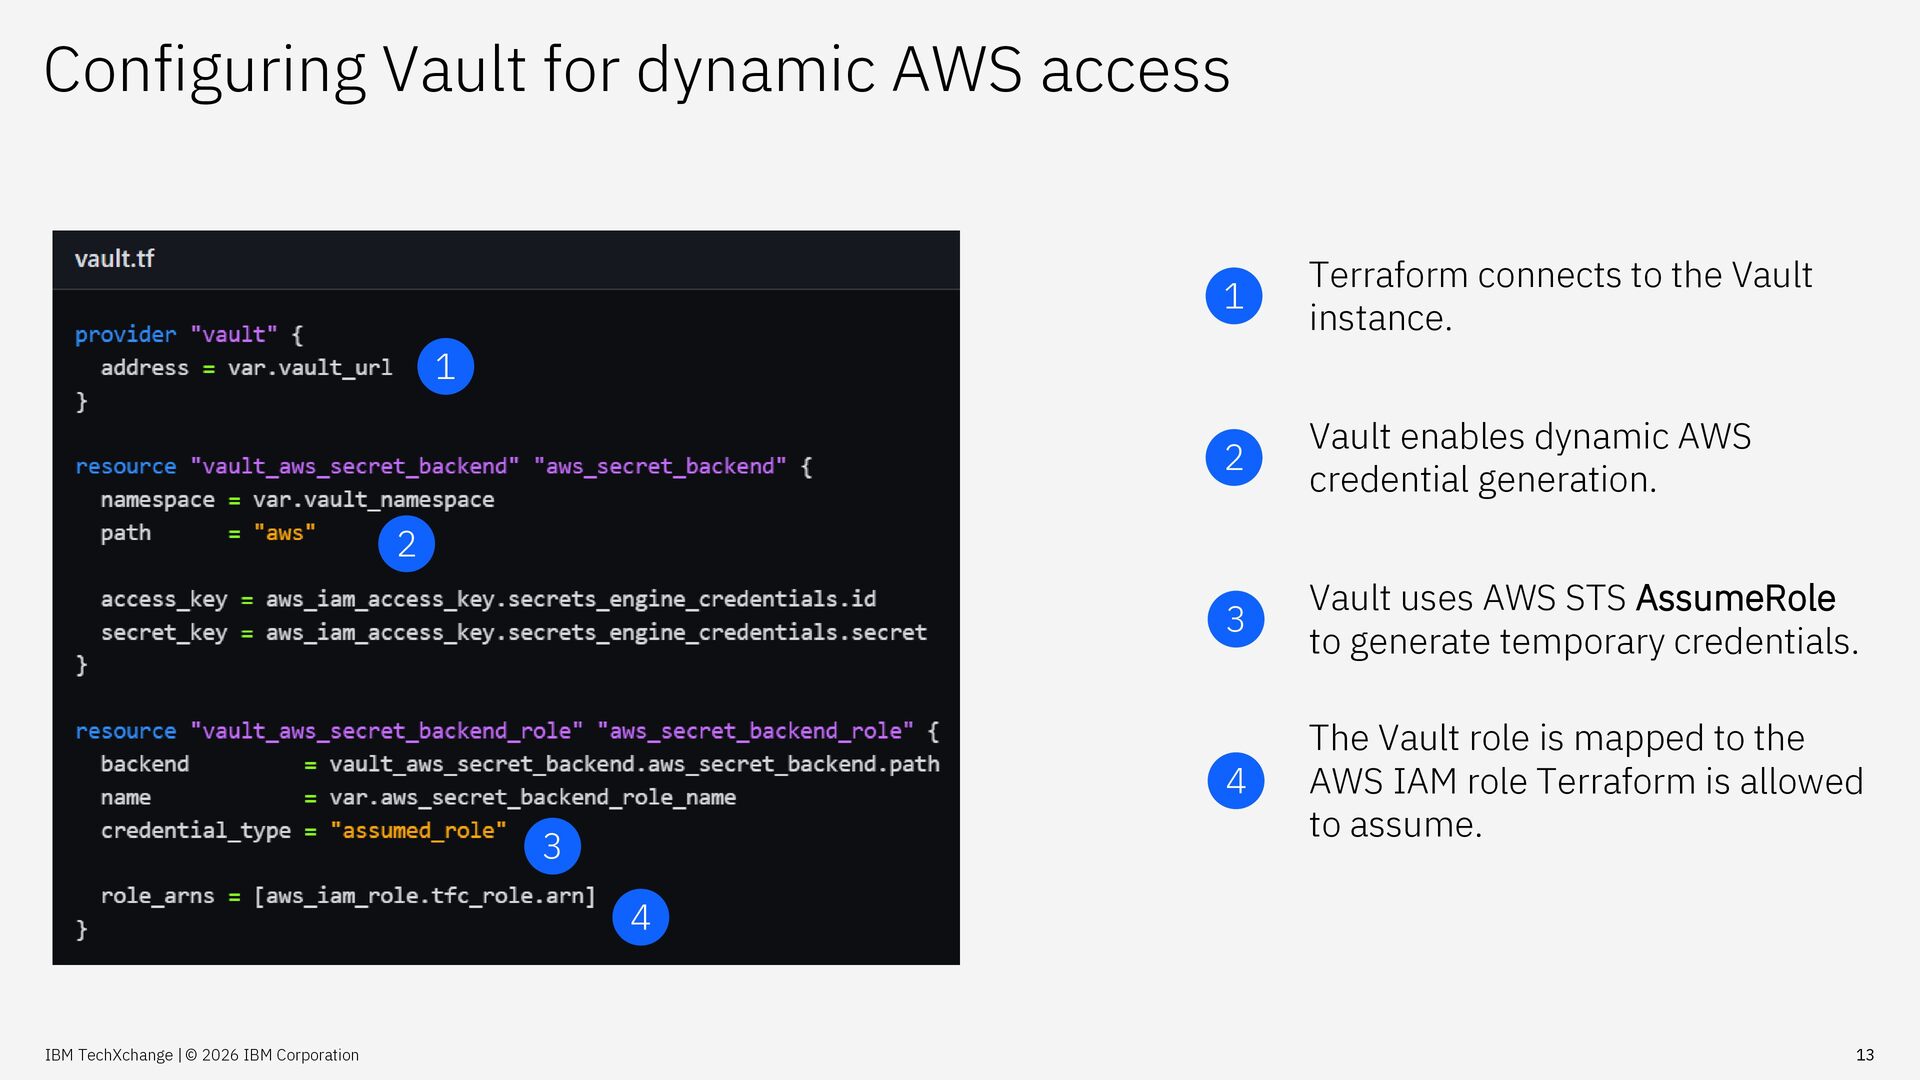
  12. Configuring Vault for dynamic AWS access 1 Terraform connects to

    the Vault instance. 2 Vault enables dynamic AWS credential generation. 3 Vault uses AWS STS AssumeRole to generate temporary credentials. 4 The Vault role is mapped to the AWS IAM role Terraform is allowed to assume. 1 2 3 4 IBM TechXchange | © 2026 IBM Corporation 13
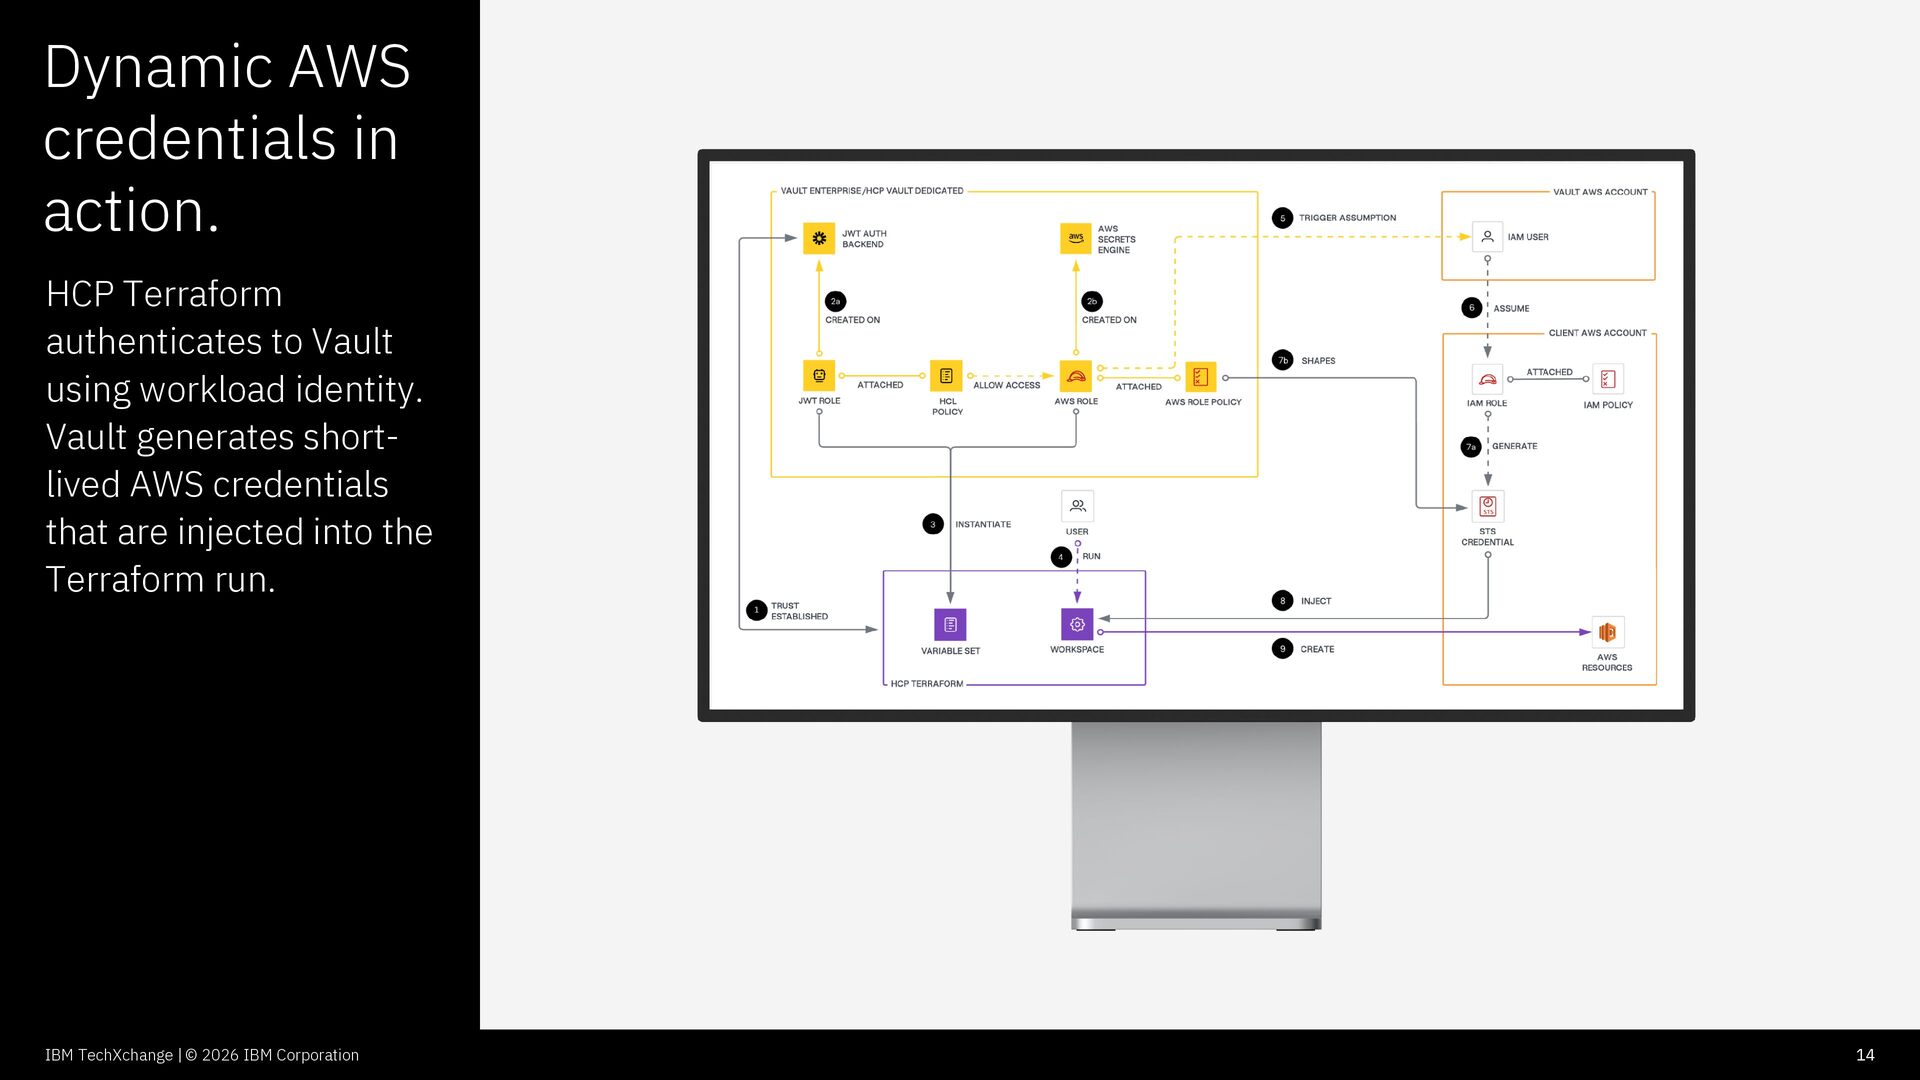
  13. Dynamic AWS credentials in action. HCP Terraform authenticates to Vault

    using workload identity. Vault generates shortlived AWS credentials that are injected into the Terraform run. IBM TechXchange | © 2026 IBM Corporation 14
  14. Building trust into AWS infrastructure AWS Credentials Terraform Automation Vault

    as the trust broker Short -lived access Long-lived access keys create persistent access and increase the impact of credential exposure. Terraform automates AWS infrastructure but still requires an authenticated identity to make changes. Vault authenticates workloads and controls AWS access through roles, policies and dynamic secrets. AWS credentials are generated on demand, scoped to the required permissions and expire automatically. IBM TechXchange | © 2026 IBM Corporation 15
  15. Terraform security is evolving Terraform Policy (tfpolicy) HCL-based Policy as

    Code integrated with HCP Terraform, with policy evaluation across the infrastructure lifecycle. Governance becomes part of the Terraform workflow. IBM TechXchange | © 2026 IBM Corporation Terraform MCP Server HashiCorp Agent Skills Connect AI assistants and agents to Terraform workflows using trusted infrastructure context and organizational guardrails. AI can interact with infrastructure, but inside controlled workflows. Reusable skills give AI agents Terraformspecific knowledge for code generation, testing, refactoring, providers and Stacks. From generic AI to infrastructure-aware agents. 17
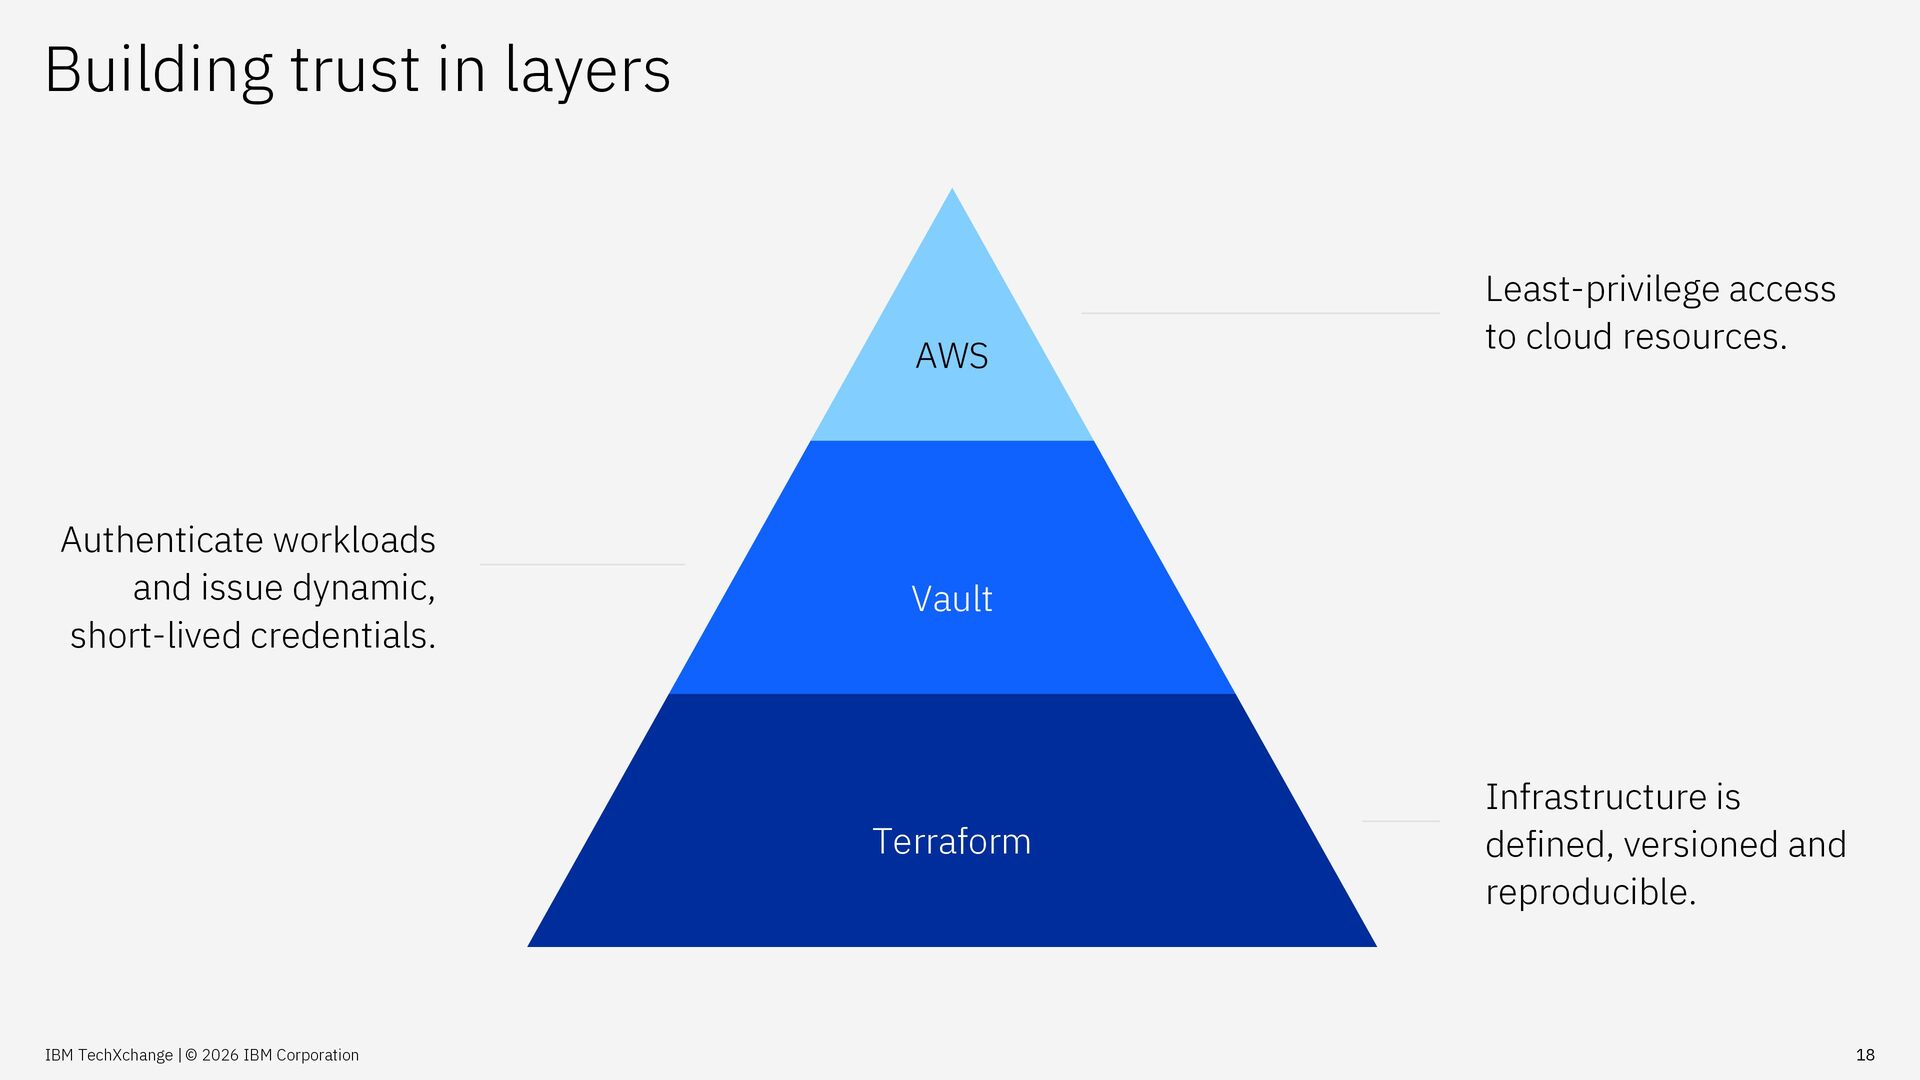
  16. Building trust in layers AWS Authenticate workloads and issue dynamic,

    short-lived credentials. Vault Terraform IBM TechXchange | © 2026 IBM Corporation Least-privilege access to cloud resources. Infrastructure is defined, versioned and reproducible. 18
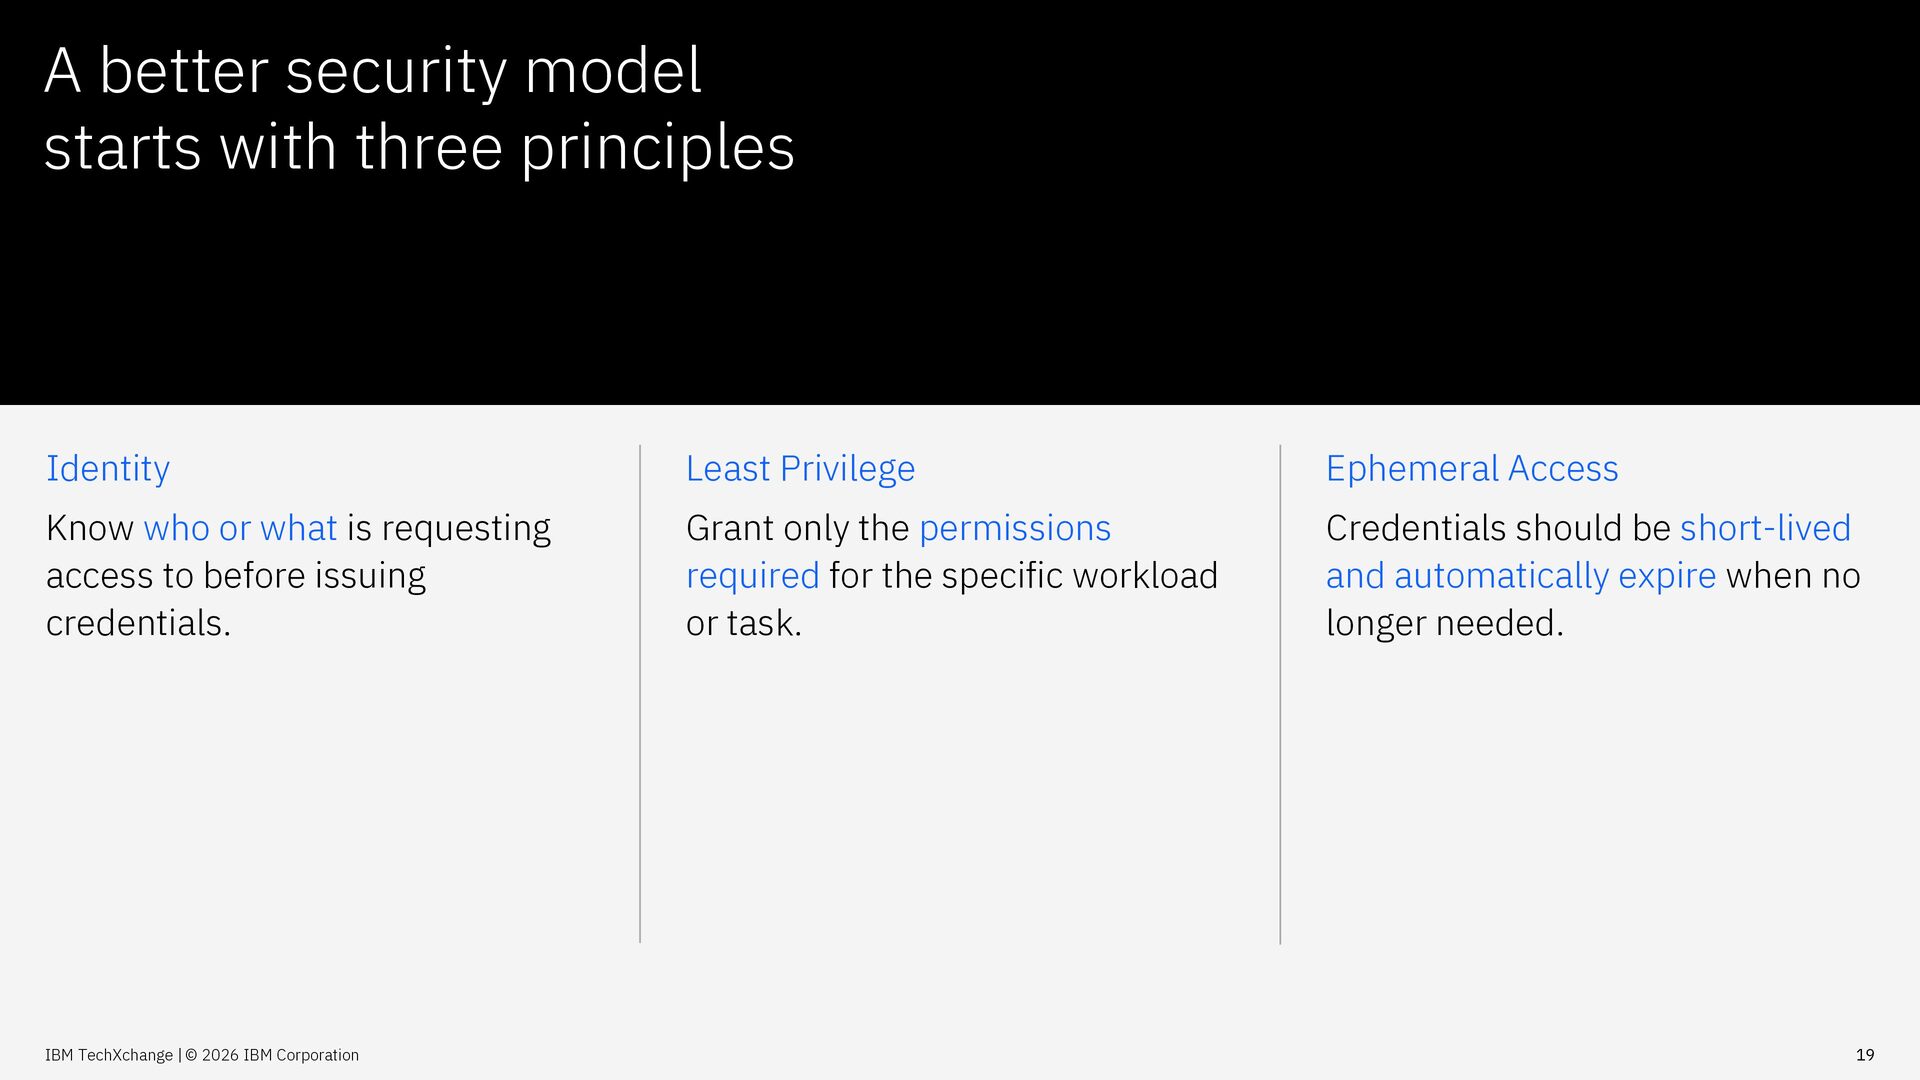
  17. A better security model starts with three principles Identity Least

    Privilege Ephemeral Access Know who or what is requesting access to before issuing credentials. Grant only the permissions required for the specific workload or task. Credentials should be short-lived and automatically expire when no longer needed. IBM TechXchange | © 2026 IBM Corporation 19
  18. “No secrets in code. Centralized control. Credentials delivered at runtime..”

    CI/CD Pipeline with Vault Amaury Borges Souza IBM TechXchange | © 2026 IBM Corporation 20
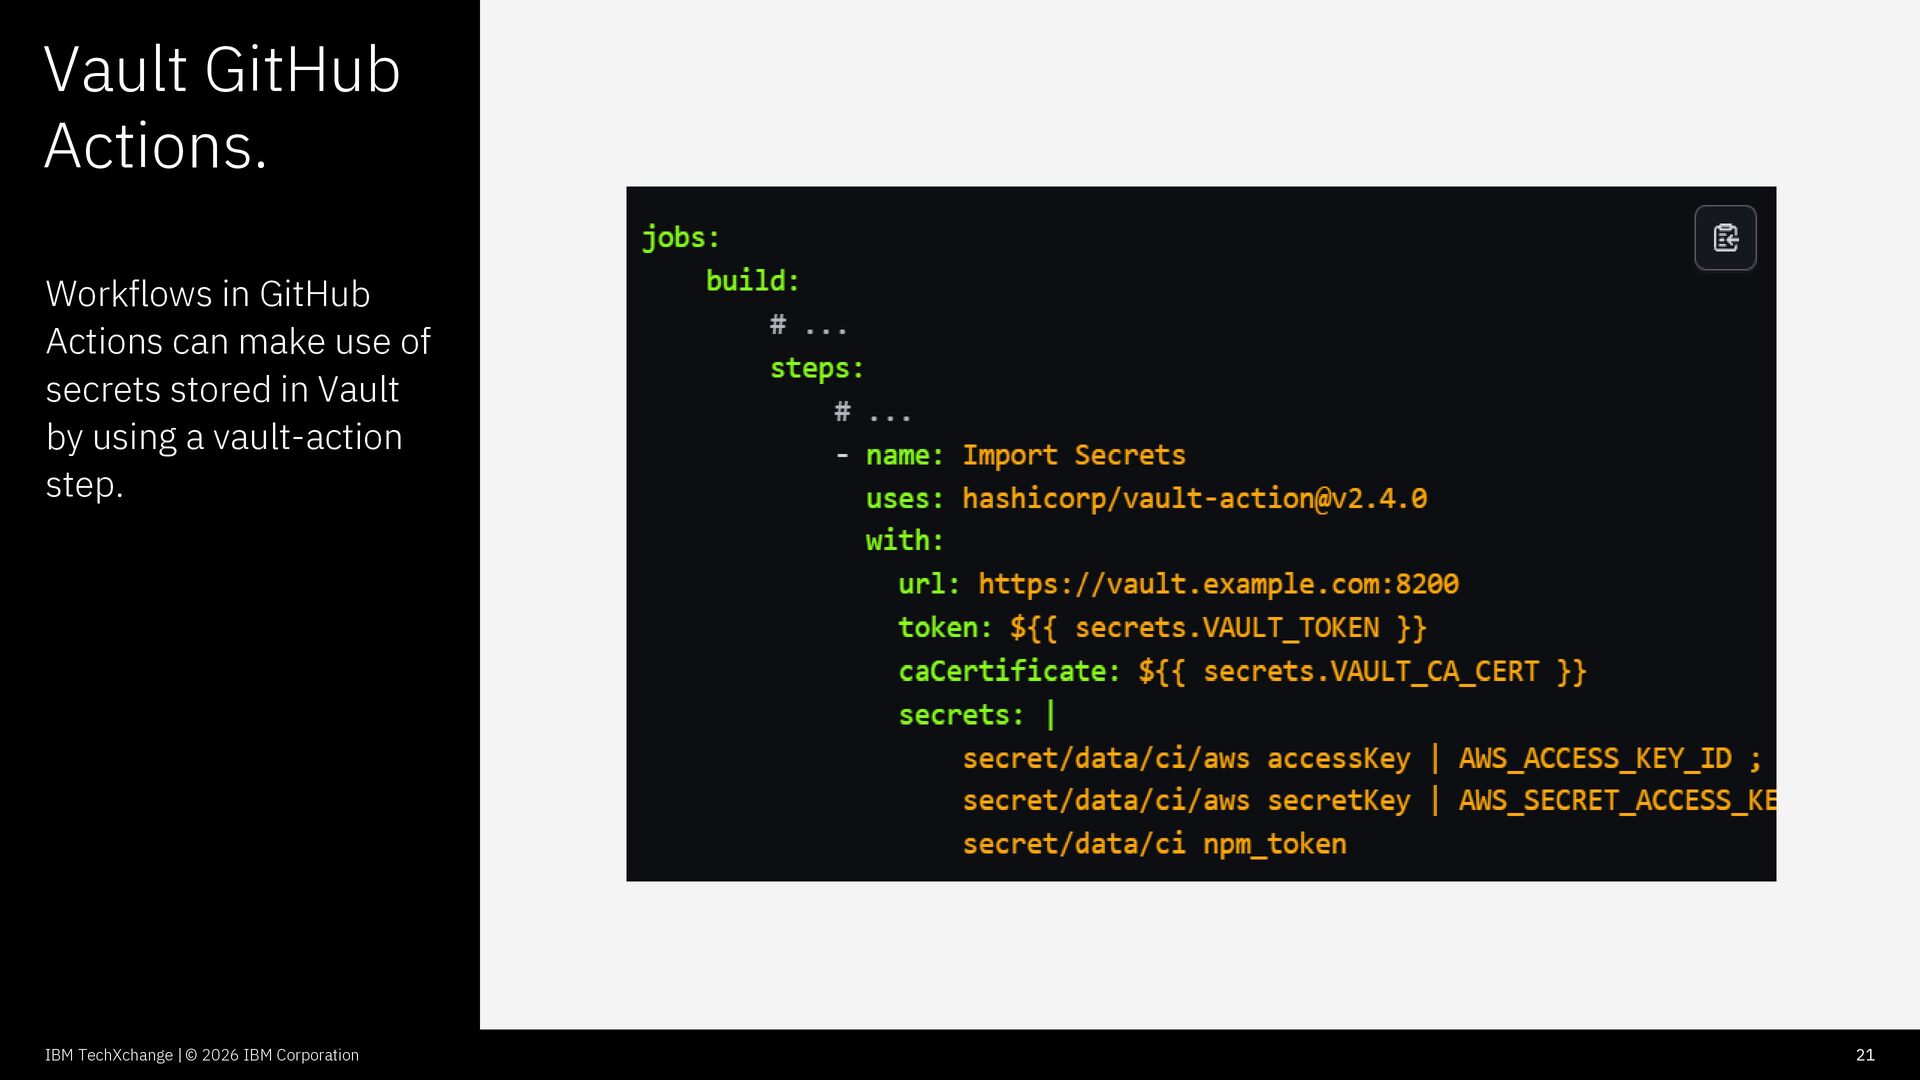
  19. Vault GitHub Actions. Workflows in GitHub Actions can make use

    of secrets stored in Vault by using a vault-action step. IBM TechXchange | © 2026 IBM Corporation 21
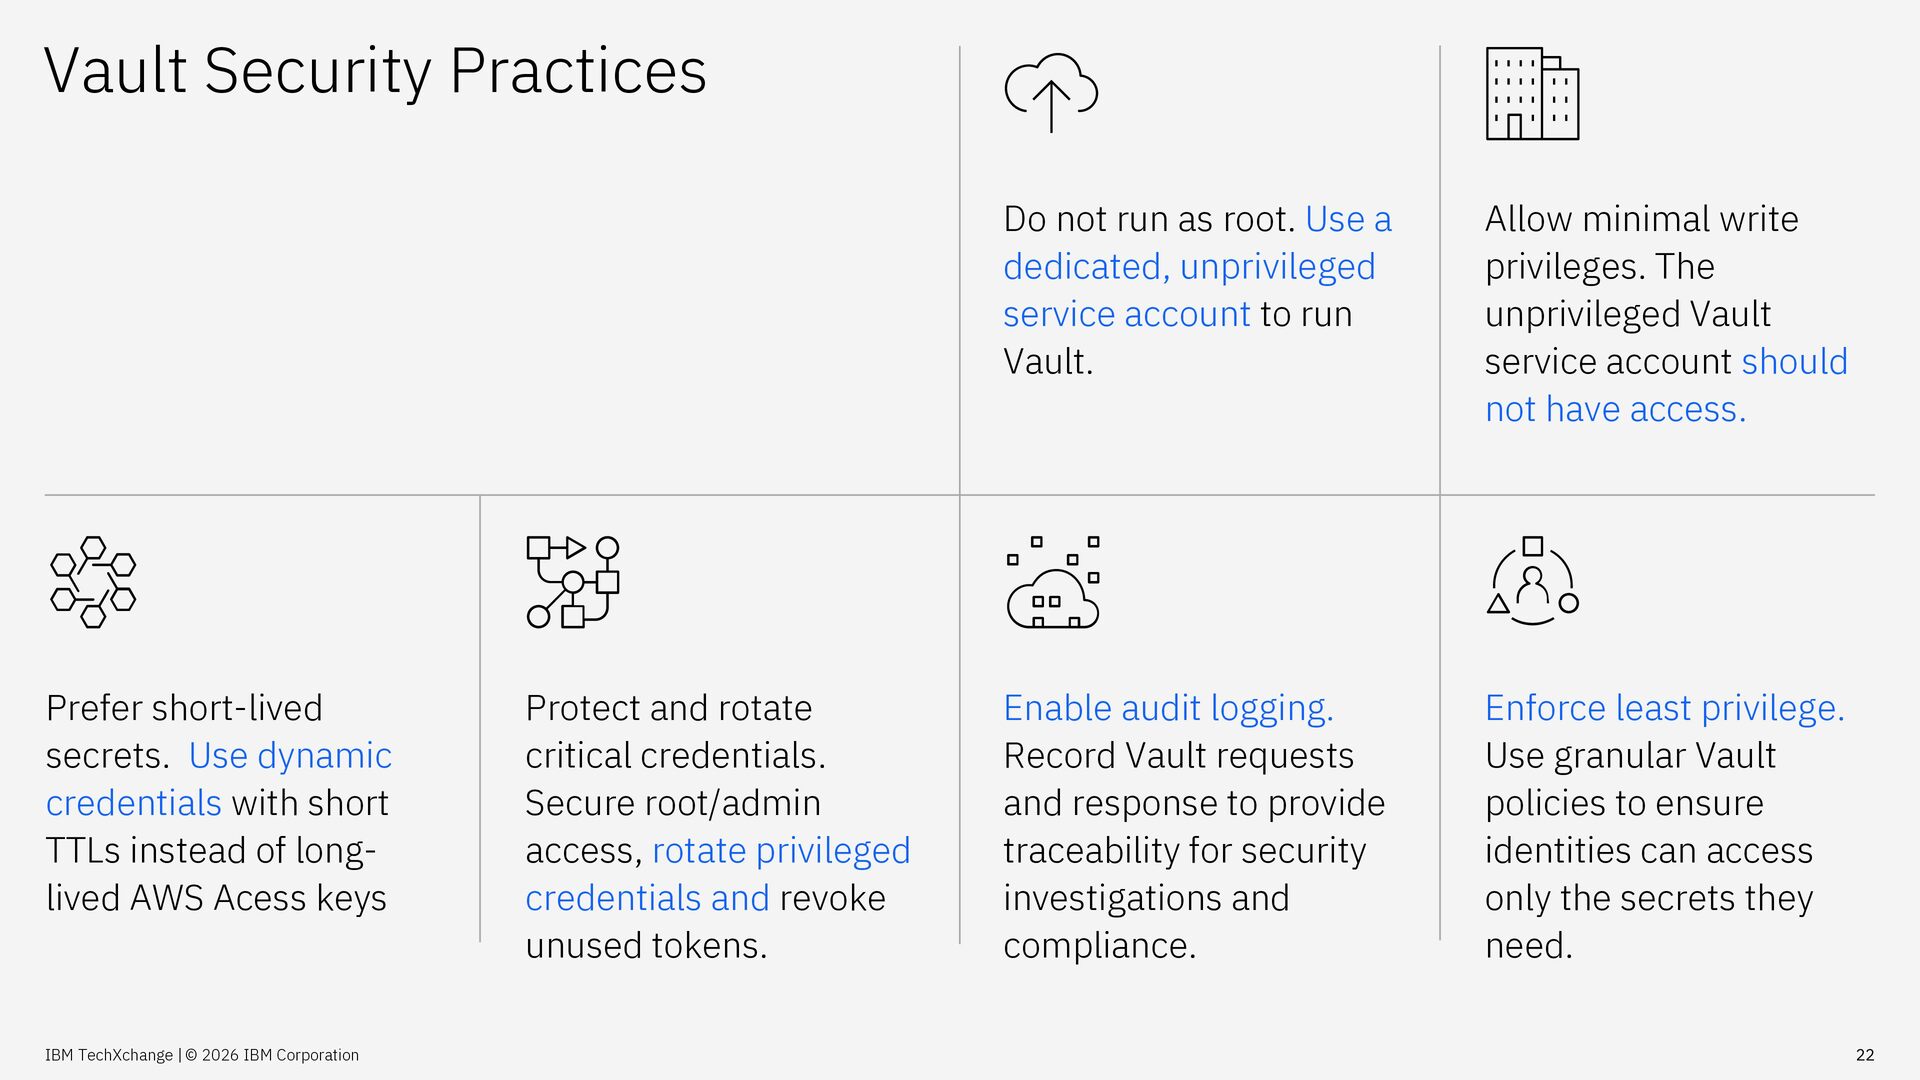
  20. Vault Security Practices Prefer short-lived secrets. Use dynamic credentials with

    short TTLs instead of longlived AWS Acess keys IBM TechXchange | © 2026 IBM Corporation Protect and rotate critical credentials. Secure root/admin access, rotate privileged credentials and revoke unused tokens. Do not run as root. Use a dedicated, unprivileged service account to run Vault. Allow minimal write privileges. The unprivileged Vault service account should not have access. Enable audit logging. Record Vault requests and response to provide traceability for security investigations and compliance. Enforce least privilege. Use granular Vault policies to ensure identities can access only the secrets they need. 22