Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Supply Chain Attack
Search
Andreas Mosti
May 03, 2021
91
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Supply Chain Attack
Talk I gave for Bekk Trondheim principles and practices group for security, spring 2021.
Andreas Mosti
May 03, 2021
More Decks by Andreas Mosti
See All by Andreas Mosti
Deterministic Builds and where to find them
andmos
0
94
Correct Maps Are Useless: A guide to mental models
andmos
0
220
LEGO I Praksis
andmos
0
110
Supply Chain Attacks: Når den digitale forsyningslinja blir angrepsvektor
andmos
0
55
IoIT: Internet of Insecure Things
andmos
0
150
Containers'n stuff
andmos
0
79
IoT - Bevisstgjøring
andmos
0
72
GitOps in a nutshell
andmos
0
240
OpenFaaS: Serverless platform with no strings attached?
andmos
0
350
Featured
See All Featured
How to train your dragon (web standard)
notwaldorf
96
6.9k
Designing Dashboards & Data Visualisations in Web Apps
destraynor
232
55k
The Art of Programming - Codeland 2020
erikaheidi
57
14k
Why Mistakes Are the Best Teachers: Turning Failure into a Pathway for Growth
auna
0
330
Impact Scores and Hybrid Strategies: The future of link building
tamaranovitovic
0
470
My Coaching Mixtape
mlcsv
0
370
BBQ
matthewcrist
90
10k
Breaking role norms: Why Content Design is so much more than writing copy - Taylor Woolridge
uxyall
1
470
Abbi's Birthday
coloredviolet
4
10k
Self-Hosted WebAssembly Runtime for Runtime-Neutral Checkpoint/Restore in Edge–Cloud Continuum
chikuwait
0
900
Lessons Learnt from Crawling 1000+ Websites
charlesmeaden
PRO
1
1.7k
From π to Pie charts
rasagy
1
420
Transcript
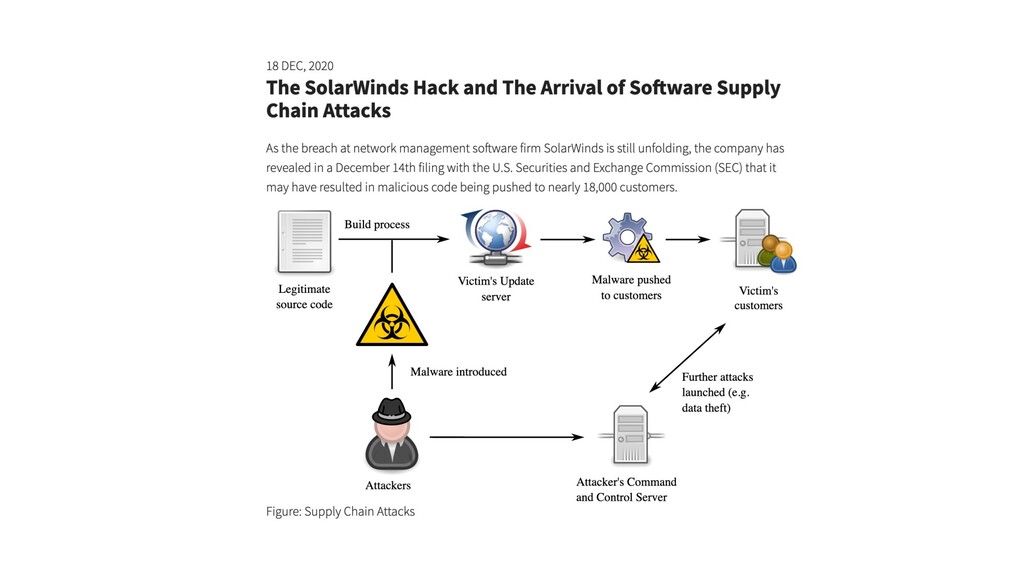
Supply Chain Attack
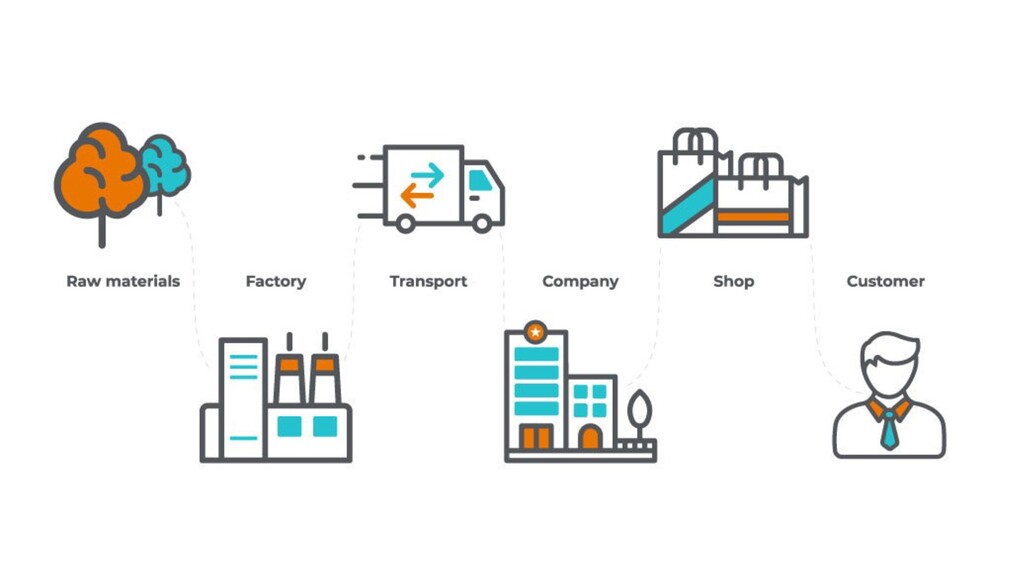
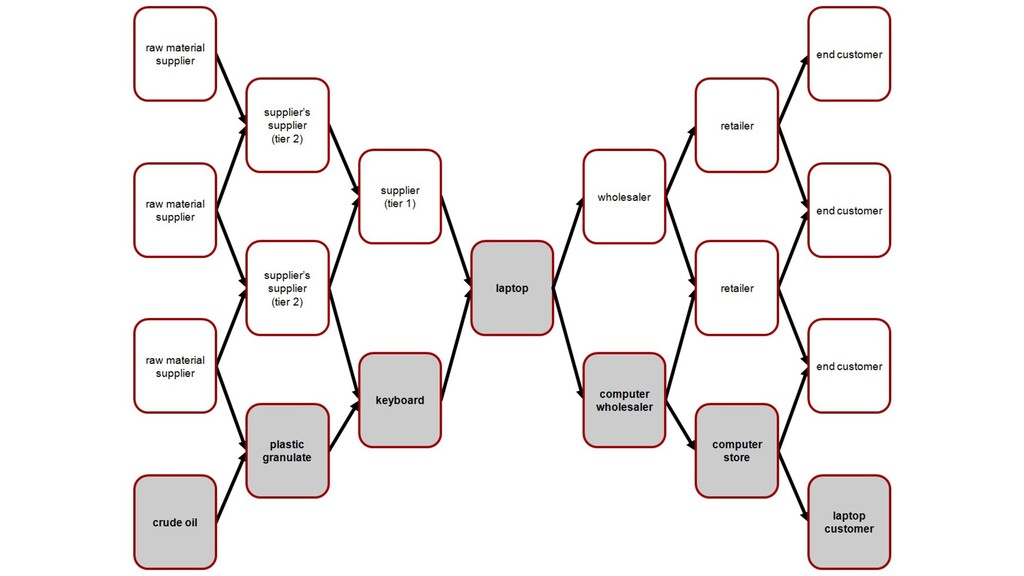
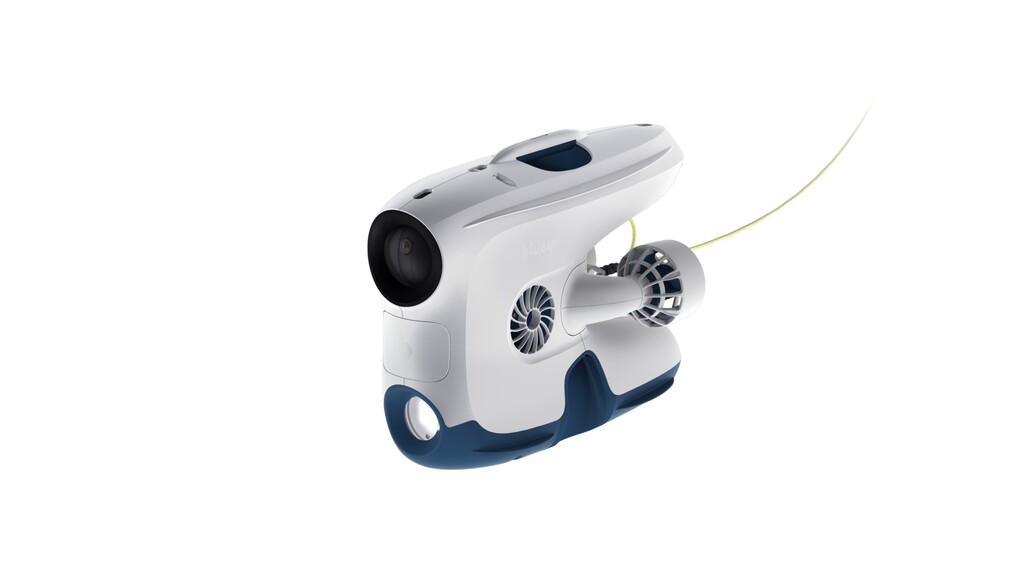
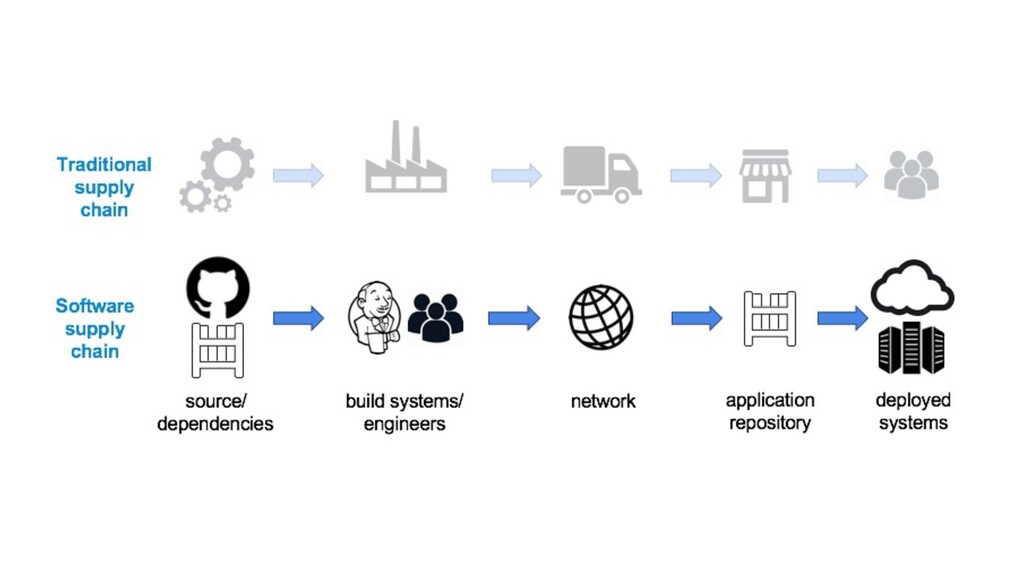
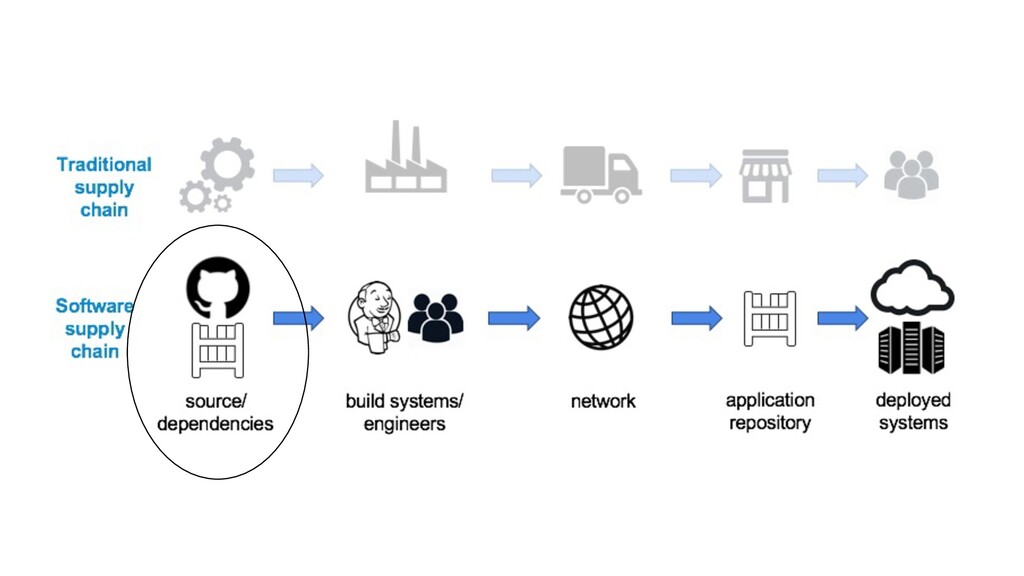
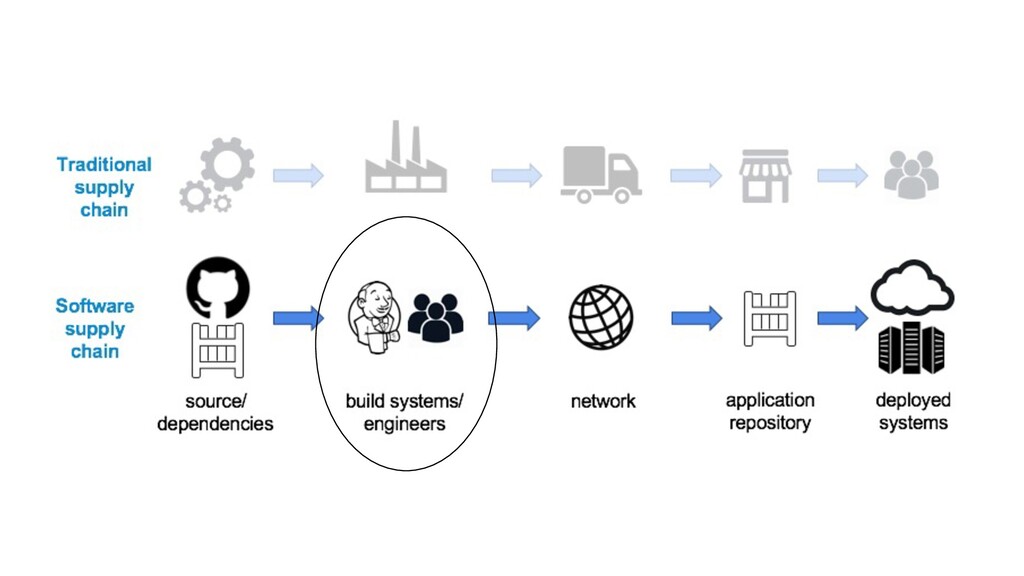
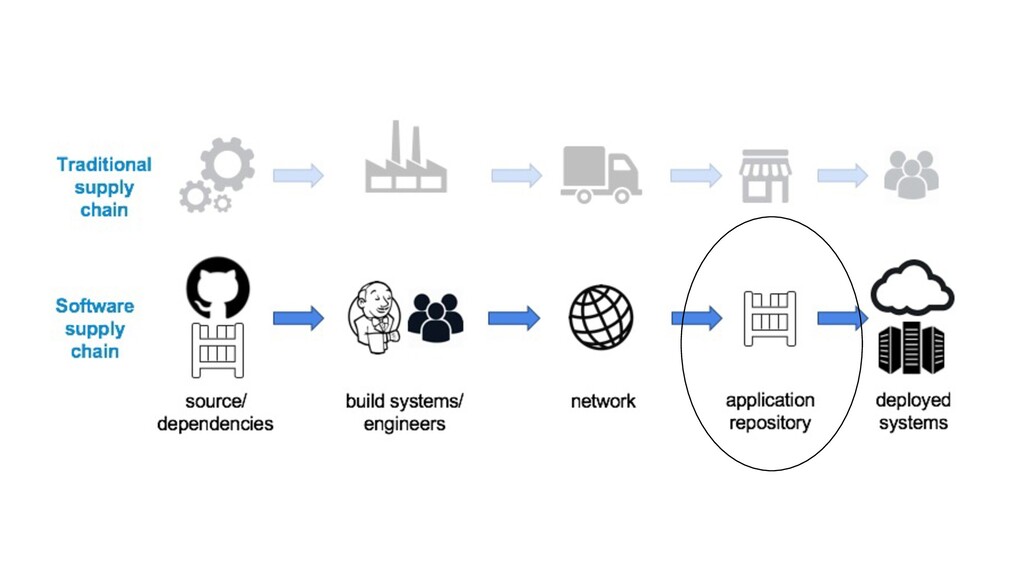
What’s a supply chain?
None
None
None
Ca. 1000 parts, most of them “passive”…
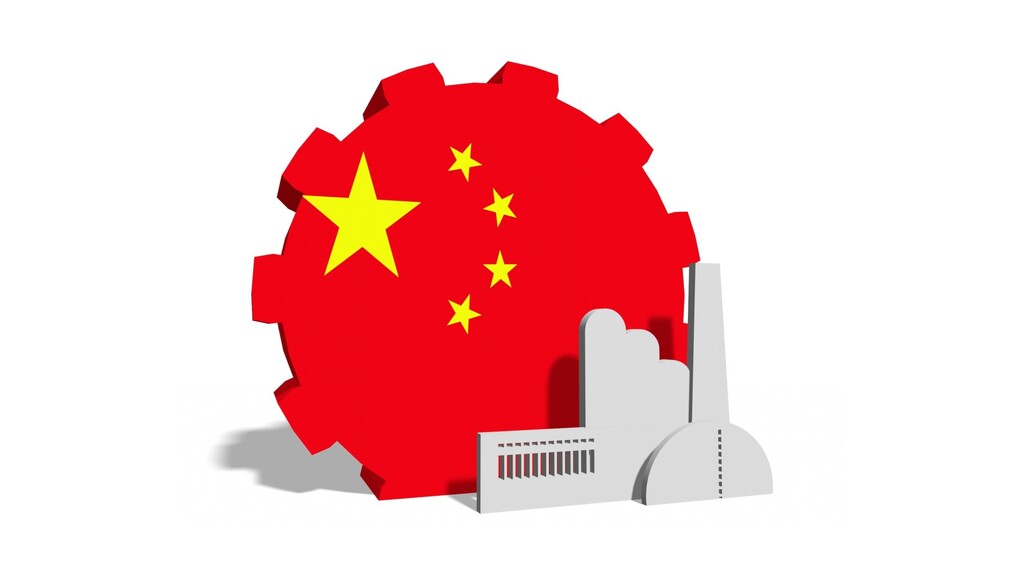
But 35 critical components, single-source dependencies
None
None
None
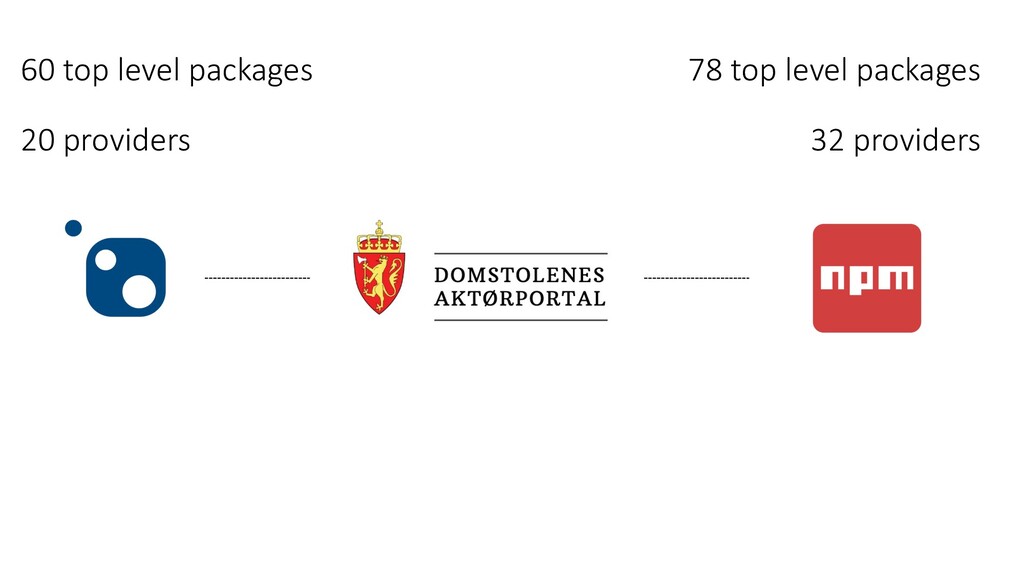
60 top level packages 20 providers 78 top level packages
32 providers
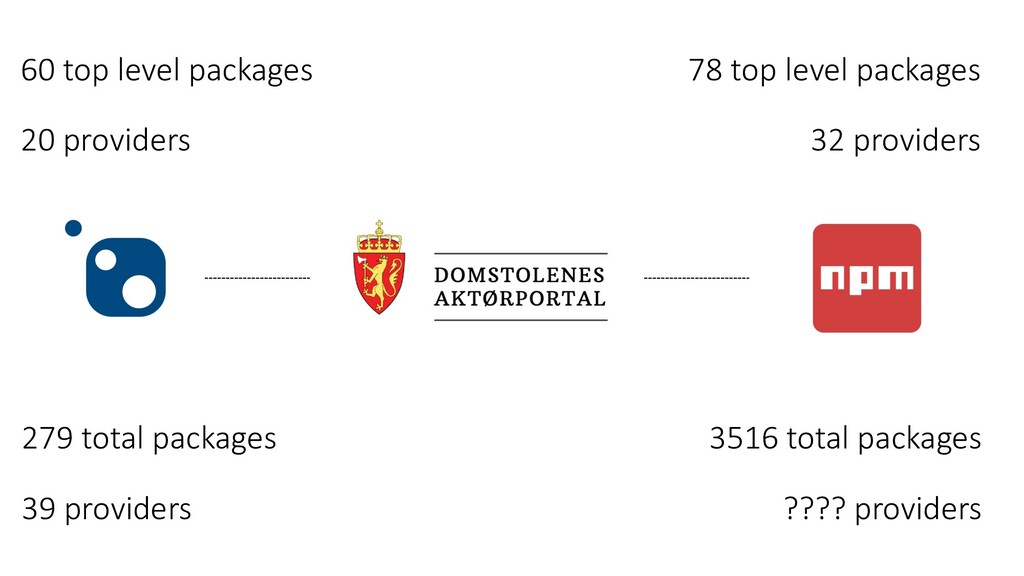
60 top level packages 20 providers 78 top level packages
32 providers 279 total packages 39 providers 3516 total packages ???? providers
None
None
None
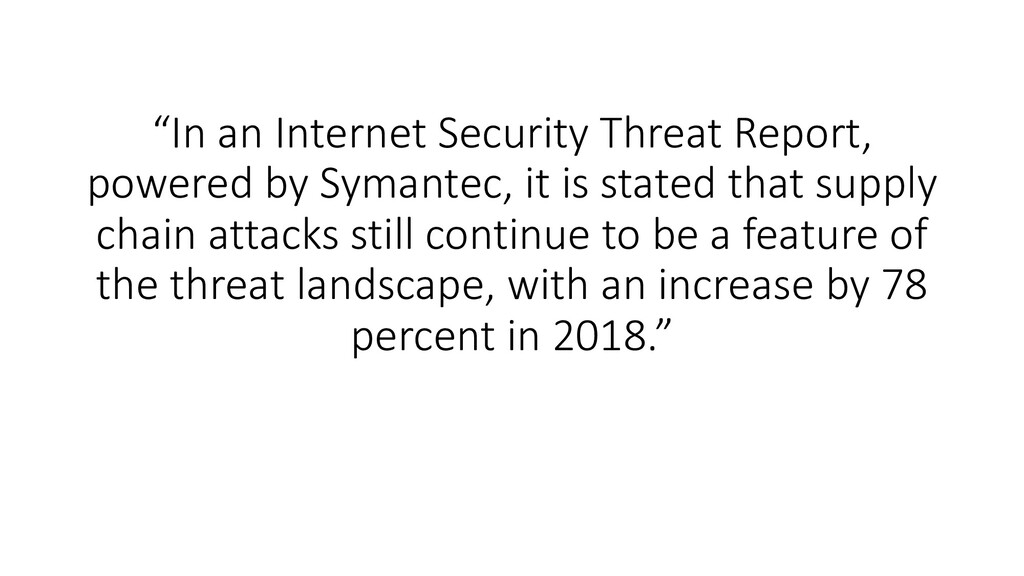
“In an Internet Security Threat Report, powered by Symantec, it
is stated that supply chain attacks still continue to be a feature of the threat landscape, with an increase by 78 percent in 2018.”
None
None
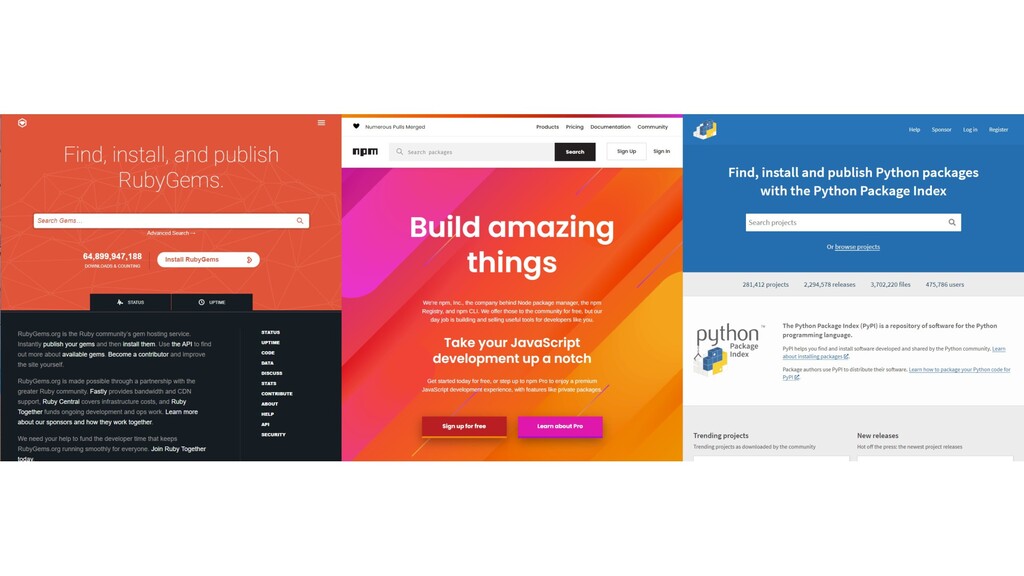
We go to the markedplace
None
“None of the package hosting services can ever guarantee that
all the code its users upload is malware-free”
None
Dependency Confusion
None
None
None
None
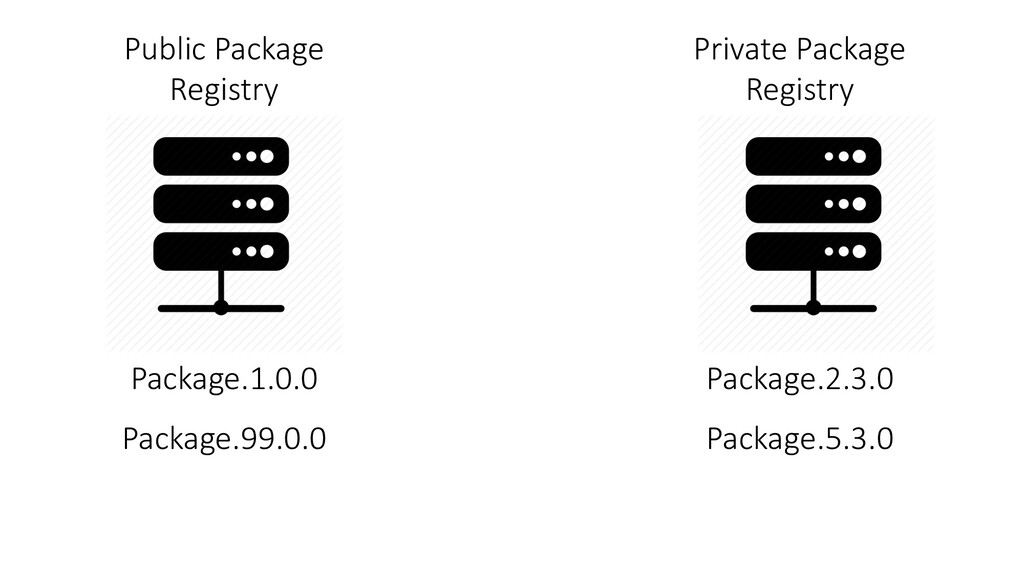
Public Package Registry Private Package Registry Package.1.0.0 Package.2.3.0 Package.99.0.0 Package.5.3.0
None
None
None
Service breaches
None
None
None
None
None
None
None
None
None
None
None
None
Worth mentioning: • Stolen signature key • Leaked API keys/passwords
• ????
How do we protect ourselves?


 andmos
 notwaldorf
 destraynor
 erikaheidi
 auna
 tamaranovitovic
 mlcsv
 matthewcrist
 uxyall
 coloredviolet
 chikuwait
 charlesmeaden
 rasagy