Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Introduction to Fuzzing with AFL
Search
Ayush Priya
November 16, 2021
Technology
78
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Introduction to Fuzzing with AFL
This talk is an introduction to using AFL or American Fuzzy Lop to fuzz binaries.
Ayush Priya
November 16, 2021
More Decks by Ayush Priya
See All by Ayush Priya
Scrubbing PII from Logs in LogStash
ayushpriya10
0
900
Introduction to Deserialization Attacks
ayushpriya10
2
710
Web Assembly for Hackers
ayushpriya10
0
110
Other Decks in Technology
See All in Technology
僕のハーネスを紹介します
watany
6
1.6k
AIで選択肢が広がった組織設計の理想と現実
konifar
12
4.8k
顧客価値を追いかけたら、プライシングにたどり着いた
sansantech
PRO
2
1k
なぜAI時代に技術記事を書くのか?どう書くのか? 〜bunの場合〜
kworkdev
PRO
0
120
背中から、背中へ ー 社外コミュニティで学んだ「雑に背中を押す」という恩送り ー / easygoing encouragement and pay forward to community
naitosatoshi
0
320
書き手が人でもAIでも正しくなる道、 SREを埋め込んだDeveloper Platform / tech drivers day8
chmikata
4
750
AIコーディングを実践してきた1年を振り返る / Looking Back on a Year of Practicing AI Coding
takedatakashi
1
130
ガチで放置できるClaude Code実行環境の作り方.pdf
lamaglama39
5
9.7k
Filter What the LLM Reads: RAG Governance with AgentCore Gateway
yakumo
0
110
freeeにおける AI を用いた ブラウザ動作確認の自動化の取り組み
freee
PRO
0
220
DevelopersIO 2026 Tokyo 現時点の衛星通信サービスの現状を整理してみる
maroon1st
0
310
AIをリアル世界に解き放つ 〜M5Stack×AIであなたのアイディアを手の平に〜
hamadakoji
1
530
Featured
See All Featured
Leveraging LLMs for student feedback in introductory data science courses - posit::conf(2025)
minecr
1
450
Hiding What from Whom? A Critical Review of the History of Programming languages for Music
tomoyanonymous
3
1.4k
Art, The Web, and Tiny UX
lynnandtonic
304
22k
Fireside Chat
paigeccino
43
4.1k
From Legacy to Launchpad: Building Startup-Ready Communities
dugsong
0
360
Ruling the World: When Life Gets Gamed
codingconduct
0
420
The Mindset for Success: Future Career Progression
greggifford
PRO
0
550
Reflections from 52 weeks, 52 projects
jeffersonlam
356
22k
Money Talks: Using Revenue to Get Sh*t Done
nikkihalliwell
0
540
SEO in 2025: How to Prepare for the Future of Search
ipullrank
3
3.9k
What's in a price? How to price your products and services
michaelherold
247
13k
Exploring anti-patterns in Rails
aemeredith
4
540
Transcript
Introduction to fuzzing with AFL
Ayush Priya VIT, Vellore @ayushpriya10 https://ayushpriya.com https://www.linkedin.com/in/ayushpriya10
What am I learning? • What is fuzzing and fuzzers?
• What is AFL? • How to use AFL?
Why am I learning this? • Discover undiscovered bugs •
Build a robust approach to development • (Maybe make some money)
What is Fuzzing? • A form of testing • Random
invalid input • Behaviour analysis
"You can find bugs in your sleep." - Craig Young
Why fuzz at all? • Unique test cases • Eliminates
methodology bias • Metrics - Code Coverage, Path Coverage
Types of fuzzers • Mutational • Grammar • Feedback-based
Introduction to AFL • Open-source • Smart fuzzer: PoC -
“Hello JPG”
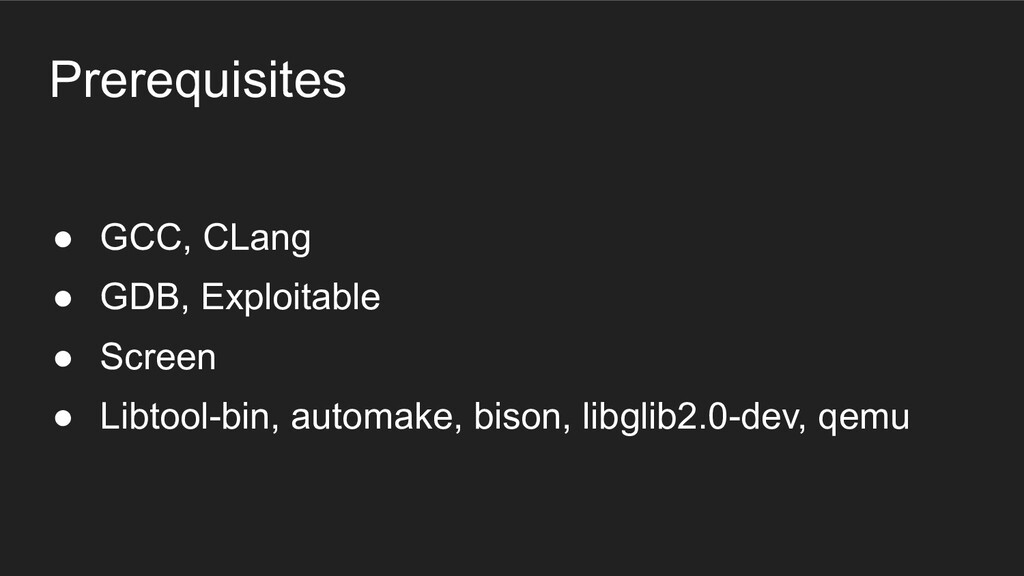
Prerequisites • GCC, CLang • GDB, Exploitable • Screen •
Libtool-bin, automake, bison, libglib2.0-dev, qemu
Installation • Install AFL • Enable LLVM mode • Enable
QEMU mode
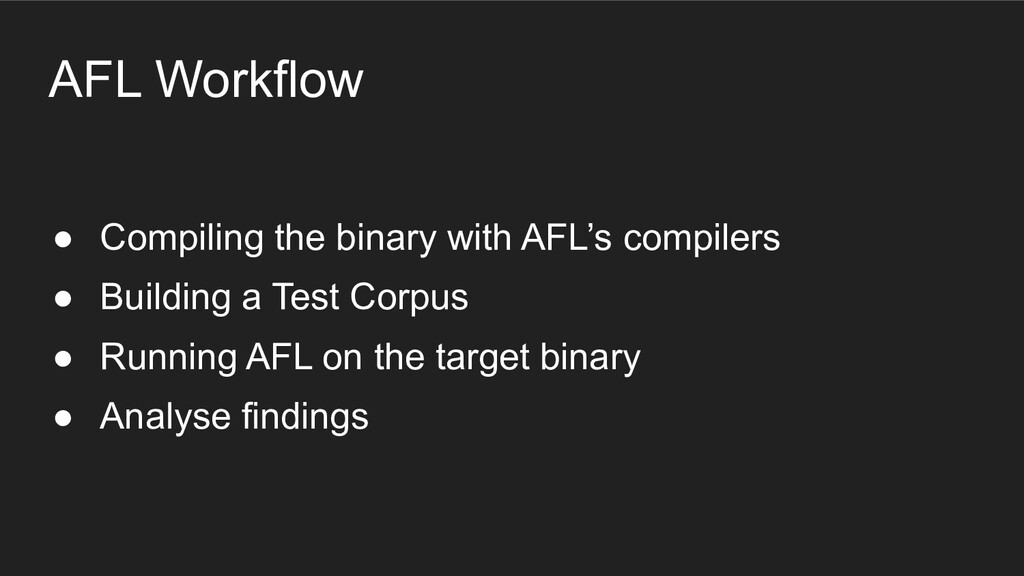
AFL Workflow • Compiling the binary with AFL’s compilers •
Building a Test Corpus • Running AFL on the target binary • Analyse findings
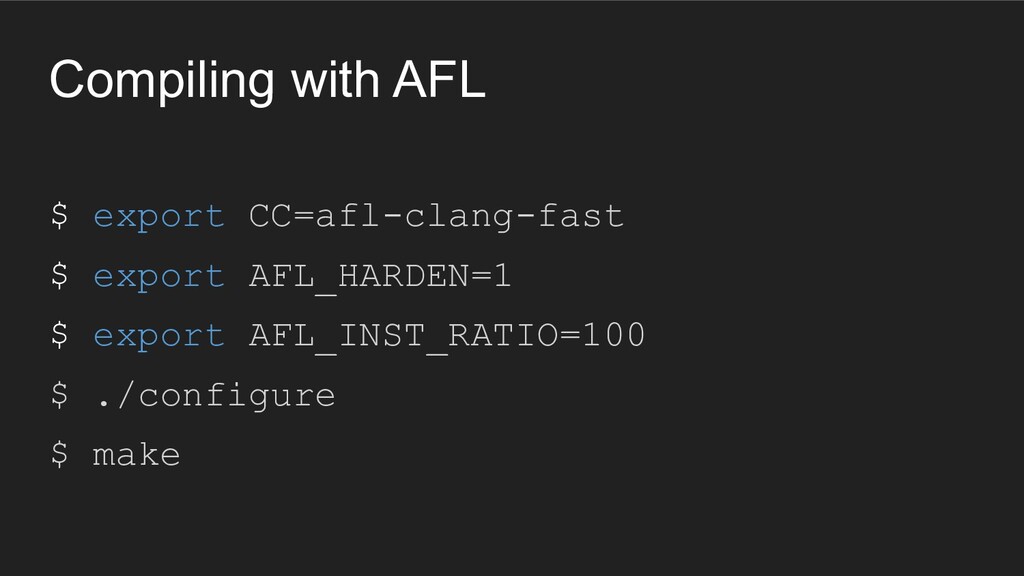
Compiling with AFL $ export CC=afl-clang-fast $ export AFL_HARDEN=1 $
export AFL_INST_RATIO=100 $ ./configure $ make
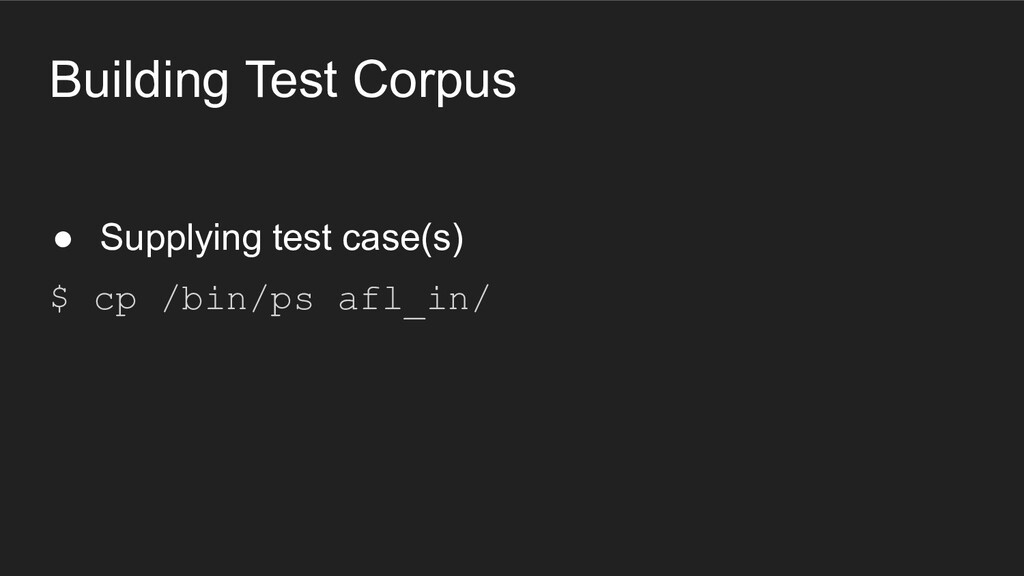
Building Test Corpus • Supplying test case(s) $ cp /bin/ps
afl_in/
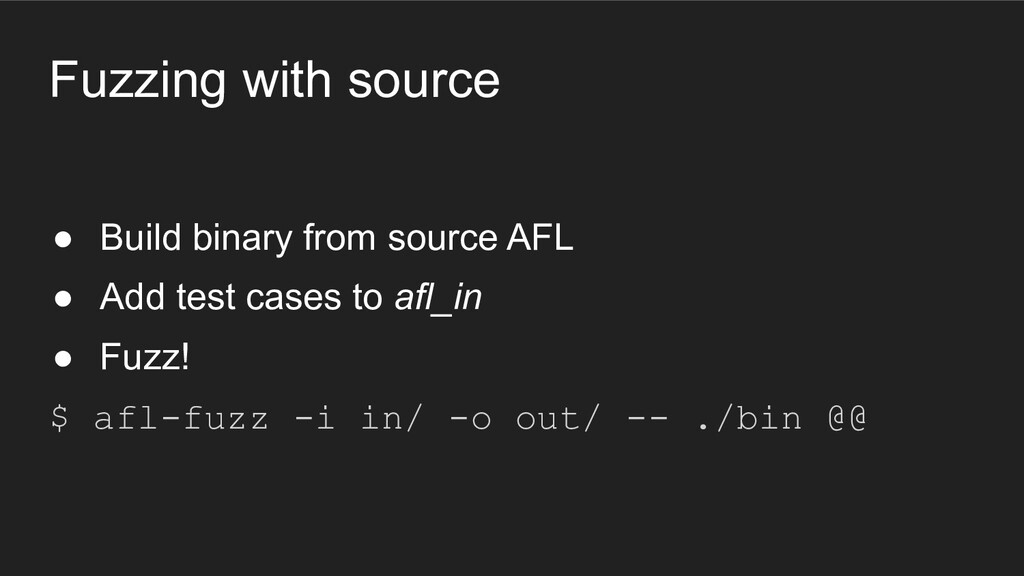
Fuzzing with source • Build binary from source AFL •
Add test cases to afl_in • Fuzz! $ afl-fuzz -i in/ -o out/ -- ./bin @@
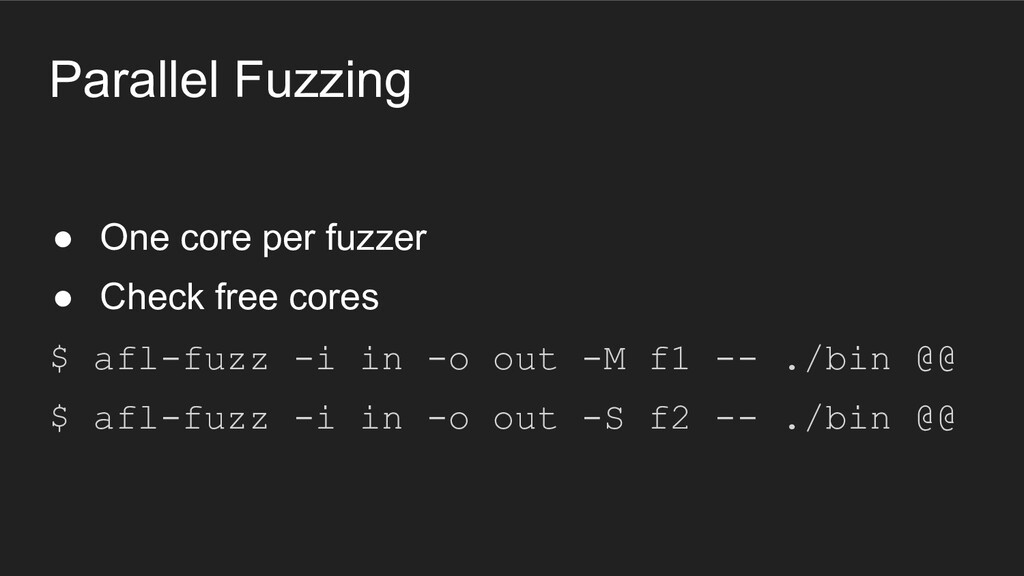
Parallel Fuzzing • One core per fuzzer • Check free
cores $ afl-fuzz -i in -o out -M f1 -- ./bin @@ $ afl-fuzz -i in -o out -S f2 -- ./bin @@
Output Structure • One folder per fuzzer • /crashes, /hangs,
/queue
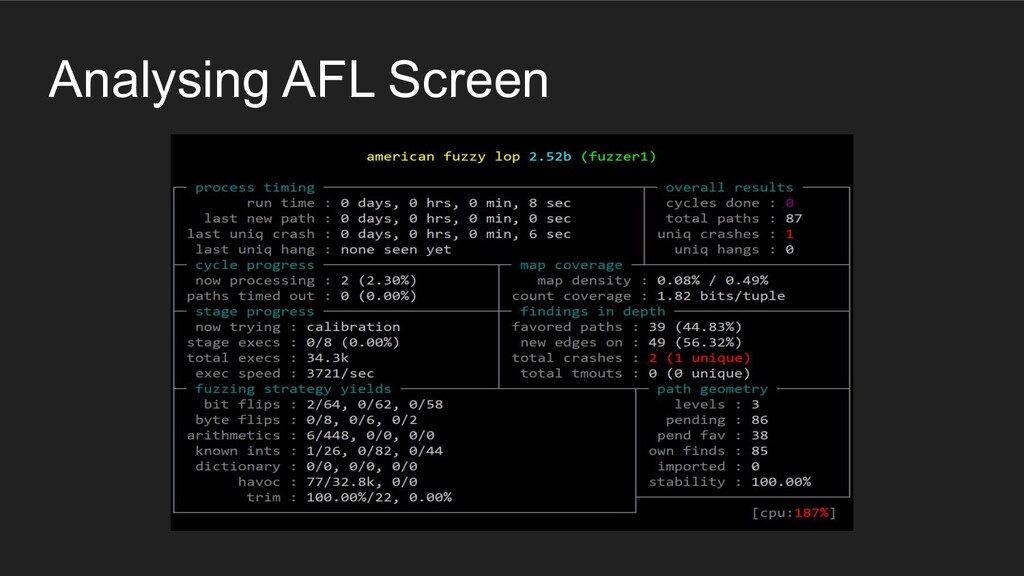
Analysing AFL Screen
Hands-on • Clone fuzzgoat • Compile with AFL • Fuzz
in parallel • Check status
GDB and Exploitable • Open binary with GDB • Choose
a crash case • Run test case • Classify with Exploitable
Optimising Fuzzing • Execution Speed, Fail Fast • Isolate test
code • Minimise test cases • Minimise test files
Fuzzing a binary without source • Linux binaries • AFL’s
QEMU Mode
Limitations of AFL • Supports file/STDIN input • Supports selective
binaries • Supports selective OSs
Thanks!


 ayushpriya10
 watany
 konifar
 sansantech
 kworkdev
 naitosatoshi
 chmikata
 takedatakashi
 lamaglama39
 yakumo
 freee
 maroon1st
 hamadakoji
 minecr
 tomoyanonymous
 lynnandtonic
 paigeccino
 dugsong
 codingconduct
 greggifford
 jeffersonlam
 nikkihalliwell
 ipullrank
 michaelherold
 aemeredith