Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
The first few milliseconds of HTTPS - nluug
Search
Joshua Thijssen
November 20, 2014
210
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
The first few milliseconds of HTTPS - nluug
Joshua Thijssen
November 20, 2014
More Decks by Joshua Thijssen
See All by Joshua Thijssen
RAFT: A story on how clusters of computers keep your data in sync
jaytaph
0
87
The first few milliseconds of HTTPS
jaytaph
0
330
Paradoxes and theorems every developer should know
jaytaph
0
380
Paradoxes and theorems every developer should know
jaytaph
0
810
The first few milliseconds of HTTPS - PHPNW16
jaytaph
1
310
compiler_-_php010.pdf
jaytaph
0
180
Paradoxes and theorems every developer should know
jaytaph
0
320
Introduction into interpreters, compilers and JIT
jaytaph
1
400
Paradoxes and theorems every developer should know
jaytaph
1
1k
Featured
See All Featured
Visual Storytelling: How to be a Superhuman Communicator
reverentgeek
2
720
jQuery: Nuts, Bolts and Bling
dougneiner
66
8.6k
Measuring Dark Social's Impact On Conversion and Attribution
stephenakadiri
2
310
Done Done
chrislema
187
17k
Crafting Experiences
bethany
1
390
Building an army of robots
kneath
307
47k
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
70
67k
CSS Pre-Processors: Stylus, Less & Sass
bermonpainter
360
31k
Pawsitive SEO: Lessons from My Dog (and Many Mistakes) on Thriving as a Consultant in the Age of AI
davidcarrasco
0
280
The Curious Case for Waylosing
cassininazir
1
580
Building Better People: How to give real-time feedback that sticks.
wjessup
371
20k
Intergalactic Javascript Robots from Outer Space
tanoku
273
28k
Transcript
The first 200 milliseconds of HTTPS 1 Joshua Thijssen jaytaph
2
➡ What’s happening in the first 200+ milliseconds in a
initial HTTPS connection. 2
➡ What’s happening in the first 200+ milliseconds in a
initial HTTPS connection. ➡ Give tips and hints on hardening your setup. 2
➡ What’s happening in the first 200+ milliseconds in a
initial HTTPS connection. ➡ Give tips and hints on hardening your setup. ➡ Give you insights in new and upcoming technologies. 2
➡ What’s happening in the first 200+ milliseconds in a
initial HTTPS connection. ➡ Give tips and hints on hardening your setup. ➡ Give you insights in new and upcoming technologies. ➡ Show you things to you (probably) didn’t knew. 2
This talk is inspired by a blogpost from Jeff Moser
http://www.moserware.com/2009/06/first-few-milliseconds-of-https.html Unknown fact! 3
HTTPS == HTTP on top of TLS 4
Transport Layer Security (TLS) 5
Secure Socket Layer (SSL) 6 A short and scary history
then now 7
then now SSL 1.0 Vaporware 1994 7
then now feb 1995 SSL 2.0 Not-so-secure-socket-layer SSL 1.0 Vaporware
1994 7
then now feb 1995 SSL 2.0 Not-so-secure-socket-layer jun 1996 SSL
3.0 Something stable! SSL 1.0 Vaporware 1994 7
then now feb 1995 SSL 2.0 Not-so-secure-socket-layer jun 1996 SSL
3.0 Something stable! jan 1999 TLS 1.0 SSL 3.1 SSL 1.0 Vaporware 1994 7
then now feb 1995 SSL 2.0 Not-so-secure-socket-layer jun 1996 SSL
3.0 Something stable! jan 1999 TLS 1.0 SSL 3.1 apr 2006 TLS 1.1 SSL 1.0 Vaporware 1994 7
then now feb 1995 SSL 2.0 Not-so-secure-socket-layer jun 1996 SSL
3.0 Something stable! jan 1999 TLS 1.0 SSL 3.1 apr 2006 TLS 1.1 TLS 1.2 aug 2008 SSL 1.0 Vaporware 1994 7
https://www.trustworthyinternet.org/ssl-pulse/ 25,7% 99,6% 99,3% 18,2% 20,7% SSL 2.0 SSL 3.0
TLS 1.0 TLS 1.1 TLS 1.2 8 November 2013
https://www.trustworthyinternet.org/ssl-pulse/ 25,7% 99,6% 99,3% 18,2% 20,7% SSL 2.0 SSL 3.0
TLS 1.0 TLS 1.1 TLS 1.2 8 19,4% 98,0% 99,3% 42,0% 44,3% SSL 2.0 SSL 3.0 TLS 1.0 TLS 1.1 TLS 1.2 November 2013 Oct 2014
https://www.trustworthyinternet.org/ssl-pulse/ 25,7% 99,6% 99,3% 18,2% 20,7% SSL 2.0 SSL 3.0
TLS 1.0 TLS 1.1 TLS 1.2 8 19,4% 98,0% 99,3% 42,0% 44,3% SSL 2.0 SSL 3.0 TLS 1.0 TLS 1.1 TLS 1.2 November 2013 Oct 2014 16,6% 60,6% 99,5% 45,4% 48,1% SSL 2.0 SSL 3.0 TLS 1.0 TLS 1.1 TLS 1.2 Nov 2014
RFC 5246 (TLS v1.2) 9
10 Record Layer
10 Record Layer Type Version Length
10 Record Layer Type Version Length Protocol
10 Record Layer Type Version Length Protocol Protocol Protocol
10 Record Layer Type Version Length Protocol Protocol Protocol Record
Layer Type Version Length Protocol
➡ Handshake protocol records ➡ Setup communication ➡ Change Cipher
Spec protocol records ➡ Change communication ➡ Alert protocol records ➡ Errors ➡ Application Data protocol records ➡ Actual data transfers 11
12 https://github.com/vincentbernat/rfc5077/blob/master/ssl-handshake.svg
Attention: (live) wiresharking up ahead 13
14
TLS_ECDHE_ECDSA_WITH_AES_128_GCM_SHA256 15
TLS ECDHE_ECDSA WITH AES_128_GCM SHA256 16
TLS ECDHE_ECDSA WITH AES_128_GCM SHA256 Cipher for exchanging key information
16
TLS ECDHE_ECDSA WITH AES_128_GCM SHA256 Cipher for exchanging key information
Cipher for authenticating key information 16
TLS ECDHE_ECDSA WITH AES_128_GCM SHA256 Cipher for exchanging key information
Cipher for authenticating key information Actual cipher (and length) used for communication 16
TLS ECDHE_ECDSA WITH AES_128_GCM SHA256 Cipher for exchanging key information
Cipher for authenticating key information Hash algo for message authenticating Actual cipher (and length) used for communication 16
TLS_RSA_WITH_AES_256_CBC_SHA256 17
TLS_NULL_WITH_NULL_NULL 18
Client gives cipher options, Server ultimately decides on cipher! 19
THIS IS WHY YOU SHOULD ALWAYS CONFIGURE YOUR CIPHERS ON
YOUR WEB SERVER! 20 Unknown fact!
21 https://cipherli.st SSLCipherSuite AES256+EECDH:AES256+EDH SSLProtocol All -SSLv2 -SSLv3 SSLCompression off
# Requires Apache >= 2.4 SSLHonorCipherOrder On SSLUseStapling on # Requires Apache >= 2.4 SSLStaplingCache "shmcb:logs/stapling-cache(150000)" # Requires >= Apache 2.4 Header always set Strict-Transport-Security "max-age=63072000; includeSubDomains" Header always set X-Frame-Options DENY ssl_ciphers 'AES256+EECDH:AES256+EDH'; ssl_protocols TLSv1 TLSv1.1 TLSv1.2; ssl_prefer_server_ciphers on; ssl_session_cache builtin:1000 shared:SSL:10m; add_header Strict-Transport-Security "max-age=63072000; includeSubDomains"; add_header X-Frame-Options DENY; ssl_stapling on; # Requires nginx >= 1.3.7 ssl_stapling_verify on; # Requires nginx => 1.3.7 resolver $DNS-IP-1 $DNS-IP-2 valid=300s; resolver_timeout 5s; Apache: nginx:
https://www.ssllabs.com/ssltest/ 22
23
24
25 ➡ SNI (Server Name Indication) ➡ Extension 0x0000 ➡
Pretty much every decent browser / server. ➡ IE6, Win XP, Blackberry, Android 2.x, java 1.6.x ➡ So no worries!
26
What an SSL certificate is NOT: 27 ➡ SSL certificate
(but a X.509 certificate) ➡ Automatically secure ➡ Automatically trustworthy ➡ In any way better self-signed certificates ➡ Cheap
What an SSL certificate is: 28 ➡ The best way
(but not perfect) to prove authenticity ➡ A way to bootstrap encrypted communication ➡ Misleading ➡ (Too) Expensive
29
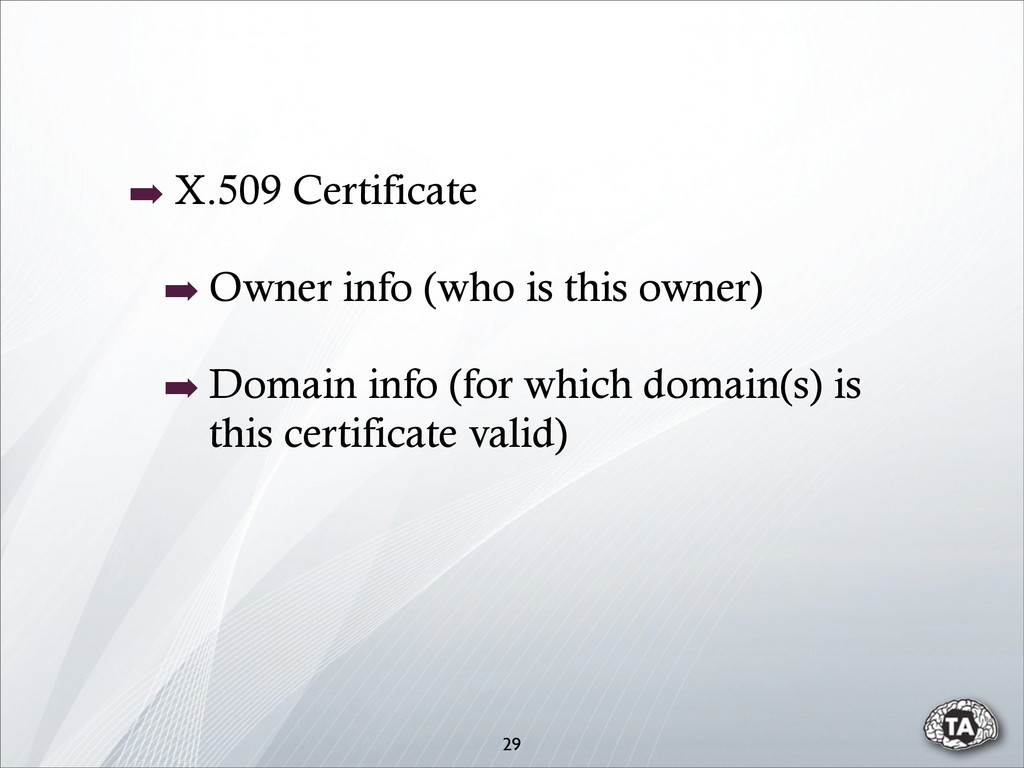
29 ➡ X.509 Certificate
29 ➡ X.509 Certificate ➡ Owner info (who is this
owner)
29 ➡ X.509 Certificate ➡ Owner info (who is this
owner) ➡ Domain info (for which domain(s) is this certificate valid)
29 ➡ X.509 Certificate ➡ Owner info (who is this
owner) ➡ Domain info (for which domain(s) is this certificate valid) ➡ Expiry info (from when to when is this certificate valid)
30 yourdomain.com
30 yourdomain.com Intermediate CA
30 yourdomain.com Intermediate CA
30 yourdomain.com Root CA Intermediate CA
30 yourdomain.com Root CA Intermediate CA
30 yourdomain.com Root CA Intermediate CA
31 IMPLIED TRU$T
➡ (Root) Certificate Authorities ➡ They are built into your
browser / OS and you will automatically trust them. 32
33 wget http://mxr.mozilla.org/mozilla-central/source/security/nss/lib/ckfw/builtins/certdata.txt\?raw\=1 -O - -q | grep Issuer |
sort | uniq | wc -l
33 wget http://mxr.mozilla.org/mozilla-central/source/security/nss/lib/ckfw/builtins/certdata.txt\?raw\=1 -O - -q | grep Issuer |
sort | uniq | wc -l 182 And rising...
34
34 ➡ X.509 certificates are used to authenticate the server.
34 ➡ X.509 certificates are used to authenticate the server.
➡ Servers can ask clients to authenticate themselves as well.
34 ➡ X.509 certificates are used to authenticate the server.
➡ Servers can ask clients to authenticate themselves as well. ➡ APIs
35
36 Generating secrets:
36 pre master secret server rand client rand Generating secrets:
+ +
36 pre master secret server rand client rand master secret
Generating secrets: + +
36 pre master secret server rand client rand master secret
master secret server rand client rand Generating secrets: + + + +
36 pre master secret server rand client rand master secret
master secret server rand client rand key buffer Generating secrets: + + + +
36 pre master secret server rand client rand master secret
client MAC client KEY client IV server MAC server KEY server IV master secret server rand client rand key buffer Generating secrets: + + + +
https://github.com/jaytaph/TLS-decoder 37 http://www.adayinthelifeof.nl/2013/12/30/decoding-tls-with-php/ Try it yourself, php style:
38
39
40
41 Wireshark CAN decrypt your HTTPS traffic Unknown fact! SSLKEYLOGFILE
https://isc.sans.edu/forums/diary/Psst+Your+Browser+Knows+All+Your+Secrets+/16415
42 launchctl setenv SSLKEYLOGFILE /tmp/keylog.secret on a mac:
➡ TLS has overhead in computation and transfers. But definitely
worth it. ➡ Google likes it. ➡ Some ciphersuites are better, but slower. ➡ Speed / Security compromise ➡ (try: “openssl speed”) 43
Are we safe yet? 44
euh,.. no :/ 45
46 PRE MASTER SECRET
What if somebody* got hold of the site private key?
47
48
49
50
51
(PERFECT) FORWARDING SECRECY 52
Compromising the pre-master secret does not compromise our communication. 53
PFS: Can’t compromise other keys with a compromised key. 54
Unfortunately.. 55
56 PFS needs server AND browser support
57 http://news.netcraft.com/archives/2013/06/25/ssl-intercepted-today-decrypted-tomorrow.html
58 http://news.netcraft.com/archives/2013/06/25/ssl-intercepted-today-decrypted-tomorrow.html
Update your cipher suite list and place PFS ciphers at
the top 59
But beware: heavy computations 60
61 SSL Test https://www.ssllabs.com/ssltest/
-ETOOMUCHINFO 62
63 https://www.ssllabs.com/projects/best-practices/index.html
http://farm1.static.flickr.com/73/163450213_18478d3aa6_d.jpg 64
65 Find me on twitter: @jaytaph Find me for development
and training: www.noxlogic.nl Find me on email:
[email protected]
Find me for blogs: www.adayinthelifeof.nl


 jaytaph
 reverentgeek
 dougneiner
 stephenakadiri
 chrislema
 bethany
 kneath
 madoxten
 bermonpainter
 davidcarrasco
 cassininazir
 wjessup
 tanoku