Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
DjangoCon - JSON Web Tokens
Search
José Padilla
September 04, 2014
Programming
11k
15
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
DjangoCon - JSON Web Tokens
DjangoCon US 2014 talk on JSON Web Tokens
José Padilla
September 04, 2014
More Decks by José Padilla
See All by José Padilla
Python, Government, and Contracts
jpadilla
0
90
Python, Government, and Contracts
jpadilla
0
5.2k
Python Type Hints
jpadilla
0
630
Developer Ergonomics
jpadilla
0
2.2k
BFTW: The Backend
jpadilla
4
250
eventos
jpadilla
0
240
JWT
jpadilla
2
500
Ember.js + Django
jpadilla
3
2.2k
UPRB Basic Workshop
jpadilla
2
260
Other Decks in Programming
See All in Programming
React Native에 현대적인 빌드 도구 더하기: Rollipop 구현기
leegeunhyeok
0
180
あなたの await、OS まで届いてる? strace で覗く JavaScript の非同期
hasutosasaki
1
2.3k
조합이폭발하는디자인시스템이걸눈으로도테스트하라고요
giljongyu
0
740
SODA - FACT BOOK(JP)
sodainc
1
40k
AI Augmentation Techniques with Liberty
ivargrimstad
1
420
Goコンパイラを作ってGoをもっと理解する / Build a Go compiler to better understand Go
ikura_hamu
0
130
Vue.jsで作る空間解析アプリとCapacitorプラグインのData Bridge
hal_spidernight
1
170
Railsのためのパスキー実践入門 〜マルチテナントSaaSでの意思決定〜
utakaha
4
3.7k
SODA - FACT BOOK(EN)
sodainc
1
220
Snowflake Openflow Connector利用の勘所 / 20261024developersio2026tokyo-snowflake-openflow
kasacchiful
PRO
0
320
當我們開始不讀 Code - AI Agent 時代,Code Review 與 Clean Code 還剩下什麼?
jame2408
1
370
AmebaブログはKMPから卒業します
kmars0605
0
340
Featured
See All Featured
SERP Conf. Vienna - Web Accessibility: Optimizing for Inclusivity and SEO
sarafernandez
2
1.6k
SEO Brein meetup: CTRL+C is not how to scale international SEO
lindahogenes
2
3k
The MySQL Ecosystem @ GitHub 2015
samlambert
251
13k
Claude Code のすすめ
schroneko
67
230k
GraphQLとの向き合い方2022年版
quramy
50
15k
DevOps and Value Stream Thinking: Enabling flow, efficiency and business value
helenjbeal
2
440
The Spectacular Lies of Maps
axbom
PRO
1
1.1k
jQuery: Nuts, Bolts and Bling
dougneiner
66
8.7k
Performance Is Good for Brains [We Love Speed 2024]
tammyeverts
12
1.9k
Impact Scores and Hybrid Strategies: The future of link building
tamaranovitovic
0
480
Google's AI Overviews - The New Search
badams
0
1.7k
A Guide to Academic Writing Using Generative AI - A Workshop
ks91
PRO
1
560
Transcript
JWT
“jot”
JSON Web Tokens
José Padilla
Flickr: Bryan Vincent
Co-founder at blimp.io
/jpadilla
jpadilla.com
Why?
Single Sign-on
Action Links
Webhooks
Token-based Auth
What?
“Compact URL-safe means of representing claims to be transferred between
two parties. The claims in a JWT are encoded as a JSON object that is digitally signed using JSON Web Signature (JWS).” - IETF.
None
None
None
None
None
None
JOSE
JavaScript Object Signing and Encryption
JWA
JSON Web Algorithms
JWK
JSON Web Key
JWT
JSON Web Token
JWS
JSON Web Signature
JWE
JSON Web Encryption
Today it’s all about JWT
How?
Internet-Draft
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
{ "typ": "JWT", "alg": "HS256" } eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
import json import hmac from hashlib import sha256 from base64
import urlsafe_b64encode ! segments = [] ! header_dict = { 'typ':'JWT', 'alg': 'HS256' } ! json_header = json.dumps(header_dict) ! header = urlsafe_b64encode(json_header).rstrip('=') segments.append(header) eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
{! "user_id": 1! } eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
payload_dict = { 'user_id': 1 } ! json_payload = json.dumps(payload)
! payload = urlsafe_b64encode(json_payload).rstrip('=') segments.append(payload) eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
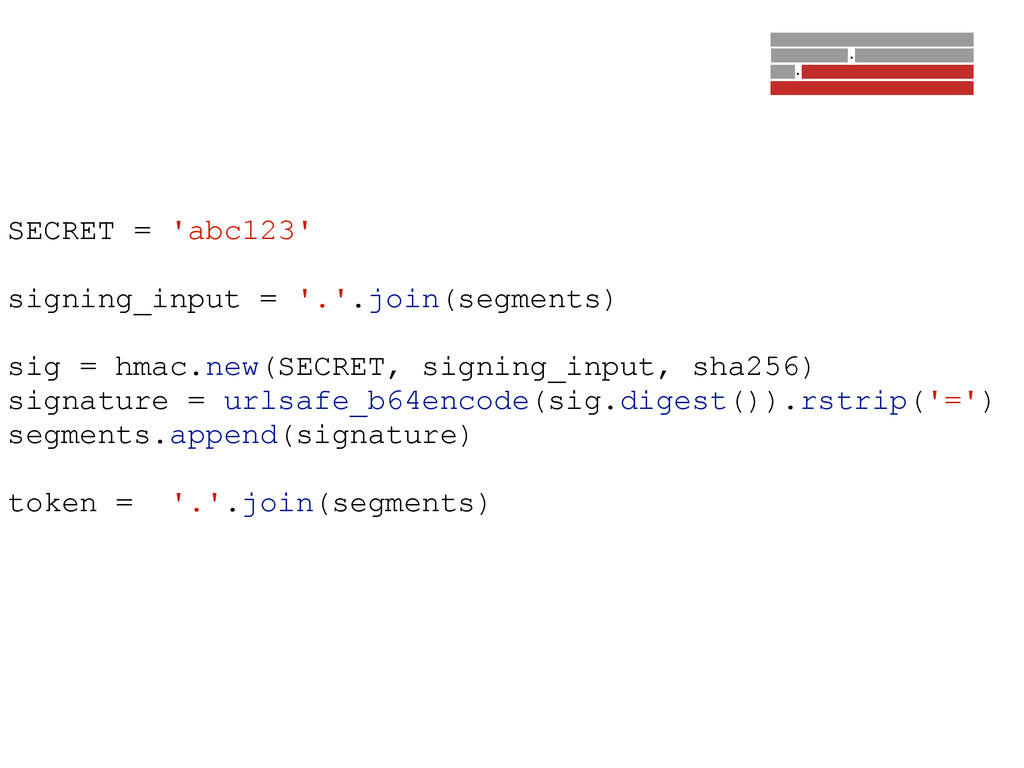
SECRET = 'abc123' ! signing_input = '.'.join(segments) ! sig =
hmac.new(SECRET, signing_input, sha256) signature = urlsafe_b64encode(sig.digest()).rstrip('=') segments.append(signature) ! token = '.'.join(segments) eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
eyJ0eXAiOiJKV1QiLCJhbGciOi JIUzI1NiJ9.eyJ1c2VyX2lkIjo xfQ.xpCS8TTq1a53OIps1ByTdm 6Sh-A1ZoCId3e2YYWjapU
PyJWT
$ pip install PyJWT
import jwt ! SECRET_KEY = "abc123" payload = {"user_id": 1}
! jwt_token = jwt.encode(payload, SECRET_KEY) ! payload = jwt.decode(jwt_token, SECRET_KEY)
/progrium/pyjwt
Django JWT Auth
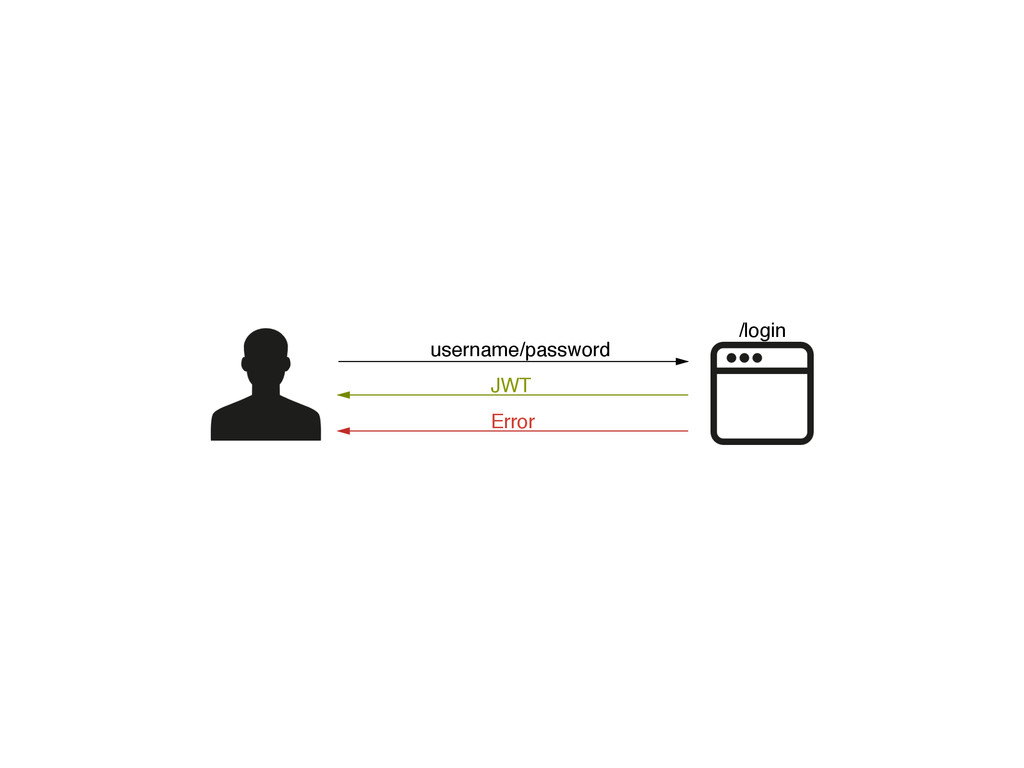
username/password JWT Error /login
Authorization: Bearer <JWT> JWT Error /restricted
$ pip install django-jwt
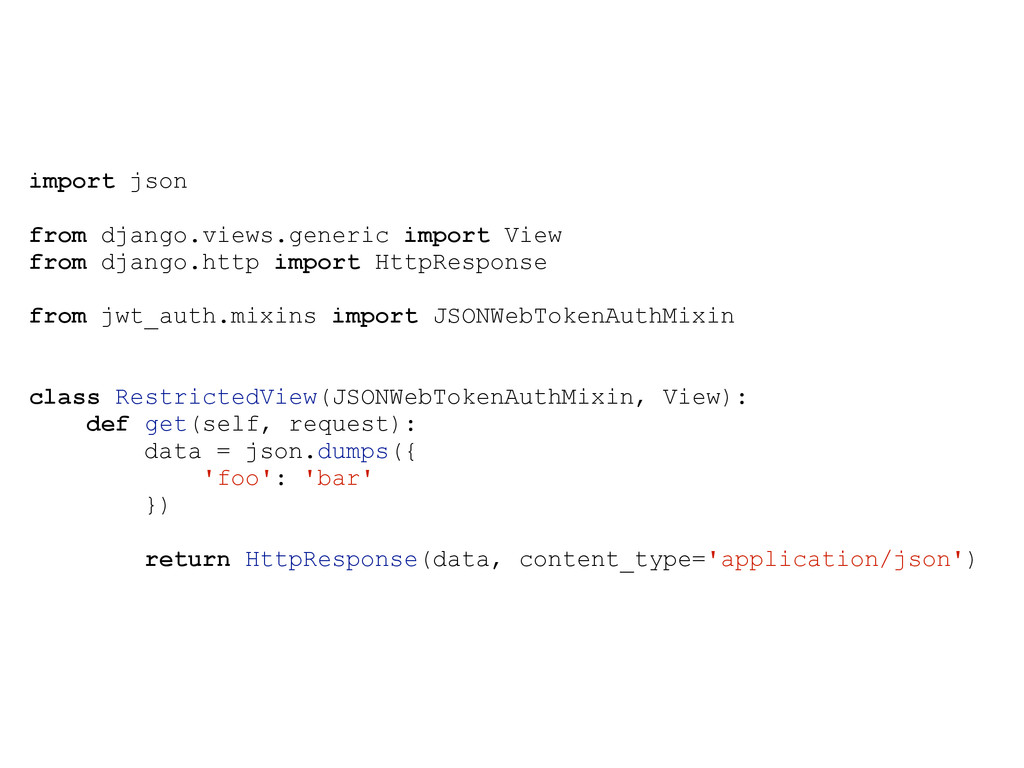
import json ! from django.views.generic import View from django.http import
HttpResponse ! from jwt_auth.mixins import JSONWebTokenAuthMixin ! ! class RestrictedView(JSONWebTokenAuthMixin, View): def get(self, request): data = json.dumps({ 'foo': 'bar' }) return HttpResponse(data, content_type='application/json')
from django.conf.urls import patterns from .views import RestrictedView urlpatterns =
patterns( '', ! (r'^login/$', 'jwt_auth.views.obtain_jwt_token'), (r'^restricted/$', RestrictedView.as_view()), )
/jpadilla/django-jwt-auth
DRF JWT Auth
$ pip install djangorestframework-jwt
from rest_framework.views import APIView from rest_framework.response import Response from rest_framework.permissions
import IsAuthenticated from rest_framework_jwt.authentication import JSONWebTokenAuthentication class RestrictedView(APIView): permission_classes = (IsAuthenticated, ) authentication_classes = (JSONWebTokenAuthentication, ) def get(self, request): data = { 'foo': 'bar' } ! return Response(data)
from django.conf.urls import patterns from .views import RestrictedView urlpatterns =
patterns( '', ! (r'^login/', 'rest_framework_jwt.views.obtain_jwt_token'), (r'^restricted/$', RestrictedView.as_view()), )
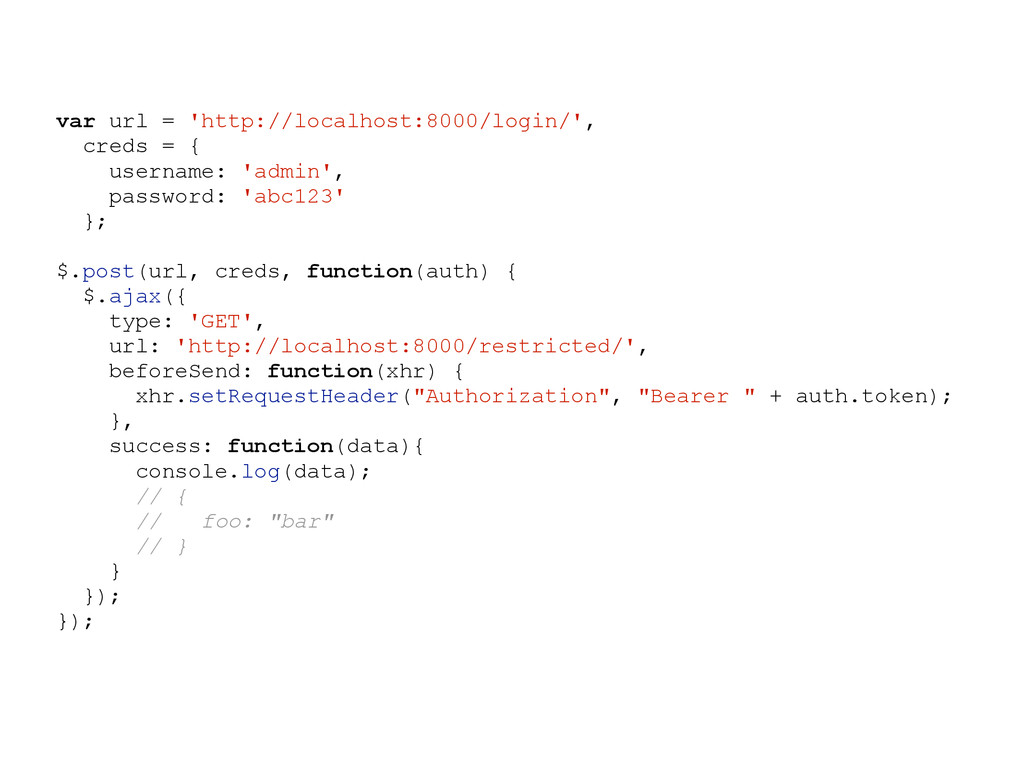
var url = 'http://localhost:8000/login/', creds = { username: 'admin', password:
'abc123' }; $.post(url, creds, function(auth) { $.ajax({ type: 'GET', url: 'http://localhost:8000/restricted/', beforeSend: function(xhr) { xhr.setRequestHeader("Authorization", "Bearer " + auth.token); }, success: function(data){ console.log(data); // { // foo: "bar" // } } }); });
/GetBlimp/django-rest-framework-jwt
Recap • It’s a standard • It’s simple • Third
party libraries • Single Sign-on • Action links • Authentication • CORS • Stateless • No CSRF • CDN • Mobile/WebSockets
Django REST Framework Sprint
Thanks Questions? http:/ /bit.ly/djangocon-jwt


 jpadilla
 leegeunhyeok
 hasutosasaki
 giljongyu
 sodainc
 ivargrimstad
 ikura_hamu
 hal_spidernight
 utakaha
 kasacchiful
 jame2408
 kmars0605
 sarafernandez
 lindahogenes
 samlambert
 schroneko
 quramy
 helenjbeal
 axbom
 dougneiner
 tammyeverts
 tamaranovitovic
 badams
 ks91