Share
Embed
OpenShift Commons Gathering Chicago 2023 - Trusted Artifact Signer: Private Sigstore
Sally O'Malley (Red Hat) presents at the OpenShift Commons Gathering Co-Located with KubeCon + CloudNativeCon North America 2023.
OpenShift Commons
November 17, 2023
Transcript
15 slides
-
rekor keycloak cosign sigstore fulcio TUF gitsign rekor CLI trillian
CTlog Image by Wynne O’Malley -
Software supply chains… are not ideal! Developers Build systems (CI,
Compliers) Code reviewers package Code Dependency Consumers Artifact (container,.) • Replay / freeze attacks • Compromised keys • Account Compromise • Swapped hashes • Compromise of build systems • Easy reconnaissance (open configuration) • Typosquatting • Maintainer account takeover -
Imagine a world where signing and key management is greatly
simplified… and transparency reigns supreme -
Sigstore is to software signing and provenance, what Let’s Encrypt
is to HTTPS / SSL -
Trusted Artifact Signer: Sigstore stack TUF server for trust root
establish root of trust, serves publickeys & root CA cert that clients can verify with Fulcio CA server issues short-lived code signing certificates based on authenticated OIDC identity Certificate Transparency Log append-only immutable, verifiable transparency log that stores the signing certificates Rekor API-based server for validation and a transparency log for storage Trillian backend for Rekor -implementation of the transparency log - tamper-proof append-only Rekor CLI verify an artifact is stored within the transparency log, query the log, and retrieval of entries Cosign container signing tool Gitsign keyless signing for Git commits Helm upstream Sigstore scaffold chart with OpenShift specific configuration & resources -
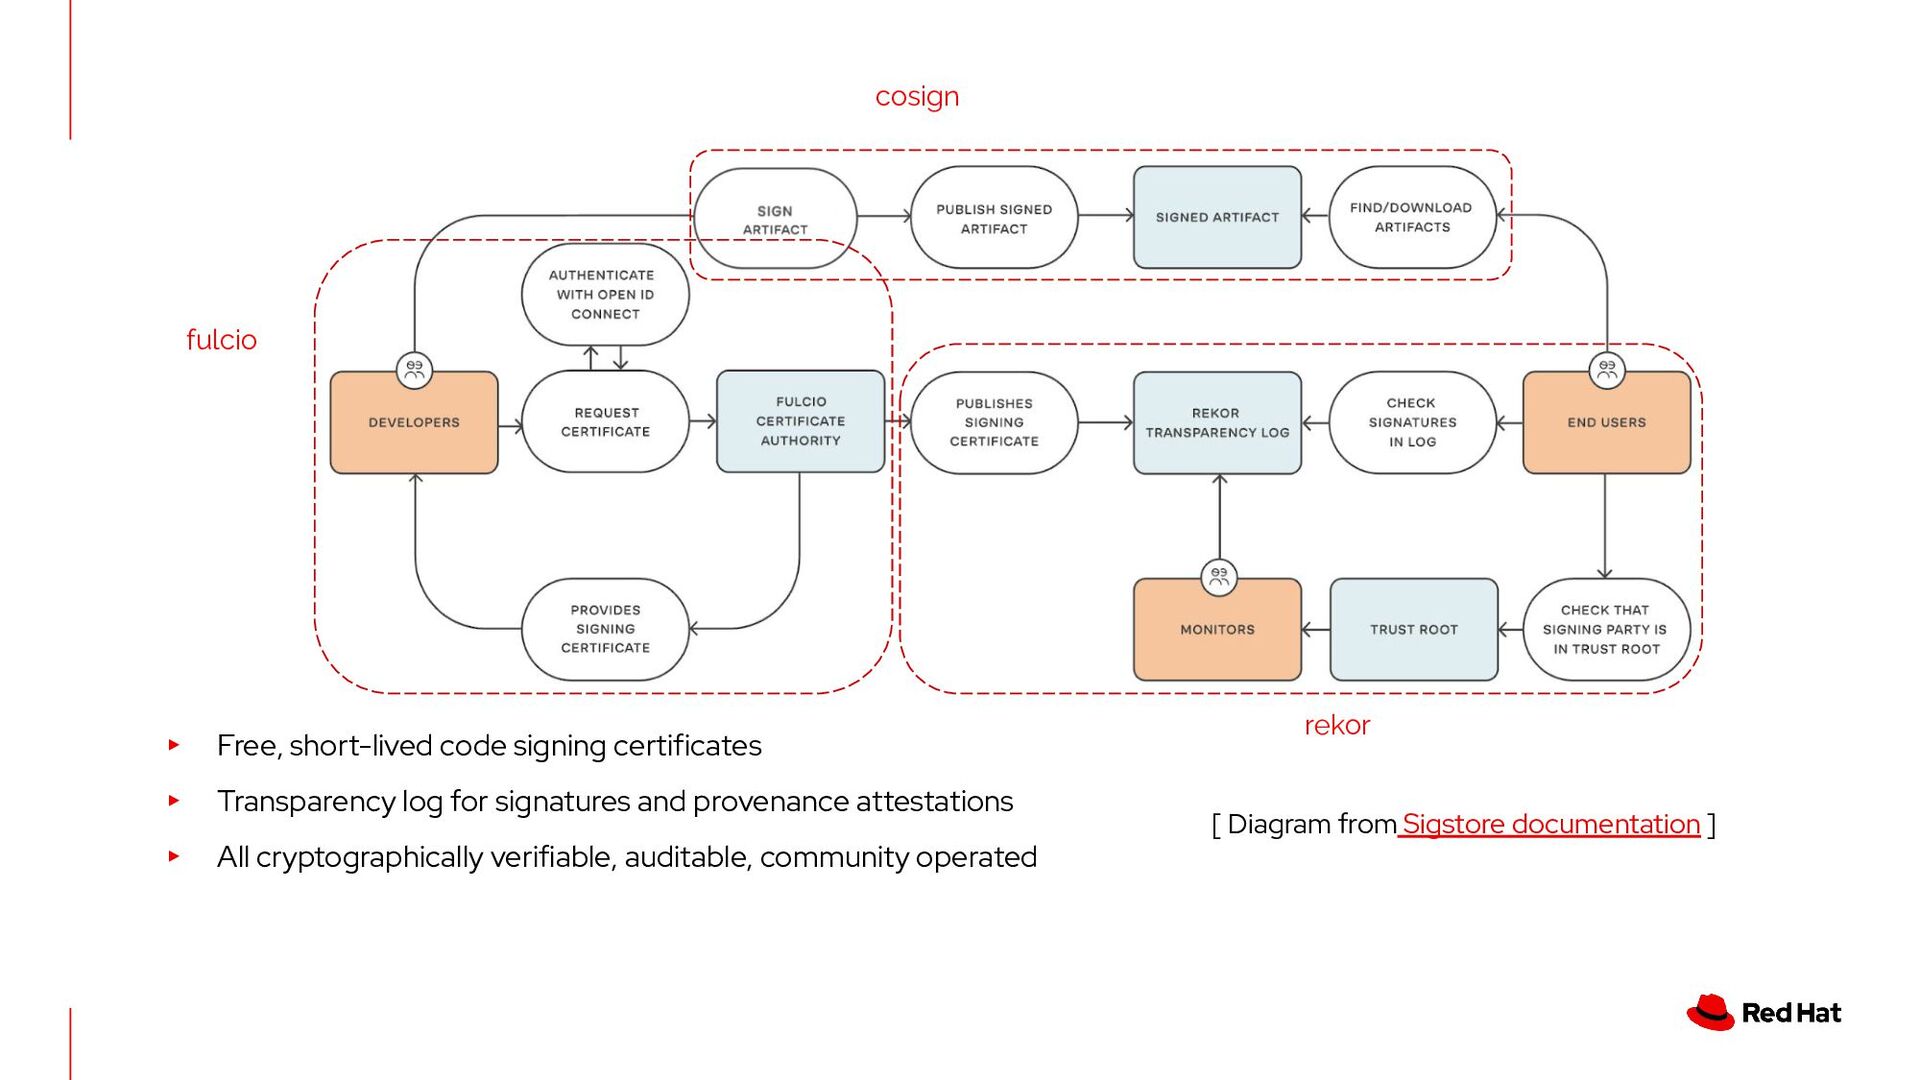
fulcio cosign rekor ▸ Free, short-lived code signing certificates ▸
Transparency log for signatures and provenance attestations ▸ All cryptographically verifiable, auditable, community operated [ Diagram from Sigstore documentation ] -
Fulcio Architecture Authenticate with OIDC; prove possession of private key
Return CodeSign Certificate Publish Cert to Log OIDC PROVIDER Verify signed ID token from configured OIDC provider FULCIO: CERTIFICATE AUTHORITY FULCIO: KEY TRANSPARENCY LOG Diagram shared from speakerdeck.com/redhatlivestream -
Rekor Architecture Developer Sign and Publish Artifacts Signed Artifact rekor:
Signature Transparency Log Publish signatures +S Diagram shared from speakerdeck.com/redhatlivestream -
Cosign Architecture ▸ Obtains keypair (either existing key locally, KMS,
or ephemeral key pair); ▸ Requests code signing certificate from fulcio ▸ Downloads container manifest from registry, generates signature ▸ Uploads signature, public key (and certificate chain) to container registry as OCI object ▸ Creates entry in rekor for the signed container Container registry cosign REKOR: Signature Transparency Log FULCIO: CERTIFICATE AUTHORITY Diagram shared from speakerdeck.com/redhatlivestream -
Enforcement of image signatures at pod admission Policy Enforcement Tools
Admission Controller Integration with policy enforcement tools, such as OPA Gatekeeper and Kyverno, and RH Advanced Cluster Security Tekton Chains Image and artifact signing as part of CI/CD workflows (also GitHub Actions) Sigstore Integrations -
Resources / References 14 • Introducing sigstore: Signing for the
Masses • Sigstore: An Open Answer to Software Supply Chain and Trust Blogs • OpenShift Commons Briefing • KubeCon 2021 Videos • https://www.sigstore.dev Project Website • https://sigstore.slack.com Slack -
linkedin.com/company/red-hat youtube.com/user/RedHatVideos facebook.com/redhatinc twitter.com/RedHat Red Hat is the world’s leading
provider of enterprise open source software solutions. Award-winning support, training, and consulting services make Red Hat a trusted adviser to the Fortune 500. Thank you