Public Sector on Air: CodeReady Workspaces with...

Share
Embed
Public Sector on Air: CodeReady Workspaces with Zohaib Khan
CodeReady Workspaces can break the COVID barriers to developer productivity with Zohaib Khan
Public Sector on Air features Red Hatters, partners, and customers from public sector entities talking about common problems that need to be solved in the sector.
https://openshift.tv

Red Hat Livestreaming
July 27, 2020
Transcript
40 slides
-
CONFIDENTIAL Designator Red Hat CodeReady Workspaces COVID Ready Developer Workspaces
and IDE Zohaib Khan App Modernization Lead - Red Hat 1 -
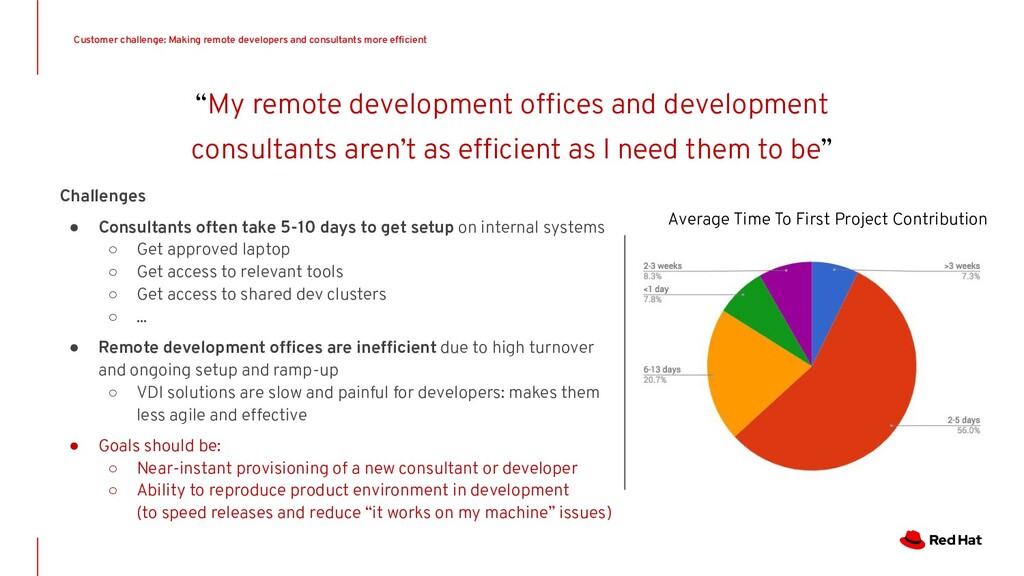
Challenges • Consultants often take 5-10 days to get setup
on internal systems ◦ Get approved laptop ◦ Get access to relevant tools ◦ Get access to shared dev clusters ◦ ... • Remote development offices are inefficient due to high turnover and ongoing setup and ramp-up ◦ VDI solutions are slow and painful for developers: makes them less agile and effective • Goals should be: ◦ Near-instant provisioning of a new consultant or developer ◦ Ability to reproduce product environment in development (to speed releases and reduce “it works on my machine” issues) “My remote development offices and development consultants aren’t as efficient as I need them to be” Average Time To First Project Contribution Customer challenge: Making remote developers and consultants more efficient -
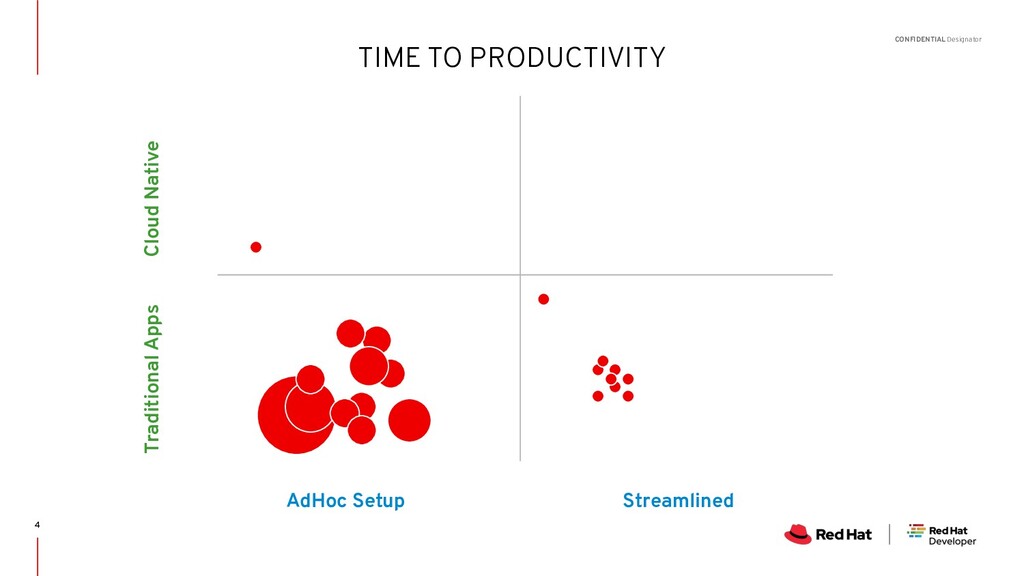
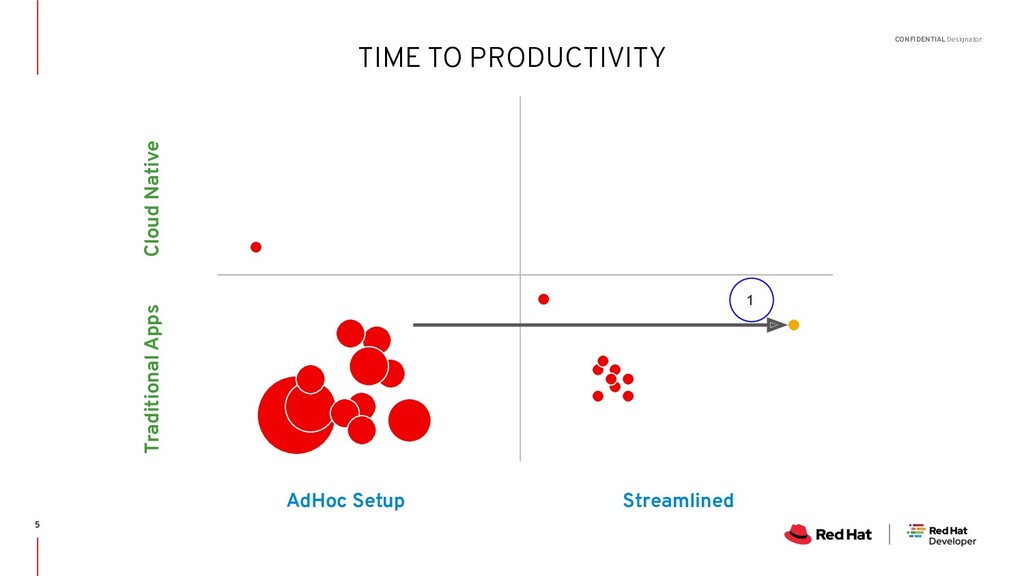
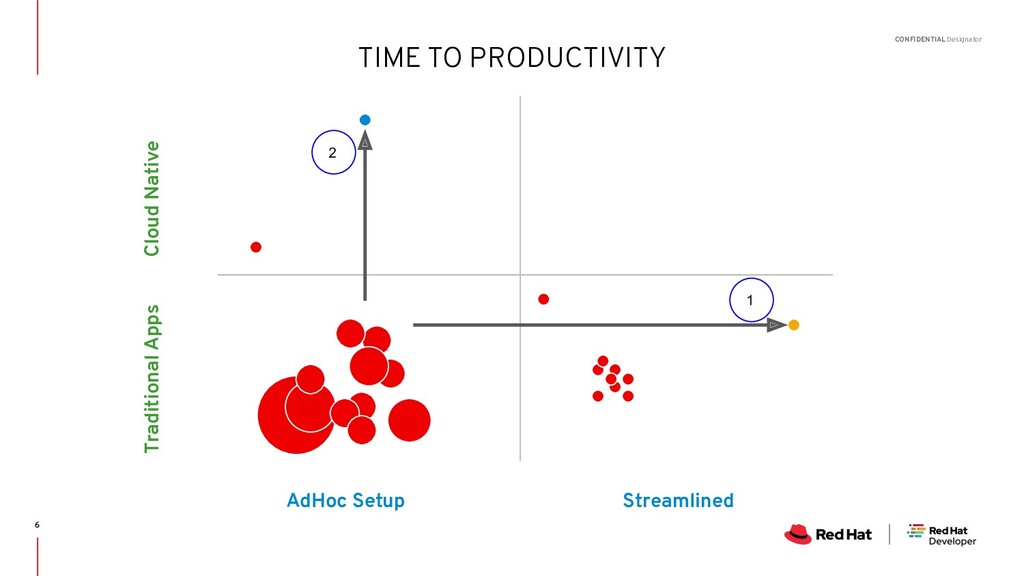
CONFIDENTIAL Designator TIME TO PRODUCTIVITY 6 AdHoc Setup Streamlined Traditional
Apps Cloud Native 1 2 -
CONFIDENTIAL Designator WHERE WE ARE TODAY Vast majority of an
organization’s developers are not experts at containers or Kubernetes. Development is done on the desktop, usually outside containers. Production is moving to a Kubernetes distribution like OpenShift. INTRO 7 -
“>80% of my development teams aren’t Kubernetes and container experts”
Customer challenge: Enabling teams on Kubernetes Google Search Trend: Kubernetes and Linux Containers 5 year old technology.. very new! Challenge • Development happens on laptops: not in Kubernetes, sometimes in containers • IT is moving to Kubernetes in production • Devs have programming knowledge, but little experience with containers and Kubernetes • Training every developer to become a container and Kube expert isn’t viable: too hard, too long Need a way to make devs productive on Kube now, but enable their learning journey going forward -
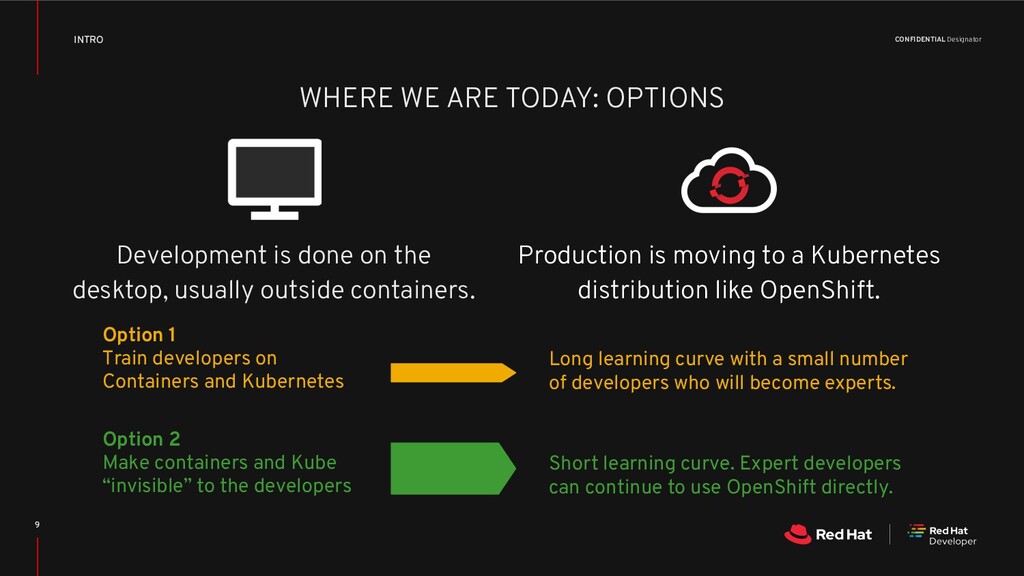
CONFIDENTIAL Designator Option 1 Train developers on Containers and Kubernetes
Option 2 Make containers and Kube “invisible” to the developers Long learning curve with a small number of developers who will become experts. Short learning curve. Expert developers can continue to use OpenShift directly. INTRO 9 WHERE WE ARE TODAY: OPTIONS Development is done on the desktop, usually outside containers. Production is moving to a Kubernetes distribution like OpenShift. -
CONFIDENTIAL Designator THE KEY QUESTION What’s needed to allow an
authorized developer to contribute to a project without deep containers and Kubernetes knowledge? INTRO 10 -
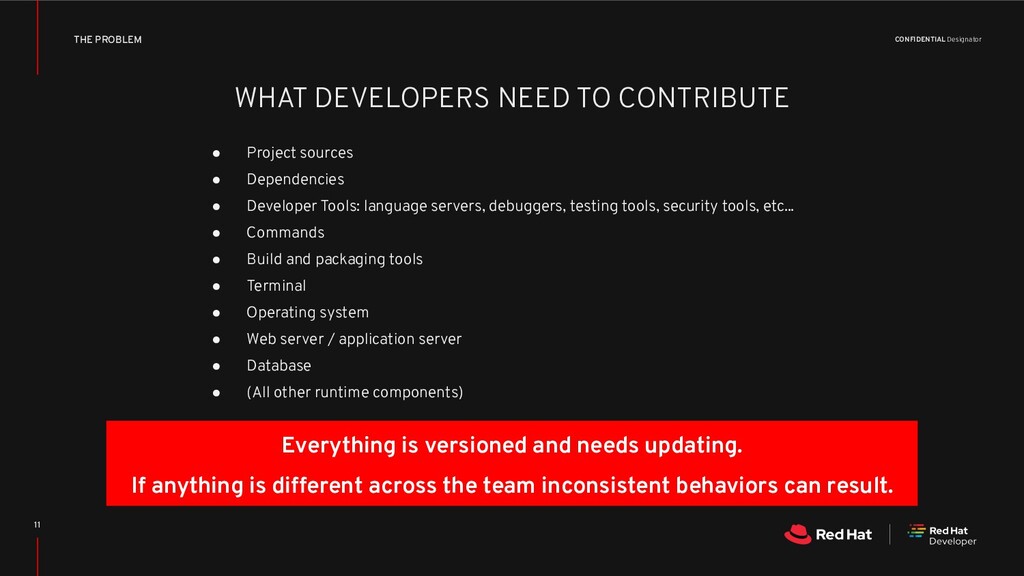
CONFIDENTIAL Designator WHAT DEVELOPERS NEED TO CONTRIBUTE • Project sources
• Dependencies • Developer Tools: language servers, debuggers, testing tools, security tools, etc... • Commands • Build and packaging tools • Terminal • Operating system • Web server / application server • Database • (All other runtime components) Everything is versioned and needs updating. If anything is different across the team inconsistent behaviors can result. THE PROBLEM 11 -
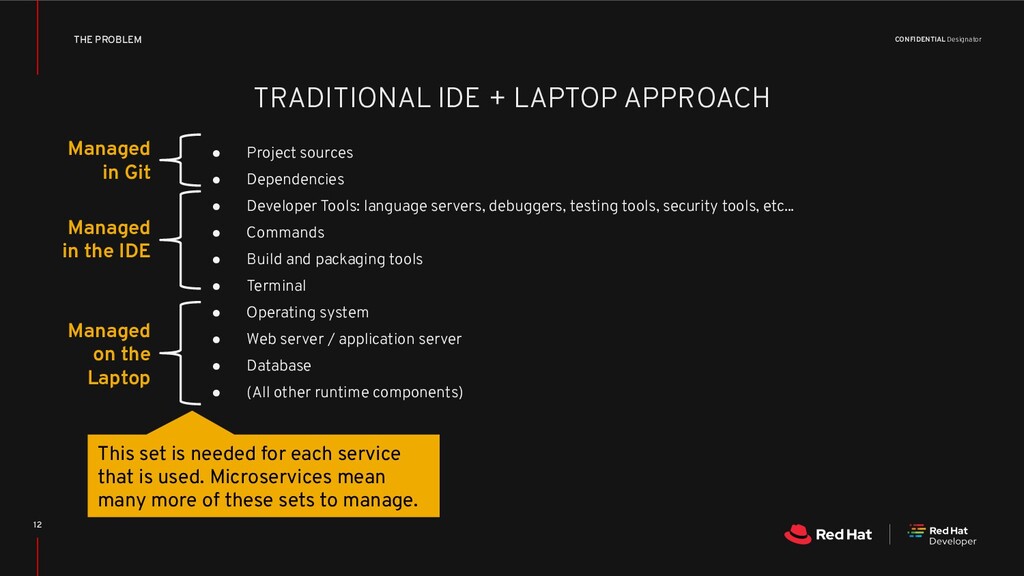
CONFIDENTIAL Designator TRADITIONAL IDE + LAPTOP APPROACH Managed in the
IDE Managed on the Laptop Managed in Git This set is needed for each service that is used. Microservices mean many more of these sets to manage. THE PROBLEM 12 • Project sources • Dependencies • Developer Tools: language servers, debuggers, testing tools, security tools, etc... • Commands • Build and packaging tools • Terminal • Operating system • Web server / application server • Database • (All other runtime components) -
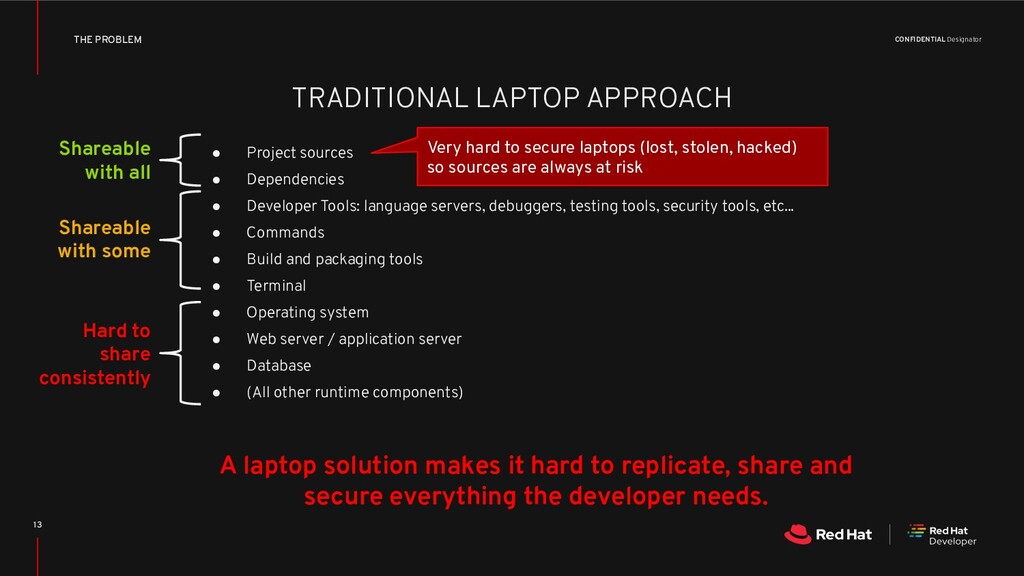
CONFIDENTIAL Designator TRADITIONAL LAPTOP APPROACH Shareable with some Hard to
share consistently Shareable with all THE PROBLEM 13 • Project sources • Dependencies • Developer Tools: language servers, debuggers, testing tools, security tools, etc... • Commands • Build and packaging tools • Terminal • Operating system • Web server / application server • Database • (All other runtime components) Very hard to secure laptops (lost, stolen, hacked) so sources are always at risk A laptop solution makes it hard to replicate, share and secure everything the developer needs. -
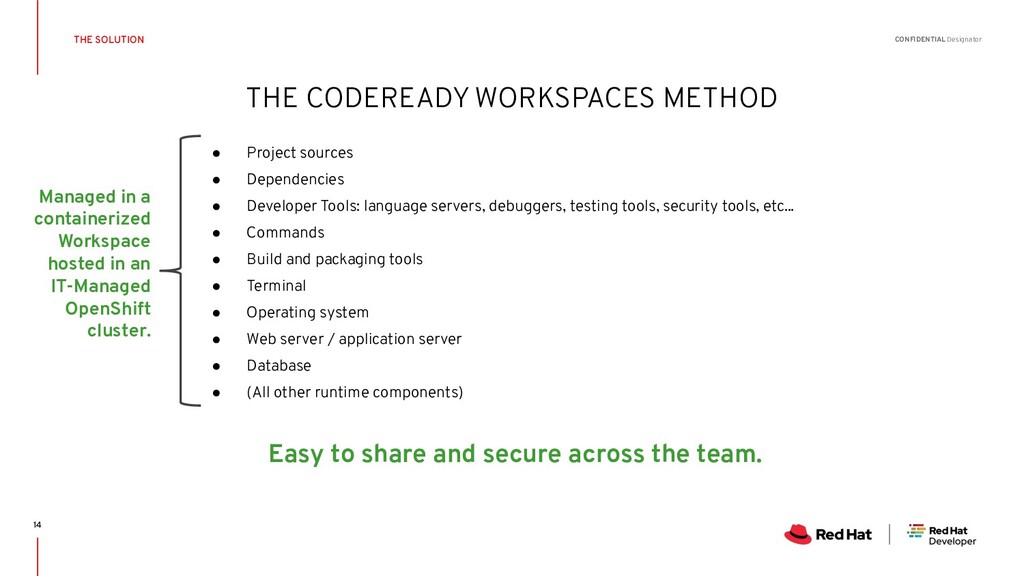
CONFIDENTIAL Designator Managed in a containerized Workspace hosted in an
IT-Managed OpenShift cluster. THE CODEREADY WORKSPACES METHOD Easy to share and secure across the team. THE SOLUTION 14 • Project sources • Dependencies • Developer Tools: language servers, debuggers, testing tools, security tools, etc... • Commands • Build and packaging tools • Terminal • Operating system • Web server / application server • Database • (All other runtime components) -
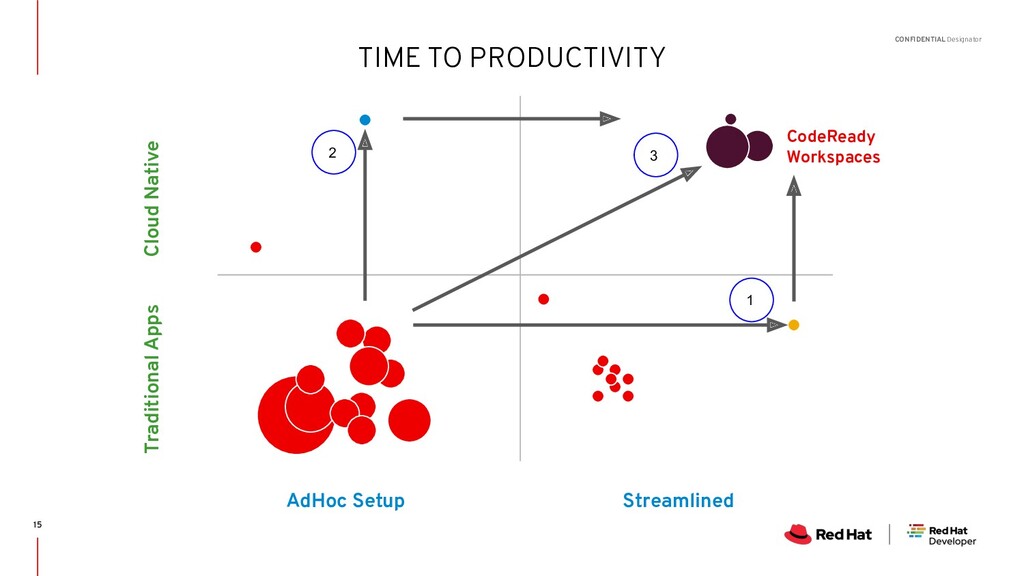
CONFIDENTIAL Designator TIME TO PRODUCTIVITY 15 AdHoc Setup Streamlined Traditional
Apps Cloud Native 1 2 3 CodeReady Workspaces -
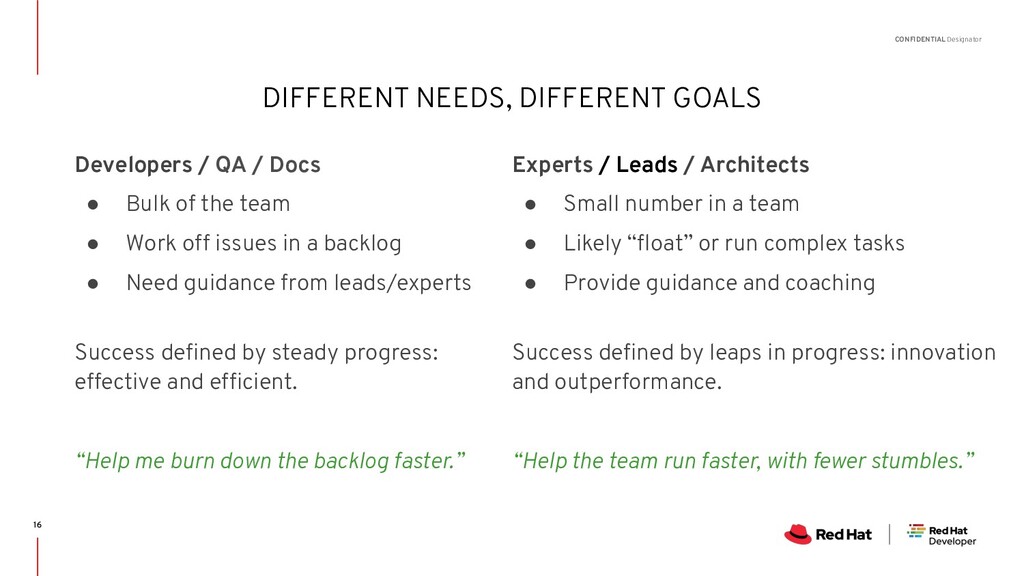
CONFIDENTIAL Designator Developers / QA / Docs • Bulk of
the team • Work off issues in a backlog • Need guidance from leads/experts Success defined by steady progress: effective and efficient. “Help me burn down the backlog faster.” DIFFERENT NEEDS, DIFFERENT GOALS Experts / Leads / Architects • Small number in a team • Likely “float” or run complex tasks • Provide guidance and coaching Success defined by leaps in progress: innovation and outperformance. “Help the team run faster, with fewer stumbles.” 16 -
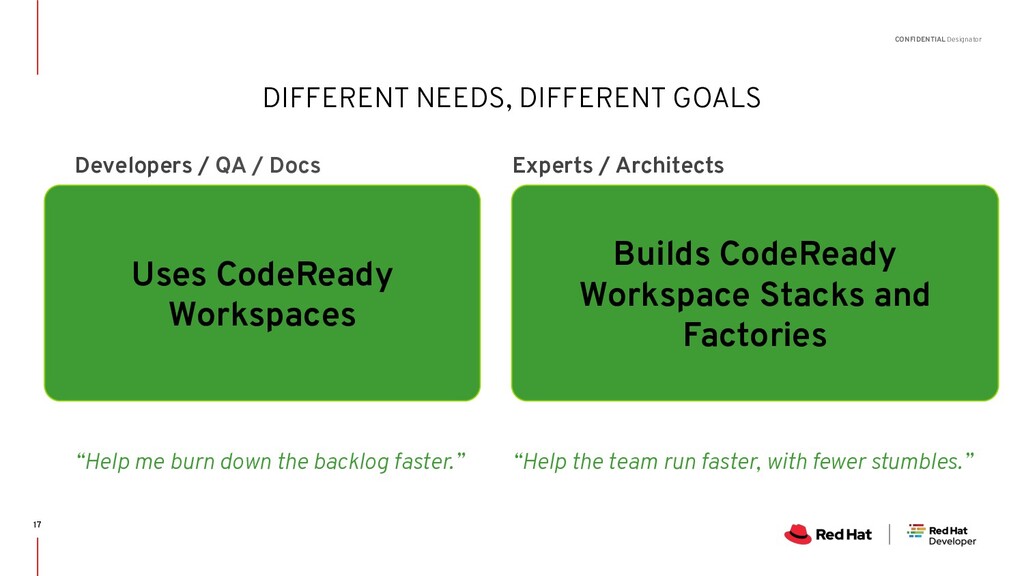
CONFIDENTIAL Designator Developers / QA / Docs • Bulk of
the team • Work off issues in a backlog • Need guidance from leads/experts Success defined by steady progress: effective and efficient. “Help me burn down the backlog faster.” DIFFERENT NEEDS, DIFFERENT GOALS Experts / Architects • Small number in a team • Likely “float” or run complex tasks • Provide guidance and coaching Success defined by leaps in progress: innovation and outperformance. “Help the team run faster, with fewer stumbles.” Uses CodeReady Workspaces Builds CodeReady Workspace Stacks and Factories 17 -
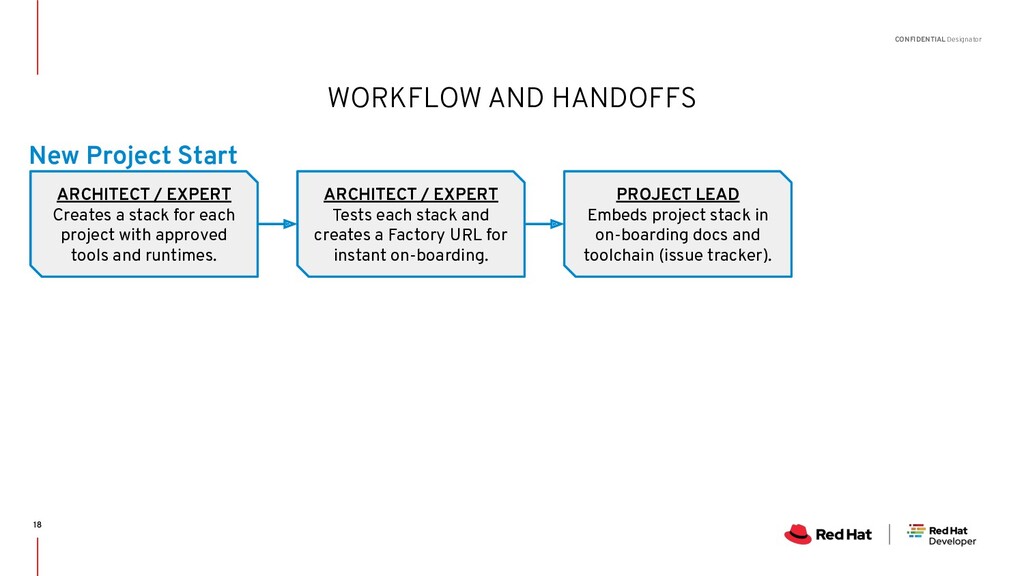
CONFIDENTIAL Designator WORKFLOW AND HANDOFFS ARCHITECT / EXPERT Creates a
stack for each project with approved tools and runtimes. ARCHITECT / EXPERT Tests each stack and creates a Factory URL for instant on-boarding. PROJECT LEAD Embeds project stack in on-boarding docs and toolchain (issue tracker). New Project Start 18 -
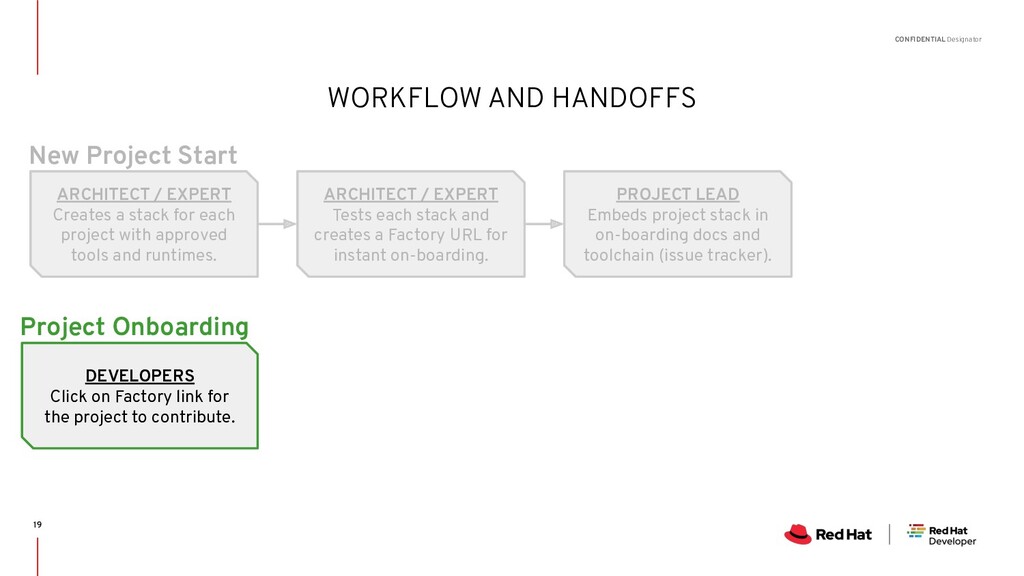
CONFIDENTIAL Designator WORKFLOW AND HANDOFFS ARCHITECT / EXPERT Creates a
stack for each project with approved tools and runtimes. ARCHITECT / EXPERT Tests each stack and creates a Factory URL for instant on-boarding. PROJECT LEAD Embeds project stack in on-boarding docs and toolchain (issue tracker). DEVELOPERS Click on Factory link for the project to contribute. New Project Start Project Onboarding 19 -
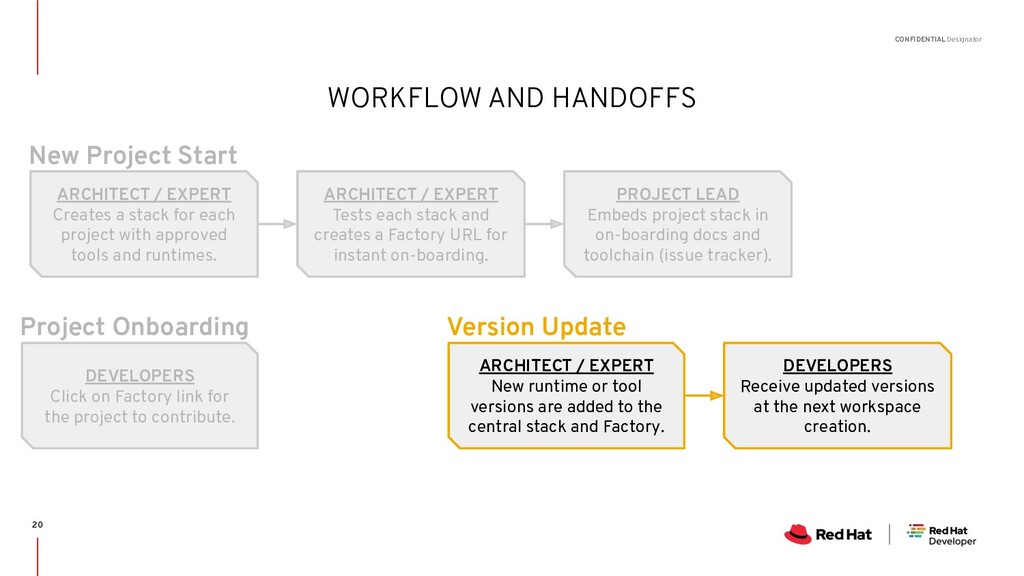
CONFIDENTIAL Designator DEVELOPERS Click on Factory link for the project
to contribute. WORKFLOW AND HANDOFFS ARCHITECT / EXPERT Creates a stack for each project with approved tools and runtimes. ARCHITECT / EXPERT Tests each stack and creates a Factory URL for instant on-boarding. PROJECT LEAD Embeds project stack in on-boarding docs and toolchain (issue tracker). ARCHITECT / EXPERT New runtime or tool versions are added to the central stack and Factory. DEVELOPERS Receive updated versions at the next workspace creation. New Project Start Version Update Project Onboarding 20 -
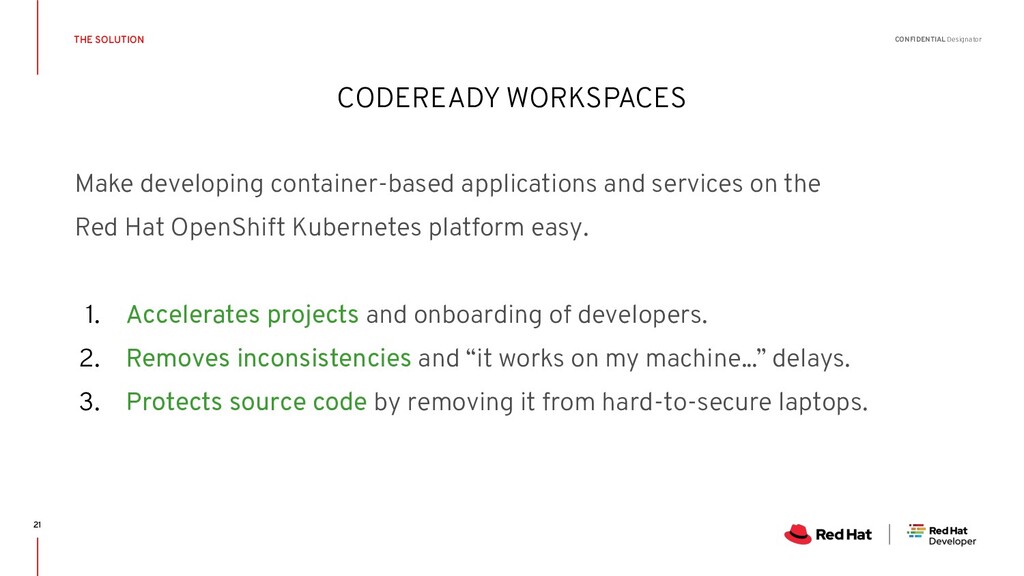
CONFIDENTIAL Designator Make developing container-based applications and services on the
Red Hat OpenShift Kubernetes platform easy. 1. Accelerates projects and onboarding of developers. 2. Removes inconsistencies and “it works on my machine...” delays. 3. Protects source code by removing it from hard-to-secure laptops. CODEREADY WORKSPACES THE SOLUTION 21 -
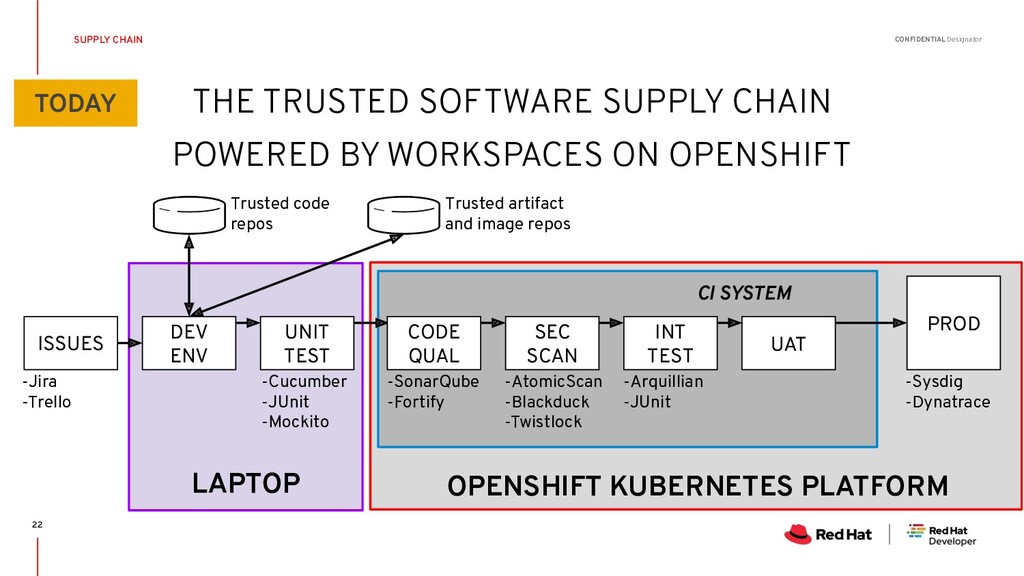
CONFIDENTIAL Designator THE TRUSTED SOFTWARE SUPPLY CHAIN POWERED BY WORKSPACES
ON OPENSHIFT -Cucumber -JUnit -Mockito -SonarQube -Fortify -AtomicScan -Blackduck -Twistlock Trusted code repos -Sysdig -Dynatrace -Jira -Trello CI SYSTEM ISSUES DEV ENV UNIT TEST CODE QUAL SEC SCAN INT TEST UAT PROD Trusted artifact and image repos OPENSHIFT KUBERNETES PLATFORM -Arquillian -JUnit LAPTOP TODAY SUPPLY CHAIN 22 -
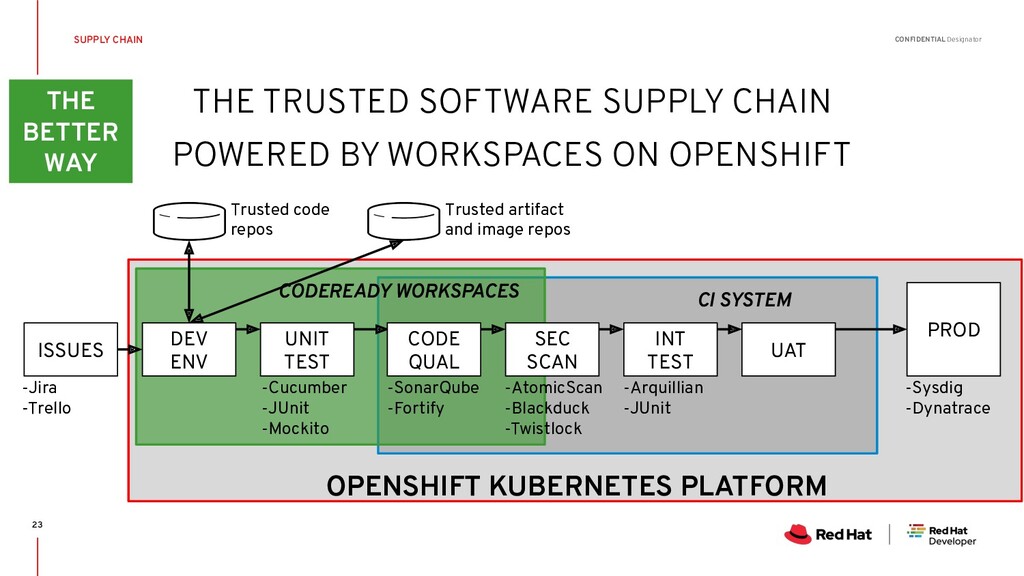
CONFIDENTIAL Designator THE TRUSTED SOFTWARE SUPPLY CHAIN POWERED BY WORKSPACES
ON OPENSHIFT -Cucumber -JUnit -Mockito -SonarQube -Fortify -AtomicScan -Blackduck -Twistlock Trusted code repos -Sysdig -Dynatrace -Jira -Trello CI SYSTEM ISSUES DEV ENV UNIT TEST CODE QUAL SEC SCAN INT TEST UAT PROD Trusted artifact and image repos OPENSHIFT KUBERNETES PLATFORM -Arquillian -JUnit THE BETTER WAY CODEREADY WORKSPACES SUPPLY CHAIN 23 -
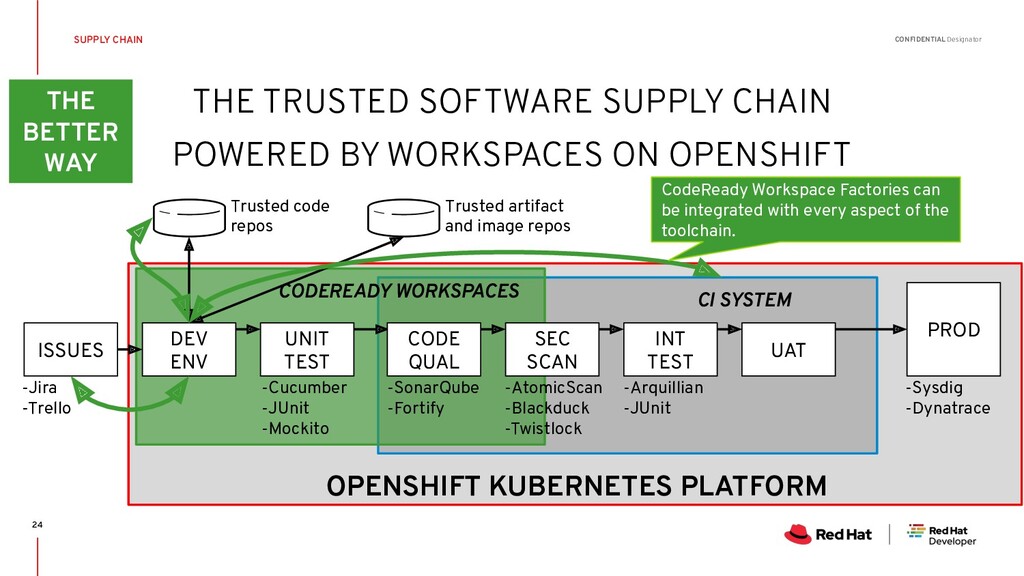
CONFIDENTIAL Designator THE TRUSTED SOFTWARE SUPPLY CHAIN POWERED BY WORKSPACES
ON OPENSHIFT -Cucumber -JUnit -Mockito -SonarQube -Fortify -AtomicScan -Blackduck -Twistlock Trusted code repos -Sysdig -Dynatrace -Jira -Trello CI SYSTEM ISSUES DEV ENV UNIT TEST CODE QUAL SEC SCAN INT TEST UAT PROD Trusted artifact and image repos OPENSHIFT KUBERNETES PLATFORM -Arquillian -JUnit CODEREADY WORKSPACES CodeReady Workspace Factories can be integrated with every aspect of the toolchain. THE BETTER WAY SUPPLY CHAIN 24 -
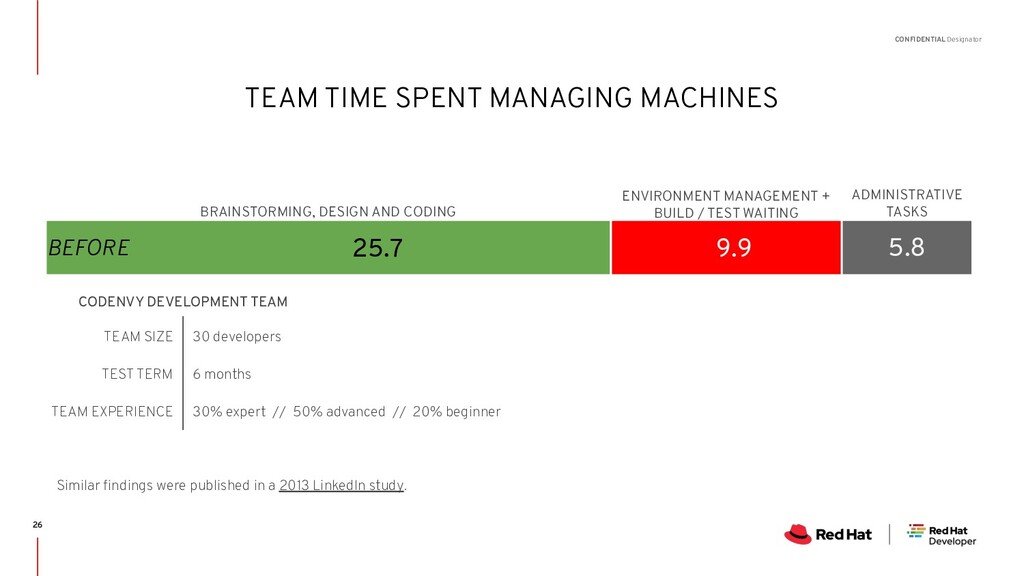
CONFIDENTIAL Designator TEAM TIME SPENT MANAGING MACHINES 25.7 5.8 9.9
ENVIRONMENT MANAGEMENT + BUILD / TEST WAITING ADMINISTRATIVE TASKS BRAINSTORMING, DESIGN AND CODING BEFORE TEAM SIZE 30 developers TEST TERM 6 months TEAM EXPERIENCE 30% expert // 50% advanced // 20% beginner Similar findings were published in a 2013 LinkedIn study. CODENVY DEVELOPMENT TEAM 26 -
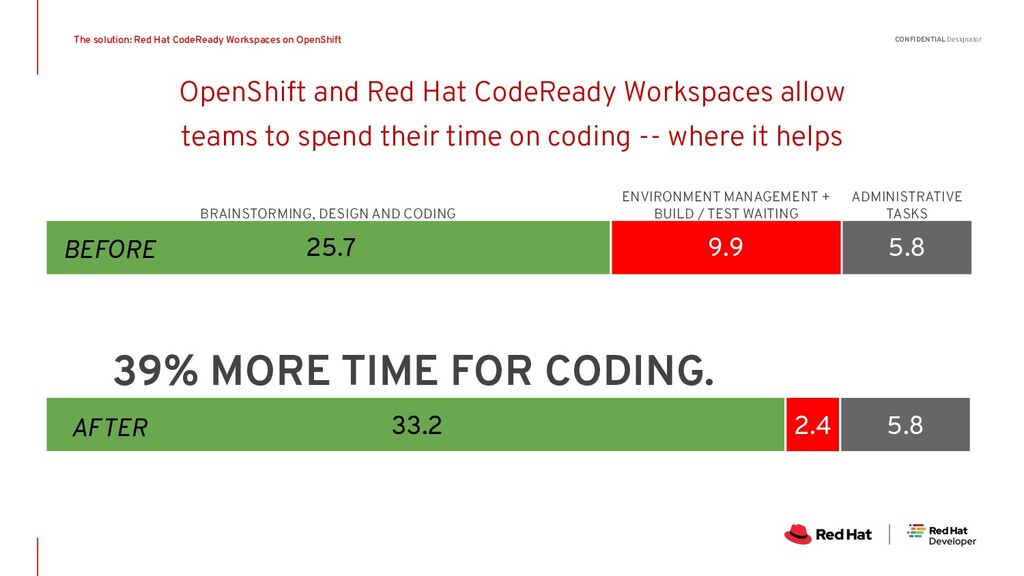
CONFIDENTIAL Designator 33.2 5.8 2.4 25.7 5.8 9.9 ENVIRONMENT MANAGEMENT
+ BUILD / TEST WAITING ADMINISTRATIVE TASKS BRAINSTORMING, DESIGN AND CODING AFTER BEFORE 39% MORE TIME FOR CODING. 2.4 OpenShift and Red Hat CodeReady Workspaces allow teams to spend their time on coding -- where it helps The solution: Red Hat CodeReady Workspaces on OpenShift -
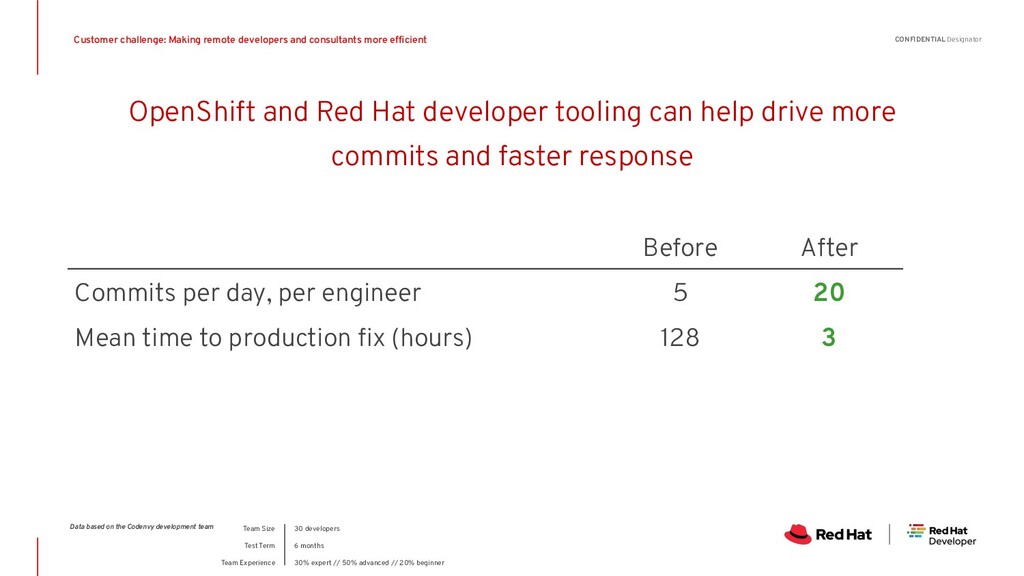
CONFIDENTIAL Designator Before After Commits per day, per engineer 5
20 Mean time to production fix (hours) 128 3 OpenShift and Red Hat developer tooling can help drive more commits and faster response Customer challenge: Making remote developers and consultants more efficient Data based on the Codenvy development team Team Size Test Term Team Experience 30 developers 6 months 30% expert // 50% advanced // 20% beginner -
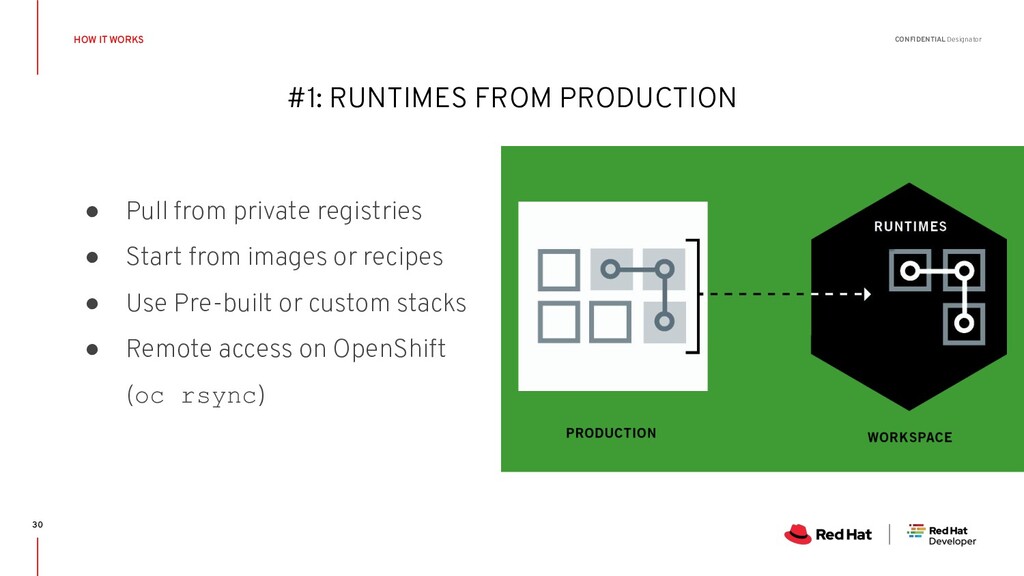
CONFIDENTIAL Designator #1: RUNTIMES FROM PRODUCTION • Pull from private
registries • Start from images or recipes • Use Pre-built or custom stacks • Remote access on OpenShift (oc rsync) HOW IT WORKS 30 -
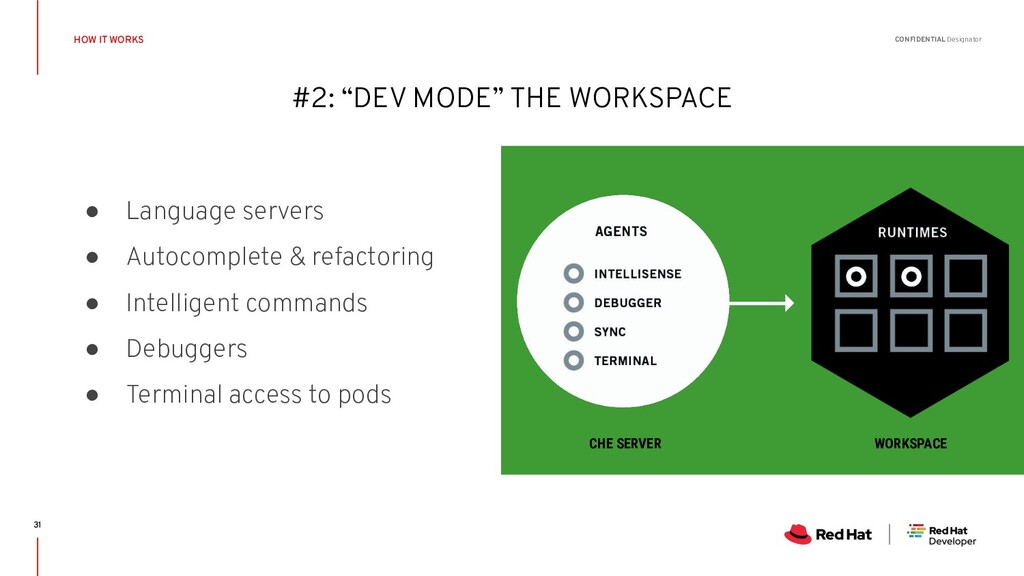
CONFIDENTIAL Designator #2: “DEV MODE” THE WORKSPACE • Language servers
• Autocomplete & refactoring • Intelligent commands • Debuggers • Terminal access to pods CHE SERVER WORKSPACE HOW IT WORKS 31 -
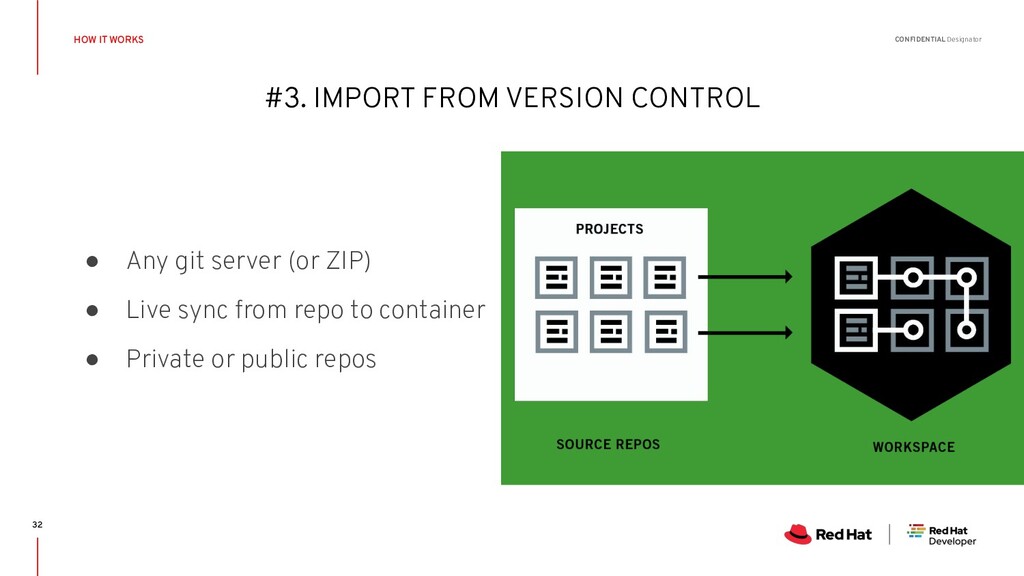
CONFIDENTIAL Designator #3. IMPORT FROM VERSION CONTROL • Any git
server (or ZIP) • Live sync from repo to container • Private or public repos HOW IT WORKS 32 -
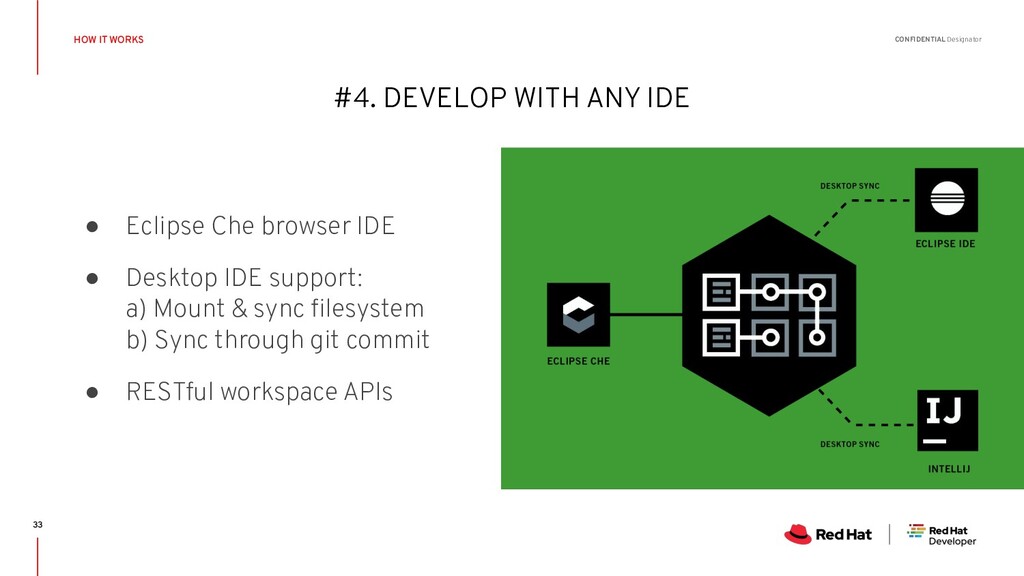
CONFIDENTIAL Designator #4. DEVELOP WITH ANY IDE • Eclipse Che
browser IDE • Desktop IDE support: a) Mount & sync filesystem b) Sync through git commit • RESTful workspace APIs HOW IT WORKS 33 -
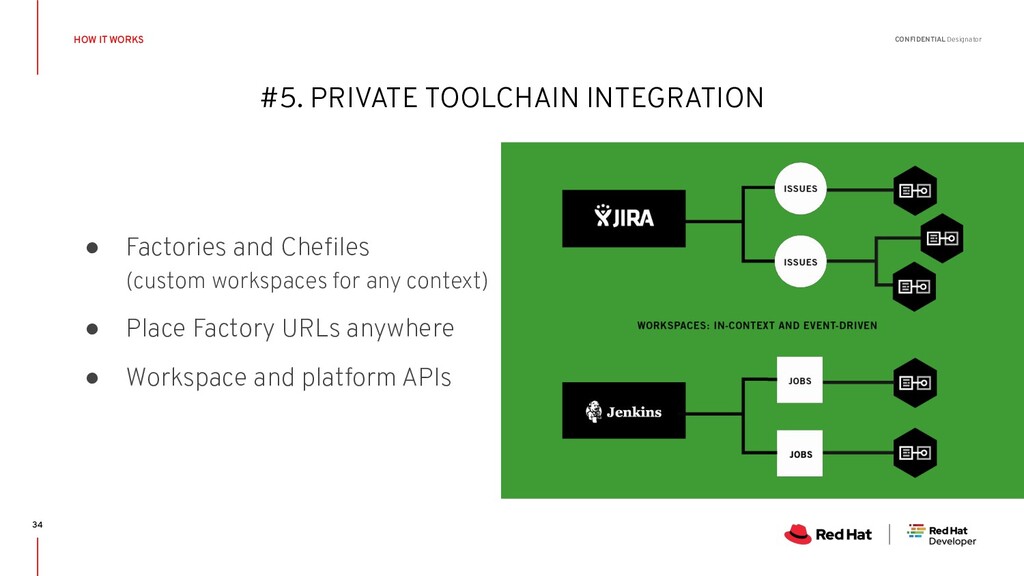
CONFIDENTIAL Designator #5. PRIVATE TOOLCHAIN INTEGRATION • Factories and Chefiles
(custom workspaces for any context) • Place Factory URLs anywhere • Workspace and platform APIs HOW IT WORKS 34 -
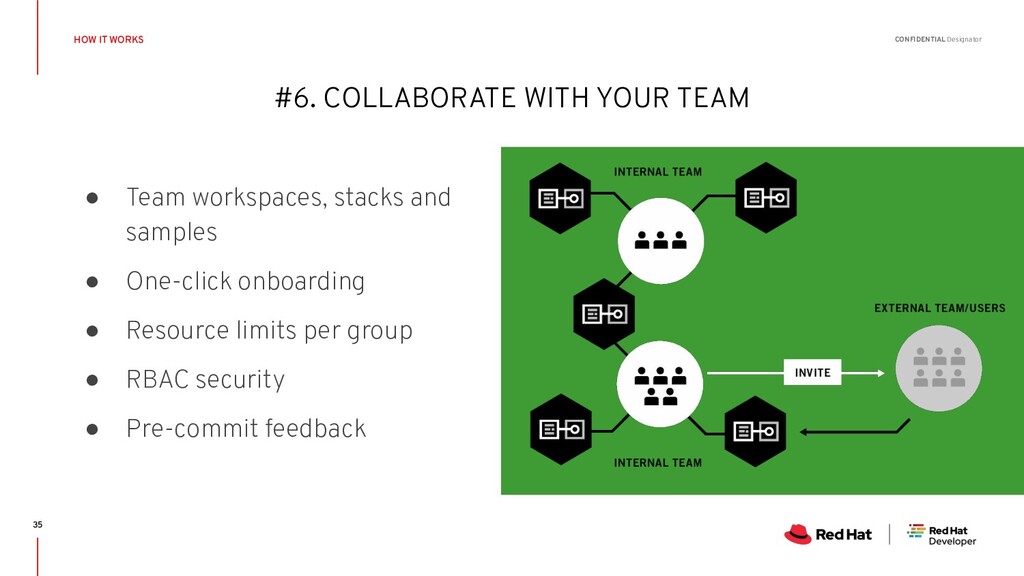
CONFIDENTIAL Designator #6. COLLABORATE WITH YOUR TEAM • Team workspaces,
stacks and samples • One-click onboarding • Resource limits per group • RBAC security • Pre-commit feedback HOW IT WORKS 35 -
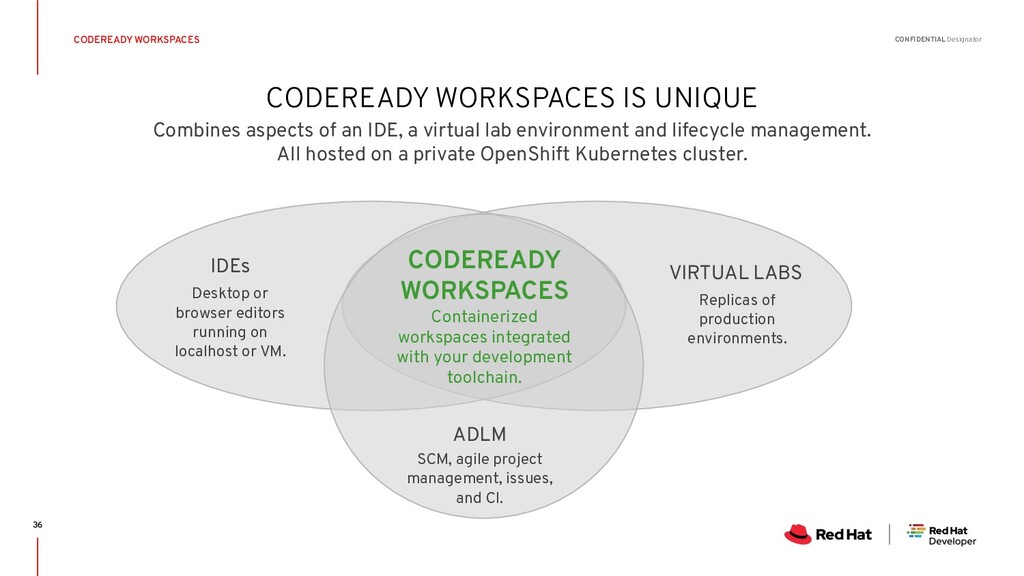
CONFIDENTIAL Designator CODEREADY WORKSPACES IS UNIQUE IDEs VIRTUAL LABS Desktop
or browser editors running on localhost or VM. Replicas of production environments. Containerized workspaces integrated with your development toolchain. ADLM CODEREADY WORKSPACES SCM, agile project management, issues, and CI. Combines aspects of an IDE, a virtual lab environment and lifecycle management. All hosted on a private OpenShift Kubernetes cluster. CODEREADY WORKSPACES 36 -
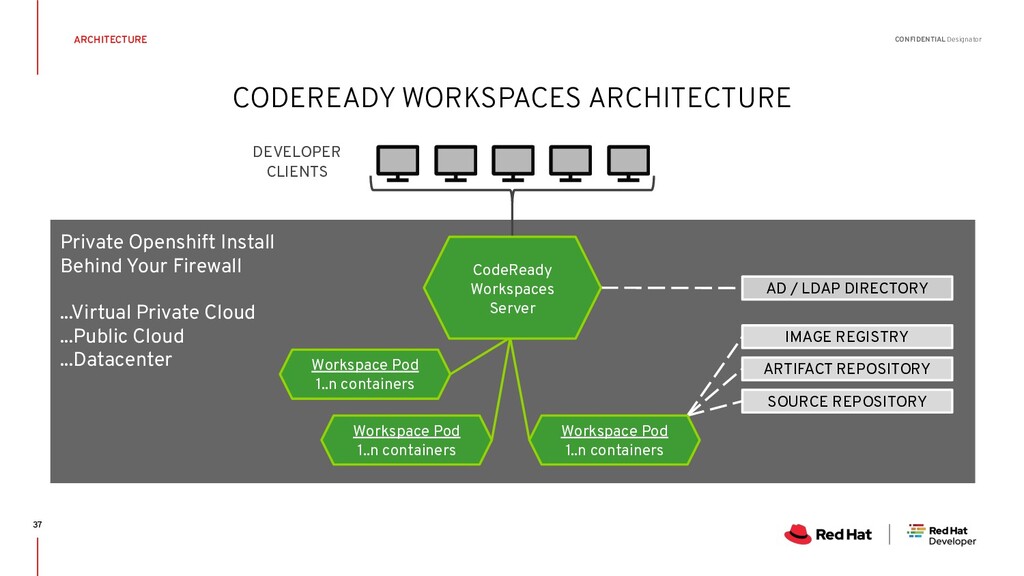
CONFIDENTIAL Designator CODEREADY WORKSPACES ARCHITECTURE Private Openshift Install Behind Your
Firewall ...Virtual Private Cloud ...Public Cloud ...Datacenter SOURCE REPOSITORY ARTIFACT REPOSITORY AD / LDAP DIRECTORY DEVELOPER CLIENTS IMAGE REGISTRY Workspace Pod 1..n containers CodeReady Workspaces Server Workspace Pod 1..n containers Workspace Pod 1..n containers ARCHITECTURE 37 -
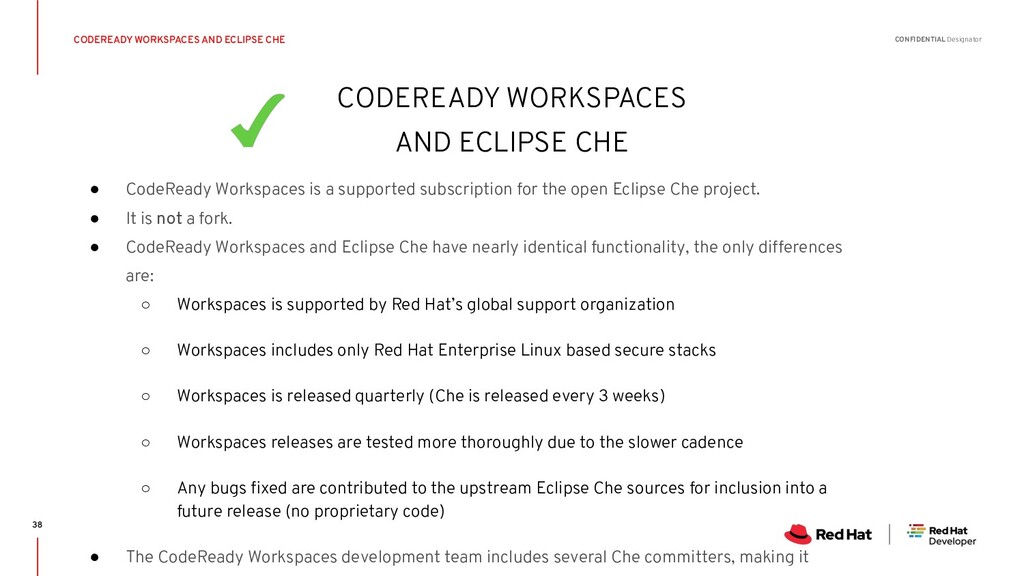
CONFIDENTIAL Designator • CodeReady Workspaces is a supported subscription for
the open Eclipse Che project. • It is not a fork. • CodeReady Workspaces and Eclipse Che have nearly identical functionality, the only differences are: ◦ Workspaces is supported by Red Hat’s global support organization ◦ Workspaces includes only Red Hat Enterprise Linux based secure stacks ◦ Workspaces is released quarterly (Che is released every 3 weeks) ◦ Workspaces releases are tested more thoroughly due to the slower cadence ◦ Any bugs fixed are contributed to the upstream Eclipse Che sources for inclusion into a future release (no proprietary code) • The CodeReady Workspaces development team includes several Che committers, making it CODEREADY WORKSPACES AND ECLIPSE CHE CODEREADY WORKSPACES AND ECLIPSE CHE 38 -
Red Hat CodeReady Workspaces makes it easy and safe for
anyone to contribute to a project - even without container or Kubernetes knowledge.
 redhatlivestreaming
 inariku
 atalie2m
 silmin_
 jcabot
 grimoh
 ryoskdara_
 nejumi
 ota1022
 lycorptech_jp
 jackojacko_
 pipepasta
 iwamot
 szymonslowik
 sstephenson
 varn
 chriscoyier
 aleyda
 kristinabergwall1
 frankvandijk
 deanohume
 sarafernandez
 brad_frost
 baasie
 rkendrick25