Share
Embed
Living the 'JetSec Lifestyle'
In this talk we will look at the Jetpack Security (JetSec) libraries, the common mobile security problems they solve, how they work and the functionality they offer to developers in code
Ed Holloway-George
June 02, 2023
Transcript
53 slides
-
@sp4ghetticode / spght.dev Living the “JetSec Lifestyle” 🏖 Ed Holloway-George
@ Android Meetup - June 2023 -
@sp4ghetticode / spght.dev Who am I? • Lead Android Dev
@ ASOS • Android Google Dev Expert • I like to talk about mobile security a lot • Available on all good social media platforms (inc. Tw*tter) • More talks @ spght.dev Introduction -
@sp4ghetticode / spght.dev Retrofit Hilt Koin Timber Leak Canary Accompanist
Paparazzi ActionBar Sherlock Ktor Appyx Glide Coil Mockk SQLDelight What is your favourite Android library? -
@sp4ghetticode / spght.dev - Most Android Developers, 2023 “Mobile security
is hard & easy to get wrong” -
@sp4ghetticode / spght.dev Jetpack Security JetSec solves this • Simple
use libraries • Follows security best practises • Addresses common mobile security use-cases What is it? -
@sp4ghetticode / spght.dev Jetpack Security What is it? Suite of
security related libraries: • security-crypto • security-app-authenticator • security-identity-credential -
@sp4ghetticode / spght.dev Jetpack Security What is it? Suite of
security related libraries: • security-crypto - stable and ktx available • security-app-authenticator - alpha • security-identity-credential - alpha -
@sp4ghetticode / spght.dev Jetpack Security security-crypto library What is it
trying to solve? • OWASP Mobile Top 10 - #2 Insecure Data Storage • SharedPreferences by default are insecure • Stored in plaintext • XML file has known location /data/data/<package_name>/shared_prefs • Also trivial exploits exist to access production app’s prefs More details: • “Don’t get stung by OWASP” @ spght.dev/talks • “Unpacking Android Security: Part 2” @ spght.dev/archive -
@sp4ghetticode / spght.dev Jetpack Security security-crypto library • EncryptedSharedPreferences •
Wraps the existing SharedPreferences API • Keys and Values encrypted using AES-256 • EncryptedFile • Secure impl of FileInputStream / FileOutputStream -
@sp4ghetticode / spght.dev Jetpack Security security-crypto library Who should use
this? • Banking/FinTech Apps • Medical Apps • Chat Apps • Basically anything regulated • Or anyone misusing SharedPreferences… (No PII please) -
@sp4ghetticode / spght.dev Jetpack Security security-crypto library • How does
it work? • Uses Tink under the hood • Helps to provide a simple API to perform cryptography correctly • Keyset: Key to encrypt data stored in SharedPreferences/File • Master Key: Encrypts all keysets • Utilises the Android Keystore system • Secure storage of crypto keys • Has options for hardware key storage (if available), time-bound keys and more… -
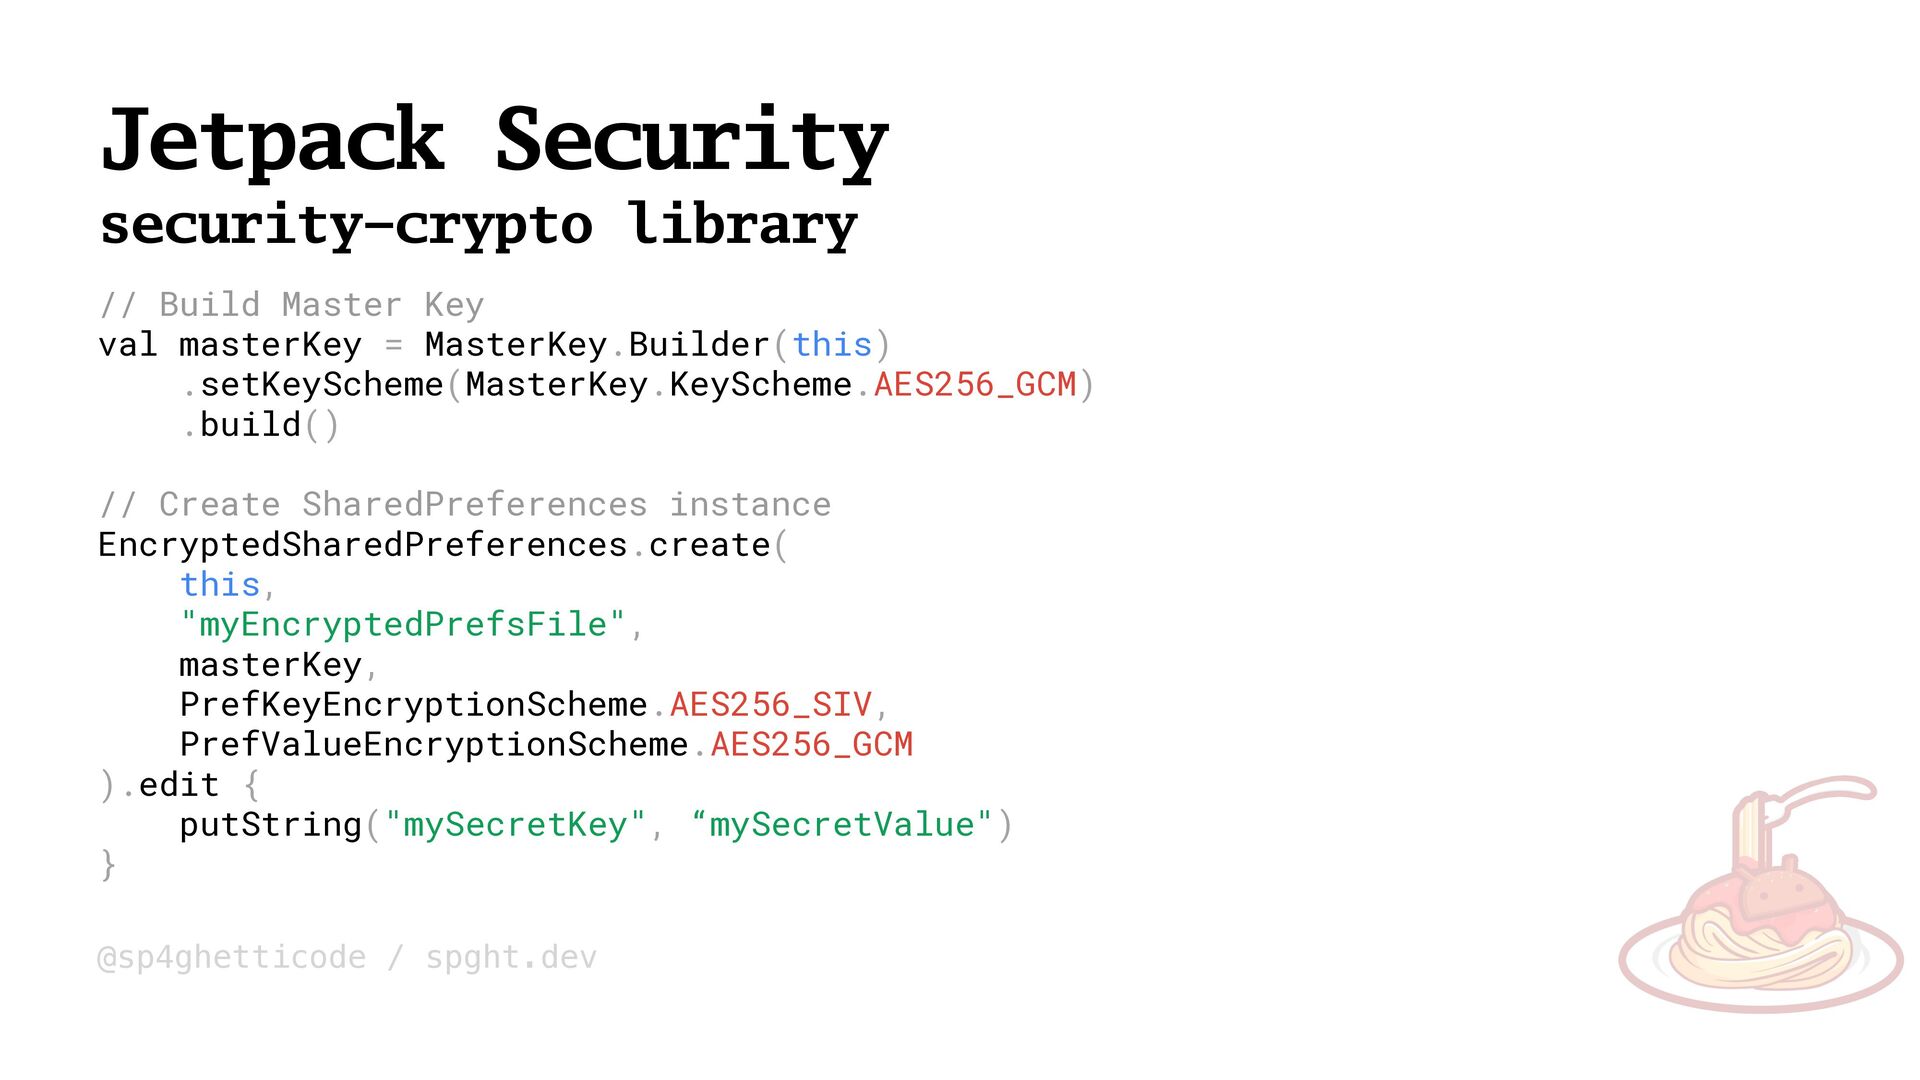
@sp4ghetticode / spght.dev Jetpack Security security-crypto library // Build Master
Key val masterKey = MasterKey.Builder(this) .setKeyScheme(MasterKey.KeyScheme.AES256_GCM) .build() // Create SharedPreferences instance EncryptedSharedPreferences.create( this, "myEncryptedPrefsFile", masterKey, PrefKeyEncryptionScheme.AES256_SIV, PrefValueEncryptionScheme.AES256_GCM ).edit { putString("mySecretKey", “mySecretValue") } -
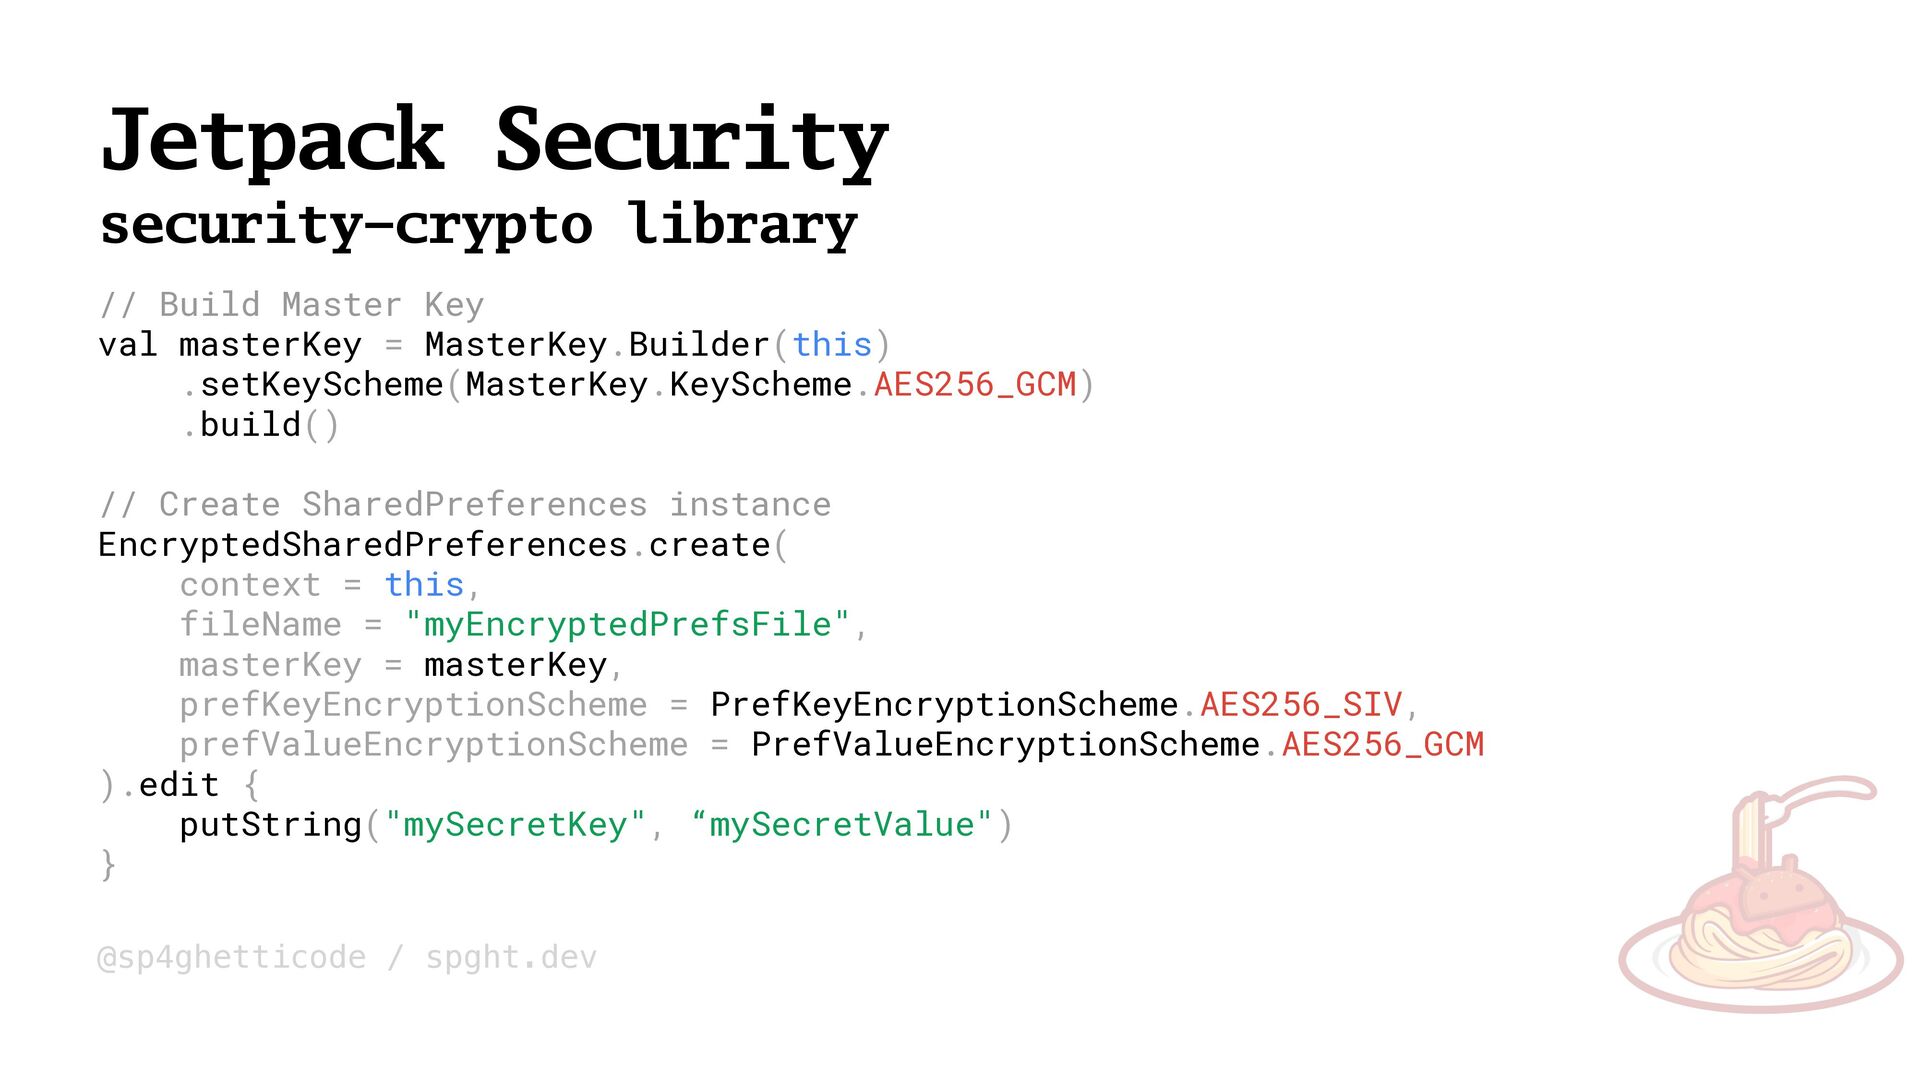
@sp4ghetticode / spght.dev Jetpack Security security-crypto library // Build Master
Key val masterKey = MasterKey.Builder(this) .setKeyScheme(MasterKey.KeyScheme.AES256_GCM) .build() // Create SharedPreferences instance EncryptedSharedPreferences.create( context = this, fileName = "myEncryptedPrefsFile", masterKey = masterKey, prefKeyEncryptionScheme = PrefKeyEncryptionScheme.AES256_SIV, prefValueEncryptionScheme = PrefValueEncryptionScheme.AES256_GCM ).edit { putString("mySecretKey", “mySecretValue") } -
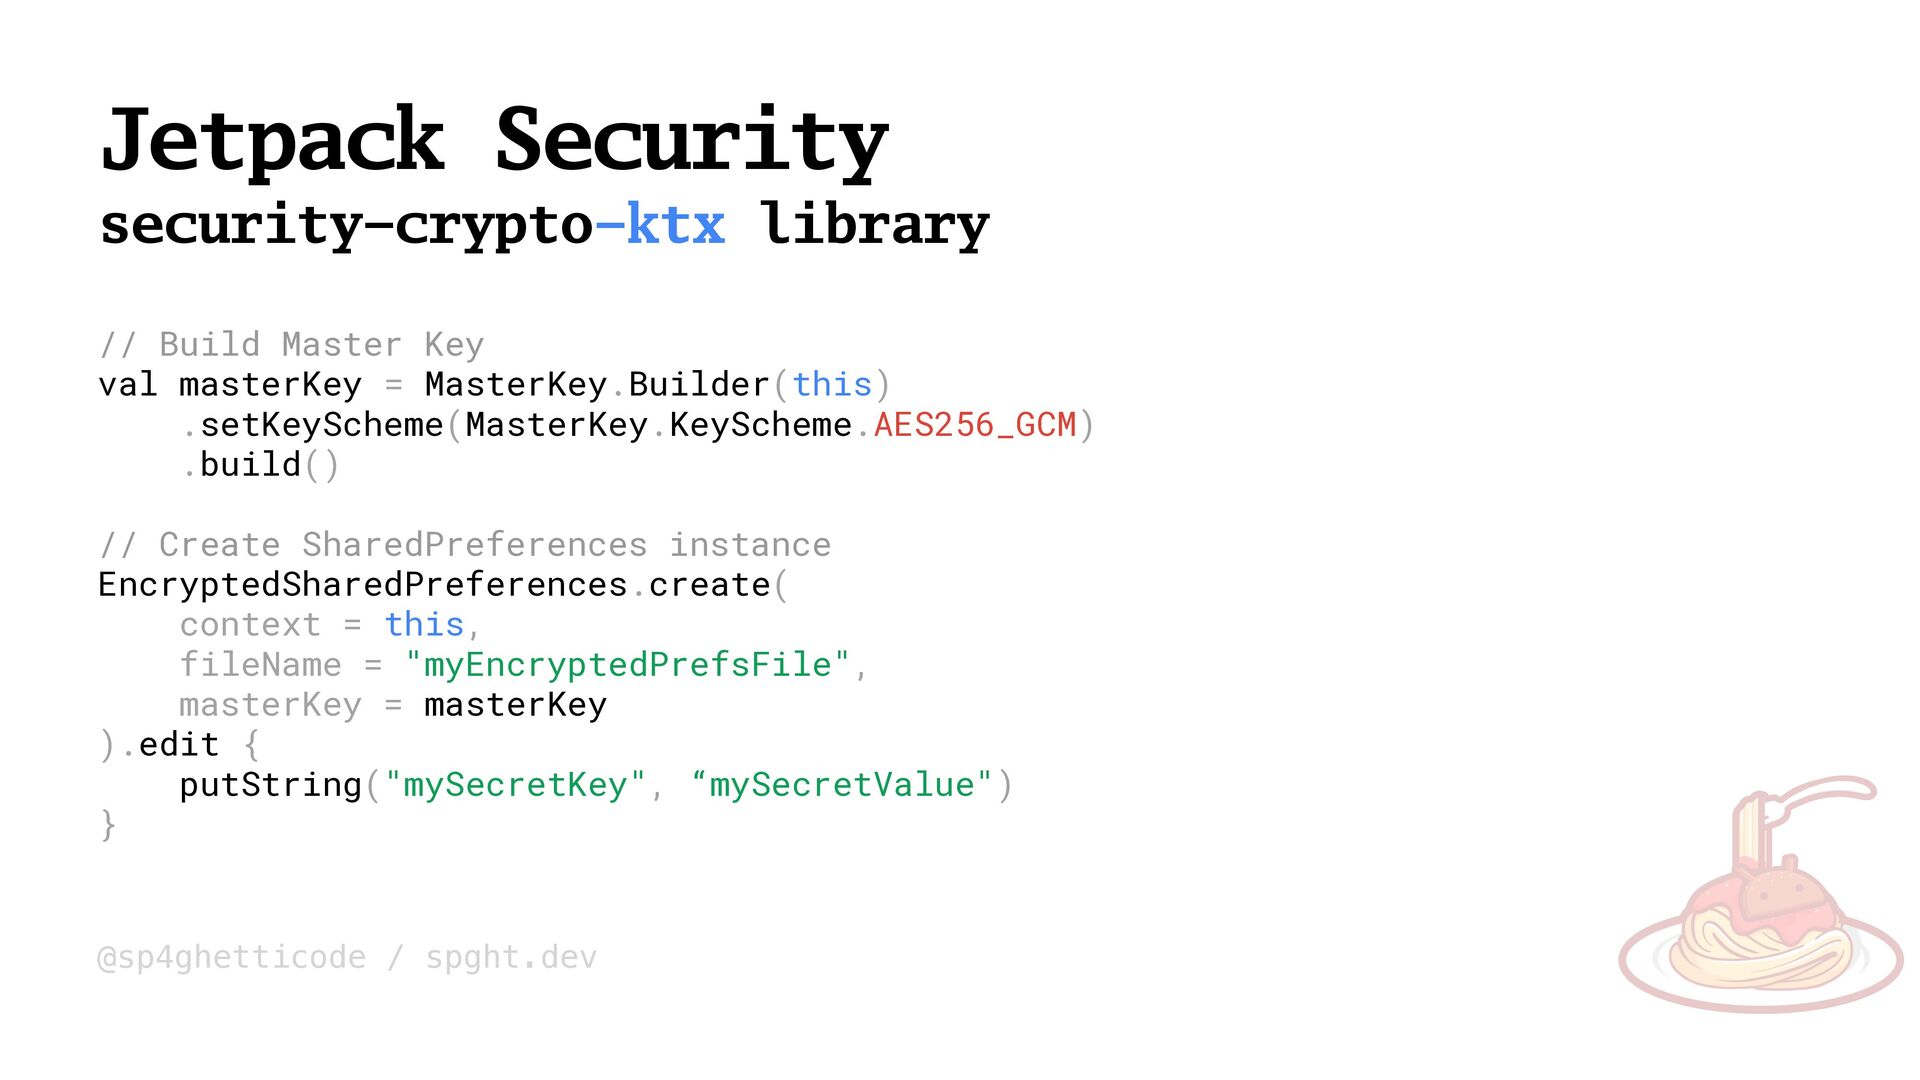
@sp4ghetticode / spght.dev Jetpack Security security-crypto-ktx library // Build Master
Key val masterKey = MasterKey.Builder(this) .setKeyScheme(MasterKey.KeyScheme.AES256_GCM) .build() // Create SharedPreferences instance EncryptedSharedPreferences.create( context = this, fileName = "myEncryptedPrefsFile", masterKey = masterKey ).edit { putString("mySecretKey", “mySecretValue") } -
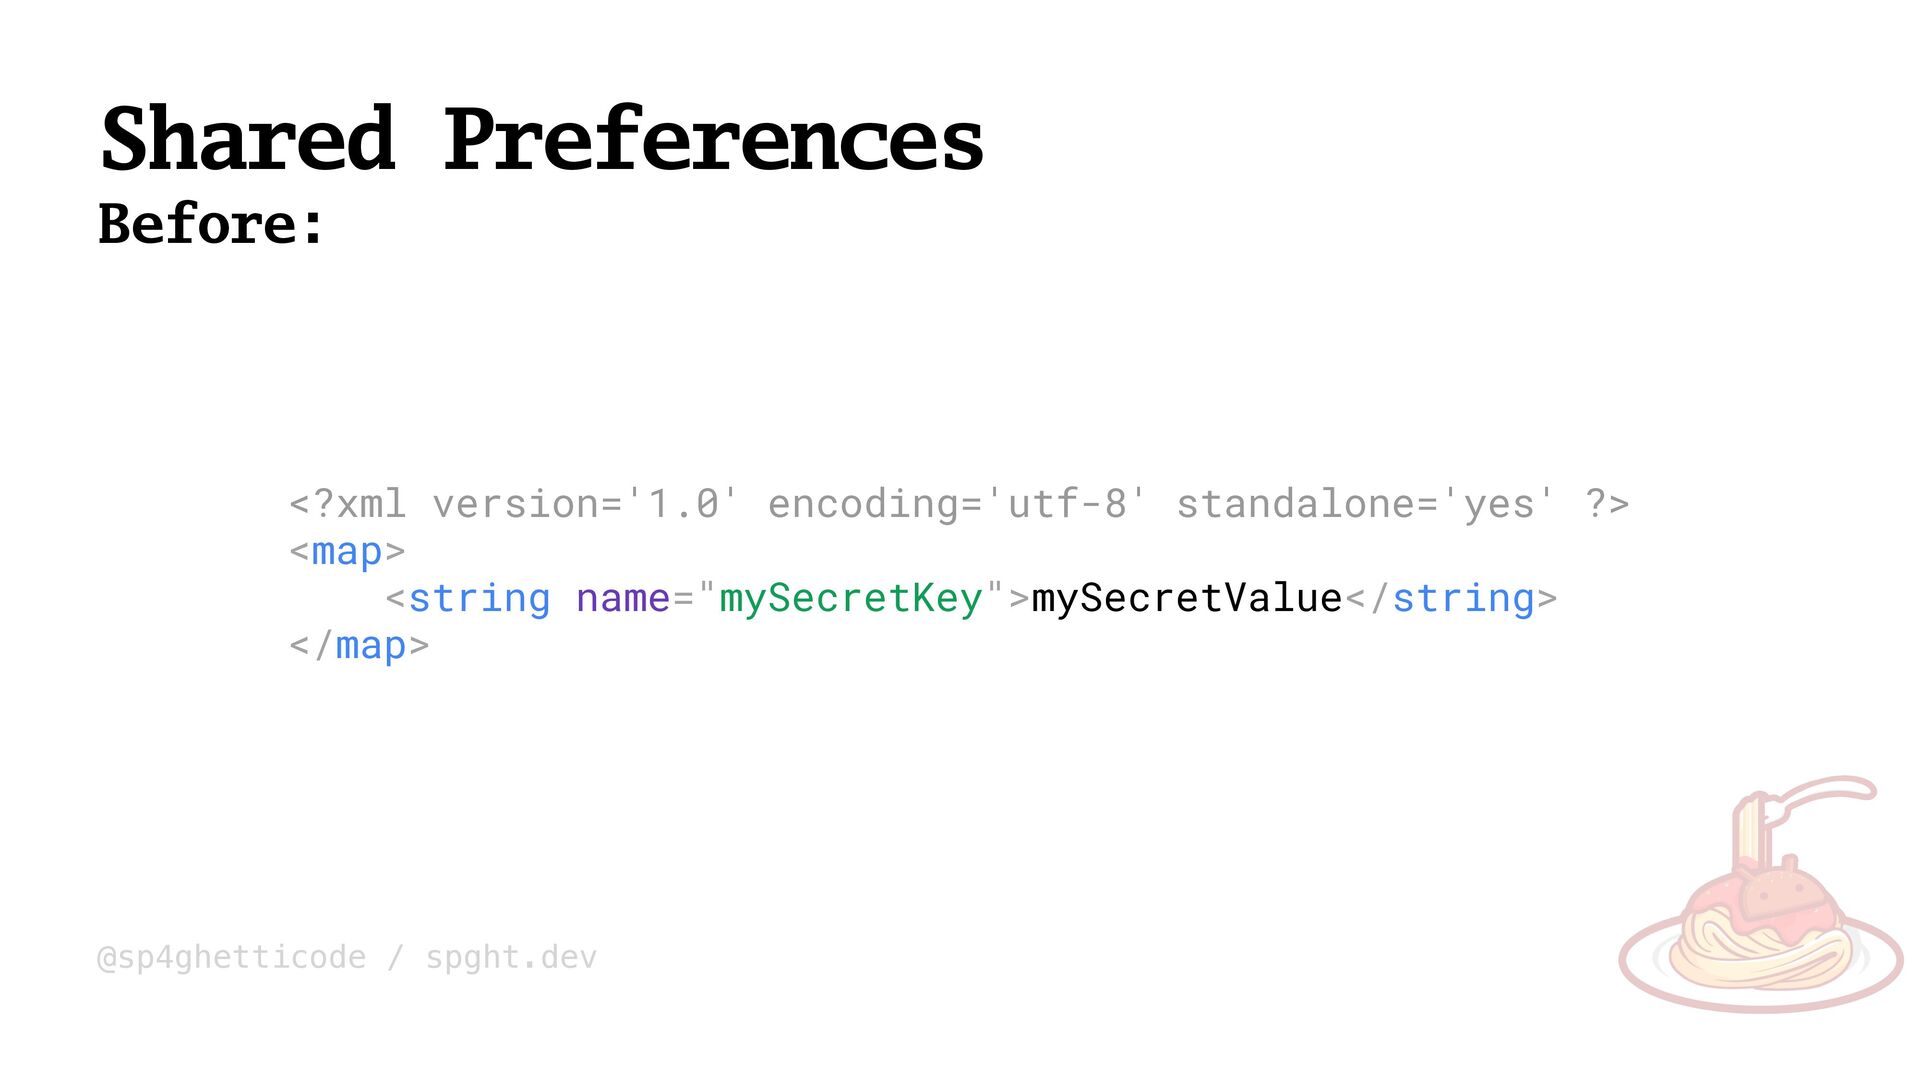
@sp4ghetticode / spght.dev Shared Preferences Before: <?xml version='1.0' encoding='utf-8' standalone='yes'
?> <map> <string name="mySecretKey">mySecretValue</string> </map> -
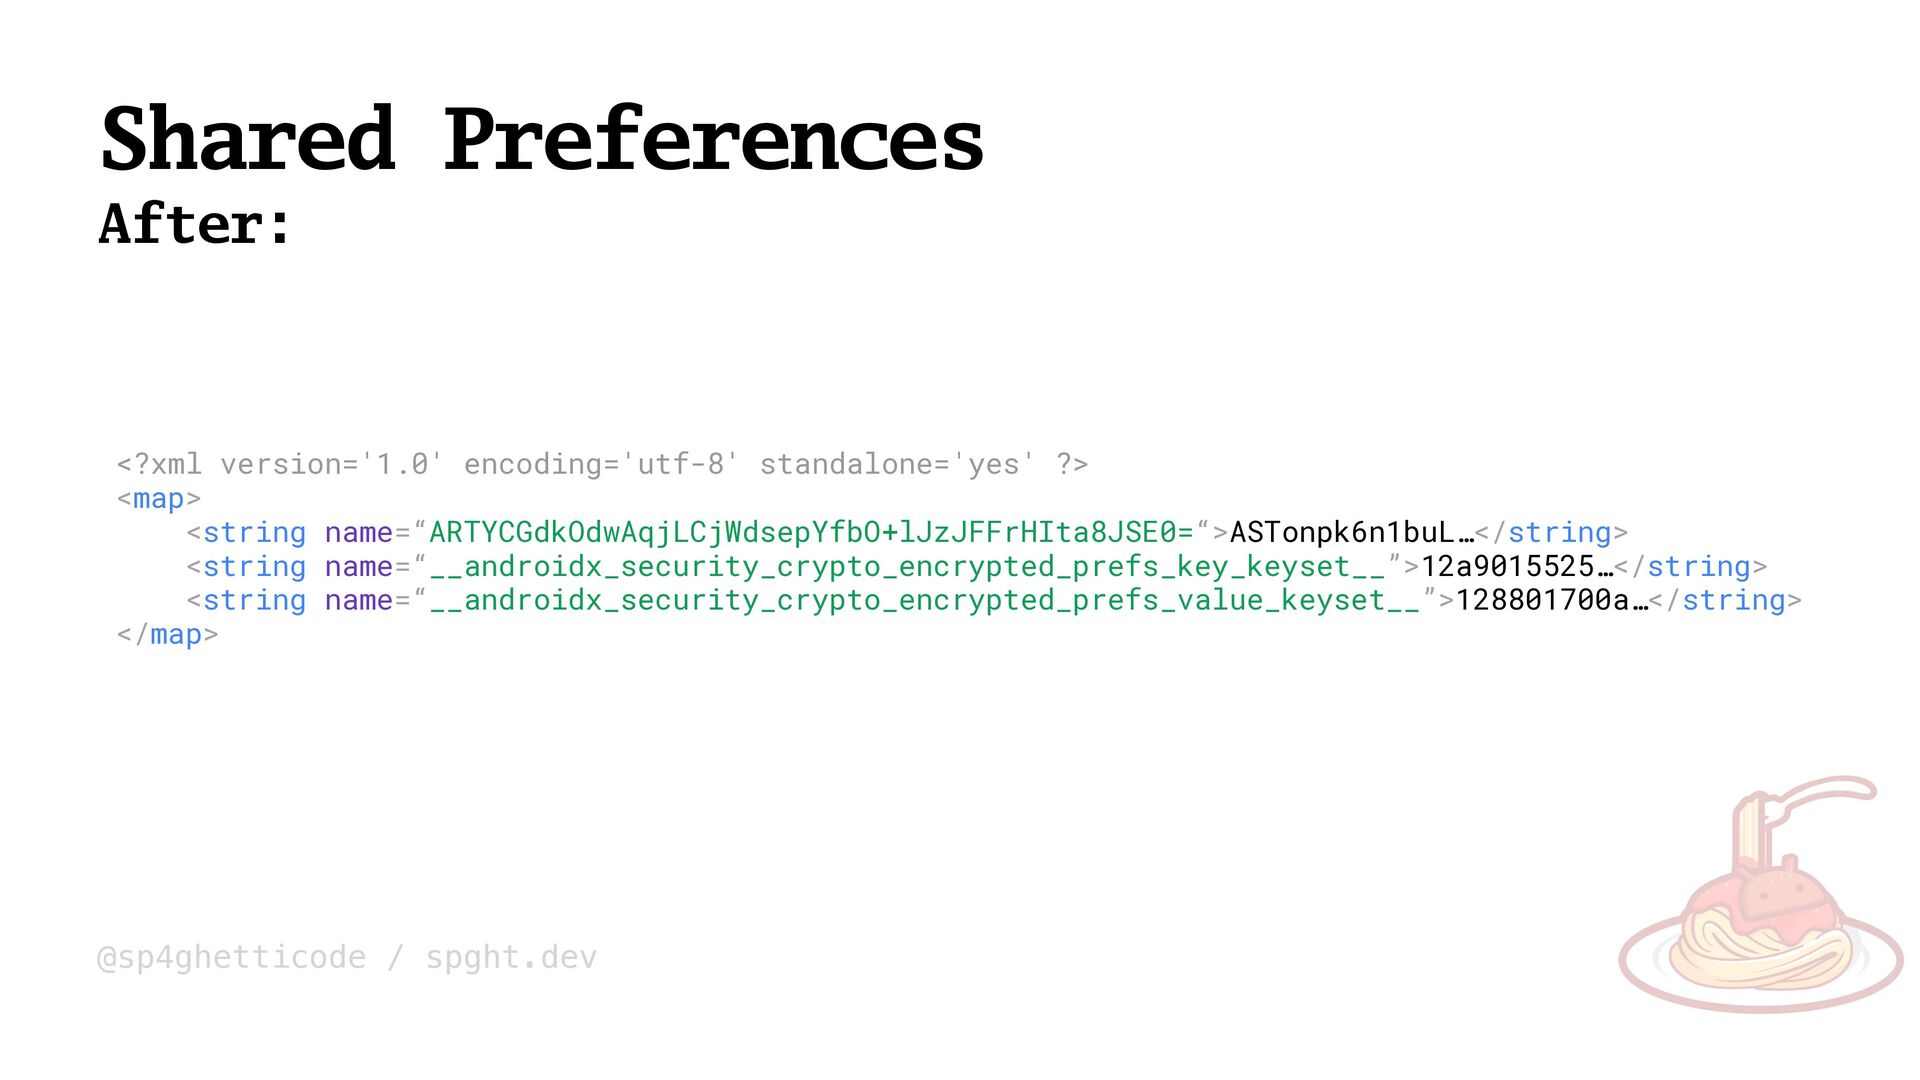
@sp4ghetticode / spght.dev Shared Preferences After: <?xml version='1.0' encoding='utf-8' standalone='yes'
?> <map> <string name=“ARTYCGdkOdwAqjLCjWdsepYfbO+lJzJFFrHIta8JSE0=“>ASTonpk6n1buL…</string> <string name=“__androidx_security_crypto_encrypted_prefs_key_keyset__”>12a9015525…</string> <string name=“__androidx_security_crypto_encrypted_prefs_value_keyset__”>128801700a…</string> </map> -
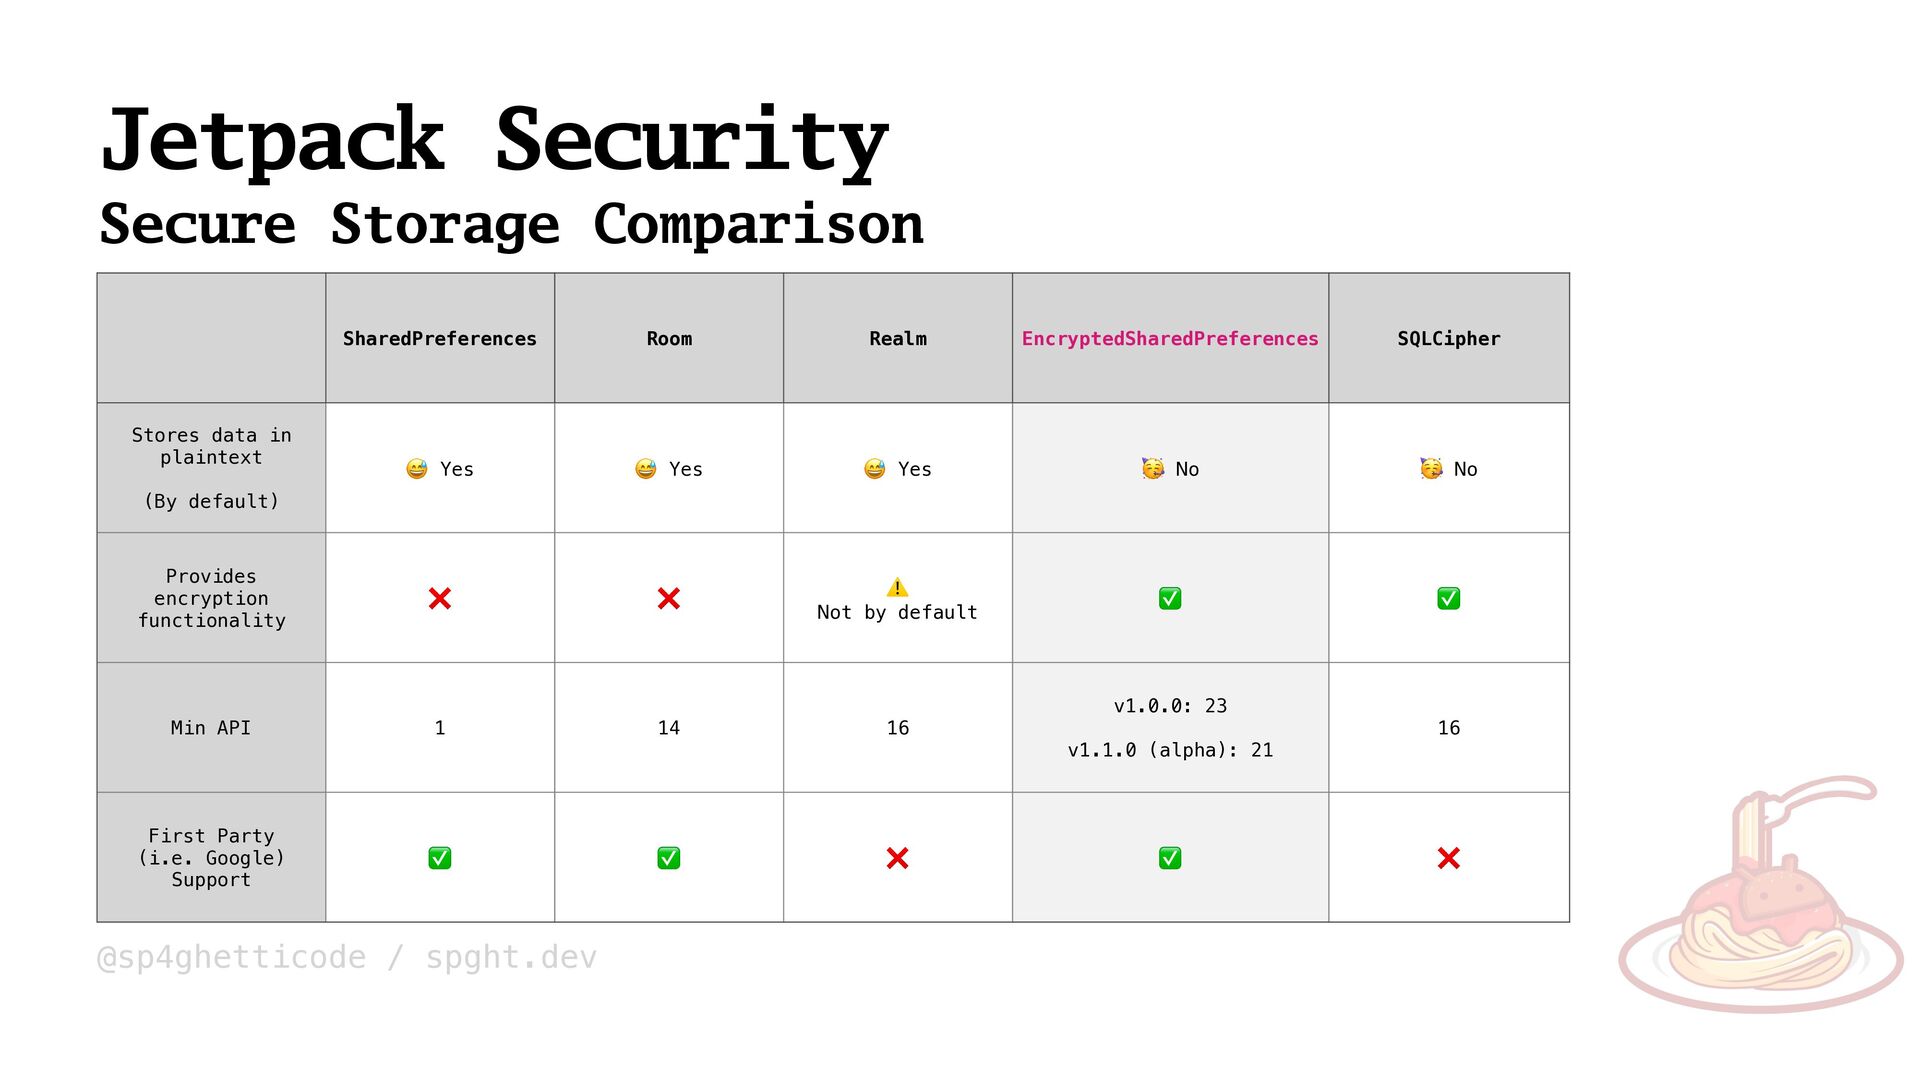
@sp4ghetticode / spght.dev Jetpack Security Secure Storage Comparison SharedPreferences Room
Realm EncryptedSharedPreferences SQLCipher Stores data in plaintext (By default) 😅 Yes 😅 Yes 😅 Yes 🥳 No 🥳 No Provides encryption functionality ❌ ❌ ⚠ Not by default ✅ ✅ Min API 1 14 16 v1.0.0: 23 v1.1.0 (alpha): 21 16 First Party (i.e. Google) Support ✅ ✅ ❌ ✅ ❌ -
@sp4ghetticode / spght.dev Jetpack Security security-app-authenticator library What is it
trying to solve? • OWASP Mobile Top 10 - #8 Code Tampering • We sometimes need to verify an app via its signing identity • i.e. How can we ensure an app hasn’t been modified? • How do we verify the identity of a calling process during IPC? More details: • “Don’t get stung by OWASP - Part 2” @ spght.dev/talks -
@sp4ghetticode / spght.dev Jetpack Security security-app-authenticator library • AppAuthenticator •
Able to verify an app on device • Consumes an application package name and SHA-256 hash • Returns SIGNATURE_MATCH or SIGNATURE_NOT_MATCH • SHA-256 can supplied via XML resource or input stream -
@sp4ghetticode / spght.dev Jetpack Security security-app-authenticator library Who should use
this? • Similar apps to security-crypto • Banking/FinTech • Any app particularly targeted by hackers 😈 • Maybe all of us! It’s easy to setup… -
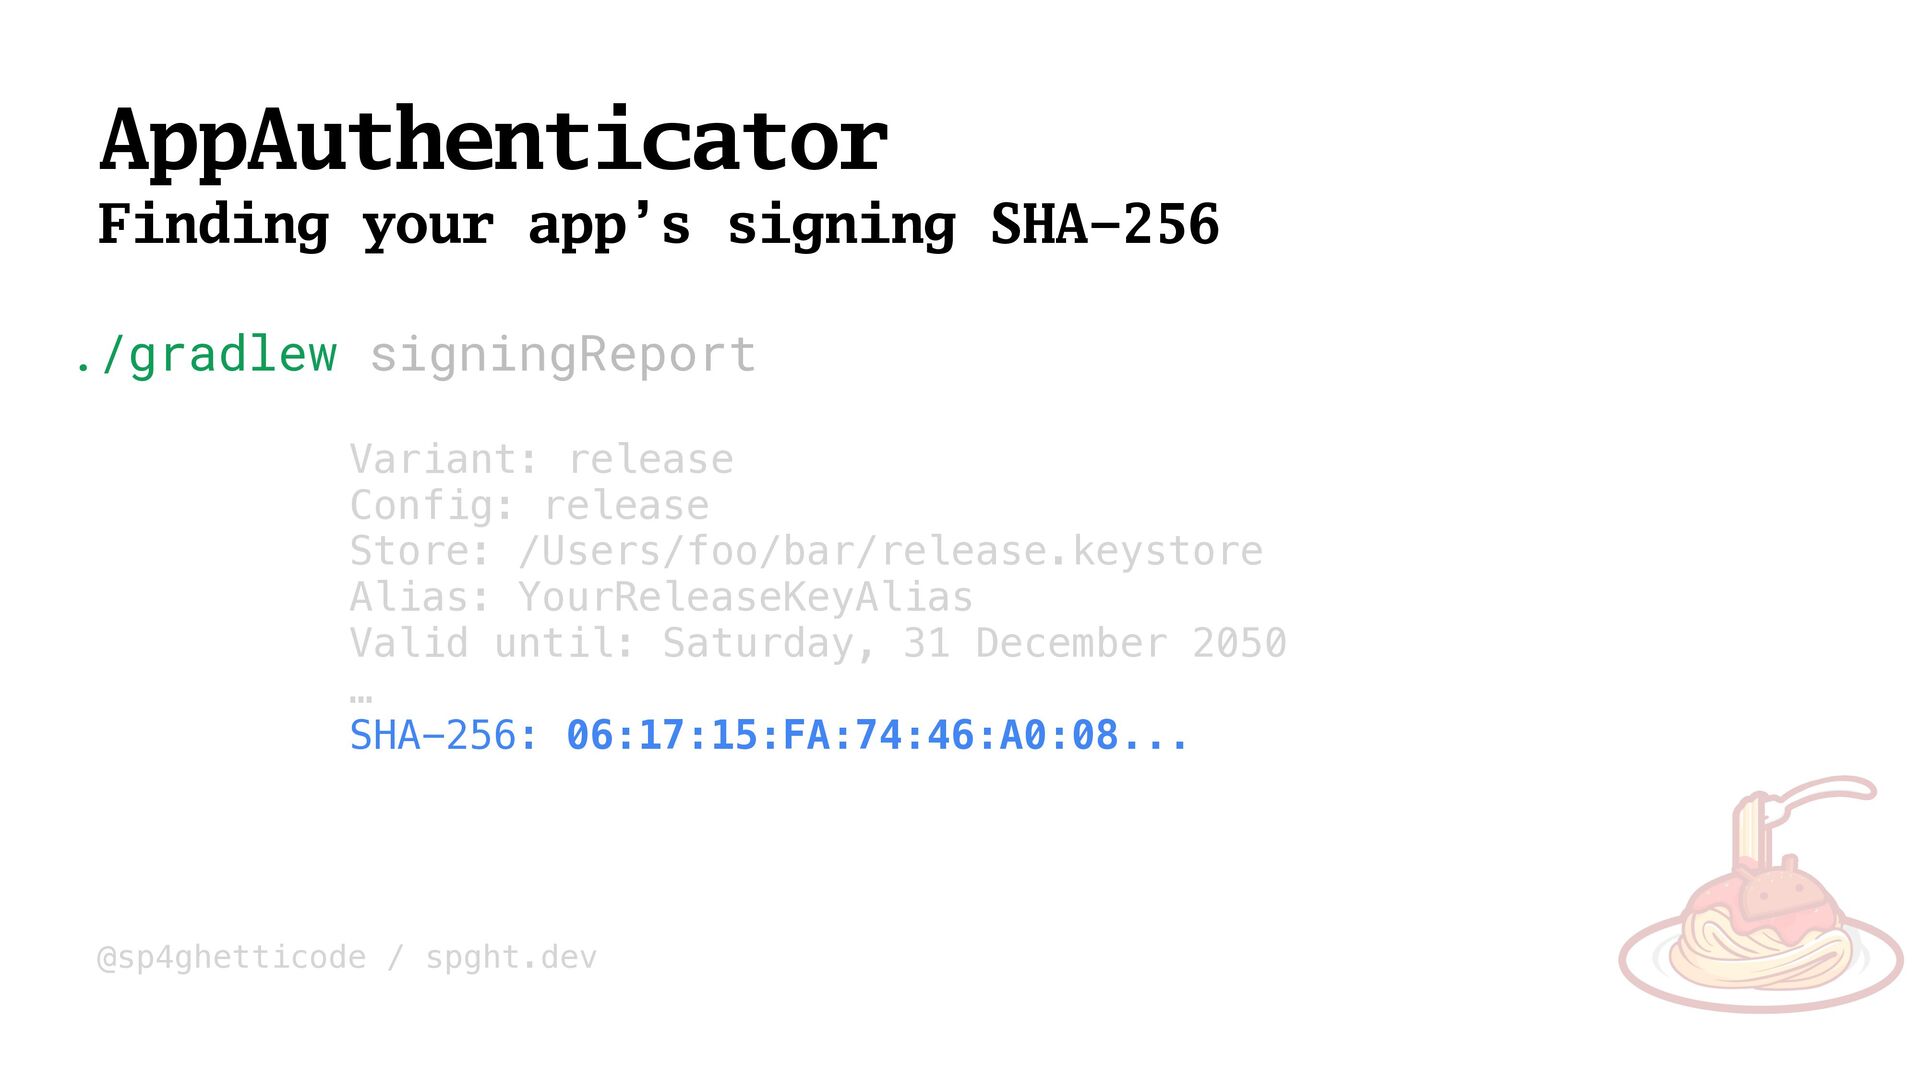
@sp4ghetticode / spght.dev AppAuthenticator Finding your app’s signing SHA-256 ./gradlew
signingReport Variant: release Config: release Store: /Users/foo/bar/release.keystore Alias: YourReleaseKeyAlias Valid until: Saturday, 31 December 2050 … SHA-256: 06:17:15:FA:74:46:A0:08... -
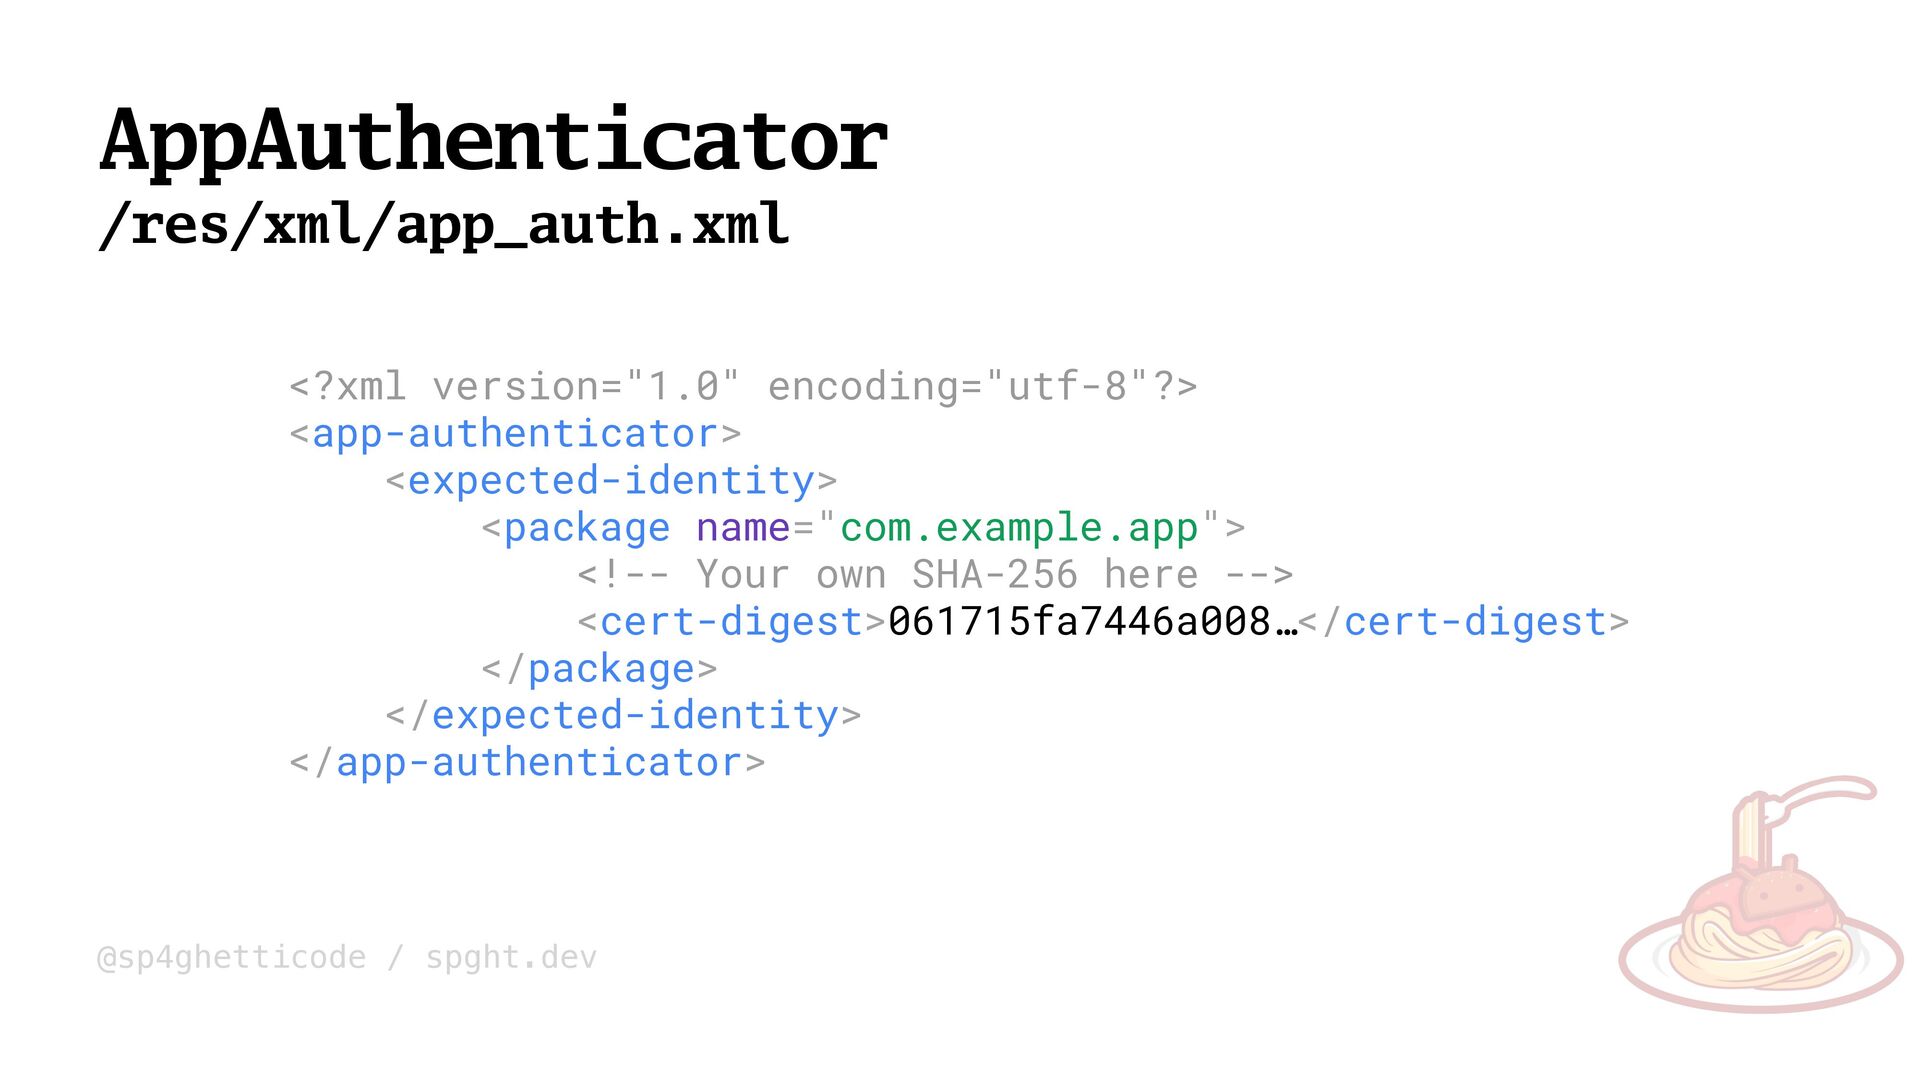
@sp4ghetticode / spght.dev AppAuthenticator /res/xml/app_auth.xml <?xml version="1.0" encoding="utf-8"?> <app-authenticator> <expected-identity>
<package name="com.example.app"> <!-- Your own SHA-256 here --> <cert-digest>061715fa7446a008…</cert-digest> </package> </expected-identity> </app-authenticator> -
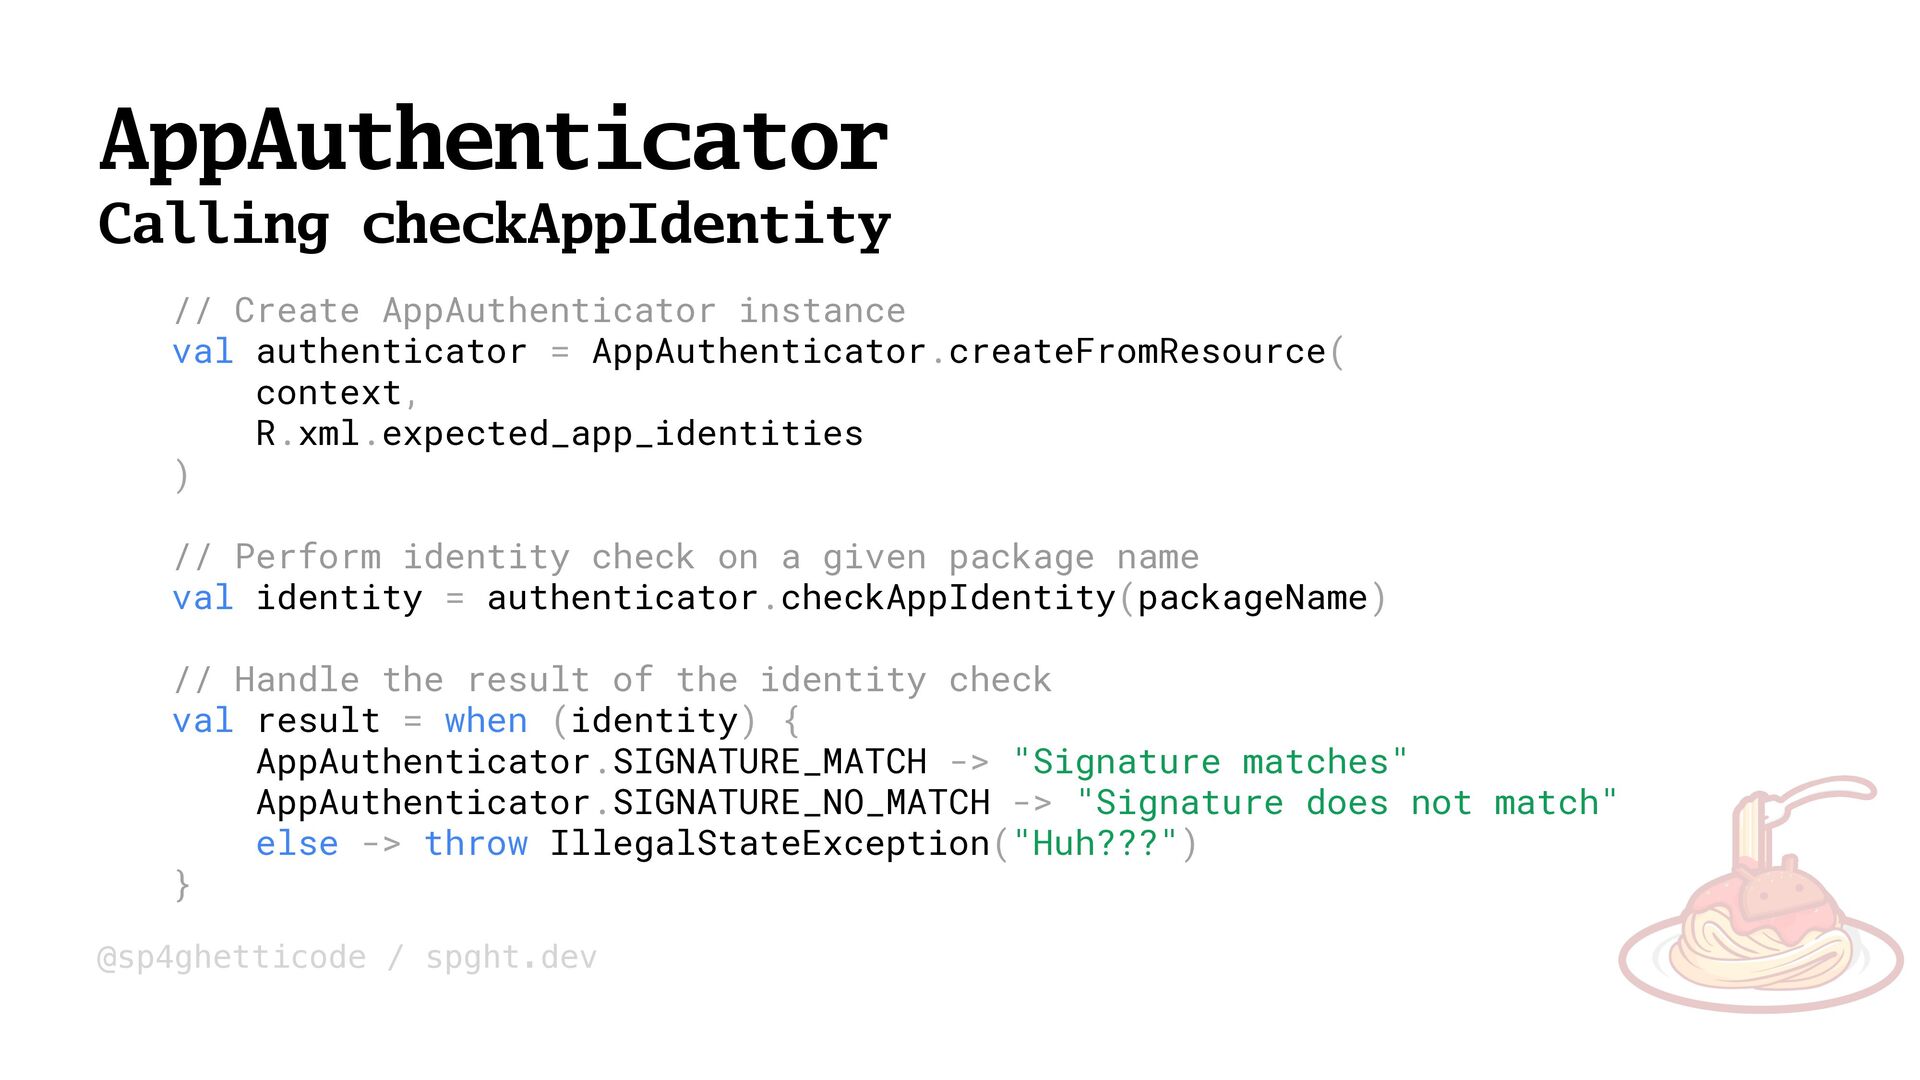
@sp4ghetticode / spght.dev AppAuthenticator Calling checkAppIdentity // Create AppAuthenticator instance
val authenticator = AppAuthenticator.createFromResource( context, R.xml.expected_app_identities ) // Perform identity check on a given package name val identity = authenticator.checkAppIdentity(packageName) // Handle the result of the identity check val result = when (identity) { AppAuthenticator.SIGNATURE_MATCH -> "Signature matches" AppAuthenticator.SIGNATURE_NO_MATCH -> "Signature does not match" else -> throw IllegalStateException("Huh???") } -
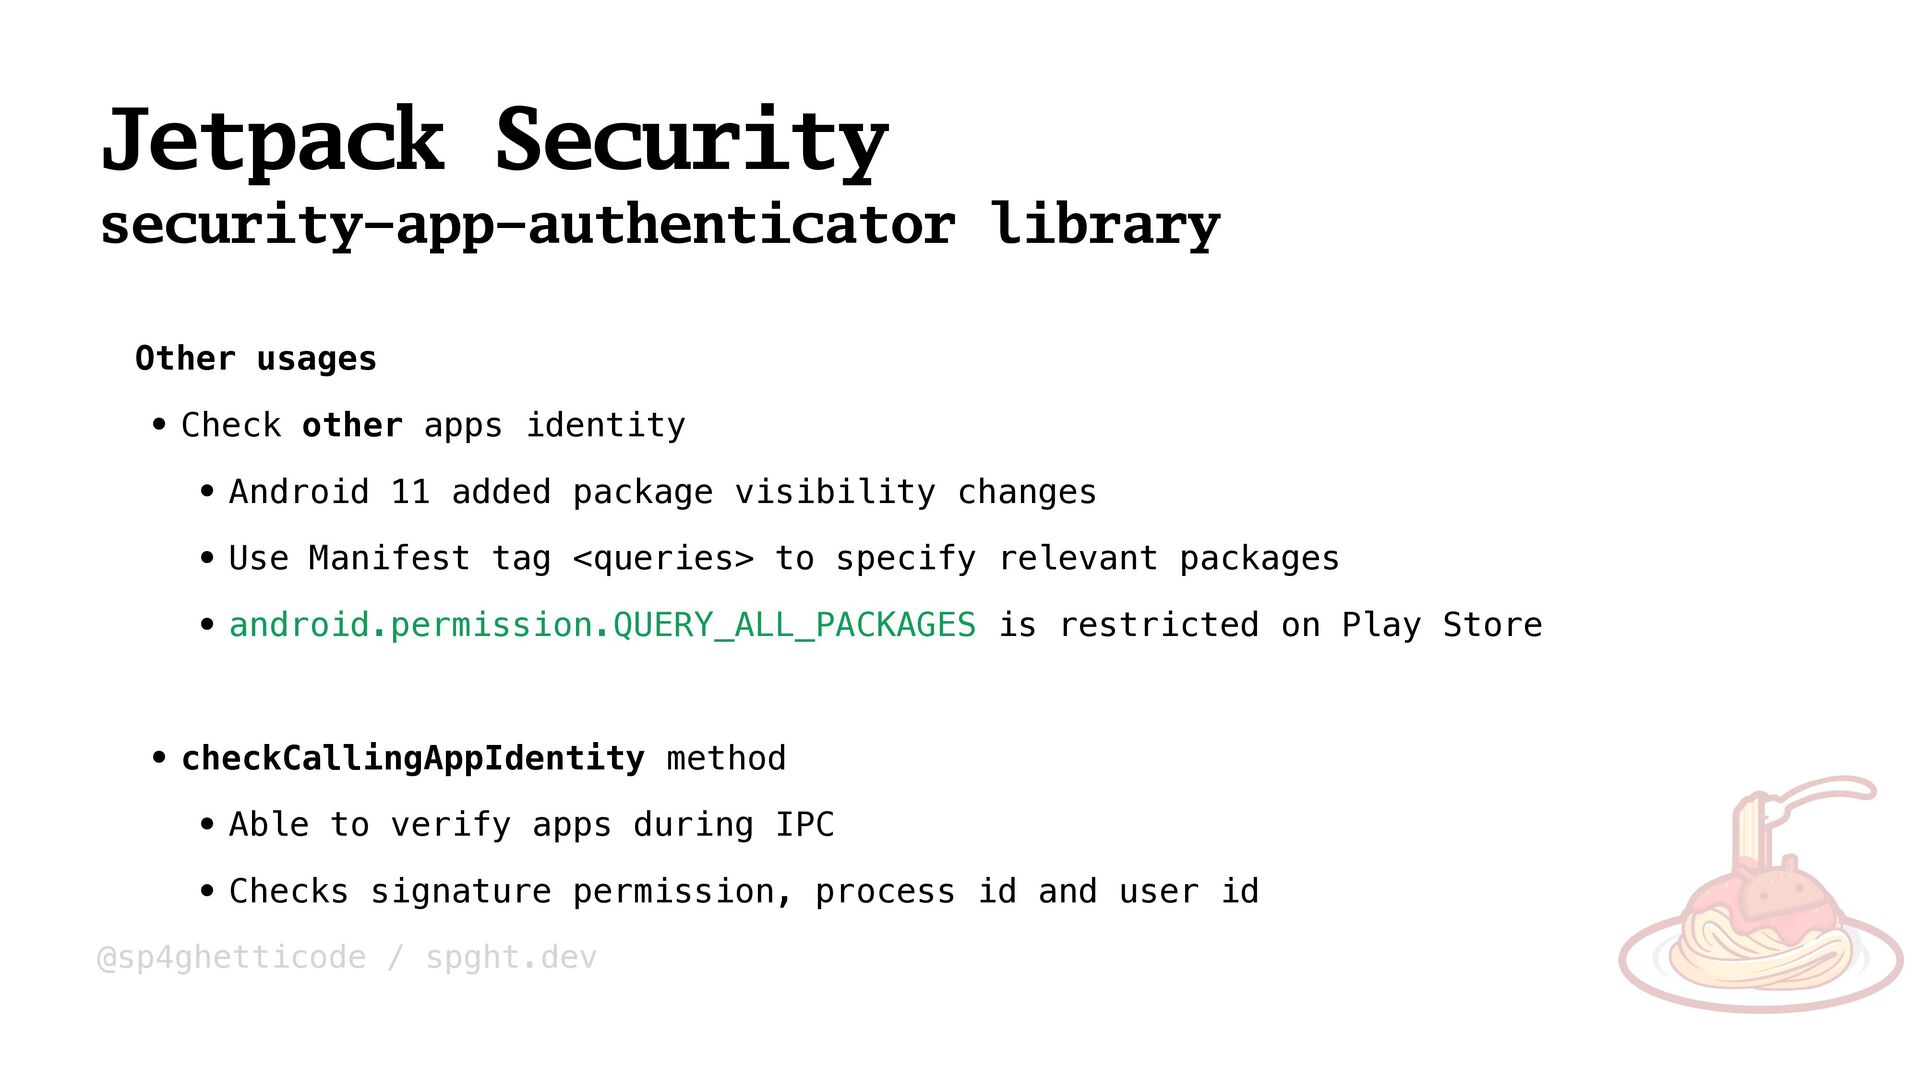
@sp4ghetticode / spght.dev Jetpack Security security-app-authenticator library Other usages •
Check other apps identity • Android 11 added package visibility changes • Use Manifest tag <queries> to specify relevant packages • android.permission.QUERY_ALL_PACKAGES is restricted on Play Store • checkCallingAppIdentity method • Able to verify apps during IPC • Checks signature permission, process id and user id -
@sp4ghetticode / spght.dev Jetpack Security security-identity-credential library What is it
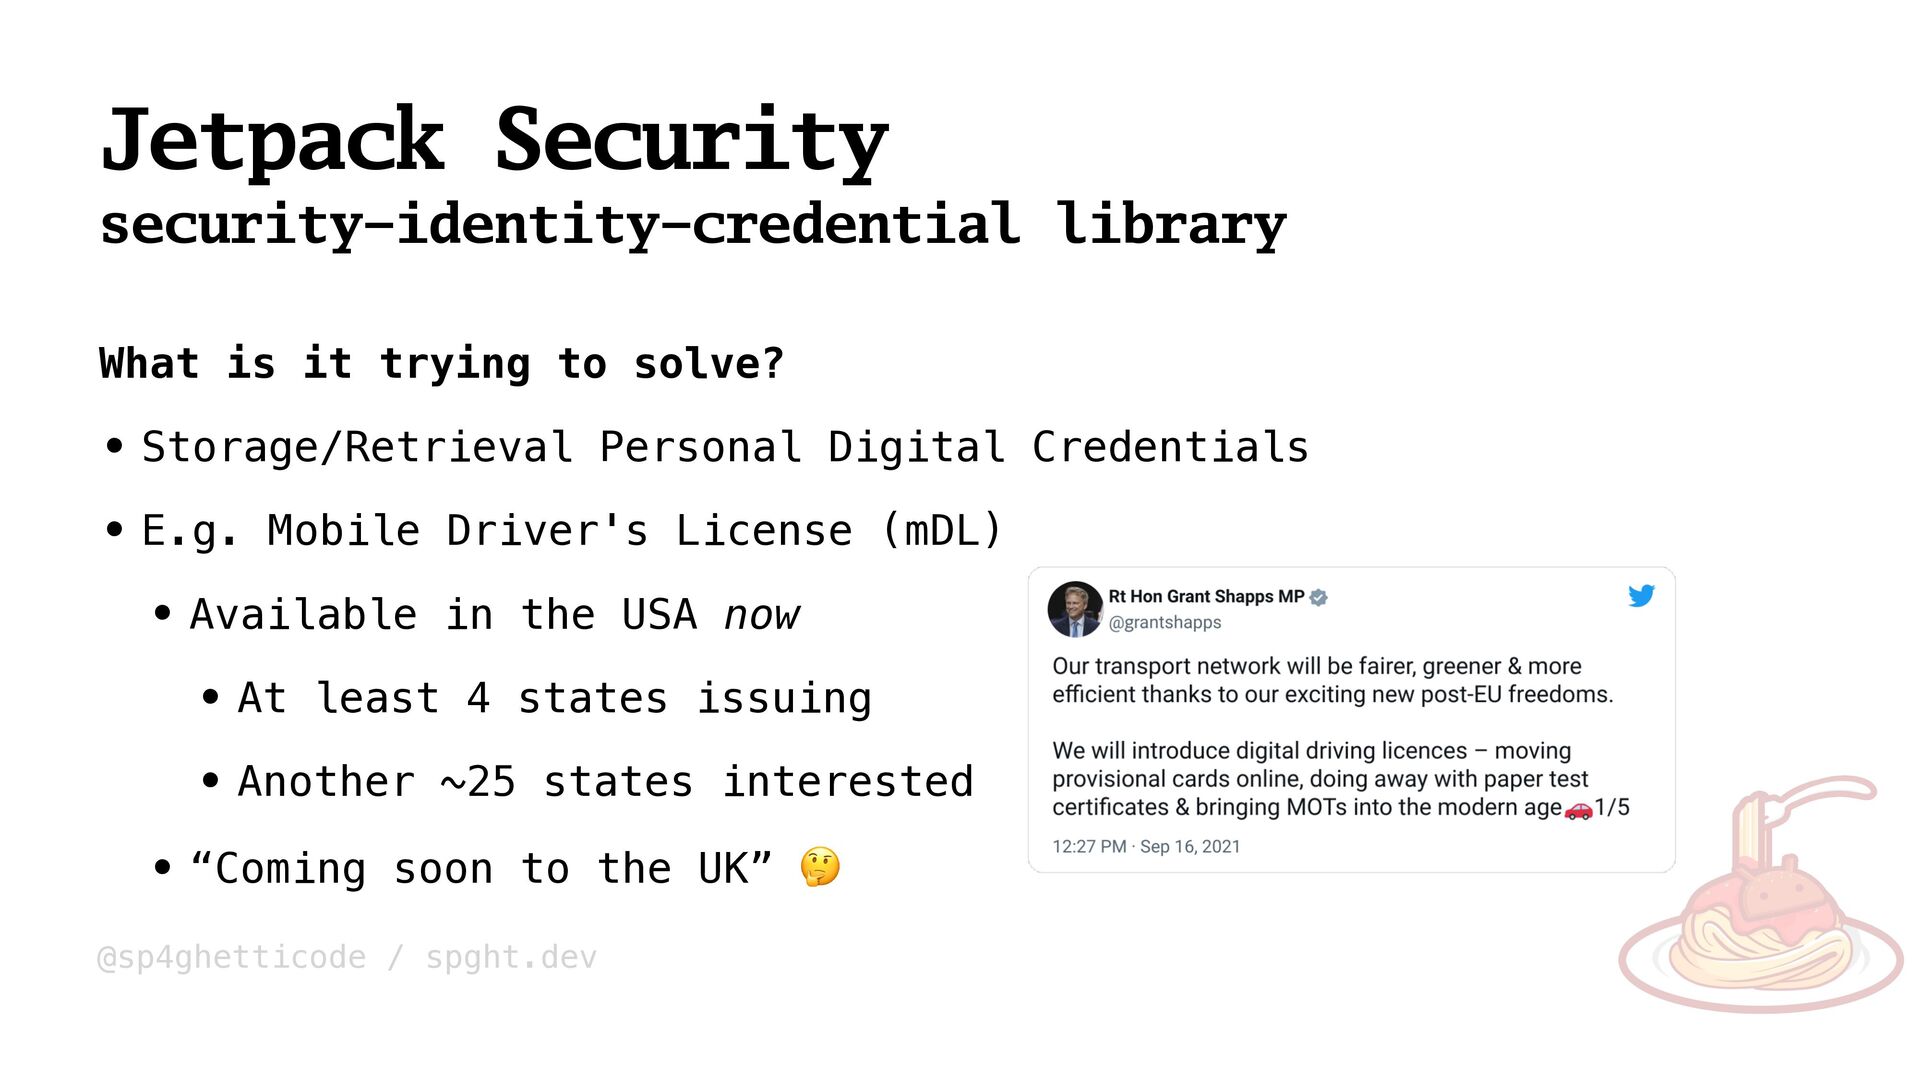
trying to solve? • Storage/Retrieval Personal Digital Credentials • E.g. Mobile Driver's License (mDL) • Available in the USA now • At least 4 states issuing • Another ~25 states interested • “Coming soon to the UK” 🤔 -
@sp4ghetticode / spght.dev Jetpack Security security-identity-credential library Who should use
this? • mDL issuers / receivers • Government Agencies • Services that require proof of identity, age, residence, etc. • But probably none of us (yet)… • It’s very early days! -
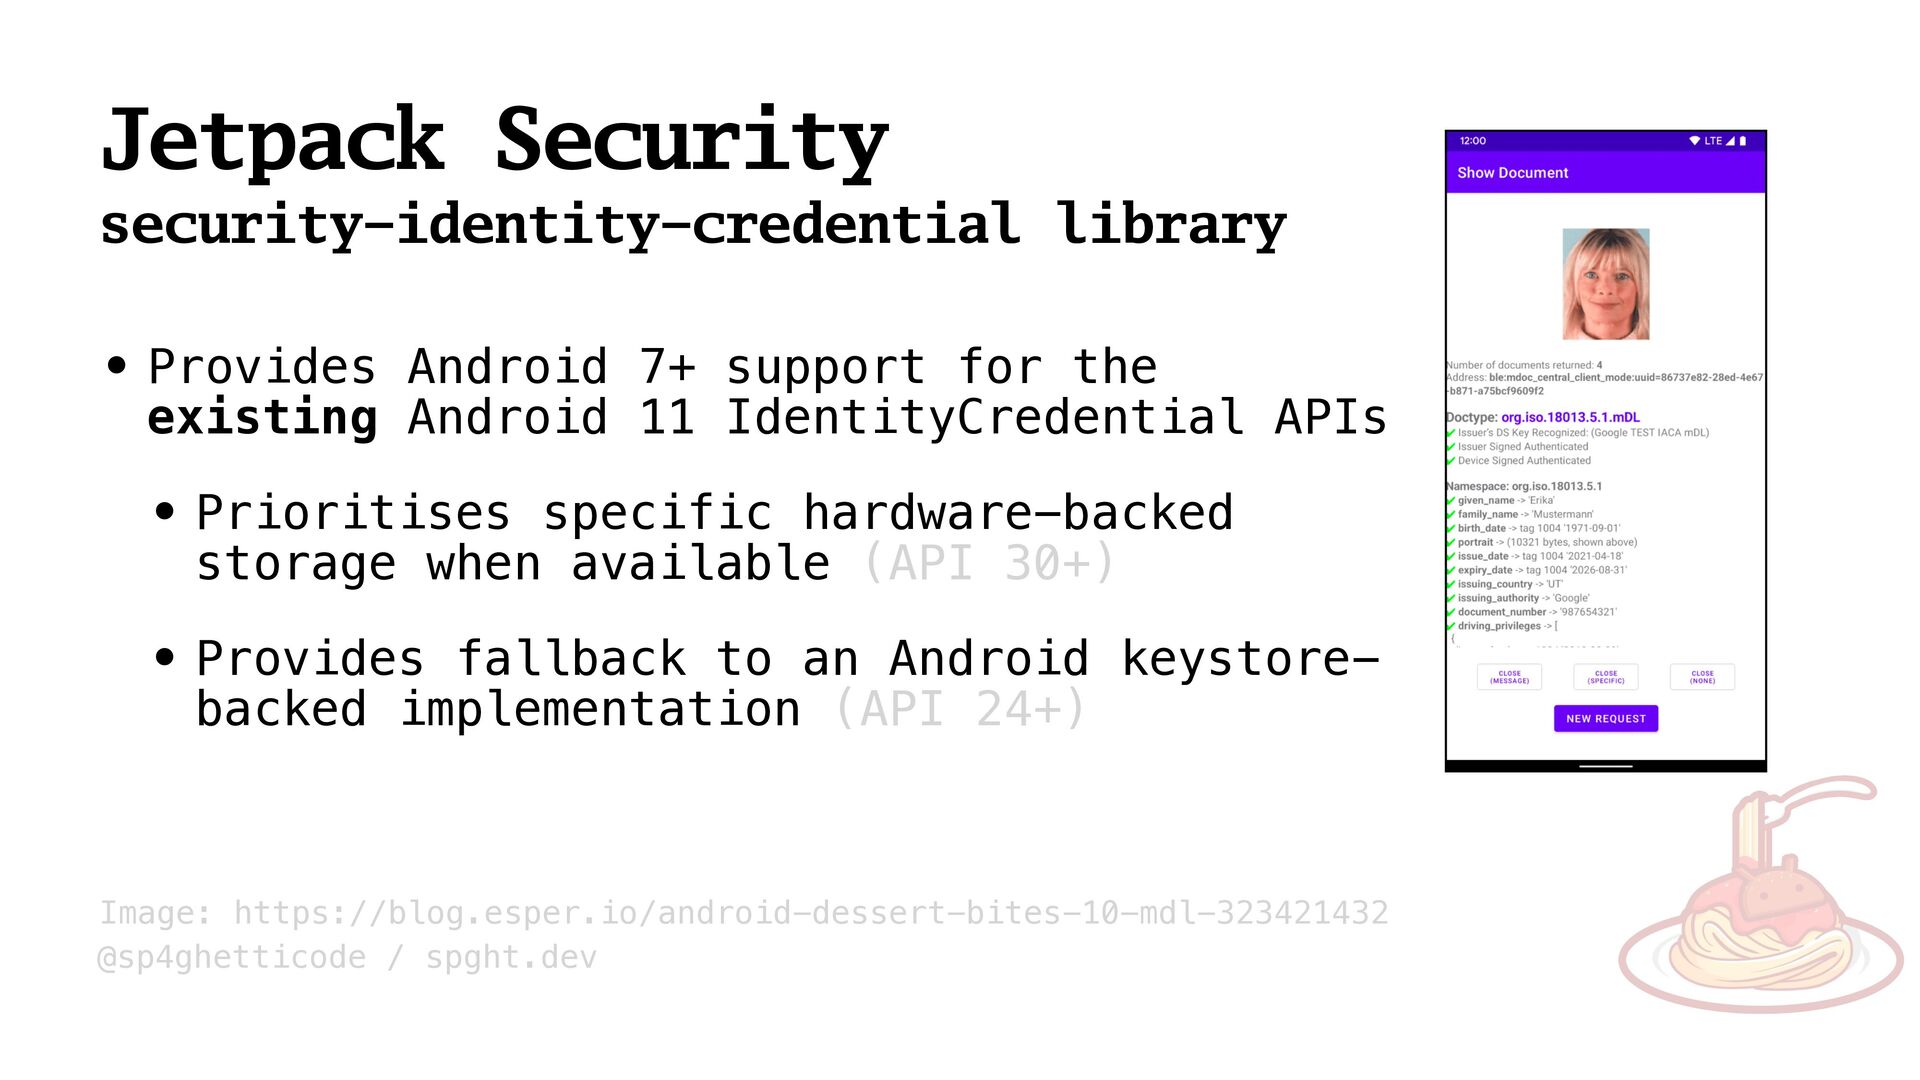
@sp4ghetticode / spght.dev • Provides Android 7+ support for the
existing Android 11 IdentityCredential APIs • Prioritises specific hardware-backed storage when available (API 30+) • Provides fallback to an Android keystore- backed implementation (API 24+) Image: https://blog.esper.io/android-dessert-bites-10-mdl-323421432 Jetpack Security security-identity-credential library -
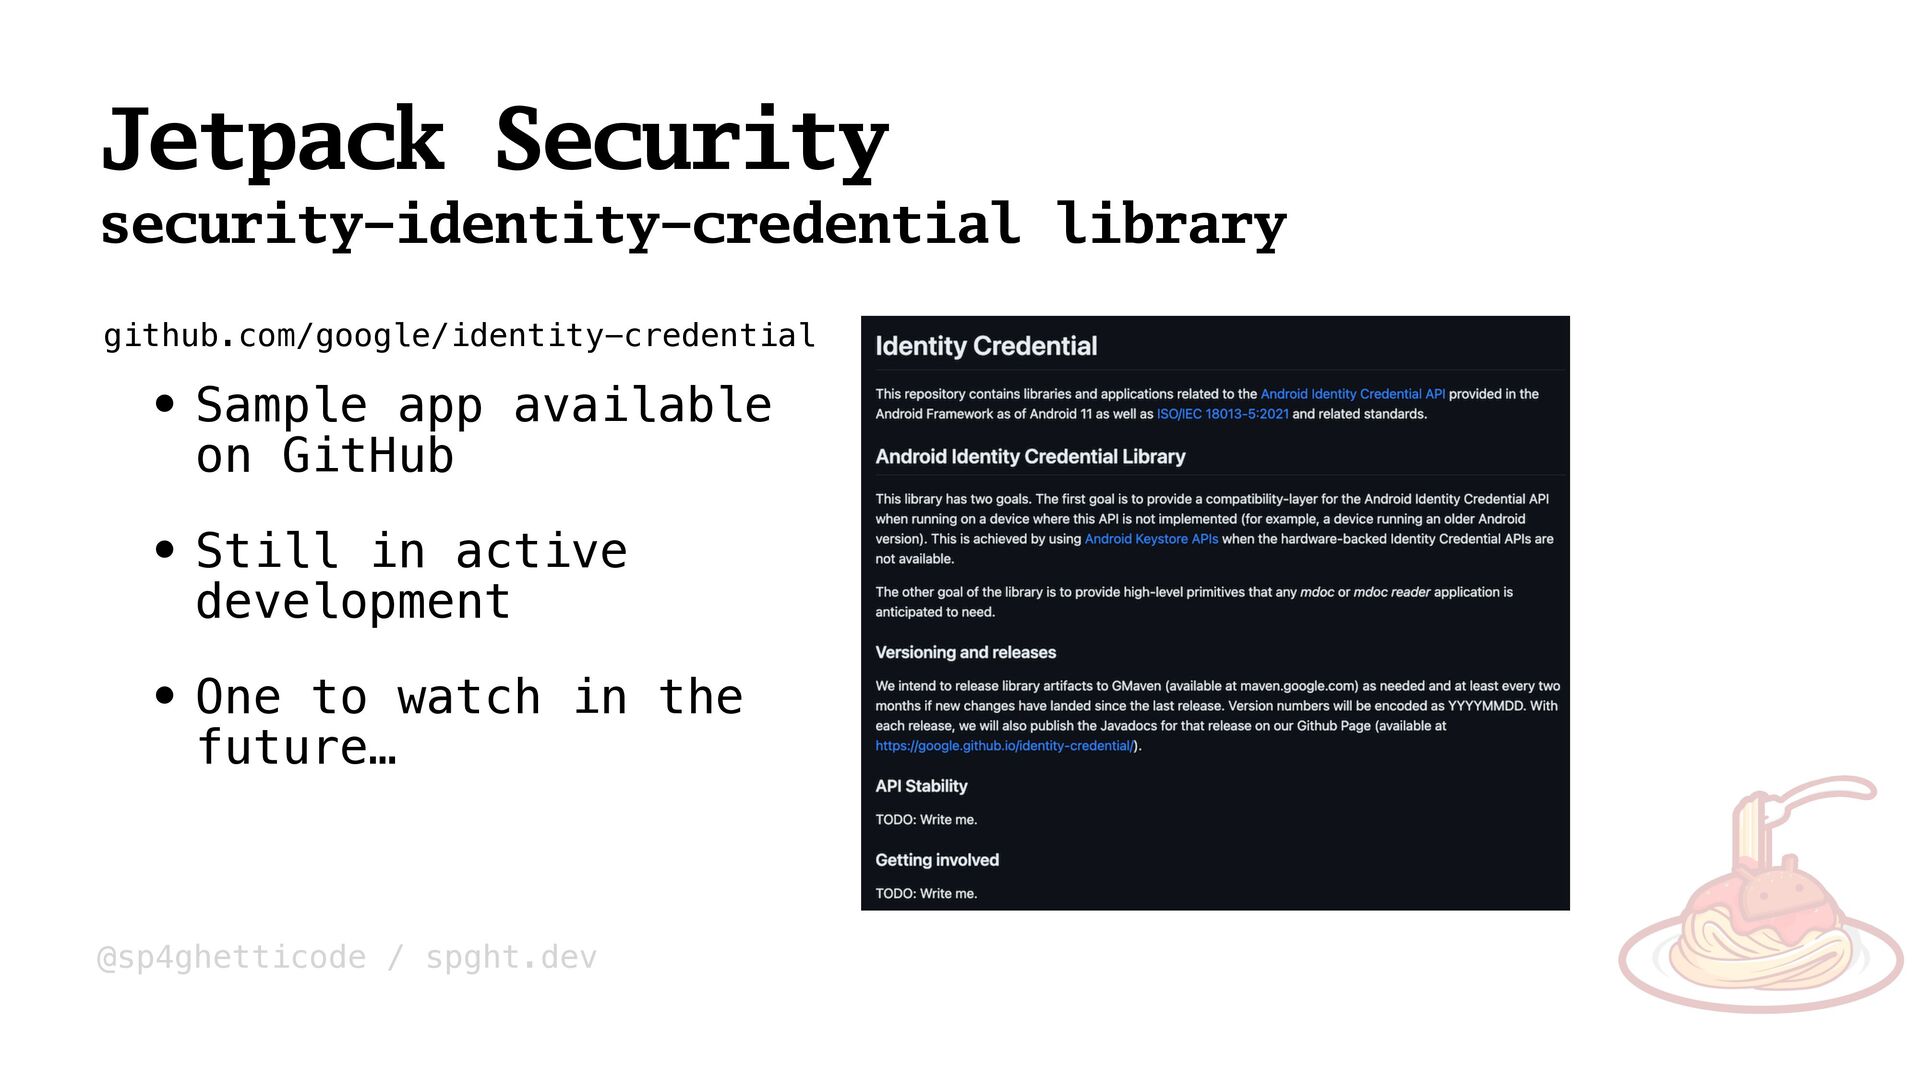
@sp4ghetticode / spght.dev • Sample app available on GitHub •
Still in active development • One to watch in the future… Jetpack Security security-identity-credential library github.com/google/identity-credential -
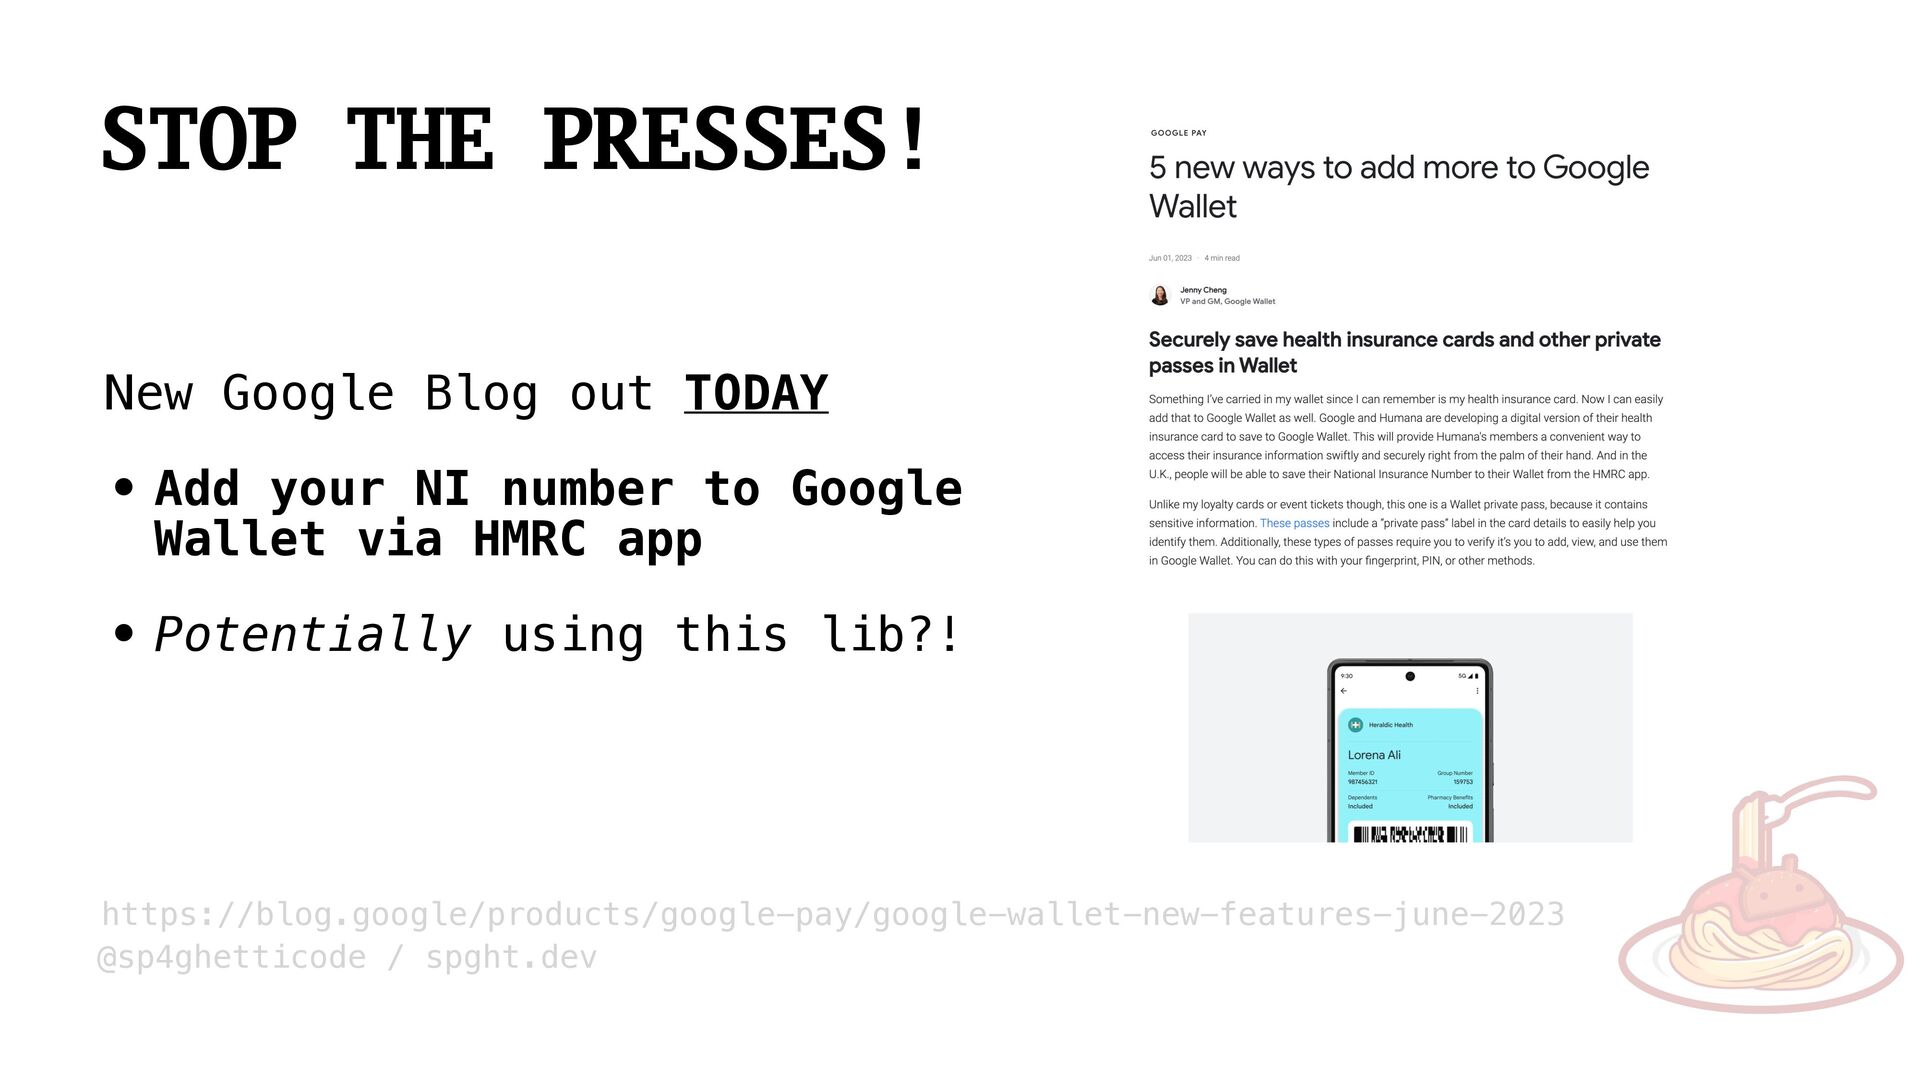
@sp4ghetticode / spght.dev STOP THE PRESSES! https://blog.google/products/google-pay/google-wallet-new-features-june-2023 New Google Blog
out TODAY • Add your NI number to Google Wallet via HMRC app • Potentially using this lib?!