Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Speed up your CI/CD pipelines by caching build ...

Speed up your CI/CD pipelines by caching build & runtime artifacts

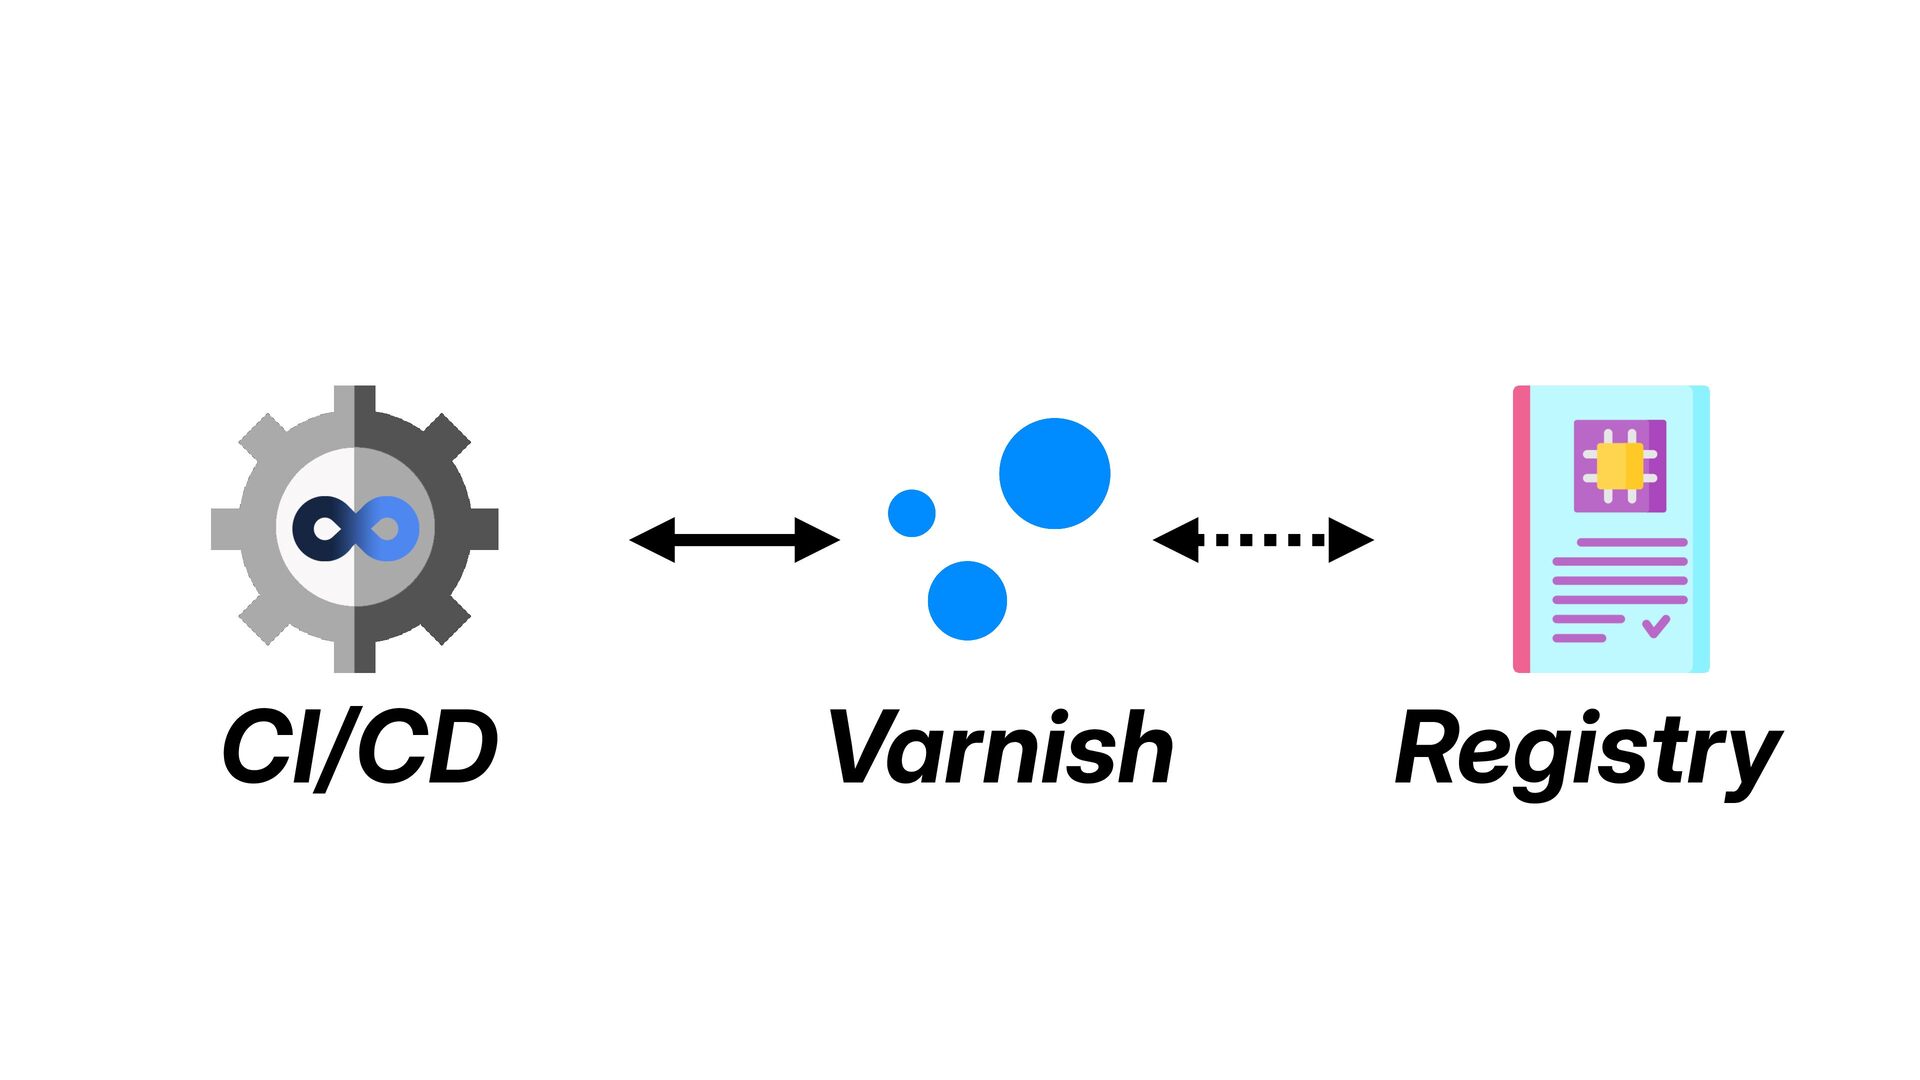
Slides for my WeAreDevelopers World Congress 2026 presentation on how to accelerate CI/CD pipelines by caching your software artifacts.

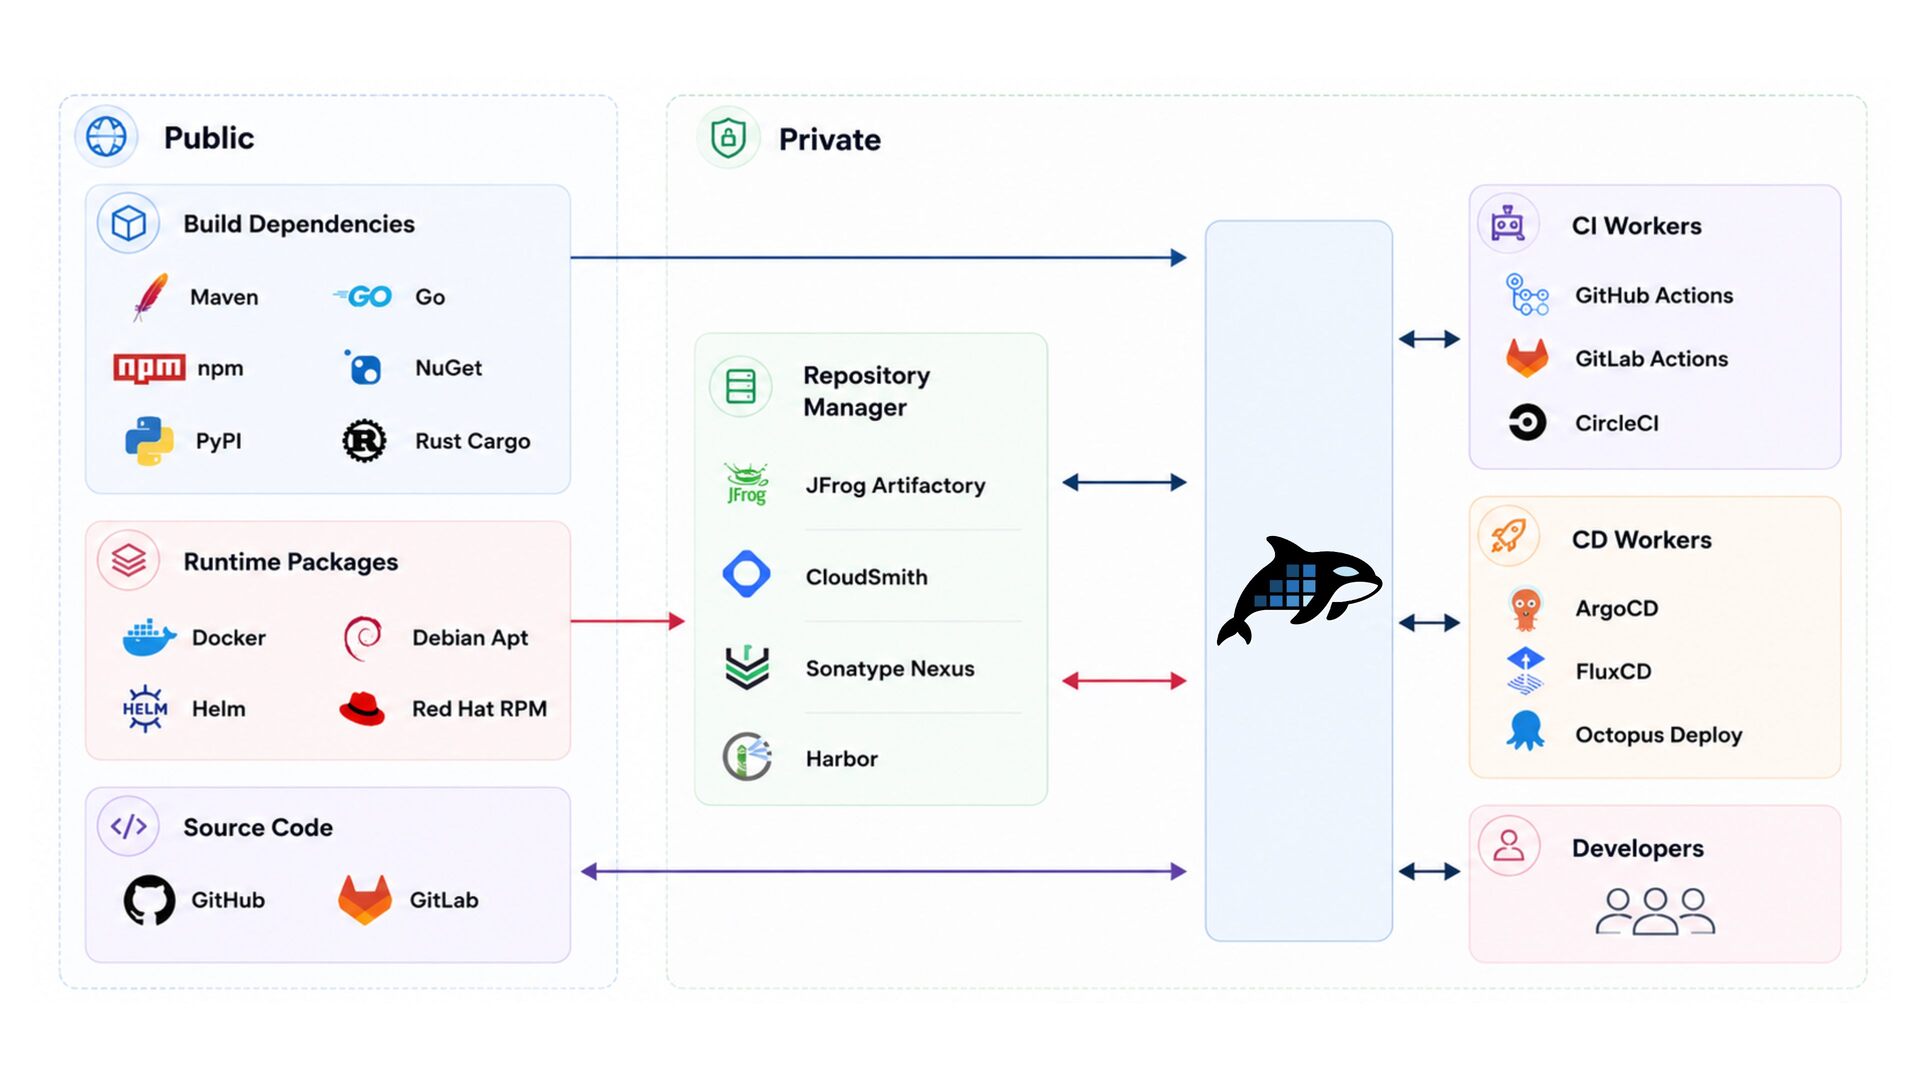
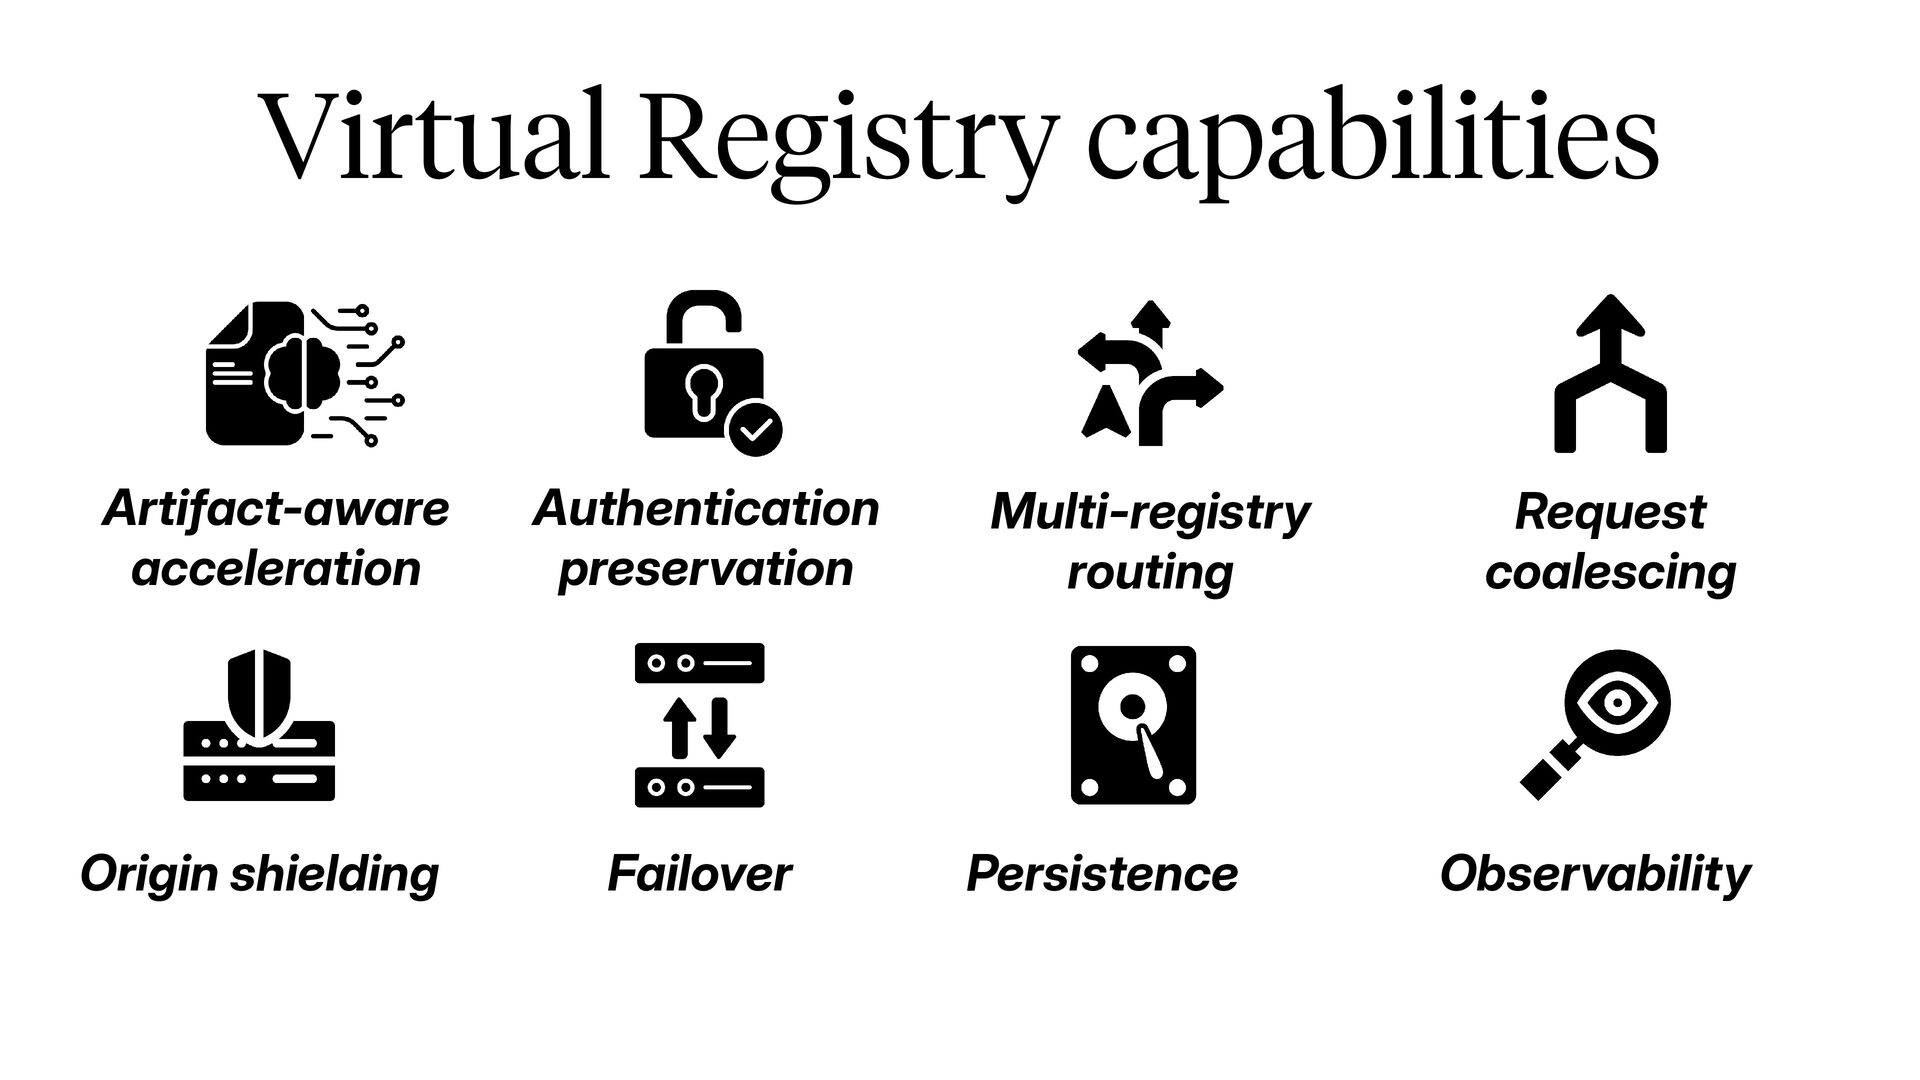
This presentation explains how a Virtual Registry with artifact caching capabilities can accelerate and offload pressure from your package registries. We cover package ecosystems like Docker, NPM, PyPi, and more.

See https://feryn.eu/presentations/speed-up-your-ci-cd-pipelines-by-caching-build-runtime-artifacts-wearedevelopers-world-congress-2026 for more information

Thijs Feryn PRO

July 09, 2026

Transcript

67 slides
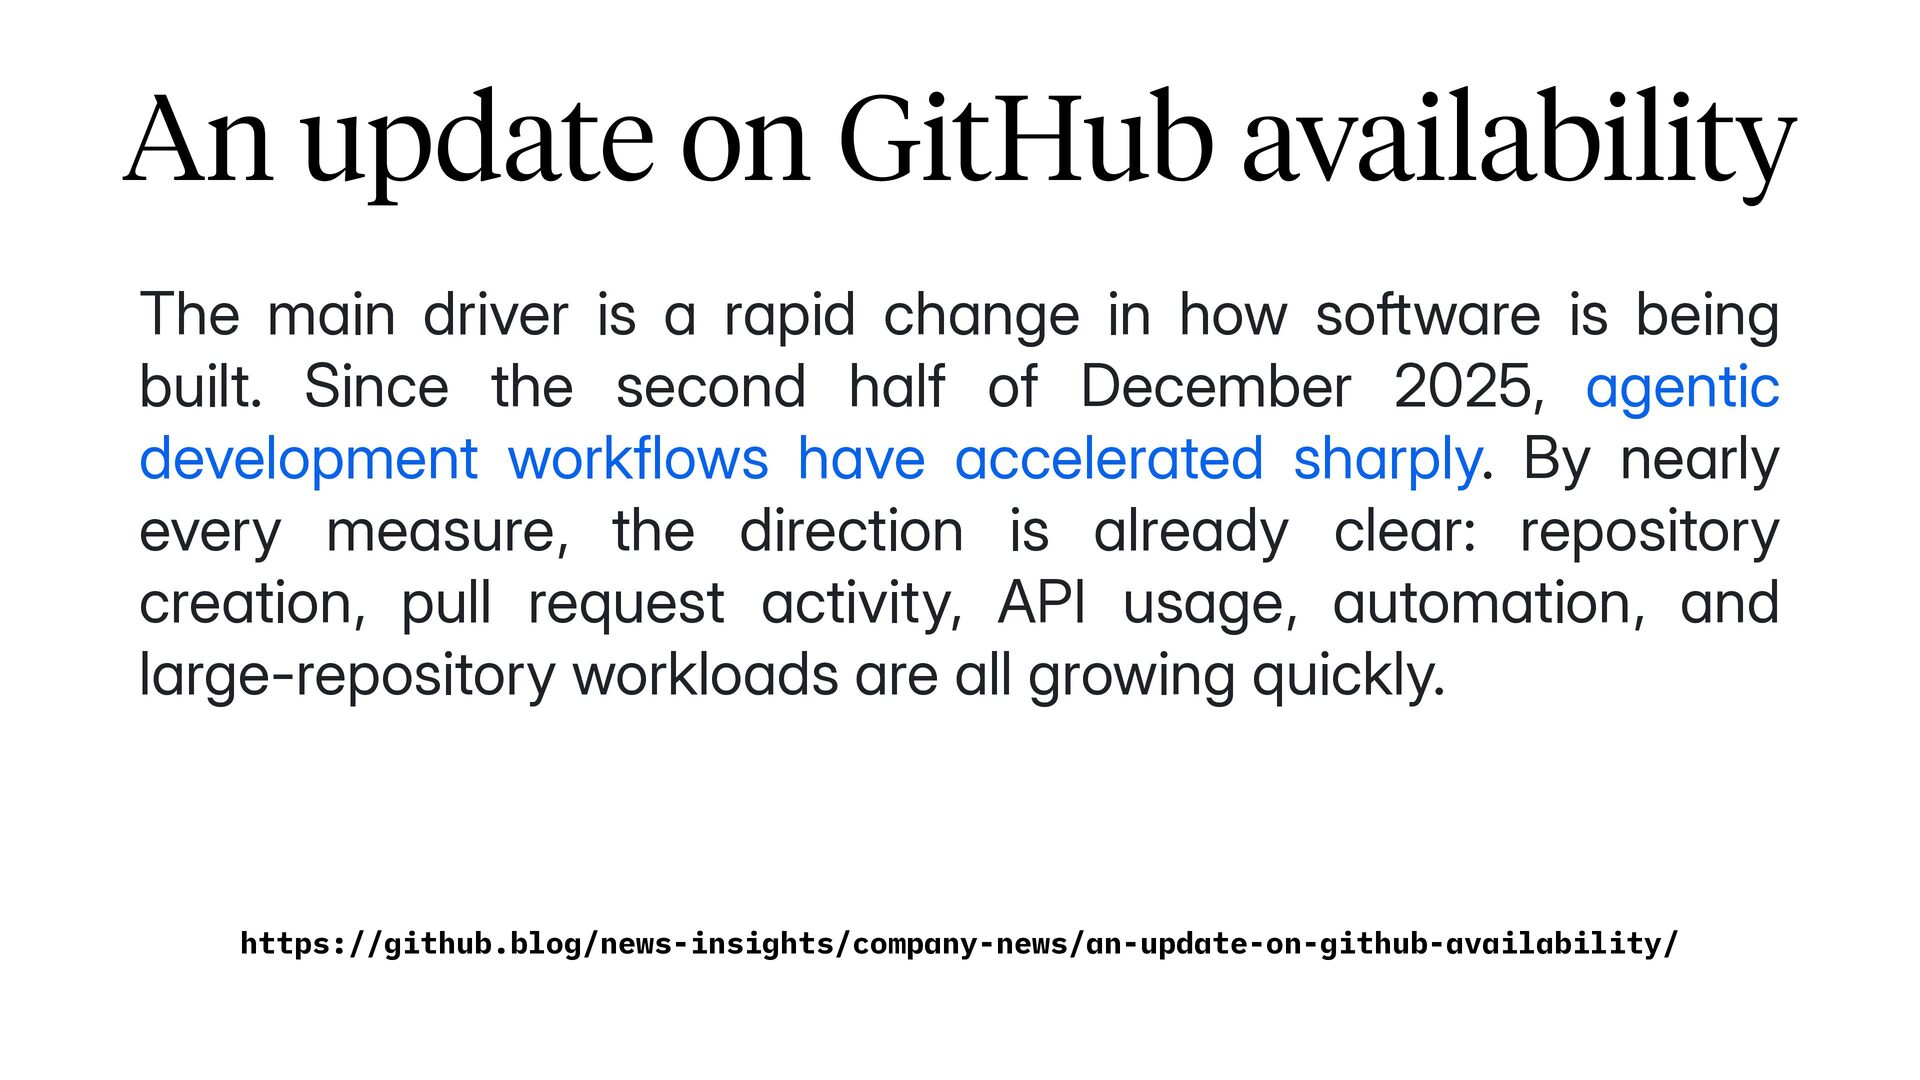
  1. An update on GitHub availability The main driver is a

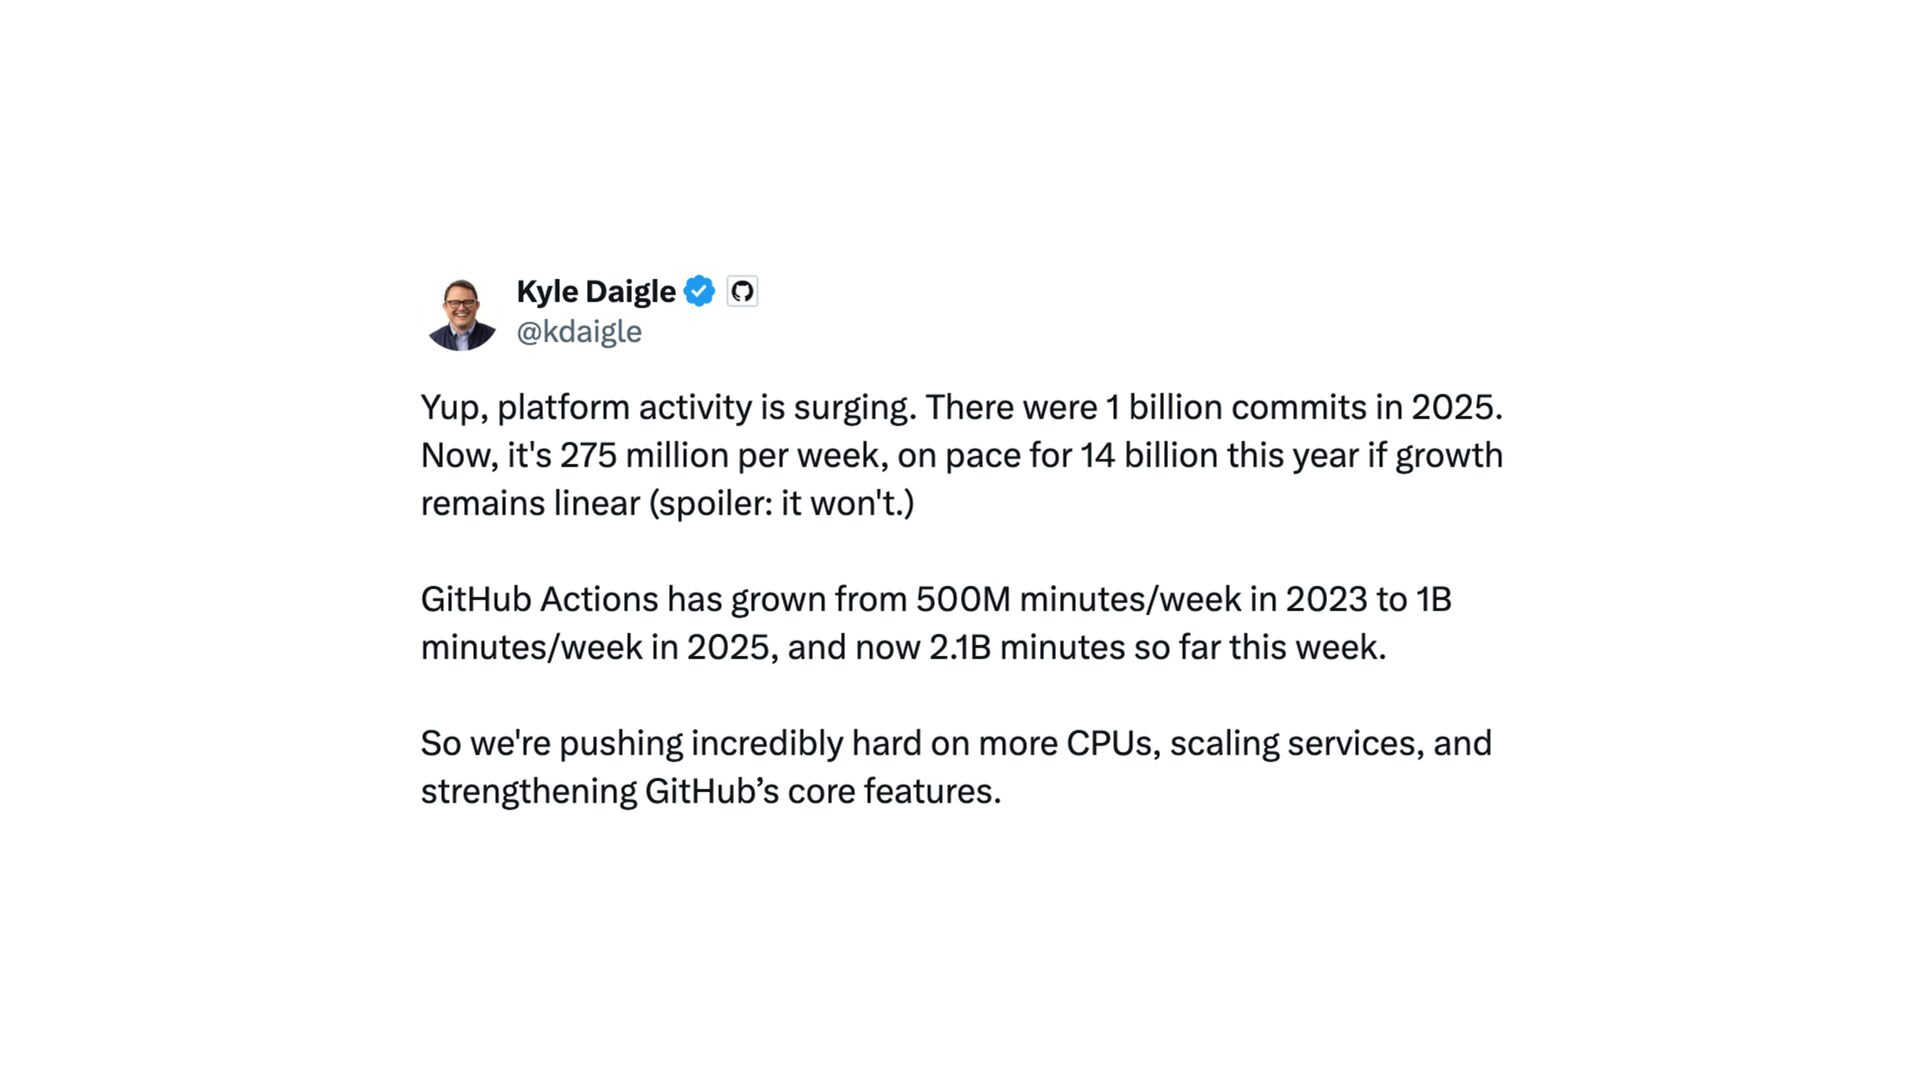
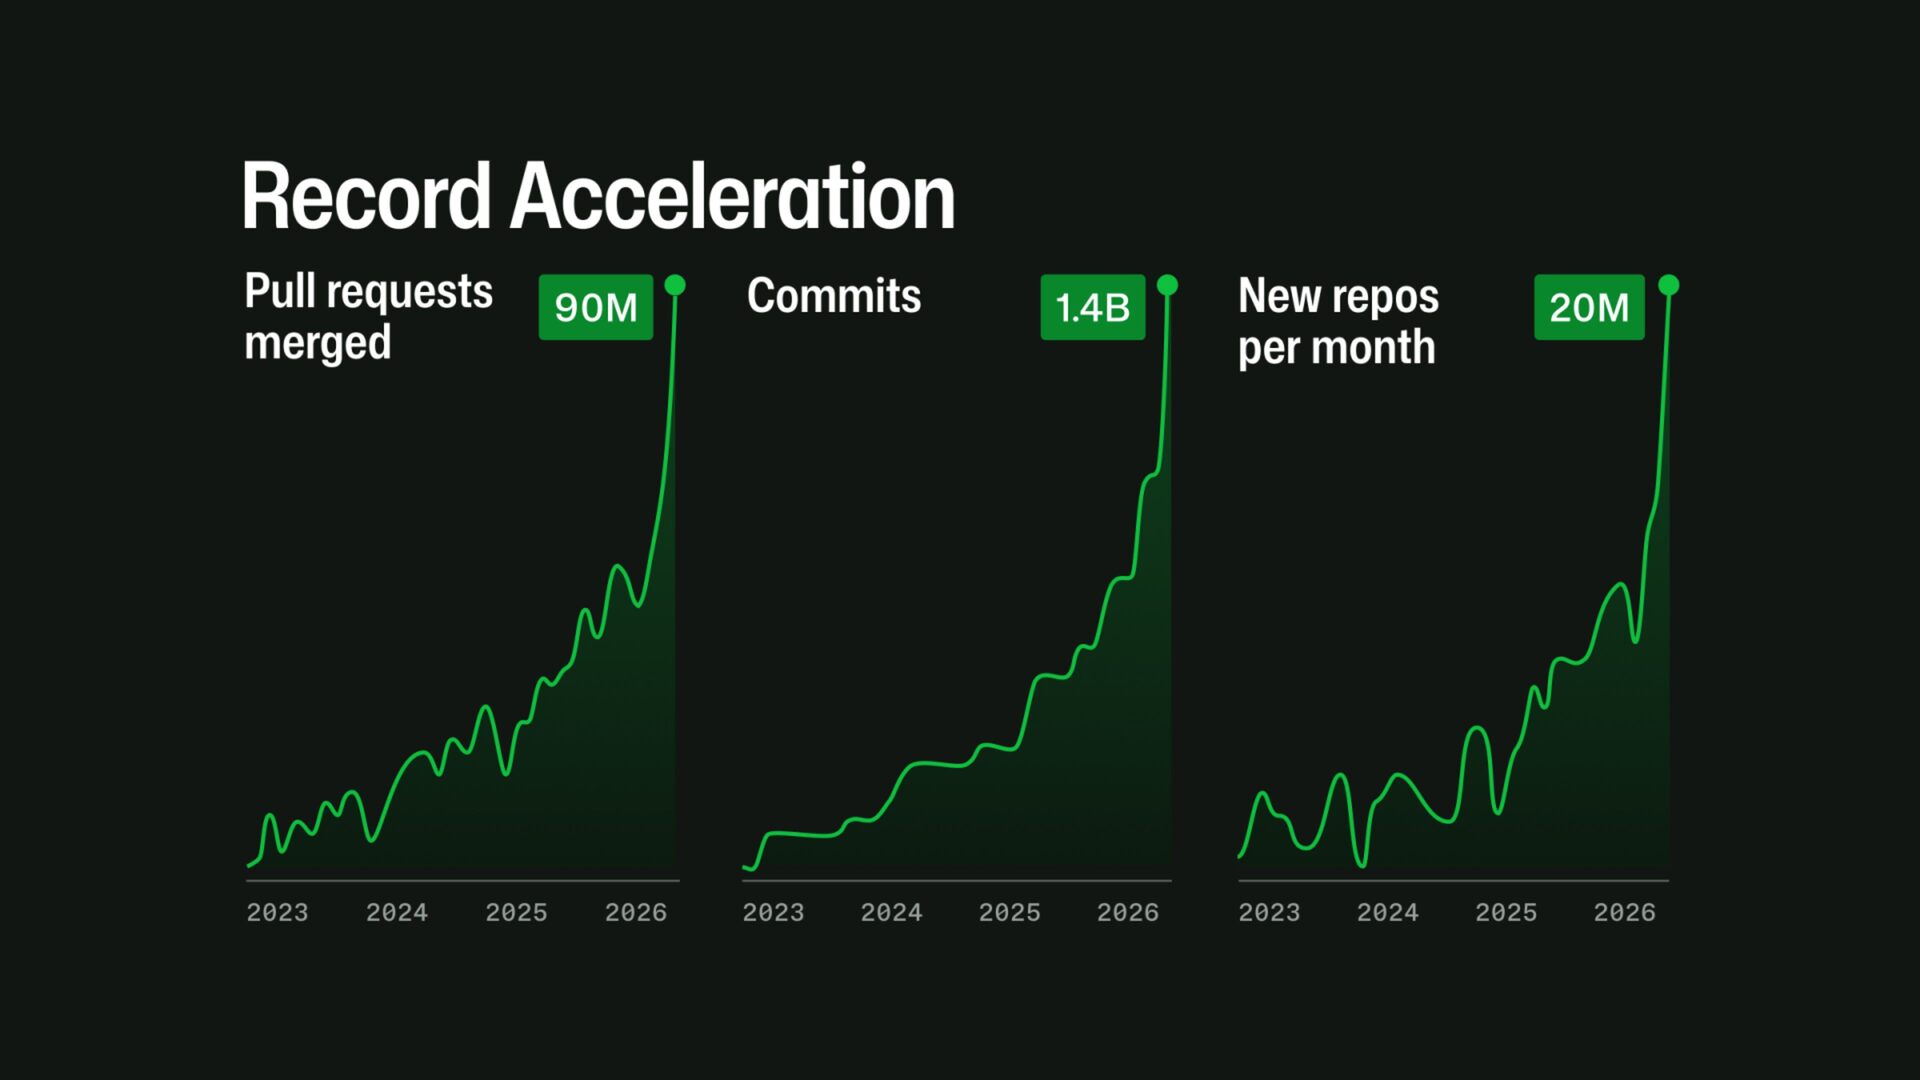
    rapid change in how software is being built. Since the second half of December 2025, agentic development workflows have accelerated sharply. By nearly every measure, the direction is already clear: repository creation, pull request activity, API usage, automation, and large-repository workloads are all growing quickly. https://github.blog/news-insights/company-news/an-update-on-github-availability/
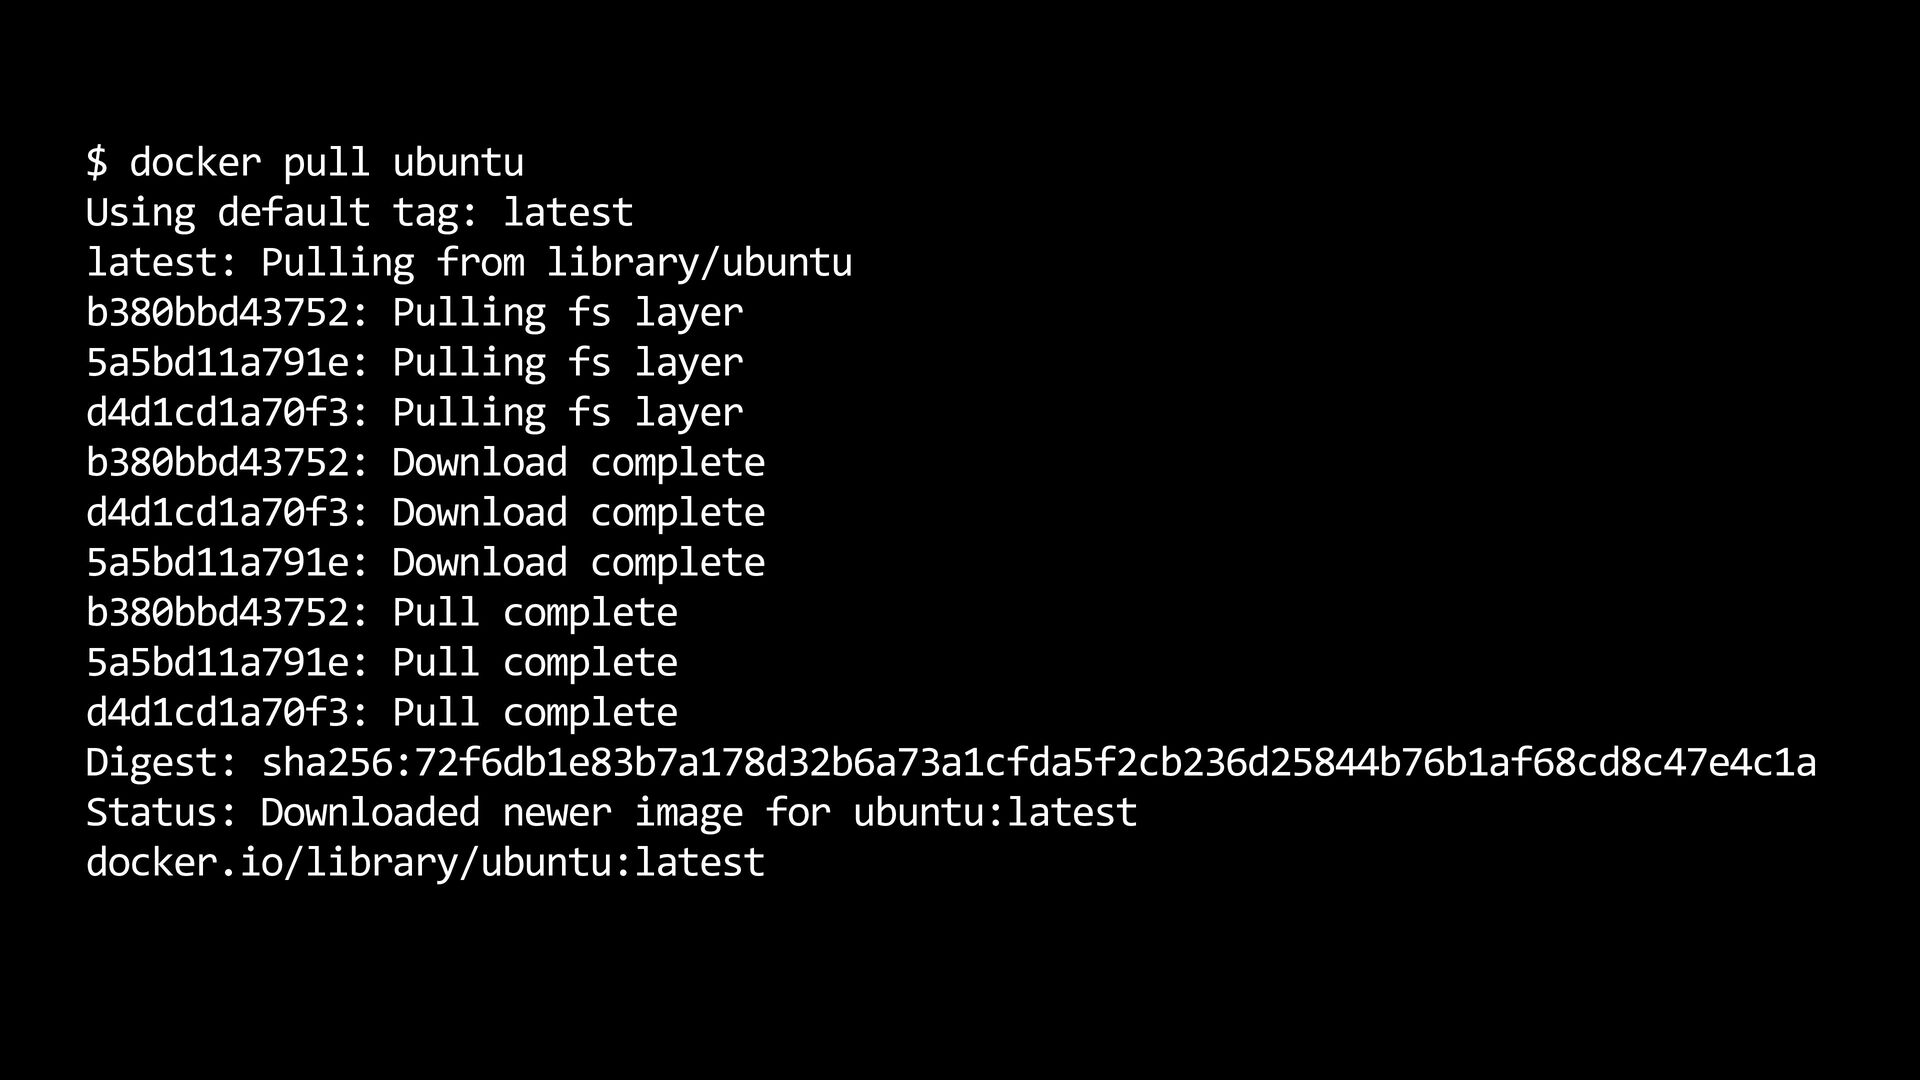
  2. $ docker pull ubuntu Using default tag: latest latest: Pulling

    from library/ubuntu b380bbd43752: Pulling fs layer 5a5bd11a791e: Pulling fs layer d4d1cd1a70f3: Pulling fs layer b380bbd43752: Download complete d4d1cd1a70f3: Download complete 5a5bd11a791e: Download complete b380bbd43752: Pull complete 5a5bd11a791e: Pull complete d4d1cd1a70f3: Pull complete Digest: sha256:72f6db1e83b7a178d32b6a73a1cfda5f2cb236d25844b76b1af68cd8c47e4c1a Status: Downloaded newer image for ubuntu:latest docker.io/library/ubuntu:latest
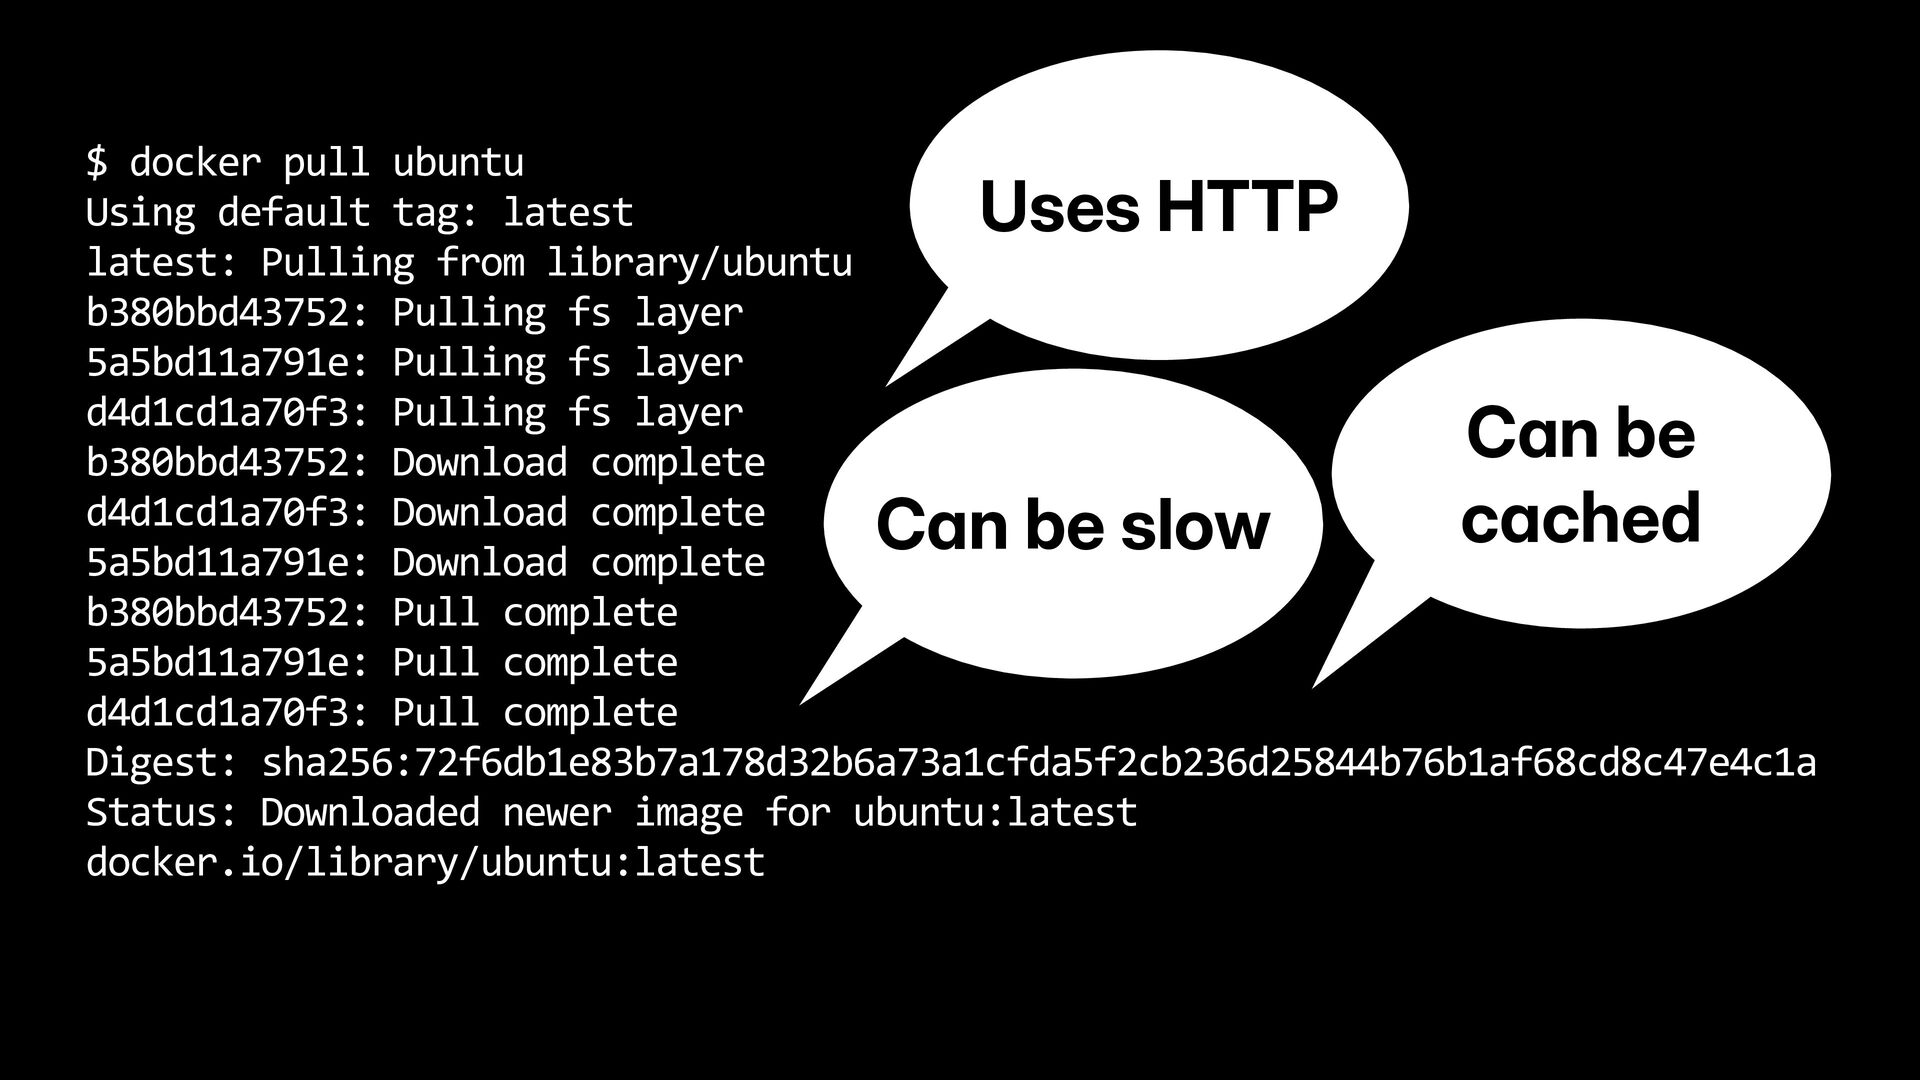
  3. $ docker pull ubuntu Using default tag: latest latest: Pulling

    from library/ubuntu b380bbd43752: Pulling fs layer 5a5bd11a791e: Pulling fs layer d4d1cd1a70f3: Pulling fs layer b380bbd43752: Download complete d4d1cd1a70f3: Download complete 5a5bd11a791e: Download complete b380bbd43752: Pull complete 5a5bd11a791e: Pull complete d4d1cd1a70f3: Pull complete Digest: sha256:72f6db1e83b7a178d32b6a73a1cfda5f2cb236d25844b76b1af68cd8c47e4c1a Status: Downloaded newer image for ubuntu:latest docker.io/library/ubuntu:latest Uses HTTP Can be slow Can be cached
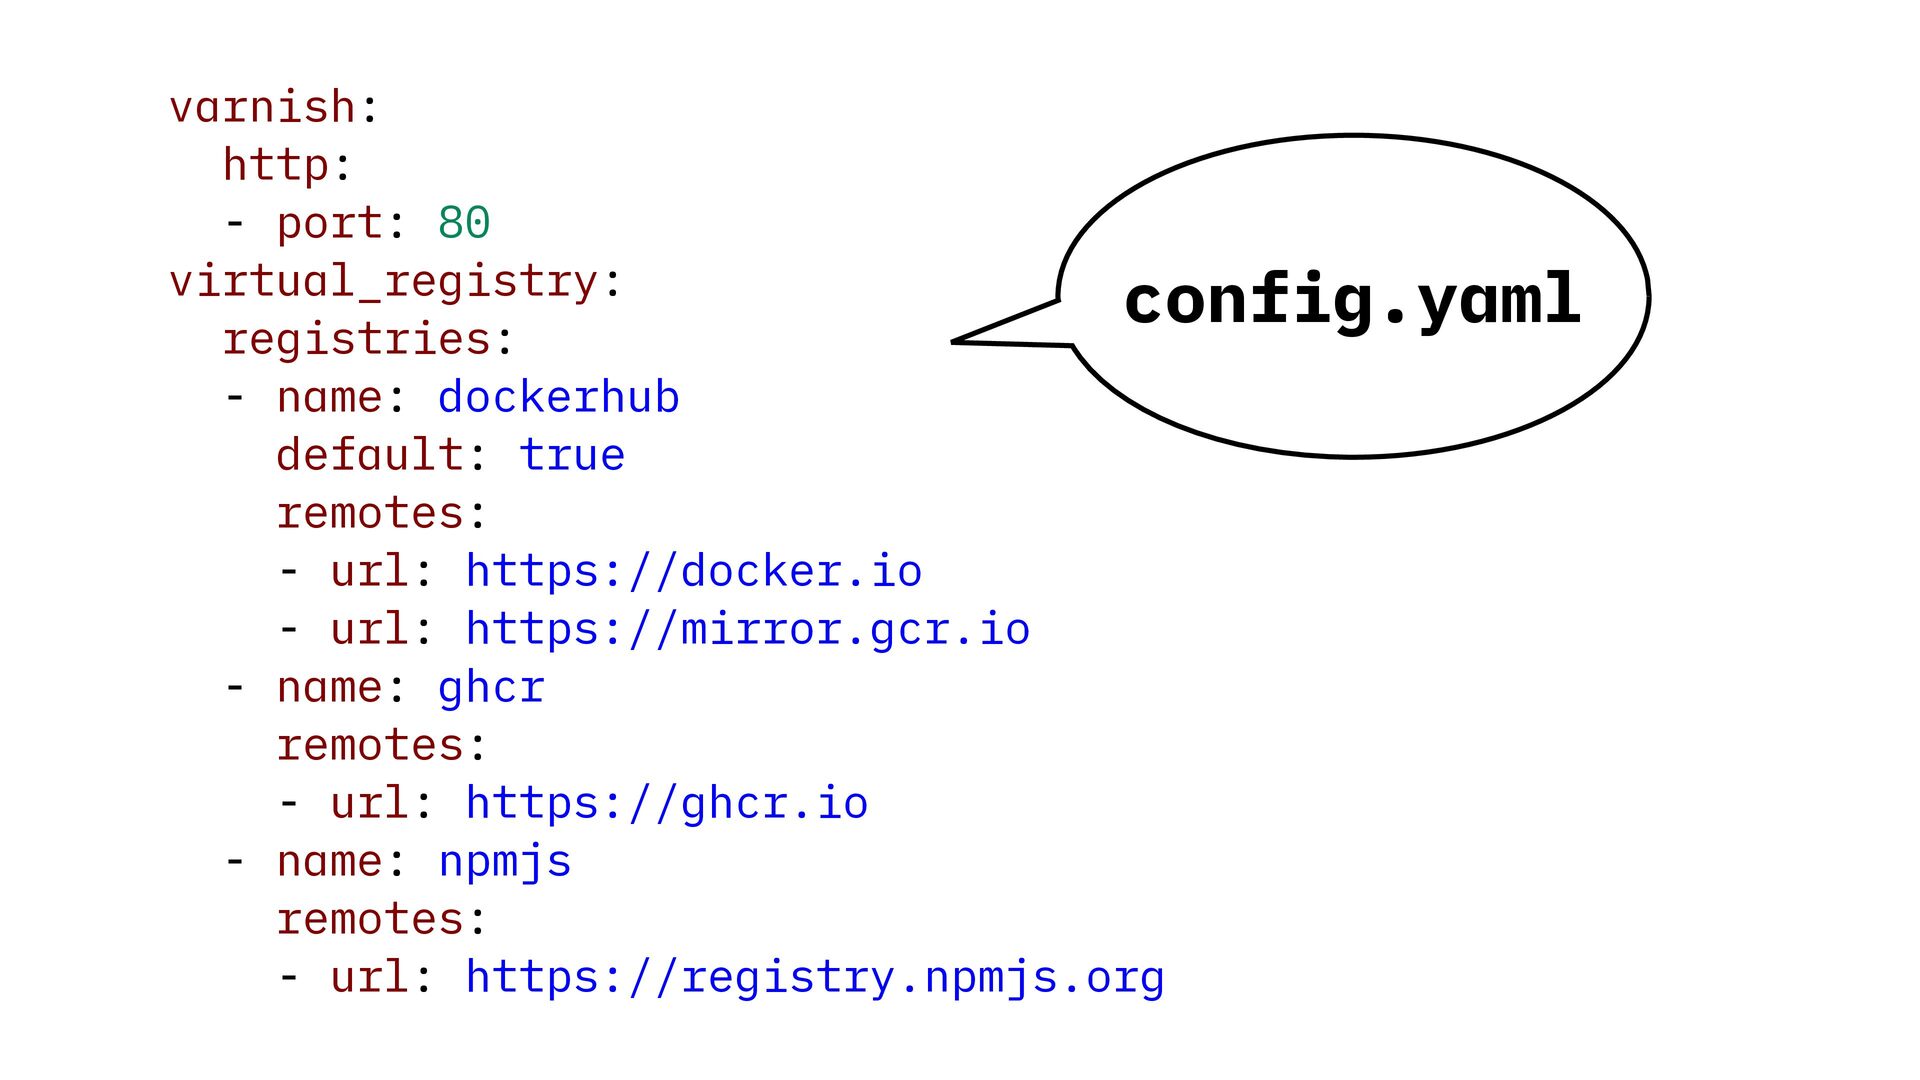
  4. varnish: http: - port: 80 virtual_registry: config.yaml registries: - name:

    dockerhub default: true remotes: - url: https://docker.io - url: https://mirror.gcr.io - name: ghcr remotes: - url: https://ghcr.io - name: npmjs remotes: - url: https://registry.npmjs.org
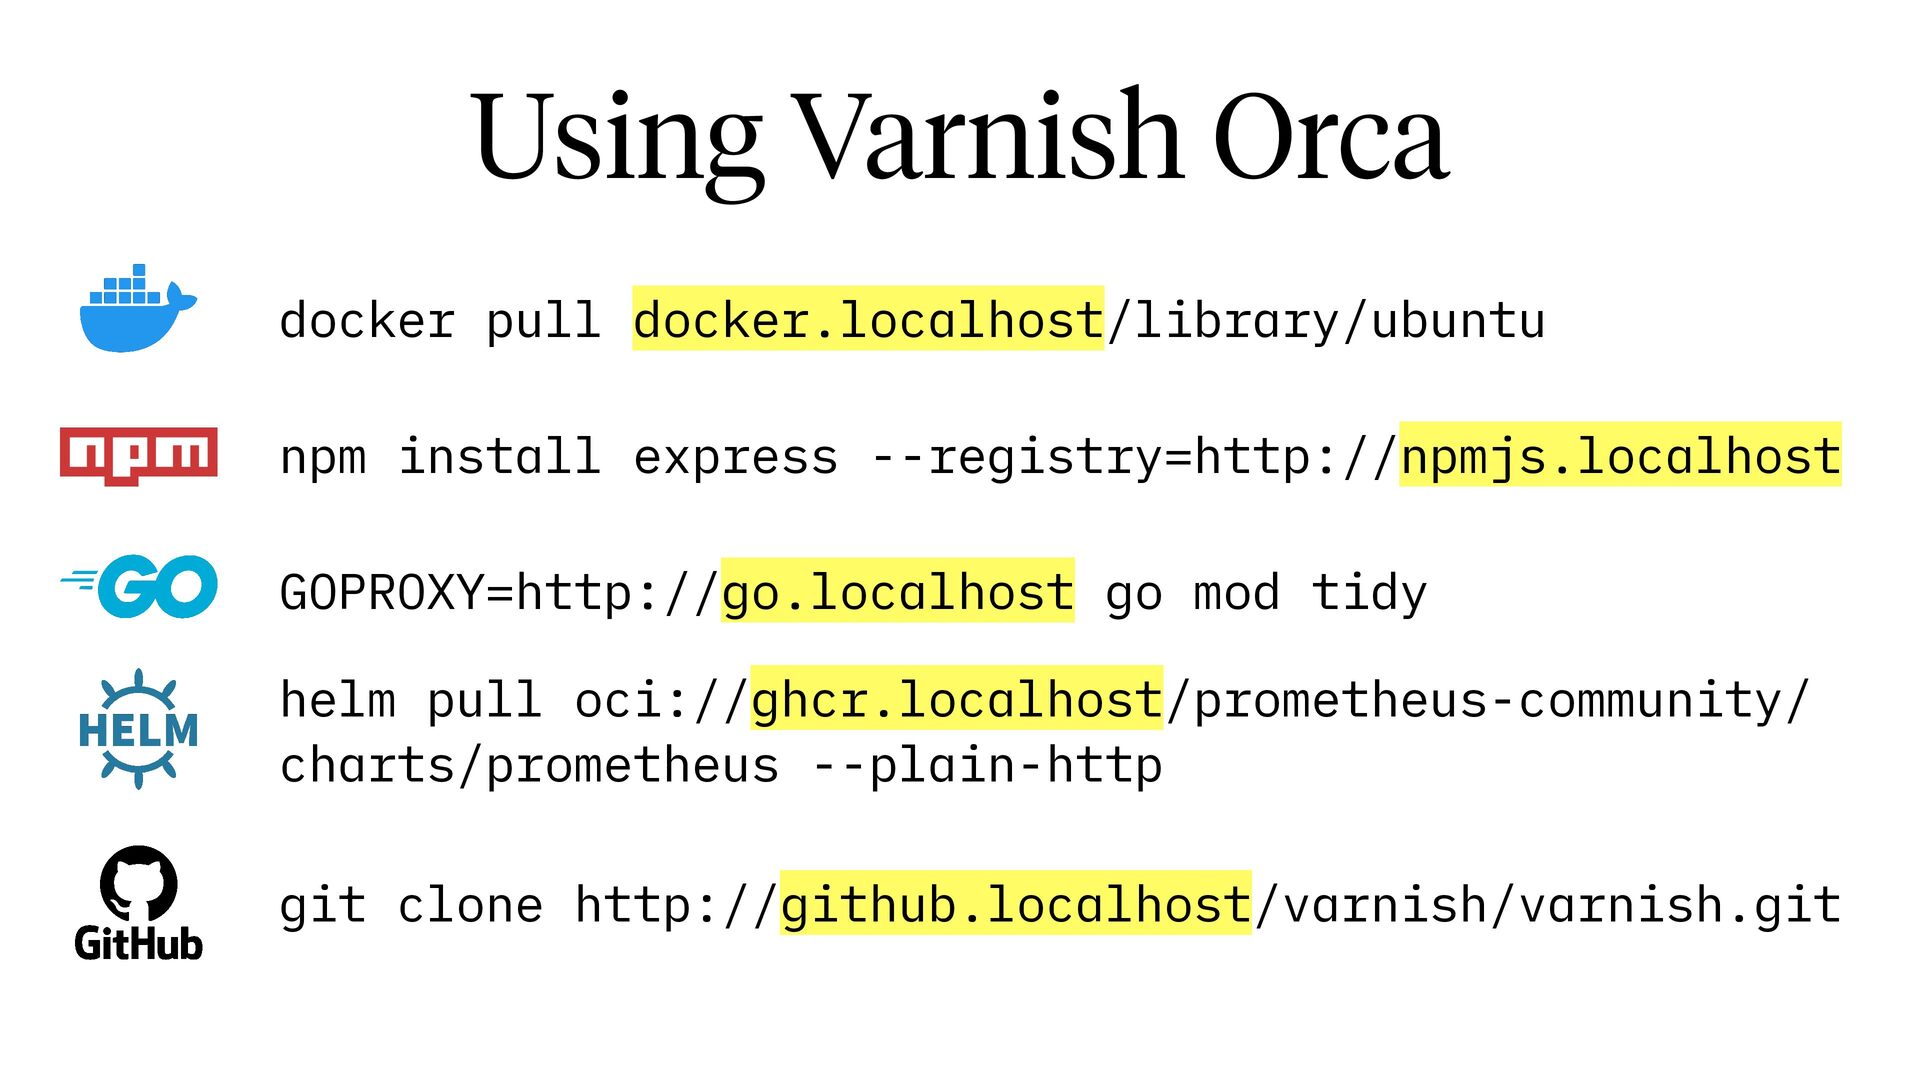
  5. Using Varnish Orca docker pull docker.localhost/library/ubuntu npm install express --registry=http://npmjs.localhost

    GOPROXY=http://go.localhost go mod tidy helm pull oci://ghcr.localhost/prometheus-community/ charts/prometheus --plain-http git clone http://github.localhost/varnish/varnish.git
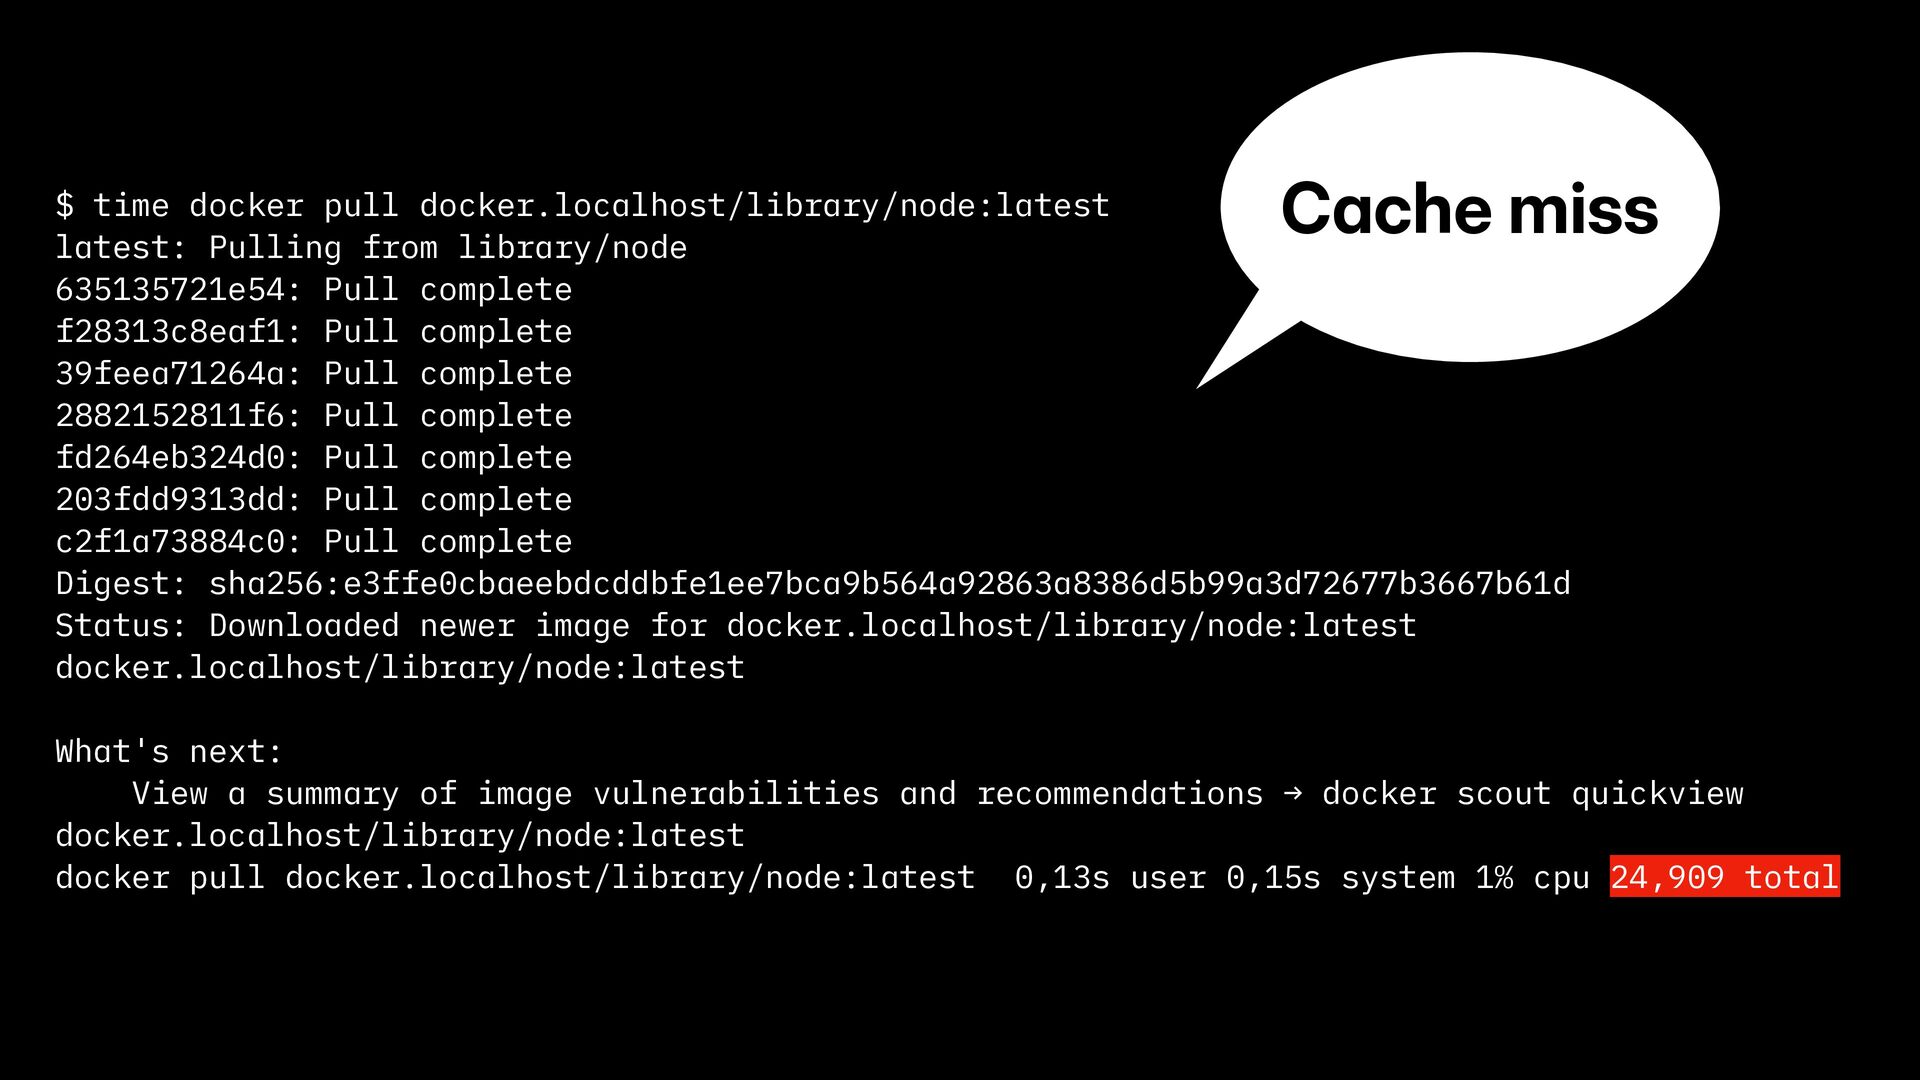
  6. Cache miss $ time docker pull docker.localhost/library/node:latest latest: Pulling from

    library/node 635135721e54: Pull complete f28313c8eaf1: Pull complete 39feea71264a: Pull complete 2882152811f6: Pull complete fd264eb324d0: Pull complete 203fdd9313dd: Pull complete c2f1a73884c0: Pull complete Digest: sha256:e3ffe0cbaeebdcddbfe1ee7bca9b564a92863a8386d5b99a3d72677b3667b61d Status: Downloaded newer image for docker.localhost/library/node:latest docker.localhost/library/node:latest What's next: View a summary of image vulnerabilities and recommendations → docker scout quickview docker.localhost/library/node:latest docker pull docker.localhost/library/node:latest 0,13s user 0,15s system 1% cpu 24,909 total
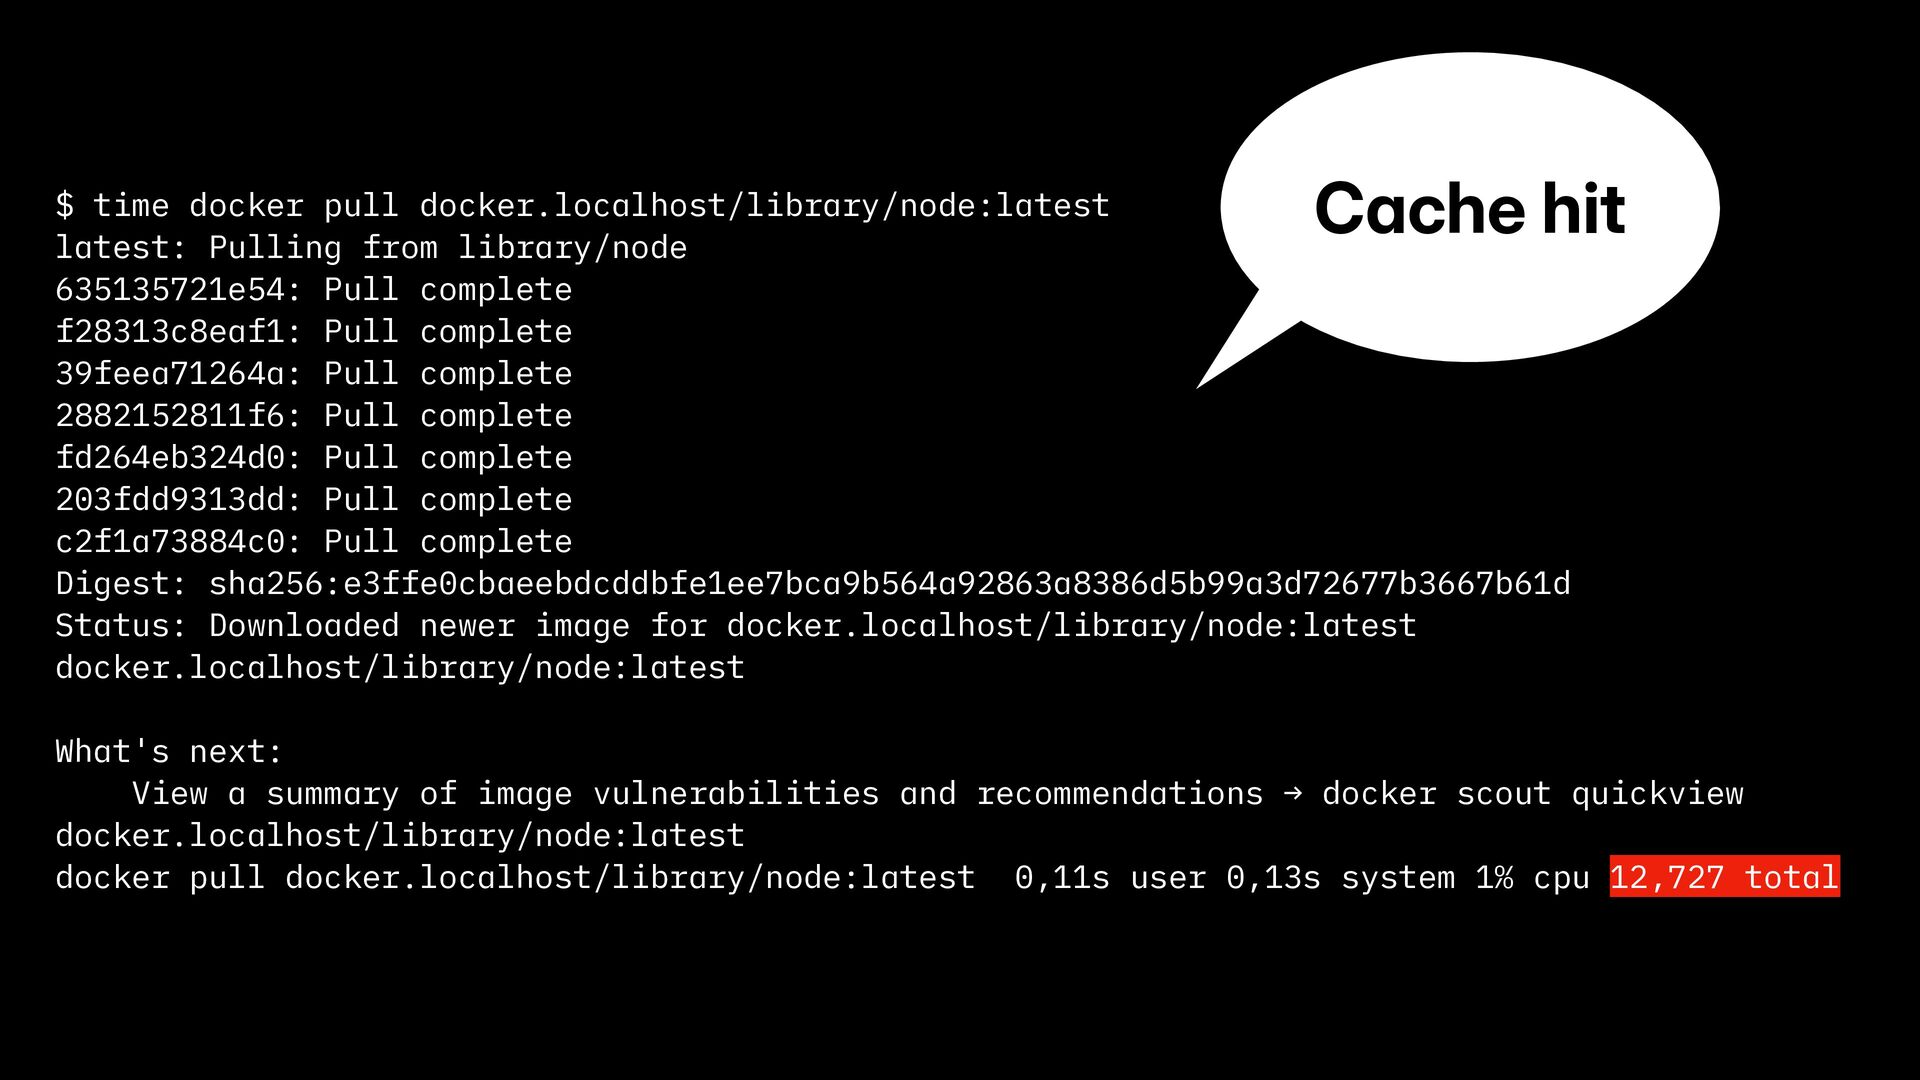
  7. Cache hit $ time docker pull docker.localhost/library/node:latest latest: Pulling from

    library/node 635135721e54: Pull complete f28313c8eaf1: Pull complete 39feea71264a: Pull complete 2882152811f6: Pull complete fd264eb324d0: Pull complete 203fdd9313dd: Pull complete c2f1a73884c0: Pull complete Digest: sha256:e3ffe0cbaeebdcddbfe1ee7bca9b564a92863a8386d5b99a3d72677b3667b61d Status: Downloaded newer image for docker.localhost/library/node:latest docker.localhost/library/node:latest What's next: View a summary of image vulnerabilities and recommendations → docker scout quickview docker.localhost/library/node:latest docker pull docker.localhost/library/node:latest 0,11s user 0,13s system 1% cpu 12,727 total
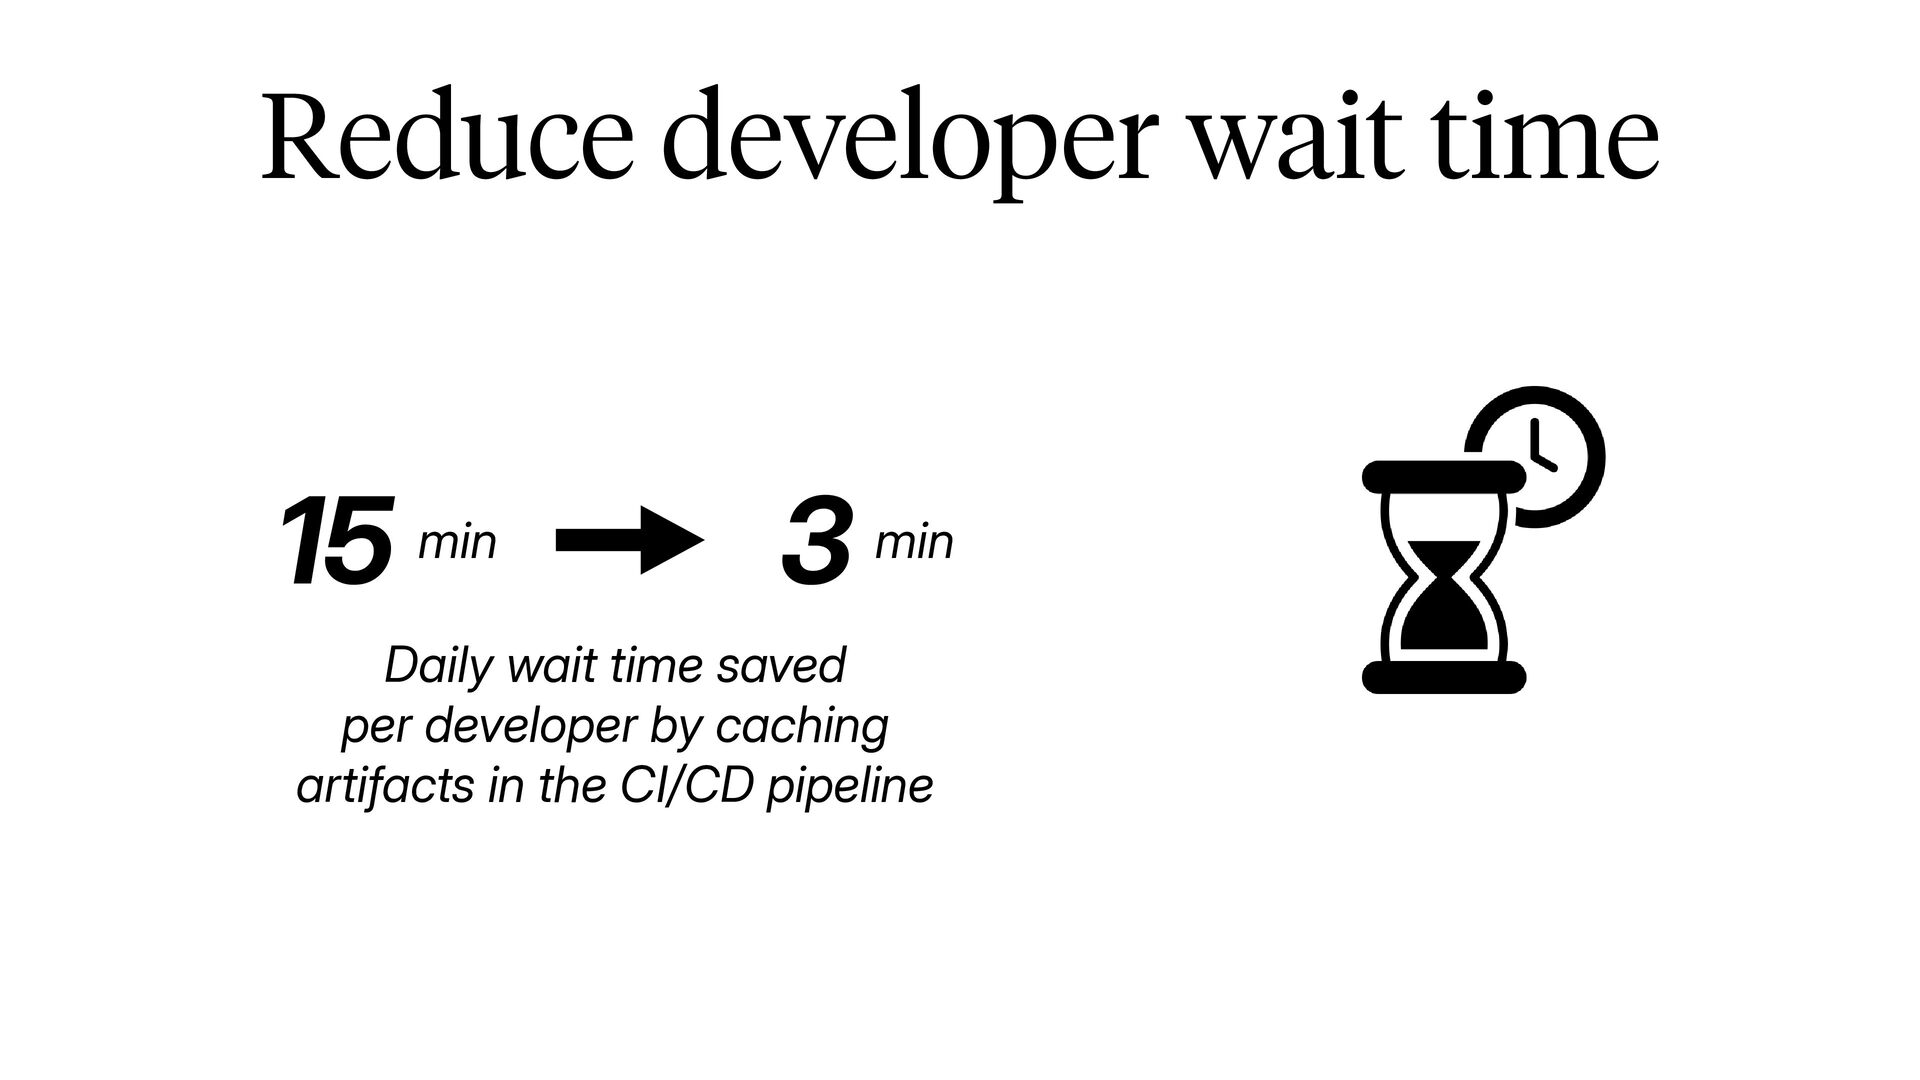
  8. Reduce developer wait time 15 min 3 min Daily wait

    time saved per developer by caching artifacts in the CI/CD pipeline
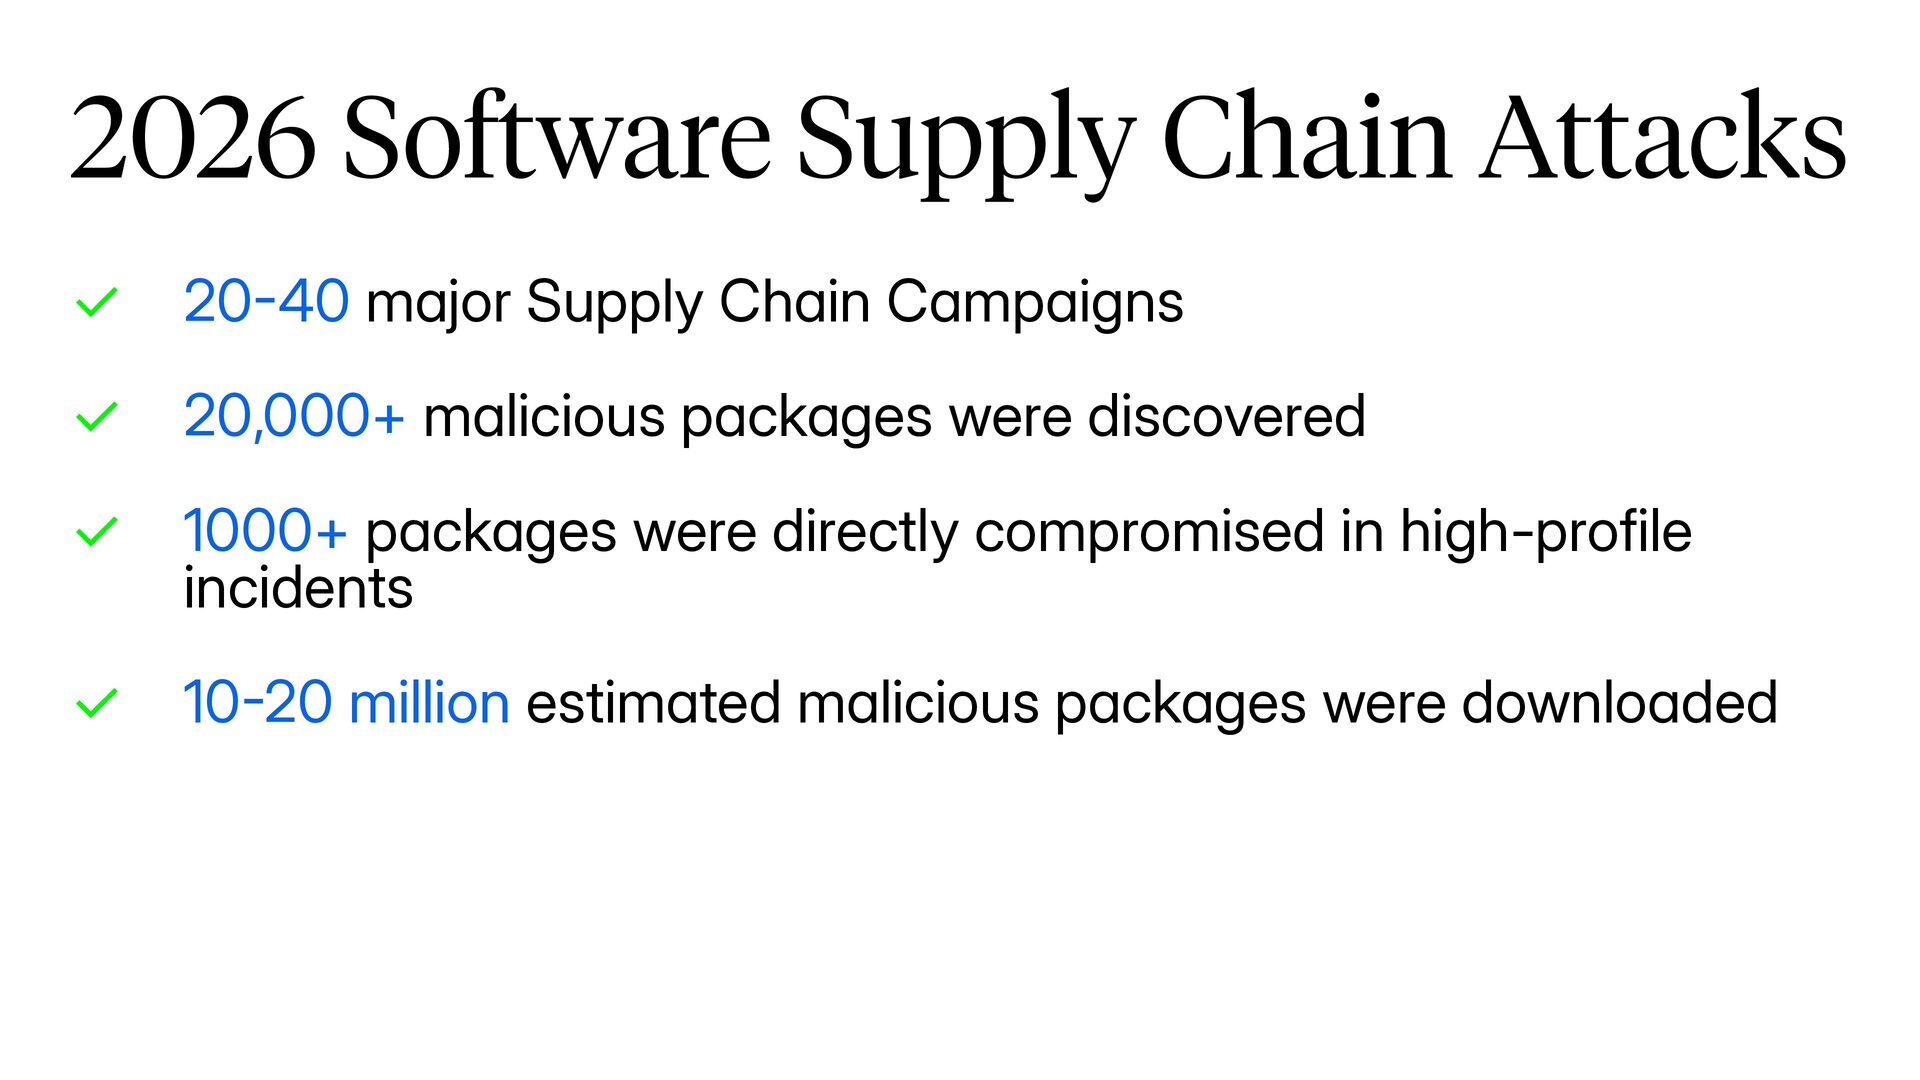
  9. - - 2026 Software Supply Chain Attacks ✓ 20 40

    major Supply Chain Campaigns ✓ 20,000+ malicious packages were discovered ✓ 1000+ packages were directly compromised in high-profile incidents ✓ 10 20 million estimated malicious packages were downloaded
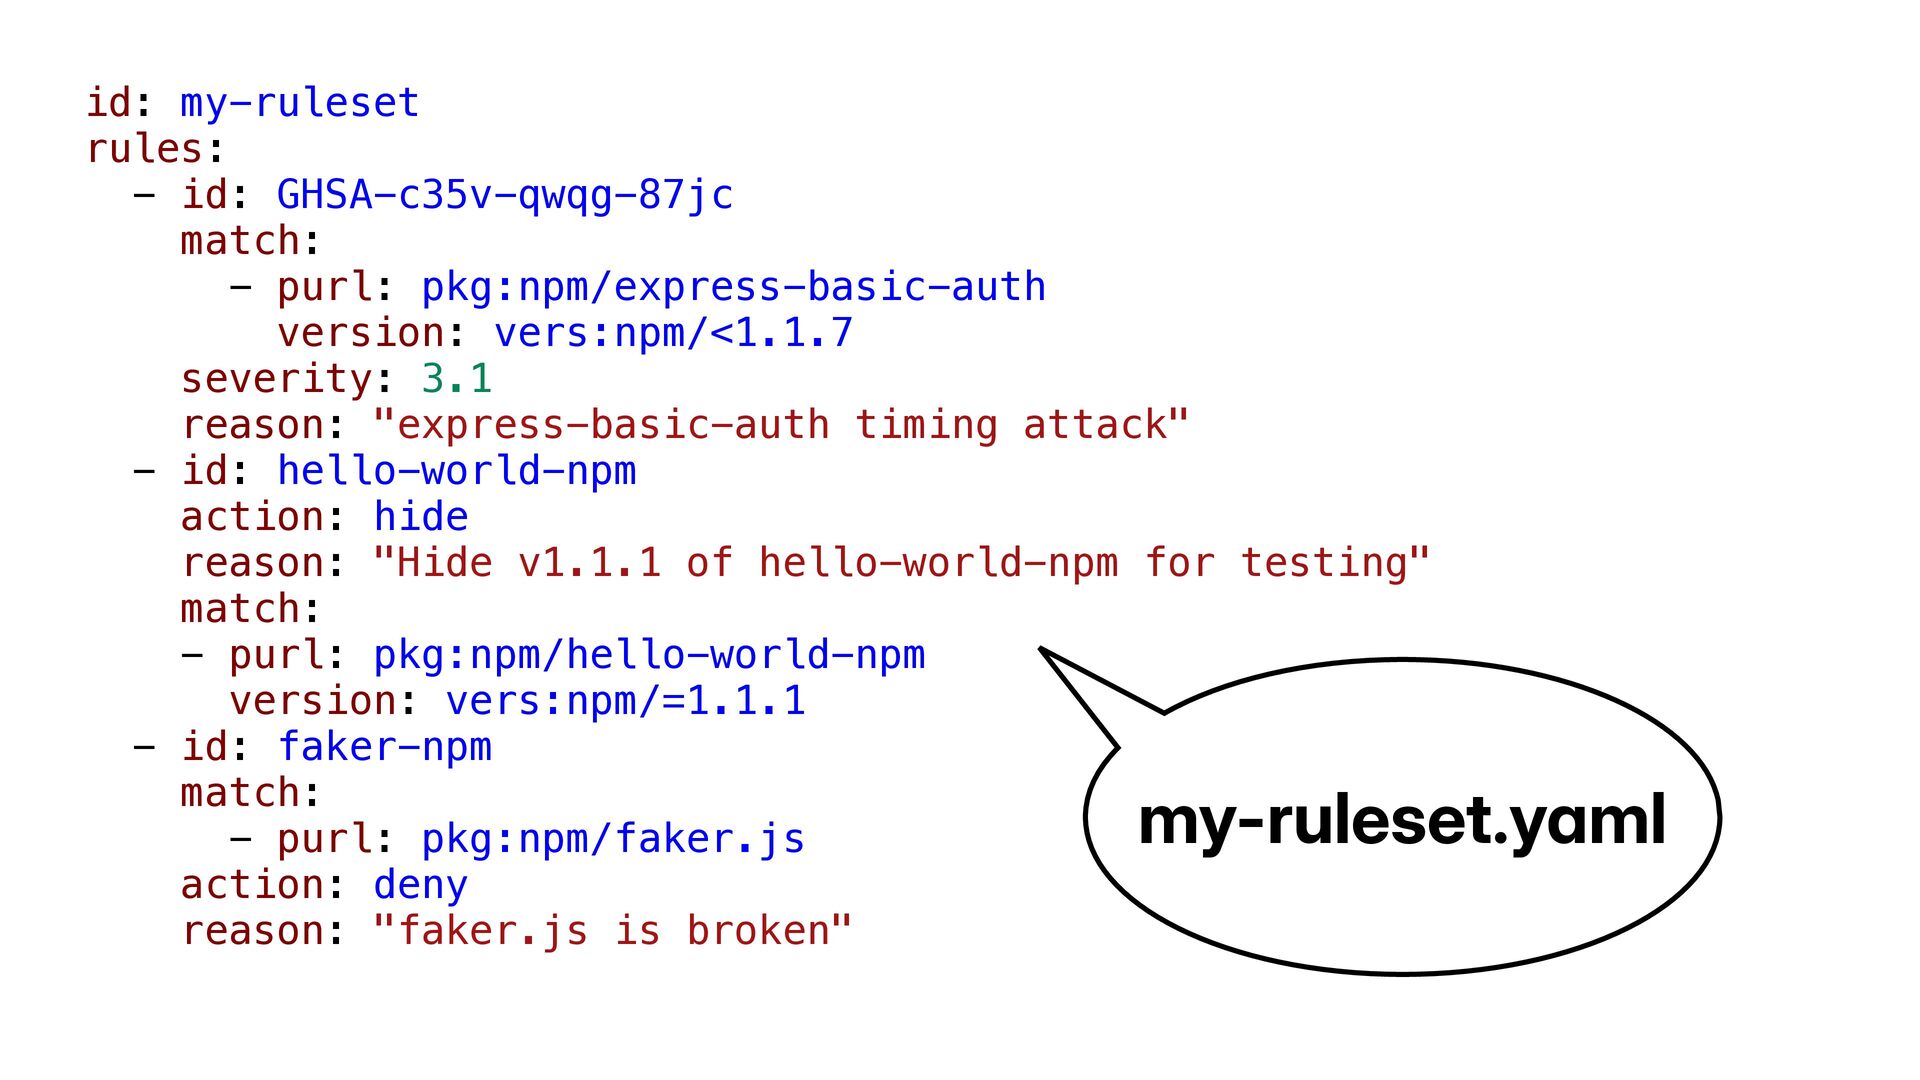
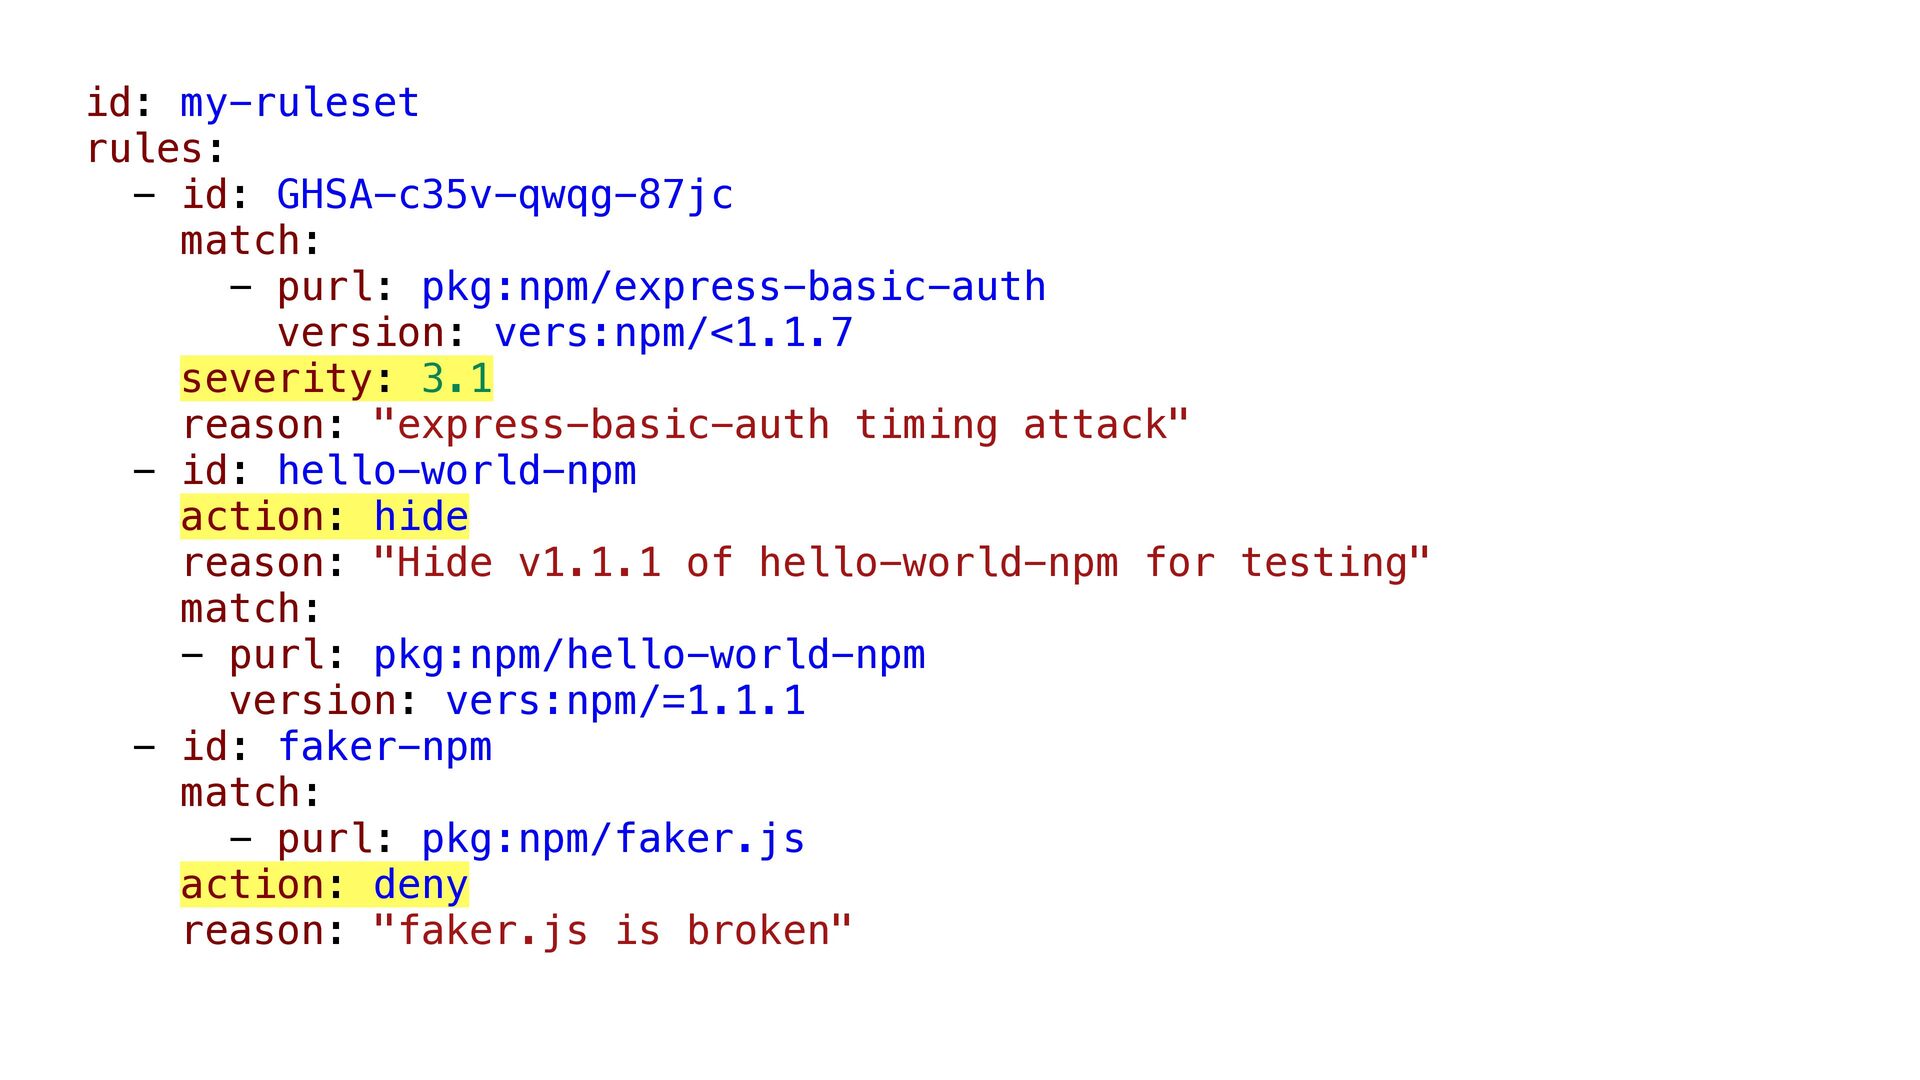
  10. id: my-ruleset rules: - id: GHSA-c35v-qwqg-87jc match: - purl: pkg:npm/express-basic-auth

    version: vers:npm/<1.1.7 severity: 3.1 reason: "express-basic-auth timing attack" - id: hello-world-npm action: hide reason: "Hide v1.1.1 of hello-world-npm for testing" match: - purl: pkg:npm/hello-world-npm version: vers:npm/=1.1.1 - id: faker-npm match: - purl: pkg:npm/faker.js action: deny reason: "faker.js is broken" my-ruleset.yaml
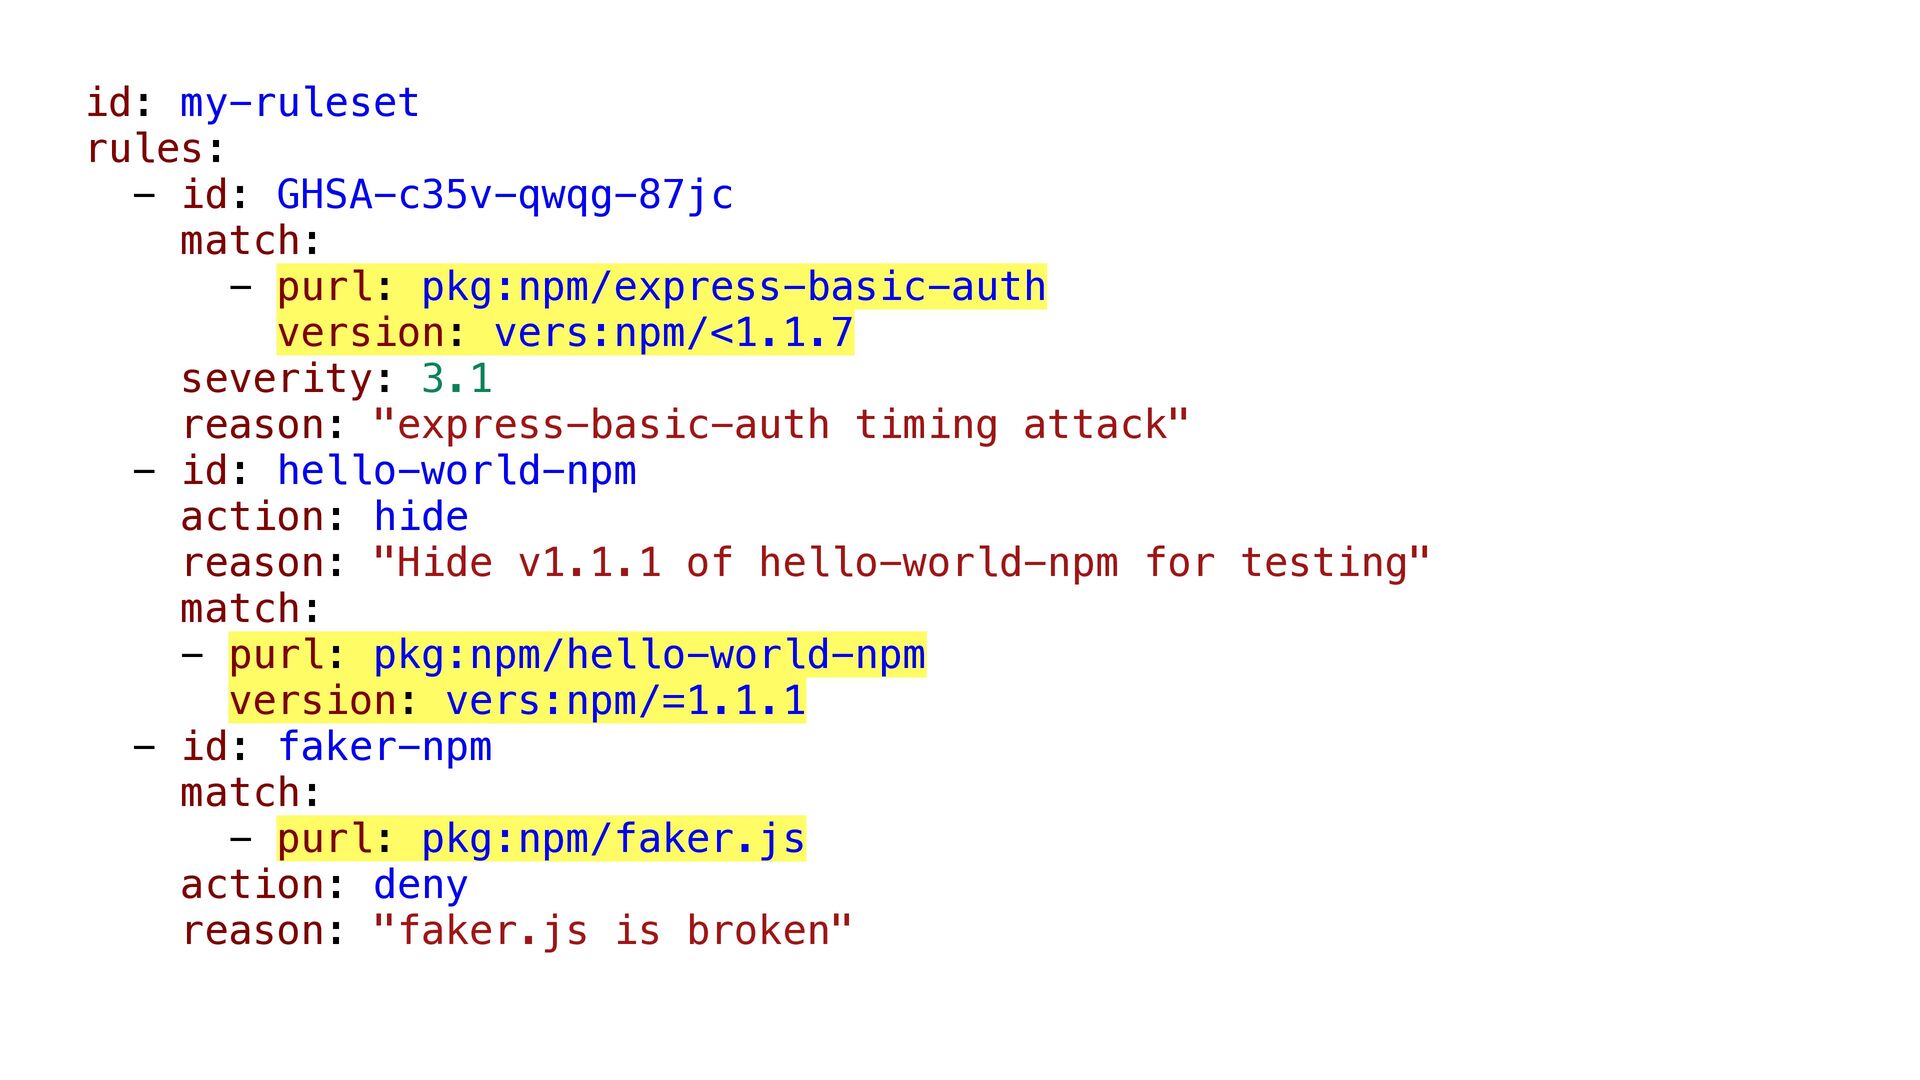
  11. id: my-ruleset rules: - id: GHSA-c35v-qwqg-87jc match: - purl: pkg:npm/express-basic-auth

    version: vers:npm/<1.1.7 severity: 3.1 reason: "express-basic-auth timing attack" - id: hello-world-npm action: hide reason: "Hide v1.1.1 of hello-world-npm for testing" match: - purl: pkg:npm/hello-world-npm version: vers:npm/=1.1.1 - id: faker-npm match: - purl: pkg:npm/faker.js action: deny reason: "faker.js is broken"
  12. id: my-ruleset rules: - id: GHSA-c35v-qwqg-87jc match: - purl: pkg:npm/express-basic-auth

    version: vers:npm/<1.1.7 severity: 3.1 reason: "express-basic-auth timing attack" - id: hello-world-npm action: hide reason: "Hide v1.1.1 of hello-world-npm for testing" match: - purl: pkg:npm/hello-world-npm version: vers:npm/=1.1.1 - id: faker-npm match: - purl: pkg:npm/faker.js action: deny reason: "faker.js is broken"
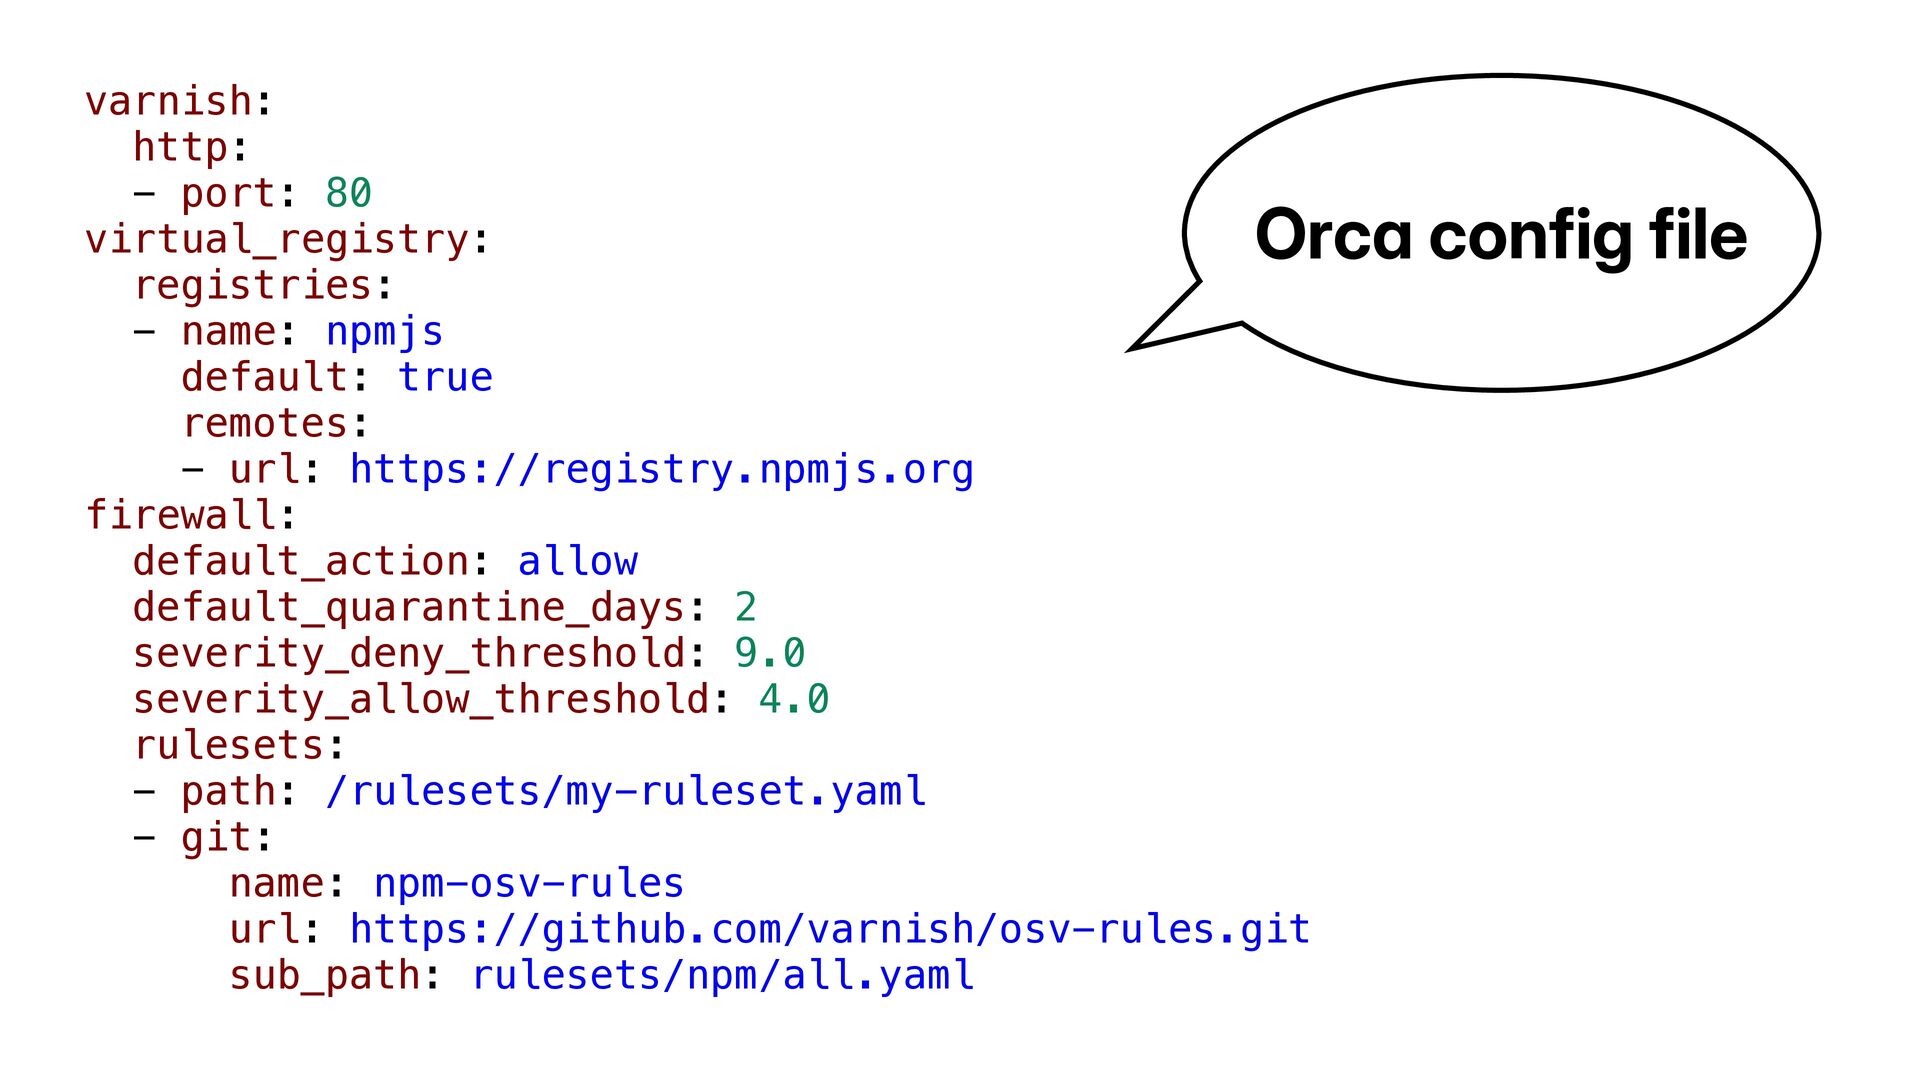
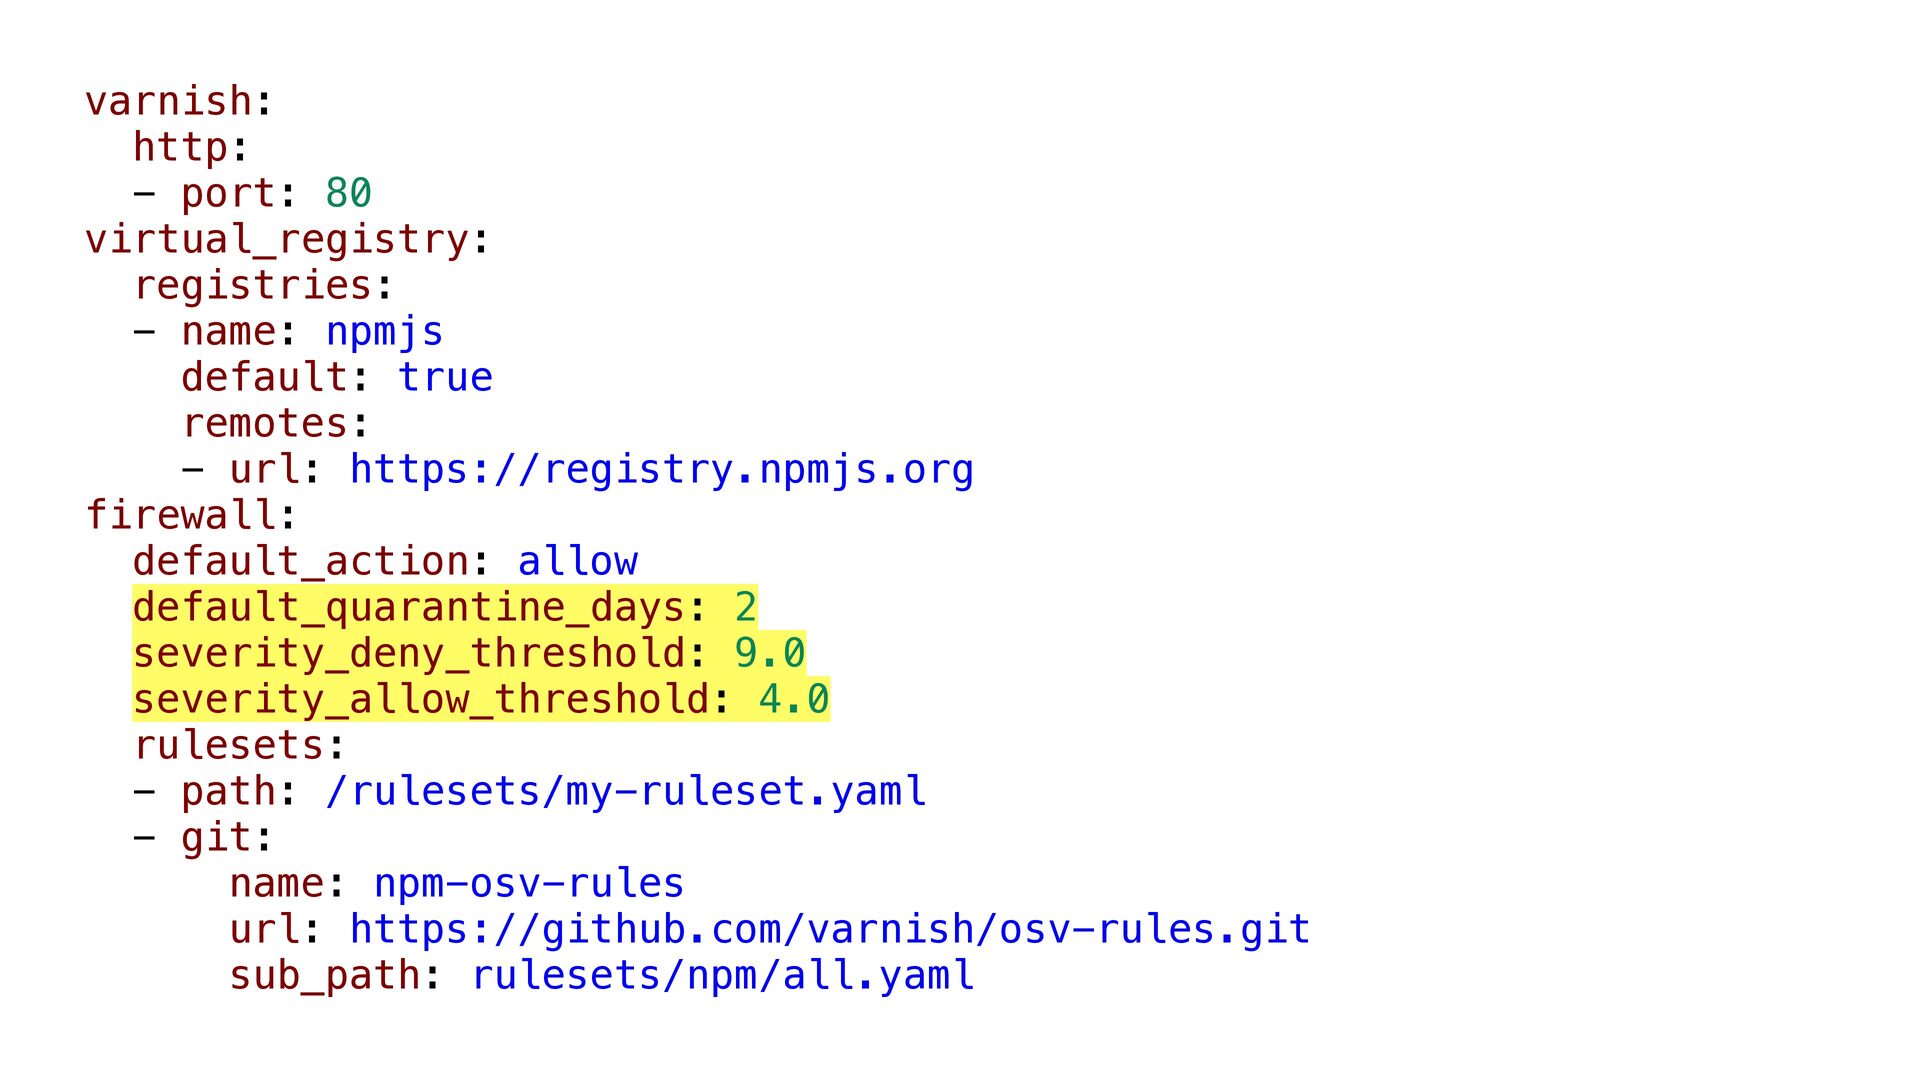
  13. varnish: http: - port: 80 virtual_registry: registries: - name: npmjs

    default: true remotes: - url: https://registry.npmjs.org firewall: default_action: allow default_quarantine_days: 2 severity_deny_threshold: 9.0 severity_allow_threshold: 4.0 rulesets: - path: /rulesets/my-ruleset.yaml - git: name: npm-osv-rules url: https://github.com/varnish/osv-rules.git sub_path: rulesets/npm/all.yaml Orca config file
  14. varnish: http: - port: 80 virtual_registry: registries: - name: npmjs

    default: true remotes: - url: https://registry.npmjs.org firewall: default_action: allow default_quarantine_days: 2 severity_deny_threshold: 9.0 severity_allow_threshold: 4.0 rulesets: - path: /rulesets/my-ruleset.yaml - git: name: npm-osv-rules url: https://github.com/varnish/osv-rules.git sub_path: rulesets/npm/all.yaml
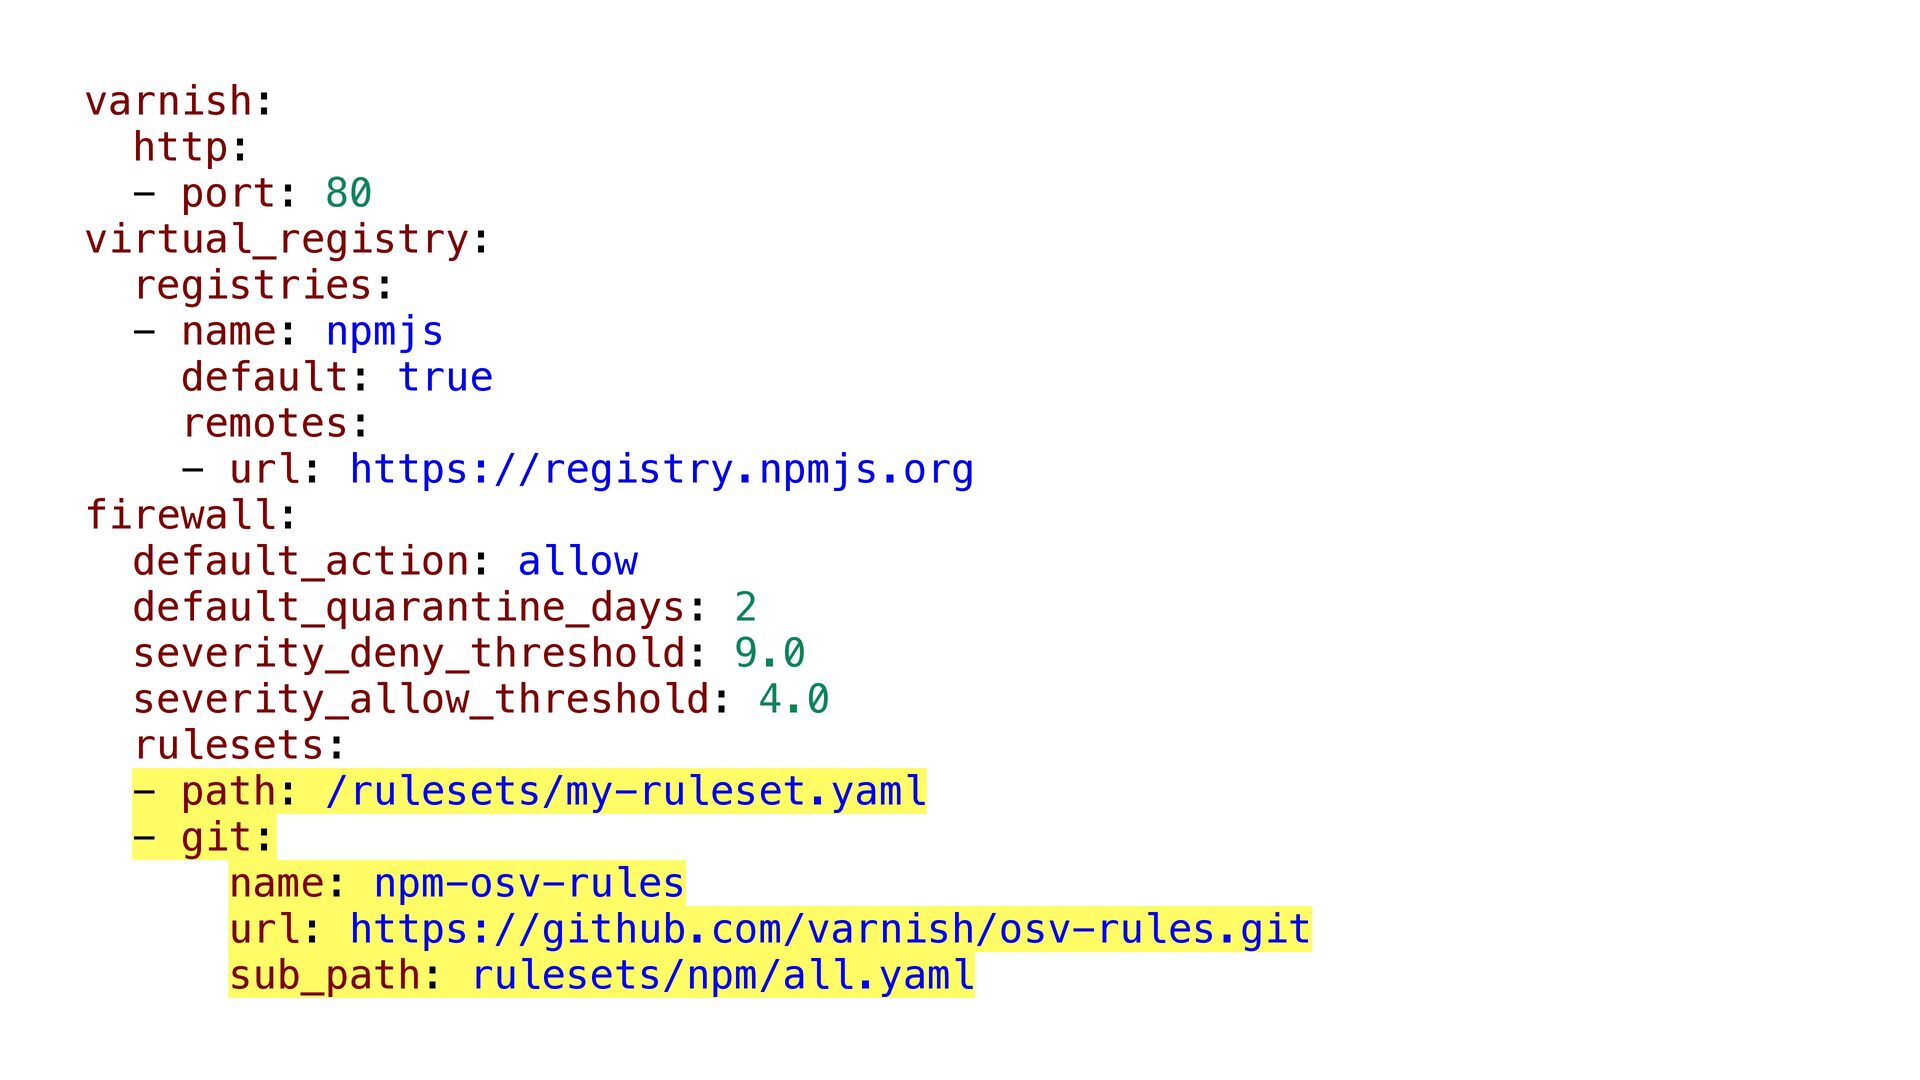
  15. varnish: http: - port: 80 virtual_registry: registries: - name: npmjs

    default: true remotes: - url: https://registry.npmjs.org firewall: default_action: allow default_quarantine_days: 2 severity_deny_threshold: 9.0 severity_allow_threshold: 4.0 rulesets: - path: /rulesets/my-ruleset.yaml - git: name: npm-osv-rules url: https://github.com/varnish/osv-rules.git sub_path: rulesets/npm/all.yaml
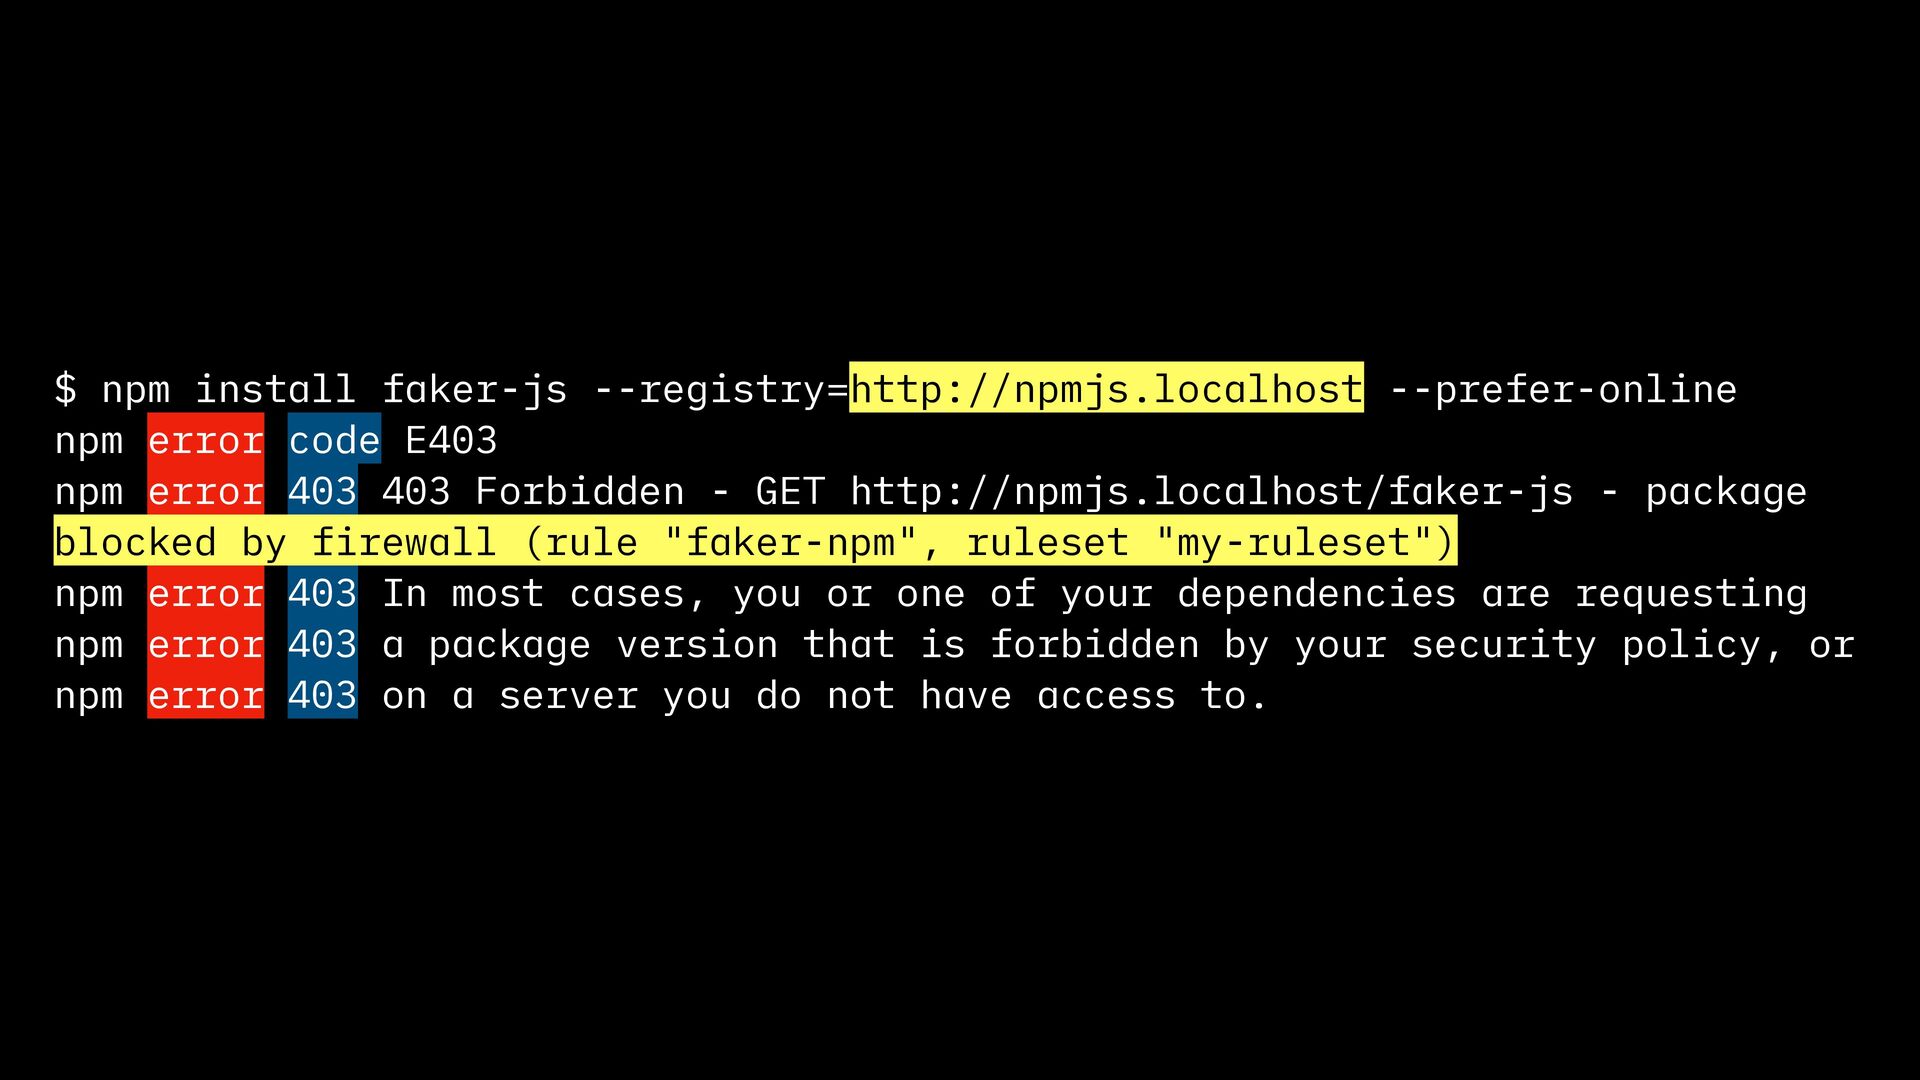
  16. $ npm install faker-js --registry=http://npmjs.localhost --prefer-online npm error code E403

    npm error 403 403 Forbidden - GET http://npmjs.localhost/faker-js - package blocked by firewall (rule "faker-npm", ruleset "my-ruleset") npm error 403 In most cases, you or one of your dependencies are requesting npm error 403 a package version that is forbidden by your security policy, or npm error 403 on a server you do not have access to.

More Decks by Thijs Feryn

Other Decks in Technology