Share
Embed
Guard: o poder da autenticação do Symfony Security
Existem muitas maneiras interessantes de autenticar um usuário: API token, social login, um formulário HTML tradicional ou qualquer outra coisa que você possa imaginar.
Mas criar um sistema de autenticação personalizado no Symfony costumava significar muitos arquivos, muito código e muita complexidade. Agora, não mais.
Symfony Guard: um sistema de autenticação simples, mas expansível, parte do componente Symfony Security. Com poucas classes conseguimos implementar autenticação por API token, social login ou até mesmo integrar com algum sistema de autenticação legado.
Não significa que não teremos trabalho algum de implementação, mas o que teremos vai ser mais claro, simples e divertido.

Diana Arnos
May 17, 2019
Transcript
113 slides
-
@dianaarnos Dev, Sec, Music, Kung Fu. Dev / Architect @
Senha Segura Evangelist @ PHPSP Evangelist @ PHPWomenBR -
AUTENTICAÇÃO É O PROCESSO DE IDENTIFICAR SE ALGUÉM É QUEM
REALMENTE DIZ SER -
AUTORIZAÇÃO É O PROCESSO DE VERIFICAR SE ESSE ALGUÉM PODE
EXECUTAR DETERMINADA AÇÃO -
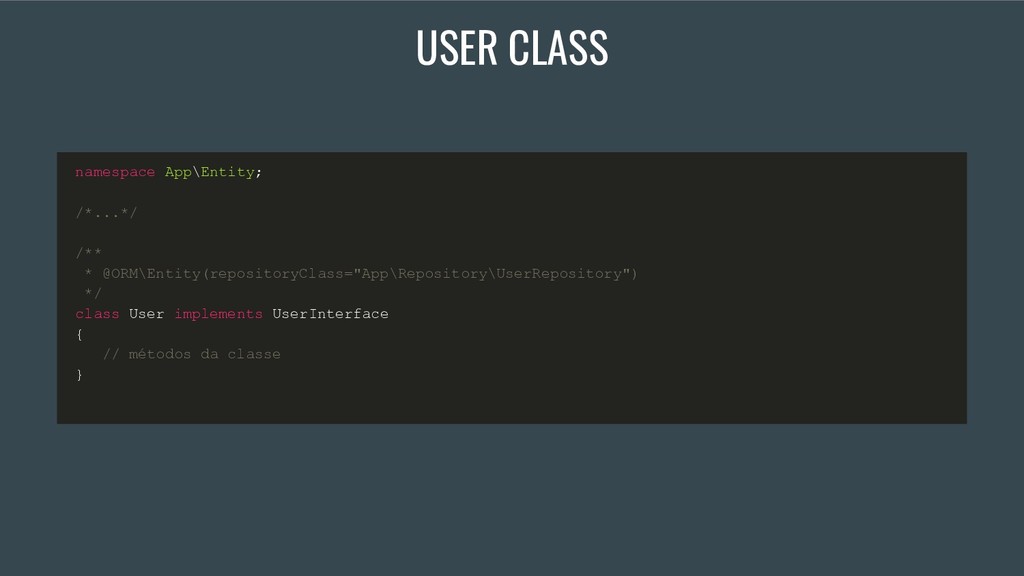
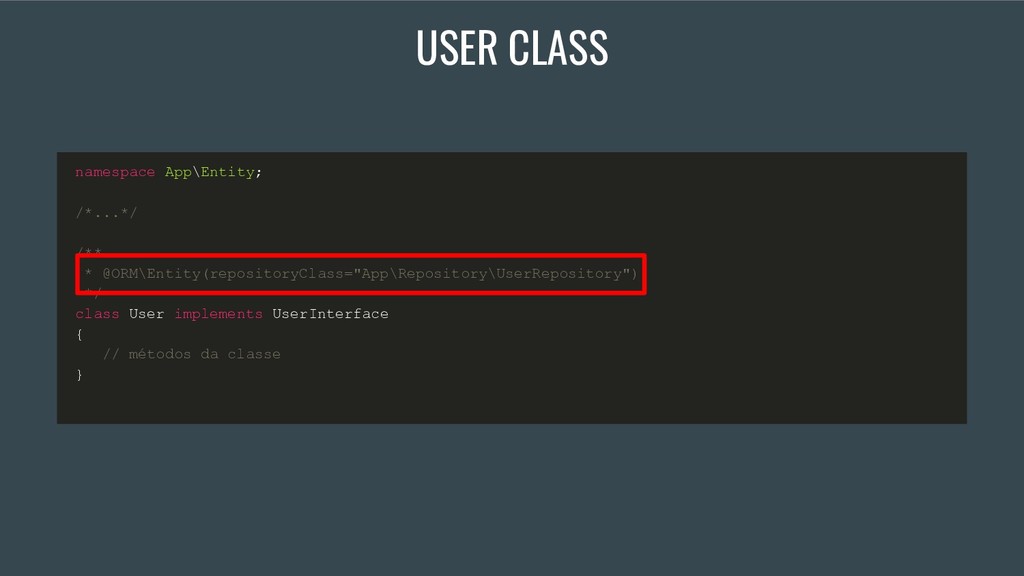
namespace App\Entity; /*...*/ /** * @ORM\Entity(repositoryClass="App\Repository\UserRepository") */ class User implements
UserInterface { // métodos da classe } USER CLASS -
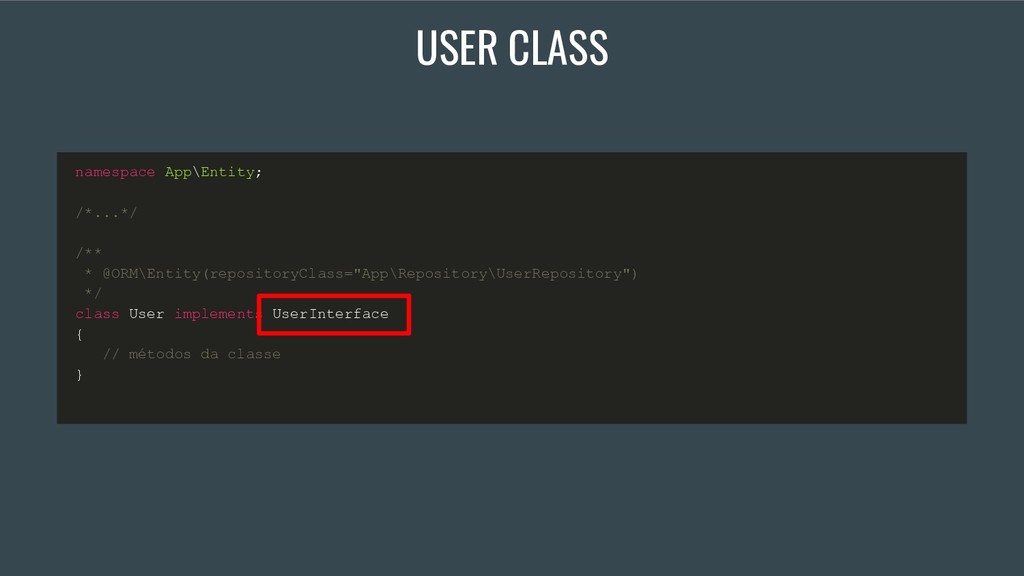
namespace App\Entity; /*...*/ /** * @ORM\Entity(repositoryClass="App\Repository\UserRepository") */ class User implements
UserInterface { // métodos da classe } USER CLASS -
namespace App\Entity; /*...*/ /** * @ORM\Entity(repositoryClass="App\Repository\UserRepository") */ class User implements
UserInterface { // métodos da classe } USER CLASS -
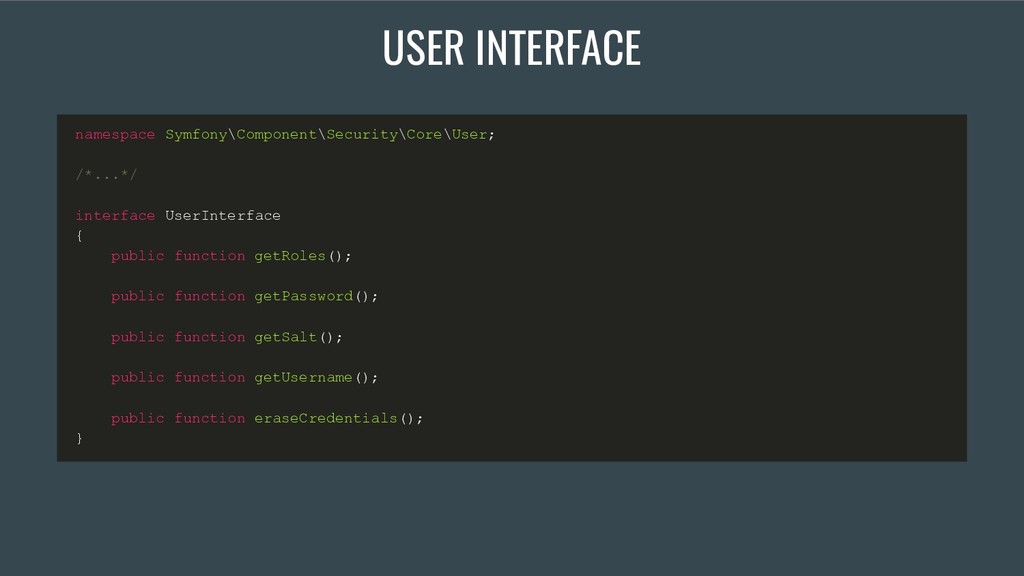
namespace Symfony\Component\Security\Core\User; /*...*/ interface UserInterface { public function getRoles(); public
function getPassword(); public function getSalt(); public function getUsername(); public function eraseCredentials(); } USER INTERFACE -
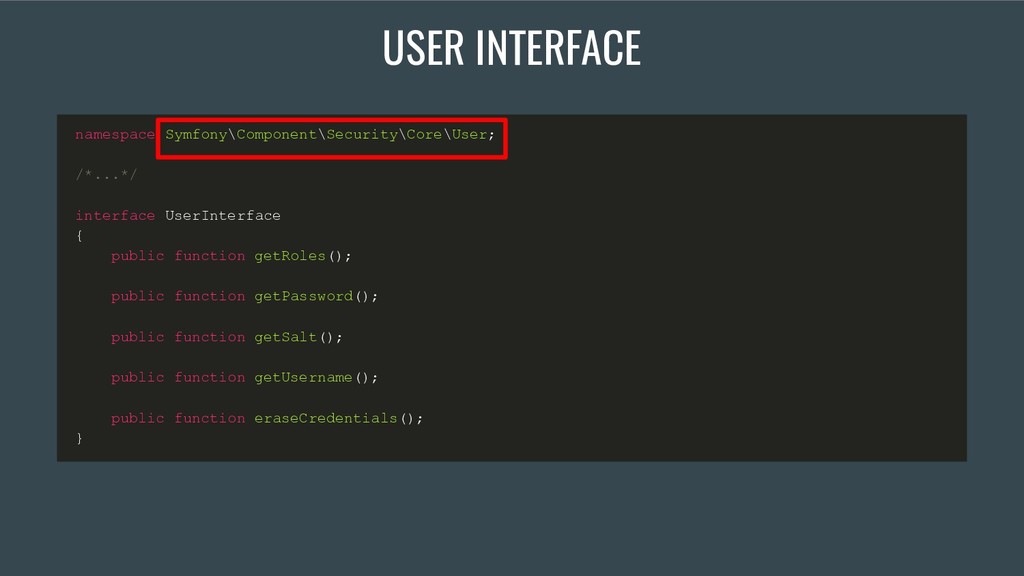
namespace Symfony\Component\Security\Core\User; /*...*/ interface UserInterface { public function getRoles(); public
function getPassword(); public function getSalt(); public function getUsername(); public function eraseCredentials(); } USER INTERFACE -
What style of authentication do you want? [Empty authenticator ]:
[0] Empty authenticator [1] Login form authenticator > 1 The class name of the authenticator to create (e.g. AppCustomAuthenticator ): > LoginFormAuthenticator Choose a name for the controller class (e.g. SecurityController ) [SecurityController ]: > -
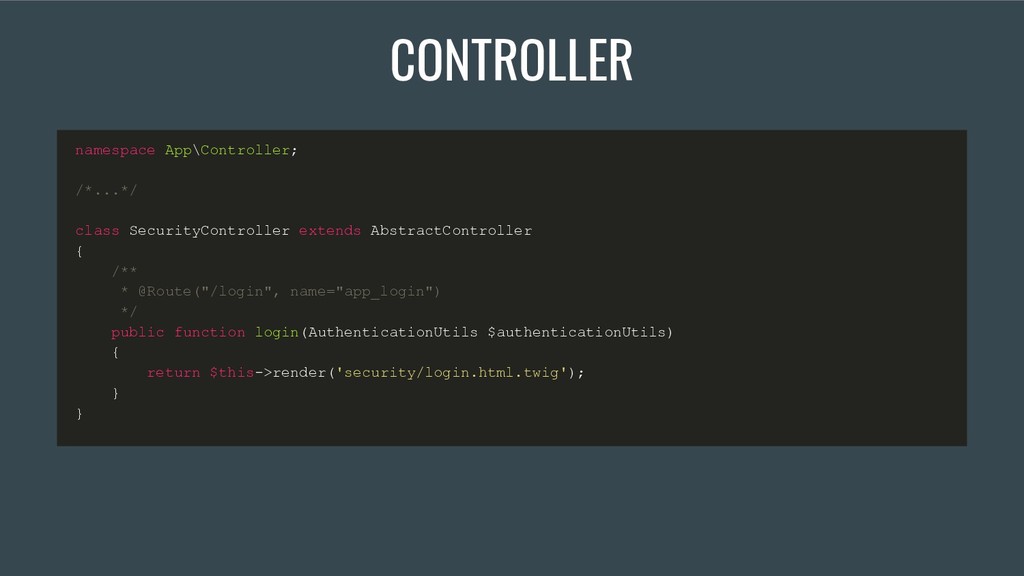
CONTROLLER namespace App\Controller; /*...*/ class SecurityController extends AbstractController { /**
* @Route("/login", name="app_login") */ public function login(AuthenticationUtils $authenticationUtils) { return $this->render('security/login.html.twig'); } } -
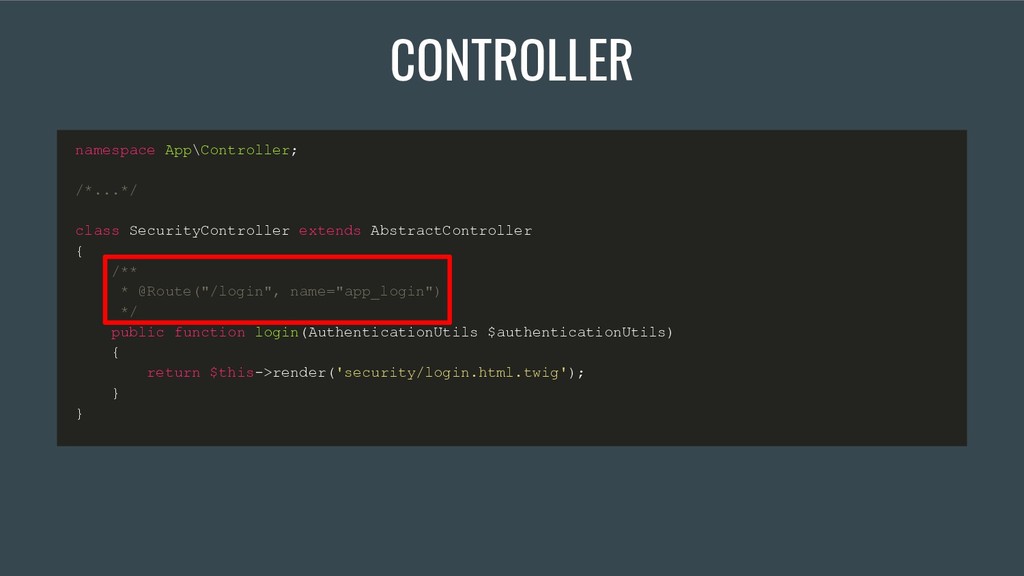
CONTROLLER namespace App\Controller; /*...*/ class SecurityController extends AbstractController { /**
* @Route("/login", name="app_login") */ public function login(AuthenticationUtils $authenticationUtils) { return $this->render('security/login.html.twig'); } } -
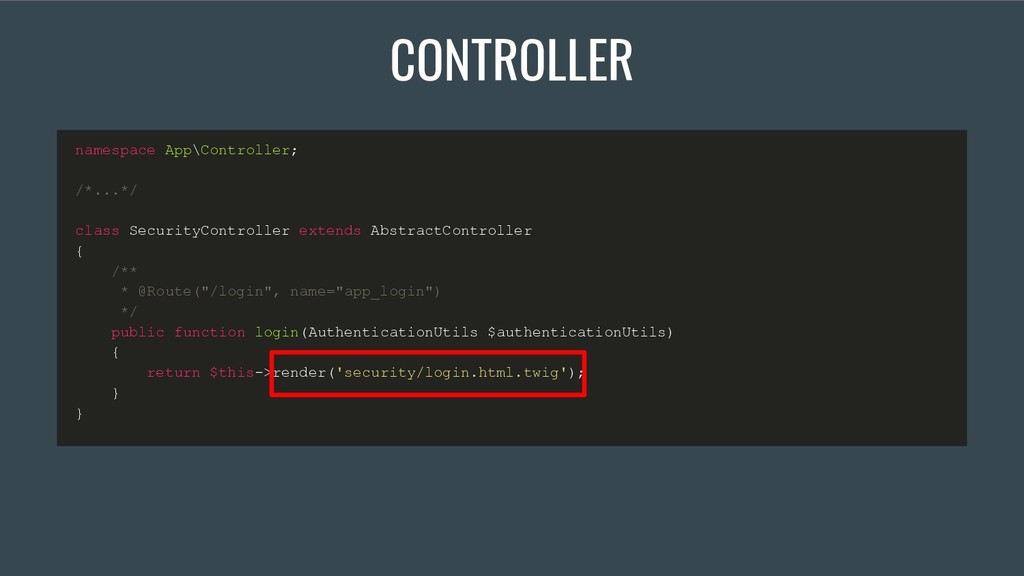
CONTROLLER namespace App\Controller; /*...*/ class SecurityController extends AbstractController { /**
* @Route("/login", name="app_login") */ public function login(AuthenticationUtils $authenticationUtils) { return $this->render('security/login.html.twig'); } } -
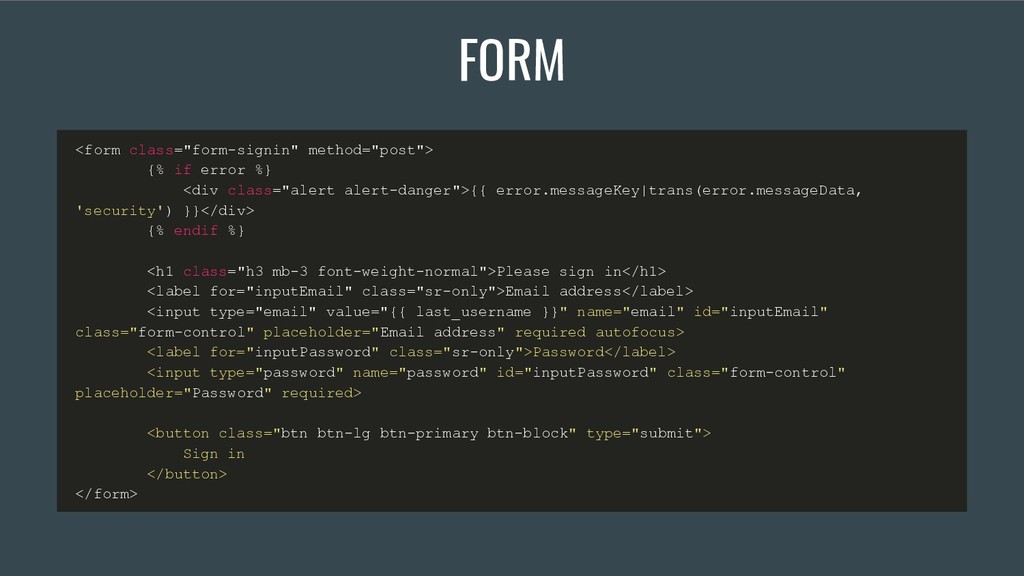
FORM <form class="form-signin" method="post"> {% if error %} <div class="alert
alert-danger">{{ error.messageKey|trans(error.messageData, 'security') }}</div> {% endif %} <h1 class="h3 mb-3 font-weight-normal">Please sign in</h1> <label for="inputEmail" class="sr-only">Email address</label> <input type="email" value="{{ last_username }}" name="email" id="inputEmail" class="form-control" placeholder="Email address" required autofocus> <label for="inputPassword" class="sr-only">Password</label> <input type="password" name="password" id="inputPassword" class="form-control" placeholder="Password" required> <button class="btn btn-lg btn-primary btn-block" type="submit"> Sign in </button> </form> -
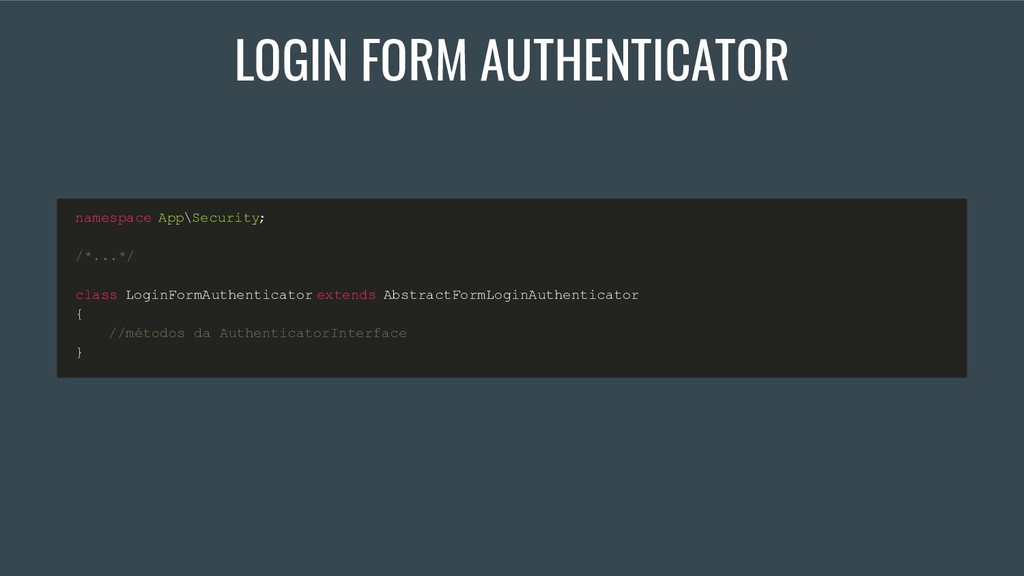
LOGIN FORM AUTHENTICATOR namespace App\Security; /*...*/ class LoginFormAuthenticator extends AbstractFormLoginAuthenticator
{ //métodos da AuthenticatorInterface } -
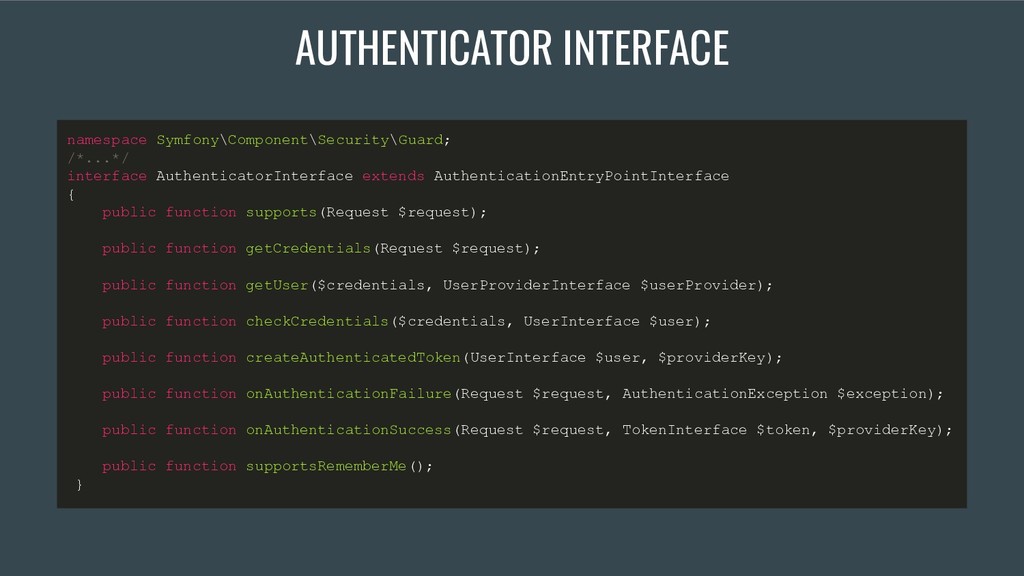
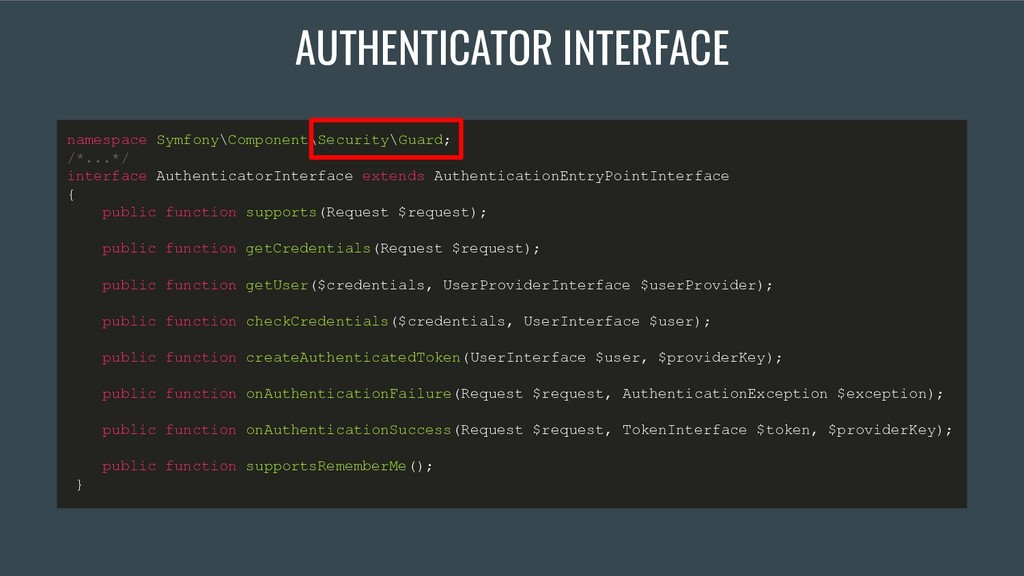
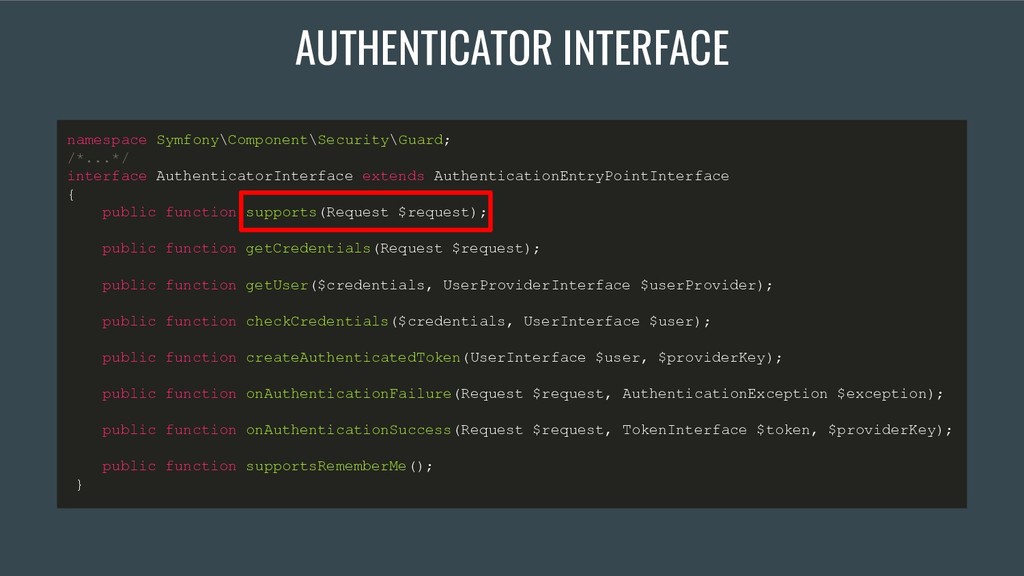
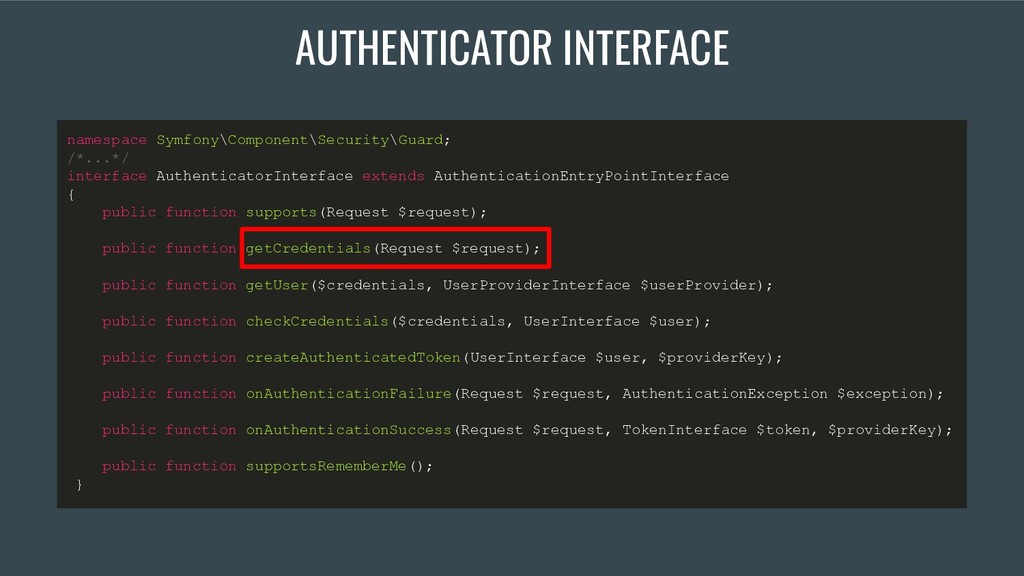
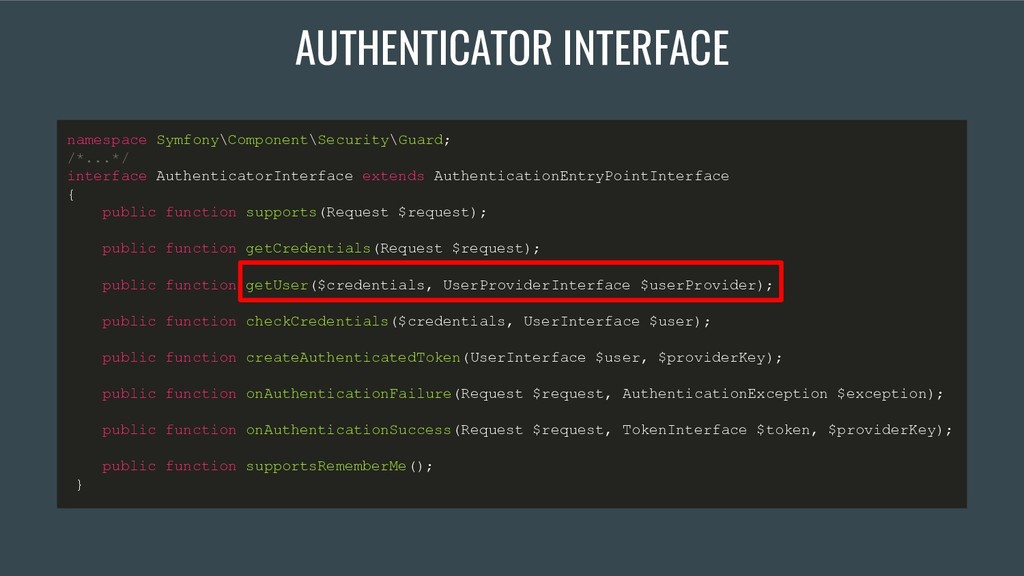
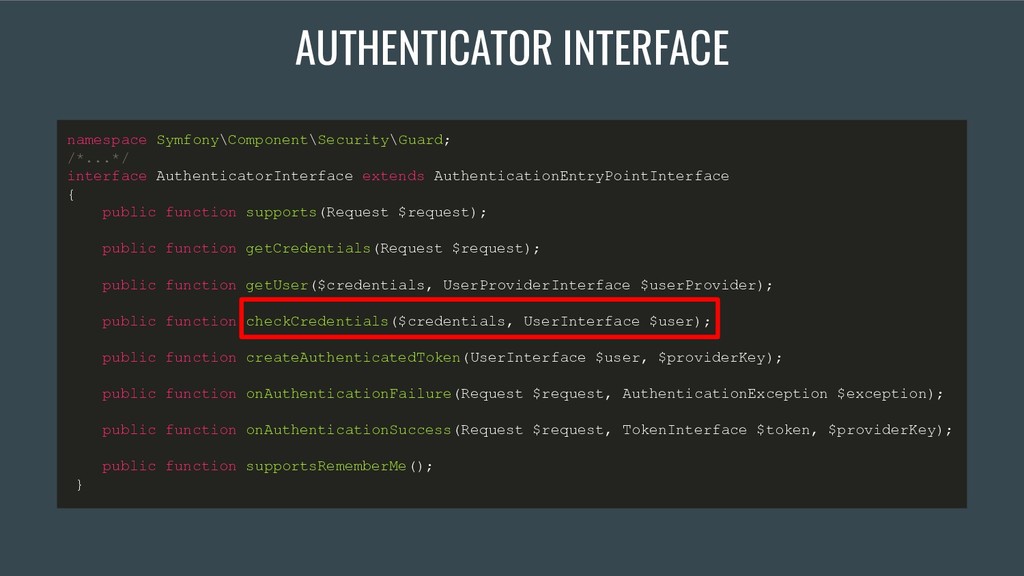
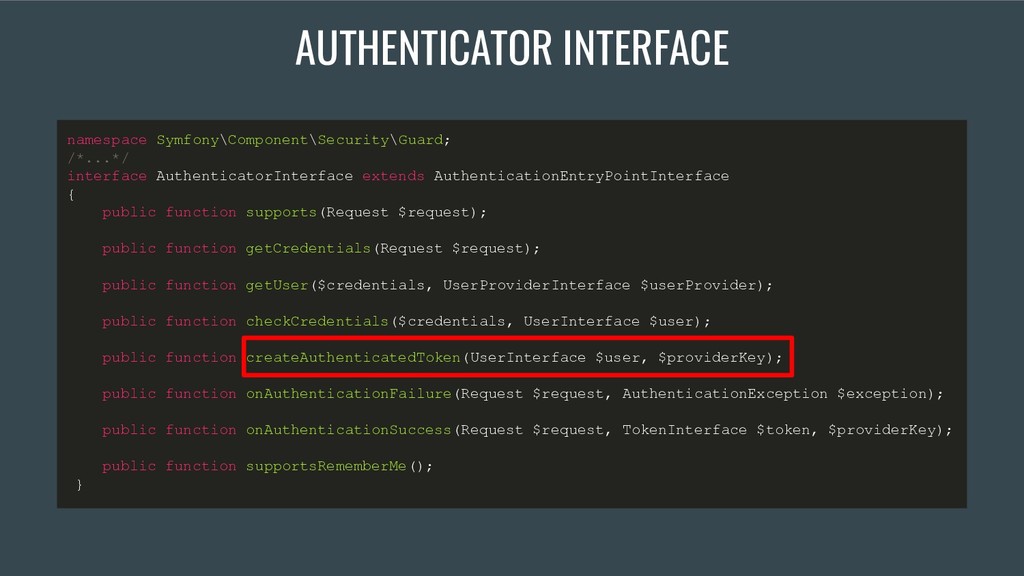
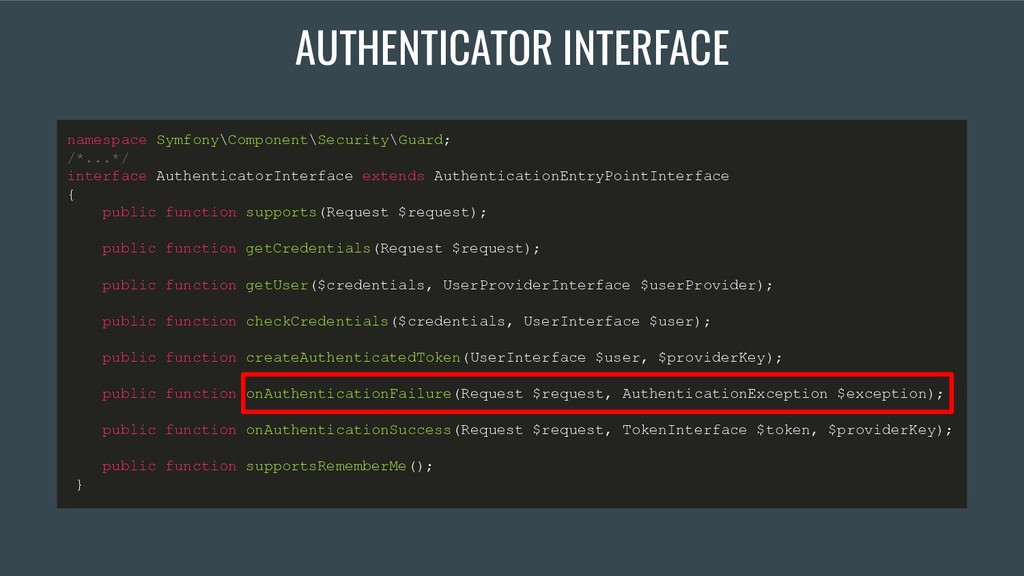
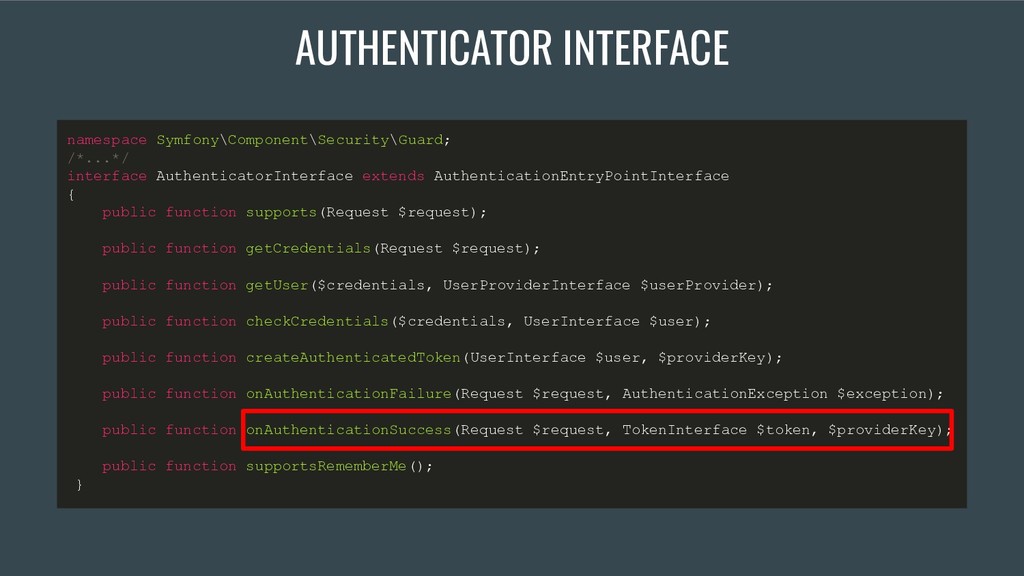
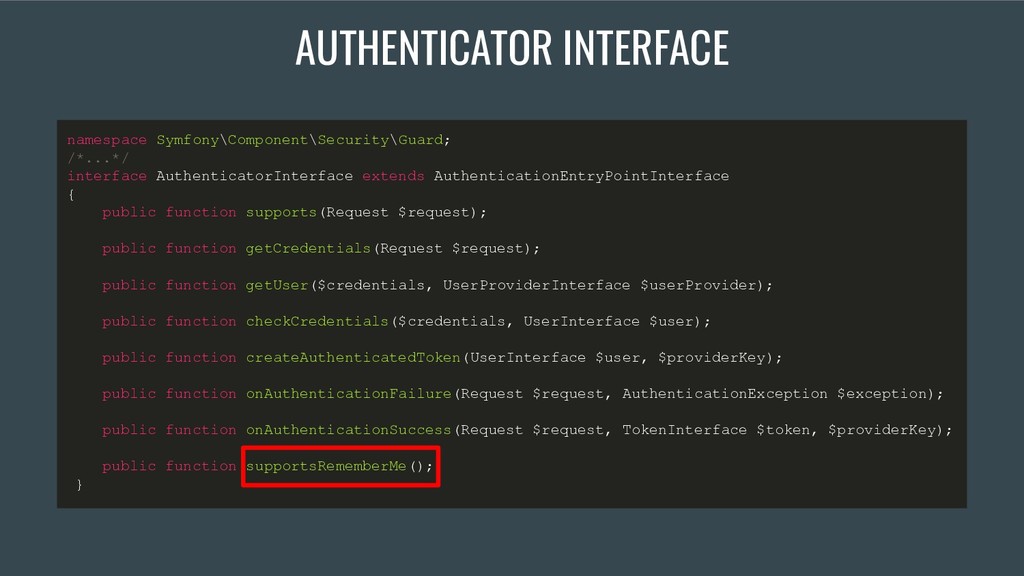
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
namespace Symfony\Component\Security\Guard; /*...*/ interface AuthenticatorInterface extends AuthenticationEntryPointInterface { public function
supports(Request $request); public function getCredentials(Request $request); public function getUser($credentials, UserProviderInterface $userProvider); public function checkCredentials($credentials, UserInterface $user); public function createAuthenticatedToken(UserInterface $user, $providerKey); public function onAuthenticationFailure(Request $request, AuthenticationException $exception); public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey); public function supportsRememberMe(); } AUTHENTICATOR INTERFACE -
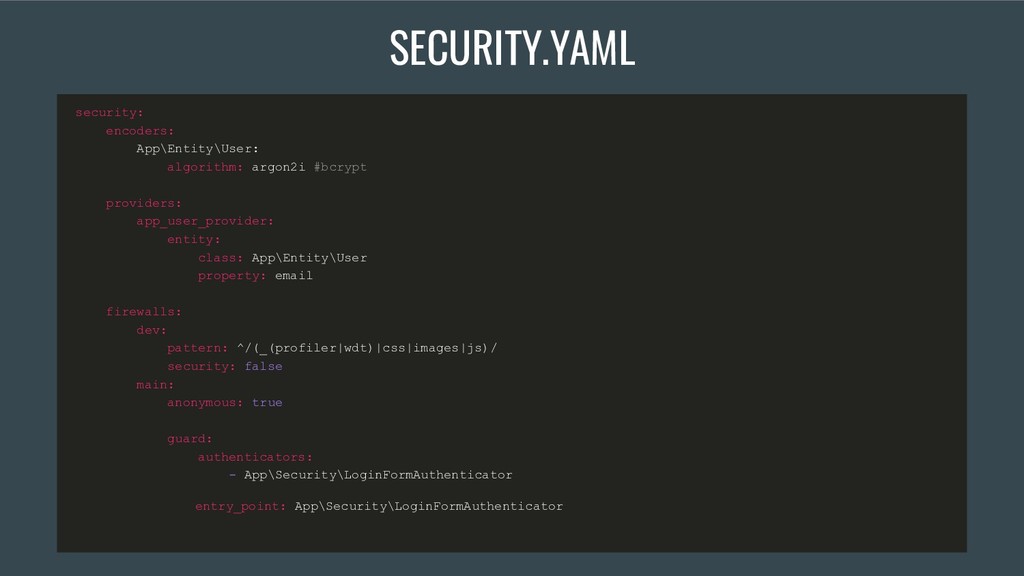
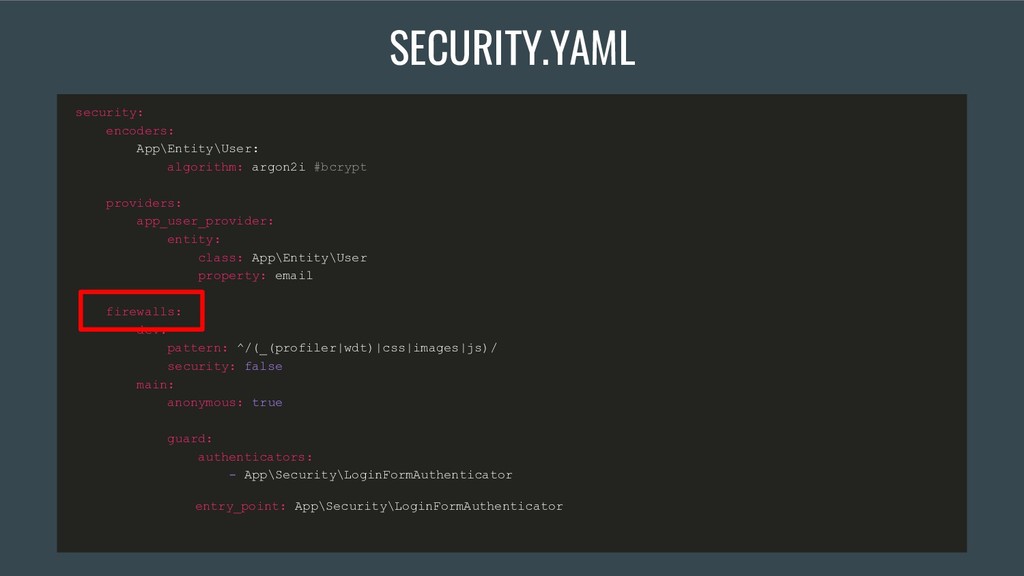
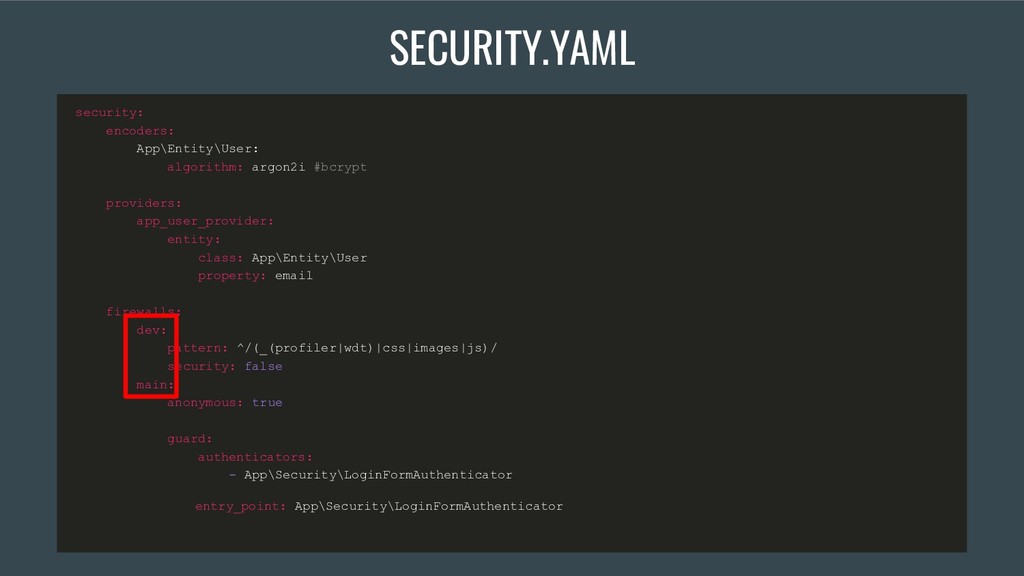
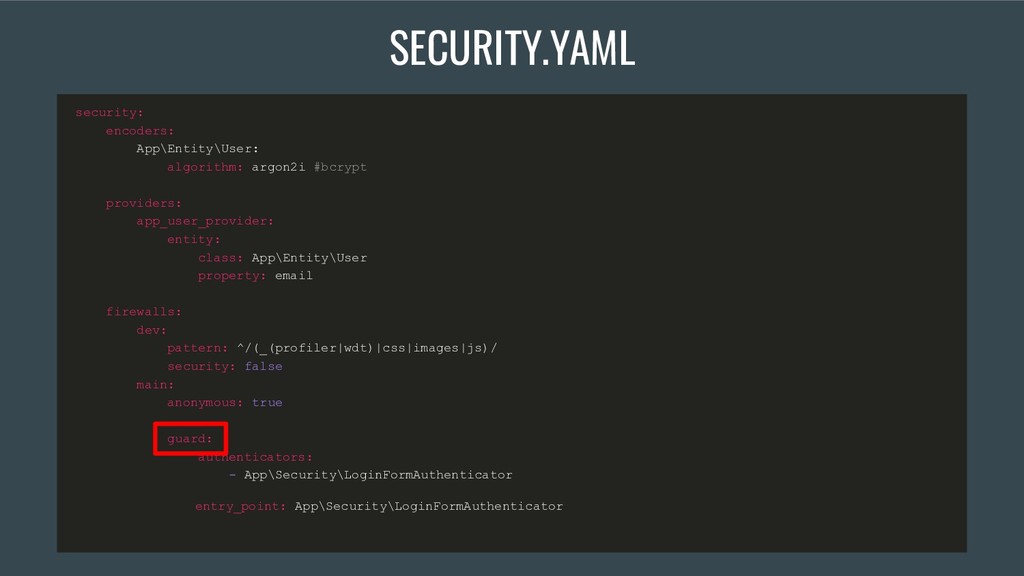
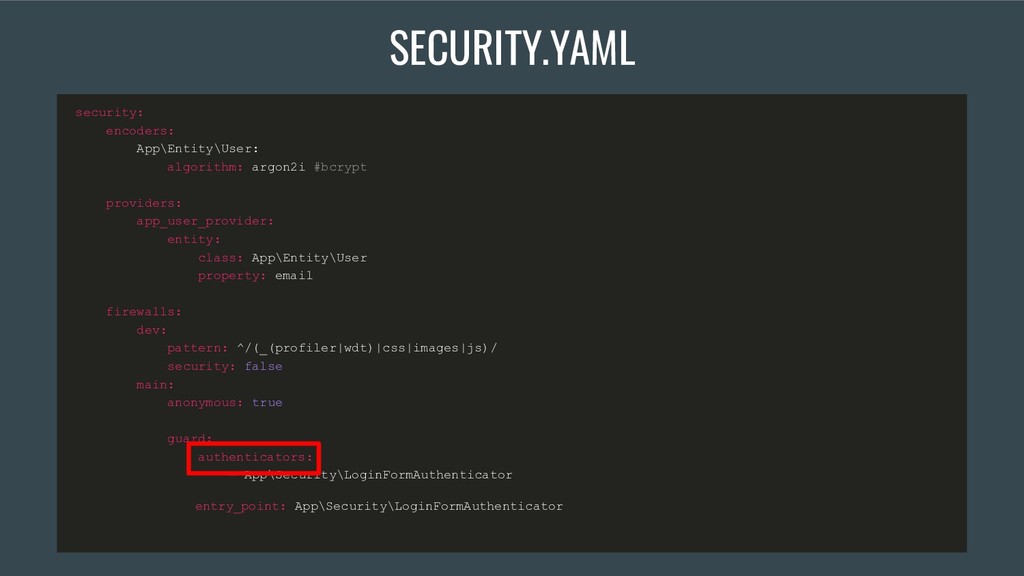
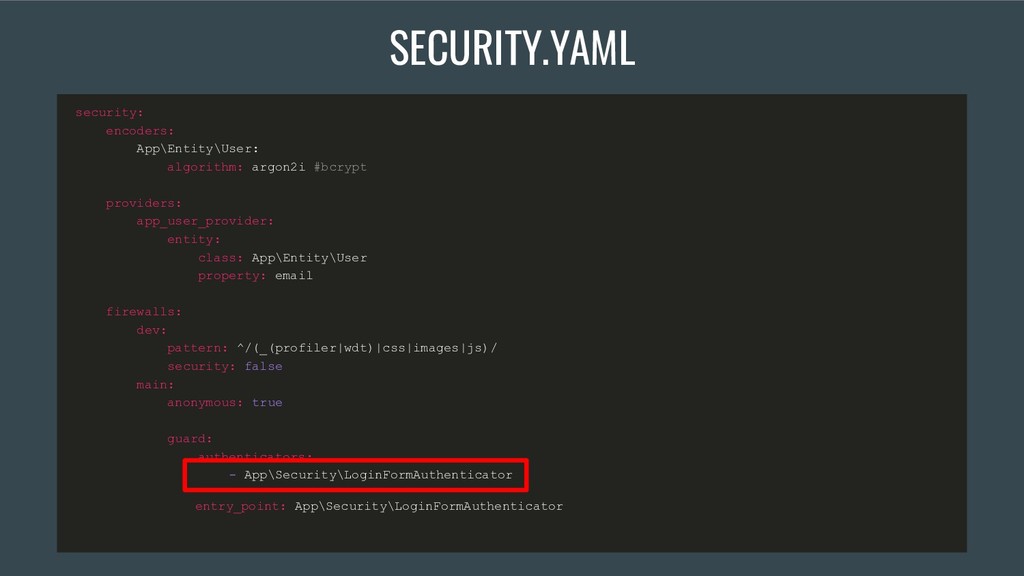
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
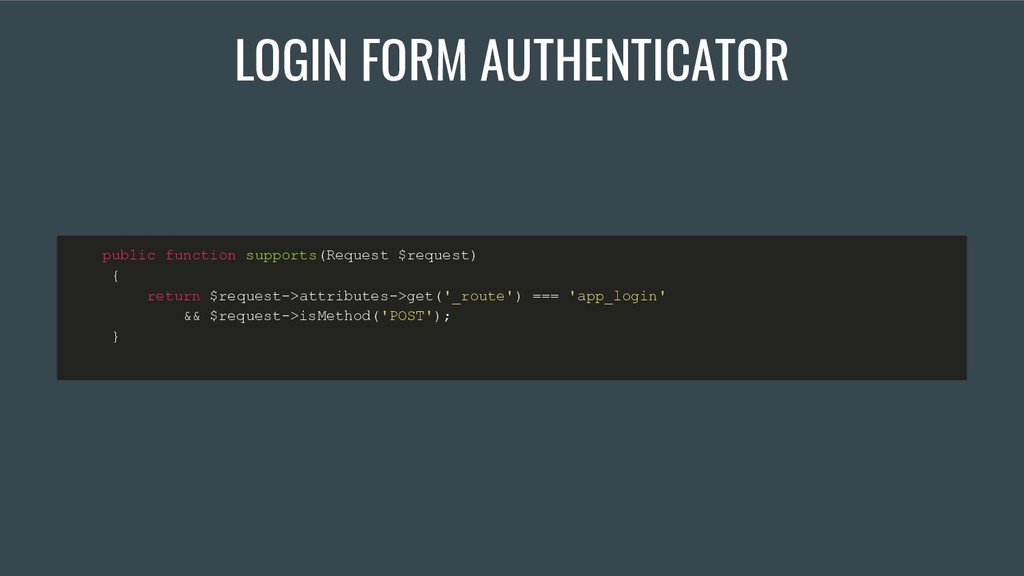
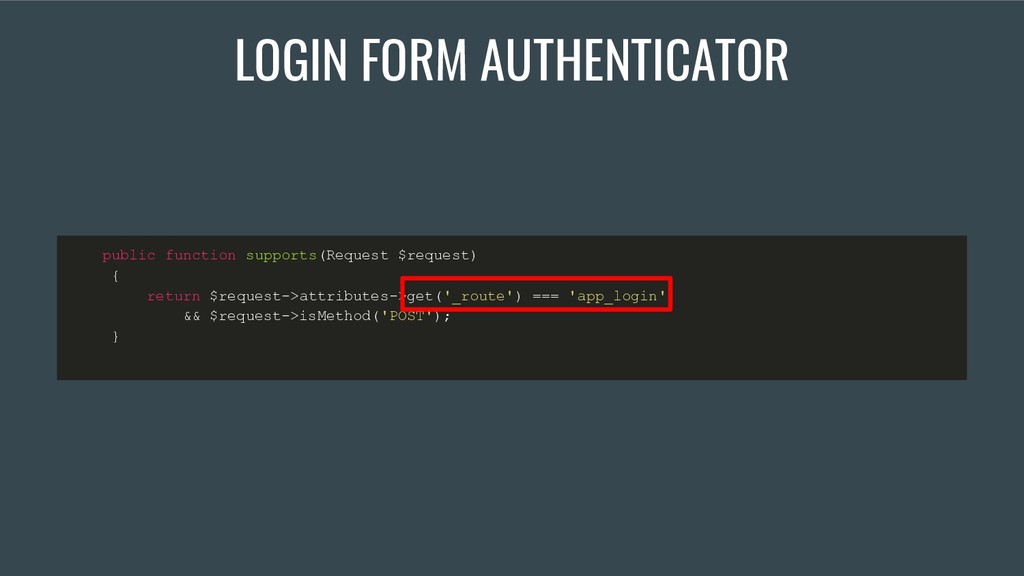
LOGIN FORM AUTHENTICATOR public function supports(Request $request) { return $request->attributes->get('_route')
=== 'app_login' && $request->isMethod('POST'); } -
LOGIN FORM AUTHENTICATOR public function supports(Request $request) { return $request->attributes->get('_route')
=== 'app_login' && $request->isMethod('POST'); } -
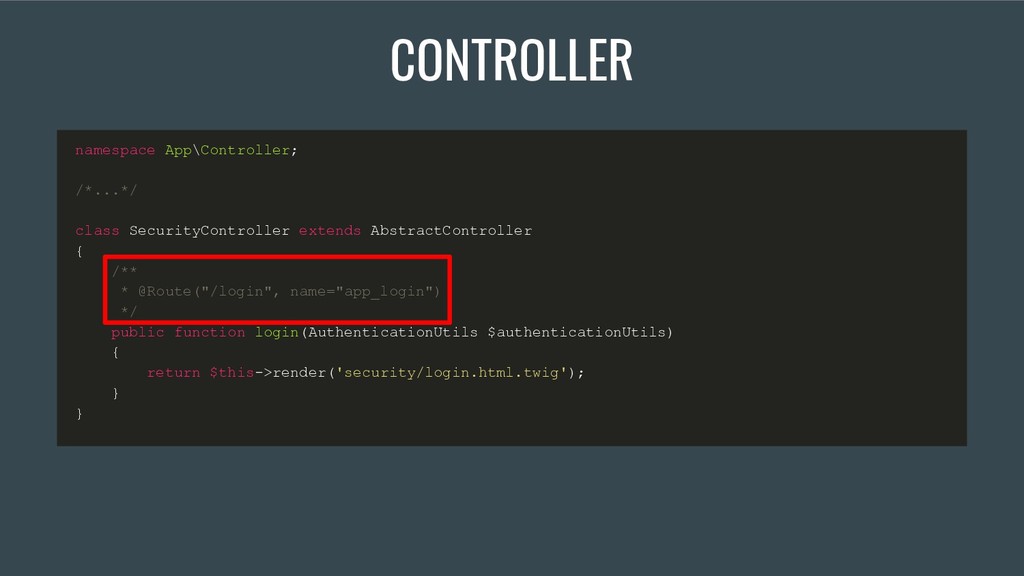
CONTROLLER namespace App\Controller; /*...*/ class SecurityController extends AbstractController { /**
* @Route("/login", name="app_login") */ public function login(AuthenticationUtils $authenticationUtils) { return $this->render('security/login.html.twig'); } } -
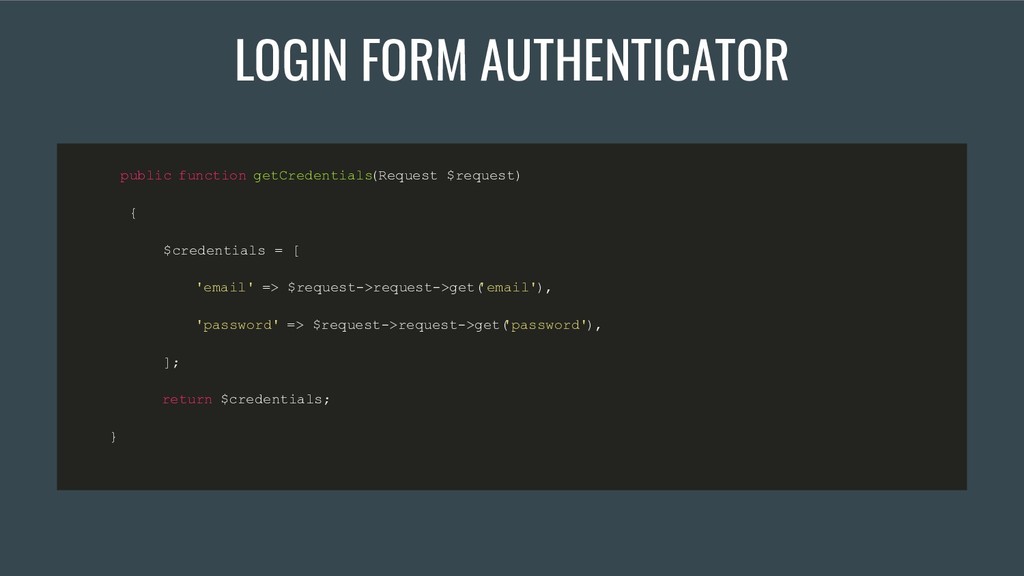
LOGIN FORM AUTHENTICATOR public function getCredentials (Request $request) { $credentials
= [ 'email' => $request->request->get( 'email'), 'password' => $request->request->get( 'password'), ]; return $credentials; } -
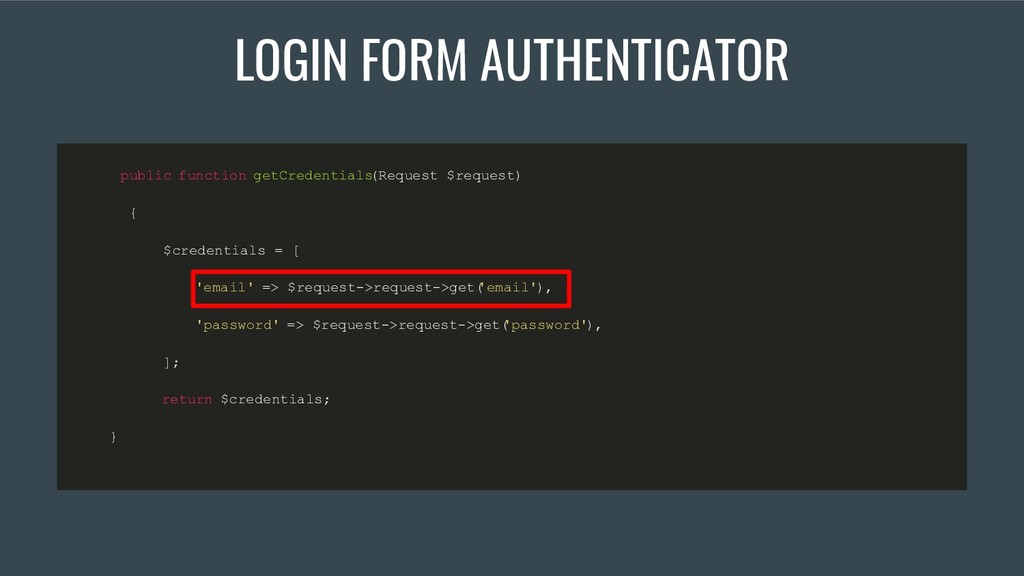
LOGIN FORM AUTHENTICATOR public function getCredentials (Request $request) { $credentials
= [ 'email' => $request->request->get( 'email'), 'password' => $request->request->get( 'password'), ]; return $credentials; } -
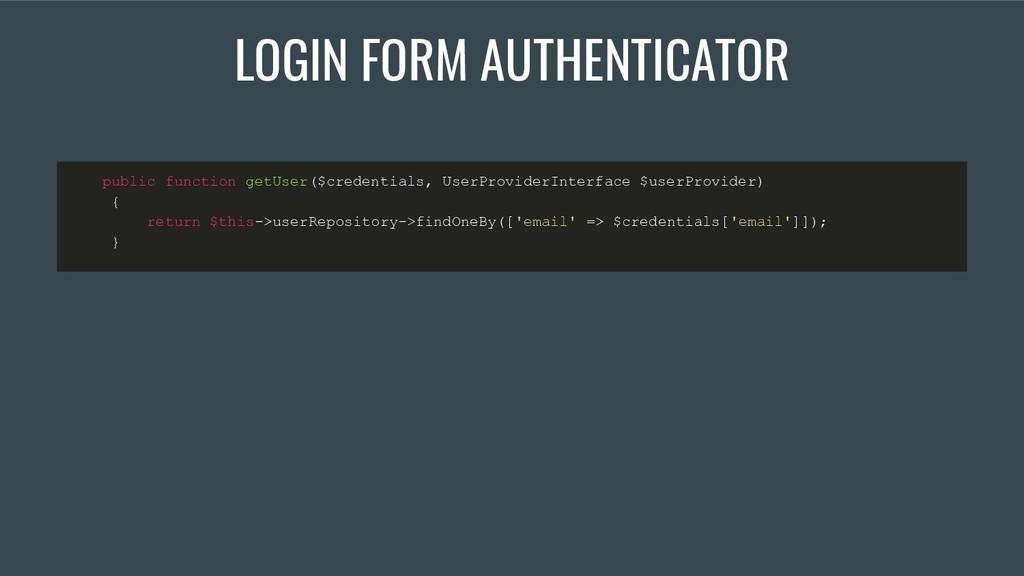
LOGIN FORM AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { return
$this->userRepository->findOneBy(['email' => $credentials['email']]); } -
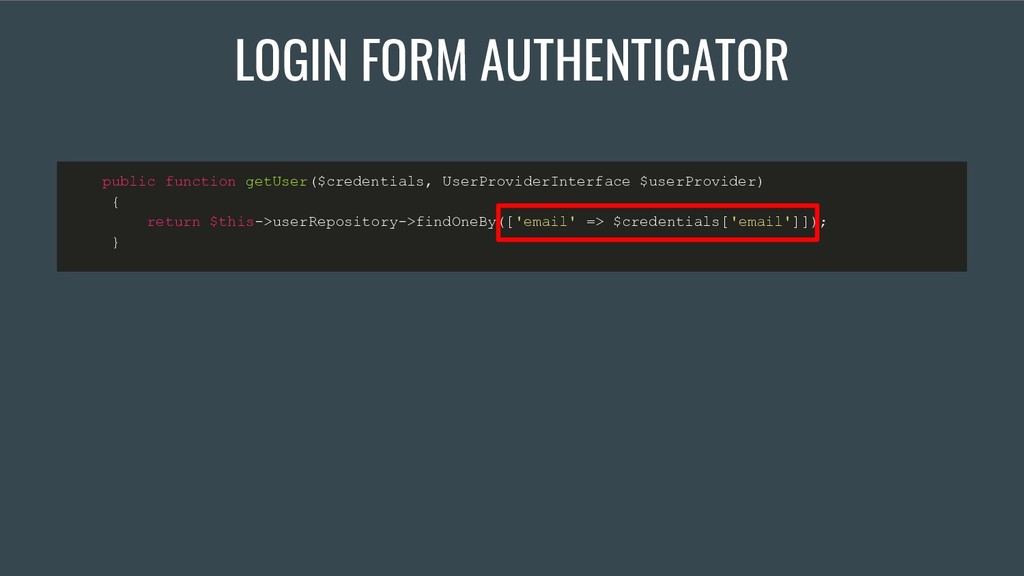
LOGIN FORM AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { return
$this->userRepository->findOneBy(['email' => $credentials['email']]); } -
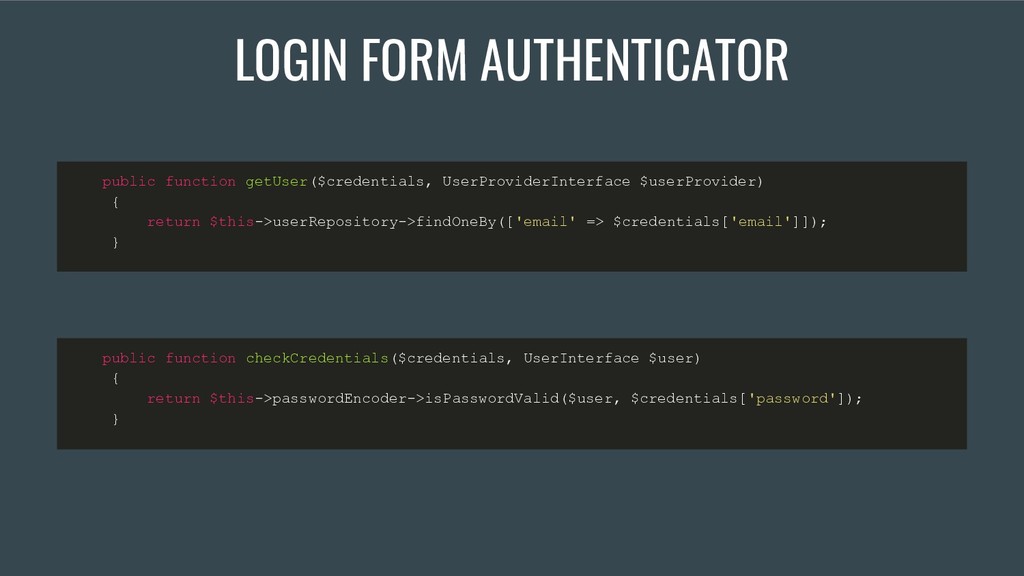
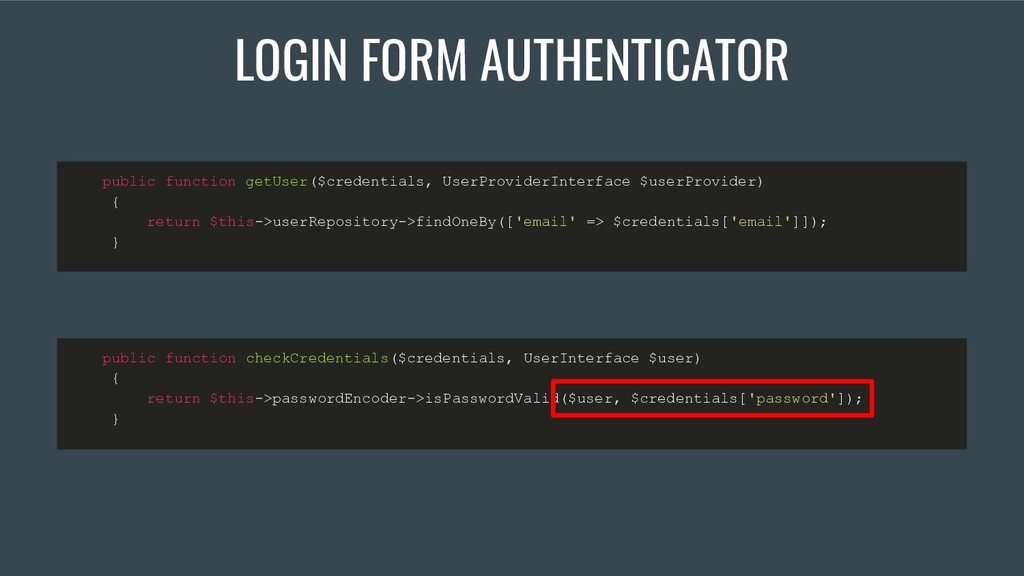
LOGIN FORM AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { return
$this->userRepository->findOneBy(['email' => $credentials['email']]); } public function checkCredentials($credentials, UserInterface $user) { return $this->passwordEncoder->isPasswordValid($user, $credentials['password']); } -
LOGIN FORM AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { return
$this->userRepository->findOneBy(['email' => $credentials['email']]); } public function checkCredentials($credentials, UserInterface $user) { return $this->passwordEncoder->isPasswordValid($user, $credentials['password']); } -
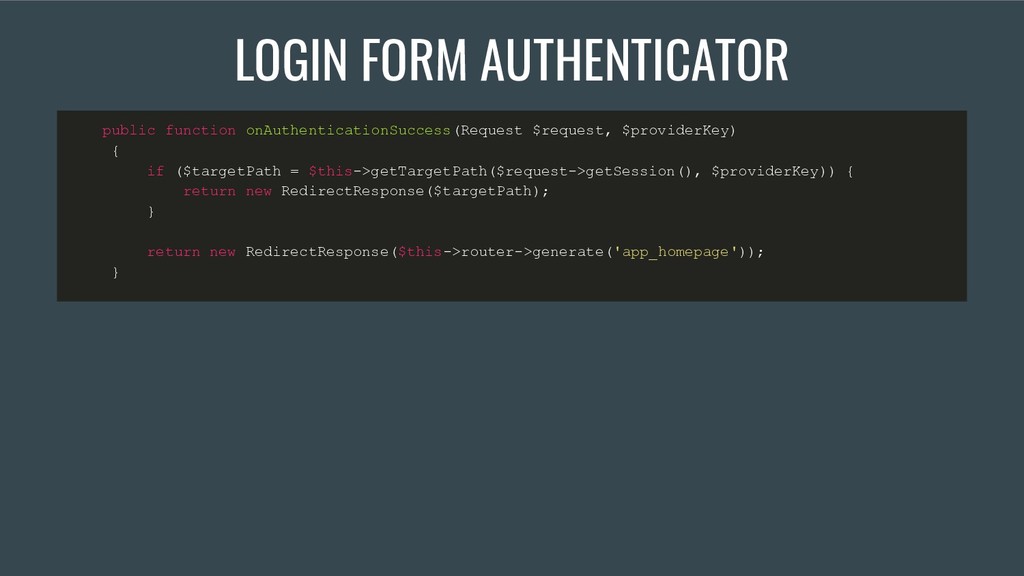
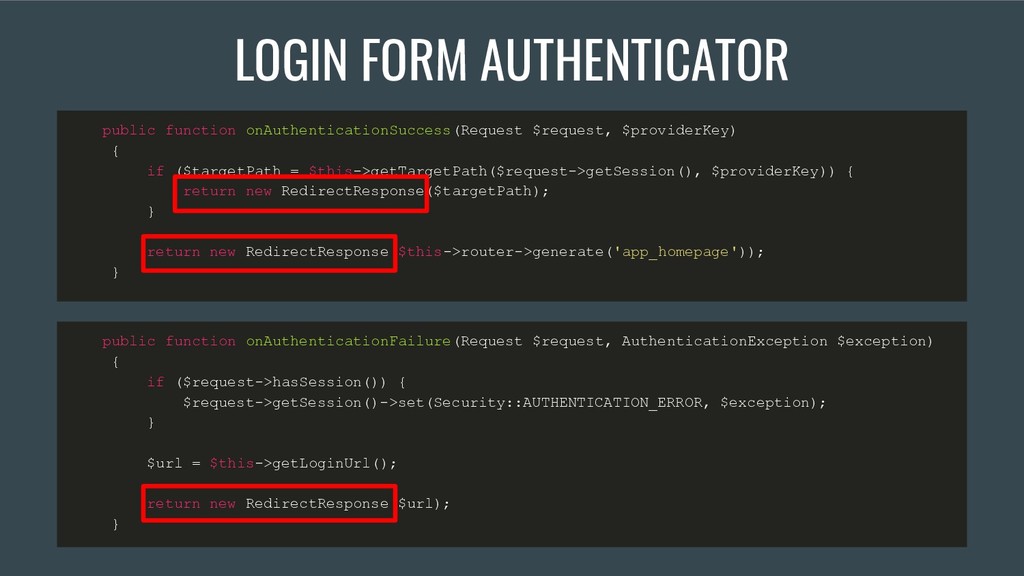
LOGIN FORM AUTHENTICATOR public function onAuthenticationSuccess(Request $request, $providerKey) { if
($targetPath = $this->getTargetPath($request->getSession(), $providerKey)) { return new RedirectResponse($targetPath); } return new RedirectResponse($this->router->generate('app_homepage')); } -
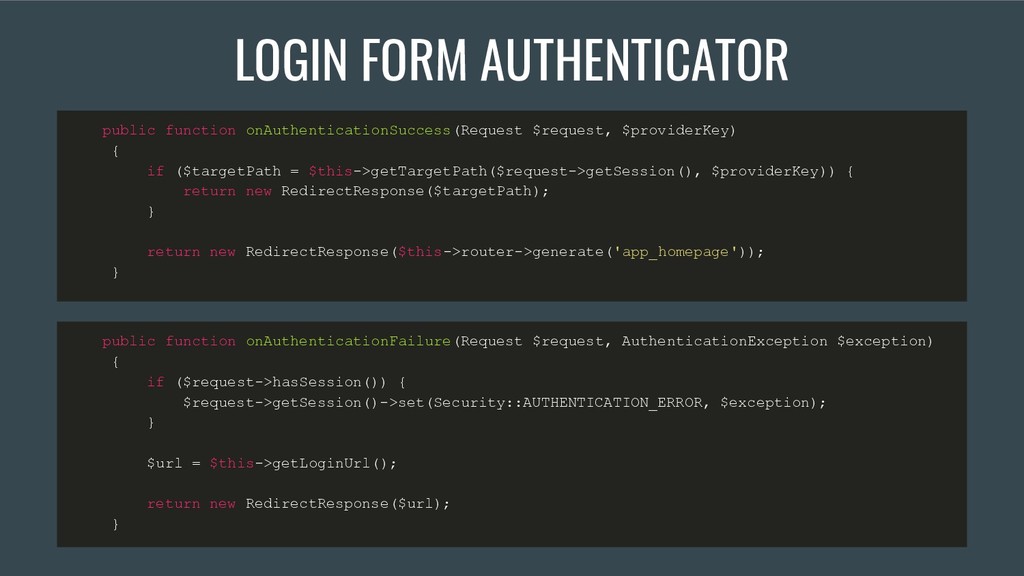
LOGIN FORM AUTHENTICATOR public function onAuthenticationSuccess(Request $request, $providerKey) { if
($targetPath = $this->getTargetPath($request->getSession(), $providerKey)) { return new RedirectResponse($targetPath); } return new RedirectResponse($this->router->generate('app_homepage')); } public function onAuthenticationFailure(Request $request, AuthenticationException $exception) { if ($request->hasSession()) { $request->getSession()->set(Security::AUTHENTICATION_ERROR, $exception); } $url = $this->getLoginUrl(); return new RedirectResponse($url); } -
LOGIN FORM AUTHENTICATOR public function onAuthenticationSuccess(Request $request, $providerKey) { if
($targetPath = $this->getTargetPath($request->getSession(), $providerKey)) { return new RedirectResponse($targetPath); } return new RedirectResponse($this->router->generate('app_homepage')); } public function onAuthenticationFailure(Request $request, AuthenticationException $exception) { if ($request->hasSession()) { $request->getSession()->set(Security::AUTHENTICATION_ERROR, $exception); } $url = $this->getLoginUrl(); return new RedirectResponse($url); } -
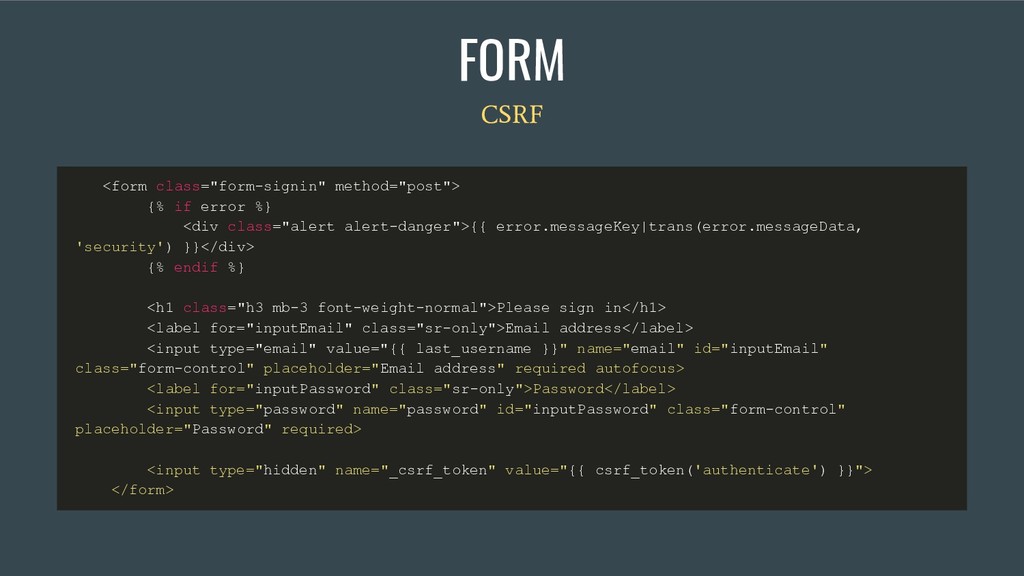
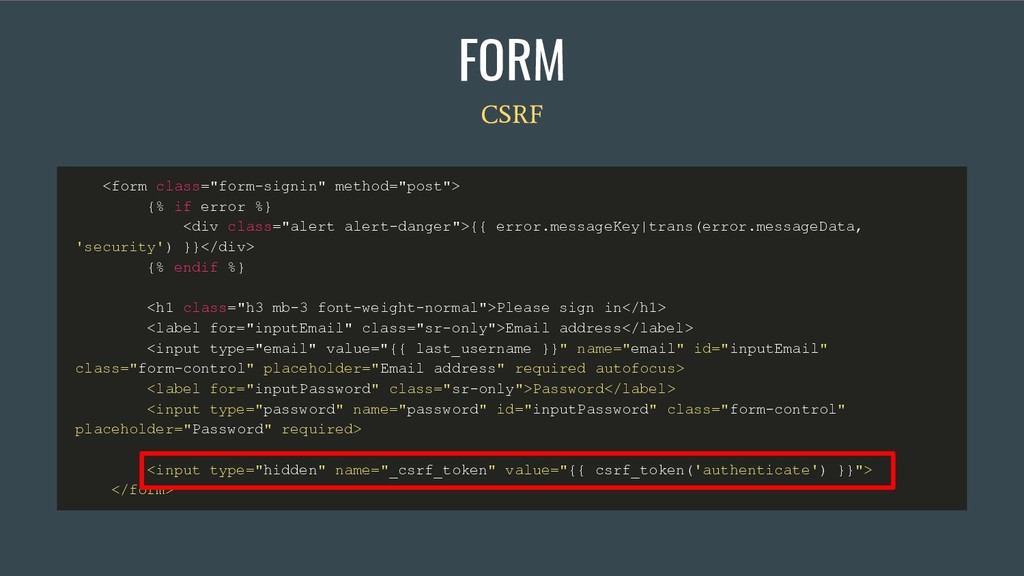
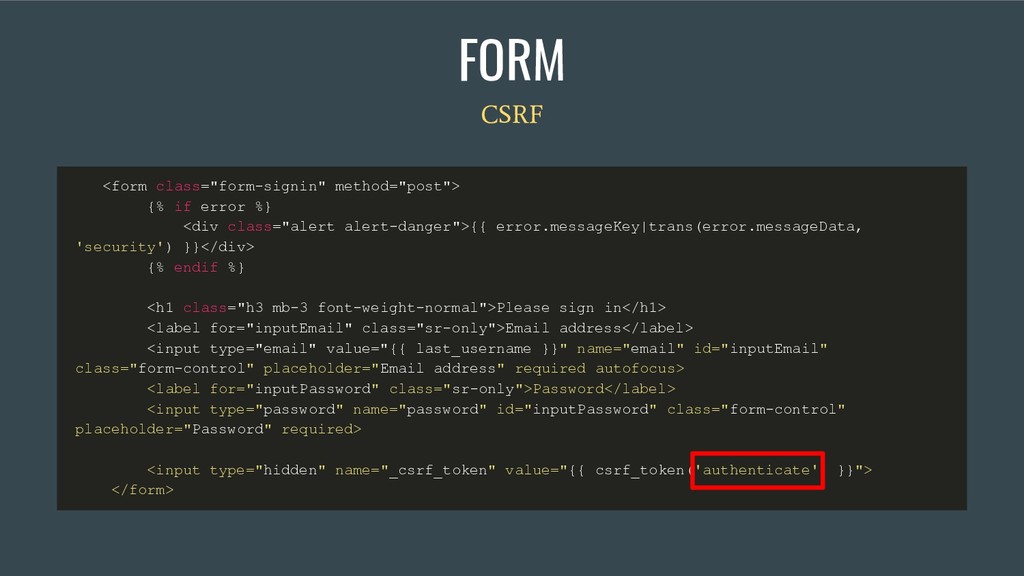
FORM CSRF <form class="form-signin" method="post"> {% if error %} <div
class="alert alert-danger">{{ error.messageKey|trans(error.messageData, 'security') }}</div> {% endif %} <h1 class="h3 mb-3 font-weight-normal">Please sign in</h1> <label for="inputEmail" class="sr-only">Email address</label> <input type="email" value="{{ last_username }}" name="email" id="inputEmail" class="form-control" placeholder="Email address" required autofocus> <label for="inputPassword" class="sr-only">Password</label> <input type="password" name="password" id="inputPassword" class="form-control" placeholder="Password" required> <input type="hidden" name="_csrf_token" value="{{ csrf_token('authenticate') }}"> </form> -
FORM CSRF <form class="form-signin" method="post"> {% if error %} <div
class="alert alert-danger">{{ error.messageKey|trans(error.messageData, 'security') }}</div> {% endif %} <h1 class="h3 mb-3 font-weight-normal">Please sign in</h1> <label for="inputEmail" class="sr-only">Email address</label> <input type="email" value="{{ last_username }}" name="email" id="inputEmail" class="form-control" placeholder="Email address" required autofocus> <label for="inputPassword" class="sr-only">Password</label> <input type="password" name="password" id="inputPassword" class="form-control" placeholder="Password" required> <input type="hidden" name="_csrf_token" value="{{ csrf_token('authenticate') }}"> </form> -
FORM CSRF <form class="form-signin" method="post"> {% if error %} <div
class="alert alert-danger">{{ error.messageKey|trans(error.messageData, 'security') }}</div> {% endif %} <h1 class="h3 mb-3 font-weight-normal">Please sign in</h1> <label for="inputEmail" class="sr-only">Email address</label> <input type="email" value="{{ last_username }}" name="email" id="inputEmail" class="form-control" placeholder="Email address" required autofocus> <label for="inputPassword" class="sr-only">Password</label> <input type="password" name="password" id="inputPassword" class="form-control" placeholder="Password" required> <input type="hidden" name="_csrf_token" value="{{ csrf_token('authenticate') }}"> </form> -
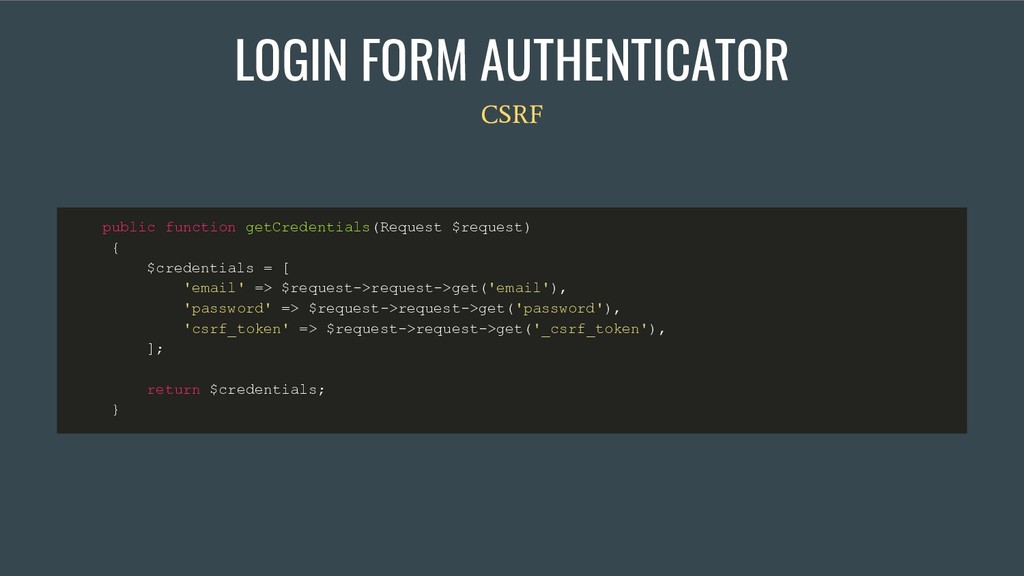
LOGIN FORM AUTHENTICATOR CSRF public function getCredentials(Request $request) { $credentials
= [ 'email' => $request->request->get('email'), 'password' => $request->request->get('password'), 'csrf_token' => $request->request->get('_csrf_token'), ]; return $credentials; } -
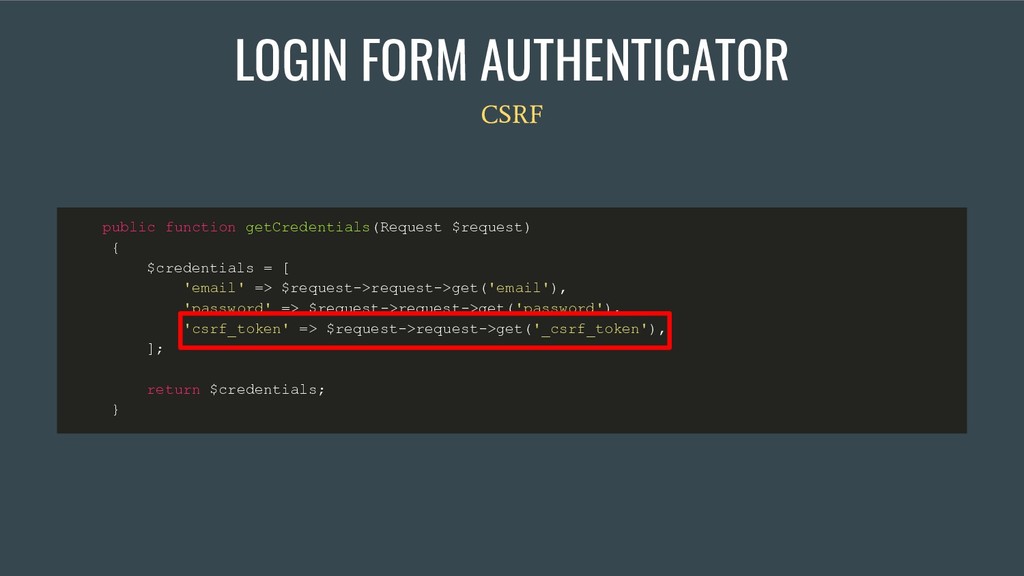
LOGIN FORM AUTHENTICATOR CSRF public function getCredentials(Request $request) { $credentials
= [ 'email' => $request->request->get('email'), 'password' => $request->request->get('password'), 'csrf_token' => $request->request->get('_csrf_token'), ]; return $credentials; } -
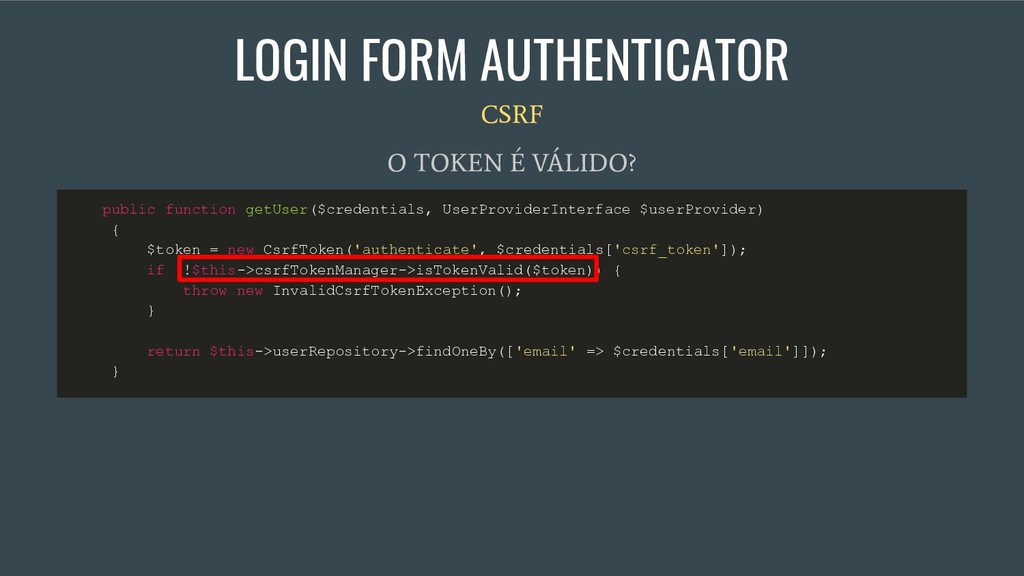
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
checkCredentials($credentials, UserInterface $user) { } -
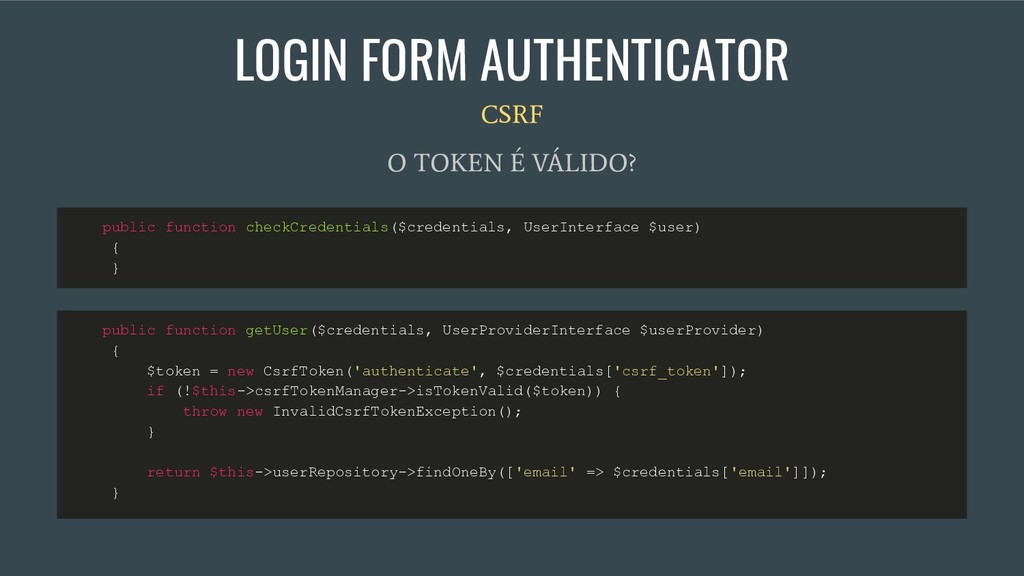
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
checkCredentials($credentials, UserInterface $user) { } public function getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } -
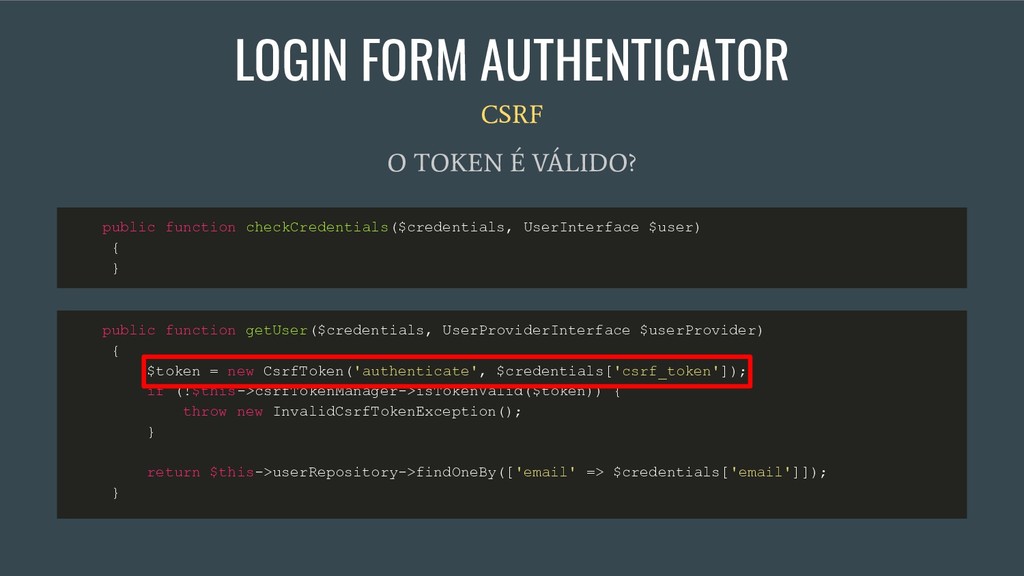
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
checkCredentials($credentials, UserInterface $user) { } public function getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } -
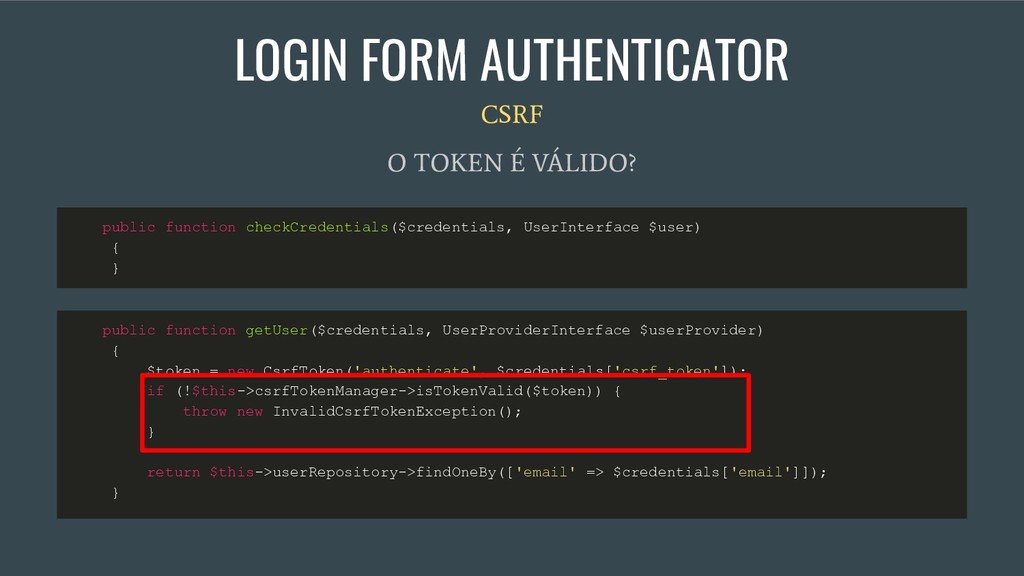
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
checkCredentials($credentials, UserInterface $user) { } public function getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } -
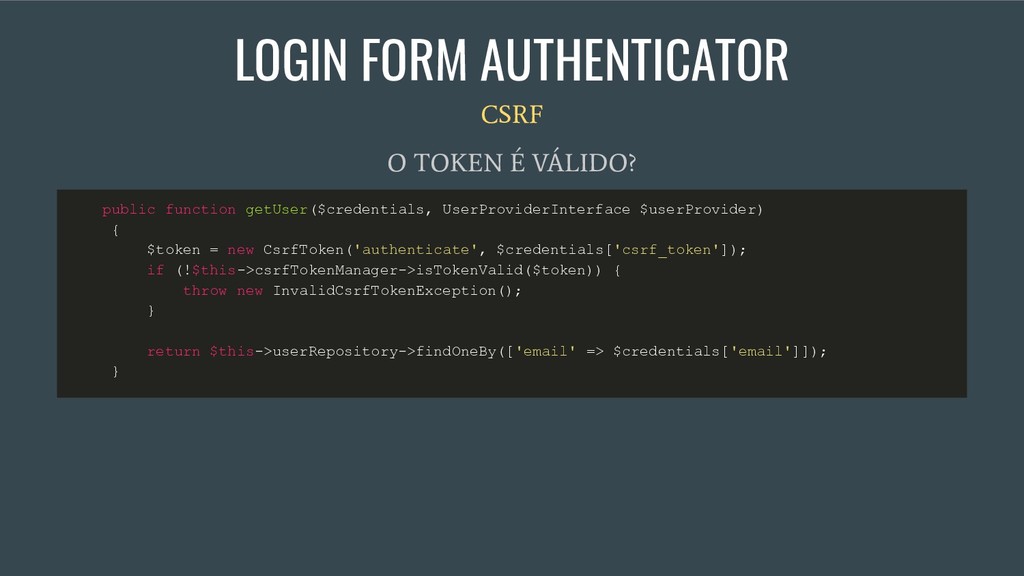
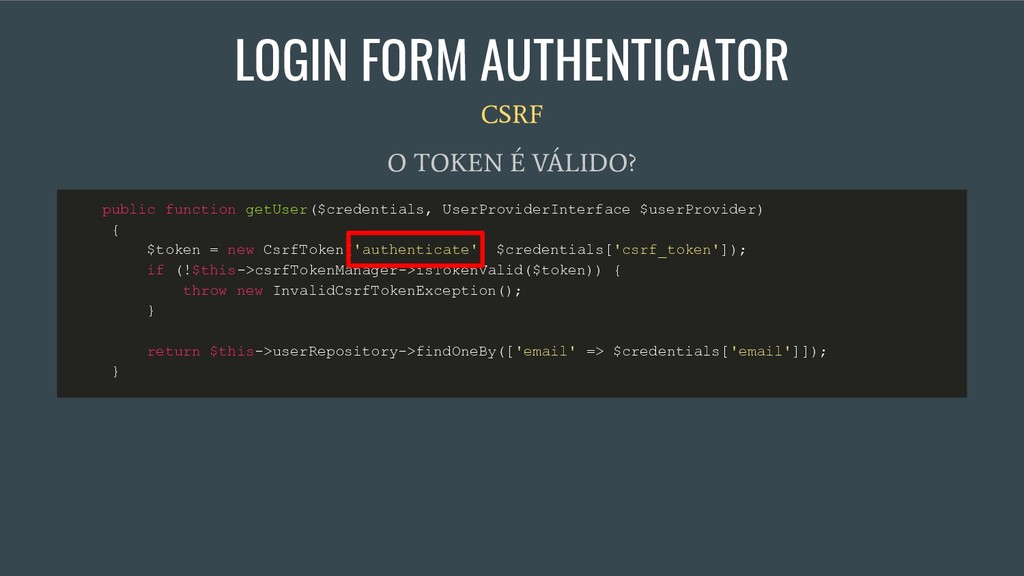
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } -
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } -
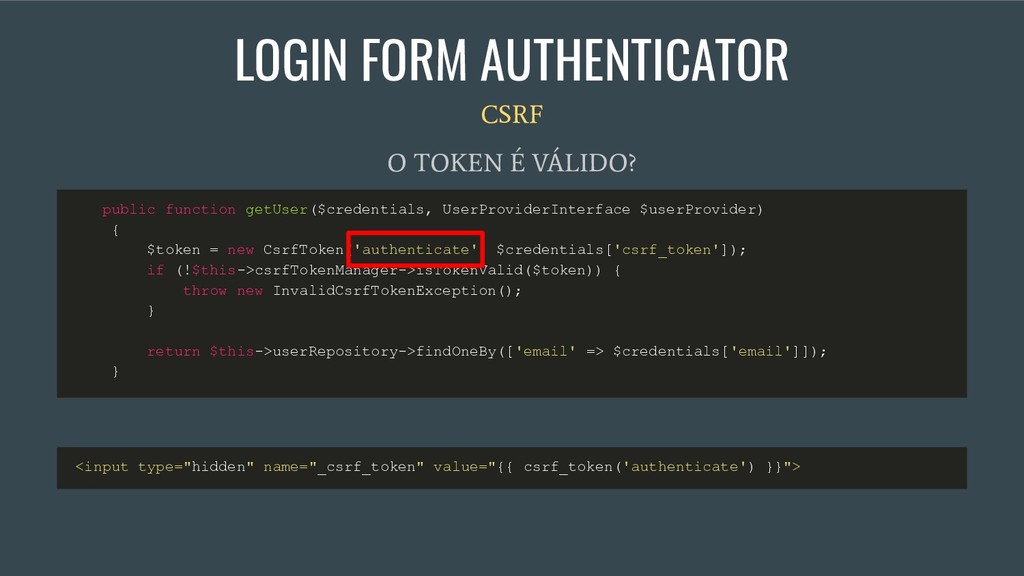
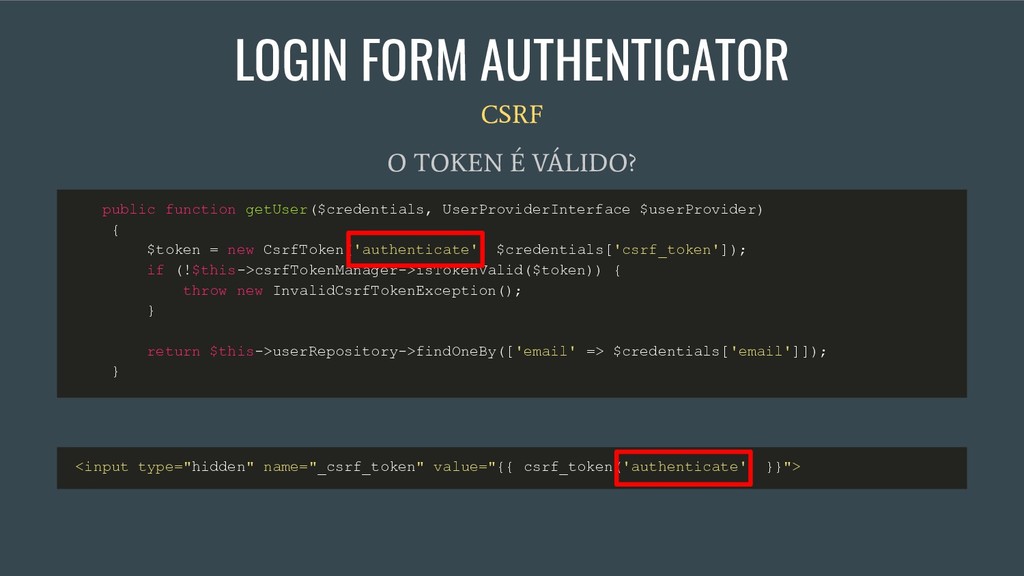
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } <input type="hidden" name="_csrf_token" value="{{ csrf_token('authenticate') }}"> -
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } <input type="hidden" name="_csrf_token" value="{{ csrf_token('authenticate') }}"> -
LOGIN FORM AUTHENTICATOR CSRF O TOKEN É VÁLIDO? public function
getUser($credentials, UserProviderInterface $userProvider) { $token = new CsrfToken('authenticate', $credentials['csrf_token']); if (!$this->csrfTokenManager->isTokenValid($token)) { throw new InvalidCsrfTokenException(); } return $this->userRepository->findOneBy(['email' => $credentials['email']]); } -
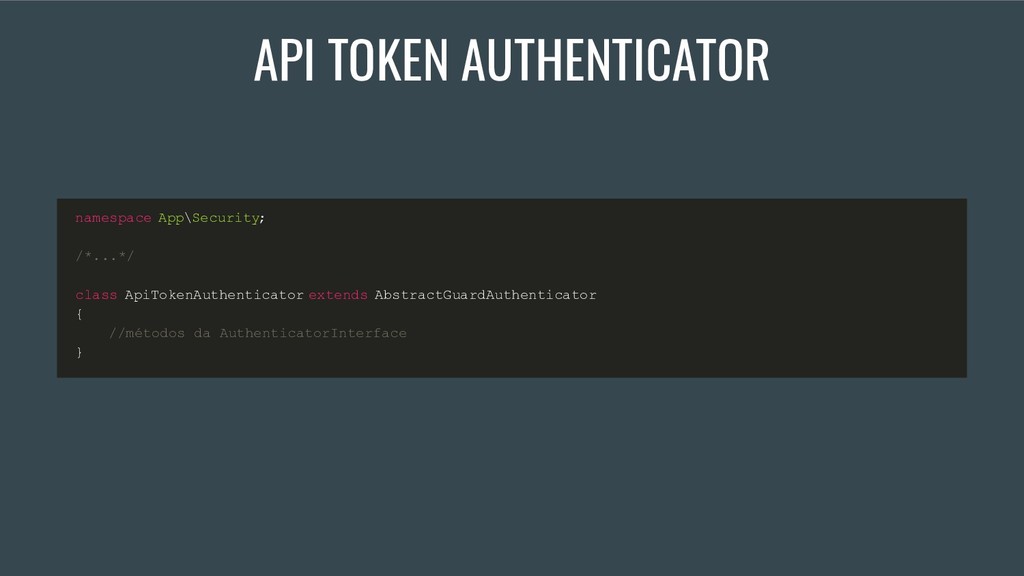
API TOKEN AUTHENTICATOR namespace App\Security; /*...*/ class ApiTokenAuthenticator extends AbstractGuardAuthenticator
{ //métodos da AuthenticatorInterface } -
API TOKEN AUTHENTICATOR namespace App\Security; /*...*/ class ApiTokenAuthenticator extends AbstractGuardAuthenticator
{ //métodos da AuthenticatorInterface } -
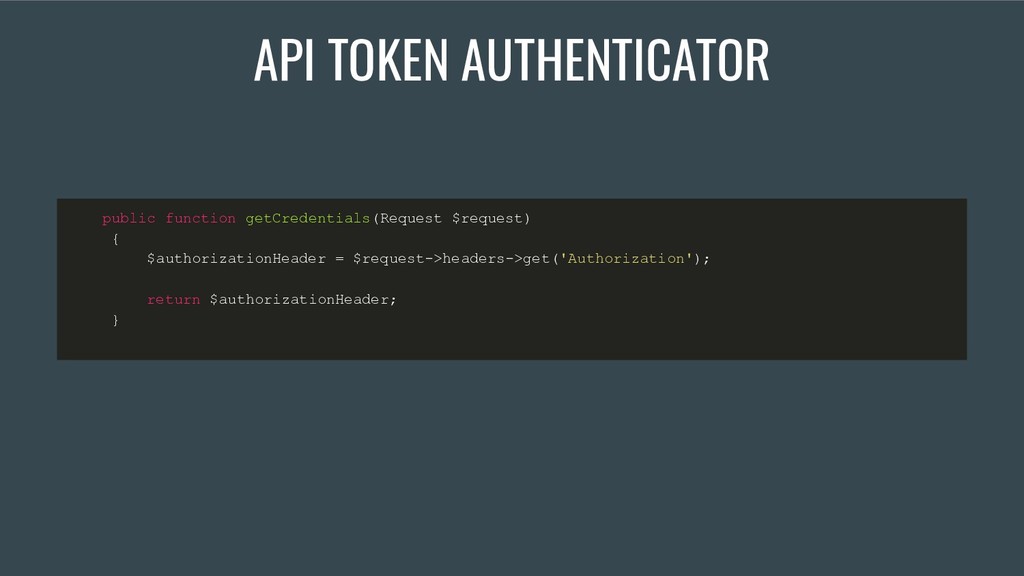
API TOKEN AUTHENTICATOR public function getCredentials(Request $request) { $authorizationHeader =
$request->headers->get('Authorization'); return $authorizationHeader; } -
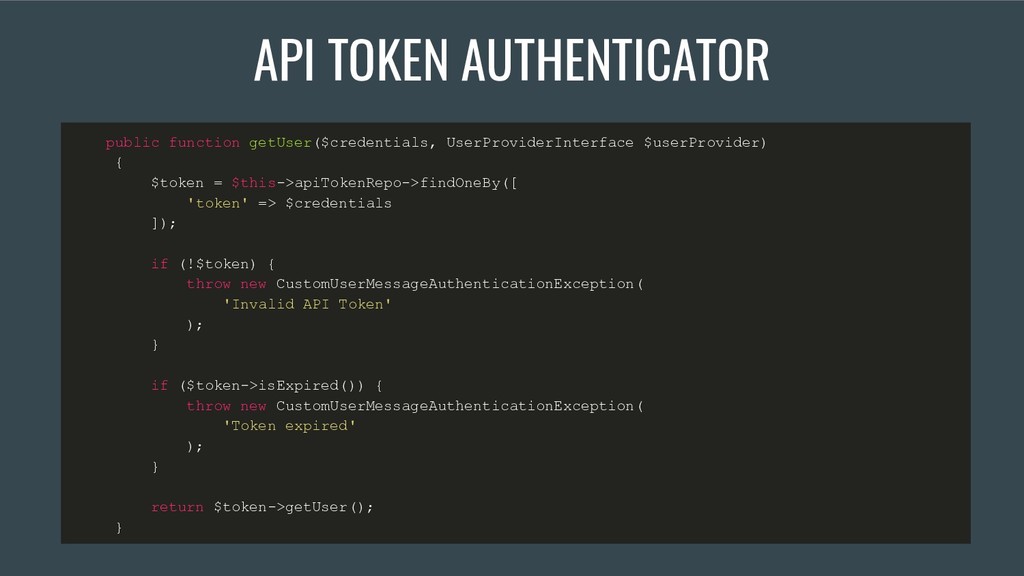
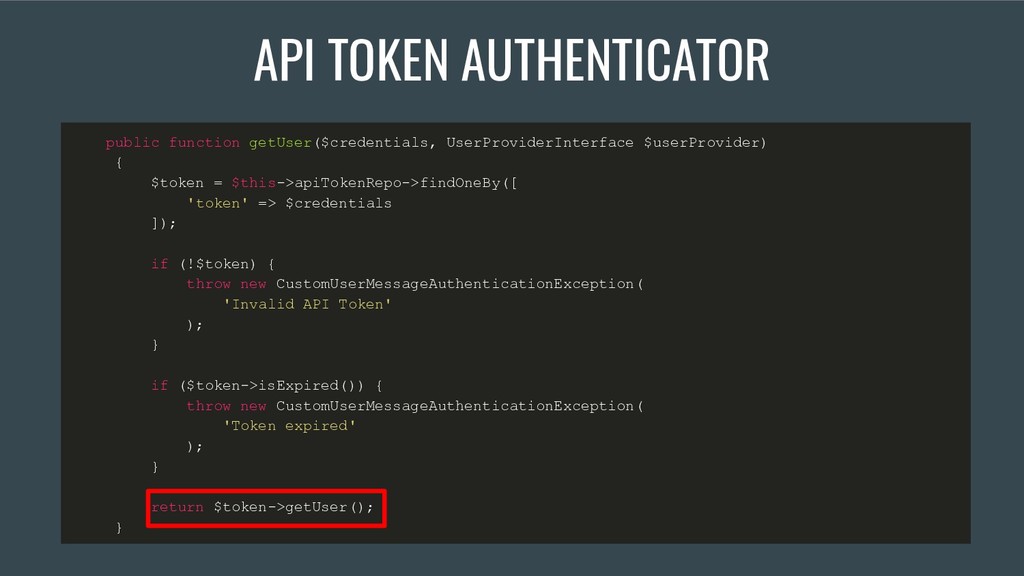
API TOKEN AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { $token
= $this->apiTokenRepo->findOneBy([ 'token' => $credentials ]); if (!$token) { throw new CustomUserMessageAuthenticationException( 'Invalid API Token' ); } if ($token->isExpired()) { throw new CustomUserMessageAuthenticationException( 'Token expired' ); } return $token->getUser(); } -
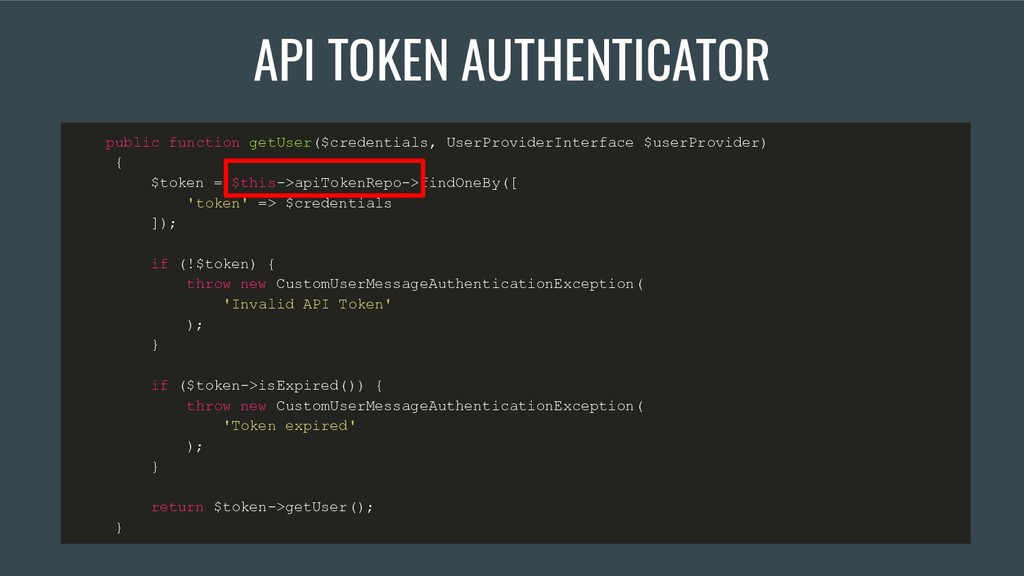
API TOKEN AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { $token
= $this->apiTokenRepo->findOneBy([ 'token' => $credentials ]); if (!$token) { throw new CustomUserMessageAuthenticationException( 'Invalid API Token' ); } if ($token->isExpired()) { throw new CustomUserMessageAuthenticationException( 'Token expired' ); } return $token->getUser(); } -
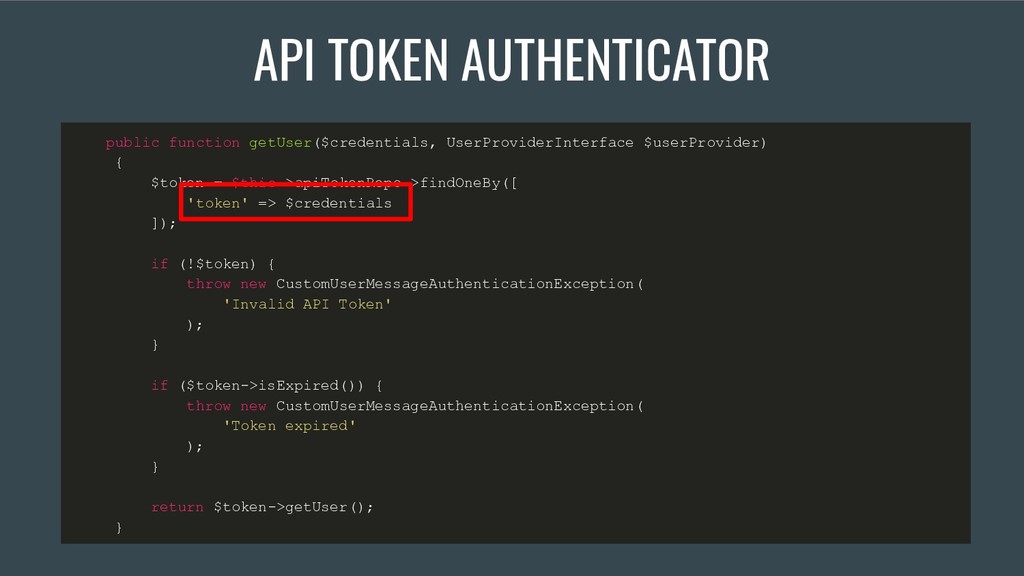
API TOKEN AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { $token
= $this->apiTokenRepo->findOneBy([ 'token' => $credentials ]); if (!$token) { throw new CustomUserMessageAuthenticationException( 'Invalid API Token' ); } if ($token->isExpired()) { throw new CustomUserMessageAuthenticationException( 'Token expired' ); } return $token->getUser(); } -
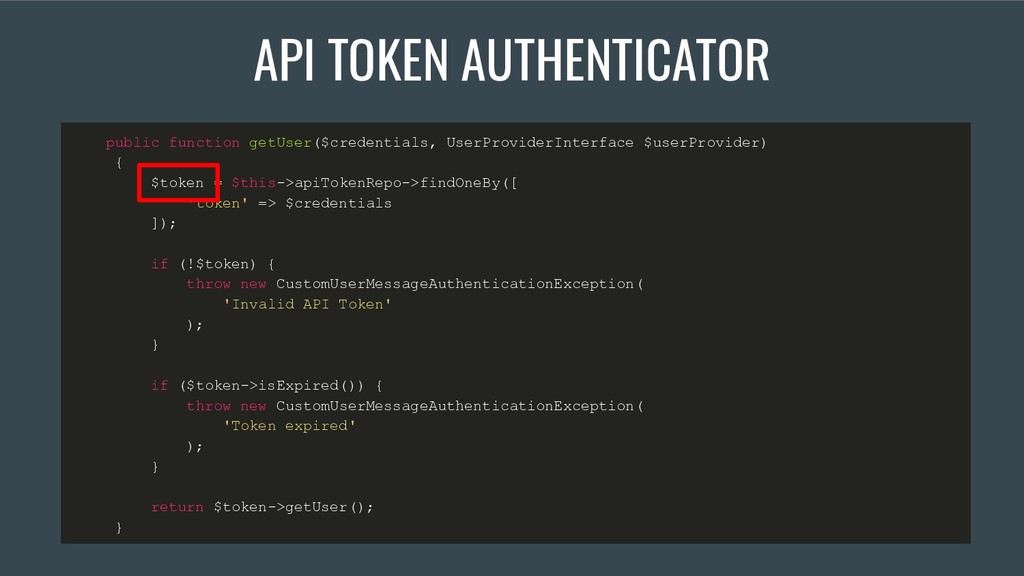
API TOKEN AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { $token
= $this->apiTokenRepo->findOneBy([ 'token' => $credentials ]); if (!$token) { throw new CustomUserMessageAuthenticationException( 'Invalid API Token' ); } if ($token->isExpired()) { throw new CustomUserMessageAuthenticationException( 'Token expired' ); } return $token->getUser(); } -
API TOKEN AUTHENTICATOR public function getUser($credentials, UserProviderInterface $userProvider) { $token
= $this->apiTokenRepo->findOneBy([ 'token' => $credentials ]); if (!$token) { throw new CustomUserMessageAuthenticationException( 'Invalid API Token' ); } if ($token->isExpired()) { throw new CustomUserMessageAuthenticationException( 'Token expired' ); } return $token->getUser(); } -
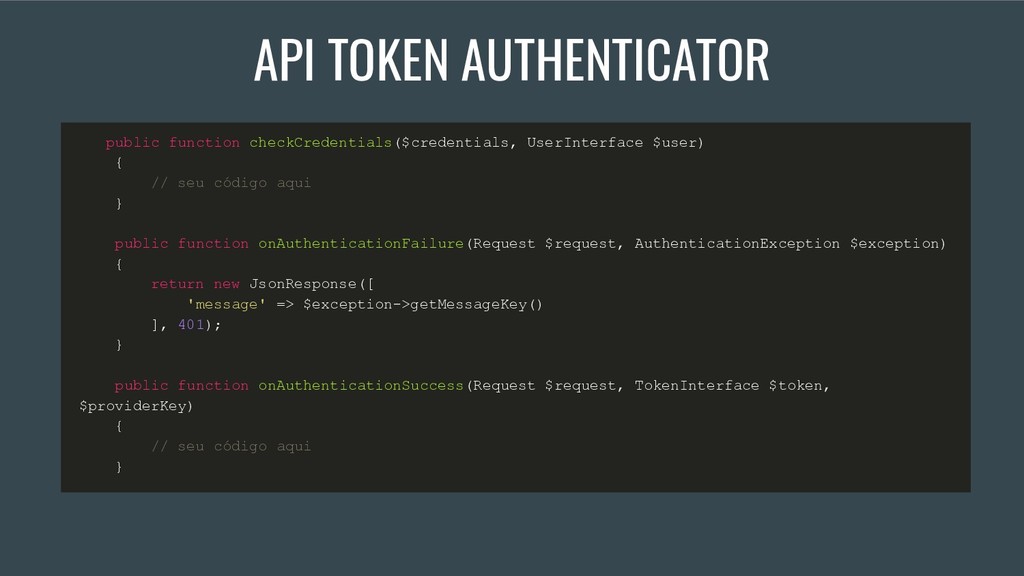
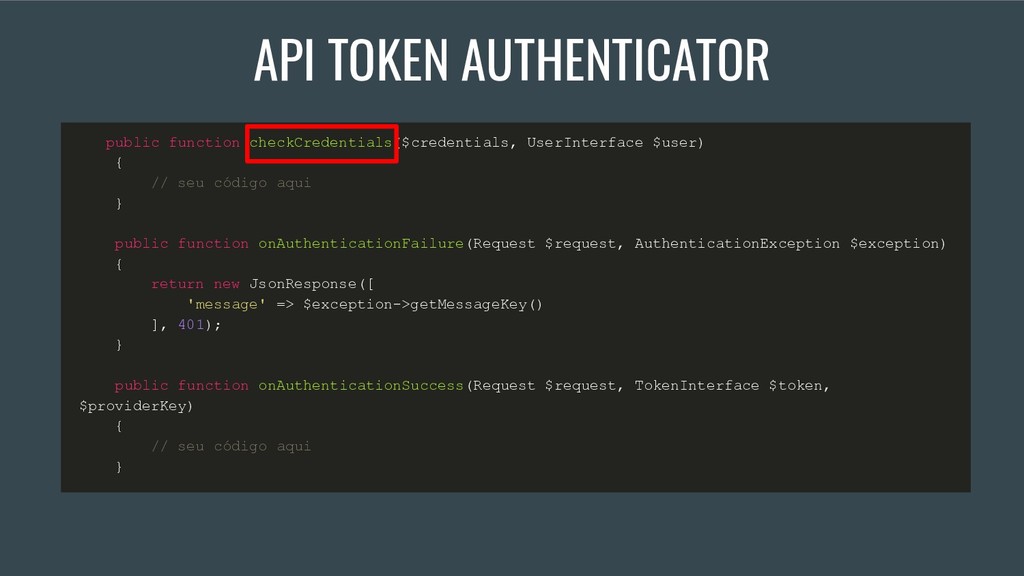
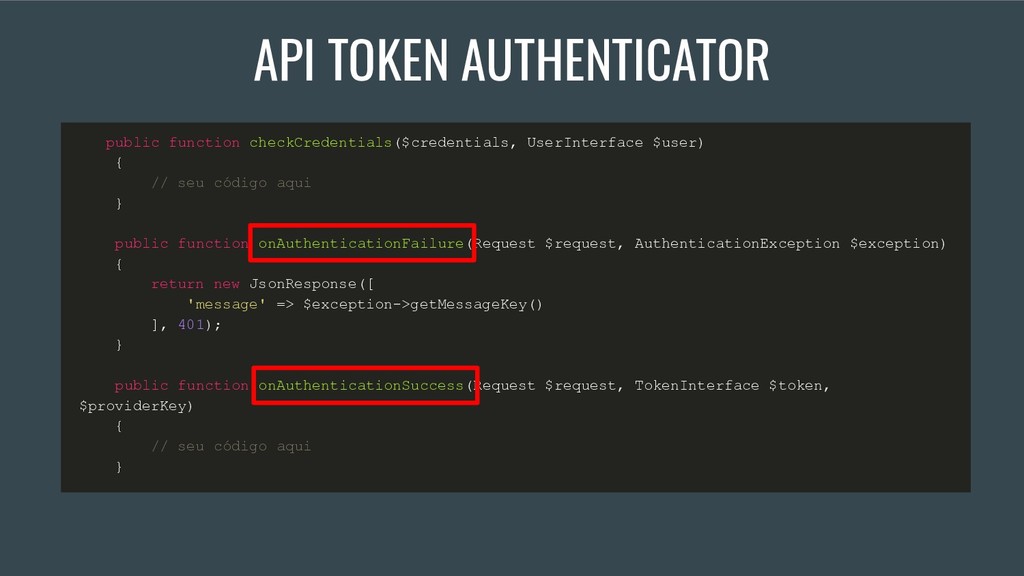
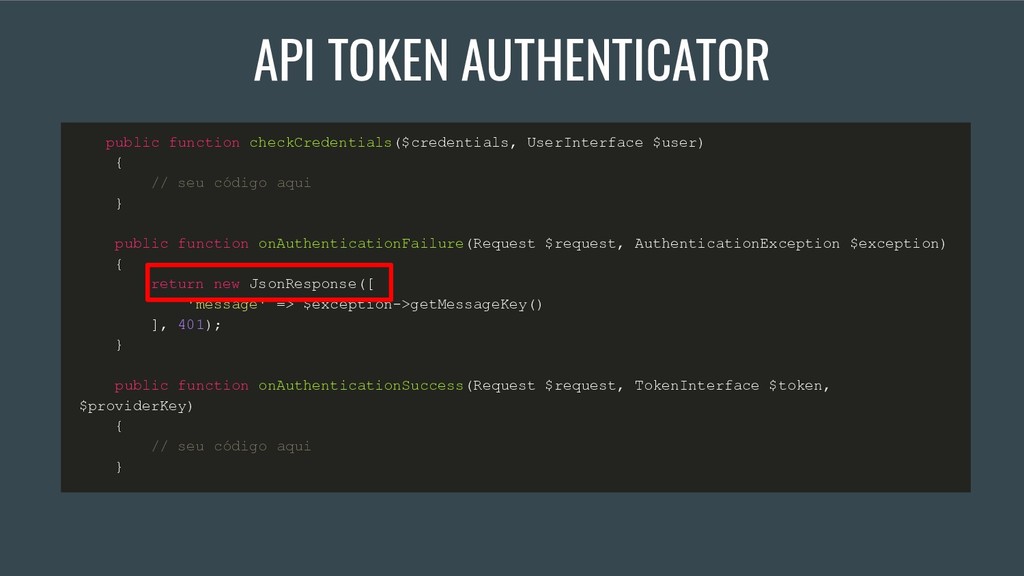
API TOKEN AUTHENTICATOR public function checkCredentials($credentials, UserInterface $user) { //
seu código aqui } public function onAuthenticationFailure(Request $request, AuthenticationException $exception) { return new JsonResponse([ 'message' => $exception->getMessageKey() ], 401); } public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey) { // seu código aqui } -
API TOKEN AUTHENTICATOR public function checkCredentials($credentials, UserInterface $user) { //
seu código aqui } public function onAuthenticationFailure(Request $request, AuthenticationException $exception) { return new JsonResponse([ 'message' => $exception->getMessageKey() ], 401); } public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey) { // seu código aqui } -
API TOKEN AUTHENTICATOR public function checkCredentials($credentials, UserInterface $user) { //
seu código aqui } public function onAuthenticationFailure(Request $request, AuthenticationException $exception) { return new JsonResponse([ 'message' => $exception->getMessageKey() ], 401); } public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey) { // seu código aqui } -
API TOKEN AUTHENTICATOR public function checkCredentials($credentials, UserInterface $user) { //
seu código aqui } public function onAuthenticationFailure(Request $request, AuthenticationException $exception) { return new JsonResponse([ 'message' => $exception->getMessageKey() ], 401); } public function onAuthenticationSuccess(Request $request, TokenInterface $token, $providerKey) { // seu código aqui } -
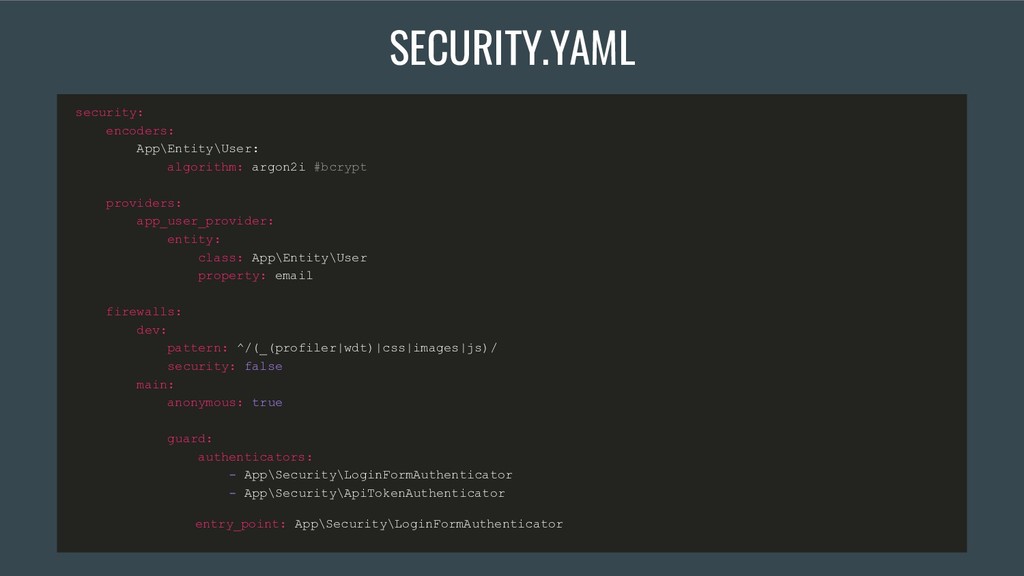
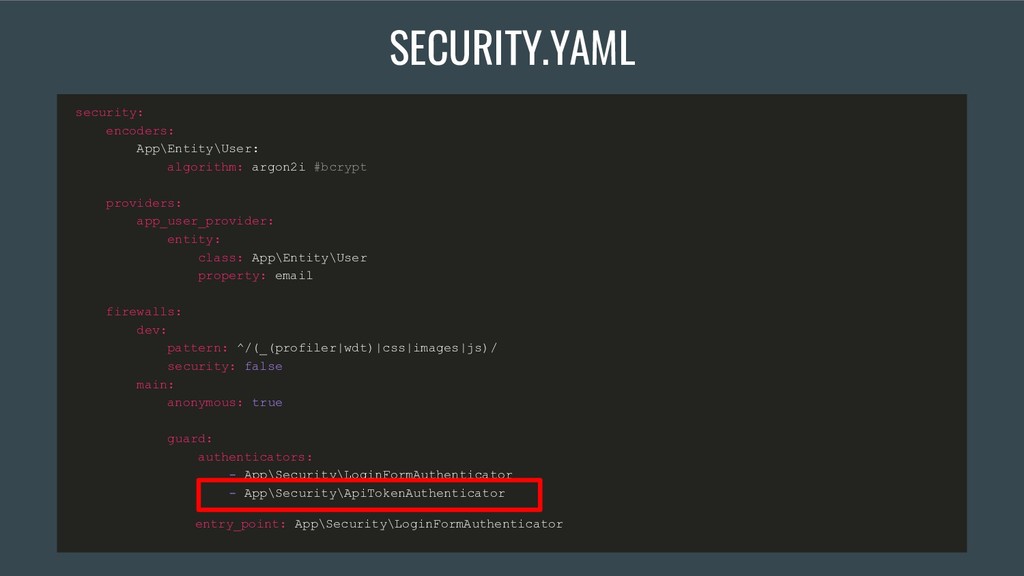
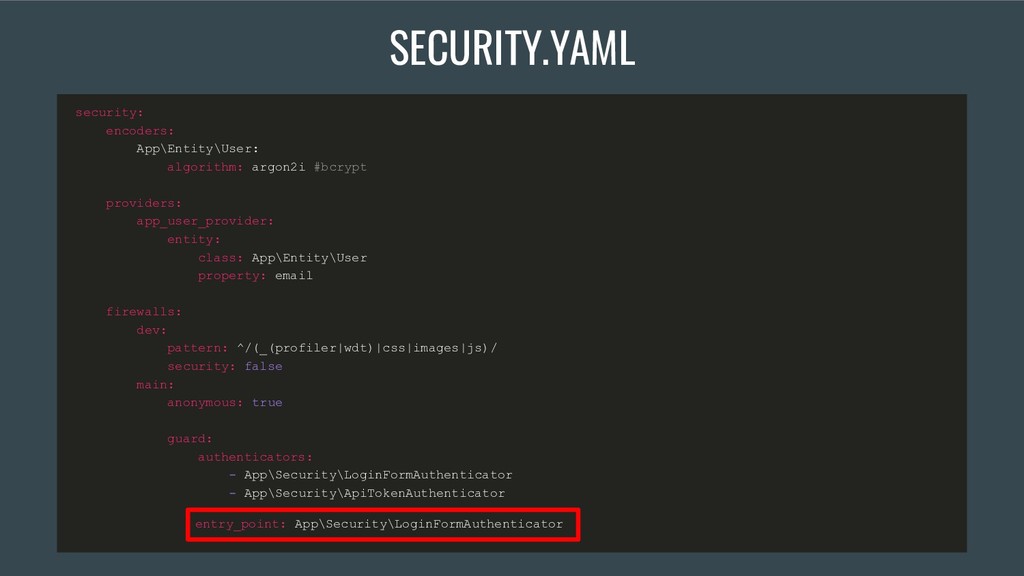
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator - App\Security\ApiTokenAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator - App\Security\ApiTokenAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML -
security: encoders: App\Entity\User: algorithm: argon2i #bcrypt providers: app_user_provider: entity: class:
App\Entity\User property: email firewalls: dev: pattern: ^/(_(profiler|wdt)|css|images|js)/ security: false main: anonymous: true guard: authenticators: - App\Security\LoginFormAuthenticator - App\Security\ApiTokenAuthenticator entry_point: App\Security\LoginFormAuthenticator SECURITY.YAML
 dianaarnos
 t0yohei
 ktombow
 akihisaikeda
 hakkadaikon
 kazuki1023
 fuqda
 yuzneri
 barnbarn
 meihei3
 simas
 hal_spidernight
 quramy
 akademiya2063
 sabderemane
 khoart
 palkan
 eileencodes
 varn
 katiecoart
 ryanjones
 honzajavorek
 keathley
 lara
 destraynor