Share
Embed
iOS applications auditing
EUSecWest 2012, Amsterdam
Application Security Forum 2013, Yverdon
Julien Bachmann
November 07, 2012
Transcript
51 slides
-
› Motivations › Quick review of the environment › Common
flaws › Information gathering › Network analysis › Software reverse engineering -
Preamble › Security engineer @ SCRT › Teacher @ HEIG-VD
› Areas of interest focused on reverse engineering, software vulnerabilities, mobile devices security and OS internals › Not an Apple fanboy › But like all the cool kids... › Goals › This presentation aims at sharing experience and knowledge in iOS apps pentesting › Contact › @milkmix_ -
motivations | why ? › More and more applications ›
Most of Fortune-500 are deploying iPads › Growth in mobile banking › Mobile eShop › Internal applications › Need for security › Access and storage of sensitive information › Online payments -
environment | devices › Latest devices › Apple A5 /
A5X / A6 / A6X › Based on ARMv7 specifications › Processor › RISC › Load-store architecture › Fixed length 32-bits instructions -
environment | simulator › Beware › Simulator != emulator ›
More like a sandbox › Code compiled for Intel processors › 32-bits › ~/Library/Application Support/iPhone Simulator/<v>/Applications/<id>/ -
environment | applications › Localisation › ~/Music/iTunes/iTunes Music/Mobile Applications/ ›
/var/mobile/Applications/<guid>/<appname>.app/ › .ipa › Used to deploy applications › Zip file -
environment | applications › .plist › Used to store properties
› XML files, sometimes in a binary format › Associates keys (CFString, CFNumber, …) with values › plutil (1) › Convert binary plist file to its XML representation -
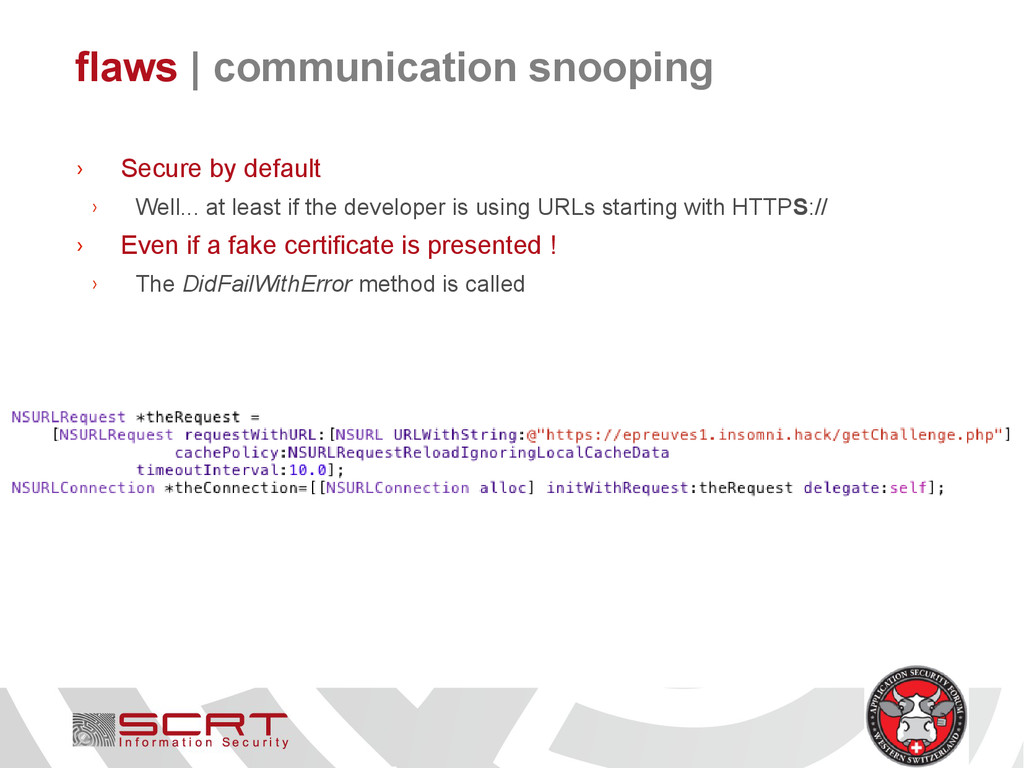
flaws | communication snooping › Secure by default › Well...
at least if the developer is using URLs starting with HTTPS:// › Even if a fake certificate is presented ! › The DidFailWithError method is called -
flaws | communication snooping › Ok, but what about real
life ? › A lot of development environments are using self-signed certificates › No built-in method to include certificates in the simulator › Obviously, what did the developers ? › Let's check what's on stackoverflow.com... -
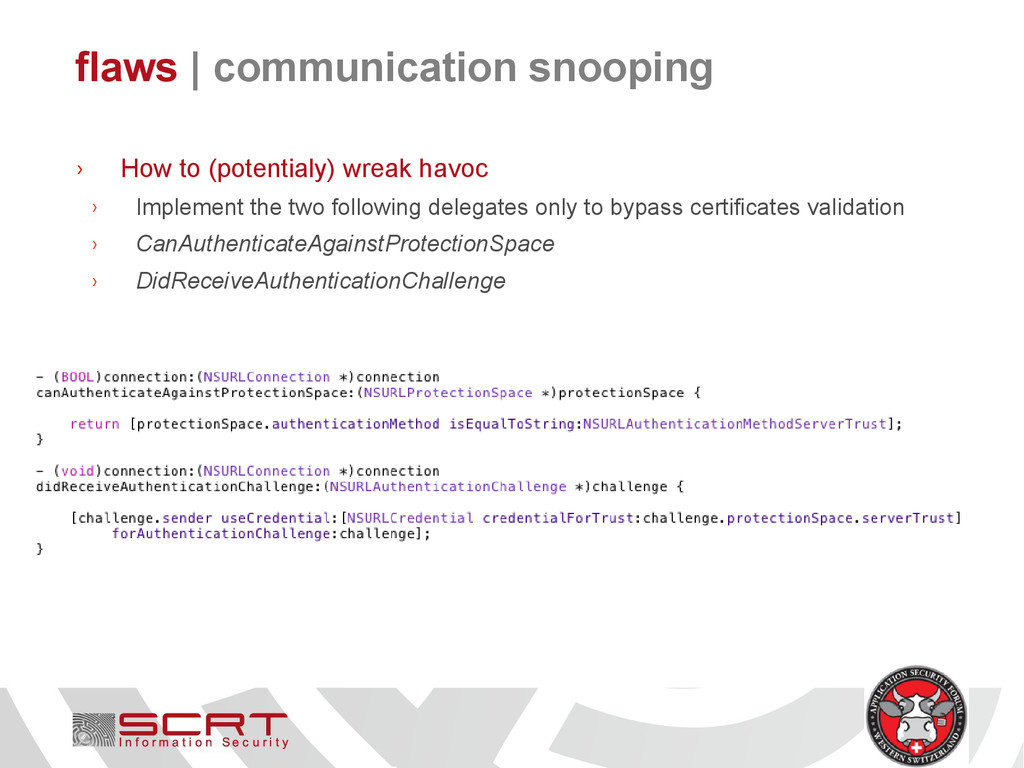
flaws | communication snooping › How to (potentialy) wreak havoc
› Implement the two following delegates only to bypass certificates validation › CanAuthenticateAgainstProtectionSpace › DidReceiveAuthenticationChallenge -
flaws | data storage › Most applications are working connected
› Still some information locally stored › plist › SQLite3 databases › ... › Could include sensitive data › Built-in protection › Data Protection API since iOS 4.0 › http://code.google.com/p/iphone-dataprotection/ › New attributes when working on files, Keychain entries or databases › Automatically used when calling NSURLCredentialStorage:setDefaultCredential but could not change protection type -
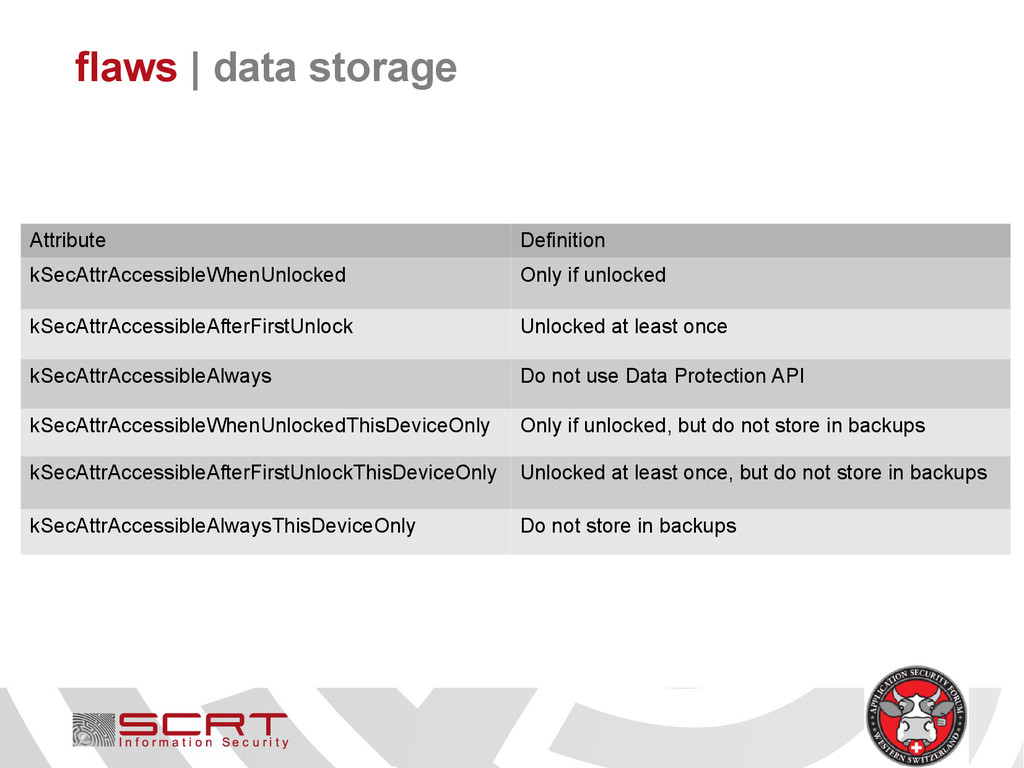
flaws | data storage Attribute Definition kSecAttrAccessibleWhenUnlocked Only if unlocked
kSecAttrAccessibleAfterFirstUnlock Unlocked at least once kSecAttrAccessibleAlways Do not use Data Protection API kSecAttrAccessibleWhenUnlockedThisDeviceOnly Only if unlocked, but do not store in backups kSecAttrAccessibleAfterFirstUnlockThisDeviceOnly Unlocked at least once, but do not store in backups kSecAttrAccessibleAlwaysThisDeviceOnly Do not store in backups -
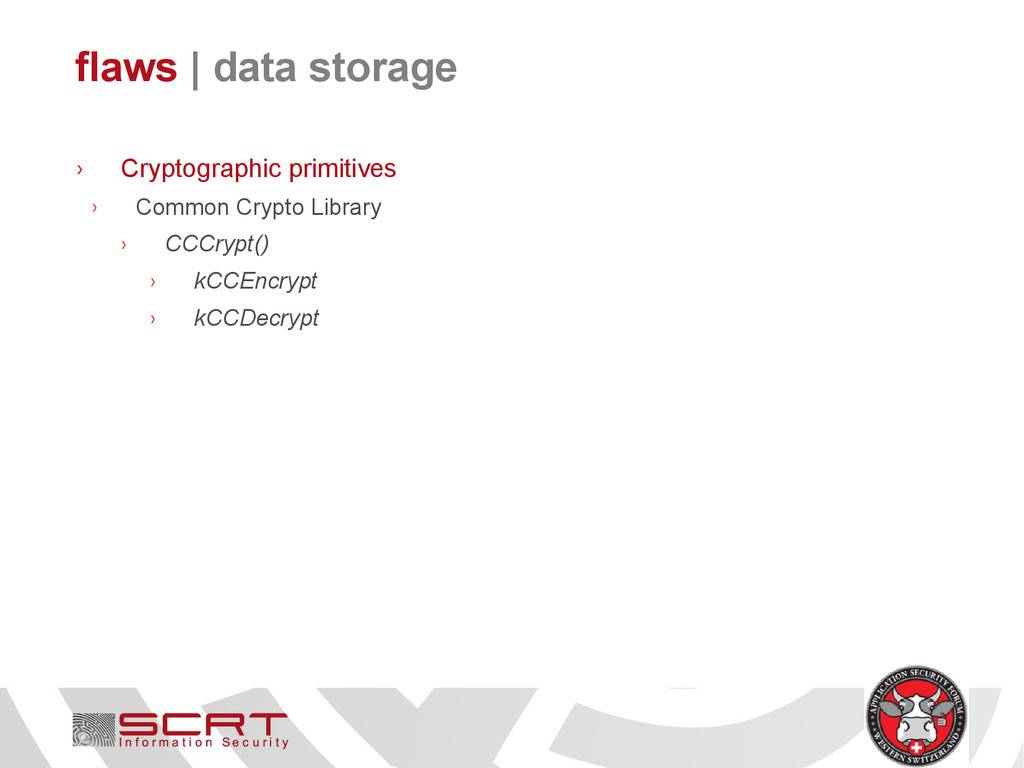
flaws | data storage › Cryptographic primitives › Common Crypto
Library › CCCrypt() › kCCEncrypt › kCCDecrypt -
flaws | information disclosure › The previous seems obvious, but...
› Logs ? › Automagically created files ? -
flaws | external interactions › Files handling › CFBundleDocumentTypes in
Info.plist › IPC-like mechanism › URIs handlers › CFBundleURLTypes in Info.plist › Implementation of handleOpenURL or OpenURL -
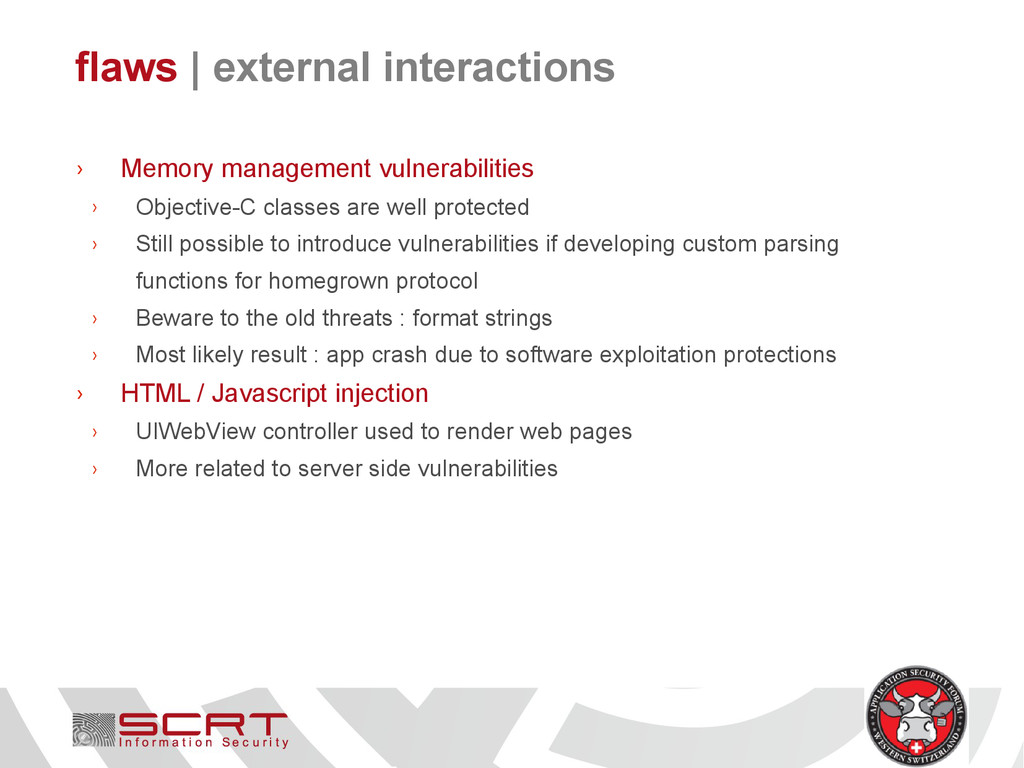
flaws | external interactions › Memory management vulnerabilities › Objective-C
classes are well protected › Still possible to introduce vulnerabilities if developing custom parsing functions for homegrown protocol › Beware to the old threats : format strings › Most likely result : app crash due to software exploitation protections › HTML / Javascript injection › UIWebView controller used to render web pages › More related to server side vulnerabilities -
flaws | server side › Most of the time, included
in the scope of the audit › Lot of applications are communicating with web-services › Common flaws › No need to present the Top10 -
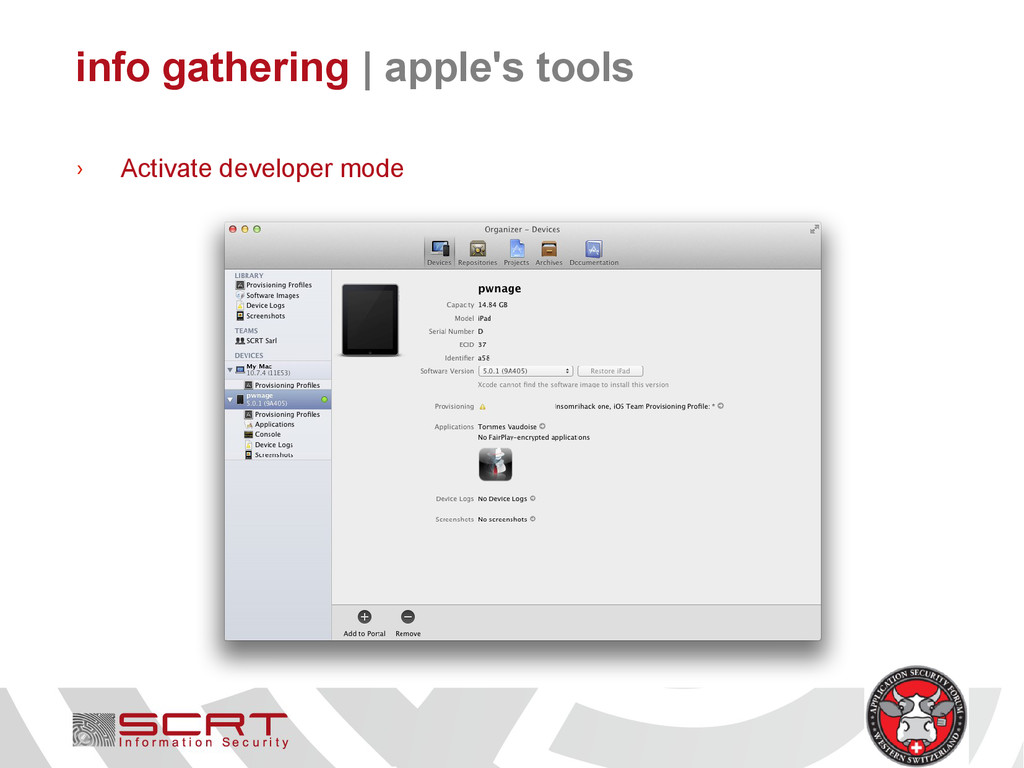
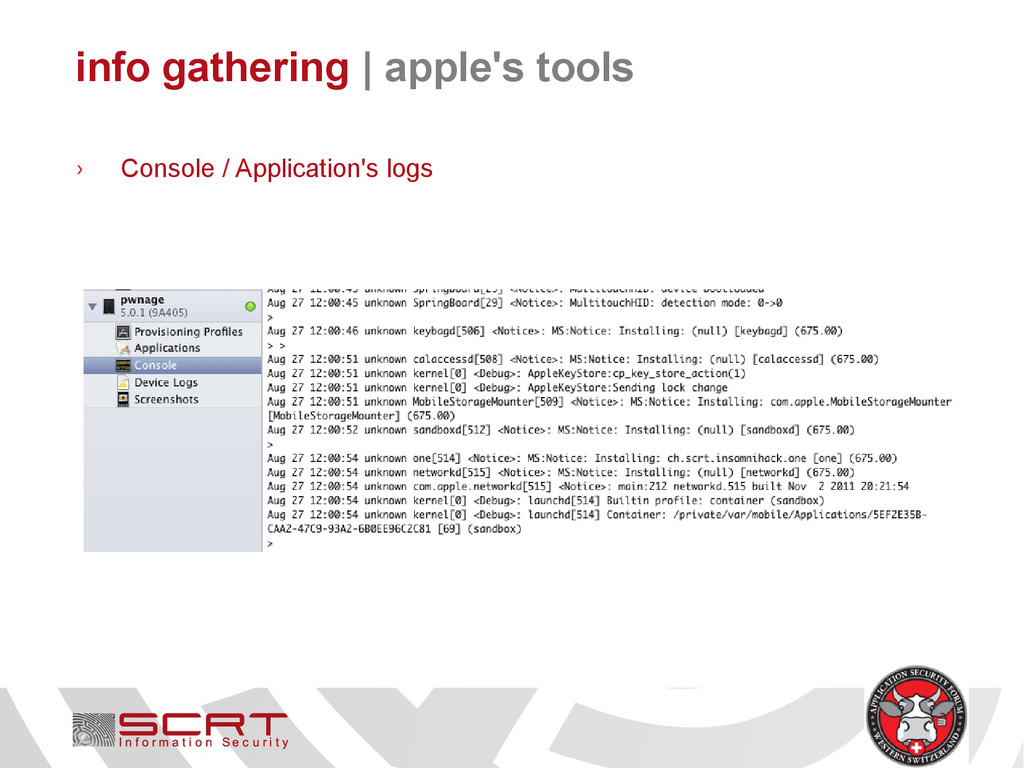
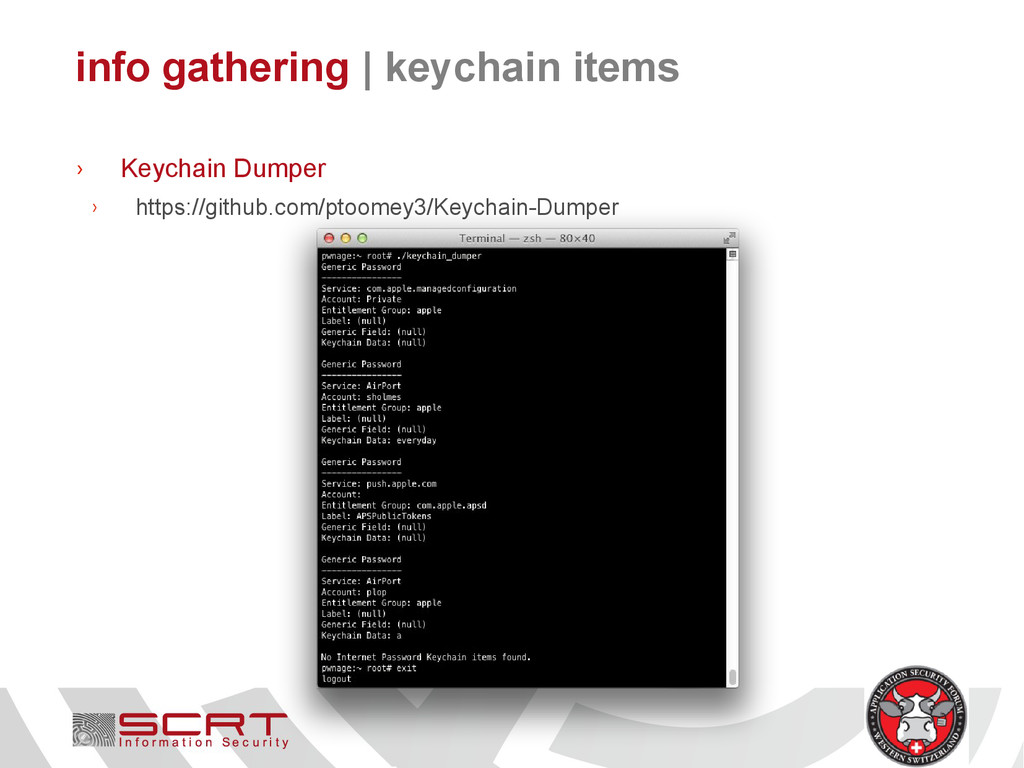
info gathering | apple's tools › First idea most people
will have › Let's jailbreak it ! › There is another way › Stealthier to do a first recon › Still, jailbreaking the auditor's device is mandatory › Kudos to the jailbreakers teams for their work ! -
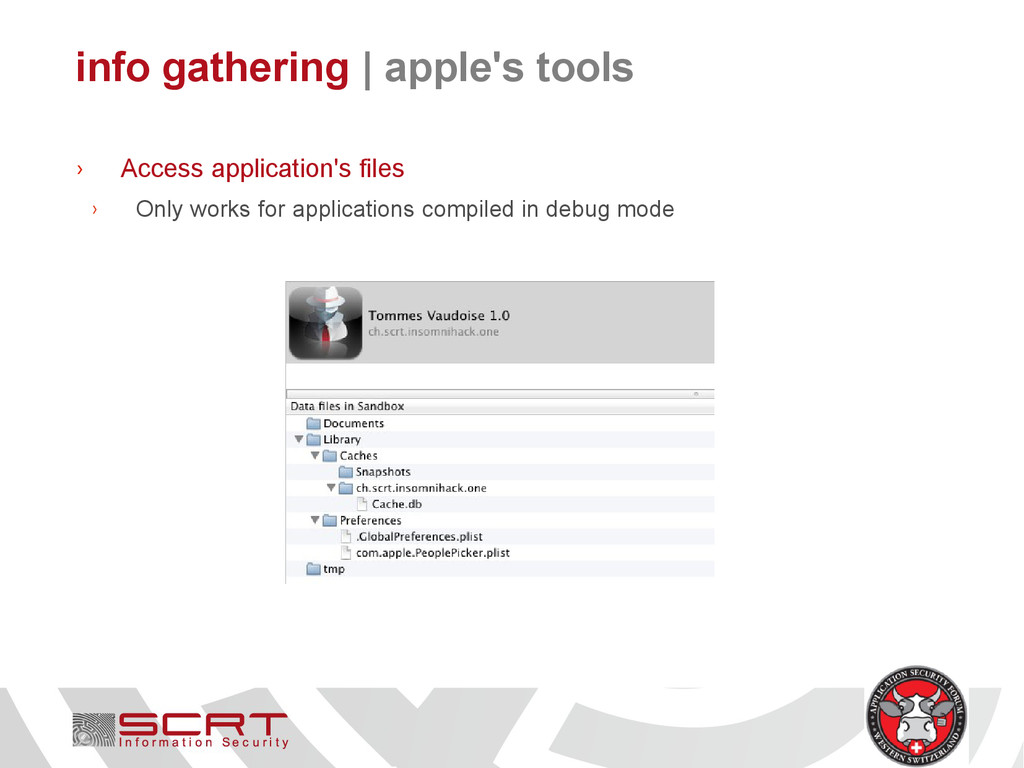
info gathering | apple's tools › Access application's files ›
Only works for applications compiled in debug mode -
info gathering | getting access to the device › Now
you can do it › Enough documentation on jailbreaking online › Personnal choice › Create a firmware with the smalest footprint as jailbreak detection mechanisms mostly check for Cydia presence › Use device that can be pwned using bootloader vulnerability in DFU mode › Use tcprelay.py relying on usbmux to ssh to the device through the usb cable -
network analysis | communication snooping › Main idea › Use
{burp ;zap ;...} to intercept the trafic and manipulate it › Problem › What about if the developers are using SSL and best-practices ? -
network analysis | communication snooping › If you are doing
an assignment mixing pentest and code review › Use the Simulator › Certificates store › Based on a SQLite3 database › ~/Library/Application Support/iPhone Simulator/<sdk>/Library/Keychains/TrustStore.sqlite3 › GDSSecurity released a script automating the insertion of x509 certificates in the database › https://github.com/GDSSecurity/Add-Trusted-Certificate-to-iOS-Simulator -
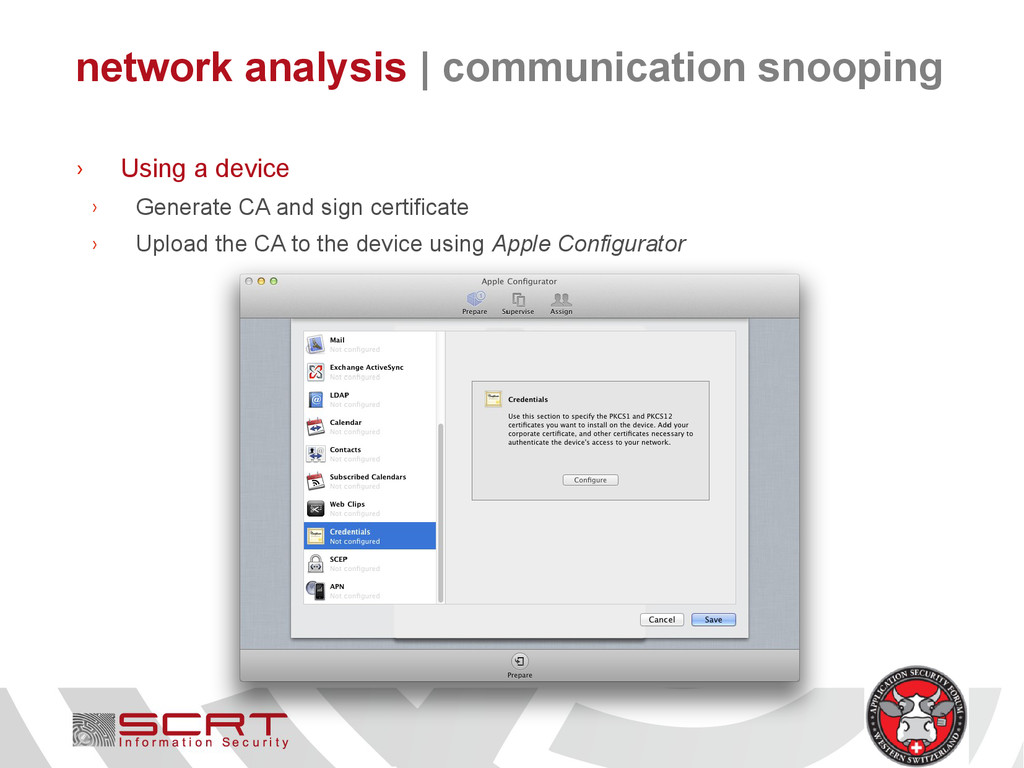
network analysis | communication snooping › Using a device ›
Generate CA and sign certificate › Upload the CA to the device using Apple Configurator -
network analysis | communication snooping › Won't go further on
this subject › Joins classic web service pentesting › Except you are using a specific application and not a browser -
reverse engineering | why ? › Pentesting is not code
review › If you want to understand an application behavior you have to reverse it › Static › Hexdump › otool › IDA Pro › Hopper › Dynamic › GDB -
reverse engineering | need to know › Architecture › File
format for Objective-C executables › ARM basics › Language › Objective-C basics › ARM assembly basics › AppStore › How to decrypt AppStore binaries -
reverse engineering | appstore › Applications from the AppStore are
encrypted › DRM › Fair Play like › Do it manually › GDB, set, go ! › Automatic › Crackulous (won't work on executables compiled with PIE) › Clutch -
reverse engineering | obj-c to arm › Objective-C › [ObjectPointer
Method:42] › C++ equivalent › ObjectPointer->Method(42) › Pseudo C generated by the compiler › objc_msgSend(ObjectPointer, "Method", 42) › ARM assembly › -
reverse engineering | obj-c to arm › Reflective language ›
Access to own definition › Call methods from names -
reverse engineering | where to begin ? › Main class
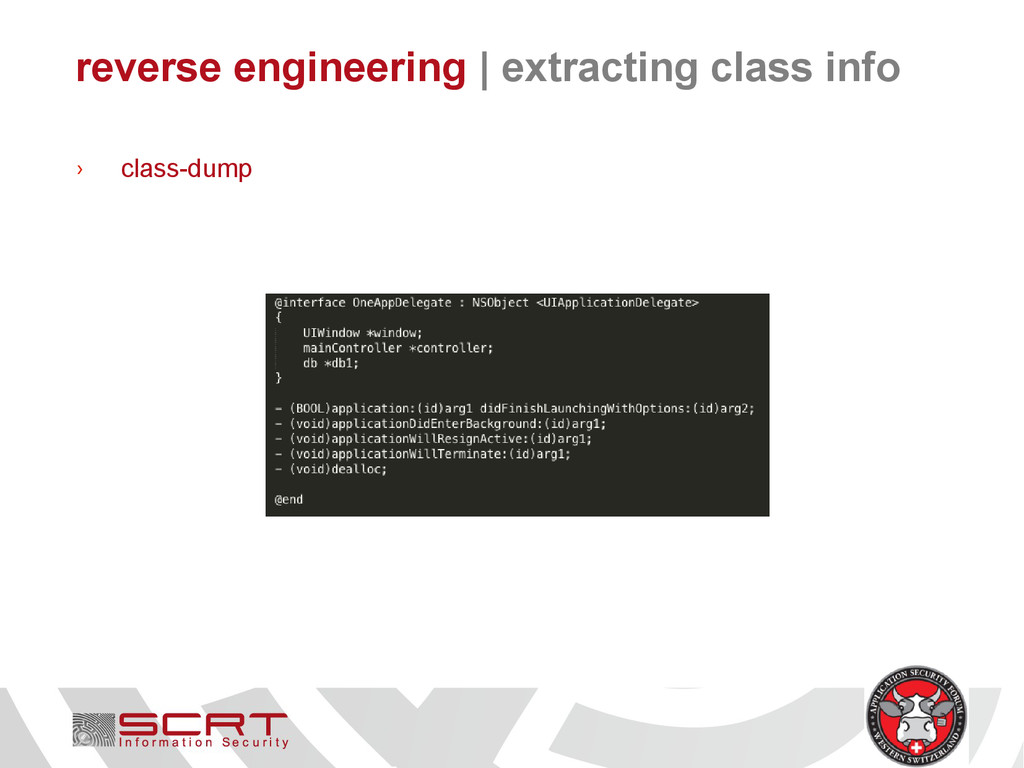
› Derived from UIApplicationDelegate › Implements applicationDidFinishLaunching or applicationDidFinishLaunchingWithOptions › Views › Derived from UI*ViewController › Implement viewDidLoad -
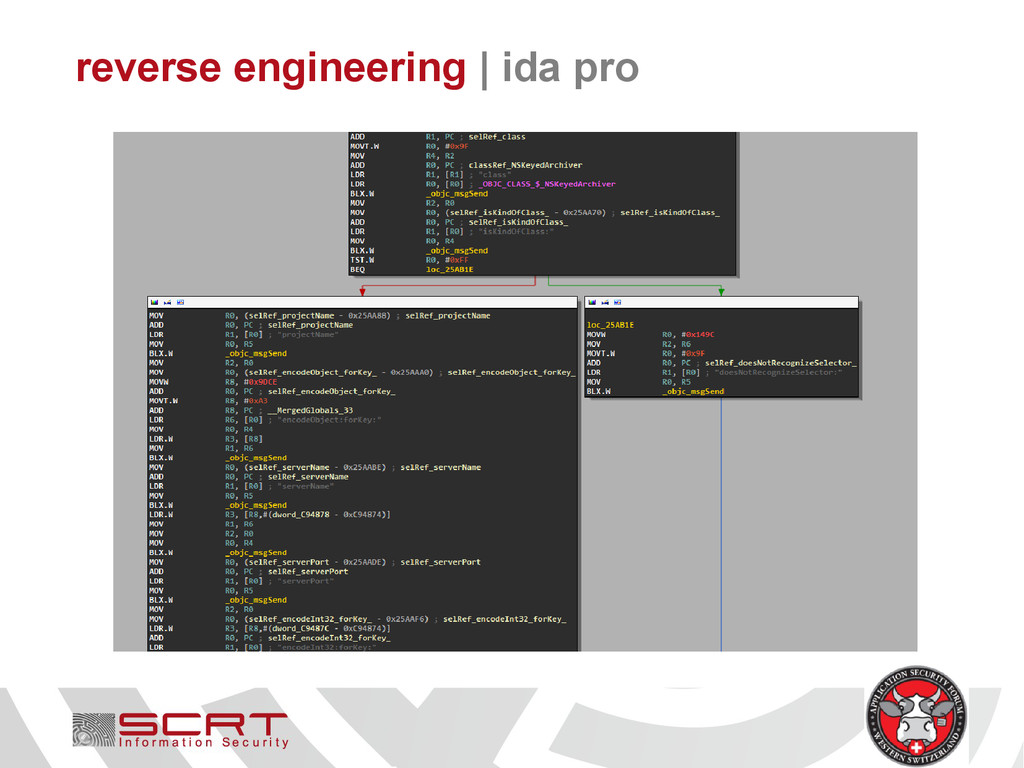
reverse engineering | static analysis › Goals › Understand the
application's algorithms › Tools › IDA Pro › Hopper › fixobjc.idc to resolve XREFs and parse Obj-C structures › Built-in functionality since version 6.2 -
reverse engineering | dynamic analysis › Goals › Understand the
application's algorithms › Allows to tamper data › But data tampering is not done with Burp ? › What happens when the protocol is encrypted ? › Need to find the function encrypting the data › Set breakpoint › Modify the data in-memory -
reverse engineering | dynamic analysis › GDB › Provided by
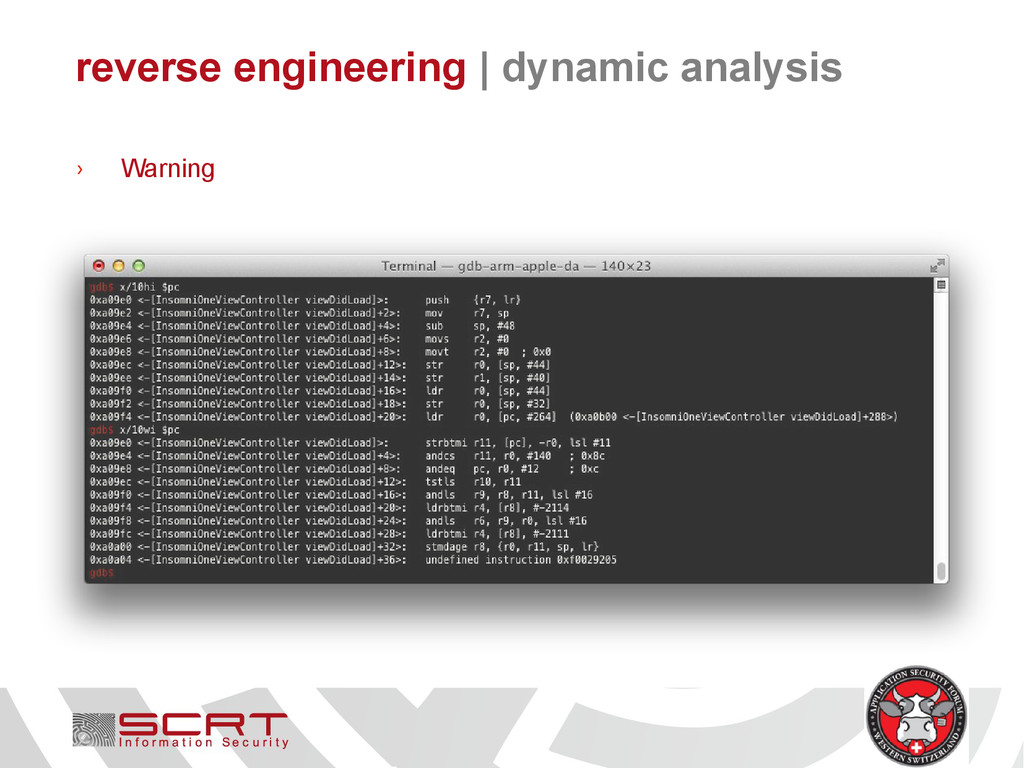
Apple as part of iOS SDK › Standalone version or gdbserver with gdb version for ARM targets › Advantage of gdbserver is ability to launch GUI applications › Highly recommend gdbinit* by @osxreverser › Entitlement › Binary will not run out-of-the-box on iDevices › Need to add entitlements after extracting ARMv7 binary › ldid to the rescue * http://reverse.put.as/gdbinit/ -
reverse engineering | dynamic analysis › Startup › # ~/debugserver-armv7
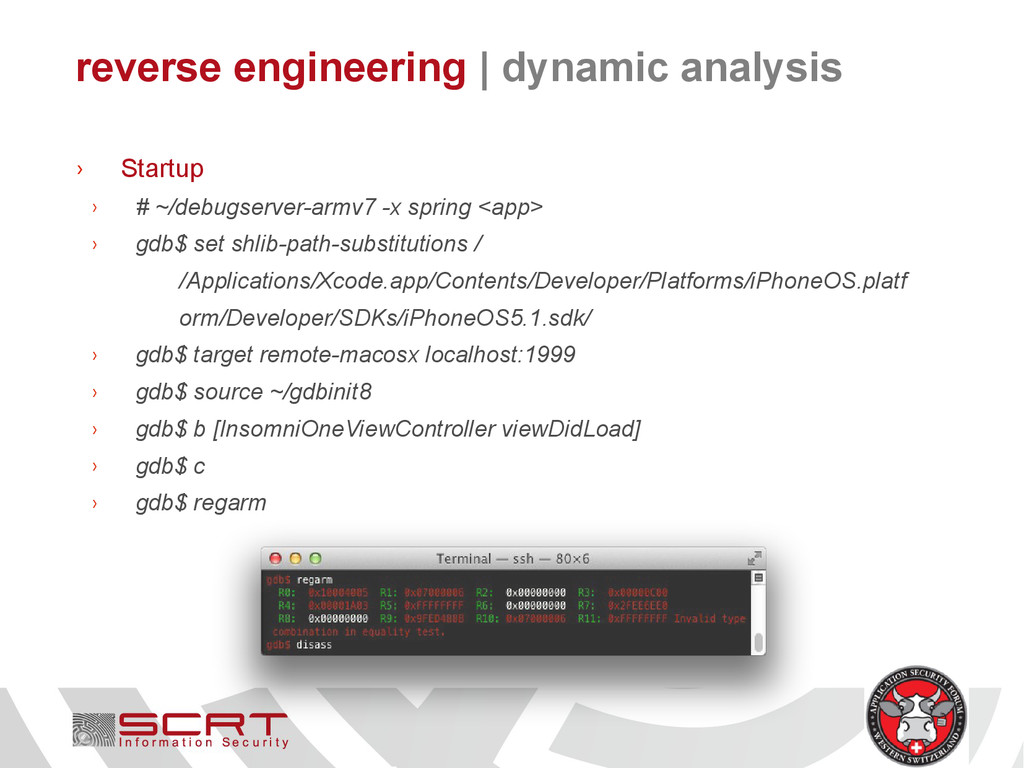
-x spring <app> › gdb$ set shlib-path-substitutions / /Applications/Xcode.app/Contents/Developer/Platforms/iPhoneOS.platf orm/Developer/SDKs/iPhoneOS5.1.sdk/ › gdb$ target remote-macosx localhost:1999 › gdb$ source ~/gdbinit8 › gdb$ b [InsomniOneViewController viewDidLoad] › gdb$ c › gdb$ regarm -
reverse engineering | dynamic analysis › Inspect / modify memory
› gdb$ po $r2 › gdb$ set {int}0xcafebabe = 1337 › For large amount of data › $ cat data.mod | hexdump -ve '1/4 "set {unsigned char *}( <addr> + %#2_ax) = %#02x\n"' > data.gdb -
reverse engineering | instrumentation › Automating an attack › Suppose
you found something (SQL injection, …) › Possible to call methods using gdb's call directive › Too slow to modify data on the fly by hands › Solution › Use code injection to modify the behaviour of the application › Modify data automagically -
reverse engineering | instrumentation › This is where you start
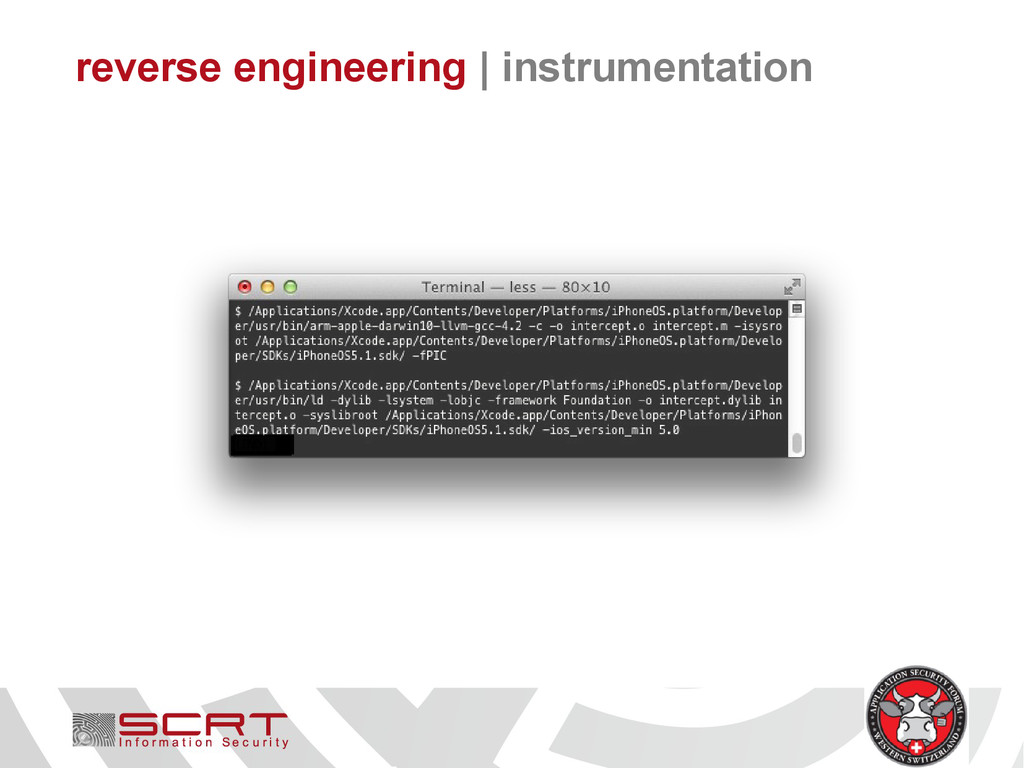
loving Objective-C › Hooking is a bundled feature › It's called 'swizzling' › Principle › Use the functions provided by Apple, like › class_replaceMethod › method_exchangeimplementations -
reverse engineering | instrumentation › Injecting into process › DYLD_PRELOAD
for stand-alone launch › DYLD_INSERT_LIBRARIES and SpringBoard.plist modification to inject in all graphical applications