Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
iOS malware: myth or reality?
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
Julien Bachmann
June 08, 2016
Technology
1.4k
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
iOS malware: myth or reality?
talk given at Security B-Sides London
Julien Bachmann
June 08, 2016
More Decks by Julien Bachmann
See All by Julien Bachmann
Advanced exploitation on Linux: ROP and infoleaks
milkmix
3
3.8k
Elasticsearch: incident detection use-cases and security best practices
milkmix
1
1.4k
Using Z3 to solve crackme
milkmix
0
2.1k
Software exploitation : ROP
milkmix
2
610
Clusis Campus 2015 : introduction to Suricata IDS
milkmix
0
320
String format exploitation in 15"
milkmix
1
390
Reversing iOS/OSX malware : wirelurker
milkmix
1
430
import-module IncidentResponse
milkmix
0
170
iOS applications auditing
milkmix
0
210
Other Decks in Technology
See All in Technology
推論基盤と Scale-Up Interconnect の現状と制約から俯瞰する技術動向
markunet
2
140
reInvent2026stby LT00 "Change your life!"
shinichirokawano
1
270
Temporal 最高!でも改めて「日付」について調べたら人類の負債すぎる件
riyaamemiya
0
230
Claude Code on Bedrock で統制をかける小ネタ集/claude-code-bedrock-governance-tips
emiki
1
13k
Gemini Intelligence 入門 ― AppFunctions と Gemini Nano
takuroabe
0
370
外国人エンジニアがVueプロトタイプで仕様を合わせている話 / Vue Fes Japan 2026 LT
eluwing
0
170
sue445's proposals 2026
sue445
0
150
野良MCPサーバーを排除せよ!MCPサーバーのガバナンス
yukiogawa
1
240
生成AI時代、PMは事業責任者に進化するともっと面白い〜PMだからこそ事業構造を動かせる時代に〜
kakehashi
PRO
0
870
クラウドサインを止めずに Nuxt へ 次の10年のために先に決めたこと
bengo4com
1
150
freeeにおけるSoftware Factory
freee
PRO
0
520
Agent × Maestro で始める モバイル E2E 端末準備からテスト実行・結果確認まで
sansantech
PRO
0
210
Featured
See All Featured
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
How to train your dragon (web standard)
notwaldorf
96
6.9k
Color Theory Basics | Prateek | Gurzu
gurzu
1
500
Game over? The fight for quality and originality in the time of robots
wayneb77
1
310
The Straight Up "How To Draw Better" Workshop
denniskardys
239
140k
Scaling GitHub
holman
464
140k
Have SEOs Ruined the Internet? - User Awareness of SEO in 2025
akashhashmi
0
530
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
Designing for humans not robots
tammielis
254
26k
The Art of Programming - Codeland 2020
erikaheidi
57
14k
The AI Search Optimization Roadmap by Aleyda Solis
aleyda
2
6.3k
Ten Tips & Tricks for a 🌱 transition
stuffmc
1
270
Transcript
C O N F I D E N T I
A L ©2016 KUDELSKI GROUP / All rights reserved. iOS MALWARE : MYTH OR REALITY? Julien Bachmann @milkmix_
INTRODUCTION
C O N F I D E N T I
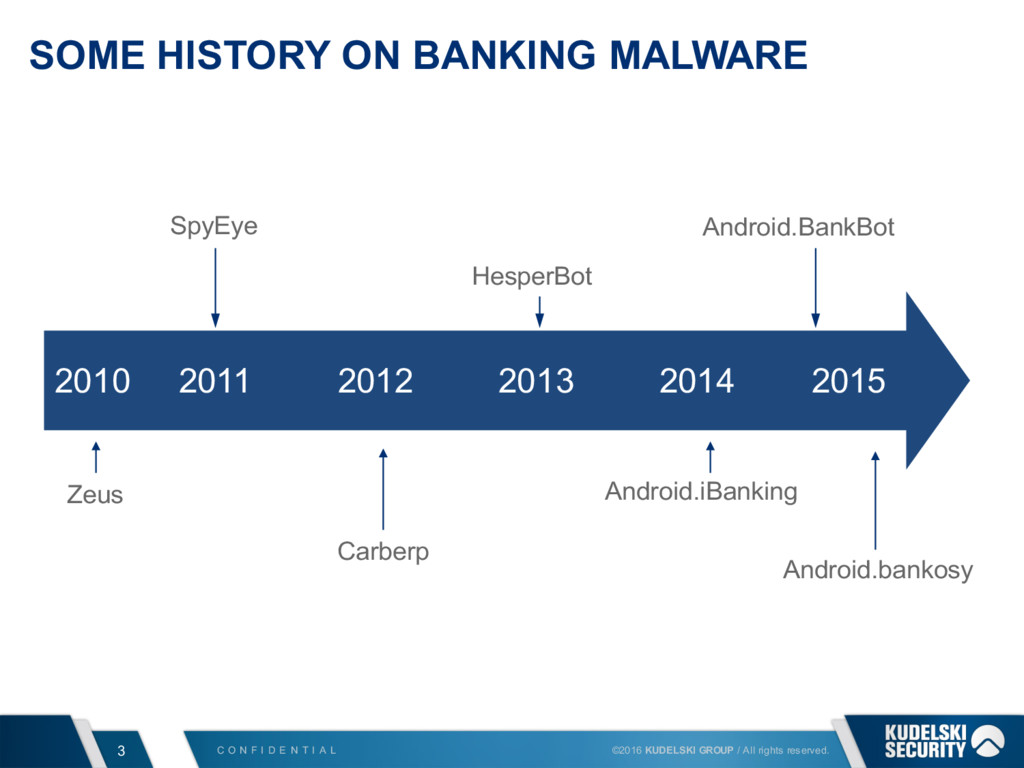
A L 3 ©2016 KUDELSKI GROUP / All rights reserved. 2010 2011 2012 2013 2014 2015 SOME HISTORY ON BANKING MALWARE Zeus SpyEye Carberp HesperBot Android.iBanking Android.BankBot Android.bankosy
C O N F I D E N T I
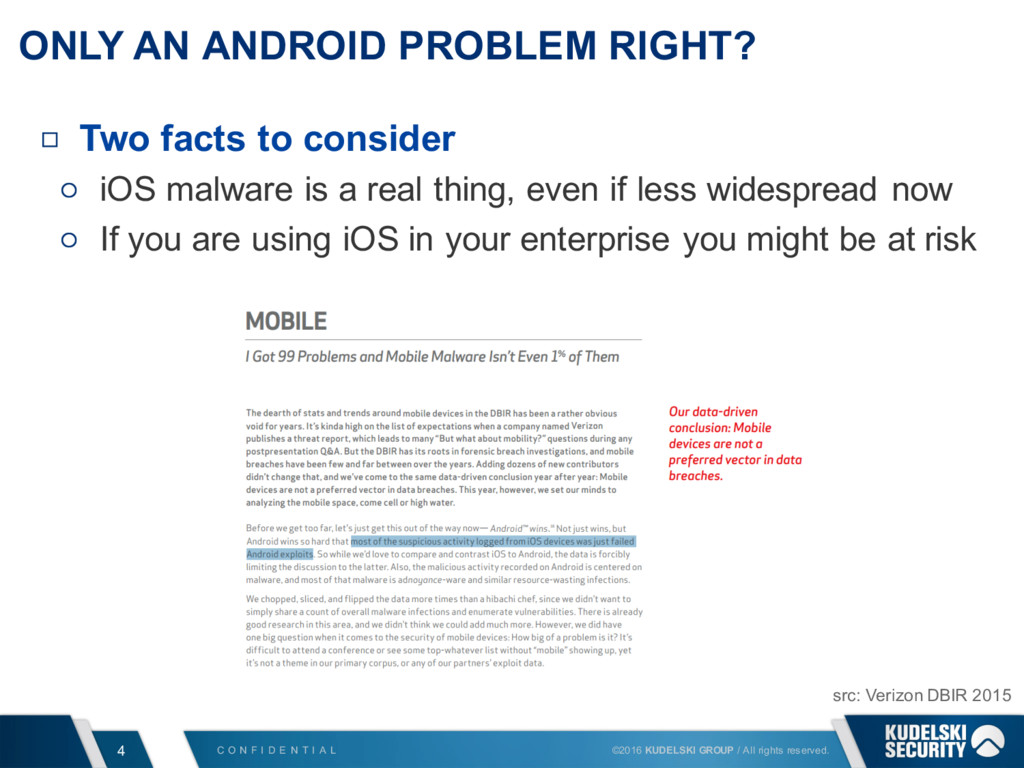
A L 4 ©2016 KUDELSKI GROUP / All rights reserved. ONLY AN ANDROID PROBLEM RIGHT? Two facts to consider iOS malware is a real thing, even if less widespread now If you are using iOS in your enterprise you might be at risk src: Verizon DBIR 2015
C O N F I D E N T I
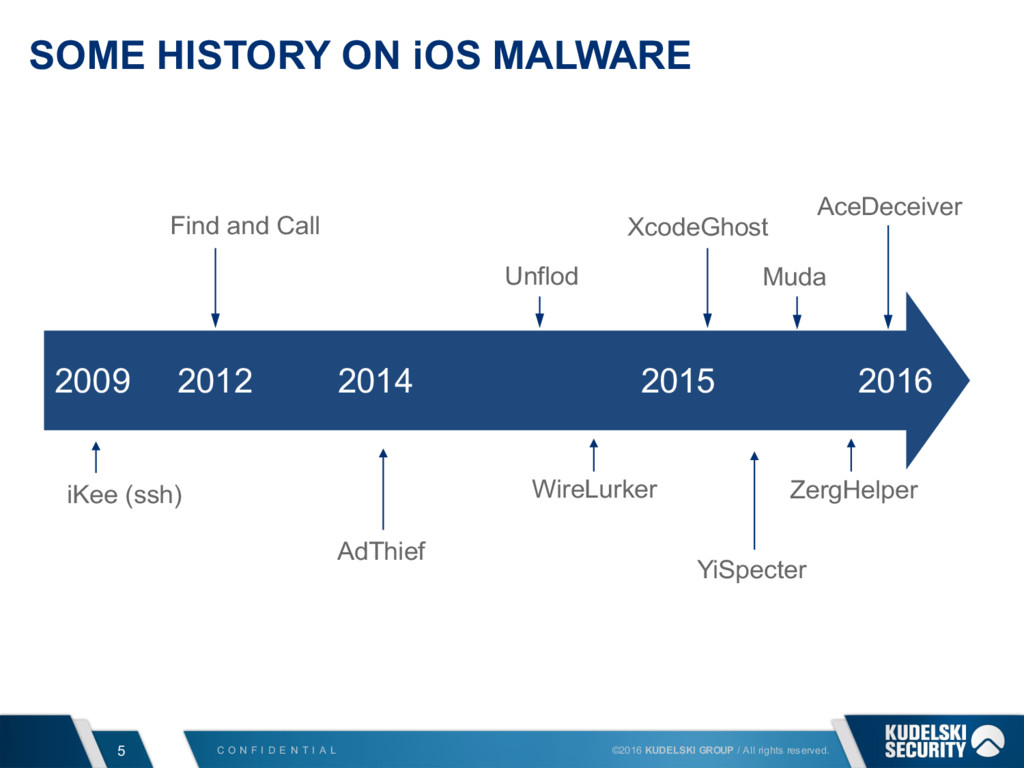
A L 5 ©2016 KUDELSKI GROUP / All rights reserved. 2009 2012 2014 2015 2016 SOME HISTORY ON iOS MALWARE iKee (ssh) Find and Call AdThief Unflod WireLurker XcodeGhost YiSpecter Muda ZergHelper AceDeceiver
QUICK RECAP ON iOS SECURITY
C O N F I D E N T I
A L 7 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION Limited number of installation paths Closed platform well restricted by Apple Only authorized methods controlled by Apple on non- jailbroken device
C O N F I D E N T I
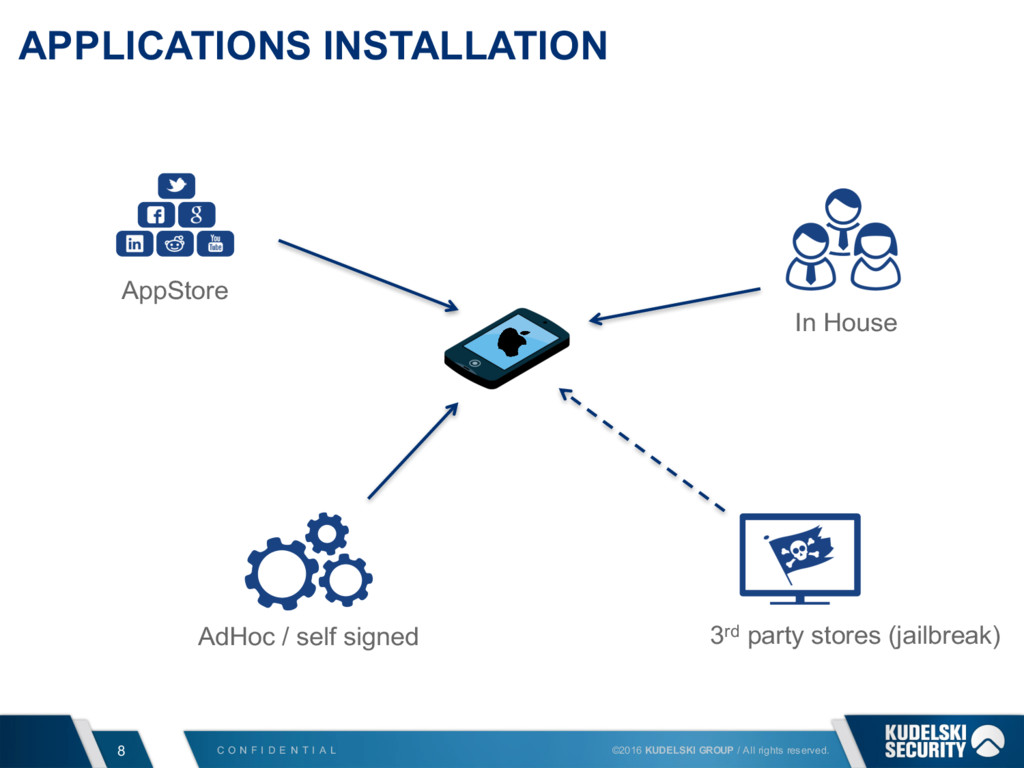
A L 8 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION AppStore AdHoc / self signed In House 3rd party stores (jailbreak)
C O N F I D E N T I
A L 9 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION AppStore Require Developer certificate Applications are reviewed In House Common method for enterprise applications Require Enterprise Developer account Require Provisioning profile installed on device Ad Hoc Used during development Limited to 100 devices with provisioned UDID Self signed New with iOS 9 and Xcode 7, sign for personal devices
C O N F I D E N T I
A L 10 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS INSTALLATION The jailbroken case Several advantages while jailbreaking a device Allows to validate security of applications But disable code signing validations Allows installing applications from untrusted sources
C O N F I D E N T I
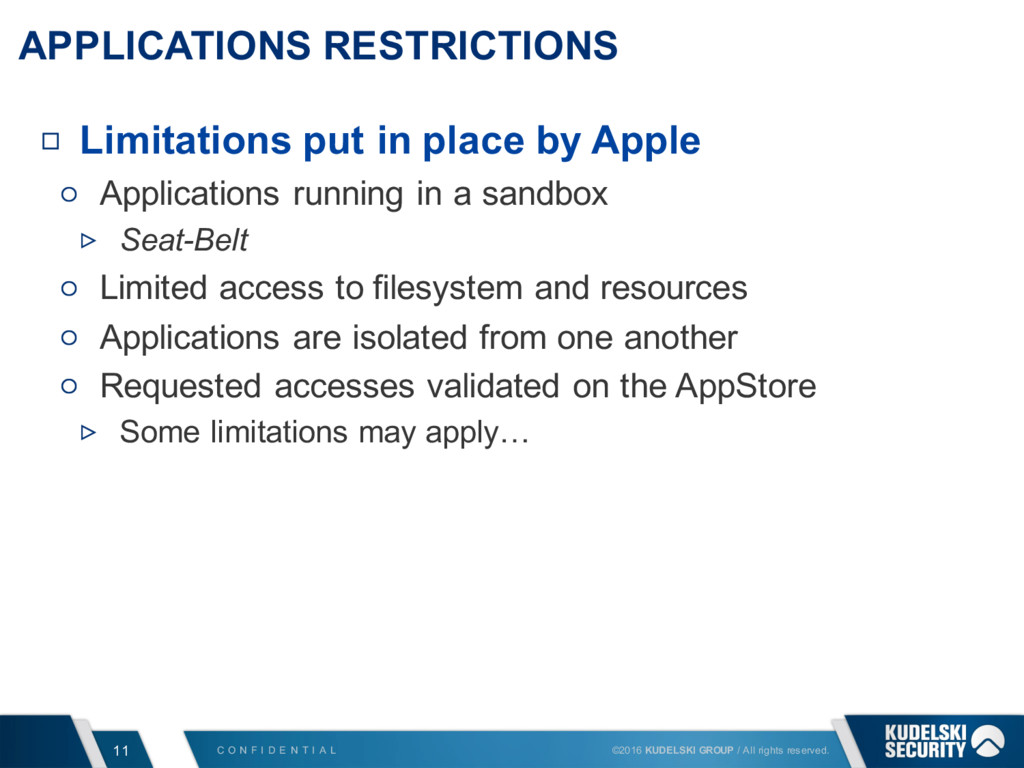
A L 11 ©2016 KUDELSKI GROUP / All rights reserved. APPLICATIONS RESTRICTIONS Limitations put in place by Apple Applications running in a sandbox Seat-Belt Limited access to filesystem and resources Applications are isolated from one another Requested accesses validated on the AppStore Some limitations may apply…
C O N F I D E N T I
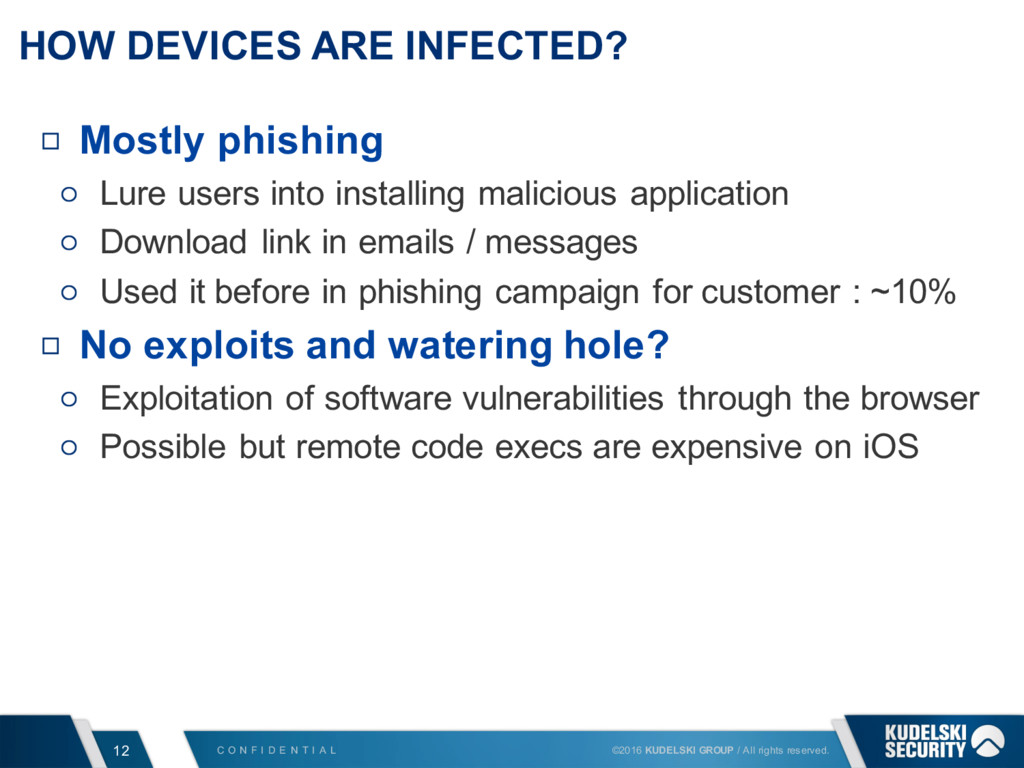
A L 12 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED? Mostly phishing Lure users into installing malicious application Download link in emails / messages Used it before in phishing campaign for customer : ~10% No exploits and watering hole? Exploitation of software vulnerabilities through the browser Possible but remote code execs are expensive on iOS
C O N F I D E N T I
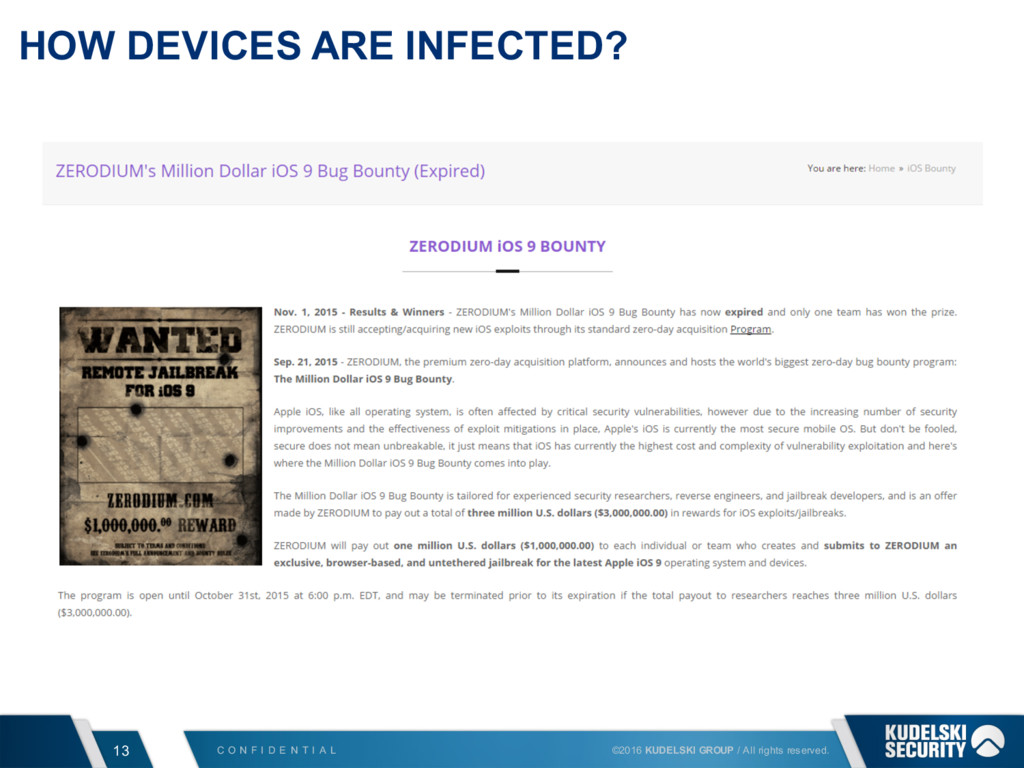
A L 13 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED?
C O N F I D E N T I
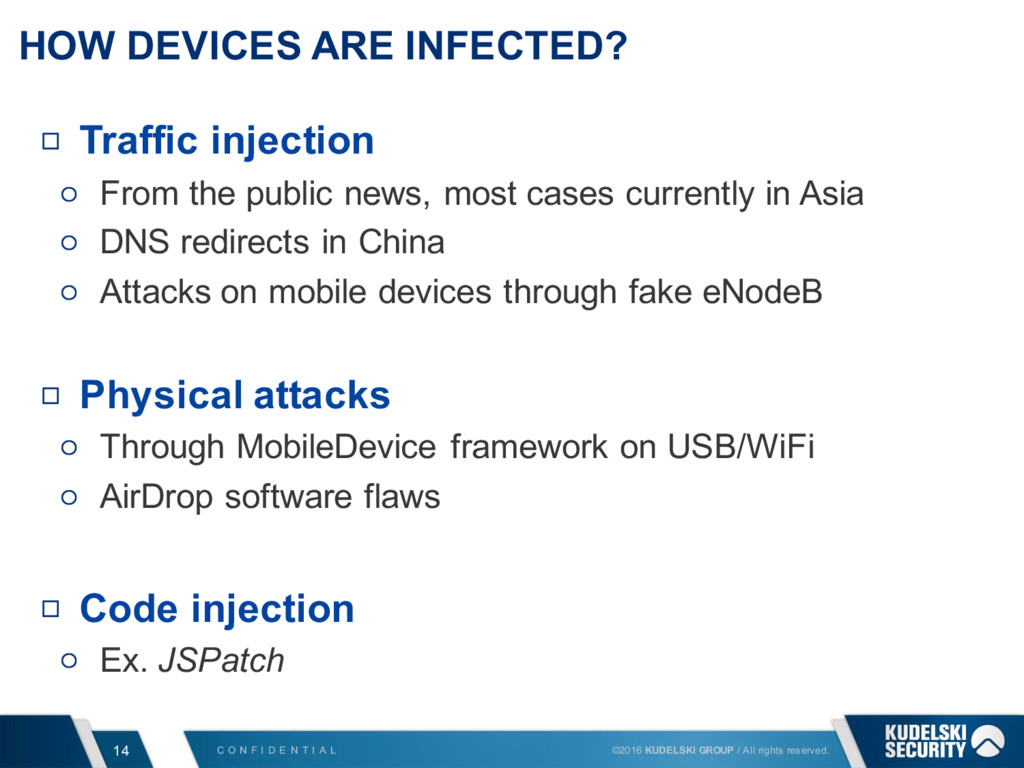
A L 14 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED? Traffic injection From the public news, most cases currently in Asia DNS redirects in China Attacks on mobile devices through fake eNodeB Physical attacks Through MobileDevice framework on USB/WiFi AirDrop software flaws Code injection Ex. JSPatch
C O N F I D E N T I
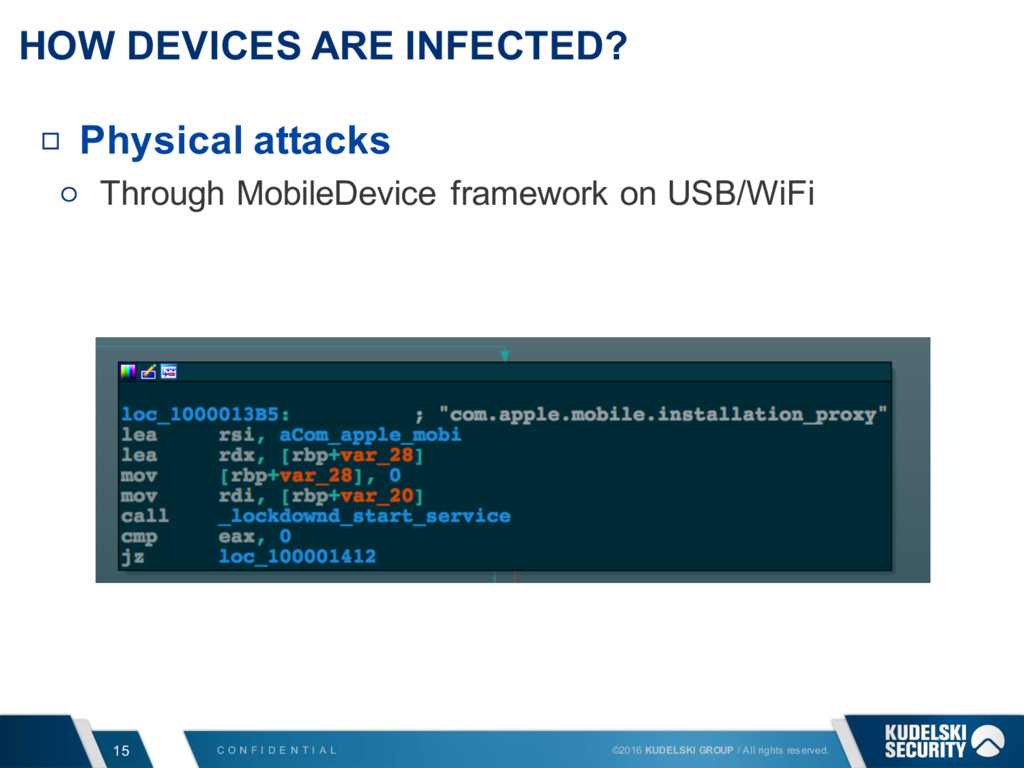
A L 15 ©2016 KUDELSKI GROUP / All rights reserved. HOW DEVICES ARE INFECTED? Physical attacks Through MobileDevice framework on USB/WiFi
C O N F I D E N T I
A L 16 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? Phishing is not enough Code signing still performed by iOS Except on jailbroken devices Ad Hoc Too complicated, requires UDID Leaks in the past years, limited now with Apple restrictions Potentially on very targeted attacks Enterprise Developer Certificate User validation Certificate can be easily revoked by Apple upon detection
C O N F I D E N T I
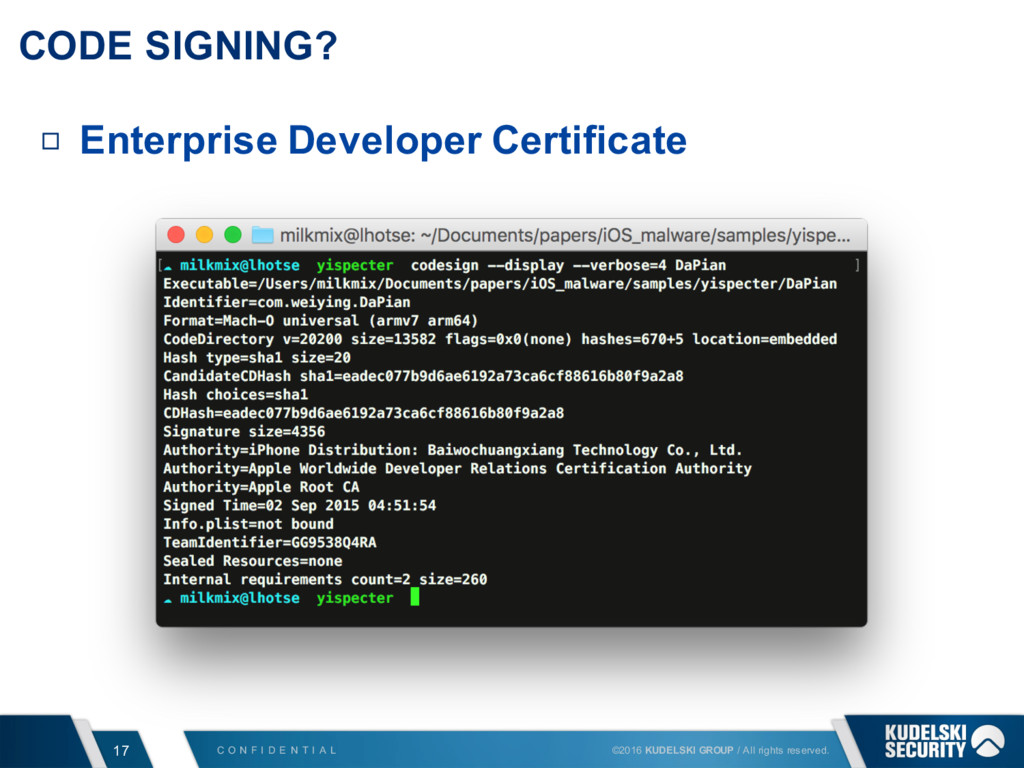
A L 17 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? Enterprise Developer Certificate
C O N F I D E N T I
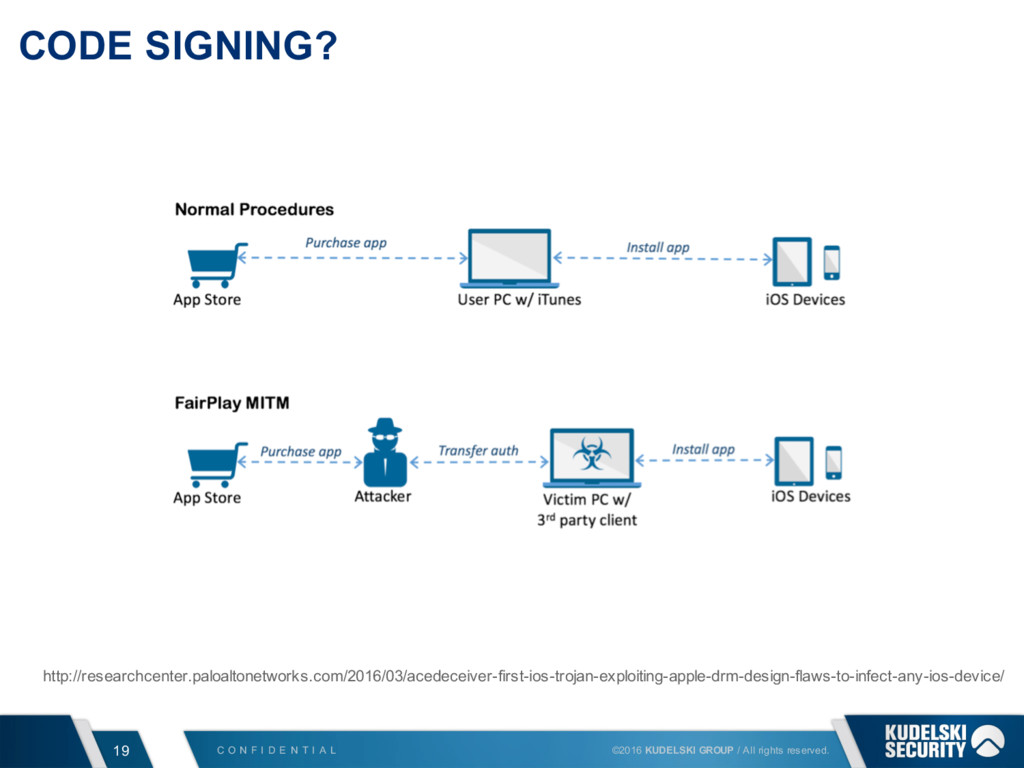
A L 18 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? Recently in the news “Malware bypassing Apple code signing mechanism” AceDeceiver Truth (explanation w/o the hype) Still requires to be published and accepted by Apple at least once in one of the stores (US, CH, CN, …) Can use geolocation of incoming IP addresses to enable/disable features in the code Possible to exploit design flaw in the validation process when installing from iTunes on Mac/PC Allows to install the malware from Mac/PC even if certificate revoked
C O N F I D E N T I
A L 19 ©2016 KUDELSKI GROUP / All rights reserved. CODE SIGNING? http://researchcenter.paloaltonetworks.com/2016/03/acedeceiver-first-ios-trojan-exploiting-apple-drm-design-flaws-to-infect-any-ios-device/
MALICIOUS ACTIONS
C O N F I D E N T I
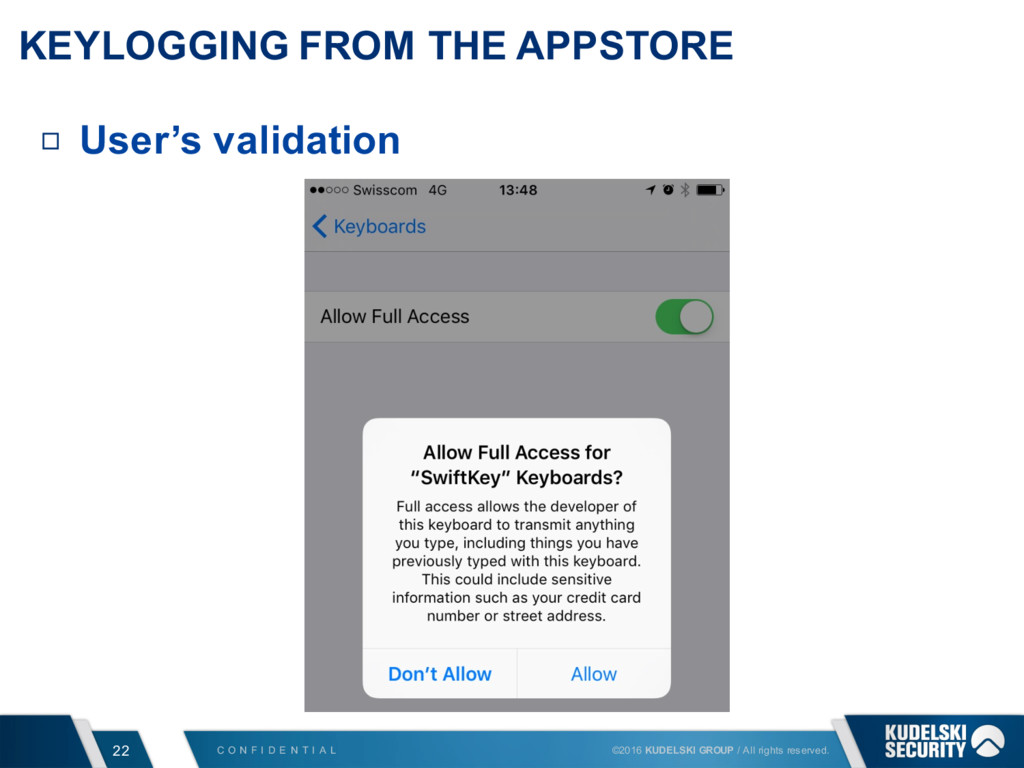
A L 21 ©2016 KUDELSKI GROUP / All rights reserved. APPSTORE PERMISSIONS Audio recording Easily performed through the API When in background applications are preempted by iOS Except if defined as background application Ribbon displayed to the user Keylogging Since iOS8 : extensions (keyboard, browser filtering, …) Isolated from standard application so no access to Internet or files… … except if requested
C O N F I D E N T I
A L 22 ©2016 KUDELSKI GROUP / All rights reserved. KEYLOGGING FROM THE APPSTORE User’s validation
C O N F I D E N T I
A L 23 ©2016 KUDELSKI GROUP / All rights reserved. PRIVATE API In the news
C O N F I D E N T I
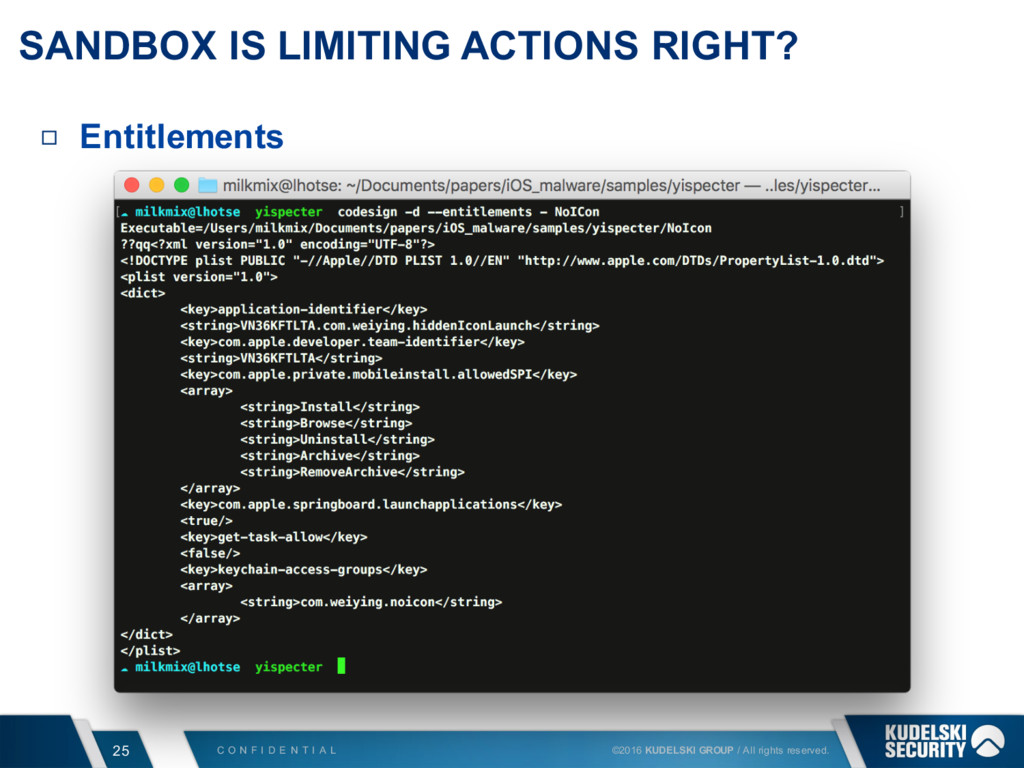
A L 24 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Entitlements 1. Developers should specify entitlements at compilation • http://newosxbook.com/ent.jl 2. Validated by the AppStore 3. Some additional rights for selected partners 4. Enforced on device by seat-belt Private API Forbidden by Apple in the guidelines Still requires entitlements to access data due to sandbox Does not break applications isolation principle Would require to elevate privileges to do so Or flaws in the private APIs validation mechanism (Stefan Esser app) Difficult to detect with automated analysis (static and dynamic)
C O N F I D E N T I
A L 25 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Entitlements
C O N F I D E N T I
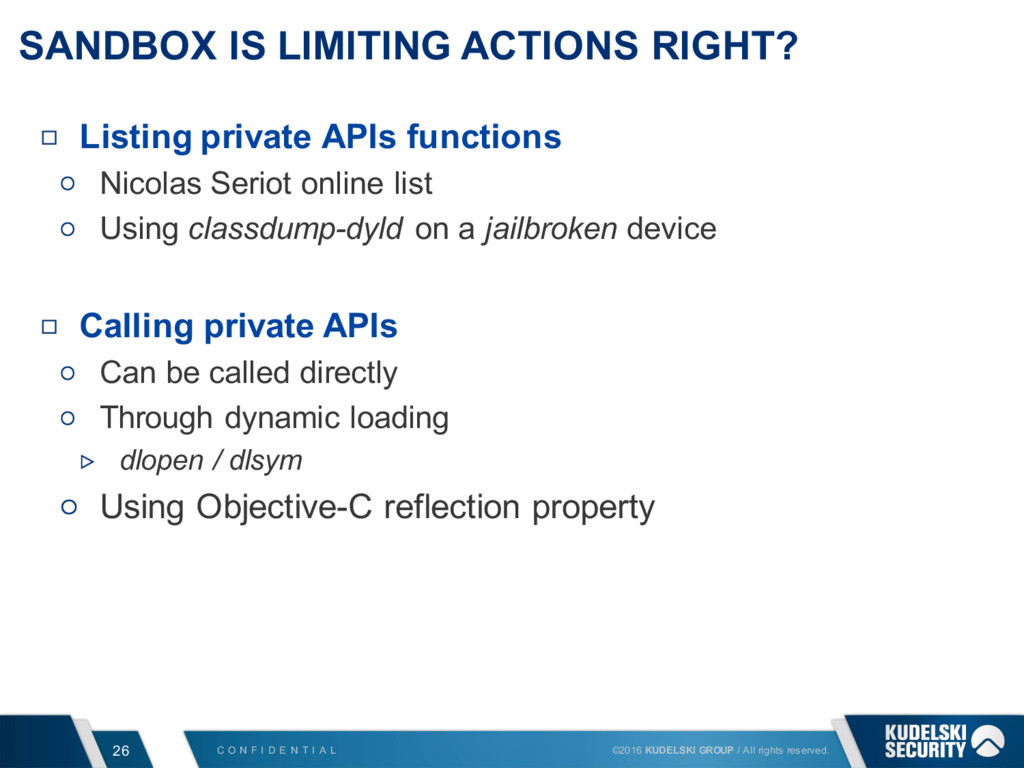
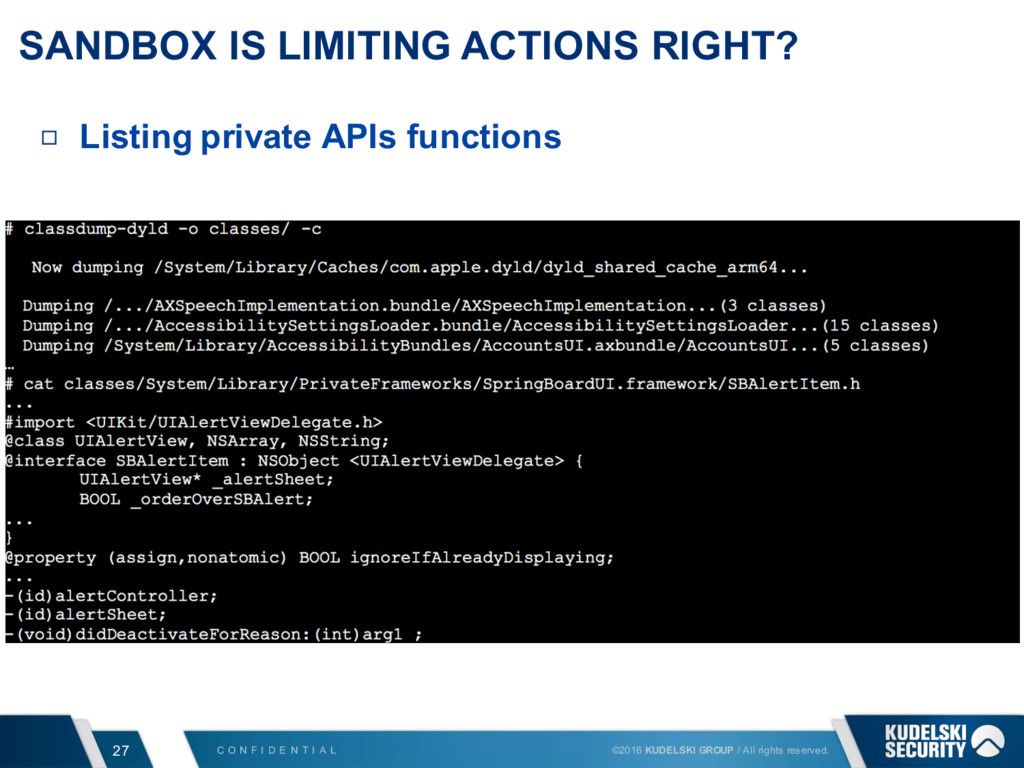
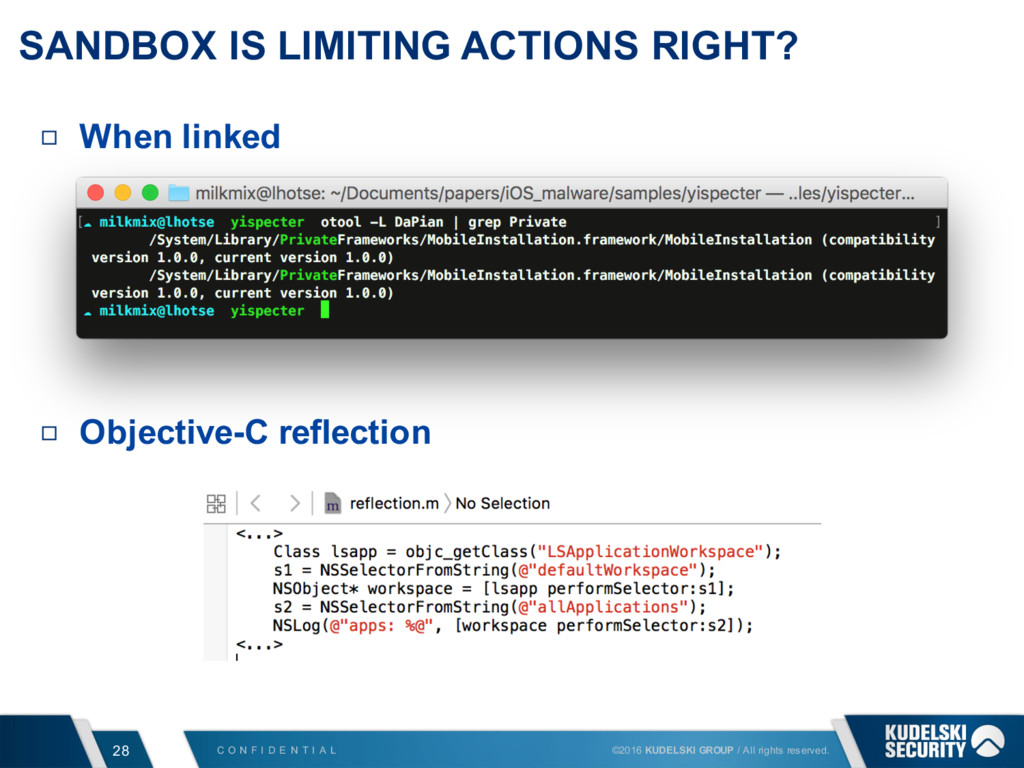
A L 26 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Listing private APIs functions Nicolas Seriot online list Using classdump-dyld on a jailbroken device Calling private APIs Can be called directly Through dynamic loading dlopen / dlsym Using Objective-C reflection property
C O N F I D E N T I
A L 27 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? Listing private APIs functions
C O N F I D E N T I
A L 28 ©2016 KUDELSKI GROUP / All rights reserved. SANDBOX IS LIMITING ACTIONS RIGHT? When linked Objective-C reflection
C O N F I D E N T I
A L 29 ©2016 KUDELSKI GROUP / All rights reserved. THE IN HOUSE CASE Entitlements Defined at compilation Not validated by Apple outside of the AppStore flow As seen allows to use more sensitive Private API functions Offers more possibilities CoreTelephony framework Notifications on calls or messages IMSI / IMEI retrieval Install applications Access private information …
NON-APPLICATION BASED ATTACKS
C O N F I D E N T I
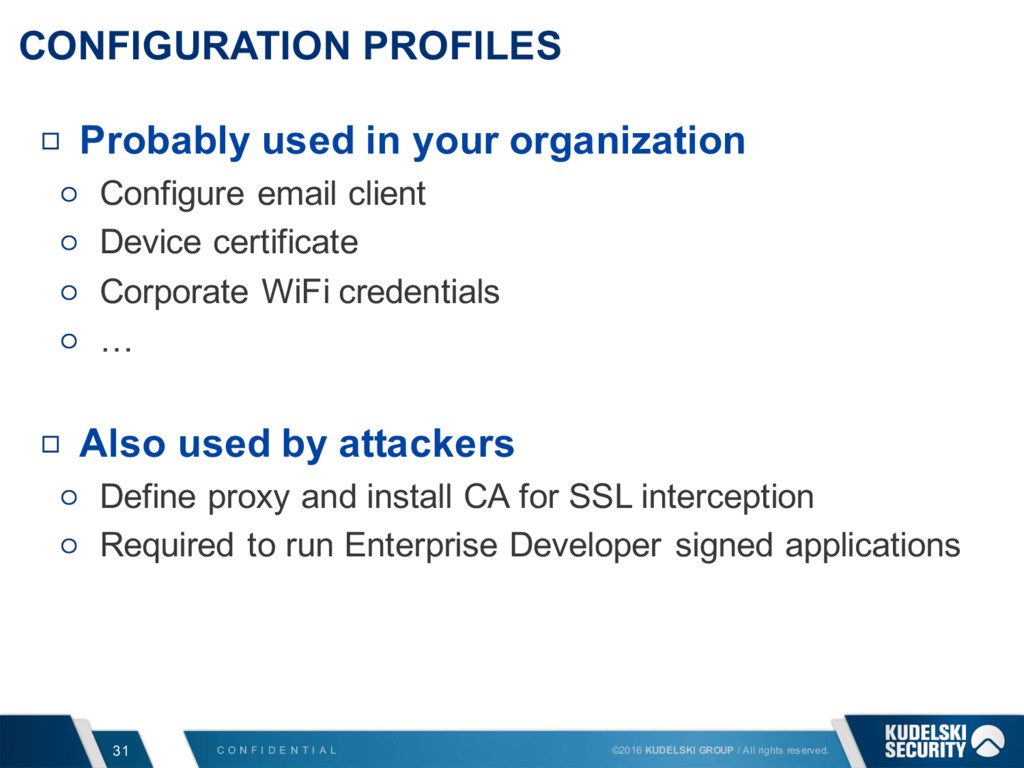
A L 31 ©2016 KUDELSKI GROUP / All rights reserved. CONFIGURATION PROFILES Probably used in your organization Configure email client Device certificate Corporate WiFi credentials … Also used by attackers Define proxy and install CA for SSL interception Required to run Enterprise Developer signed applications
PROTECTION AND DETECTION
C O N F I D E N T I
A L 33 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION Mobile devices are more complex to protect Network side Not always using your egress point Web filtering / network monitoring not applicable Endpoint side Operating system less open to 3rd party drivers Applications isolation Not an AV friendly environment
C O N F I D E N T I
A L 34 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE NETWORK IDS like features Use rulesets specific to mobile malware Examples Emerging Threats MOBILE_MALWARE rules Lookout Mobile Threat Intelligence feed Android only AFAIK Detect access to non-corporate configuration Detect download of IPA files signed with external Enterprise Developer accounts
C O N F I D E N T I
A L 35 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Leverage existing MDM/MAM solution Retrieve installed provisioning profiles All external ones should be suspicious Retrieve installed applications bundle names Match known malicious
C O N F I D E N T I
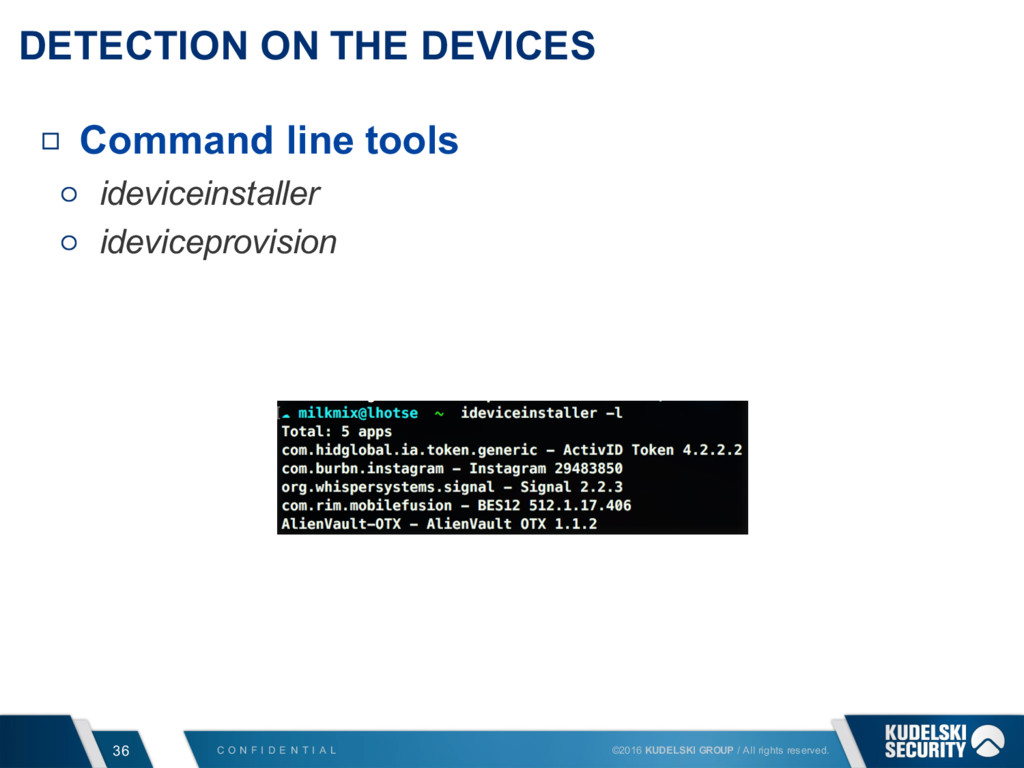
A L 36 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Command line tools ideviceinstaller ideviceprovision
C O N F I D E N T I
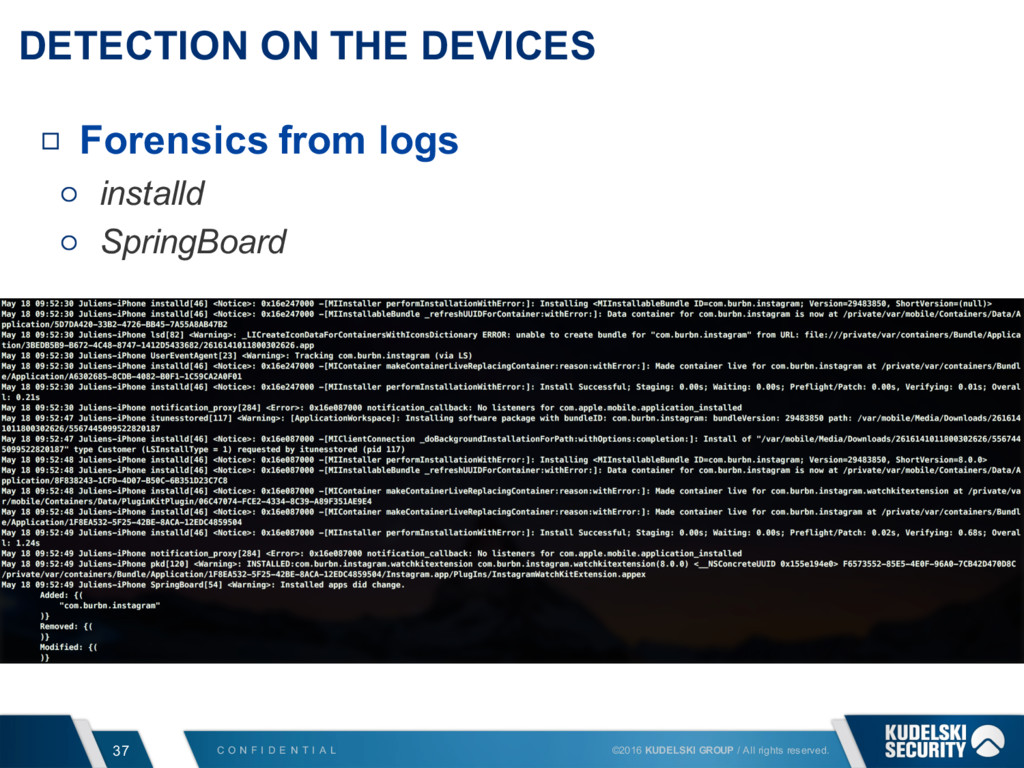
A L 37 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Forensics from logs installd SpringBoard
C O N F I D E N T I
A L 38 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Forensics from side channels logs Battery usage Data usage Both contain applications name and last executed timestamp Available from backups
C O N F I D E N T I
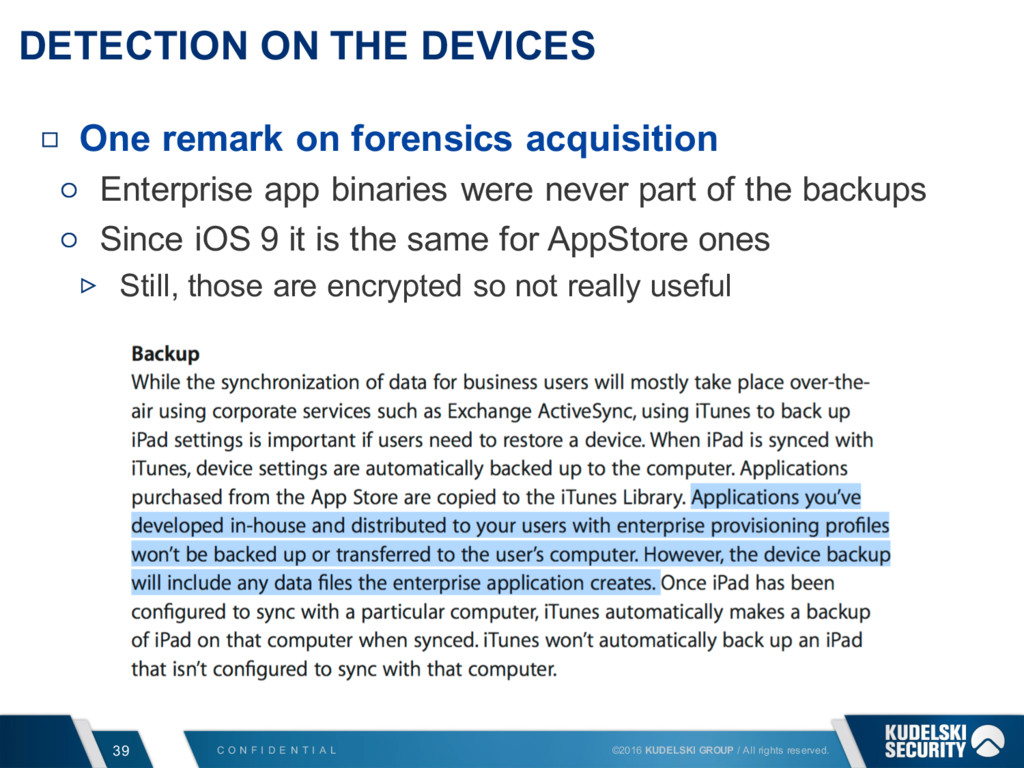
A L 39 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES One remark on forensics acquisition Enterprise app binaries were never part of the backups Since iOS 9 it is the same for AppStore ones Still, those are encrypted so not really useful
C O N F I D E N T I
A L 40 ©2016 KUDELSKI GROUP / All rights reserved. DETECTION ON THE DEVICES Future? USB scanning terminal to match known malicious bundles Workstation AV scanning connected devices
C O N F I D E N T I
A L 41 ©2016 KUDELSKI GROUP / All rights reserved. PROTECTION Update devices Decrease potential vulnerabilities exploitation Prevent known jailbreaking methods Device hardening iOS security best-practices Disable AirDrop Force 6-digits passcode …
C O N F I D E N T I
A L 42 ©2016 KUDELSKI GROUP / All rights reserved. PROTECTION Users training Do not install 3rd party provisioning profiles Do not install applications outside of the AppStore or provided by corporate MDM
C O N F I D E N T I
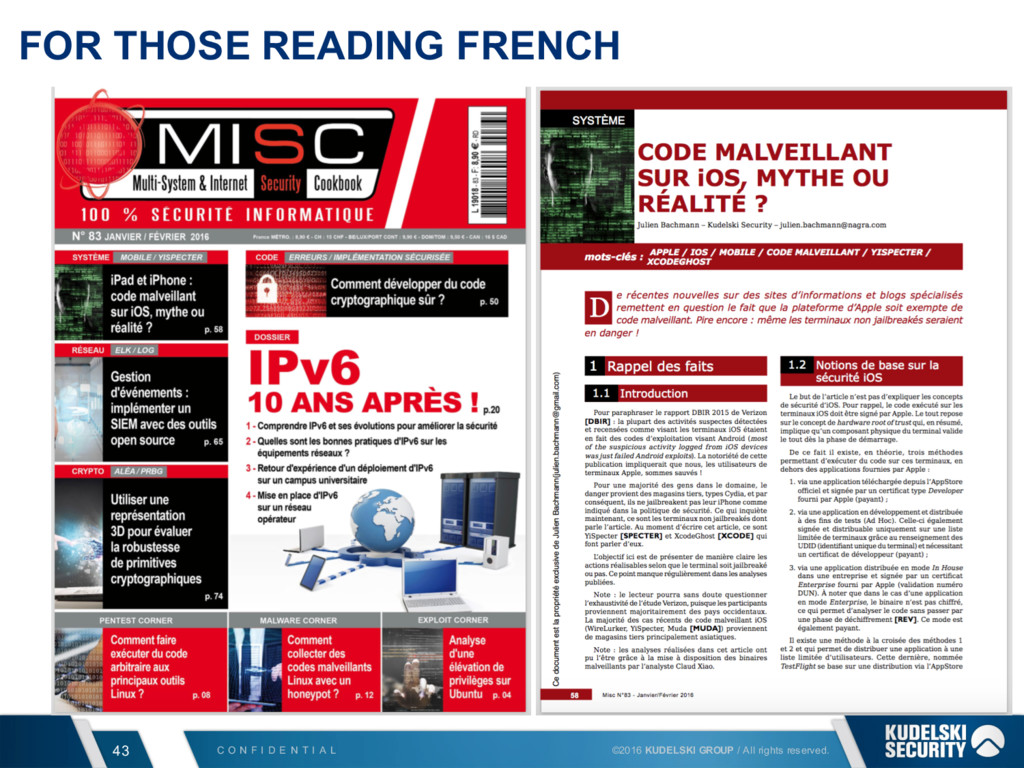
A L 43 ©2016 KUDELSKI GROUP / All rights reserved. FOR THOSE READING FRENCH
C O N F I D E N T I
A L 44 ©2016 KUDELSKI GROUP / All rights reserved. ACKNOWLEDGEMENTS Claud Xiao from Palo Alto for sharing his samples with the research community
C O N F I D E N T I
A L 45 ©2016 KUDELSKI GROUP / All rights reserved.


 milkmix
 markunet
 shinichirokawano
 riyaamemiya
 emiki
 takuroabe
 eluwing
 sue445
 yukiogawa
 kakehashi
 bengo4com
 freee
 sansantech
 aki_iinuma
 notwaldorf
 gurzu
 wayneb77
 denniskardys
 holman
 akashhashmi
 panda_program
 tammielis
 erikaheidi
 aleyda
 stuffmc