Share
Embed
Clusis Campus 2015 : introduction to Suricata IDS
An introduction to Suricata IDS given during CLUSIS Campus 2015 in Geneva
Julien Bachmann
January 28, 2015
Transcript
34 slides
-
2 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION IDS
or IPS ? Intrusion Detection System Intrusion Prevention System Based on signatures Vulnerability centric -
3 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Vulnerability
centric Prevention and detection based Assume you know all possible threats Signature based detection Some behavioral approach but not so common No feedback Opposite to threat centric approach -
4 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Threat
centric Suppose prevention will fail… Based on attackers TTPs Tools, Tactics and Procedures Uses bad experiences as feedback to improve -
5 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Suricata
Open Source project Run by the Open Information Security Foundation Initiative by DHS in 2008… … but now supported by group of vendors -
6 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Also
an IPS NetFilter on Linux ipfw on BSD Mode Bridge -
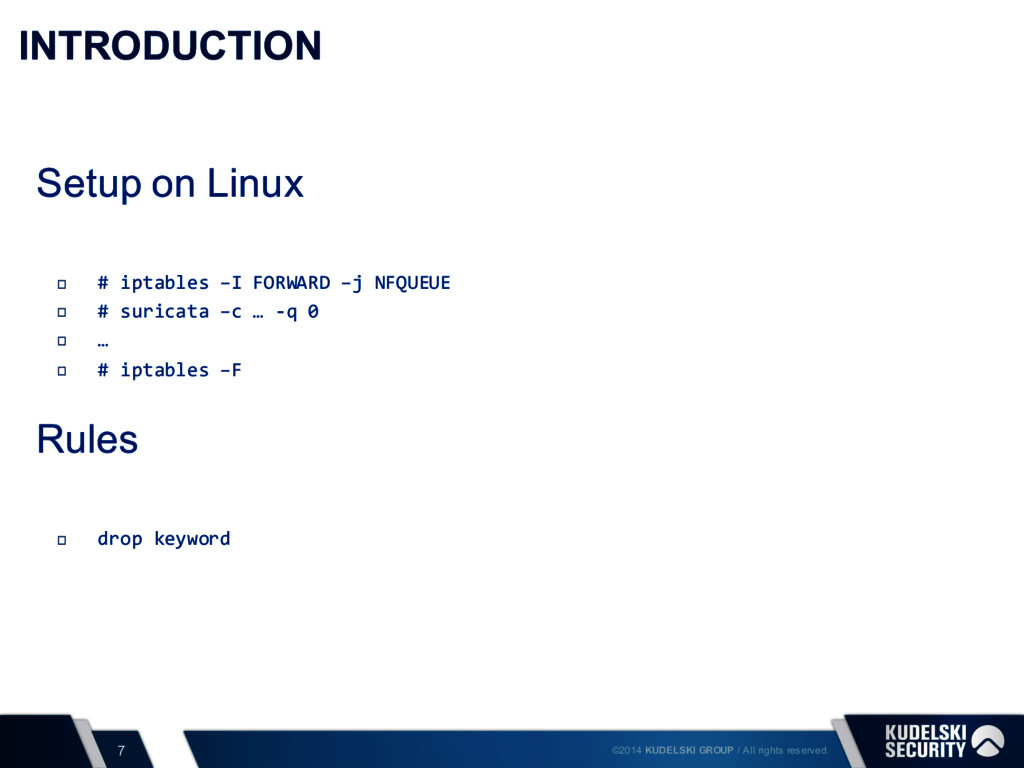
7 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Setup
on Linux # iptables –I FORWARD –j NFQUEUE # suricata –c … -q 0 … # iptables –F Rules drop keyword -
8 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Why
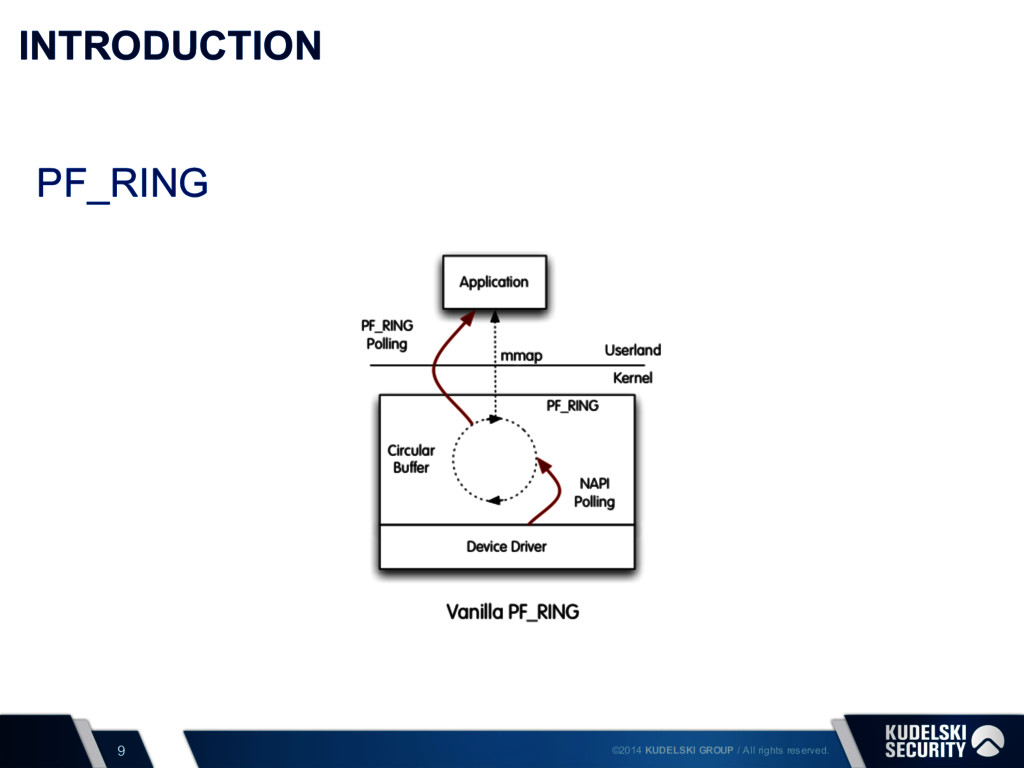
not SNORT ? Only solution for quite some time Which has an aging core (ok, v3 is out…) Support multi-threading Support for capture cards or PF_RING on commodity hardware 10Gb/s on Xeon with 8 cores GPU acceleration for regexp matching! who doesn’t have a GPU in their IDS nowadays? -
10 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Signatures
Support for SNORT ones except SO rules EmergingThreats Customs including LUA scripts for detection with some logic -
11 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Deployment
Packages or easily self-compiled Configuration suricata.yaml Rules management oinkmaster -
12 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION For
testing purposes The Security Onion Stamus Networks SELKS -
13 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Why
would I use this ? Complimentary to commercial solution Write your custom rules newly published vulnerability malware infection ongoing incident response capitalize on previous attacks Threat centric approach -
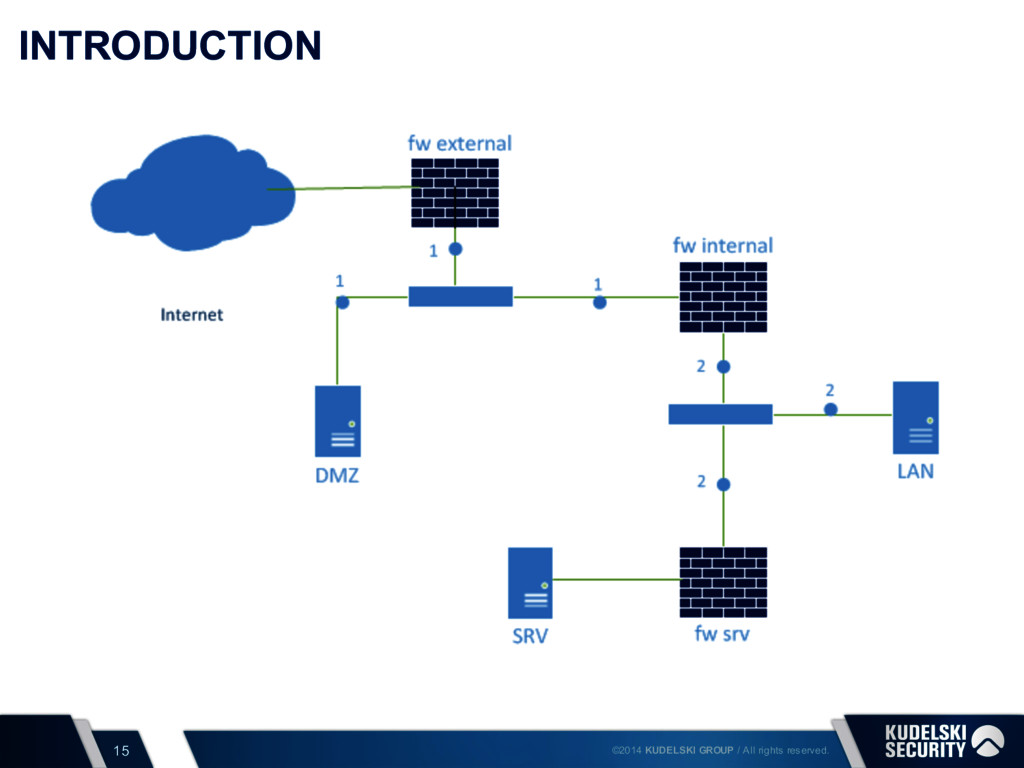
14 ©2014 KUDELSKI GROUP / All rights reserved. INTRODUCTION Deployment
strategies Important rule: Know your network Ingress / Egress points Internet access proxies VPN Partners Copy traffic using port mirroring -
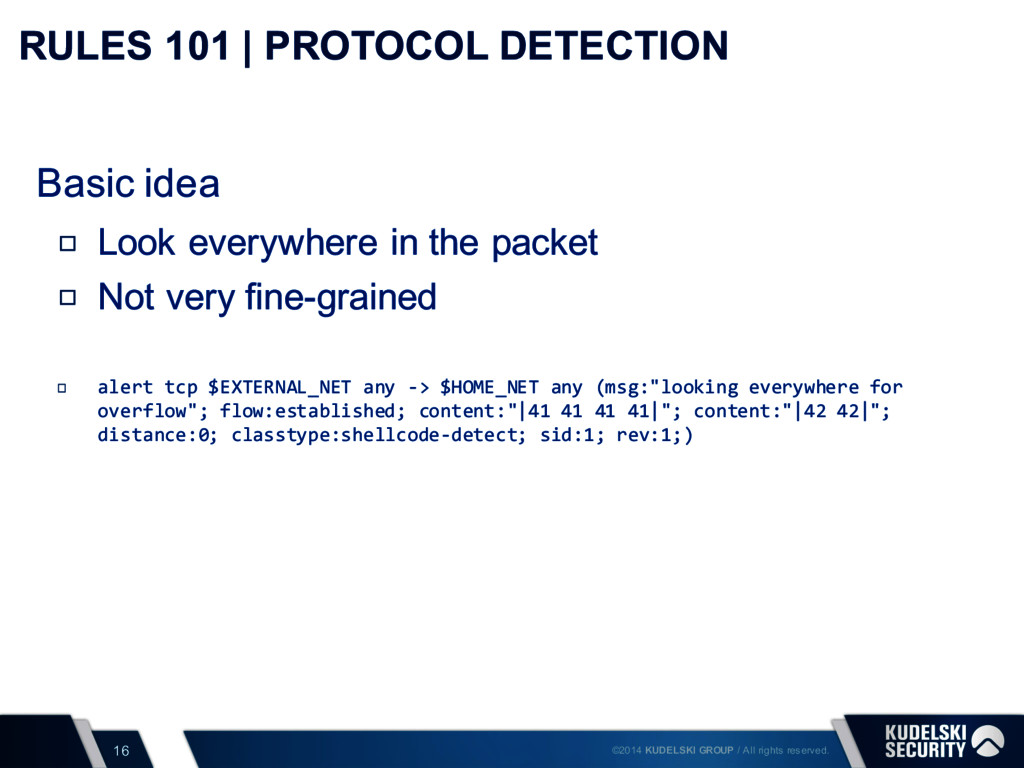
16 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
| PROTOCOL DETECTION Basic idea Look everywhere in the packet Not very fine-grained alert tcp $EXTERNAL_NET any -> $HOME_NET any (msg:"looking everywhere for overflow"; flow:established; content:"|41 41 41 41|"; content:"|42 42|"; distance:0; classtype:shellcode-detect; sid:1; rev:1;) -
17 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
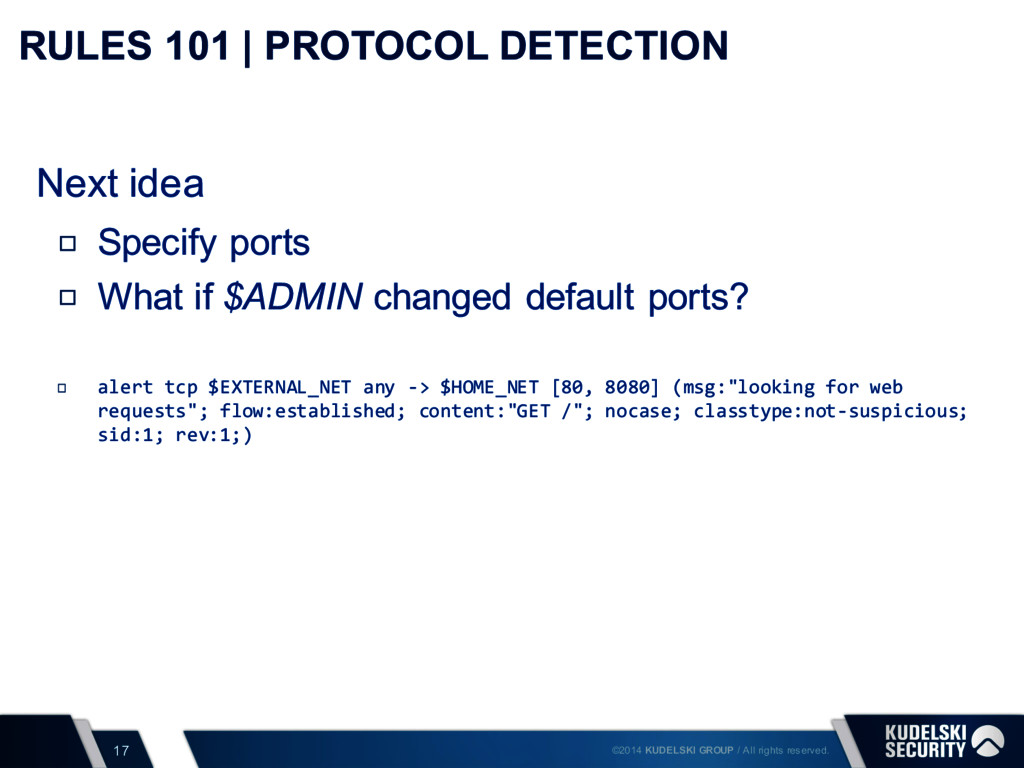
| PROTOCOL DETECTION Next idea Specify ports What if $ADMIN changed default ports? alert tcp $EXTERNAL_NET any -> $HOME_NET [80, 8080] (msg:"looking for web requests"; flow:established; content:"GET /"; nocase; classtype:not-suspicious; sid:1; rev:1;) -
18 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
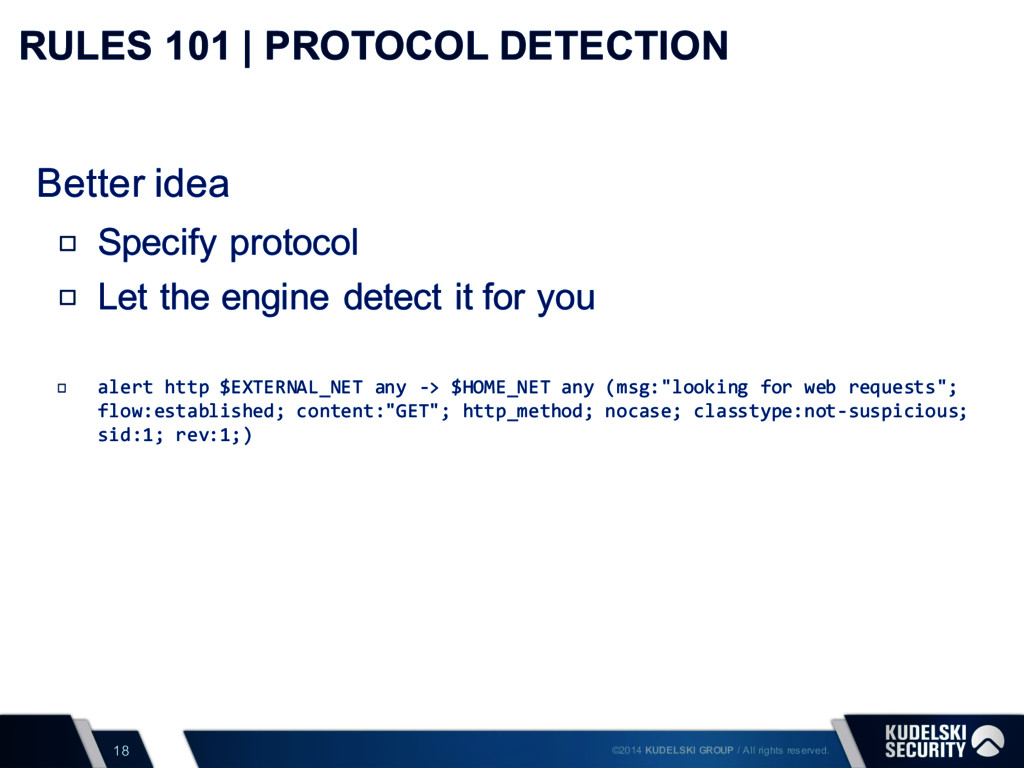
| PROTOCOL DETECTION Better idea Specify protocol Let the engine detect it for you alert http $EXTERNAL_NET any -> $HOME_NET any (msg:"looking for web requests"; flow:established; content:"GET"; http_method; nocase; classtype:not-suspicious; sid:1; rev:1;) -
19 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
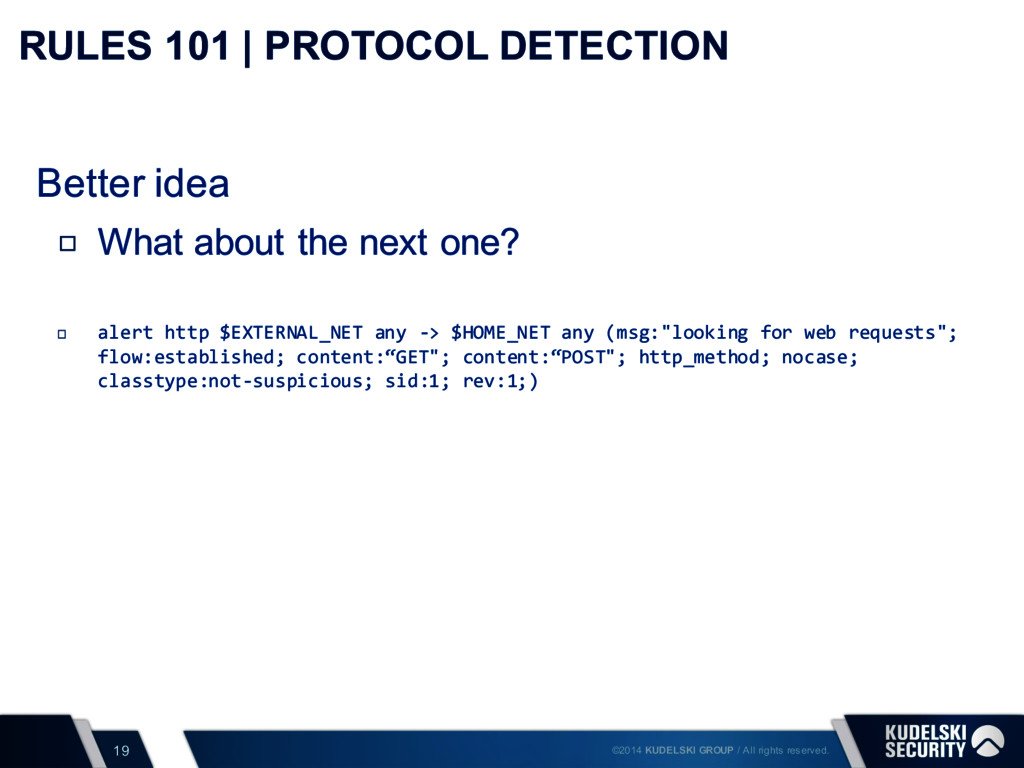
| PROTOCOL DETECTION Better idea What about the next one? alert http $EXTERNAL_NET any -> $HOME_NET any (msg:"looking for web requests"; flow:established; content:“GET"; content:“POST"; http_method; nocase; classtype:not-suspicious; sid:1; rev:1;) -
20 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
| DEMO Analyze malware communications Malware.pcap -
21 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
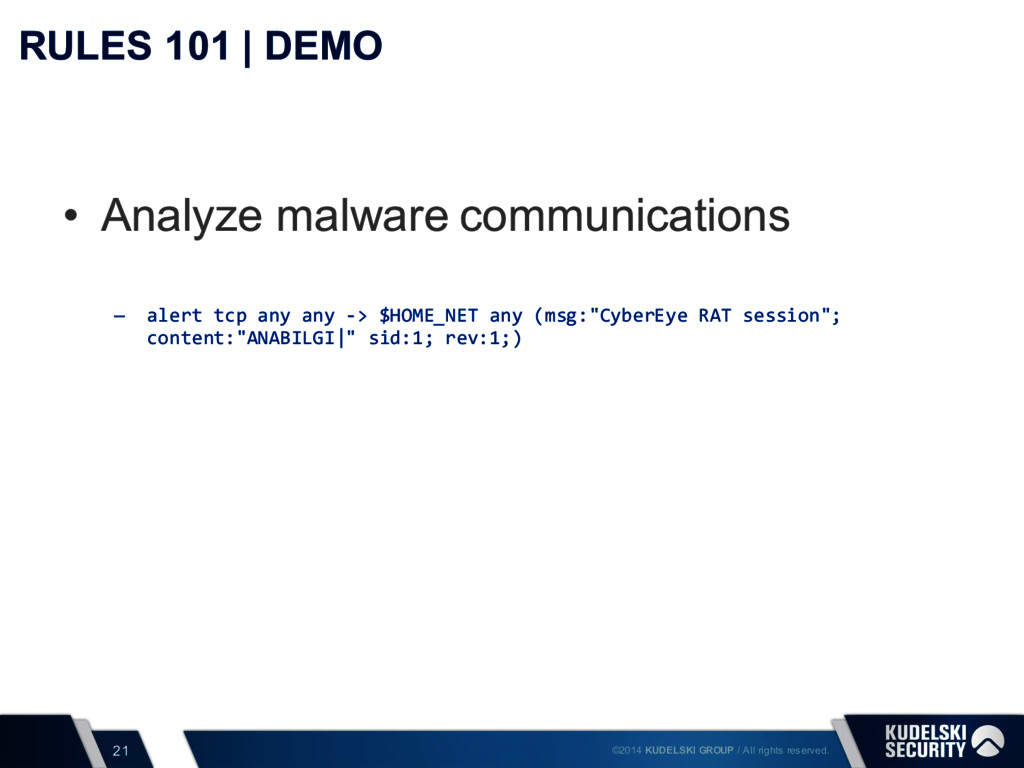
| DEMO • Analyze malware communications – alert tcp any any -> $HOME_NET any (msg:"CyberEye RAT session"; content:"ANABILGI|" sid:1; rev:1;) -
22 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
| PROTOCOL DETECTION Several implemented HTTP DNS SMB SSH FTP TLS Jabber … Allows to match specific fields -
23 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
| PROTOCOL DETECTION Wait, TLS and SSH? Isn’t it encrypted? Not so fast, no TLS decryption on the fly Mainly allows to extract information Fingerprint IssuerDN … -
24 ©2014 KUDELSKI GROUP / All rights reserved. RULES 101
| PROTOCOL DETECTION Use case Remember Comodo story? Log proactively -
25 ©2014 KUDELSKI GROUP / All rights reserved. RULES ADVANCED
| FILES No need to dig the PCAPs manually Possible to extract files matching rules Enable file-store in suricata.yaml -
26 ©2014 KUDELSKI GROUP / All rights reserved. RULES ADVANCED
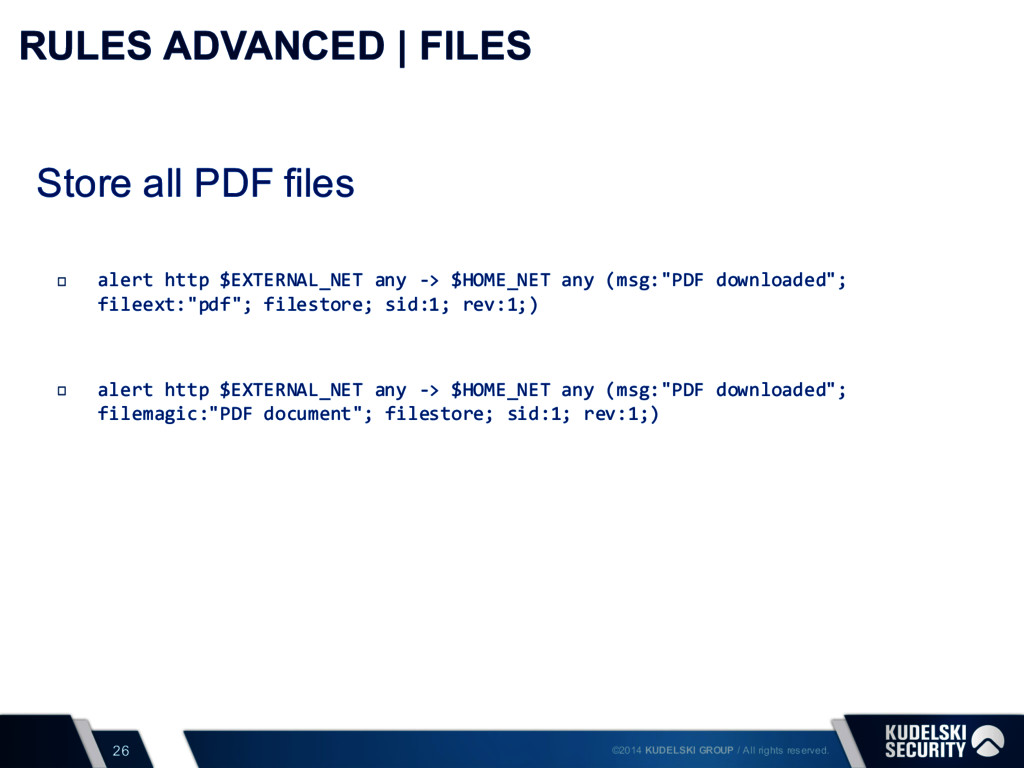
| FILES Store all PDF files alert http $EXTERNAL_NET any -> $HOME_NET any (msg:"PDF downloaded"; fileext:"pdf"; filestore; sid:1; rev:1;) alert http $EXTERNAL_NET any -> $HOME_NET any (msg:"PDF downloaded"; filemagic:"PDF document"; filestore; sid:1; rev:1;) -
27 ©2014 KUDELSKI GROUP / All rights reserved. RULES ADVANCED
| FILES Detect suspicious files upload alert http $EXTERNAL_NET any -> $DMZ any (msg:"possible webshell upload attempt"; fileext:"png"; filemagic:!"PNG"; filestore; sid:1; rev:1;) -
28 ©2014 KUDELSKI GROUP / All rights reserved. RULES ADVANCED
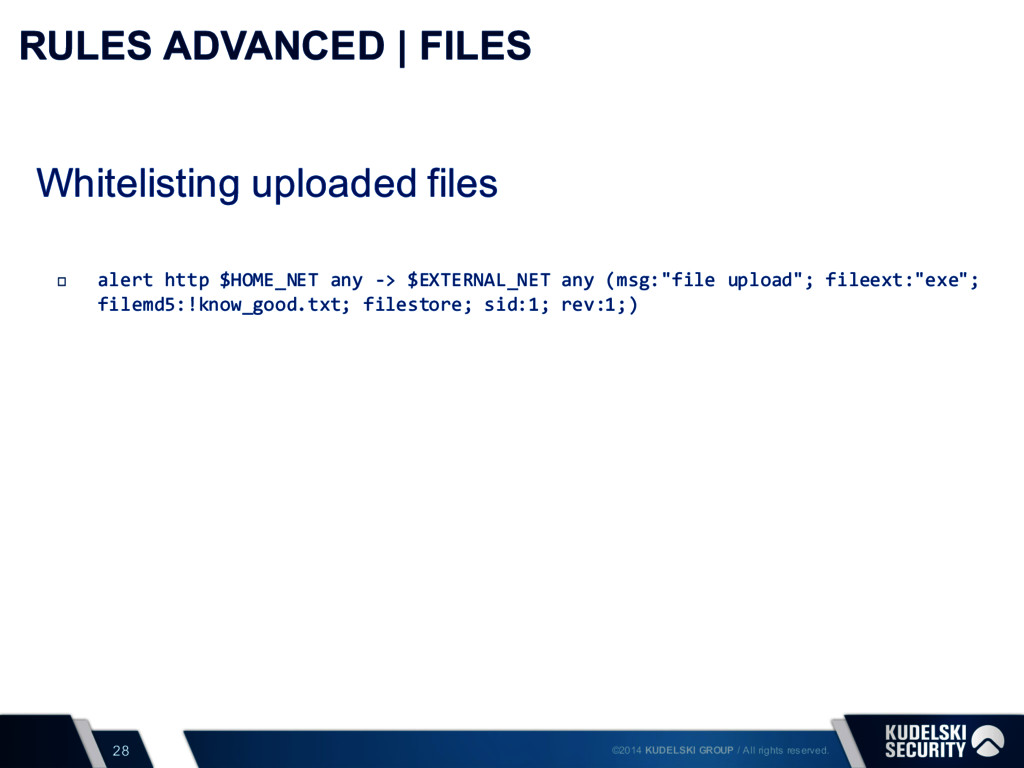
| FILES Whitelisting uploaded files alert http $HOME_NET any -> $EXTERNAL_NET any (msg:"file upload"; fileext:"exe"; filemd5:!know_good.txt; filestore; sid:1; rev:1;) -
29 ©2014 KUDELSKI GROUP / All rights reserved. MONITORING |
TOOLS How do I review the events? syslog: not that practical Graphical tools $COMMERCIAL_PRODUCT Snorby OSSIM Sguil ELK -
30 ©2014 KUDELSKI GROUP / All rights reserved. MONITORING |
ELK ElasticSearch Logstash Kibana Not really in that order Logstash : read logs and forward and/or transform ElasticSearch : indexed storage Kibana : web interface to ES -
31 ©2014 KUDELSKI GROUP / All rights reserved. MONITORING |
ELK Configuration in Suricata 1. Enable EVE output 2. Configure Logstash to read from EVE file 3. Profit -
32 ©2014 KUDELSKI GROUP / All rights reserved. MONITORING |
DEMO SELK Using Stamus Network SELK -
33 ©2014 KUDELSKI GROUP / All rights reserved. CONCLUSION |
FINAL WORDS Things I did not discuss Sensor hardening LUA scripting engine Rules sets comparison -
34 ©2014 KUDELSKI GROUP / All rights reserved. CONCLUSION |
FINAL WORDS Things to keep in mind There are alternative to commercial tools Preconfigured distributions Incident response can benefit custom rules ELK stack becoming more and more used in DFIR