Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
駭客看 Django
Search
Orange
May 26, 2013
Technology
13k
25
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
駭客看 Django
Taiwan Python Conference 2013
Orange
May 26, 2013
More Decks by Orange
See All by Orange
Best Practices - The Upload
p8361
0
650
Security in PHP 那些在滲透測試的小技巧
p8361
0
780
網頁安全 Web Security 入門
p8361
0
850
Bug Bounty 獎金獵人甘苦談 - 那些年我回報過的漏洞
p8361
13
38k
那些 Web Hacking 中的奇技淫巧
p8361
16
15k
關於 HITCON CTF 的那些事 之 Web 狗如何在險惡的 CTF 世界中存活?
p8361
6
14k
PHPConf 2013 - 矛盾大對決
p8361
53
29k
0-Day 輕鬆談 - Happy Fuzzing Internet Explorer
p8361
15
13k
Other Decks in Technology
See All in Technology
AI時代のPRレビューにどう向き合うか?
kairim0
1
250
Code for Security プロジェクト紹介 2026年10月
yu23ki14
0
110
SAENM ~Jupyterで残すPoCの試行錯誤、未来の自分と仲間を助ける記録!~
terapyon
0
150
Webの常識が通じないHTMLメールのダークモード
teamlab
PRO
0
140
初海外で注意すべきこと12選!!!安全快適なre:invent生活にするために
yuuuuuuu168
1
180
PagerDuty Tech Hub-鳴らすけれど、人は動かない
ezaki
0
180
CloudWatch Logsのコスト最適化:どこまでAIに任せてどこから人間が承認すべきか
yama3133
0
120
Post AI時代のリファクタリング実践記 / Refactoring in the post AI era
kaminashi
1
300
LLM-as-a-Judgeは本当に信頼できるのか――評価器を評価する話
taka_aki
1
490
二歩目のフロントエンド・ウェブアクセシビリティ
camiha
2
690
V8のArray.prototype.flatを最大約20倍速くするまでと、巨大OSSへの大規模コミットの道のり
riyaamemiya
0
310
Running Kotlin + Quarkus with Lambda
nealle
1
4k
Featured
See All Featured
Fireside Chat
paigeccino
43
4.1k
Designing for Performance
lara
612
70k
Testing 201, or: Great Expectations
jmmastey
46
8.3k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Mobile First: as difficult as doing things right
swwweet
225
10k
Leveraging Curiosity to Care for An Aging Population
cassininazir
1
540
Building a A Zero-Code AI SEO Workflow
portentint
PRO
0
790
Darren the Foodie - Storyboard
khoart
PRO
4
4k
JAMstack: Web Apps at Ludicrous Speed - All Things Open 2022
reverentgeek
1
640
It's Worth the Effort
3n
188
29k
How to Grow Your eCommerce with AI & Automation
katarinadahlin
PRO
2
330
Money Talks: Using Revenue to Get Sh*t Done
nikkihalliwell
0
520
Transcript
駭客看 DJANGO 2013/05/26 @ PyCon <
[email protected]
>
本場演講「四不一沒有」
四不一沒有 • 四不 – 我不是駭客 – 我不會寫 django – 不會有 django 新漏洞( 請洽七月台灣駭客年會
) – 這場演講不難,真的很簡單 • 沒有 – 這場演講沒有梗,有笑點的話拜託笑一下
About Me • 蔡政達 aka Orange • 2009 台灣駭客年會競賽 冠軍
• 2011, 2012 全國資安競賽 金盾獎冠軍 • 2011 東京 AVTOKYO 講師 • 2012 香港 VXRLConf 講師 • 台灣 PHPConf, WebConf 講 師 • 專精於 – 駭客攻擊手法 – Web Security – Windows Vulnerability Exploitation
About Me • CHROOT Security Group 成員 • NISRA 資訊安全研究會
成員 • Disclosed – Windows MS12-071(CVE-2012-4775) – Django (CVE-2013-0305) • Blog – http://blog.orange.tw/
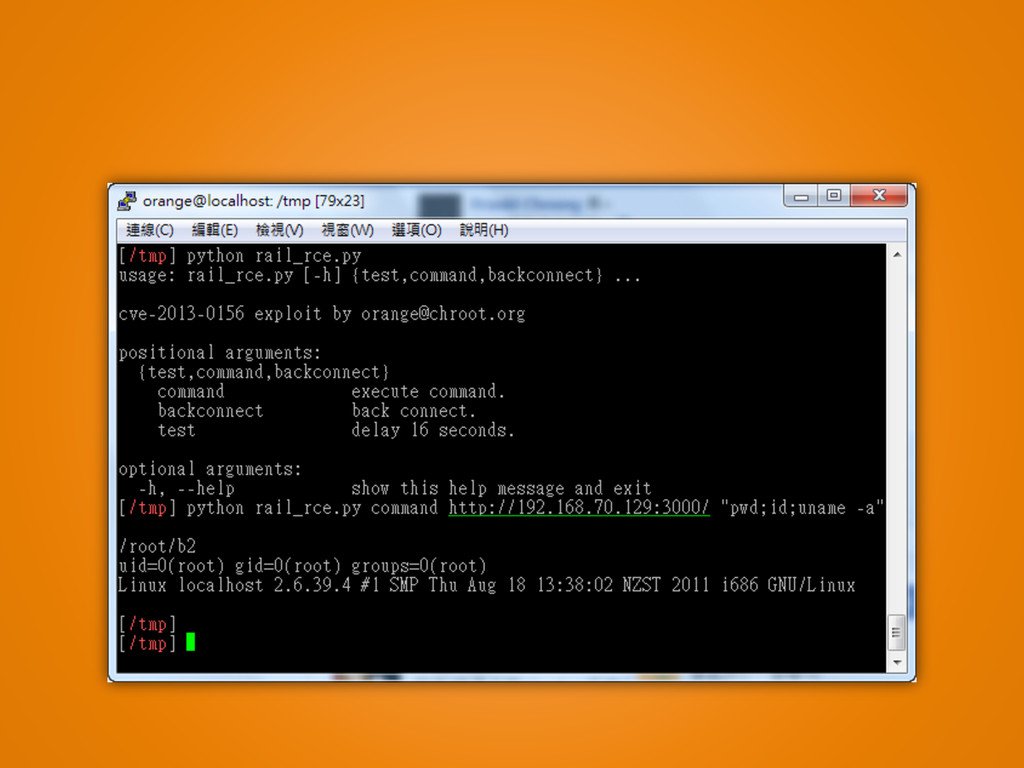
2013 年 X 月 O 日 天氣晴,今天是寒假的第一天… 幹, Rails 爆遠端執行代碼漏洞欸
None
Django 會不會有同樣的問題呢? 學生什麼都沒有, 最多的就是時間。 來研究個 Open Source 專案很正常吧!
Vulnerabilities by Year Django
Vulnerabilities by Year Django 同樣情境跟 Rails 比較...
包含至少 8 個 Remote Code Execution
......
其實我今天是來推廣 Rails 開玩笑的啦我沒有要戰語言 T_T
Django 現有的保護機制 Django Security Overview
Security Overview • Built-in XSS protection • Built-in SQL Injection
protection – ORM ( Q Object ) • Built-in CSRF protection – django.middleware.csrf.CsrfViewMiddleware – Check REFERER header – Compare CSRF token
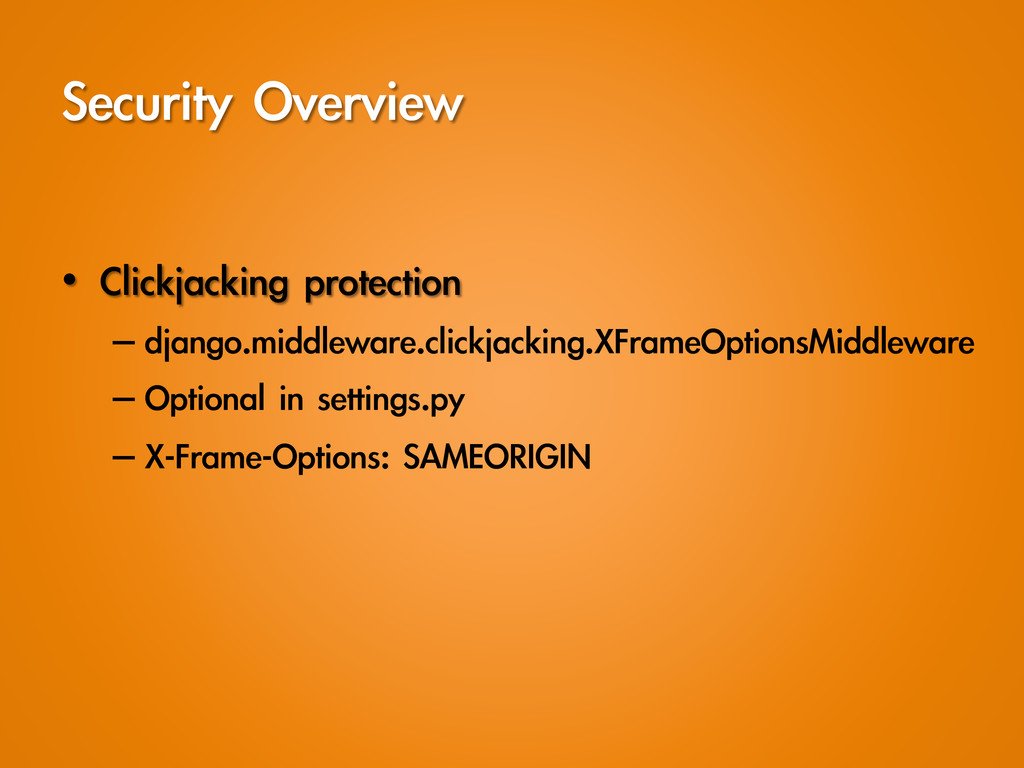
Security Overview • Clickjacking protection – django.middleware.clickjacking.XFrameOptionsMiddleware – Optional in settings.py – X-Frame-Options:
SAMEORIGIN
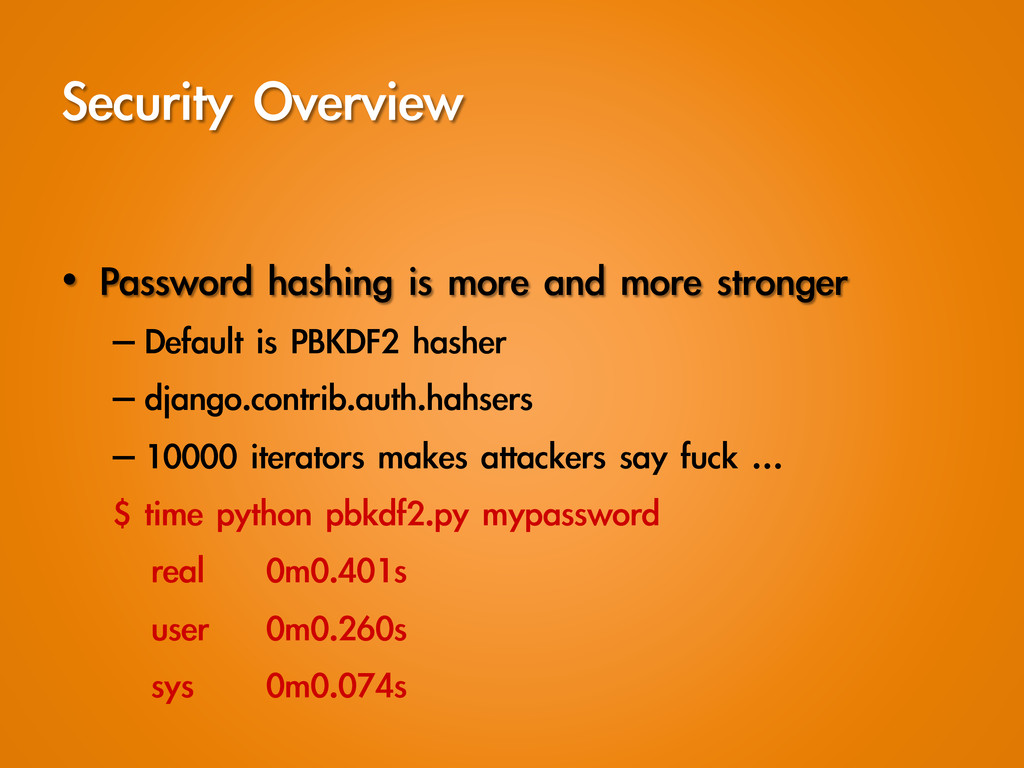
Security Overview • Password hashing is more and more stronger
– Default is PBKDF2 hasher – django.contrib.auth.hahsers – 10000 iterators makes attackers say fuck … $ time python pbkdf2.py mypassword real 0m0.401s user 0m0.260s sys 0m0.074s
攻擊手法 Some Attacking Vectors
Some Attacking Vectors • VERY VERY BASIC attacking way •
Weak admin password • Debug mode on – Leakage URL pattern – Leakage database password
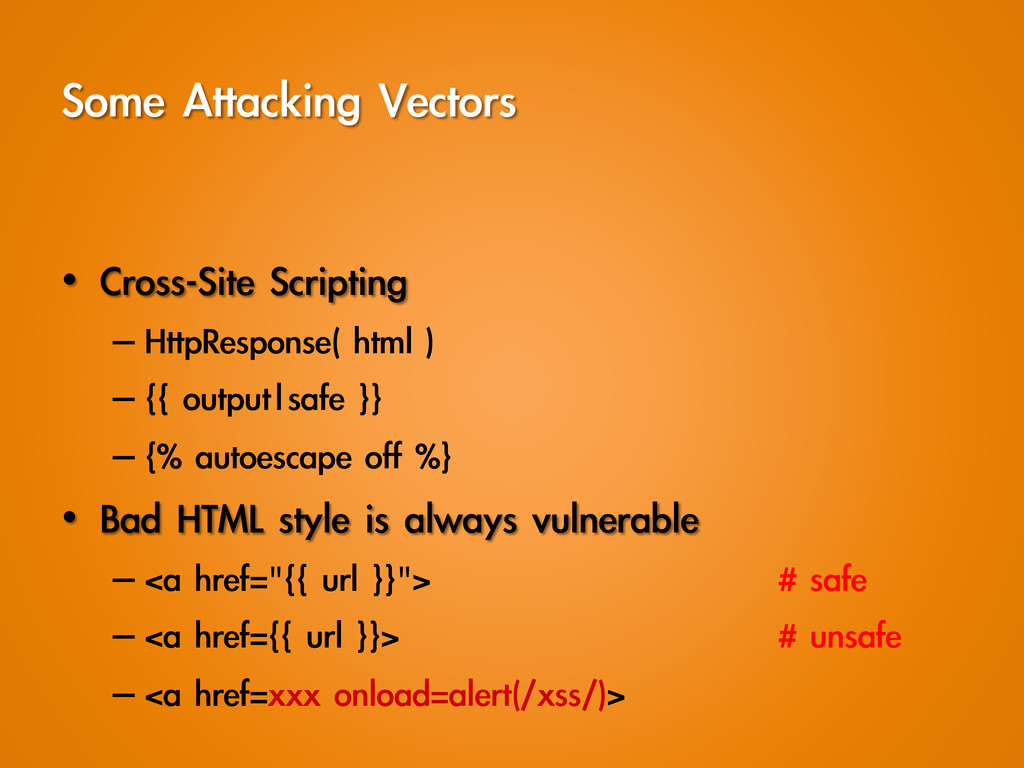
Some Attacking Vectors • Cross-Site Scripting – HttpResponse( html ) – {{
output|safe }} – {% autoescape off %} • Bad HTML style is always vulnerable – <a href="{{ url }}"> # safe – <a href={{ url }}> # unsafe – <a href=xxx onload=alert(/xss/)>
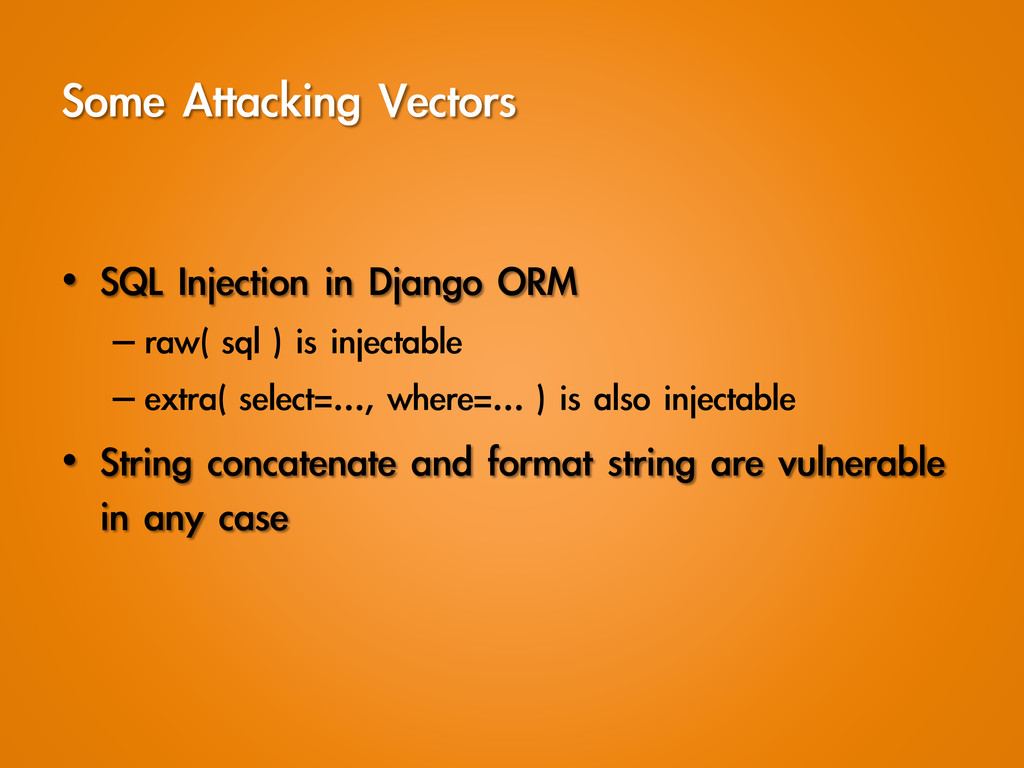
Some Attacking Vectors • SQL Injection in Django ORM – raw(
sql ) is injectable – extra( select=…, where=… ) is also injectable • String concatenate and format string are vulnerable in any case
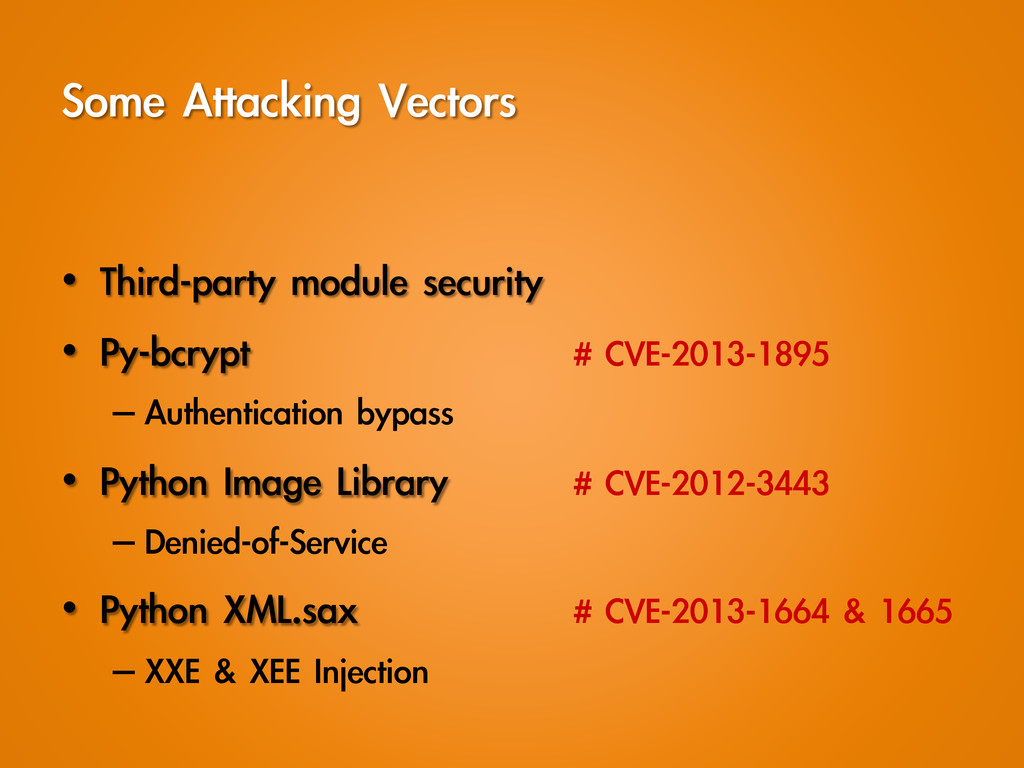
Some Attacking Vectors • Third-party module security • Py-bcrypt #
CVE-2013-1895 – Authentication bypass • Python Image Library # CVE-2012-3443 – Denied-of-Service • Python XML.sax # CVE-2013-1664 & 1665 – XXE & XEE Injection
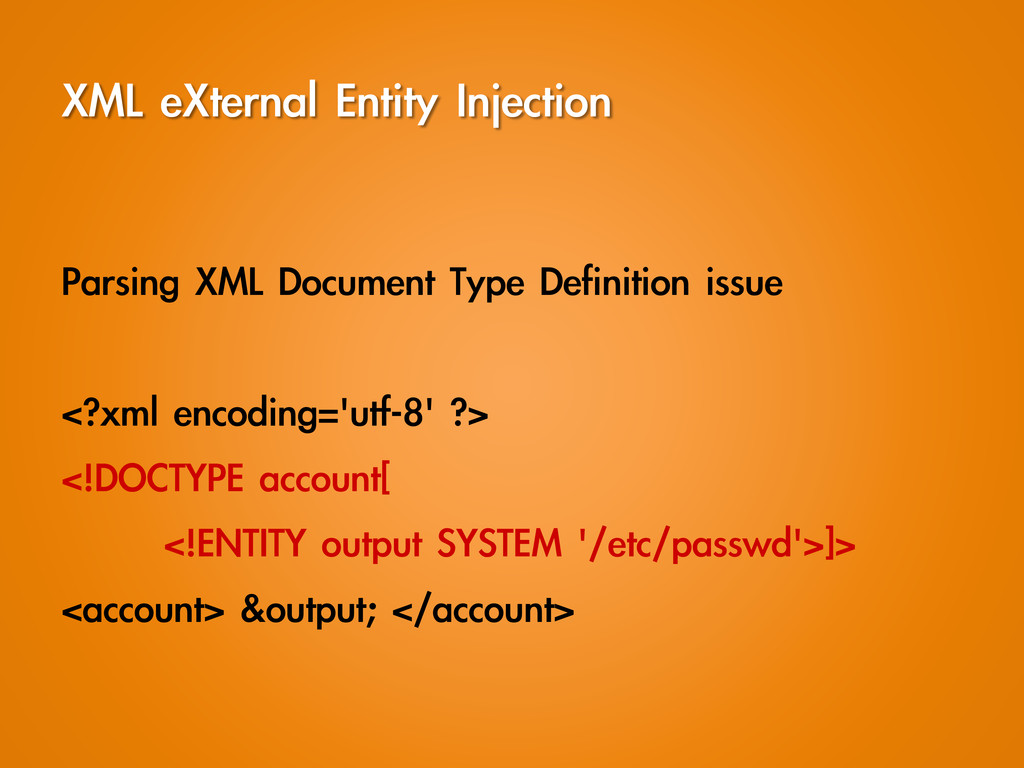
XML eXternal Entity Injection Parsing XML Document Type Definition issue
<?xml encoding='utf-8' ?> <!DOCTYPE account[ <!ENTITY output SYSTEM '/etc/passwd'>]> <account> &output; </account>
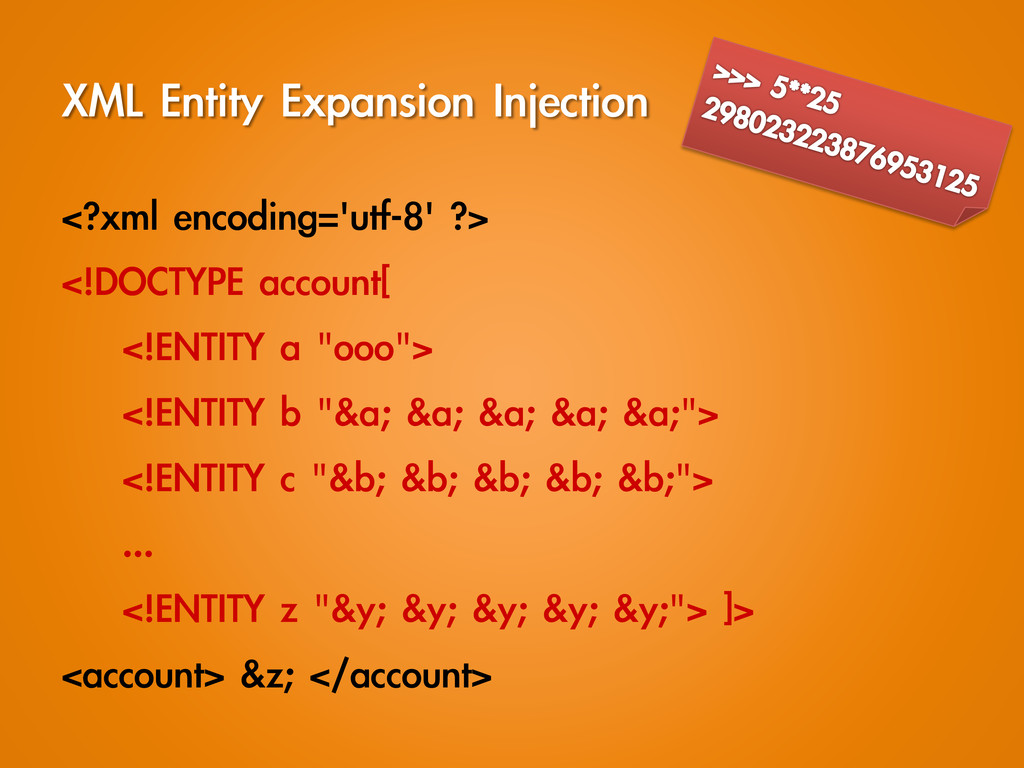
XML Entity Expansion Injection <?xml encoding='utf-8' ?> <!DOCTYPE account[ <!ENTITY
a "ooo"> <!ENTITY b "&a; &a; &a; &a; &a;"> <!ENTITY c "&b; &b; &b; &b; &b;"> ... <!ENTITY z "&y; &y; &y; &y; &y;"> ]> <account> &z; </account>
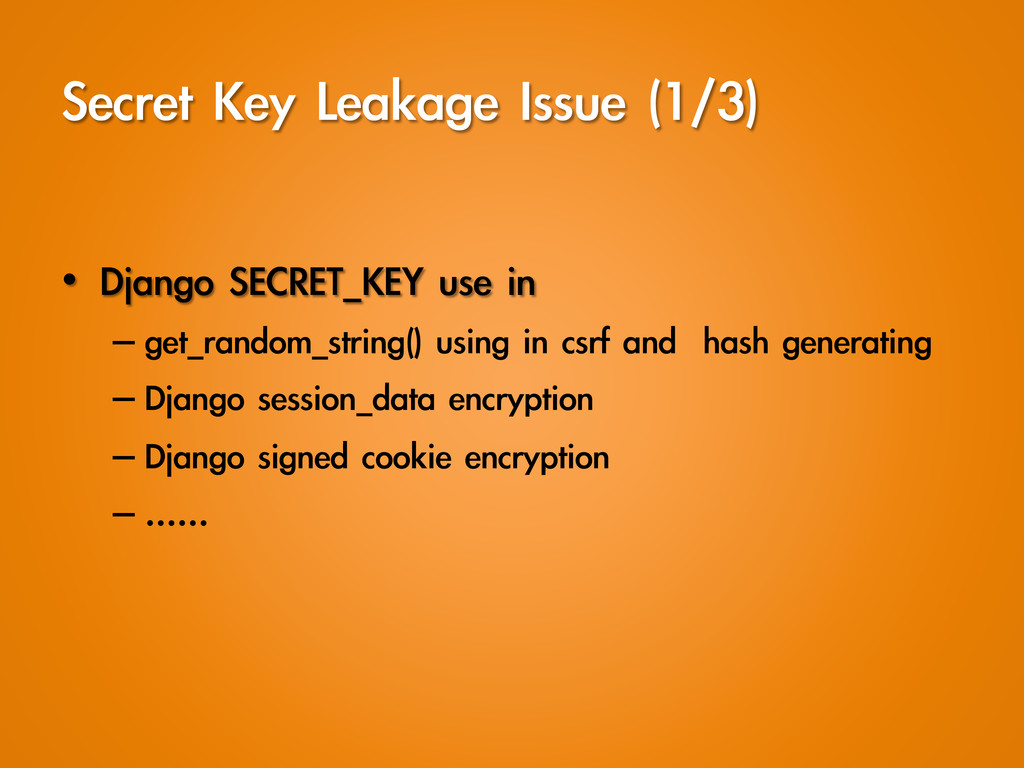
Secret Key Leakage Issue (1/3) • Django SECRET_KEY use in
– get_random_string() using in csrf and hash generating – Django session_data encryption – Django signed cookie encryption – ……
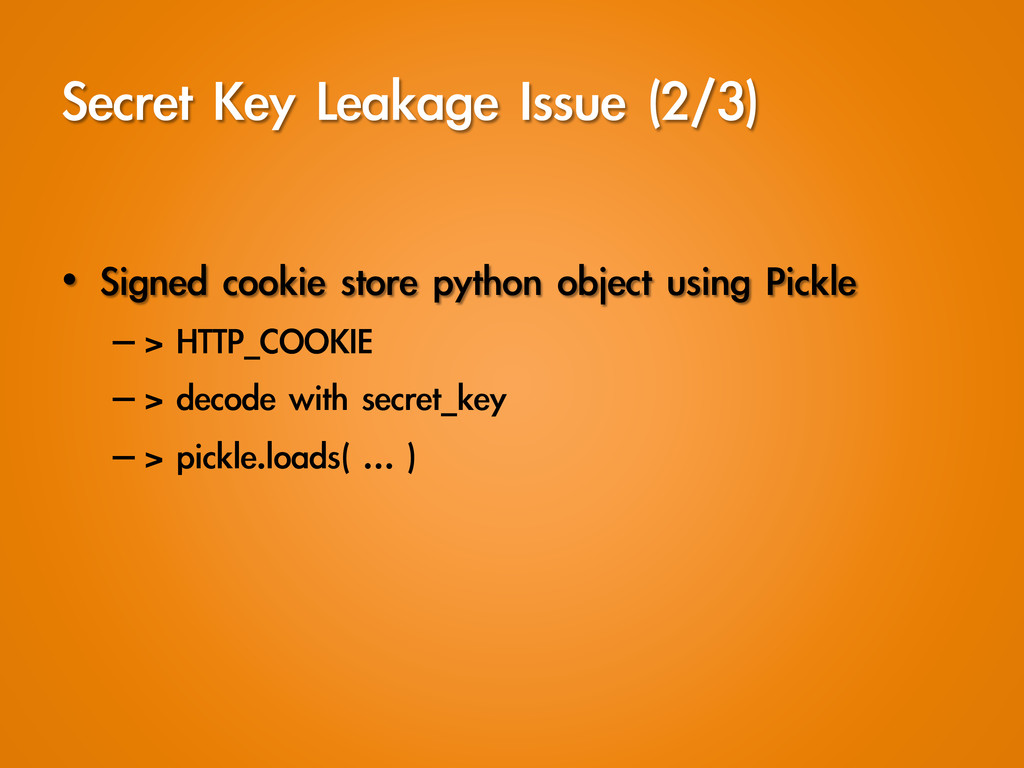
Secret Key Leakage Issue (2/3) • Signed cookie store python
object using Pickle – > HTTP_COOKIE – > decode with secret_key – > pickle.loads( … )
Pickle & cPickle • A module that serializing and De-serializing
python objects • Execute command >>> import pickle >>> pickle.loads( "cos\nsystem\n(S'/bin/sh'\ntR." ) • You can observe by using pickletools >>> import pickletools >>> pickletools.dis( "cos\nsystem\n(S'/bin/sh'\ntR." )
Secret Key Leakage Issue (3/3) • Signed_cookie is encoded by
Pickle – > HTTP_COOKIE # malicious cookie – > decode with secret_key – > pickle.loads( … ) # code execution • Protect your SECRET_KEY ( ex .gitignore )
Conclusion • I think Django is a secure framework •
More and more wrapper make the attack difficult • People is always the most dangerous things
Reference • Django Weblog – https://www.djangoproject.com/weblog/ • Security in Django – https://docs.djangoproject.com/en/dev/topics/security/
• CVE Details – http://www.cvedetails.com/
Any Questions ? Whatever can be asked
Thanks. <
[email protected]
>


 p8361
 kairim0
 yu23ki14
 terapyon
 teamlab
 yuuuuuuu168
 ezaki
 yama3133
 kaminashi
 taka_aki
 camiha
 riyaamemiya
 nealle
 paigeccino
 lara
 jmmastey
 aki_iinuma
 swwweet
 cassininazir
 portentint
 khoart
 reverentgeek
 3n
 katarinadahlin
 nikkihalliwell