Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
SECCON Beginners CTF2021のCryptoを解いてみよう
Search
ushigai
October 17, 2021
Technology
1.1k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
SECCON Beginners CTF2021のCryptoを解いてみよう
ushigai
October 17, 2021
More Decks by ushigai
See All by ushigai
暗号目線で俯瞰するSSL/TLS / security minicamp in Tokyo 2022 TLS
ushigai
0
740
Crypto超入門 / SECCON Beginners Live 2022
ushigai
2
1.9k
Other Decks in Technology
See All in Technology
Azure Copilot Resiliency Agentをいろいろ試してみる
tomokusaba
0
140
生成AIを使って「人が」考える技術 ― AI時代の人機共想と実践ノウハウ|UNITT AC2026
ishiirikie
0
450
AIに会社の文脈を理解させる技術~上流工程・非エンジニアにも広げるハーネスエンジニアリング実践~
ochtum
0
190
Claude Designがめちゃくちゃ便利なので使ってほしい
diggymo
0
160
AWS FinOps Agent 結局何が得意なの?
siromi
0
220
Lambda MicroVMsが分からなすぎたので使い所を1から考えてみた
tsukuboshi
1
260
AI駆動開発で仕様はどこまで書くべきか? ― 人とAIの責務境界から考える開発プロセスの実践
takahiromatsui
1
240
LT:「このままでいいのかな?」から一歩踏み出した私のデータキャリア選択〜社会人3年目に上京を決意したリアル〜Snowflake女子会 vol.8
snowwmn0824
0
120
spanner-autoscalerに学ぶ CRD設計パターン 〜自動化と緊急時対応を両立する Kubernetesコントローラーの作り方〜
tkuchiki
0
210
【ゲームメーカーズスクランブル2026】『Shadowverse: Worlds Beyond』UIとアニメーションで実現する最高のユーザー体験を叶えるプロトタイピング
cygames
PRO
1
700
認知負荷を吸収し、プロダクトをまたぐPR Preview基盤の設計事例
taiki45
2
550
Amazon Bedrock Agents ClassicからAmazon Bedrock AgentCoreへ移行した際、ガードレール設定が2箇所に割れた話
matsunobu
0
160
Featured
See All Featured
Imperfection Machines: The Place of Print at Facebook
scottboms
270
14k
Designing for Performance
lara
611
70k
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
710
Design of three-dimensional binary manipulators for pick-and-place task avoiding obstacles (IECON2024)
konakalab
0
600
世界の人気アプリ100個を分析して見えたペイウォール設計の心得
akihiro_kokubo
PRO
74
42k
Building Experiences: Design Systems, User Experience, and Full Site Editing
marktimemedia
1
610
Templates, Plugins, & Blocks: Oh My! Creating the theme that thinks of everything
marktimemedia
31
2.9k
Design in an AI World
tapps
1
340
KATA
mclloyd
PRO
35
16k
Collaborative Software Design: How to facilitate domain modelling decisions
baasie
1
330
RailsConf & Balkan Ruby 2019: The Past, Present, and Future of Rails at GitHub
eileencodes
141
35k
Mobile First: as difficult as doing things right
swwweet
225
10k
Transcript
SECCON Beginners CTF 2021の Cryptoを解いてみよう SECCON Beginners Live 2021 2021/10/17
自己紹介 • うしがぃ@ushigai_sub • 所属 • 都立産業技術高等専門学校(4年) • SECCON Beginners
運営チーム • 趣味 • ピアノ:小6から7年間 • ルービックキューブ3×3:1/5/100=13.89/18.88/23.19 • 将棋:アマ二段 1/24
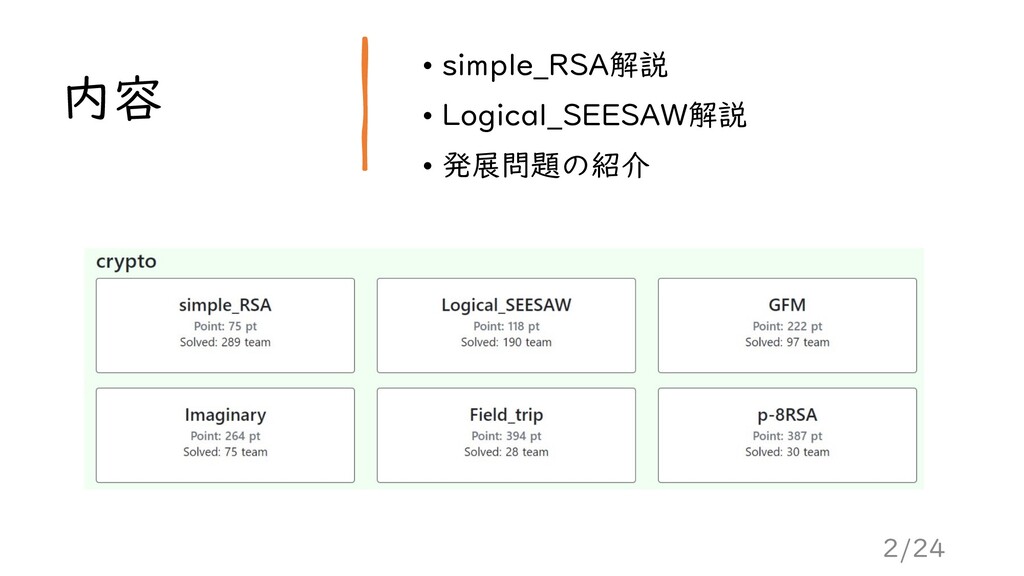
内容 • simple_RSA解説 • Logical_SEESAW解説 • 発展問題の紹介 2/24
お話の対象層 3/25 Beginner Easy Medium Hard • 過去問解説はBeginner向け • 発展問題はEasy向け
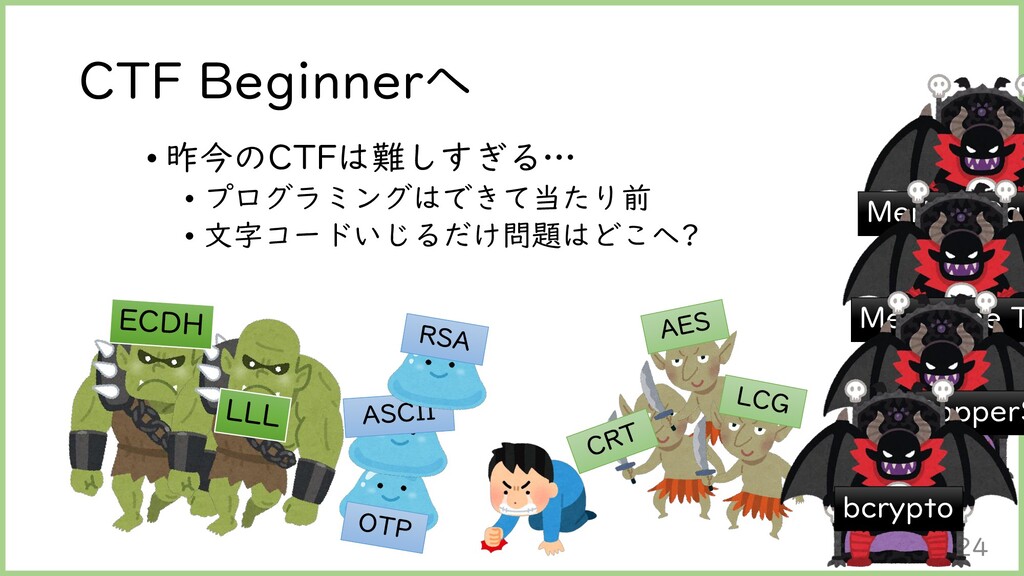
CTF Beginnerへ 4/24 • 昨今のCTFは難しすぎる… • プログラミングはできて当たり前 • 文字コードいじるだけ問題はどこへ? Merkle-Dam
Mersenne T CopperS bcrypto
CTF Beginnerへ • 勉強方法(主観) • 本・常設での勉強 • 迷路本 • picoCTF
• 分からないことがあったら? • 誰かに聞く • おいしいものを食べる 5/24
simple_RSA解説 •simple_RSA • 難易度Beginner • 75points/289solves •RSA暗号の自明な脆弱性を攻撃する問題 → Low public
exponent attack 6/24
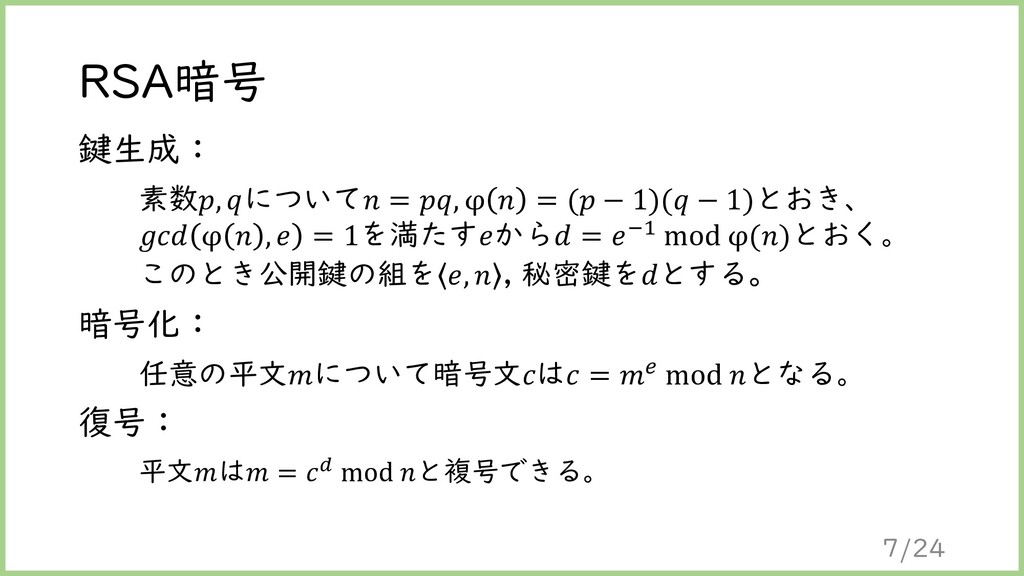
RSA暗号 鍵生成: 素数𝑝, 𝑞について𝑛 = 𝑝𝑞, φ 𝑛 = (𝑝
− 1)(𝑞 − 1)とおき、 𝑔𝑐𝑑 φ 𝑛 , 𝑒 = 1を満たす𝑒から𝑑 = 𝑒−1 mod φ(𝑛)とおく。 このとき公開鍵の組を 𝑒, 𝑛 , 秘密鍵を𝑑とする。 暗号化: 任意の平文𝑚について暗号文𝑐は𝑐 = 𝑚𝑒 mod 𝑛となる。 復号: 平文𝑚は𝑚 = 𝑐𝑑 mod 𝑛と複号できる。 7/24
CTFにおけるRSA暗号 • Beginner • 暗号化・復号の計算方法 • factorDB等ツールの使用 • RSA暗号の典型的な脆弱性の攻撃 •
Easy ~ Medium • 簡単な代数方程式の計算 • 鍵共有・署名 • Hard ~ • CopperSmiths Method • 数学力でぶん殴る • etc… 8/24
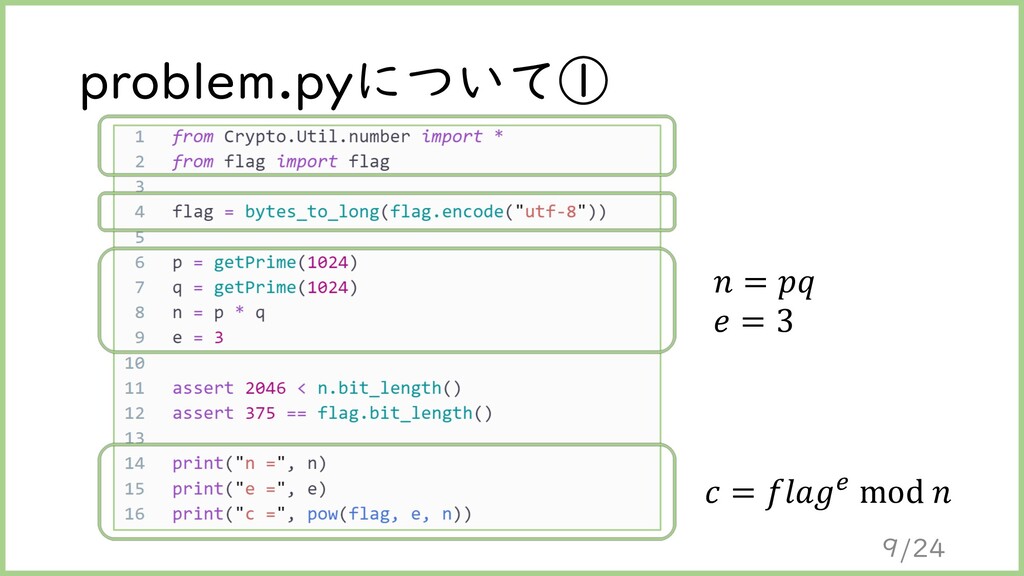
problem.pyについて① 𝑛 = 𝑝𝑞 𝑒 = 3 𝑐 = 𝑓𝑙𝑎𝑔𝑒
mod 𝑛 9/24
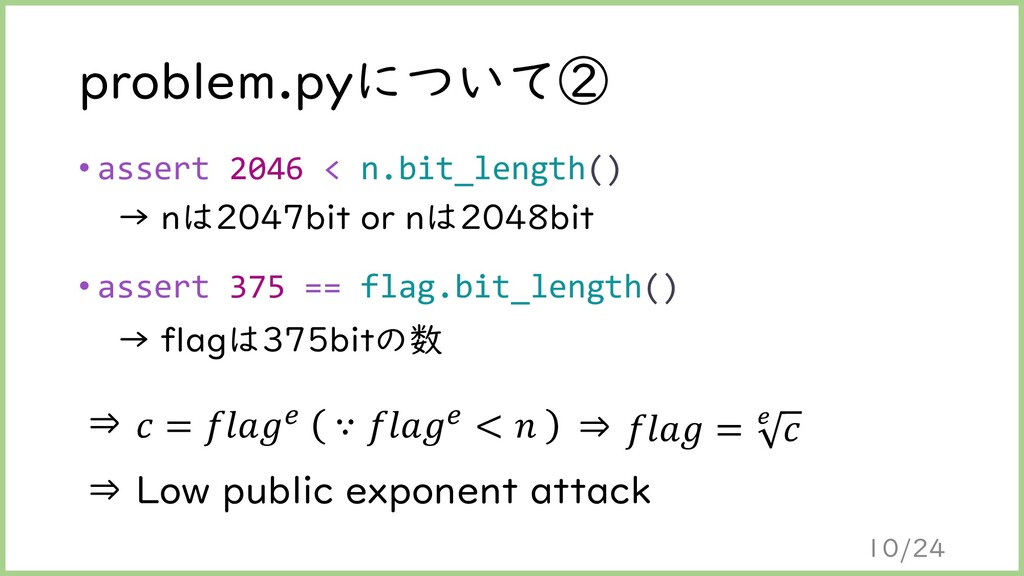
problem.pyについて② • assert 2046 < n.bit_length() → nは2047bit or nは2048bit
• assert 375 == flag.bit_length() → flagは375bitの数 ⇒ 𝑐 = 𝑓𝑙𝑎𝑔𝑒 ∵ 𝑓𝑙𝑎𝑔𝑒 < 𝑛 ⇒ Low public exponent attack 10/24 ⇒ 𝑓𝑙𝑎𝑔 = 𝑒 𝑐
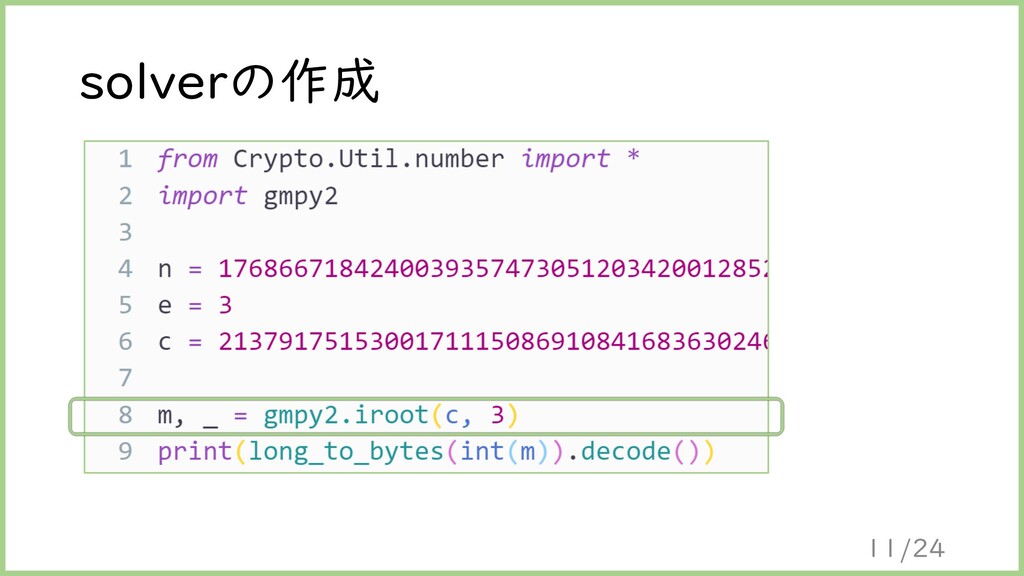
solverの作成 11/24
Logical_SEESAW解説 • Logical_SEESAW • 難易度Beginner • 118points/190solves • パズル問(自作暗号) •
論理演算・コーディング 12/24
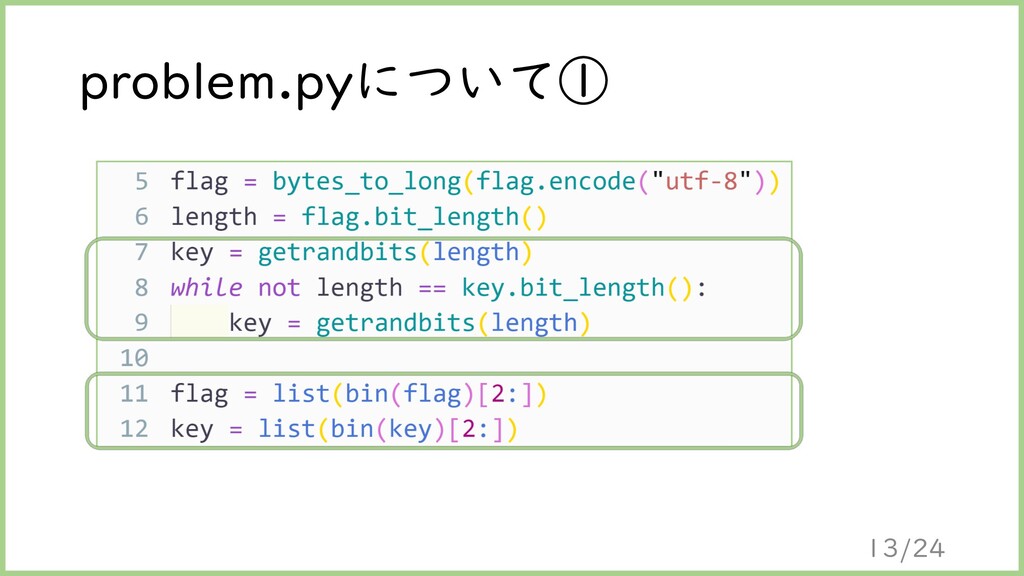
problem.pyについて① 13/24
problem.pyについて② flagの各bitに対して適用確立0.5で flagとkeyのAND演算を行っている 14/24
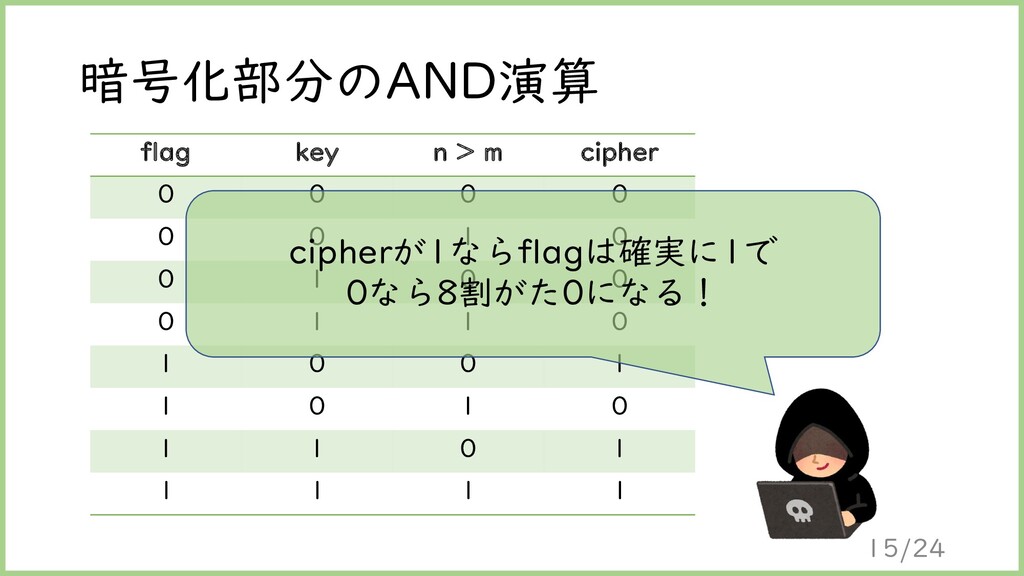
暗号化部分のAND演算 flag key n > m cipher 0 0 0
0 0 0 1 0 0 1 0 0 0 1 1 0 1 0 0 1 1 0 1 0 1 1 0 1 1 1 1 1 cipherが1ならflagは確実に1で 0なら8割がた0になる! 15/24
攻撃 • cipherが1ならflagは確実に1 • cipherが0ならflagは8割方0 ⇒ 各bitに対して1個でも1が含まれていれば1で 全部0なら0 ⇒ OR演算で実装・復号できる
16/24
solverの作成 17 /24
復号でノイズが乗る確率は? • 簡単のために入力値は1で固定 • あるiでcipher[0, 16)[i]がすべて0のとき正しく復号できない • 1回でノイズが乗る確率は1/4 ⇒ 1
4 16 ≒ 2.32 × 10⁻¹⁰ 18/24 flag key n > m cipher 0 0 0 0 0 0 1 0 0 1 0 0 0 1 1 0 1 0 0 1 1 0 1 0 1 1 0 1 1 1 1 1 23200000000回に1回しか ノイズのらないんじゃね?
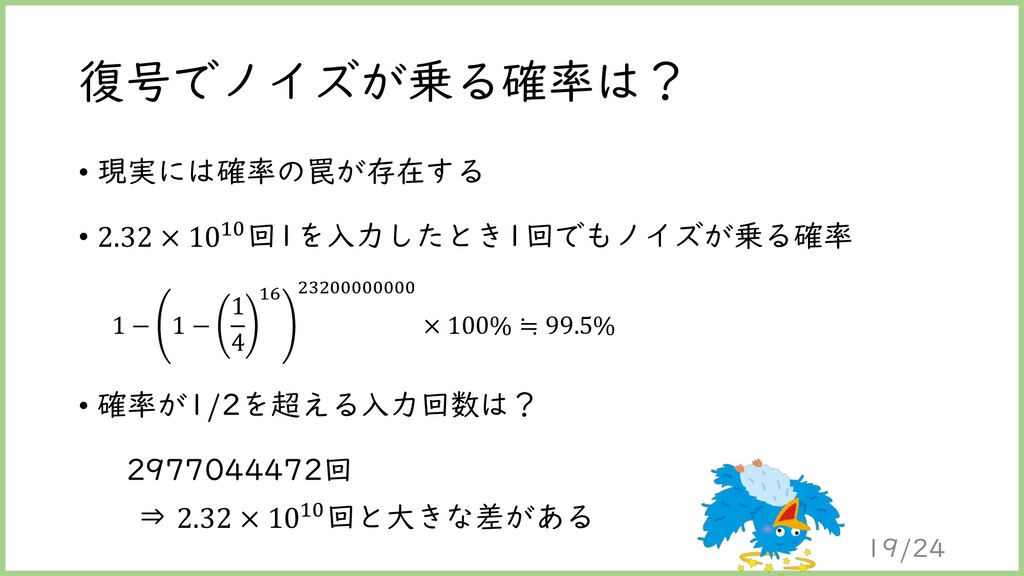
復号でノイズが乗る確率は? • 現実には確率の罠が存在する • 2.32 × 10¹⁰回1を入力したとき1回でもノイズが乗る確率 • 確率が1/2を超える入力回数は? 2977044472回
⇒ 2.32 × 10¹⁰回と大きな差がある 19/24 1 − 1 − 1 4 16 23200000000 × 100% ≒ 99.5%
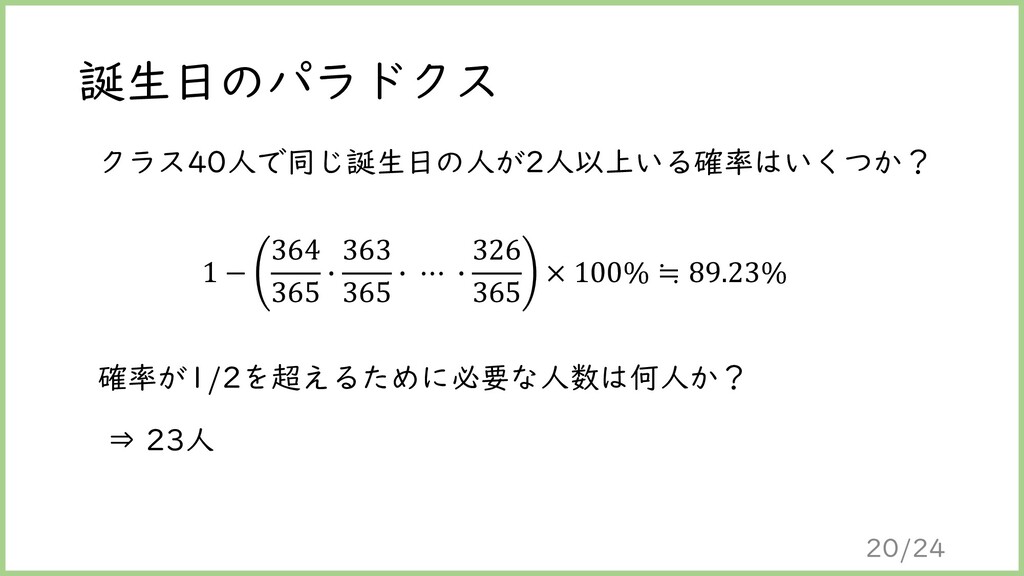
誕生日のパラドクス 20/24 クラス40人で同じ誕生日の人が2人以上いる確率はいくつか? 1 − 364 365 ∙ 363 365
∙ ⋯ ∙ 326 365 × 100% ≒ 89.23% 確率が1/2を超えるために必要な人数は何人か? ⇒ 23人
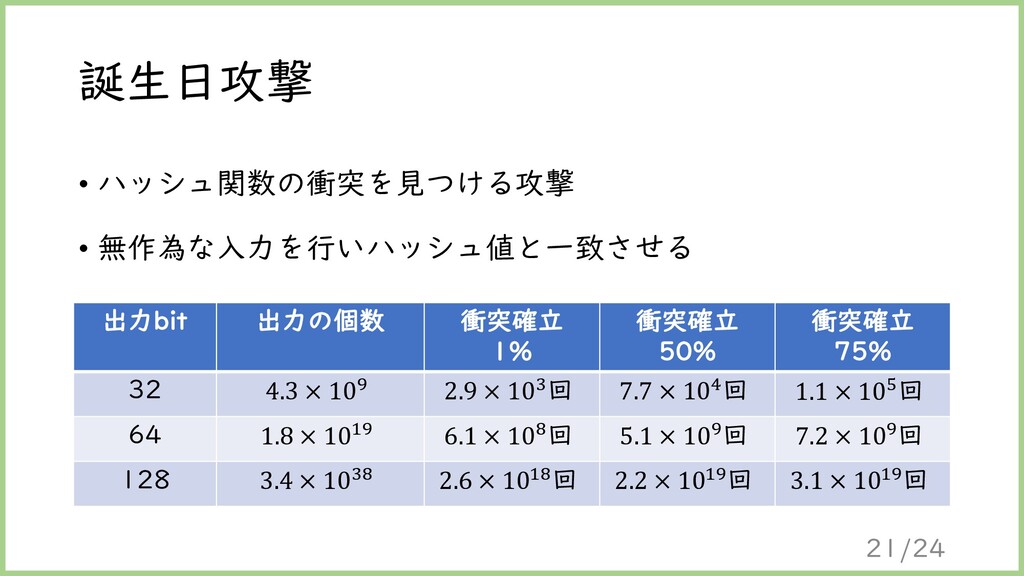
誕生日攻撃 • ハッシュ関数の衝突を見つける攻撃 • 無作為な入力を行いハッシュ値と一致させる 21/24 出力bit 出力の個数 衝突確立 1%
衝突確立 50% 衝突確立 75% 32 4.3 × 10⁹ 2.9 × 10³回 7.7 × 10⁴回 1.1 × 10⁵回 64 1.8 × 10¹⁹ 6.1 × 10⁸回 5.1 × 10⁹回 7.2 × 10⁹回 128 3.4 × 1038 2.6 × 10¹⁸回 2.2 × 10¹⁹回 3.1 × 10¹⁹回
発展問題の紹介 22/24
さいごに 23/24 • CTFはとても楽しいです • ぜひ一緒に楽しみましょう
お世話になったところ • イラスト https://www.irasutoya.com/ • 誕生日攻撃の出力bitと衝突確立の関係 https://ja.wikipedia.org/wiki/%E8%AA%95%E7%94%9F%E6%97 %A5%E6%94%BB%E6%92%83 • SECCON
Beginners CTF 2021(GitHub) https://github.com/SECCON/Beginners_CTF_2021 24/24


 ushigai
 tomokusaba
 ishiirikie
 ochtum
 diggymo
 siromi
 tsukuboshi
 takahiromatsui
 snowwmn0824
 tkuchiki
 cygames
 taiki45
 matsunobu
 scottboms
 lara
 baasie
 konakalab
 akihiro_kokubo
 marktimemedia
 tapps
 mclloyd
 eileencodes
 swwweet






![復号でノイズが乗る確率は? • 簡単のために入力値は1で固定 • あるiでcipher[0, 16)[i]がすべて0のとき正しく復号できない • 1回でノイズが乗る確率は1/4 ⇒ 1](https://files.speakerdeck.com/presentations/ddf625d483324d95b6063da672149da3/slide_18.jpg)