Share
Embed
TerraformとWerckerとAWS Organizationsで始めるステージング・開発環境構築 / terraform-wercker-aws-organizations
- terraform
- wercker
- aws organizations

youyo
June 27, 2017
Transcript
45 slides
-
എܠ ͜Μͳ͍͕͋Γ·ͨ͠ • ීஈΠϯϑϥΤϯδχΞͱͯ͠AWSڥͷߏஙΛ͍ͯ͠Δ • ͍͍ՃݮίʔυԽ͍ͨ͠ • ߏஙΛࣗಈԽ͍ͨ͠ => વΠϯϑϥଆΰϦΰϦݕূͰ͖Δ։ൃڥ/εςʔδϯά
ڥඞཁͩΑͶɻGithub-Flowͷ͍ͤͨΑͶɻ -
Ͳ͏Δ͔ • ίʔυԽ͍ͨ͠ => Terraform • ߏஙΛࣗಈԽ͍ͨ͠ => Wercker •
ϓϩμΫγϣϯͱΞΧϯτϨϕϧͰ͞Εͨ ։ൃ/εςʔδϯάڥ΄͍͠ => AWS Organiza3ons -
Terraform • AWSͰ͍͏Cloudforma.on • ༷ʑͳϦιʔεΛίʔυͱͯ͠දݱͰ͖Δ • ϓϩόΠμʔͱ͍͏ϓϥάΠϯػߏΛ࣋ͪɺ༷ʑͳαʔϏε͕ ϓϩόΠμʔͱͯ͠ఏڙ͞ΕΔ • AWSͦͷ͏ͪͷҰͭɻͦͷଞAzureGCP,
Fastly, Github, HerokuͳͲͨ͘͞Μ͋Δɻࣗ࡞Ͱ͖Δɻ -
Wercker • CI as a Service • CircleCIͱ͔TravisCIͷؒ • ࣮ߦڥͱͯ͠ಠࣗͷDockerίϯςφΛར༻Ͱ͖Δ
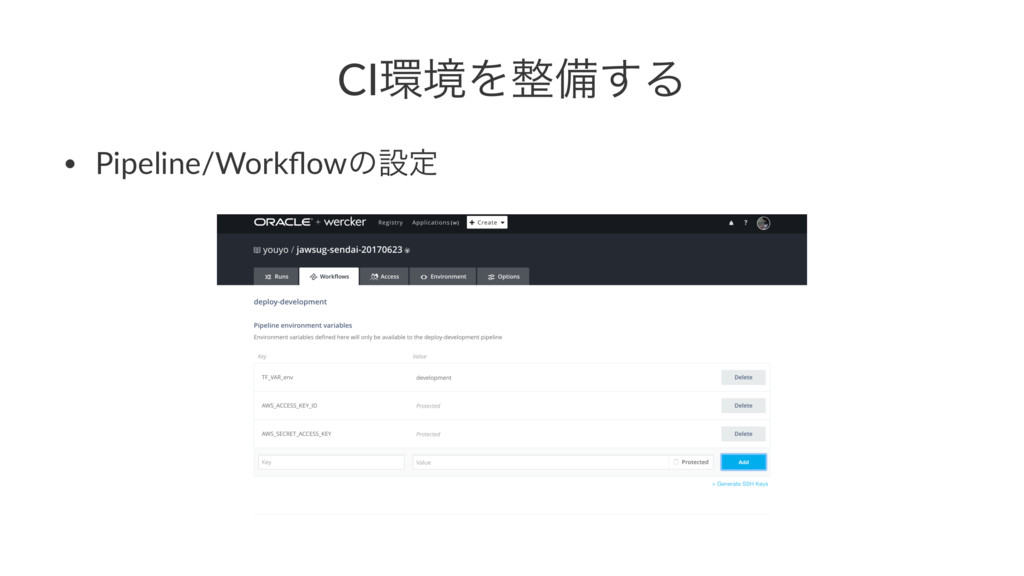
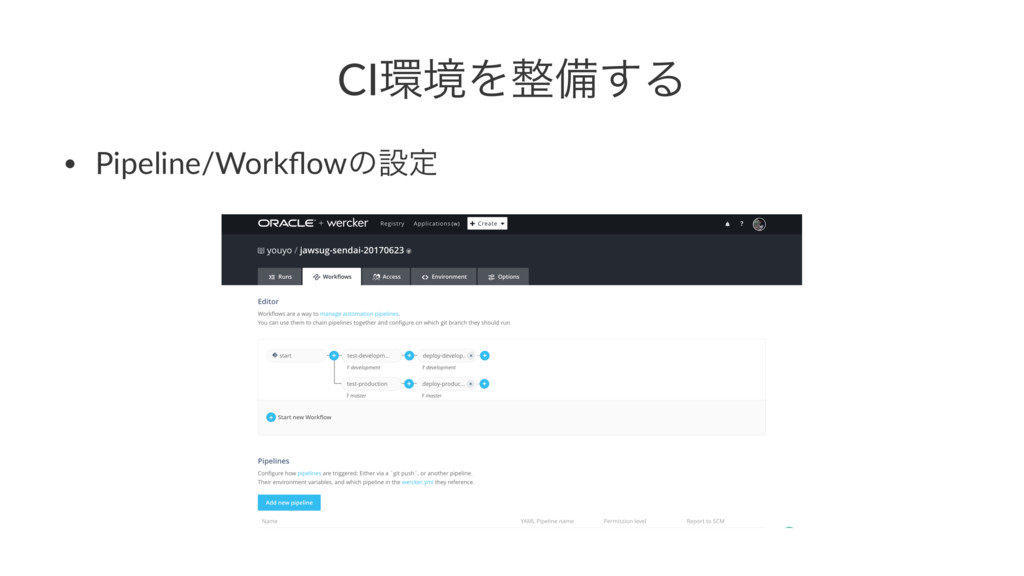
• ෳͷsteps(࣮ߦ͖͢ίϚϯυͷ୯ҐΈ͍ͨͳ)͔Βߏ͞Ε ΔPipeline͕͋ΓɺPipeline୯ҐͰڥมͷઃఆ͕Ͱ͖Δ -
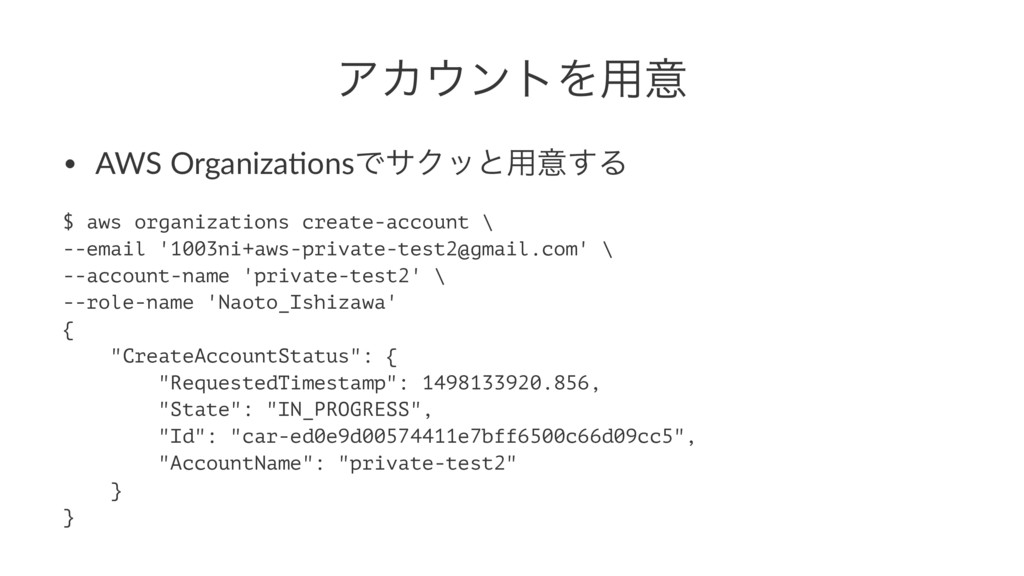
ΞΧϯτΛ༻ҙ • AWS Organiza-onsͰαΫοͱ༻ҙ͢Δ $ aws organizations create-account \ --email
'[email protected]' \ --account-name 'private-test2' \ --role-name 'Naoto_Ishizawa' { "CreateAccountStatus": { "RequestedTimestamp": 1498133920.856, "State": "IN_PROGRESS", "Id": "car-ed0e9d00574411e7bff6500c66d09cc5", "AccountName": "private-test2" } } -
ΞΧϯτΛ༻ҙ $ aws organizations list-create-account-status | \ jq '.CreateAccountStatuses[] |
\ select(.AccountName == "private-test2")' { "AccountName": "private-test2", "State": "SUCCEEDED", "RequestedTimestamp": 1498133926.284, "CompletedTimestamp": 1498133931.048, "Id": "car-ed0e9d00574411e7bff6500c66d09cc5", "AccountId": "591019932956" } -
ΞΧϯτΛ༻ҙ $ cat <<EOL>> ~/.aws/config [profile private-test2] role_arn = arn:aws:iam::591019932956:role/Naoto_Ishizawa
source_profile = default EOL $ awslogin -profile private-test2 • terraform༻ͷIAMϢʔβʔΛ࡞͓ͯ͘͠ • ,stateϑΝΠϧอଘ༻ͷS3όέοτ࡞͓ͯ͘͠ -
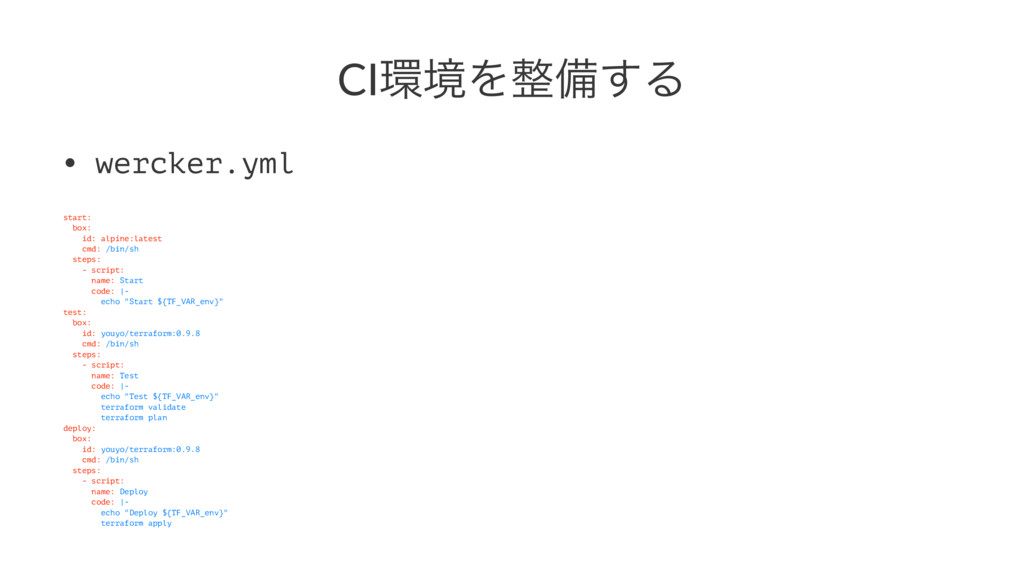
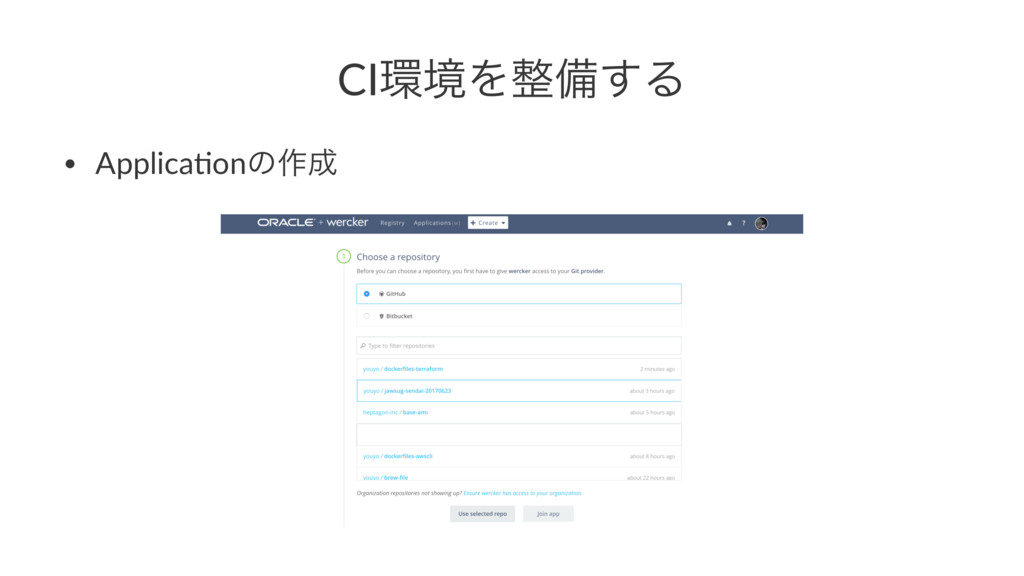
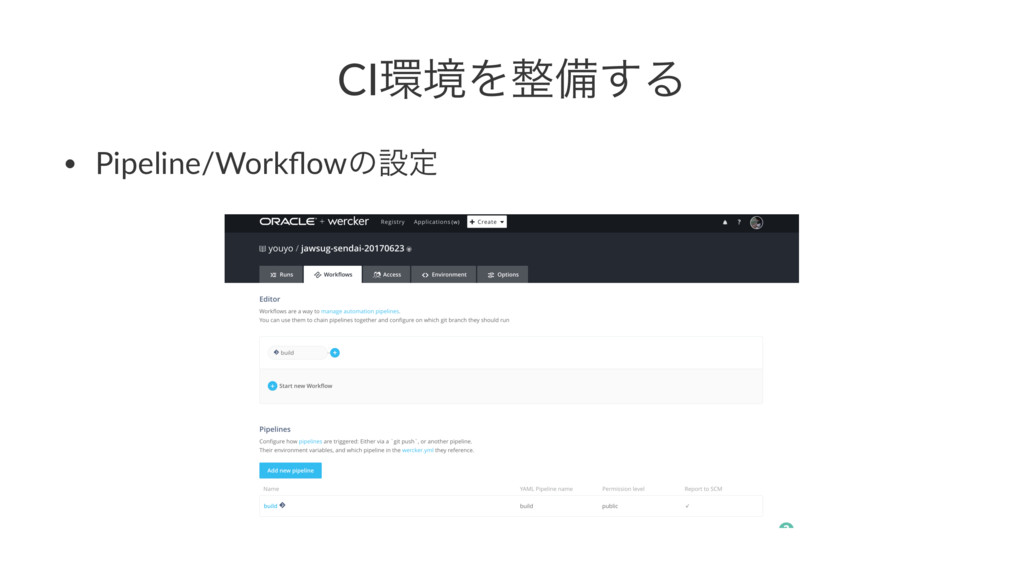
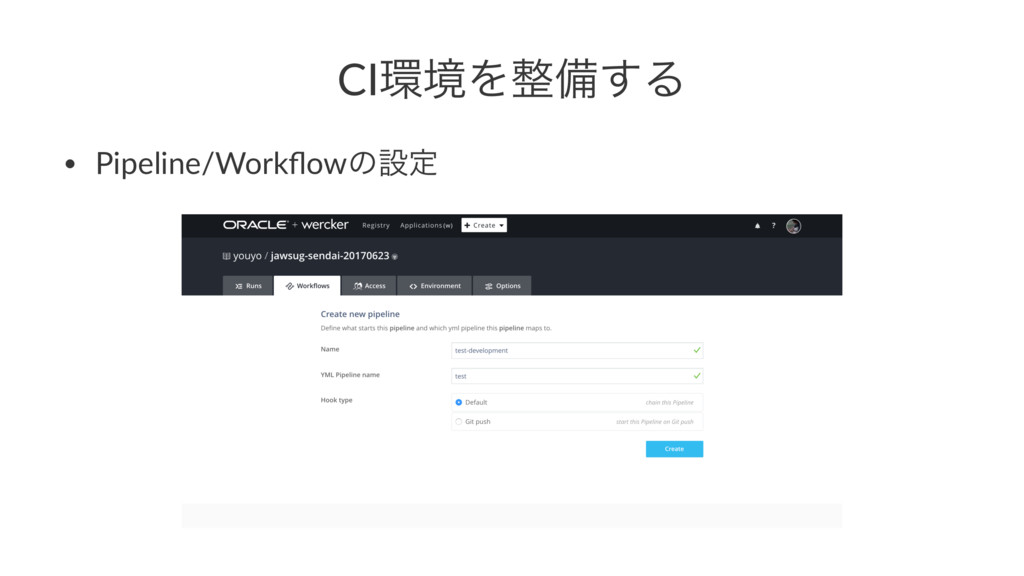
CIڥΛඋ͢Δ • wercker.yml start: box: id: alpine:latest cmd: /bin/sh steps:
- script: name: Start code: |- echo "Start ${TF_VAR_env}" test: box: id: youyo/terraform:0.9.8 cmd: /bin/sh steps: - script: name: Test code: |- echo "Test ${TF_VAR_env}" terraform validate terraform plan deploy: box: id: youyo/terraform:0.9.8 cmd: /bin/sh steps: - script: name: Deploy code: |- echo "Deploy ${TF_VAR_env}" terraform apply -
CIڥΛඋ͢Δ • ֤ڥ͝ͱʹpipelineΛ༻ҙ͢Δ • pipeline͝ͱʹڥม͕ઃఆՄೳ => commit͢ΔbranchʹΑͬͯ༻͢ΔawsΞΧϯτͷΓସ ͕͑Մೳ • wercker.yml
ʹมΛهड़͢Δ͜ͱͰ͖Δ͕ΞΫηεΩʔ ͳͲͷൿಗใαΠτ্͔Βઃఆ͢Δ͜ͱͰӅṭͰ͖Δ -
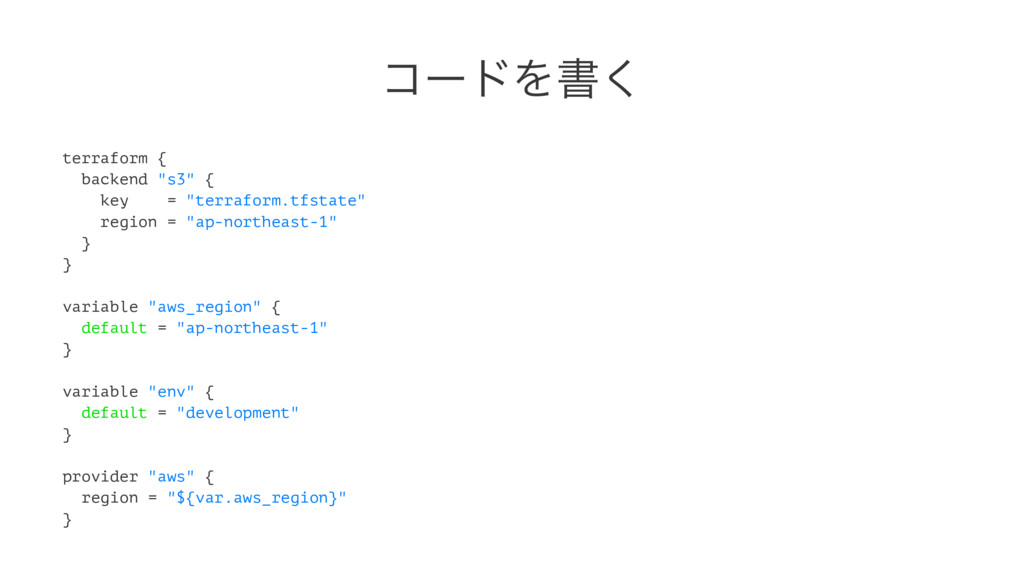
ίʔυΛॻ͘ terraform { backend "s3" { key = "terraform.tfstate" region
= "ap-northeast-1" } } variable "aws_region" { default = "ap-northeast-1" } variable "env" { default = "development" } provider "aws" { region = "${var.aws_region}" } -
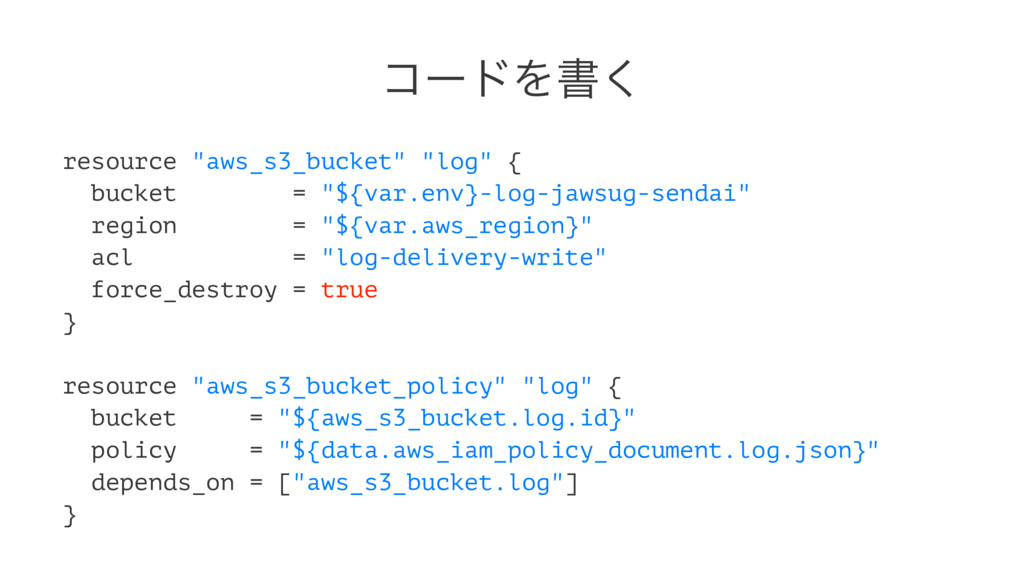
ίʔυΛॻ͘ resource "aws_s3_bucket" "log" { bucket = "${var.env}-log-jawsug-sendai" region =
"${var.aws_region}" acl = "log-delivery-write" force_destroy = true } resource "aws_s3_bucket_policy" "log" { bucket = "${aws_s3_bucket.log.id}" policy = "${data.aws_iam_policy_document.log.json}" depends_on = ["aws_s3_bucket.log"] } -
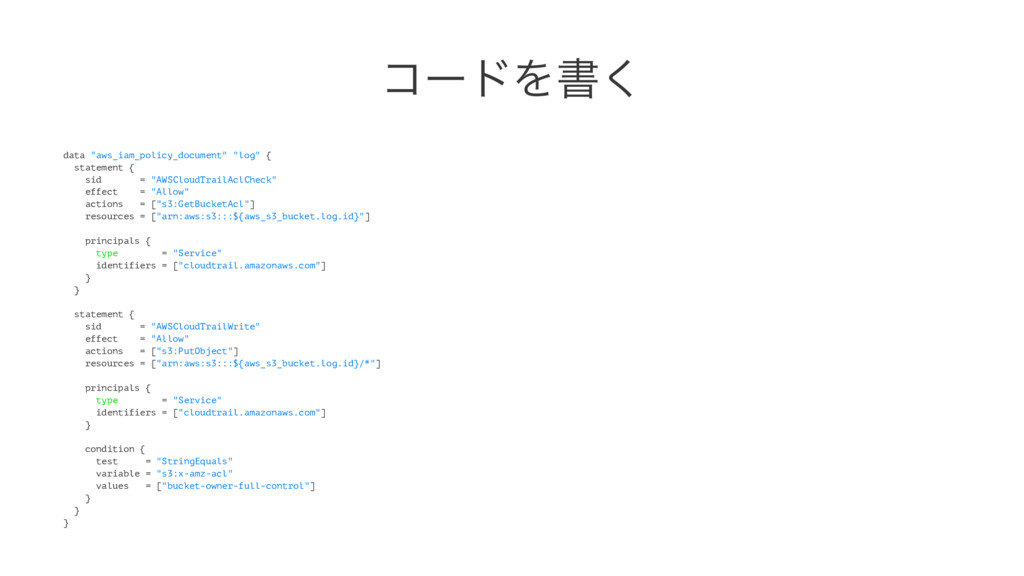
ίʔυΛॻ͘ data "aws_iam_policy_document" "log" { statement { sid = "AWSCloudTrailAclCheck"
effect = "Allow" actions = ["s3:GetBucketAcl"] resources = ["arn:aws:s3:::${aws_s3_bucket.log.id}"] principals { type = "Service" identifiers = ["cloudtrail.amazonaws.com"] } } statement { sid = "AWSCloudTrailWrite" effect = "Allow" actions = ["s3:PutObject"] resources = ["arn:aws:s3:::${aws_s3_bucket.log.id}/*"] principals { type = "Service" identifiers = ["cloudtrail.amazonaws.com"] } condition { test = "StringEquals" variable = "s3:x-amz-acl" values = ["bucket-owner-full-control"] } } } -
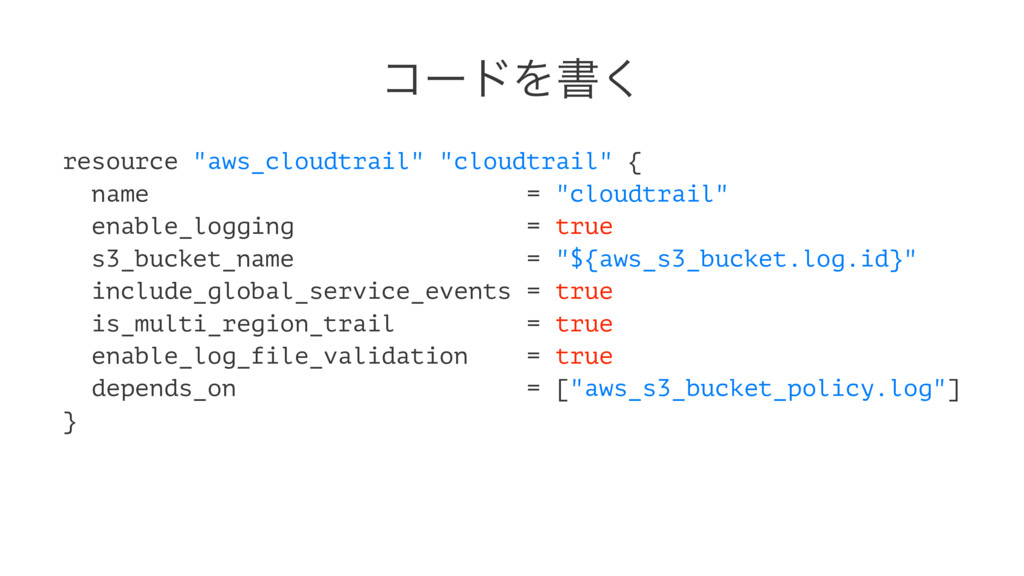
ίʔυΛॻ͘ resource "aws_cloudtrail" "cloudtrail" { name = "cloudtrail" enable_logging =
true s3_bucket_name = "${aws_s3_bucket.log.id}" include_global_service_events = true is_multi_region_trail = true enable_log_file_validation = true depends_on = ["aws_s3_bucket_policy.log"] } -
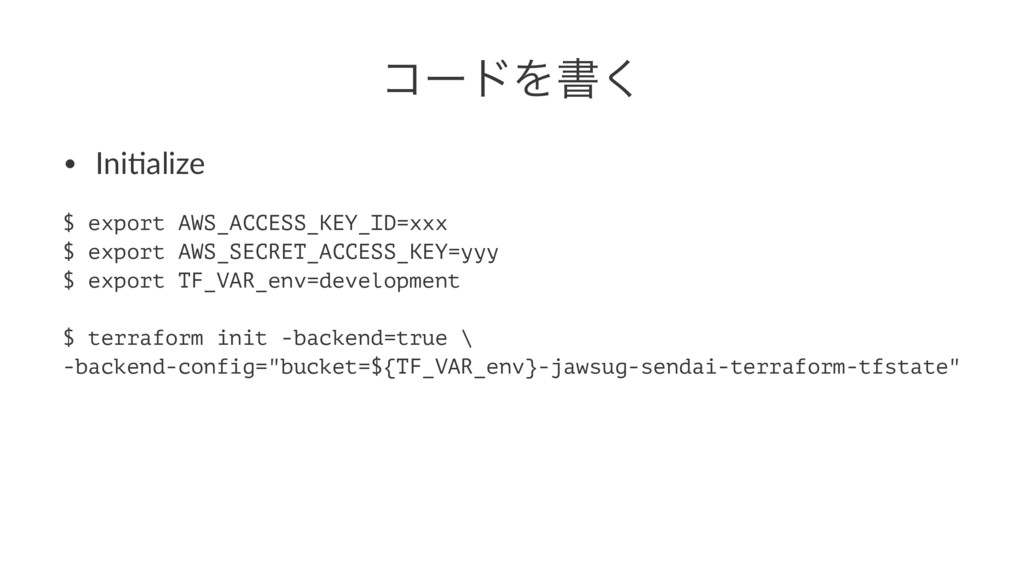
ίʔυΛॻ͘ • Ini%alize $ export AWS_ACCESS_KEY_ID=xxx $ export AWS_SECRET_ACCESS_KEY=yyy $
export TF_VAR_env=development $ terraform init -backend=true \ -backend-config="bucket=${TF_VAR_env}-jawsug-sendai-terraform-tfstate" -
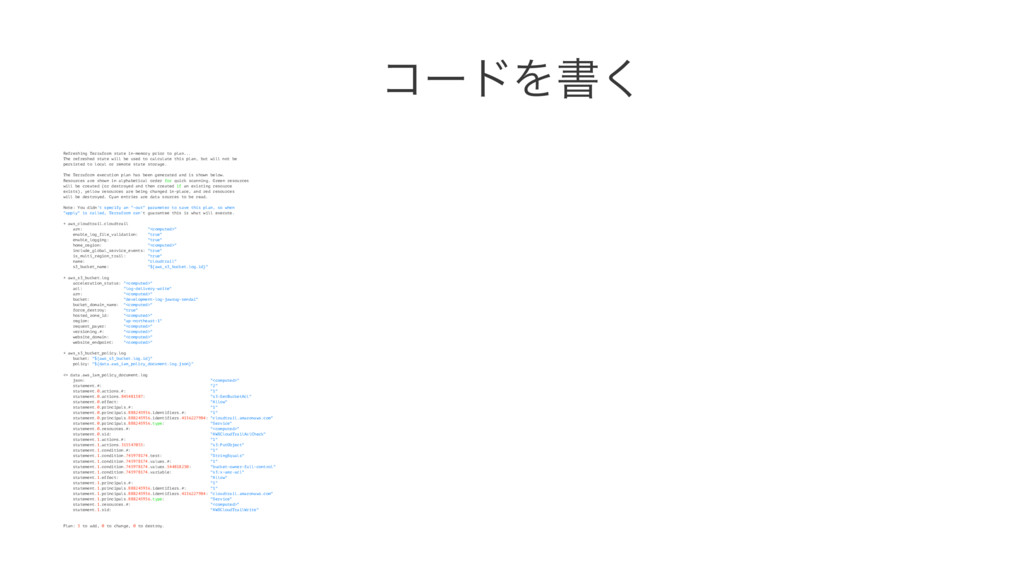
ίʔυΛॻ͘ Refreshing Terraform state in-memory prior to plan... The refreshed
state will be used to calculate this plan, but will not be persisted to local or remote state storage. The Terraform execution plan has been generated and is shown below. Resources are shown in alphabetical order for quick scanning. Green resources will be created (or destroyed and then created if an existing resource exists), yellow resources are being changed in-place, and red resources will be destroyed. Cyan entries are data sources to be read. Note: You didn't specify an "-out" parameter to save this plan, so when "apply" is called, Terraform can't guarantee this is what will execute. + aws_cloudtrail.cloudtrail arn: "<computed>" enable_log_file_validation: "true" enable_logging: "true" home_region: "<computed>" include_global_service_events: "true" is_multi_region_trail: "true" name: "cloudtrail" s3_bucket_name: "${aws_s3_bucket.log.id}" + aws_s3_bucket.log acceleration_status: "<computed>" acl: "log-delivery-write" arn: "<computed>" bucket: "development-log-jawsug-sendai" bucket_domain_name: "<computed>" force_destroy: "true" hosted_zone_id: "<computed>" region: "ap-northeast-1" request_payer: "<computed>" versioning.#: "<computed>" website_domain: "<computed>" website_endpoint: "<computed>" + aws_s3_bucket_policy.log bucket: "${aws_s3_bucket.log.id}" policy: "${data.aws_iam_policy_document.log.json}" <= data.aws_iam_policy_document.log json: "<computed>" statement.#: "2" statement.0.actions.#: "1" statement.0.actions.845481387: "s3:GetBucketAcl" statement.0.effect: "Allow" statement.0.principals.#: "1" statement.0.principals.888245936.identifiers.#: "1" statement.0.principals.888245936.identifiers.4136227984: "cloudtrail.amazonaws.com" statement.0.principals.888245936.type: "Service" statement.0.resources.#: "<computed>" statement.0.sid: "AWSCloudTrailAclCheck" statement.1.actions.#: "1" statement.1.actions.315547055: "s3:PutObject" statement.1.condition.#: "1" statement.1.condition.745978174.test: "StringEquals" statement.1.condition.745978174.values.#: "1" statement.1.condition.745978174.values.544818230: "bucket-owner-full-control" statement.1.condition.745978174.variable: "s3:x-amz-acl" statement.1.effect: "Allow" statement.1.principals.#: "1" statement.1.principals.888245936.identifiers.#: "1" statement.1.principals.888245936.identifiers.4136227984: "cloudtrail.amazonaws.com" statement.1.principals.888245936.type: "Service" statement.1.resources.#: "<computed>" statement.1.sid: "AWSCloudTrailWrite" Plan: 3 to add, 0 to change, 0 to destroy. -
ίʔυΛॻ͘ • 3ͭͷϦιʔε͕Ճ͞ΕΔ Plan: 3 to add, 0 to change,
0 to destroy. -
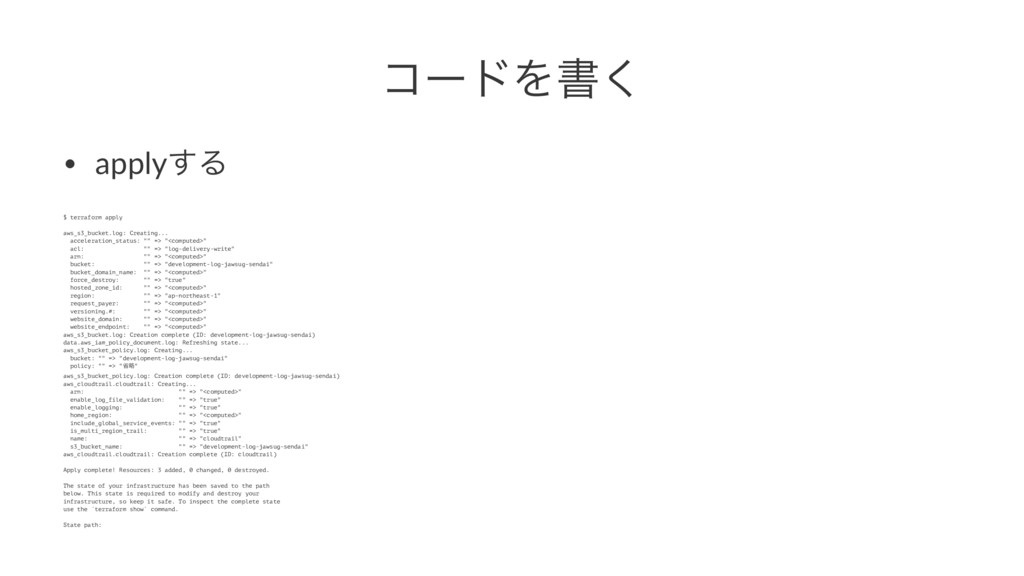
ίʔυΛॻ͘ • apply͢Δ $ terraform apply aws_s3_bucket.log: Creating... acceleration_status: ""
=> "<computed>" acl: "" => "log-delivery-write" arn: "" => "<computed>" bucket: "" => "development-log-jawsug-sendai" bucket_domain_name: "" => "<computed>" force_destroy: "" => "true" hosted_zone_id: "" => "<computed>" region: "" => "ap-northeast-1" request_payer: "" => "<computed>" versioning.#: "" => "<computed>" website_domain: "" => "<computed>" website_endpoint: "" => "<computed>" aws_s3_bucket.log: Creation complete (ID: development-log-jawsug-sendai) data.aws_iam_policy_document.log: Refreshing state... aws_s3_bucket_policy.log: Creating... bucket: "" => "development-log-jawsug-sendai" policy: "" => "লུ" aws_s3_bucket_policy.log: Creation complete (ID: development-log-jawsug-sendai) aws_cloudtrail.cloudtrail: Creating... arn: "" => "<computed>" enable_log_file_validation: "" => "true" enable_logging: "" => "true" home_region: "" => "<computed>" include_global_service_events: "" => "true" is_multi_region_trail: "" => "true" name: "" => "cloudtrail" s3_bucket_name: "" => "development-log-jawsug-sendai" aws_cloudtrail.cloudtrail: Creation complete (ID: cloudtrail) Apply complete! Resources: 3 added, 0 changed, 0 destroyed. The state of your infrastructure has been saved to the path below. This state is required to modify and destroy your infrastructure, so keep it safe. To inspect the complete state use the `terraform show` command. State path: -
ίʔυΛॻ͘ • showͯ͠ΈΔ $ terraform show aws_cloudtrail.cloudtrail: id = cloudtrail
arn = arn:aws:cloudtrail:ap-northeast-1:591019932956:trail/cloudtrail cloud_watch_logs_group_arn = cloud_watch_logs_role_arn = enable_log_file_validation = true enable_logging = true home_region = ap-northeast-1 include_global_service_events = true is_multi_region_trail = true kms_key_id = name = cloudtrail s3_bucket_name = development-log-jawsug-sendai s3_key_prefix = sns_topic_name = tags.% = 0 aws_s3_bucket.log: id = development-log-jawsug-sendai acceleration_status = acl = log-delivery-write arn = arn:aws:s3:::development-log-jawsug-sendai bucket = development-log-jawsug-sendai bucket_domain_name = development-log-jawsug-sendai.s3.amazonaws.com force_destroy = true hosted_zone_id = Z2M4EHUR26P7ZW logging.# = 0 region = ap-northeast-1 request_payer = BucketOwner tags.% = 0 versioning.# = 1 versioning.0.enabled = false versioning.0.mfa_delete = false website.# = 0 aws_s3_bucket_policy.log: id = development-log-jawsug-sendai bucket = development-log-jawsug-sendai policy = { "Version": "2012-10-17", "Statement": [ { "Sid": "AWSCloudTrailAclCheck", "Effect": "Allow", "Action": "s3:GetBucketAcl", "Resource": "arn:aws:s3:::development-log-jawsug-sendai", "Principal": { "Service": "cloudtrail.amazonaws.com" } }, { "Sid": "AWSCloudTrailWrite", "Effect": "Allow", "Action": "s3:PutObject", "Resource": "arn:aws:s3:::development-log-jawsug-sendai/*", "Principal": { "Service": "cloudtrail.amazonaws.com" }, "Condition": { "StringEquals": { "s3:x-amz-acl": "bucket-owner-full-control" } } } ] } data.aws_iam_policy_document.log: id = 3591822430 json = { "Version": "2012-10-17", "Statement": [ { "Sid": "AWSCloudTrailAclCheck", "Effect": "Allow", "Action": "s3:GetBucketAcl", "Resource": "arn:aws:s3:::development-log-jawsug-sendai", "Principal": { "Service": "cloudtrail.amazonaws.com" } }, { "Sid": "AWSCloudTrailWrite", "Effect": "Allow", "Action": "s3:PutObject", "Resource": "arn:aws:s3:::development-log-jawsug-sendai/*", "Principal": { "Service": "cloudtrail.amazonaws.com" }, "Condition": { "StringEquals": { "s3:x-amz-acl": "bucket-owner-full-control" } } } ] } statement.# = 2 statement.0.actions.# = 1 statement.0.actions.845481387 = s3:GetBucketAcl statement.0.condition.# = 0 statement.0.effect = Allow statement.0.not_actions.# = 0 statement.0.not_principals.# = 0 statement.0.not_resources.# = 0 statement.0.principals.# = 1 statement.0.principals.888245936.identifiers.# = 1 statement.0.principals.888245936.identifiers.4136227984 = cloudtrail.amazonaws.com statement.0.principals.888245936.type = Service statement.0.resources.# = 1 statement.0.resources.2709316599 = arn:aws:s3:::development-log-jawsug-sendai statement.0.sid = AWSCloudTrailAclCheck statement.1.actions.# = 1 statement.1.actions.315547055 = s3:PutObject statement.1.condition.# = 1 statement.1.condition.745978174.test = StringEquals statement.1.condition.745978174.values.# = 1 statement.1.condition.745978174.values.544818230 = bucket-owner-full-control statement.1.condition.745978174.variable = s3:x-amz-acl statement.1.effect = Allow statement.1.not_actions.# = 0 statement.1.not_principals.# = 0 statement.1.not_resources.# = 0 statement.1.principals.# = 1 statement.1.principals.888245936.identifiers.# = 1 statement.1.principals.888245936.identifiers.4136227984 = cloudtrail.amazonaws.com statement.1.principals.888245936.type = Service statement.1.resources.# = 1 statement.1.resources.3865598363 = arn:aws:s3:::development-log-jawsug-sendai/* statement.1.sid = AWSCloudTrailWrite -
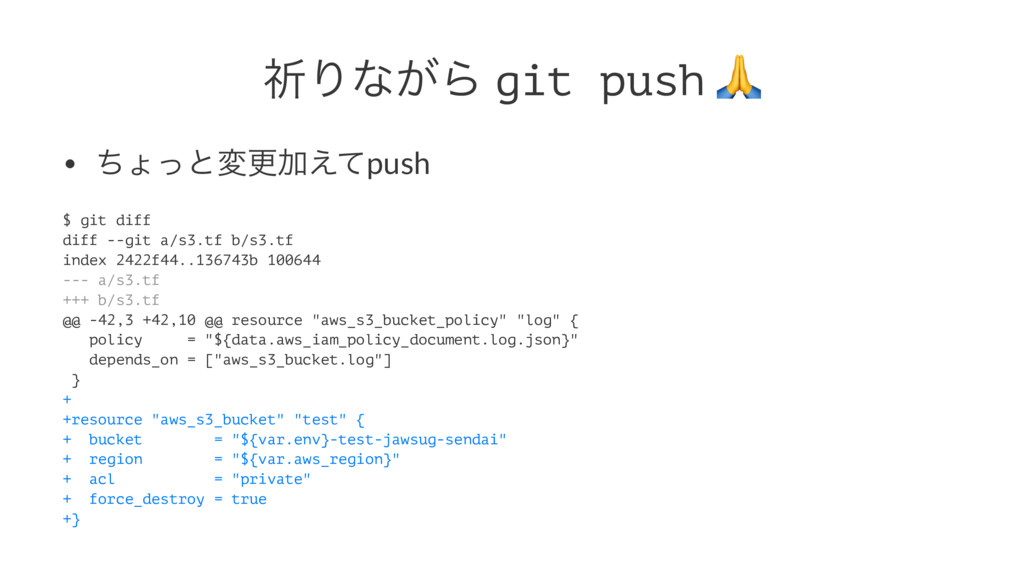
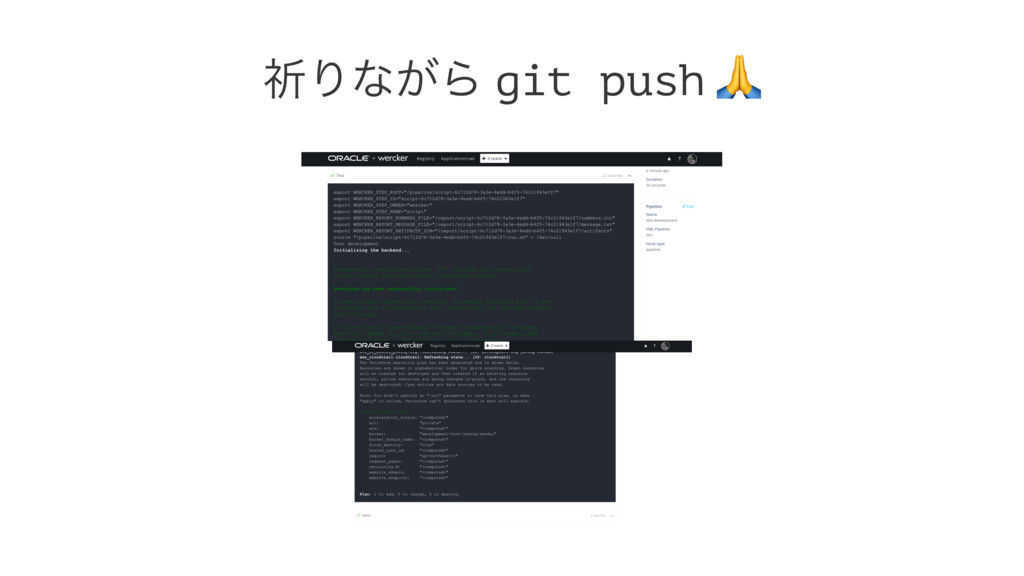
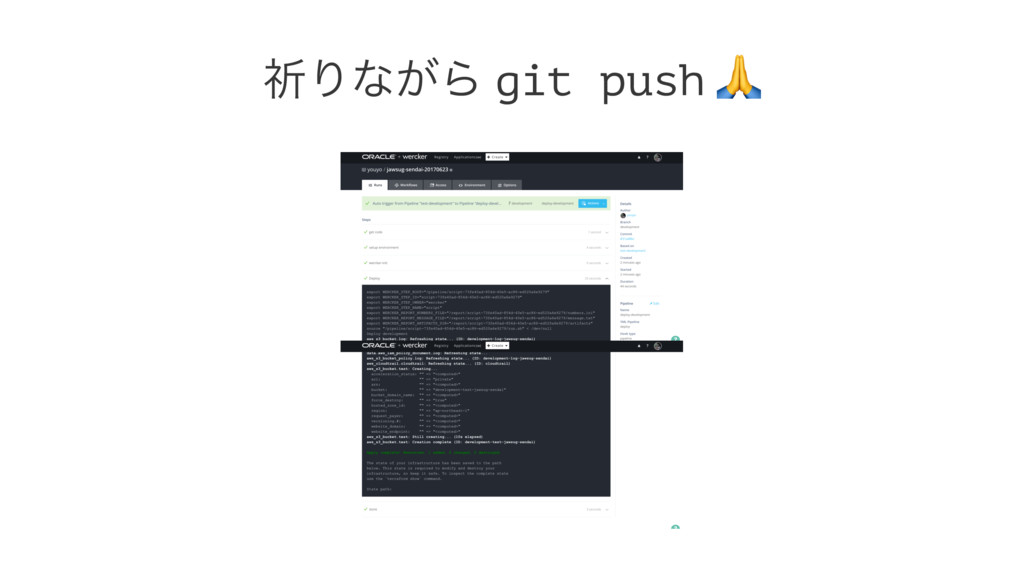
فΓͳ͕Β git push ! • ͪΐͬͱมߋՃ͑ͯpush $ git diff diff
--git a/s3.tf b/s3.tf index 2422f44..136743b 100644 --- a/s3.tf +++ b/s3.tf @@ -42,3 +42,10 @@ resource "aws_s3_bucket_policy" "log" { policy = "${data.aws_iam_policy_document.log.json}" depends_on = ["aws_s3_bucket.log"] } + +resource "aws_s3_bucket" "test" { + bucket = "${var.env}-test-jawsug-sendai" + region = "${var.aws_region}" + acl = "private" + force_destroy = true +} -
·ͱΊ • AWS Organiza-ons/Terraform/WerckerͳͲΛΈ߹Θͤͯίʔ υԽ/ࣗಈԽͰ͖ͨ • ͋͘͜͜·Ͱ͍͍ײ͡ͷελʔτ • ੜ࢈ੑߴ͘։ൃ͍ͯ͜͠͏ •
ຊͷࢿྉͪ͜Βʹ h8ps:/ /github.com/youyo/jawsug-sendai-20170623
 youyo
 oracle4engineer
 maguroalternative
 wind111
 iwamot
 tsukuboshi
 ivry_presentationmaterials
 yama3133
 munenick
 henryofficial
 comi190327
 torounit
 davetheseo
 aleyda
 addyosmani
 jacobtomlinson
 reverentgeek
 greggifford
 twada
 sstephenson
 codingconduct
 brettharned
 marketingsoph
 baasie