Upgrade to Pro — share decks privately, control downloads, hide ads and more …

APIsecure 2023 - Princess of Thieves: How I Hac...

APIsecure 2023 - Princess of Thieves: How I Hacked 50 Banks, Alissa Knight

APIsecure 2023 - The world's first and only API security conference
March 14 & 15, 2023

Princess of Thieves: How I Hacked 50 Banks
Alissa Knight, Partner at Knight Group

------

Check out our conferences at https://www.apidays.global/

Do you want to sponsor or talk at one of our conferences?
https://apidays.typeform.com/to/ILJeAaV8

Learn more on APIscene, the global media made by the community for the community:
https://www.apiscene.io

Explore the API ecosystem with the API Landscape:
https://apilandscape.apiscene.io/

FOST, powered by apidays PRO

March 21, 2023

Transcript

17 slides
  1. Princess of Thieves 21st Century Bank Robbery in Hacking Banks

    and Cryptocurrency Exchanges Alissa Knight
  2. “If I were to advise a hostile nation state on

    how to cripple the U.S. financial system, I’d tell them to start with the APIs first.” - Anonymous
  3. About Alissa Knight • Recovering hacker of 23 years •

    Arrested in 1997 • Worked for U.S. IC in cyber warfare • Run family of companies with wife: Knight Ink, Knight Events, Knight Studios, Knight Publishing, Knight Coffee • Writer, Director and Producer: Scorched Earth, Ransom, HEAT, Dark Ops, Underdog Games • Published Author • Serial Entrepreneur • API Hacker: mHealth, FHIR, Connected Cars, Banks
  4. About the Research • Hack Cryptocurrency Exchange Apps and APIs:

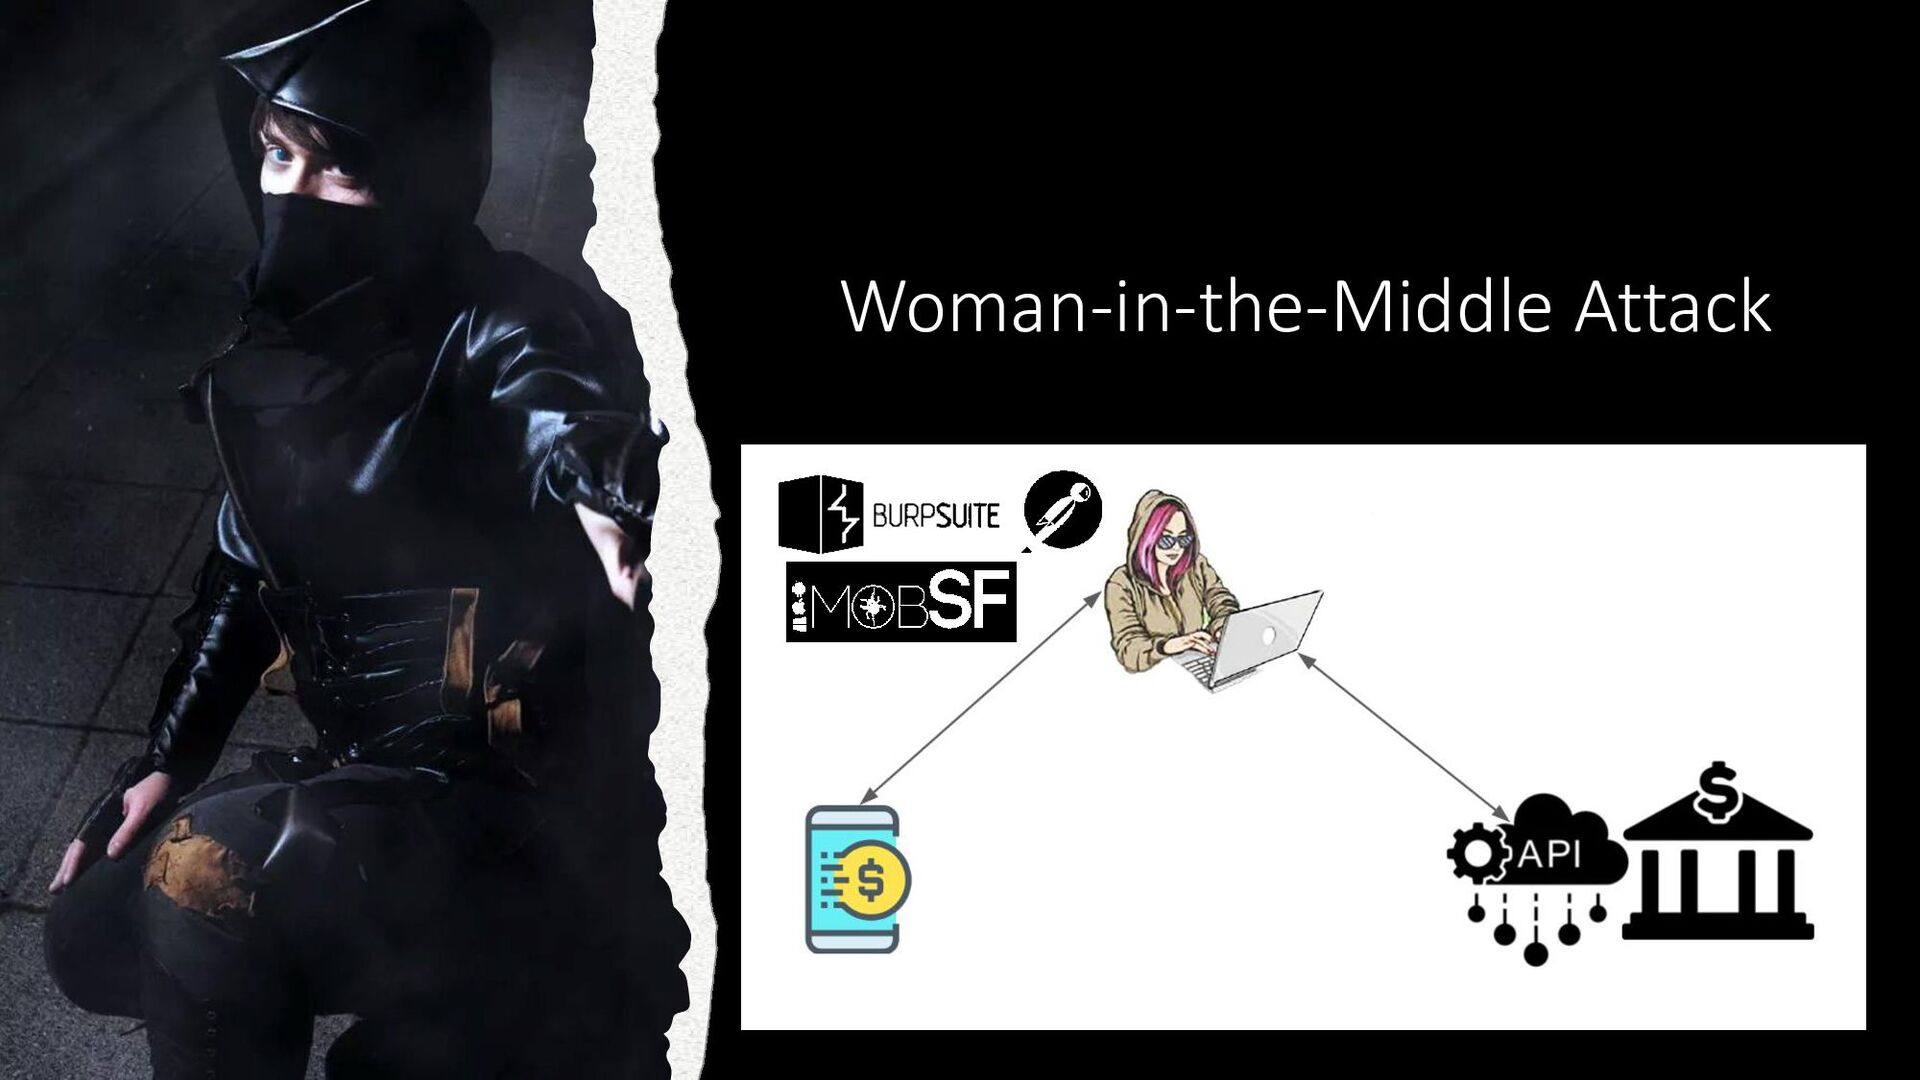
    No limit • Hacked so far: 11 • Hardcoded working production passwords, API keys/tokens found: 49 • Total account holders affected: 123,150,000 • Total assets: $269,100,000,000 • Most common vulnerability found: API1.2019: Broken Object Level Authorization • Vulnerable to WITM attack: 10
  5. Maybe you’re thinking they were small Maybe you are thinking

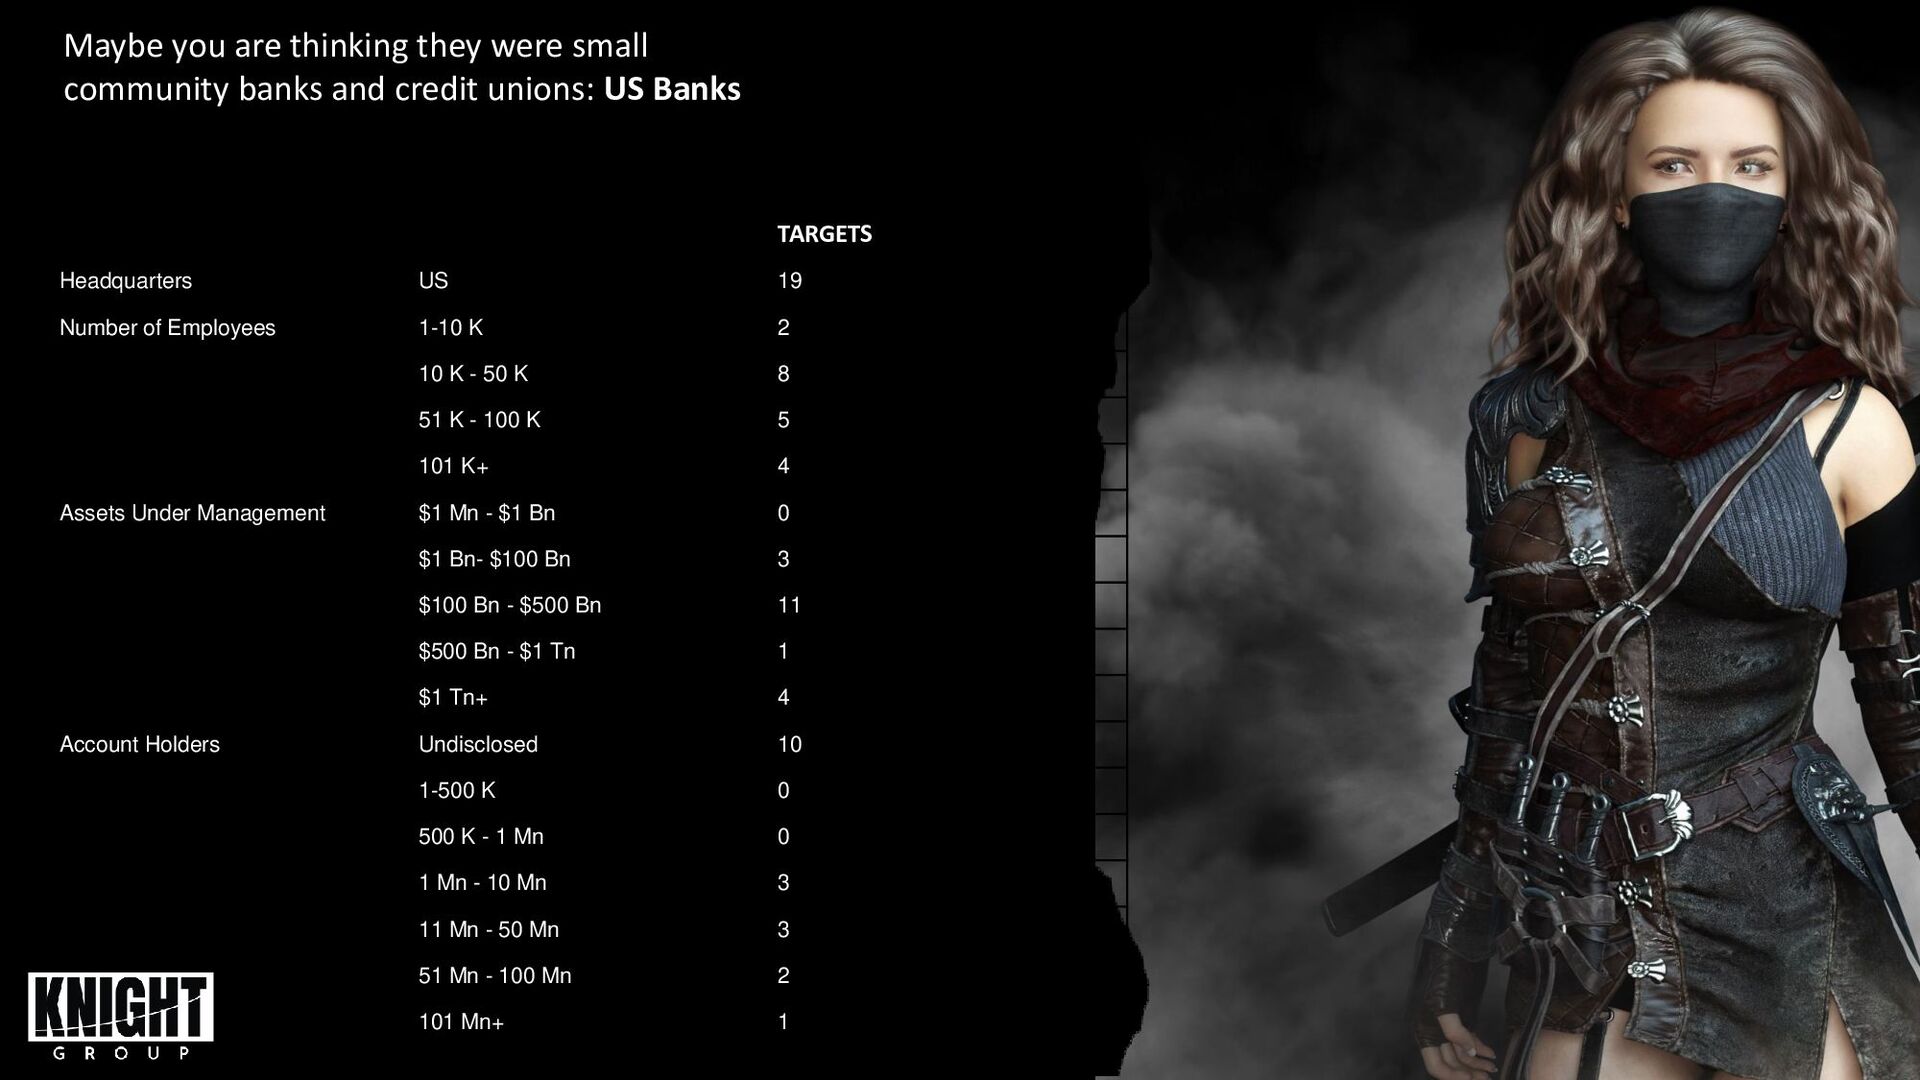
    they were small community banks and credit unions: US Banks TARGETS Headquarters US 19 Number of Employees 1-10 K 2 10 K - 50 K 8 51 K - 100 K 5 101 K+ 4 Assets Under Management $1 Mn - $1 Bn 0 $1 Bn- $100 Bn 3 $100 Bn - $500 Bn 11 $500 Bn - $1 Tn 1 $1 Tn+ 4 Account Holders Undisclosed 10 1-500 K 0 500 K - 1 Mn 0 1 Mn - 10 Mn 3 11 Mn - 50 Mn 3 51 Mn - 100 Mn 2 101 Mn+ 1
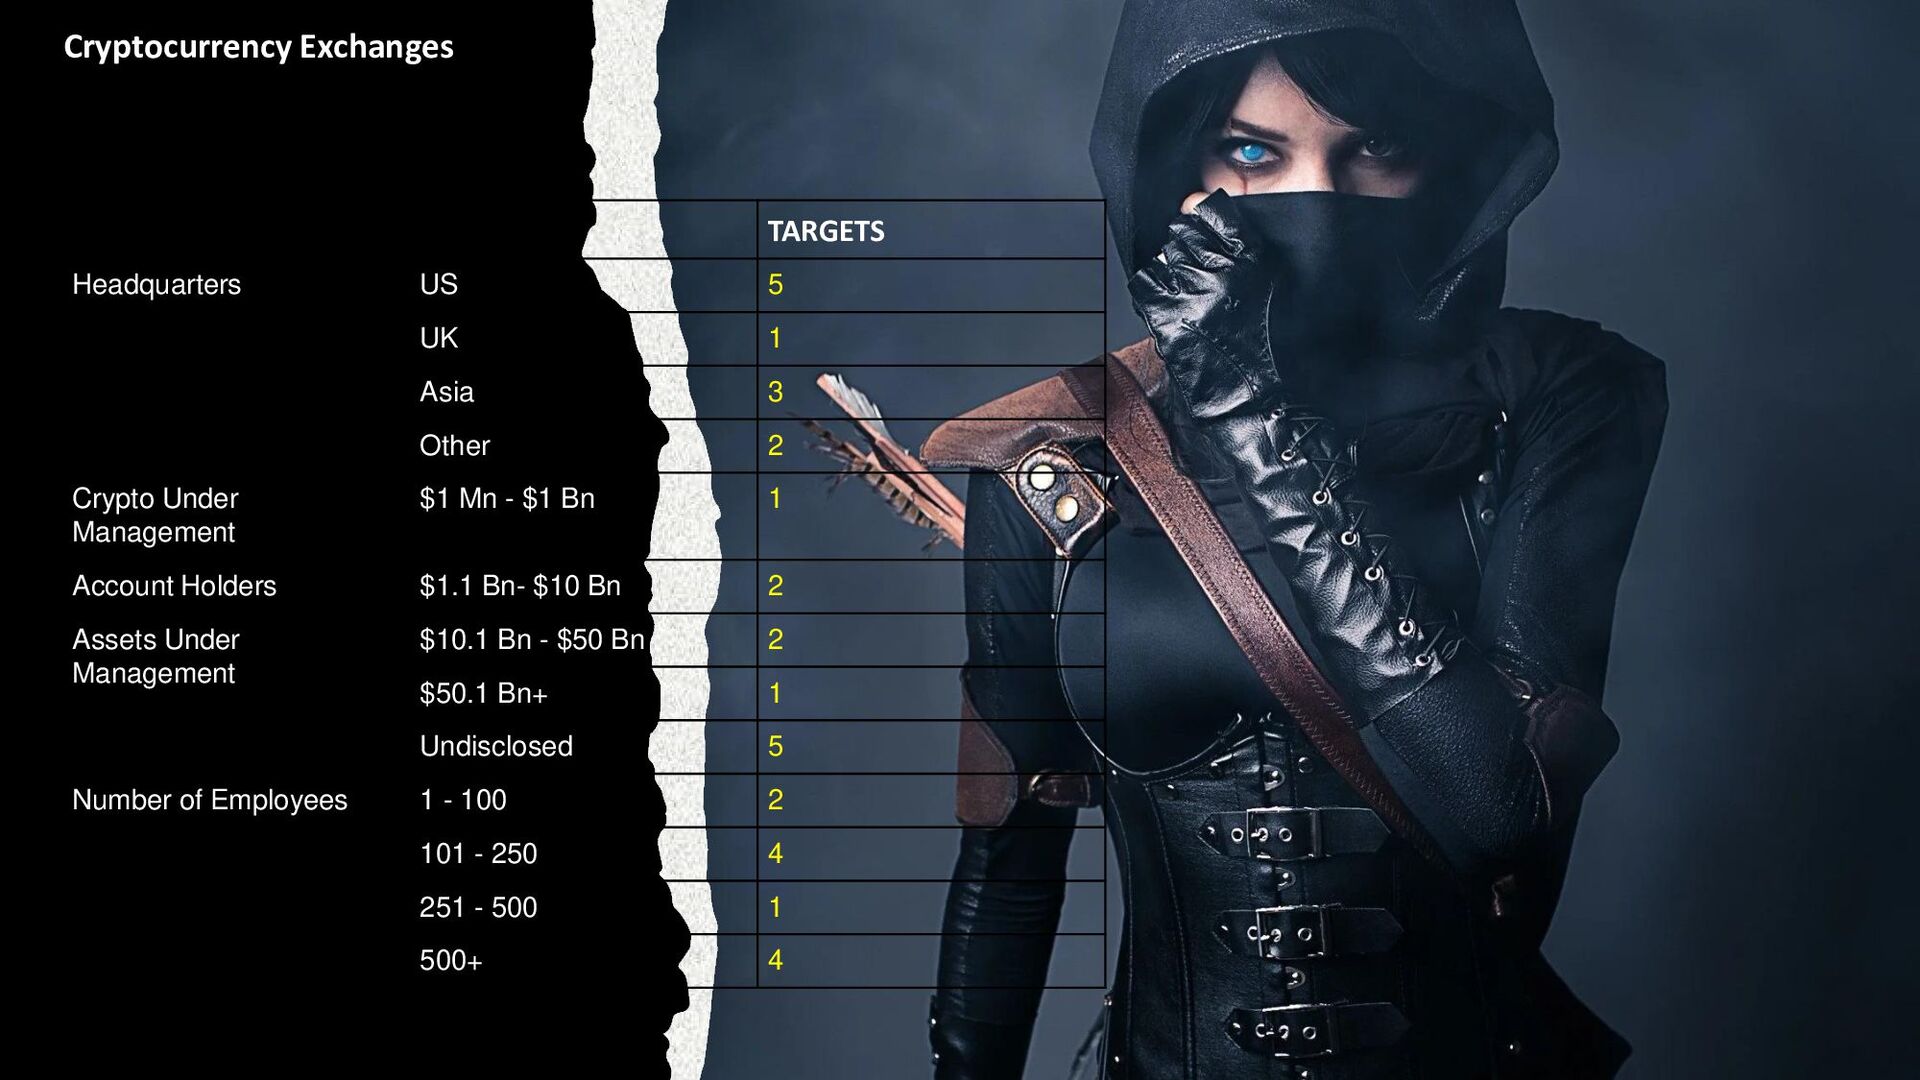
  6. TARGETS Headquarters US 5 UK 1 Asia 3 Other 2

    Crypto Under Management $1 Mn - $1 Bn 1 Account Holders $1.1 Bn- $10 Bn 2 Assets Under Management $10.1 Bn - $50 Bn 2 $50.1 Bn+ 1 Undisclosed 5 Number of Employees 1 - 100 2 101 - 250 4 251 - 500 1 500+ 4 Cryptocurrency Exchanges
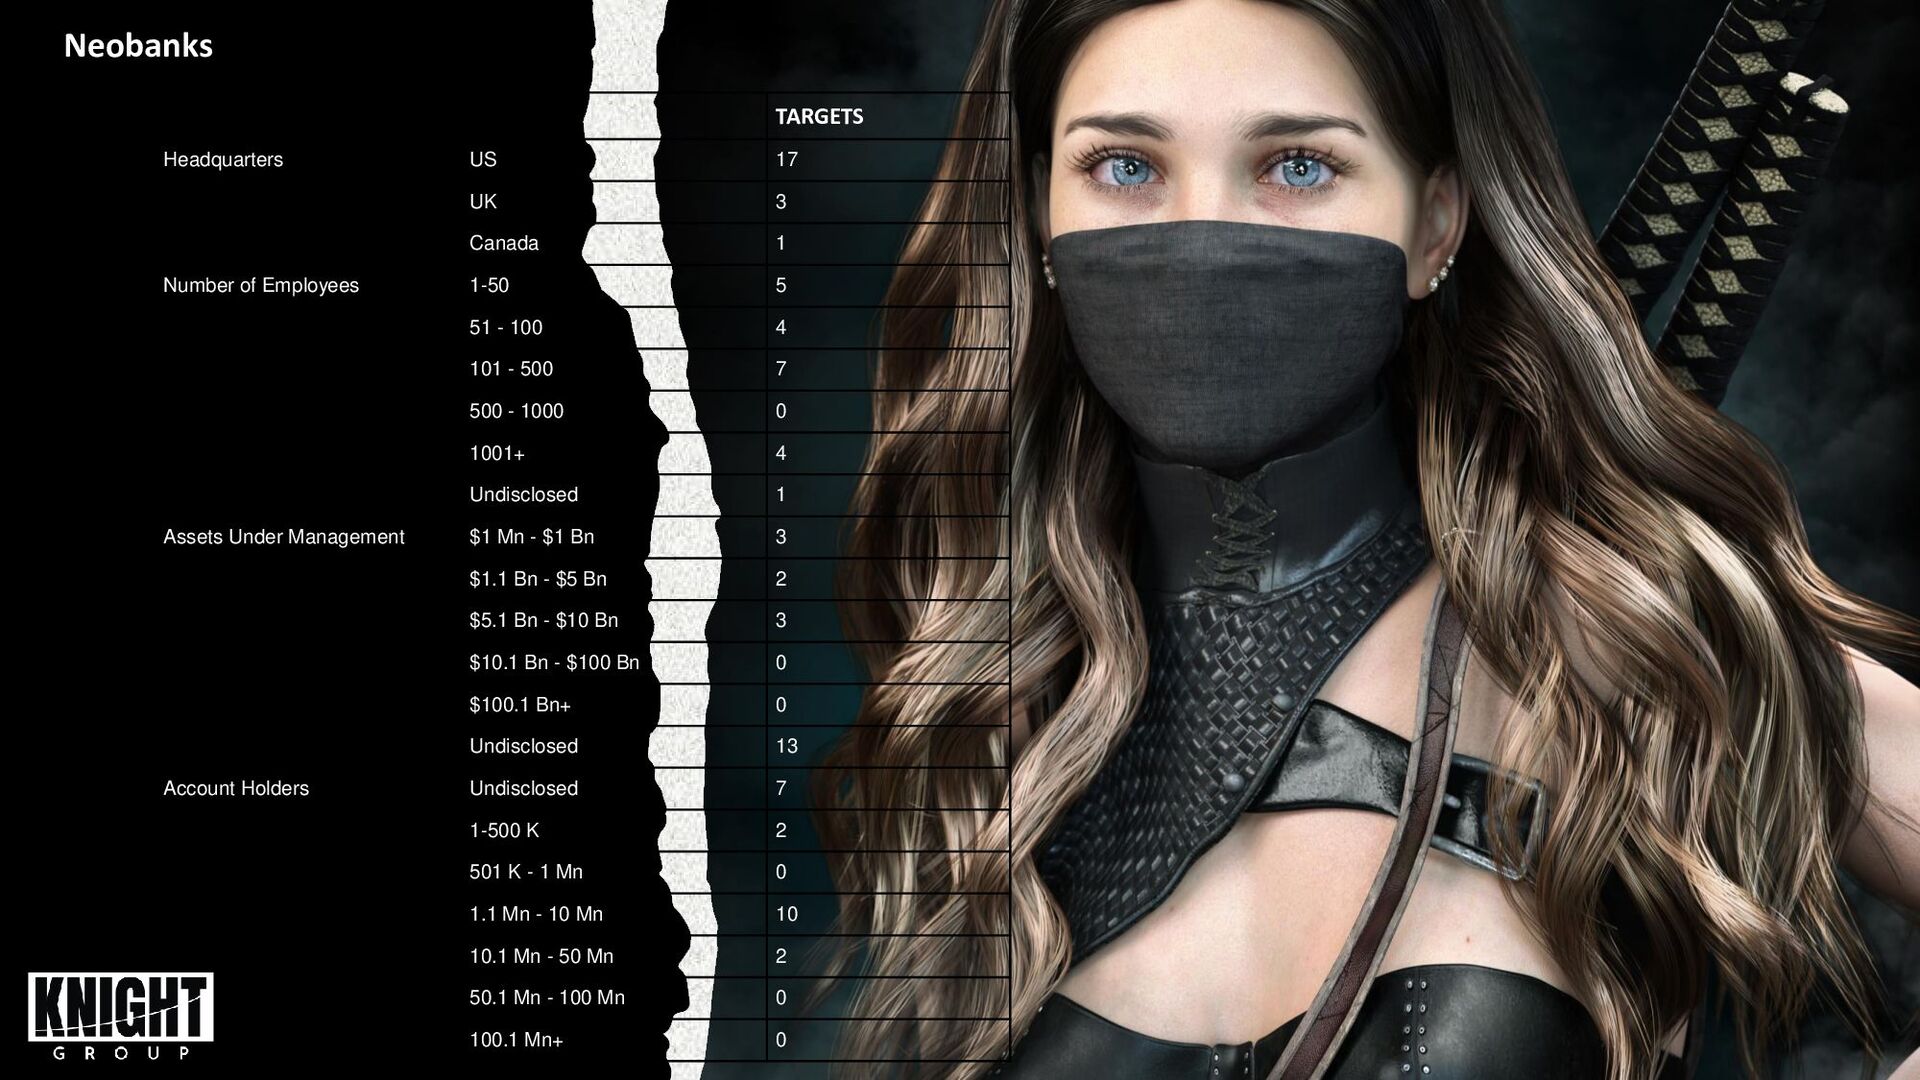
  7. Neobanks TARGETS Headquarters US 17 UK 3 Canada 1 Number

    of Employees 1-50 5 51 - 100 4 101 - 500 7 500 - 1000 0 1001+ 4 Undisclosed 1 Assets Under Management $1 Mn - $1 Bn 3 $1.1 Bn - $5 Bn 2 $5.1 Bn - $10 Bn 3 $10.1 Bn - $100 Bn 0 $100.1 Bn+ 0 Undisclosed 13 Account Holders Undisclosed 7 1-500 K 2 501 K - 1 Mn 0 1.1 Mn - 10 Mn 10 10.1 Mn - 50 Mn 2 50.1 Mn - 100 Mn 0 100.1 Mn+ 0
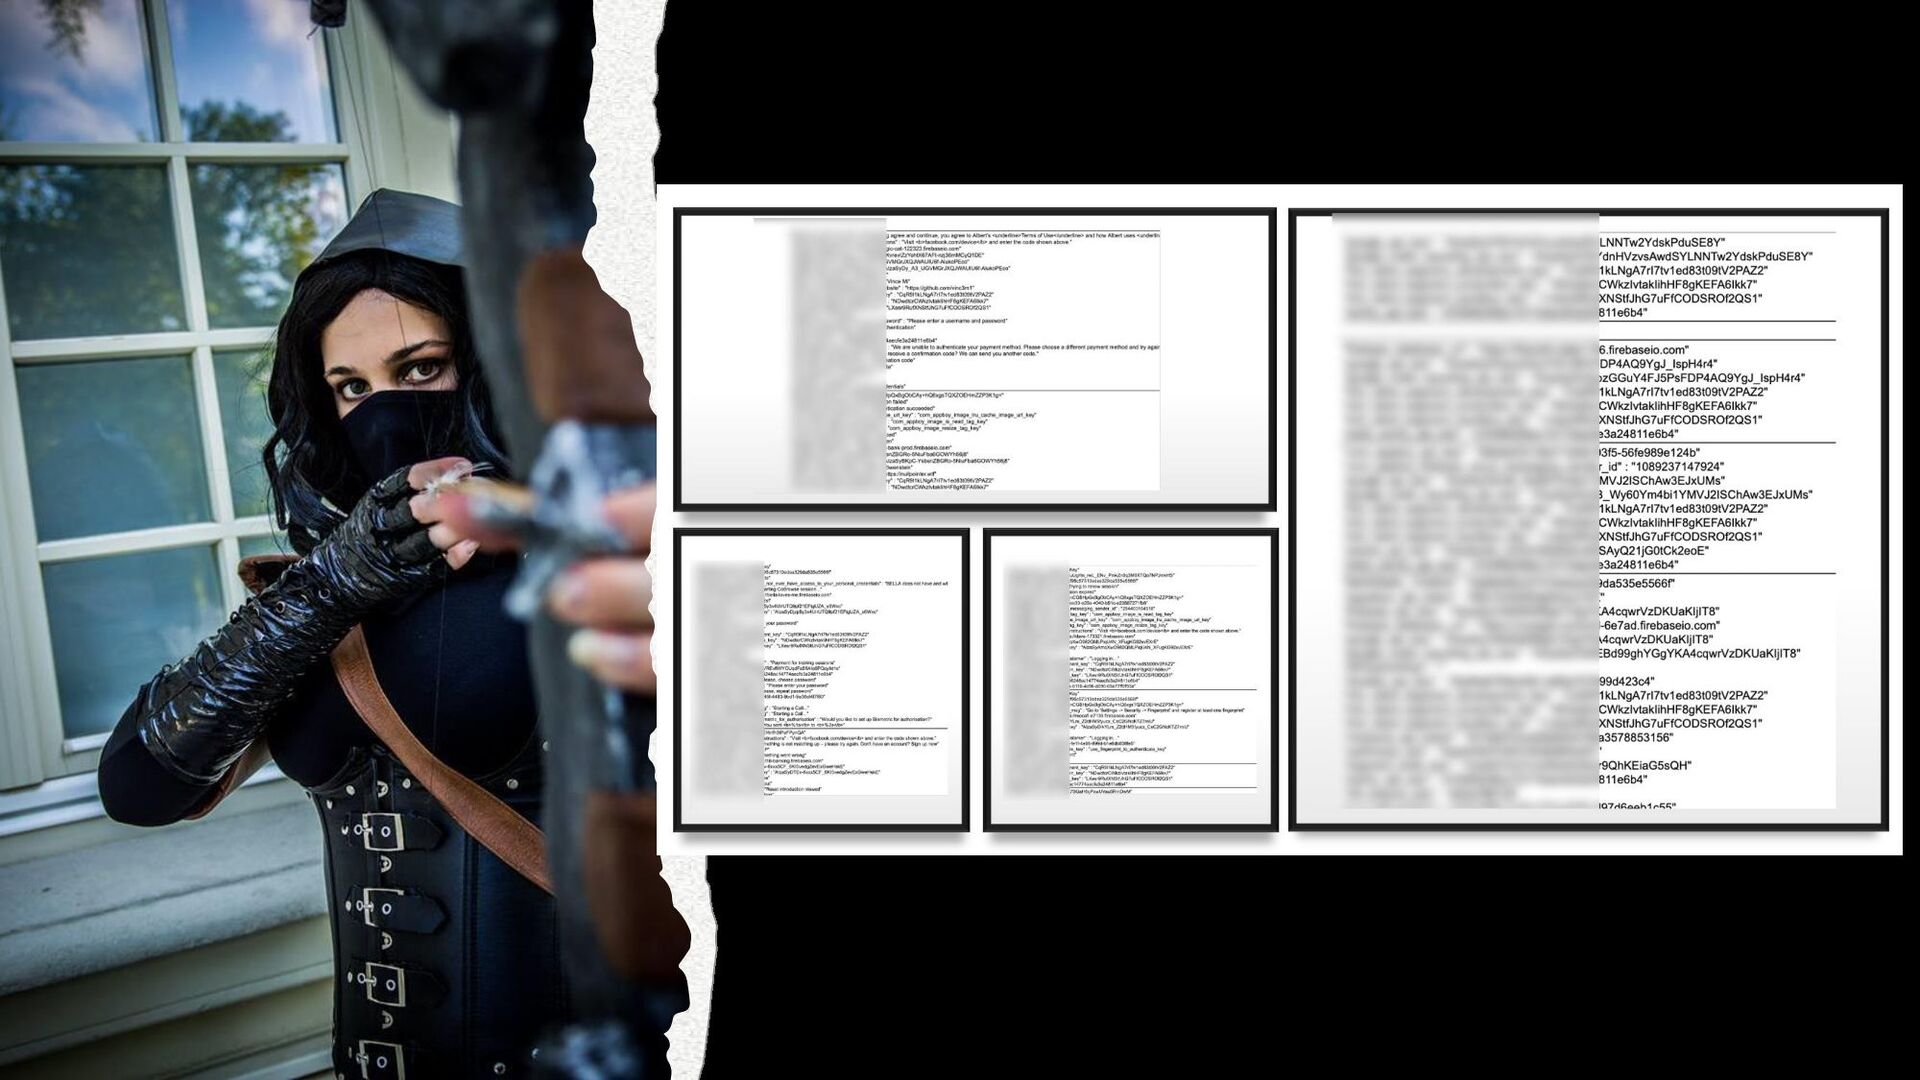
  8. "CAPTCHA_SITE_KEY" : "6Le06_kSAAAAAD8X40zsM1PgPgSYzvZ1lxZJlad6" "KRAKEN_API_URL" : "https://api.kraken.com" "KRAKEN_CF_ACCESS_CLIENT_SECRET" : "" "LAUNCHDARKLY_MOBILE_KEY"

    : "mob-e7ec4413-9481-4e01-b38f-6eb2e6d51e59" "LAUNCHDARKLY_MOBILE_KEY_DEV" : "mob-fa44a940-6ea4-4955-8753-42ebbe2a13e5" "MIXPANEL_APP_KEY" : "431a8da1ac98248fb4b0e70e308c0383" "MIXPANEL_APP_KEY_DEV" : "26fccedcffd50afc20bc4a760a7c47f3" "SIFT_BEACON_KEY" : "0f318a5903" "google_api_key" : "AIzaSyA7NYdnHVzvsAwdSYLNNTw2YdskPduSE8Y" "google_crash_reporting_api_key" : "AIzaSyA7NYdnHVzvsAwdSYLNNTw2YdskPduSE8Y" "link_client_segment_development_key" : "CqR9l1kLNgA7rI7tv1ed83t09tV2PAZ2" "link_client_segment_production_key" : "NDwdtcrCWkzIvtakIihHF8gKEFA6Ikk7" "link_client_segment_sandbox_key" : "LXesr9RufXNStfJhG7uFfCODSROf2QS1" "sentry_api_key" : "e7bf46248ac14774aecfe3a24811e6b4" "firebase_database_url" : "https://friendly-slate-746.firebaseio.com" "google_api_key" : "AIzaSyDOepzGGuY4FJ5PsFDP4AQ9YgJ_IspH4r4" "google_crash_reporting_api_key" : "AIzaSyDOepzGGuY4FJ5PsFDP4AQ9YgJ_IspH4r4" "link_client_segment_development_key" : "CqR9l1kLNgA7rI7tv1ed83t09tV2PAZ2" "link_client_segment_production_key" : "NDwdtcrCWkzIvtakIihHF8gKEFA6Ikk7" "link_client_segment_sandbox_key" : "LXesr9RufXNStfJhG7uFfCODSROf2QS1" "plaid_sentry_api_key" : "e7bf46248ac14774aecfe3a24811e6b4" "com_appboy_api_key" : "28a5a033-3be7-4e8d-93f5-56fe989e124b" "com_appboy_firebase_cloud_messaging_sender_id" : "1089237147924" "google_api_key" : "AIzaSyDGJB_Wy60Ym4bi1YMVJ2ISChAw3EJxUMs" "google_crash_reporting_api_key" : "AIzaSyDGJB_Wy60Ym4bi1YMVJ2ISChAw3EJxUMs" "link_client_segment_development_key" : "CqR9l1kLNgA7rI7tv1ed83t09tV2PAZ2" "link_client_segment_production_key" : "NDwdtcrCWkzIvtakIihHF8gKEFA6Ikk7" "link_client_segment_sandbox_key" : "LXesr9RufXNStfJhG7uFfCODSROf2QS1" "places_api_key" : "AIzaSyAb_vQ7jOd626GkxaRSAyQ21jG0tCk2eoE" "plaid_sentry_api_key" : "e7bf46248ac14774aecfe3a24811e6b4" "MIXPANEL_TOKEN" : "3a89bf95c57310edea329da535e5566f" "appsflyer_api_token" : "iN9vYkX6Z9njjNAavLfVK" "firebase_api_key" : "AIzaSyCN4EBd99ghYGgYKA4cqwrVzDKUaKIjIT8" "firebase_database_url" : "https://voyager-android-6e7ad.firebaseio.com" "google_api_key" : "AIzaSyCN4EBd99ghYGgYKA4cqwrVzDKUaKIjIT8" "google_crash_reporting_api_key" : "AIzaSyCN4EBd99ghYGgYKA4cqwrVzDKUaKIjIT8" "idPlusAuthKey" : "" "iterable_api_key" : "32af4a678fab48c1a65a757699d423c4" "link_client_segment_development_key" : "CqR9l1kLNgA7rI7tv1ed83t09tV2PAZ2" "link_client_segment_production_key" : "NDwdtcrCWkzIvtakIihHF8gKEFA6Ikk7" "link_client_segment_sandbox_key" : "LXesr9RufXNStfJhG7uFfCODSROf2QS1" "mixpanel_api_token" : "67c9e07eca2fb6940476fa3578853156" "optimizely_key" : "SaaXGkHf1MVh3K9DBRwRV" "segment_write_key" : "howE47zj1h1sG5wScNmr9QhKEiaG5sQH" "sentry_api_key" : "e7bf46248ac14774aecfe3a24811e6b4" "sift_beacon_key" : "a63a7867c8" "socurePublicKey" : "d0532f88-2146-472e-9292-d97d6eeb1c55" REDCATED
  9. What I learned from robbing banks • Despite it being

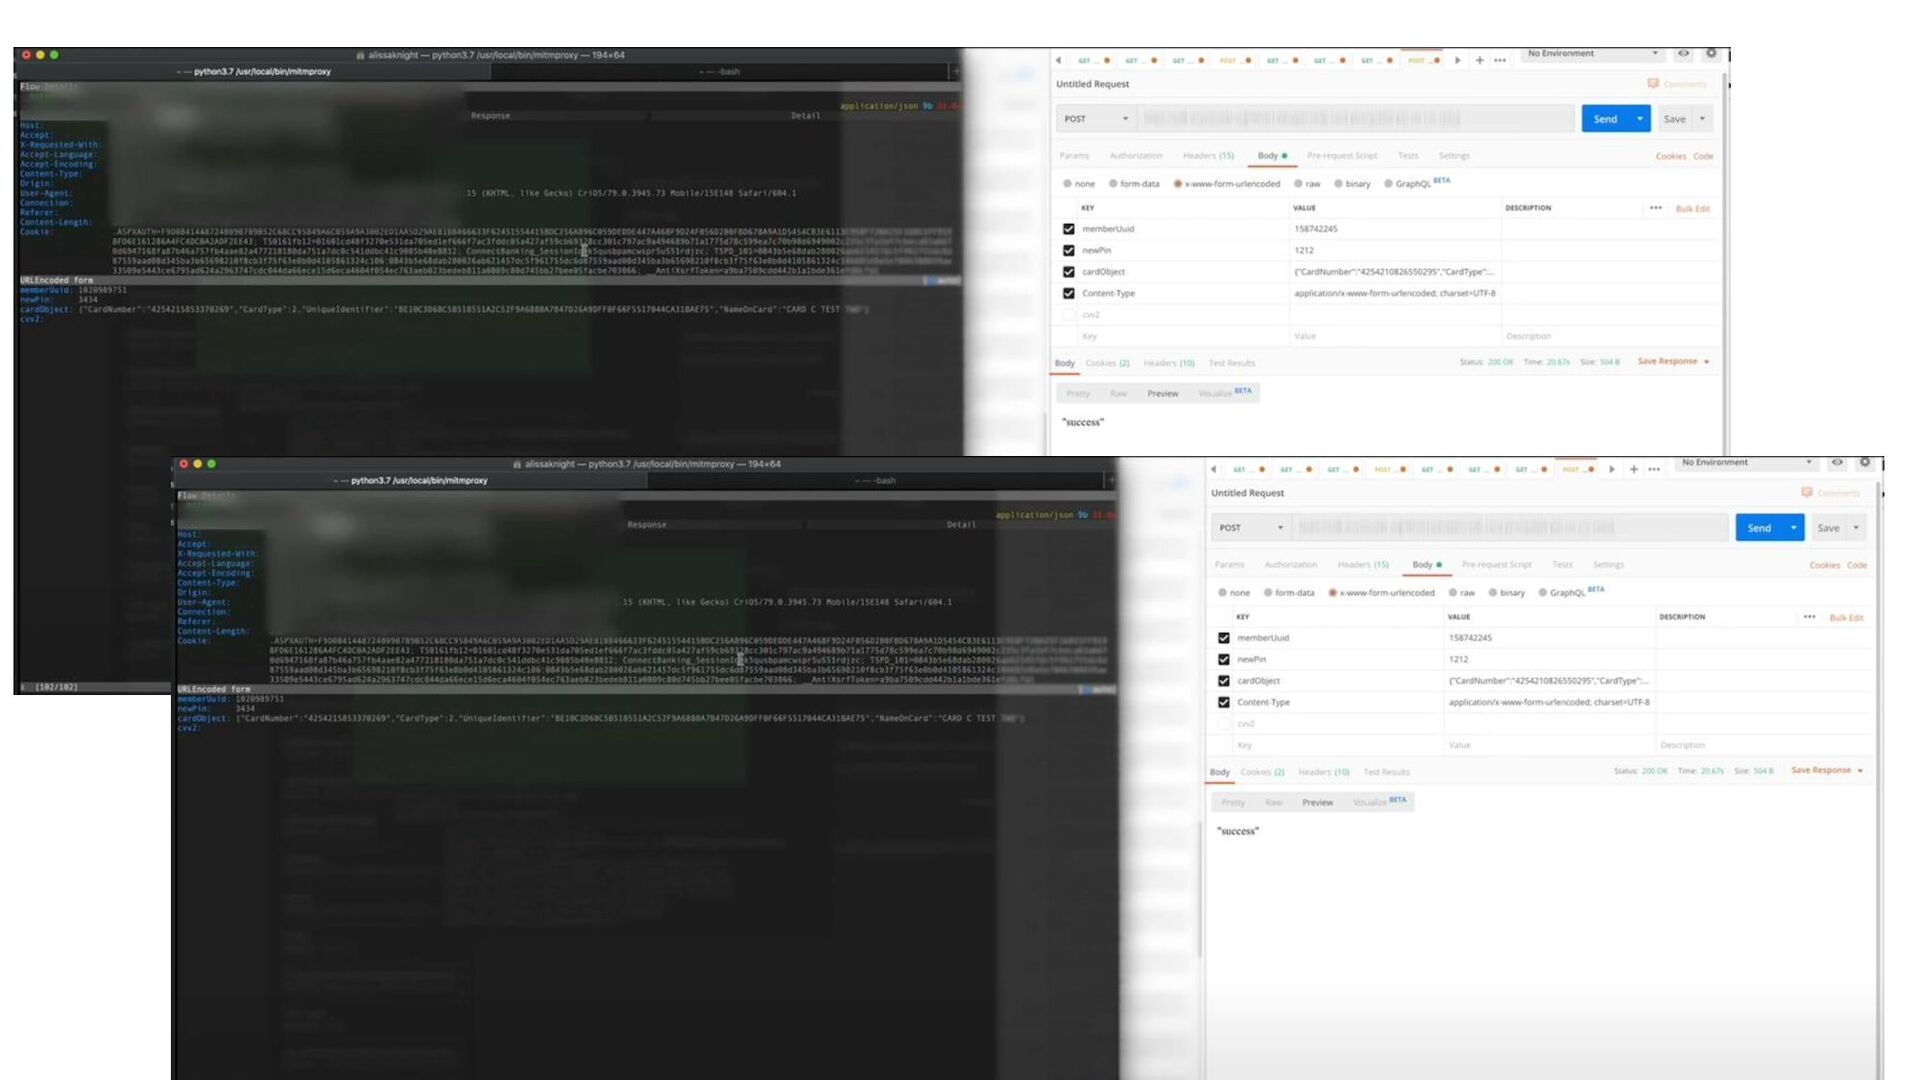
    2021, developers are still not authorizing authenticated API requests (and it’s systemic) • Organizations are not maintaining asset catalogues of their APIs: You can’t protect what you don’t know you have • There is still no context in security: Organizations are still using WAFs to secure APIs, which are incapable of detecting logic attacks against applications • Many companies are “transferring” their risk when outsourcing. Because one of the banks outsourced their API development, the vulnerability affected 300 other banks where the code was reused. • No penetration testing!

More Decks by FOST, powered by apidays

Other Decks in Programming