Share
Embed
ICS Threat: Triton Malware
This presentation talks about the Industrial Control System threat with a focus of Triton malware that targeted SIS Schneider Triconex.

Thomas Roccia
September 10, 2018
Transcript
31 slides
-
The Next Generation of ICS Malware Overview of Triton Thomas
ROCCIA Security Researcher, Advanced Threat Research -
2 CNES COMET SSI - Thomas Roccia – 2018 Whoami
Thomas ROCCIA Security Researcher, Advanced Threat Research @fr0gger_ https://securingtomorrow.mcafee.com/author/thomas-roccia/ http://troccia.tdgt.org Disclaimer: all the research presented are based on the public and internal information collected by the actors who were engaged during the investigation. A combined investigation and collaboration within the following actors: The FBI, NCCIC, Schneider Electric, McAfee, FireEye, DragosInc, Nozomi, Cyberx… -
3 CNES COMET SSI - Thomas Roccia – 2018 Agenda
• Brief ICS Malware History • Safety Instrumented System (SIS) • TRITON Attack Overview • Detection Demo • About the Attackers • Take Away -
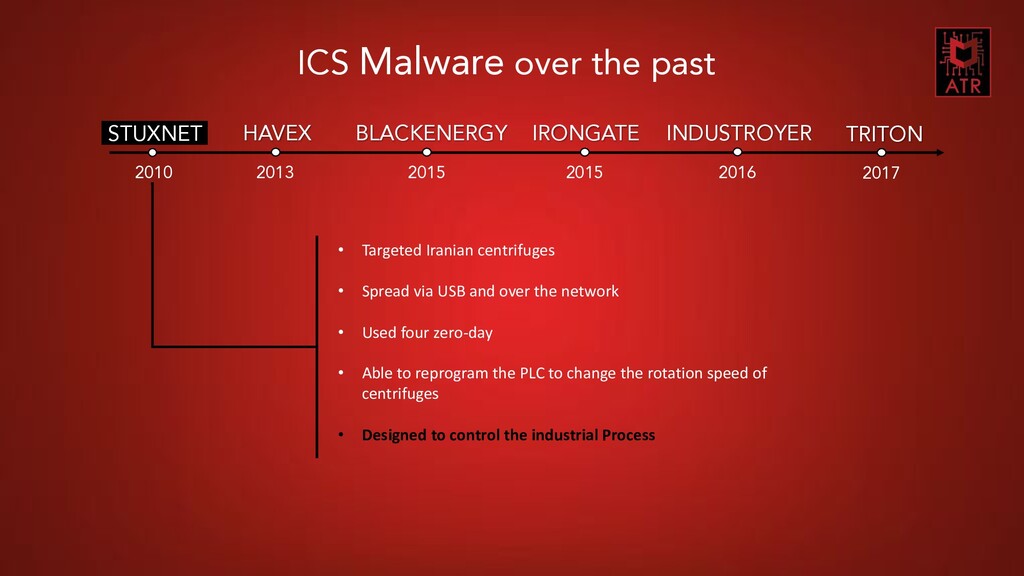
4 CNES COMET SSI - Thomas Roccia – 2018 STUXNET
2010 HAVEX 2013 BLACKENERGY 2015 IRONGATE 2015 INDUSTROYER 2016 TRITON 2017 ICS Malware over the past -
5 CNES COMET SSI - Thomas Roccia – 2018 STUXNET
2010 HAVEX 2013 BLACKENERGY 2015 IRONGATE 2015 INDUSTROYER 2016 TRITON 2017 ICS Malware over the past • Targeted Iranian centrifuges • Spread via USB and over the network • Used four zero-day • Able to reprogram the PLC to change the rotation speed of centrifuges • Designed to control the industrial Process -
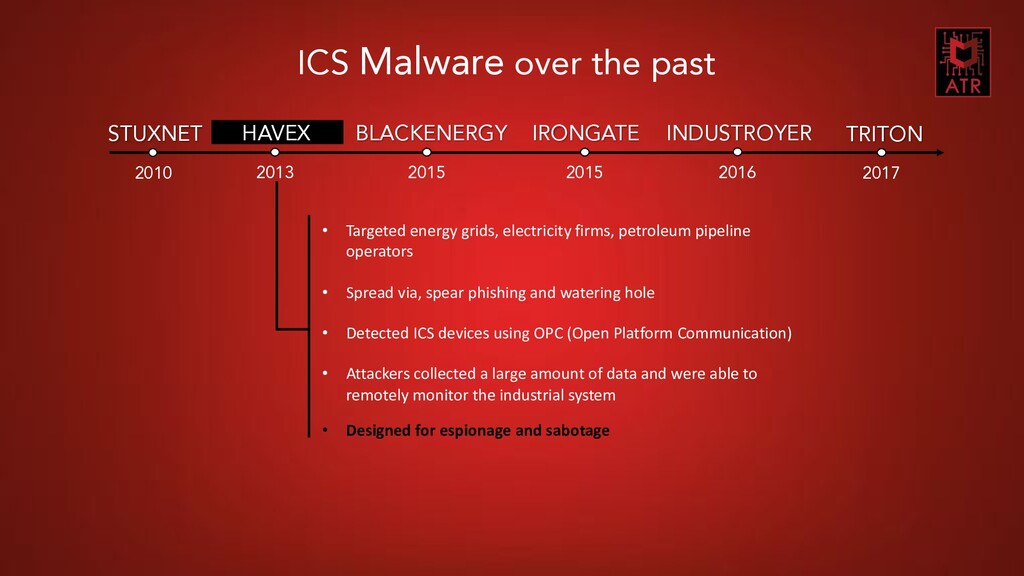
6 CNES COMET SSI - Thomas Roccia – 2018 2010
STUXNET HAVEX 2013 BLACKENERGY 2015 IRONGATE 2015 INDUSTROYER 2016 TRITON 2017 ICS Malware over the past • Targeted energy grids, electricity firms, petroleum pipeline operators • Spread via, spear phishing and watering hole • Detected ICS devices using OPC (Open Platform Communication) • Attackers collected a large amount of data and were able to remotely monitor the industrial system • Designed for espionage and sabotage -
7 CNES COMET SSI - Thomas Roccia – 2018 STUXNET
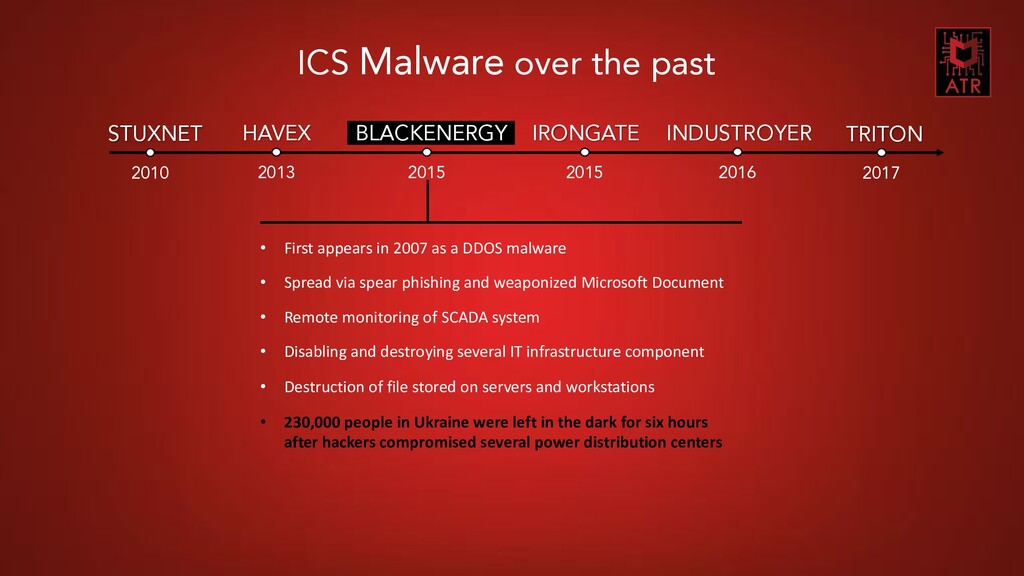
2010 HAVEX 2013 BLACKENERGY 2015 IRONGATE 2015 INDUSTROYER 2016 TRITON 2017 ICS Malware over the past • First appears in 2007 as a DDOS malware • Spread via spear phishing and weaponized Microsoft Document • Remote monitoring of SCADA system • Disabling and destroying several IT infrastructure component • Destruction of file stored on servers and workstations • 230,000 people in Ukraine were left in the dark for six hours after hackers compromised several power distribution centers -
8 CNES COMET SSI - Thomas Roccia – 2018 STUXNET
2010 HAVEX 2013 IRONGATE 2015 INDUSTROYER 2016 TRITON 2017 ICS Malware over the past • The malware targets a simulated Siemens control system environment • Stuxnet-like behavior • Includes evasion mechanisms (anti-vm, antiav…) • Mostly written in Python • Probably a penetration tool or a Proof of concept BLACKENERGY 2015 -
9 CNES COMET SSI - Thomas Roccia – 2018 STUXNET
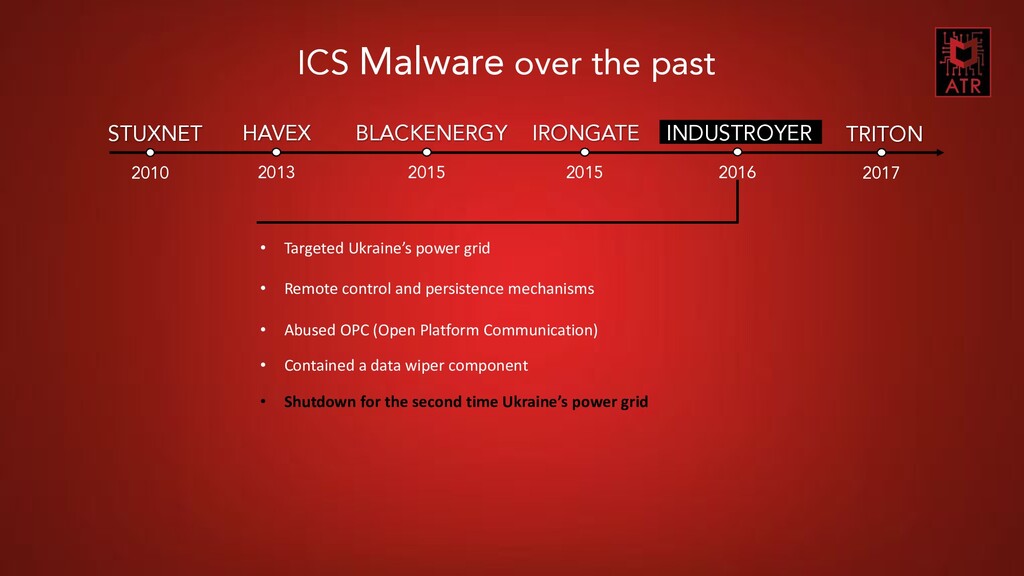
2010 HAVEX 2013 INDUSTROYER 2016 TRITON 2017 ICS Malware over the past • Targeted Ukraine’s power grid • Remote control and persistence mechanisms • Abused OPC (Open Platform Communication) • Contained a data wiper component • Shutdown for the second time Ukraine’s power grid IRONGATE 2015 BLACKENERGY 2015 -
10 CNES COMET SSI - Thomas Roccia – 2018 STUXNET
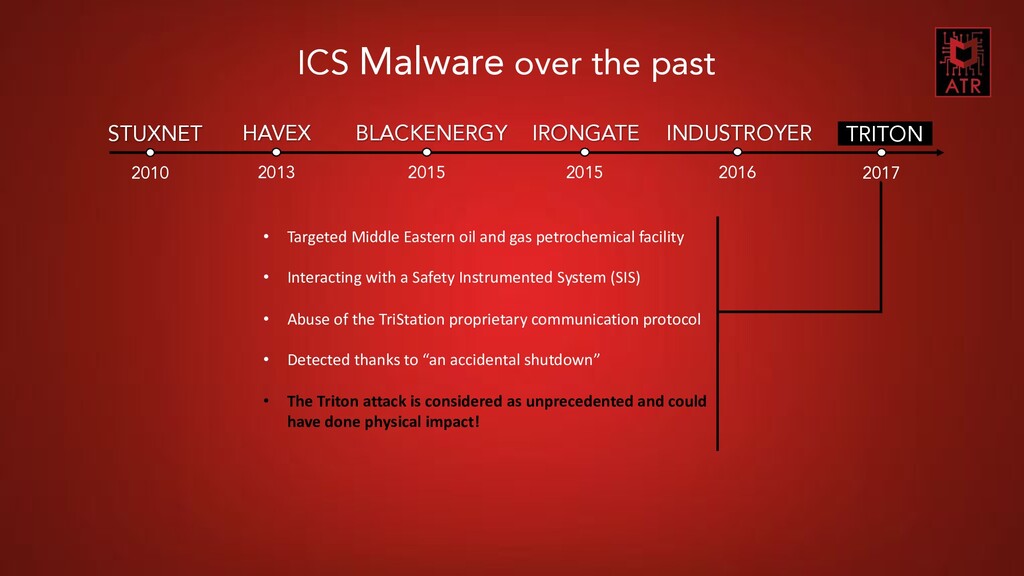
2010 HAVEX 2013 TRITON 2017 • Targeted Middle Eastern oil and gas petrochemical facility • Interacting with a Safety Instrumented System (SIS) • Abuse of the TriStation proprietary communication protocol • Detected thanks to “an accidental shutdown” • The Triton attack is considered as unprecedented and could have done physical impact! BLACKENERGY 2015 IRONGATE 2015 INDUSTROYER 2016 ICS Malware over the past -
11 CNES COMET SSI - Thomas Roccia – 2018 STUXNET
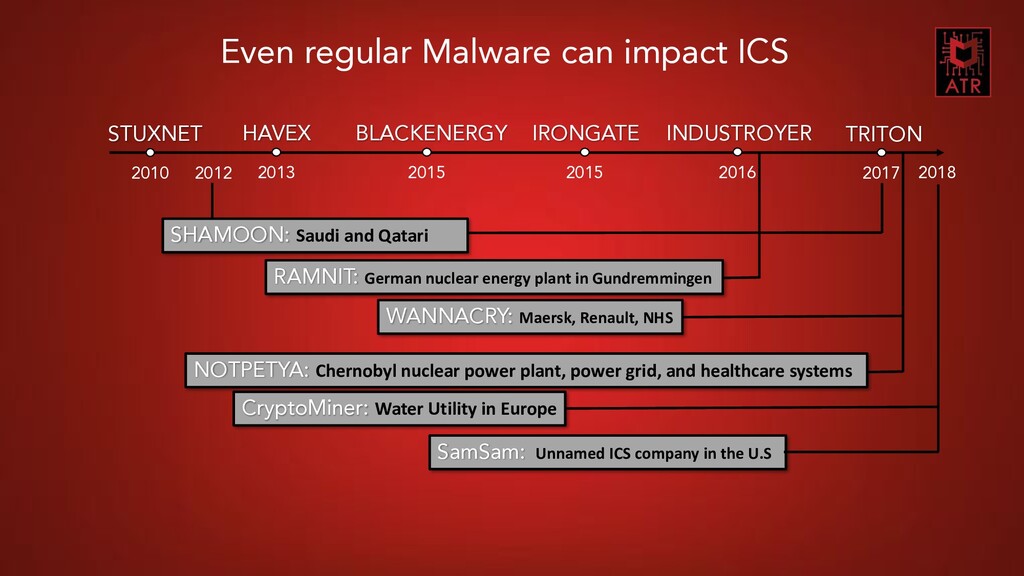
2010 HAVEX 2013 TRITON 2017 BLACKENERGY 2015 IRONGATE 2015 INDUSTROYER 2016 Even regular Malware can impact ICS WANNACRY: Maersk, Renault, NHS SamSam: Unnamed ICS company in the U.S NOTPETYA: Chernobyl nuclear power plant, power grid, and healthcare systems RAMNIT: German nuclear energy plant in Gundremmingen SHAMOON: Saudi and Qatari 2012 CryptoMiner: Water Utility in Europe 2018 -
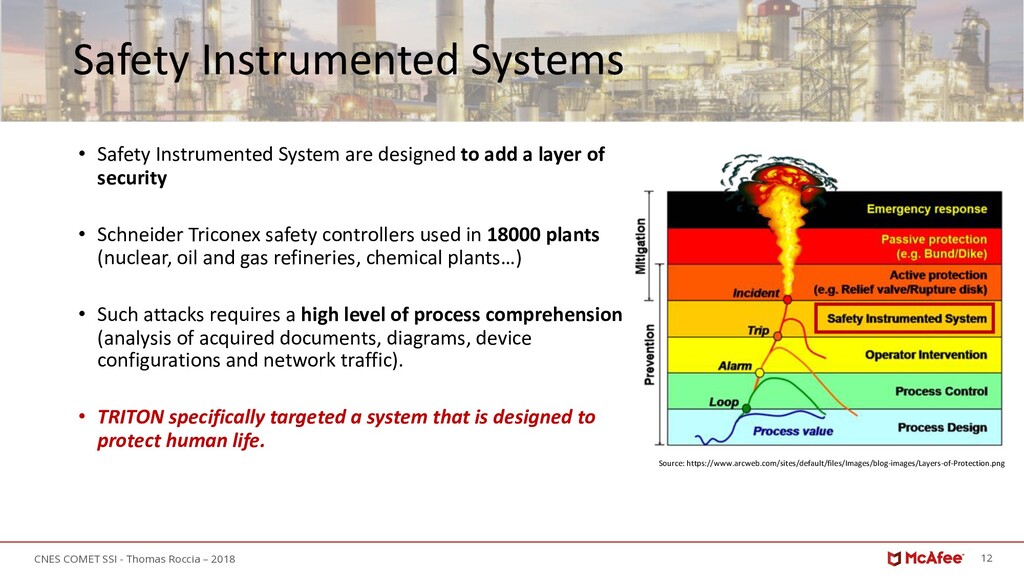
12 CNES COMET SSI - Thomas Roccia – 2018 Safety
Instrumented Systems • Safety Instrumented System are designed to add a layer of security • Schneider Triconex safety controllers used in 18000 plants (nuclear, oil and gas refineries, chemical plants…) • Such attacks requires a high level of process comprehension (analysis of acquired documents, diagrams, device configurations and network traffic). • TRITON specifically targeted a system that is designed to protect human life. Source: https://www.arcweb.com/sites/default/files/Images/blog-images/Layers-of-Protection.png -
13 CNES COMET SSI - Thomas Roccia – 2018 Attackers
Collected Many Information -
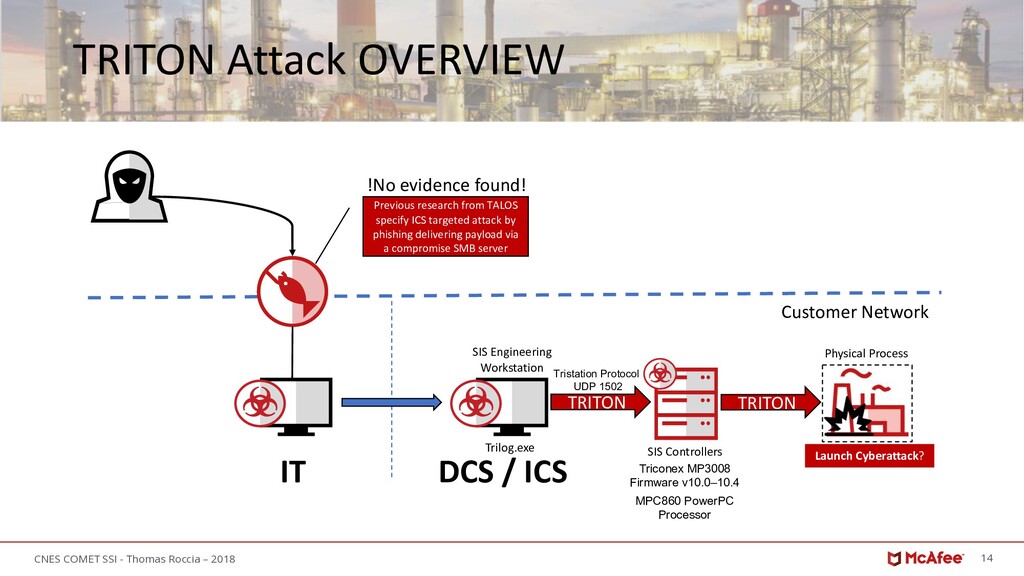
14 CNES COMET SSI - Thomas Roccia – 2018 TRITON
Attack OVERVIEW Customer Network Previous research from TALOS specify ICS targeted attack by phishing delivering payload via a compromise SMB server !No evidence found! IT DCS / ICS TRITON SIS Controllers SIS Engineering Workstation Physical Process TRITON Launch Cyberattack? Trilog.exe Triconex MP3008 Firmware v10.0–10.4 MPC860 PowerPC Processor Tristation Protocol UDP 1502 -
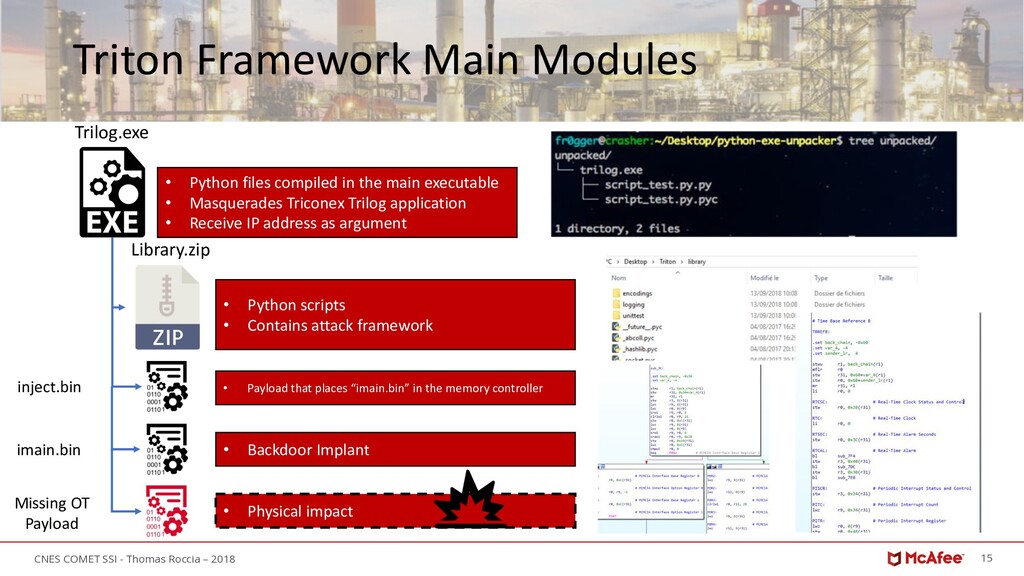
15 CNES COMET SSI - Thomas Roccia – 2018 Triton
Framework Main Modules Trilog.exe • Python files compiled in the main executable • Masquerades Triconex Trilog application • Receive IP address as argument • Python scripts • Contains attack framework Library.zip • Payload that places “imain.bin” in the memory controller inject.bin imain.bin • Backdoor Implant Missing OT Payload • Physical impact -
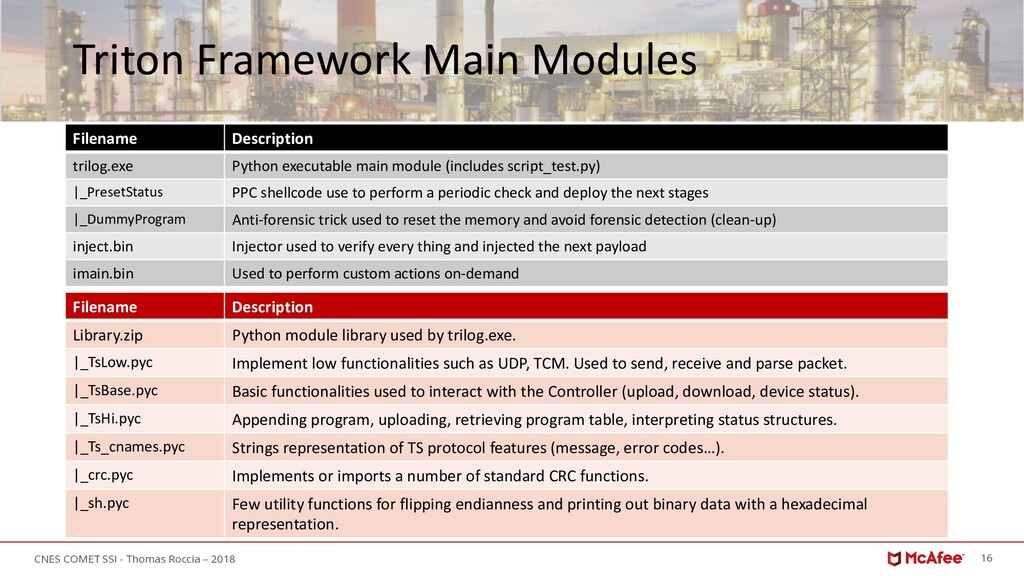
16 CNES COMET SSI - Thomas Roccia – 2018 Triton
Framework Main Modules Filename Description trilog.exe Python executable main module (includes script_test.py) |_PresetStatus PPC shellcode use to perform a periodic check and deploy the next stages |_DummyProgram Anti-forensic trick used to reset the memory and avoid forensic detection (clean-up) inject.bin Injector used to verify every thing and injected the next payload imain.bin Used to perform custom actions on-demand Filename Description Library.zip Python module library used by trilog.exe. |_TsLow.pyc Implement low functionalities such as UDP, TCM. Used to send, receive and parse packet. |_TsBase.pyc Basic functionalities used to interact with the Controller (upload, download, device status). |_TsHi.pyc Appending program, uploading, retrieving program table, interpreting status structures. |_Ts_cnames.pyc Strings representation of TS protocol features (message, error codes…). |_crc.pyc Implements or imports a number of standard CRC functions. |_sh.pyc Few utility functions for flipping endianness and printing out binary data with a hexadecimal representation. -
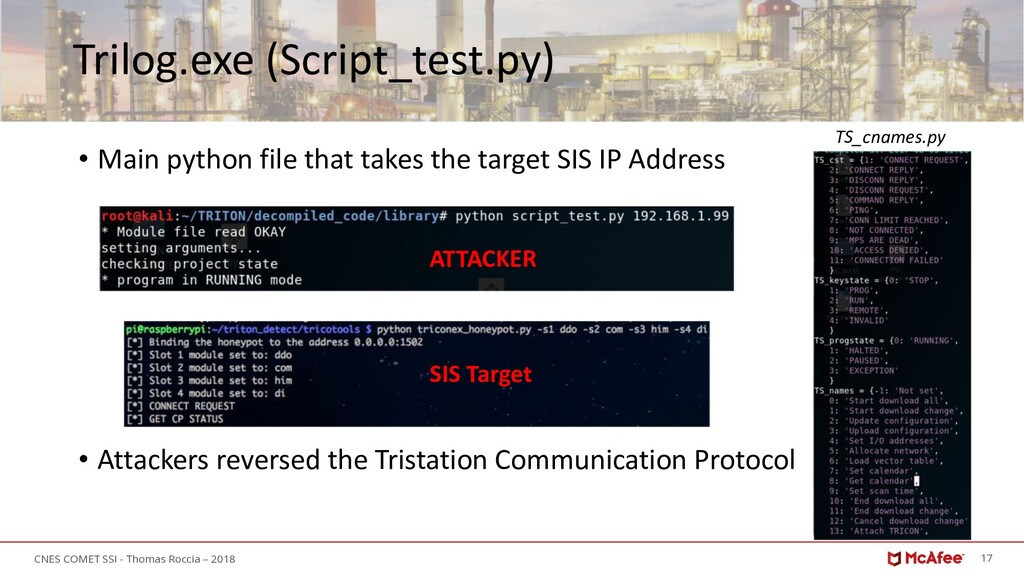
17 CNES COMET SSI - Thomas Roccia – 2018 Trilog.exe
(Script_test.py) • Main python file that takes the target SIS IP Address • Attackers reversed the Tristation Communication Protocol ATTACKER SIS Target TS_cnames.py -
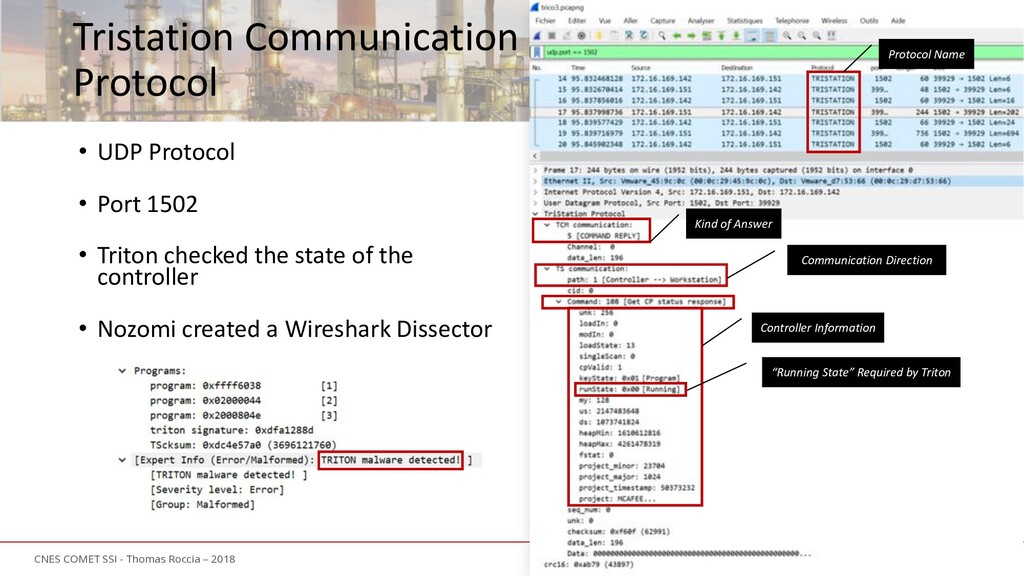
18 CNES COMET SSI - Thomas Roccia – 2018 Tristation
Communication Protocol • UDP Protocol • Port 1502 • Triton checked the state of the controller • Nozomi created a Wireshark Dissector Protocol Name Kind of Answer Communication Direction Controller Information “Running State” Required by Triton -
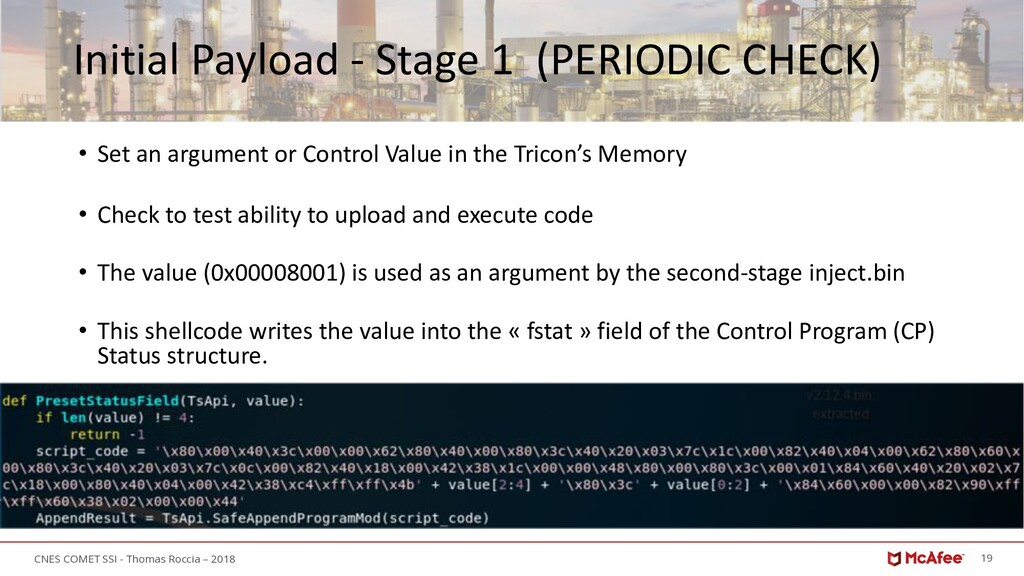
19 CNES COMET SSI - Thomas Roccia – 2018 Initial
Payload - Stage 1 (PERIODIC CHECK) • Set an argument or Control Value in the Tricon’s Memory • Check to test ability to upload and execute code • The value (0x00008001) is used as an argument by the second-stage inject.bin • This shellcode writes the value into the « fstat » field of the Control Program (CP) Status structure. -
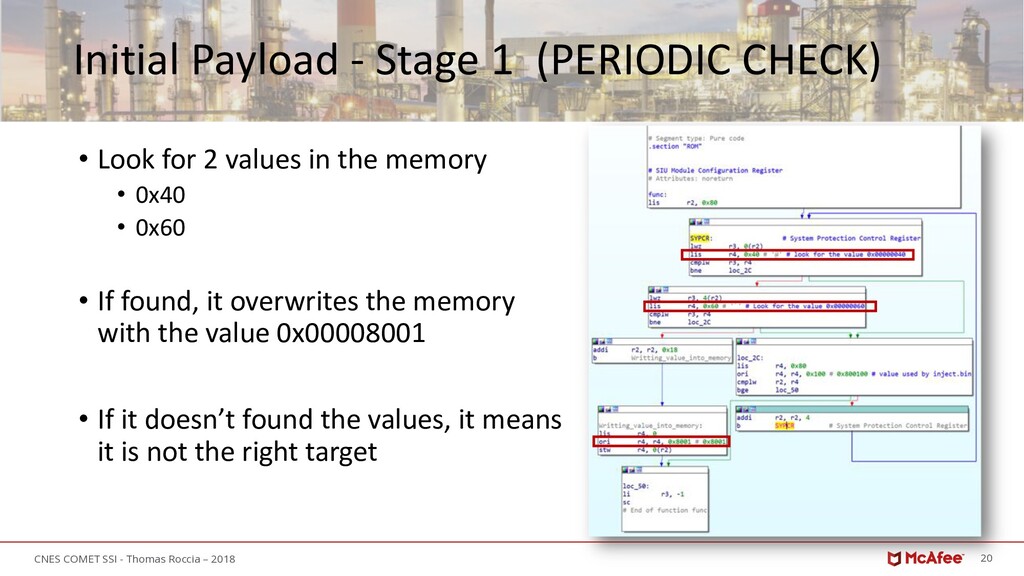
20 CNES COMET SSI - Thomas Roccia – 2018 Initial
Payload - Stage 1 (PERIODIC CHECK) • Look for 2 values in the memory • 0x40 • 0x60 • If found, it overwrites the memory with the value 0x00008001 • If it doesn’t found the values, it means it is not the right target -
21 CNES COMET SSI - Thomas Roccia – 2018 Implant
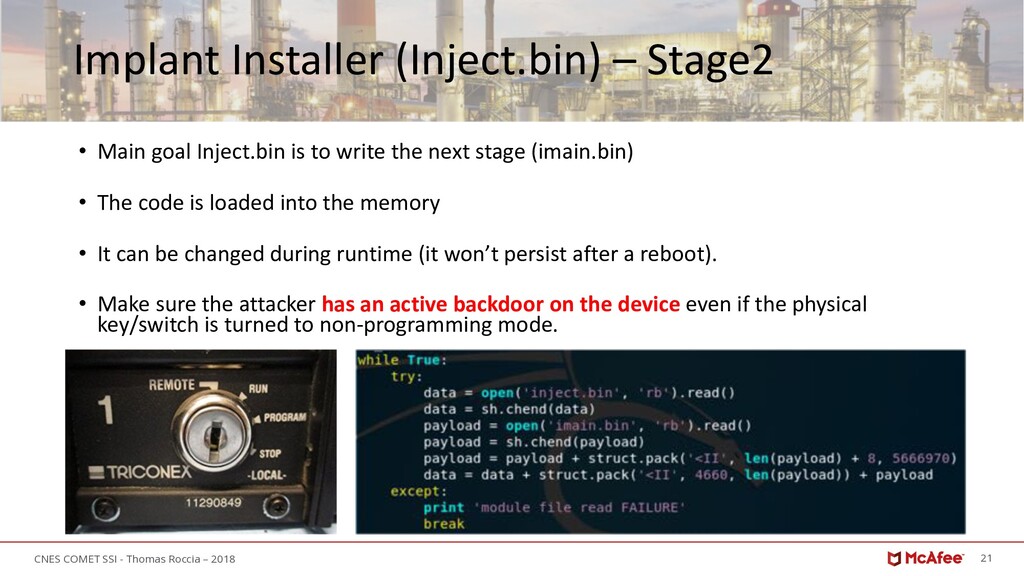
Installer (Inject.bin) – Stage2 • Main goal Inject.bin is to write the next stage (imain.bin) • The code is loaded into the memory • It can be changed during runtime (it won’t persist after a reboot). • Make sure the attacker has an active backdoor on the device even if the physical key/switch is turned to non-programming mode. -
22 CNES COMET SSI - Thomas Roccia – 2018 Implant
Installer (Inject.bin) – Stage2 • Inject.bin assumes the argument written by the first stage payload resides at a static address and uses it as: 1. A countdown for the number of cycles to idle 2. A step counter to track and control execution progress 3. A field for writing debug information upon failure. • Attackers monitor inject.bin for problems. • If no problems are detected, the stage 3 is injected and 'Script SUCCESS' is output. • If an exception occured a dummy program containing nothing but a system_call (-1) is appended. -
23 CNES COMET SSI - Thomas Roccia – 2018 Backdoor
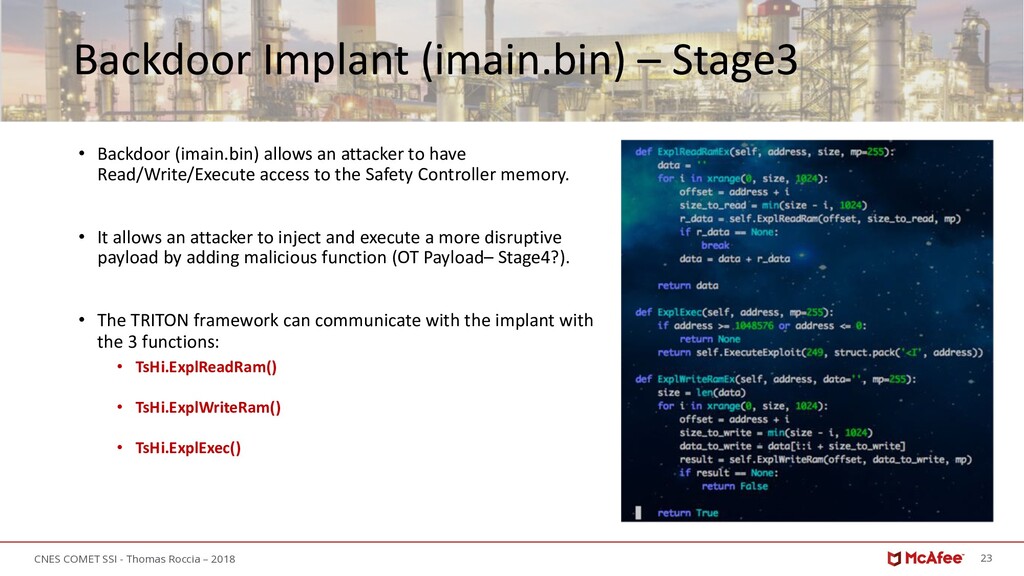
Implant (imain.bin) – Stage3 • Backdoor (imain.bin) allows an attacker to have Read/Write/Execute access to the Safety Controller memory. • It allows an attacker to inject and execute a more disruptive payload by adding malicious function (OT Payload– Stage4?). • The TRITON framework can communicate with the implant with the 3 functions: • TsHi.ExplReadRam() • TsHi.ExplWriteRam() • TsHi.ExplExec() -
24 CNES COMET SSI - Thomas Roccia – 2018 Backdoor
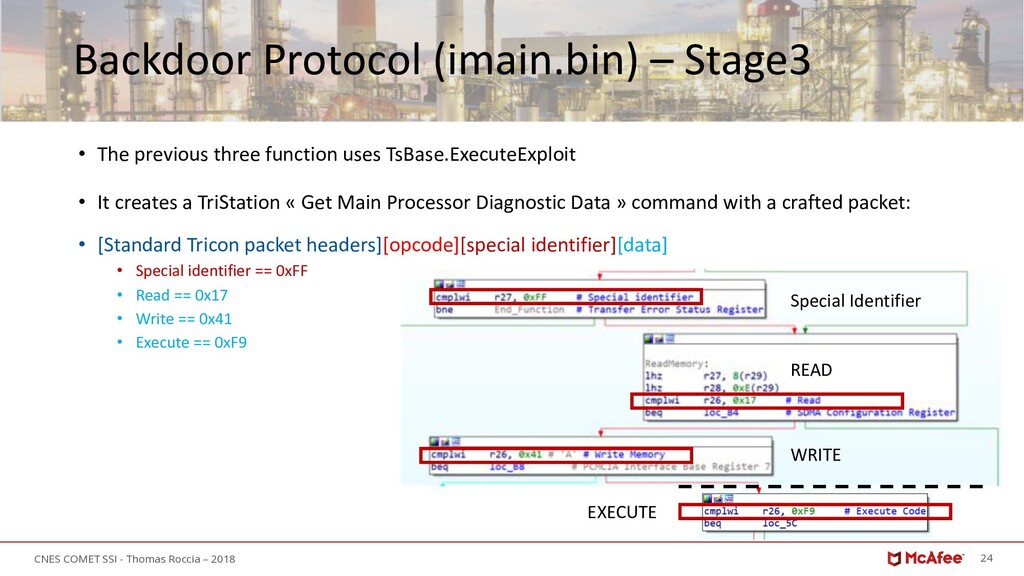
Protocol (imain.bin) – Stage3 • The previous three function uses TsBase.ExecuteExploit • It creates a TriStation « Get Main Processor Diagnostic Data » command with a crafted packet: • [Standard Tricon packet headers][opcode][special identifier][data] • Special identifier == 0xFF • Read == 0x17 • Write == 0x41 • Execute == 0xF9 Special Identifier READ WRITE EXECUTE -
25 CNES COMET SSI - Thomas Roccia – 2018 OT
Payload (missing) – Stage 4 • Fourth stage payload (OT Payload) wasn’t recovered • All the investigation specified that the attack has been detected before a cyber- physical damage scenario -
26 CNES COMET SSI - Thomas Roccia – 2018 Demo
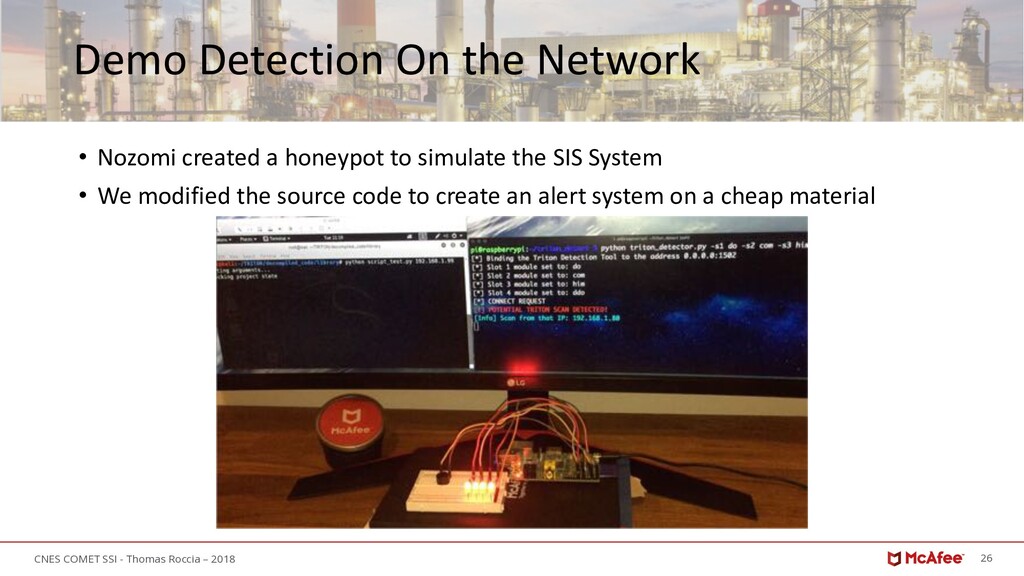
Detection On the Network • Nozomi created a honeypot to simulate the SIS System • We modified the source code to create an alert system on a cheap material -
27 CNES COMET SSI - Thomas Roccia – 2018 About
the Attackers • The sophistication of the attack and the resources needed could indicate the attackers had high budget to conduct it. • External sources point to different direction. • However attribution is not something easy and can lead to false conclusion. • It is still currently unclear where the attackers comes from… • And what was the end goal (disruption or destruction?) • One thing is sure, attackers are gaining more experience and increased their arsenal! -
28 CNES COMET SSI - Thomas Roccia – 2018 Lesson
Learned / Takeaways • Devices « insecure by design » have been exposed to hyper-connected environments they were not quite designed for. • There is a lack of basic IT/OT security hygiene and early warning insights • The same technique can be used against other ICS systems/OT vendors. • Kudos to Schneider Electric to share the incident and detail about the investigation and take the appropriate actions (creating a new way to detect such attacks). -
29 CNES COMET SSI - Thomas Roccia – 2018 References
• https://blog.schneider-electric.com/cyber-security/2018/08/07/one-year-after-triton-building-ongoing-industry-wide- cyber-resilience/ • https://www.youtube.com/watch?v=f09E75bWvkk • https://ics-cert.us-cert.gov/sites/default/files/ICSJWG-Archive/QNL_DEC_17/Waterfall_top-20-attacks-article-d2%20- %20Article_S508NC.pdf • https://www.fireeye.com/blog/threat-research/2017/12/attackers-deploy-new-ics-attack-framework-triton.html • https://www.midnightbluelabs.com/blog/2018/1/16/analyzing-the-triton-industrial-malware • https://www.nozominetworks.com/2018/07/18/blog/new-triton-analysis-tool-wireshark-dissector-for-tristation-protocol/ • https://cyberx-labs.com/en/blog/triton-post-mortem-analysis-latest-ot-attack-framework/ • https://vimeo.com/275906105 • https://vimeo.com/248057640 • https://blog.talosintelligence.com/2017/07/template-injection.html -
30 CNES COMET SSI - Thomas Roccia – 2018 Thank
You Thomas ROCCIA Security Researcher, Advanced Threat Research @fr0gger_ https://securingtomorrow.mcafee.com/author/thomas-roccia/ Q/A -
31 CNES COMET SSI - Thomas Roccia – 2018 McAfee,
the McAfee logo and [insert <other relevant McAfee Names>] are trademarks or registered trademarks of McAfee LLC or its subsidiaries in the U.S. and/or other countries. Other names and brands may be claimed as the property of others. Copyright © 2017 McAfee LLC. 3
 fr0gger
 henryofficial
 inariku
 eiei114
 oracle4engineer
 masu_mi
 kintotechdev
 shift_evolve
 ballas_inc
 sansantech
 falken
 smashingmag
 tapps
 ammeep
 mkilby
 tmiket
 portentint
 jct
 techseoconnect
 cassininazir
 hannesfritz
 lcolladotor
 aleyda