Share
Embed
Twitter OAuth2.0 Beta
iddance Lesson3 TwitterのOAuth 2.0とかCIBAの使い所を知ろうの会の資料です。
https://idance.connpass.com/event/226073/
kg0r0
October 27, 2021
Transcript
48 slides
-
もくじ • はじめに • OAuth2.0おさらい • Twitter OAuth2.0 Beta解説 •
Twiiter OAuth2.0 Betaのココ が気になる • おわりに 2 -
⾃⼰紹介 • 合路 健⼈ (@kg0r0) • アクセス制御関連の技術を中⼼に⾊々やっ てます • 技術同⼈サークル「Secure旅団
(第陸拾 参連隊)」で不定期活動 https://techbookfest.org/organization/ 5667545562480640 4 -
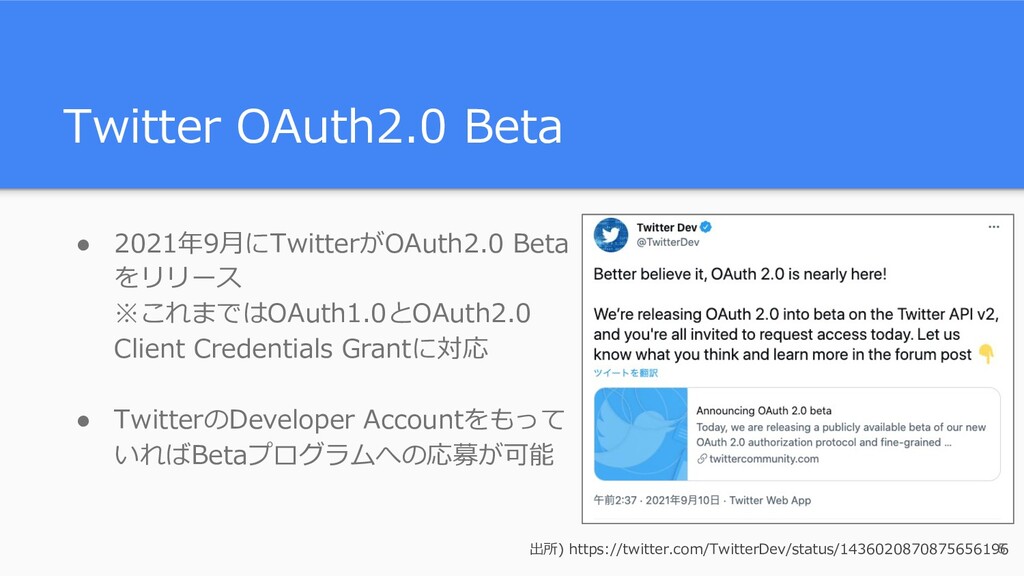
Twitter OAuth2.0 Beta • 2021年9⽉にTwitterがOAuth2.0 Beta をリリース ※これまではOAuth1.0とOAuth2.0 Client Credentials
Grantに対応 • TwitterのDeveloper Accountをもって いればBetaプログラムへの応募が可能 出所) https://twitter.com/TwitterDev/status/1436020870875656196 5 -
OAuth2.0 Client ID • Developer Portalに OAuth2.0のClient IDが 追加される •
リダイレクトURIの登録 はOAuth1.0と共通 6 -
OAuth2.0 • サードパーティーアプリケーショ ンによるHTTPサービスへの限定的 なアクセスを可能にする認可フレ ームワーク • RFC 5849に記載されている OAuth
1.0 プロトコルを廃⽌し, その代替となるもの 出所) https://openid-foundation-japan.github.io/rfc6749.ja.html 8 -
OAuth2.0 Client Type • Confidential Client クライアントシークレットの機密性を維持することができるクライアント (Webアプリケーションなど) • Public
Client クライアントシークレットの機密性を維持することができないクライアント (JavaScriptアプリやNativeアプリなど) 9 -
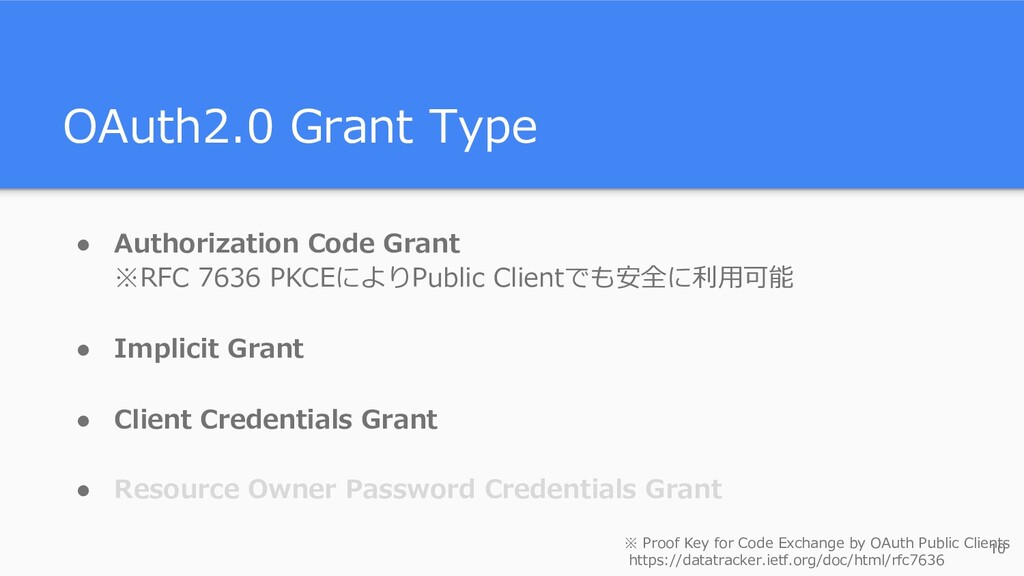
OAuth2.0 Grant Type • Authorization Code Grant ※RFC 7636 PKCEによりPublic
Clientでも安全に利⽤可能 • Implicit Grant • Client Credentials Grant • Resource Owner Password Credentials Grant ※ Proof Key for Code Exchange by OAuth Public Clients https://datatracker.ietf.org/doc/html/rfc7636 10 -
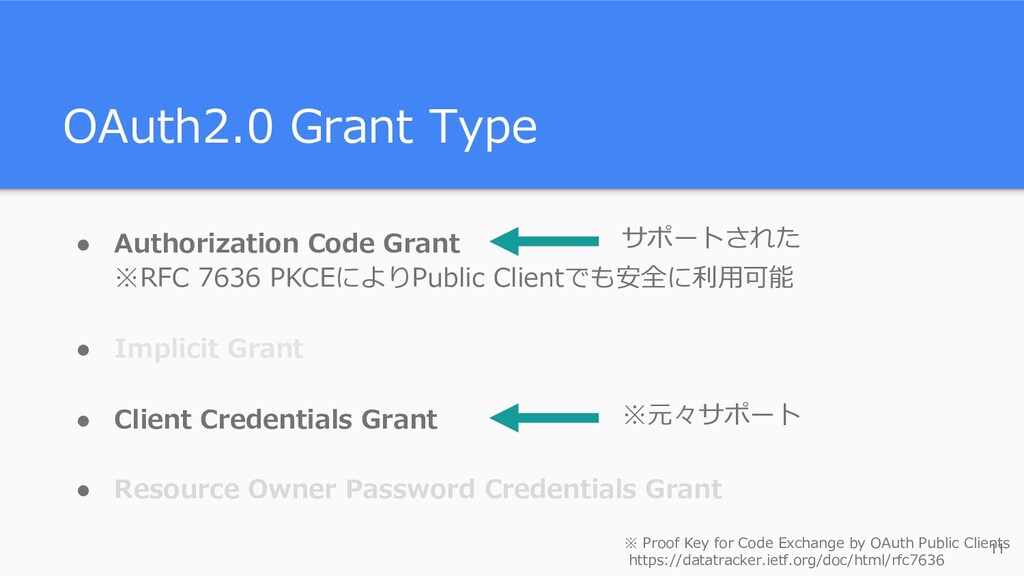
OAuth2.0 Grant Type • Authorization Code Grant ※RFC 7636 PKCEによりPublic
Clientでも安全に利⽤可能 • Implicit Grant • Client Credentials Grant • Resource Owner Password Credentials Grant サポートされた ※元々サポート ※ Proof Key for Code Exchange by OAuth Public Clients https://datatracker.ietf.org/doc/html/rfc7636 11 -
Authorization Code Flow with PKCE [1] Init Resource Owner Client
Authorization Server Resource Server [2] Redirect to Authorization Server [3]Authorization Request (code_challenge,code_challenge_method) [5] Redirect back to Client [6] Authorization Response w/ Authorization Code [7] Token Request (code_verifier) [8] Token Response [9] API Request [10] API Response [4] End-User Authentication & Consent 13 -
Authorization Code Flow with PKCE [1] Init Resource Owner Client
Authorization Server Resource Server [2] Redirect to Authorization Server [3]Authorization Request (code_challenge,code_challenge_method) [5] Redirect back to Client [6] Authorization Response w/ Authorization Code [7] Token Request (code_verifier) [8] Token Response [9] API Request [10] API Response [4] End-User Authentication & Consent 14 -
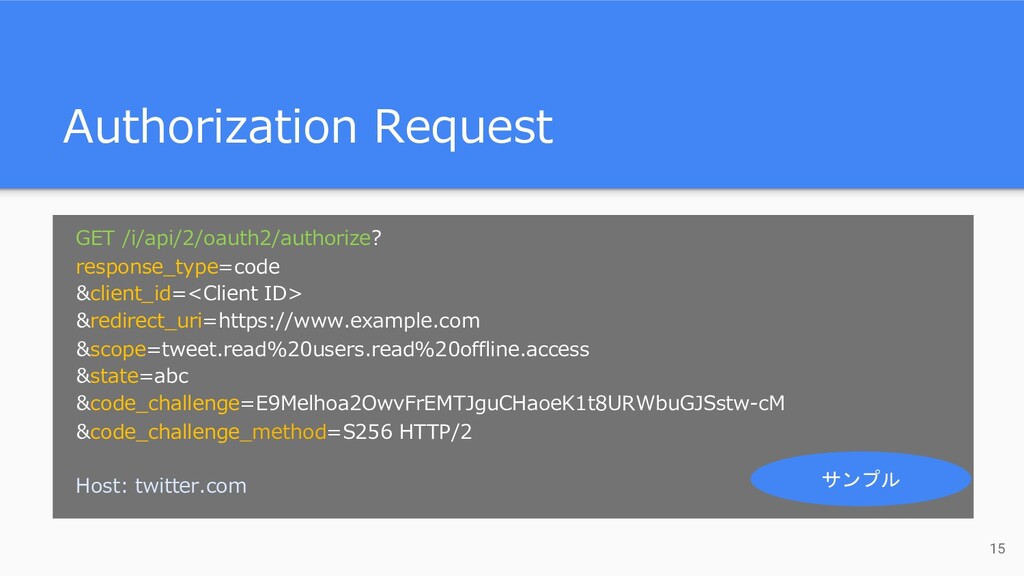
Authorization Request GET /i/api/2/oauth2/authorize? response_type=code &client_id=<Client ID> &redirect_uri=https://www.example.com &scope=tweet.read%20users.read%20offline.access &state=abc
&code_challenge=E9Melhoa2OwvFrEMTJguCHaoeK1t8URWbuGJSstw-cM &code_challenge_method=S256 HTTP/2 Host: twitter.com 15 サンプル -
Authorization Code Flow with PKCE [1] Init Resource Owner Client
Authorization Server Resource Server [2] Redirect to Authorization Server [3]Authorization Request (code_challenge,code_challenge_method) [5] Redirect back to Client [6] Authorization Response w/ Authorization Code [7] Token Request (code_verifier) [8] Token Response [9] API Request [10] API Response [4] End-User Authentication & Consent 17 -
Authorization Code Flow with PKCE [1] Init Resource Owner Client
Authorization Server Resource Server [2] Redirect to Authorization Server [3]Authorization Request (code_challenge,code_challenge_method) [5] Redirect back to Client [6] Authorization Response w/ Authorization Code [7] Token Request (code_verifier) [8] Token Response [9] API Request [10] API Response [4] End-User Authentication & Consent 19 -
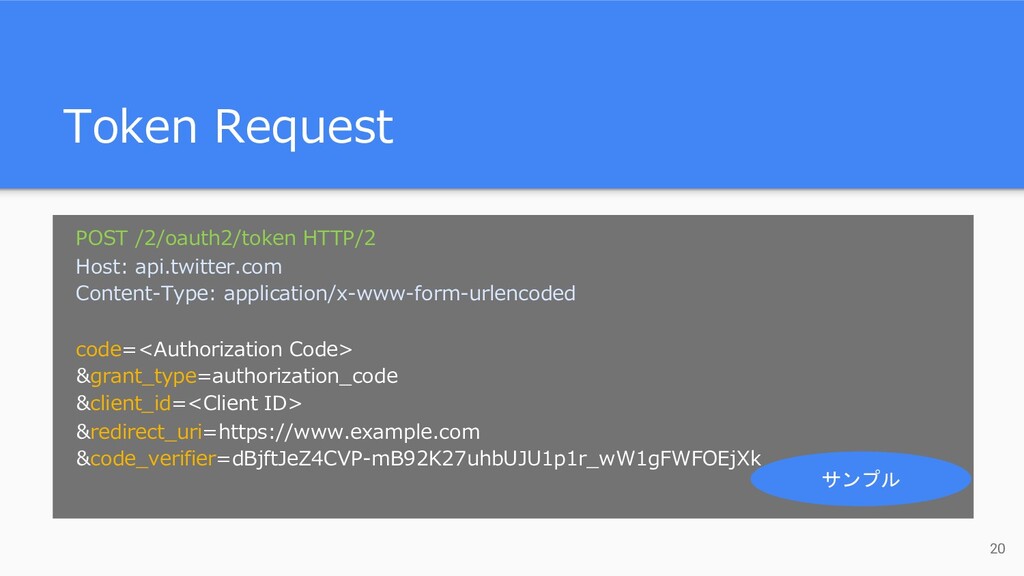
Token Request POST /2/oauth2/token HTTP/2 Host: api.twitter.com Content-Type: application/x-www-form-urlencoded code=<Authorization
Code> &grant_type=authorization_code &client_id=<Client ID> &redirect_uri=https://www.example.com &code_verifier=dBjftJeZ4CVP-mB92K27uhbUJU1p1r_wW1gFWFOEjXk 20 サンプル -
Authorization Code Flow with PKCE [1] Init Resource Owner Client
Authorization Server Resource Server [2] Redirect to Authorization Server [3]Authorization Request (code_challenge,code_challenge_method) [5] Redirect back to Client [6] Authorization Response w/ Authorization Code [7] Token Request (code_verifier) [8] Token Response [9] API Request [10] API Response [4] End-User Authentication & Consent 21 -
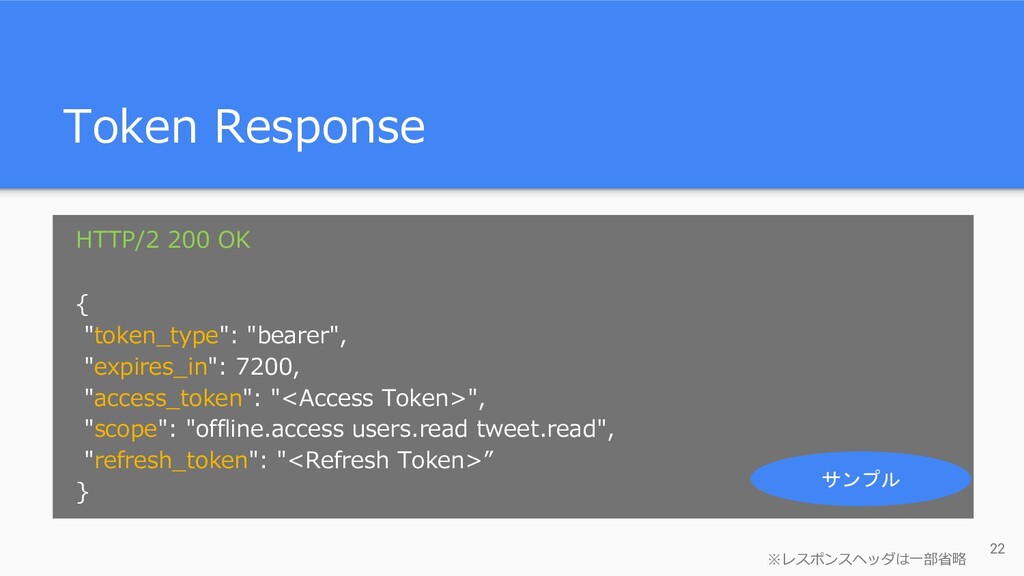
Token Response HTTP/2 200 OK { "token_type": "bearer", "expires_in": 7200,
"access_token": "<Access Token>", "scope": "offline.access users.read tweet.read", "refresh_token": "<Refresh Token>” } ※レスポンスヘッダは⼀部省略 22 サンプル -
Authorization Code Flow with PKCE [1] Init Resource Owner Client
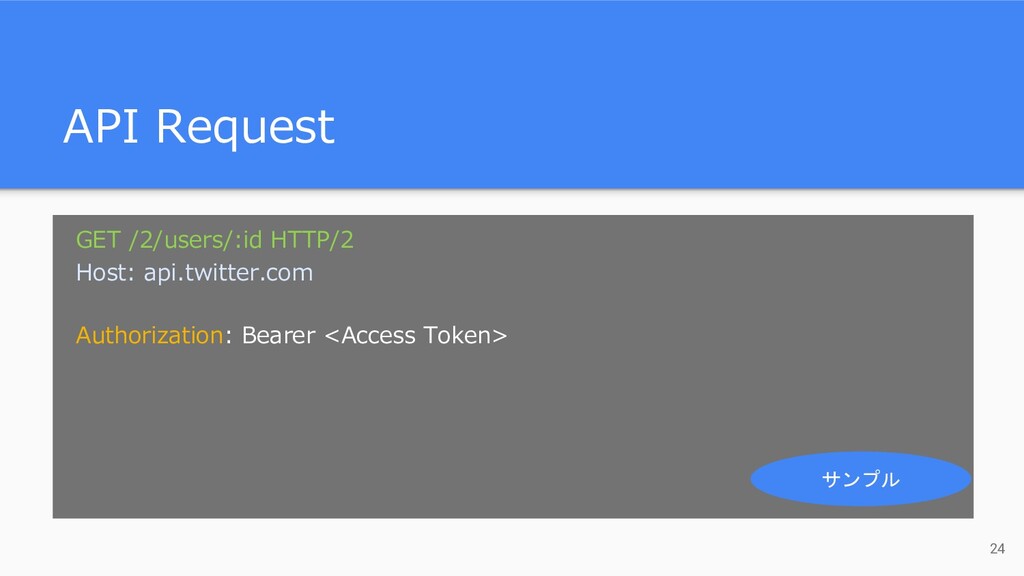
Authorization Server Resource Server [2] Redirect to Authorization Server [3]Authorization Request (code_challenge,code_challenge_method) [5] Redirect back to Client [6] Authorization Response w/ Authorization Code [7] Token Request (code_verifier) [8] Token Response [9] API Request [10] API Response [4] End-User Authentication & Consent 23 -
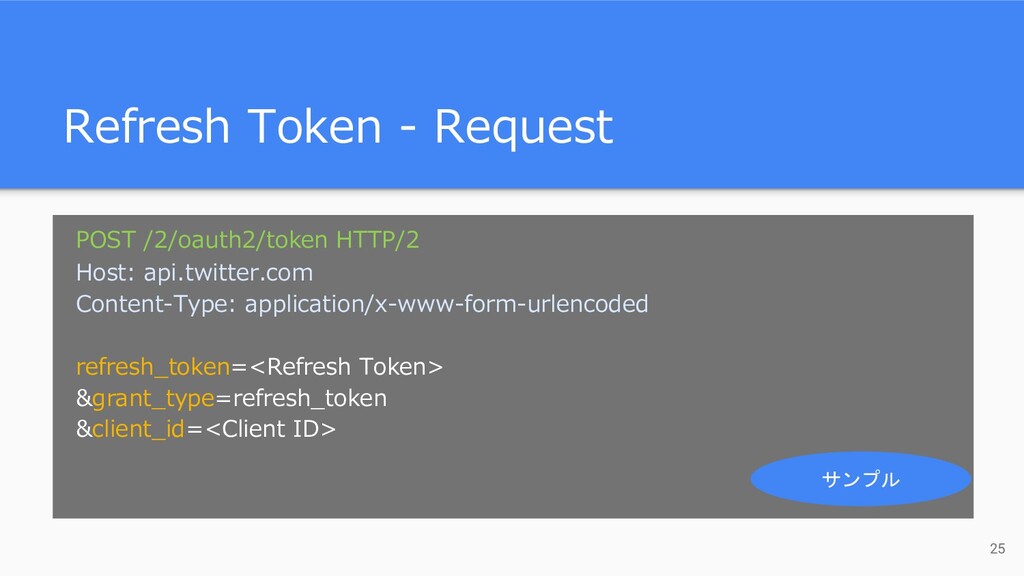
Refresh Token - Request POST /2/oauth2/token HTTP/2 Host: api.twitter.com Content-Type:
application/x-www-form-urlencoded refresh_token=<Refresh Token> &grant_type=refresh_token &client_id=<Client ID> 25 サンプル -
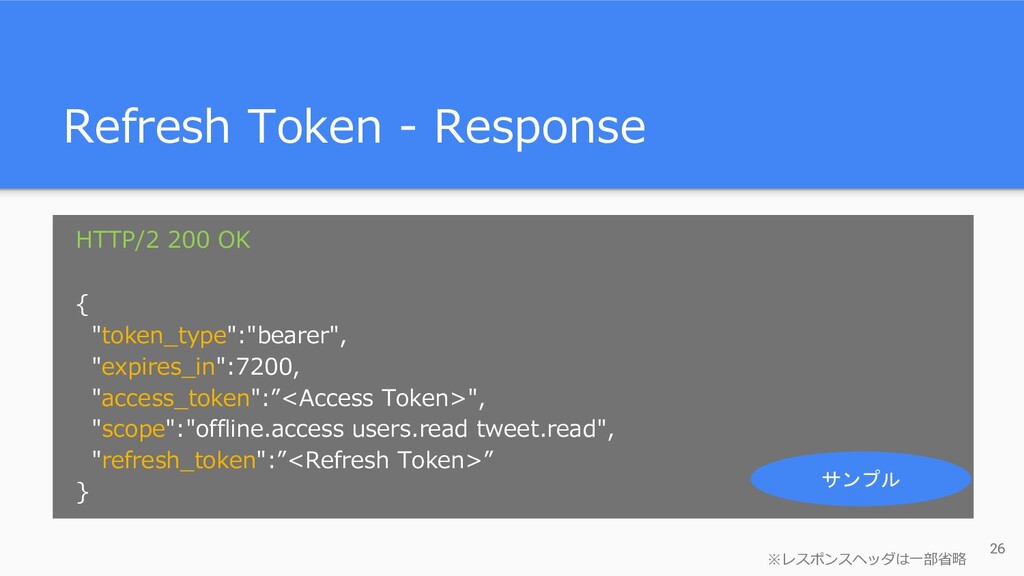
Refresh Token - Response HTTP/2 200 OK { "token_type":"bearer", "expires_in":7200,
"access_token":”<Access Token>", "scope":"offline.access users.read tweet.read", "refresh_token":”<Refresh Token>” } 26 サンプル ※レスポンスヘッダは⼀部省略 -
Revoke Token - Request POST /2/oauth2/revoke HTTP/2 Host: api.twitter.com Content-Type:
application/x-www-form-urlencoded token=<Access Token> &token_type_hint=access_token &client_id=<Client ID> 27 サンプル -
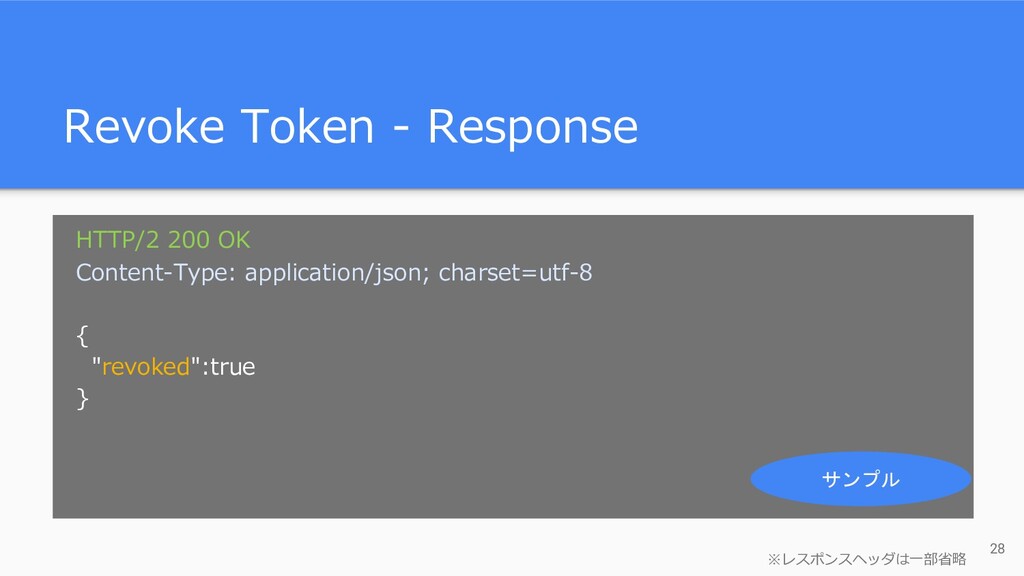
Revoke Token - Response HTTP/2 200 OK Content-Type: application/json; charset=utf-8
{ "revoked":true } 28 サンプル ※レスポンスヘッダは⼀部省略 -
OAuth Core 1.0 Revision A • Security Considerationsの中 でも実装依存で不備を作り込 みやすい項⽬に注⽬
◦ Secrecy of the Client Credentials ◦ Scoping of Access Requests ◦ Cross-Site Request Forgery (CSRF) 出所) https://openid-foundation-japan.github.io/rfc5849.ja.html 32 -
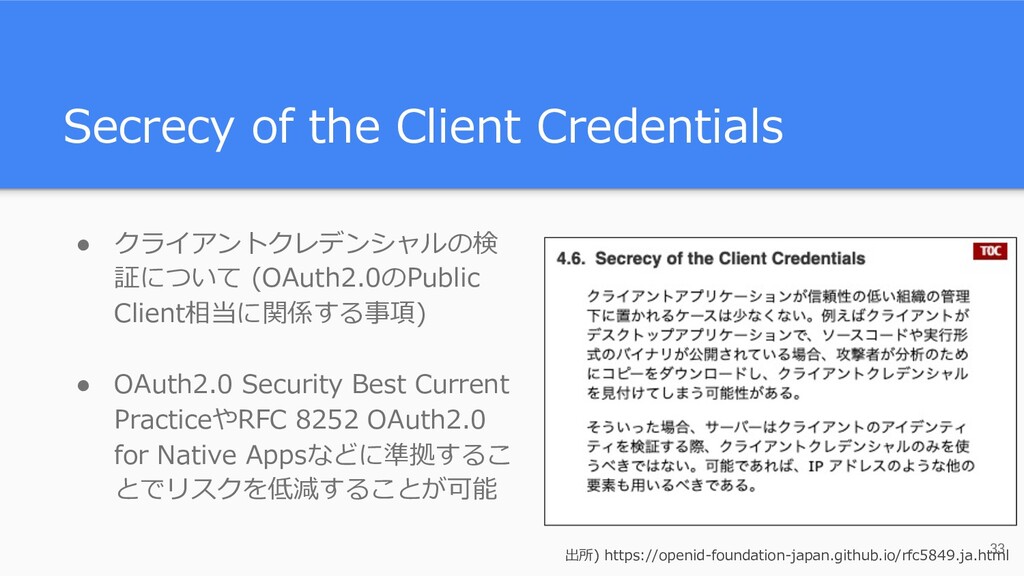
Secrecy of the Client Credentials • クライアントクレデンシャルの検 証について (OAuth2.0のPublic Client相当に関係する事項)
• OAuth2.0 Security Best Current PracticeやRFC 8252 OAuth2.0 for Native Appsなどに準拠するこ とでリスクを低減することが可能 33 出所) https://openid-foundation-japan.github.io/rfc5849.ja.html -
Scoping of Access Requests (1/3) • OAuth1.0ではクライアントに許 可する権限のスコープを定める⽅ 法が提供されておらず実装依存 •
OAuth2.0ではscopeパラメーター を⽤いて要求するアクセス範囲を 明⽰ 34 出所) https://openid-foundation-japan.github.io/rfc5849.ja.html -
Scoping of Access Requests (2/3) Twitter OAuth1.0 Twitter OAuth2.0 35
従来よりも細かく権限が指定できそう -
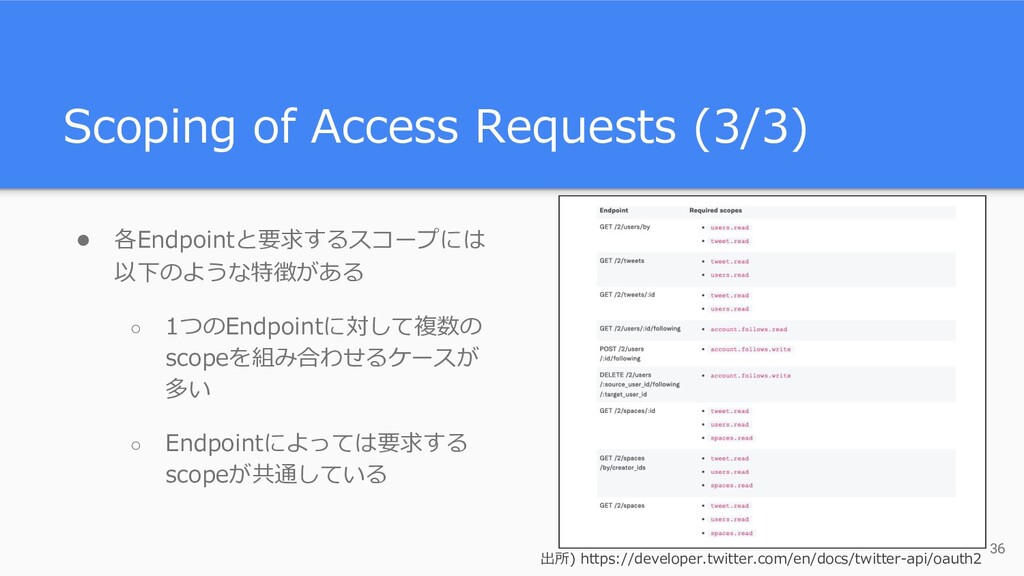
Scoping of Access Requests (3/3) 36 • 各Endpointと要求するスコープには 以下のような特徴がある ◦
1つのEndpointに対して複数の scopeを組み合わせるケースが 多い ◦ Endpointによっては要求する scopeが共通している 出所) https://developer.twitter.com/en/docs/twitter-api/oauth2 -
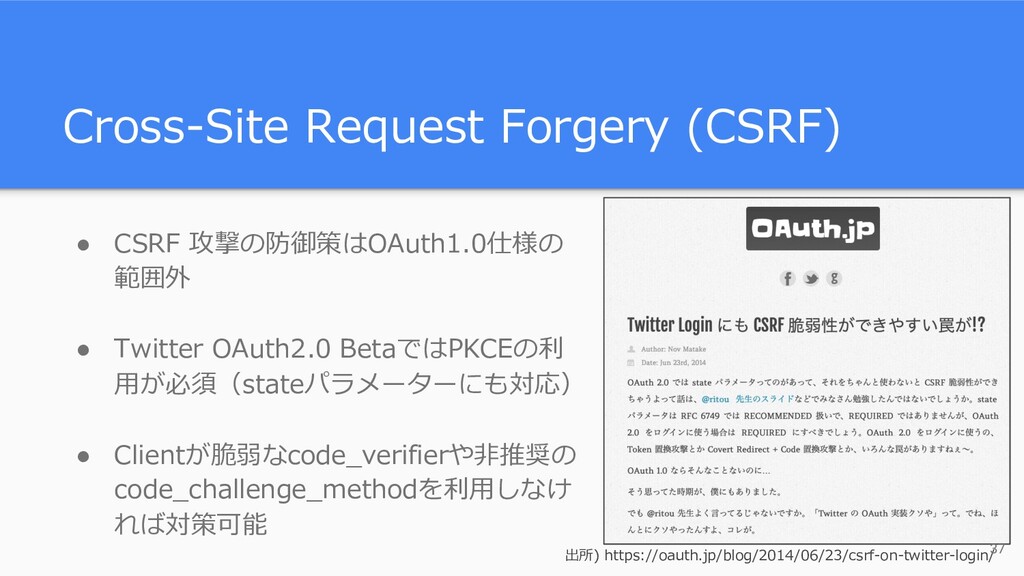
Cross-Site Request Forgery (CSRF) • CSRF 攻撃の防御策はOAuth1.0仕様の 範囲外 • Twitter
OAuth2.0 BetaではPKCEの利 ⽤が必須(stateパラメーターにも対応) • Clientが脆弱なcode_verifierや⾮推奨の code_challenge_methodを利⽤しなけ れば対策可能 出所) https://oauth.jp/blog/2014/06/23/csrf-on-twitter-login/ 37 -
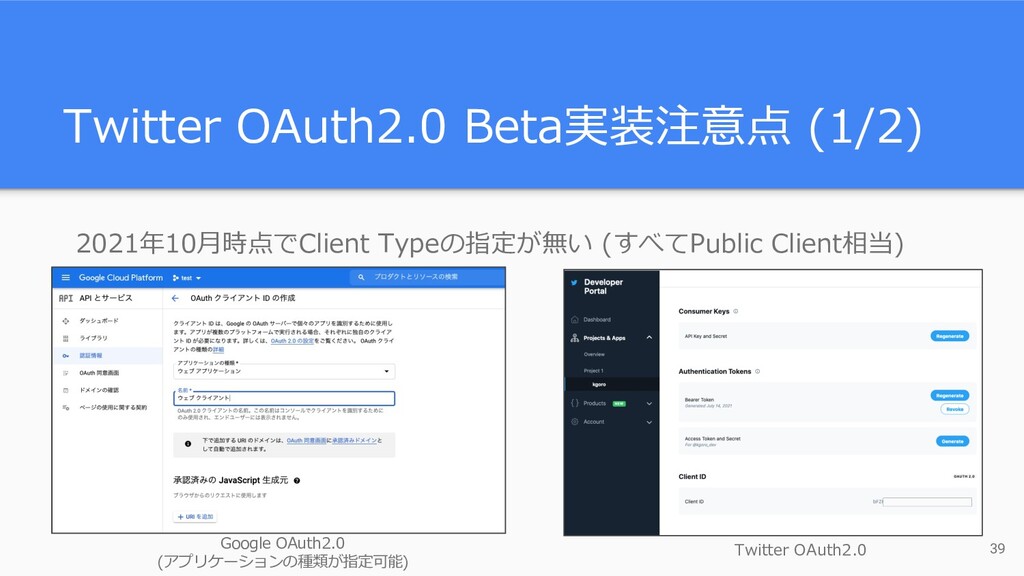
Twitter OAuth2.0 Beta実装注意点 (1/2) 2021年10⽉時点でClient Typeの指定が無い (すべてPublic Client相当) 39 Google
OAuth2.0 (アプリケーションの種類が指定可能) Twitter OAuth2.0 -
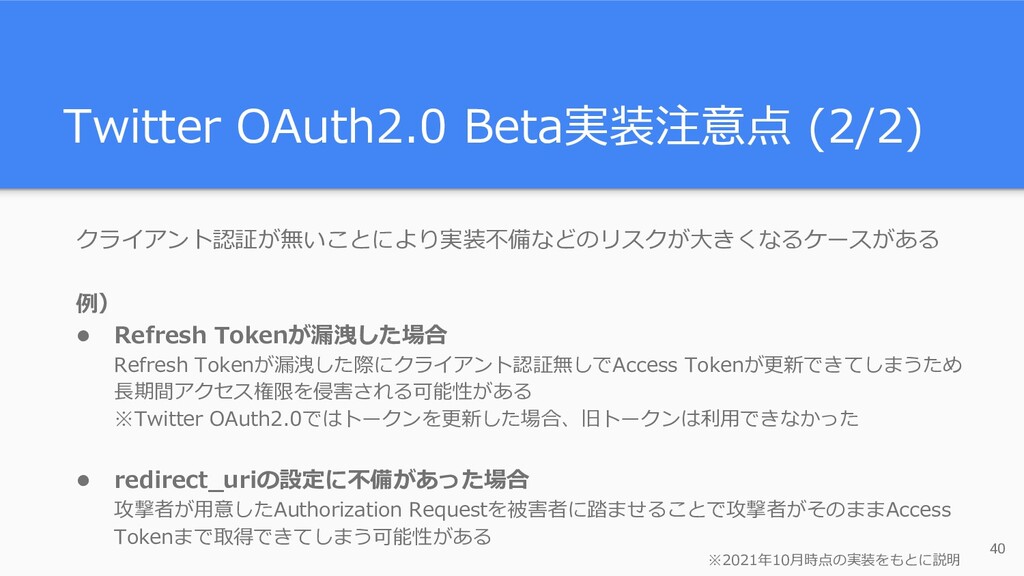
Twitter OAuth2.0 Beta実装注意点 (2/2) クライアント認証が無いことにより実装不備などのリスクが⼤きくなるケースがある 例) • Refresh Tokenが漏洩した場合 Refresh
Tokenが漏洩した際にクライアント認証無しでAccess Tokenが更新できてしまうため ⻑期間アクセス権限を侵害される可能性がある ※Twitter OAuth2.0ではトークンを更新した場合、旧トークンは利⽤できなかった • redirect_uriの設定に不備があった場合 攻撃者が⽤意したAuthorization Requestを被害者に踏ませることで攻撃者がそのままAccess Tokenまで取得できてしまう可能性がある 40 ※2021年10⽉時点の実装をもとに説明 -
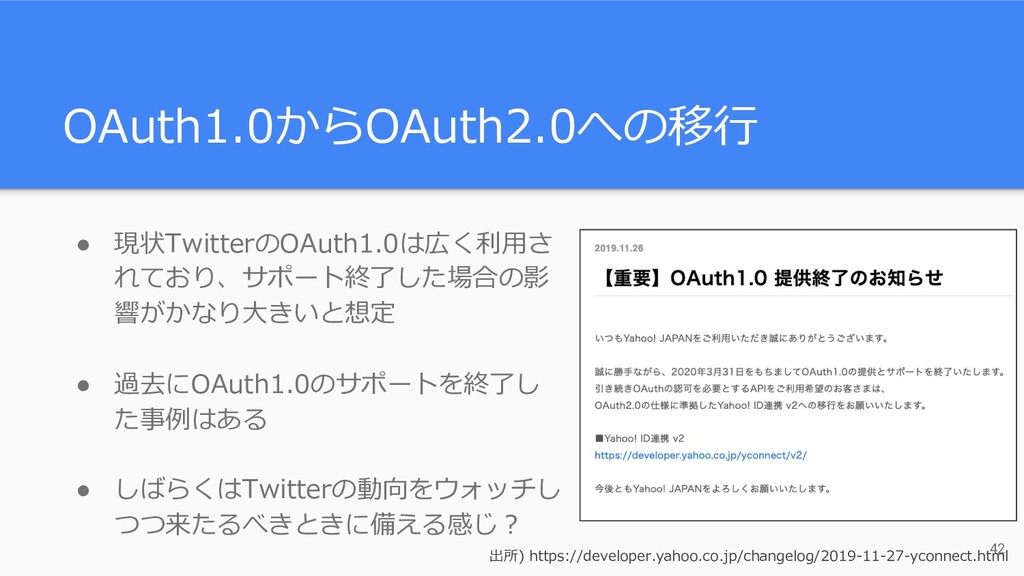
OAuth1.0からOAuth2.0への移⾏ • 現状TwitterのOAuth1.0は広く利⽤さ れており、サポート終了した場合の影 響がかなり⼤きいと想定 • 過去にOAuth1.0のサポートを終了し た事例はある • しばらくはTwitterの動向をウォッチし
つつ来たるべきときに備える感じ︖ 42 出所) https://developer.yahoo.co.jp/changelog/2019-11-27-yconnect.html -
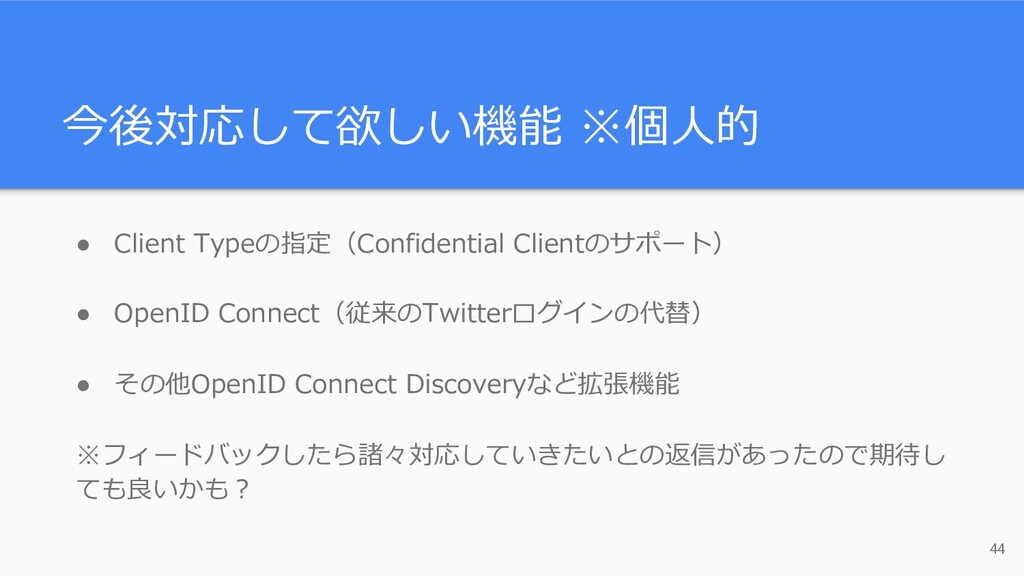
今後対応して欲しい機能 ※個⼈的 • Client Typeの指定(Confidential Clientのサポート) • OpenID Connect(従来のTwitterログインの代替) •
その他OpenID Connect Discoveryなど拡張機能 ※フィードバックしたら諸々対応していきたいとの返信があったので期待し ても良いかも︖ 44 -
おまけ ⼀応⾊々つくって試してみました (不具合などあればIssueやPRもらえると嬉しいです) • Twitter OAuth2.0 Beta Authorization Code Grant
w/ PKCE https://github.com/kg0r0/twitter-oauth2-client • Twitter OAuth2.0 Client Credentials Grant https://github.com/kg0r0/twitter-client-credentials • Twitter OAuth1.0 https://github.com/kg0r0/twitter-login-example 47 -
参考 • Twitter Developer Platform – OAuth2.0 https://developer.twitter.com/en/docs/twitter-api/oauth2 • Developer
Platform - Application-only authentication and OAuth 2.0 Bearer Token https://developer.twitter.com/en/docs/authentication/oauth-2-0/application-only • The OAuth 1.0 Protocol https://openid-foundation-japan.github.io/rfc5849.ja.html • The OAuth 2.0 Authorization Framework https://openid-foundation-japan.github.io/rfc6749.ja.html • Proof Key for Code Exchange by OAuth Public Clients https://datatracker.ietf.org/doc/html/rfc7636 • TwitterのOAuth2.0 Betaためしてみた! https://zenn.dev/kg0r0/articles/8d787860e9b2e1 48