Share
Embed
Transcript
32 slides
-
Who am I? 2 Marc Obrador Co-founder & Head of
Product Architecture @ Build38 Barcelona [email protected] @marcobrador /in/marc-obrador February 2020 Build38 | Intro to Mobile App Security -
3 Agenda 1. Introduction 2. Some Common Threads 1. Man-In-The-Middle
2. App Tampering & Repackaging 3. Root / Jailbreak 3. Recap @marcobrador February 2020 Build38 | Intro to Mobile App Security -
4 Agenda 1. Introduction 2. Some Common Threads 1. Man-In-The-Middle
2. App Tampering & Repackaging 3. Root / Jailbreak 3. Recap @marcobrador February 2020 Build38 | Intro to Mobile App Security -
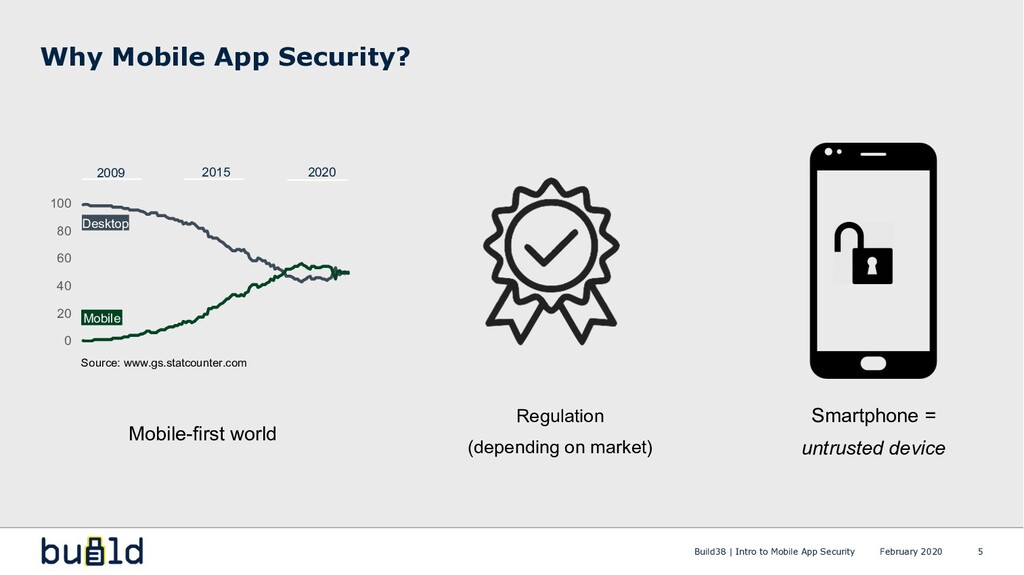
Mobile-first world Why Mobile App Security? 5 Smartphone = untrusted
device Regulation (depending on market) Desktop Mobile 2009 2015 2020 0 20 40 60 80 100 Source: www.gs.statcounter.com February 2020 Build38 | Intro to Mobile App Security -
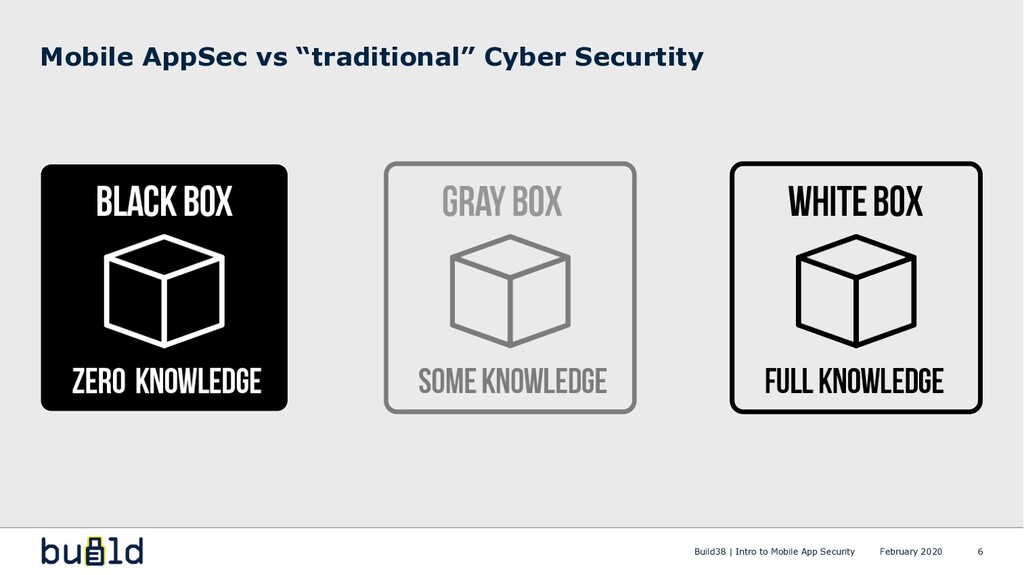
Mobile AppSec vs “traditional” Cyber Securtity 6 February 2020 Build38
| Intro to Mobile App Security -
Let’s first switch our perspective Is there anything I can
do? Build38 | Intro to Mobile App Security 7 February 2020 -
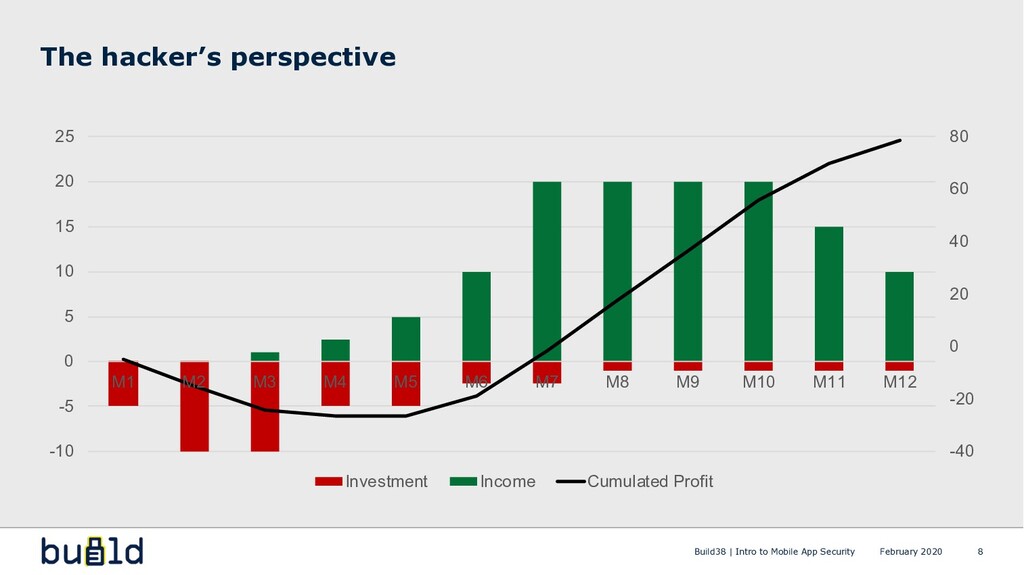
-40 -20 0 20 40 60 80 -10 -5 0
5 10 15 20 25 M1 M2 M3 M4 M5 M6 M7 M8 M9 M10 M11 M12 Investment Income Cumulated Profit The hacker’s perspective Build38 | Intro to Mobile App Security 8 February 2020 -
Is there anything I can do? Build38 | Intro to
Mobile App Security 9 February 2020 -
Make it unattractive for the hacker Is there anything I
can do? Build38 | Intro to Mobile App Security 10 February 2020 -
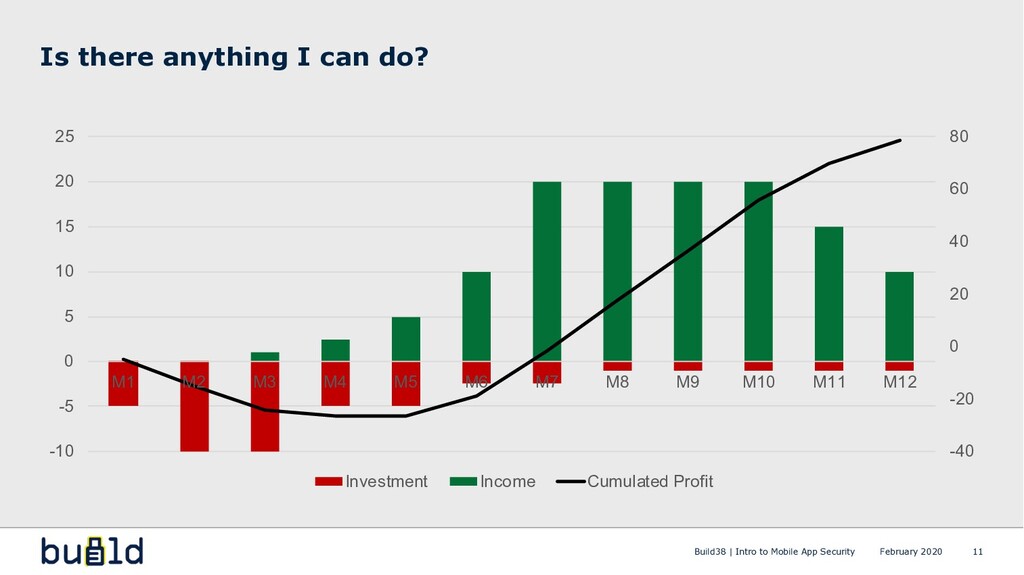
-40 -20 0 20 40 60 80 -10 -5 0
5 10 15 20 25 M1 M2 M3 M4 M5 M6 M7 M8 M9 M10 M11 M12 Investment Income Cumulated Profit Is there anything I can do? Build38 | Intro to Mobile App Security 11 February 2020 -
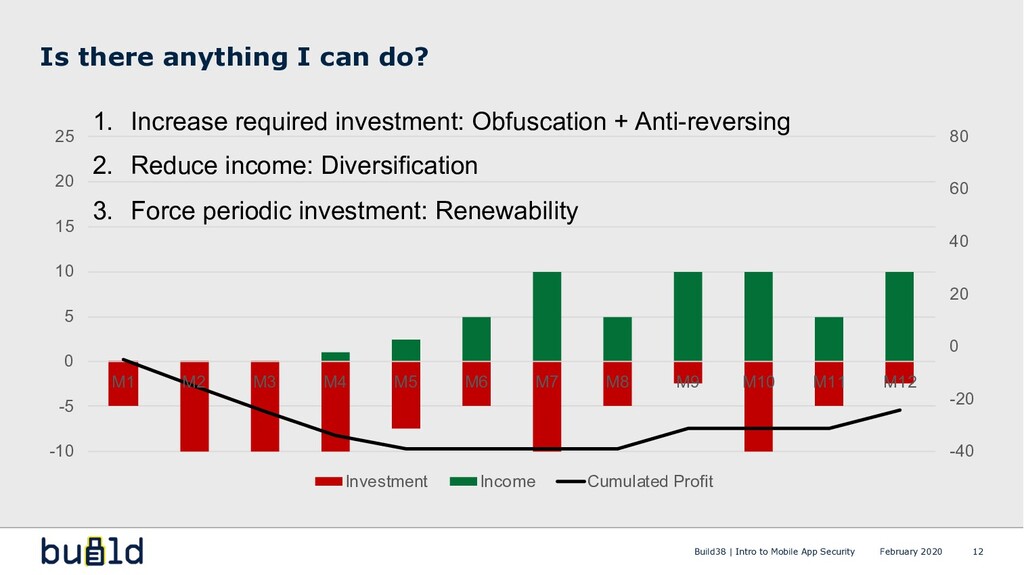
-40 -20 0 20 40 60 80 -10 -5 0
5 10 15 20 25 M1 M2 M3 M4 M5 M6 M7 M8 M9 M10 M11 M12 Investment Income Cumulated Profit Is there anything I can do? Build38 | Intro to Mobile App Security 12 1. Increase required investment: Obfuscation + Anti-reversing 2. Reduce income: Diversification 3. Force periodic investment: Renewability February 2020 -
Things to protect Build38 | Intro to Mobile App Security
13 User Data Business Data / IP DRM February 2020 -
14 Agenda 1. Introduction 2. Some Common Threads 1. Man-In-The-Middle
2. App Tampering & Repackaging 3. Root / Jailbreak 3. Recap @marcobrador February 2020 Build38 | Intro to Mobile App Security -
15 Agenda 1. Introduction 2. Some Common Threads 1. Man-In-The-Middle
2. App Tampering & Repackaging 3. Root / Jailbreak 3. Recap @marcobrador February 2020 Build38 | Intro to Mobile App Security -
MITM Build38 | Intro to Mobile App Security 16 February
2020 HTTPS is assumed! -
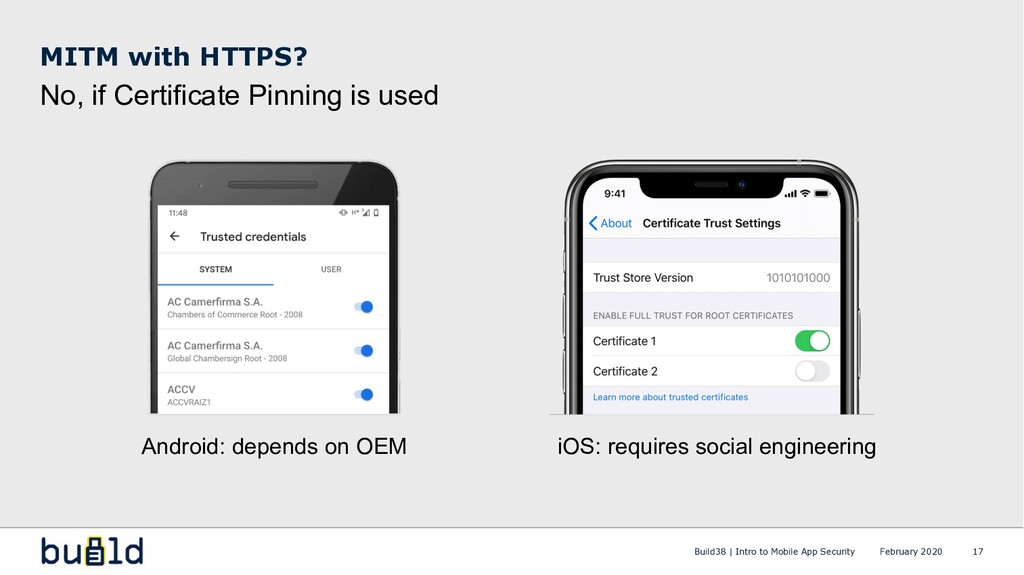
MITM with HTTPS? Build38 | Intro to Mobile App Security
17 February 2020 Android: depends on OEM iOS: requires social engineering No, if Certificate Pinning is used -
18 Agenda 1. Introduction 2. Some Common Threads 1. Man-In-The-Middle
2. App Tampering & Repackaging 3. Root / Jailbreak 3. Recap @marcobrador February 2020 Build38 | Intro to Mobile App Security -
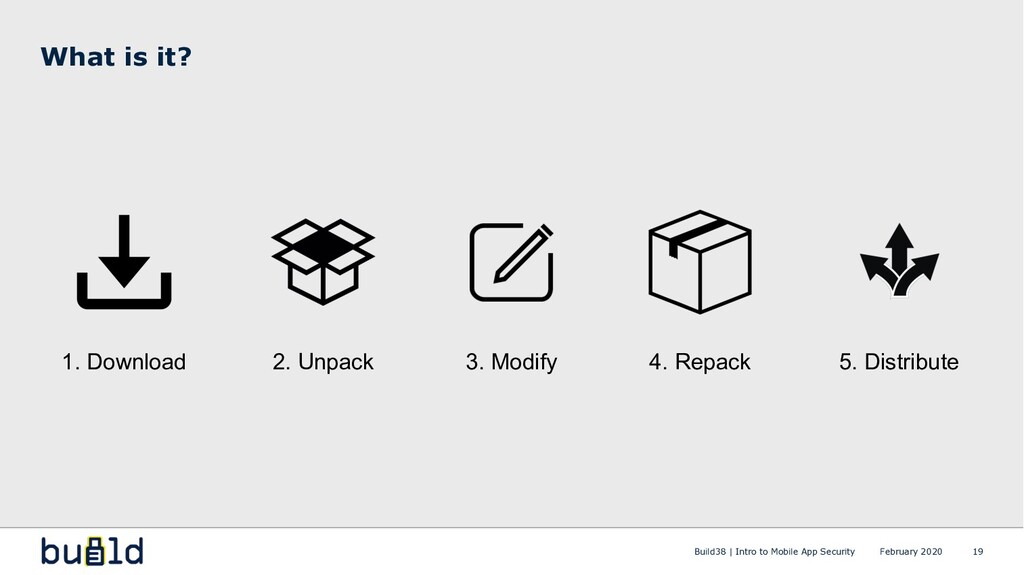
What is it? 19 February 2020 Build38 | Intro to
Mobile App Security 1. Download 2. Unpack 3. Modify 4. Repack 5. Distribute -
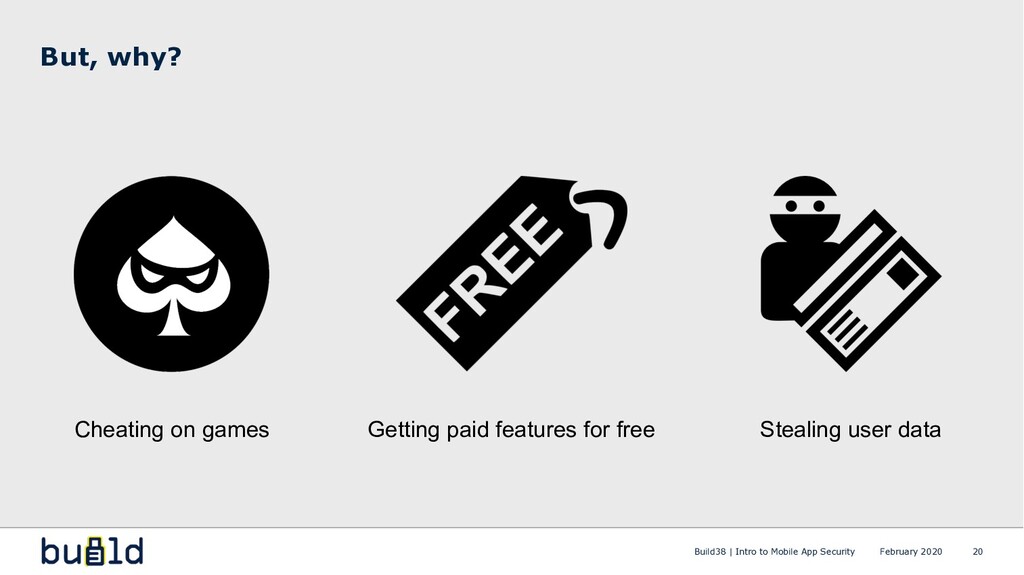
But, why? 20 February 2020 Build38 | Intro to Mobile
App Security Cheating on games Getting paid features for free Stealing user data -
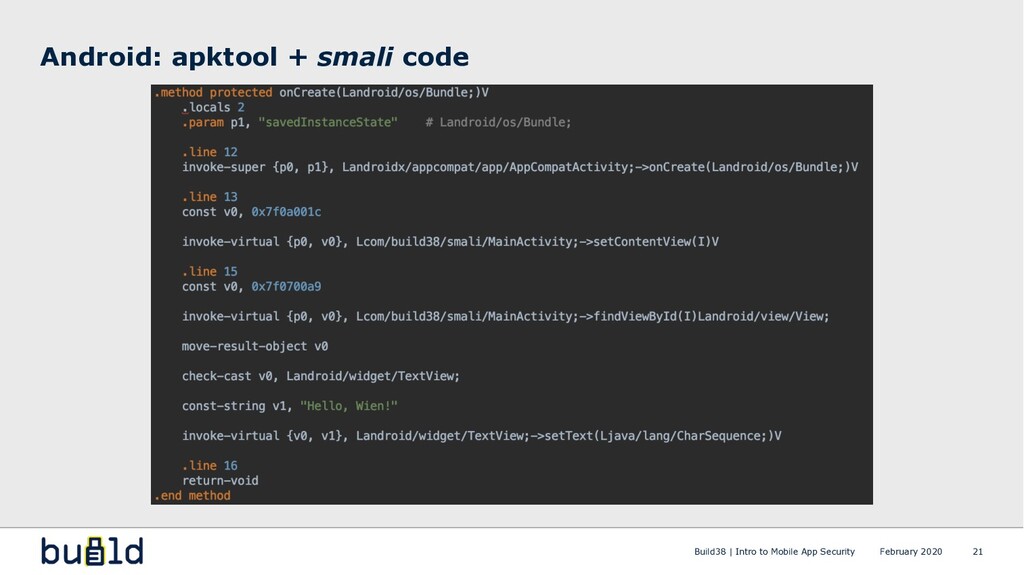
Android: apktool + smali code 21 February 2020 Build38 |
Intro to Mobile App Security -
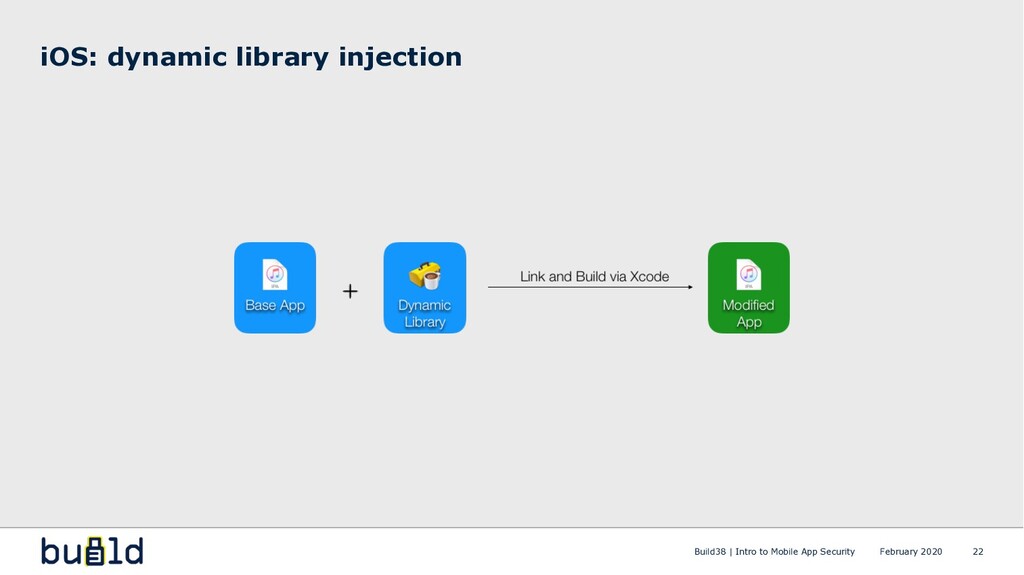
iOS: dynamic library injection 22 February 2020 Build38 | Intro
to Mobile App Security -
Protecting against app repackaging 23 Obfuscation Detect it February 2020
Build38 | Intro to Mobile App Security -
24 Agenda 1. Introduction 2. Some Common Threads 1. Man-In-The-Middle
2. App Tampering & Repackaging 3. Root / Jailbreak 3. Recap @marcobrador February 2020 Build38 | Intro to Mobile App Security -
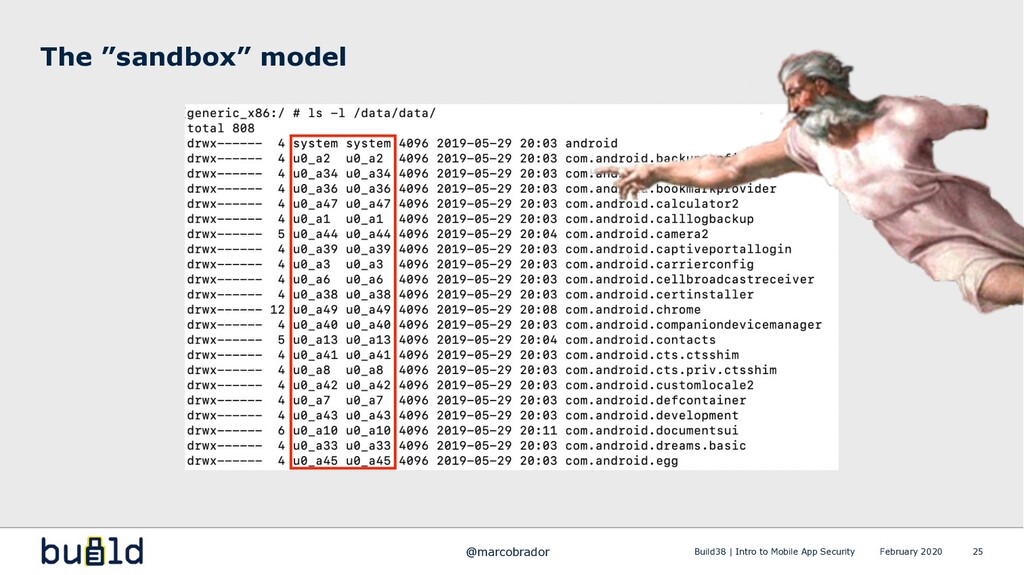
The ”sandbox” model 25 @marcobrador February 2020 Build38 | Intro
to Mobile App Security -
Root / Jailbreak Detection 26 /scottyab/rootbeer /KimChangYoun/rootbeerFresh /Stericson/RootTools /avltree9798/isJailbroken /thii/DTTJailbreakDetection
@marcobrador February 2020 Build38 | Intro to Mobile App Security -
27 What to do if Root / Jailbreak is found?
@marcobrador February 2020 Build38 | Intro to Mobile App Security -
What to do if Root is found? 28 Sources: -
https://techcrunch.com/2019/08/29/google-iphone-secretly-hacked/ - https://googleprojectzero.blogspot.com/2019/08/a-very-deep-dive-into-ios-exploit.html @marcobrador February 2020 Build38 | Intro to Mobile App Security -
Nothing Restrict some sensitive functionality Deny service Design your security
model assuming that root can (and will) happen What to do if Root is found? 29 @marcobrador February 2020 Build38 | Intro to Mobile App Security -
30 Agenda 1. Introduction 2. Some Common Threads 1. Man-In-The-Middle
2. App Tampering & Repackaging 3. Root / Jailbreak 3. Recap @marcobrador February 2020 Build38 | Intro to Mobile App Security -
- 100% protection does not exist – aim for “good
enough” - Certificate Pinning is a good idea - Apps can be reverse engineered and repackaged § Move security-relevant logic to backend or write it in native C - Root can be really bad – come up with a plan Recap 31 February 2020 Build38 | Intro to Mobile App Security