Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
UCCU Monthly Talk: Ransomware
Search
NotSurprised
September 30, 2018
Research
190
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
UCCU Monthly Talk: Ransomware
Attack & Defend between Black hat & White hat. Characteristic ransomware families.
NotSurprised
September 30, 2018
More Decks by NotSurprised
See All by NotSurprised
iThome2024 Wailing Wall of Enterprise Security
notsurprised
0
540
NSYSU ISC 2021 Internet Of Things
notsurprised
0
180
IRCON2021-Mediatek-ActiveDirectory-Hardening
notsurprised
0
190
iThome2021 Its Okay to be Old Driver
notsurprised
1
860
Xmas2020-Its-Okay-to-be-Old-Driver
notsurprised
1
360
NCU2020 Information Security 101
notsurprised
0
190
iThome CyberSec2020-Chaos Of Vehicle Communications
notsurprised
3
800
Becks.io#5 Get start to Old Driver in Windows Kernel
notsurprised
2
1.8k
MOPCON2019 Chaos of Vehicle Communications
notsurprised
1
510
Other Decks in Research
See All in Research
PGDM: Physically Guided Diffusion Model for L Downscaling
satai
3
490
2025年度秋葉原ウォーカブルプロジェクト調査報告 「アキバらしいウォーカブル」とは何か
izumiyama_lab
1
230
Fukui Shibiten 39 - AI Art
butchi
0
200
多様なデータを許容し学習し続ける模倣学習 / Advanced Imitation Learning for VLA
prinlab
0
330
[最先端NLP勉強会2026] Checklists Are Better Than Reward Models For Aligning Language Models
nzw0301
1
310
【ローカルAIに向き合う展示会vol.2】液体時間定数型モジュールを用いた オリジナルの双方向エンコーダーモデルNexteraBERT 推論速度向上検討並びにダウンストリーム評価
rikkabotan7
0
200
医療LLMの現在地〜最新研究から社会実装までを考える〜
kento1109
1
1.8k
高性能計算機クラスタを用いた大規模点群処理による森林の単木抽出と構造解析
kentaitakura
1
130
Karkada さんの論文 × 2 の紹介: (1) Closed-Form Training Dynamics Reveal Learned Features and Linear Structure in Word2Vec-like Models, (2) Symmetry in language statistics shapes the geometry of model representations
eumesy
PRO
1
760
実例から見るLLMのマンガ理解:実務VQAタスクによる長期的文脈と視覚情報の定性評価
kzmssk
0
140
JICA QUEST 共創×革新プログラム Impact Report(海ノ向こうコーヒー)
ontheslope
0
650
Research Engineerという仕事 / Research Engineering: Bridging Research and Business
chck
1
350
Featured
See All Featured
Redefining SEO in the New Era of Traffic Generation
szymonslowik
1
430
How to Grow Your eCommerce with AI & Automation
katarinadahlin
PRO
2
280
Rebuilding a faster, lazier Slack
samanthasiow
85
9.6k
How People are Using Generative and Agentic AI to Supercharge Their Products, Projects, Services and Value Streams Today
helenjbeal
1
330
How to Build an AI Search Optimization Roadmap - Criteria and Steps to Take #SEOIRL
aleyda
1
2.2k
Marketing to machines
jonoalderson
1
5.8k
The Spectacular Lies of Maps
axbom
PRO
1
1k
Tips & Tricks on How to Get Your First Job In Tech
honzajavorek
1
770
Build your cross-platform service in a week with App Engine
jlugia
234
19k
DevOps and Value Stream Thinking: Enabling flow, efficiency and business value
helenjbeal
1
390
Avoiding the “Bad Training, Faster” Trap in the Age of AI
tmiket
0
250
Building Adaptive Systems
keathley
44
3.2k
Transcript
NotSurprised @ UCCU
[email protected]
> NotSurprised • ITRI engineer • UCCU hacker • 中山資管五年學碩士
Email :
[email protected]
> • Background • Attack & Defend • Families •
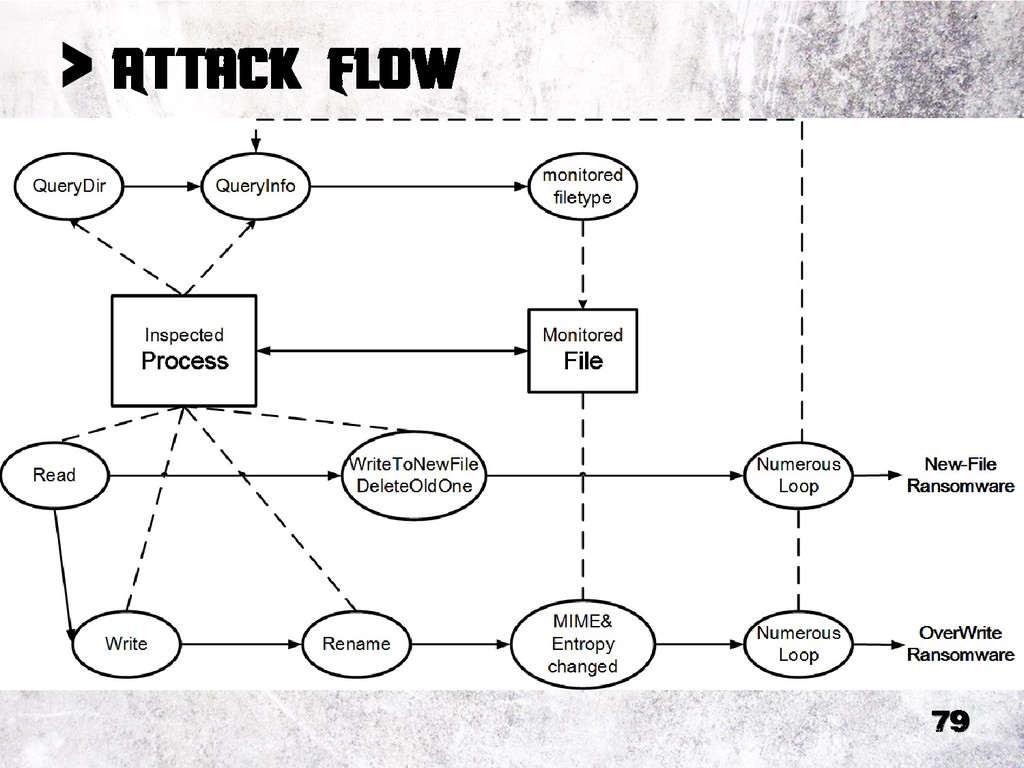
Attack Flow
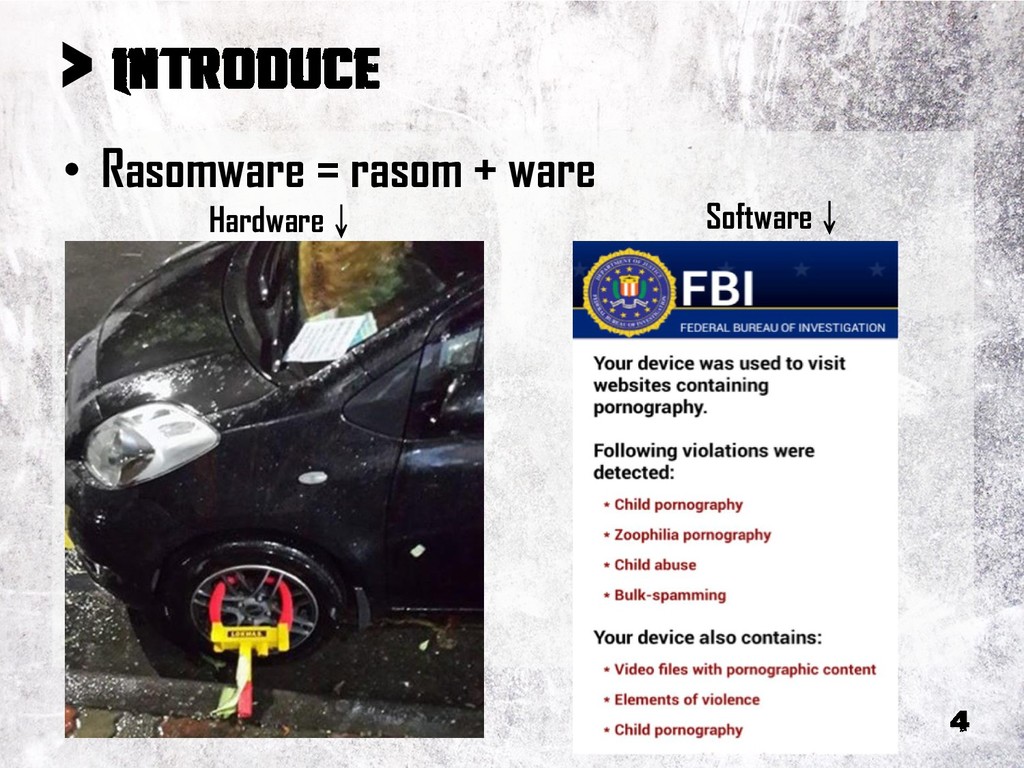
> • Rasomware = rasom + ware Hardware↓ Software↓
> • 2013末開始活動的CryptoLocker在遭瓦解以前取得估計約三百萬美 元的贖金。 • 2014年開始的CryptoWall,被美國聯邦調查局估計在2015年6月以 前獲得超過一百八十萬美元的贖金。 • 根據FBI在2016年八月的保守估計指出,2016年前半年中,全球勒索 軟體造成的總損失約超過十億美元。
• 2016年所發現的勒索軟體的變種數量相較2015年提升了30倍,趨勢 科技則預估2017年會有勒索軟體的數量還會再上升25個百分比。 • Spam、Botnet、ExploitKits為勒索軟體散布主要途徑。2016年臺 灣的資安威脅當中,勒索軟體橫據前十大。2015年度臺灣面臨垃圾 郵件嚴重性亦是全球第三名,殭屍網路受害度是全球第三名。
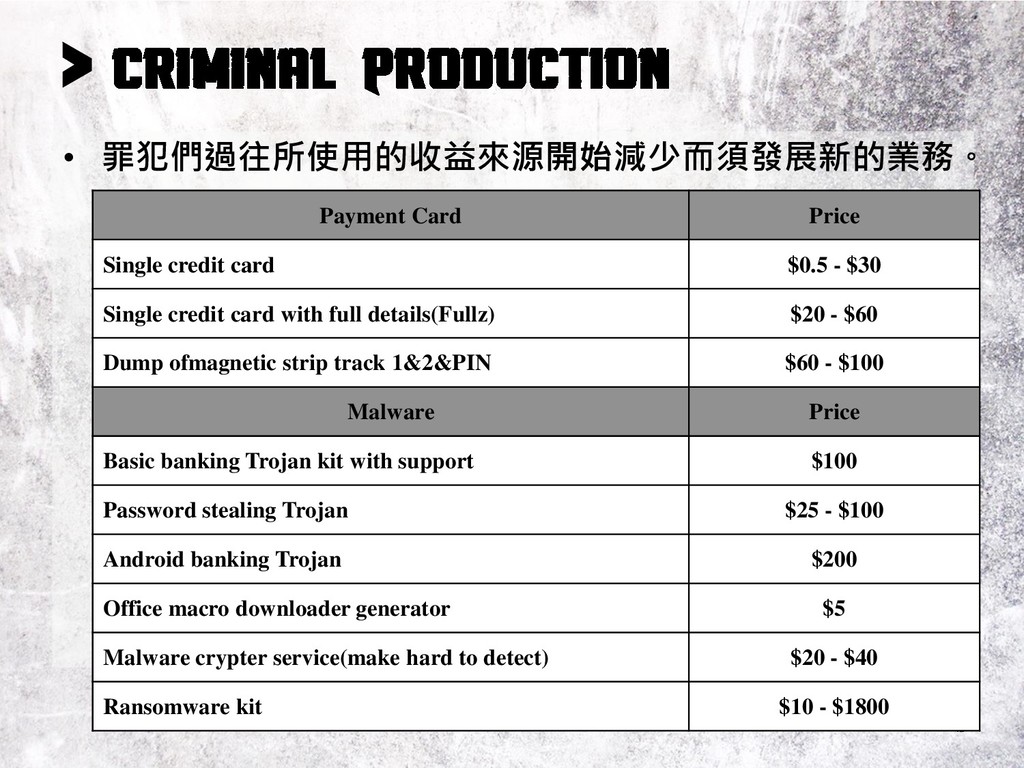
> • 罪犯們過往所使用的收益來源開始減少而須發展新的業務。 Payment Card Price Single credit card $0.5
- $30 Single credit card with full details(Fullz) $20 - $60 Dump ofmagnetic strip track 1&2&PIN $60 - $100 Malware Price Basic banking Trojan kit with support $100 Password stealing Trojan $25 - $100 Android banking Trojan $200 Office macro downloader generator $5 Malware crypter service(make hard to detect) $20 - $40 Ransomware kit $10 - $1800
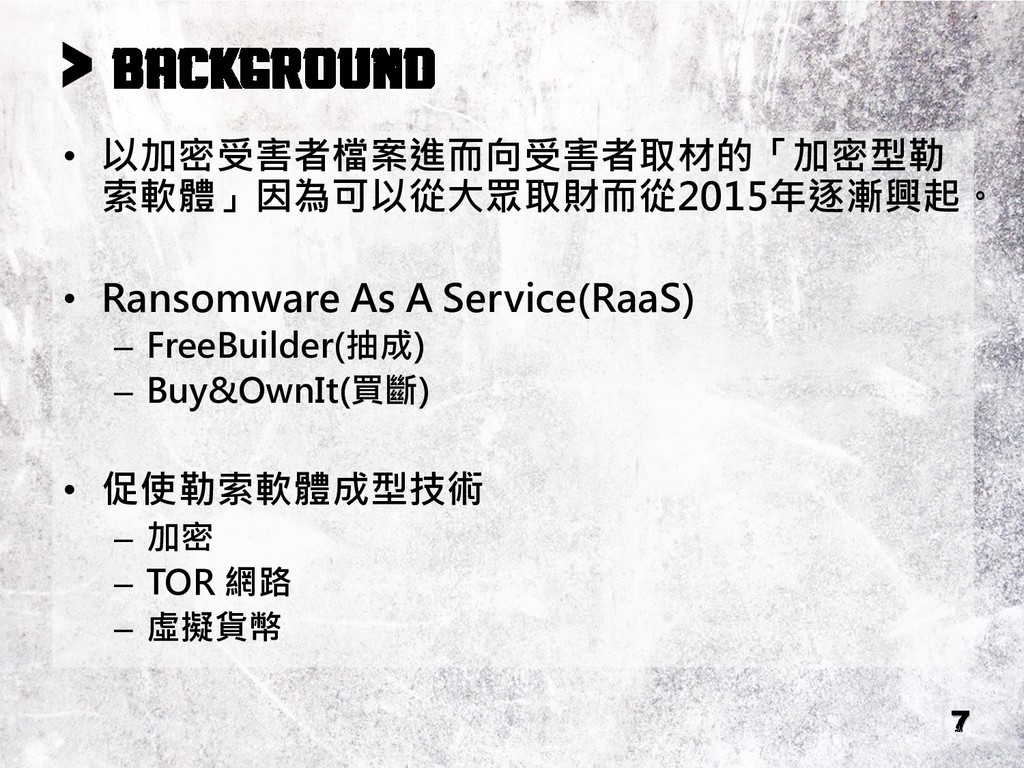
> • 以加密受害者檔案進而向受害者取材的「加密型勒 索軟體」因為可以從大眾取財而從2015年逐漸興起。 • Ransomware As A Service(RaaS) –
FreeBuilder(抽成) – Buy&OwnIt(買斷) • 促使勒索軟體成型技術 – 加密 – TOR 網路 – 虛擬貨幣
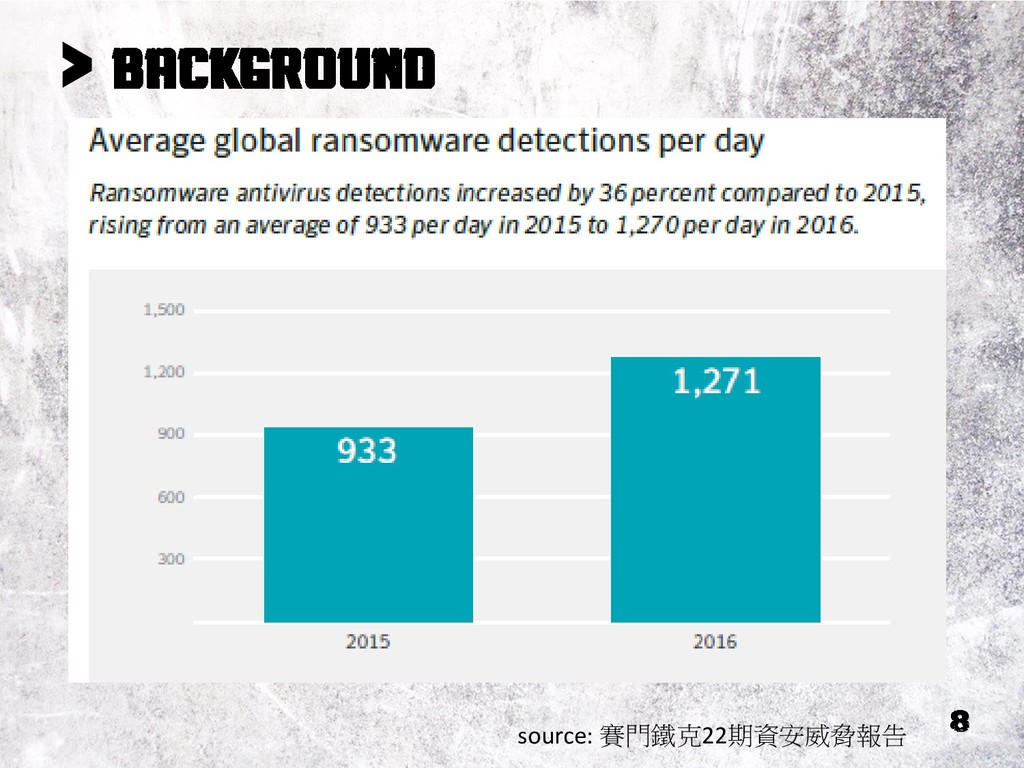
> source: 賽門鐵克22期資安威脅報告
>
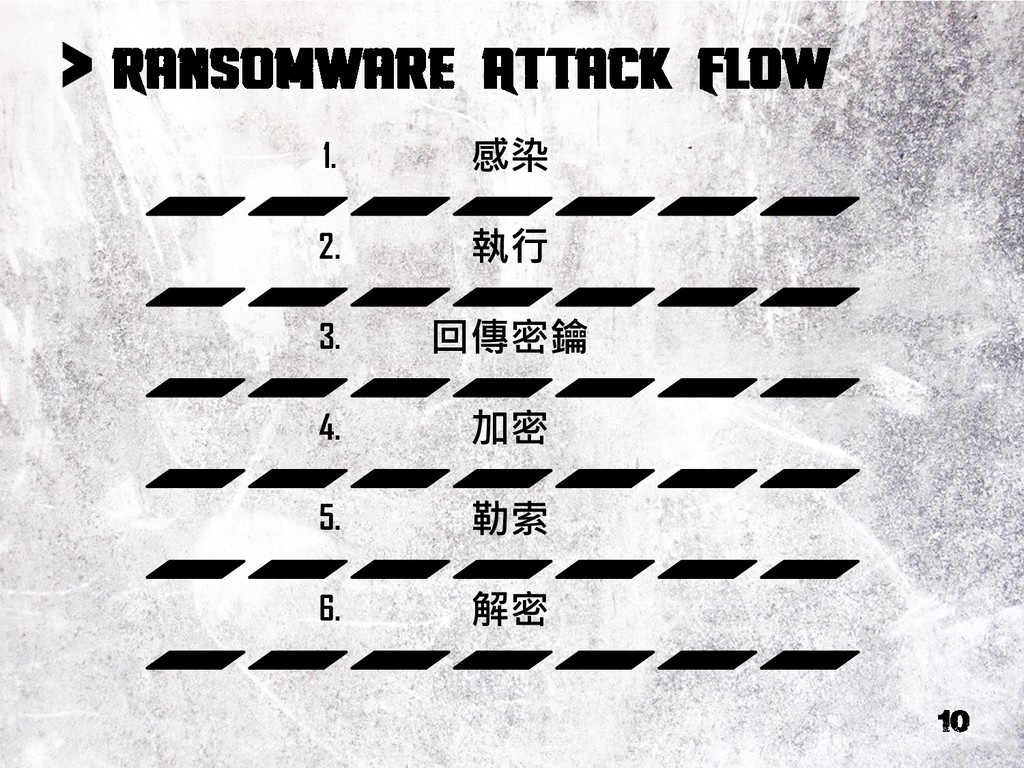
> 感染 執行 回傳密鑰 加密 勒索 解密 1. 2. 3.
4. 5. 6.
None
>
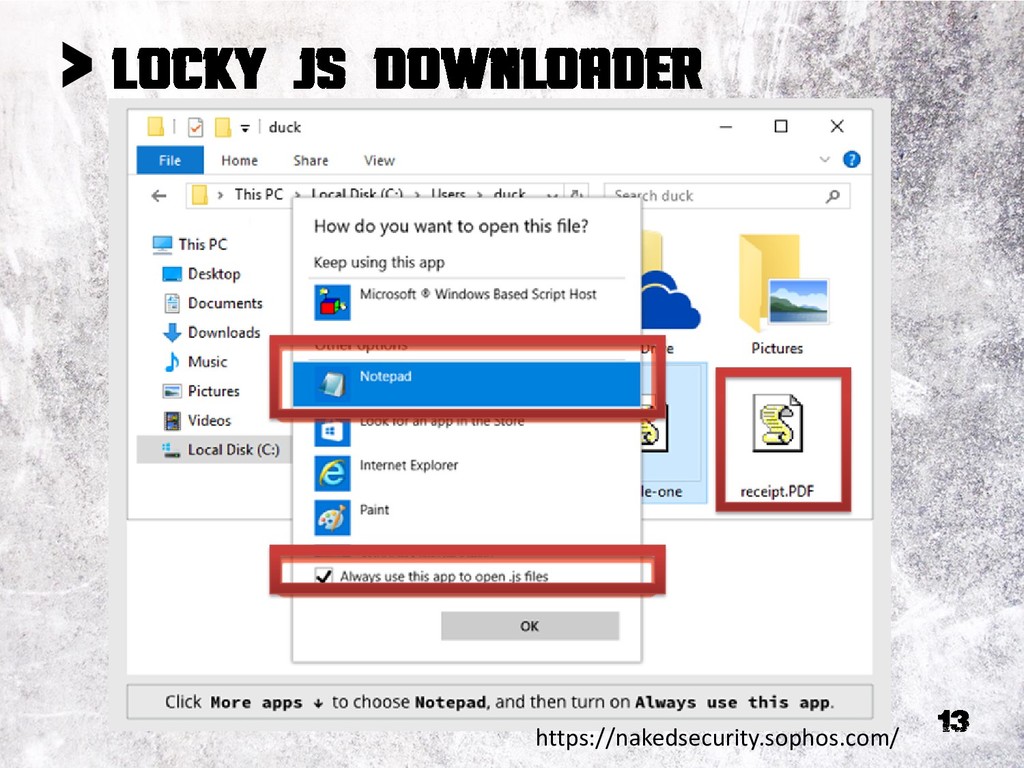
> https://nakedsecurity.sophos.com/
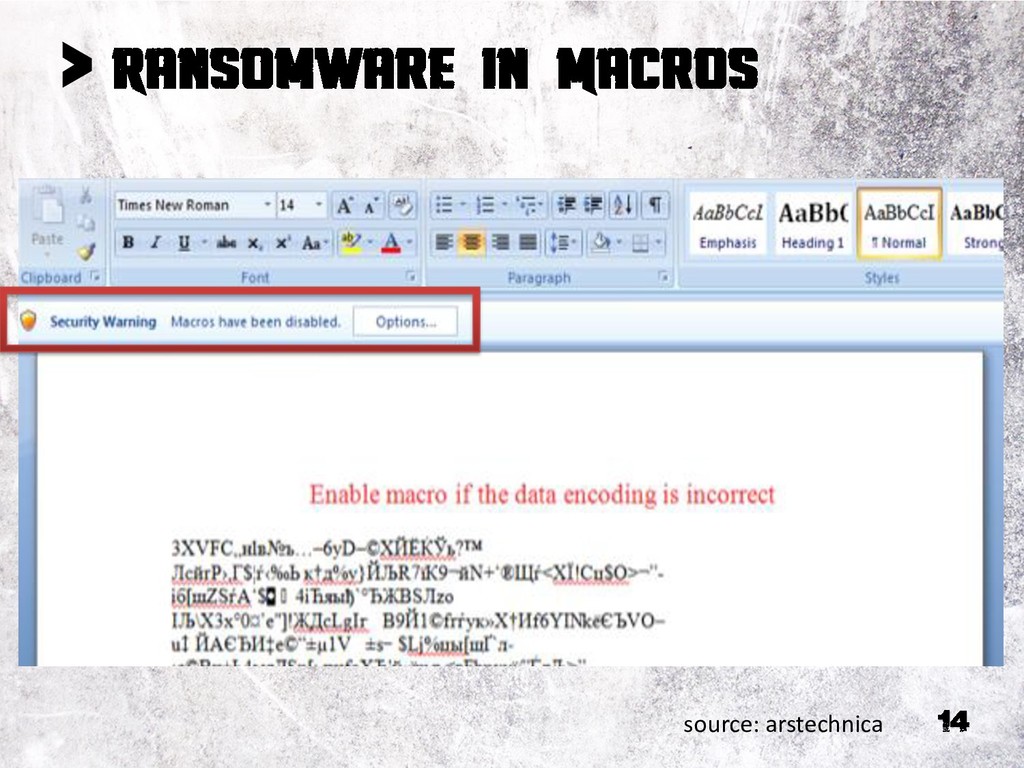
> source: arstechnica
None
None
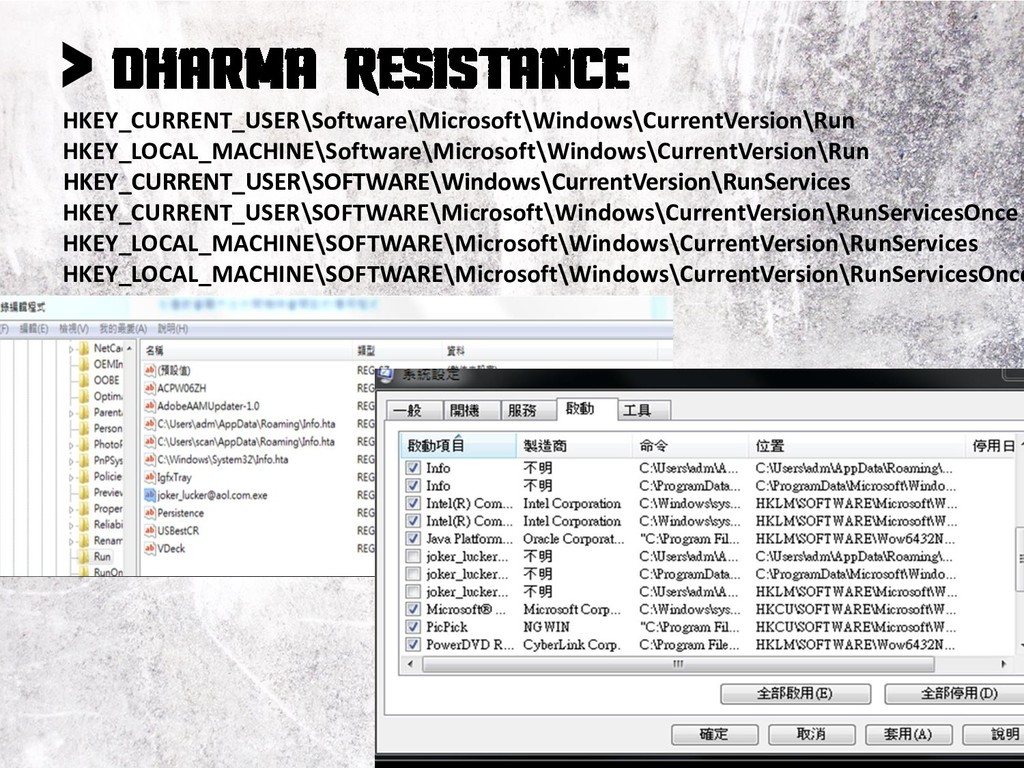
> HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run HKEY_CURRENT_USER\SOFTWARE\Windows\CurrentVersion\RunServices HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\RunServicesOnce HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\RunServices HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\RunServicesOnce
None
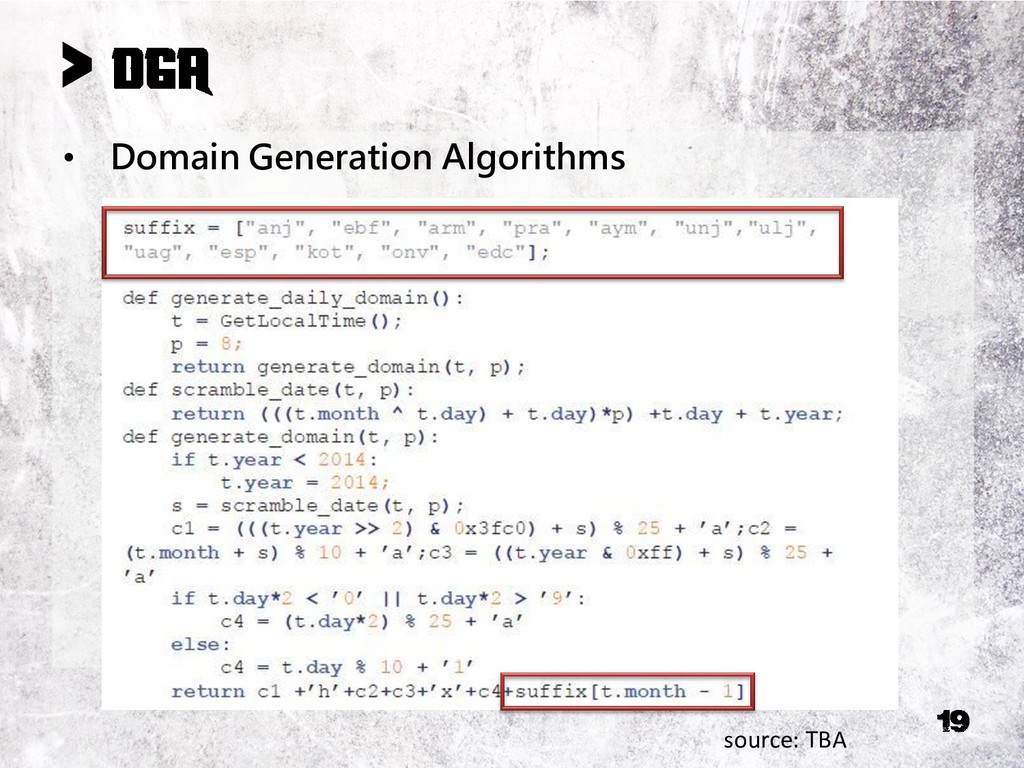
> • Domain Generation Algorithms source: TBA
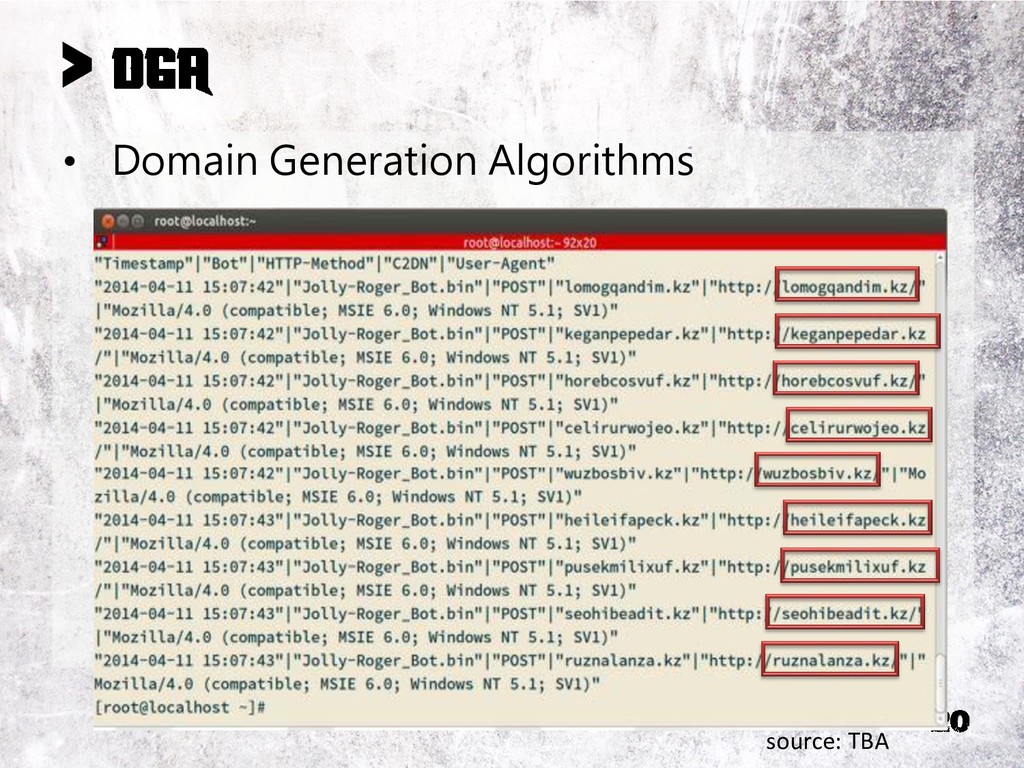
> • Domain Generation Algorithms source: TBA
None
None
> • before
> • before
>
>
None
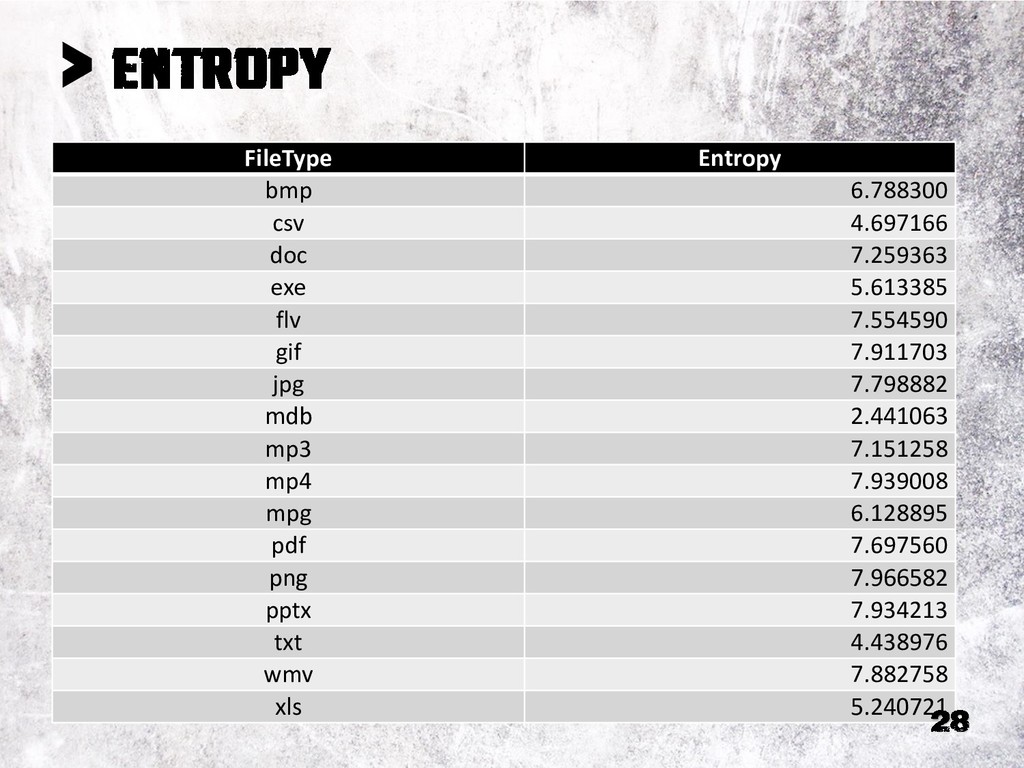
> FileType Entropy bmp 6.788300 csv 4.697166 doc 7.259363 exe
5.613385 flv 7.554590 gif 7.911703 jpg 7.798882 mdb 2.441063 mp3 7.151258 mp4 7.939008 mpg 6.128895 pdf 7.697560 png 7.966582 pptx 7.934213 txt 4.438976 wmv 7.882758 xls 5.240721
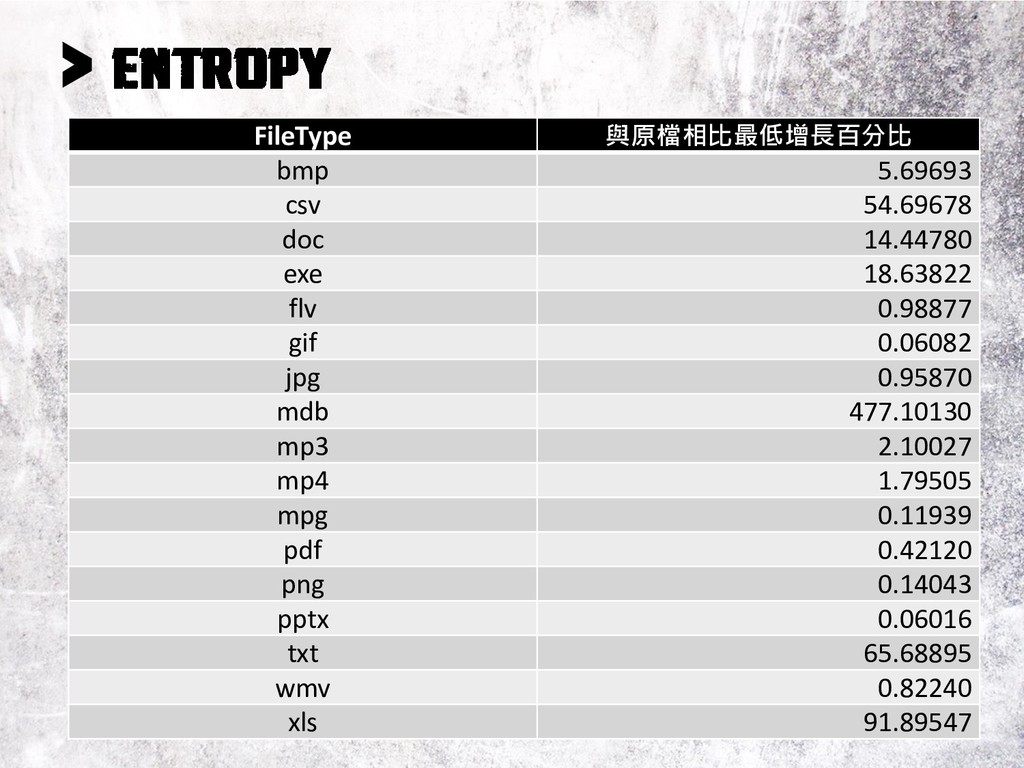
> FileType 與原檔相比最低增長百分比 bmp 5.69693 csv 54.69678 doc 14.44780 exe
18.63822 flv 0.98877 gif 0.06082 jpg 0.95870 mdb 477.10130 mp3 2.10027 mp4 1.79505 mpg 0.11939 pdf 0.42120 png 0.14043 pptx 0.06016 txt 65.68895 wmv 0.82240 xls 91.89547
None
None
>
> source: TBA
──
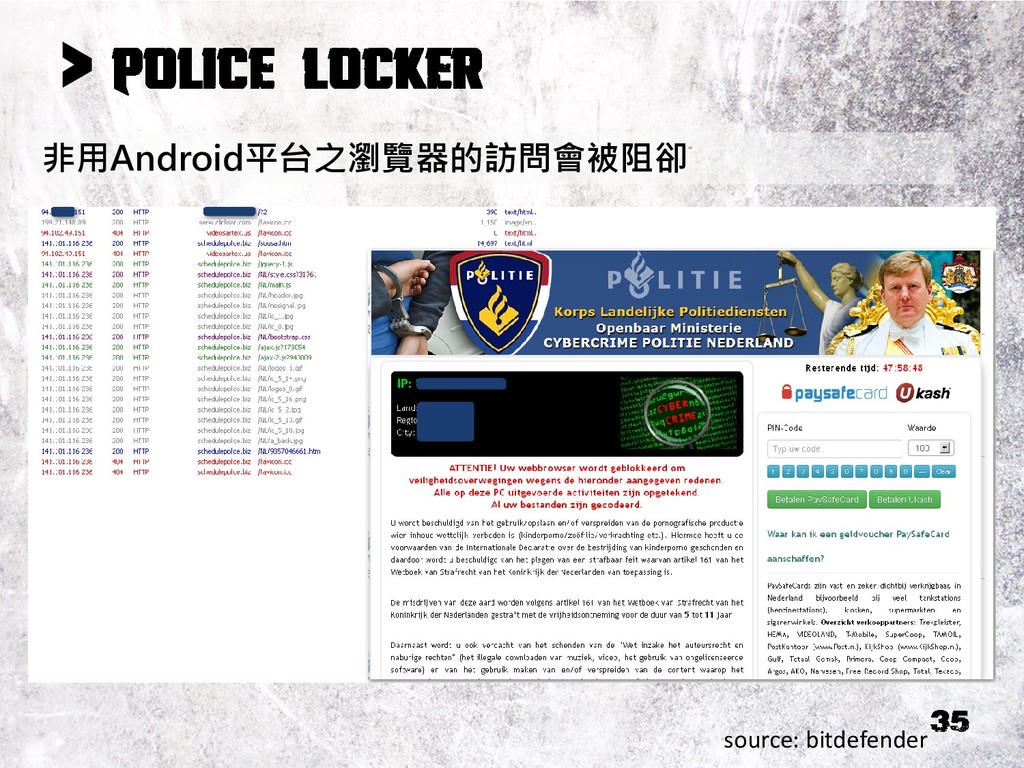
> 非用Android平台之瀏覽器的訪問會被阻卻 source: bitdefender
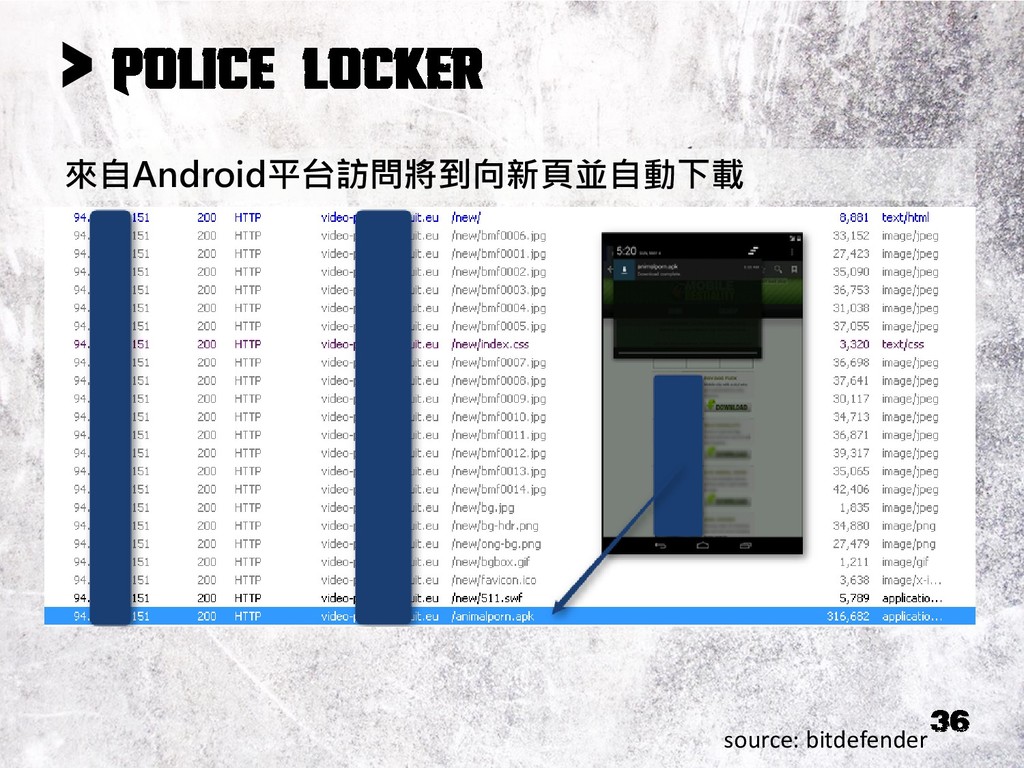
> 來自Android平台訪問將到向新頁並自動下載 source: bitdefender
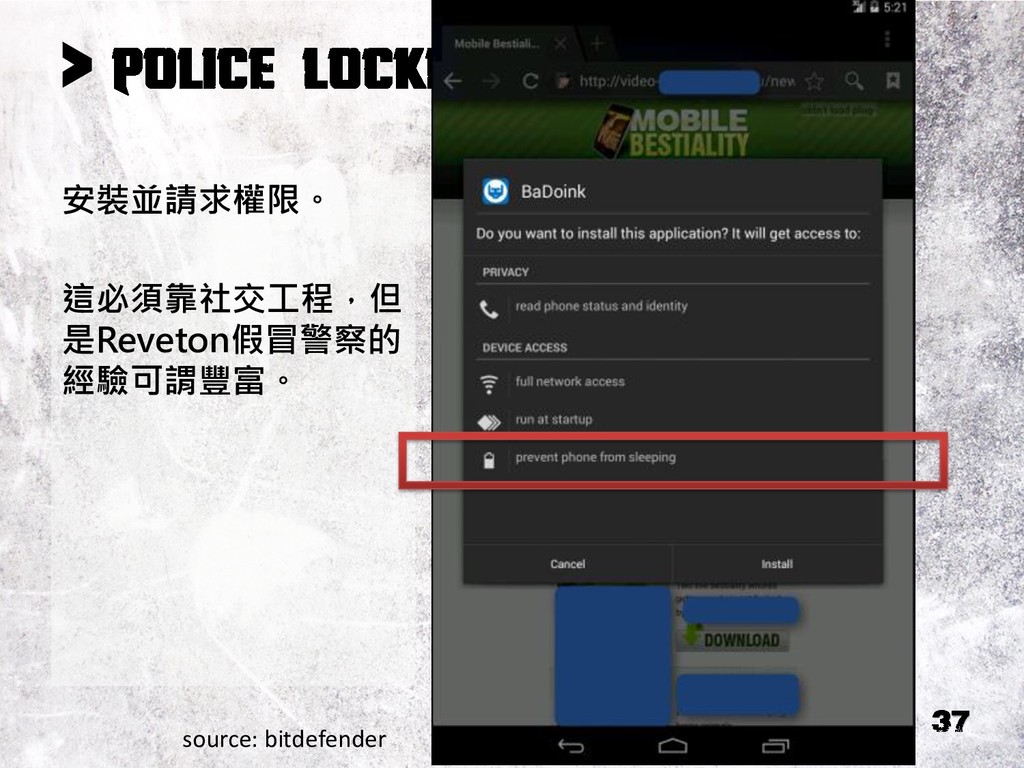
> 安裝並請求權限。 這必須靠社交工程,但 是Reveton假冒警察的 經驗可謂豐富。 source: bitdefender
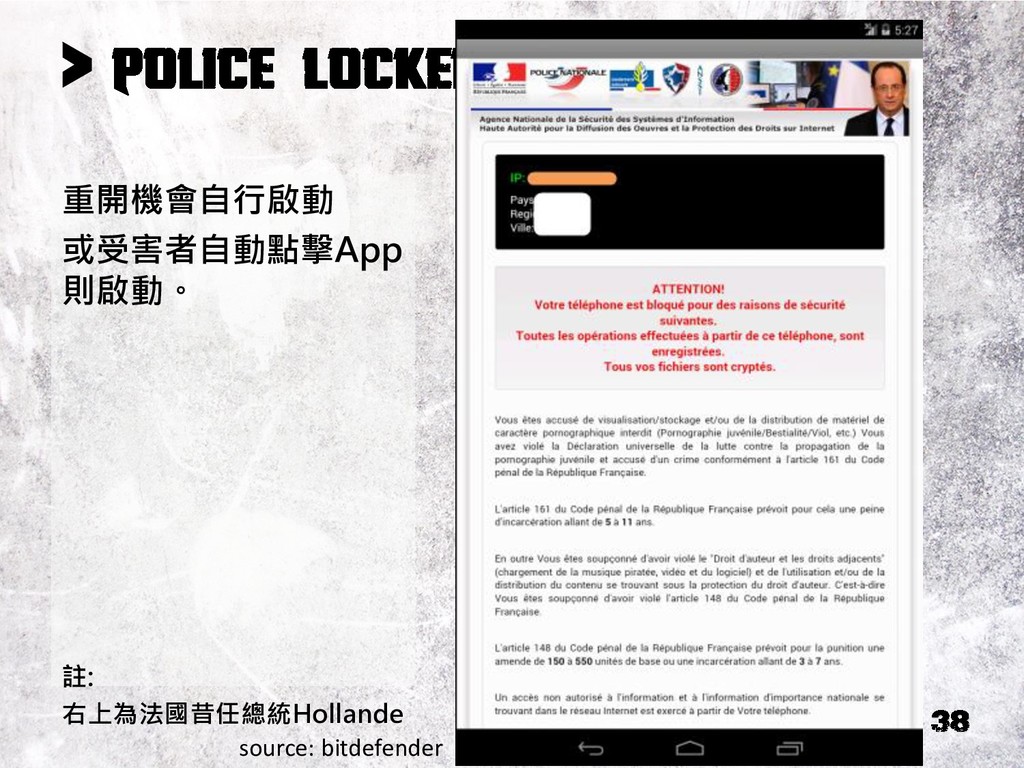
> 重開機會自行啟動 或受害者自動點擊App 則啟動。 註: 右上為法國昔任總統Hollande source: bitdefender
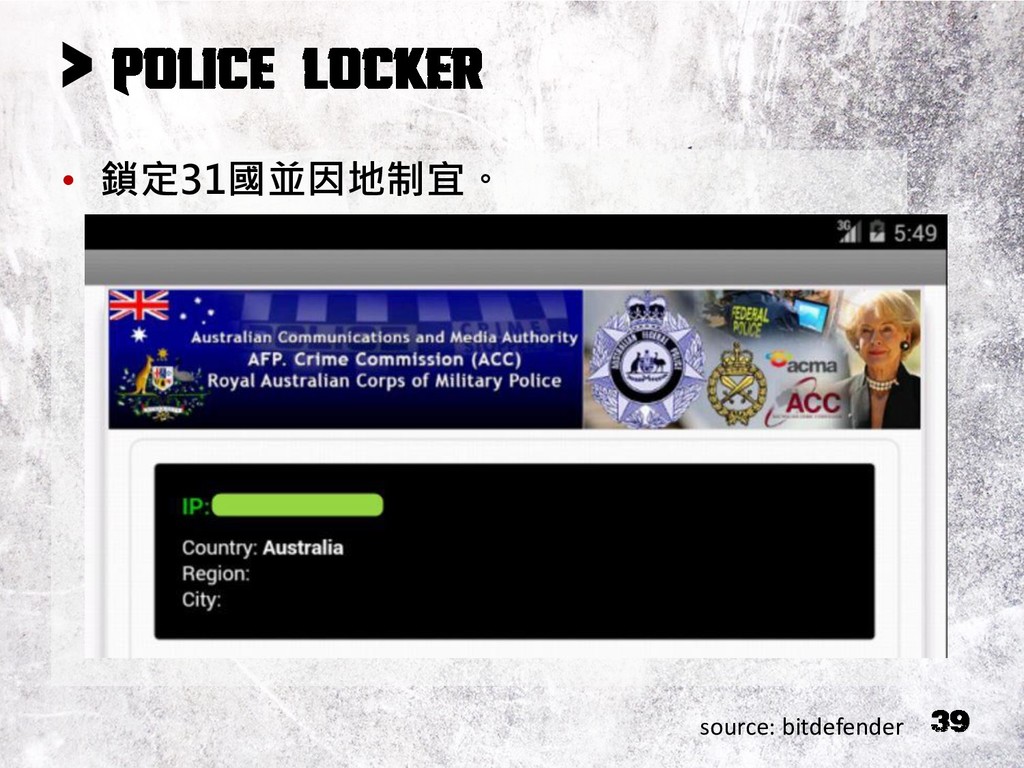
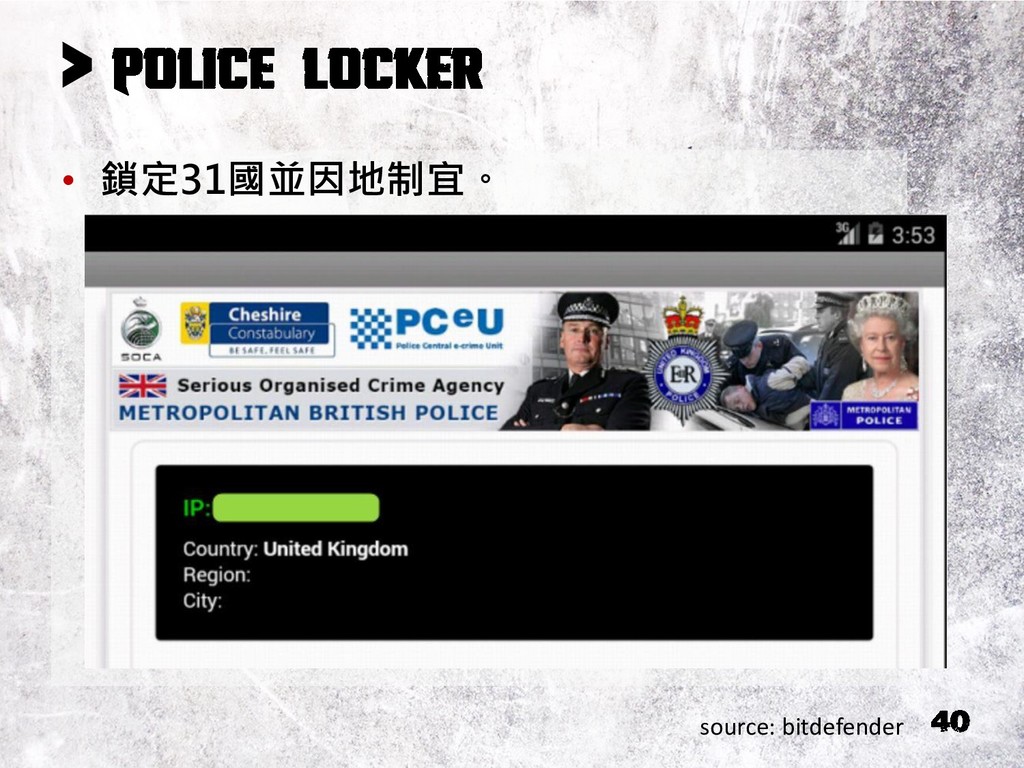
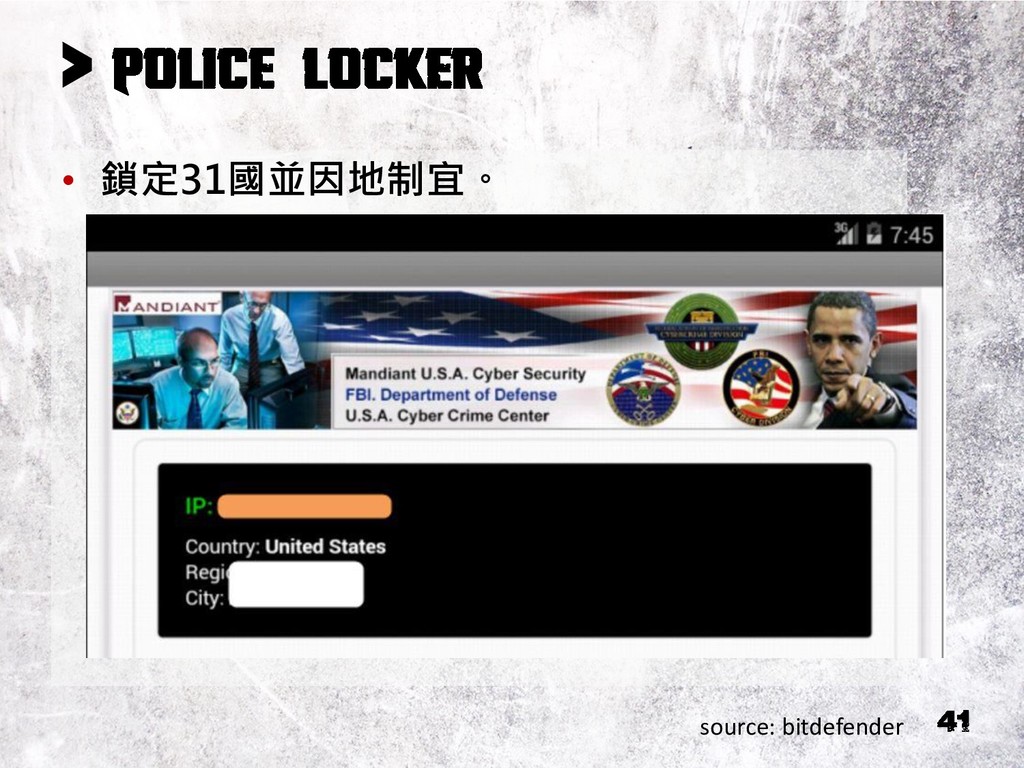
> • 鎖定31國並因地制宜。 source: bitdefender
> • 鎖定31國並因地制宜。 source: bitdefender
> • 鎖定31國並因地制宜。 source: bitdefender
──
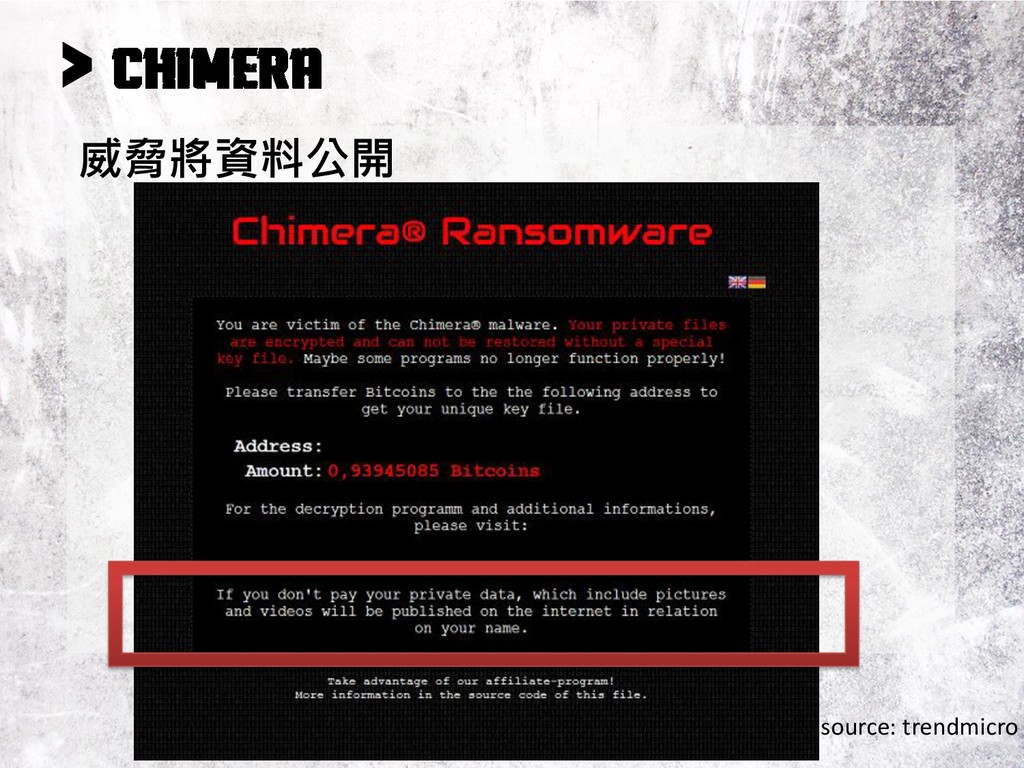
> 威脅將資料公開 source: trendmicro
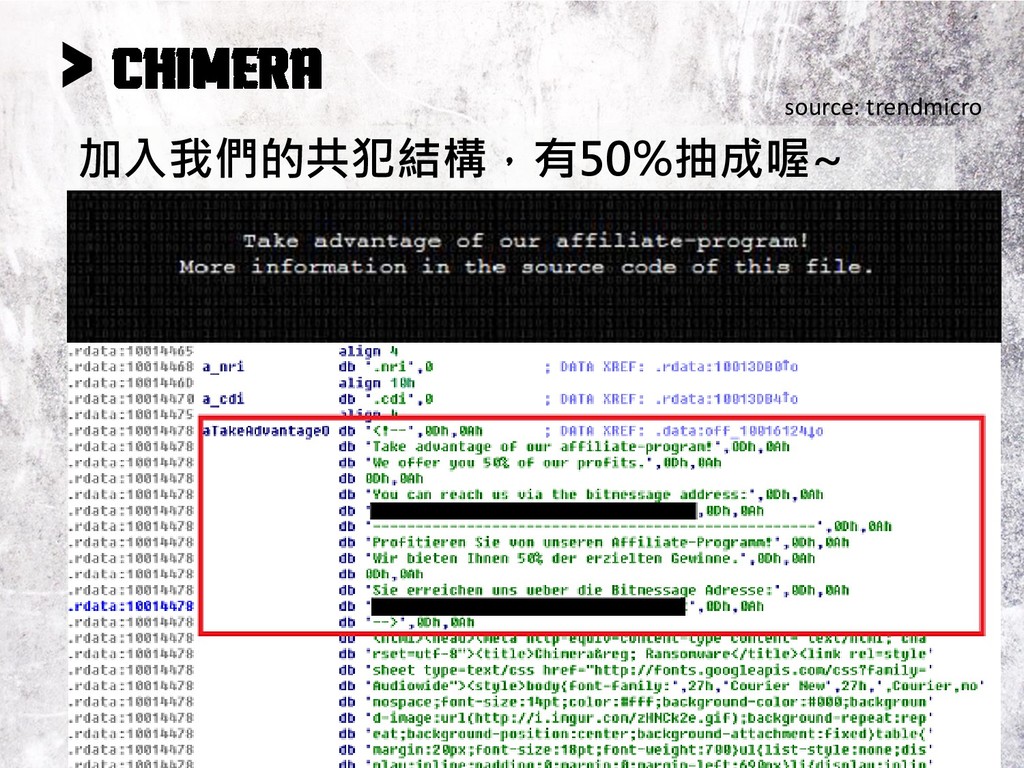
> 加入我們的共犯結構,有50%抽成喔~ source: trendmicro
> 加入我們的共犯結構,有50%抽成喔~
──
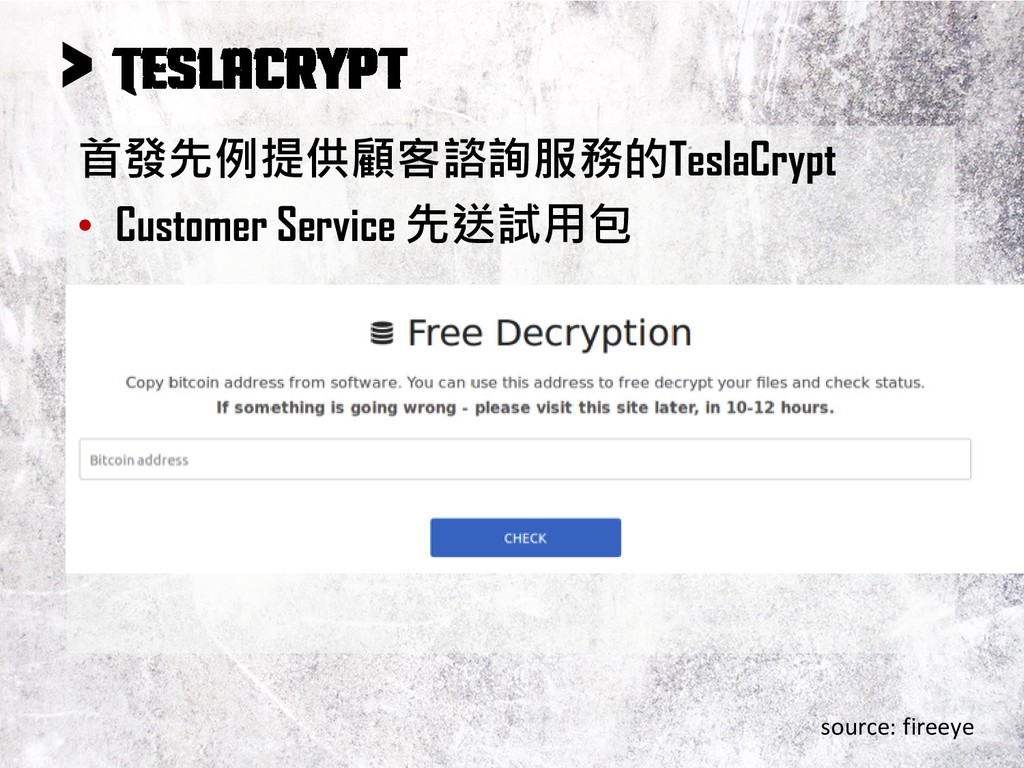
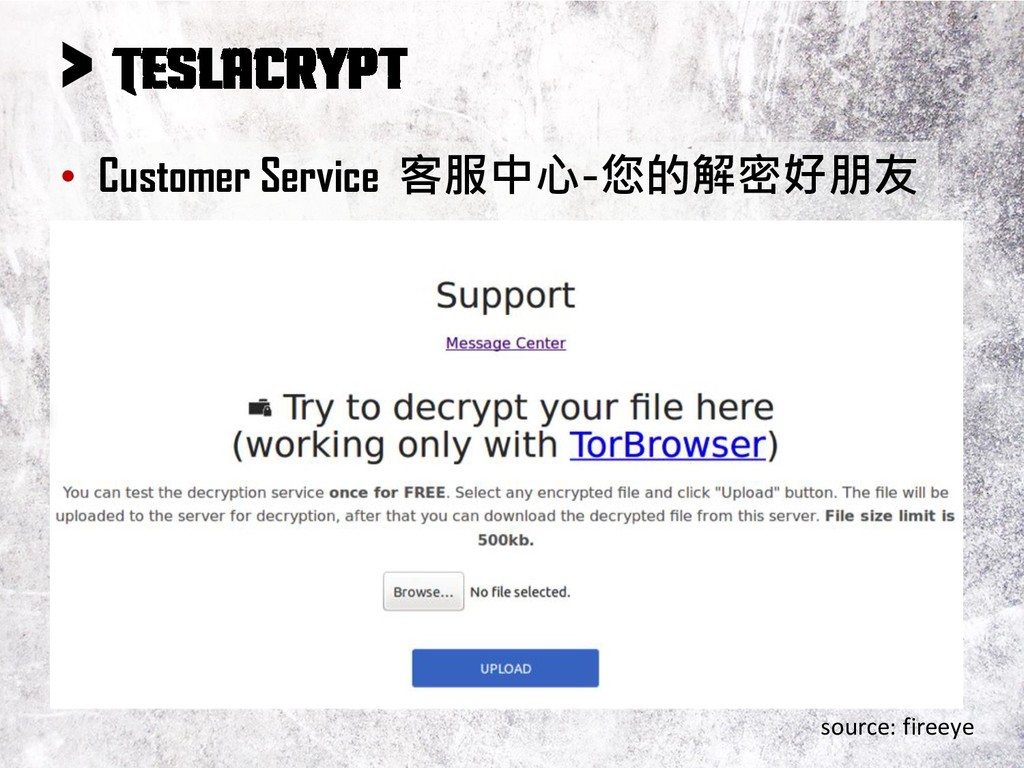
首發先例提供顧客諮詢服務的TeslaCrypt • Customer Service 先送試用包 > source: fireeye
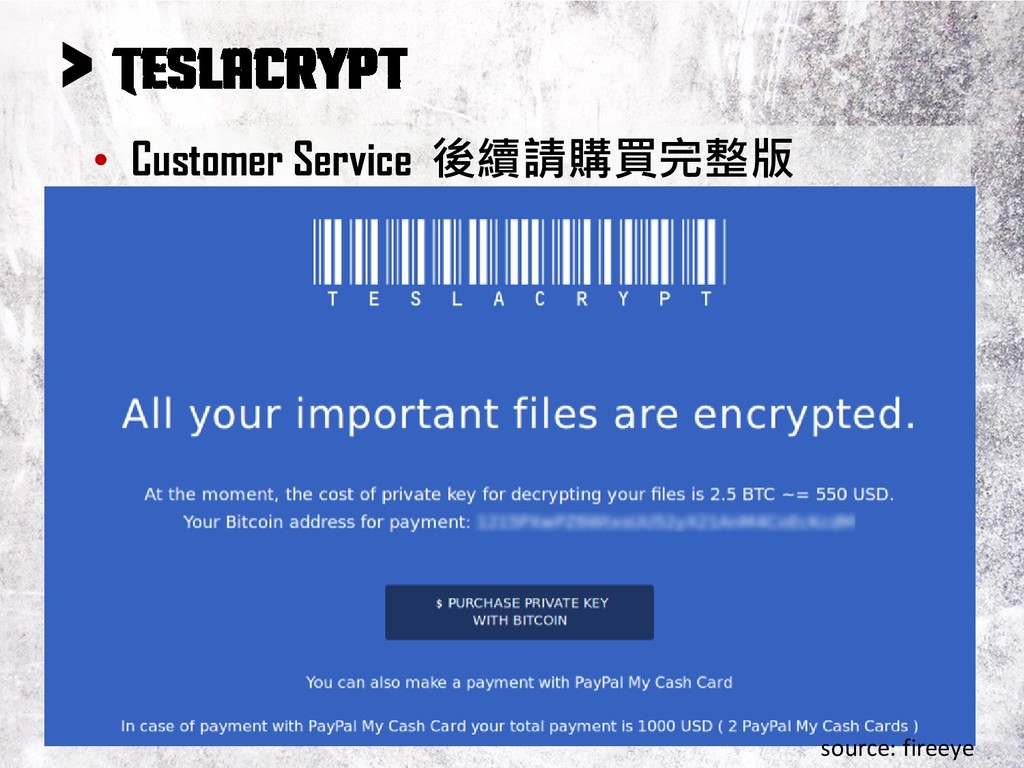
> • Customer Service 後續請購買完整版 source: fireeye
> • Customer Service 後續請購買完整版 source: fireeye
> • Customer Service 客服中心-您的解密好朋友 source: fireeye
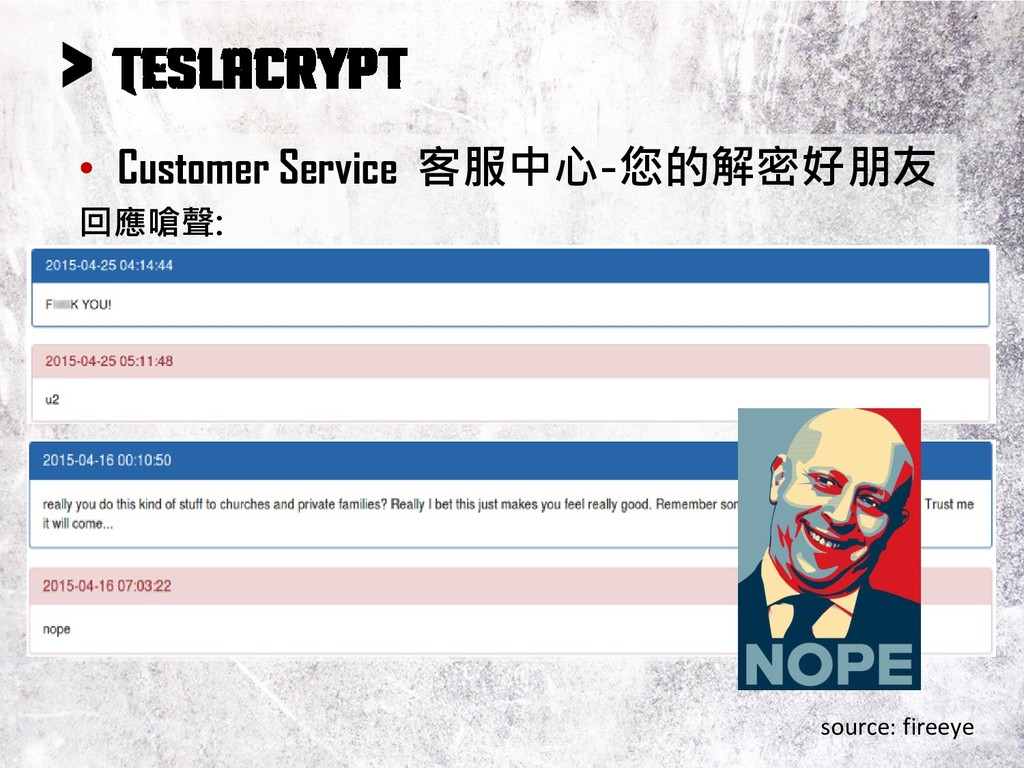
> • Customer Service 客服中心-您的解密好朋友 回應嗆聲: source: fireeye
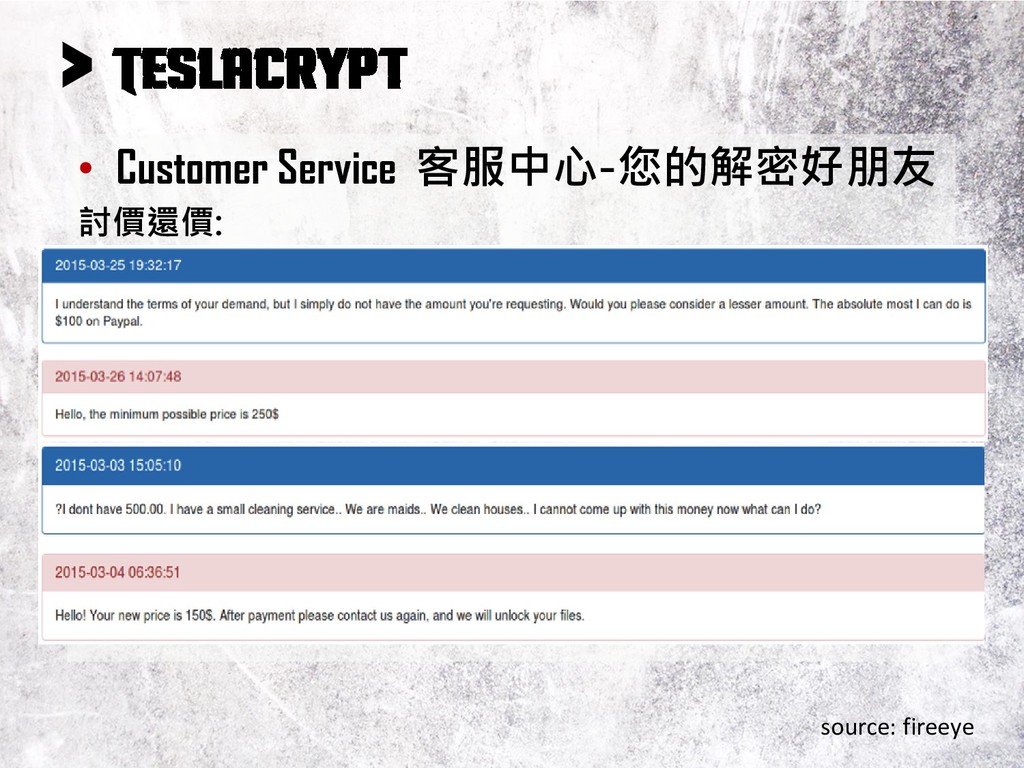
> • Customer Service 客服中心-您的解密好朋友 討價還價: source: fireeye
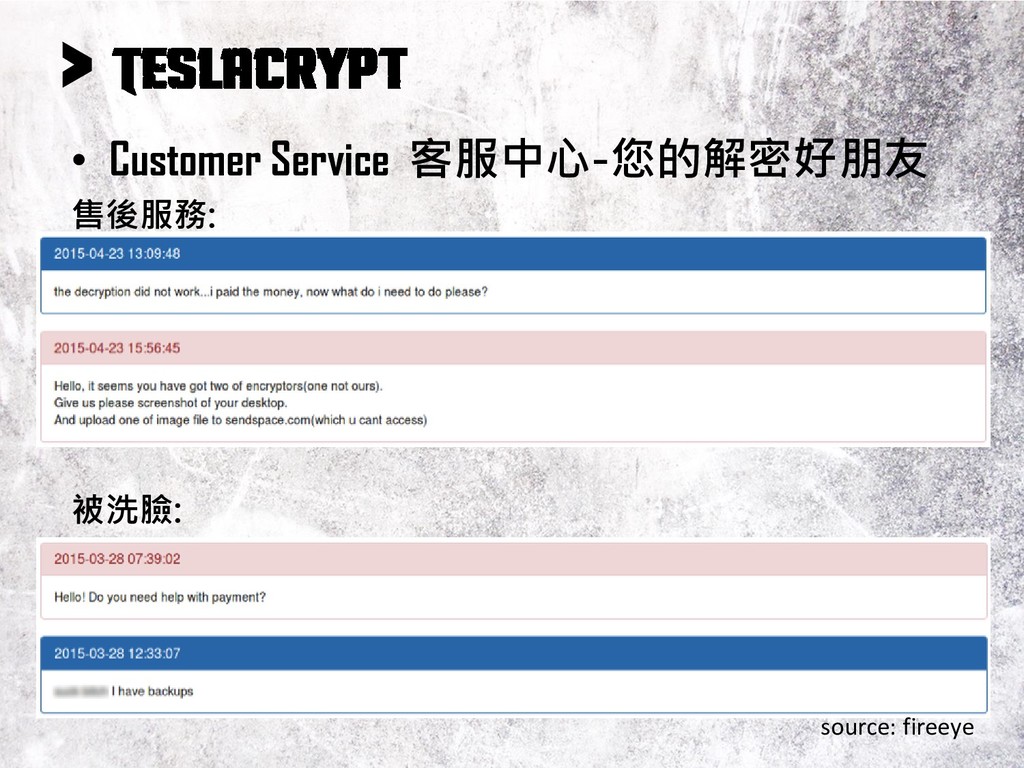
> • Customer Service 客服中心-您的解密好朋友 售後服務: 被洗臉: source: fireeye
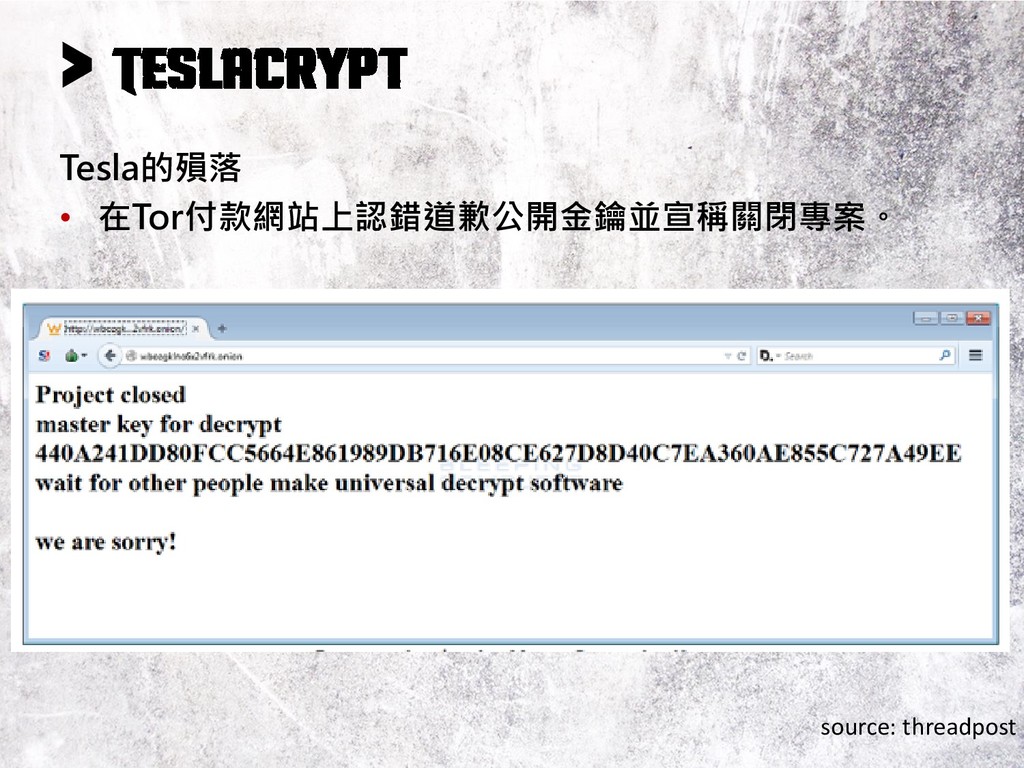
> Tesla的殞落 • 在Tor付款網站上認錯道歉公開金鑰並宣稱關閉專案。 source: threadpost
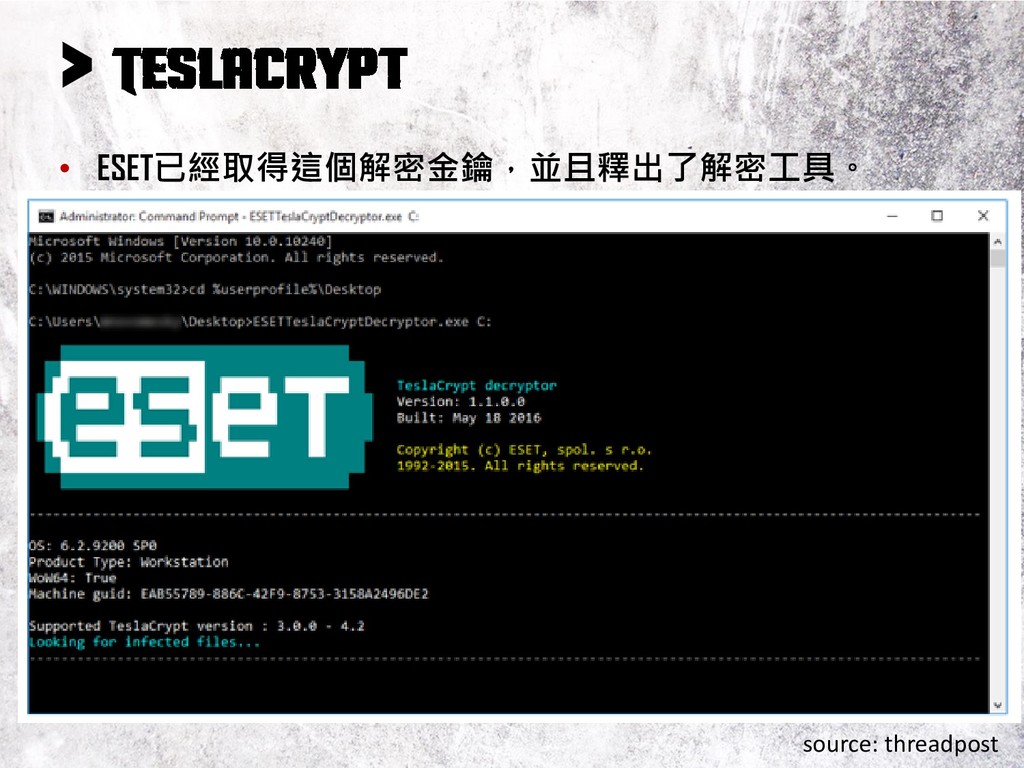
> • ESET已經取得這個解密金鑰,並且釋出了解密工具。 source: threadpost
( ) ──
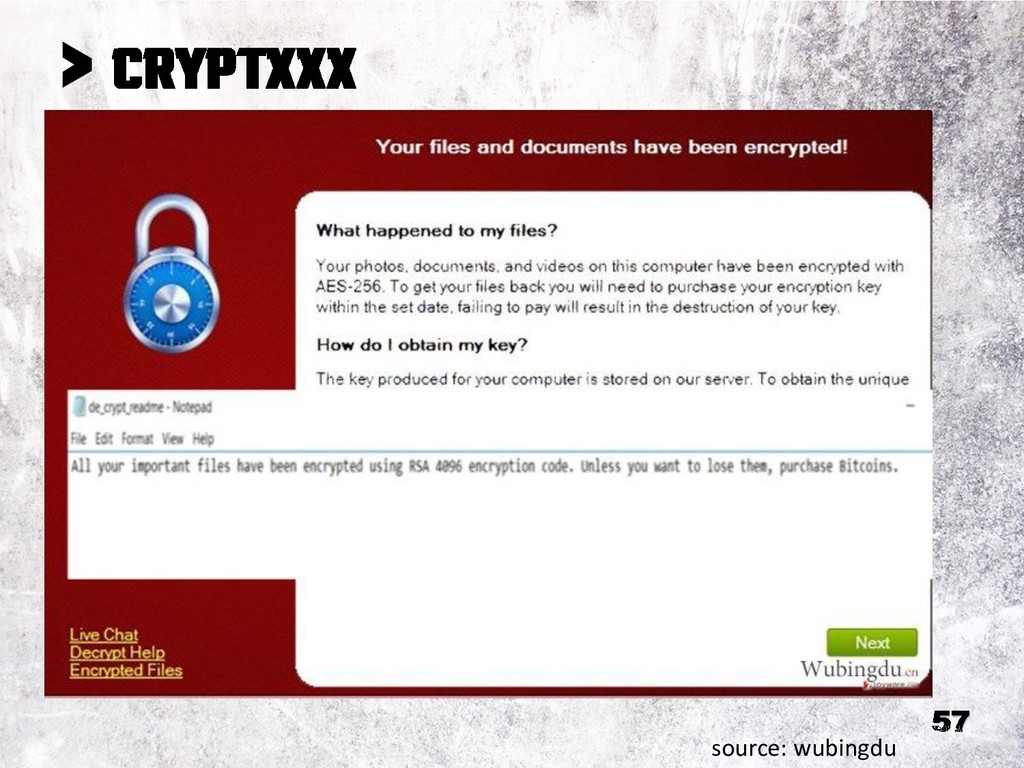
> source: wubingdu
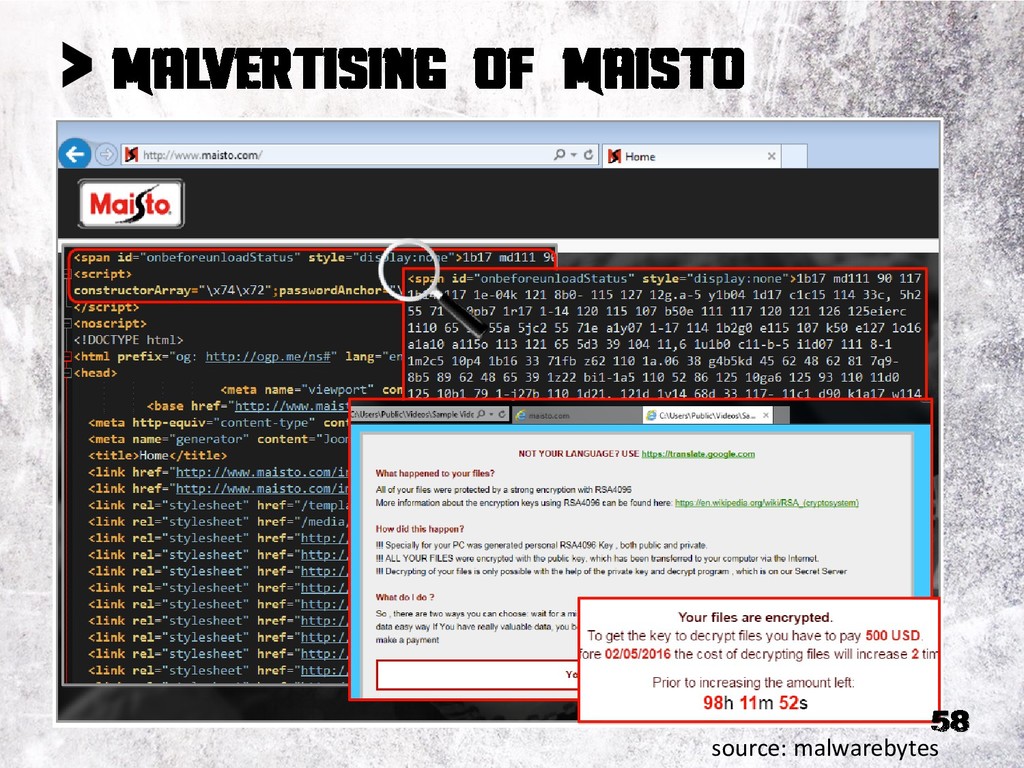
> source: malwarebytes
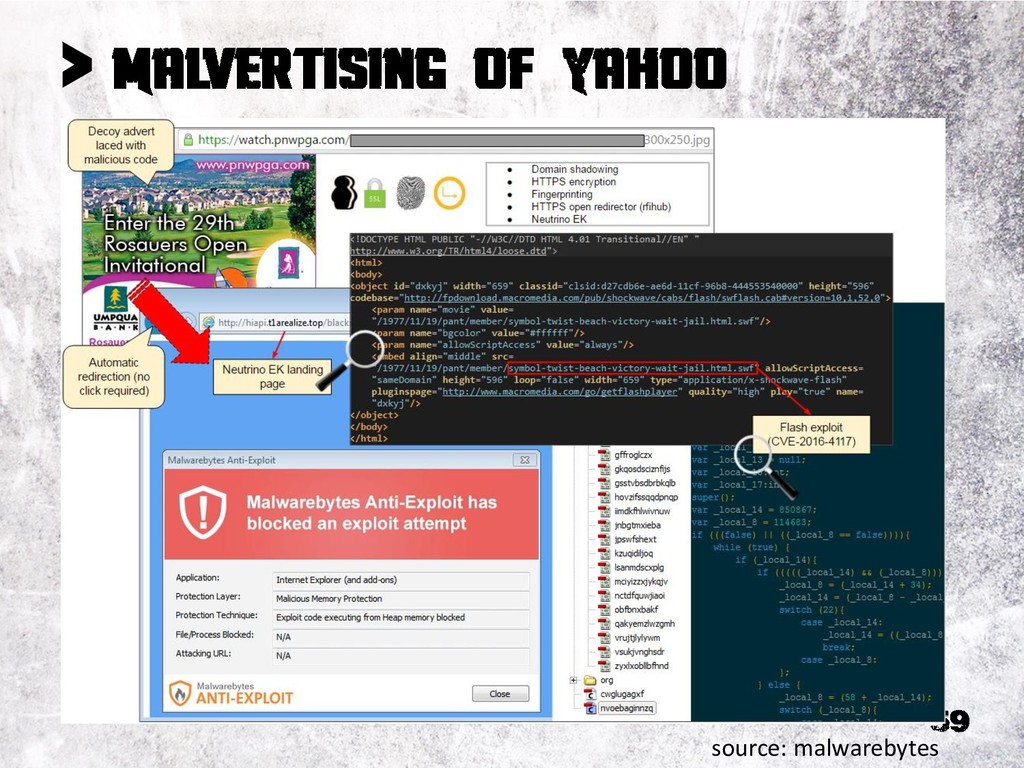
> source: malwarebytes
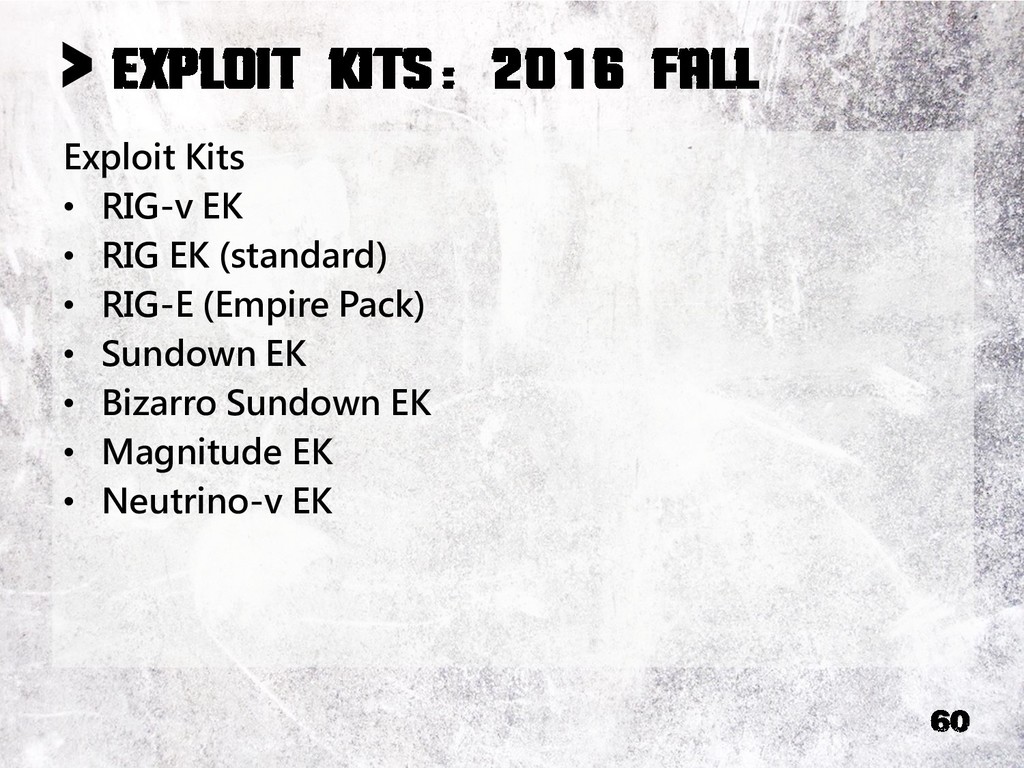
> Exploit Kits • RIG-v EK • RIG EK (standard)
• RIG-E (Empire Pack) • Sundown EK • Bizarro Sundown EK • Magnitude EK • Neutrino-v EK
──
>
──
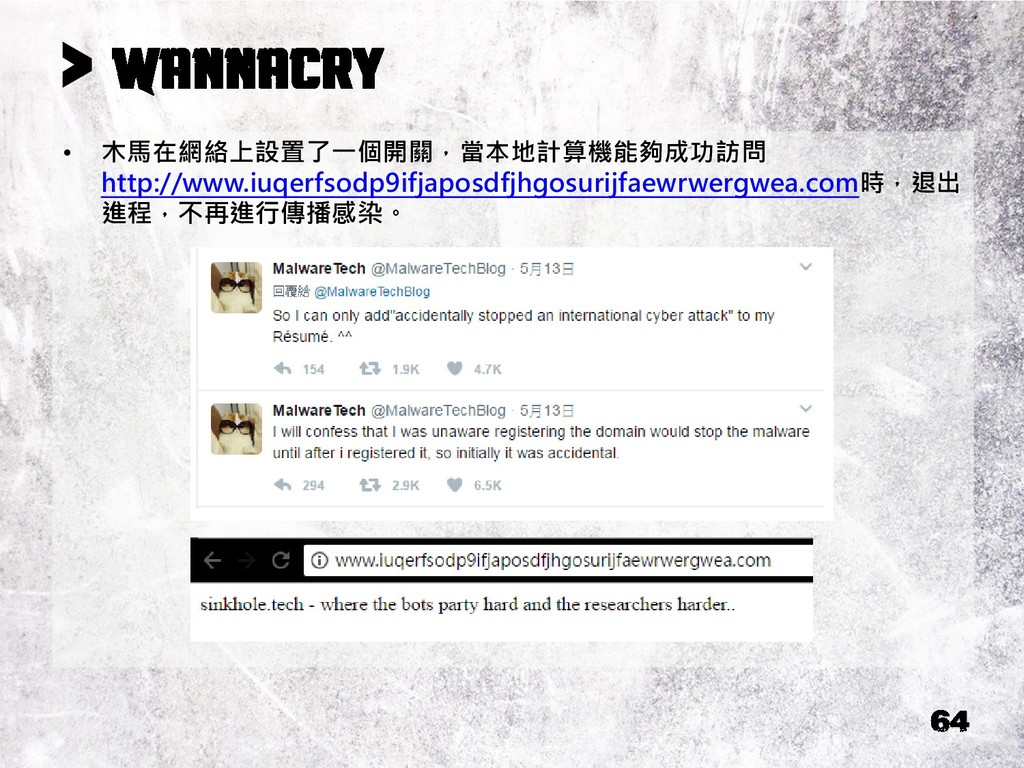
> • 木馬在網絡上設置了一個開關,當本地計算機能夠成功訪問 http://www.iuqerfsodp9ifjaposdfjhgosurijfaewrwergwea.com時,退出 進程,不再進行傳播感染。
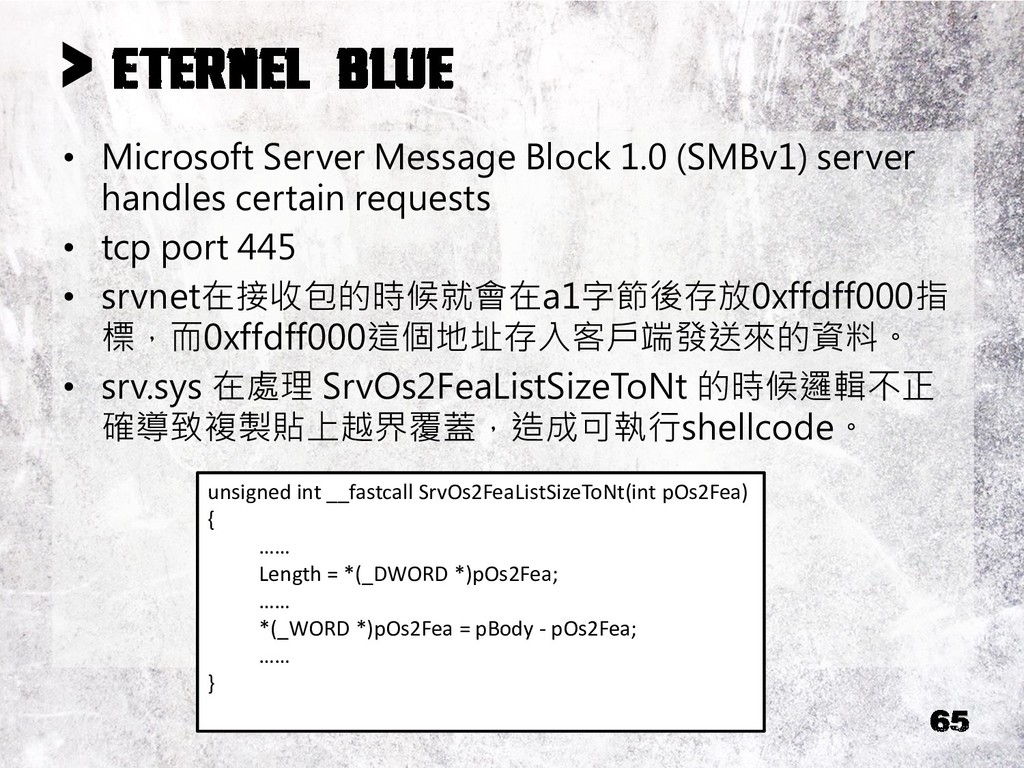
> • Microsoft Server Message Block 1.0 (SMBv1) server handles
certain requests • tcp port 445 • srvnet在接收包的時候就會在a1字節後存放0xffdff000指 標,而0xffdff000這個地址存入客戶端發送來的資料。 • srv.sys 在處理 SrvOs2FeaListSizeToNt 的時候邏輯不正 確導致複製貼上越界覆蓋,造成可執行shellcode。 unsigned int __fastcall SrvOs2FeaListSizeToNt(int pOs2Fea) { …… Length = *(_DWORD *)pOs2Fea; …… *(_WORD *)pOs2Fea = pBody - pOs2Fea; …… }
──
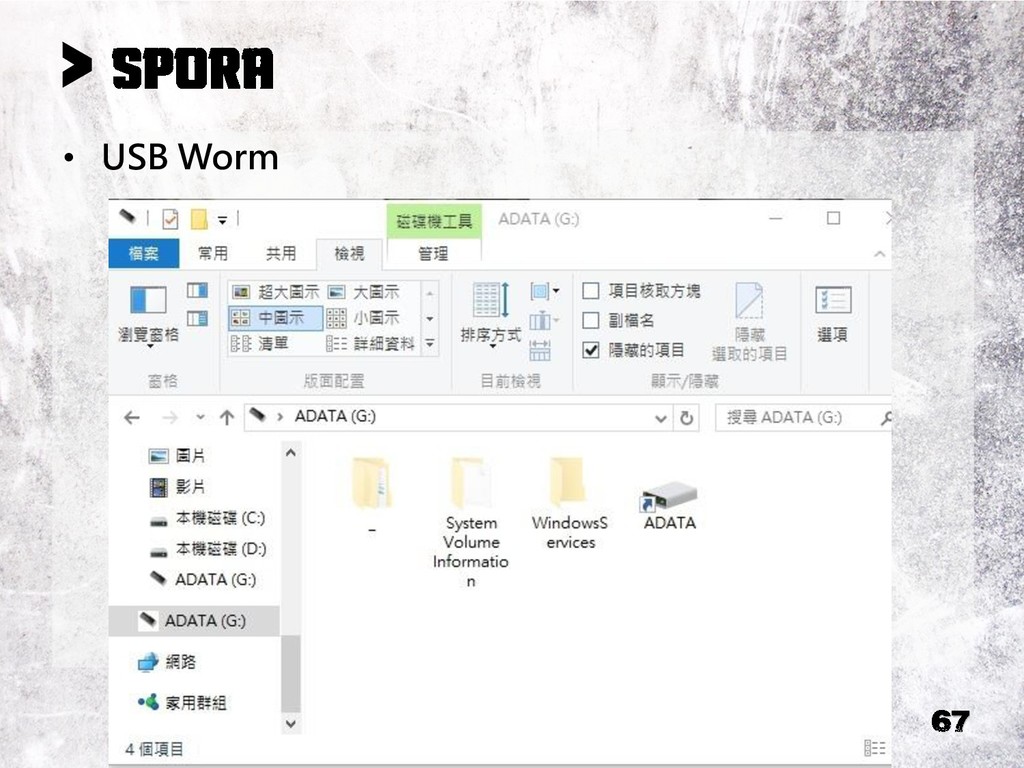
> • USB Worm
>
None
None
>
> • 加殼技術: – 一種對EXE檔案的數據壓縮及加密保護,可自我解壓檔案,並能隱藏解壓 進程。 • 混淆技術: – 將程式的代碼,轉換成一種功能上等價,但是難於閱讀和理解的形式。
• 2006年時就有80%~90%的惡意軟體使用加殼技術,其中50%使用 大眾技術或舊加殼,但相信現在這比率更高。使用Entropy、 Signature、 PE header偵測加殼等方式皆有缺陷。防毒軟體對於任 何新出的加殼技術防禦能力較低。 • 混淆是所有良性軟體開發者與惡意軟體開發者的基本要求,一定程度 的混淆能減少開發技術被解譯拷貝竊取。
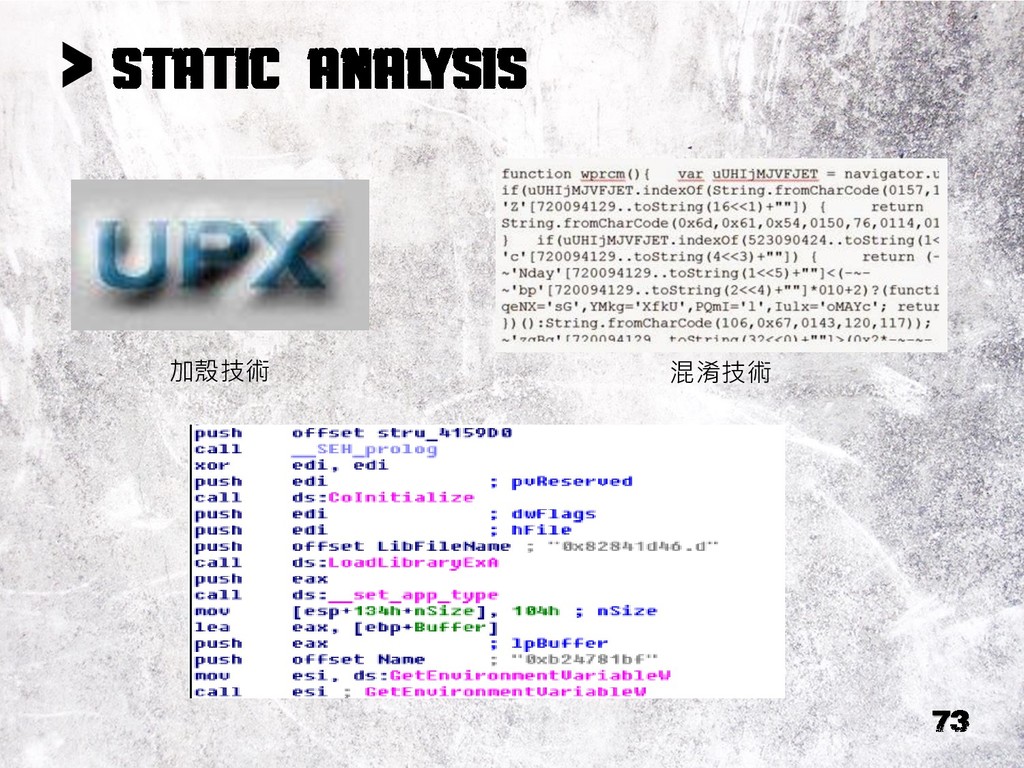
> 加殼技術 混淆技術
>
None
>
>
>
>
None


 notsurprised
 satai
 izumiyama_lab
 butchi
 prinlab
 nzw0301
 rikkabotan7
 kento1109
 kentaitakura
 eumesy
 kzmssk
 ontheslope
 chck
 szymonslowik
 katarinadahlin
 samanthasiow
 helenjbeal
 aleyda
 jonoalderson
 axbom
 honzajavorek
 jlugia
 tmiket
 keathley