Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
20171114inCyberAgent
Search
okazaki hajime
November 14, 2017
Technology
2.5k
3
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
20171114inCyberAgent
https://connpass.com/event/70903/
okazaki hajime
November 14, 2017
More Decks by okazaki hajime
See All by okazaki hajime
20220810_seccam
okazakihajime
0
160
20171222_owasp_okinawa
okazakihajime
0
930
20170218inOkinawa
okazakihajime
0
250
Other Decks in Technology
See All in Technology
リアクションエンジニア ― 小さなリアクションから、話しかけやすい組織をつくる ―
ryuguyana
1
130
新米を「売り越さない」、Aurora DSQLで作る在庫ゼロ死守の限定ドロップEC
yama3133
0
180
SLOを阻む不安
sraku2159
0
230
OneLakeをデータソースにした AI Search(Foundry IQ)の ライフサイクル管理
ryuseiiida
0
230
詳解 never 型 - ボトム型の性質を深掘り
nealle
0
150
Microsoft Entra Kerberos で実現するクラウド デバイス管理
tamaiyutaro
2
590
生き様としてのSRE
hokkai7go
1
170
Maestro MCPとClaude Code Skillsによる自律的なE2Eテスト支援
asmz
0
420
コードレビューをなくして見えたもの
henteko
0
140
新卒エンジニア、 介護士になる
ryu1013
1
690
bpf_arenaとstruct_opsを使うのが難しかった話
masu_mi
0
200
攻撃 3 時間 vs 復旧 10 時間。アクセスキー流出の非対称性を体感するために CTF を作った話
kazzpapa3
1
150
Featured
See All Featured
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Navigating Team Friction
lara
192
16k
Primal Persuasion: How to Engage the Brain for Learning That Lasts
tmiket
0
520
Fashionably flexible responsive web design (full day workshop)
malarkey
409
67k
Evolution of real-time – Irina Nazarova, EuRuKo, 2024
irinanazarova
9
1.7k
個人開発の失敗を避けるイケてる考え方 / tips for indie hackers
panda_program
123
22k
コードの90%をAIが書く世界で何が待っているのか / What awaits us in a world where 90% of the code is written by AI
rkaga
63
48k
Design in an AI World
tapps
1
380
Efficient Content Optimization with Google Search Console & Apps Script
katarinadahlin
PRO
1
970
How Software Deployment tools have changed in the past 20 years
geshan
3
35k
Agile Actions for Facilitating Distributed Teams - ADO2019
mkilby
0
330
CoffeeScript is Beautiful & I Never Want to Write Plain JavaScript Again
sstephenson
162
16k
Transcript
Dockerを始めて1週間の セキュリティエンジニア 2017/11/14(Tue) CyberAgent - AdtechStudio Security okazaki hajime
自己紹介 • 氏名:岡崎 創(おかざき はじめ) • 出身:埼玉県春日部市 (クレヨンしんちゃんの街) • 職歴: ◦ 3年くらい LAMP環境のフロントエンジニア
◦ その後、3年くらい 上記のインフラエンジニア(サーバエンジニア) ◦ その後、1年くらい Webアプリケーションの脆弱性診断 ◦ その後、サイバーエージェント アドテク本部に入社( 2015/6) • 現在:アドテク本部セキュリティグループに所属
今日はコンテナ縛り?!
本日は Docker Security Beginner
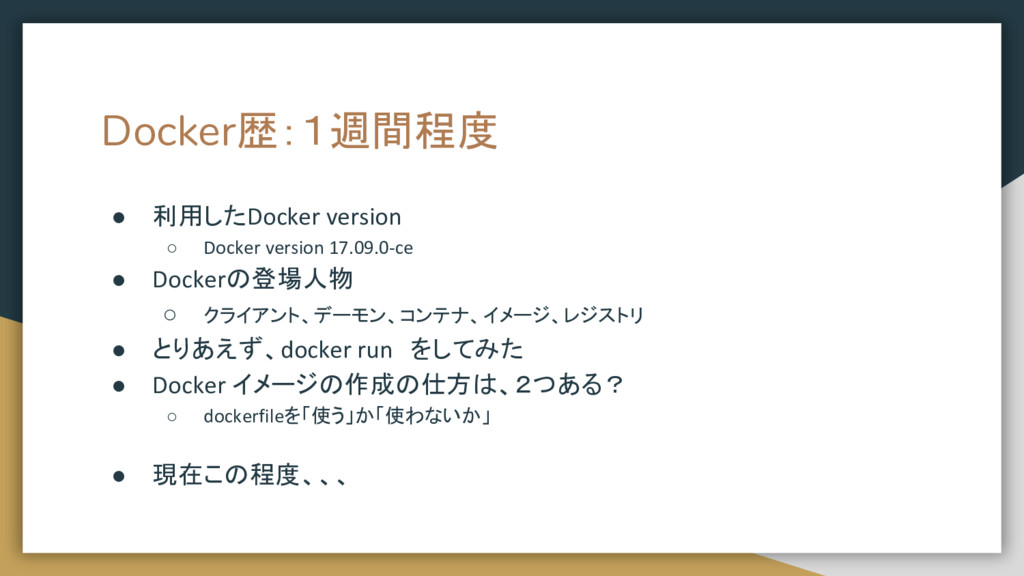
Docker歴:1週間程度 • 利用したDocker version ◦ Docker version 17.09.0-ce • Dockerの登場人物
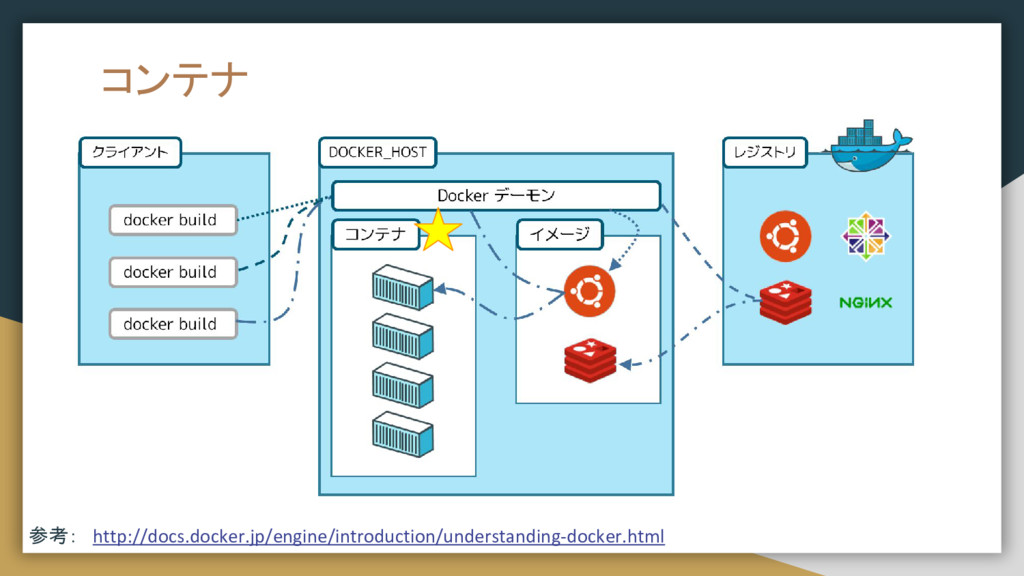
◦ クライアント、デーモン、コンテナ、イメージ、レジストリ • とりあえず、docker run をしてみた • Docker イメージの作成の仕方は、2つある? ◦ dockerfileを「使う」か「使わないか」 • 現在この程度、、、
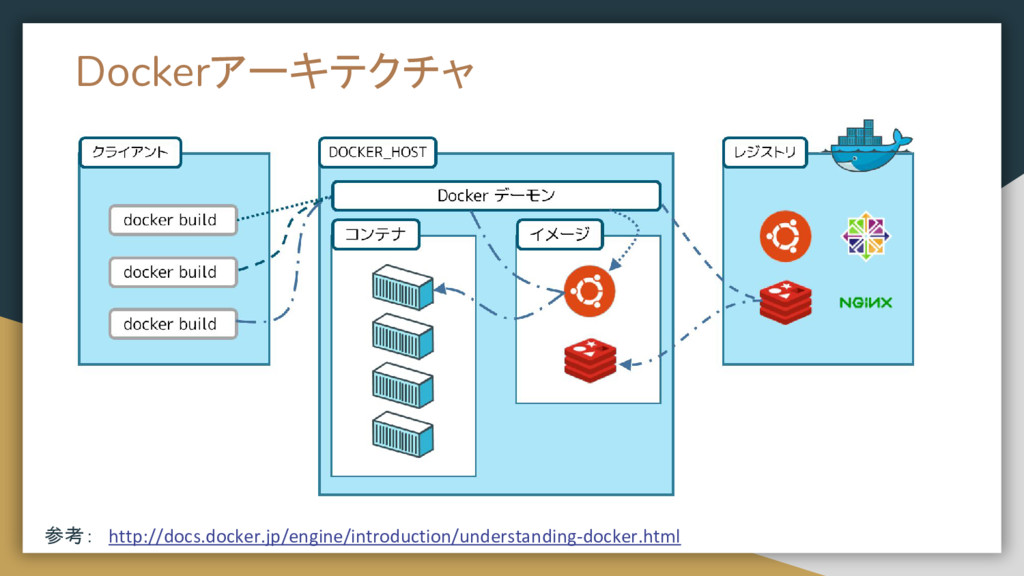
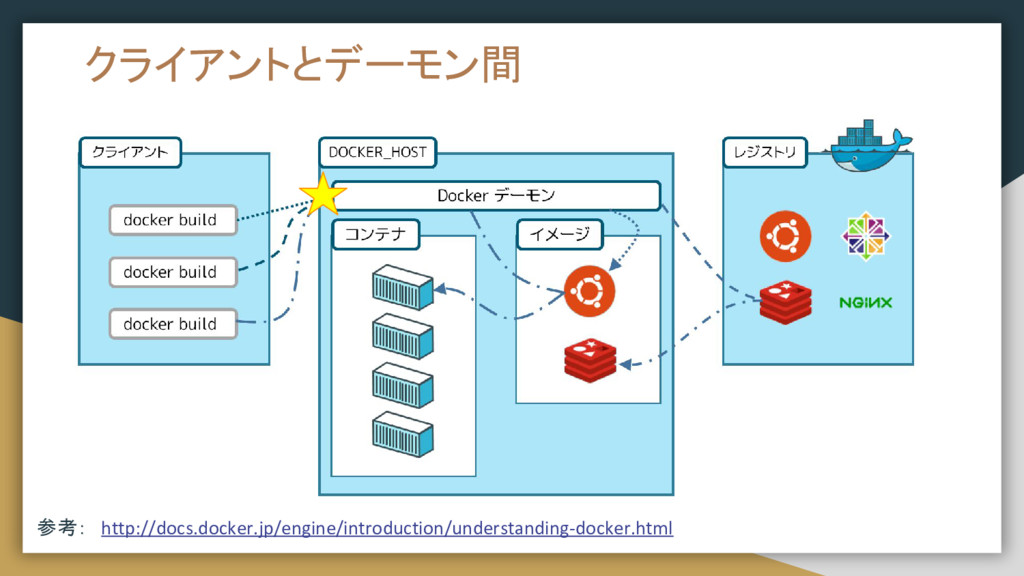
docker architecture 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html Dockerアーキテクチャ
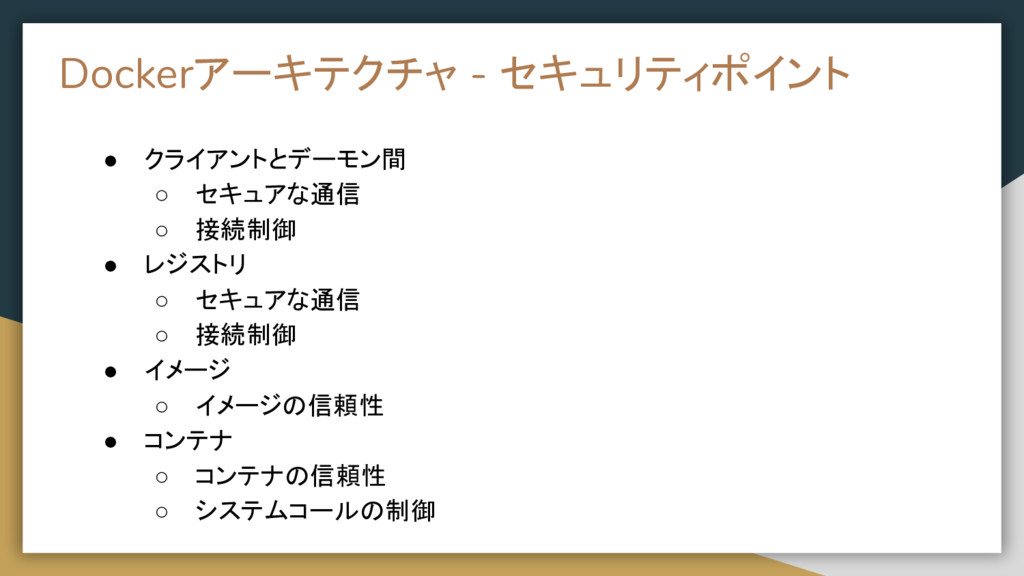
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 Dockerアーキテクチャ - セキュリティポイント
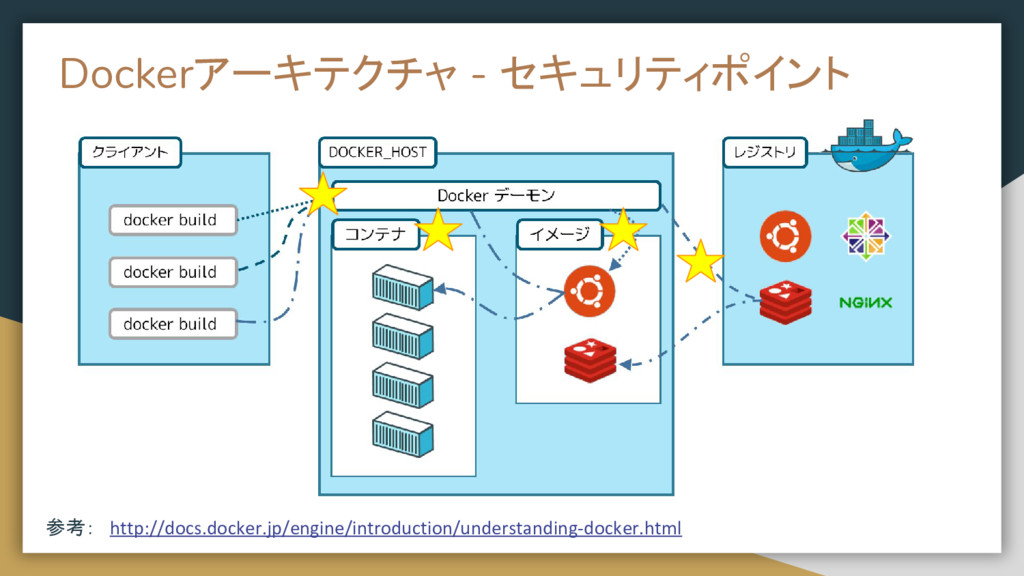
docker architecture - security point 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html Dockerアーキテクチャ - セキュリティポイント
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 クライアントとデーモン間
クライアントとデーモン間 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
クライアントとデーモン間 • TLSを利用して安全に接続しましょう • また、上記の証明書はクライアント認証にも使えます #デーモン設定に追加 $ vim /usr/lib/systemd/system/docker.service [Service]
# ExecStart=/usr/bin/dockerd ExecStart=/usr/bin/dockerd --tlsverify --tlscacert=ca.pem --tlscert=server.pem --tlskey=server-key.pem -H tcp://0.0.0.0:2376 $ systemctl daemon-reload $ systemctl restart docker
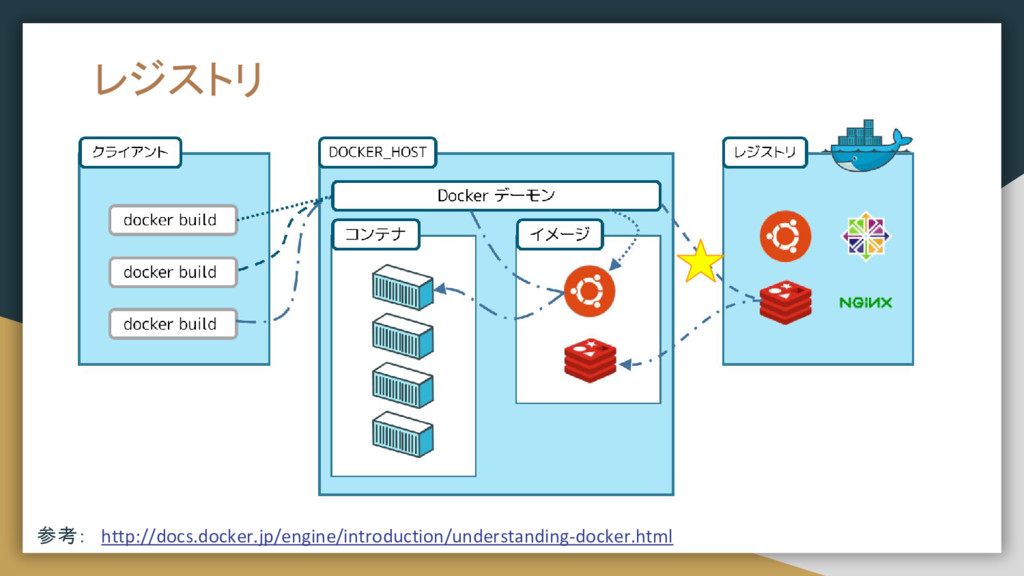
レジストリ 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 レジストリ
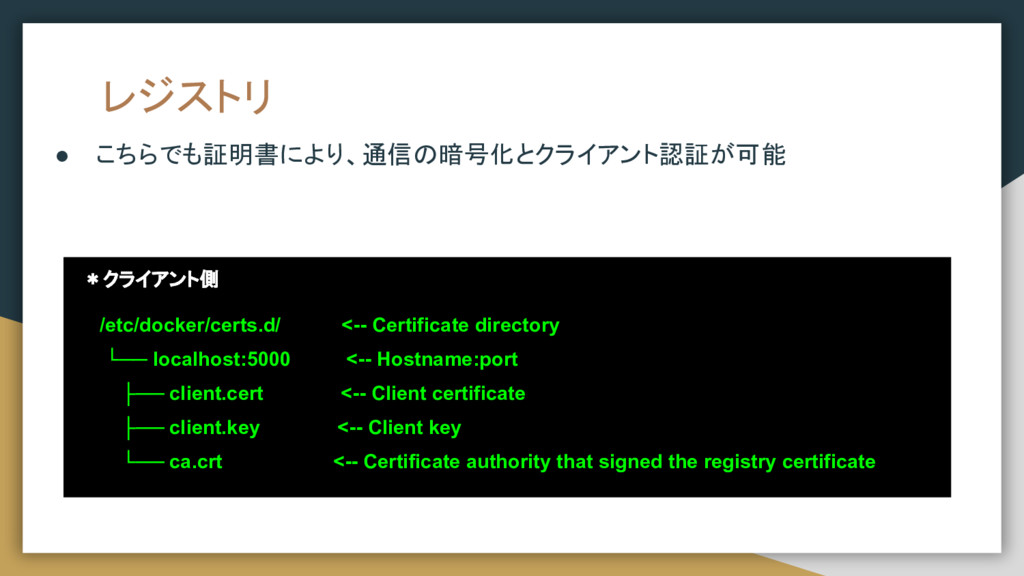
レジストリ • こちらでも証明書により、通信の暗号化とクライアント認証が可能 *クライアント側 /etc/docker/certs.d/ <-- Certificate directory └── localhost:5000
<-- Hostname:port ├── client.cert <-- Client certificate ├── client.key <-- Client key └── ca.crt <-- Certificate authority that signed the registry certificate
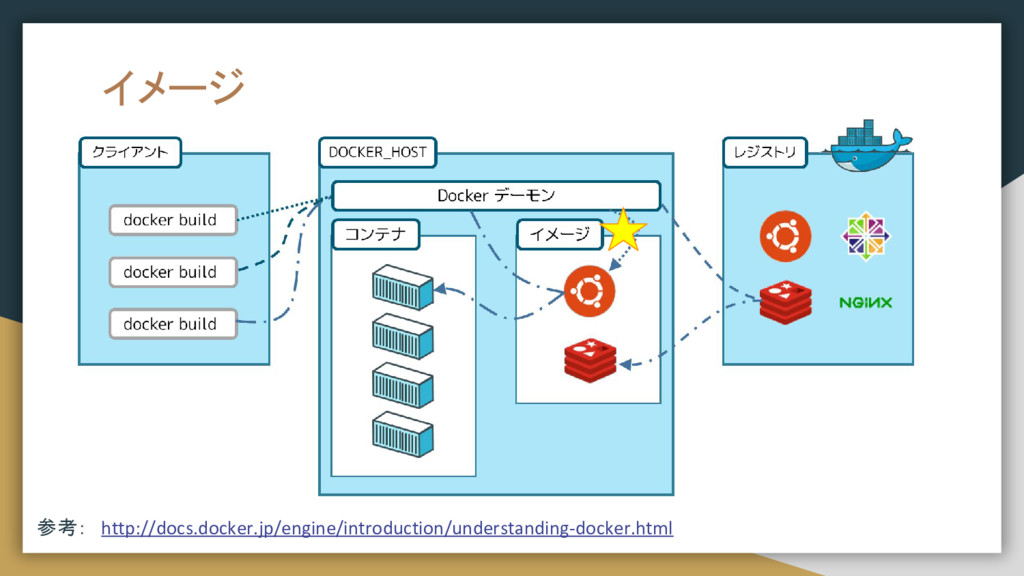
イメージ 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 イメージ
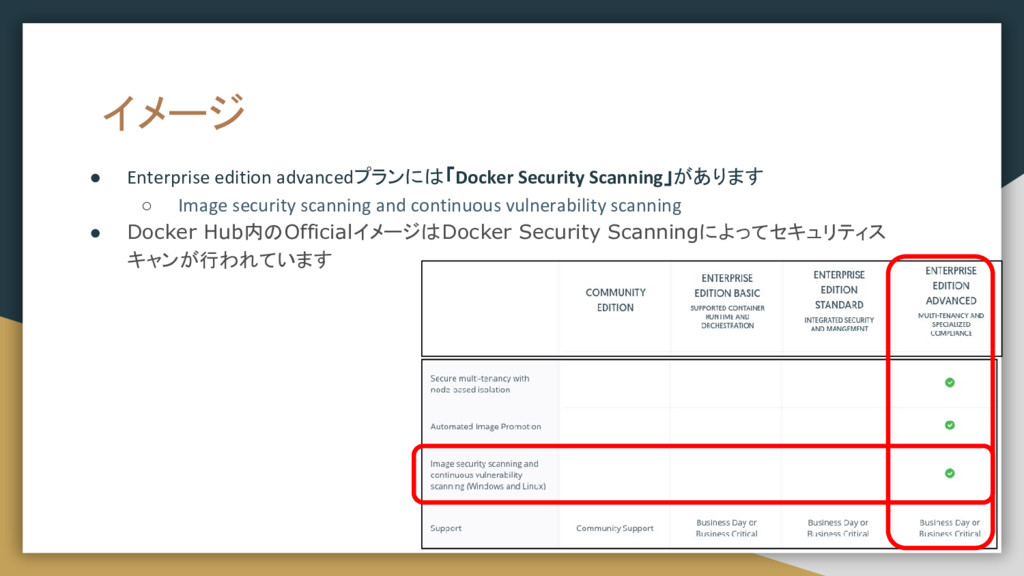
イメージ • Enterprise edition advancedプランには「Docker Security Scanning」があります ◦ Image security
scanning and continuous vulnerability scanning • Docker Hub内のOfficialイメージはDocker Security Scanningによってセキュリティス キャンが行われています
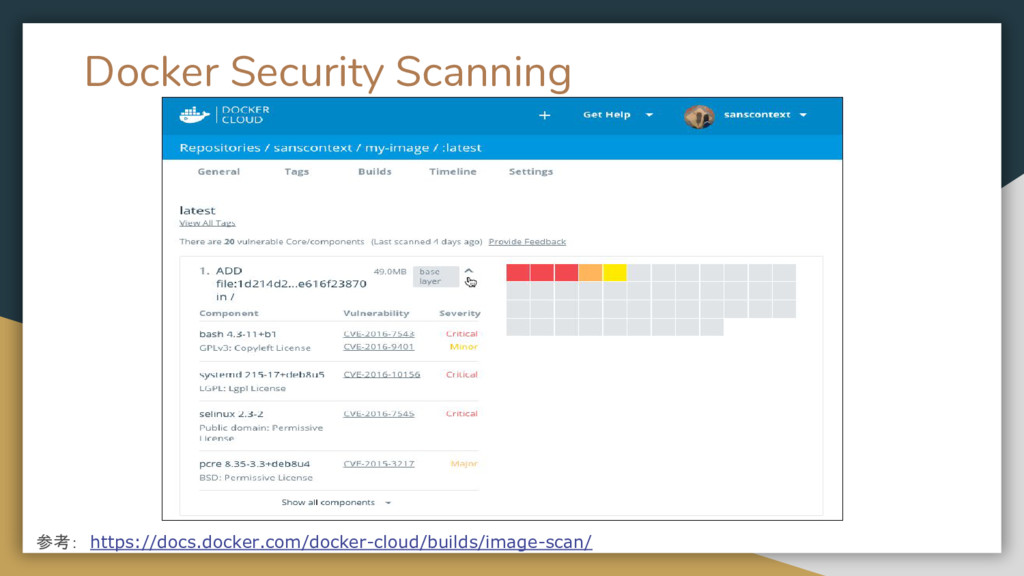
Docker Security Scanning CVE(Common Vulnerabilities and Exposures):脆弱性情報データベースと連動 参考: https://success.docker.com/Architecture/Docker_Reference_Architecture%3A_Securing_Docker_EE_and_Security_Best_Practices
Docker Security Scanning 参考: https://docs.docker.com/docker-cloud/builds/image-scan/
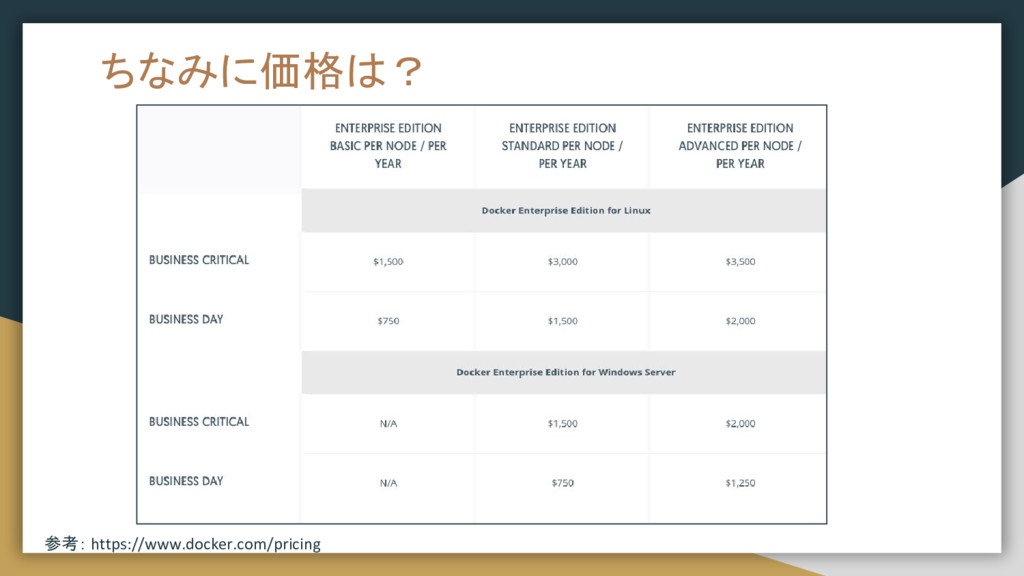
ちなみに価格は? 参考: https://www.docker.com/pricing
コンテナ 参考: http://docs.docker.jp/engine/introduction/understanding-docker.html
• クライアントとデーモン間 ◦ セキュアな通信 ◦ 接続制御 • レジストリ ◦ セキュアな通信
◦ 接続制御 • イメージ ◦ イメージの信頼性 • コンテナ ◦ コンテナの信頼性 ◦ システムコールの制御 コンテナ
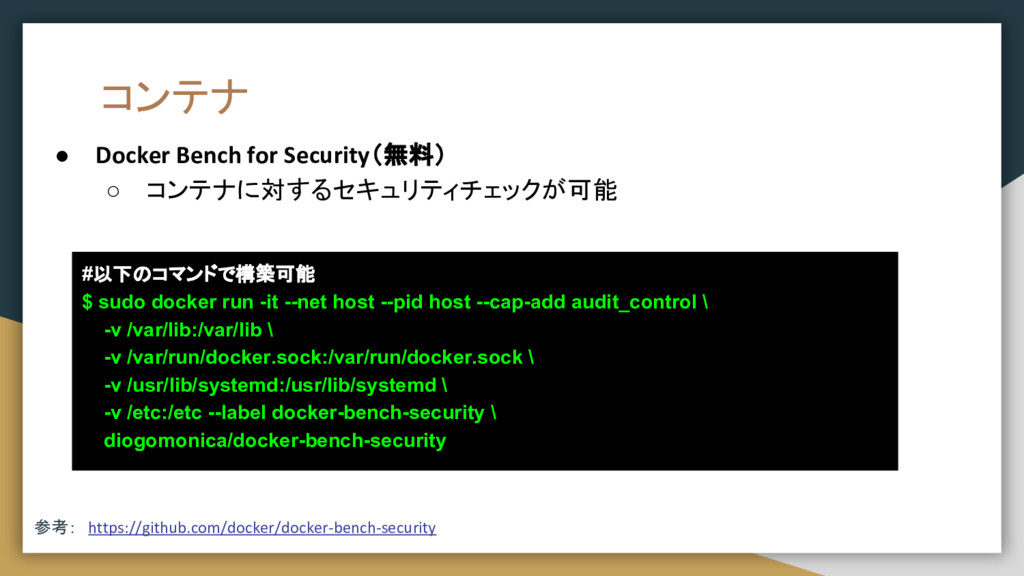
コンテナ • Docker Bench for Security(無料) ◦ コンテナに対するセキュリティチェックが可能 #以下のコマンドで構築可能 $
sudo docker run -it --net host --pid host --cap-add audit_control \ -v /var/lib:/var/lib \ -v /var/run/docker.sock:/var/run/docker.sock \ -v /usr/lib/systemd:/usr/lib/systemd \ -v /etc:/etc --label docker-bench-security \ diogomonica/docker-bench-security 参考: https://github.com/docker/docker-bench-security
無料!?
Docker Bench for Security *チェック項目 [INFO] 1 - Host Configuration
[INFO] 2 - Docker Daemon Configuration [INFO] 3 - Docker Daemon Configuration Files [INFO] 4 - Container Images and Build Files [INFO] 5 - Container Runtime [INFO] 6 - Docker Security Operations *結果 [INFO] 4 - Container Images and Build Files [WARN] 4.1 - Create a user for the container [WARN] * Running as root: vibrant_bassi [WARN] * Running as root: mysql [WARN] * Running as root: php ー> コンテナがrootユーザで動作しているため、警告!
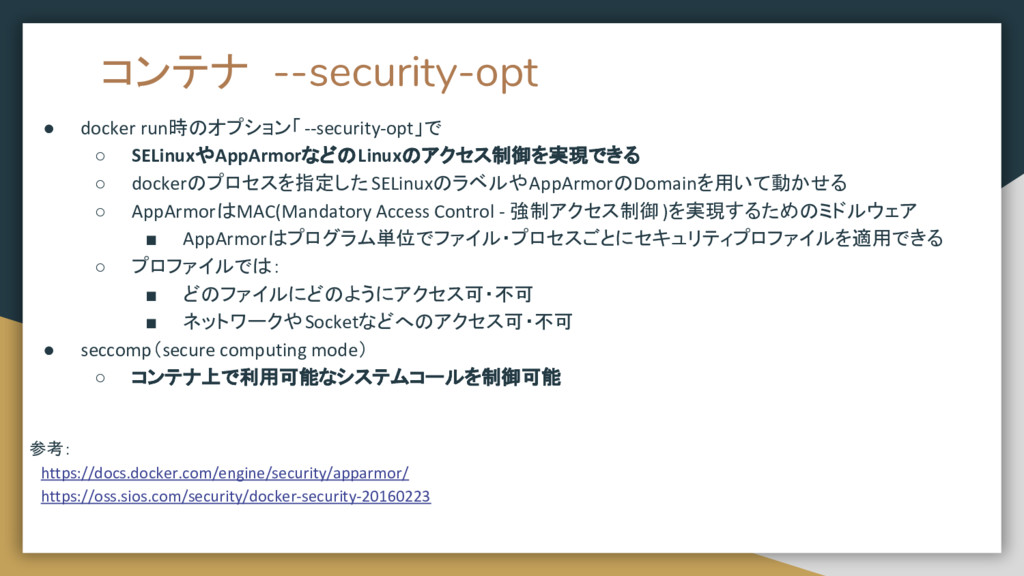
コンテナ --security-opt • docker run時のオプション「--security-opt」で ◦ SELinuxやAppArmorなどのLinuxのアクセス制御を実現できる ◦ dockerのプロセスを指定した SELinuxのラベルやAppArmorのDomainを用いて動かせる
◦ AppArmorはMAC(Mandatory Access Control - 強制アクセス制御)を実現するためのミドルウェア ▪ AppArmorはプログラム単位でファイル・プロセスごとにセキュリティプロファイルを適用できる ◦ プロファイルでは: ▪ どのファイルにどのようにアクセス可・不可 ▪ ネットワークやSocketなどへのアクセス可・不可 • seccomp(secure computing mode) ◦ コンテナ上で利用可能なシステムコールを制御可能 参考: https://docs.docker.com/engine/security/apparmor/ https://oss.sios.com/security/docker-security-20160223
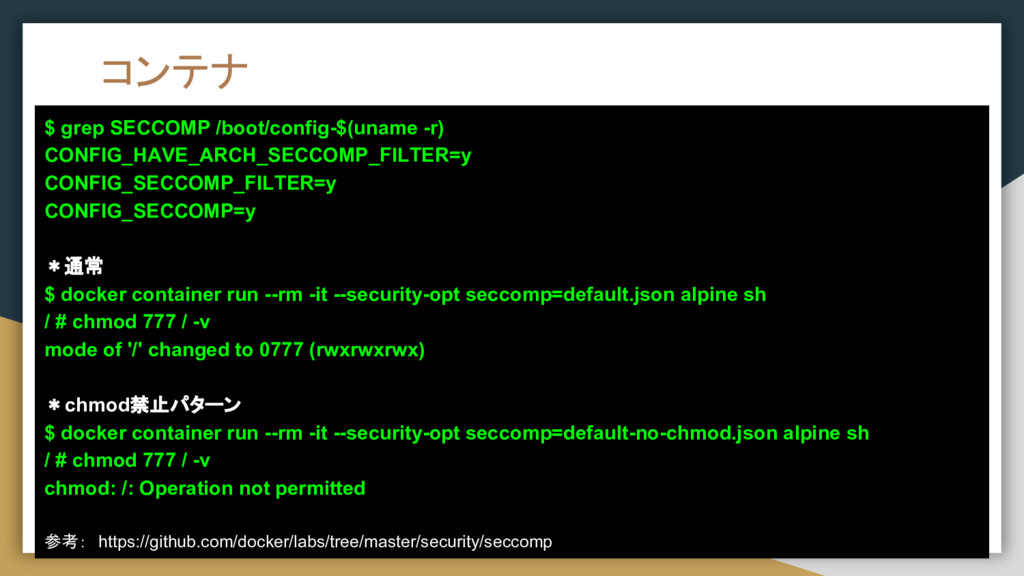
コンテナ $ grep SECCOMP /boot/config-$(uname -r) CONFIG_HAVE_ARCH_SECCOMP_FILTER=y CONFIG_SECCOMP_FILTER=y CONFIG_SECCOMP=y *通常
$ docker container run --rm -it --security-opt seccomp=default.json alpine sh / # chmod 777 / -v mode of '/' changed to 0777 (rwxrwxrwx) *chmod禁止パターン $ docker container run --rm -it --security-opt seccomp=default-no-chmod.json alpine sh / # chmod 777 / -v chmod: /: Operation not permitted 参考: https://github.com/docker/labs/tree/master/security/seccomp
このあたりは、よくわからない 今後の課題
Understanding Docker Security and Best Practices 参考: https://blog.docker.com/2015/05/understanding-docker-security-and- best-practices/ DOCKER
SECURITY blog https://www.docker.com/docker-security
ご清聴 ありがとうございました


 okazakihajime
 ryuguyana
 yama3133
 sraku2159
 ryuseiiida
 nealle
 tamaiyutaro
 hokkai7go
 asmz
 henteko
 ryu1013
 masu_mi
 kazzpapa3
 caitiem20
 lara
 tmiket
 malarkey
 irinanazarova
 panda_program
 rkaga
 tapps
 katarinadahlin
 geshan
 mkilby
 sstephenson