Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
DOM Invader - prototype pollution対応の衝撃 - / DOM ...
Search
okuken
June 27, 2022
Technology
890
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
DOM Invader - prototype pollution対応の衝撃 - / DOM Invader - prototype pollution
okuken
June 27, 2022
More Decks by okuken
See All by okuken
全集中Burp extension ISTE勉強会 第1回 / Burp ISTE study 01
okuken
0
530
全集中Burp extension ISTE v0.5.0 ー Request chain の躍進 / Burp extension ISTE v050
okuken
0
480
npm Security ー サプライチェーン攻撃の観点から ー
okuken
1
710
全集中 Burp extension ISTE リリース1周年記念 - 振り返り - / Burp extension ISTE 1st Anniversary
okuken
0
600
Dangerous usage of JNDI
okuken
0
500
全集中 Burp extension ISTE v0.4リリース / Burp extension ISTE v0.4
okuken
0
520
Web Messaging のセキュリティ - DOM Invaderを添えて - / Web Messaging Security
okuken
0
2.9k
DOM Invader - Burp Suiteの新機能でJavaScriptに立ち向かう - / DOM Invader
okuken
0
1.8k
#BurpISTEで!SECCON Beginners CTF 2021 Web問に全集中した話 / ctf4b 2021 with ISTE
okuken
1
610
Other Decks in Technology
See All in Technology
Benchmarking Disaggregated Serving on vLLM + Dynamo with a Real Coding-Agent Workload
nttcom
1
180
「事実」を「計測」して、「解釈」する 〜AWS Lambdaのメモリ最適解の見つけ方〜
maimyyym
0
150
夫婦で子育てするための育児標準化
codmoninc
PRO
0
210
子育てエンジニアの可処分時間が減っても成長を諦めない戦い方
sudoakiy
6
4.6k
触りたくないデータに、どう触るか AI時代のRBACアクセスガバナンス
ivry_presentationmaterials
0
220
不可逆な意思決定を避けながら10億超の顧客データを AI Ready にするデータ基盤設計
baseballyama
1
320
オントロジーって 結局なにもの? AI エージェントに「意味」を渡す知識設計の話
greenmidori
0
130
その Valkey 使いこなしていますか?
onk
PRO
5
1.2k
【Data Engineering Summit2026_登壇資料】医療ビッグデータ×AIエージェントを支えるデータ基盤とハーネスエンジニアリング
jmdc_presentation
0
160
FOSS4Gを活用した自治体業務DXの試み
470715
0
160
アウトプット初心者、半年間のふりかえり
4o1sobblue
0
400
継続的なAIコスト最適化
bgpat
1
310
Featured
See All Featured
What’s in a name? Adding method to the madness
productmarketing
PRO
24
4.2k
Un-Boring Meetings
codingconduct
0
450
Java REST API Framework Comparison - PWX 2021
mraible
34
9.8k
I Don’t Have Time: Getting Over the Fear to Launch Your Podcast
jcasabona
35
2.9k
"I'm Feeling Lucky" - Building Great Search Experiences for Today's Users (#IAC19)
danielanewman
230
23k
Marketing to machines
jonoalderson
1
5.9k
コードの90%をAIが書く世界で何が待っているのか / What awaits us in a world where 90% of the code is written by AI
rkaga
63
46k
Game over? The fight for quality and originality in the time of robots
wayneb77
1
300
The Cost Of JavaScript in 2023
addyosmani
55
10k
Fashionably flexible responsive web design (full day workshop)
malarkey
409
67k
職位にかかわらず全員がリーダーシップを発揮するチーム作り / Building a team where everyone can demonstrate leadership regardless of position
madoxten
69
67k
Bioeconomy Workshop: Dr. Julius Ecuru, Opportunities for a Bioeconomy in West Africa
akademiya2063
PRO
1
410
Transcript
DOM Invader ー prototype pollution 対応の衝撃 ー @okuken3 2022.06.27 第20回
初心者のためのセキュリティ勉強会
0. 自己紹介 1. DOM Invader が prototype pollution に対応! 2.
DOM Invader の復習 3. DOM Invader で prototype pollution を試してみよう! 4. まとめ Agenda
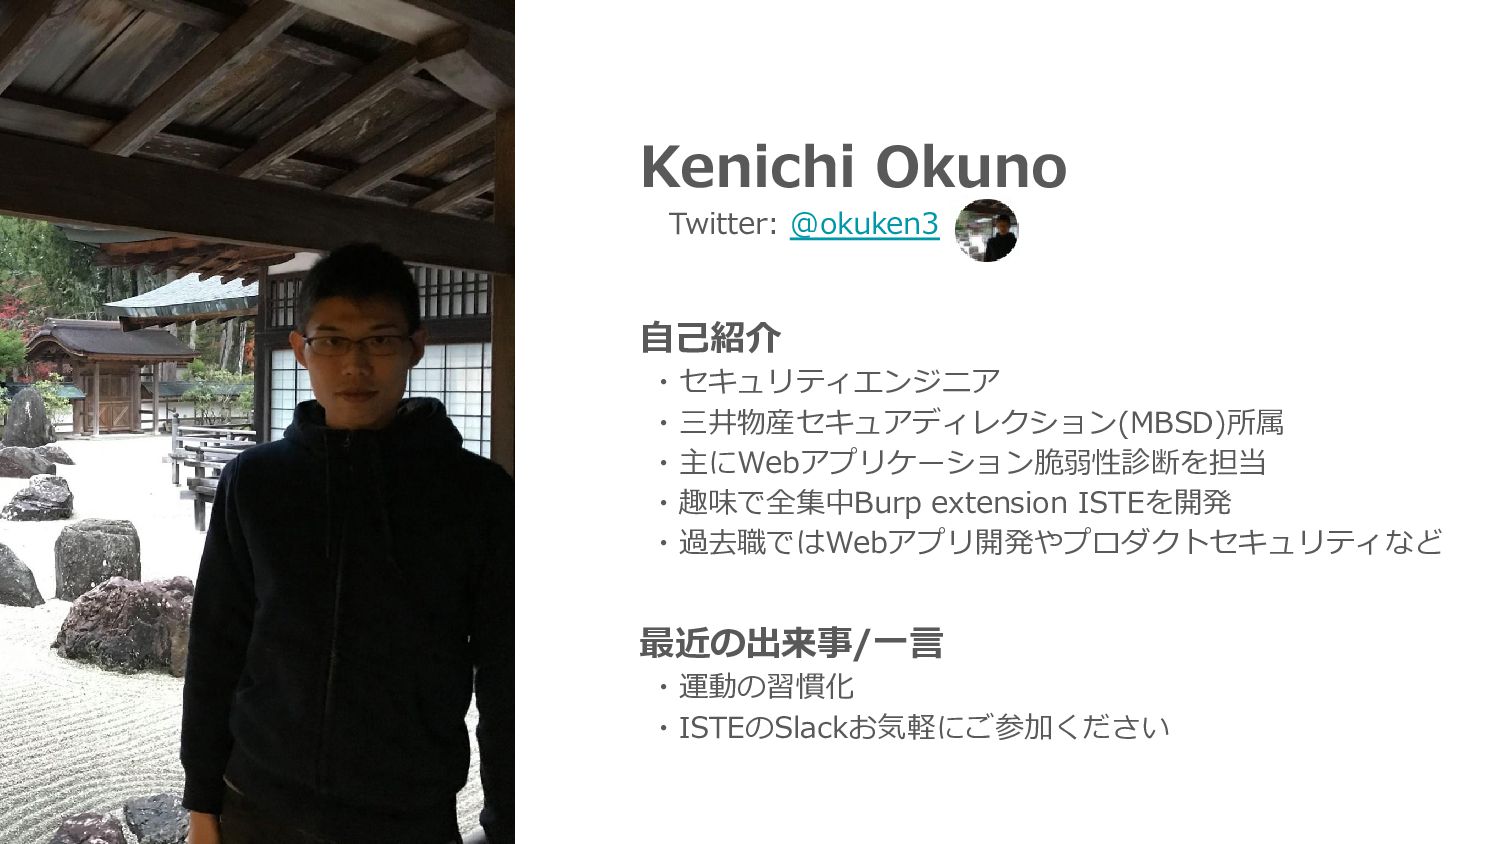
Kenichi Okuno Twitter: @okuken3 自己紹介 ・セキュリティエンジニア ・三井物産セキュアディレクション(MBSD)所属 ・主にWebアプリケーション脆弱性診断を担当 ・趣味で全集中Burp extension
ISTEを開発 ・過去職ではWebアプリ開発やプロダクトセキュリティなど 最近の出来事/一言 ・運動の習慣化 ・ISTEのSlackお気軽にご参加ください
1. DOM Invader が prototype pollution に対応!
リリース情報 Professional / Community 2022.6 [Early Adopter] (20 June 2022
at 12:37 UTC) https://portswigger.net/burp/releases/professional-community-2022-6
ドキュメント / 公式ブログ DOM Invader [PROFESSIONAL] [COMMUNITY] https://portswigger.net/burp/documentation/desktop/tools/dom-invader - prototype pollution
関連の記載はなし(2022/06/25時点) Finding client-side prototype pollution with DOM Invader https://portswigger.net/blog/finding-client-side-prototype-pollution-with-dom-invader - 解説動画あり ★おすすめ★ - prototype pollution 自体の平易な解説もあり Widespread prototype pollution gadgets https://portswigger.net/research/widespread-prototype-pollution-gadgets - prototype pollution gadget の具体例をソースコードを交えて解説
2. DOM Invader の復習
※※ 詳細は過去LT資料を参照ください ※※ DOM Invader - Burp Suiteの新機能でJavaScriptに立ち向かう - https://speakerdeck.com/okuken/dom-invader
Web Messaging のセキュリティ - DOM Invaderを添えて - https://speakerdeck.com/okuken/web-messaging-security
端的に言うと ✓ 興味深いシンクとソースを検出&一覧表示! ✓ スタックトレースの表示&該当行へジャンプ! ✓ Web Messaging 特化の機能群もあるよ! 復習
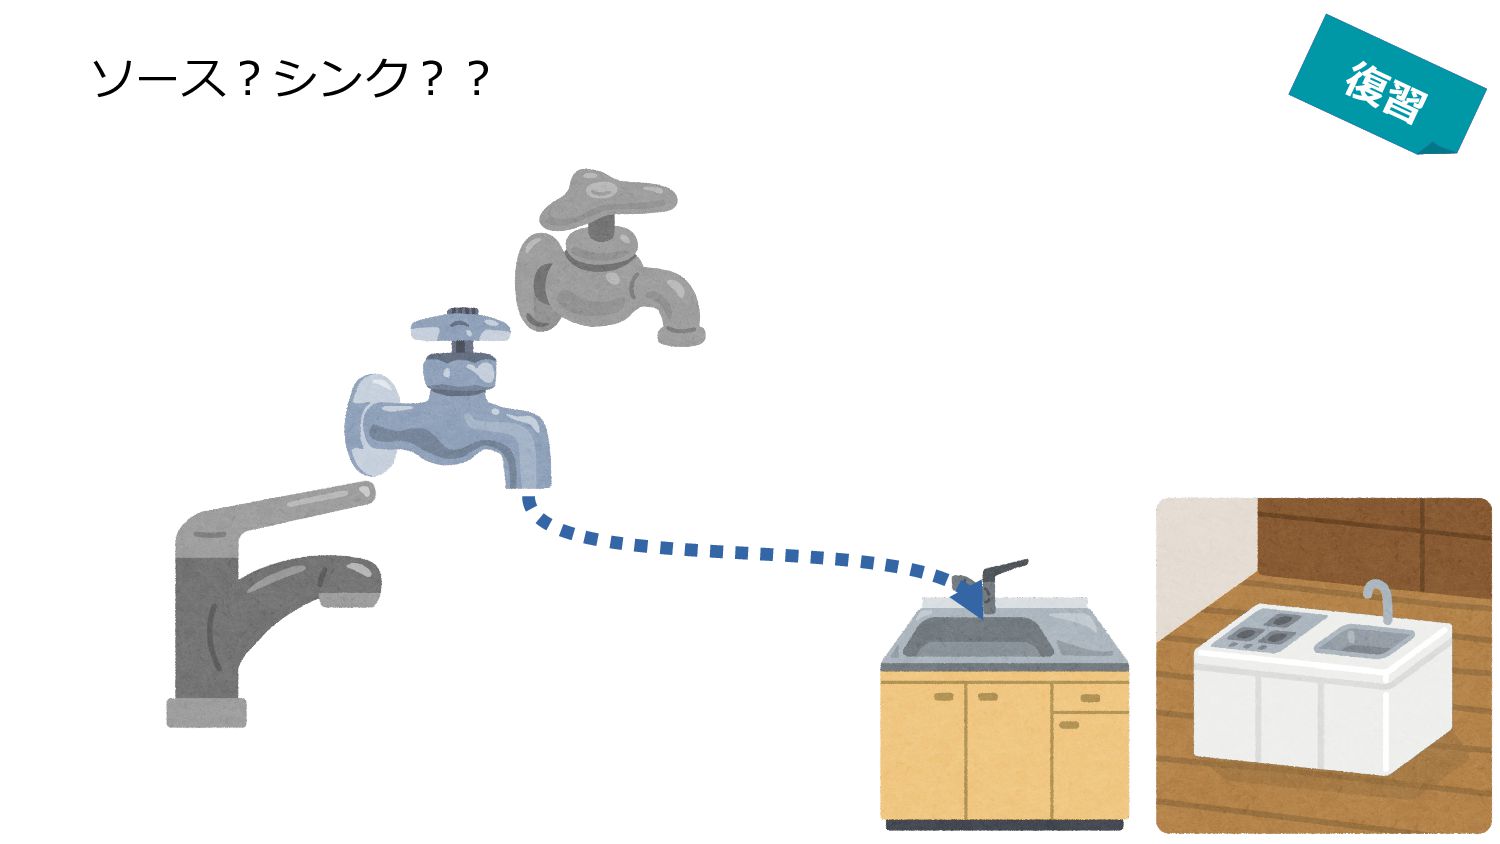
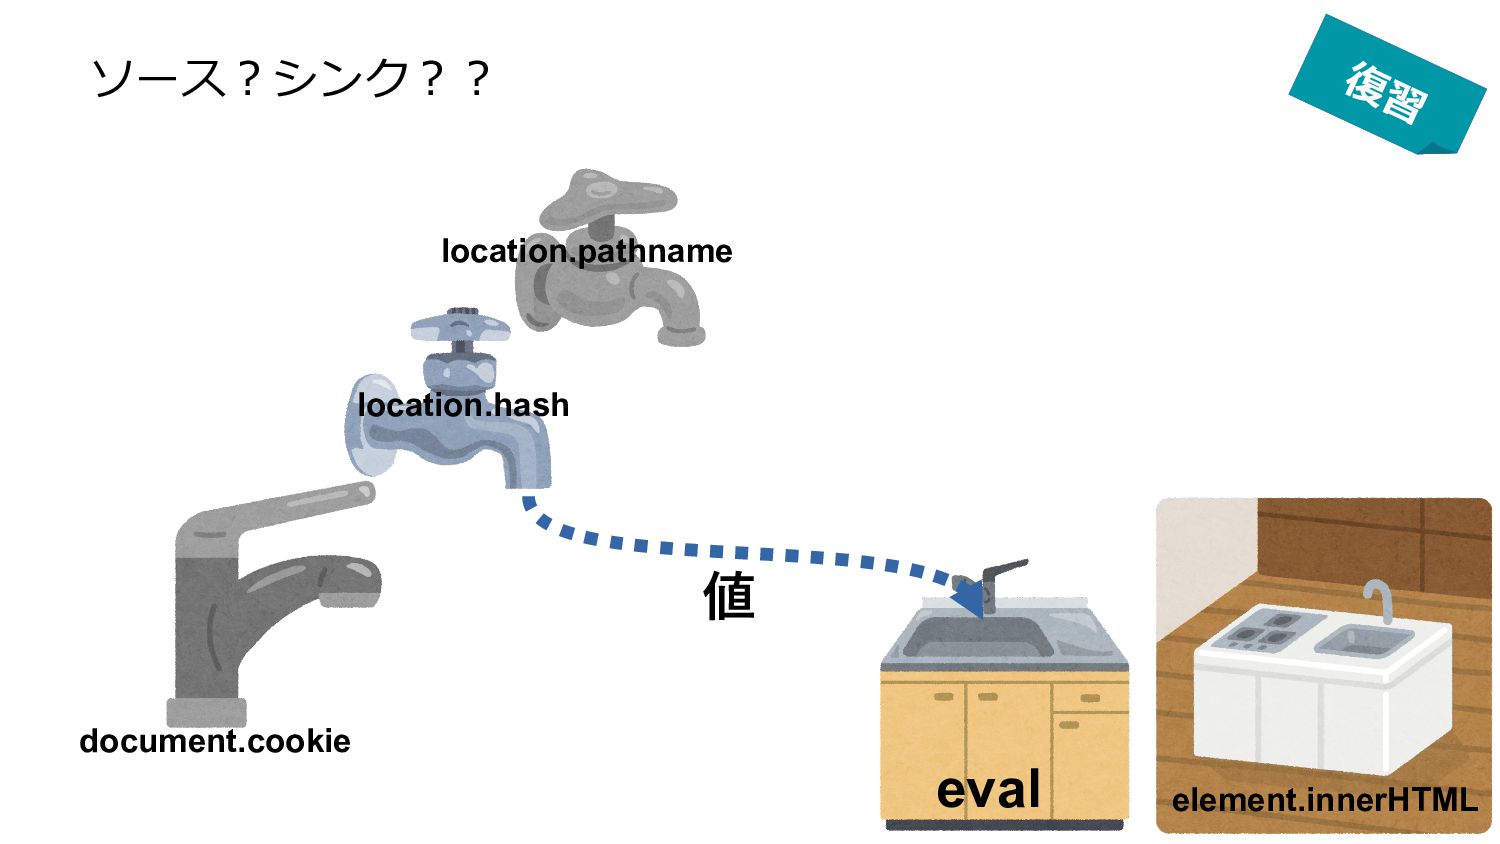
ソース?シンク?? 復習
ソース?シンク?? eval element.innerHTML 値 location.pathname document.cookie location.hash 復習
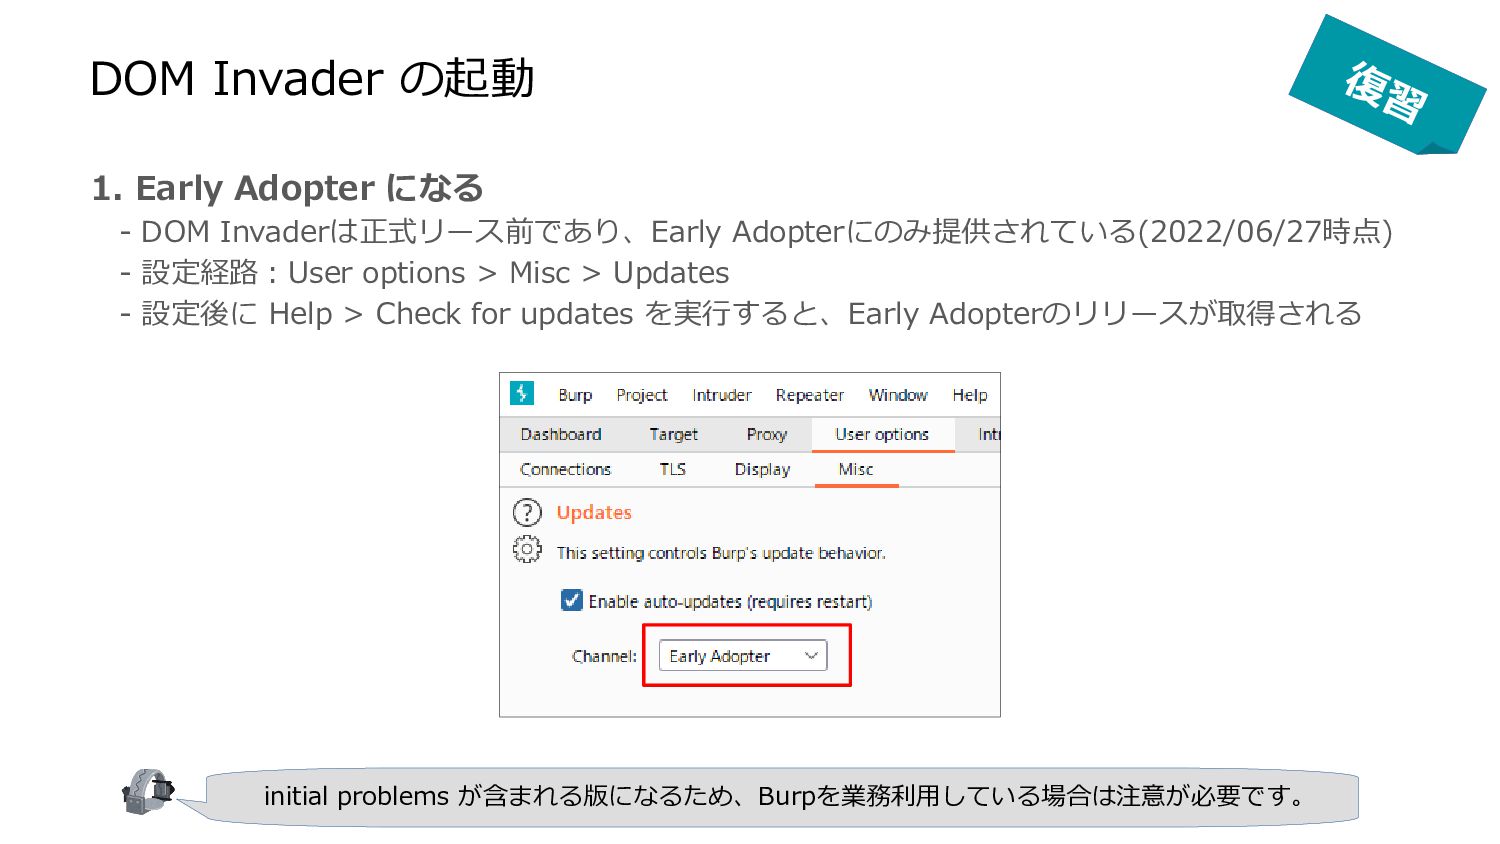
DOM Invader の起動 1. Early Adopter になる - DOM Invaderは正式リース前であり、Early
Adopterにのみ提供されている(2022/06/27時点) - 設定経路:User options > Misc > Updates - 設定後に Help > Check for updates を実行すると、Early Adopterのリリースが取得される initial problems が含まれる版になるため、Burpを業務利用している場合は注意が必要です。 復習
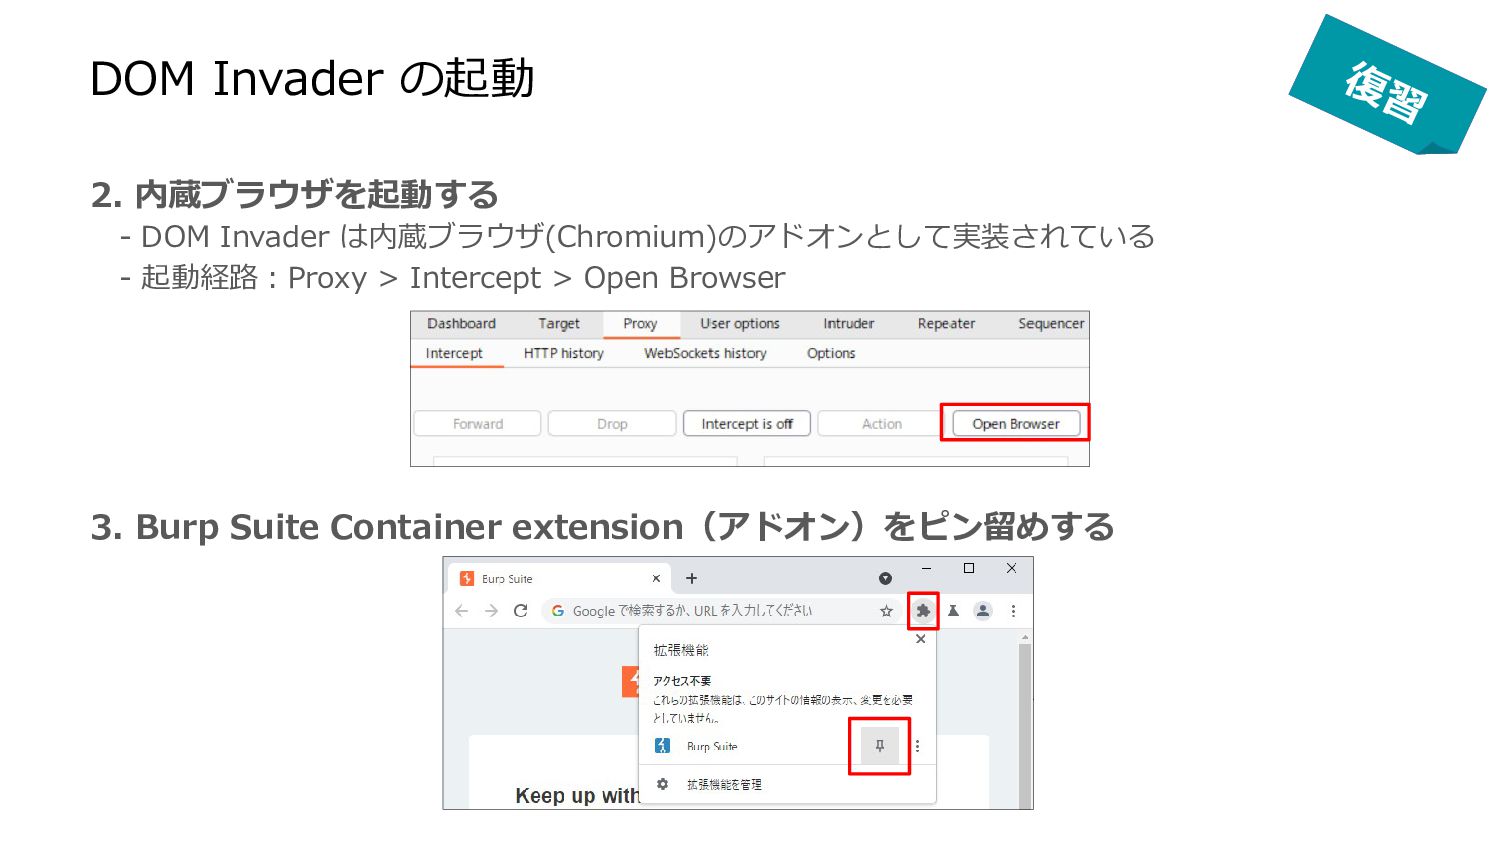
2. 内蔵ブラウザを起動する - DOM Invader は内蔵ブラウザ(Chromium)のアドオンとして実装されている - 起動経路:Proxy > Intercept
> Open Browser 3. Burp Suite Container extension(アドオン)をピン留めする DOM Invader の起動 復習
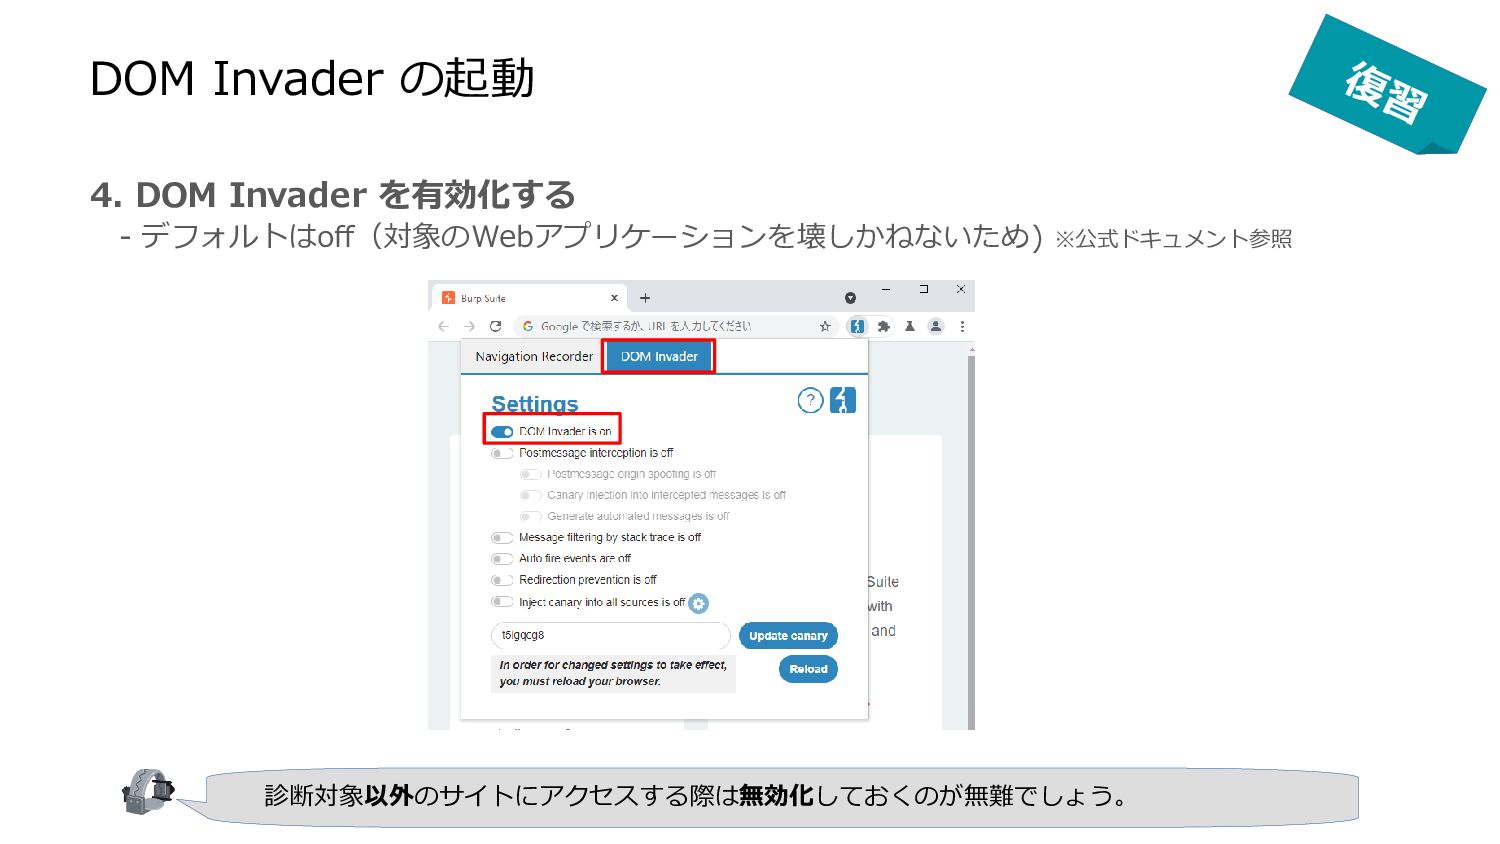
4. DOM Invader を有効化する - デフォルトはoff(対象のWebアプリケーションを壊しかねないため) ※公式ドキュメント参照 診断対象以外のサイトにアクセスする際は無効化しておくのが無難でしょう。 DOM Invader
の起動 復習
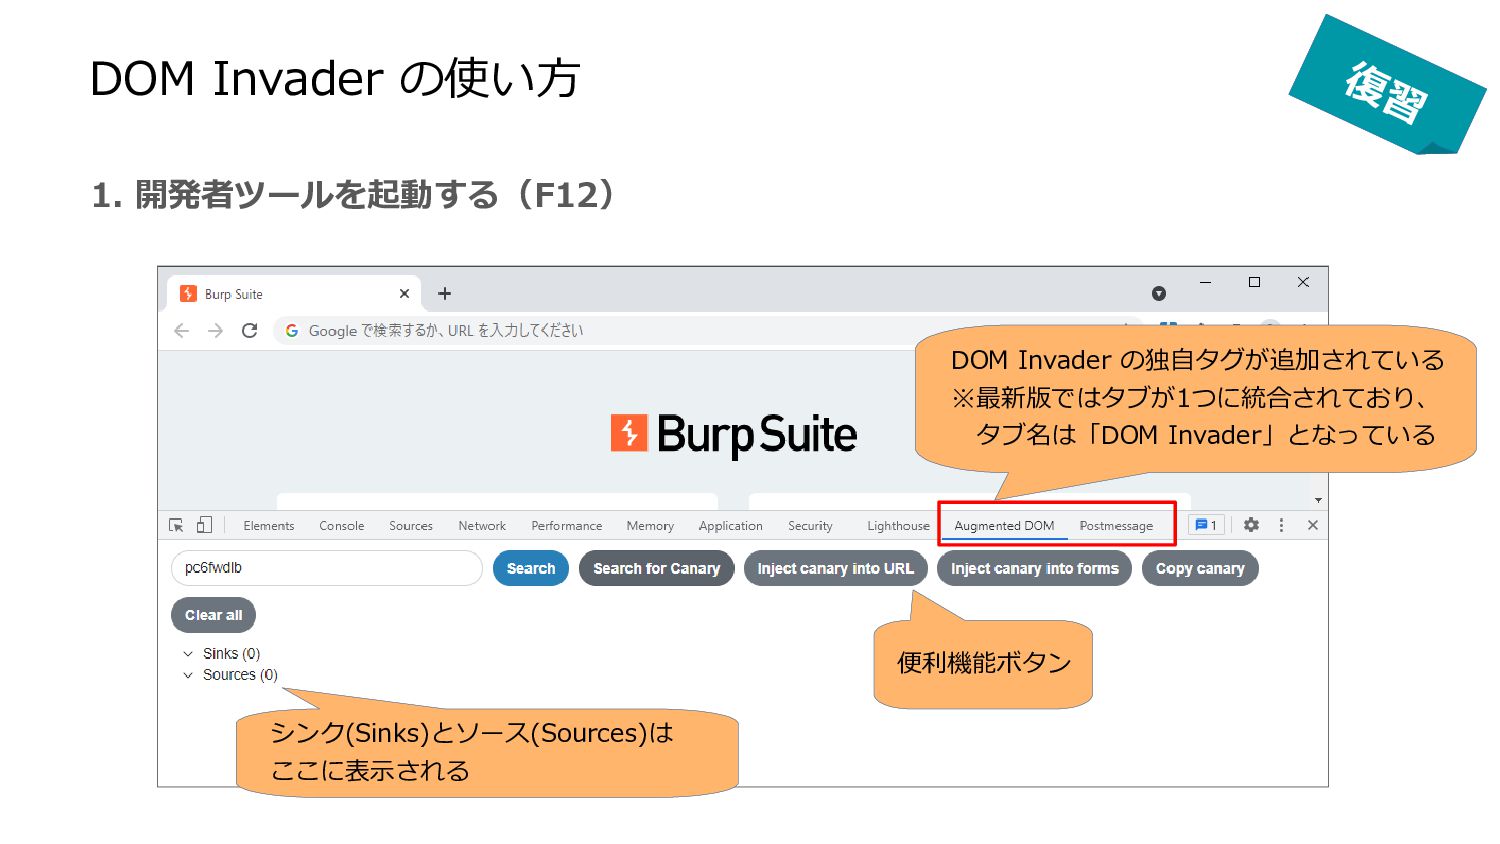
1. 開発者ツールを起動する(F12) DOM Invader の使い方 DOM Invader の独自タグが追加されている ※最新版ではタブが1つに統合されており、 タブ名は「DOM
Invader」となっている シンク(Sinks)とソース(Sources)は ここに表示される 便利機能ボタン 復習
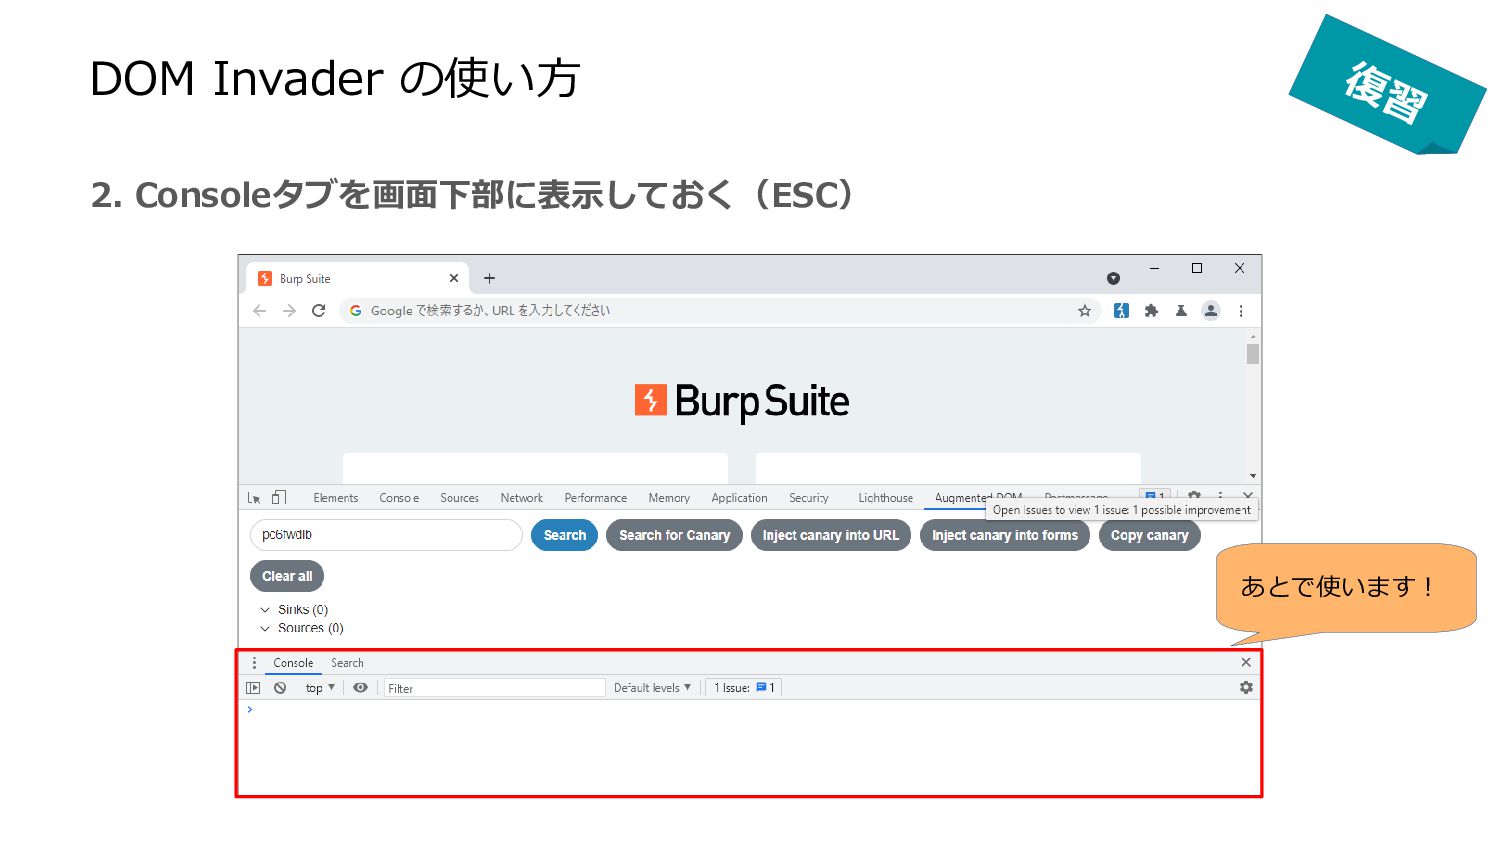
2. Consoleタブを画面下部に表示しておく(ESC) あとで使います! DOM Invader の使い方 復習
3. DOM Invader で prototype pollution を試してみよう!
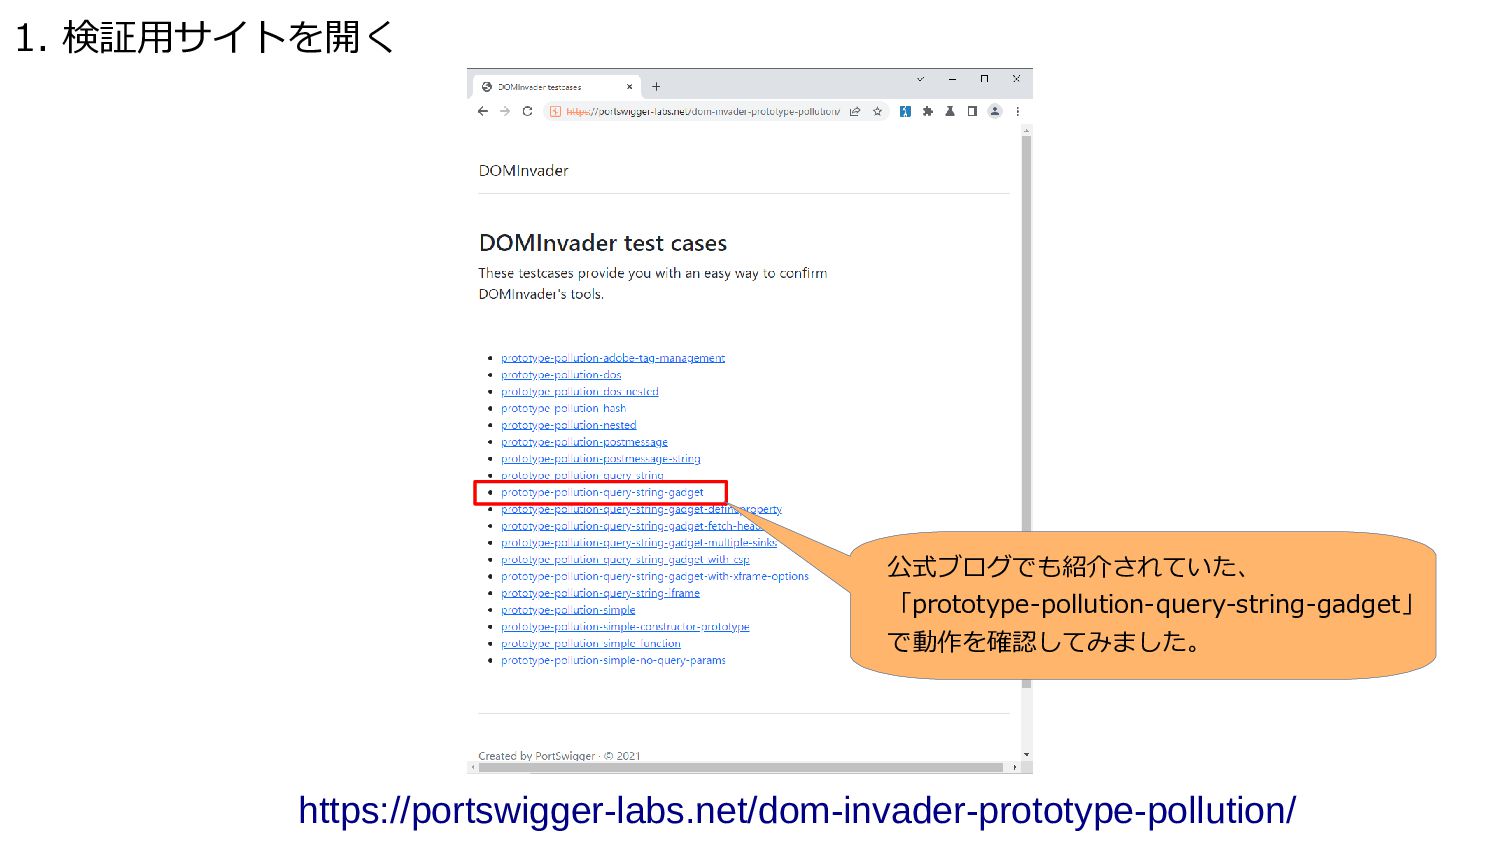
1. 検証用サイトを開く https://portswigger-labs.net/dom-invader-prototype-pollution/ 公式ブログでも紹介されていた、 「prototype-pollution-query-string-gadget」 で動作を確認してみました。
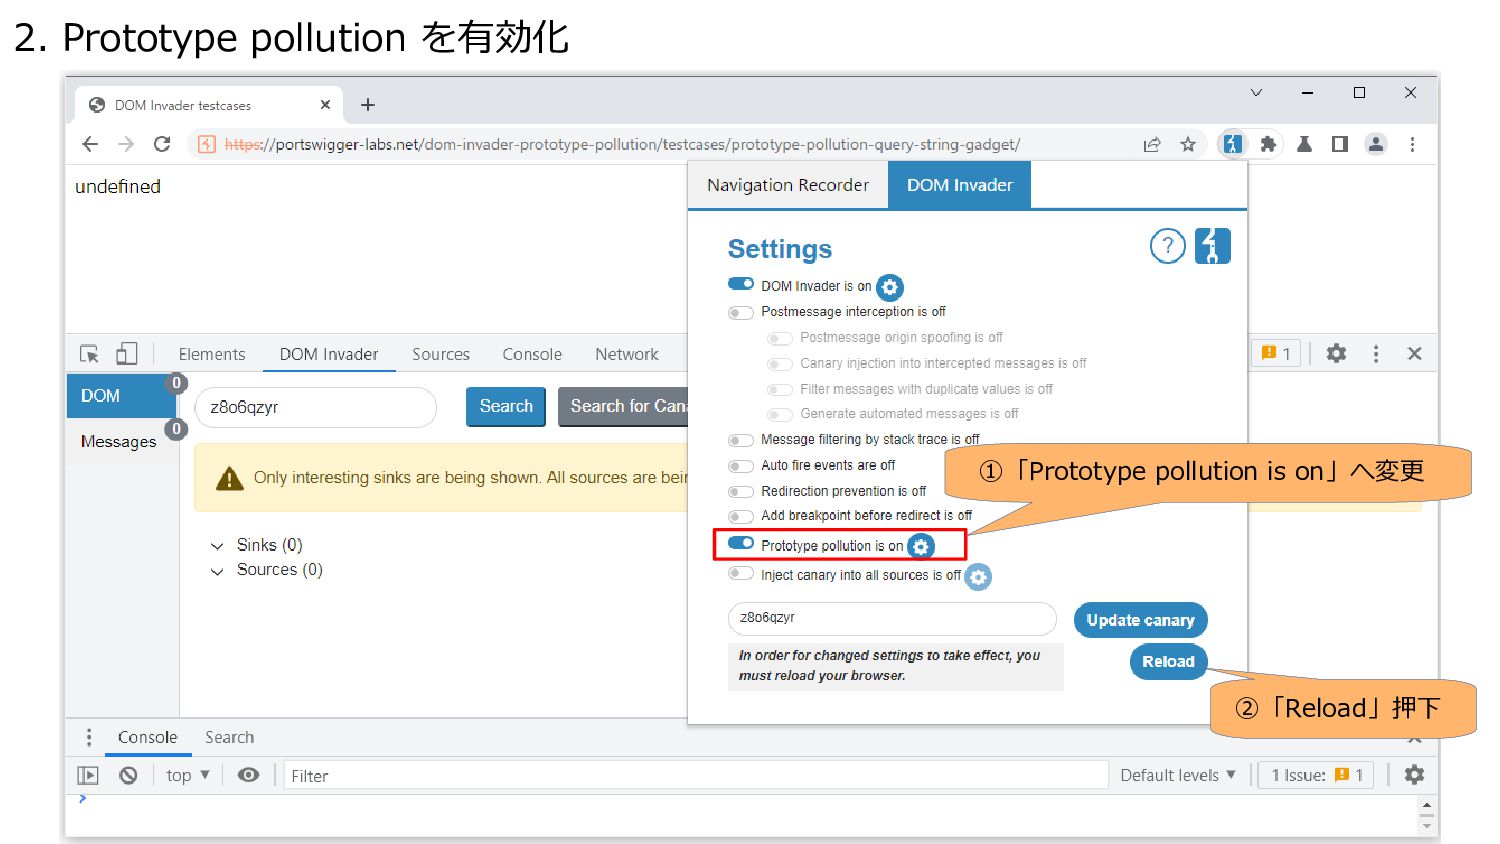
2. Prototype pollution を有効化 ①「Prototype pollution is on」へ変更 ②「Reload」押下
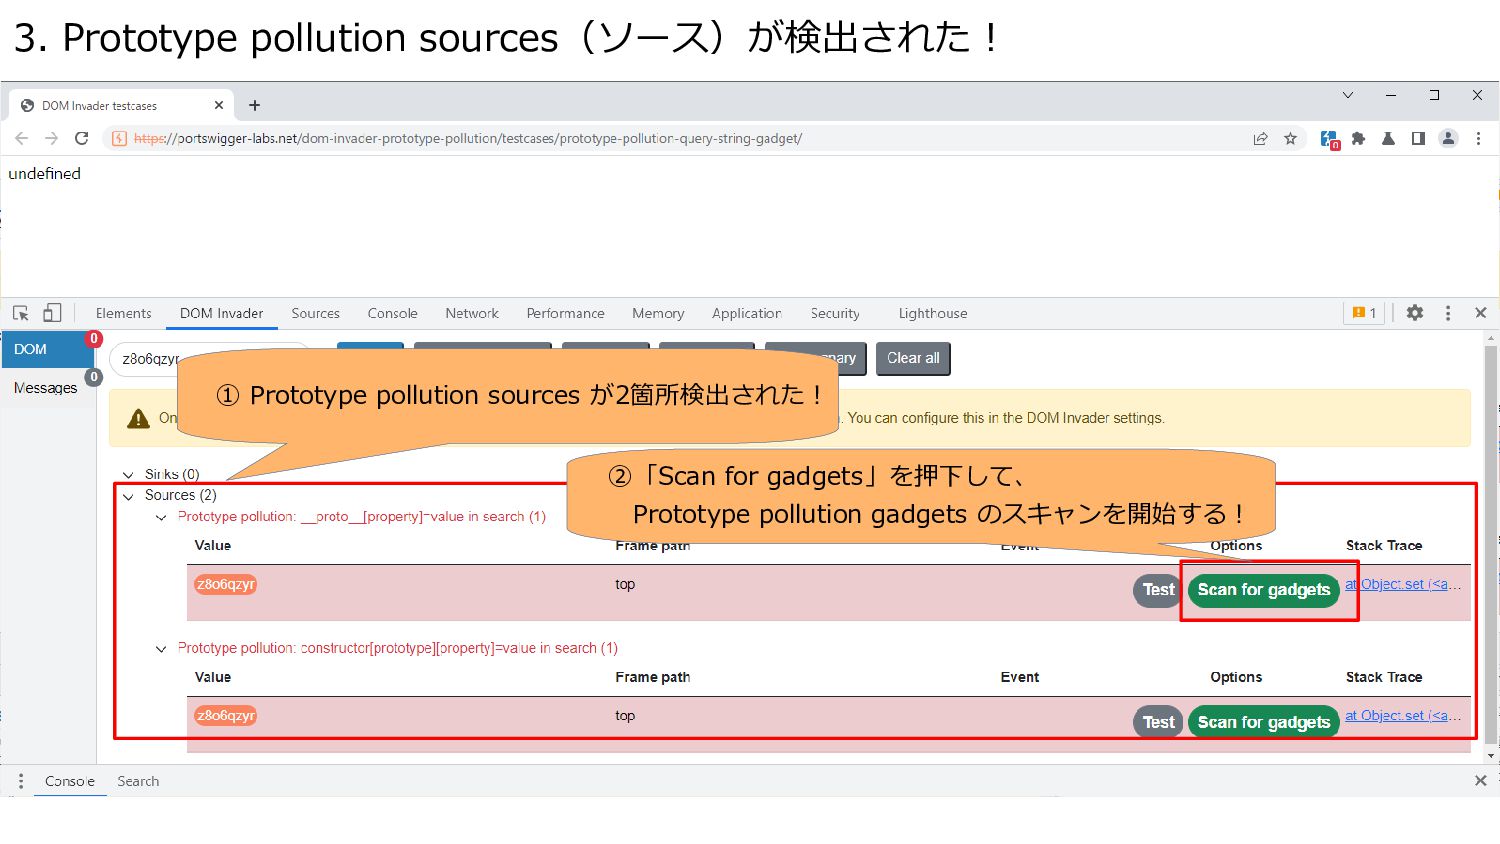
3. Prototype pollution sources(ソース)が検出された! ① Prototype pollution sources が2箇所検出された! ②「Scan
for gadgets」を押下して、 Prototype pollution gadgets のスキャンを開始する!
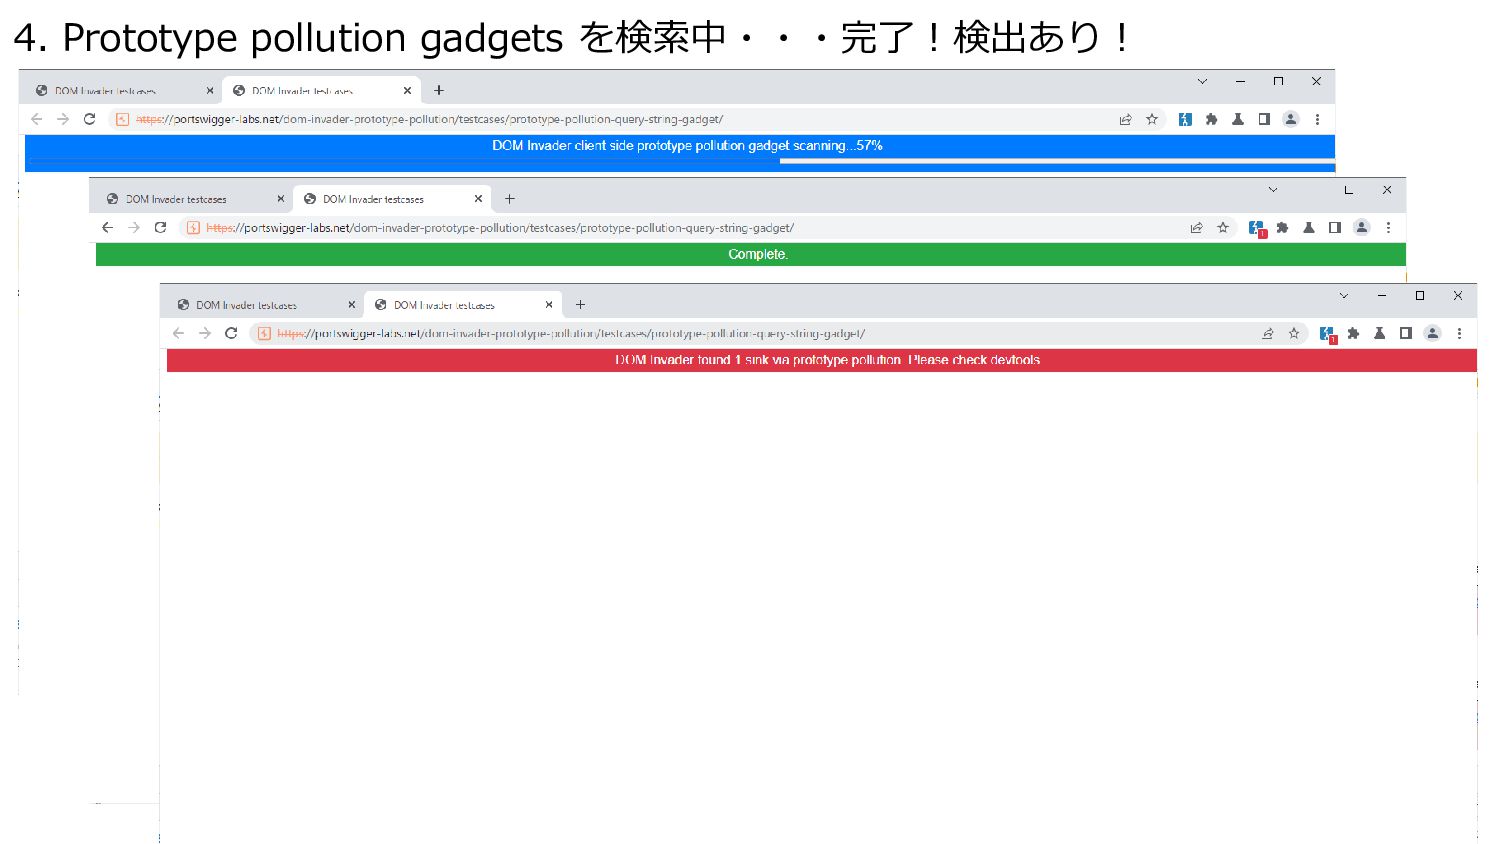
4. Prototype pollution gadgets を検索中・・・完了!検出あり!
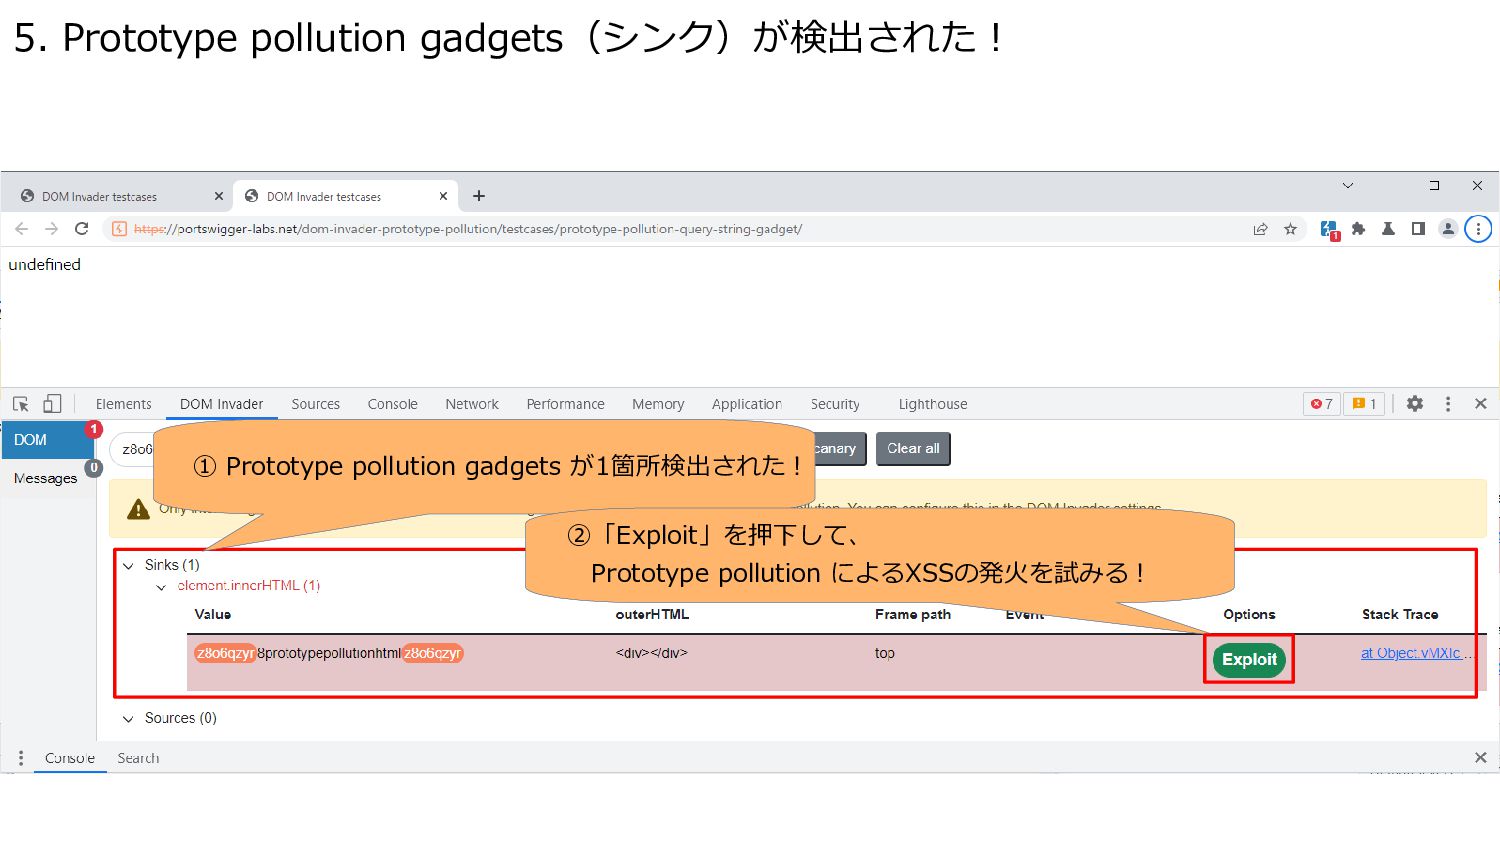
5. Prototype pollution gadgets(シンク)が検出された! ① Prototype pollution gadgets が1箇所検出された! ②「Exploit」を押下して、
Prototype pollution によるXSSの発火を試みる!
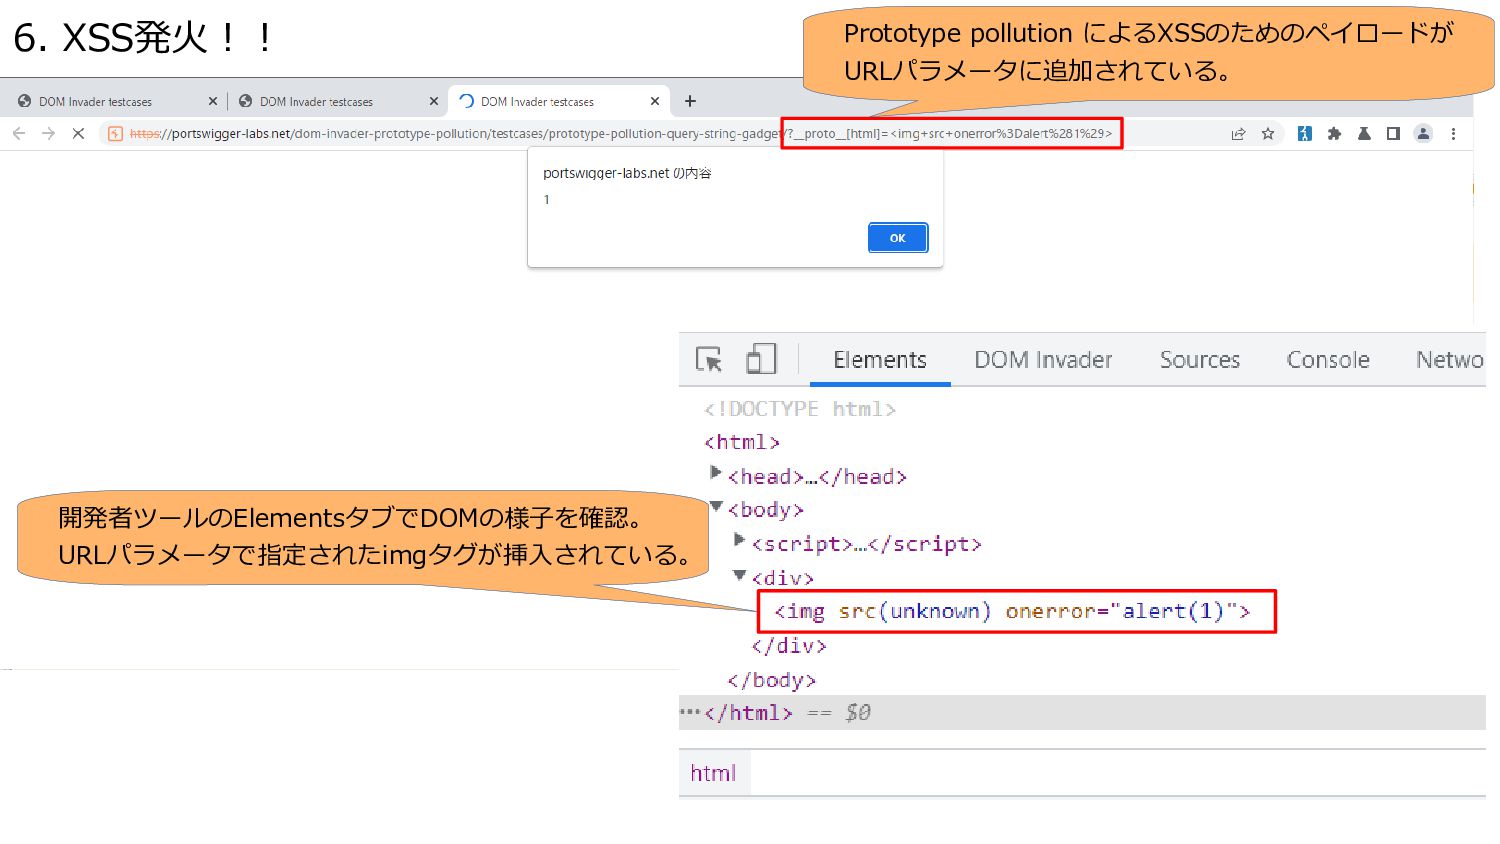
6. XSS発火!! Prototype pollution によるXSSのためのペイロードが URLパラメータに追加されている。 開発者ツールのElementsタブでDOMの様子を確認。 URLパラメータで指定されたimgタグが挿入されている。
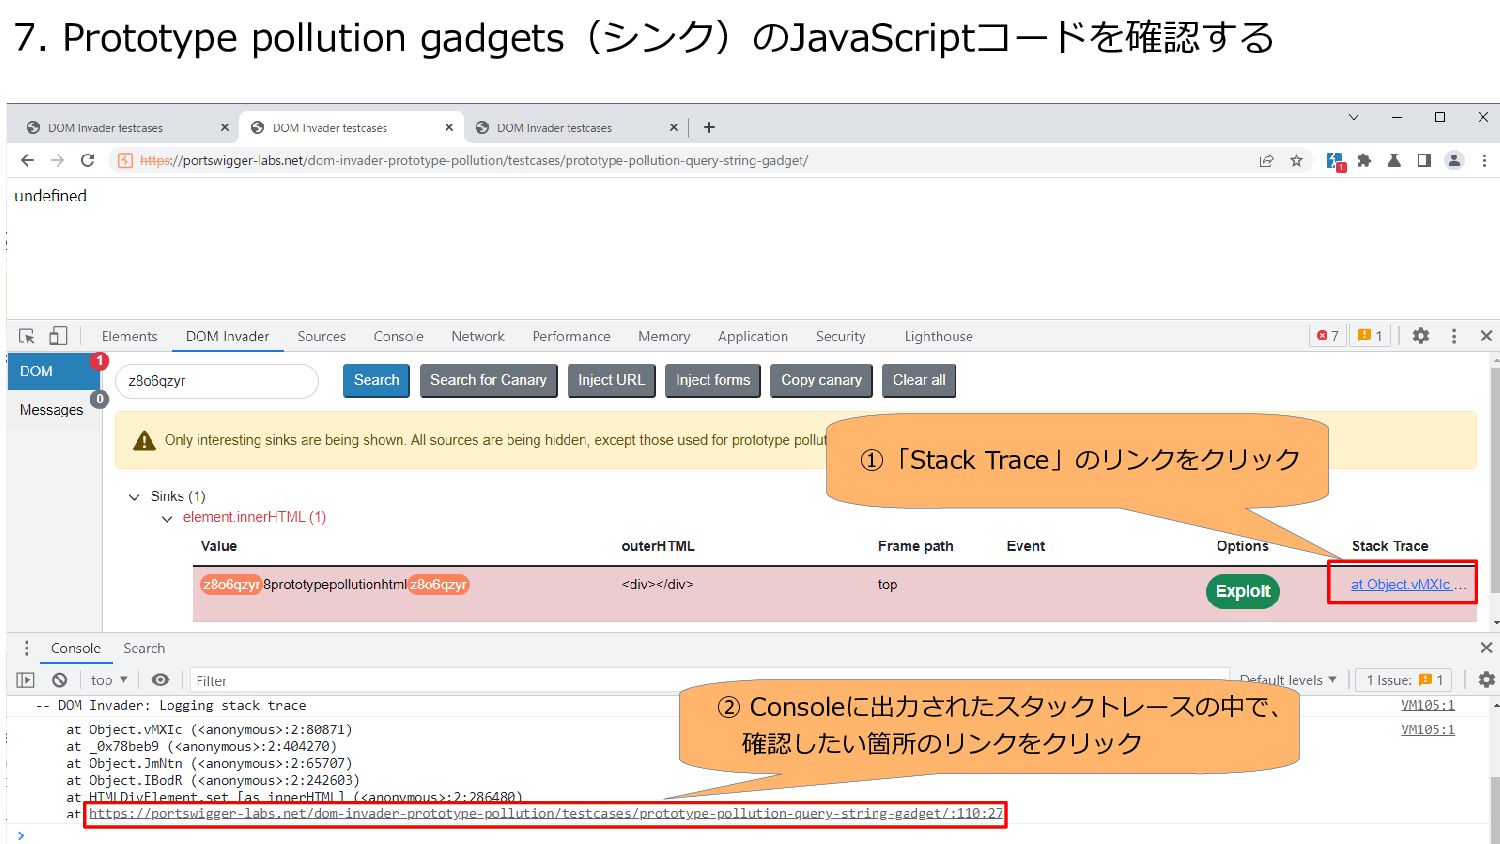
7. Prototype pollution gadgets(シンク)のJavaScriptコードを確認する ①「Stack Trace」のリンクをクリック ② Consoleに出力されたスタックトレースの中で、 確認したい箇所のリンクをクリック
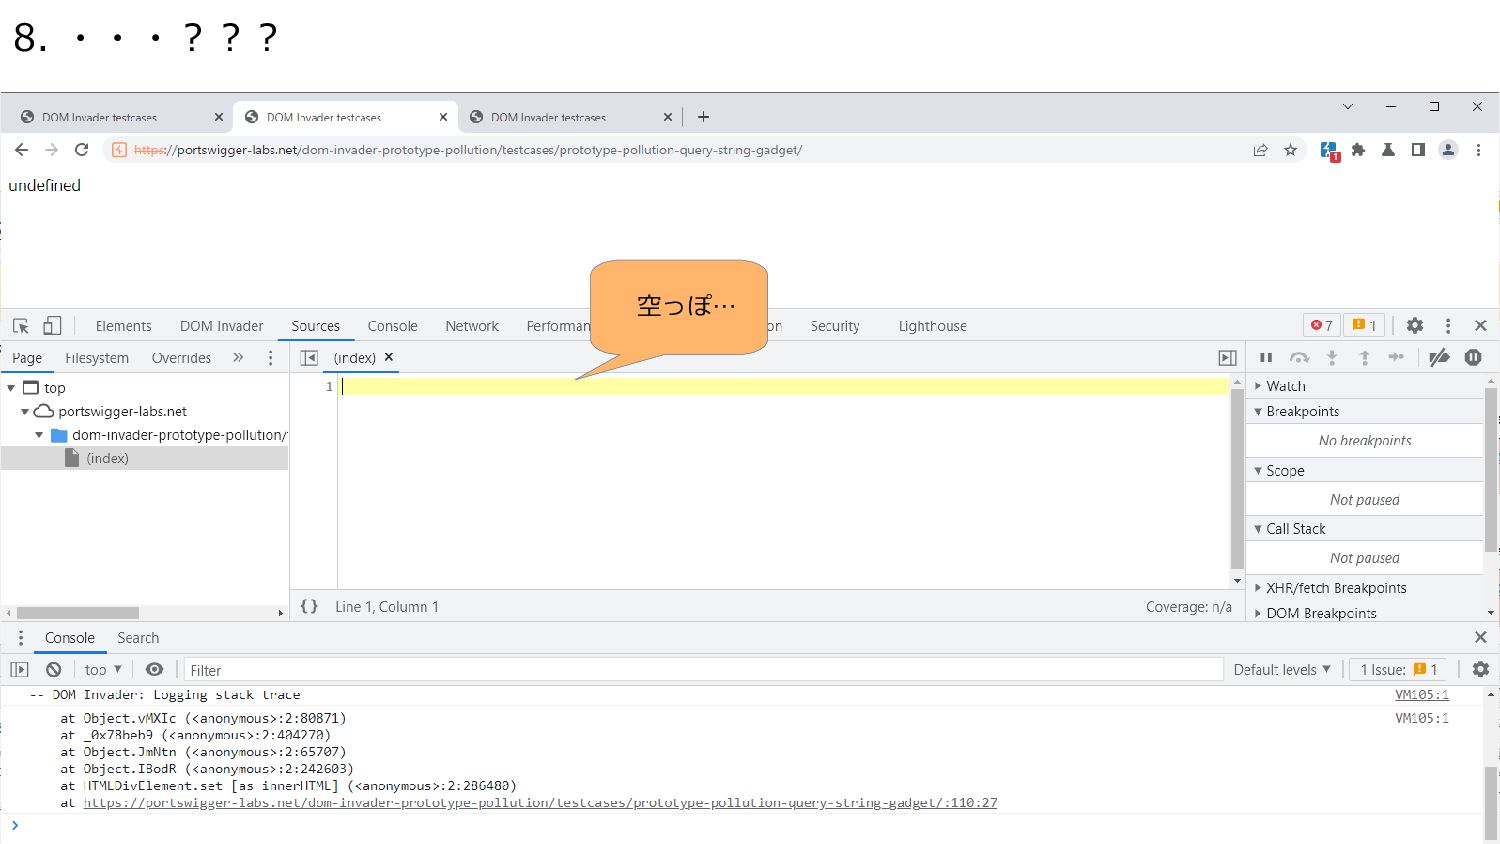
8. ・・・??? 空っぽ…
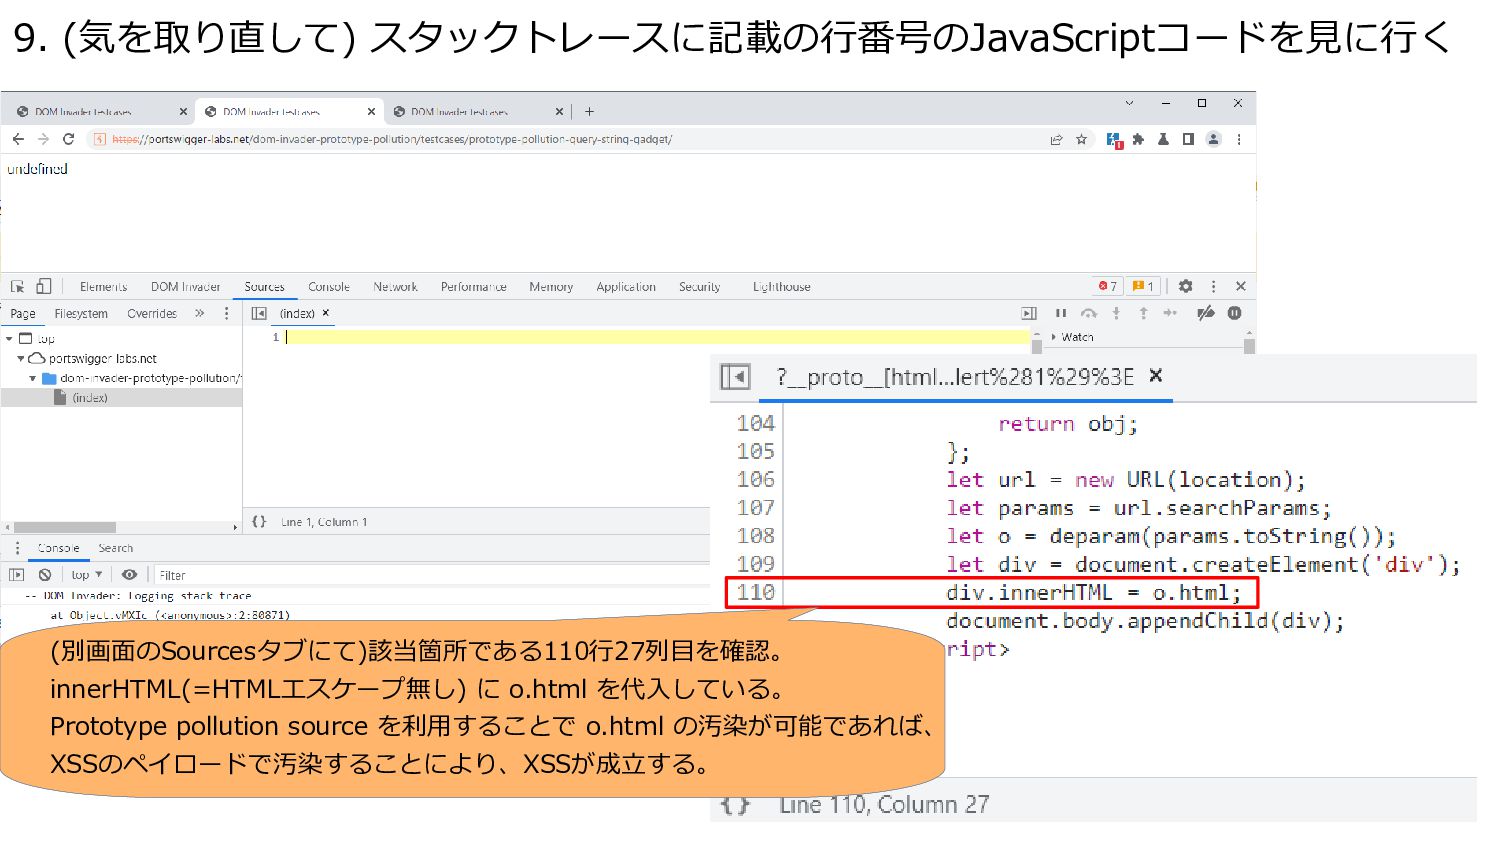
9. (気を取り直して) スタックトレースに記載の行番号のJavaScriptコードを見に行く (別画面のSourcesタブにて)該当箇所である110行27列目を確認。 innerHTML(=HTMLエスケープ無し) に o.html を代入している。 Prototype pollution
source を利用することで o.html の汚染が可能であれば、 XSSのペイロードで汚染することにより、XSSが成立する。
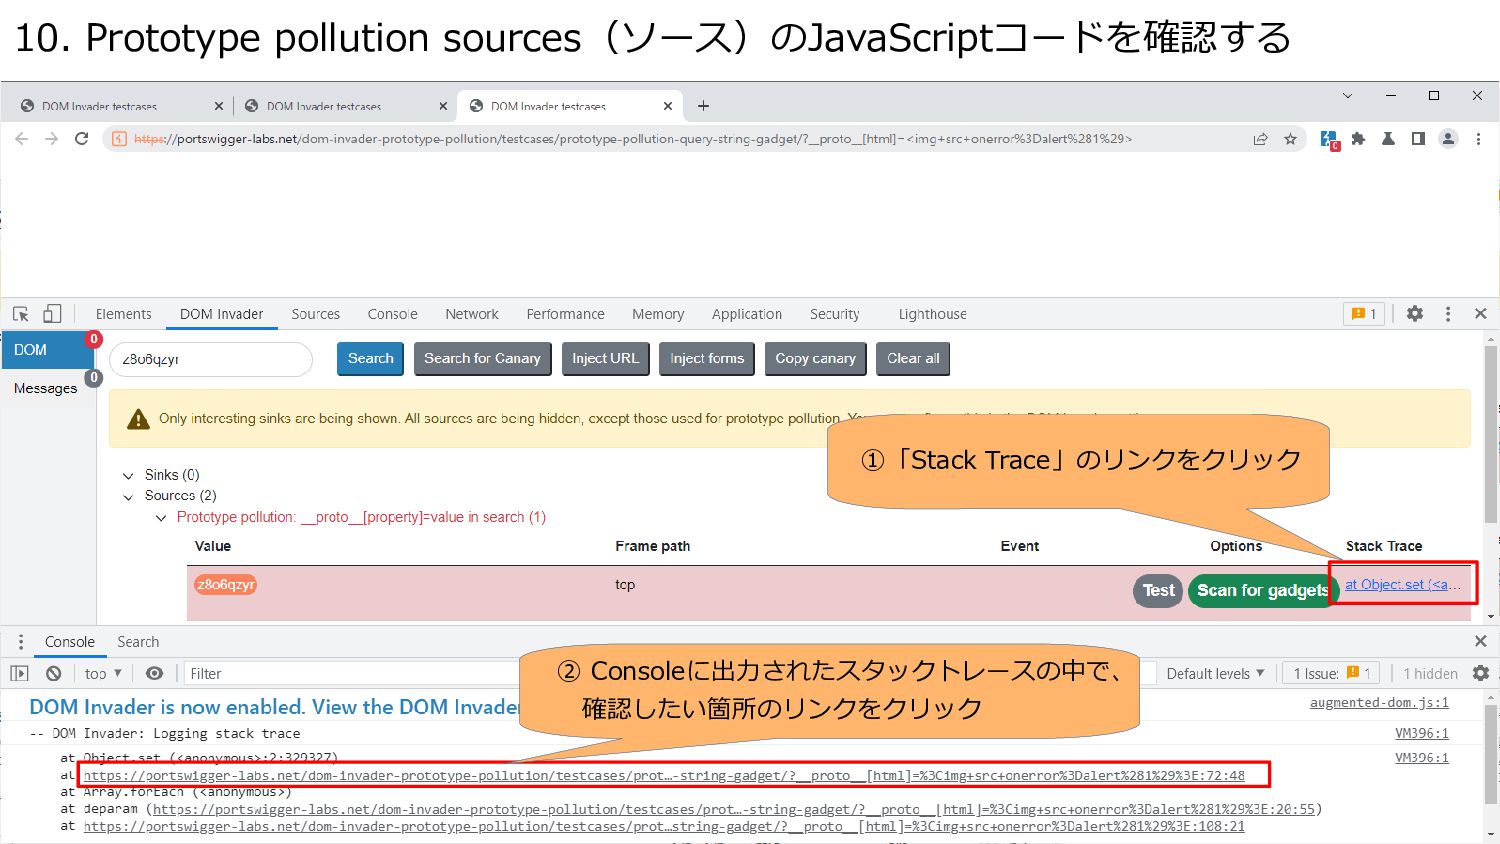
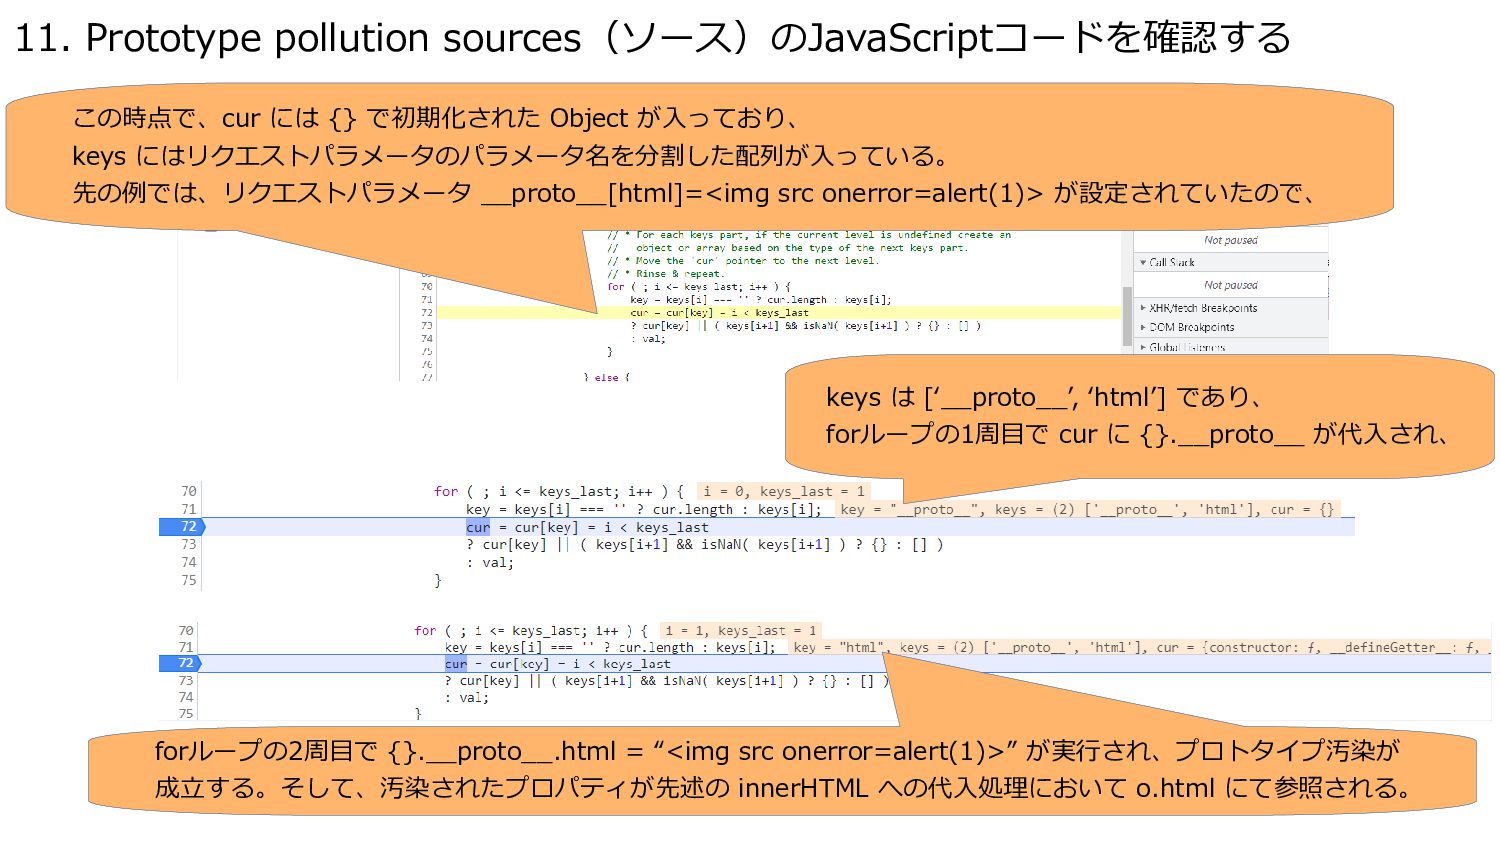
10. Prototype pollution sources(ソース)のJavaScriptコードを確認する ①「Stack Trace」のリンクをクリック ② Consoleに出力されたスタックトレースの中で、 確認したい箇所のリンクをクリック
11. Prototype pollution sources(ソース)のJavaScriptコードを確認する この時点で、cur には {} で初期化された Object が入っており、
keys にはリクエストパラメータのパラメータ名を分割した配列が入っている。 先の例では、リクエストパラメータ __proto__[html]=<img src onerror=alert(1)> が設定されていたので、 keys は [‘__proto__’, ‘html’] であり、 forループの1周目で cur に {}.__proto__ が代入され、 forループの2周目で {}.__proto__.html = “<img src onerror=alert(1)>” が実行され、プロトタイプ汚染が 成立する。そして、汚染されたプロパティが先述の innerHTML への代入処理において o.html にて参照される。
まとめ ✓ DOM Invader が prototype pollution に対応! ✓ prototype
pollution source および gadget の検出から Exploit まで! ✓ 正式リリースが待ち遠しい!
None


 okuken
 nttcom
 maimyyym
 codmoninc
 sudoakiy
 ivry_presentationmaterials
 baseballyama
 greenmidori
 onk
 jmdc_presentation
 470715
 4o1sobblue
 bgpat
 productmarketing
 codingconduct
 mraible
 jcasabona
 danielanewman
 jonoalderson
 rkaga
 wayneb77
 addyosmani
 malarkey
 madoxten
 akademiya2063