Share
Embed
npm Security ー サプライチェーン攻撃の観点から ー
okuken
March 28, 2022
Transcript
12 slides
-
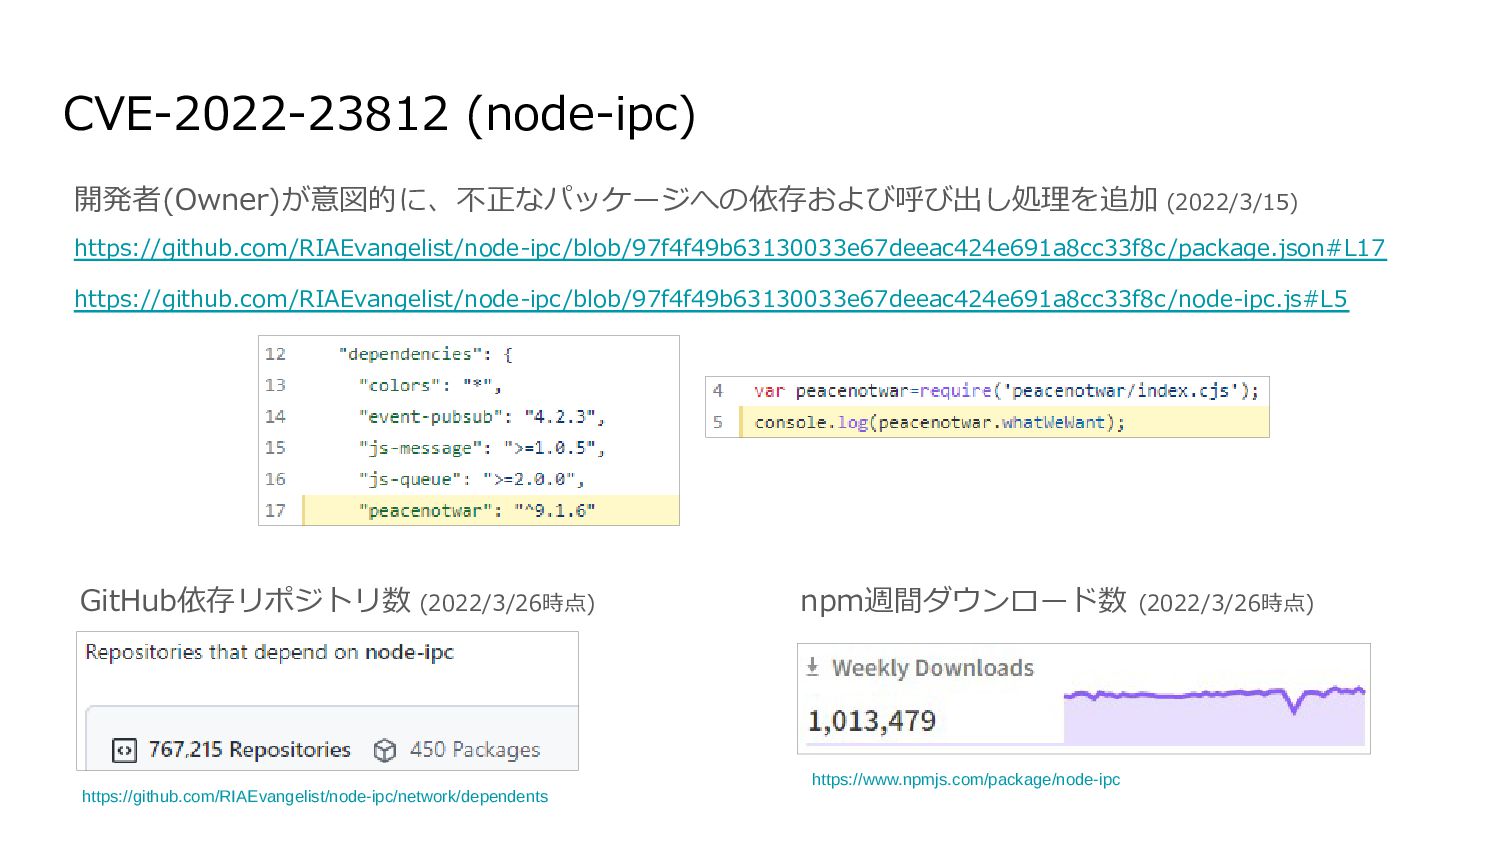
開発者(Owner)が意図的に、不正なパッケージへの依存および呼び出し処理を追加 (2022/3/15) https://github.com/RIAEvangelist/node-ipc/blob/97f4f49b63130033e67deeac424e691a8cc33f8c/package.json#L17 https://github.com/RIAEvangelist/node-ipc/blob/97f4f49b63130033e67deeac424e691a8cc33f8c/node-ipc.js#L5 CVE-2022-23812 (node-ipc) https://github.com/RIAEvangelist/node-ipc/network/dependents GitHub依存リポジトリ数 (2022/3/26時点) npm週間ダウンロード数
(2022/3/26時点) https://www.npmjs.com/package/node-ipc -
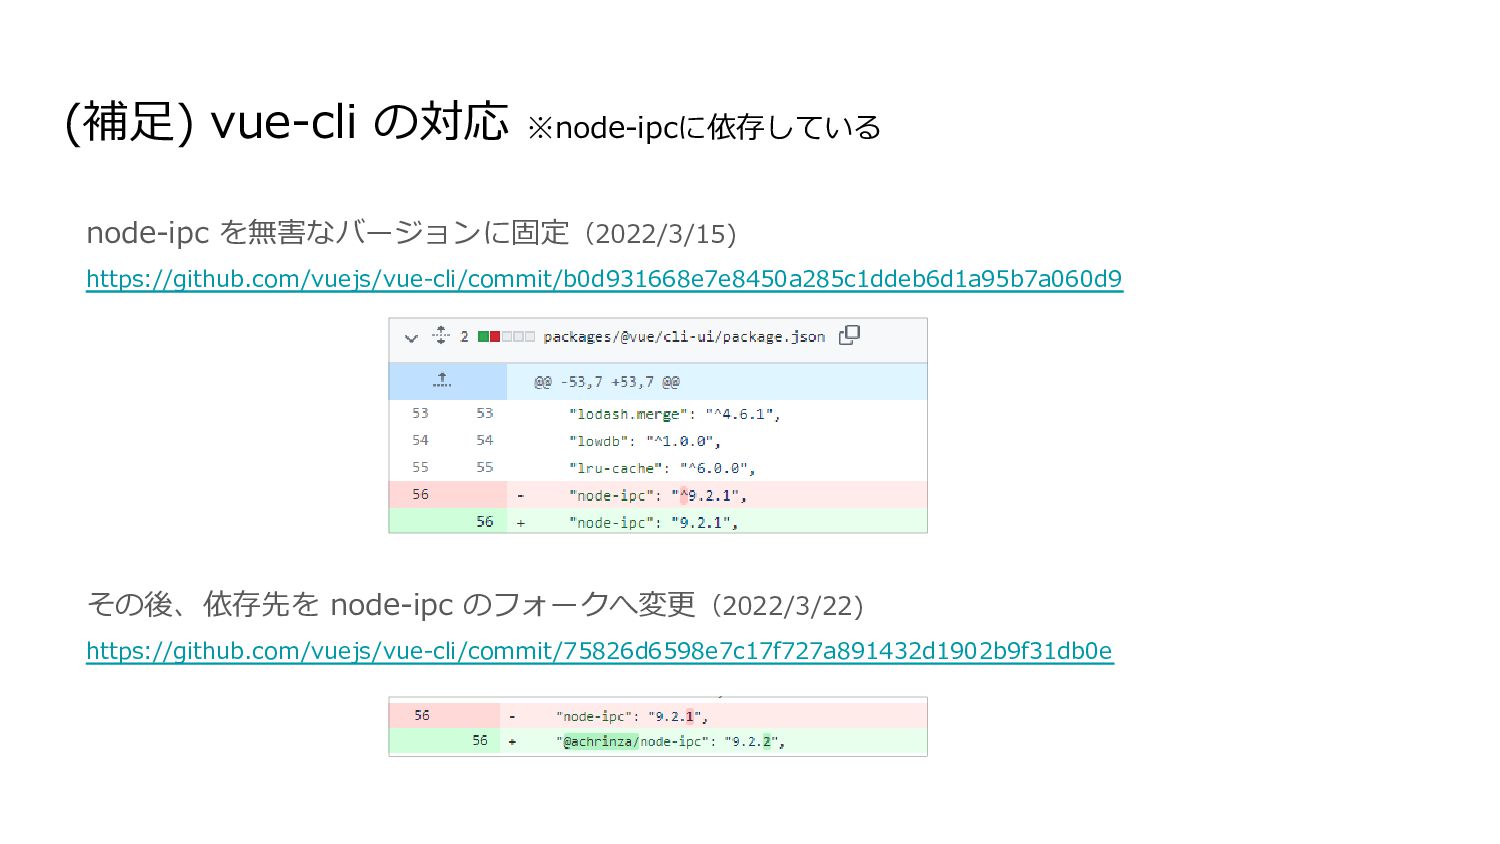
(補足) vue-cli の対応 ※node-ipcに依存している node-ipc を無害なバージョンに固定(2022/3/15) https://github.com/vuejs/vue-cli/commit/b0d931668e7e8450a285c1ddeb6d1a95b7a060d9 その後、依存先を node-ipc のフォークへ変更(2022/3/22)
https://github.com/vuejs/vue-cli/commit/75826d6598e7c17f727a891432d1902b9f31db0e -
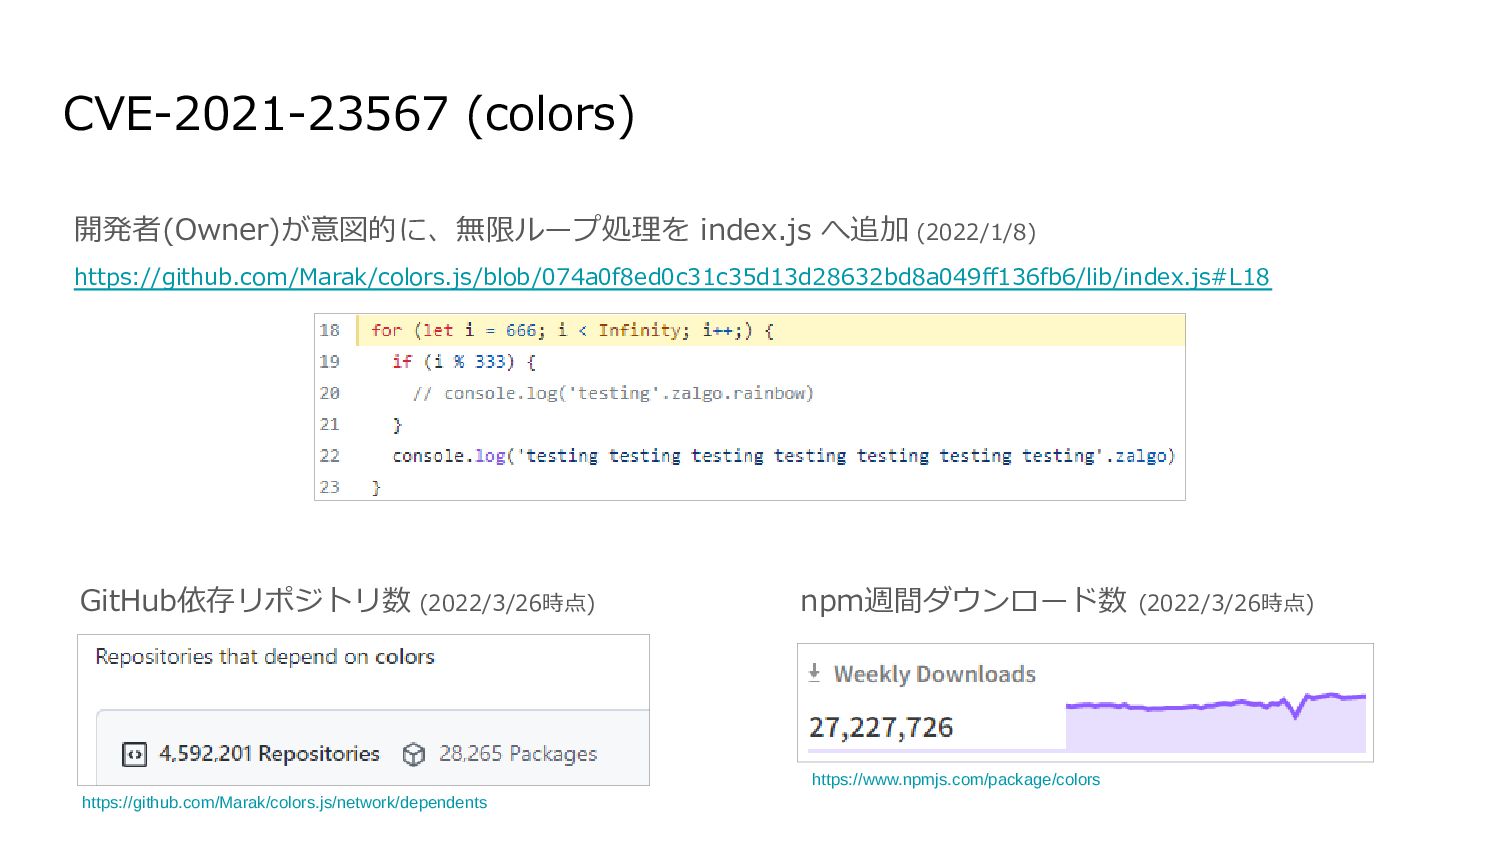
開発者(Owner)が意図的に、無限ループ処理を index.js へ追加 (2022/1/8) https://github.com/Marak/colors.js/blob/074a0f8ed0c31c35d13d28632bd8a049ff136fb6/lib/index.js#L18 CVE-2021-23567 (colors) https://github.com/Marak/colors.js/network/dependents GitHub依存リポジトリ数 (2022/3/26時点)
npm週間ダウンロード数 (2022/3/26時点) https://www.npmjs.com/package/colors -
開発者(Owner)のnpmアカウントがハイジャックされ、インストール時に動作する不正処理が追加された (2021/10/22) [参考]https://github.com/faisalman/ua-parser-js/issues/536#issuecomment-949742904 https://www.bleepingcomputer.com/news/security/popular-npm-library-hijacked-to-install-password-stealers-miners/ Embedded Malicious Code (UAParser.js) https://github.com/faisalman/ua-parser-js/network/dependents GitHub依存リポジトリ数
(2022/3/26時点) npm週間ダウンロード数 (2022/3/26時点) https://www.npmjs.com/package/ua-parser-js -
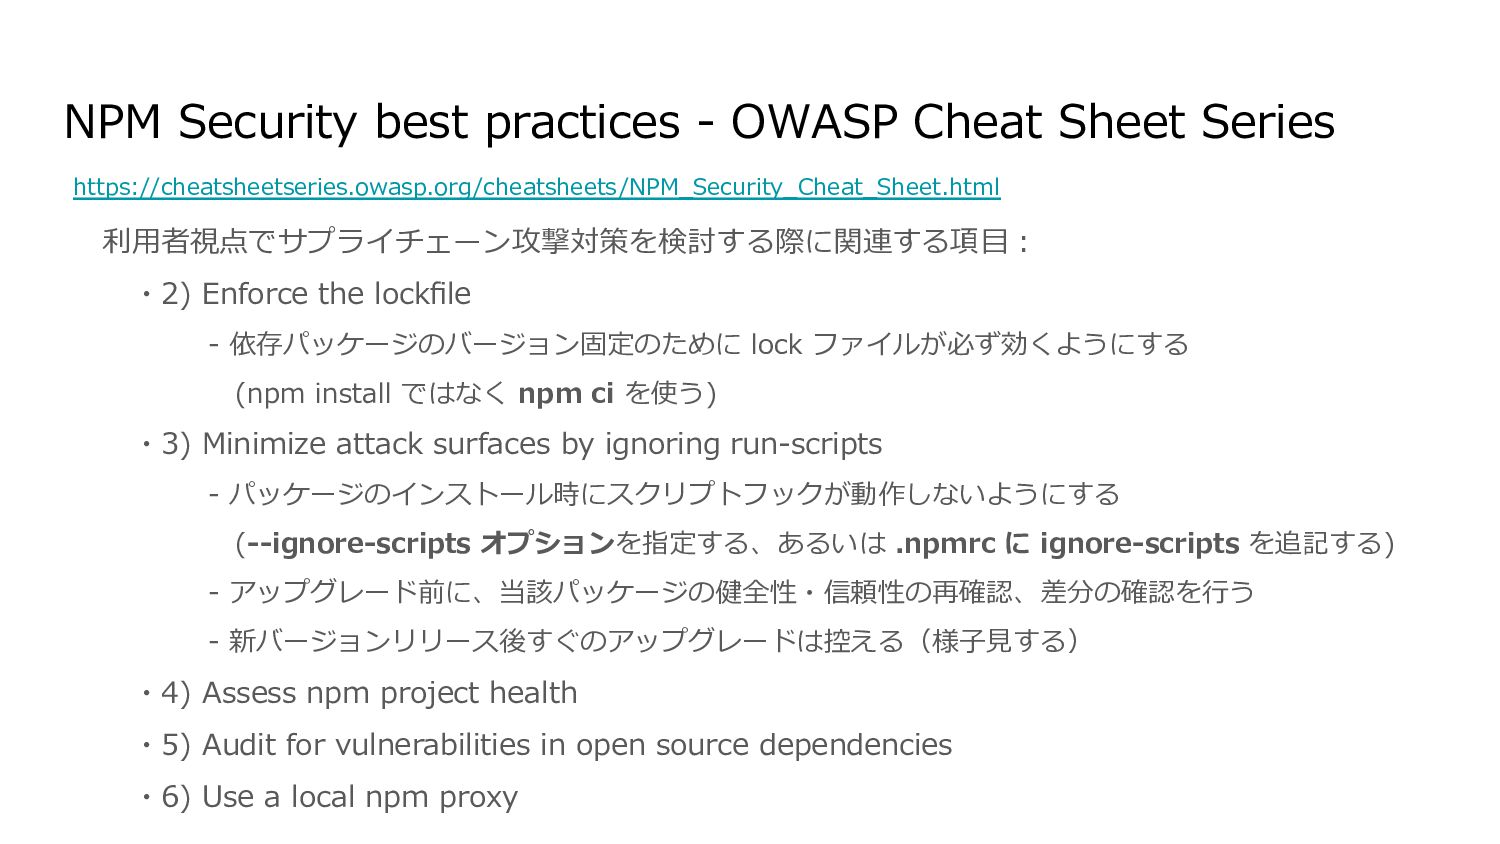
https://cheatsheetseries.owasp.org/cheatsheets/NPM_Security_Cheat_Sheet.html 利用者視点でサプライチェーン攻撃対策を検討する際に関連する項目: ・2) Enforce the lockfile - 依存パッケージのバージョン固定のために lock ファイルが必ず効くようにする
(npm install ではなく npm ci を使う) ・3) Minimize attack surfaces by ignoring run-scripts - パッケージのインストール時にスクリプトフックが動作しないようにする (--ignore-scripts オプションを指定する、あるいは .npmrc に ignore-scripts を追記する) - アップグレード前に、当該パッケージの健全性・信頼性の再確認、差分の確認を行う - 新バージョンリリース後すぐのアップグレードは控える(様子見する) ・4) Assess npm project health ・5) Audit for vulnerabilities in open source dependencies ・6) Use a local npm proxy NPM Security best practices - OWASP Cheat Sheet Series -
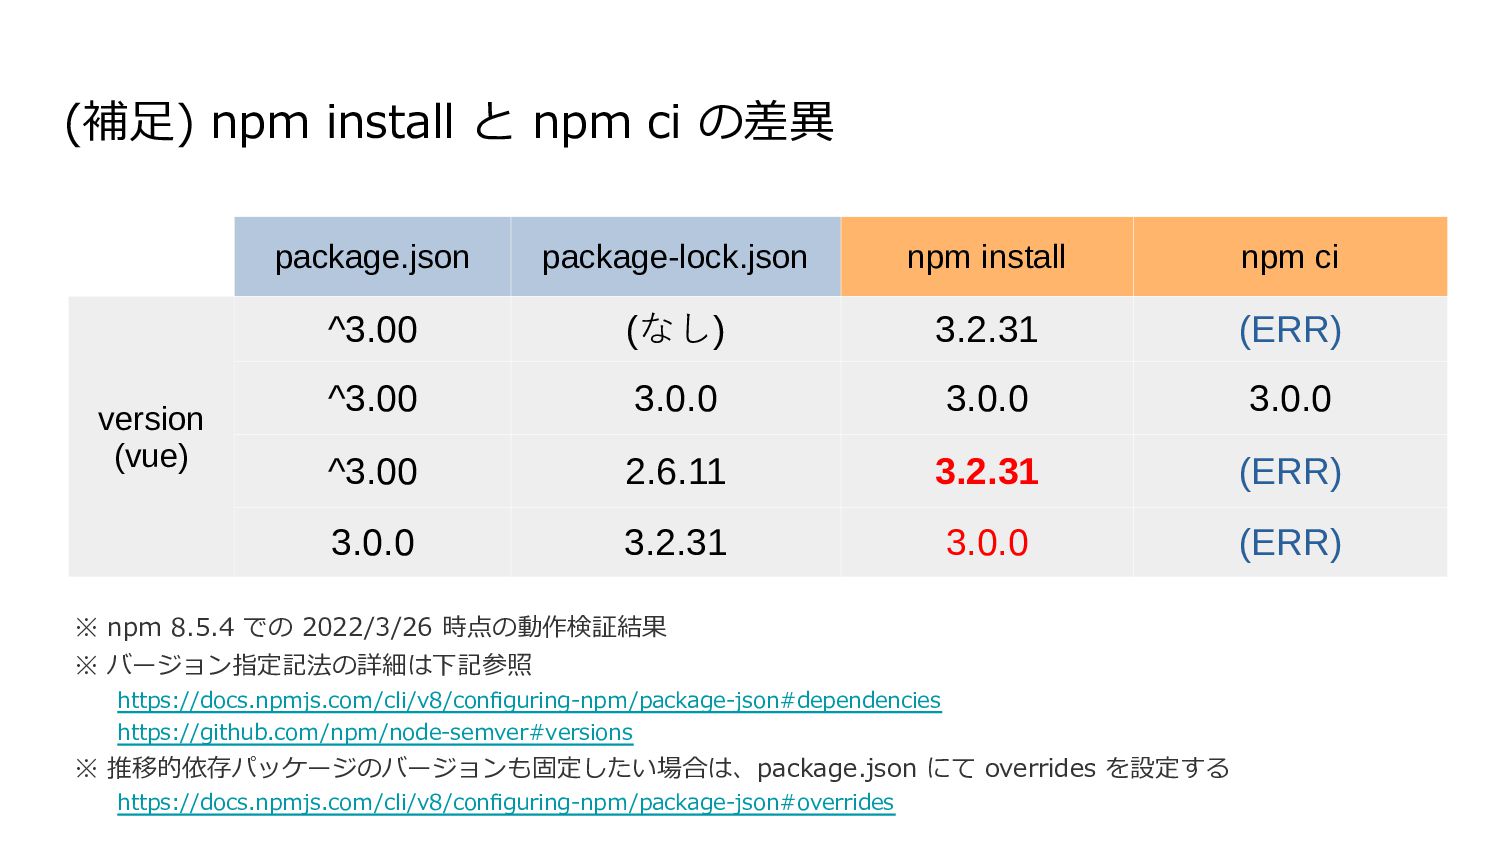
(補足) npm install と npm ci の差異 package.json package-lock.json npm
install npm ci version (vue) ^3.00 (なし) 3.2.31 (ERR) ^3.00 3.0.0 3.0.0 3.0.0 ^3.00 2.6.11 3.2.31 (ERR) 3.0.0 3.2.31 3.0.0 (ERR) ※ npm 8.5.4 での 2022/3/26 時点の動作検証結果 ※ バージョン指定記法の詳細は下記参照 https://docs.npmjs.com/cli/v8/configuring-npm/package-json#dependencies https://github.com/npm/node-semver#versions ※ 推移的依存パッケージのバージョンも固定したい場合は、package.json にて overrides を設定する https://docs.npmjs.com/cli/v8/configuring-npm/package-json#overrides -
4. 参考資料 ▪ CVE-2022-23812 (node-ipc) ・https://nvd.nist.gov/vuln/detail/CVE-2022-23812 ・https://qiita.com/SnykSec/items/6e75bd78b4deb3371550 ・https://zenn.dev/azu/articles/e248ed86fb6d34 ▪ CVE-2021-23567
(colors) ・https://nvd.nist.gov/vuln/detail/CVE-2021-23567 ・https://qiita.com/SnykSec/items/23bcd8dc873239d2bece ▪ Embedded Malicious Code (UAParser.js) ・https://security.snyk.io/vuln/SNYK-JS-UAPARSERJS-1766952 ・https://gigazine.net/news/20211025-npm-library-hijacked-password-stealers-miners/ ▪ npm Security ・https://cheatsheetseries.owasp.org/cheatsheets/NPM_Security_Cheat_Sheet.html ・https://snyk.io/blog/ten-npm-security-best-practices/