Share
Embed
Authentication and Access Control
Slides for the "Community Morning #3" meeting - http://msmvppt.github.io/community-morning-september-2015.html - Lisbon, September 2015.
The code is available - https://github.com/pmhsfelix/demos-netponto-oidc-idsrv
Pedro Felix
September 19, 2015
Transcript
56 slides
-
Authentication and Access Control using OpenID Connect, JWT and IdentityServer3
Pedro Félix - @pmhsfelix Community Morning #3 -
Outline • Authentication and access control on modern Web Apps
and APIs • OAuth 2.0, OpenID Connect and JWT • IdentityServer3 -
whoami • Teacher at the Lisbon Polytechnic Institute (ISEL) •
Software developer and consultant • Telco and media industries • Focus on Web APIs, Identity and Access Management • Designing Evolvable Web APIs with ASP.NET, O’Reilly, 2014 See http://webapibook.net/ -
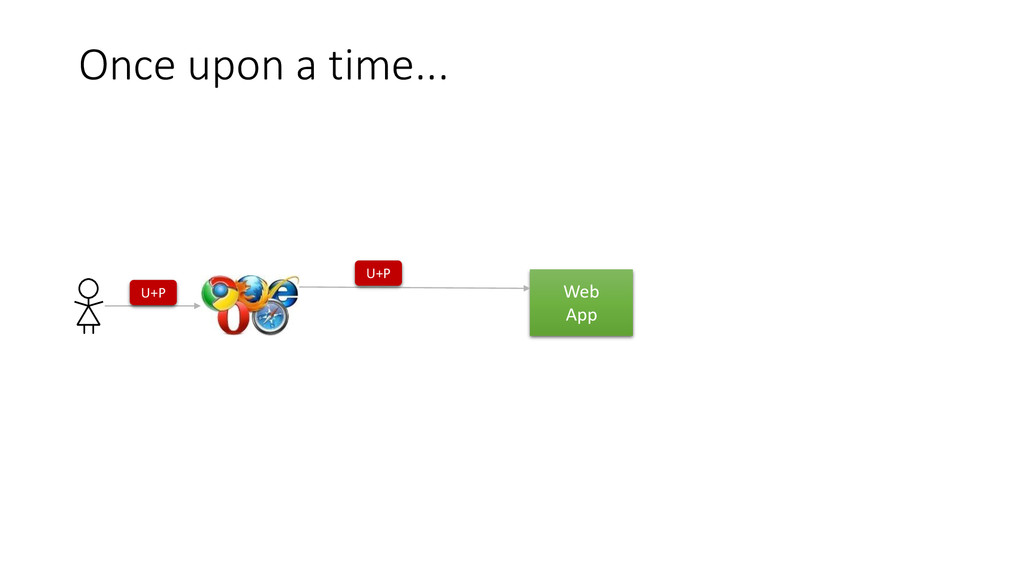
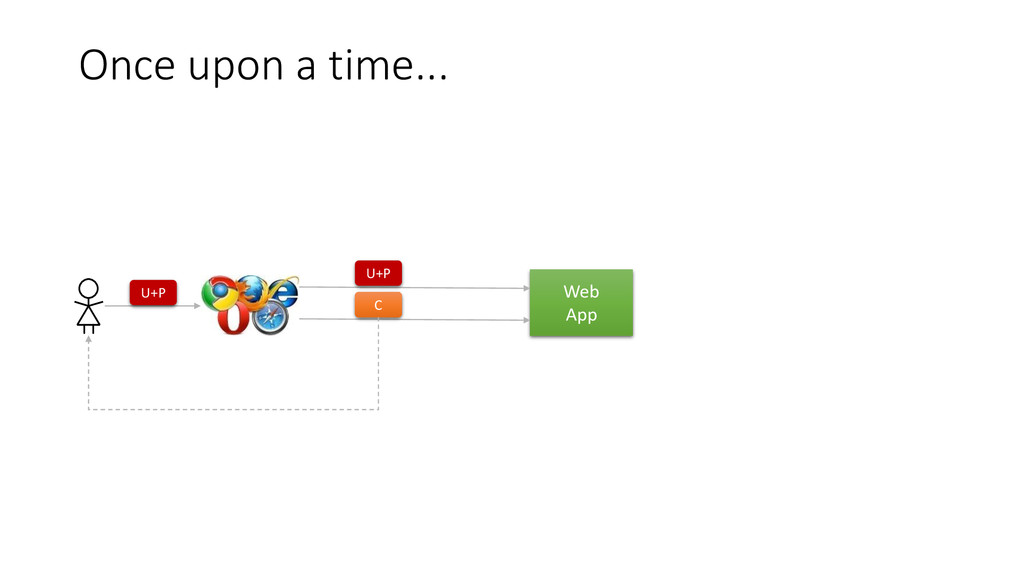
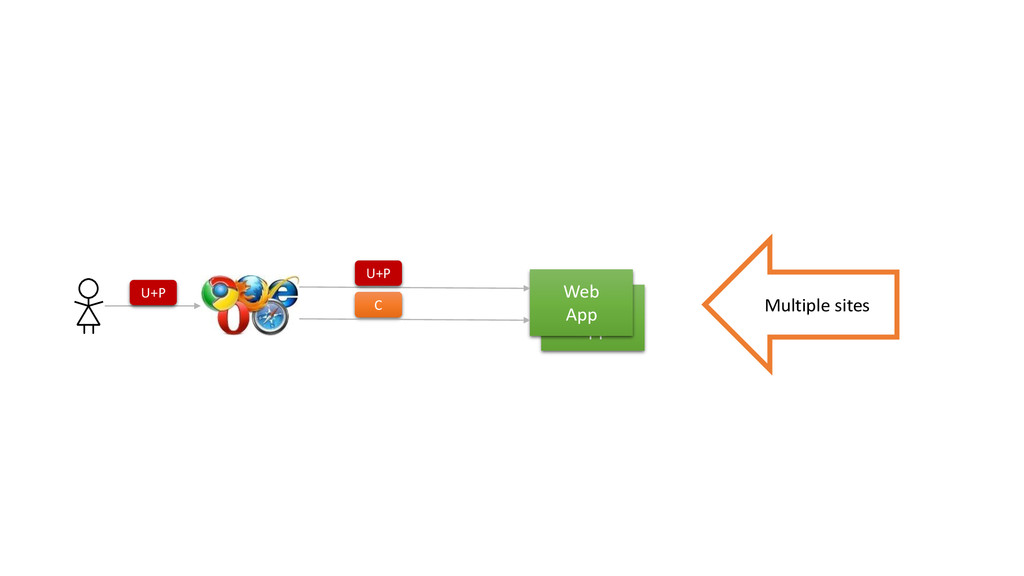
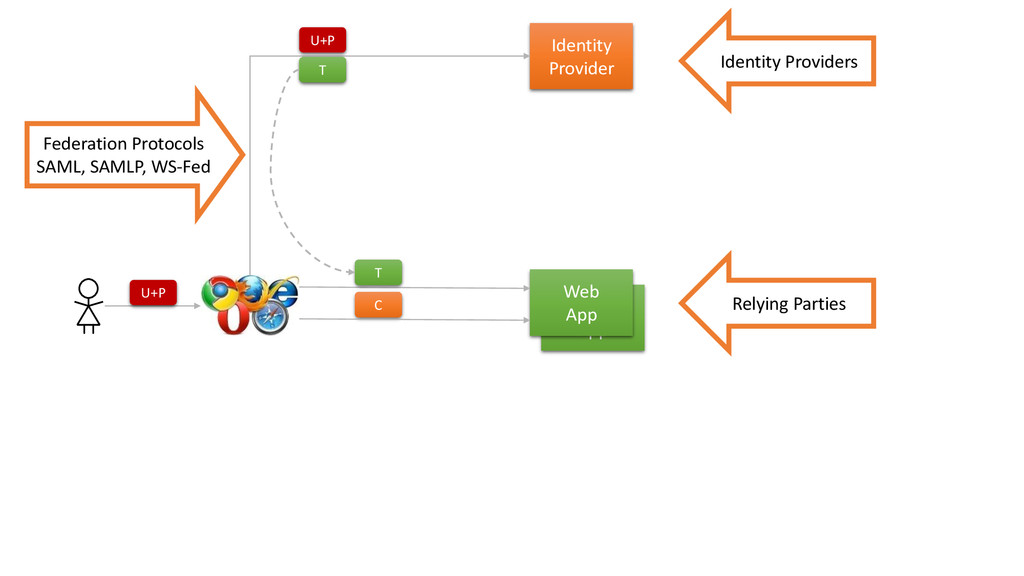
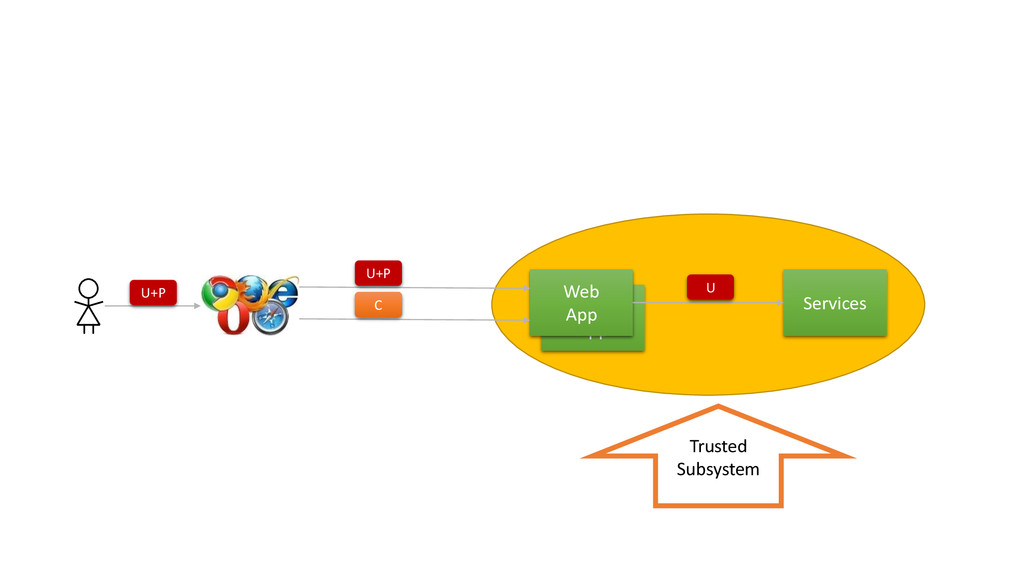
Web App Web App U+P C T Identity Provider U+P
T Identity Providers Relying Parties Federation Protocols SAML, SAMLP, WS-Fed -
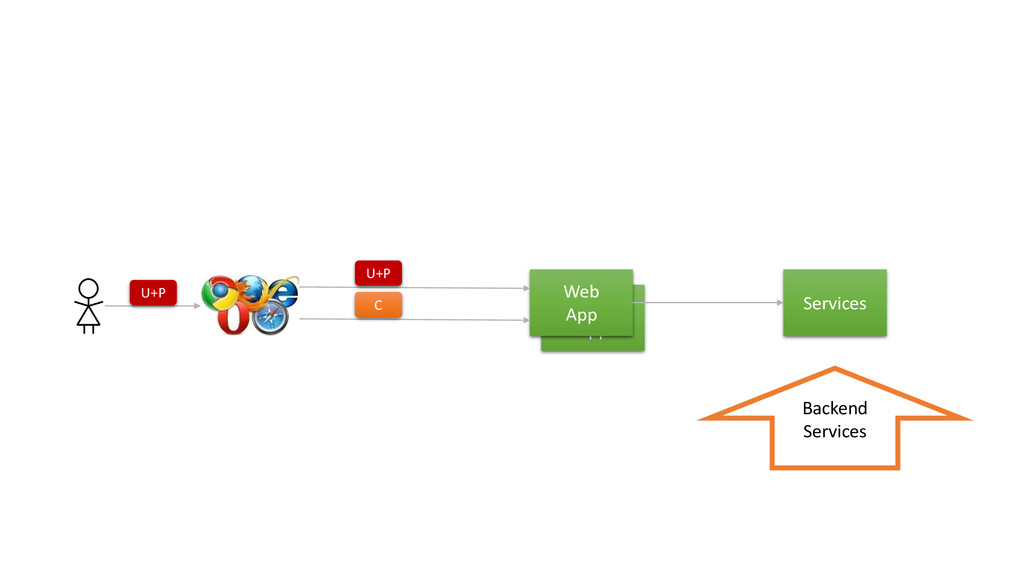
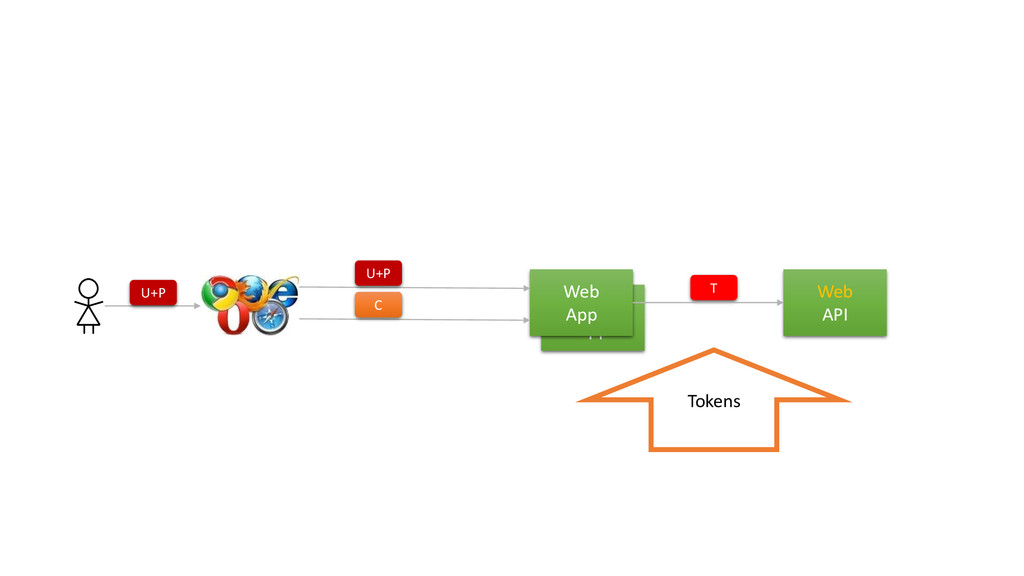
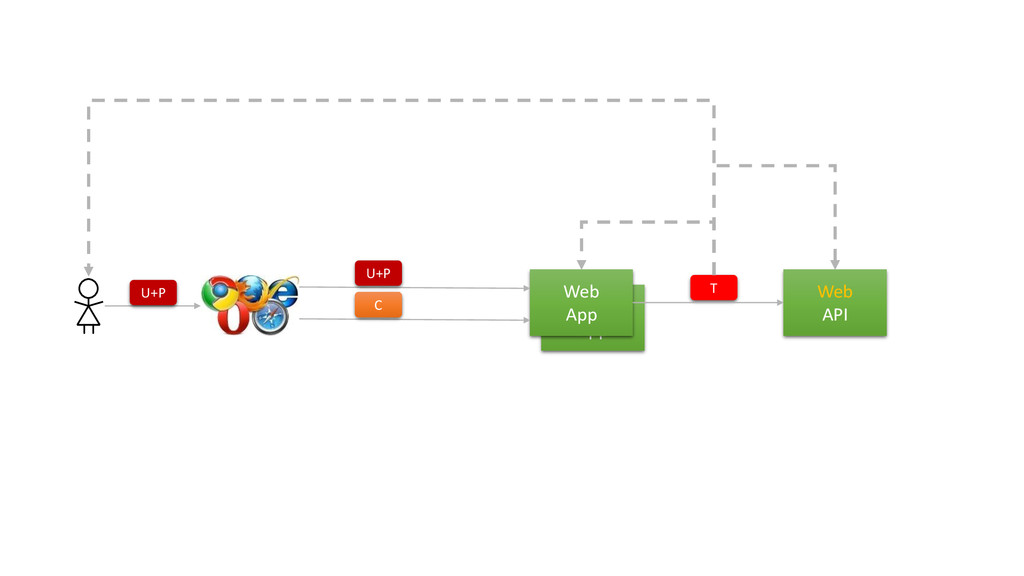
Web App Web App U+P C Web API T T
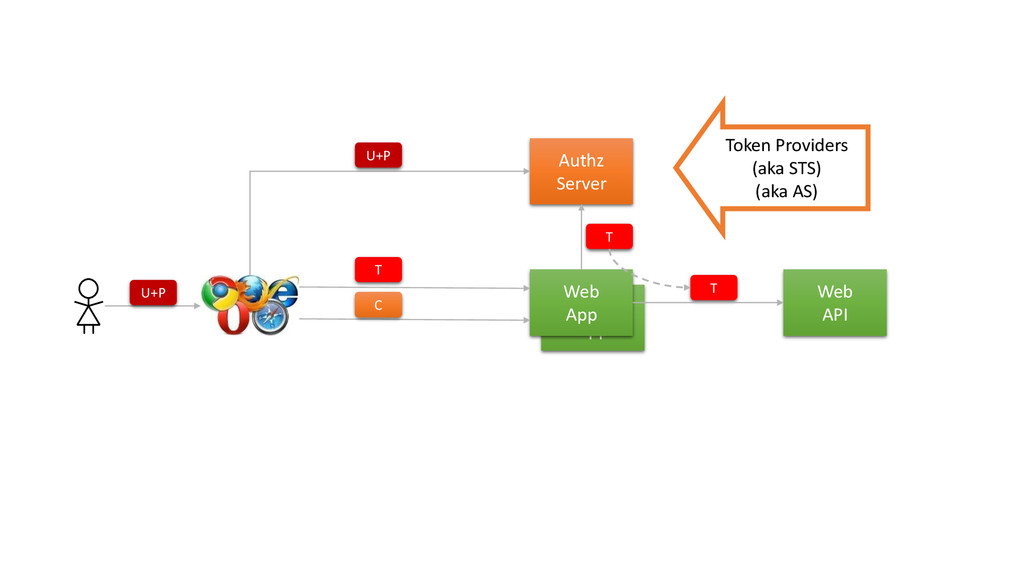
Authz Server T Token Providers (aka STS) (aka AS) U+P -
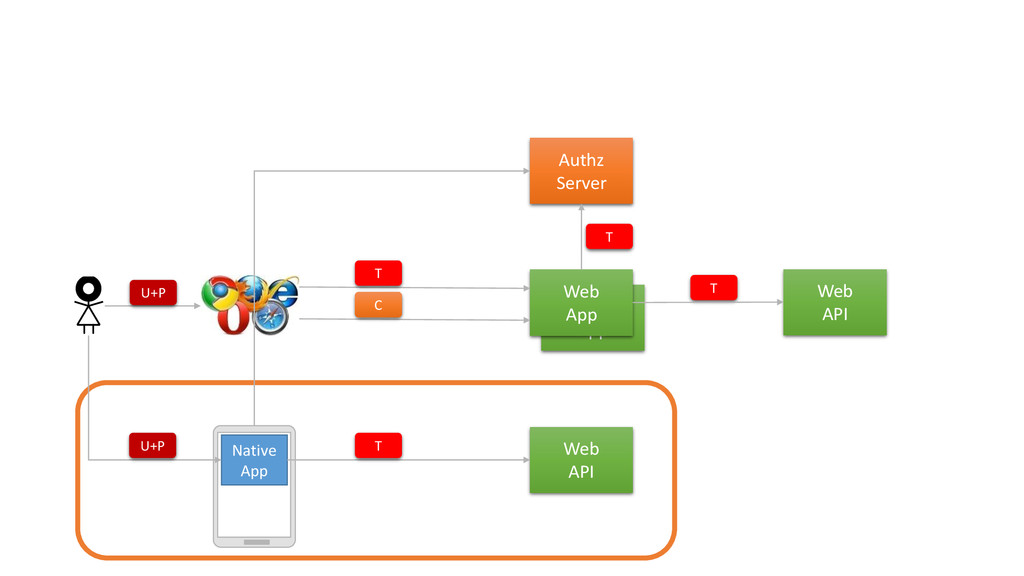
Web App Web App U+P T C Web API T
Web API Native App U+P Authz Server T T -
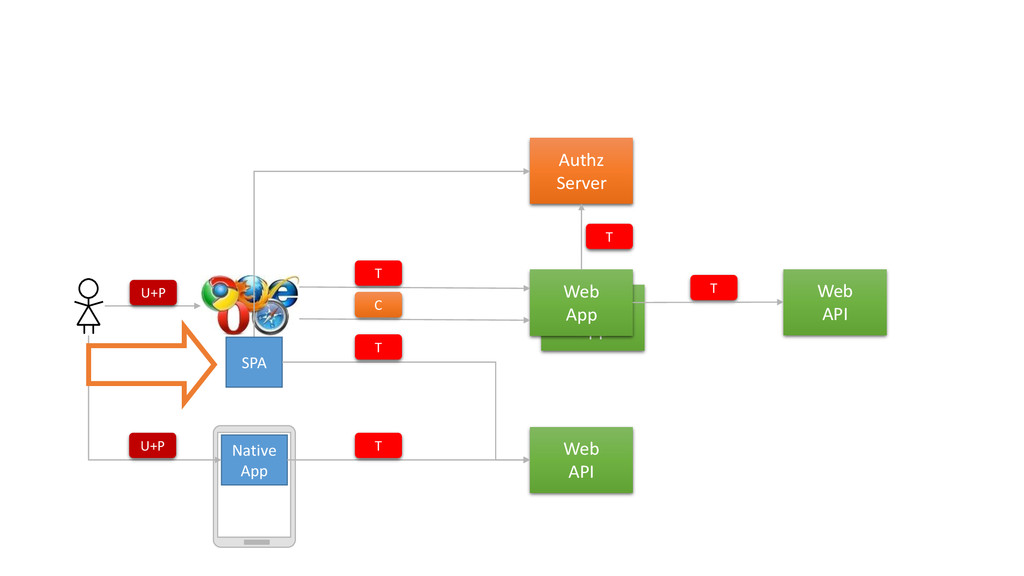
Web App Web App U+P T C Web API T
Web API Native App U+P Authz Server T T SPA T -
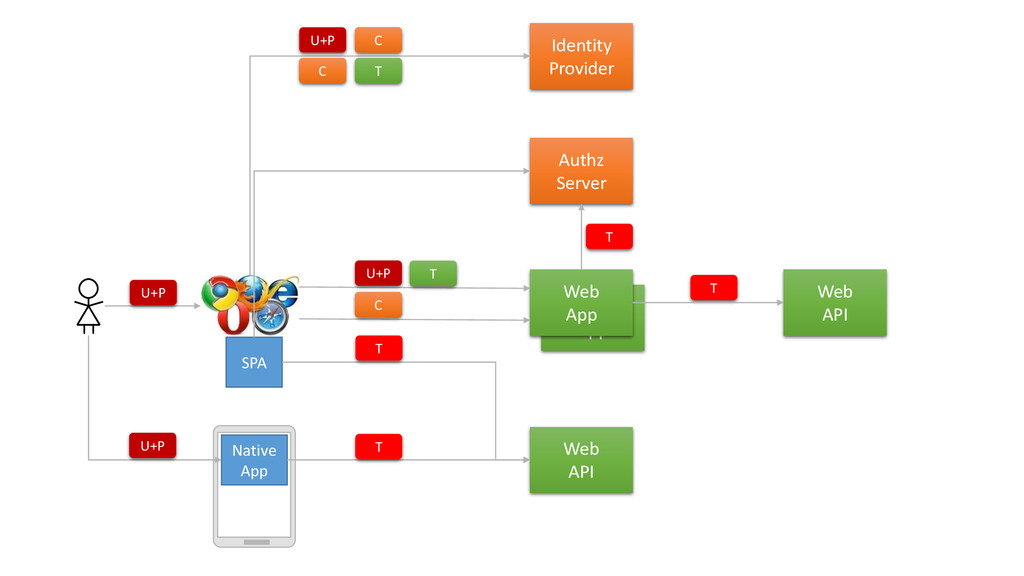
Web App Web App U+P U+P C Identity Provider U+P
C T C Web API T Web API Native App U+P T SPA T Authz Server T T -
Web App Web App U+P U+P C Identity Provider U+P
C T C Web API T Web API Native App U+P T SPA T Authz Server T T -
Challenges • How to achieve single sign-in between multiple apps?
• How to use social and partner identities? • How to access social and partner APIs? • How to secure my APIs from internal and external clients? -
Technologies • Federation • SAMLP and WS-Fed protocols • OpenID
protocol • SAML format (XML-based) -
Technologies • Federation • SAMLP and WS-Fed protocols • OpenID
protocol • SAML format (XML-based) • Token Based Access • WS-Security, WS-Trust • OAuth 1.0 • OAuth 2.0 -
Technologies • Federation • SAMLP and WS-Fed protocols • OpenID
protocol • SAML format (XML-based) • Token based access • WS-Security, WS-Trust • OAuth 1.0 • OAuth 2.0 -
OAuth 2.0 • Defines how to associate an access token
to a HTTP request -
OAuth 2.0 • Defines how to associate an access token
to a HTTP request • Define protocols for a client application to obtain access tokens... -
OAuth 2.0 • Defines how to associate an access token
to a HTTP request • Define protocols for a client application to obtain access tokens... • ... on its own behalf (server – server) • Client application identity • ... on an user’s behalf (user – server) • Client application identity • User identity • Delegated authorization scope -
OAuth 2.0 • Defines how to associate an access token
to a HTTP request • Define protocols for a client application to obtain access tokens... • ... on its own behalf (server – server) • Client application identity • ... on an user’s behalf (user – server) • Client application identity • User identity • Delegated authorization scope -
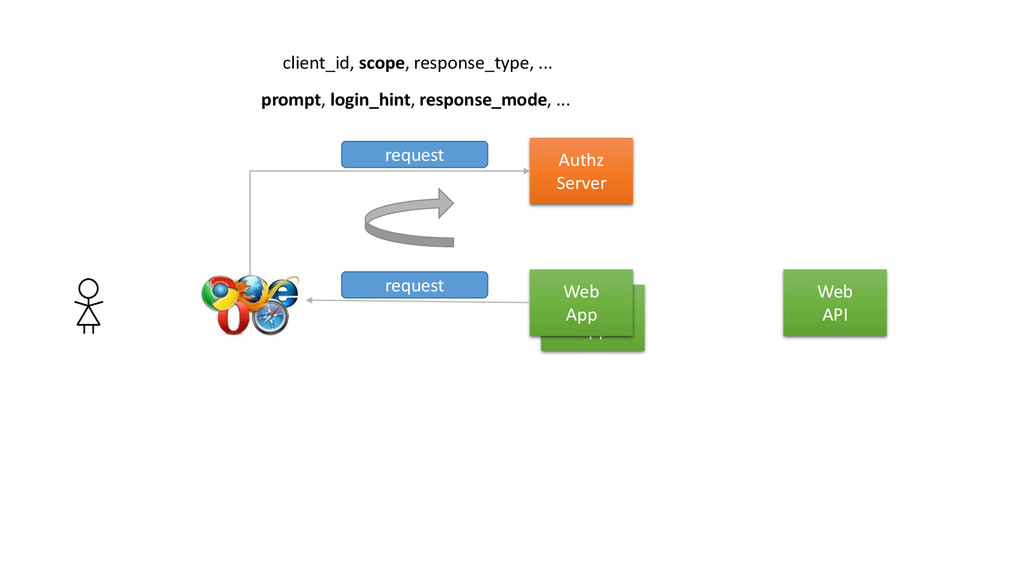
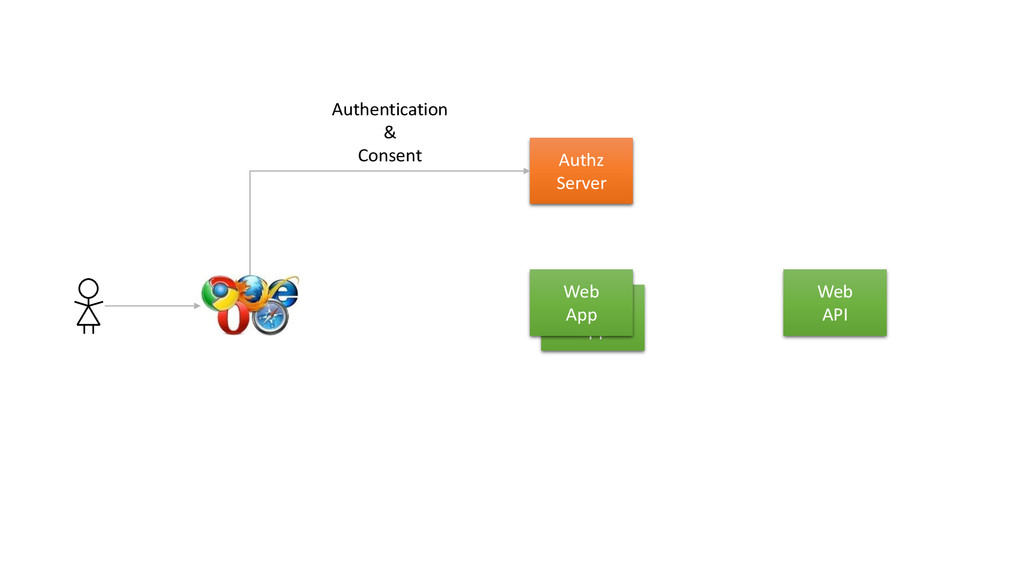
Web App Web App Web API Authz Server request request
client_id, scope, response_type, ... prompt, login_hint, response_mode, ... -
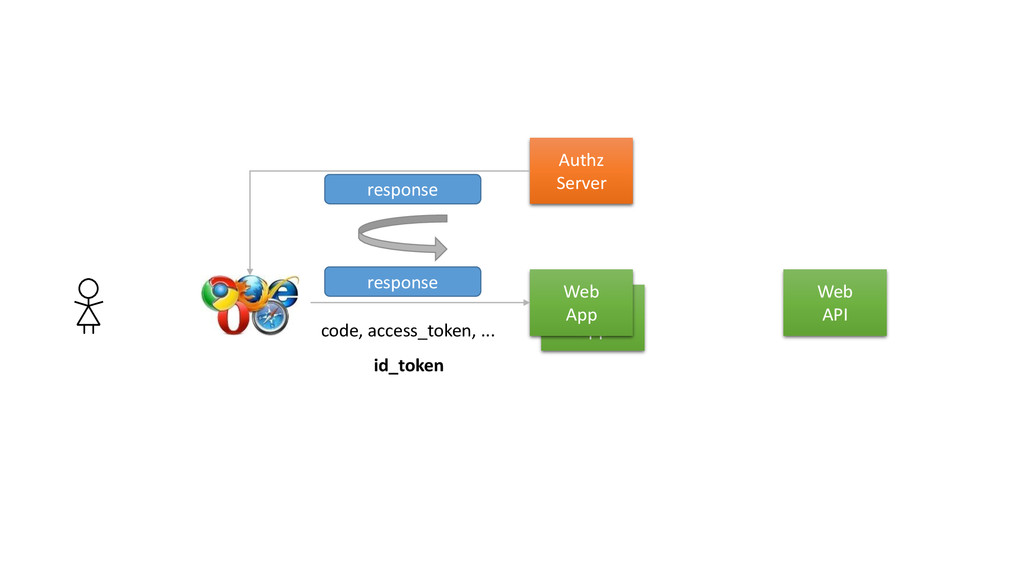
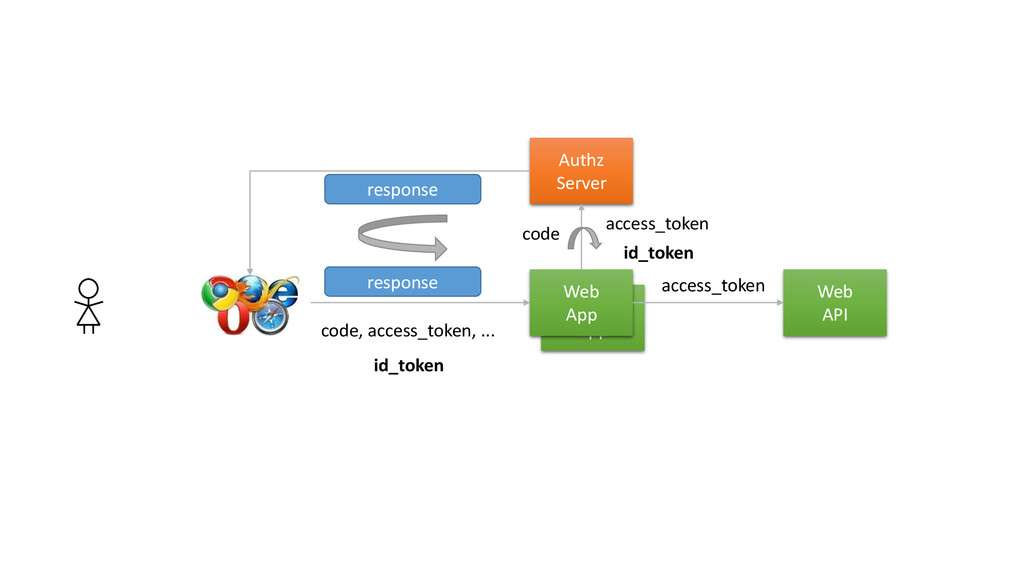
Web App Web App Web API Authz Server response response
code, access_token, ... id_token -
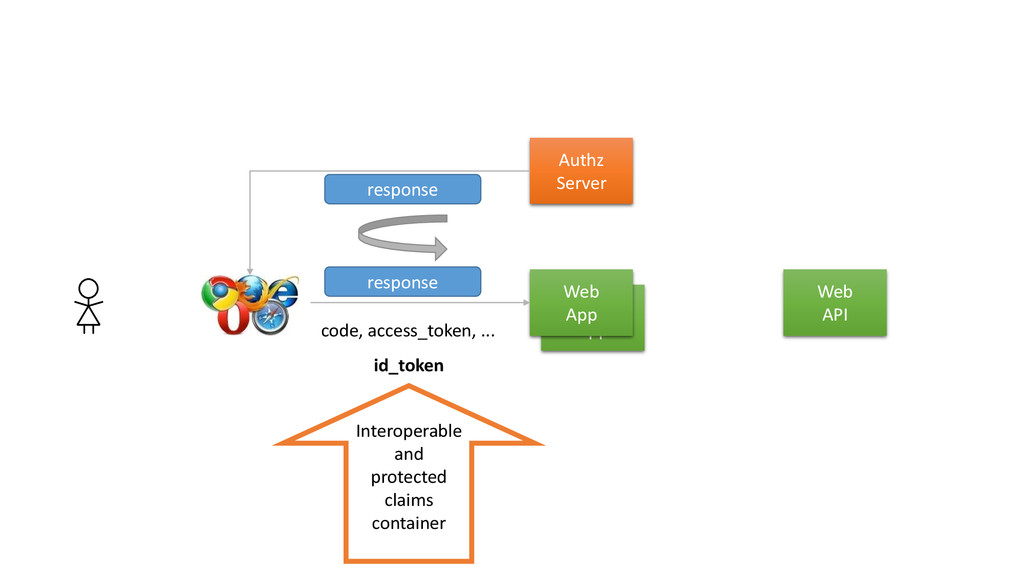
Web App Web App Web API Authz Server response response
code, access_token, ... id_token Interoperable and protected claims container -
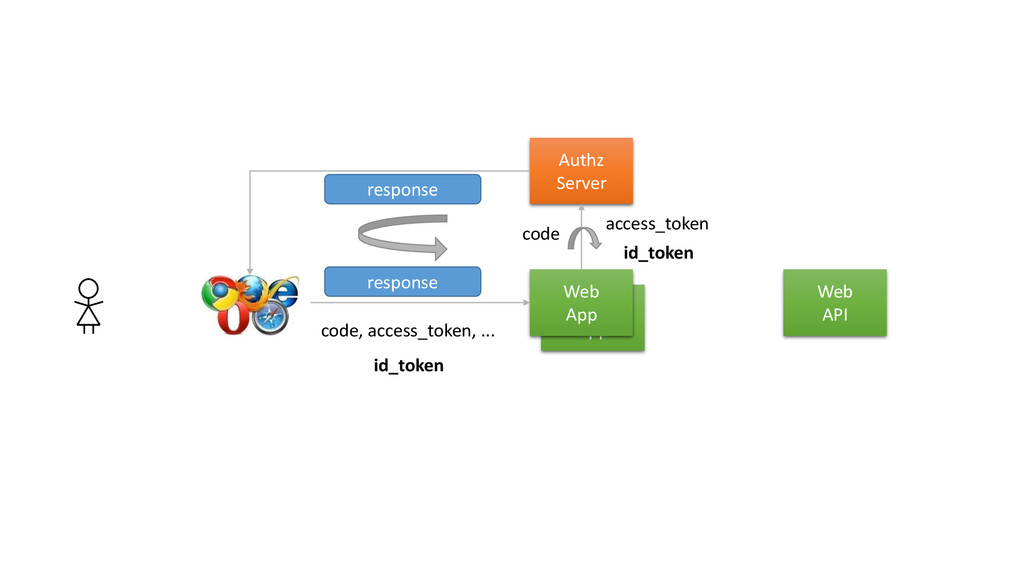
Web App Web App Web API Authz Server response response
code, access_token, ... id_token code access_token id_token -
Web App Web App Web API Authz Server response response
code, access_token, ... id_token code access_token id_token access_token -
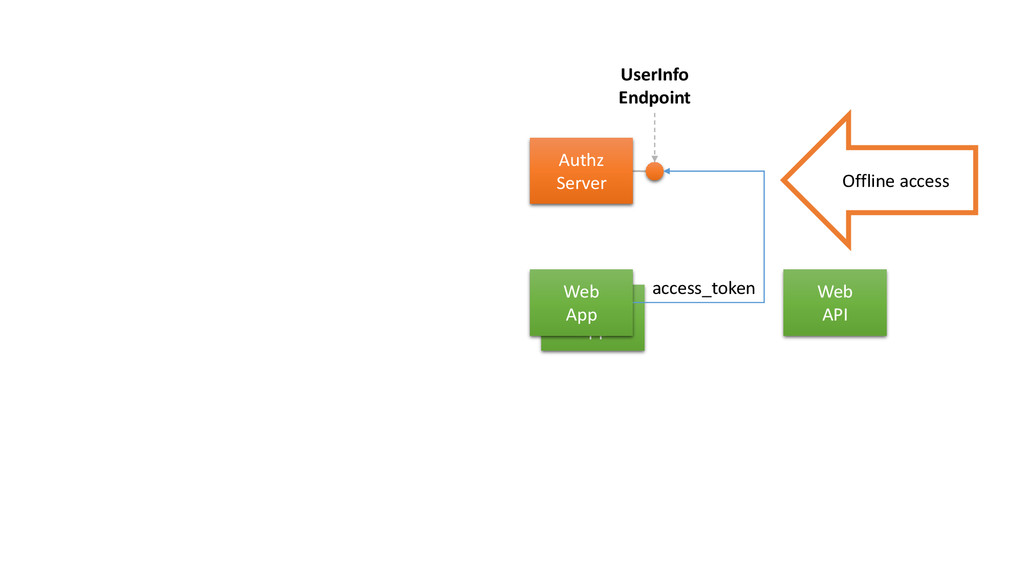
Web App Web App Web API access_token UserInfo Endpoint Authz
Server Offline access -
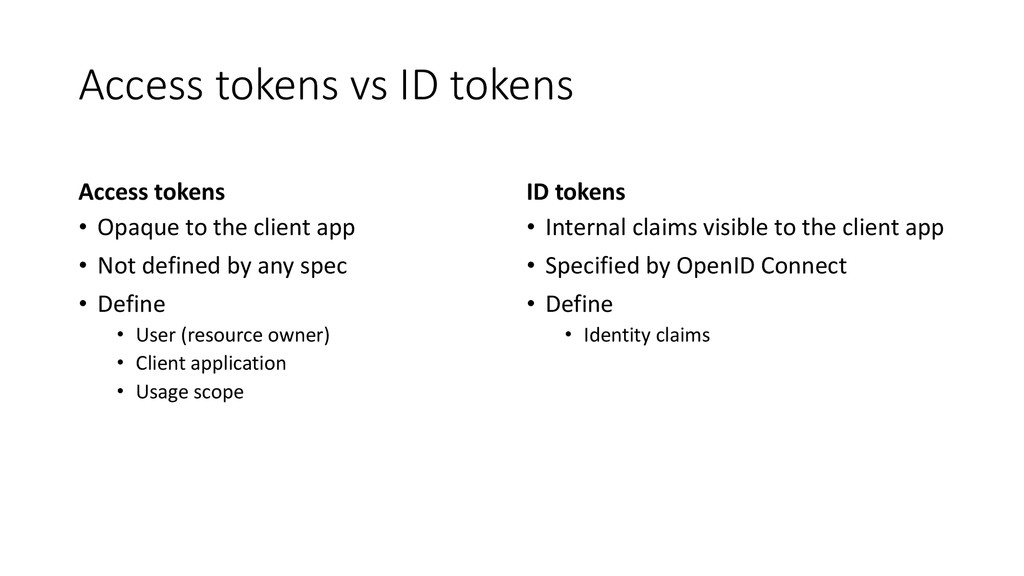
Access tokens vs ID tokens Access tokens • Opaque to
the client app • Not defined by any spec • Define • User (resource owner) • Client application • Usage scope ID tokens • Internal claims visible to the client app • Specified by OpenID Connect • Define • Identity claims -
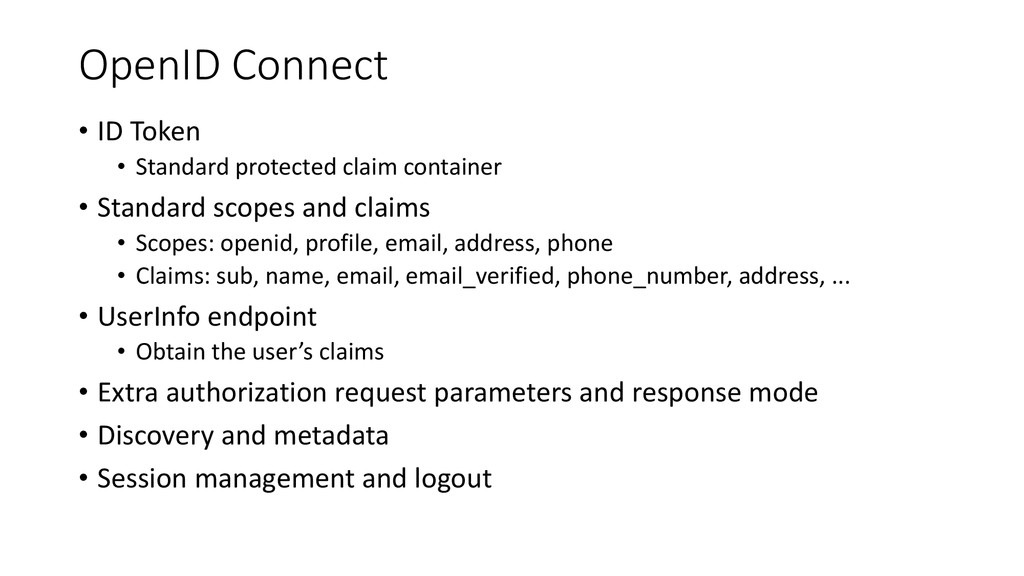
OpenID Connect • ID Token • Standard protected claim container
• Standard scopes and claims • Scopes: openid, profile, email, address, phone • Claims: sub, name, email, email_verified, phone_number, address, ... • UserInfo endpoint • Obtain the user’s claims • Extra authorization request parameters and response mode • Discovery and metadata • Session management and logout -
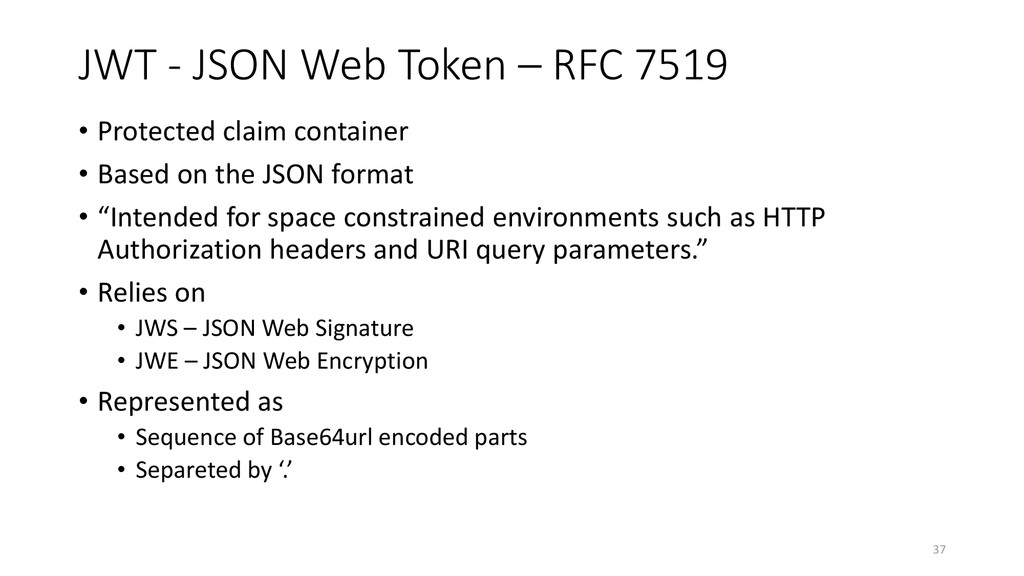
JWT - JSON Web Token – RFC 7519 • Protected
claim container • Based on the JSON format • “Intended for space constrained environments such as HTTP Authorization headers and URI query parameters.” • Relies on • JWS – JSON Web Signature • JWE – JSON Web Encryption • Represented as • Sequence of Base64url encoded parts • Separeted by ‘.’ 37 -
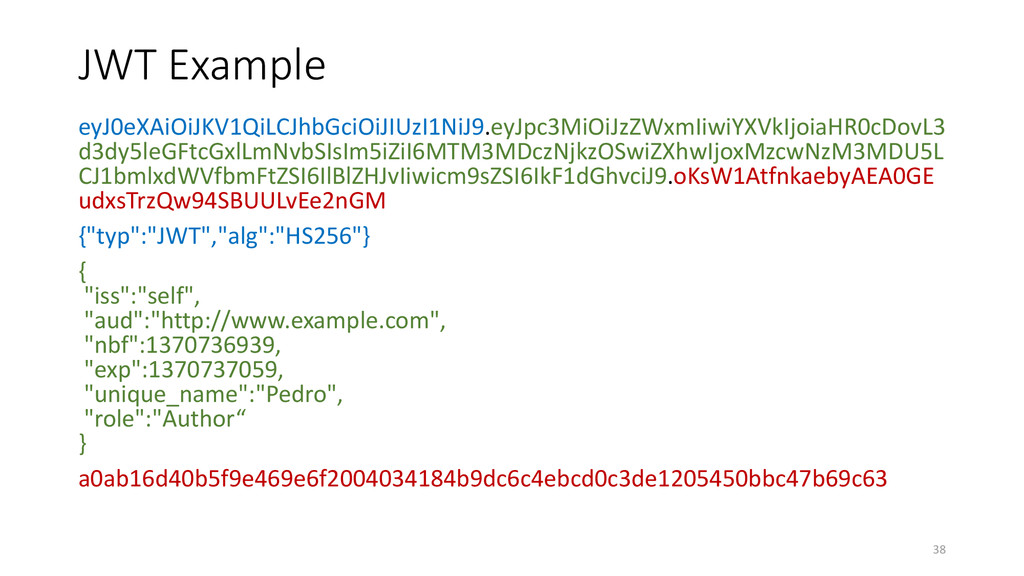
JWT Example eyJ0eXAiOiJKV1QiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiJzZWxmIiwiYXVkIjoiaHR0cDovL3 d3dy5leGFtcGxlLmNvbSIsIm5iZiI6MTM3MDczNjkzOSwiZXhwIjoxMzcwNzM3MDU5L CJ1bmlxdWVfbmFtZSI6IlBlZHJvIiwicm9sZSI6IkF1dGhvciJ9.oKsW1AtfnkaebyAEA0GE udxsTrzQw94SBUULvEe2nGM {"typ":"JWT","alg":"HS256"} { "iss":"self", "aud":"http://www.example.com",
"nbf":1370736939, "exp":1370737059, "unique_name":"Pedro", "role":"Author“ } a0ab16d40b5f9e469e6f2004034184b9dc6c4ebcd0c3de1205450bbc47b69c63 38 -
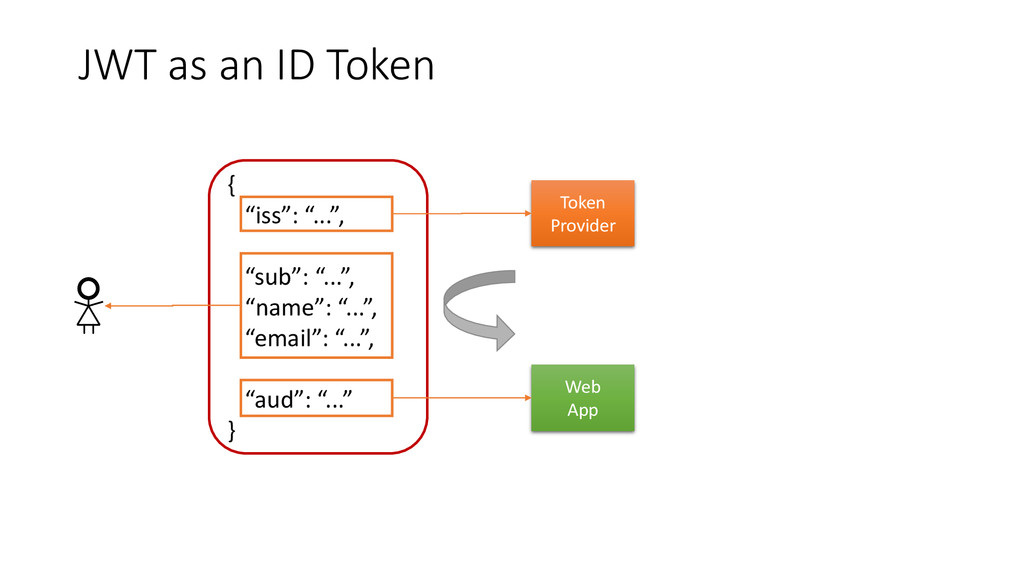
{ “iss”: “...”, “sub”: “...”, “name”: “...”, “email”: “...”, “aud”:
“...” } Web App Token Provider JWT as an ID Token -
JWT – other uses And because a secure container format
always comes in handy... • ... Access Tokens • ... Cookies -
IdentityServer3 • Open source project created by Dominick Baier and
Brock Allen • Apache 2.0 • .NET Foundation • https://github.com/IdentityServer/IdentityServer3 -
IdentityServer3 • Open source project created by Dominick Baier and
Brock Allen • Apache 2.0 • .NET Foundation • https://github.com/IdentityServer/IdentityServer3 • Extensible OpenID Connect and OAuth2 authorization server • “framework and a hostable component” • “allows implementing single sign-on and access control for modern web applications and APIs” • “using protocols like OpenID Connect and OAuth2” -
IdentityServer3 • Open source project created by Dominick Baier and
Brock Allen • Apache 2.0 • .NET Foundation • https://github.com/IdentityServer/IdentityServer3 • Extensible OpenID Connect and OAuth2 authorization server • “framework and a hostable component” • “allows implementing single sign-on and access control for modern web applications and APIs” • “using protocols like OpenID Connect and OAuth2” • Based on Katana and ASP.NET Web API -
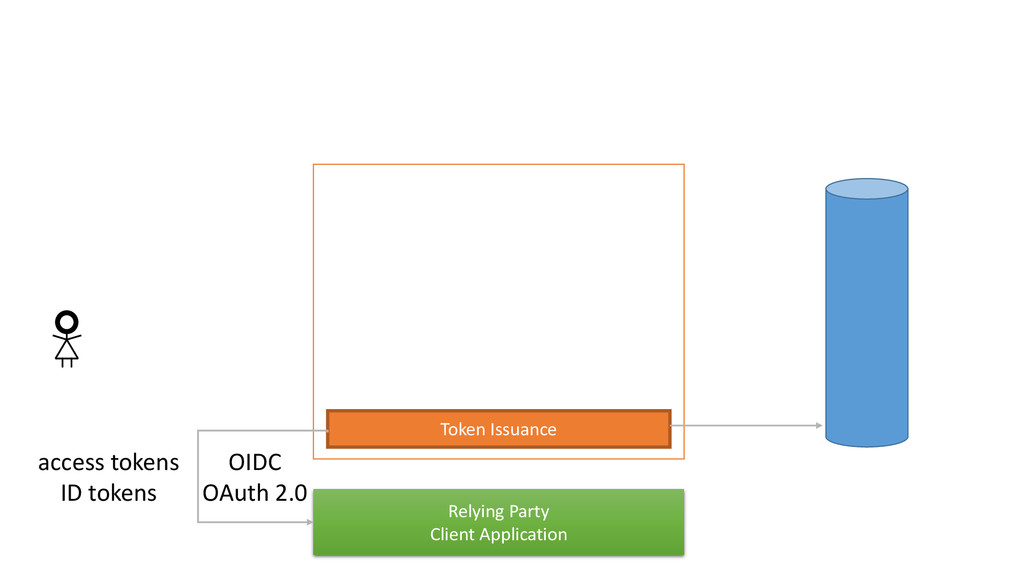
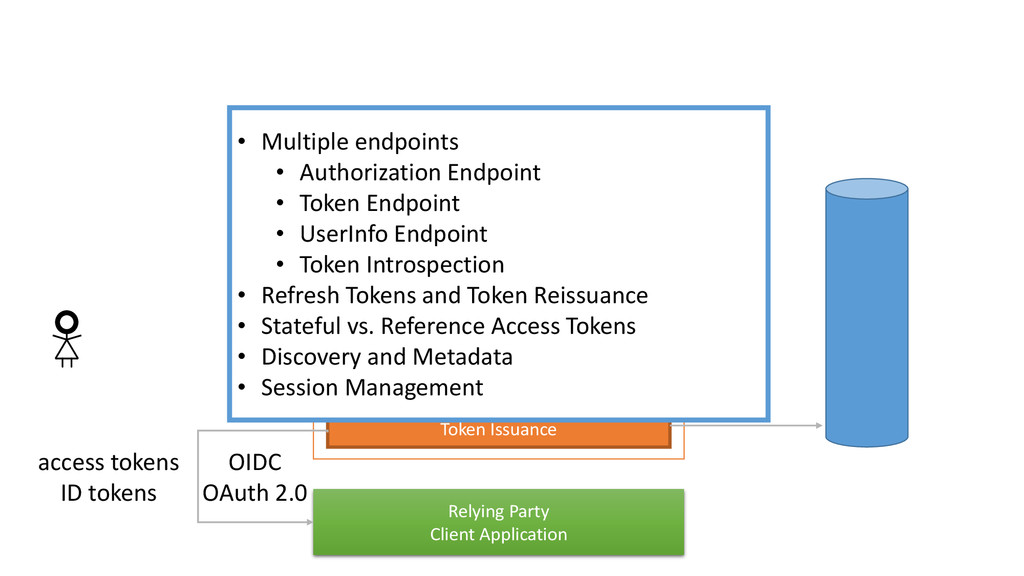
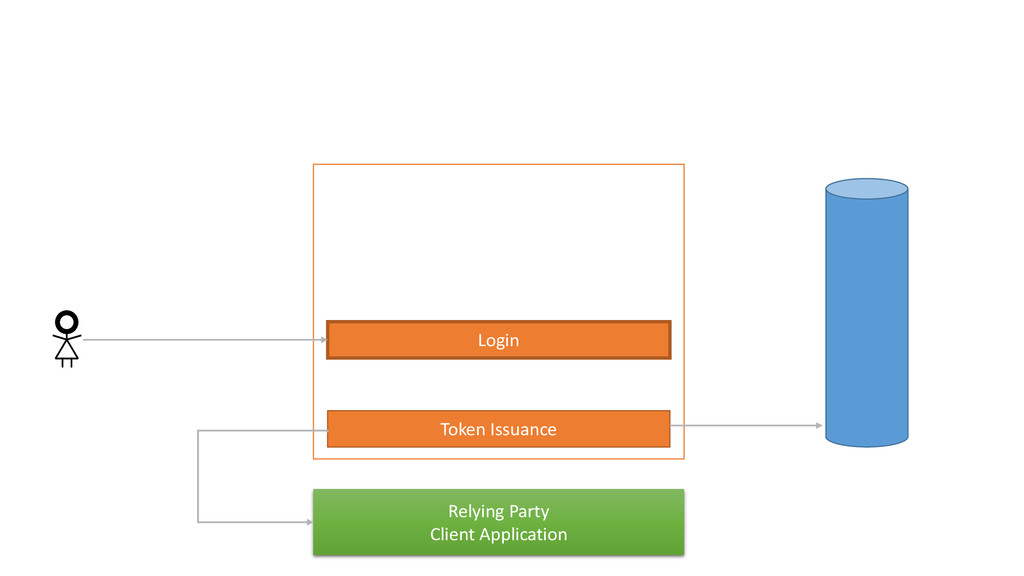
Relying Party Client Application Token Issuance access tokens ID tokens
OIDC OAuth 2.0 • Multiple endpoints • Authorization Endpoint • Token Endpoint • UserInfo Endpoint • Token Introspection • Refresh Tokens and Token Reissuance • Stateful vs. Reference Access Tokens • Discovery and Metadata • Session Management -
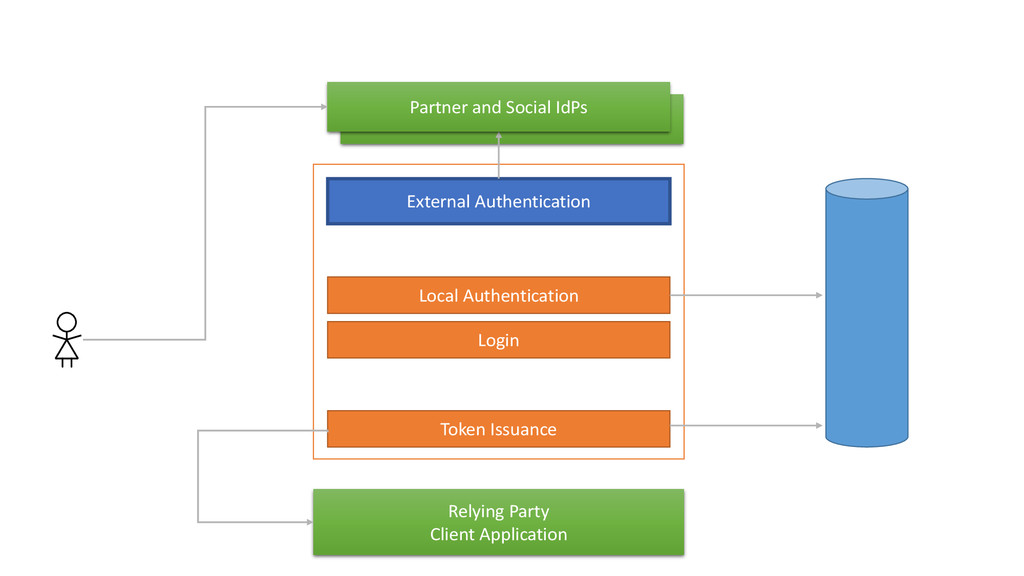
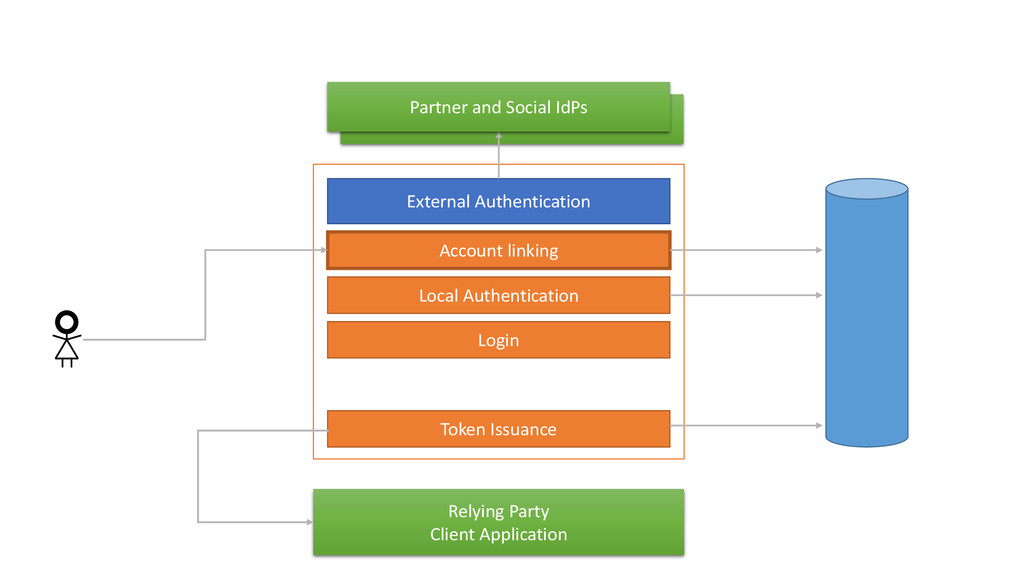
Partner and Social IdPs Relying Party Client Application Token Issuance
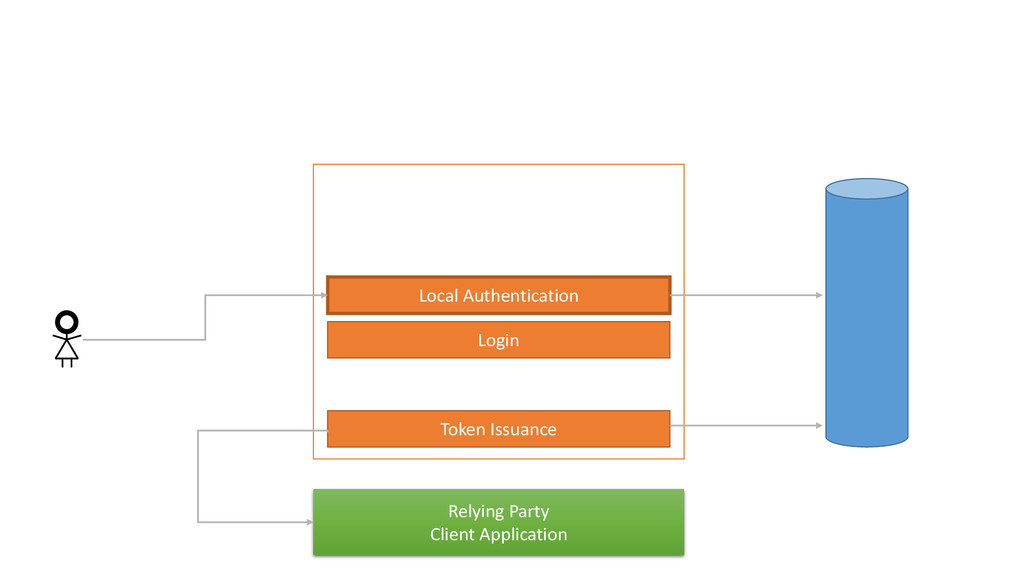
External Authentication Login Local Authentication Partner and Social IdPs -
Partner and Social IdPs Relying Party Client Application Token Issuance
External Authentication Login Local Authentication Account linking Partner and Social IdPs -
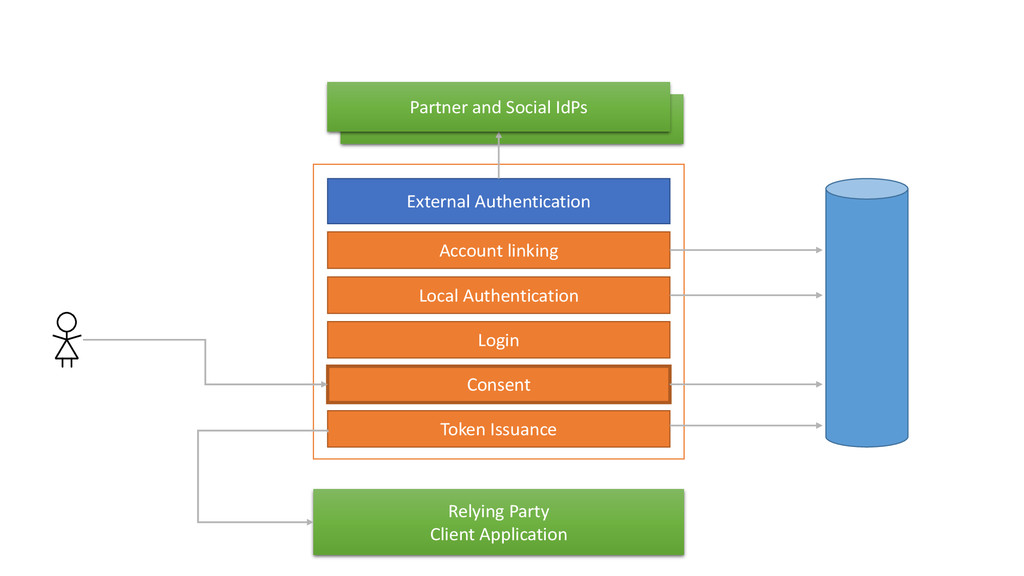
Partner and Social IdPs Relying Party Client Application Token Issuance
External Authentication Consent Login Local Authentication Account linking Partner and Social IdPs -
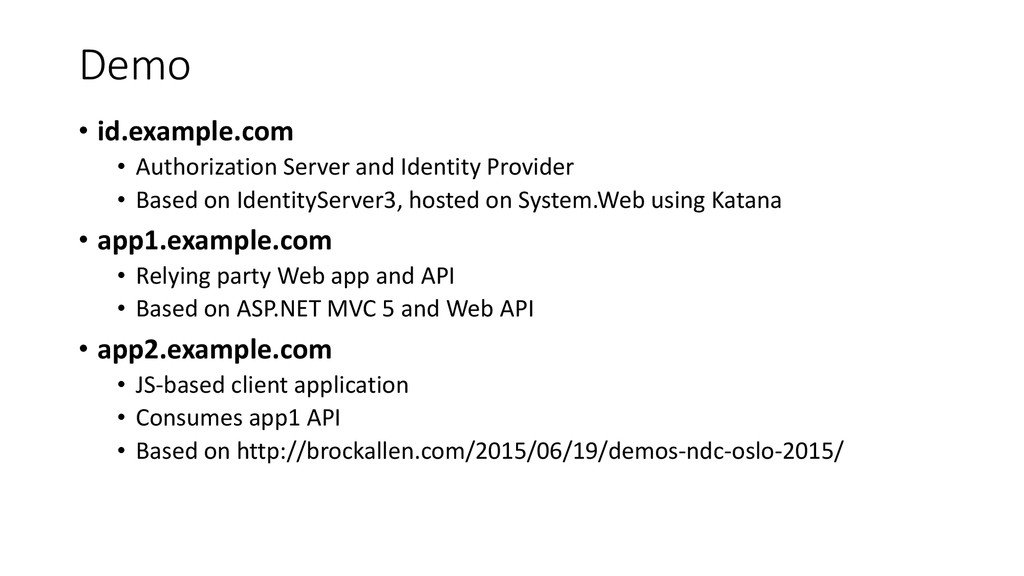
Demo • id.example.com • Authorization Server and Identity Provider •
Based on IdentityServer3, hosted on System.Web using Katana • app1.example.com • Relying party Web app and API • Based on ASP.NET MVC 5 and Web API • app2.example.com • JS-based client application • Consumes app1 API • Based on http://brockallen.com/2015/06/19/demos-ndc-oslo-2015/ -
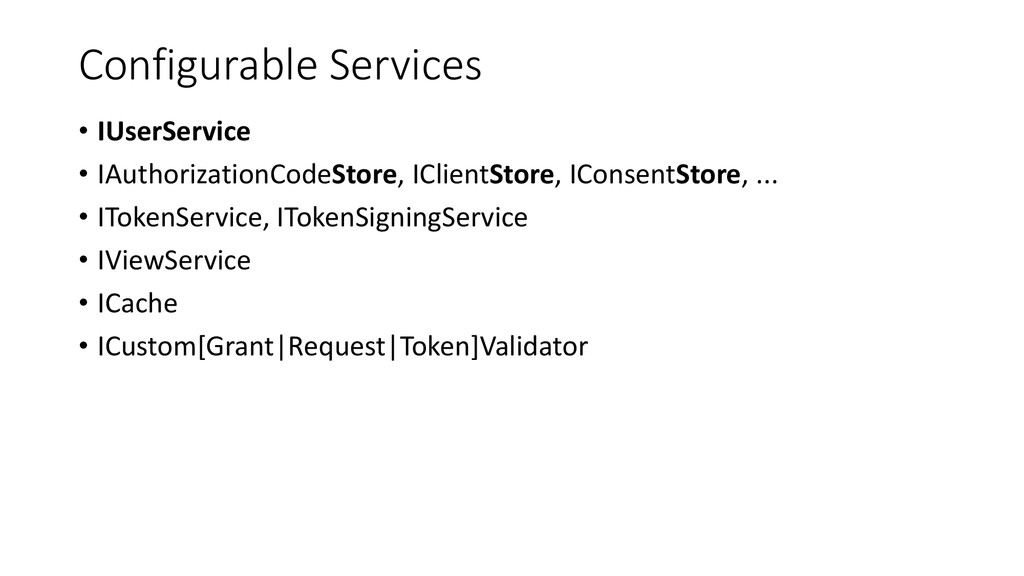
Configurable Services • IUserService • IAuthorizationCodeStore, IClientStore, IConsentStore, ... •
ITokenService, ITokenSigningService • IViewService • ICache • ICustom[Grant|Request|Token]Validator -
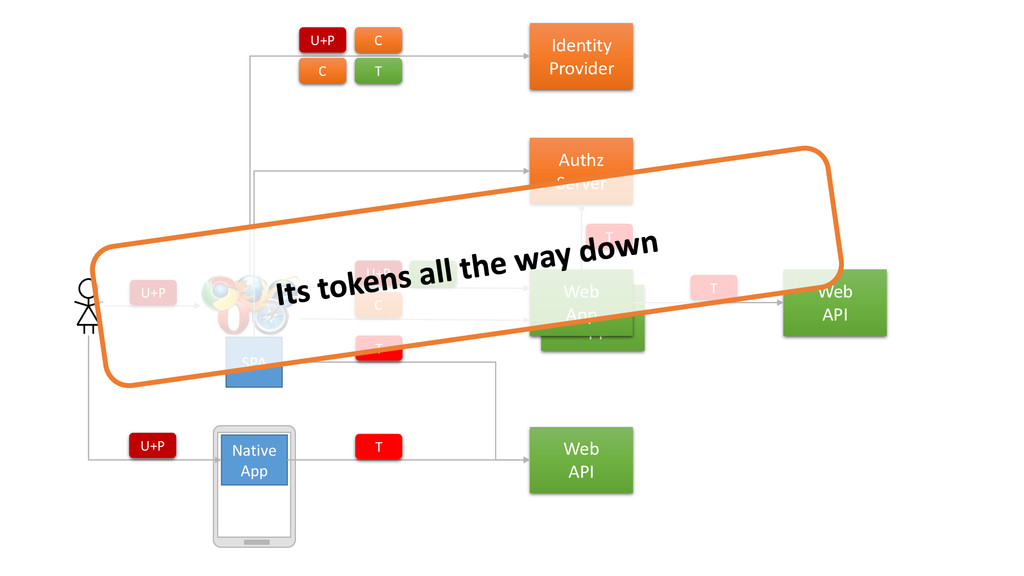
Final remarks • New authentication and access control challenges •
OpenID Connect unifies both authentication delegation, single sign-in and access delegation • JWT as a protected claims container • IdentityServer3 is a highly configurable framework for creating • Identity Providers • Authorization Servers