Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Introduction à Kubernetes
Search
Renaud Chaput
October 23, 2017
Technology
470
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Introduction à Kubernetes
Présenté à Sysadmin Days #7 :
https://sysadmindays.fr
Renaud Chaput
October 23, 2017
Transcript
40 slides
Introduction à Kubernetes
Renaud Chaput @renchap
Kubernetes
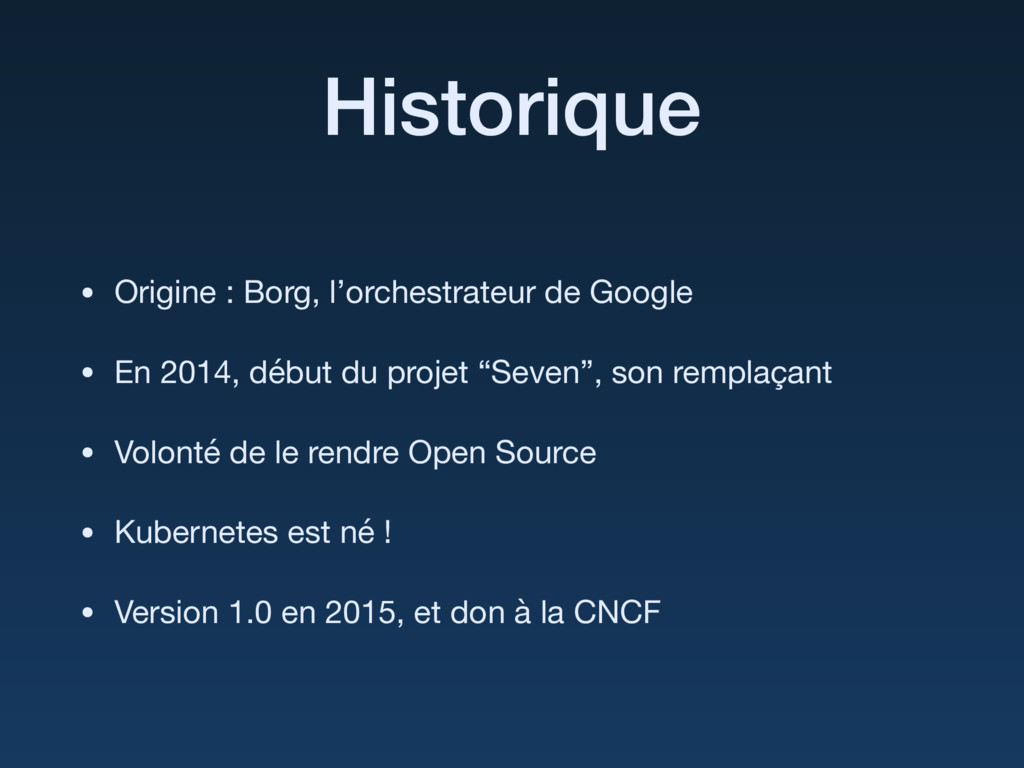
Historique • Origine : Borg, l’orchestrateur de Google • En
2014, début du projet “Seven”, son remplaçant • Volonté de le rendre Open Source • Kubernetes est né ! • Version 1.0 en 2015, et don à la CNCF
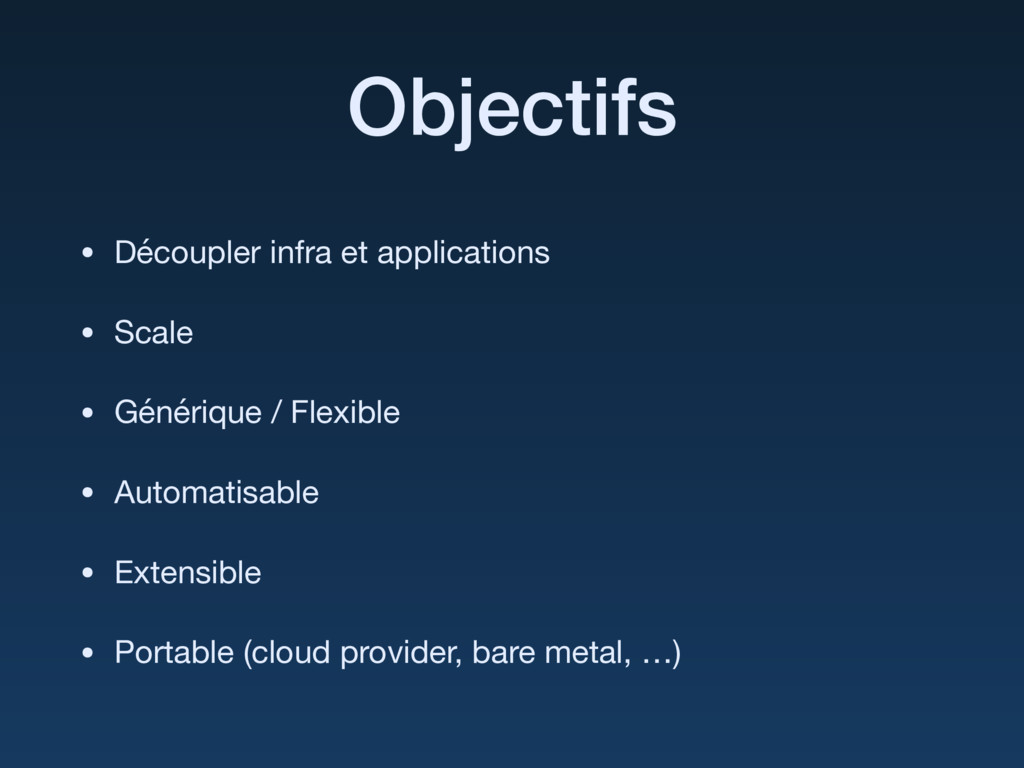
Objectifs • Découpler infra et applications • Scale • Générique
/ Flexible • Automatisable • Extensible • Portable (cloud provider, bare metal, …)
Un gros projet 1500 contributeurs 32 000 PR depuis 2014
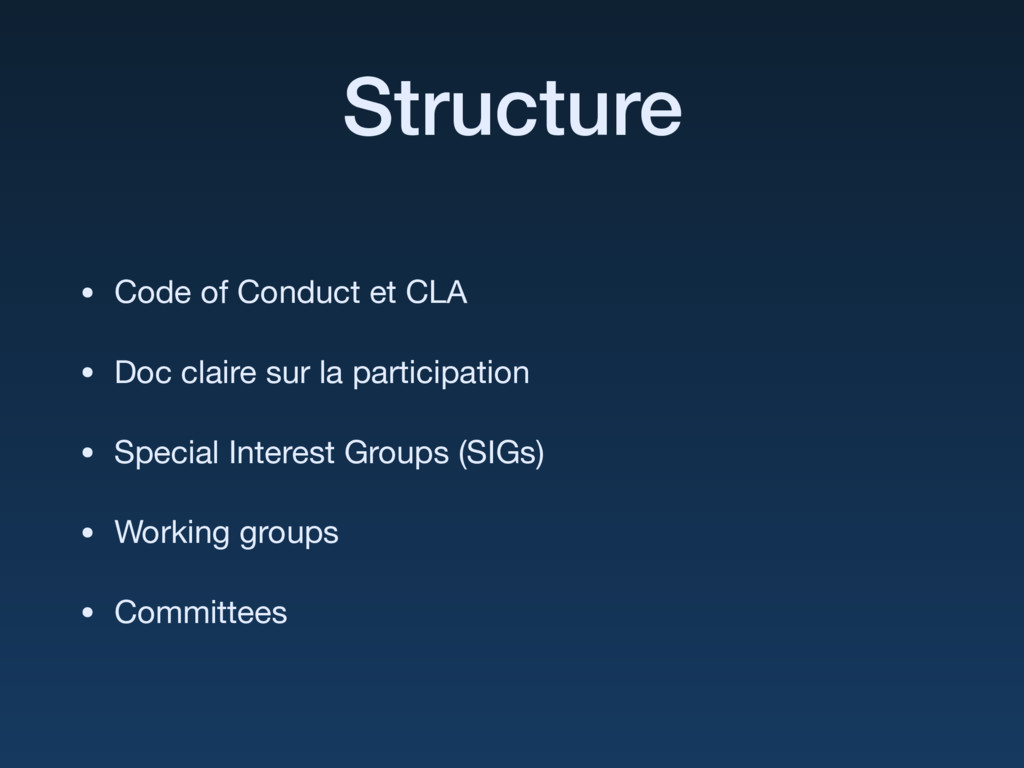
Structure • Code of Conduct et CLA • Doc claire
sur la participation • Special Interest Groups (SIGs) • Working groups • Committees
Releases
Releases
Features Alpha 1.5 Décembre 2016 Beta 1.7 Juin 2017 Stable
1.8 Septembre 2017 Alpha 1.6 Mars 2017
Fonctionnement
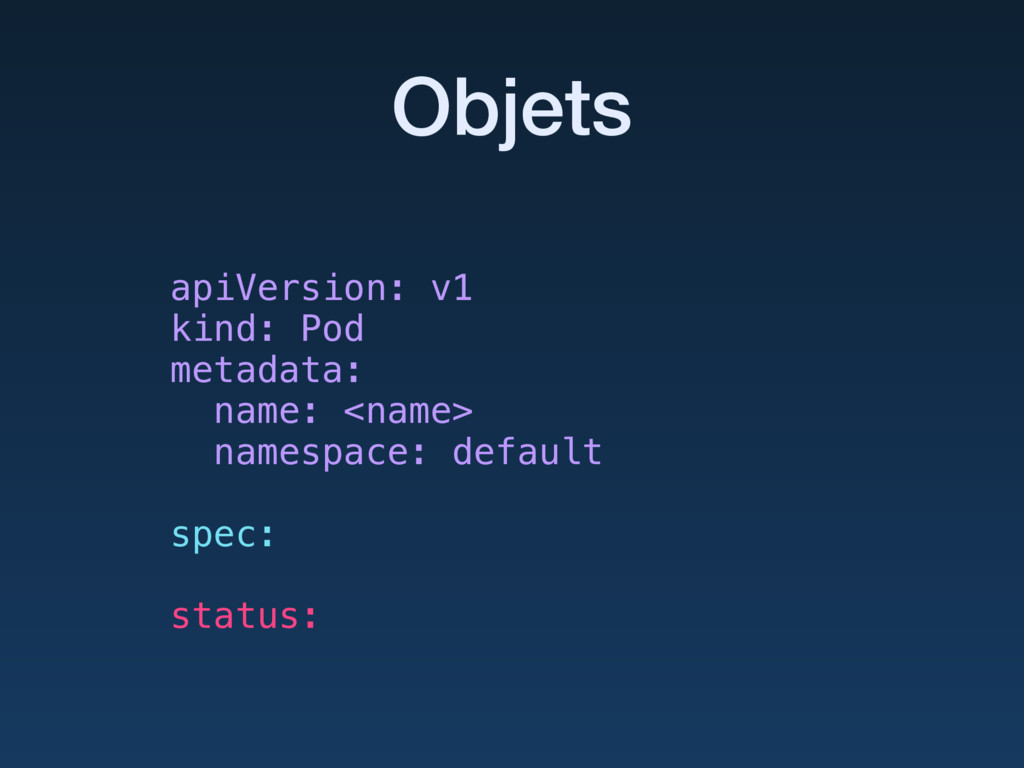
Objets apiVersion: v1 kind: Pod metadata: name: <name> namespace: default
spec: status:
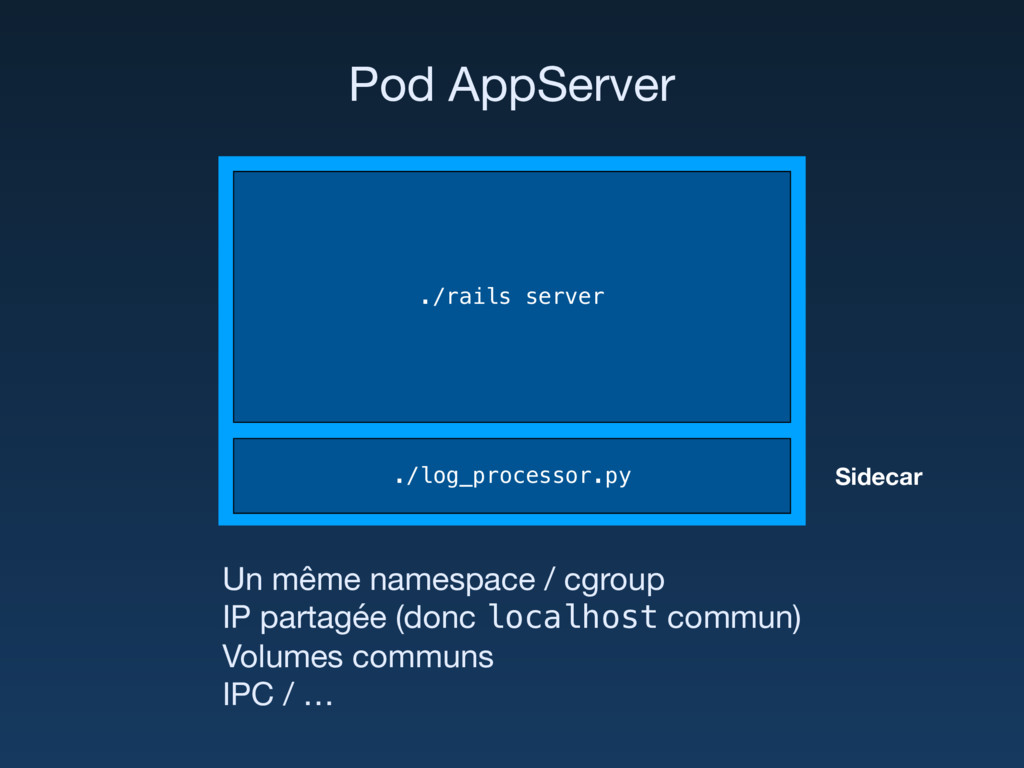
Un même namespace / cgroup IP partagée (donc localhost commun)
Volumes communs IPC / … ./rails server ./log_processor.py Pod AppServer Sidecar
apiVersion: v1 kind: Pod metadata: name: nginx spec: containers: -
name: nginx image: nginx:1.7.9 ports: - containerPort: 8080 Pod simple
Deployment apiVersion: apps/v1beta2 kind: Deployment metadata: name: nginx-deployment labels: app:
nginx spec: replicas: 3 selector: matchLabels: app: nginx template: metadata: labels: app: nginx spec: containers: - name: nginx image: nginx:1.7.9 ports: - containerPort: 8080
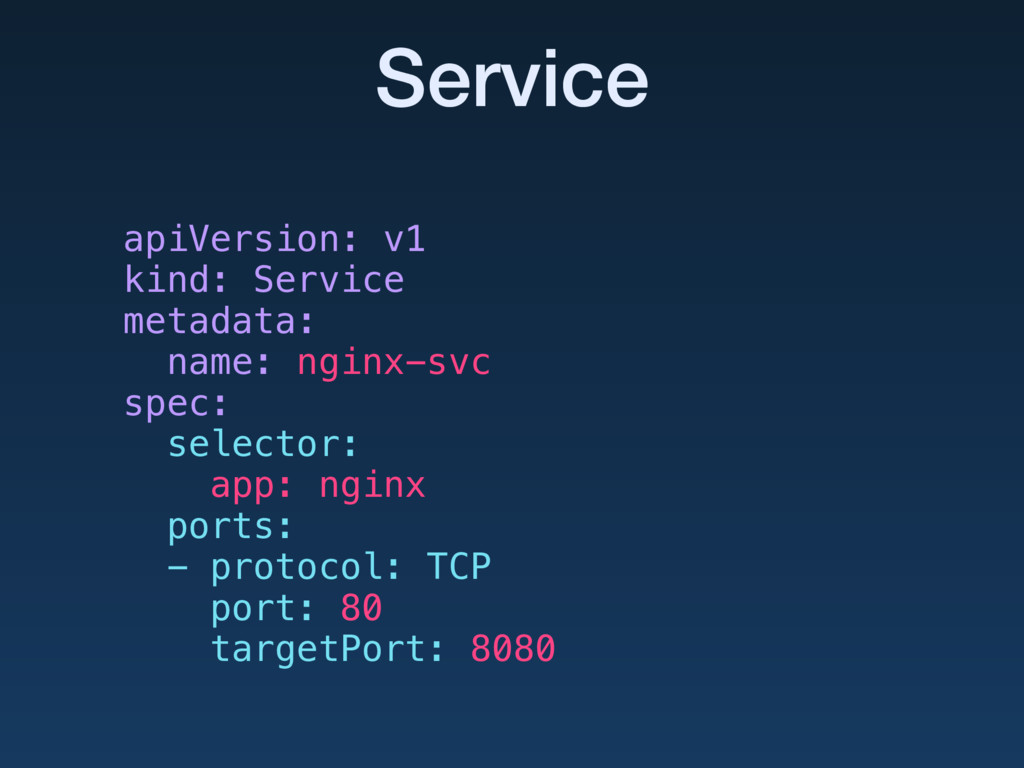
Service apiVersion: v1 kind: Service metadata: name: nginx-svc spec: selector:
app: nginx ports: - protocol: TCP port: 80 targetPort: 8080
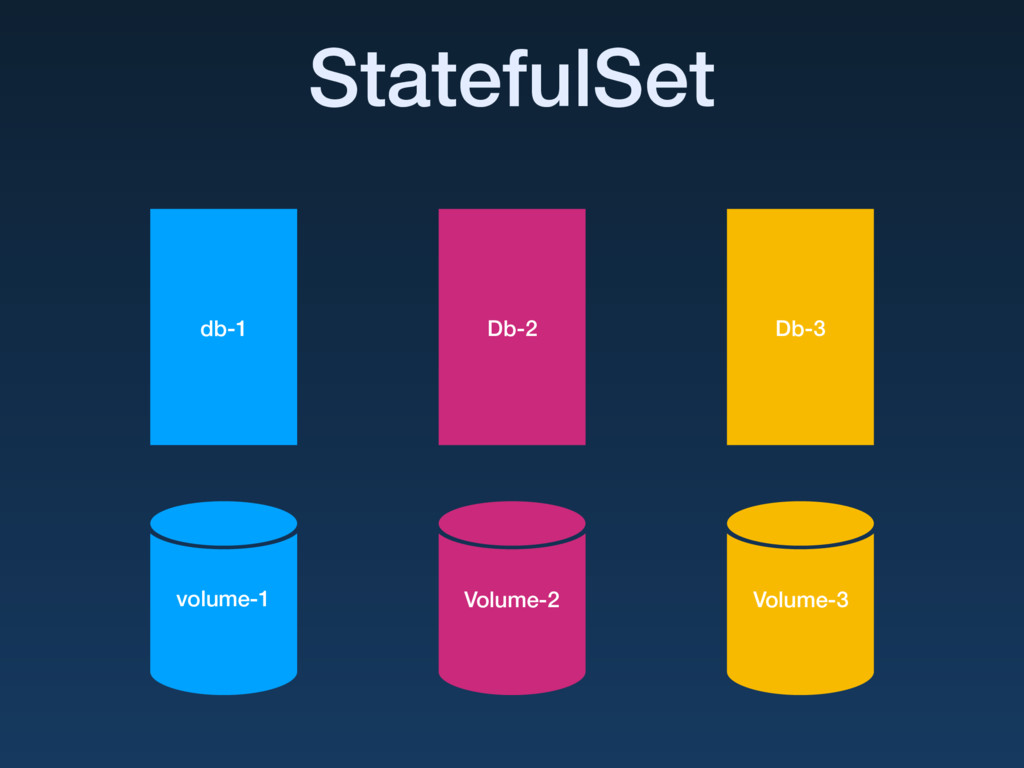
db-1 volume-1 StatefulSet Db-2 Volume-2 Db-3 Volume-3
DaemonSet Jobs CronJobs NetworkPolicy Secret Ingress Volume …
Architecture
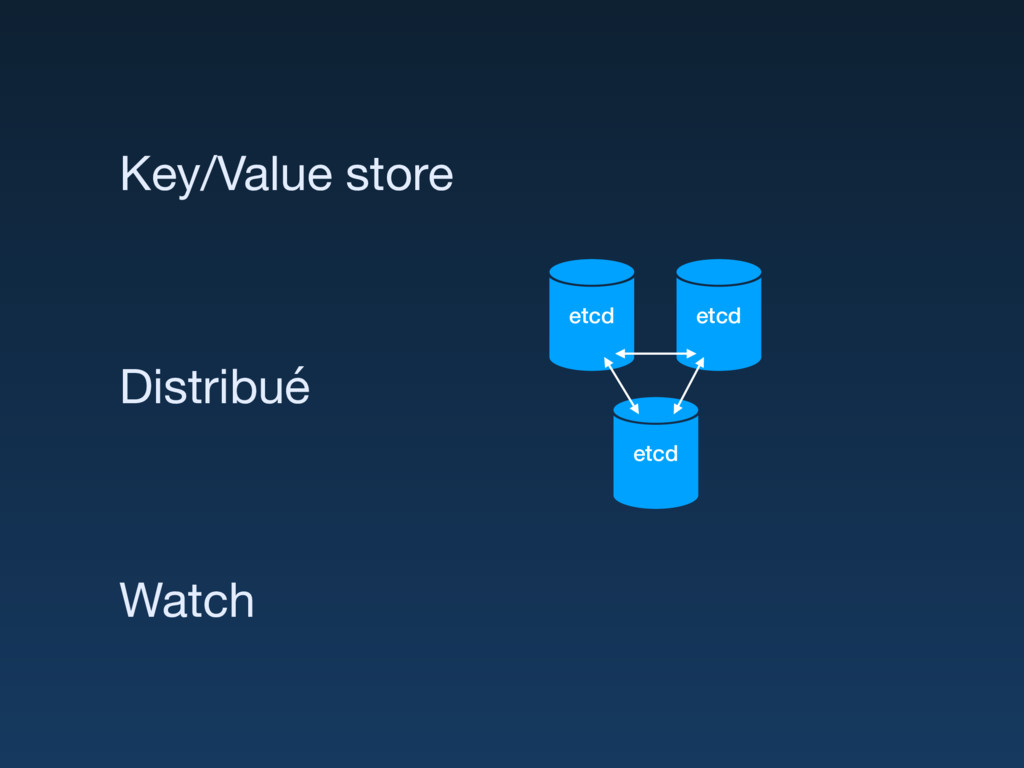
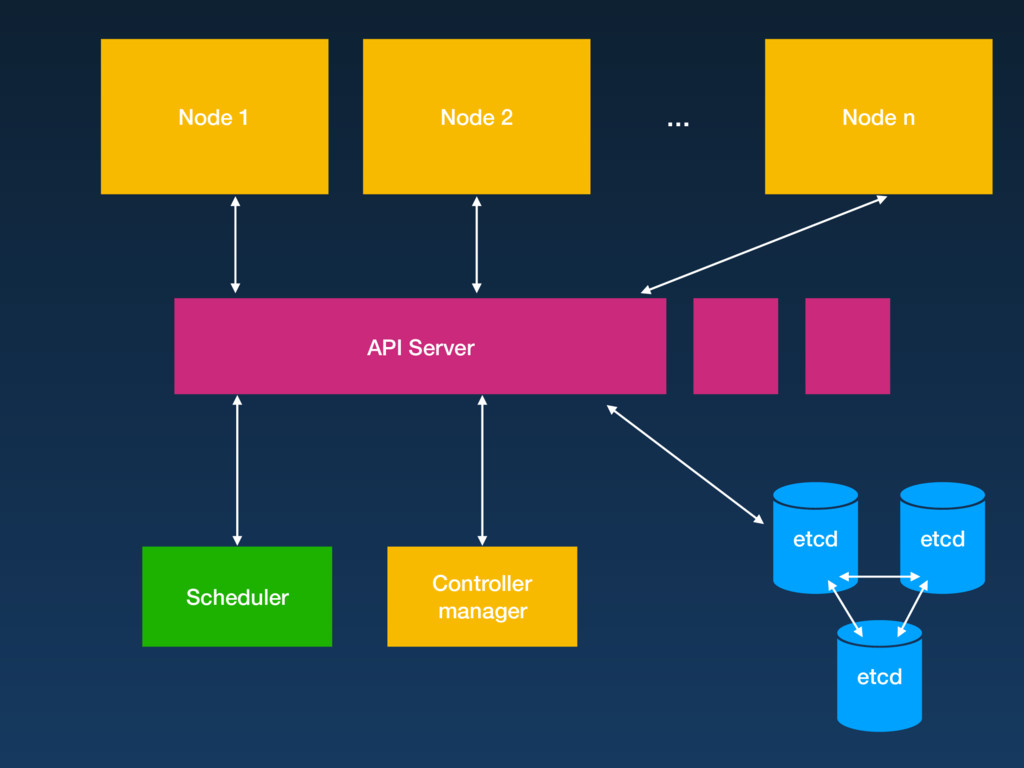
etcd etcd etcd Key/Value store Distribué Watch
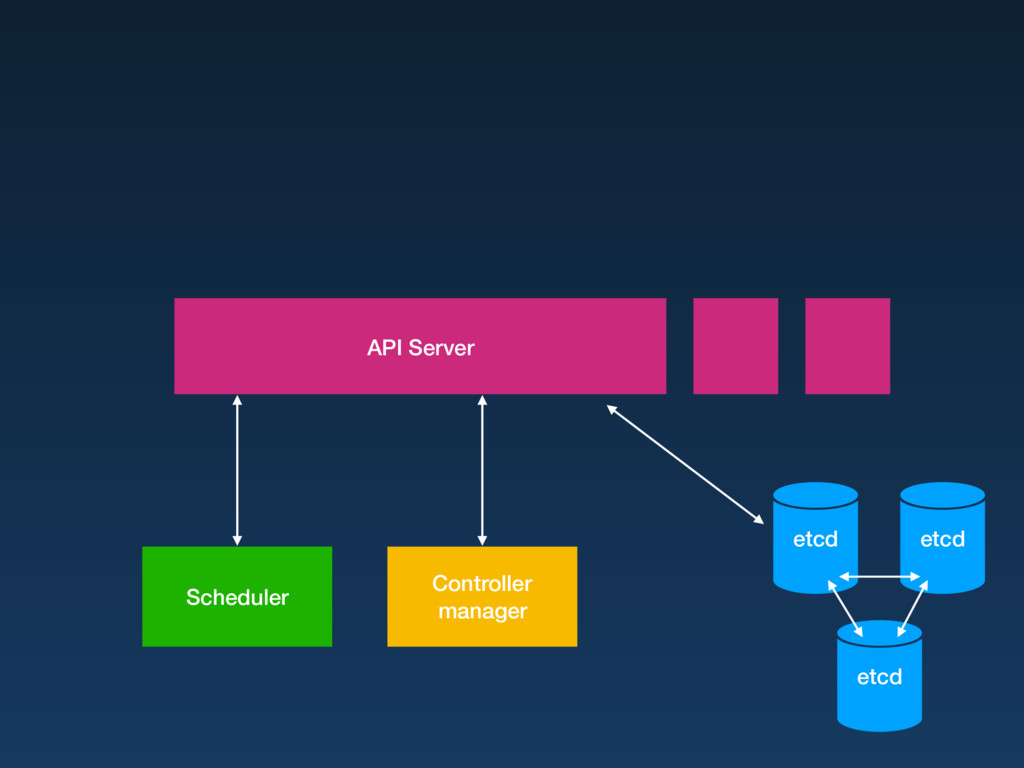
etcd etcd etcd API Server Scheduler Controller manager
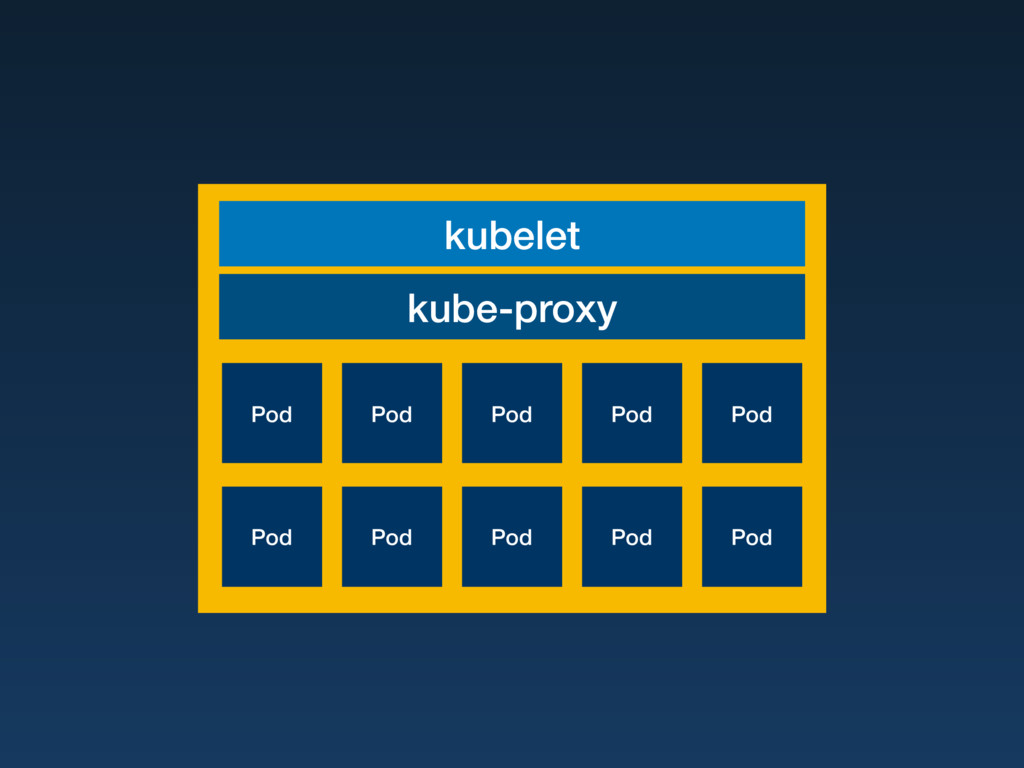
kubelet kube-proxy Pod Pod Pod Pod Pod Pod Pod Pod
Pod Pod
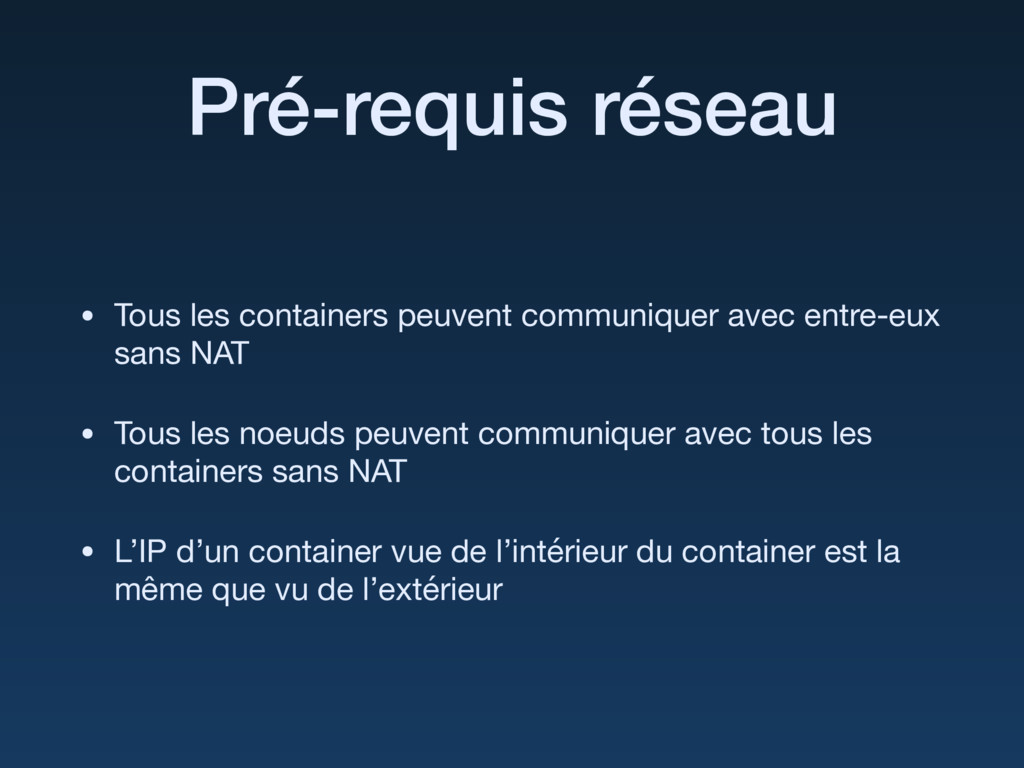
Pré-requis réseau • Tous les containers peuvent communiquer avec entre-eux
sans NAT • Tous les noeuds peuvent communiquer avec tous les containers sans NAT • L’IP d’un container vue de l’intérieur du container est la même que vu de l’extérieur
Container Runtime • Docker • CRI-O : interface OCI standard
• rkt (CoreOS) • Frakti : basé sur un hyperviseur
Node 1 Node 2 Node n etcd etcd etcd API
Server Scheduler Controller manager …
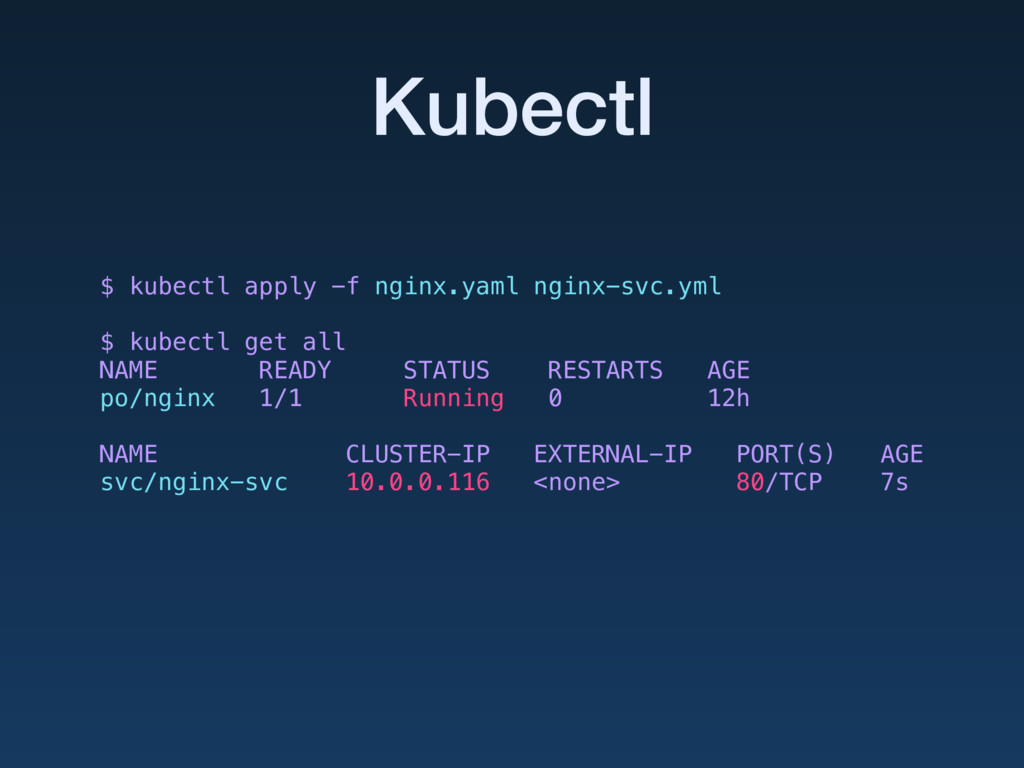
Kubectl $ kubectl apply -f nginx.yaml nginx-svc.yml $ kubectl get
all NAME READY STATUS RESTARTS AGE po/nginx 1/1 Running 0 12h NAME CLUSTER-IP EXTERNAL-IP PORT(S) AGE svc/nginx-svc 10.0.0.116 <none> 80/TCP 7s
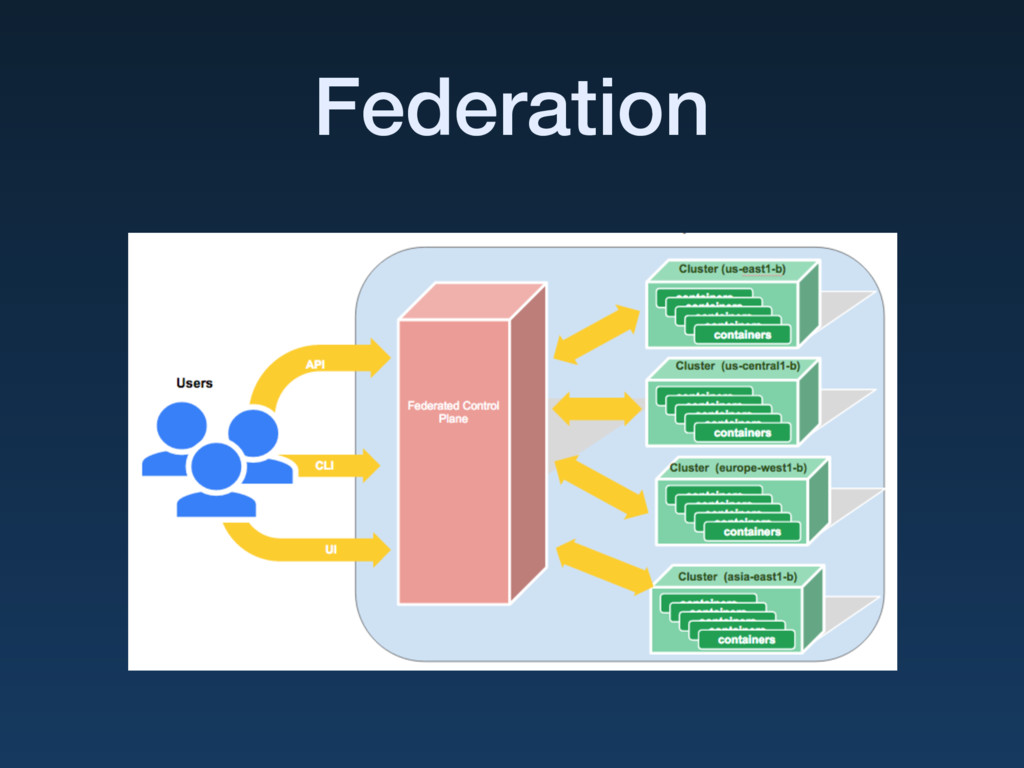
Federation
Add-ons
Kube DNS nginx-svc.my-namespace.svc.cluster.local _http._tcp.nginx-svc.my-namespace.svc.cluster.local 1-2-3-4.default.pod.cluster.local
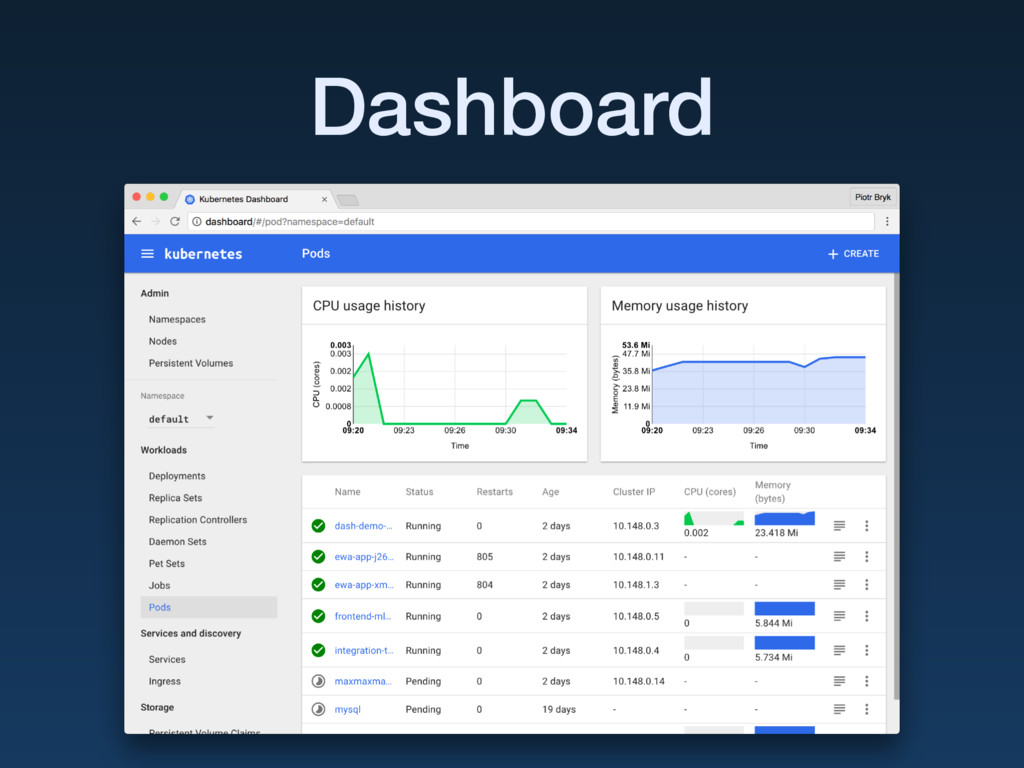
Dashboard
Ingress controllers • GCP / AWS / … • nginx
• haproxy
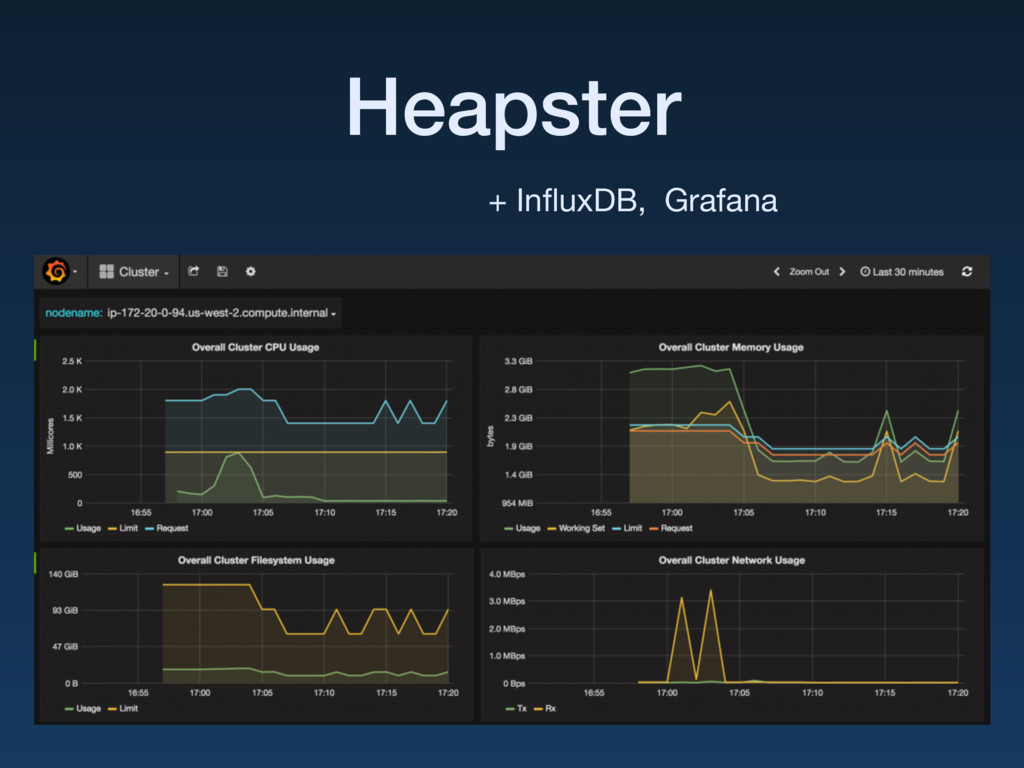
Heapster + InfluxDB, Grafana
Sécurité
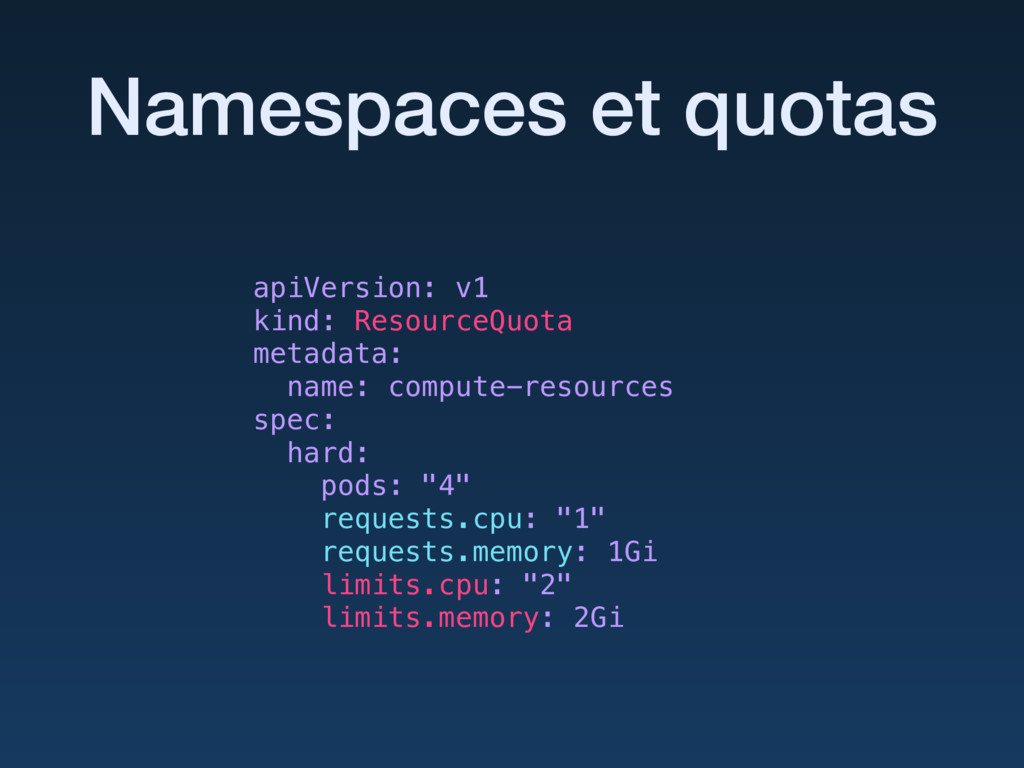
Namespaces et quotas apiVersion: v1 kind: ResourceQuota metadata: name: compute-resources
spec: hard: pods: "4" requests.cpu: "1" requests.memory: 1Gi limits.cpu: "2" limits.memory: 2Gi
PodSecurityPolicy apiVersion: extensions/v1beta1 kind: PodSecurityPolicy metadata: name: permissive spec: seLinux:
rule: RunAsAny supplementalGroups: rule: RunAsAny runAsUser: rule: RunAsAny fsGroup: rule: RunAsAny hostPorts: - min: 8000 max: 8080 volumes: - '*' allowedCapabilities: - '*'
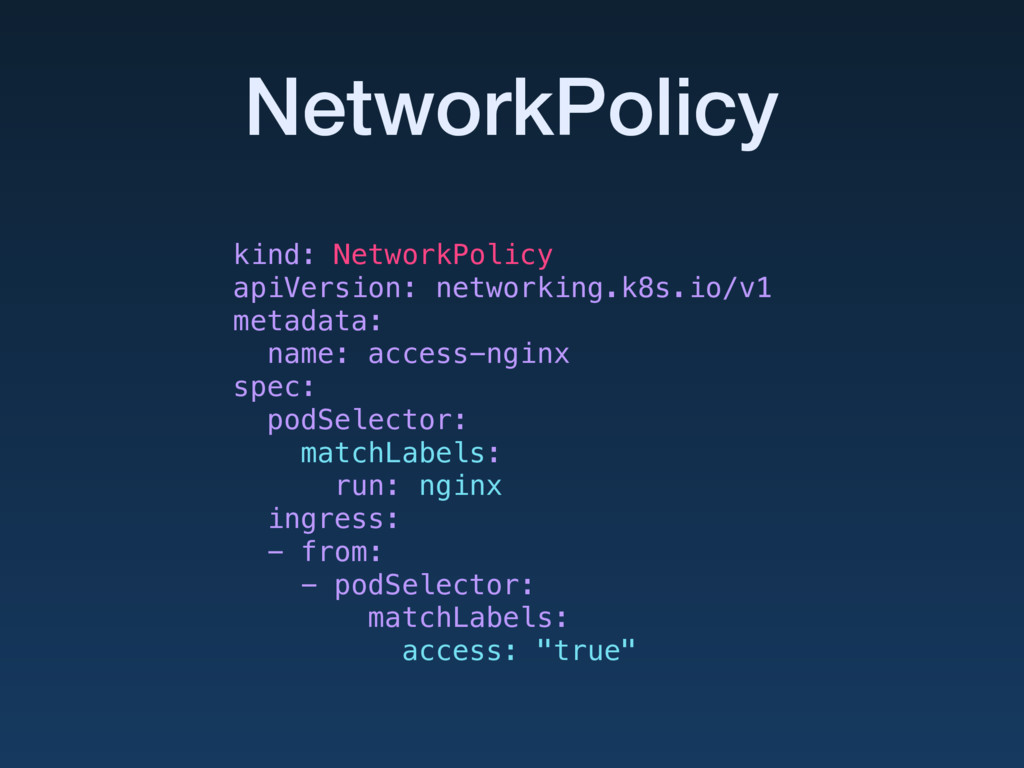
NetworkPolicy kind: NetworkPolicy apiVersion: networking.k8s.io/v1 metadata: name: access-nginx spec: podSelector:
matchLabels: run: nginx ingress: - from: - podSelector: matchLabels: access: "true"
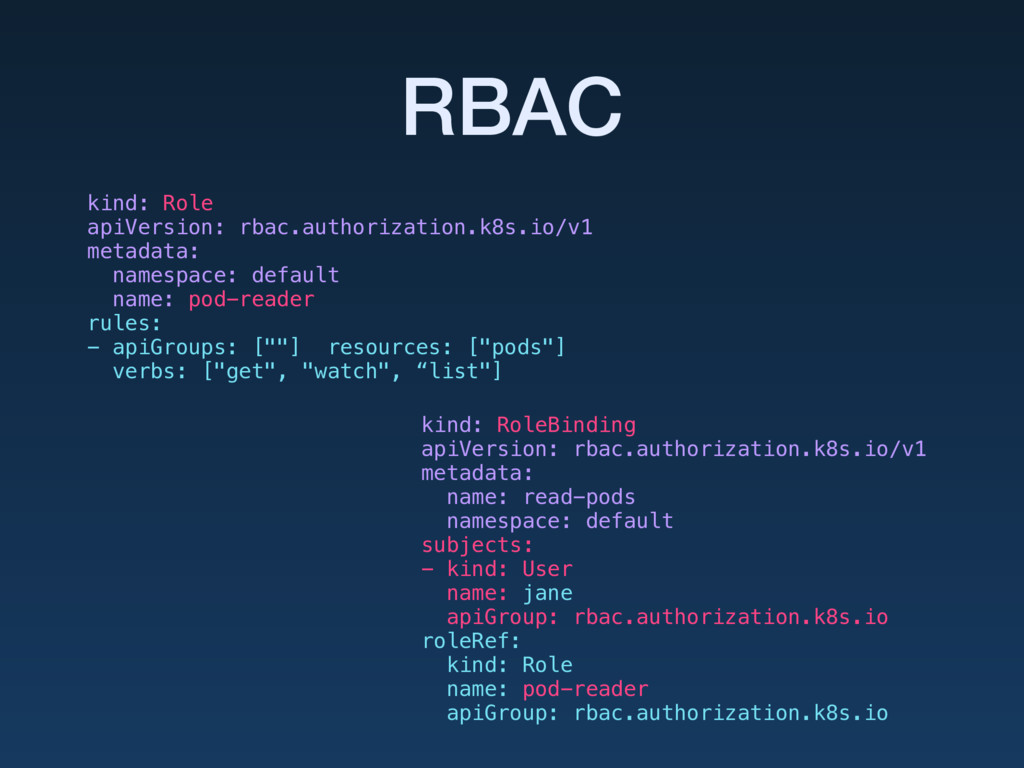
RBAC kind: Role apiVersion: rbac.authorization.k8s.io/v1 metadata: namespace: default name: pod-reader
rules: - apiGroups: [""] resources: ["pods"] verbs: ["get", "watch", “list"] kind: RoleBinding apiVersion: rbac.authorization.k8s.io/v1 metadata: name: read-pods namespace: default subjects: - kind: User name: jane apiGroup: rbac.authorization.k8s.io roleRef: kind: Role name: pod-reader apiGroup: rbac.authorization.k8s.io
Projets autour • Helm • Kops / Kube-AWS / Bootkube
/ … • Træfik • Prometheus / Sysdig / Datadog / … • Kube-lego, …
Ressources • Minikube! • kubernetes.io • Kubernetes the hard way
• Slack Kubernetes • Awesome Kubernetes
Questions ?
More Decks by Renaud Chaput
See All by Renaud Chaput
L'Infrastructure as Code au complet (par Benoit Petit)
renchap
1
740
Autour des requêtes des TSDB
renchap
2
750
Operate HBase clusters at Scale
renchap
1
480
Versions (par Olivier Delhomme)
renchap
1
510
Prevent business logic attacks using dynamic instrumentation
renchap
1
500
Atelier Paris Web : Introduction à Docker
renchap
0
130
Alkemics CI & CD with Jenkins and Docker
renchap
1
350
Les containers : décryptage
renchap
2
350
Kubernetes en production : un an après
renchap
1
380
Other Decks in Technology
See All in Technology
AI時代における医療情報システムのセキュリティ / Security of Healthcare IT Systems in the AI Era
henryofficial
0
190
人の努力に頼らないセキュリティをエンジニアリングする在り方 / An approach to engineering security that does not rely on human effort
carta_engineering
0
220
共通基盤の実装に Kotlin - Quarkus を選定した理由と採用したアーキテクチャ
nealle
1
130
属人化したISMS運用をGitHubとAIで仕組み化した1年間の記録
sioncojp
4
2.8k
会社説明資料_最新版
demaecan
0
32k
IP重複は"ランディングVPC"で受け止める ― PrivateLink と Transit Gatewayによるマルチテナント接続基盤の設計
hatahata021
3
250
パスワードのない鍵で、 データを手元に置く
ginjihayashi
0
350
【Oracle AI SPOTLIGHT ウェビナー】【特別開催:日本語で解説!】Oracle AI World 2026 最新情報フィードバック
oracle4engineer
PRO
1
280
Claude Codeで新規事業を伸ばせるか? Zennの試行錯誤の記録
wadayusuke
2
240
SSFの現在地 ― CAEP/RISCからAI Identityへ
oidfj
0
480
re:Inventを楽しむために、 1日1つ「これが楽しみ」を決めよう
beli68
0
120
IoTのデータ保存をSREの観点で考える
grimoh
1
110
Featured
See All Featured
The Web Performance Landscape in 2024 [PerfNow 2024]
tammyeverts
12
1.4k
Building Experiences: Design Systems, User Experience, and Full Site Editing
marktimemedia
1
670
Stop Working from a Prison Cell
hatefulcrawdad
274
21k
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
770
Introduction to Domain-Driven Design and Collaborative software design
baasie
1
1.1k
Deep Space Network (abreviated)
tonyrice
0
420
Docker and Python
trallard
47
4.3k
Evolution of real-time – Irina Nazarova, EuRuKo, 2024
irinanazarova
9
1.7k
How to make the Groovebox
asonas
2
2.6k
CoffeeScript is Beautiful & I Never Want to Write Plain JavaScript Again
sstephenson
162
16k
ラッコキーワード サービス紹介資料
rakko
5
5.9M
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k


 renchap
 henryofficial
 carta_engineering
 nealle
 sioncojp
 demaecan
 hatahata021
 ginjihayashi
 oracle4engineer
 wadayusuke
 oidfj
 beli68
 grimoh
 tammyeverts
 marktimemedia
 hatefulcrawdad
 baasie
 tonyrice
 trallard
 irinanazarova
 asonas
 sstephenson
 rakko
 cassininazir