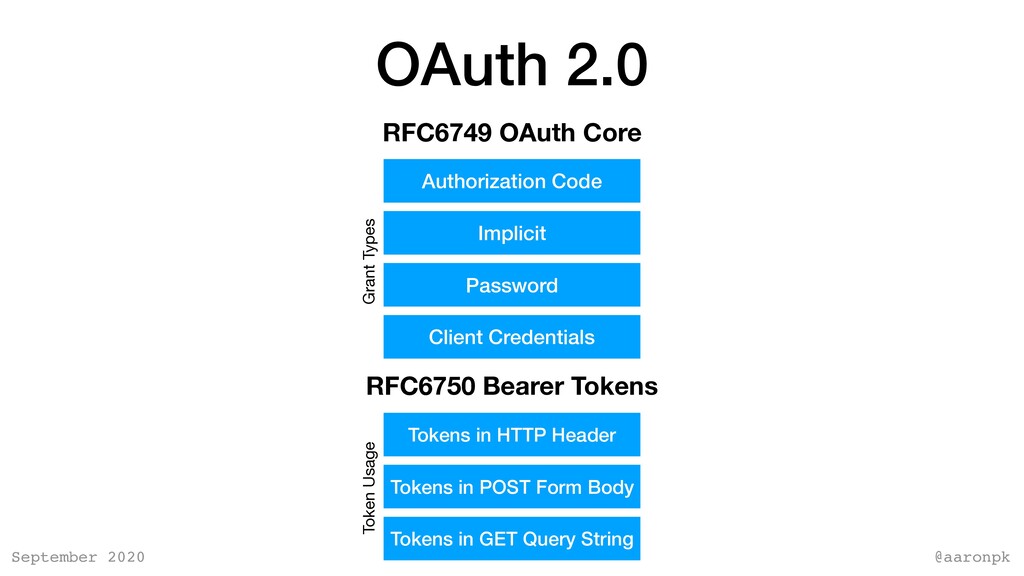
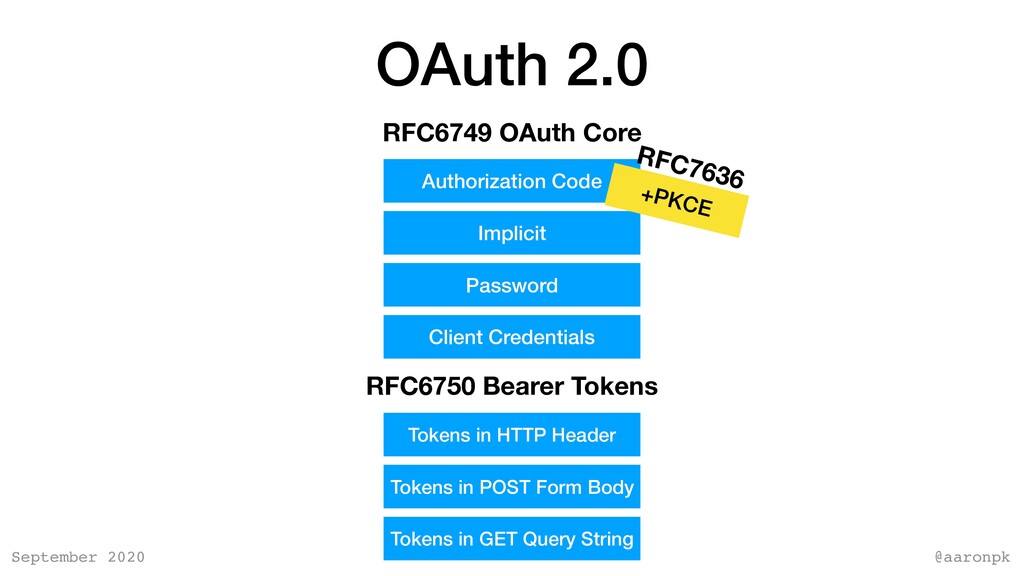
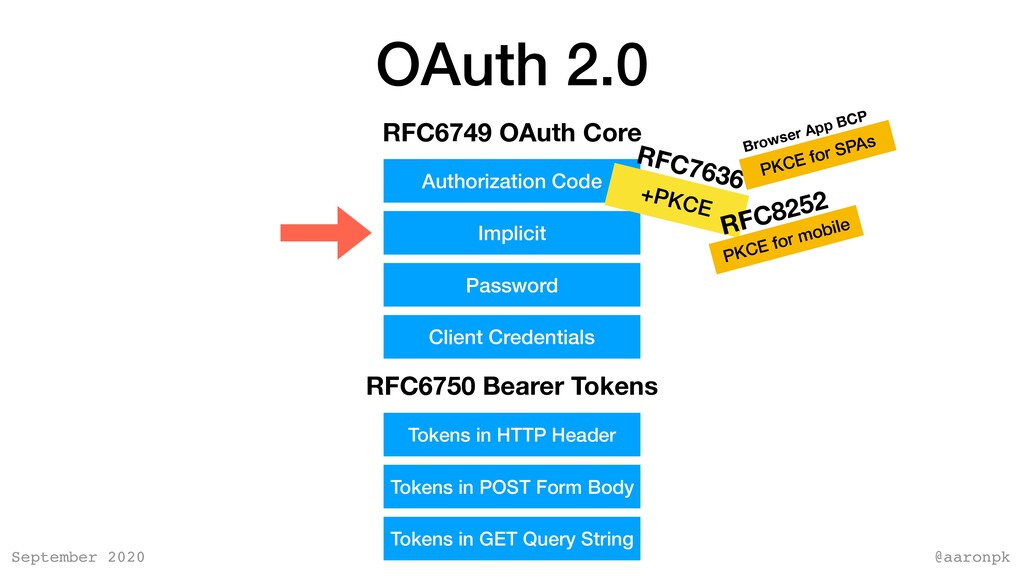
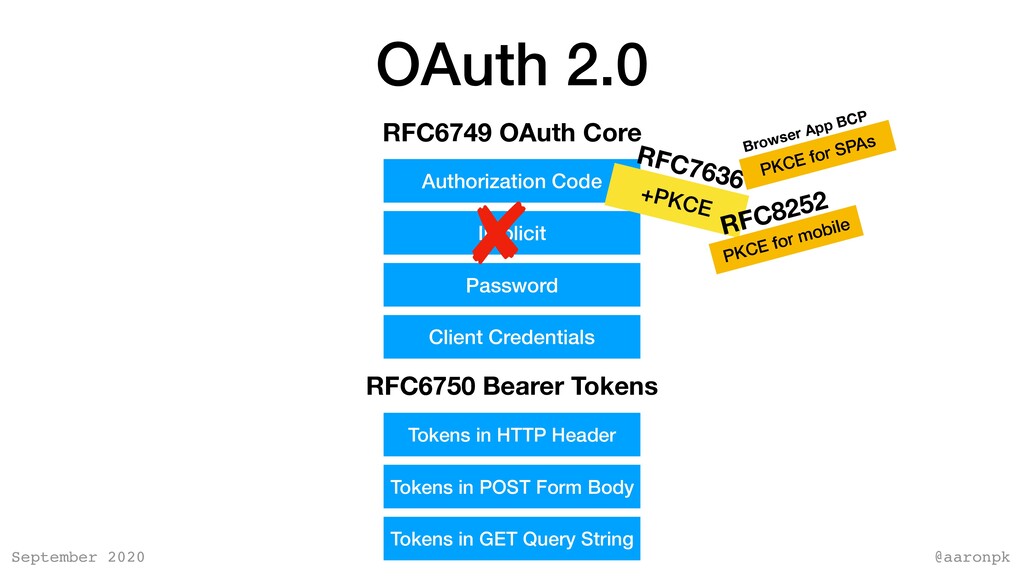
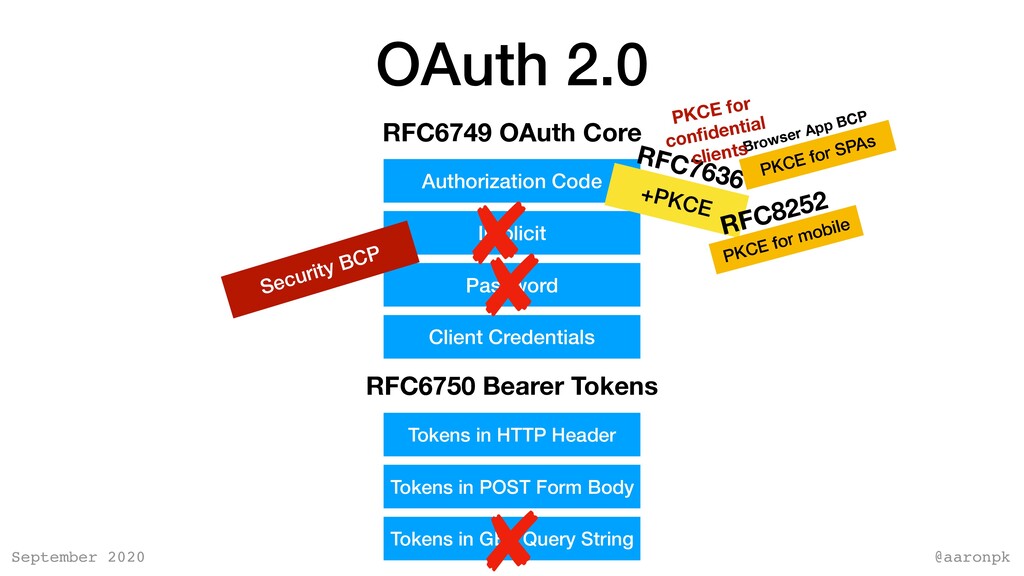
Implicit Password Client Credentials Grant Types RFC6750 Bearer Tokens Token Usage Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
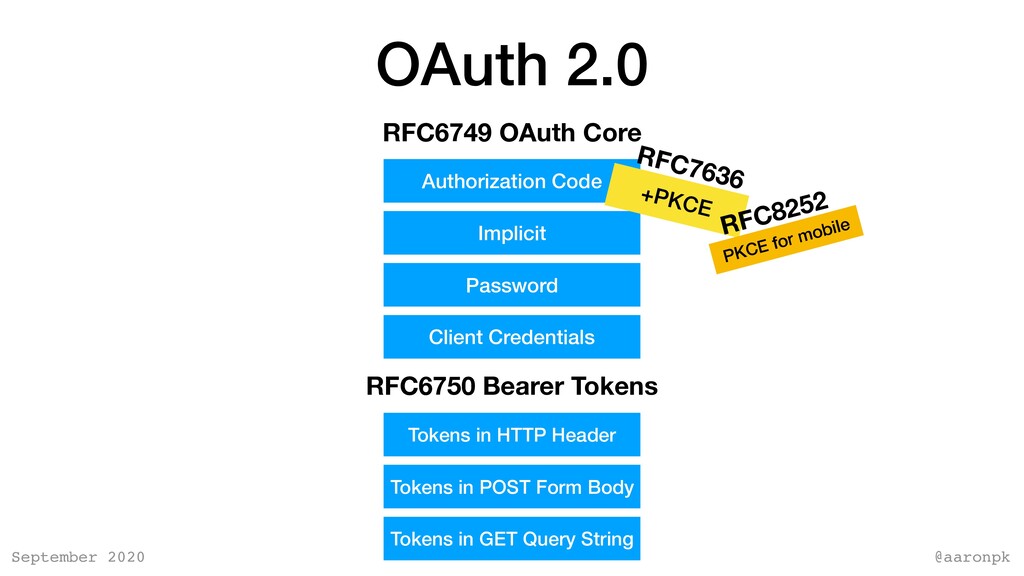
Implicit Password Client Credentials RFC6750 Bearer Tokens RFC7636 +PKCE RFC8252 PKCE for mobile Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
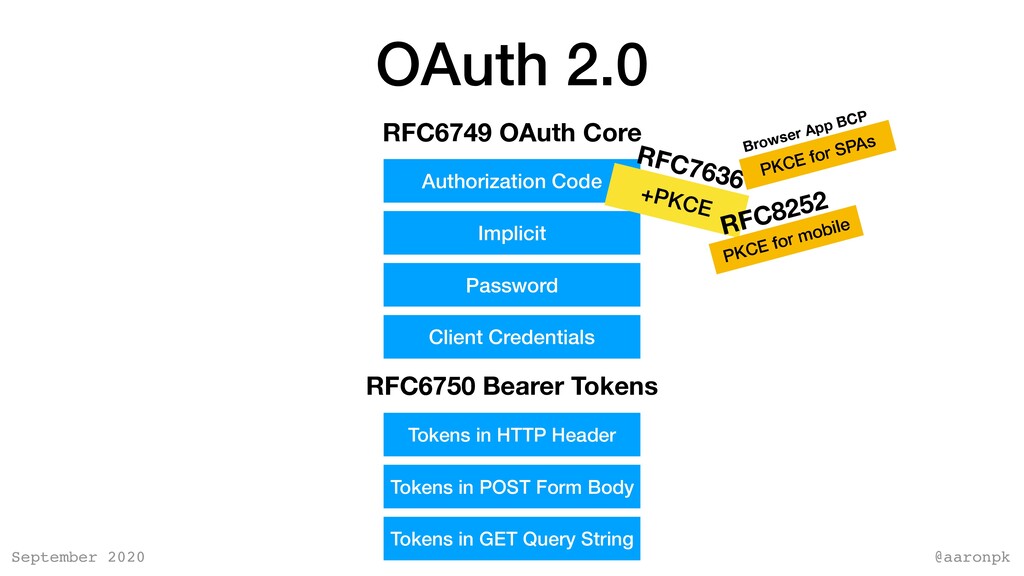
Implicit Password Client Credentials RFC6750 Bearer Tokens RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
Implicit Password Client Credentials RFC6750 Bearer Tokens RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
Implicit Password Client Credentials RFC6750 Bearer Tokens RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
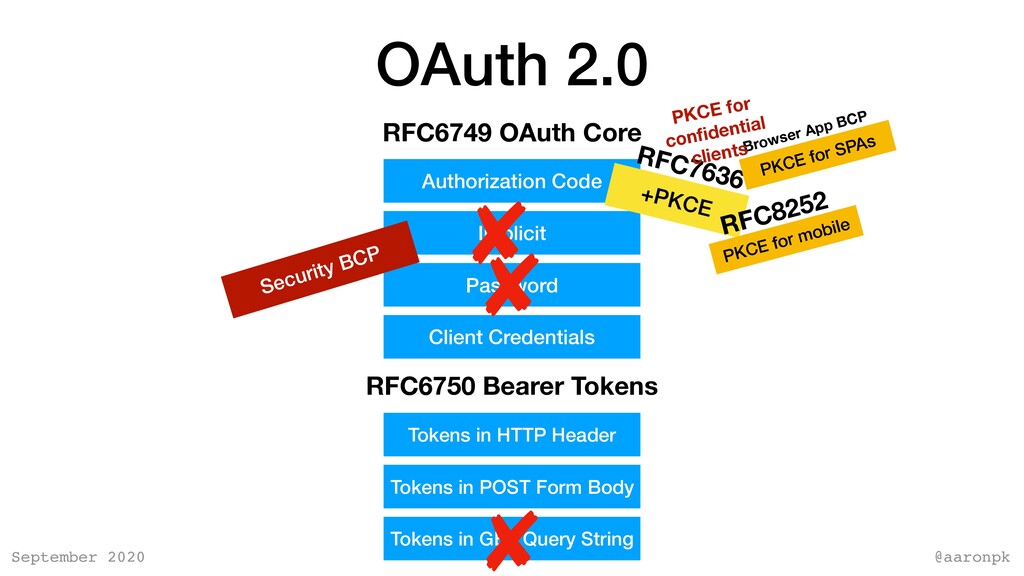
Implicit Password Client Credentials RFC6750 Bearer Tokens Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs PKCE for confidential clients Security BCP
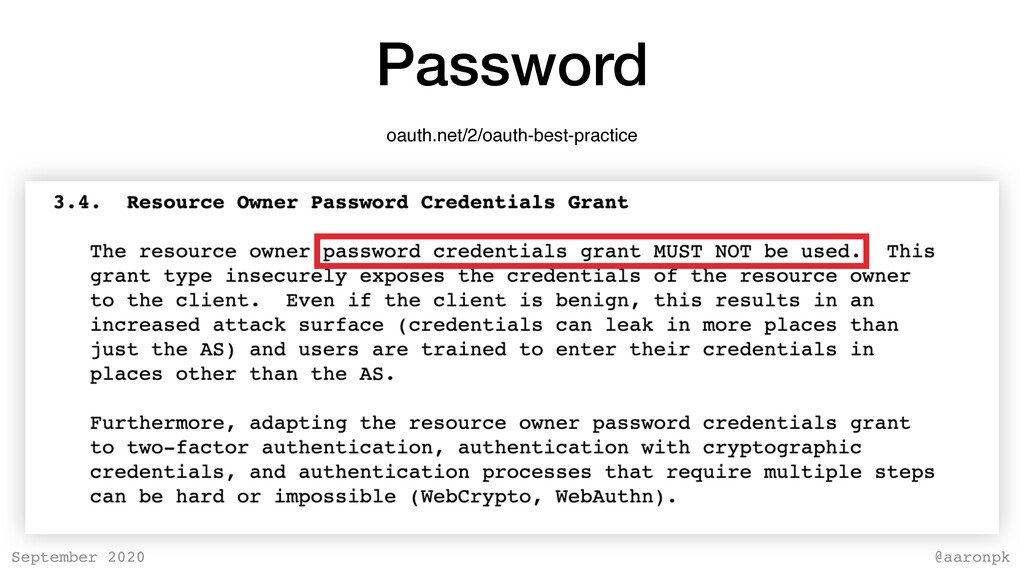
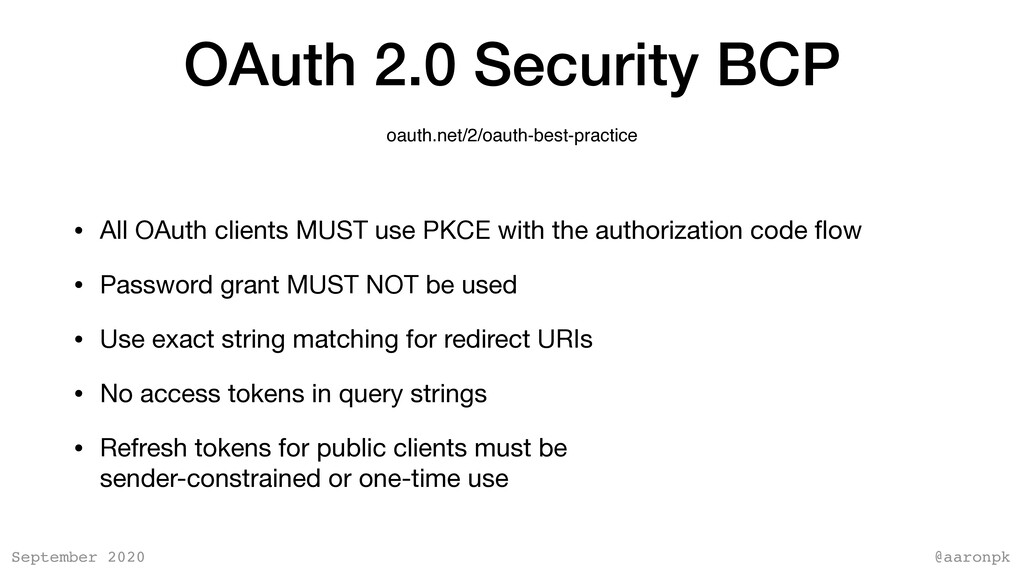
clients MUST use PKCE with the authorization code flow • Password grant MUST NOT be used • Use exact string matching for redirect URIs • No access tokens in query strings • Refresh tokens for public clients must be sender-constrained or one-time use oauth.net/2/oauth-best-practice
Implicit Password Client Credentials RFC6750 Bearer Tokens Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs PKCE for confidential clients Security BCP
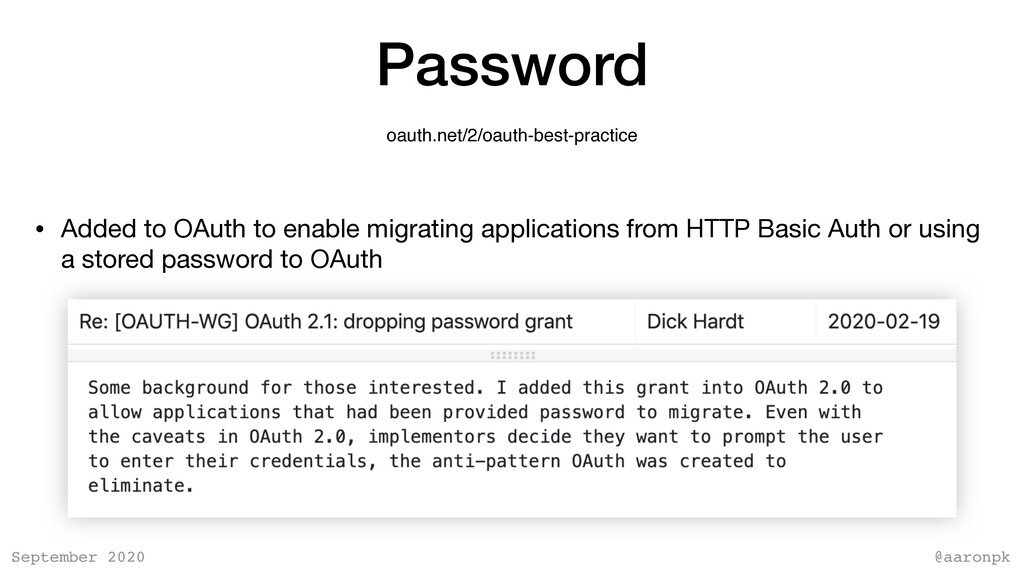
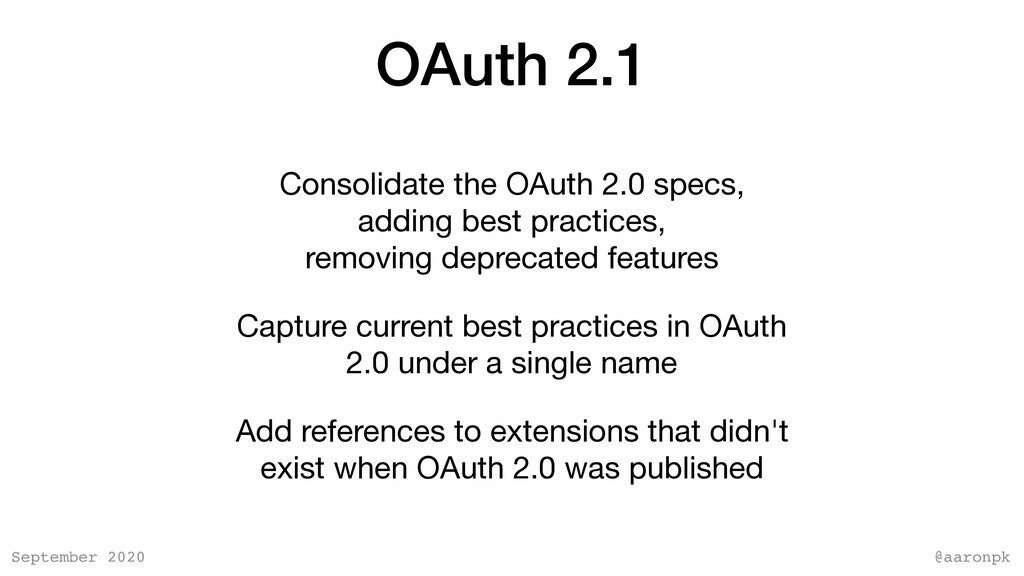
adding best practices, removing deprecated features Capture current best practices in OAuth 2.0 under a single name Add references to extensions that didn't exist when OAuth 2.0 was published
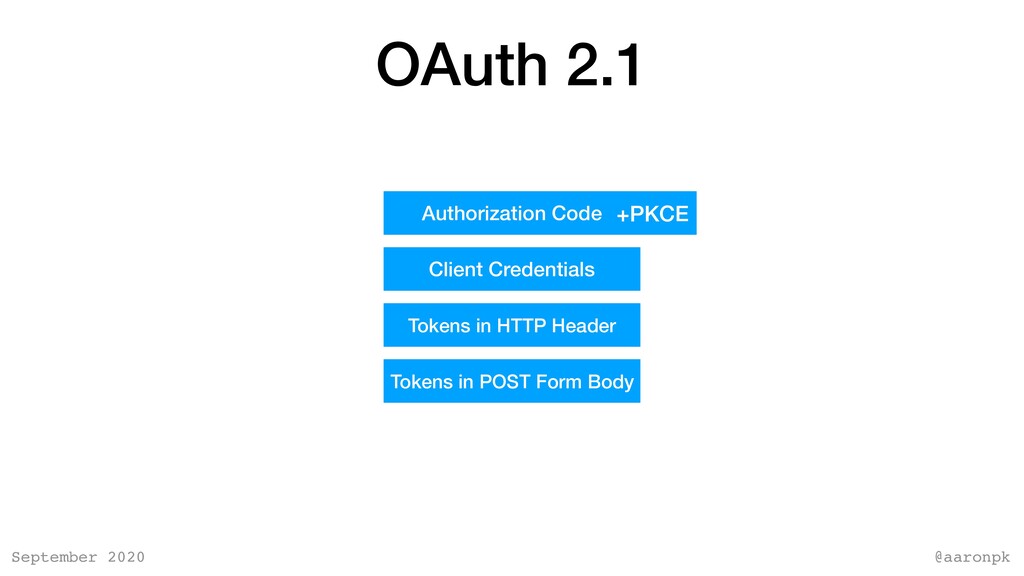
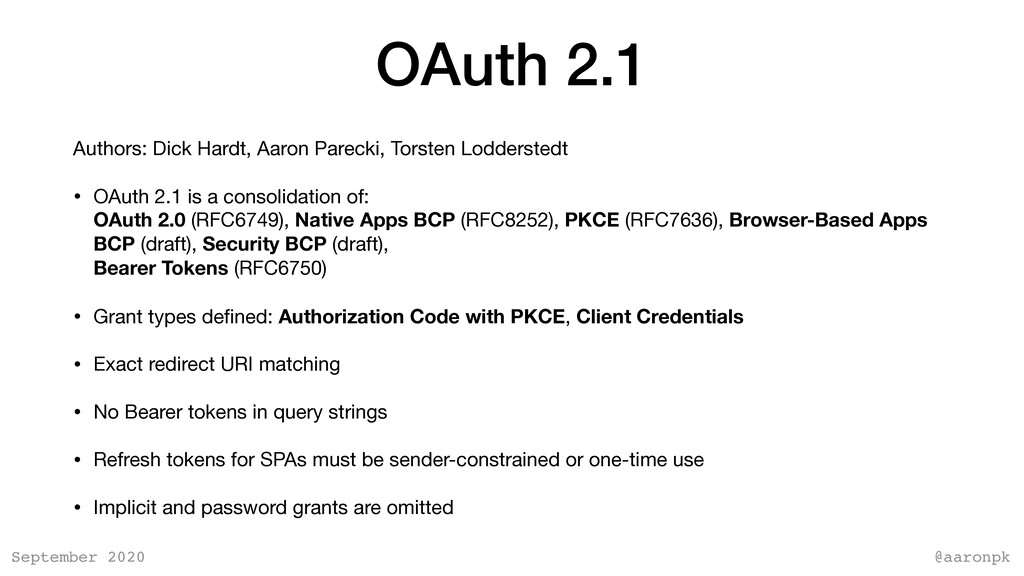
Torsten Lodderstedt • OAuth 2.1 is a consolidation of: OAuth 2.0 (RFC6749), Native Apps BCP (RFC8252), PKCE (RFC7636), Browser-Based Apps BCP (draft), Security BCP (draft), Bearer Tokens (RFC6750) • Grant types defined: Authorization Code with PKCE, Client Credentials • Exact redirect URI matching • No Bearer tokens in query strings • Refresh tokens for SPAs must be sender-constrained or one-time use • Implicit and password grants are omitted
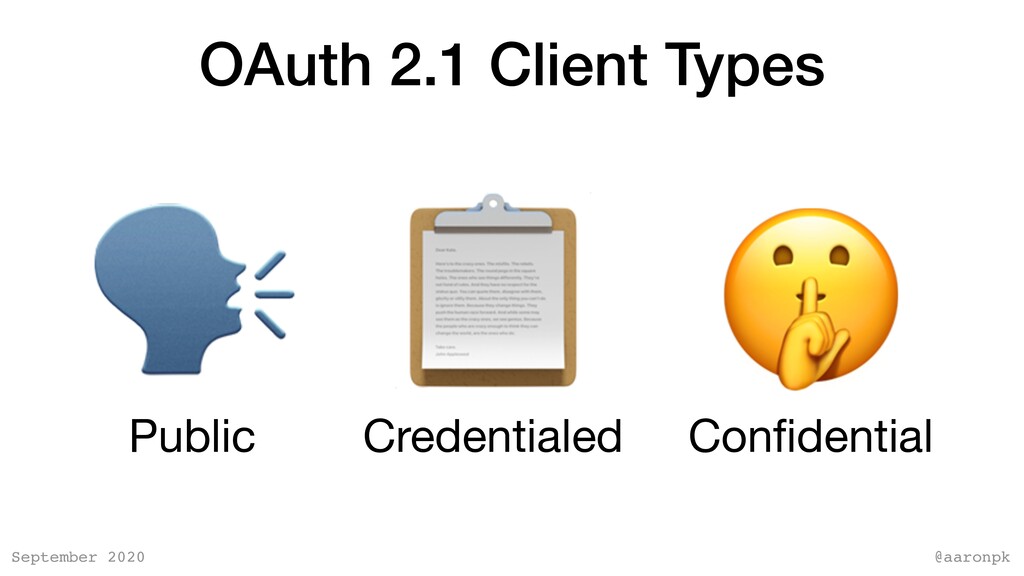
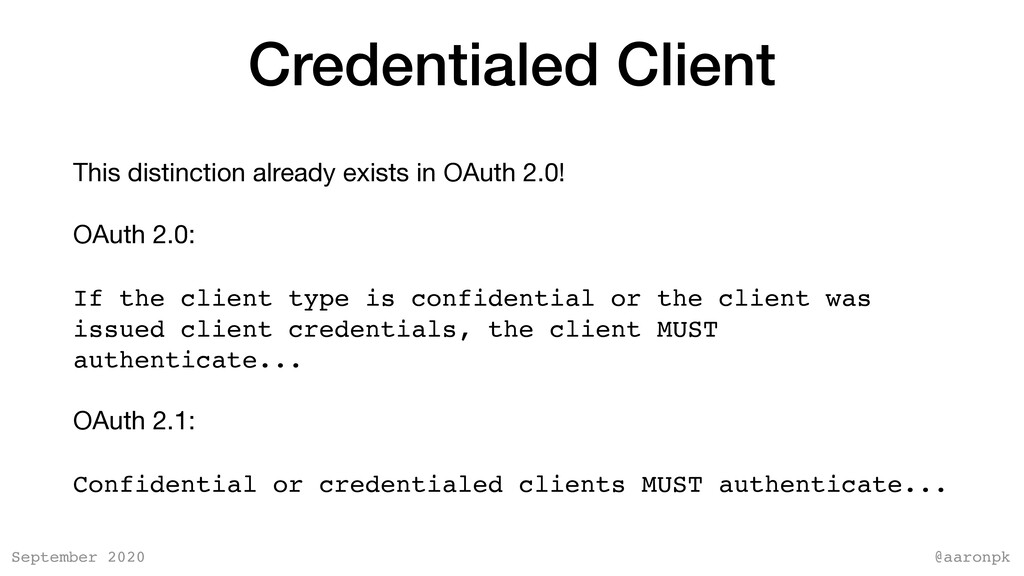
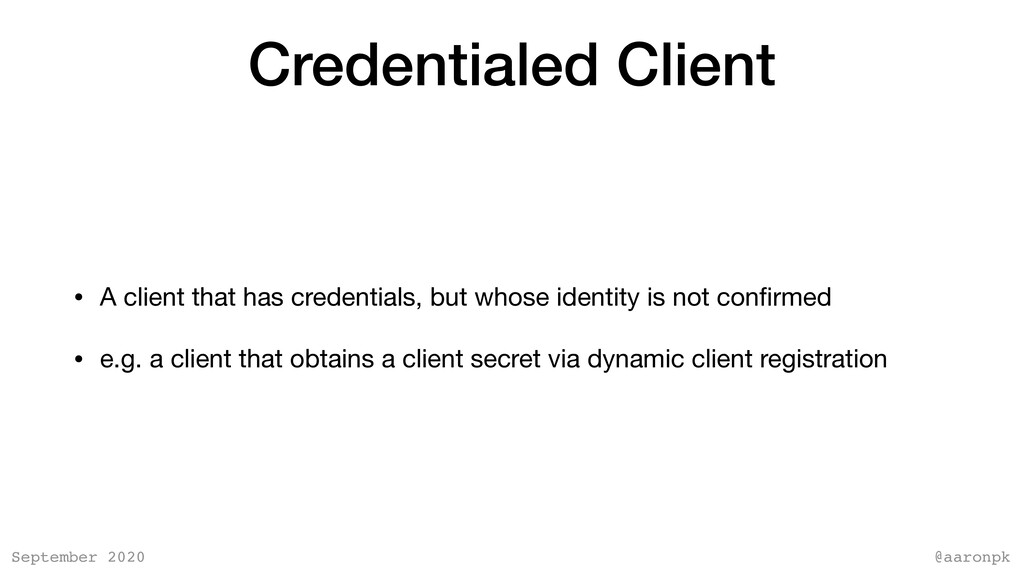
OAuth 2.0! OAuth 2.0: If the client type is confidential or the client was issued client credentials, the client MUST authenticate... OAuth 2.1: Confidential or credentialed clients MUST authenticate...


 aaronpk
 inariku
 takuyay0ne
 oidfj
 minorun365
 jacopen
 ryoskdara_
 oracle4engineer
 tnir
 demaecan
 lycorptech_jp
 kazzpapa3
 amarelo_n24
 kimpetersen
 reverentgeek
 lfama
 jonoalderson
 eileencodes
 skipperchong
 minecr
 asonas
 bermonpainter
 sstephenson
 chriscoyier