App Integrity Attestations for OAuth - OAuth Se...

App Integrity Attestations for OAuth - OAuth Security Workshop 2022
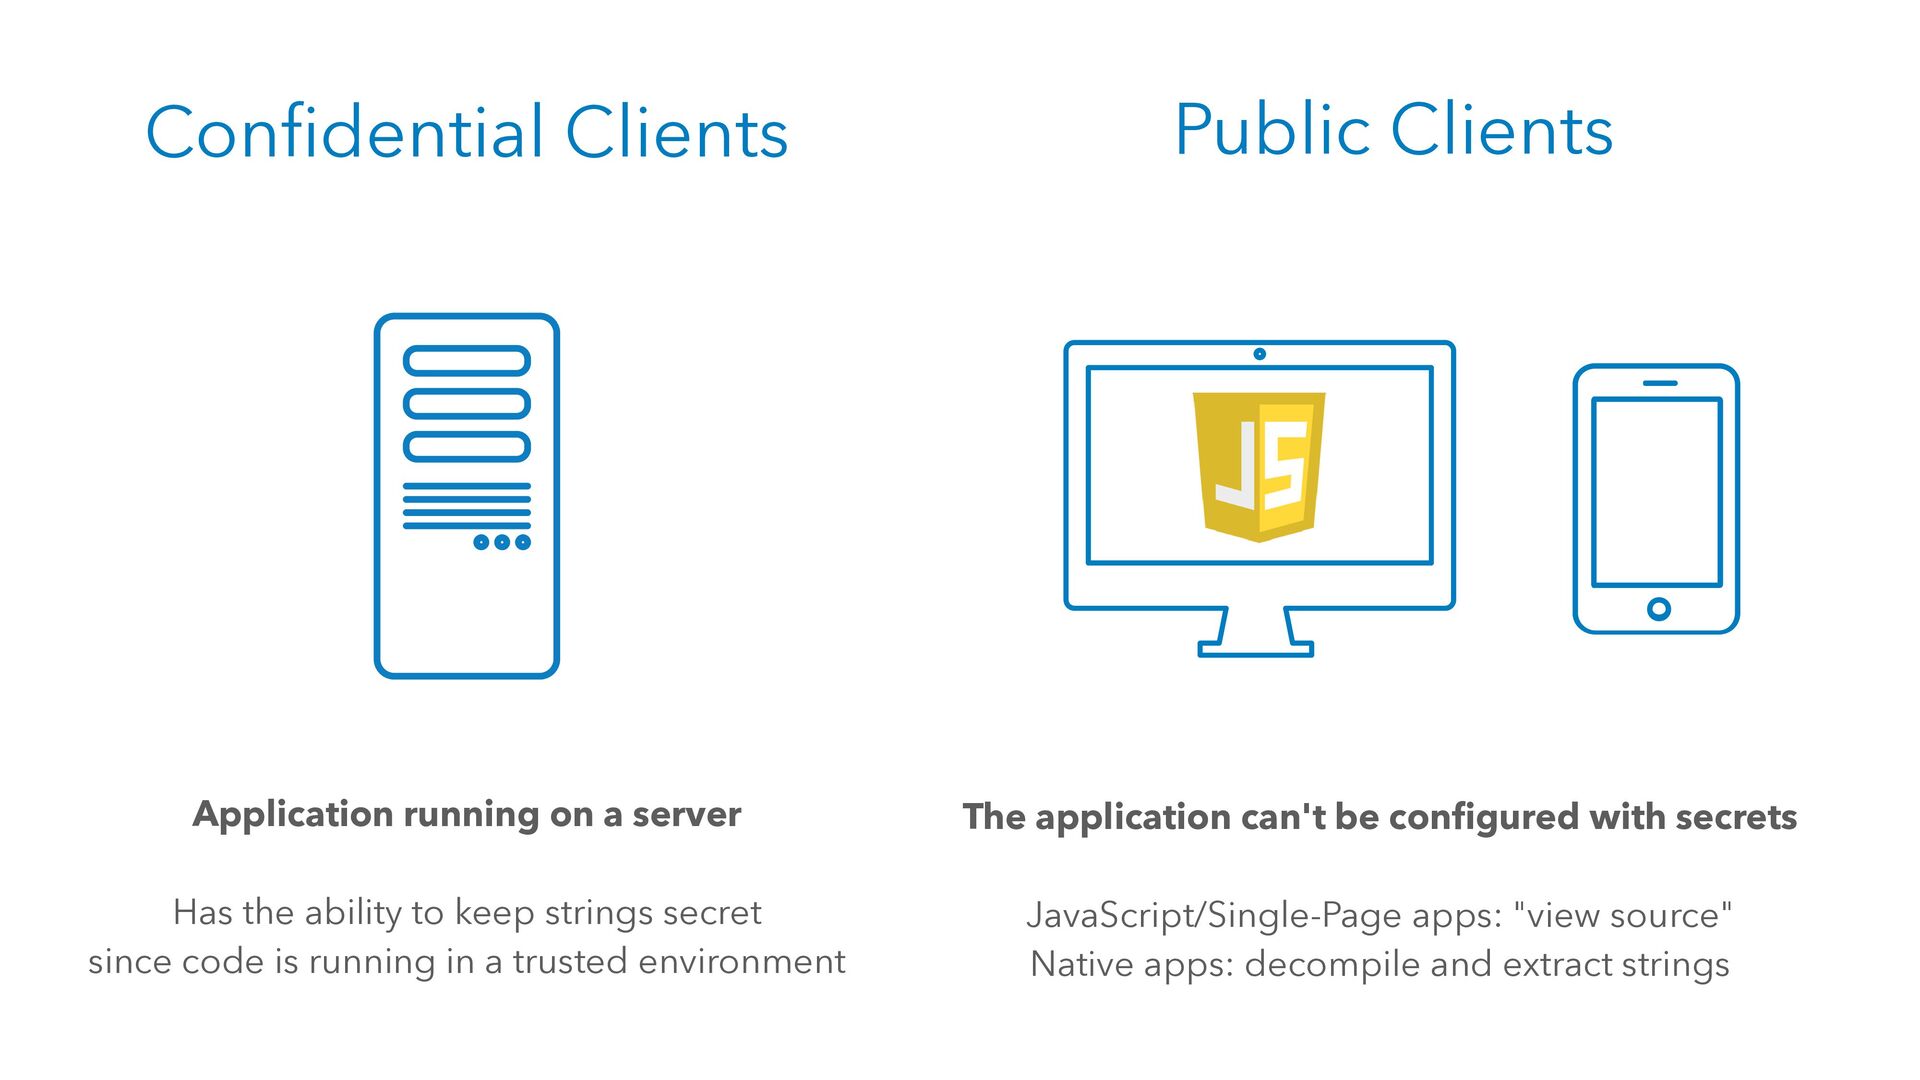
Currently, the security of native apps in OAuth is contingent upon registering the app's callback URL with the operating system, preferably as an app-claimed HTTPS URL. While this provides some level of assurance of the app's identity, it is by no means foolproof.
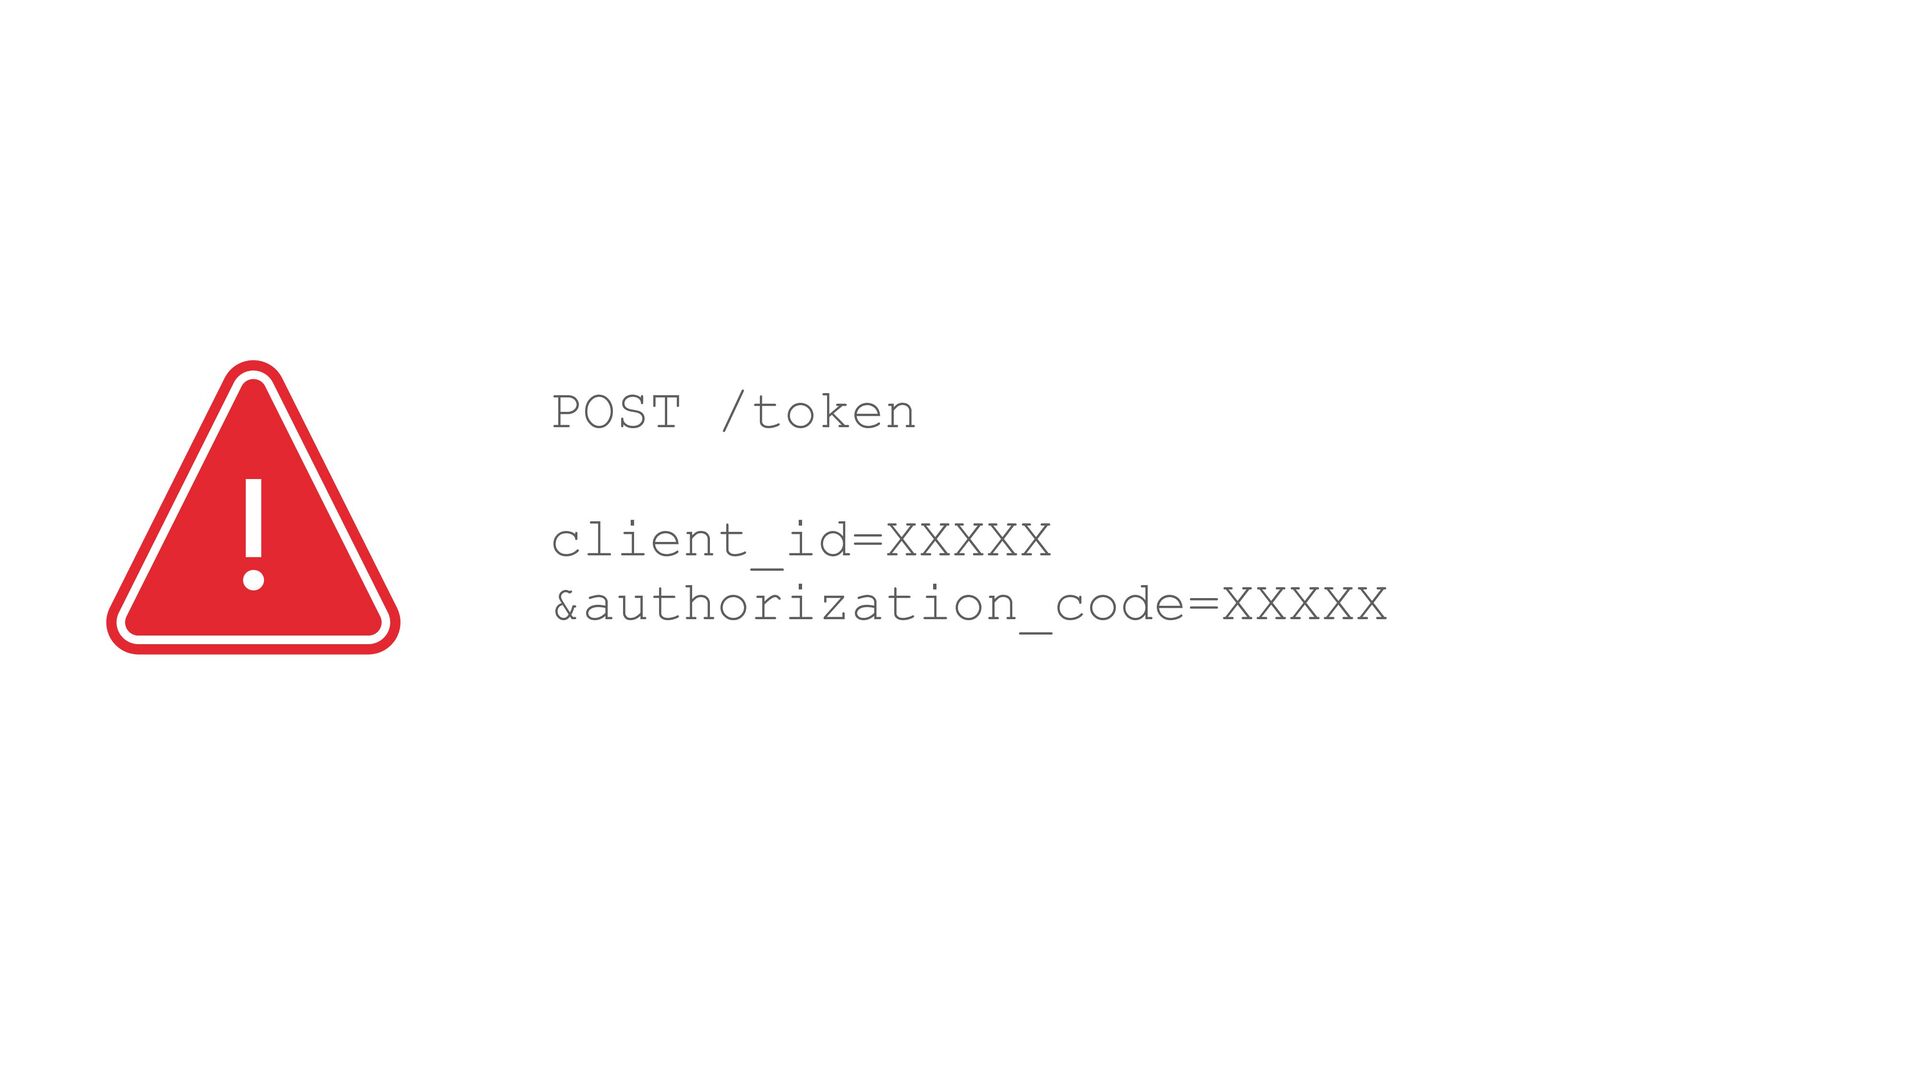
Authenticating whether a particular instance of a public client in OAuth is a legitimate instance remains a challenge.
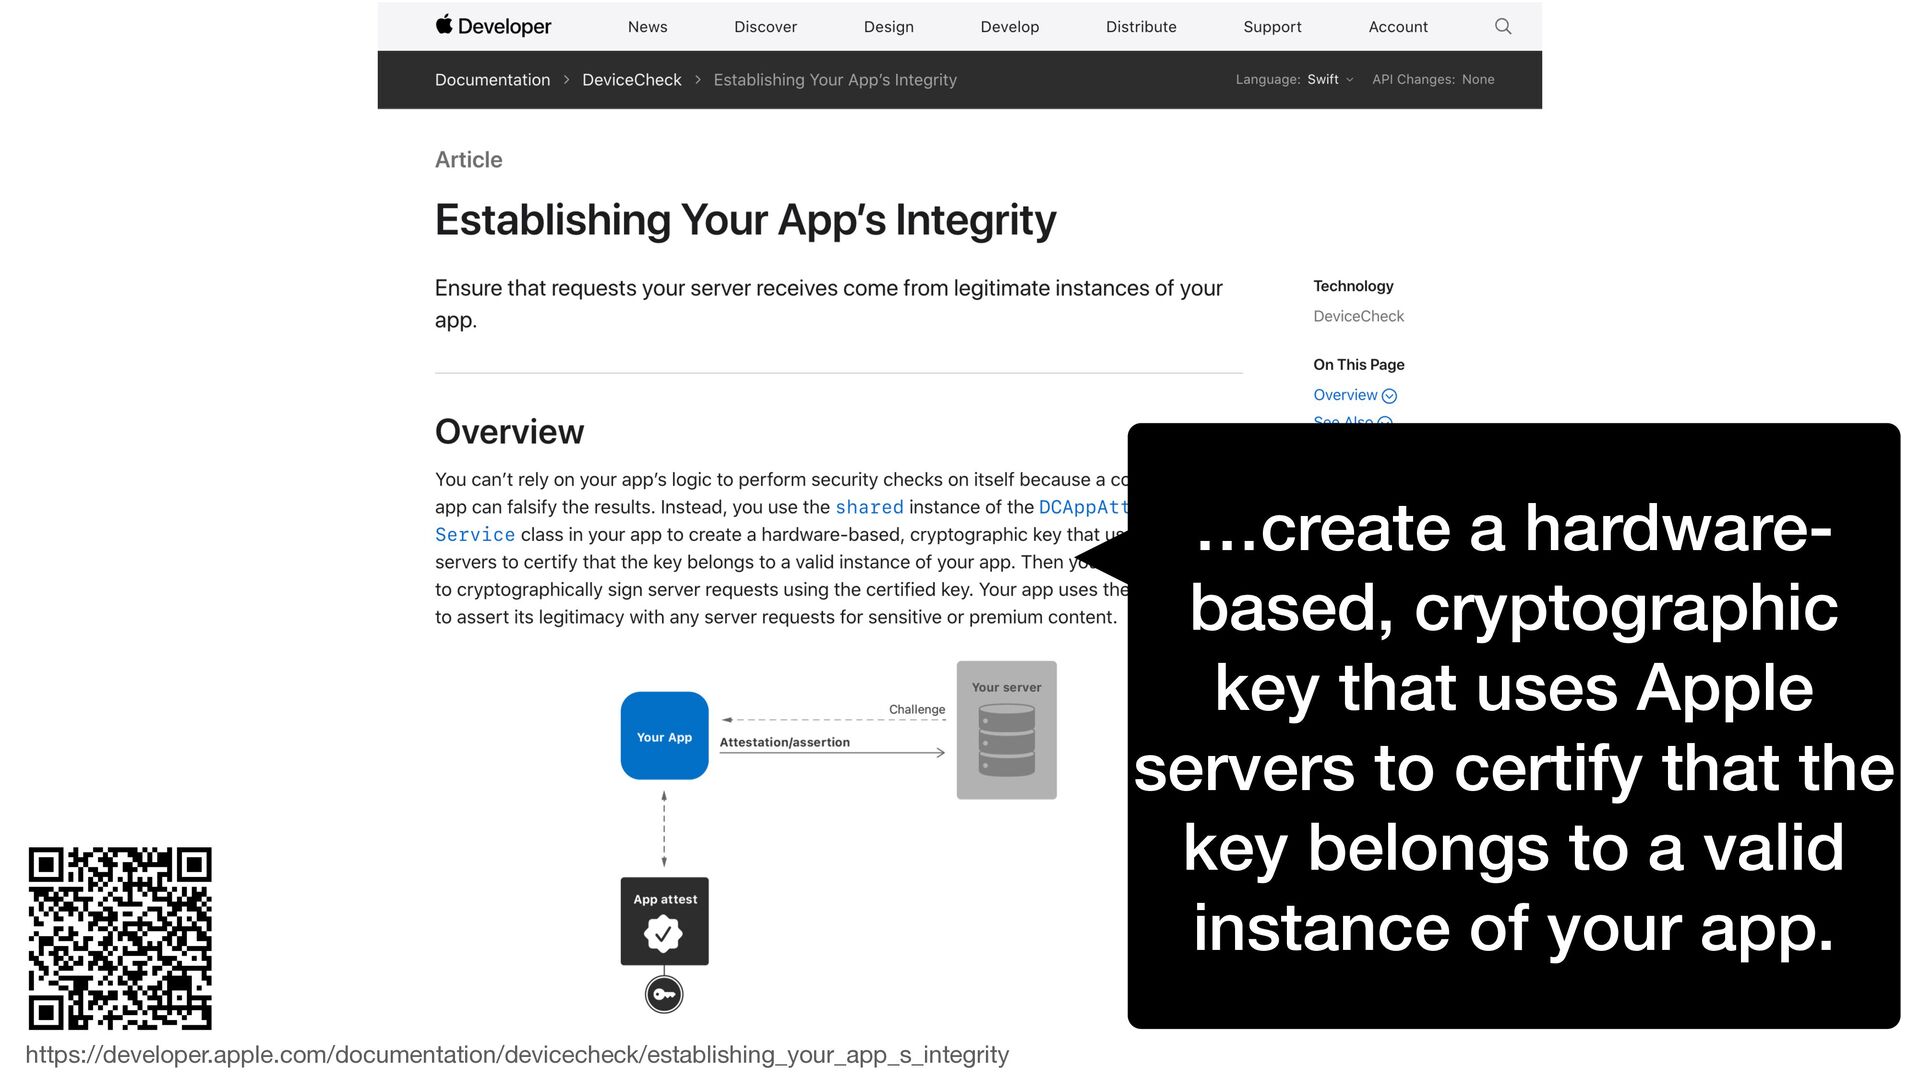
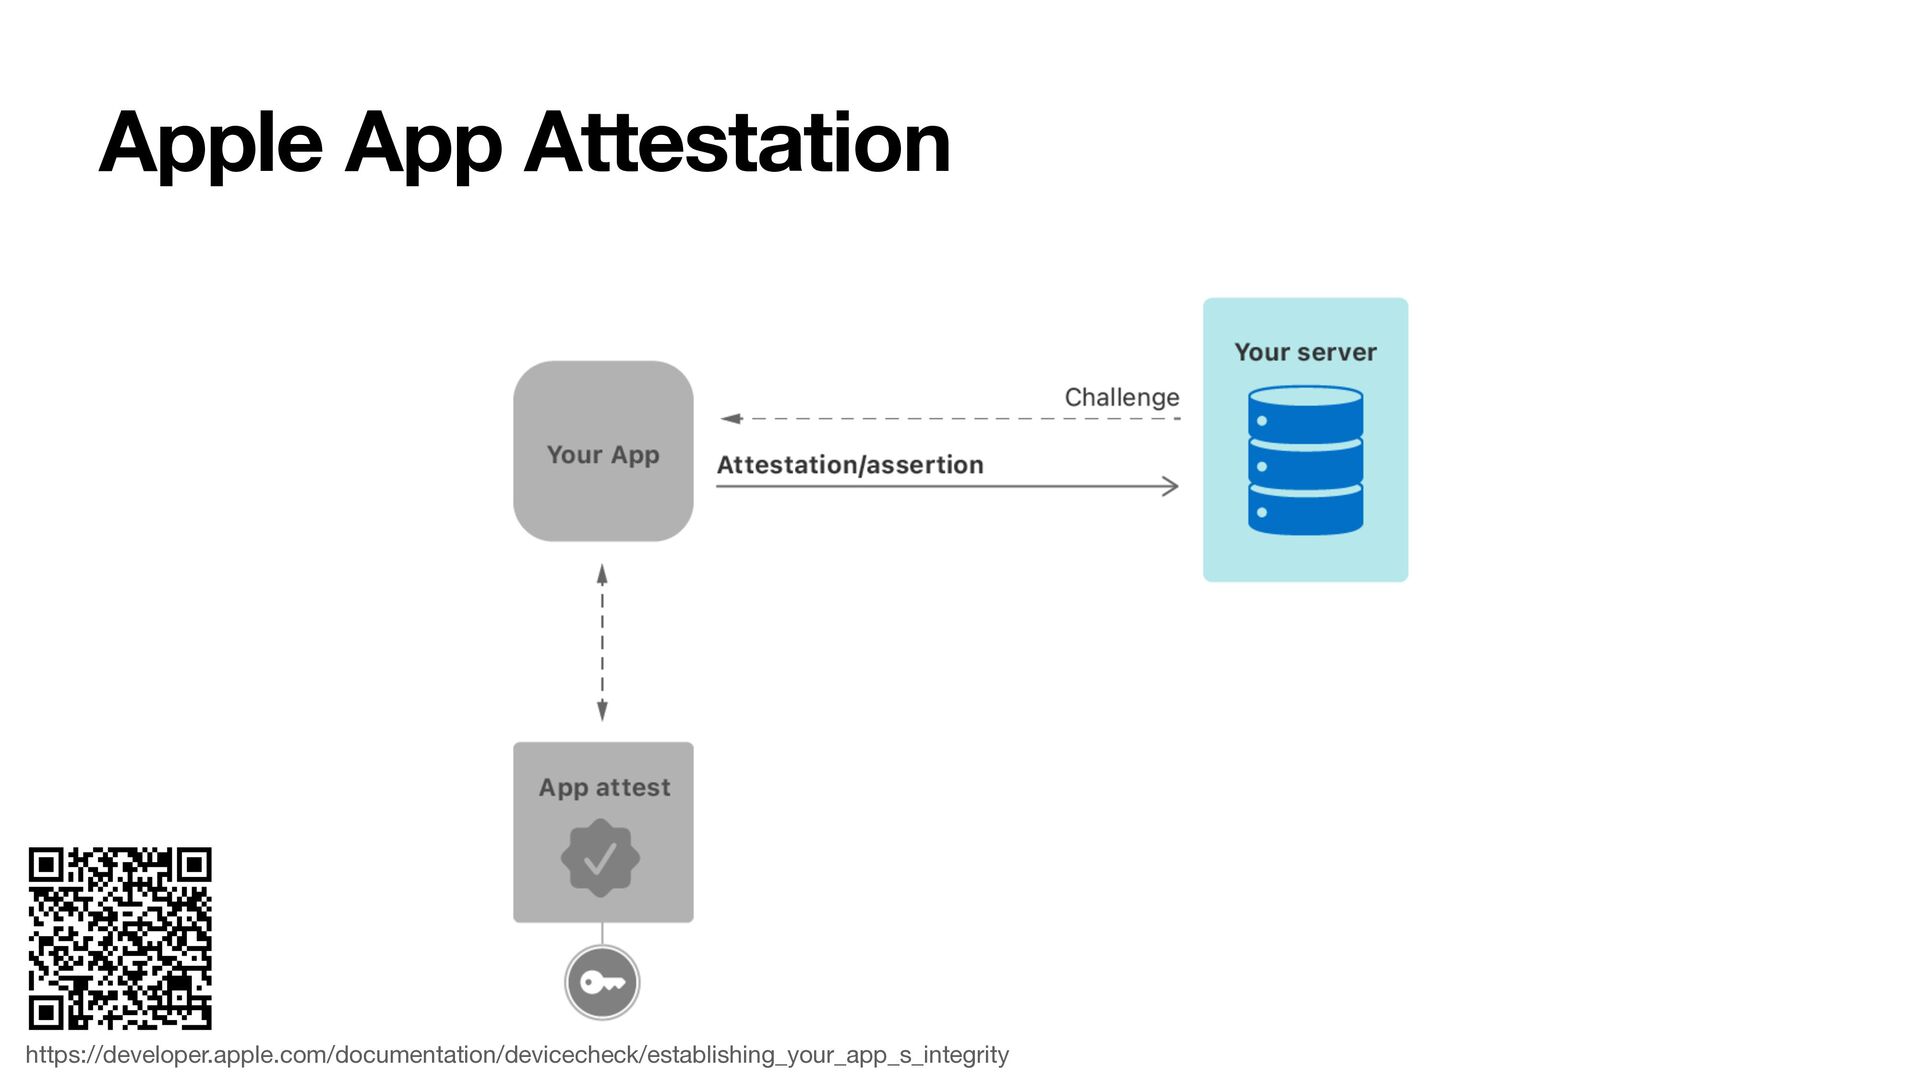
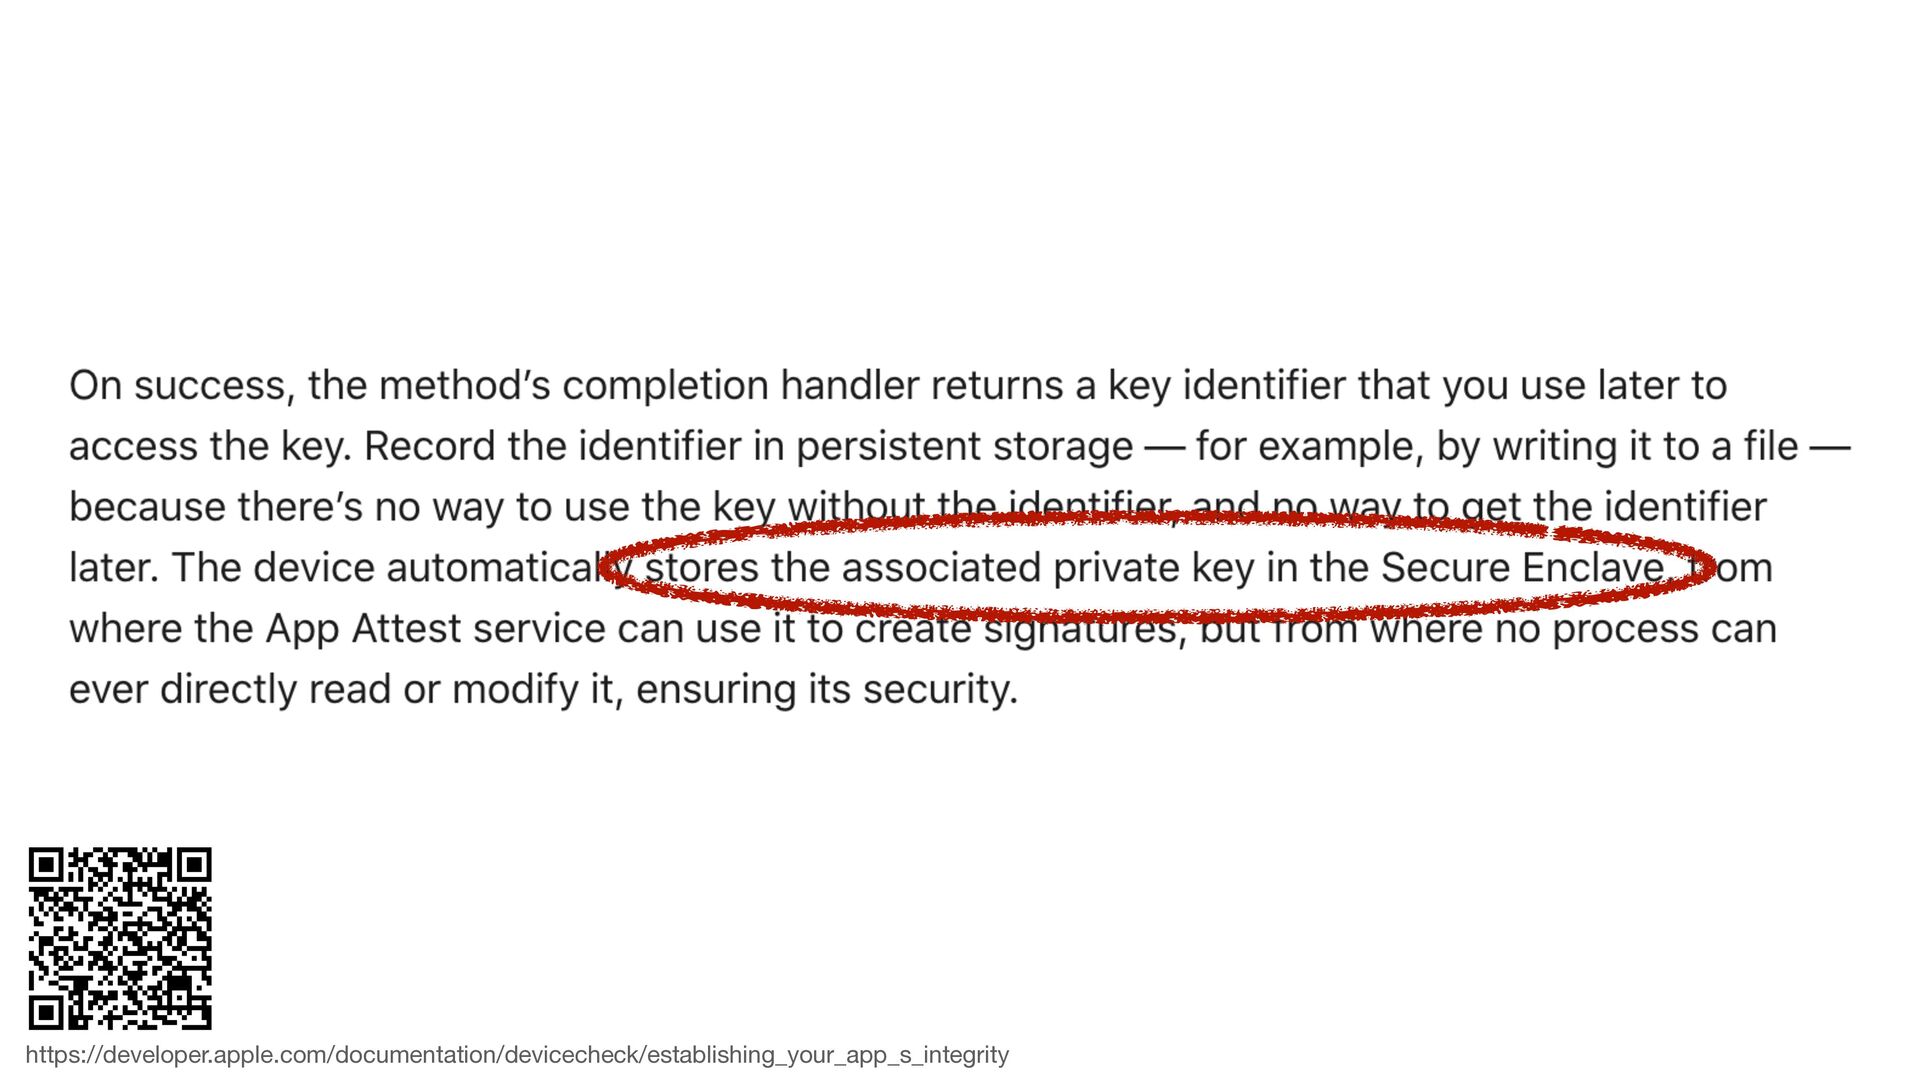
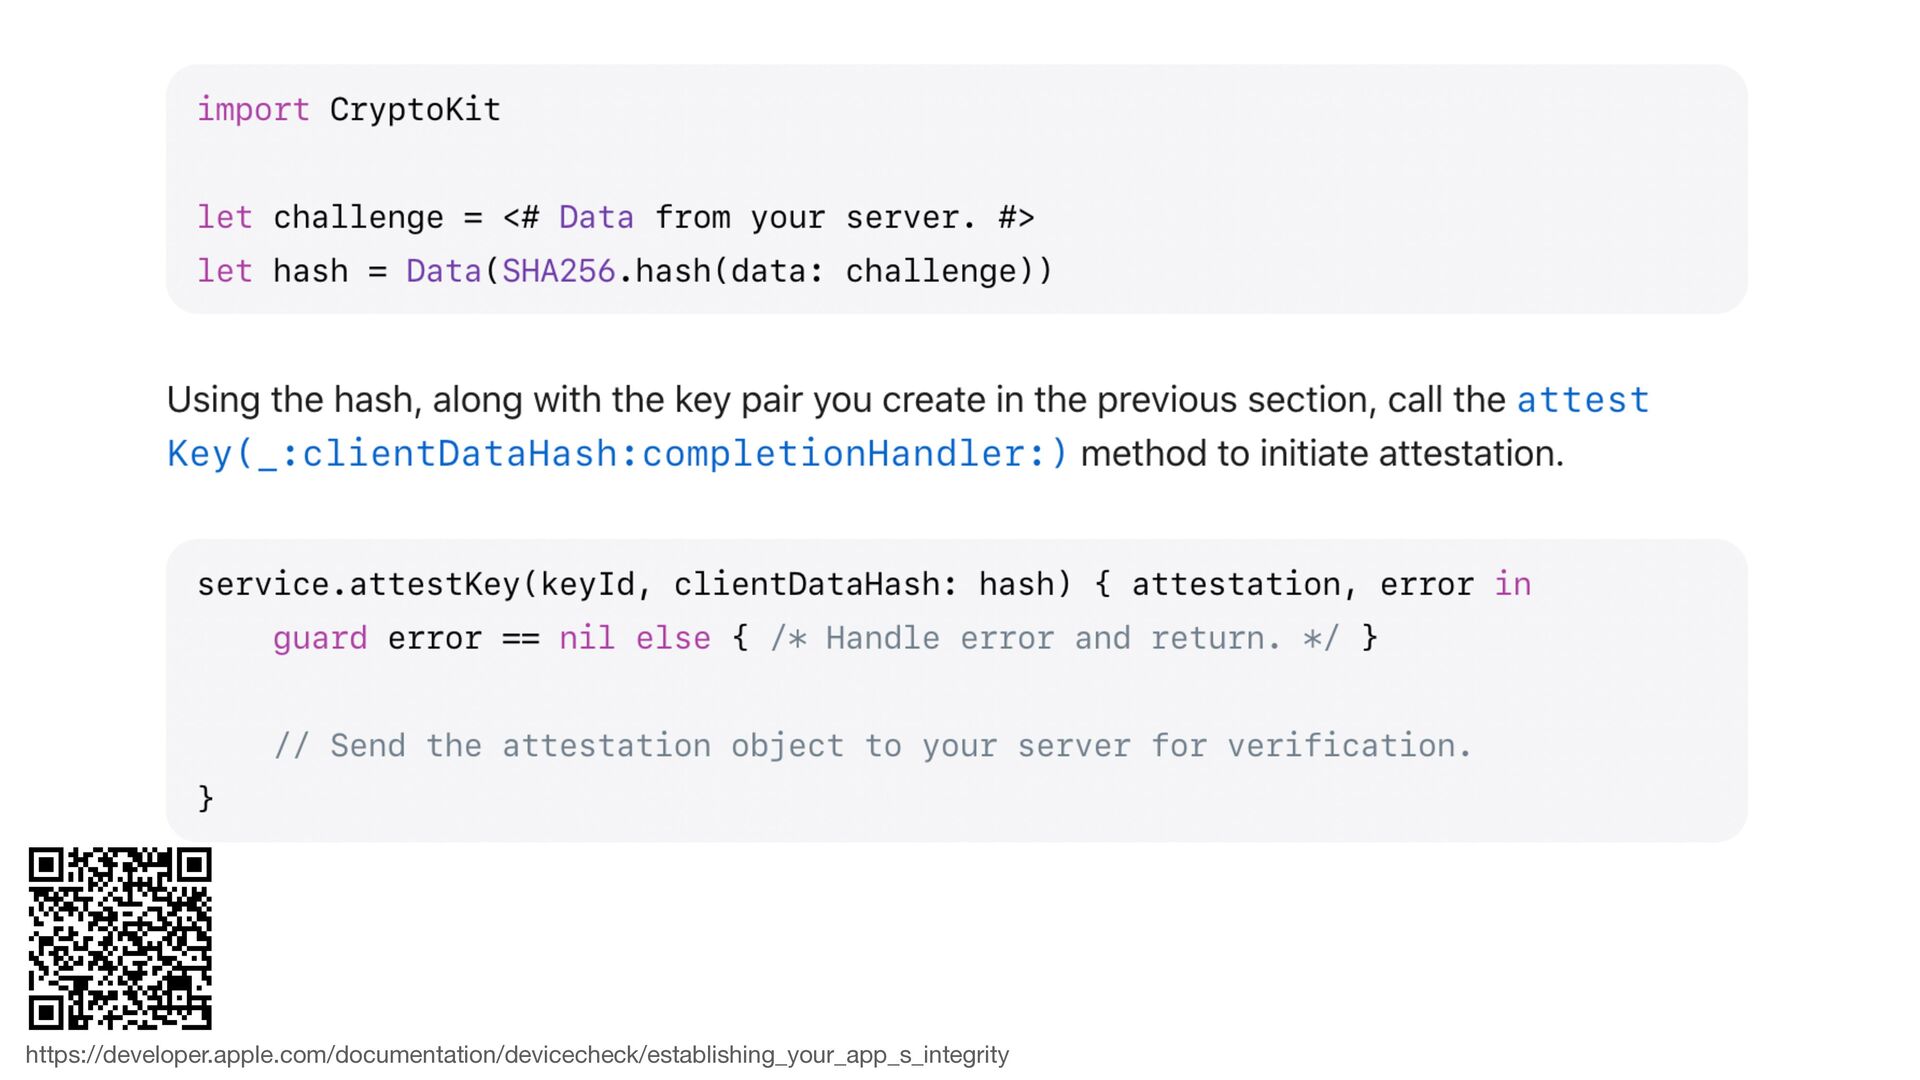
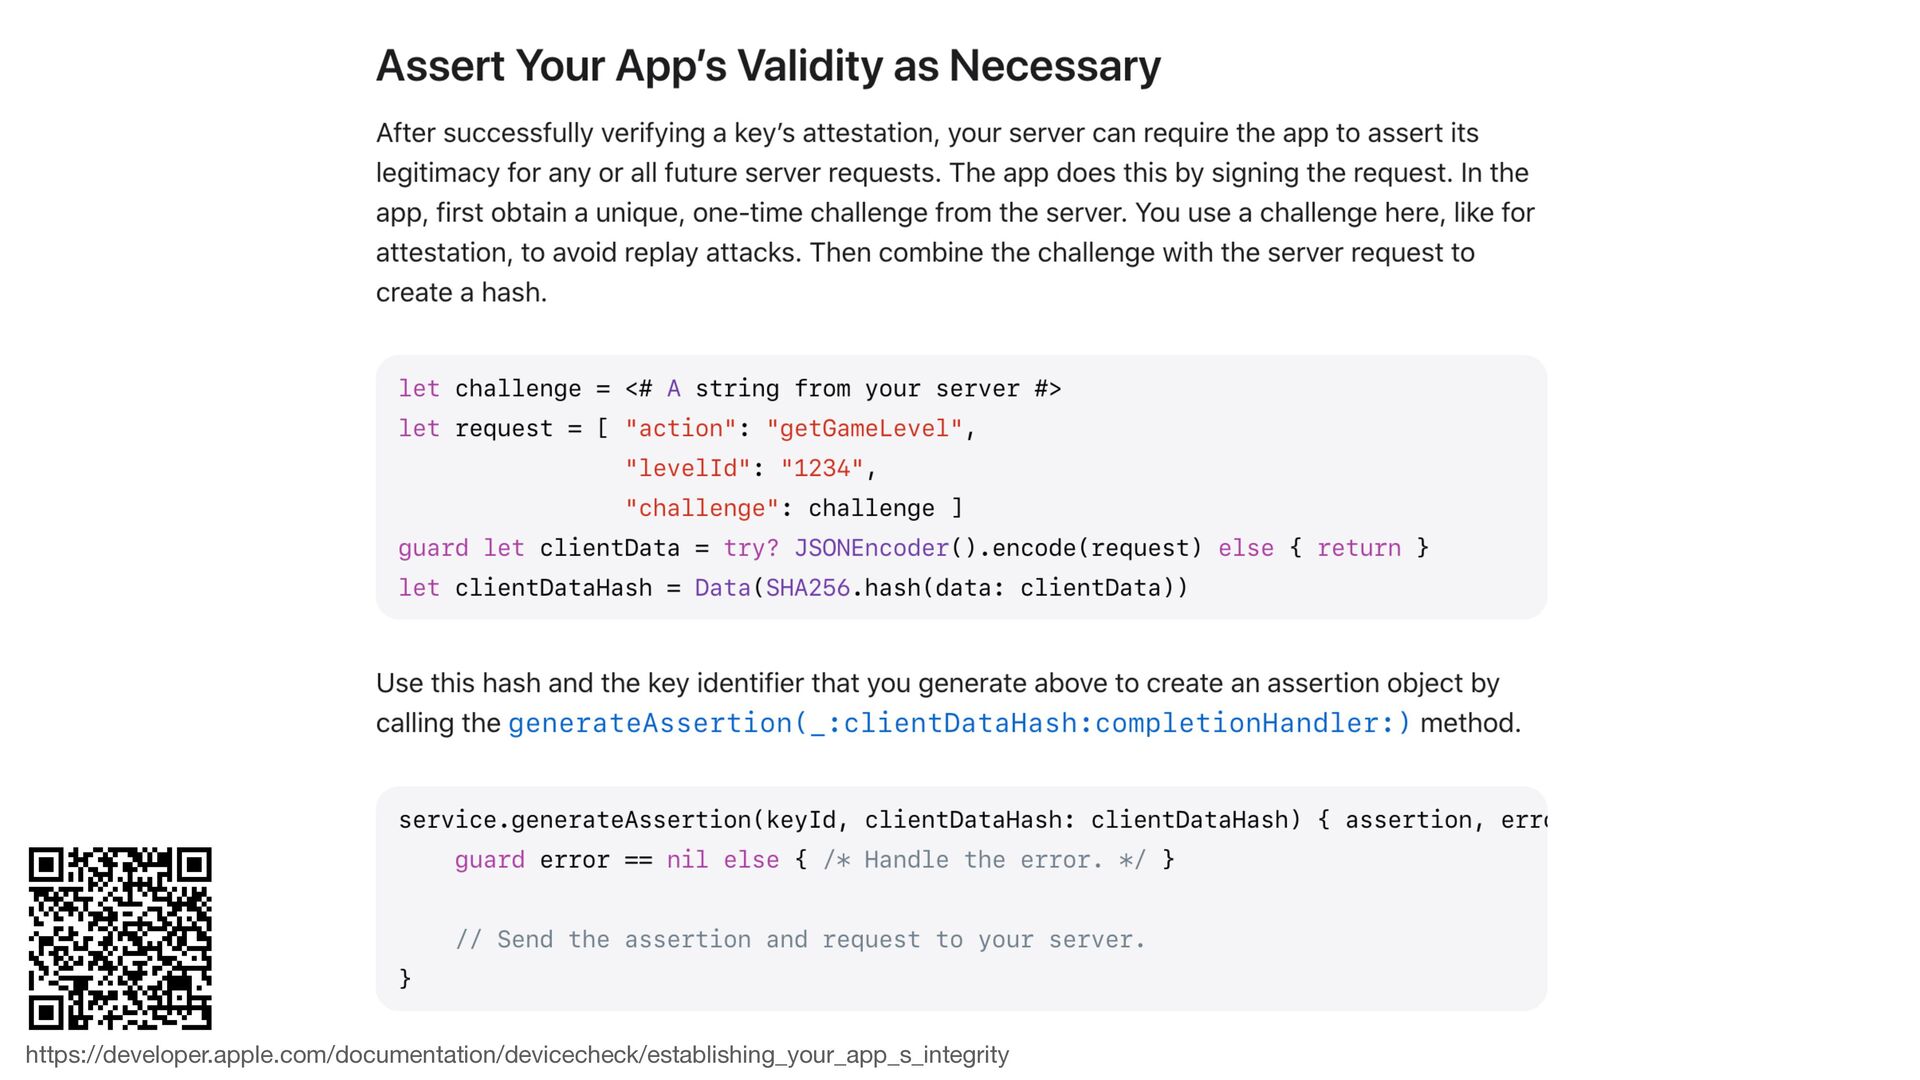
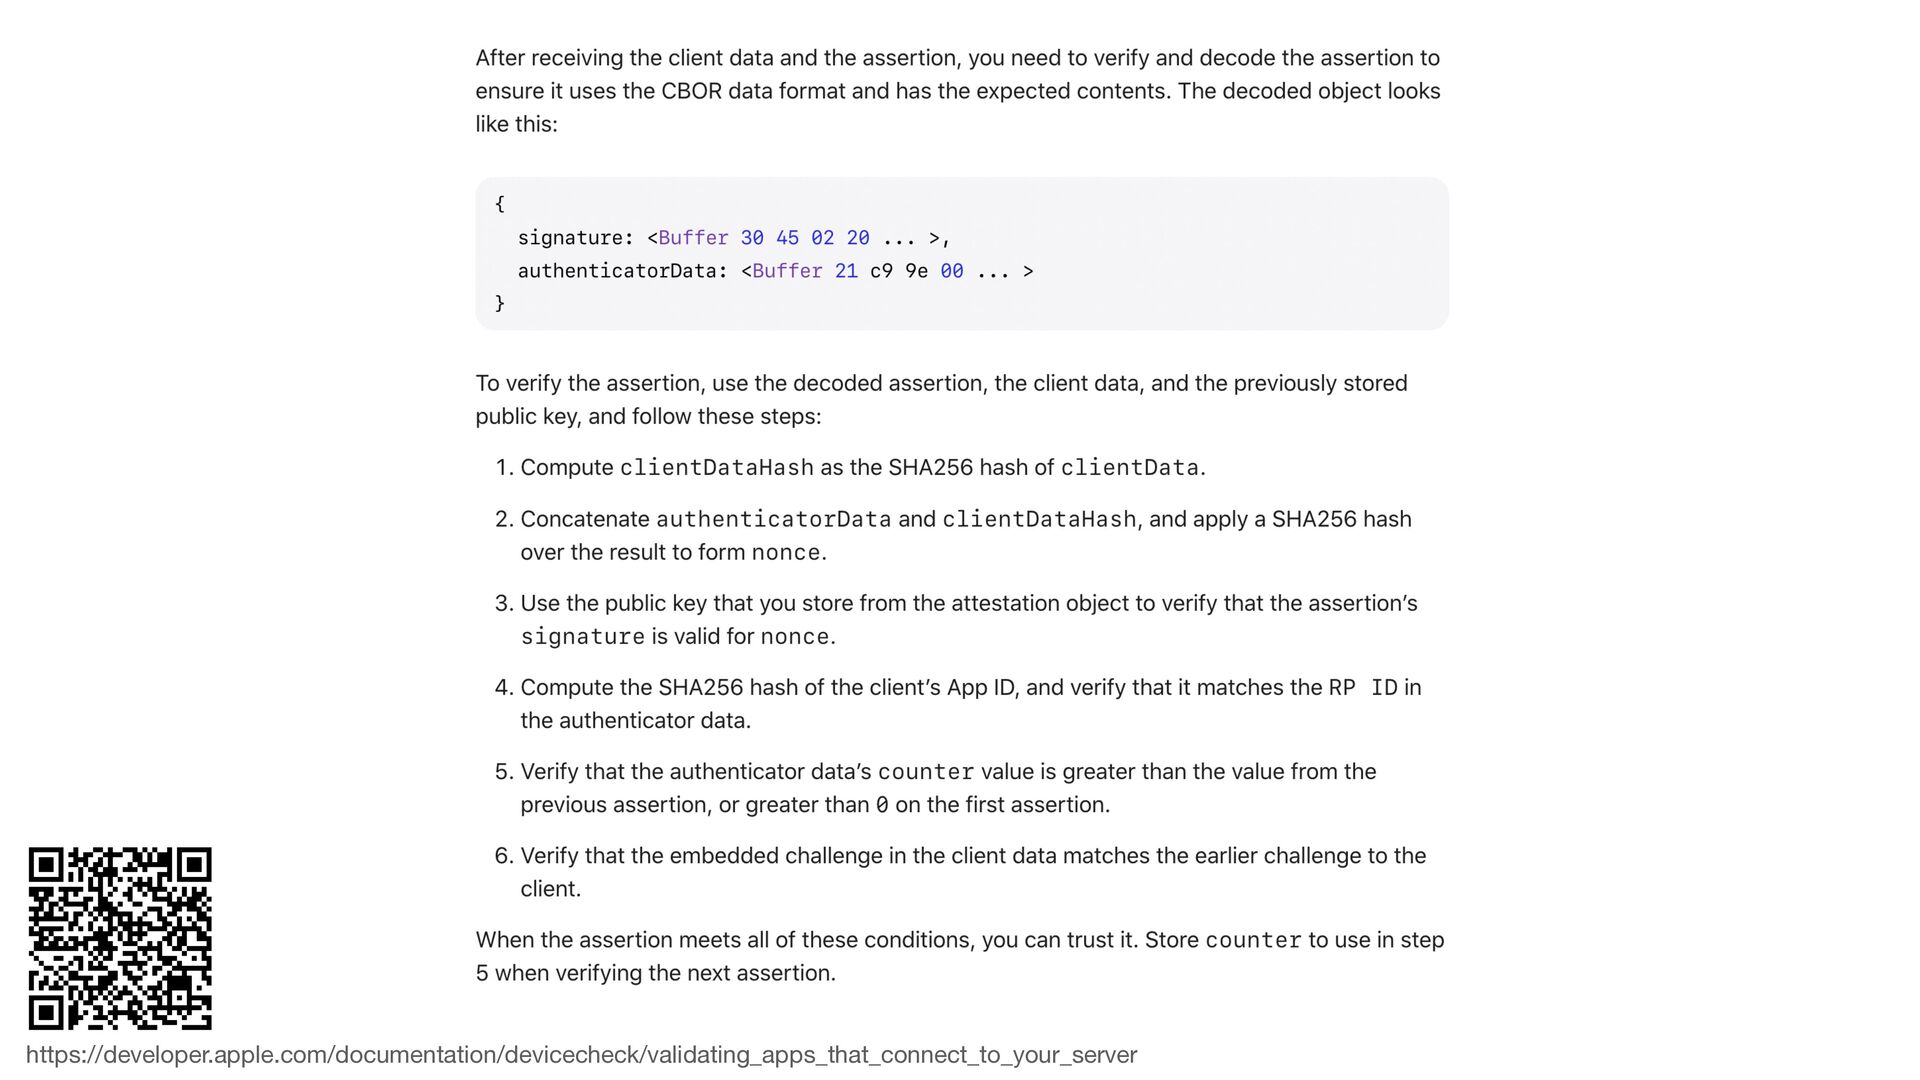
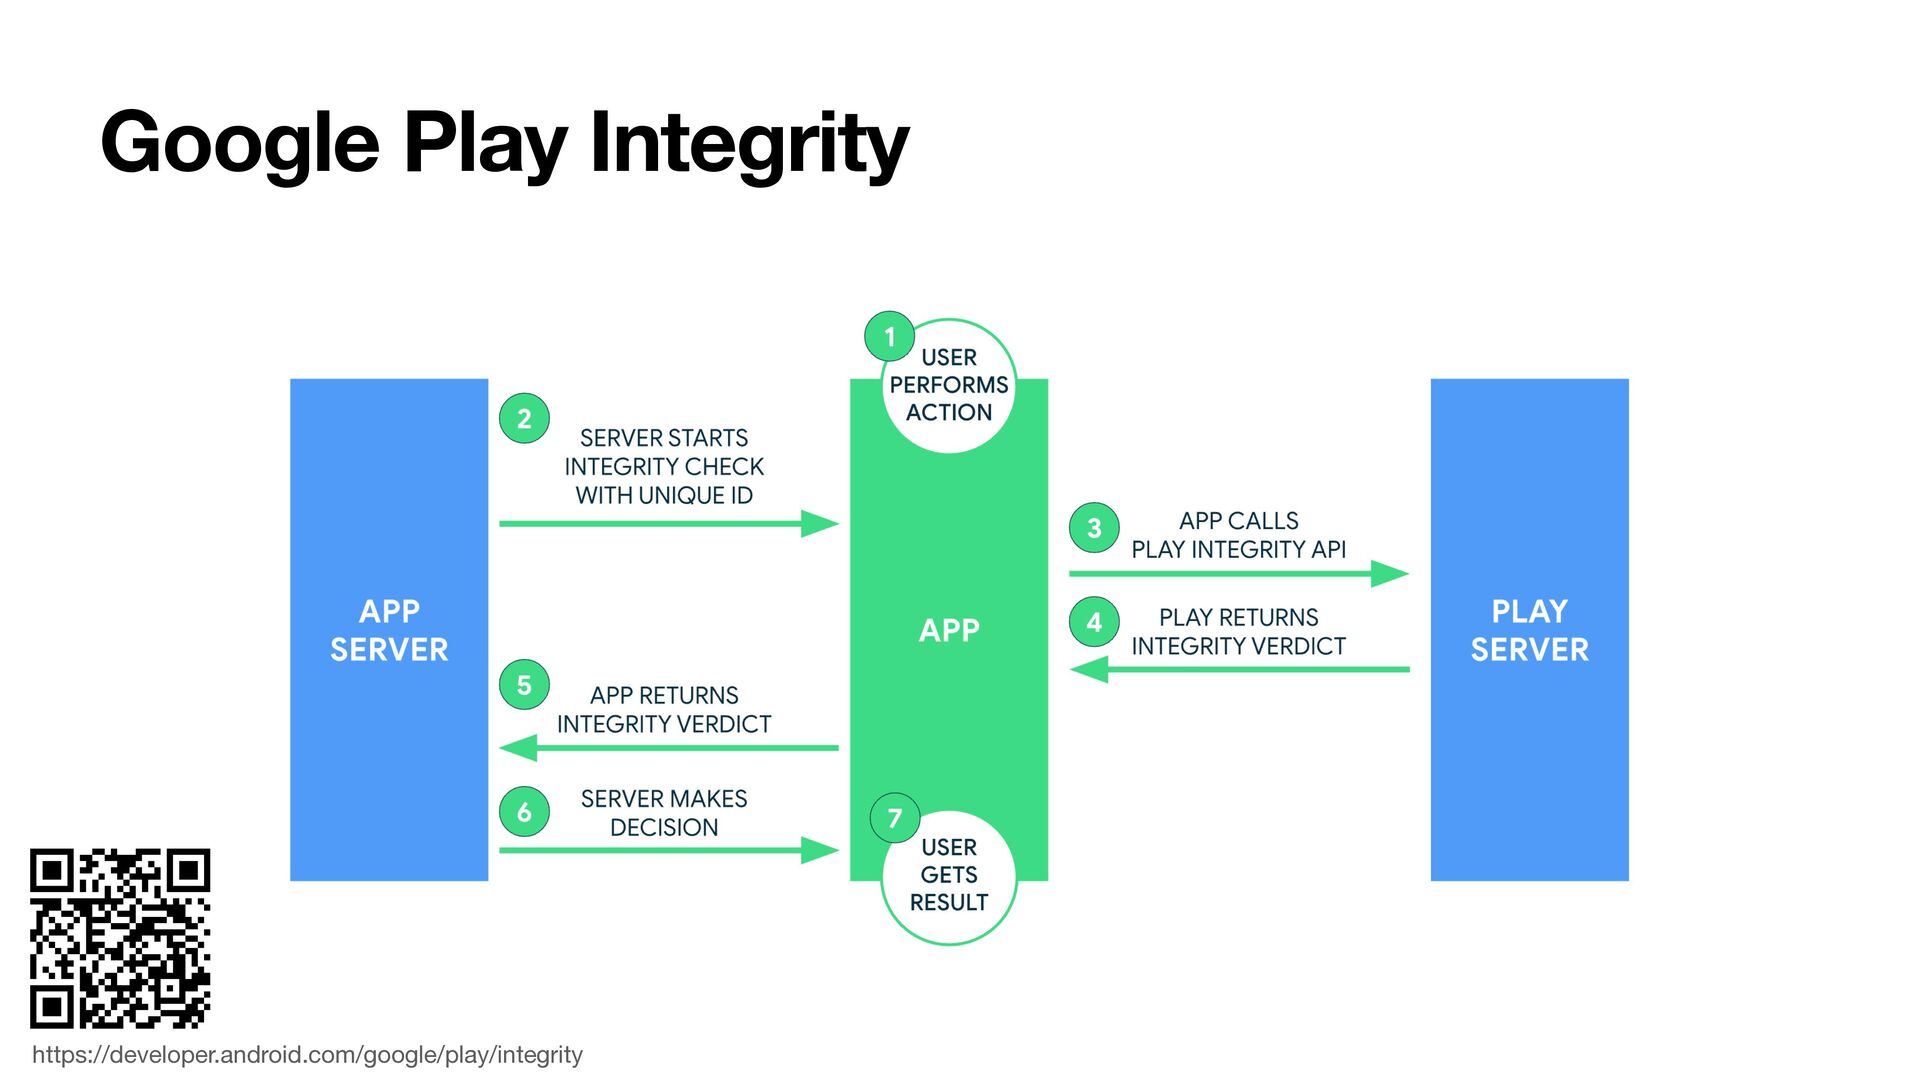
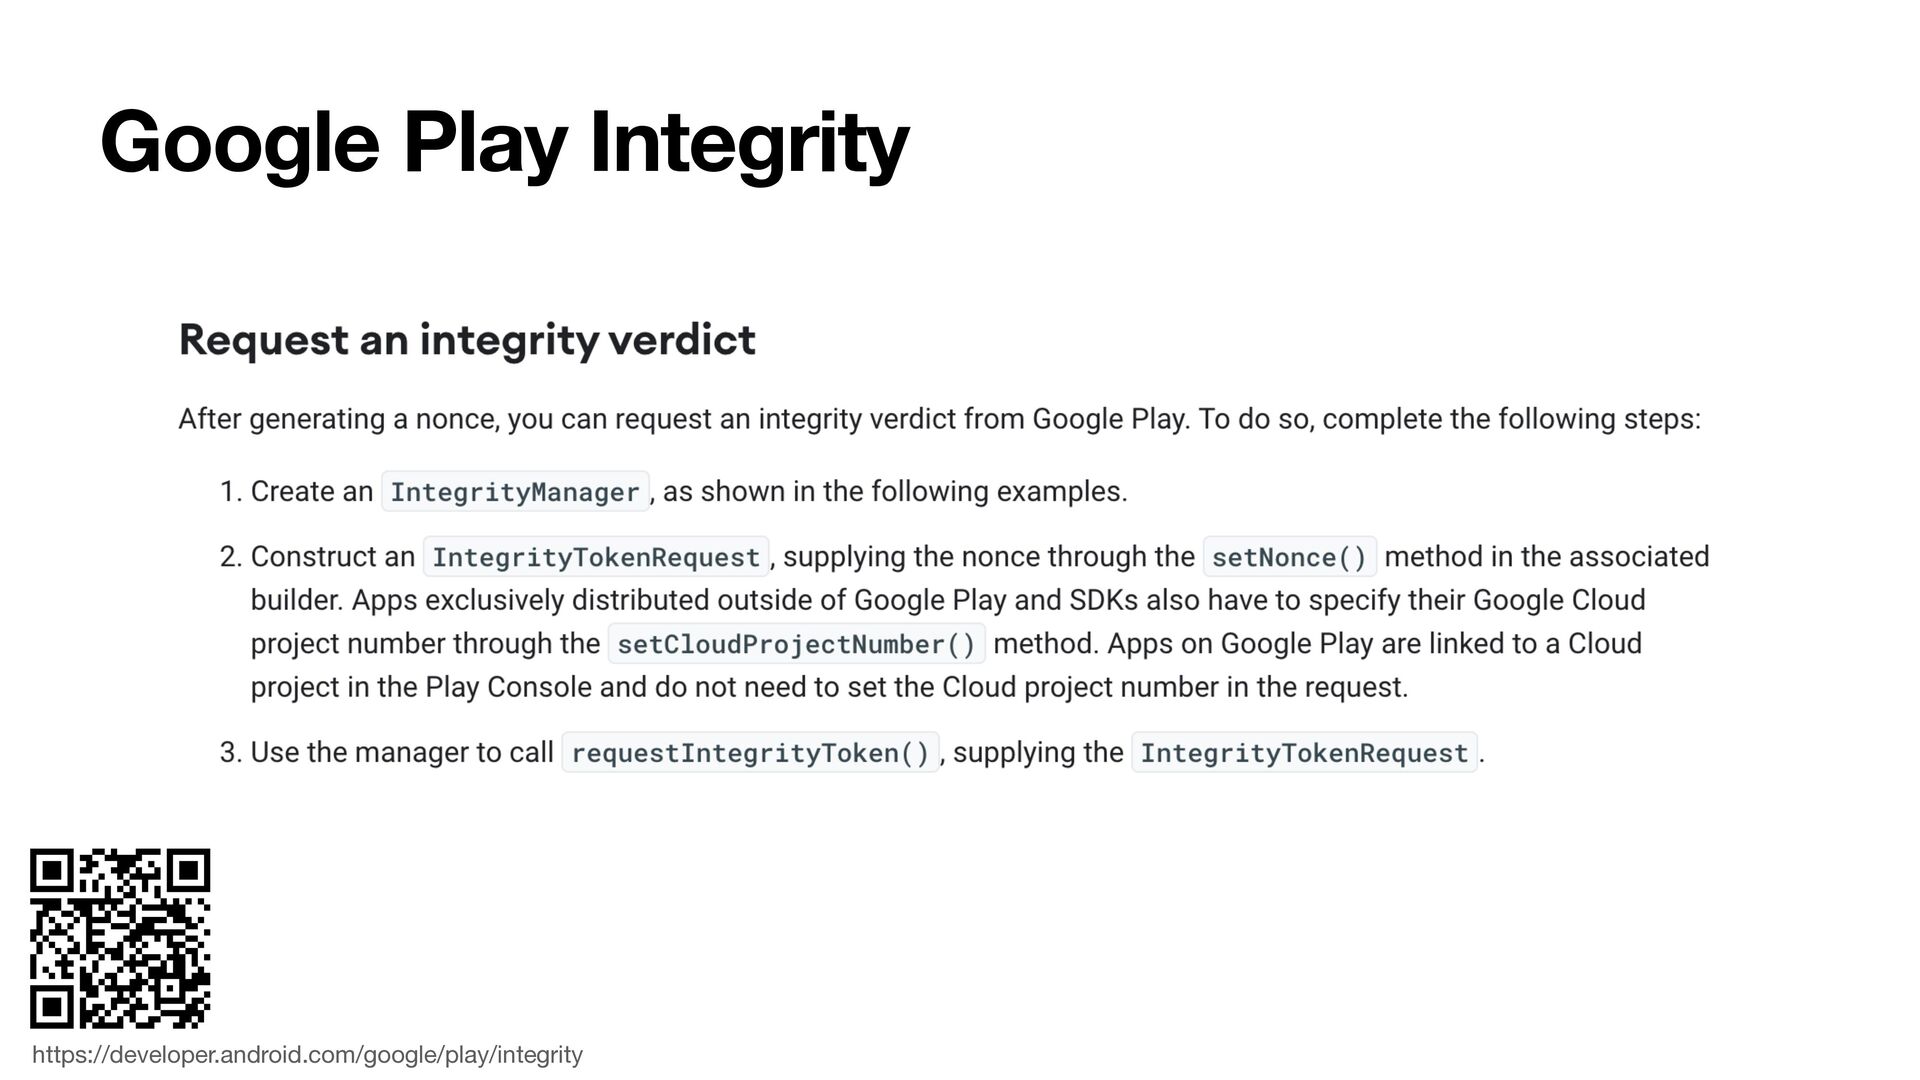
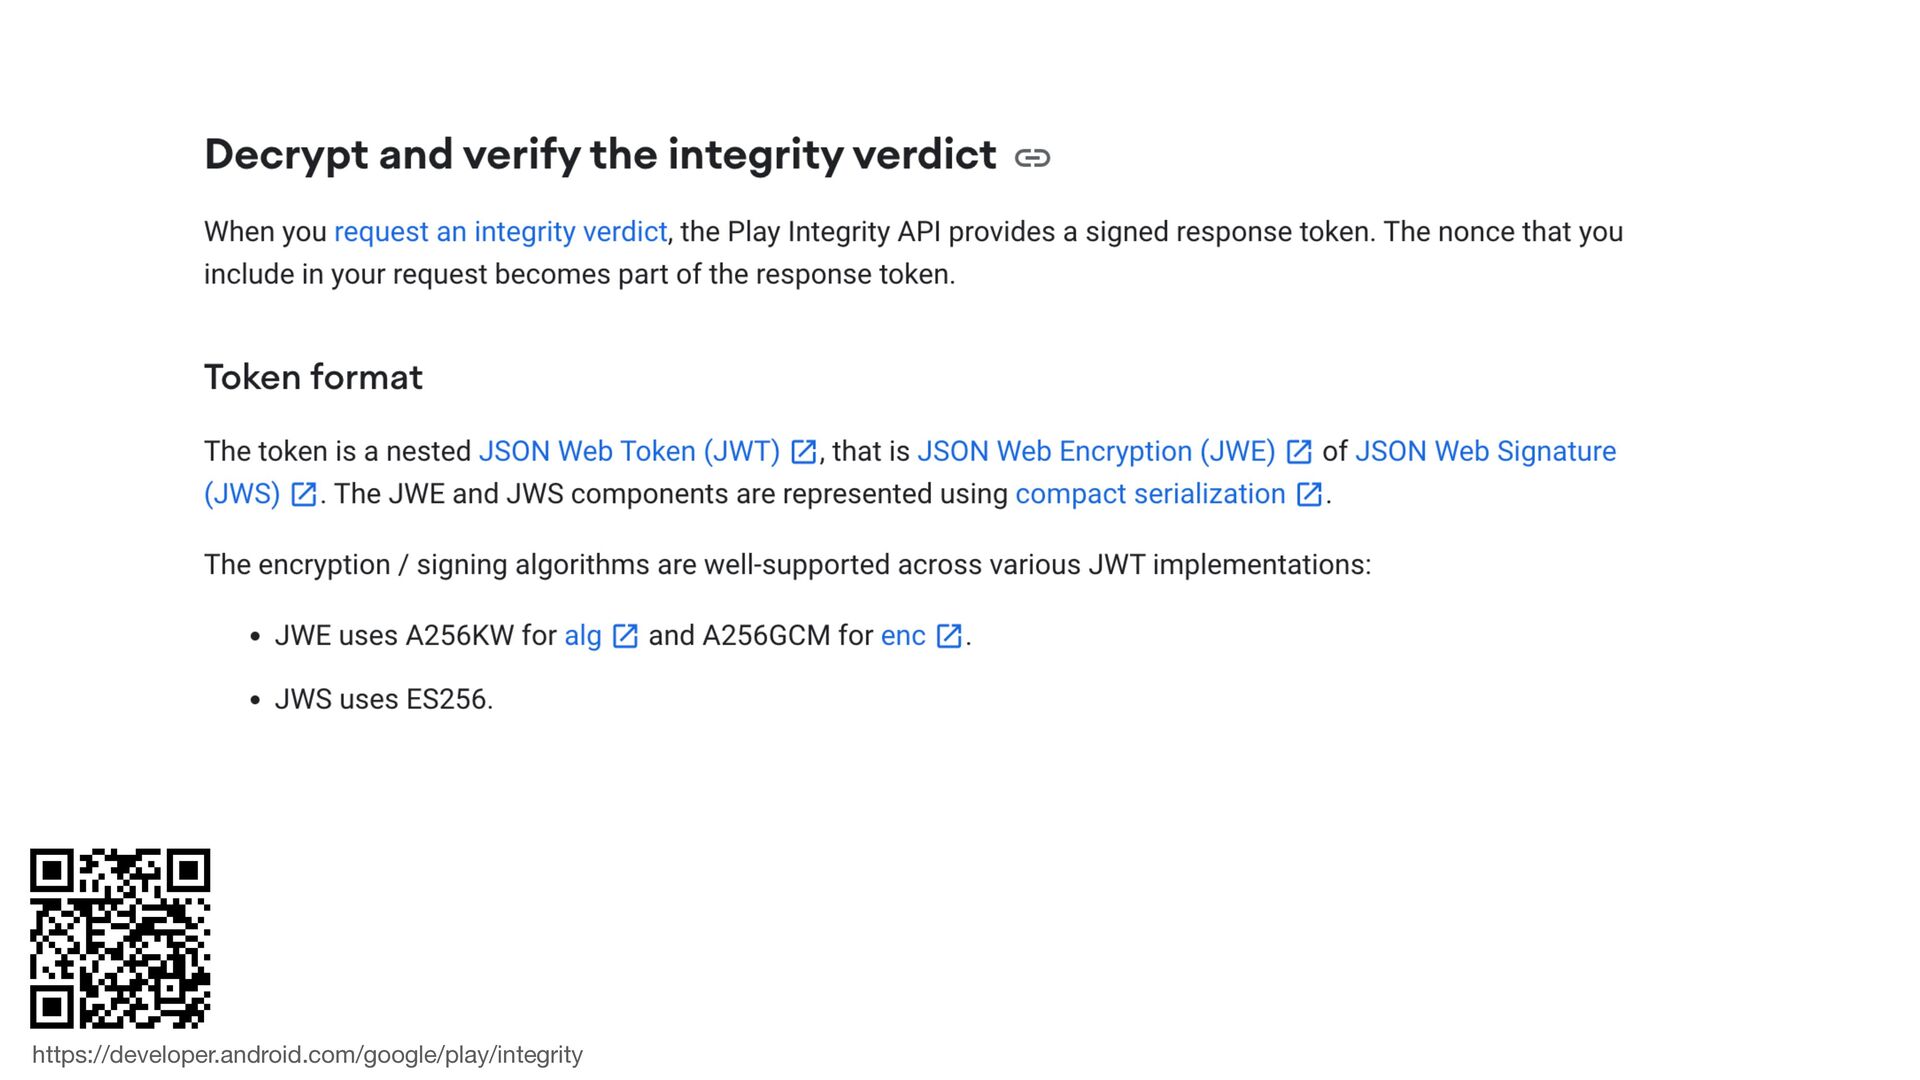
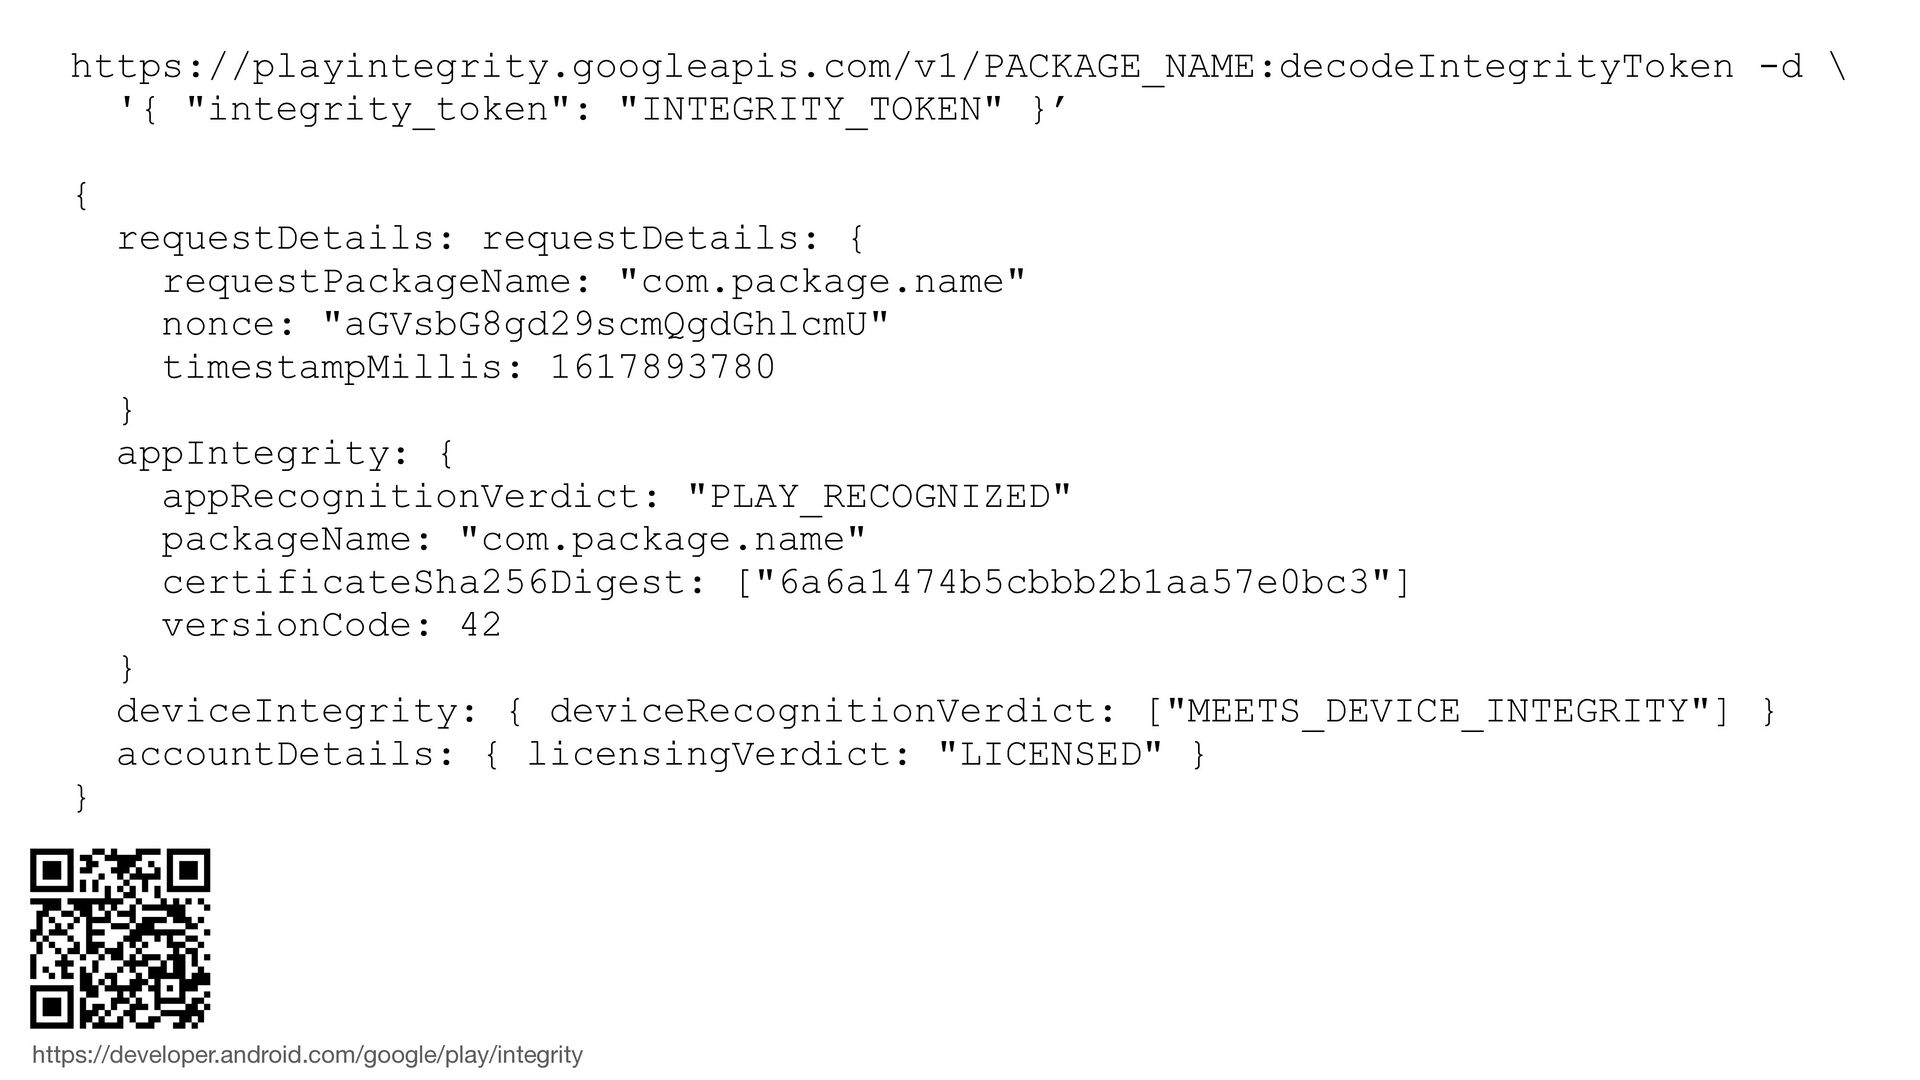
This session will explore the possibility of using Apple and Android’s “app attestation” APIs as a form of OAuth client authentication. These APIs are able to leverage on-device private keys and a certificate chain to provide an additional level of confidence that the app making an HTTP request is the same code that was shipped in the app stores.

Aaron Parecki
May 06, 2022
 aaronpk
 littlehands
 hagino3000
 ryudai
 imuta
 yama3133
 ama_ch
 ginjihayashi
 falken
 nejumi
 say_no_w
 fj_yoshimura_kosuke
 ivry_presentationmaterials
 ks91
 aleyda
 auna
 lara
 wayneb77
 jlugia
 codingconduct
 elsirapls
 skipperchong
 shpigford
 techseoconnect