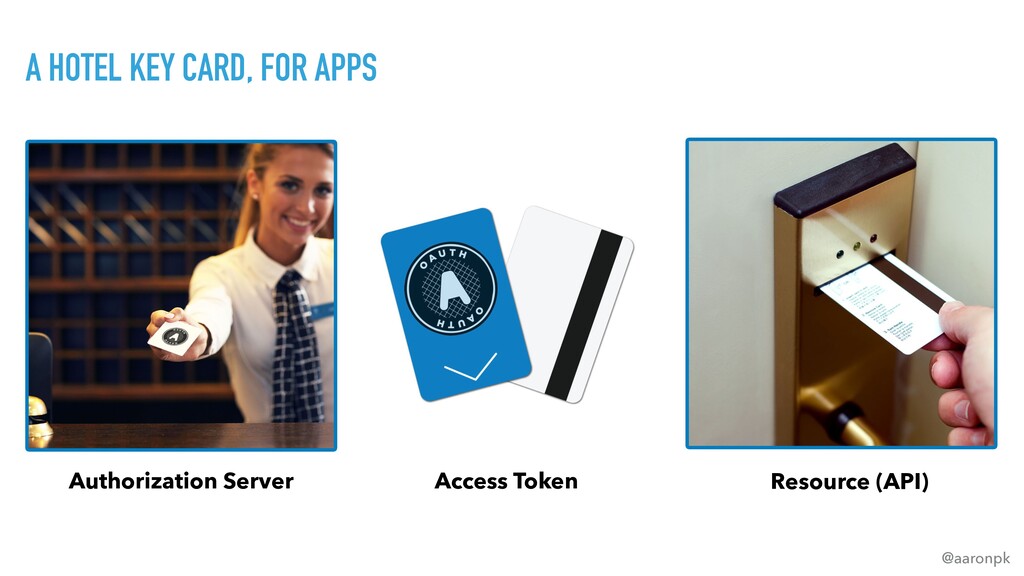
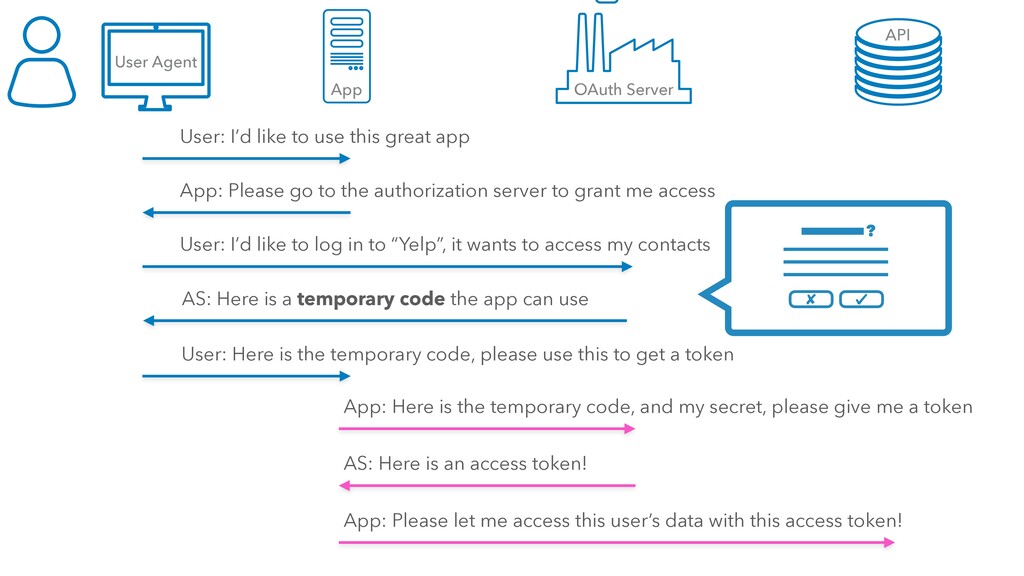
go to the authorization server to grant me access User: I’d like to log in to “Yelp”, it wants to access my contacts AS: Here is a temporary code the app can use App: Here is the temporary code, and my secret, please give me a token User: Here is the temporary code, please use this to get a token AS: Here is an access token! App: Please let me access this user’s data with this access token! User Agent App OAuth Server API ?
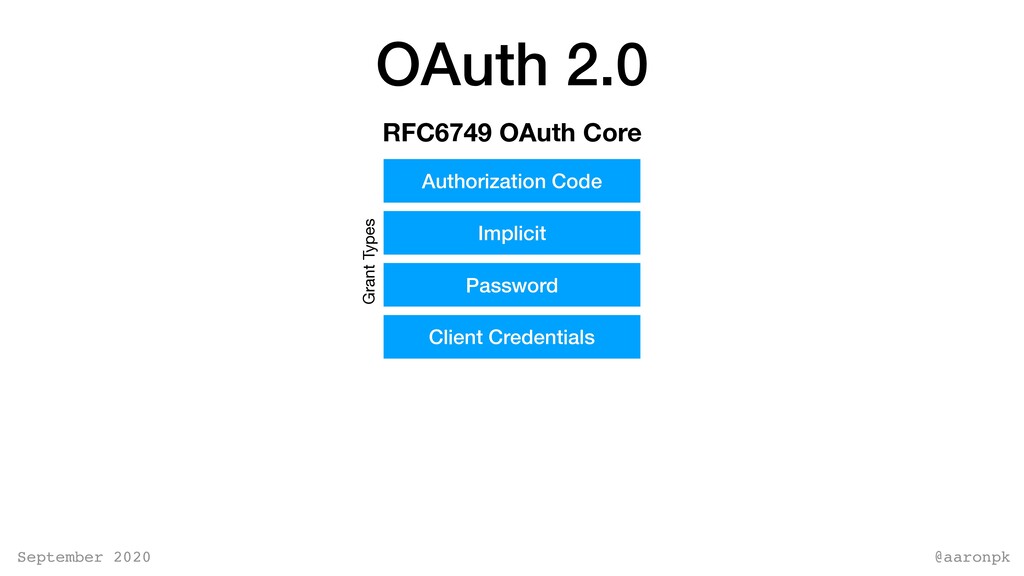
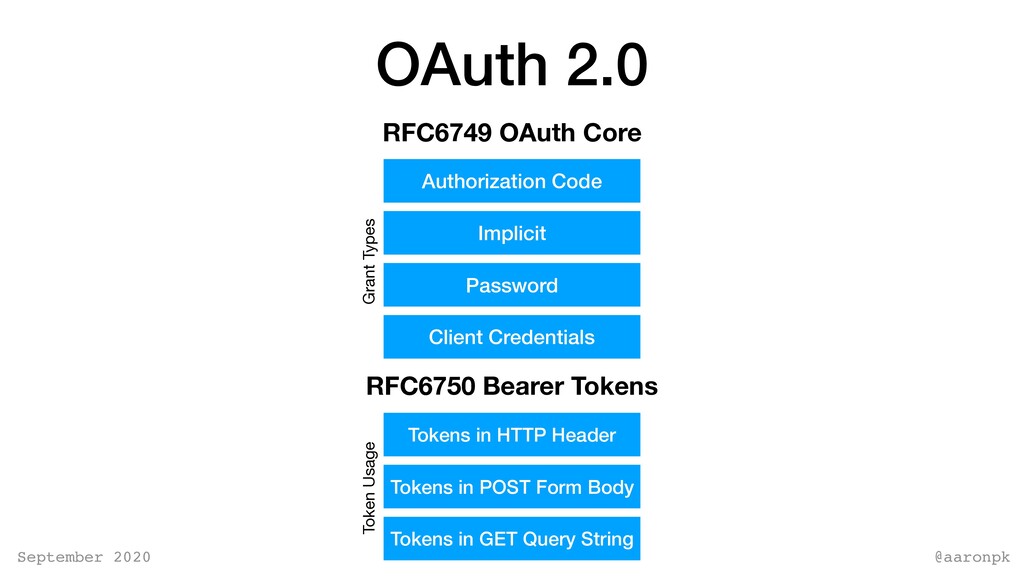
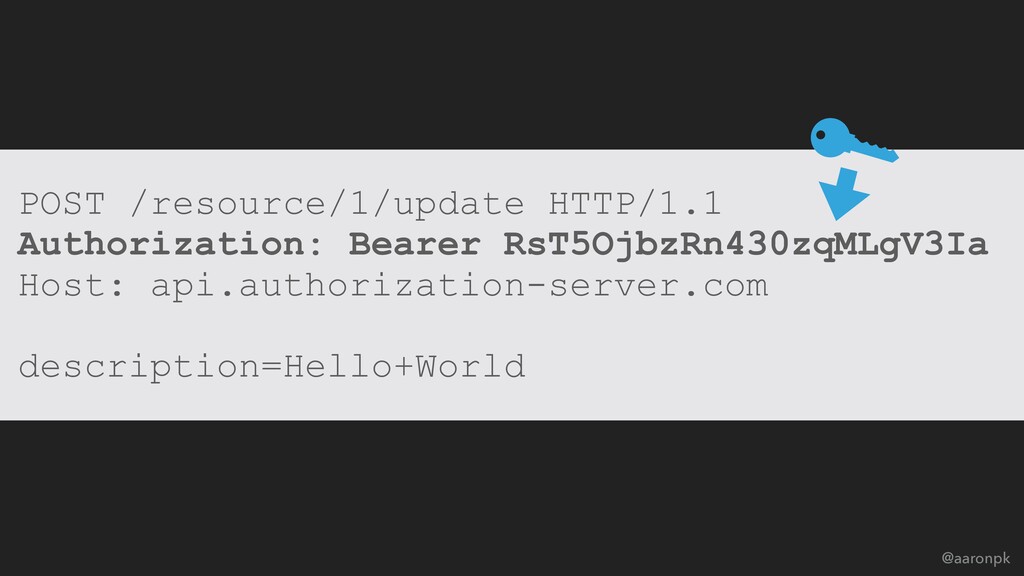
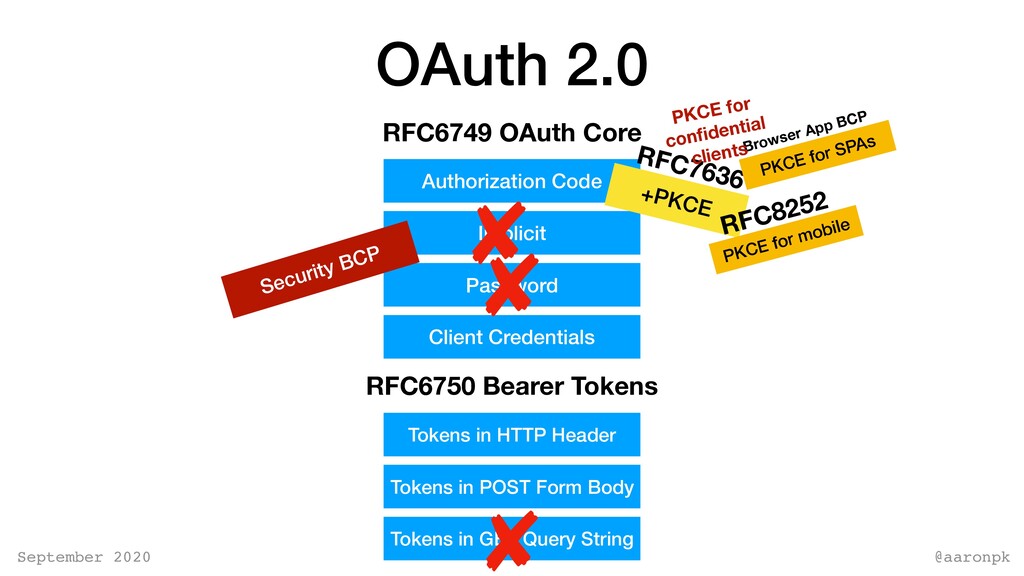
Implicit Password Client Credentials Grant Types RFC6750 Bearer Tokens Token Usage Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
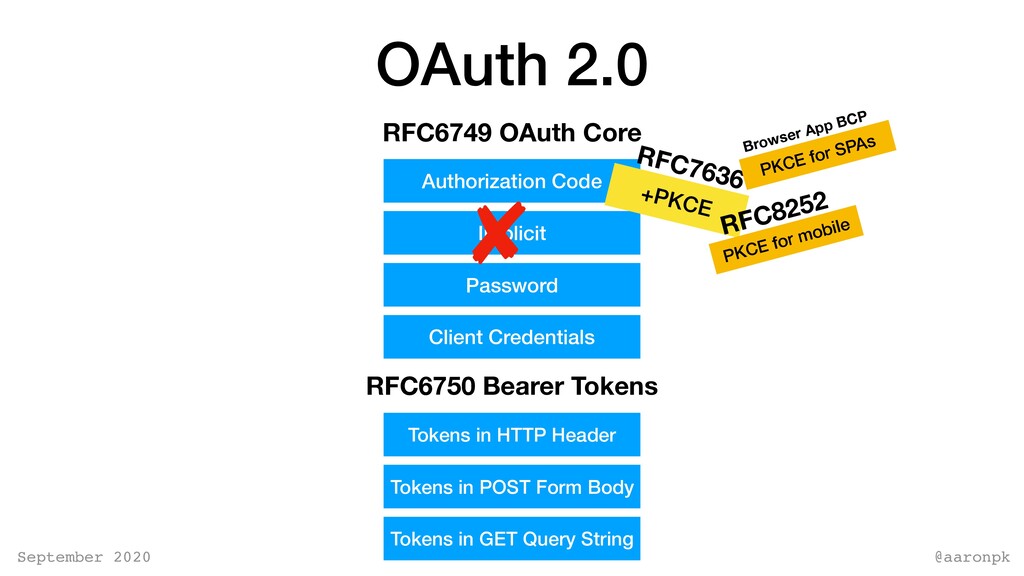
Implicit Password Client Credentials RFC6750 Bearer Tokens RFC7636 +PKCE RFC8252 PKCE for mobile Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
go to the authorization server to grant me access User: I’d like to log in to “Yelp”, it wants to access my contacts AS: Here is a temporary code the app can use App: Here is the temporary code, and my secret, please give me a token User: Here is the temporary code, please use this to get a token AS: Here is an access token! App: Please let me access this user’s data with this access token! User Agent App OAuth Server API ?
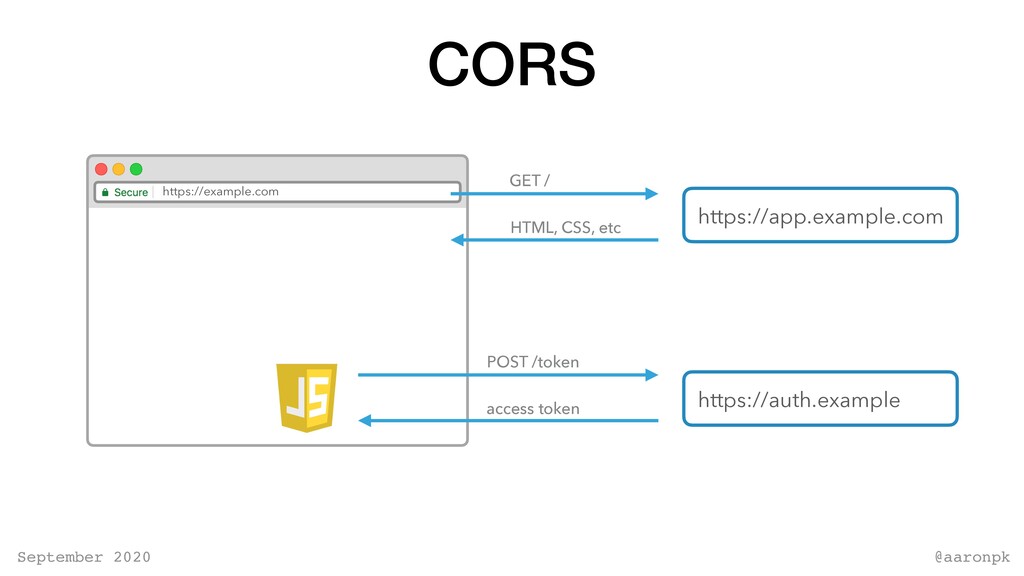
address bar The user, or malicious software, can modify the requests and responses Sent from client to server HTTPS request from client to server, so requests cannot be tampered with
Implicit Password Client Credentials RFC6750 Bearer Tokens RFC7636 +PKCE RFC8252 PKCE for mobile Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
Implicit Password Client Credentials RFC6750 Bearer Tokens RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String
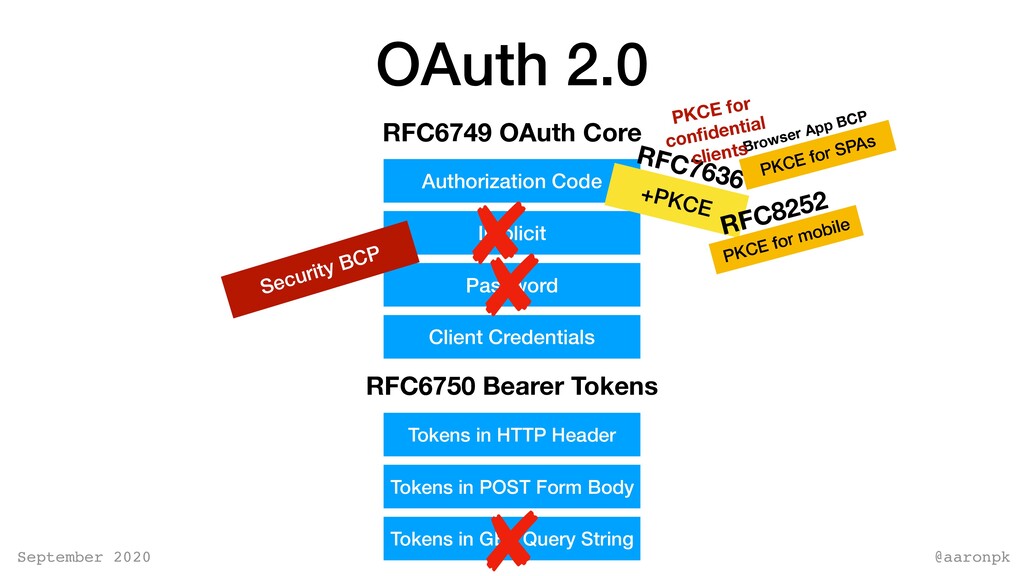
Implicit Password Client Credentials RFC6750 Bearer Tokens Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs PKCE for confidential clients Security BCP
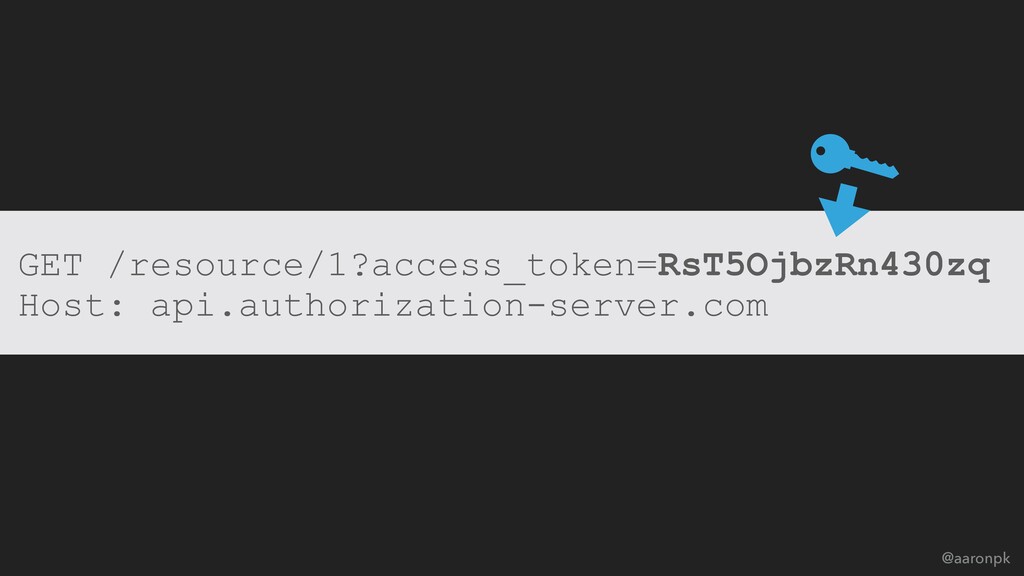
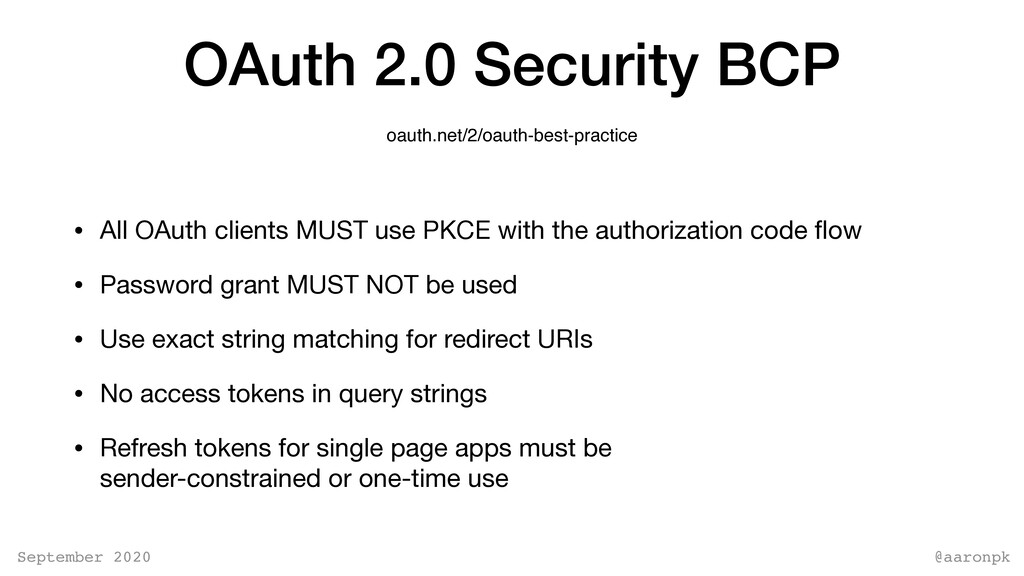
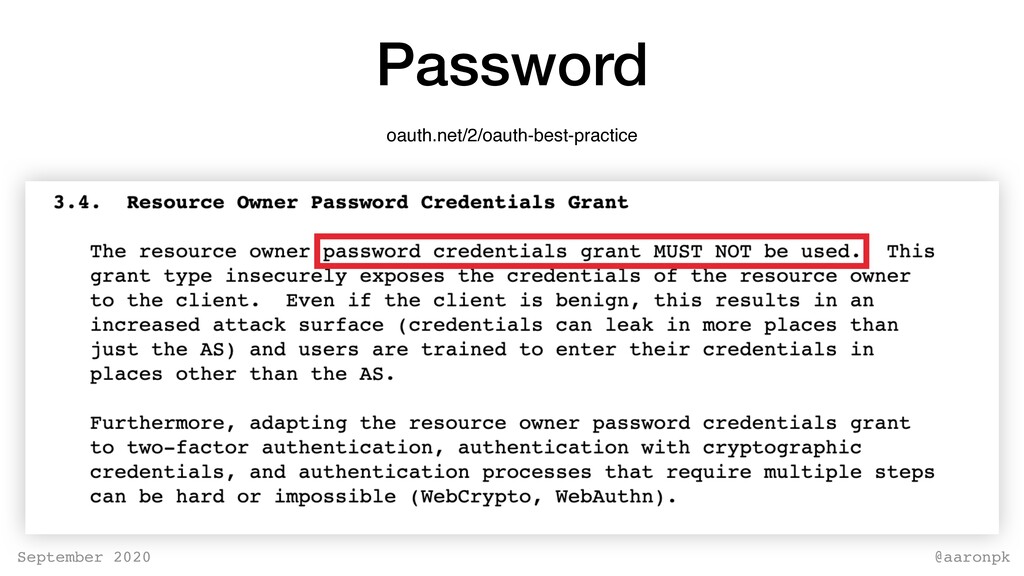
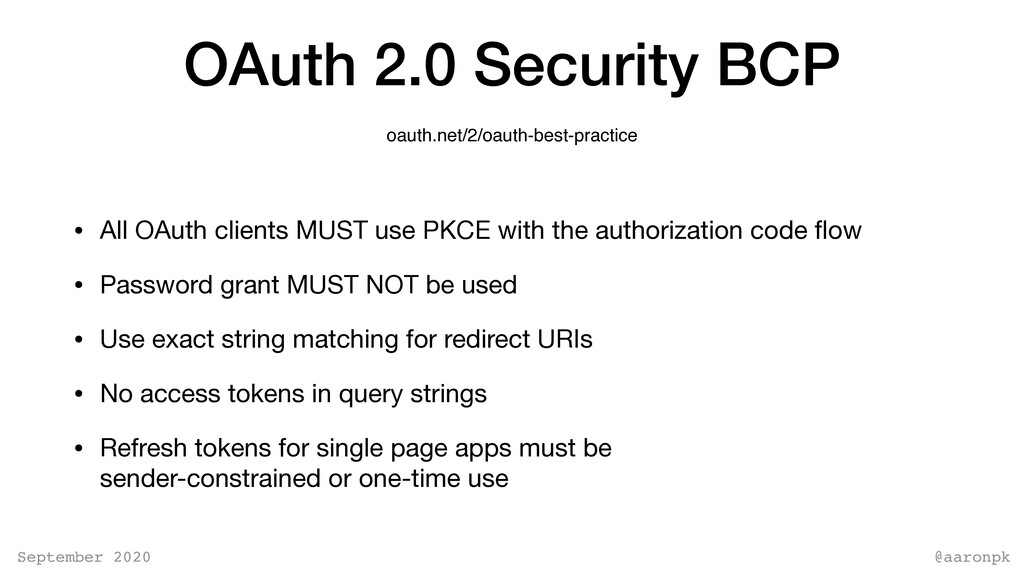
clients MUST use PKCE with the authorization code flow • Password grant MUST NOT be used • Use exact string matching for redirect URIs • No access tokens in query strings • Refresh tokens for single page apps must be sender-constrained or one-time use oauth.net/2/oauth-best-practice
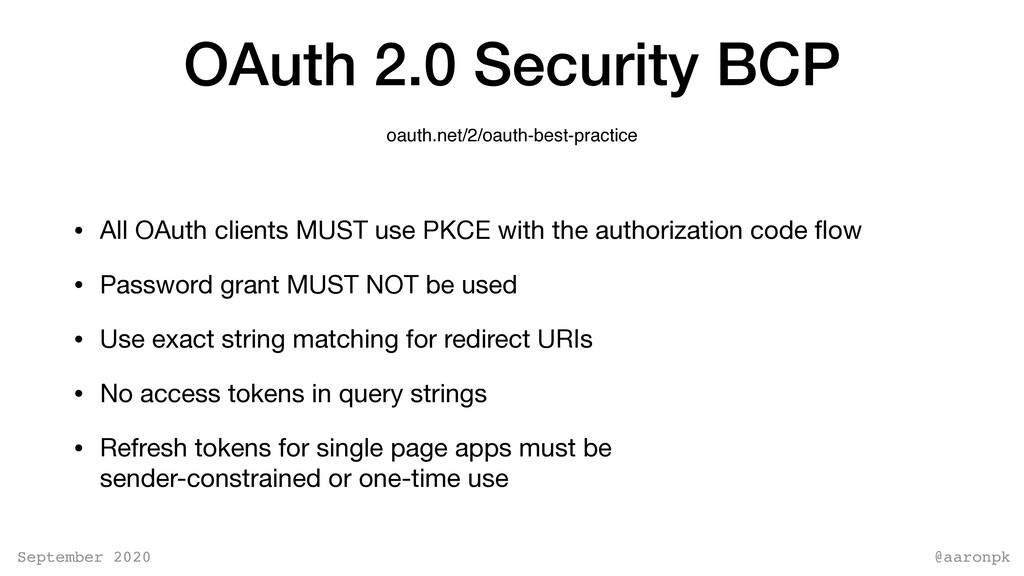
clients MUST use PKCE with the authorization code flow • Password grant MUST NOT be used • Use exact string matching for redirect URIs • No access tokens in query strings • Refresh tokens for single page apps must be sender-constrained or one-time use oauth.net/2/oauth-best-practice
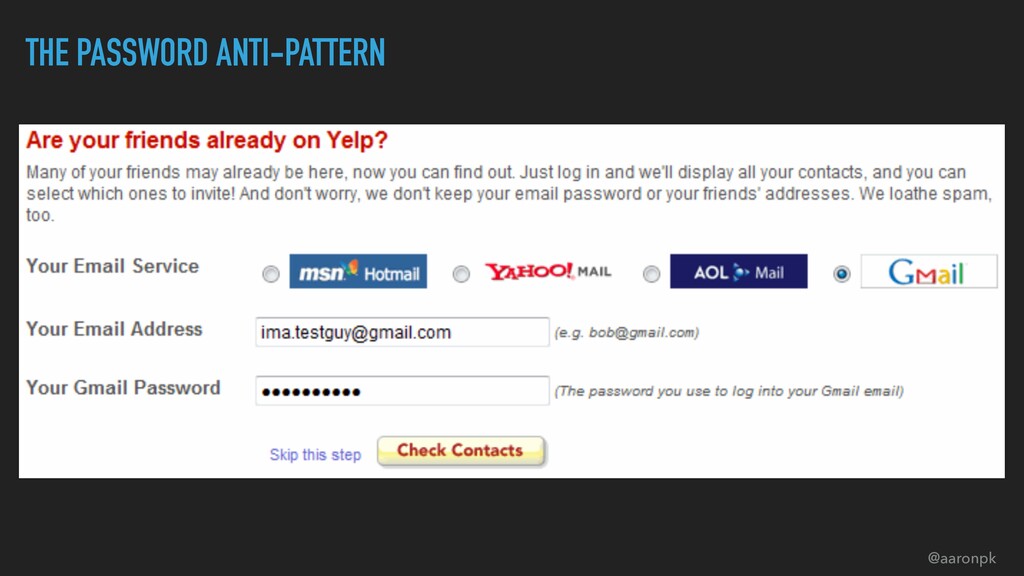
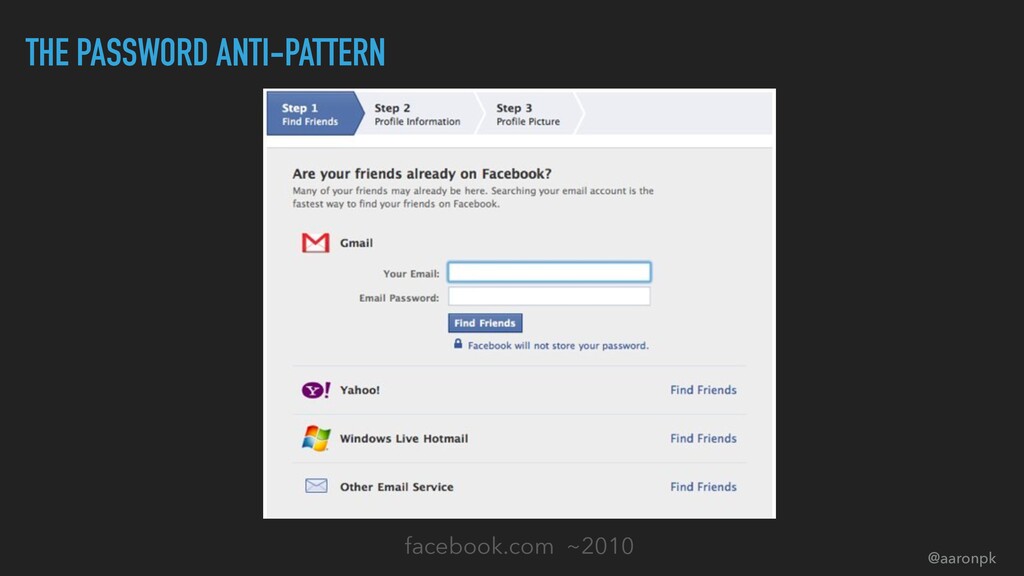
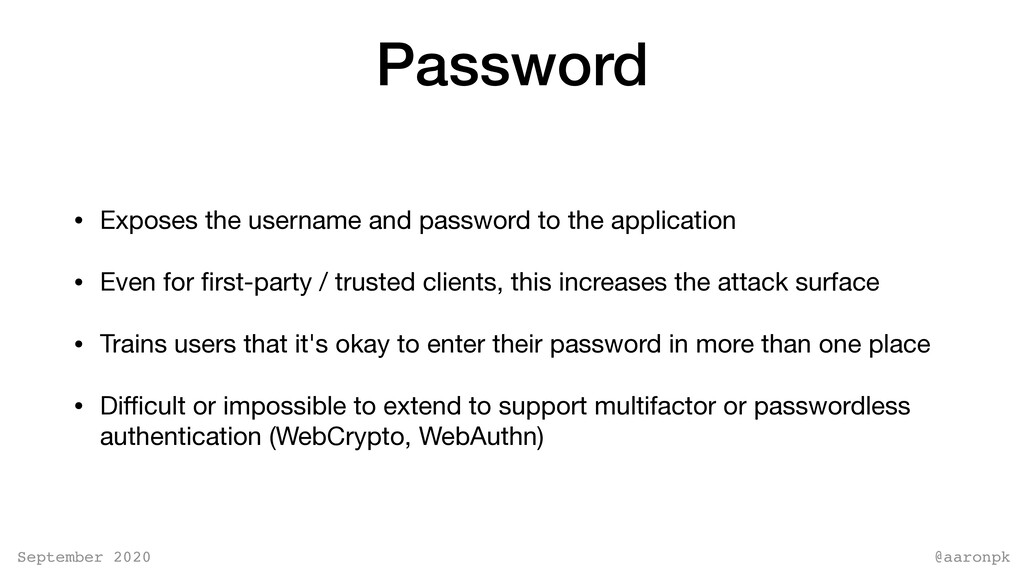
to the application • Even for first-party / trusted clients, this increases the attack surface • Trains users that it's okay to enter their password in more than one place • Difficult or impossible to extend to support multifactor or passwordless authentication (WebCrypto, WebAuthn)
clients MUST use PKCE with the authorization code flow • Password grant MUST NOT be used • Use exact string matching for redirect URIs • No access tokens in query strings • Refresh tokens for single page apps must be sender-constrained or one-time use oauth.net/2/oauth-best-practice
Implicit Password Client Credentials RFC6750 Bearer Tokens Tokens in HTTP Header Tokens in POST Form Body Tokens in GET Query String RFC7636 +PKCE RFC8252 PKCE for mobile Browser App BCP PKCE for SPAs PKCE for confidential clients Security BCP
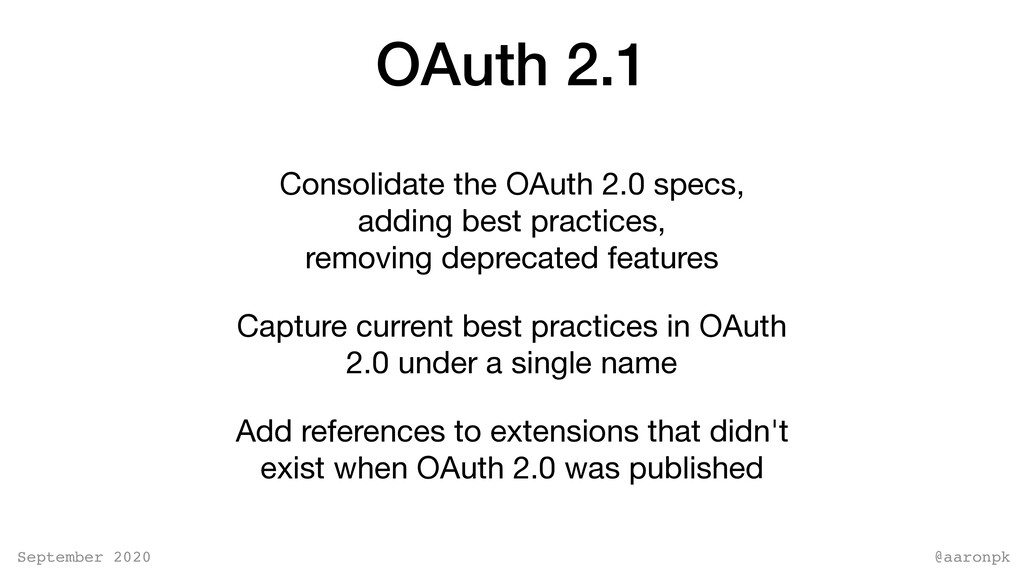
adding best practices, removing deprecated features Capture current best practices in OAuth 2.0 under a single name Add references to extensions that didn't exist when OAuth 2.0 was published
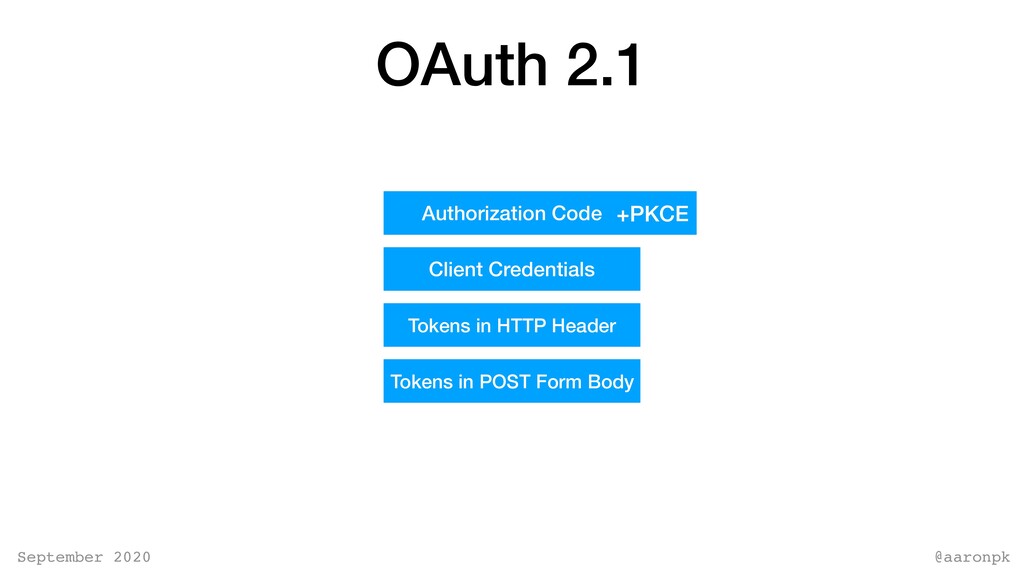
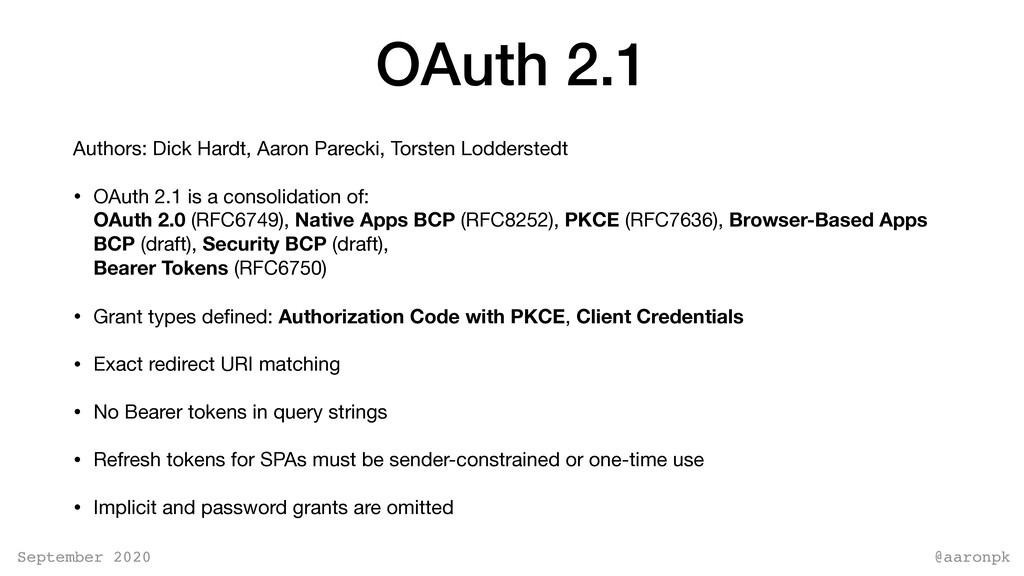
Torsten Lodderstedt • OAuth 2.1 is a consolidation of: OAuth 2.0 (RFC6749), Native Apps BCP (RFC8252), PKCE (RFC7636), Browser-Based Apps BCP (draft), Security BCP (draft), Bearer Tokens (RFC6750) • Grant types defined: Authorization Code with PKCE, Client Credentials • Exact redirect URI matching • No Bearer tokens in query strings • Refresh tokens for SPAs must be sender-constrained or one-time use • Implicit and password grants are omitted
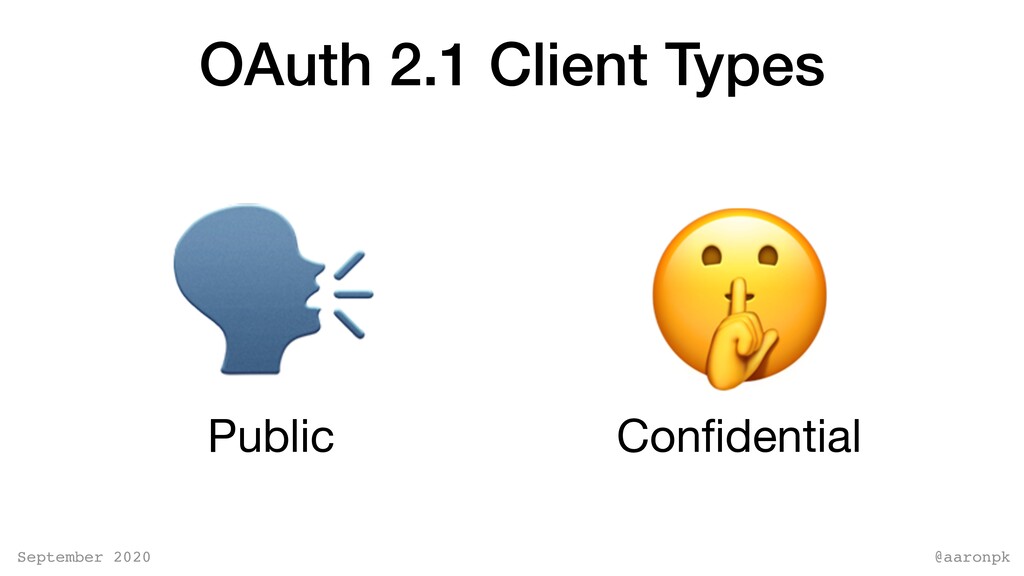
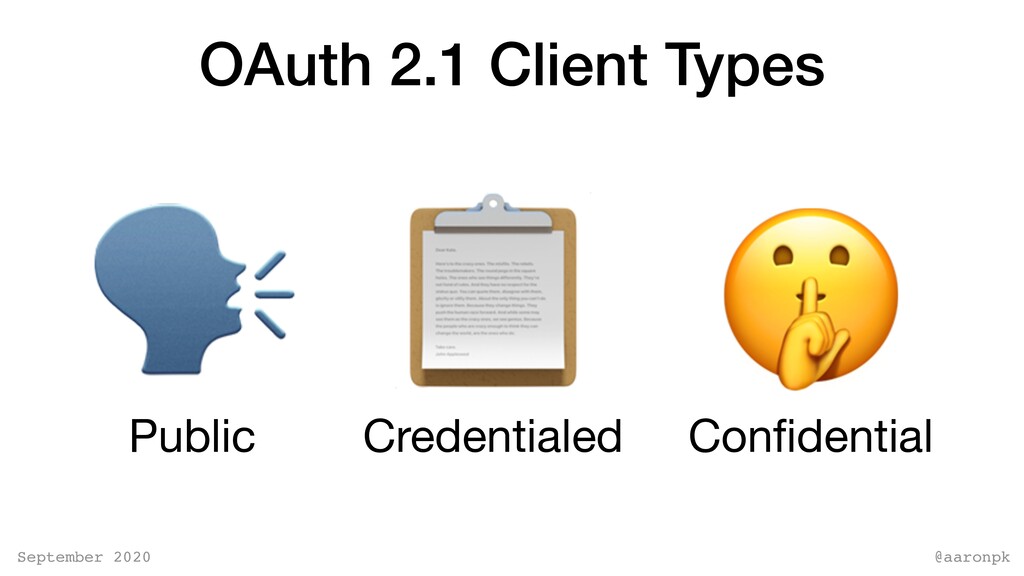
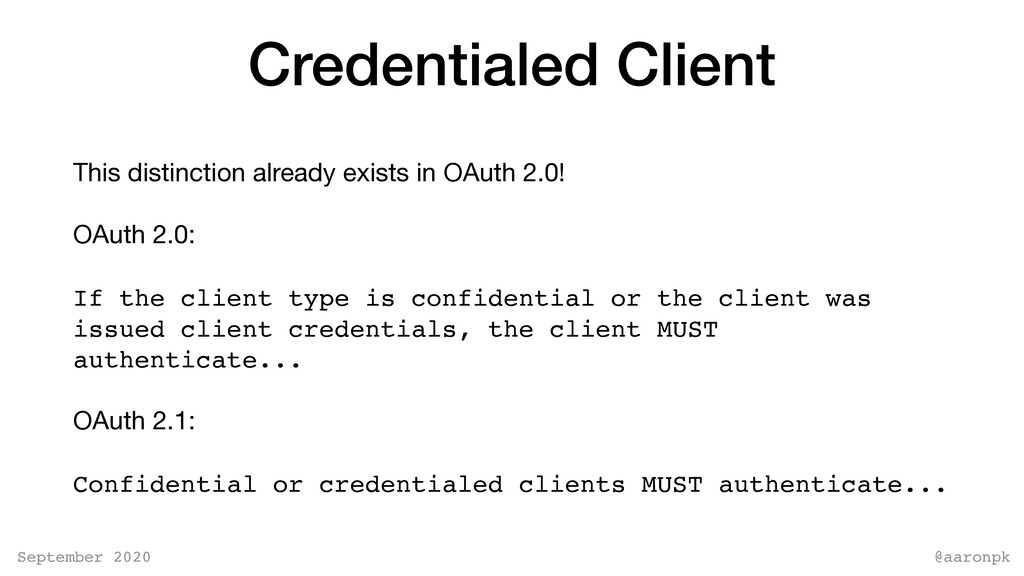
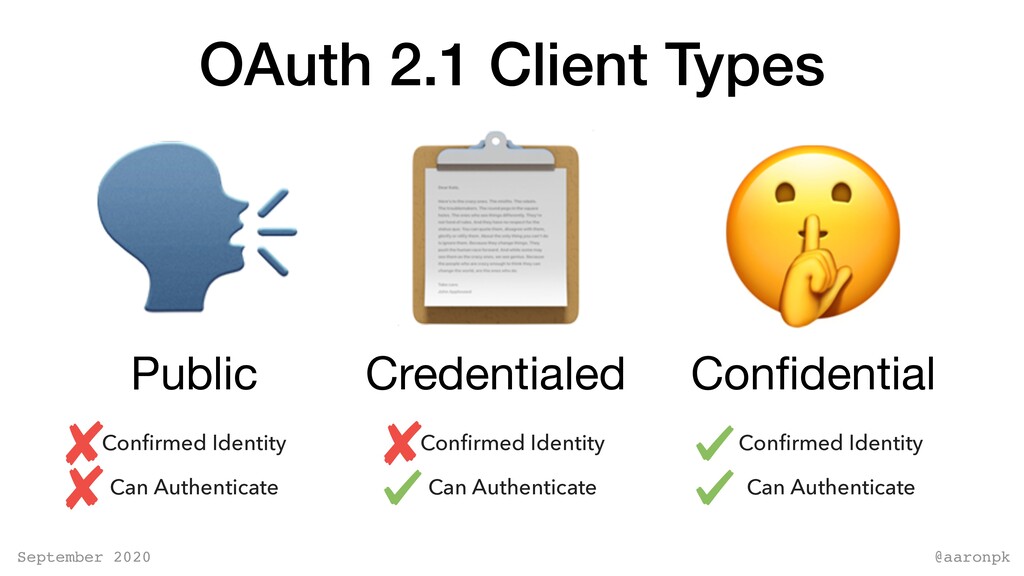
OAuth 2.0! OAuth 2.0: If the client type is confidential or the client was issued client credentials, the client MUST authenticate... OAuth 2.1: Confidential or credentialed clients MUST authenticate...


 aaronpk
 munakata
 ydah
 ginjihayashi
 atalie2m
 imuta
 sansantech
 okiyuki99
 nejumi
 masasuzu
 harutiro
 wind111
 torounit
 erikaheidi
 malarkey
 tonyrice
 codingconduct
 kimpetersen
 palkan
 ryanjones
 tamaranovitovic
 caitiem20
 chrislema
 marketingsoph
 elsirapls