Share
Embed
Transcript
16 slides
-
Choosing Targets Google Dorks Github Repos Choose VDPs Hands on
bugs over local sites .nl websites for big scope Different search engine , Different results -
OOS bugs SPF DMARC Rate Limits Dos & Ddos Phishing
User Interactions bugs In scope bugs CSRF Auth Bypass Code Injections Unauth access etc Policy and scope checking Policy Checks Reward Timeline Scope of domains Known Bugs Report format -Do Not Use single template -Plagiarisms Checks -Attack scenarios -
Finalllyyyyyy!!!! BUGS to check... CSRF : https://portswigger.net/web-security/csrf MFA issues :
Request , Response , Weak token cryptography BAC attacks : https://portswigger.net/web-security/access- control/ Info Disclosure : Wayback, Github , Directory fuzzing, Error messages , Google Dorks Exif Metadata : Stored Images , File Upload Functions , Posts 1. 2. 3. 4. 5. -
CSRF - Burpsuite extension : CSRF Scanner - Passive scanner
where function dont have token validations , We can try for easy exploits - Checking requests manually or simple burpsuite history - If tokens are there ? -> Remove token , token parameter , replace with another account token , Change request methods Ways to find... -
MFA issue - Common way - Brute forcing numericals -
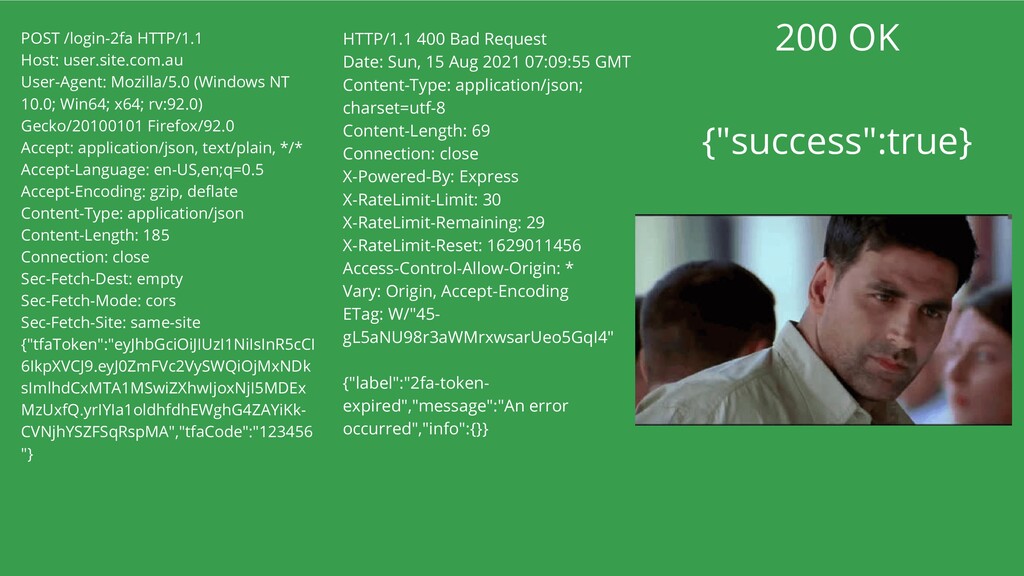
Editing request or removing requests parameters - Tampering response : eg . 400 Bad Request to 200 OK More : https://twitter.com/ADITYASHENDE17/status/12545159236684390 41?s=20 Ways to find... -
POST /login-2fa HTTP/1.1 Host: user.site.com.au User-Agent: Mozilla/5.0 (Windows NT 10.0;
Win64; x64; rv:92.0) Gecko/20100101 Firefox/92.0 Accept: application/json, text/plain, */* Accept-Language: en-US,en;q=0.5 Accept-Encoding: gzip, deflate Content-Type: application/json Content-Length: 185 Connection: close Sec-Fetch-Dest: empty Sec-Fetch-Mode: cors Sec-Fetch-Site: same-site {"tfaToken":"eyJhbGciOiJIUzI1NiIsInR5cCI 6IkpXVCJ9.eyJ0ZmFVc2VySWQiOjMxNDk sImlhdCxMTA1MSwiZXhwIjoxNjI5MDEx MzUxfQ.yrIYIa1oldhfdhEWghG4ZAYiKk- CVNjhYSZFSqRspMA","tfaCode":"123456 "} HTTP/1.1 400 Bad Request Date: Sun, 15 Aug 2021 07:09:55 GMT Content-Type: application/json; charset=utf-8 Content-Length: 69 Connection: close X-Powered-By: Express X-RateLimit-Limit: 30 X-RateLimit-Remaining: 29 X-RateLimit-Reset: 1629011456 Access-Control-Allow-Origin: * Vary: Origin, Accept-Encoding ETag: W/"45- gL5aNU98r3aWMrxwsarUeo5GqI4" {"label":"2fa-token- expired","message":"An error occurred","info":{}} 200 OK {"success":true} -
Broken Access Control: Abusing the mechanism of webapp where it
can leads to Infomration Disclosure , Unauth access, High privileges by low access level user More : https://adityashende17.medium.com/idor-to-information-disclosure-admin- account-takeover-6aa96798c70b -
Github Recon = Juicy Information https://speakerdeck.com/aditya45/github-recon-and-way- to-process - Craft own
dorks - example : "password" for login - Repo authority -
Final things Don't rush Master in one . Practice all
Scope and policies are important Think out of the box