Share
Embed
Catching up with Windows Azure Active Directory
Vorig jaar was Windows Azure AD (WAAD) nog in beta. Een jaar verder is WAAD niet alleen officieel gereleased, maar heeft het ook al allerlei uitbreidingen gekregen. Als je er vorig jaar niet bij was, of een update wilt krijgen over de
stand van zaken bij WAAD, kom dan naar deze sessie.
Alex Thissen
April 29, 2014
Transcript
34 slides
-
Laat ons weten wat u vindt van deze sessie! Vul
de evaluatie in via www.techdaysapp.nl en maak kans op een van de 20 prijzen*. Prijswinnaars worden bekend gemaakt via Twitter (#TechDaysNL). Gebruik hiervoor de code op uw badge. Let us know how you feel about this session! Give your feedback via www.techdaysapp.nl and possibly win one of the 20 prizes*. Winners will be announced via Twitter (#TechDaysNL). Use your personal code on your badge. * Over de uitslag kan niet worden gecorrespondeerd, prijzen zijn voorbeelden – All results are final, prizes are examples -
Agenda Recap of last year’s WAAD New features in Azure
AD AAD Premium Programming with ADAL Library Summary Questions and answers -
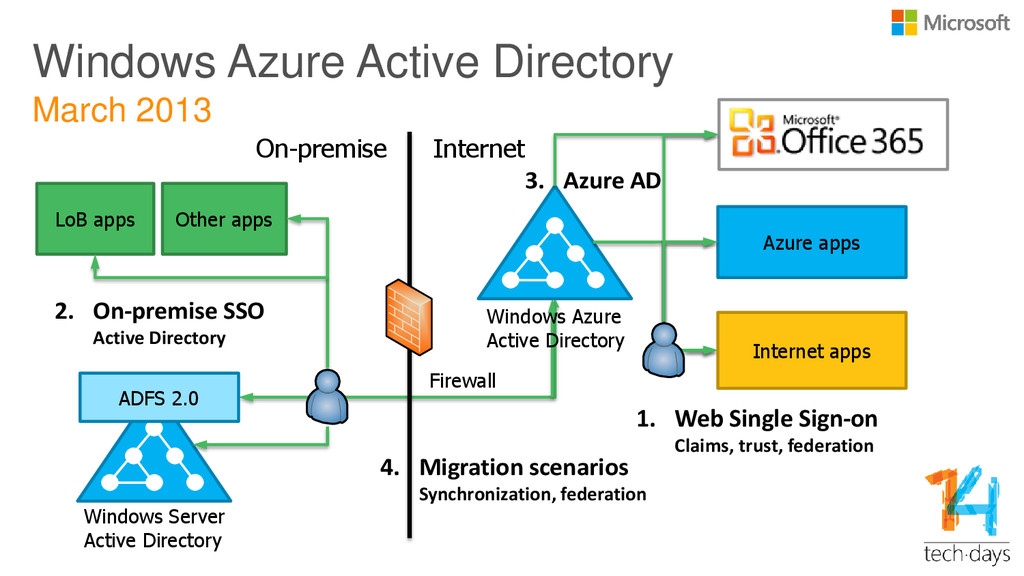
Windows Azure Active Directory March 2013 Azure apps Internet apps
ADFS 2.0 Firewall Windows Azure Active Directory LoB apps Windows Server Active Directory On-premise Internet Other apps 1. Web Single Sign-on Claims, trust, federation 2. On-premise SSO Active Directory 3. Azure AD 4. Migration scenarios Synchronization, federation -
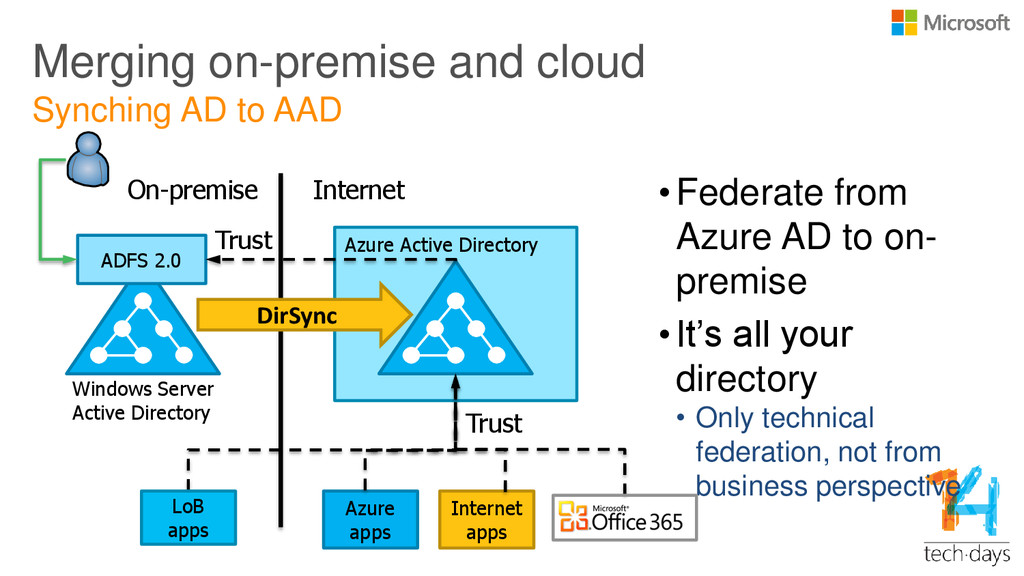
Azure Active Directory Merging on-premise and cloud •Federate from Azure
AD to on- premise •It’s all your directory • Only technical federation, not from business perspective Synching AD to AAD Windows Server Active Directory On-premise Internet DirSync Azure apps Internet apps LoB apps Trust ADFS 2.0 Trust -
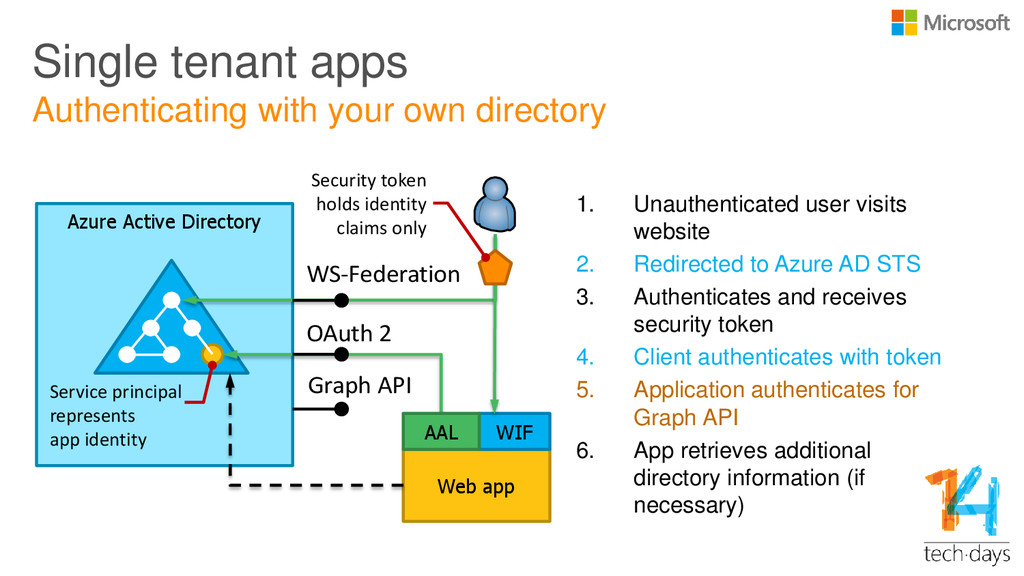
Azure Active Directory Single tenant apps 1. Unauthenticated user visits
website 2. Redirected to Azure AD STS 3. Authenticates and receives security token 4. Client authenticates with token 5. Application authenticates for Graph API 6. App retrieves additional directory information (if necessary) Authenticating with your own directory Web app OAuth 2 WS-Federation WIF Security token holds identity claims only AAL Service principal represents app identity Graph API -
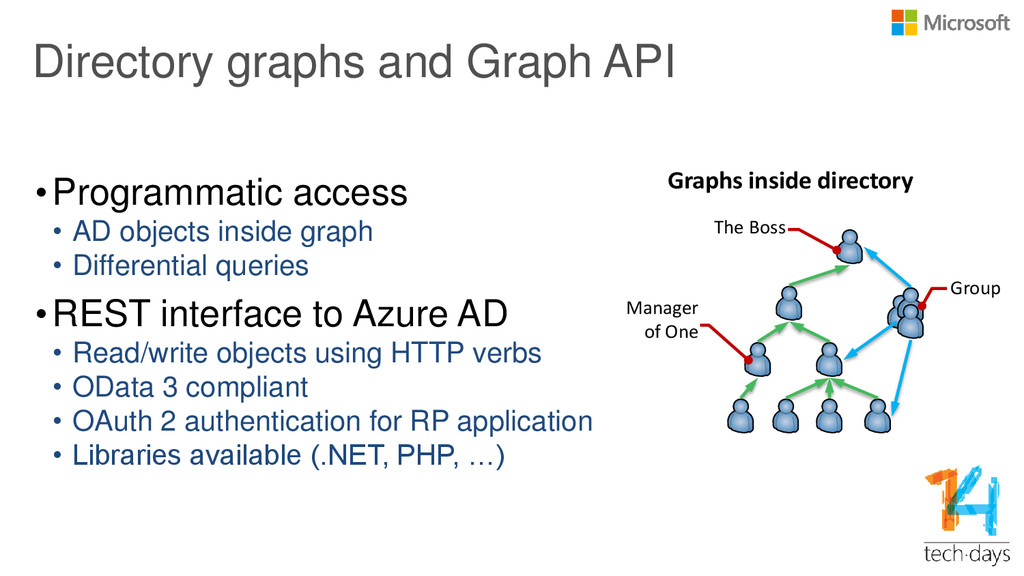
Directory graphs and Graph API •Programmatic access • AD objects
inside graph • Differential queries •REST interface to Azure AD • Read/write objects using HTTP verbs • OData 3 compliant • OAuth 2 authentication for RP application • Libraries available (.NET, PHP, …) The Boss Manager of One Graphs inside directory Group -
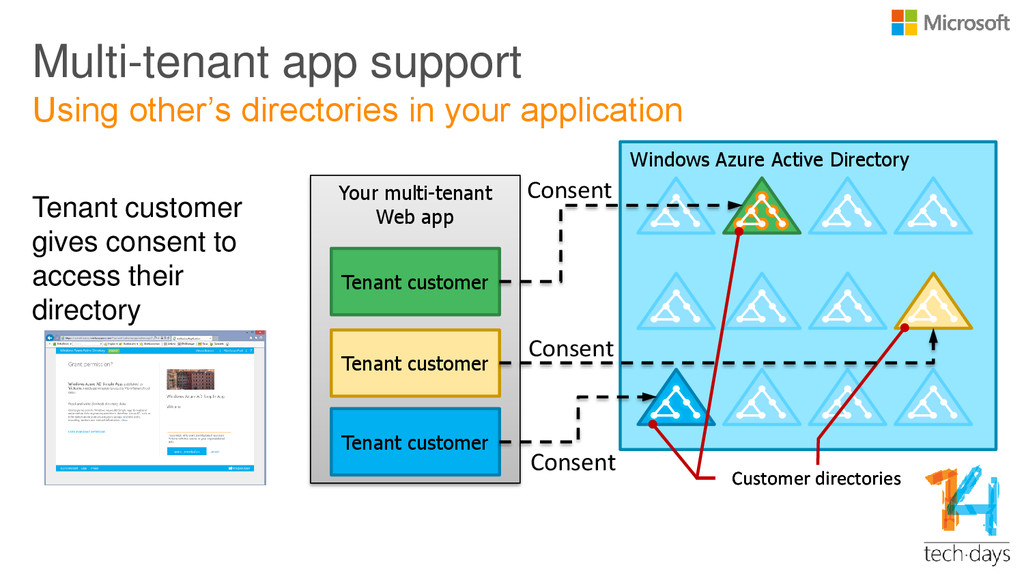
Multi-tenant app support Tenant customer gives consent to access their
directory Using other’s directories in your application Windows Azure Active Directory Customer directories Your multi-tenant Web app Tenant customer Tenant customer Tenant customer Customer directories Customer directories Consent Consent Consent -
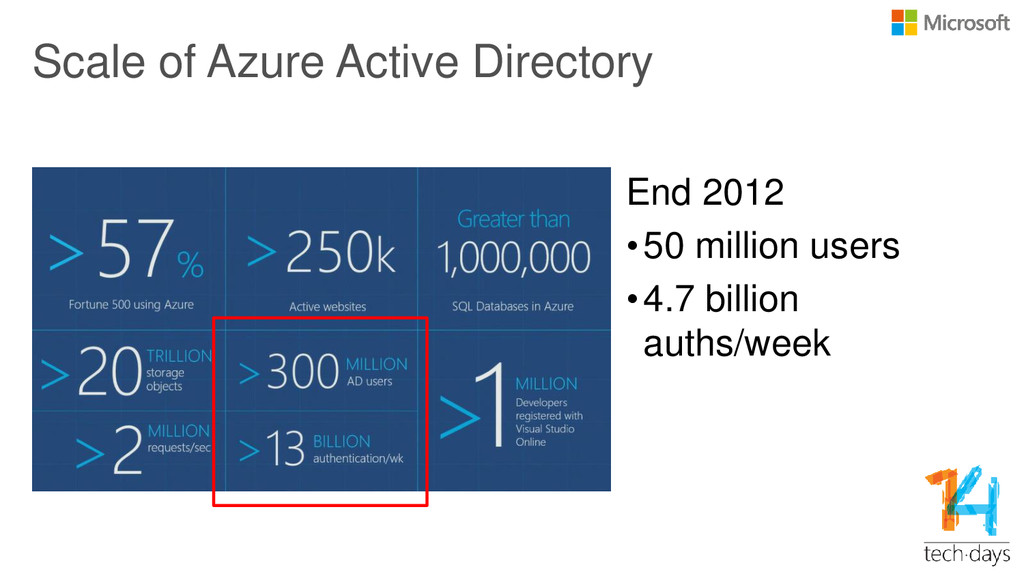
Scale of Azure Active Directory End 2012 •50 million users
•4.7 billion auths/week -
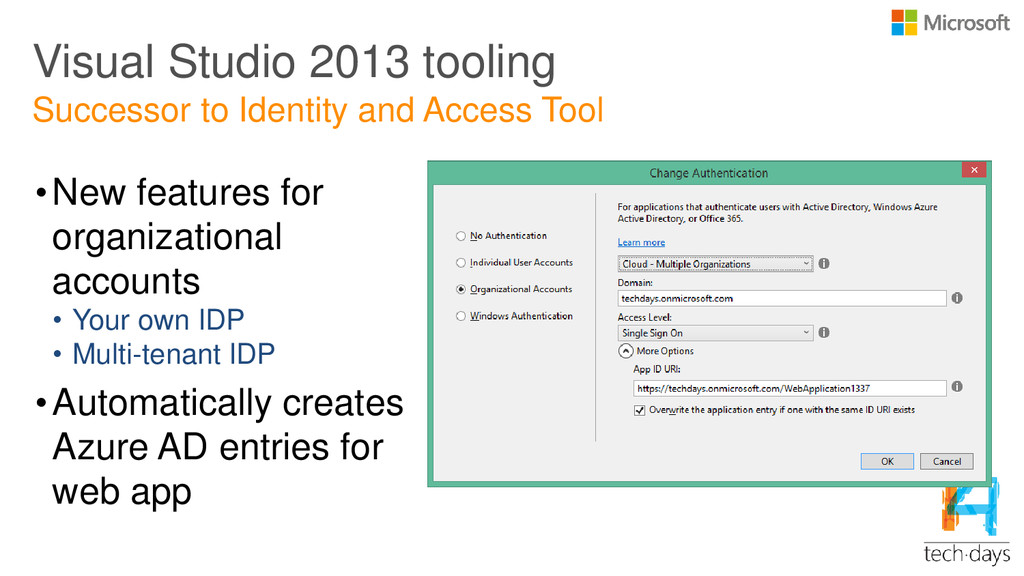
Visual Studio 2013 tooling •New features for organizational accounts •
Your own IDP • Multi-tenant IDP •Automatically creates Azure AD entries for web app Successor to Identity and Access Tool -
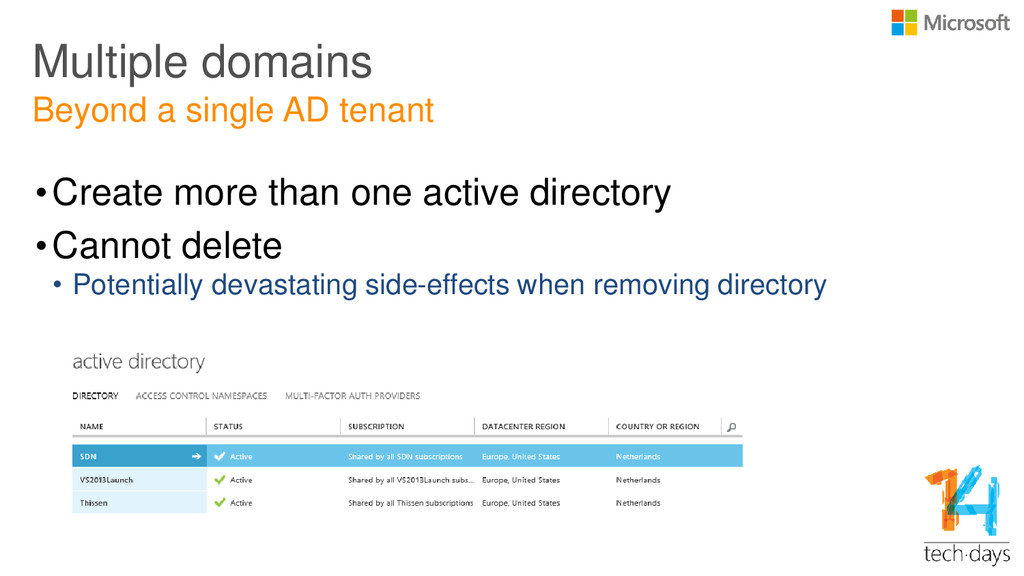
Multiple domains •Create more than one active directory •Cannot delete
• Potentially devastating side-effects when removing directory Beyond a single AD tenant -
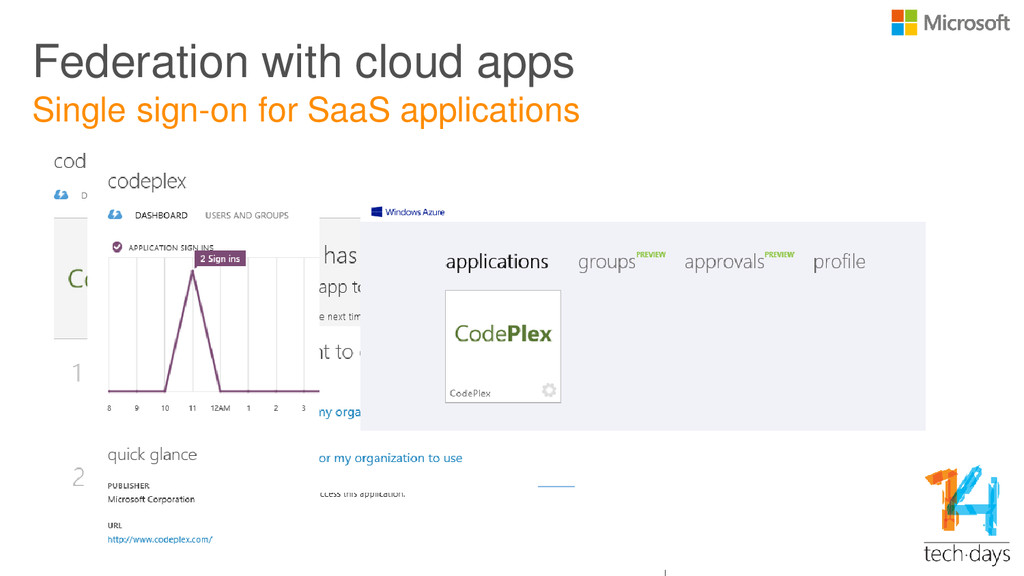
Federation with cloud apps •Pick SaaS cloud app from App
Gallery •Assign users to app Single sign-on for SaaS applications -
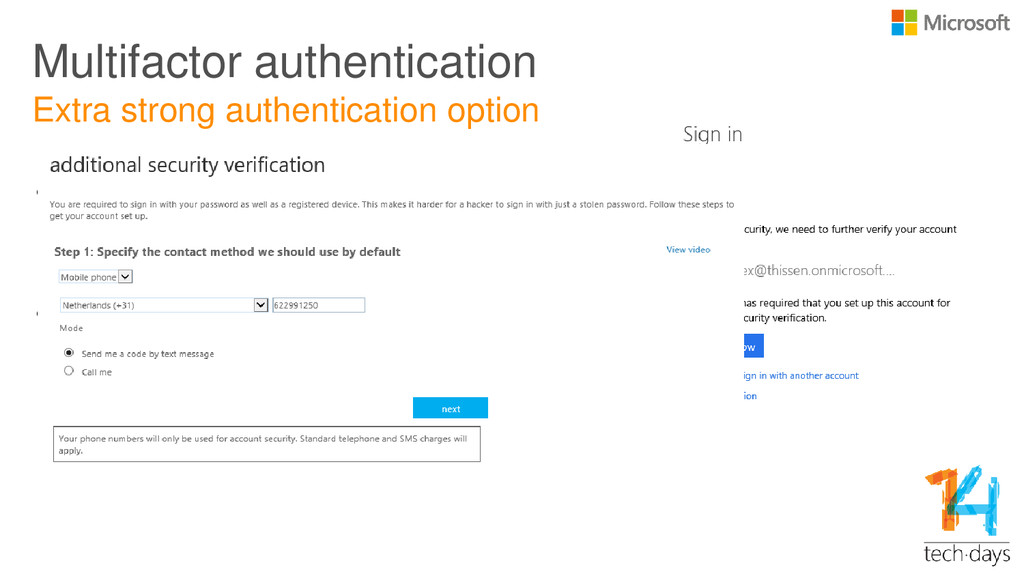
Multifactor authentication •One-time password using phone • Code sent in
SMS text message • Voice call with DTFM approval •Payment model per user or per authentication Extra strong authentication option -
Registering apps and APIs •Configure unique identifiers and characteristics •
Resources expose permissions •Define access of apps to APIs • Client apps consume resources and require permissions -
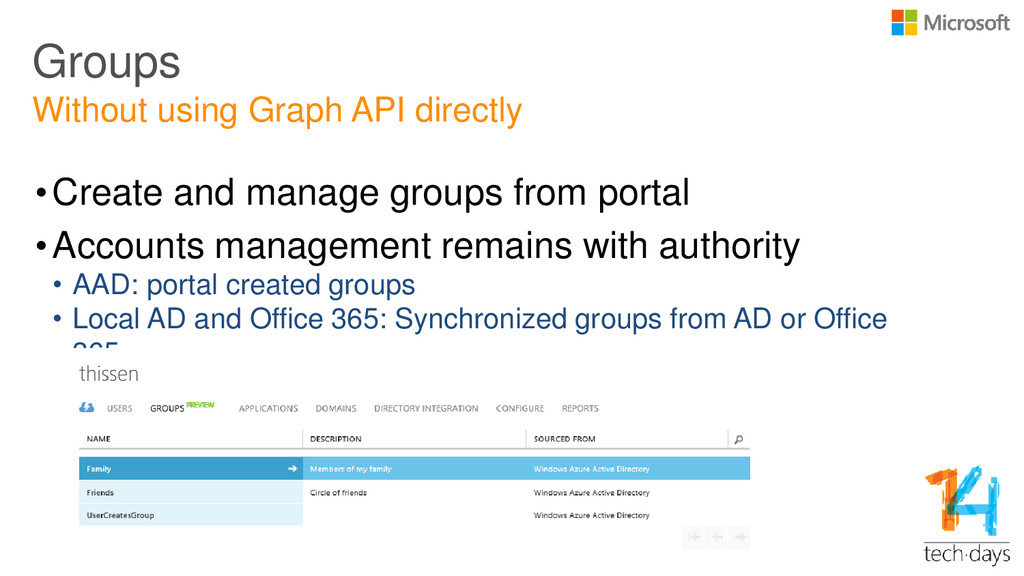
Groups •Create and manage groups from portal •Accounts management remains
with authority • AAD: portal created groups • Local AD and Office 365: Synchronized groups from AD or Office 365 Without using Graph API directly -
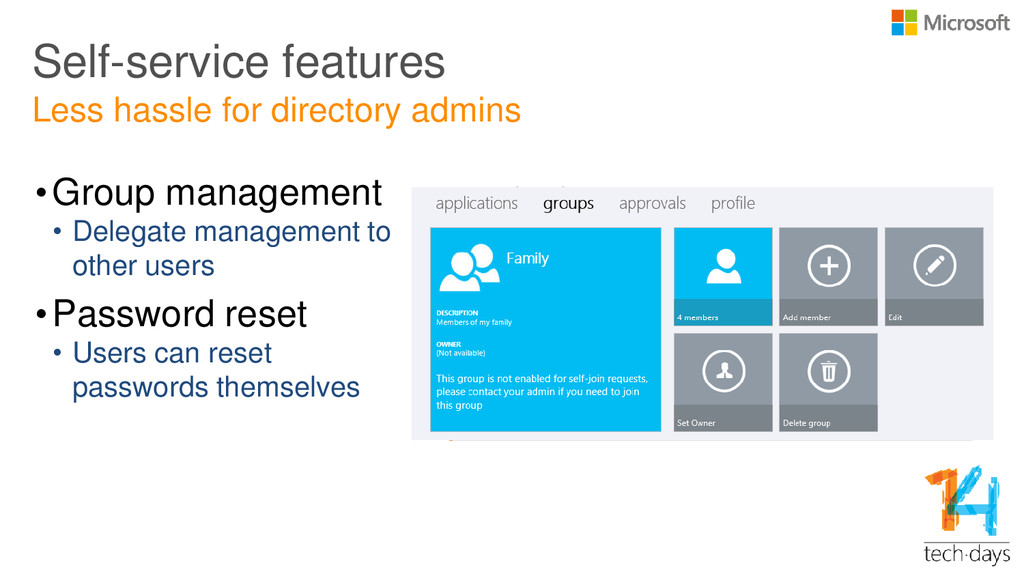
Self-service features •Group management • Delegate management to other users
•Password reset • Users can reset passwords themselves Less hassle for directory admins -
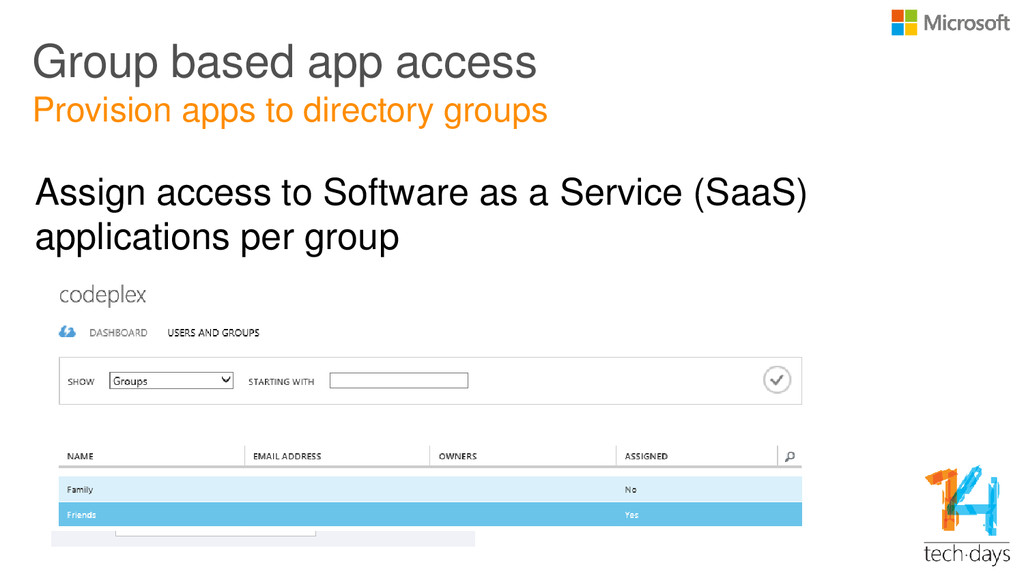
Group based app access Assign access to Software as a
Service (SaaS) applications per group Provision apps to directory groups -
Login UI branding •Customize look and feel • Sign-in page
• Access Panel pages •Available when tenant is known Company styling at Azure AD authentication -
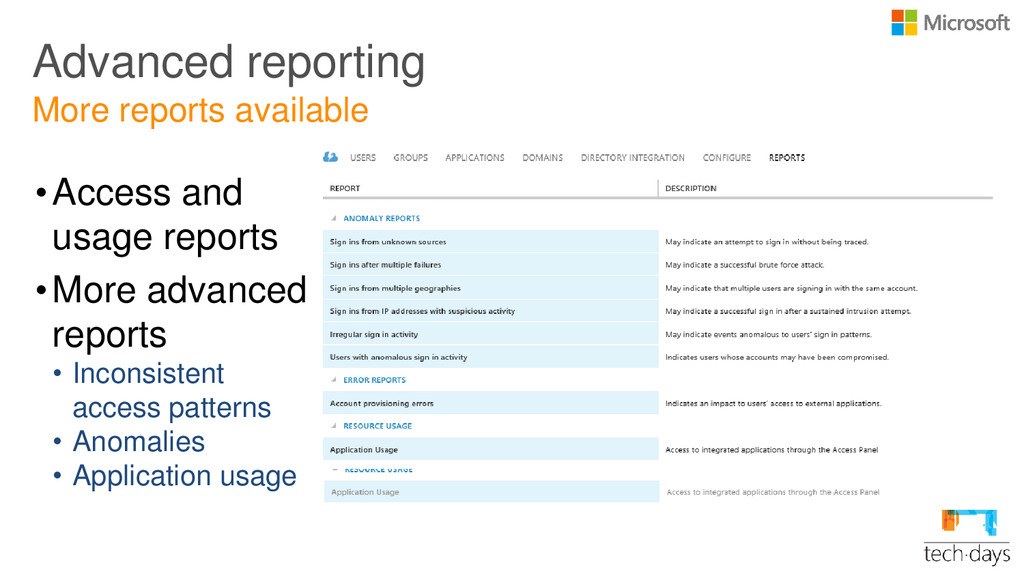
Advanced reporting •Access and usage reports •More advanced reports •
Inconsistent access patterns • Anomalies • Application usage More reports available -
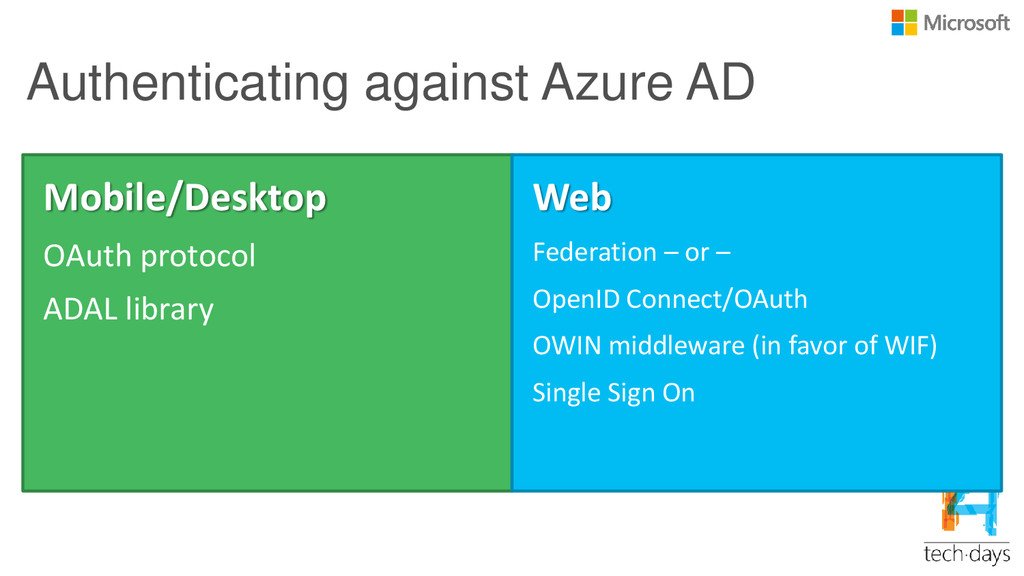
Authenticating against Azure AD Mobile/Desktop OAuth protocol ADAL library Web
Federation – or – OpenID Connect/OAuth OWIN middleware (in favor of WIF) Single Sign On -
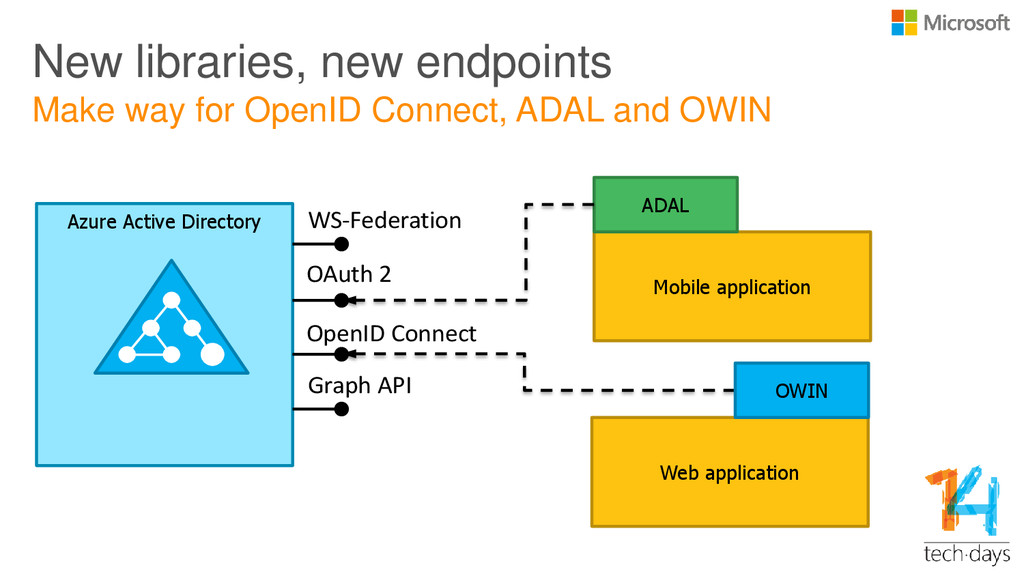
New libraries, new endpoints Make way for OpenID Connect, ADAL
and OWIN Azure Active Directory Web application OpenID Connect OAuth 2 OWIN Graph API Mobile application ADAL WS-Federation -
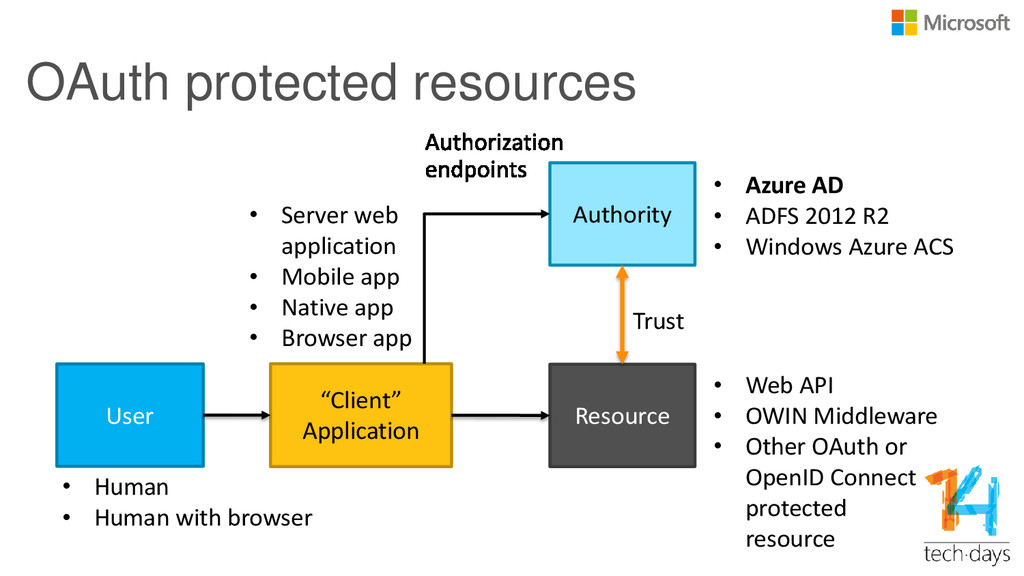
OAuth protected resources Authority • Azure AD • ADFS 2012
R2 • Windows Azure ACS Resource • Web API • OWIN Middleware • Other OAuth or OpenID Connect protected resource “Client” Application User • Human • Human with browser • Server web application • Mobile app • Native app • Browser app Trust -
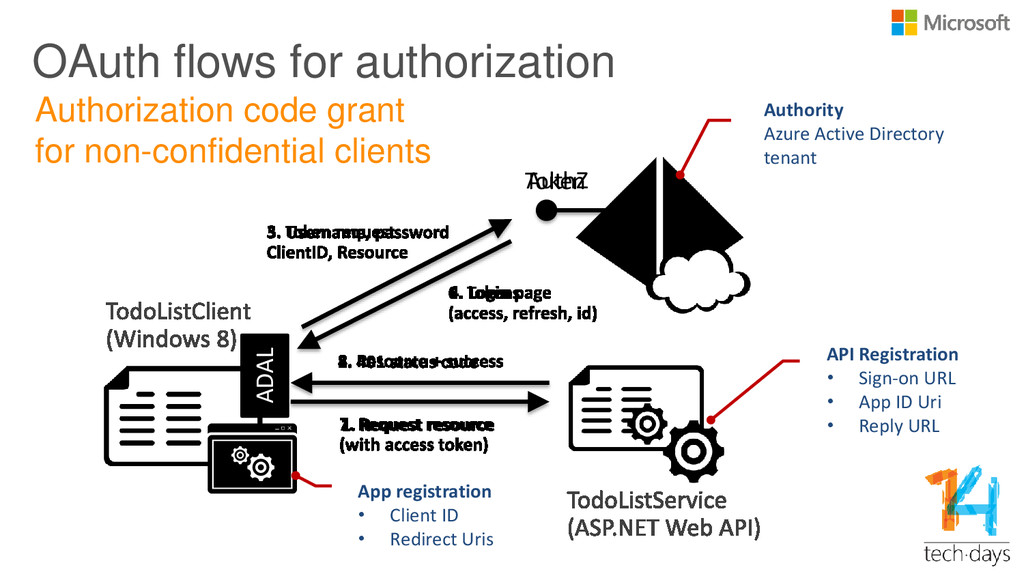
OAuth flows for authorization Authorization code grant for non-confidential clients
ADAL Authority Azure Active Directory tenant API Registration • Sign-on URL • App ID Uri • Reply URL App registration • Client ID • Redirect Uris AuthZ Token -
ADAL Library •Abstracts away most protocol considerations •Handles tokens persistence
and refresh •Exposes capabilities of WAAD and ADFS “Help developers to take advantage of Active Directory for enabling client apps to access protected resources.” -
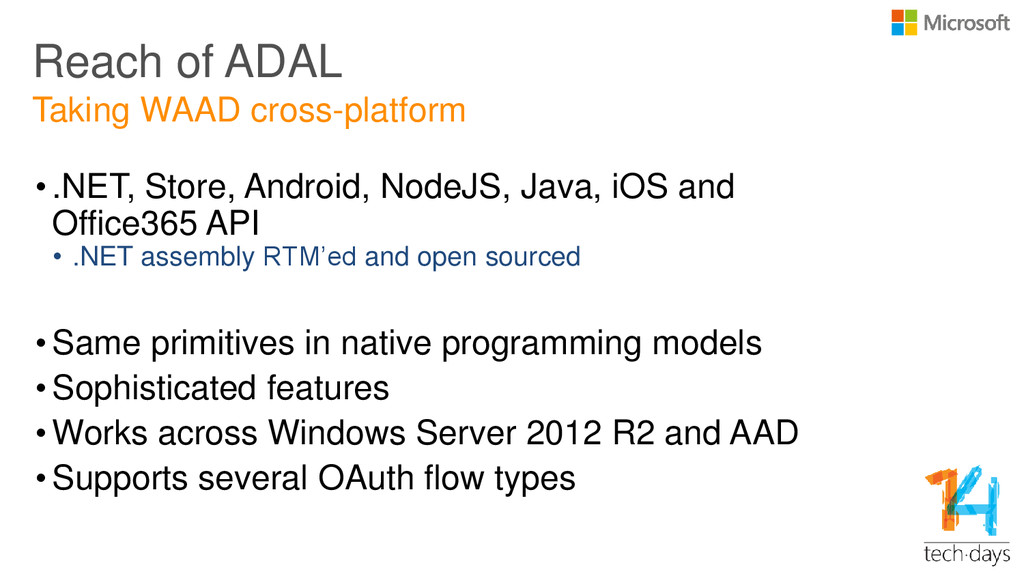
Reach of ADAL • .NET, Store, Android, NodeJS, Java, iOS
and Office365 API • .NET assembly RTM’ed and open sourced • Same primitives in native programming models • Sophisticated features • Works across Windows Server 2012 R2 and AAD • Supports several OAuth flow types Taking WAAD cross-platform -
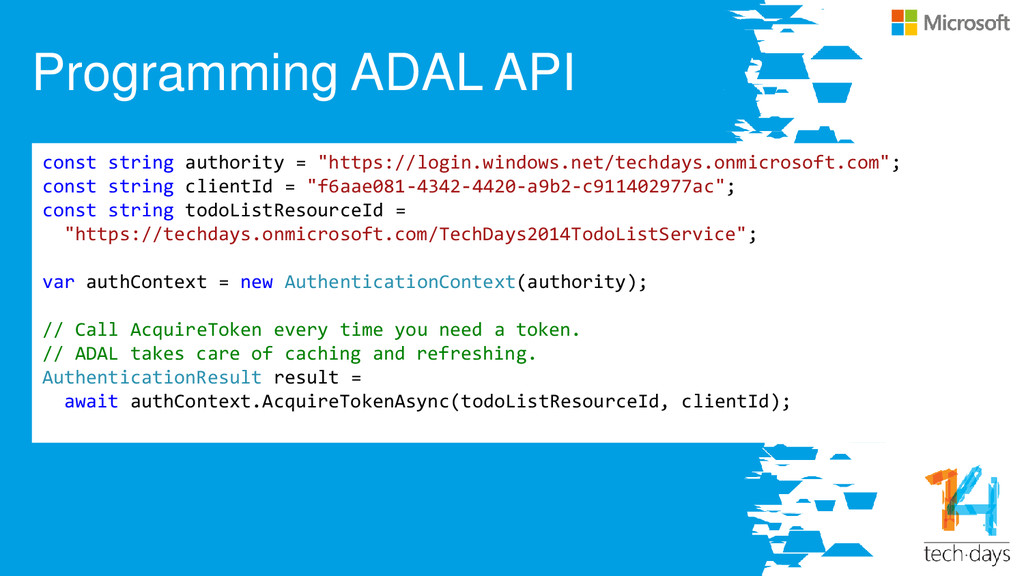
Programming ADAL API const string authority = "https://login.windows.net/techdays.onmicrosoft.com"; const string
clientId = "f6aae081-4342-4420-a9b2-c911402977ac"; const string todoListResourceId = "https://techdays.onmicrosoft.com/TechDays2014TodoListService"; var authContext = new AuthenticationContext(authority); // Call AcquireToken every time you need a token. // ADAL takes care of caching and refreshing. AuthenticationResult result = await authContext.AcquireTokenAsync(todoListResourceId, clientId); -
Summary •Azure Active Directory has grown over a year •OWIN
is new alternative to WIF for AAD in web apps •ADAL library for native, non-web apps •Tooling and SDKs allow cross-platform use of AAD Key takeaways -
Laat ons weten wat u vindt van deze sessie! Vul
de evaluatie in via www.techdaysapp.nl en maak kans op een van de 20 prijzen*. Prijswinnaars worden bekend gemaakt via Twitter (#TechDaysNL). Gebruik hiervoor de code op uw badge. Let us know how you feel about this session! Give your feedback via www.techdaysapp.nl and possibly win one of the 20 prizes*. Winners will be announced via Twitter (#TechDaysNL). Use your personal code on your badge. * Over de uitslag kan niet worden gecorrespondeerd, prijzen zijn voorbeelden – All results are final, prizes are examples