Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Step by step AWS Cloud Hacking
Search
Sponsored
·
SiteGround - Reliable hosting with speed, security, and support you can count on.
→
andresriancho
September 25, 2020
Technology
650
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Step by step AWS Cloud Hacking
andresriancho
September 25, 2020
More Decks by andresriancho
See All by andresriancho
Step by step AWS Cloud Hacking
andresriancho
2
3k
Internet-Scale analysis of AWS Cognito Security
andresriancho
1
13k
Threat Modelling
andresriancho
0
1.7k
Automated Security Analysis AWS Clouds
andresriancho
1
3.4k
Injecting into URLs / Breaking URL-Encoding
andresriancho
0
290
Galería de Fallos en Unicornios
andresriancho
1
270
Esoteric Web Application Vulnerabilities
andresriancho
0
1.2k
String Compare Timing Attacks
andresriancho
0
700
Timing Attacks
andresriancho
1
450
Other Decks in Technology
See All in Technology
LLM-as-a-Judgeは本当に信頼できるのか――評価器を評価する話
taka_aki
3
1.1k
Devin プロモコードの受け取りと適用(2026.10.27)
kinopeee
0
490
Teaching Python with three kinds of AI
reuven
0
120
DevelopersIO2026 -バックアップは“消されないこと”が9割-
yoshida0129
0
400
渡米前の準備を制す!re:Invent 2026徹底準備術 / The Ultimate Preparation Guide for re:Invent 2026
yuj1osm
1
230
外国人エンジニアがVueプロトタイプで仕様を合わせている話 / Vue Fes Japan 2026 LT
eluwing
0
170
React改造してみた
tsukina_7mochi
0
160
Metadata - Section 2: Simple Metadata & Meta Tags
mohab1
0
140
野良MCPサーバーを排除せよ!MCPサーバーのガバナンス
yukiogawa
1
240
「社外イベント=意識高い」の壁を壊せ!元々無関心だった僕らが部内で社外イベントを民主化して15人を連れ出すまで
say_no_w
0
130
企画を Software Factory-ready にする——開発が高速になったとき、PdMの仕事はどう変わったか
yachibit
1
270
導入から定着へ ~コーディングエージェントを日常業務に組み込む実践知~
yukisakai1225
0
230
Featured
See All Featured
CoffeeScript is Beautiful & I Never Want to Write Plain JavaScript Again
sstephenson
162
16k
DevOps and Value Stream Thinking: Enabling flow, efficiency and business value
helenjbeal
2
410
Paper Plane
katiecoart
PRO
5
54k
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Navigating Algorithm Shifts & AI Overviews - #SMXNext
aleyda
1
1.7k
How to Create Impact in a Changing Tech Landscape [PerfNow 2023]
tammyeverts
56
3.5k
Product Roadmaps are Hard
iamctodd
55
13k
AI in Enterprises - Java and Open Source to the Rescue
ivargrimstad
0
1.6k
Building Adaptive Systems
keathley
44
3.3k
Automating Front-end Workflow
addyosmani
1370
210k
Save Time (by Creating Custom Rails Generators)
garrettdimon
PRO
33
5.4k
Music & Morning Musume
bryan
48
7.5k
Transcript
Ekoparty 2020 Andrés Riancho
2
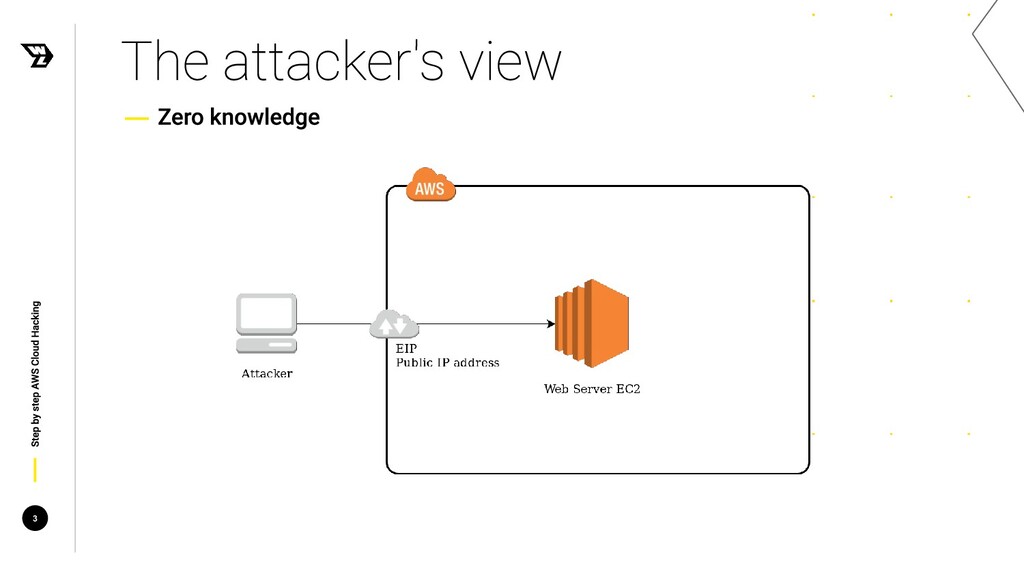
3
None
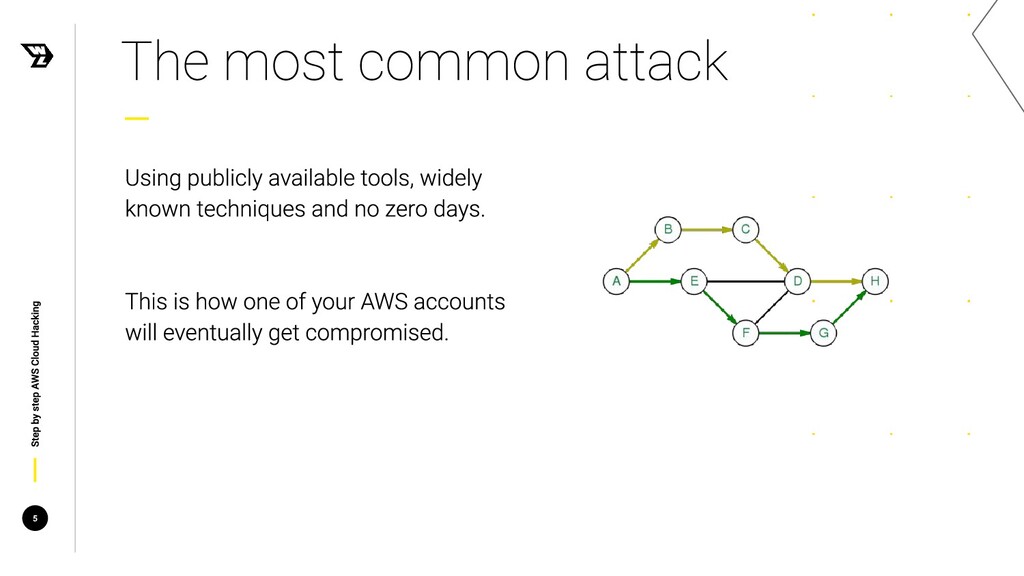
5
need credentials • • • 6
7
IAM permissions 8
9 http://169.254.169.254/ /latest/meta-data/iam/security-credentials/ /latest/meta-data/iam/security-credentials/{role-name}
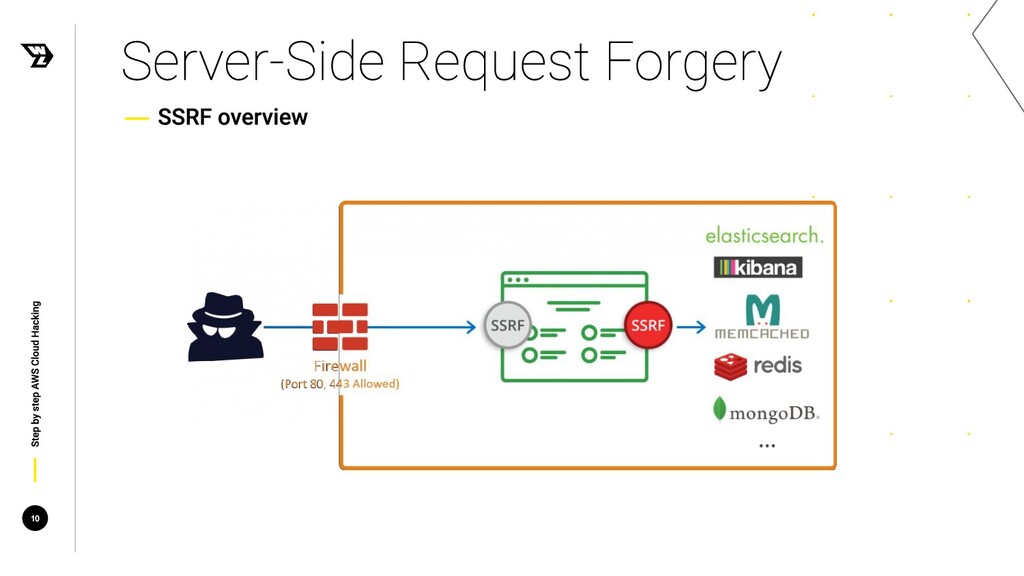
10
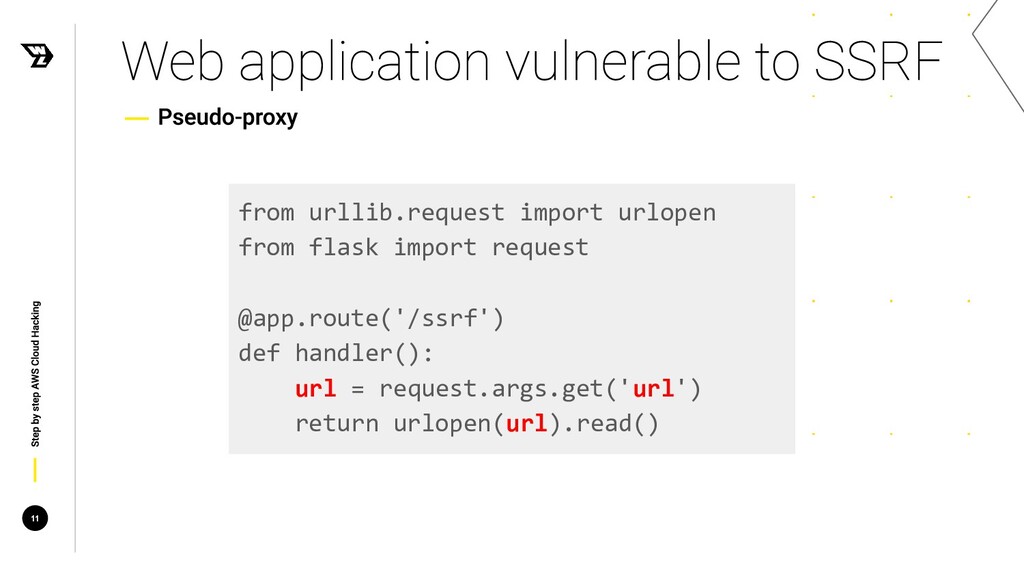
11 from urllib.request import urlopen from flask import request @app.route('/ssrf')
def handler(): url = request.args.get('url') return urlopen(url).read()
Instance metadata and S3 compromise
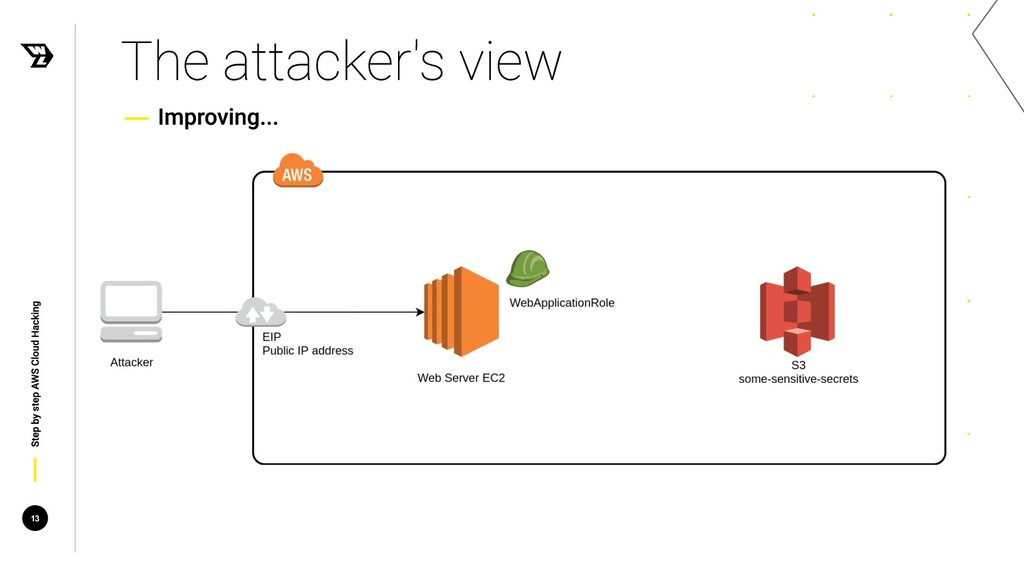
13
None
two ways to enumerate permissions IAM service In most cases
this will fail brute-force 15
Get* / List* / Describe* DryRun parameter 16
17 SUPPORTED_SERVICES = [ 'ec2', 's3' ]
18
./enumerate-iam.py
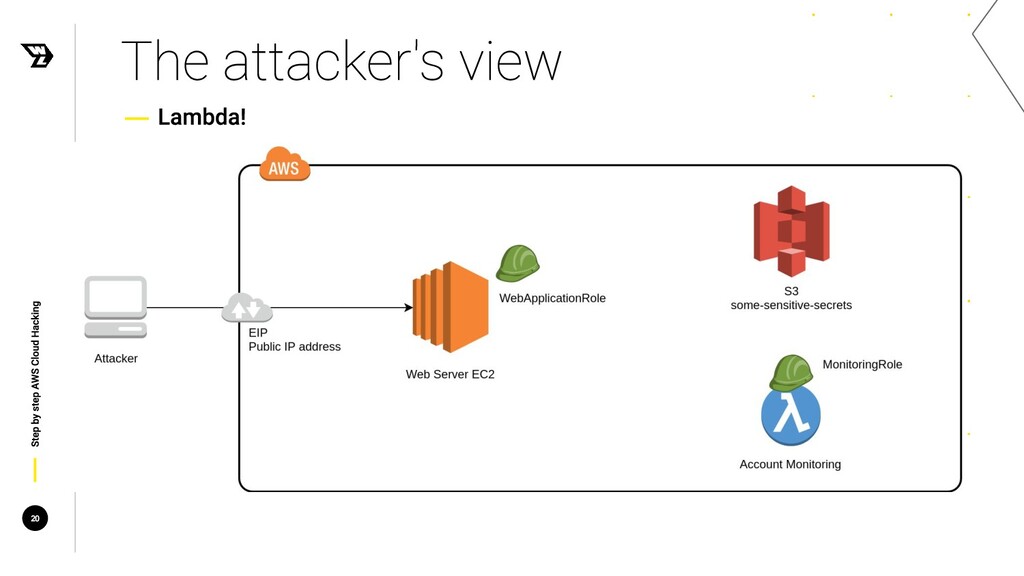
20
many things the attacker doesn't know. 21 { "Statement":[ {
"Effect":"Allow", "Action":[ "s3:*", "lambda:*", "..." ], "Resource":"*" } ] }
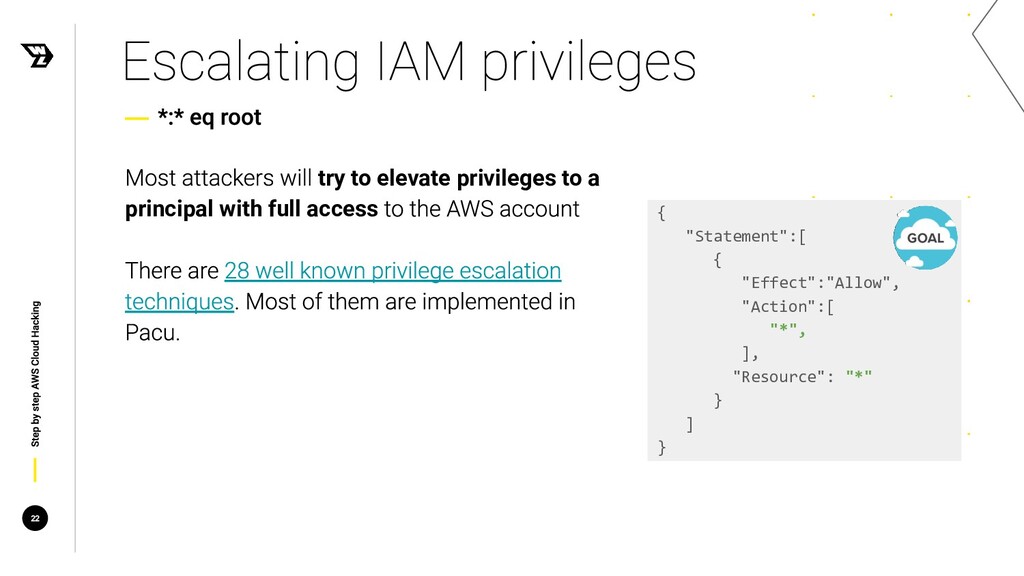
try to elevate privileges to a principal with full access
22 { "Statement":[ { "Effect":"Allow", "Action":[ "*", ], "Resource": "*" } ] }
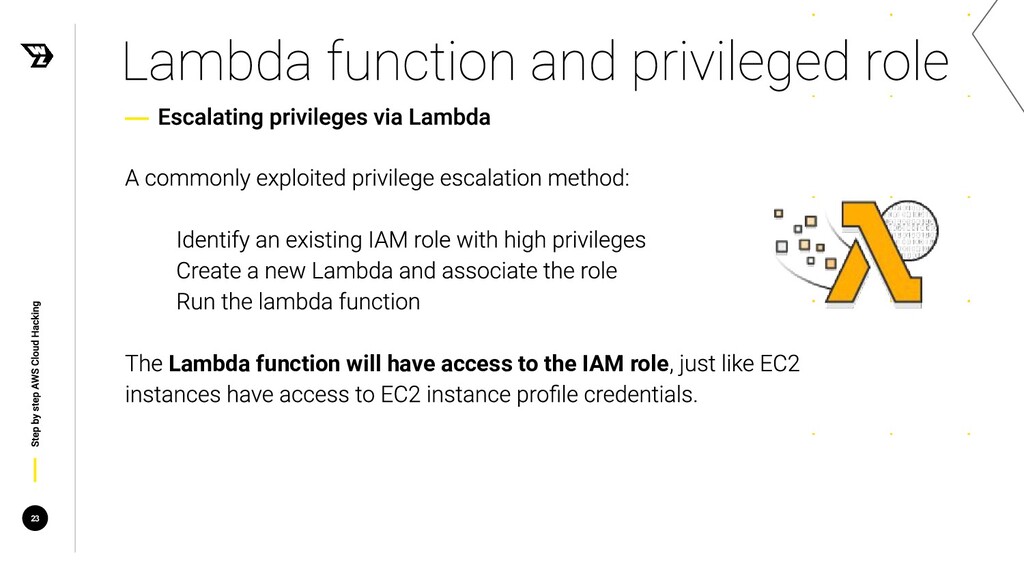
Lambda function will have access to the IAM role 23
Getting * on *
None
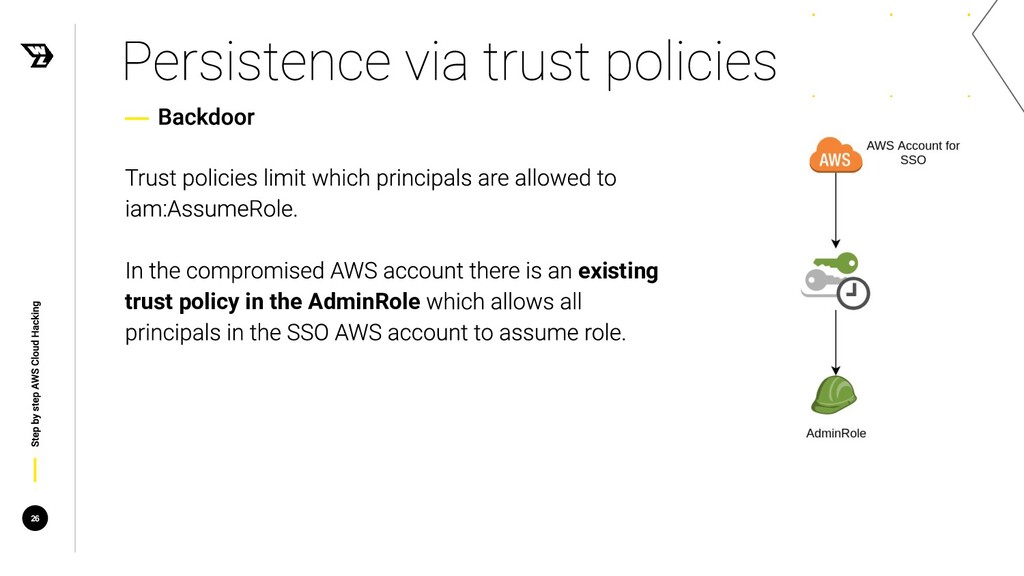
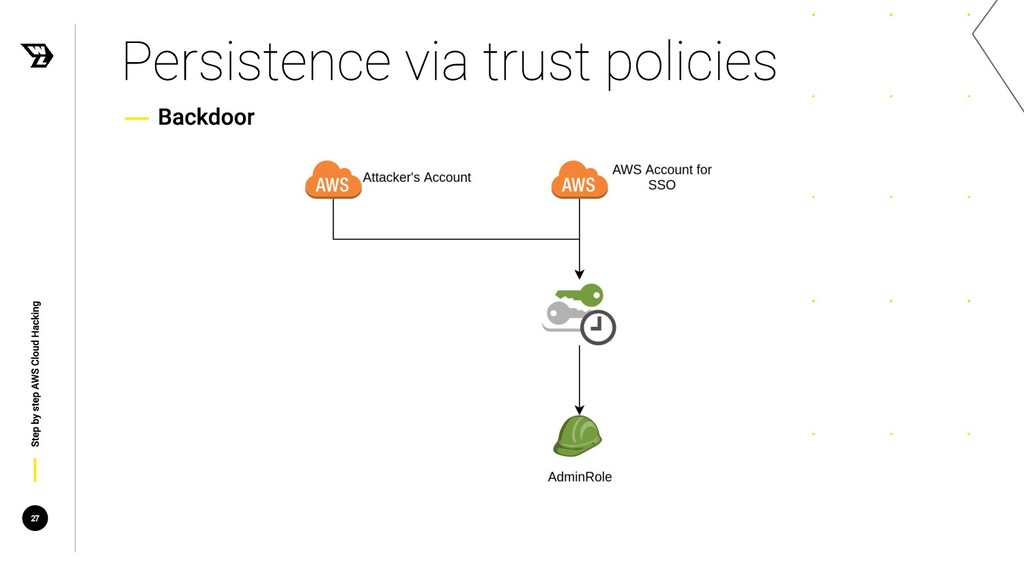
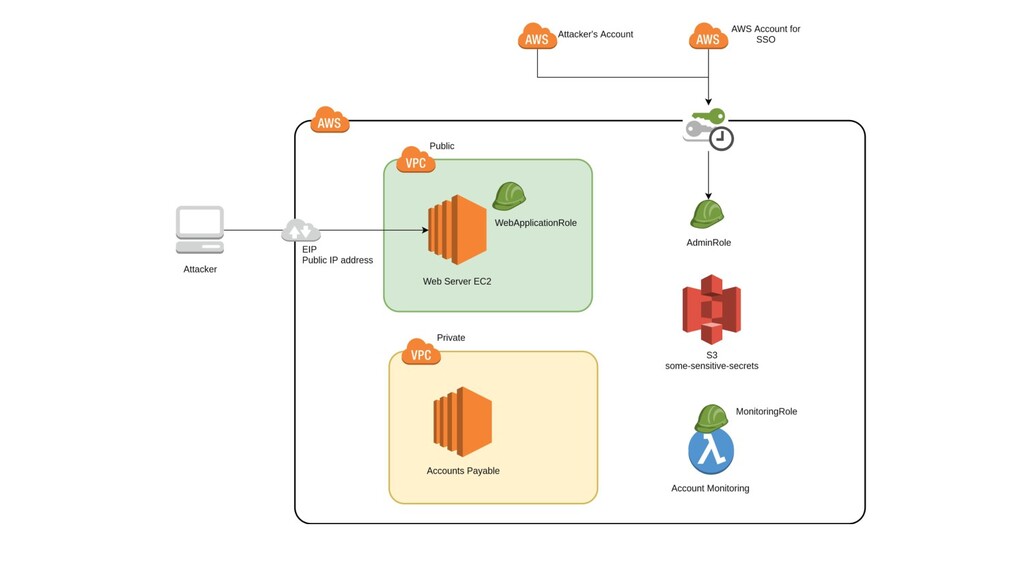
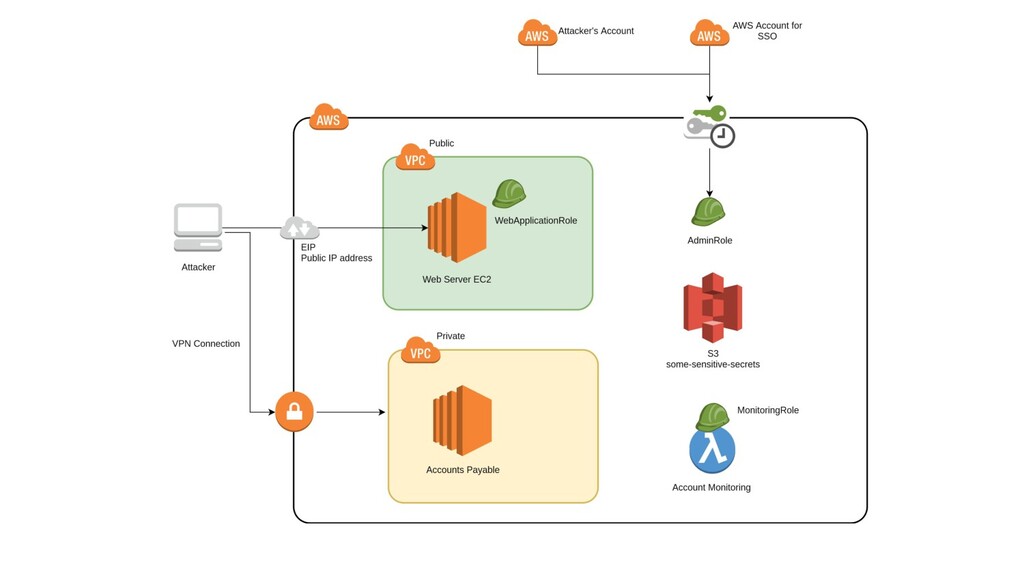
existing trust policy in the AdminRole 26
27
28 { "Effect": "Allow", "Principal": { "AWS": "arn:aws:iam::925877178748:root" }, "Action":
"sts:AssumeRole" } { "Effect": "Allow", "Principal": { "AWS": ["arn:aws:iam::925877178748:root", "arn:aws:iam::320222540496:root"] }, "Action": "sts:AssumeRole" }
Never trust the trust policy
30 ARN for the backdoored role
None
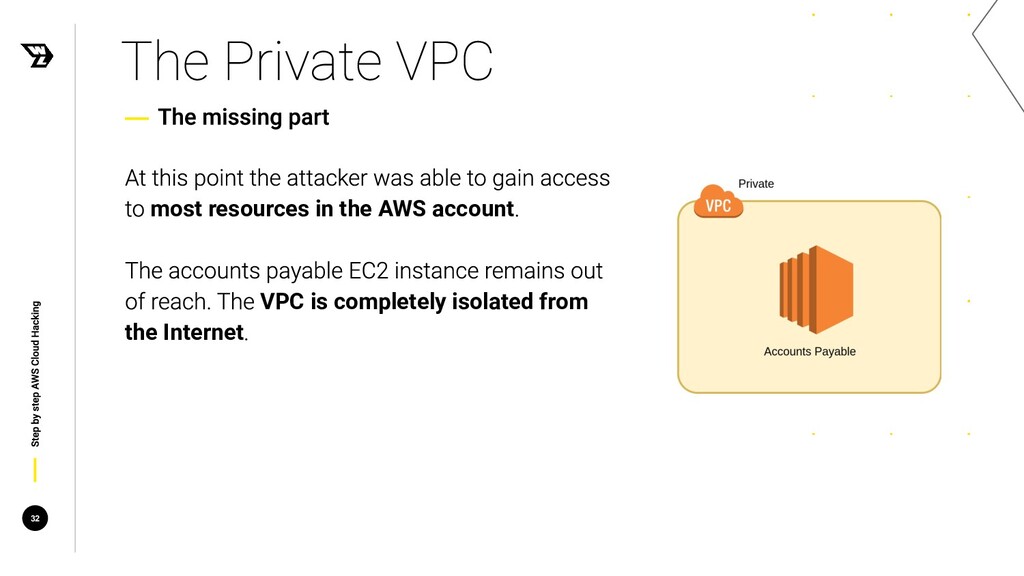
32 most resources in the AWS account VPC is completely
isolated from the Internet
None
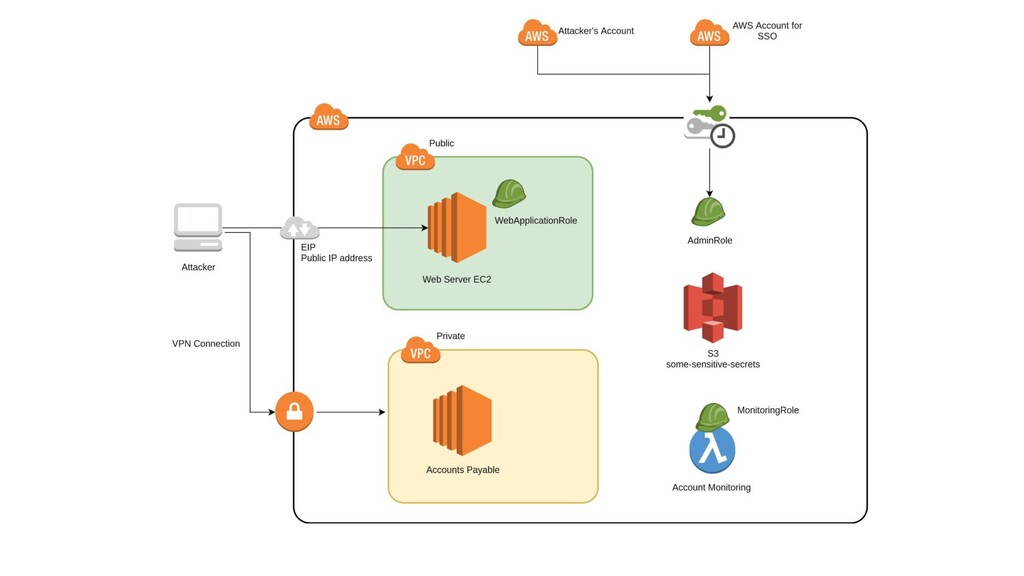
34 VPN between the attacker's workstation and a VPC
35
vpc-vpn-pivot
None
From zero to full pwn
None
40 • enumerate-iam • pacu • vpc-vpn-pivot Follow @AndresRiancho
None

 SiteGround - Reliable hosting with speed, security, and support you can count on.


 andresriancho
 taka_aki
 kinopeee
 reuven
 yoshida0129
 yuj1osm
 eluwing
 tsukina_7mochi
 mohab1
 yukiogawa
 say_no_w
 yachibit
 yukisakai1225
 sstephenson
 helenjbeal
 katiecoart
 aki_iinuma
 aleyda
 tammyeverts
 iamctodd
 ivargrimstad
 keathley
 addyosmani
 garrettdimon
 bryan