Share
Embed
DevOpsDays Portland 2026: Do software updates a bit better
A 5 minute Ignite talk from DevOpsDays Portland 2026 on doing software updates a bit better with containers and Renovate.
Zomg supply chain attacks.
Bea Hughes
September 09, 2026
Transcript
20 slides
-
It's just a jump to the left: the Time Warp
of DevSecOps Do software updates a bit better 1 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
Hi I'm Bea, I have to talk fast! <Super important
companies I've worked at to prove my credentials go here> I've done security since +++ATH0 was a problem 2 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
shifting left didn't really sell you anything You bought scanners,
added them to CI, and stopped developers being able to ship new features, just so some Java/Javascript library you weren't using in that way wouldn't be included in some image. 3 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
Containers You use them, probably, they're mandatory. Whatever. Let's do
it more securely! What if they could update themselves? 4 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
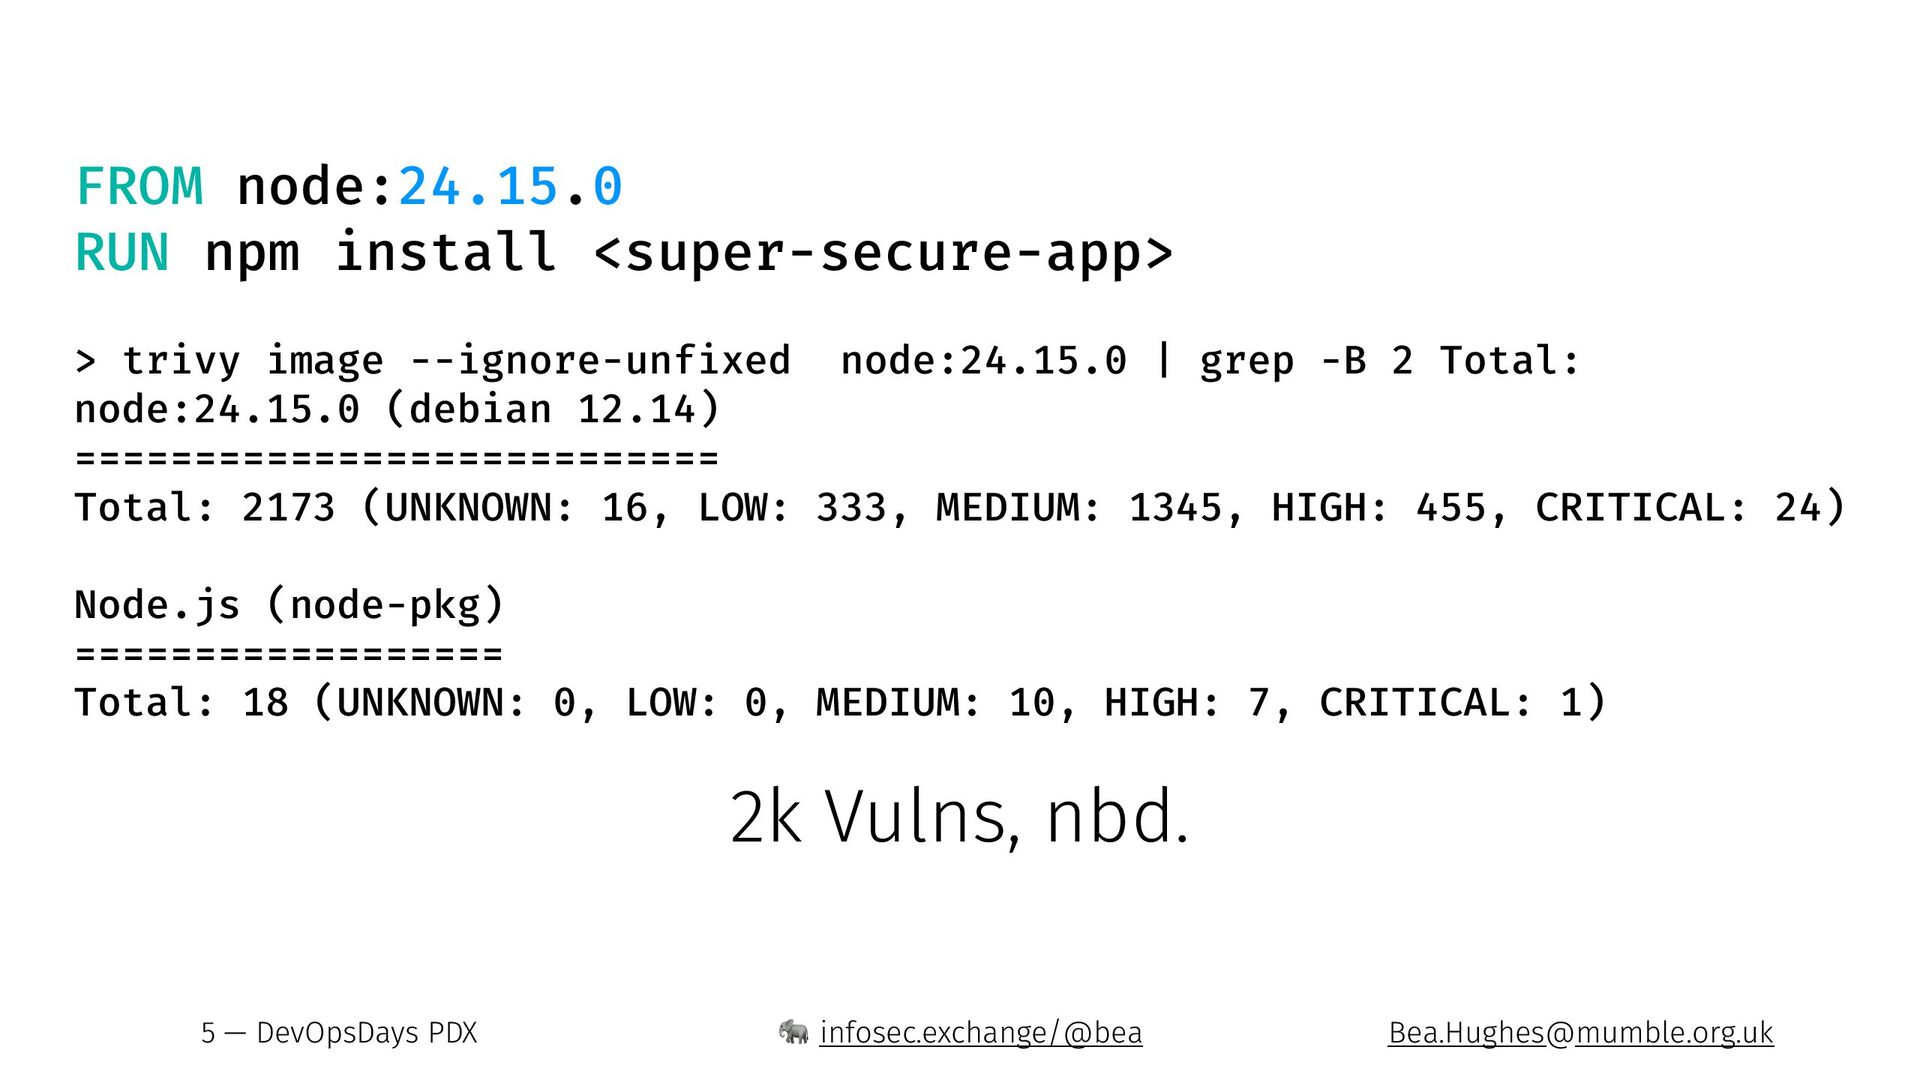
FROM node:24.15.0 RUN npm install <super-secure-app> > trivy image --ignore-unfixed
node:24.15.0 | grep -B 2 Total: node:24.15.0 (debian 12.14) =========================== Total: 2173 (UNKNOWN: 16, LOW: 333, MEDIUM: 1345, HIGH: 455, CRITICAL: 24) Node.js (node-pkg) ================== Total: 18 (UNKNOWN: 0, LOW: 0, MEDIUM: 10, HIGH: 7, CRITICAL: 1) 2k Vulns, nbd. 5 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
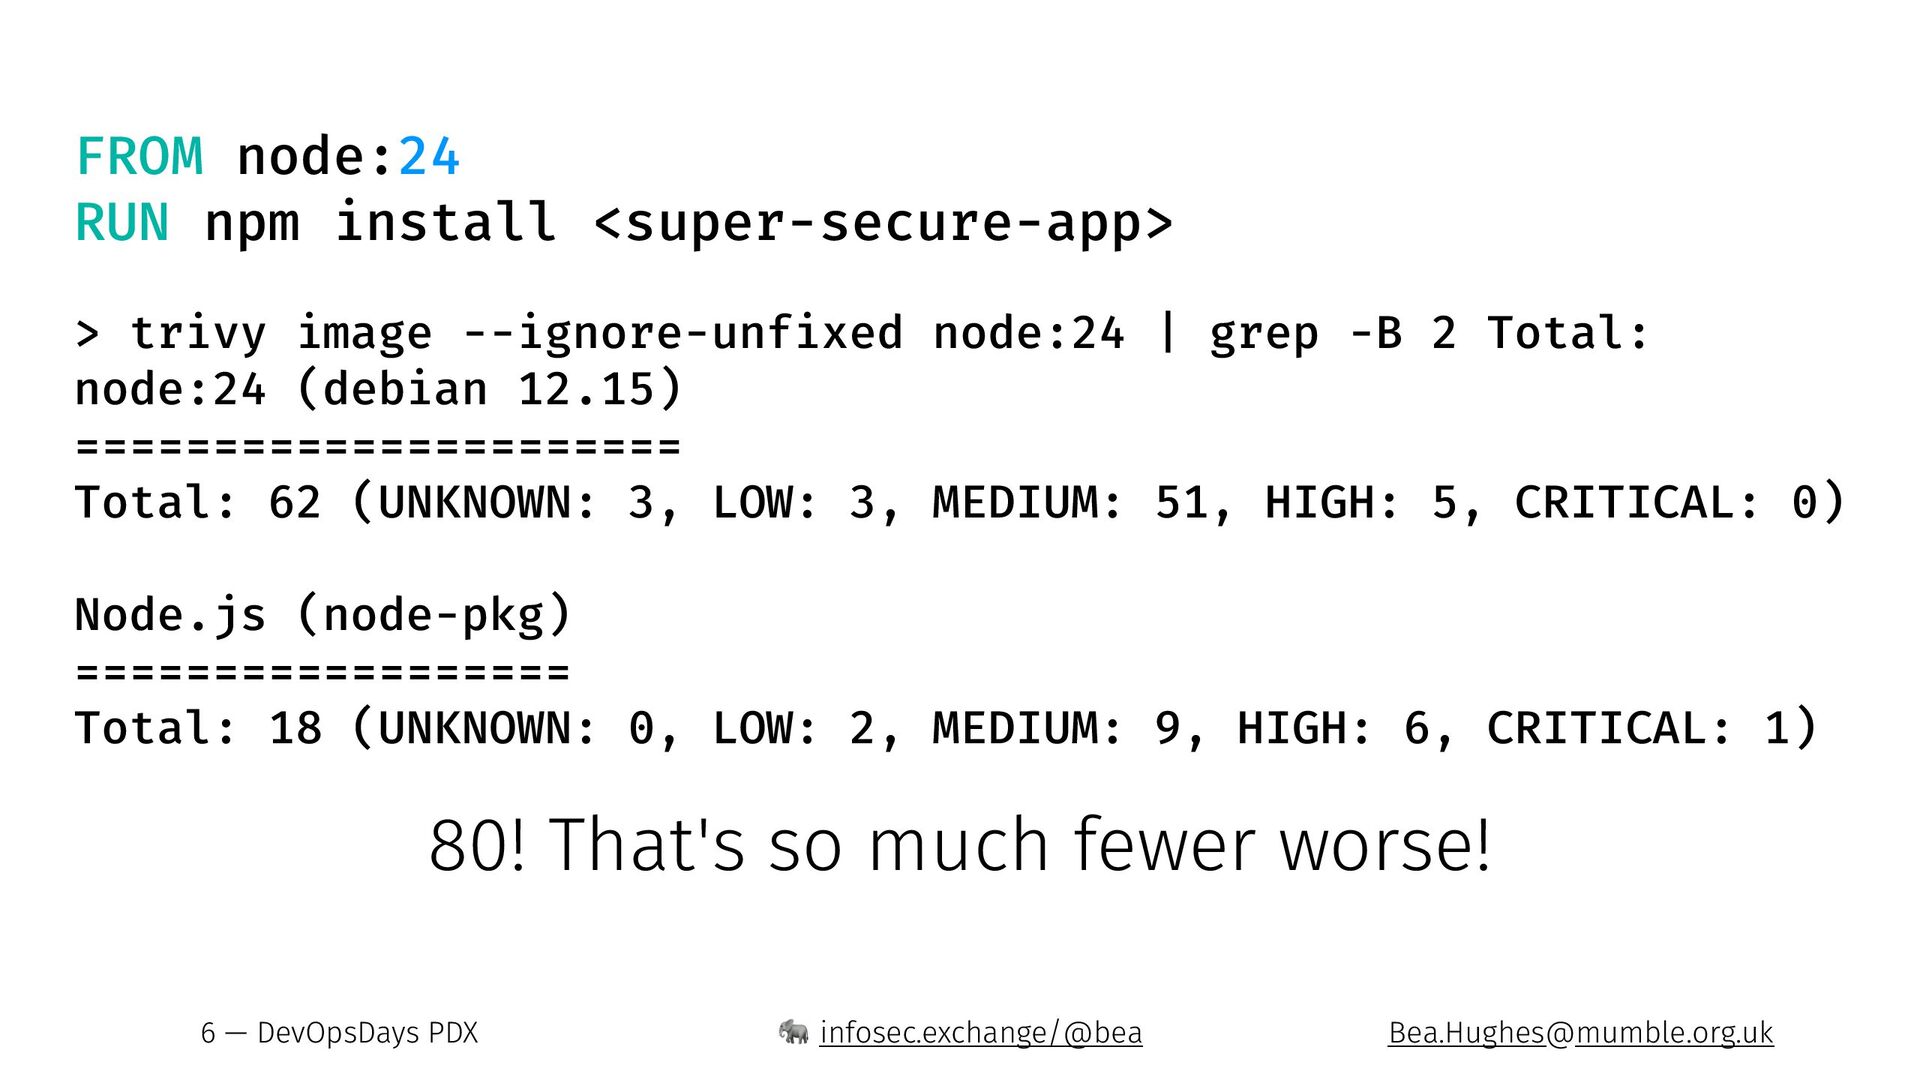
FROM node:24 RUN npm install <super-secure-app> > trivy image --ignore-unfixed
node:24 | grep -B 2 Total: node:24 (debian 12.15) ====================== Total: 62 (UNKNOWN: 3, LOW: 3, MEDIUM: 51, HIGH: 5, CRITICAL: 0) Node.js (node-pkg) ================== Total: 18 (UNKNOWN: 0, LOW: 2, MEDIUM: 9, HIGH: 6, CRITICAL: 1) 80! That's so much fewer worse! 6 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
"But won't it now break?" You are testing the build
artifact you produce, right? 7 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
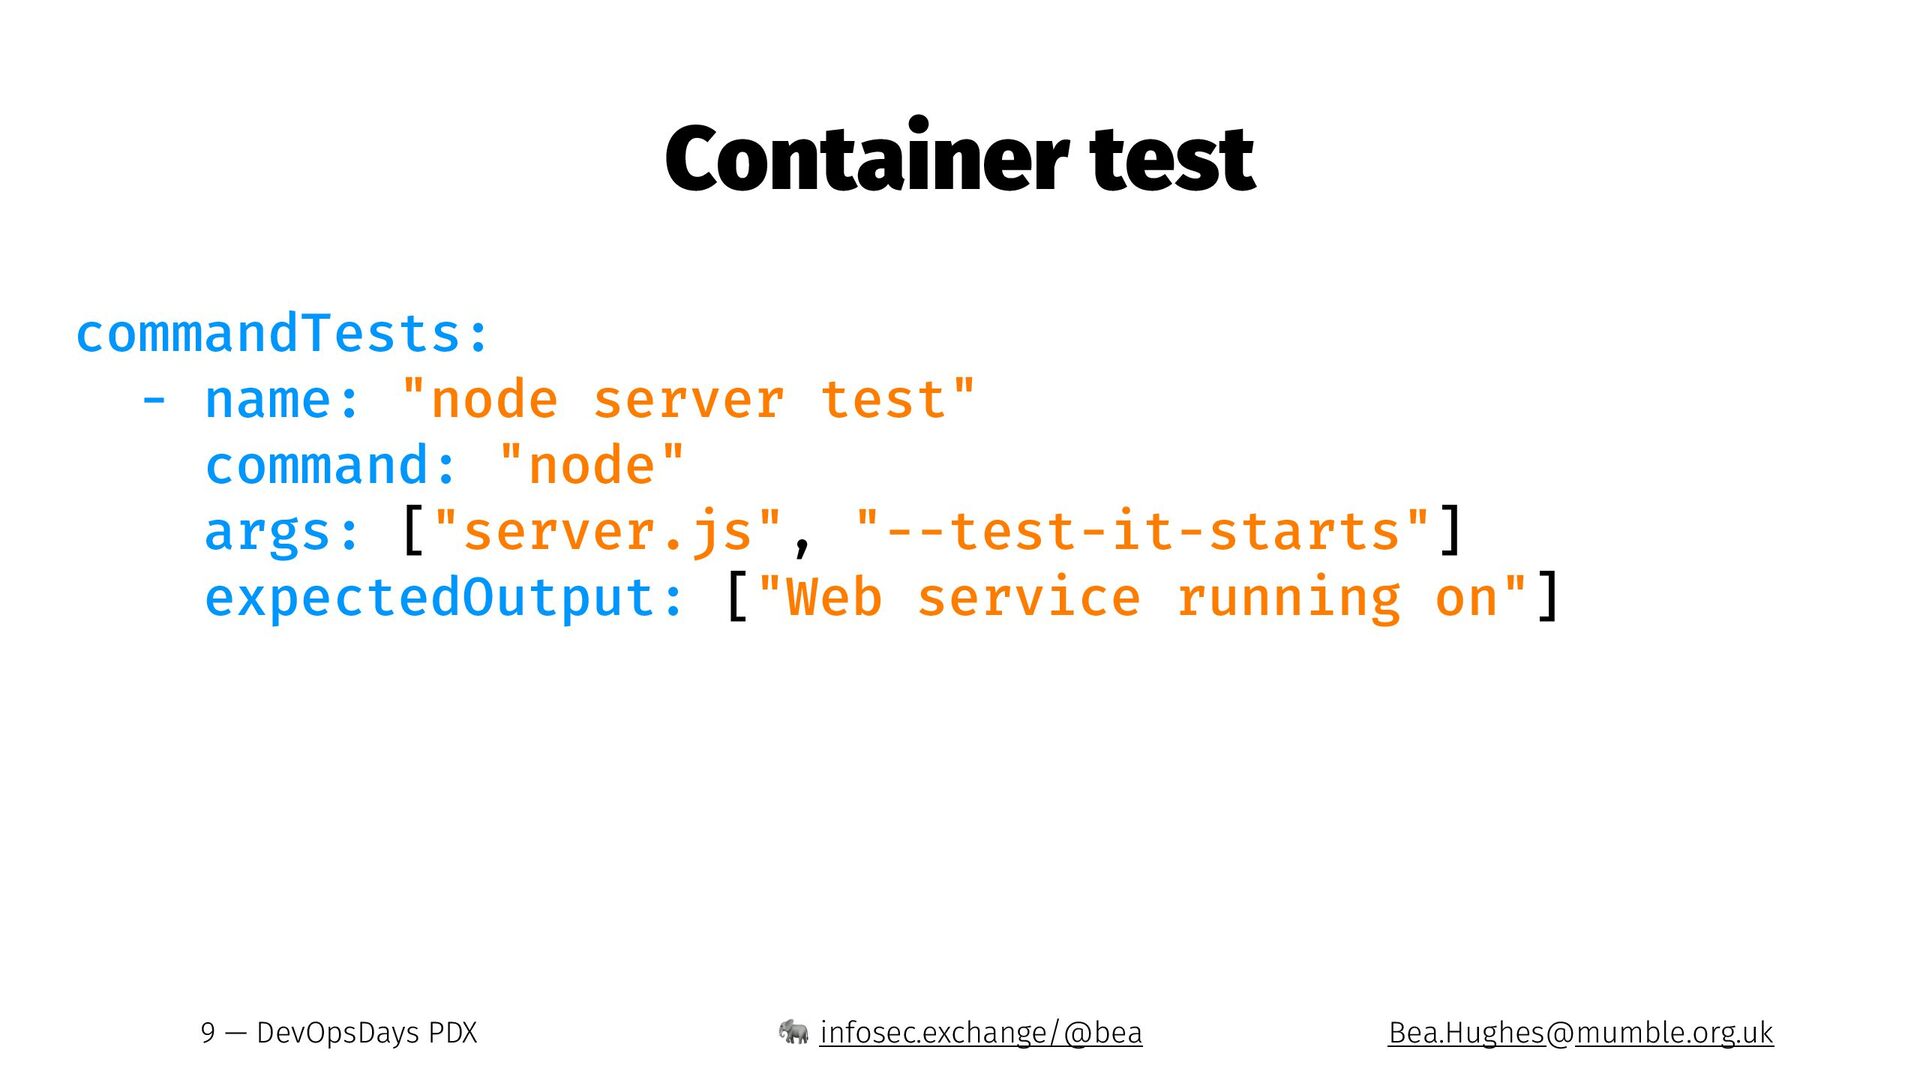
Container test commandTests: - name: "node server test" command: "node"
args: ["server.js", "--test-it-starts"] expectedOutput: ["Web service running on"] 9 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
"But you can't do that because SuPpLy ChAiN AtTaCkS!!11eleventy" 10
— DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
Which is the bigger risk? Out of date software or
SuPpLy ChAiN AtTaCkS? 11 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
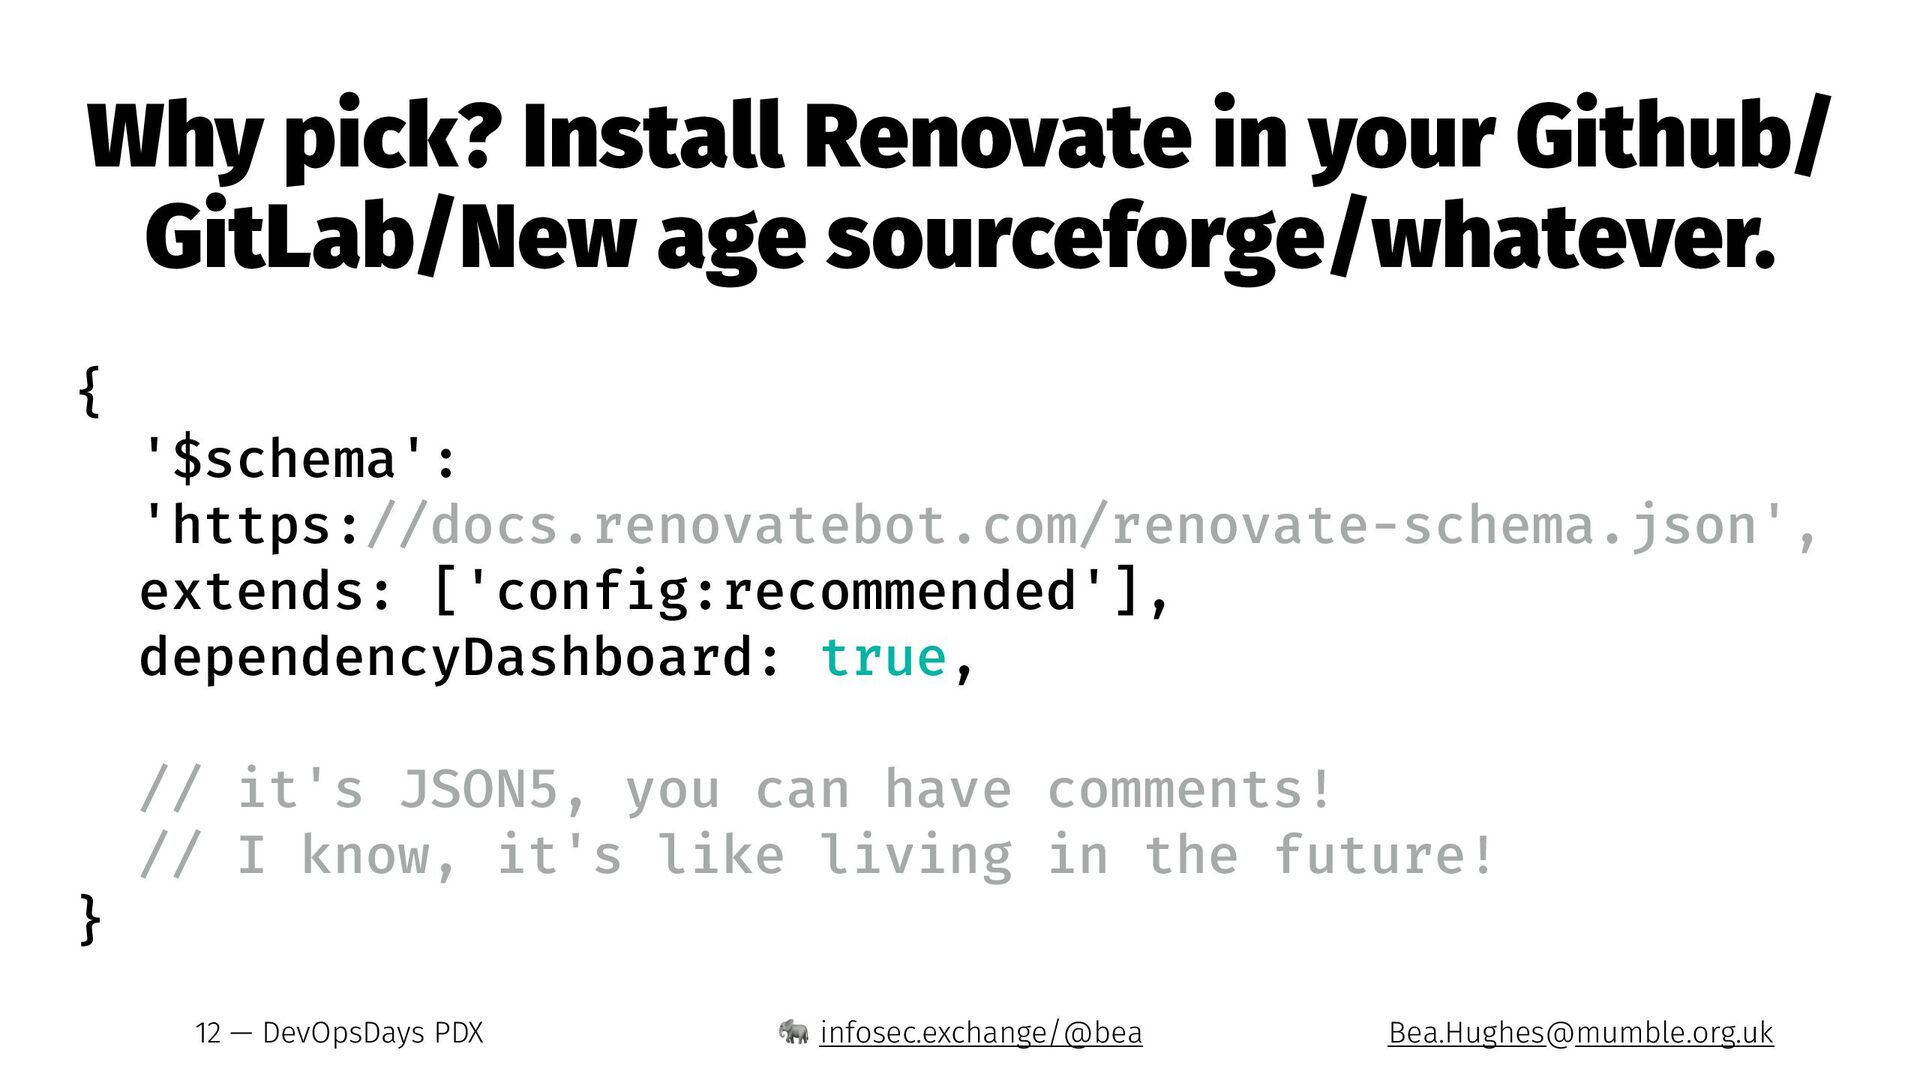
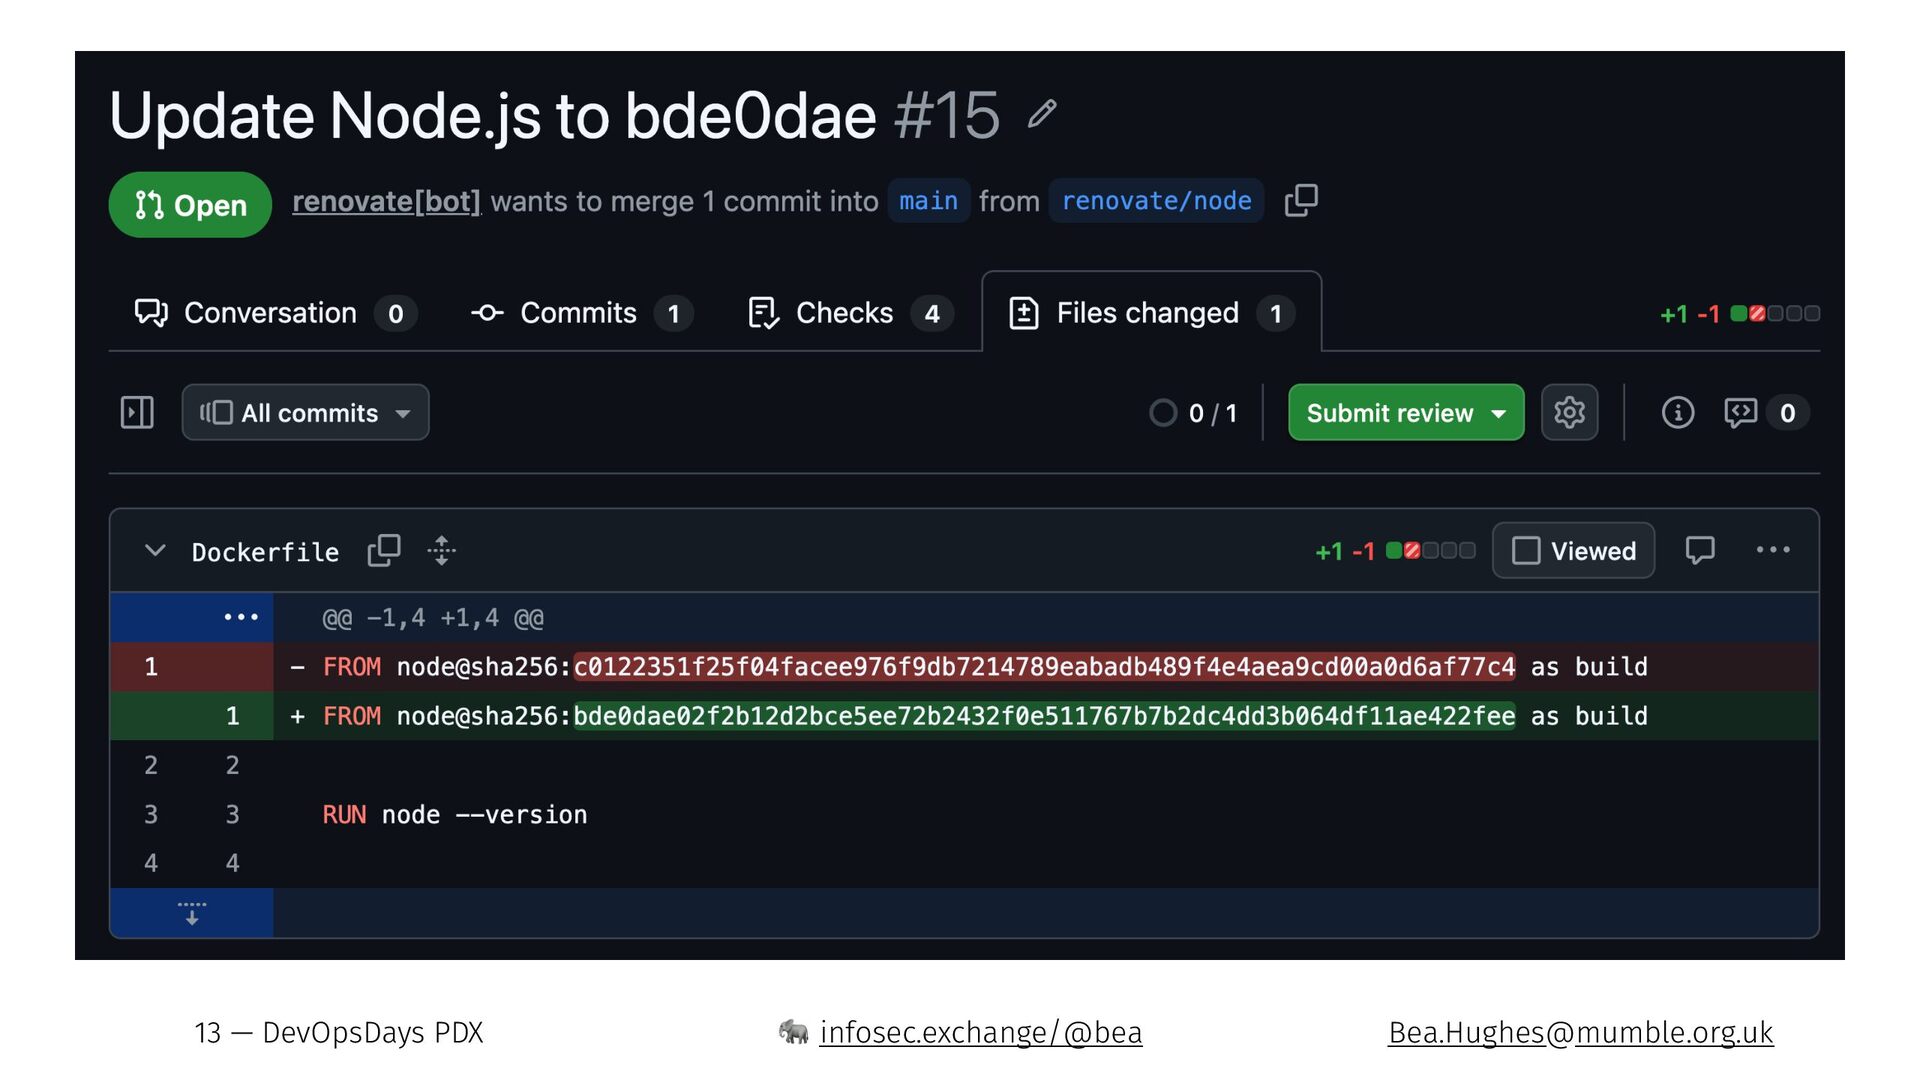
Why pick? Install Renovate in your Github/ GitLab/New age sourceforge/whatever.
{ } '$schema': 'https://docs.renovatebot.com/renovate-schema.json', extends: ['config:recommended'], dependencyDashboard: true, // it's JSON5, you can have comments! // I know, it's like living in the future! 12 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
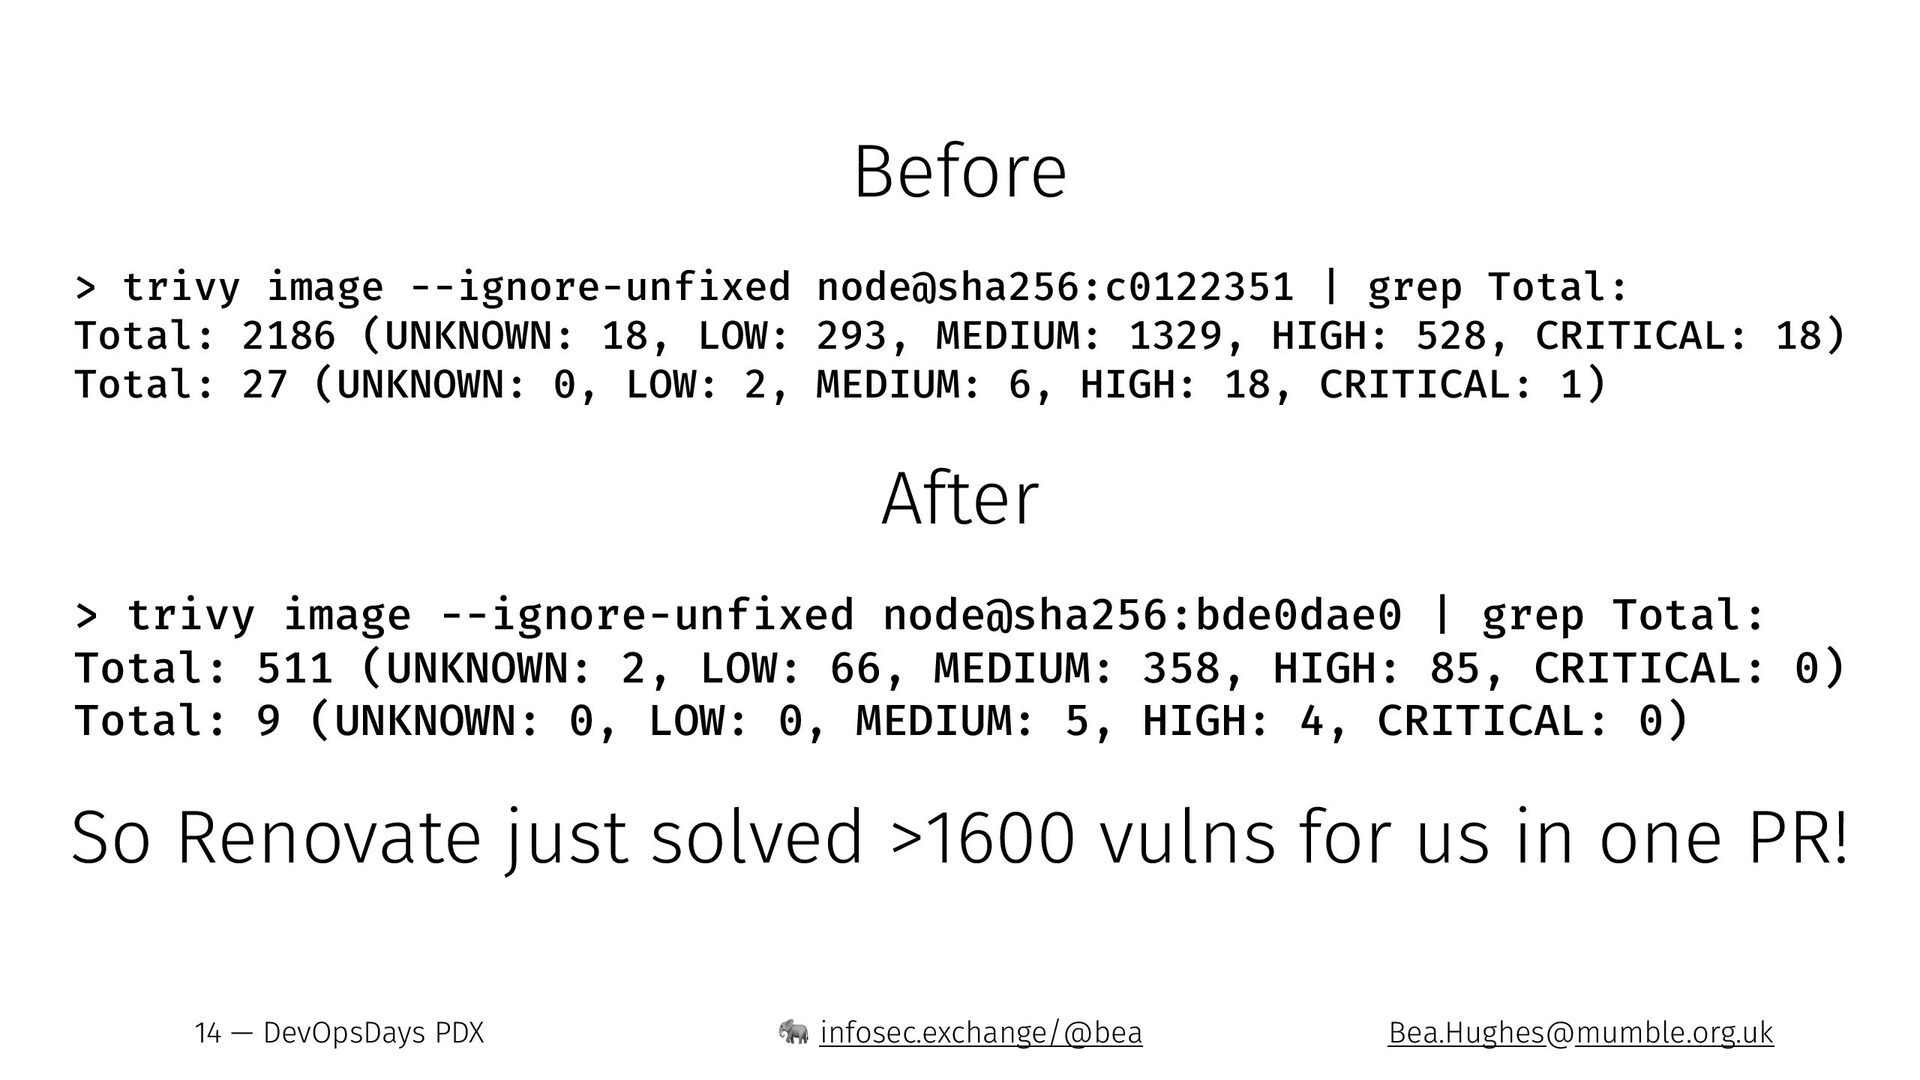
Before > trivy image --ignore-unfixed node@sha256:c0122351 | grep Total: Total:
2186 (UNKNOWN: 18, LOW: 293, MEDIUM: 1329, HIGH: 528, CRITICAL: 18) Total: 27 (UNKNOWN: 0, LOW: 2, MEDIUM: 6, HIGH: 18, CRITICAL: 1) After > trivy image --ignore-unfixed node@sha256:bde0dae0 | grep Total: Total: 511 (UNKNOWN: 2, LOW: 66, MEDIUM: 358, HIGH: 85, CRITICAL: 0) Total: 9 (UNKNOWN: 0, LOW: 0, MEDIUM: 5, HIGH: 4, CRITICAL: 0) So Renovate just solved >1600 vulns for us in one PR! 14 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
"But as I keep trying to say it's the highest
priority in the world, despite that really only coming from marketing material for things that pretend to solve this, you can't do that because SuPpLy ChAiN AtTaCkS!! 11eleventy" 15 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
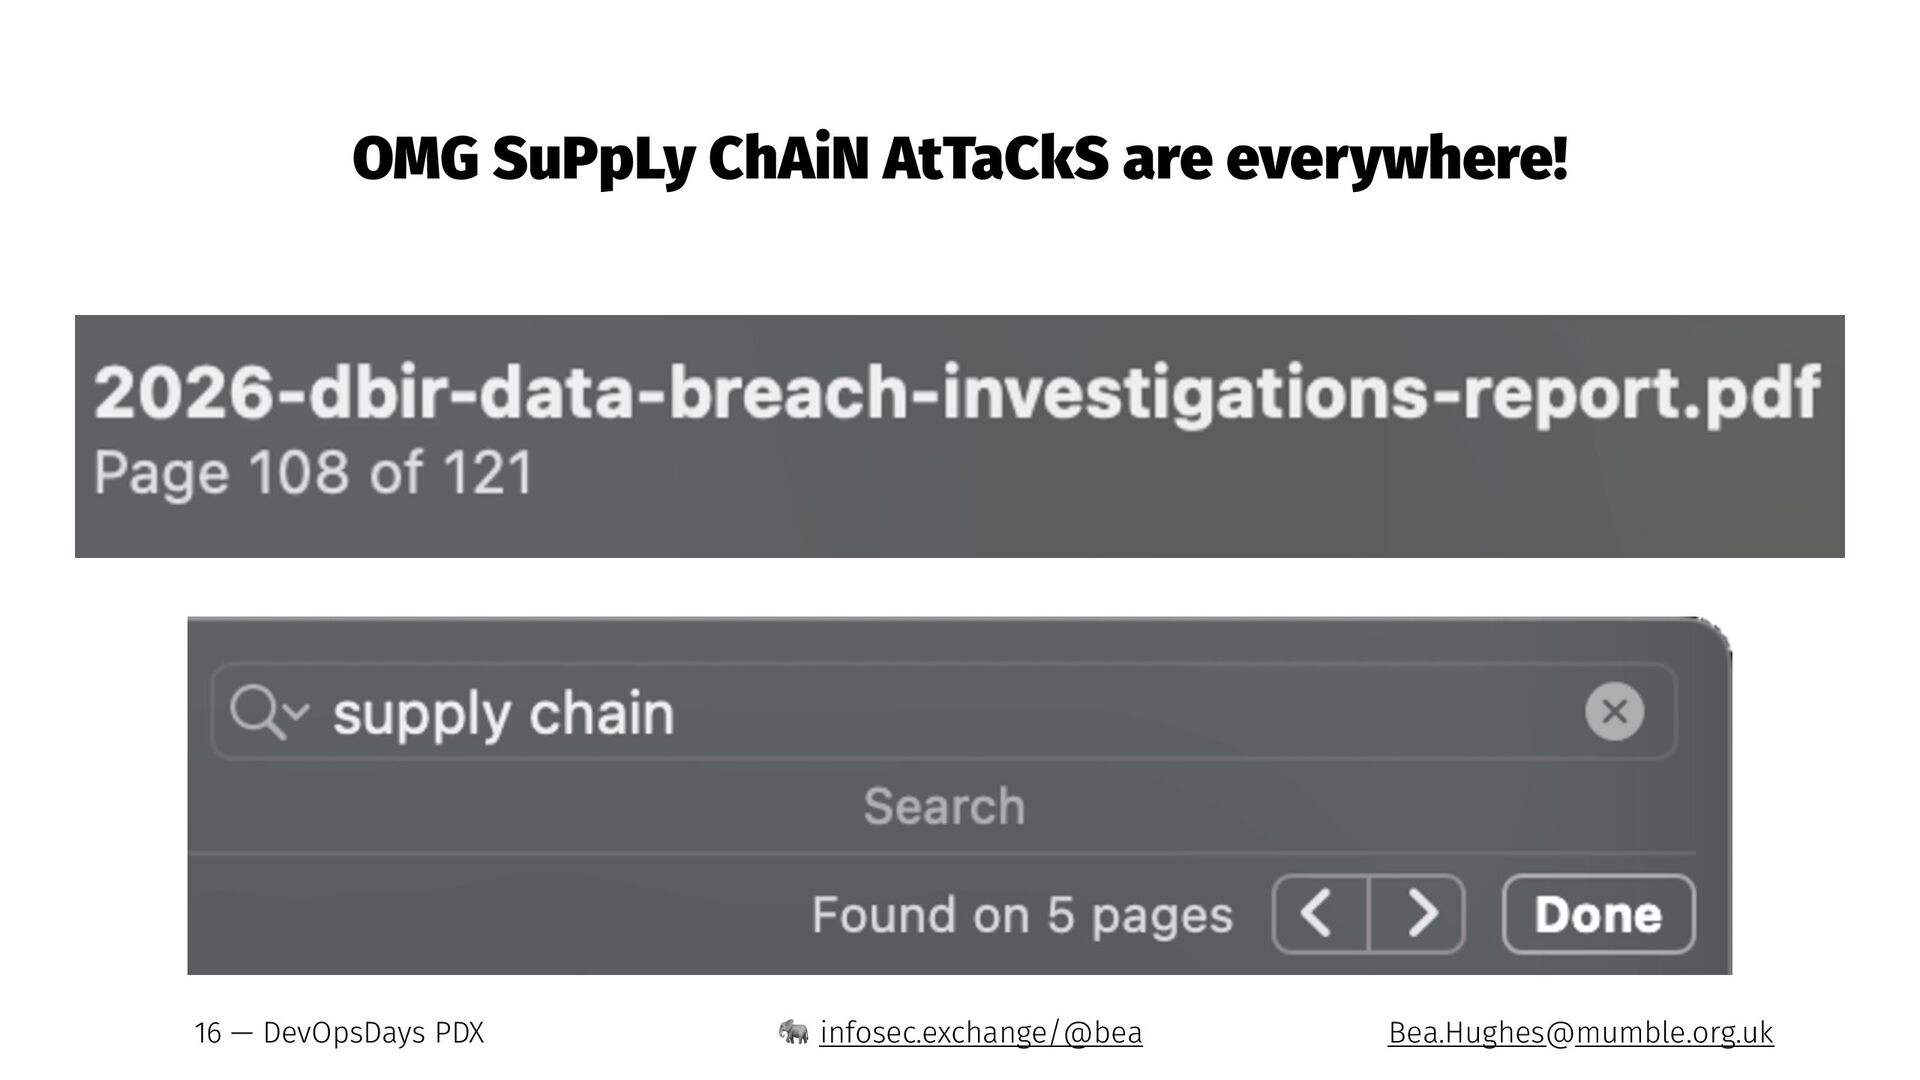
OMG SuPpLy ChAiN AtTaCkS are everywhere! 16 — DevOpsDays PDX
! infosec.exchange/@bea [email protected] -
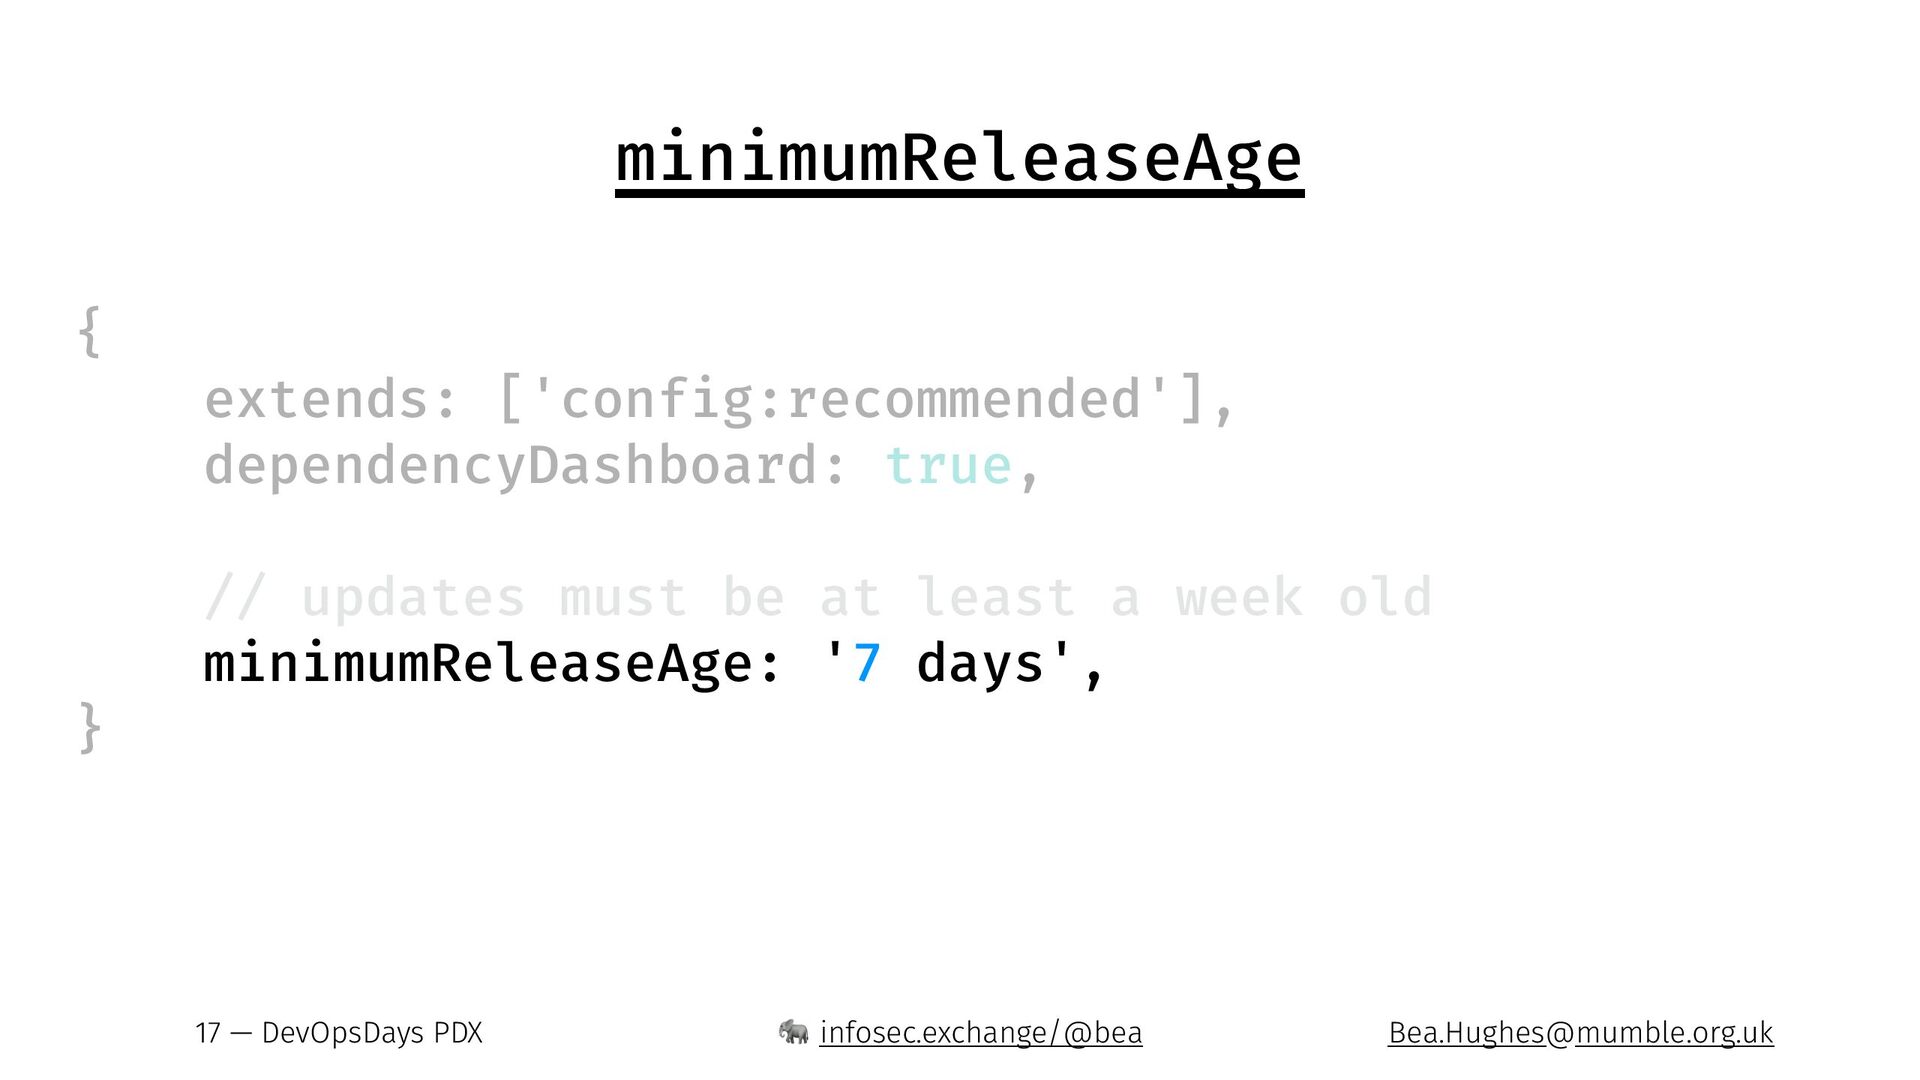
minimumReleaseAge { } extends: ['config:recommended'], dependencyDashboard: true, // updates must
be at least a week old minimumReleaseAge: '7 days', 17 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
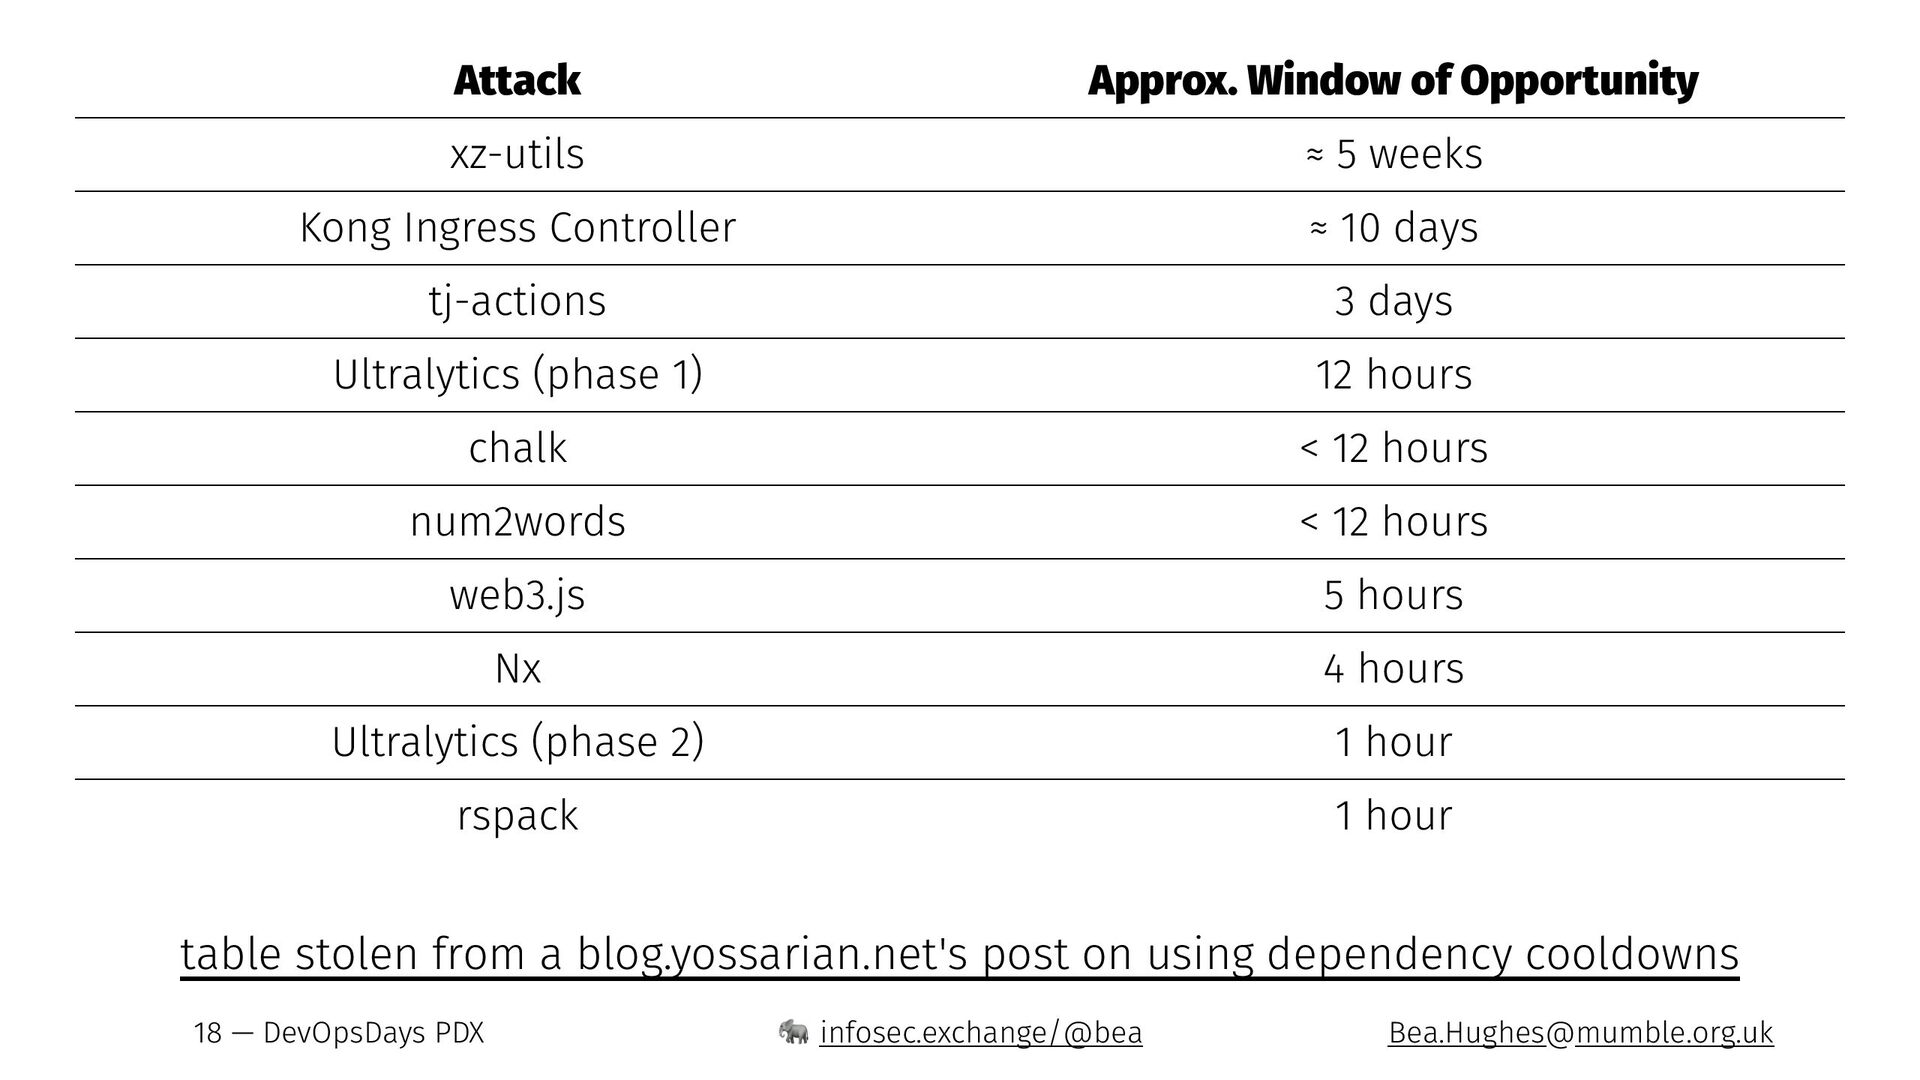
Attack Approx. Window of Opportunity xz-utils ≈ 5 weeks Kong
Ingress Controller ≈ 10 days tj-actions 3 days Ultralytics (phase 1) 12 hours chalk < 12 hours num2words < 12 hours web3.js 5 hours Nx 4 hours Ultralytics (phase 2) 1 hour rspack 1 hour table stolen from a blog.yossarian.net's post on using dependency cooldowns 18 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
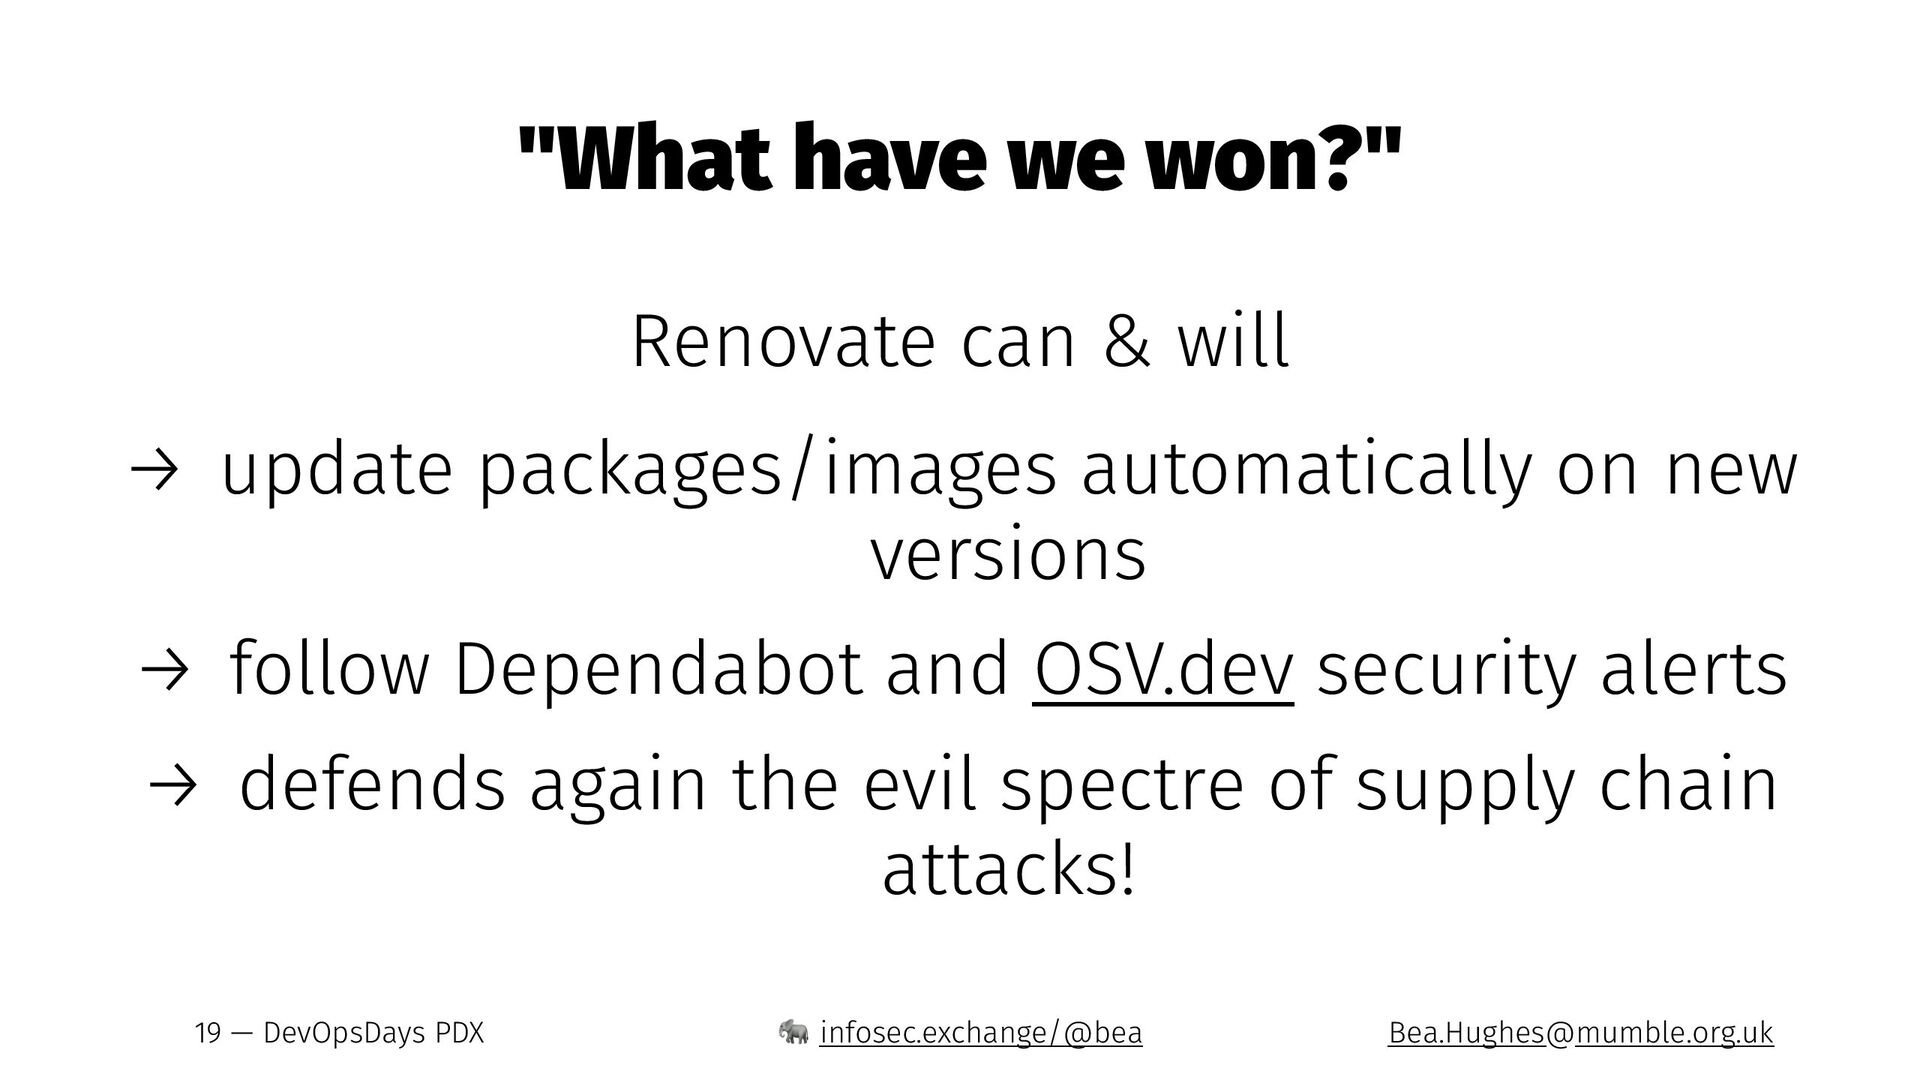
"What have we won?" Renovate can & will → update
packages/images automatically on new versions → follow Dependabot and OSV.dev security alerts → defends again the evil spectre of supply chain attacks! 19 — DevOpsDays PDX ! infosec.exchange/@bea [email protected] -
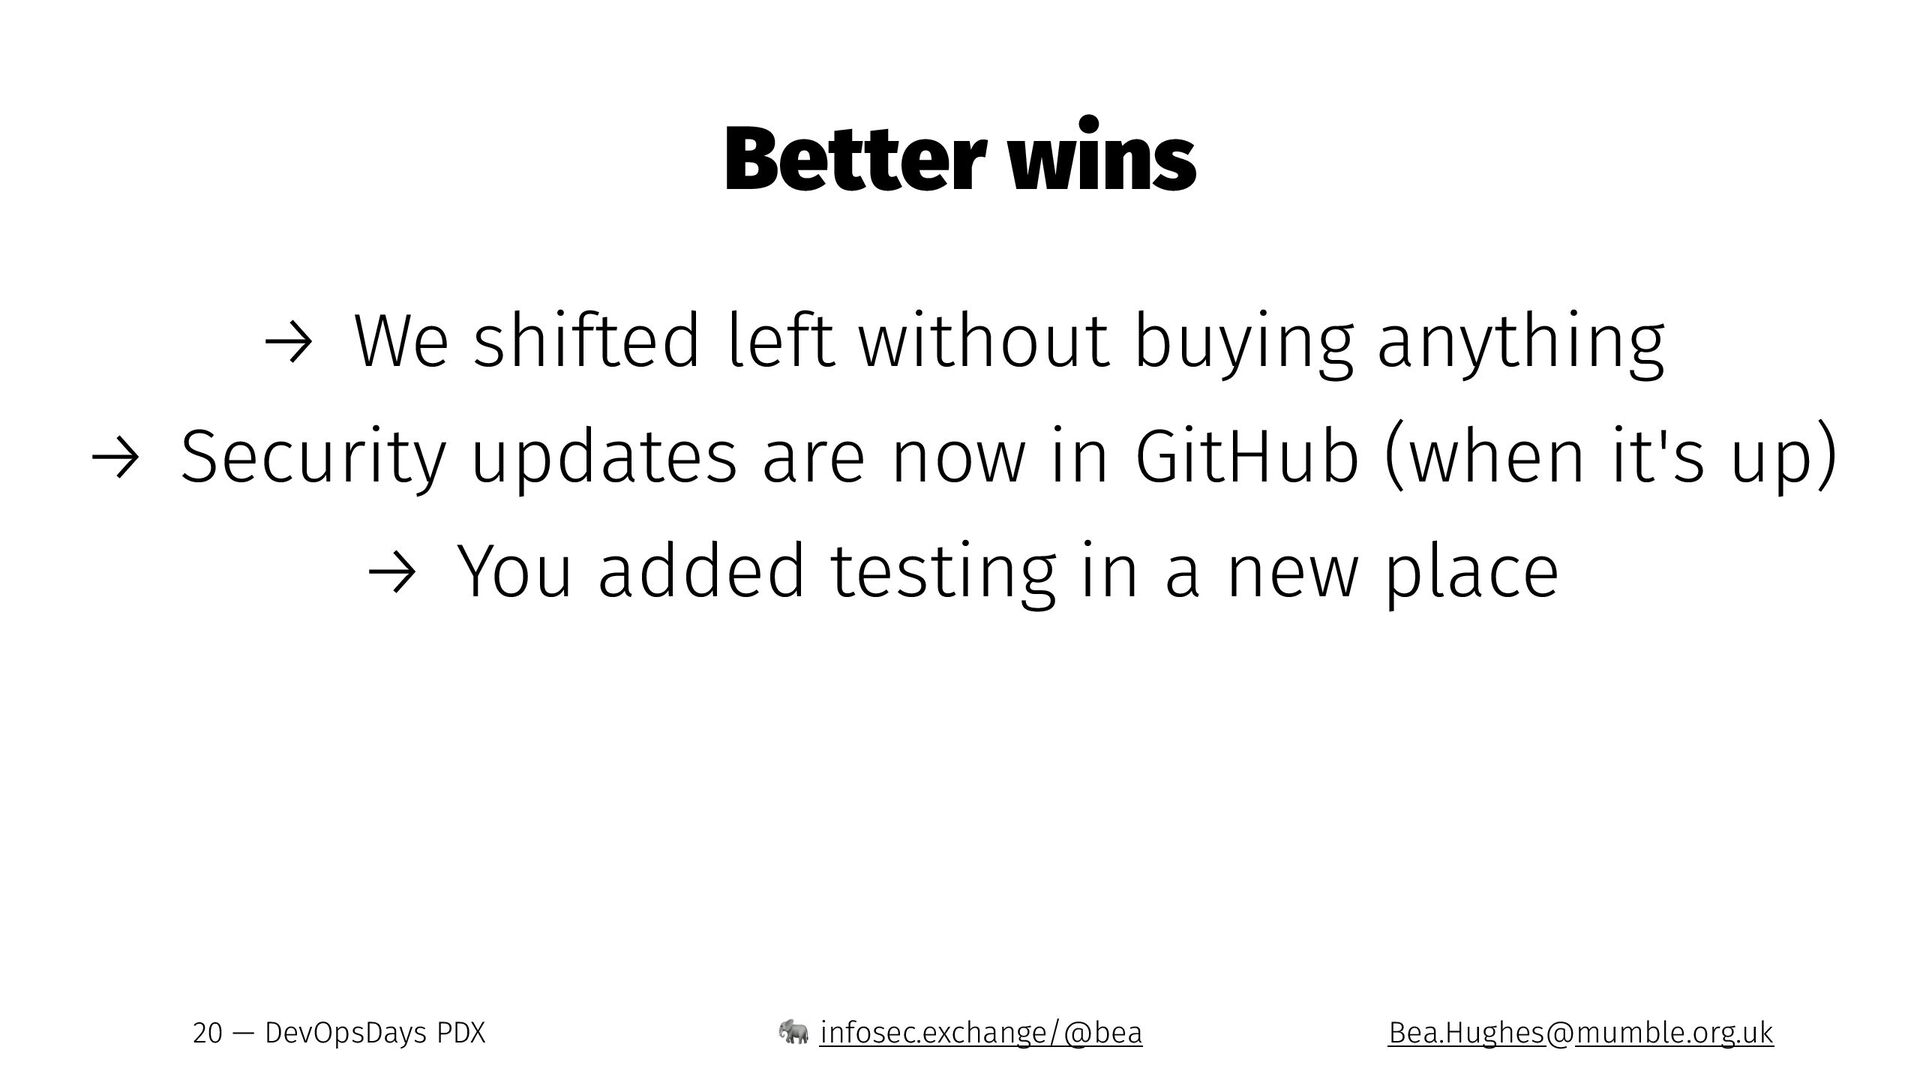
Better wins → We shifted left without buying anything →
Security updates are now in GitHub (when it's up) → You added testing in a new place 20 — DevOpsDays PDX ! infosec.exchange/@bea [email protected]