Share
Embed
AWSだ! Google Cloudだ! Azureだ! 認証連携だ!
昨今は、さまざまな要因から、複数のクラウド(IaaS)プロバイダーを活用することが多くなりました。例えば、サービスのワークロードはAWSだが、データ分析はGoogle CloudのBigQueryを使うなどです。異なるプロバイダー間でのリソースにアクセスするには、認証が必要であり、シークレットを安全に発行・交換する必要があります。クラウドプロバイダーが動的に発行する等さまざまな方式がありますが、システムの制限や運用によっては安全なシークレットの取り扱いのために、慎重な技術設計が必要になる場合もあります。
今回は、LayerXにおける要件パターン、脅威モデリングに基づく判断と実装方法を紹介することで、「どこまで気をつけるべきか?」「何を想定すべきか?」といった実務に対して参考いただけると嬉しいです
Kengo Suzuki
May 22, 2024
Transcript
66 slides
-
- ϚϧνΫϥυͷར༻Λආ͚ΒΕͳ͘ͳΓɺٱ͍͠ - ϚϧνΫϥυԼͰͷϫʔΫϩʔυؒͷॲཧ̍ͭͰ͋Δ - ͦͷॲཧͷલఏͱͯ͠ೝূ͕ॏཁͰ͋Δ - ͦͷ͋ͱͷೝূख๏ͷબͱ࣮ͷแׅతͳϦεΫରԠʹ͍ͭͯɺ ϊϋͷڞ༗ -
ͦΕʹ͏ٞͷ׆ൃԽ٩(Ň•̀ω•́Ň)و - ࣾͷڵຯΛ͋͛Δ ࠓͷత -
- ॴଐ - ࡾҪ࢈σδλϧɾΞηοτϚωδϝϯτ - ίʔϙϨʔτγεςϜ෦ - LayerX Fintechࣄۀ෦ʢˢʹग़ʣ -
ݸਓ׆ಈ - िؒχϡʔεϨʔλʔɺPodCastɺಉਓࢽ - དྷྺ - SIer > ࢿ࢈ཧɾՈܭɾձܭSP > ূ݊ձࣾ > ݱ ৬ @ken5scal χϡʔεϨλʔ: https://ken5scal.notion.site/54bda4932da14add9e9911ab3e9a6e5c podcast: https://open.spotify.com/show/73sFeKzUIkSYfCZWVBNO70 -
- ͕ࣗରԠͨ͜͠ͱ͋ΔϚϧνΫϥυϢʔεέʔε - ূ݊αʔϏεࢿ࢈ӡ༻ͷ͓٬༷͚๏ఆாͷGDriveϑΝΠϧཧ - ۚ༥αʔϏεʹ͓͚ΔϩάɾΠϕϯτͷू - Entra ID (AzureAD)ͷIaCతཧ
- AWS্ͷσʔλΛBigQueryج൫సૹ - ্هରԠதʹ;ͱࢥͬͨ͜ͱ͕͋Δ ࠓͷഎܠ -
# header { "kid": "ap-northeast-15", "typ": "JWS", "alg": "RS512" }
# Payload { "sub": “ap-northeast-1:{Cognito Pool IDͷIdentity ID}”, "aud": “ap-northeast-1:{Cognito Pool Provider ID}“, "amr": [ "authenticated", “{Cognito Pool IDͷIdentity໊}”, "{Cognito Pool IDͷIdentity໊}:ap-northeast-1:{Pol Provider ID}:${Developer ID}” ], "iss": "https://cognito-identity.amazonaws.com", "https://cognito-identity.amazonaws.com/identity-pool-arn": “arn:aws:cognito-identity:ap- northeast-1:${AWS Account ID}:identitypool/ap-northeast-1:${Pool ID}”, "exp": 1716244163, "iat": 1716243263 } 13 -
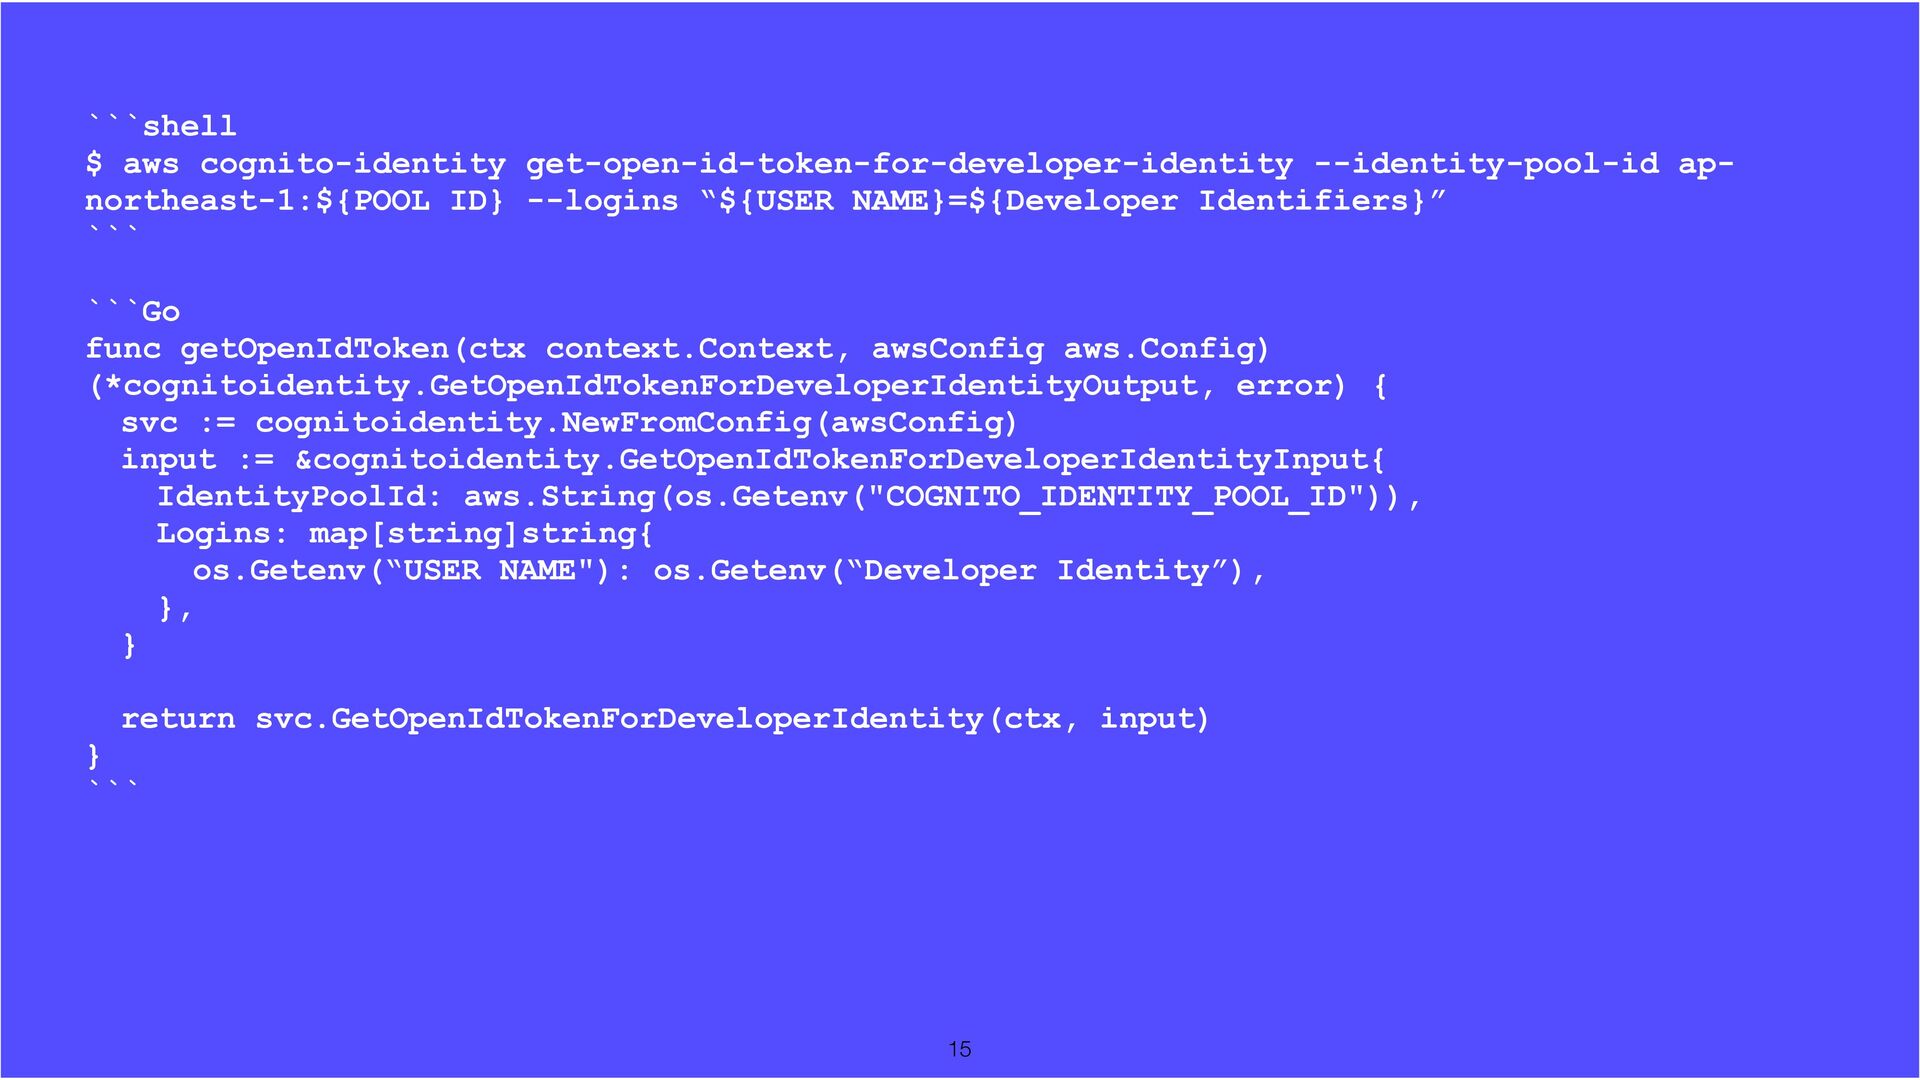
```shell $ aws cognito-identity get-open-id-token-for-developer-identity --identity-pool-id ap- northeast-1:${POOL ID} --logins
“${USER NAME}=${Developer Identifiers}” ``` ```Go func getOpenIdToken(ctx context.Context, awsConfig aws.Config) (*cognitoidentity.GetOpenIdTokenForDeveloperIdentityOutput, error) { svc := cognitoidentity.NewFromConfig(awsConfig) input := &cognitoidentity.GetOpenIdTokenForDeveloperIdentityInput{ IdentityPoolId: aws.String(os.Getenv("COGNITO_IDENTITY_POOL_ID")), Logins: map[string]string{ os.Getenv(“USER NAME"): os.Getenv(“Developer Identity”), }, } return svc.GetOpenIdTokenForDeveloperIdentity(ctx, input) } ``` 15 -
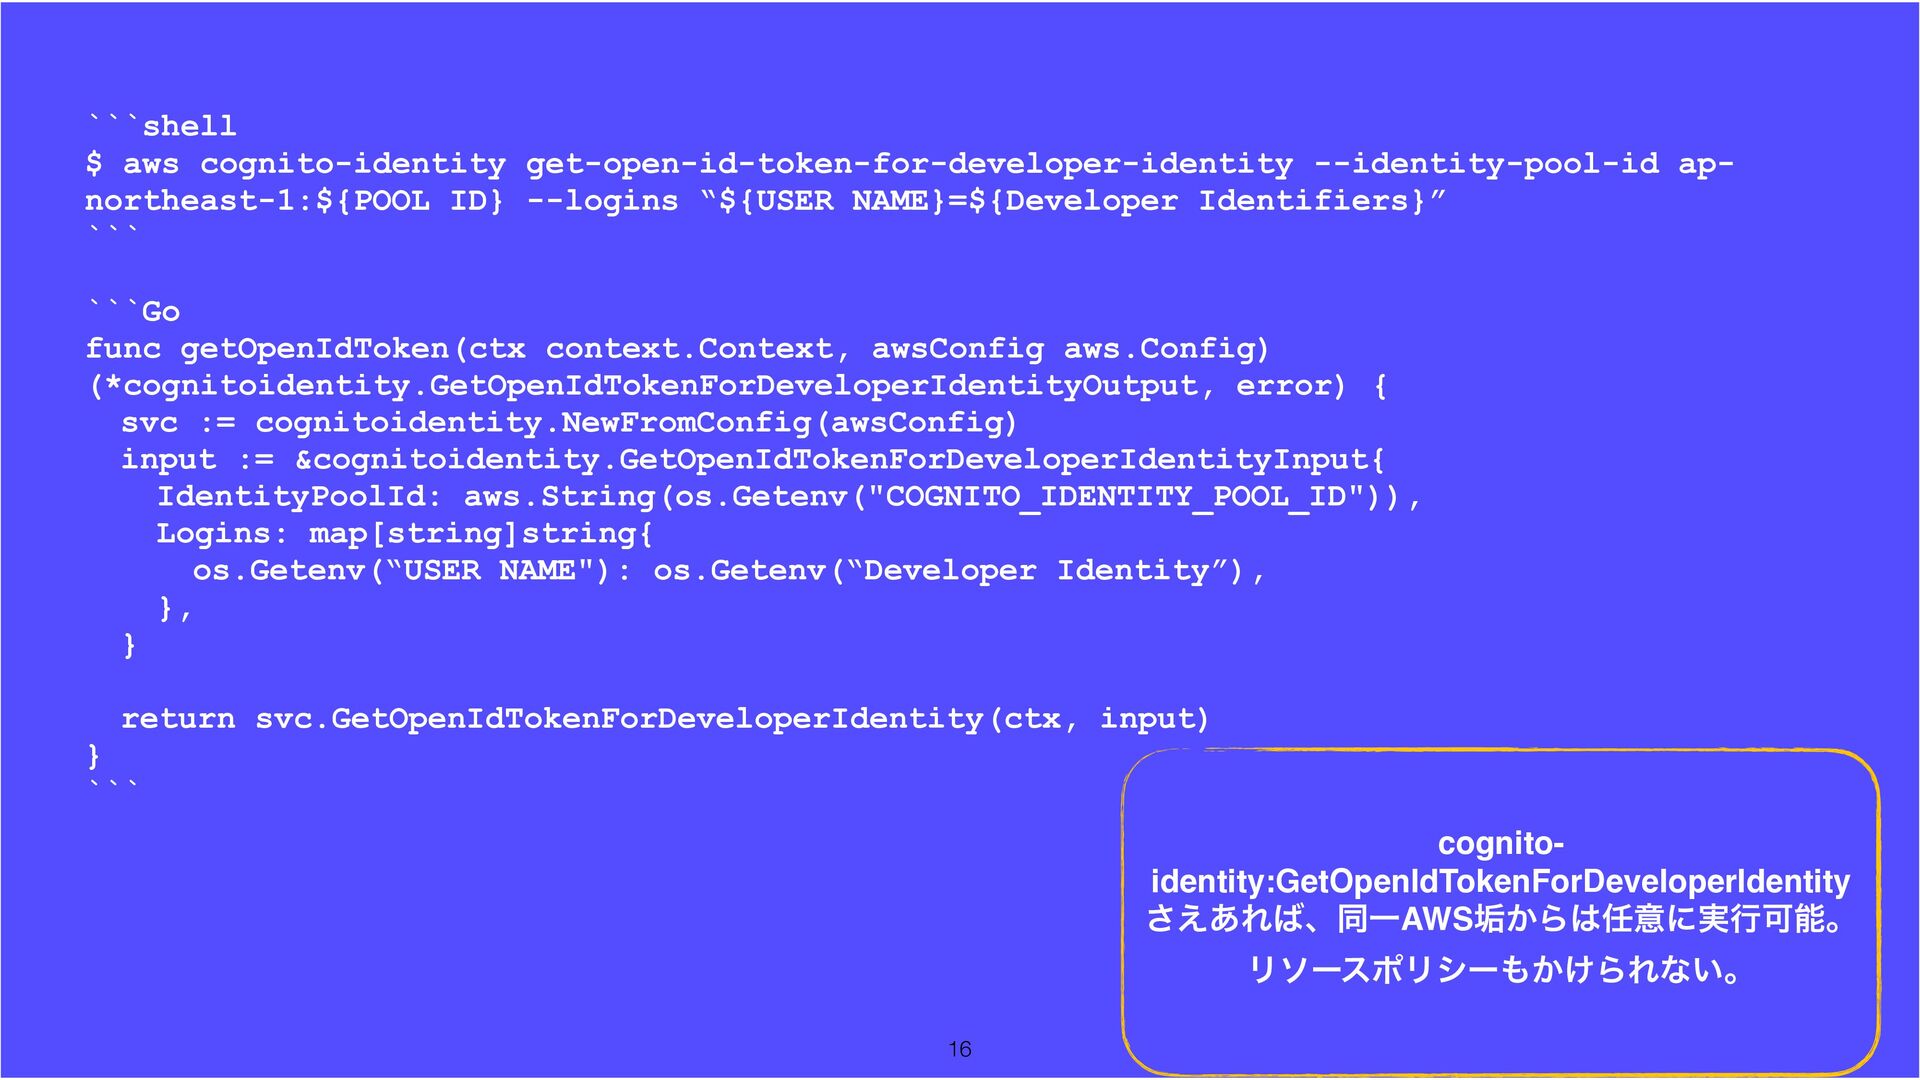
```shell $ aws cognito-identity get-open-id-token-for-developer-identity --identity-pool-id ap- northeast-1:${POOL ID} --logins
“${USER NAME}=${Developer Identifiers}” ``` ```Go func getOpenIdToken(ctx context.Context, awsConfig aws.Config) (*cognitoidentity.GetOpenIdTokenForDeveloperIdentityOutput, error) { svc := cognitoidentity.NewFromConfig(awsConfig) input := &cognitoidentity.GetOpenIdTokenForDeveloperIdentityInput{ IdentityPoolId: aws.String(os.Getenv("COGNITO_IDENTITY_POOL_ID")), Logins: map[string]string{ os.Getenv(“USER NAME"): os.Getenv(“Developer Identity”), }, } return svc.GetOpenIdTokenForDeveloperIdentity(ctx, input) } ``` 16 cognito- identity:GetOpenIdTokenForDeveloperIdentity ͑͋͞ΕɺಉҰAWS͔Βҙʹ࣮ߦՄೳɻ ϦιʔεϙϦγʔ͔͚ΒΕͳ͍ɻ -
- ʮෳͷϫʔΫϩʔυʹରͯ͠ෳͷύϒϦοΫ Ϋϥυ ϕϯμʔ͕ఏڙ ͢ΔΫϥυ ίϯϐϡʔςΟϯά αʔϏεΛ༻͢Δ͜ͱΛࢦ͠·͢ʯ - By https://cloud.google.com/learn/what-is-multicloud
- 2006: - AWS(β), Google Apps for Your Domain(ݱGoogle Workspaces)ొ - 2024: - Azure, GC, AWS, Oracle, Cloud fl are…. ϚϧνΫϥυɹͱ -
- ͢ͰʹσϑΝΫτͳαʔϏε͕͋Δ߹ - ൺֱత৽͍ٕ͠ज़ίϯηϓτʹ͓͚Δαϙʔτͷ༗ແ - Con fi dential ComputingɺLLM -
৽͍͠ϢʔεέʔεΛ࣮͢Δࡍͷαϙʔτͷ༗ແ - Google Workspacesͷࠪϩάʹ͓͚ΔBigQueryͰͷσʔλੳ - App Runner͕ͳ͍ͱ͖ɾ͋Δ͍ग़ͨͱ͖ͷGC Cloud Run WhyϚϧνΫϥυ-ಛఆͷػೳ - αʔϏεͰͷ༏Ґੑ -
- ਓؒʹΑΔೝূ - ͪ͜ΒSAMLͱ͔OIDCͰ৭ʑ͋Δ - ඇਓؒతʁͳೝূ - Cloud workload: -
ʮA logical bundle of software and data that is present in, and processed by, a cloud computing technologyʯ - https://csrc.nist.gov/glossary/term/cloud_workload - AWSͰɺEC2ɺLambdaɺApp RunnerɺECS Service - ࠓճͪ͜Β ೝূͷதͰϫʔΫϩʔυ -
- ͋Μ·ΓେࣄͰͳ͍ͷͰɺ༁͔Βͯ͠·ͤΜ͕ɺ - AAL1: - ཁٻऀ͕ՃೖऀͷΞΧϯτʹඥ͚ΒΕͨೝূثΛ੍ޚ͍ͯ͠Δ͜ͱʹରͯ͋͠ΔఔͷอূΛఏڙ͠·͢ɻ AAL1Ͱɺൣͳೝূٕज़Λ༻ͯ͠ɺγϯάϧϑΝΫλʔ·ͨϚϧνϑΝΫλʔೝূͷ͍ͣΕ͔Λཁٻ͠· ͢ɻೝূͷޭʹɺཁٻऀ͕҆શͳೝূϓϩτίϧΛ௨ͯ͡ɺೝূثͷॴ࣋ͱ੍ޚΛূ໌͢Δඞཁ͕͋Γ·͢. - AAL
2: - ཁٻऀ͕ՃೖऀͷΞΧϯτʹඥ͚ΒΕͨೝূثΛ੍ޚ͍ͯ͠Δ͜ͱʹରͯ͠ߴ͍৴པΛఏڙ͠·͢ɻೝূͷ ޭʹɺ҆શͳೝূϓϩτίϧΛ௨ͯ͡ɺҟͳΔ2ͭͷೝূཁૉͷॴ࣋ͱ੍ޚΛূ໌͢Δඞཁ͕͋Γ·͢ɻ AAL2͓ΑͼͦΕҎ্Ͱɺঝೝ͞Εͨ҉߸ٕज़͕ඞཁͰ͢ɻ - AAL 3: - ཁٻऀ͕ՃೖऀͷΞΧϯτʹඥ͚ΒΕͨೝূثΛ੍ޚ͍ͯ͠Δ͜ͱʹରͯ͠ඇৗʹߴ͍৴པΛఏڙ͠·͢ɻ AAL3ͷೝূɺ҉߸ϓϩτίϧΛ௨ͨ͡伴ͷॴ࣋ͷূ໌ʹج͍͍ͮͯ·͢ɻAAL3ͷೝূʹɺϋʔυΣΞϕʔ εͷೝূثͱɺݕূऀͳΓ͢·͠ੑΛఏڙ͢Δೝূث͕ඞཁͰ͢ɻಉ͡σόΠε͕͜ΕΒͷཁ݅Λ྆ํຬͨ͢ ͜ͱՄೳͰ͢ɻAAL3Ͱೝূ͢ΔͨΊʹɺཁٻऀ͕҆શͳೝূϓϩτίϧΛ௨ͯ͡ɺ2ͭͷҟͳΔೝূཁૉͷ ॴ࣋ͱ੍ޚΛূ໌͢Δඞཁ͕͋Γ·͢ɻঝೝ͞Εͨ҉߸ٕज़͕ඞཁͰ͢ ೝূͷڧʢAuthenticator Assurance Levelʣ -
Requirement AAL1 AAL2 AAL3 Permitted authenticator types Memorized Secret; Look-up
Secret; Out-of-Band; SF OTP Device; MF OTP Device; SF Crypto Software; SF Crypto Device; MF Crypto Software; MF OTP Device; MF Crypto Software; MF Crypto Device; or Memorized Secret plus: • Look-up Secret • Out-of-Band • SF OTP Device • SF Crypto Software MF Crypto Device; SF Crypto Device plus Memorized Secret; SF OTP Device plus MF Crypto Device or Software; SF OTP Device plus SF Crypto Software plus Memorized Secret Reauthentication 30 days 12 hours or 30 minutes inactivity; MAY use one authentication factor 12 hours or 15 minutes inactivity; SHALL use both authentication factors Security controls SP 800-53 Low Baseline (or equivalent) SP 800-53 Moderate Baseline (or equivalent) SP 800-53 High Baseline (or equivalent) Veri fi er- impersonation resistance Not required Not required Required Veri fi er-compromise resistance Not required Not required Required Replay resistance Not required Required Required Authentication intent Not required Recommended Required https://pages.nist.gov/800-63-3/sp800-63b.html#sec4 -
- FAL1: - Ճೖऀ͕RP(Relying Party)ʹରͯ͠Bearer AssetionΛड͚औΔ͜ͱΛڐՄ͠·͢ɻ͜ͷ Assertionɺঝೝ͞Εͨ҉߸ٕज़Λ༻ͯ͠IdPʹΑͬͯॺ໊͞Ε·͢ɻ - FAL2: -
Ξαʔγϣϯ͕ঝೝ͞Εͨ҉߸ٕज़Λ༻ͯ͠҉߸Խ͞ΕɺRP͚͕ͩͦΕΛ෮߸Ͱ͖ΔΑ͏ʹ ͢Δཁ݅ΛՃ͠·͢ - FAL3: - Ճೖऀ͕ɺΞαʔγϣϯࣗମʹՃ͑ͯɺΞαʔγϣϯͰࢀর͞ΕΔ҉߸伴ͷॴ࣋ূ໌Λఏࣔ ͢Δ͜ͱΛཁٻ͠·͢ɻ͜ͷΞαʔγϣϯɺIdPʹΑͬͯॺ໊͞ΕɺೝՄ͞Εͨ҉߸ٕज़Λ ༻ͯ͠RPʹରͯ͠҉߸Խ͞Ε·͢ɻ ೝূ࿈ܞͷڧʢFederation Assurance Levelʣ -
ೝূ࿈ܞͷڧ Requirement FAL1 FAL2 FAL3 Assetion Type Bearer Bearer Holder
of key Signing Not required Signed by IdP Signed by IdP Encryption Not required Encrypted Encrypted -
ೝূ - A-1: Assertion Manufacture or Modi fi cation -
A-2: Theft - A-3: Duplication - A-4: Eavesdropping - A-5: Of fl ine Cracking - A-6: Side Channel Attack - A-7: Phishing or Pharming - A-8: Social engineering - A-9: Online Guessing - A-10: Endpoint Compromise - A-11: Unauthorized Binding ڴҖ https://pages.nist.gov/800-63-3/sp800-63b.html#sec8 ೝূ࿈ܞ - F-1: Assertion Manufacture or Modi fi cation - F-2: Assertion Disclosure - F-3: Assertion Repudiation by the IdP - F-4: Assertion Repudiation by the Subscriber - F-5: Assertion Redirect - F-6: Assertion Reuse - F-7: Assertion Substitution -
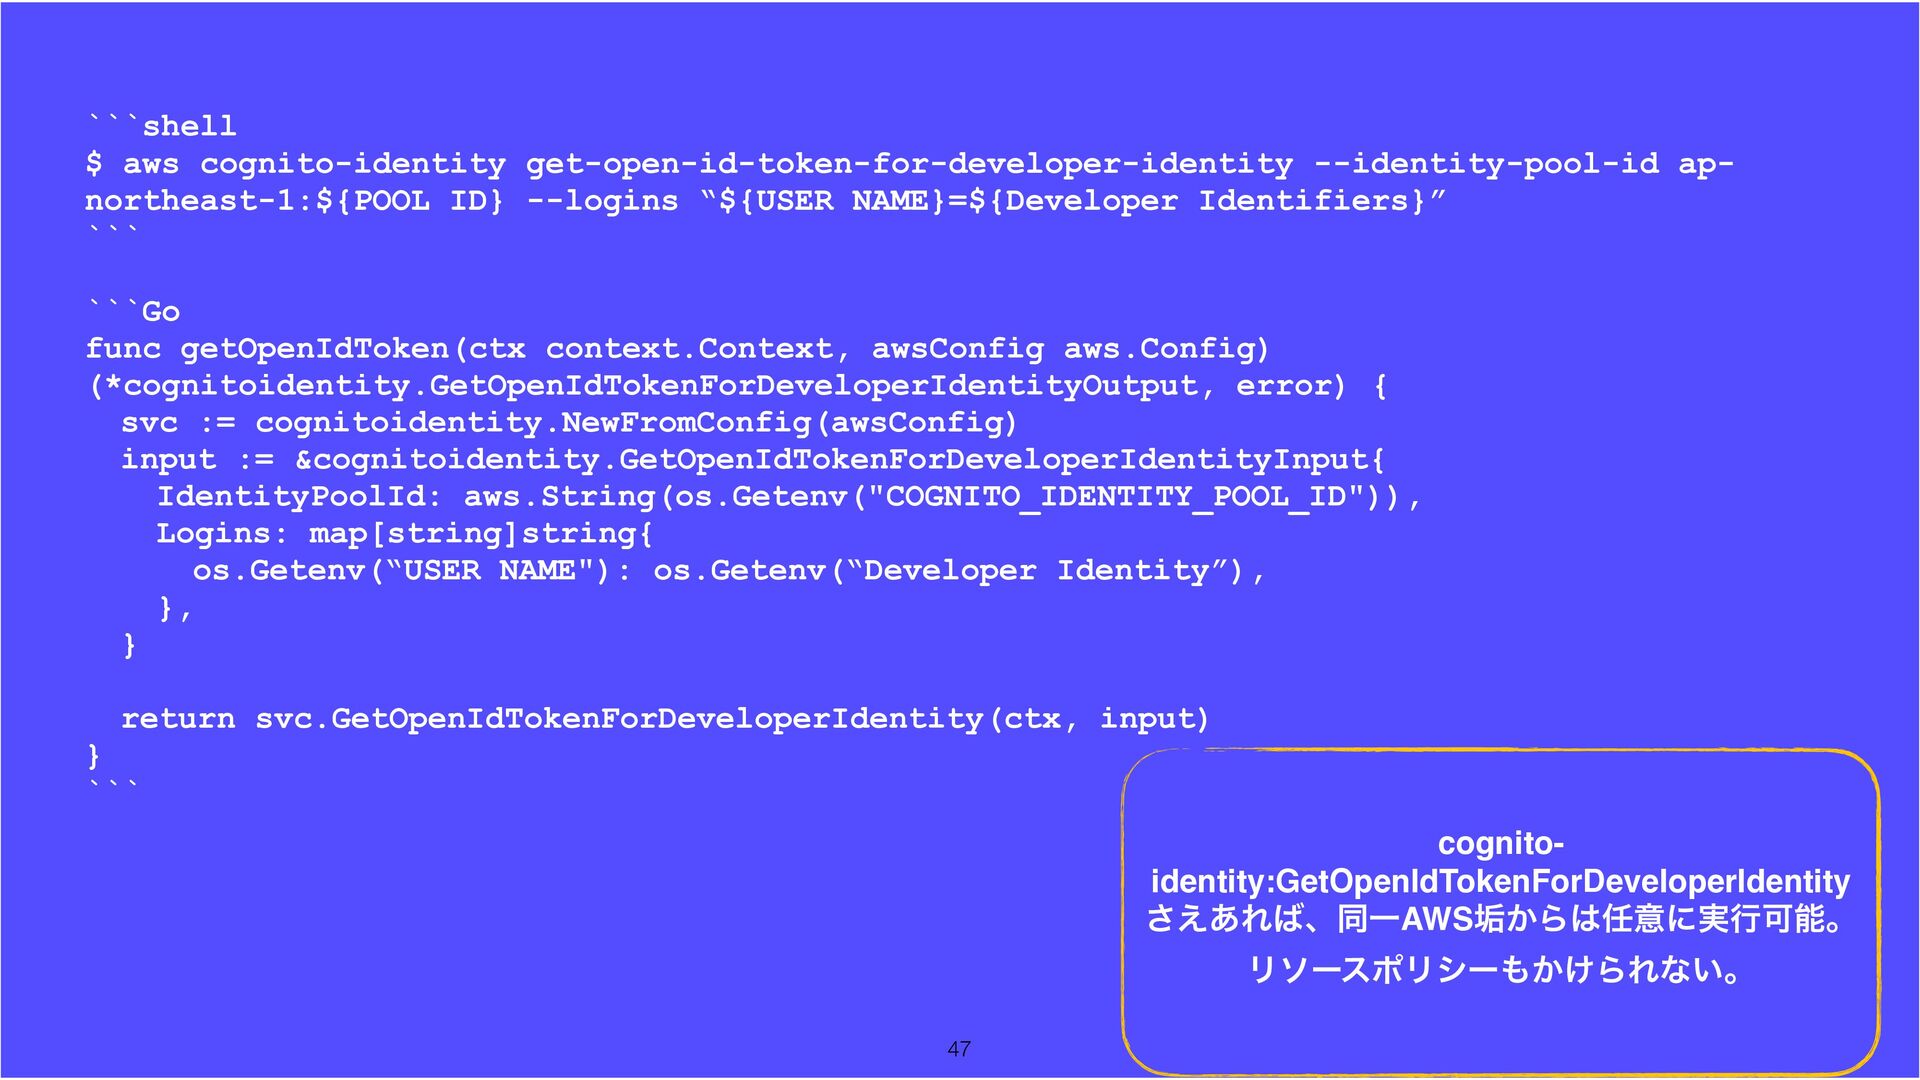
```shell $ aws cognito-identity get-open-id-token-for-developer-identity --identity-pool-id ap- northeast-1:${POOL ID} --logins
“${USER NAME}=${Developer Identifiers}” ``` ```Go func getOpenIdToken(ctx context.Context, awsConfig aws.Config) (*cognitoidentity.GetOpenIdTokenForDeveloperIdentityOutput, error) { svc := cognitoidentity.NewFromConfig(awsConfig) input := &cognitoidentity.GetOpenIdTokenForDeveloperIdentityInput{ IdentityPoolId: aws.String(os.Getenv("COGNITO_IDENTITY_POOL_ID")), Logins: map[string]string{ os.Getenv(“USER NAME"): os.Getenv(“Developer Identity”), }, } return svc.GetOpenIdTokenForDeveloperIdentity(ctx, input) } ``` 47 cognito- identity:GetOpenIdTokenForDeveloperIdentity ͑͋͞ΕɺಉҰAWS͔Βҙʹ࣮ߦՄೳɻ ϦιʔεϙϦγʔ͔͚ΒΕͳ͍ɻ -
Requirement AAL1 AAL2 AAL3 Permitted authenticator types Memorized Secret; Look-up
Secret; Out-of-Band; SF OTP Device; MF OTP Device; SF Crypto Software; SF Crypto Device; MF Crypto Software; MF OTP Device; MF Crypto Software; MF Crypto Device; or Memorized Secret plus: • Look-up Secret • Out-of-Band • SF OTP Device • SF Crypto Software MF Crypto Device; SF Crypto Device plus Memorized Secret; SF OTP Device plus MF Crypto Device or Software; SF OTP Device plus SF Crypto Software plus Memorized Secret Reauthentication 30 days 12 hours or 30 minutes inactivity; MAY use one authentication factor 12 hours or 15 minutes inactivity; SHALL use both authentication factors Security controls SP 800-53 Low Baseline (or equivalent) SP 800-53 Moderate Baseline (or equivalent) SP 800-53 High Baseline (or equivalent) Veri fi er- impersonation resistance Not required Not required Required Veri fi er-compromise resistance Not required Not required Required Replay resistance Not required Required Required Authentication intent Not required Recommended Required https://pages.nist.gov/800-63-3/sp800-63b.html#sec4 -
ೝূ࿈ܞͷڧ Requirement FAL1 FAL2 FAL3 Assetion Type Bearer Bearer Holder
of key Signing Not required Signed by IdP Signed by IdP Encryption Not required Encrypted Encrypted -
Requirement AAL1 AAL2 AAL3 Permitted authenticator types Memorized Secret; Look-up
Secret; Out-of-Band; SF OTP Device; MF OTP Device; SF Crypto Software; SF Crypto Device; MF Crypto Software; MF OTP Device; MF Crypto Software; MF Crypto Device; or Memorized Secret plus: • Look-up Secret • Out-of-Band • SF OTP Device • SF Crypto Software MF Crypto Device; SF Crypto Device plus Memorized Secret; SF OTP Device plus MF Crypto Device or Software; SF OTP Device plus SF Crypto Software plus Memorized Secret Reauthentication 30 days 12 hours or 30 minutes inactivity; MAY use one authentication factor 12 hours or 15 minutes inactivity; SHALL use both authentication factors Security controls SP 800-53 Low Baseline (or equivalent) SP 800-53 Moderate Baseline (or equivalent) SP 800-53 High Baseline (or equivalent) Veri fi er- impersonation resistance Not required Not required Required Veri fi er-compromise resistance Not required Not required Required Replay resistance Not required Required Required Authentication intent Not required Recommended Required https://pages.nist.gov/800-63-3/sp800-63b.html#sec4 -
Requirement AAL1 AAL2 AAL3 Permitted authenticator types Memorized Secret; Look-up
Secret; Out-of-Band; SF OTP Device; MF OTP Device; SF Crypto Software; SF Crypto Device; MF Crypto Software; MF OTP Device; MF Crypto Software; MF Crypto Device; or Memorized Secret plus: • Look-up Secret • Out-of-Band • SF OTP Device • SF Crypto Software MF Crypto Device; SF Crypto Device plus Memorized Secret; SF OTP Device plus MF Crypto Device or Software; SF OTP Device plus SF Crypto Software plus Memorized Secret Reauthentication 30 days 12 hours or 30 minutes inactivity; MAY use one authentication factor 12 hours or 15 minutes inactivity; SHALL use both authentication factors Security controls SP 800-53 Low Baseline (or equivalent) SP 800-53 Moderate Baseline (or equivalent) SP 800-53 High Baseline (or equivalent) Veri fi er- impersonation resistance Not required Not required Required Veri fi er-compromise resistance Not required Not required Required Replay resistance Not required Required Required Authentication intent Not required Recommended Required https://pages.nist.gov/800-63-3/sp800-63b.html#sec4 -
ೝূ࿈ܞͷڧ Requirement FAL1 FAL2 FAL3 Assetion Type Bearer Bearer Holder
of key Signing Not required Signed by IdP Signed by IdP Encryption Not required Encrypted Encrypted ಉ͡Googleͩ͠ -
- Short lived token୯ମͰ҆શੑ͕ܾ·ΔΘ͚Ͱ ͳ͍ - ൃߦϓϩηε੍ݶͳͲΛཧղ͠Α͏ - ϫʔΫϩʔυؒͷΞΫηεͰɺReplay Resistanceཁ݅ʹΑΔߴ͍ϋʔυϧͰɺͳ͔
ͳ͔AALΛຬͨ͢ͷ͕͍͠ɻFALಉ༷ - ͱ͍͑ɺϦεΫ༧͕Ͱ͖ͳ͍ͷ͋ΔɻͲ ͏͢Δ͔ʁ ·ͱΊ