Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Integrating security into an existing agile SDLC
Search
Laura Bell
September 12, 2014
Technology
180
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Integrating security into an existing agile SDLC
Laura Bell
September 12, 2014
More Decks by Laura Bell
See All by Laura Bell
DIY security for the amateur superhero
ladynerd
0
330
Hackcon 11 - Protecting our people
ladynerd
0
270
Security in a container based world
ladynerd
0
170
Securing Microservice Architectures
ladynerd
2
380
Better Connected
ladynerd
0
93
Continuous Security
ladynerd
3
1.2k
Automated Human Vulnerability Scanning with AVA
ladynerd
3
2.8k
Blindsided by security
ladynerd
0
160
Practical tools for privacy audit
ladynerd
0
240
Other Decks in Technology
See All in Technology
How we choose session proposals
kawaguti
PRO
0
170
AWS Continuum for Penetration Testing に Deep Dive してみる
asanoharuki
1
1.3k
CTO Night|NotionのAIエージェントとFDE
kzkhykw1991
0
320
Filter What the LLM Reads: RAG Governance with AgentCore Gateway
yakumo
0
110
Draft AIエージェントの トークン消費を最小化する 8つの原則
kinopeee
5
1.7k
【データ横丁主催】AI エージェント時代のTranslytical Data Platform
shisyu_gaku
0
300
QAエンジニアがSoutherを使ってみたの〜10分でわかるSouther〜
mhlyc
0
120
「作れる」と「リリースできる」の間にあったもの── PdMを外して見えた、PdMがやるべき仕事/Buildable ≠ Shippable: What Removing the PM Taught Me About the PM’s Job
yappli_developers
0
280
「社外イベント=意識高い」の壁を壊せ!元々無関心だった僕らが部内で社外イベントを民主化して15人を連れ出すまで
say_no_w
0
140
[re:Invent2026事前勉強会(有志開催)]続きは、ラスベガスの廊下で / continue-in-the-vegas-hallway
sh_fk2
0
250
ポケモン対戦を自動で記録して振り返ろう
fufufukakaka
0
400
LLM Content Moderationを支える評価・改善ループの実践
suikabar
2
360
Featured
See All Featured
The Hidden Cost of Media on the Web [PixelPalooza 2025]
tammyeverts
2
540
Highjacked: Video Game Concept Design
rkendrick25
PRO
1
490
ReactJS: Keep Simple. Everything can be a component!
pedronauck
666
130k
The untapped power of vector embeddings
frankvandijk
2
2k
Leo the Paperboy
mayatellez
10
2.4k
How to Think Like a Performance Engineer
csswizardry
28
2.9k
Navigating the Design Leadership Dip - Product Design Week Design Leaders+ Conference 2024
apolaine
2
490
How to Grow Your eCommerce with AI & Automation
katarinadahlin
PRO
2
330
Joys of Absence: A Defence of Solitary Play
codingconduct
1
550
Cheating the UX When There Is Nothing More to Optimize - PixelPioneers
stephaniewalter
287
14k
WCS-LA-2024
lcolladotor
0
920
Data-driven link building: lessons from a $708K investment (BrightonSEO talk)
szymonslowik
1
1.4k
Transcript
ARC208
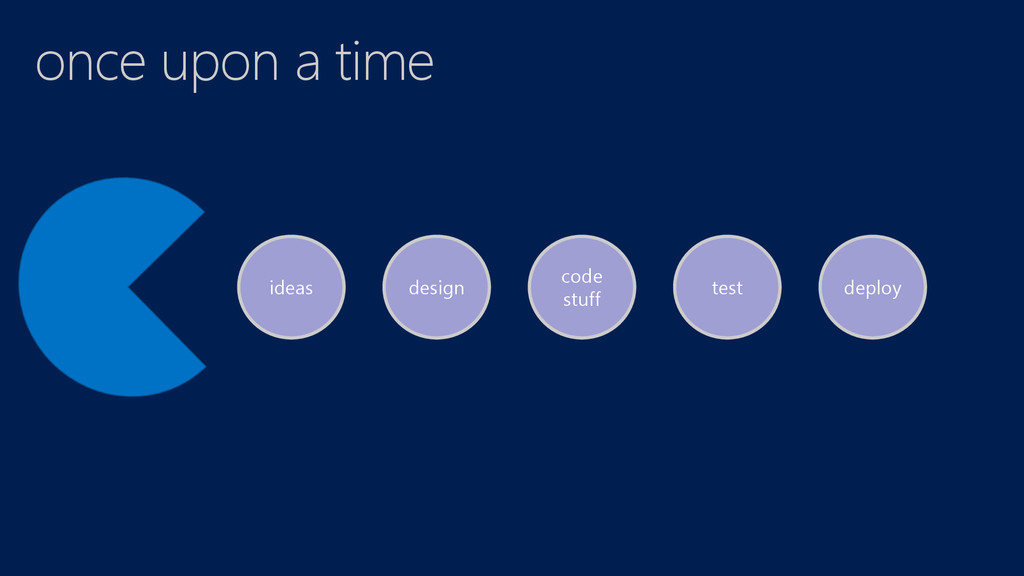
once upon a time design code stuff ideas test deploy
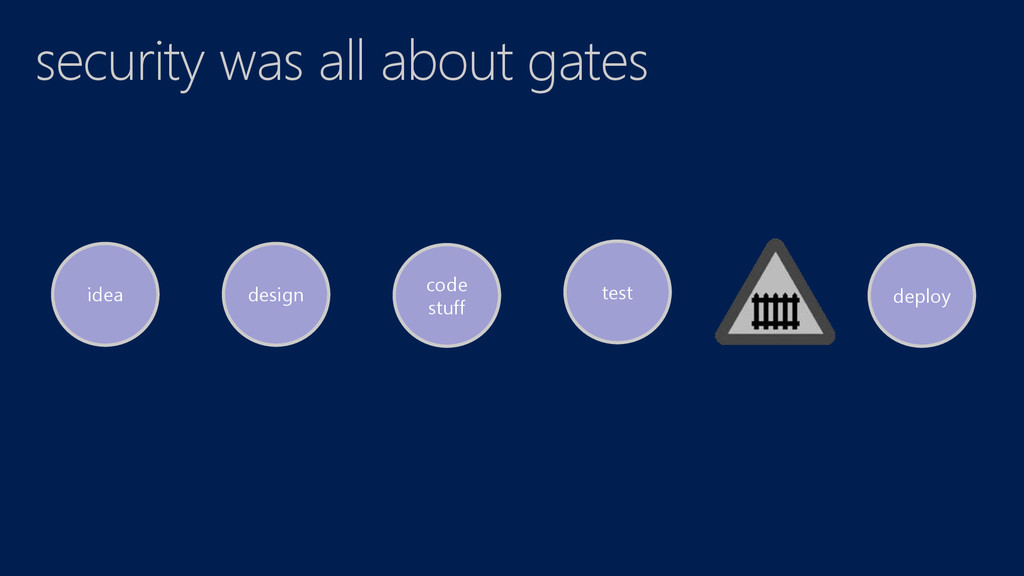
security was all about gates design code stuff idea test
deploy
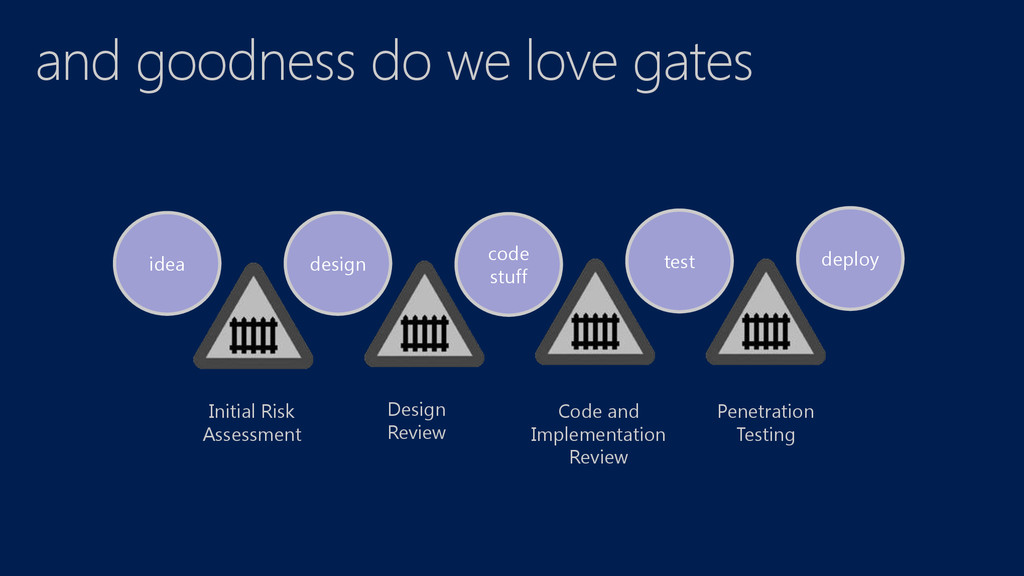
and goodness do we love gates design code stuff idea
test deploy Initial Risk Assessment Design Review Code and Implementation Review Penetration Testing
same thing, just more frequently?
None
Why don’t you do security?
we can make you look good Proactive security engagement increases:
Preparedness Credibility Market awareness Strategic thinking
So what does agile security need to be 1. Able
to empower developers 2. Cost effective 3. Pragmatic and flexible 4. Easy to integrate with existing workflows 5. Scalable
common misconceptions
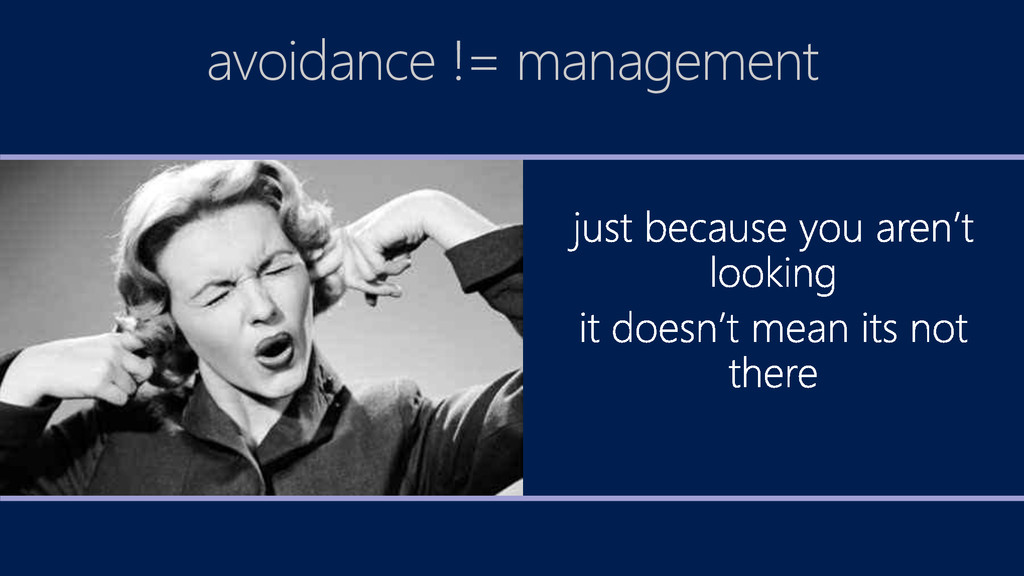
avoidance != management
too little to fail (at security)
the sky is not always falling* *except when it is
(then you should really do something about it)
agility increases risk
Ten steps to a better, stronger and more secure you
regardless of budget, organisation size or how cool you are
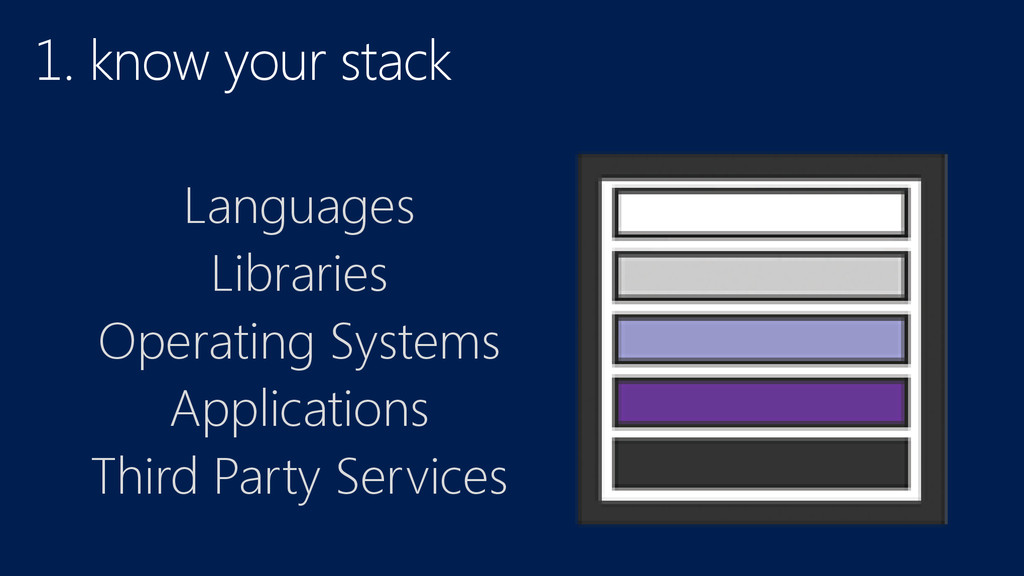
1. know your stack Languages Libraries Operating Systems Applications Third
Party Services
2. learn to add, adapt and abandon
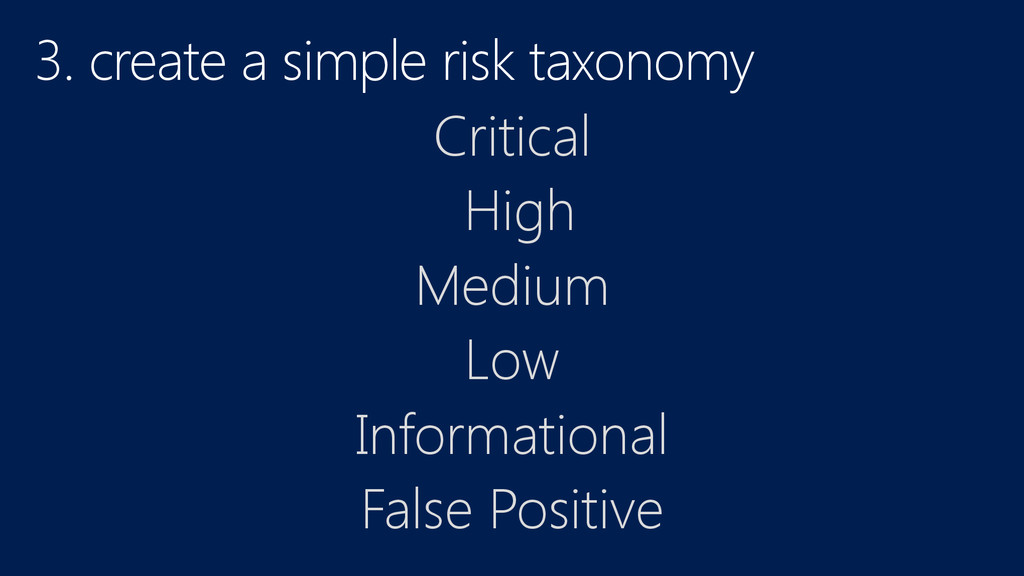
3. create a simple risk taxonomy Critical High Medium Low
Informational False Positive
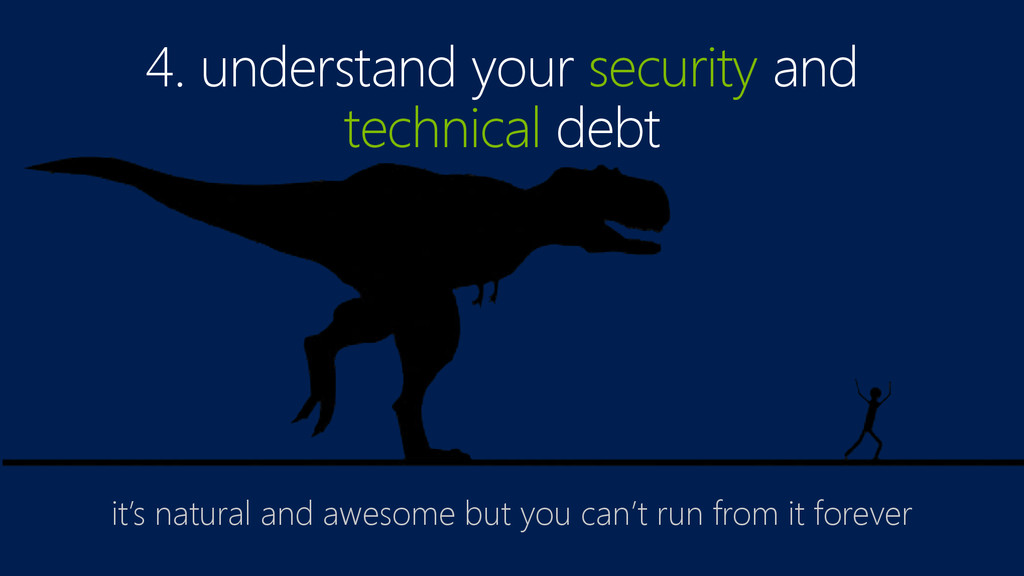
4. understand your security and technical debt it’s natural and
awesome but you can’t run from it forever
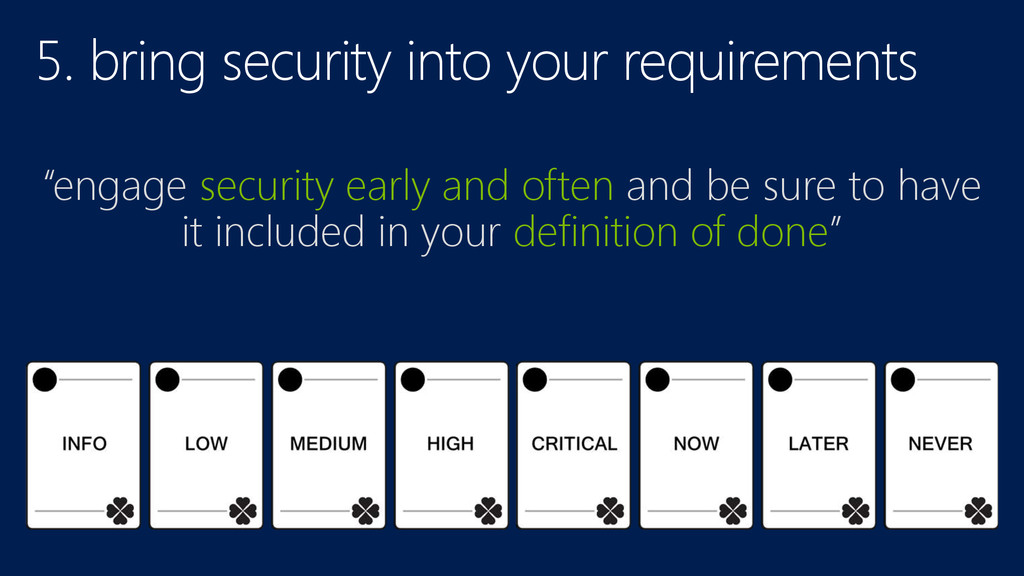
5. bring security into your requirements “engage security early and
often and be sure to have it included in your definition of done”
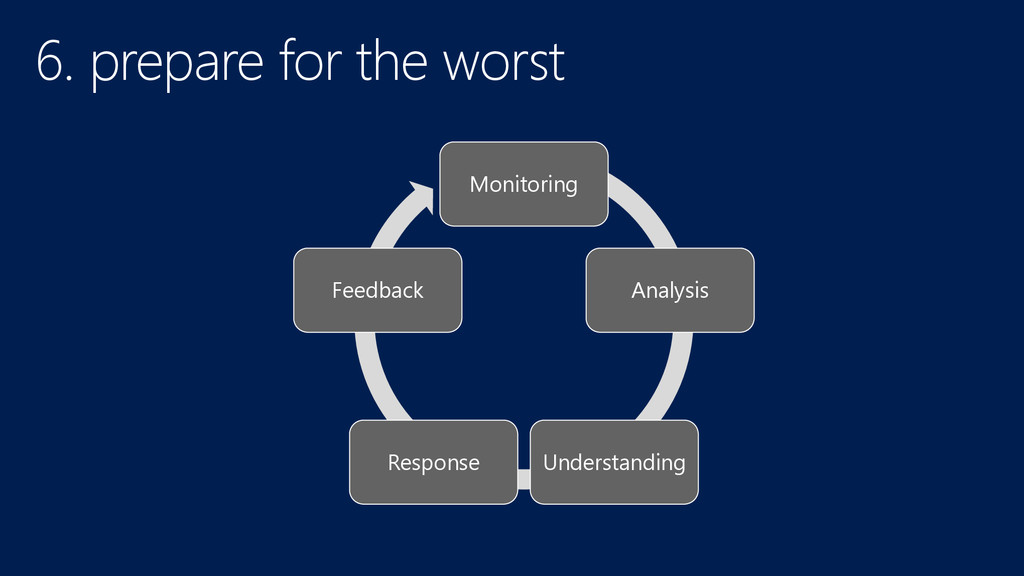
6. prepare for the worst Monitoring Analysis Understanding Response Feedback
7. build an empire one developer at a time
8. design your workflows “the best technical people I know
work really hard to make themselves redundant. “
fails
10. outsource smartly “if you are going to spend the
money, research your options, scope well and be demanding”
common challenges and how to conquer, obliterate or otherwise win
compliance is a priority “nothing is more fatal to a
new business than the fines for non-compliance”
maintain momentum “more secure today than yesterday”
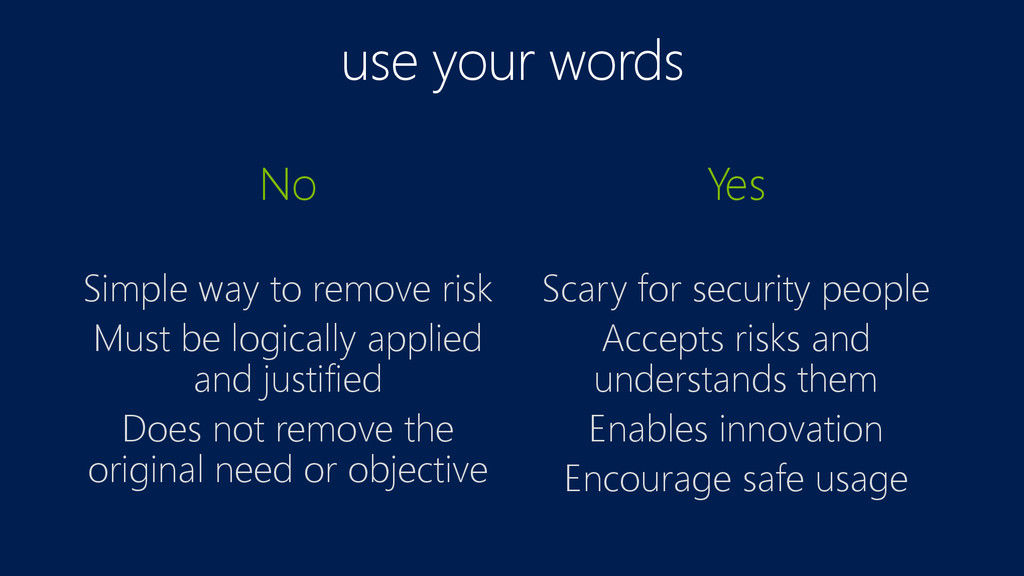
use your words No Simple way to remove risk Must
be logically applied and justified Does not remove the original need or objective Yes Scary for security people Accepts risks and understands them Enables innovation Encourage safe usage
None
Ready to get started? …take a deep breath
None
None


 ladynerd
 kawaguti
 asanoharuki
 kzkhykw1991
 yakumo
 kinopeee
 shisyu_gaku
 mhlyc
 yappli_developers
 say_no_w
 sh_fk2
 fufufukakaka
 suikabar
 tammyeverts
 rkendrick25
 pedronauck
 frankvandijk
 mayatellez
 csswizardry
 apolaine
 katarinadahlin
 codingconduct
 stephaniewalter
 lcolladotor
 szymonslowik