Share
Embed
Usable Access Control in Cloud Management Systems
Master's thesis of Science and Technology presentation at Aalto University
The thesis is published at: https://github.com/luxas/research
Presentation date: May 22, 2025
Lucas Käldström
May 22, 2025
Transcript
69 slides
-
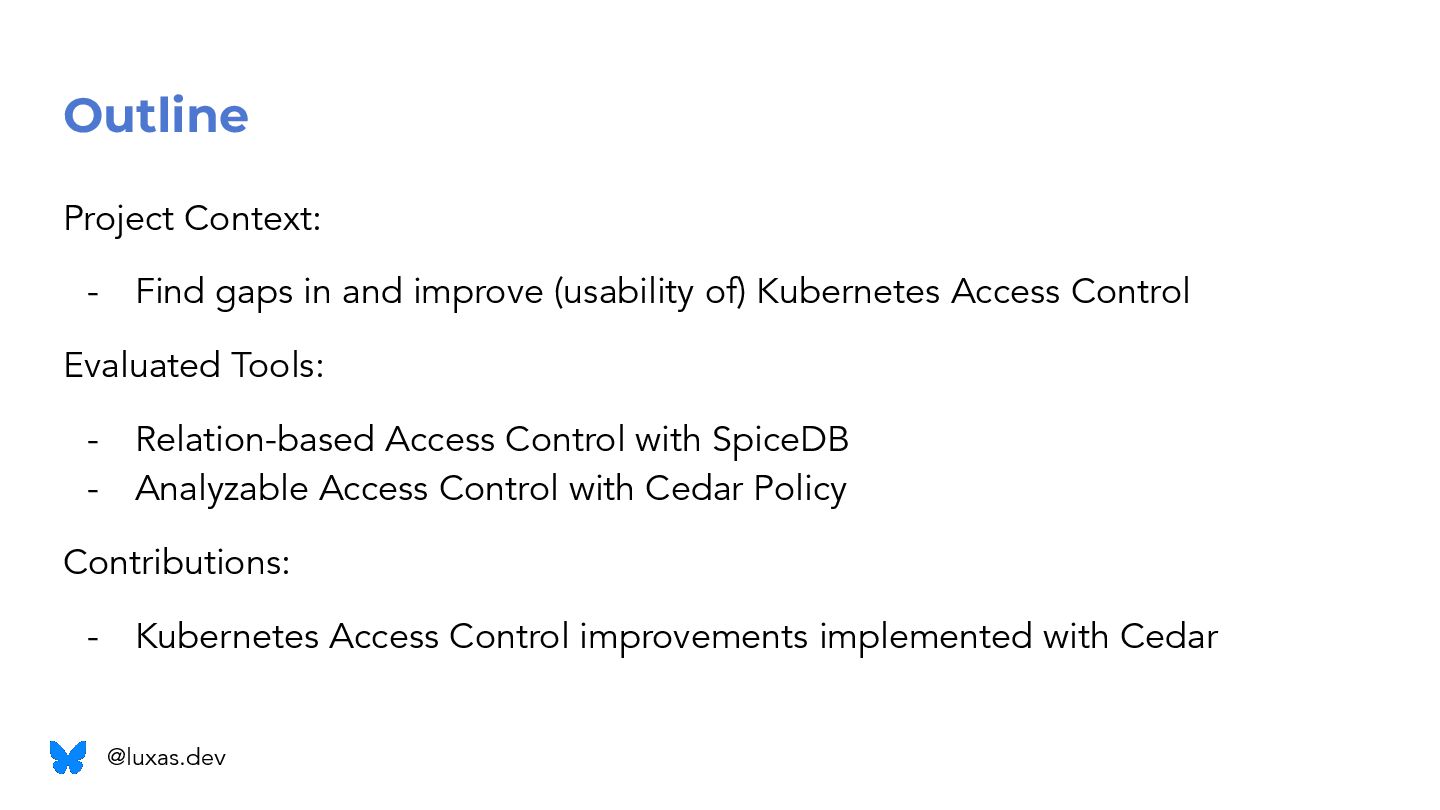
Outline Project Context: - Find gaps in and improve (usability
of) Kubernetes Access Control Evaluated Tools: - Relation-based Access Control with SpiceDB - Analyzable Access Control with Cedar Policy Contributions: - Kubernetes Access Control improvements implemented with Cedar @luxas.dev -
Production-grade Container Orchestrator Released as open source by Google in
2014, donated to Kubernetes @luxas.dev Published 2013 and 2015 -
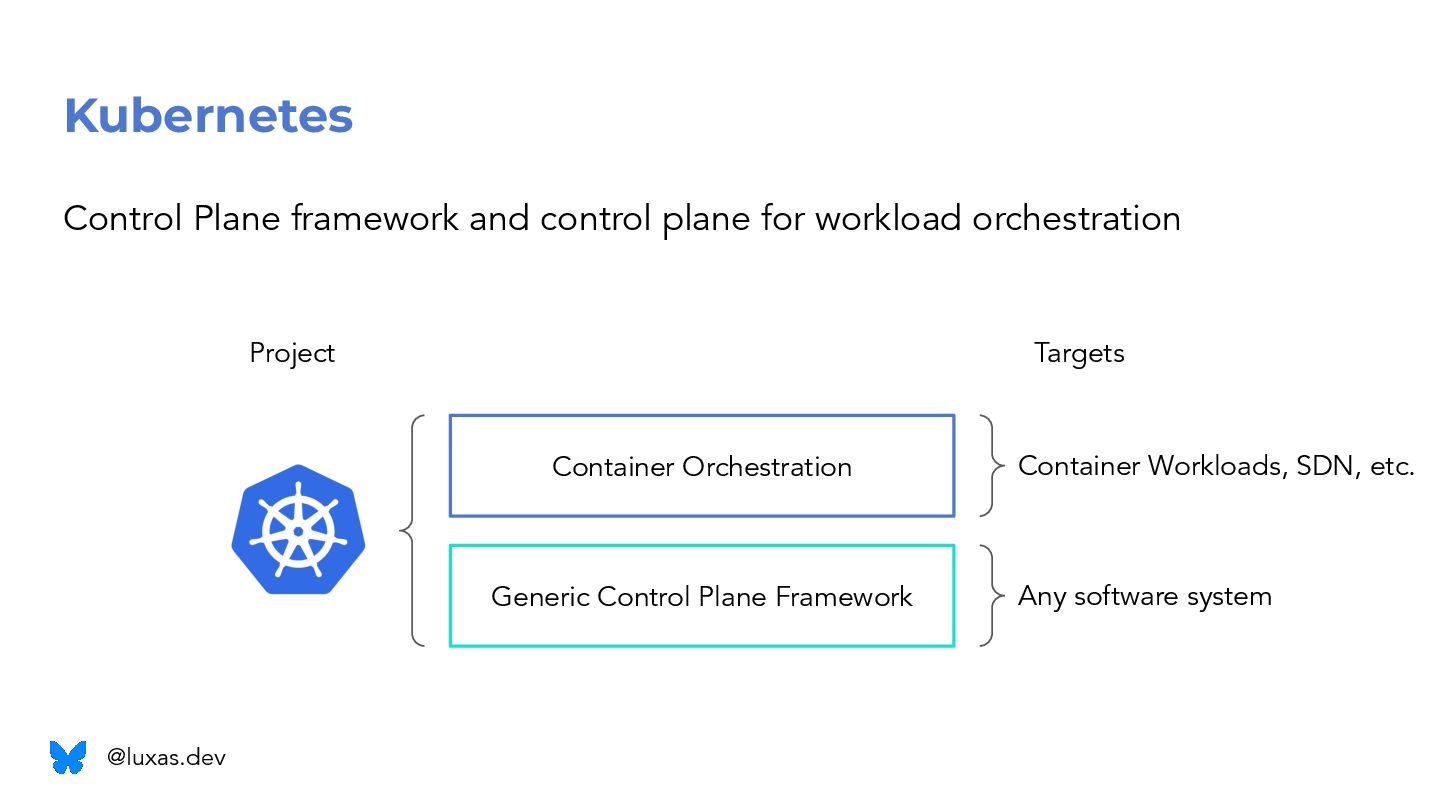
Kubernetes Control Plane framework and control plane for workload orchestration
@luxas.dev Generic Control Plane Framework Container Orchestration Project Targets Any software system Container Workloads, SDN, etc. -
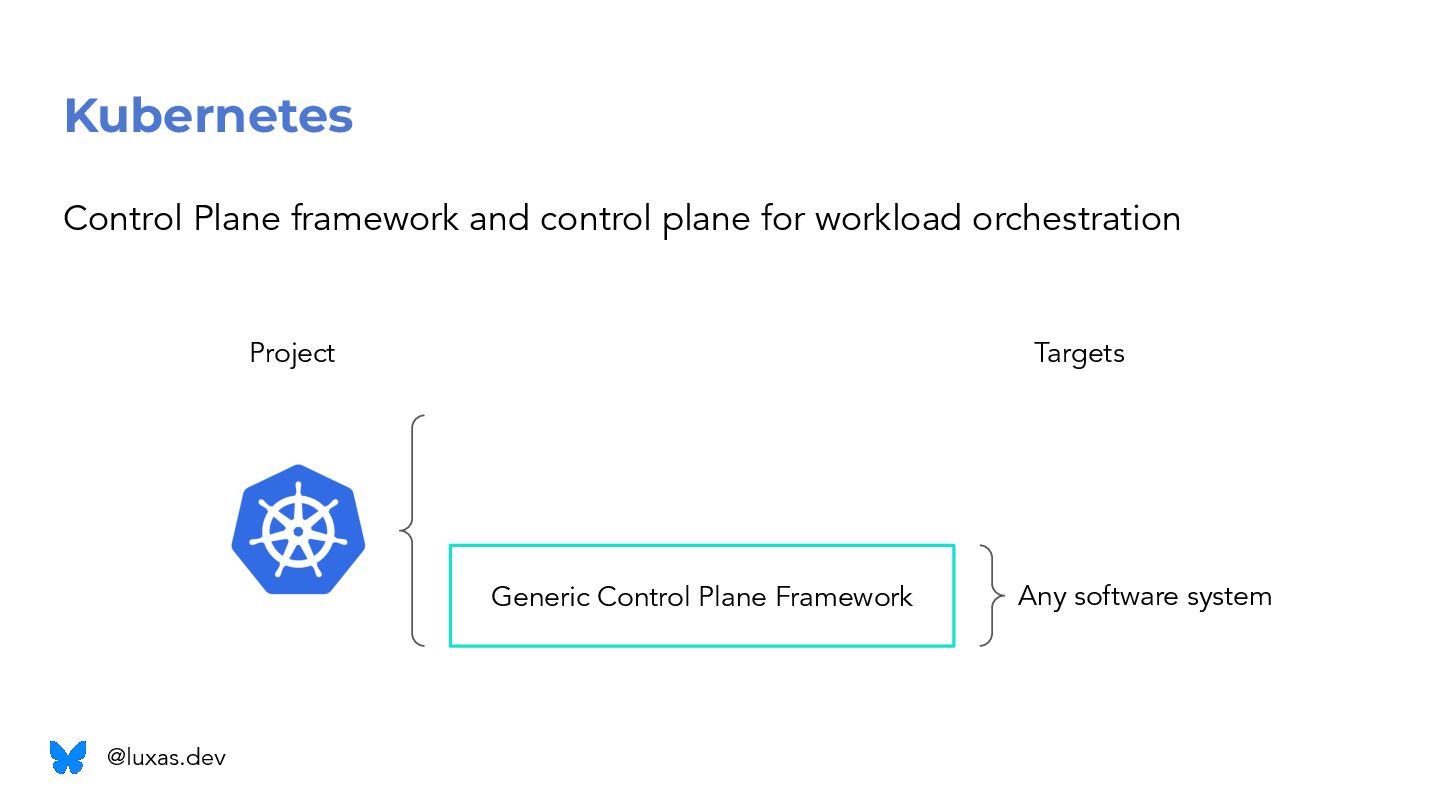
Kubernetes Control Plane framework and control plane for workload orchestration
@luxas.dev Generic Control Plane Framework Project Targets Any software system -
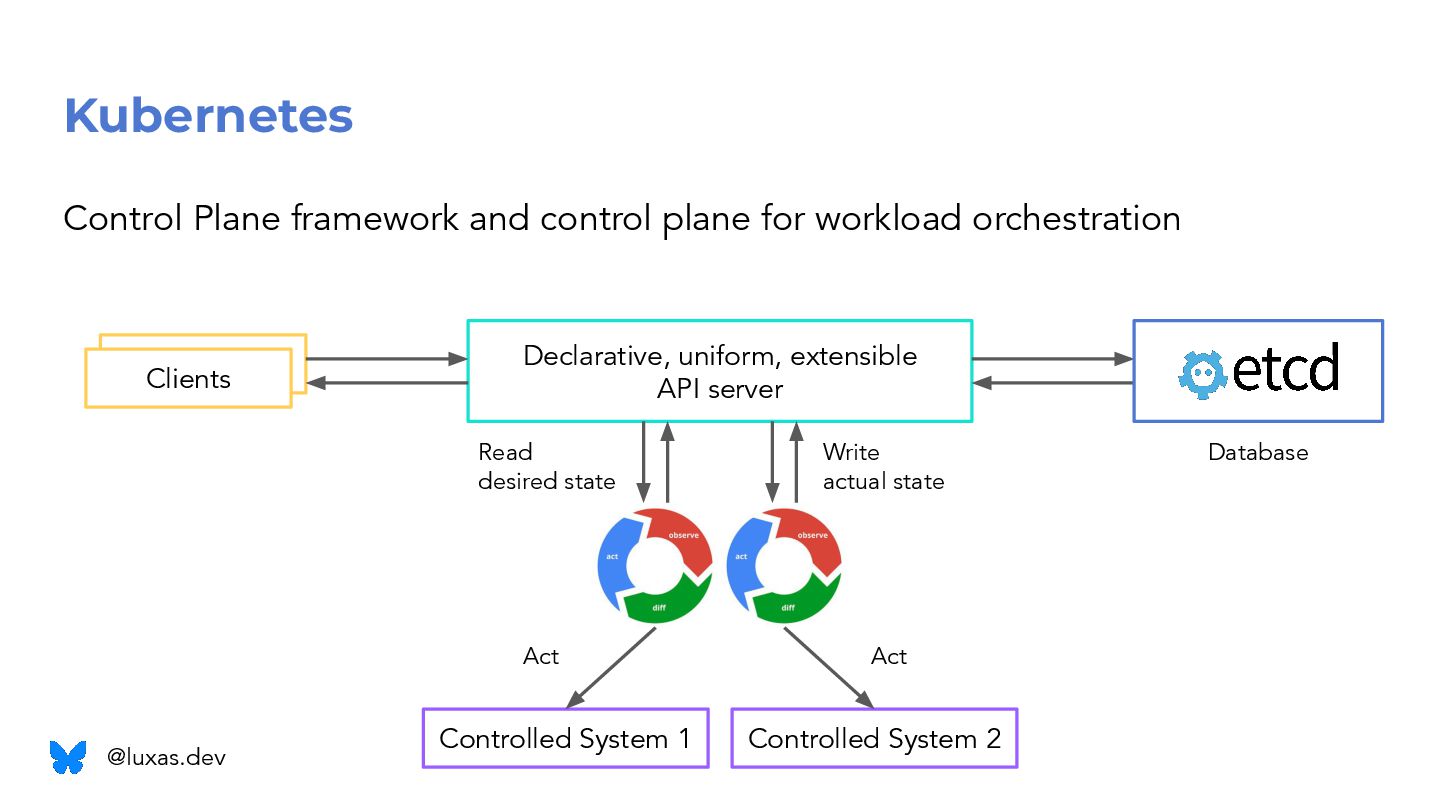
Kubernetes Control Plane framework and control plane for workload orchestration
@luxas.dev Declarative, uniform, extensible API server Clients Clients Controlled System 1 Read desired state Controlled System 2 Write actual state Act Act Database -
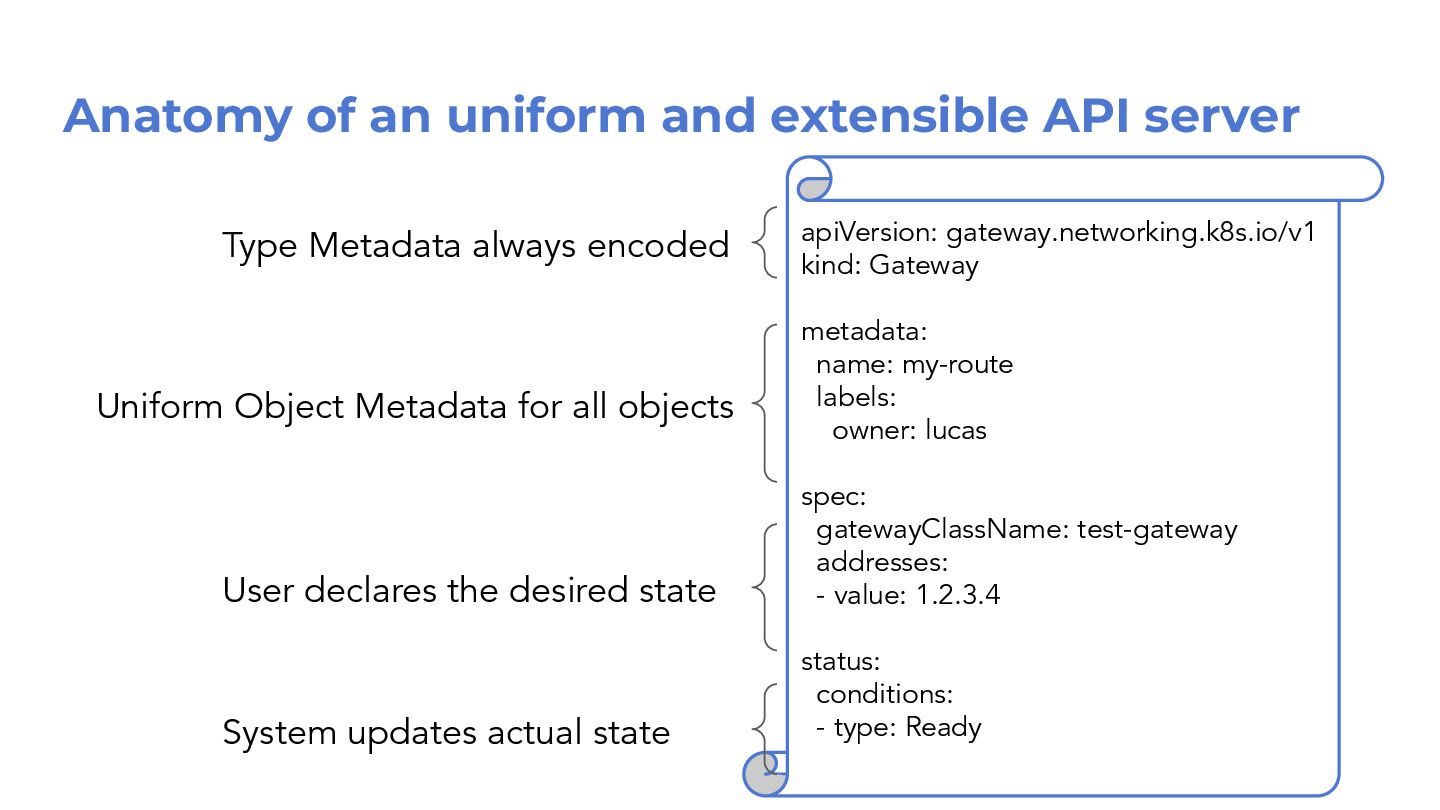
Anatomy of an uniform and extensible API server apiVersion: gateway.networking.k8s.io/v1
kind: Gateway metadata: name: my-route labels: owner: lucas spec: gatewayClassName: test-gateway addresses: - value: 1.2.3.4 status: conditions: - type: Ready Type Metadata always encoded Uniform Object Metadata for all objects User declares the desired state System updates actual state -
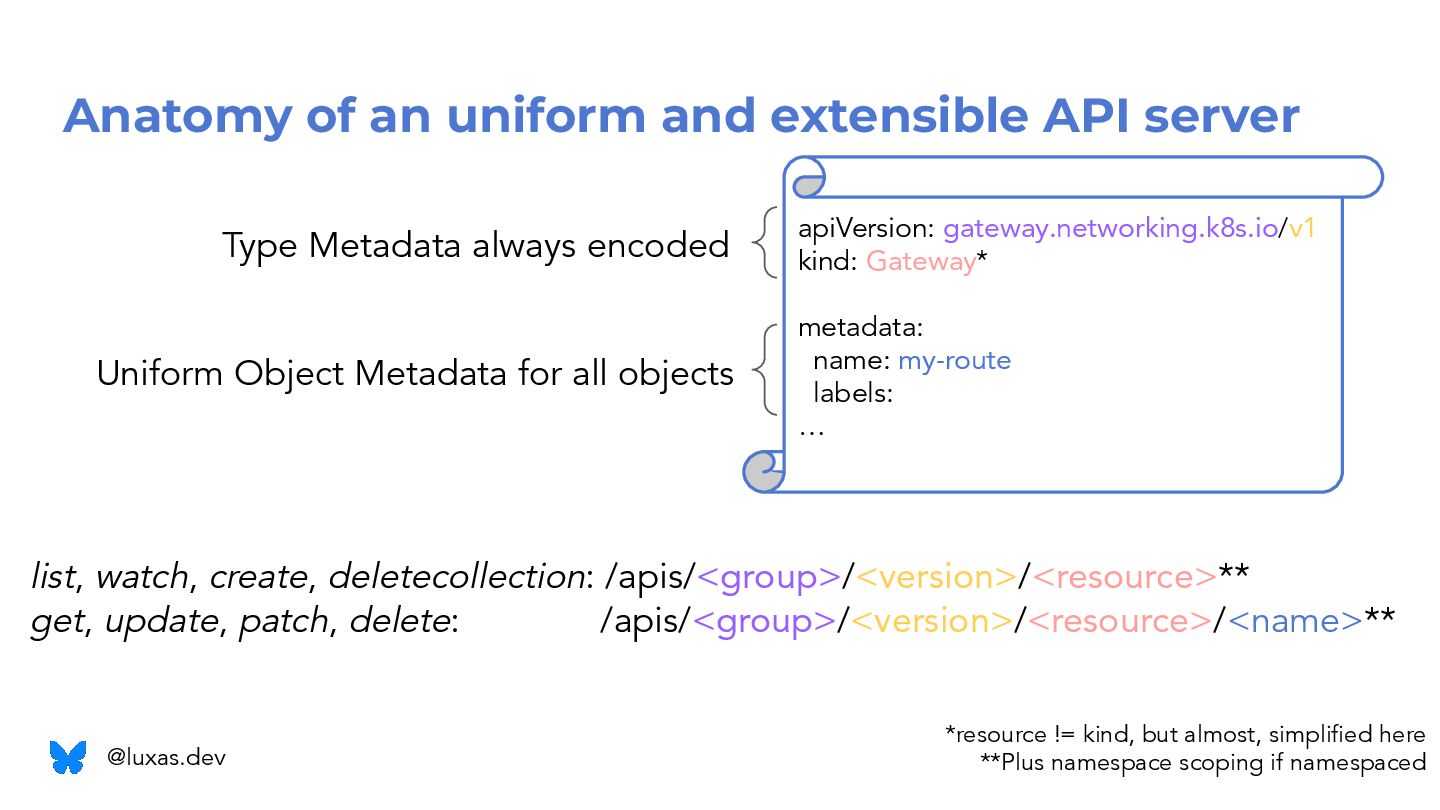
Anatomy of an uniform and extensible API server apiVersion: gateway.networking.k8s.io/v1
kind: Gateway* metadata: name: my-route labels: … Type Metadata always encoded Uniform Object Metadata for all objects list, watch, create, deletecollection: /apis/<group>/<version>/<resource>** get, update, patch, delete: /apis/<group>/<version>/<resource>/<name>** *resource != kind, but almost, simplified here **Plus namespace scoping if namespaced @luxas.dev -
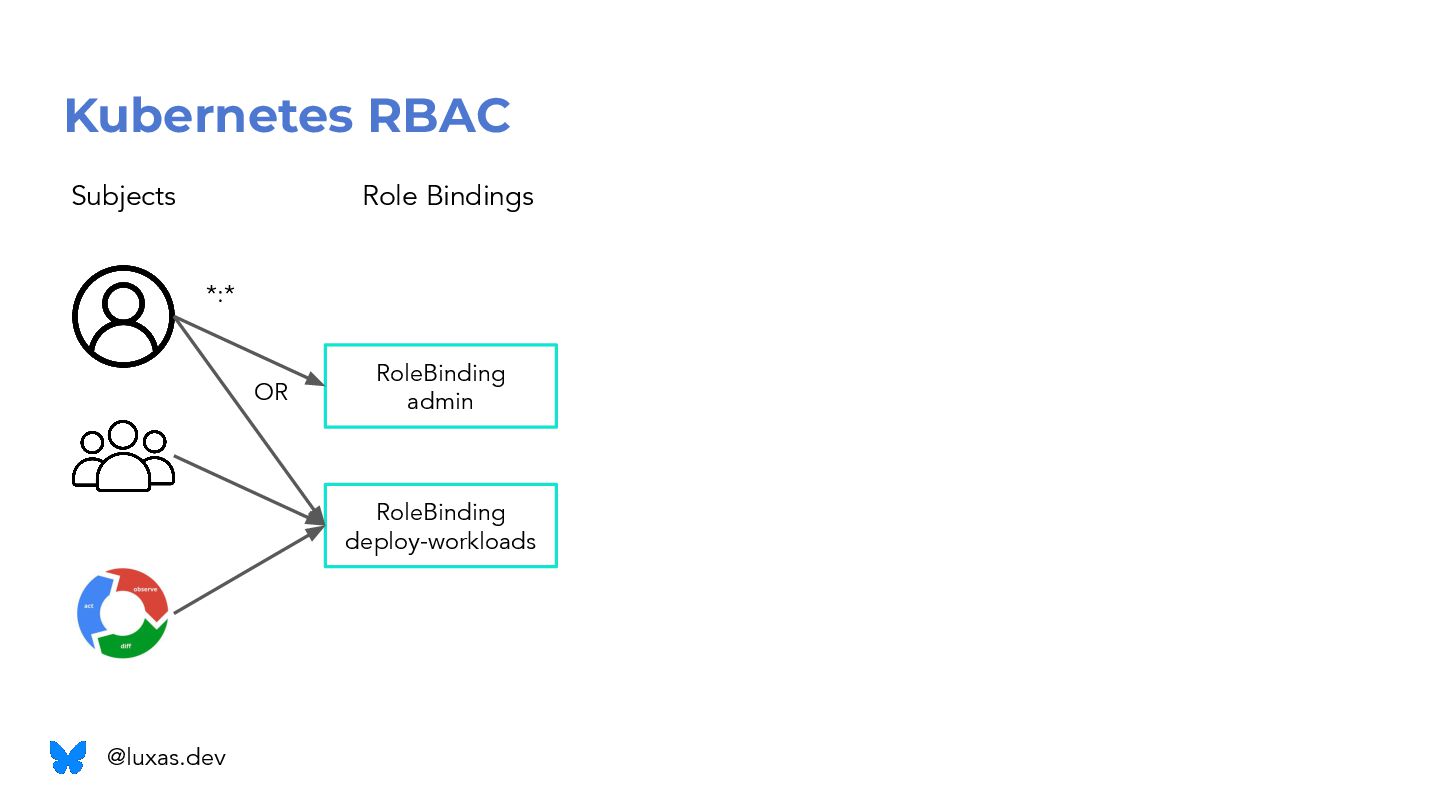
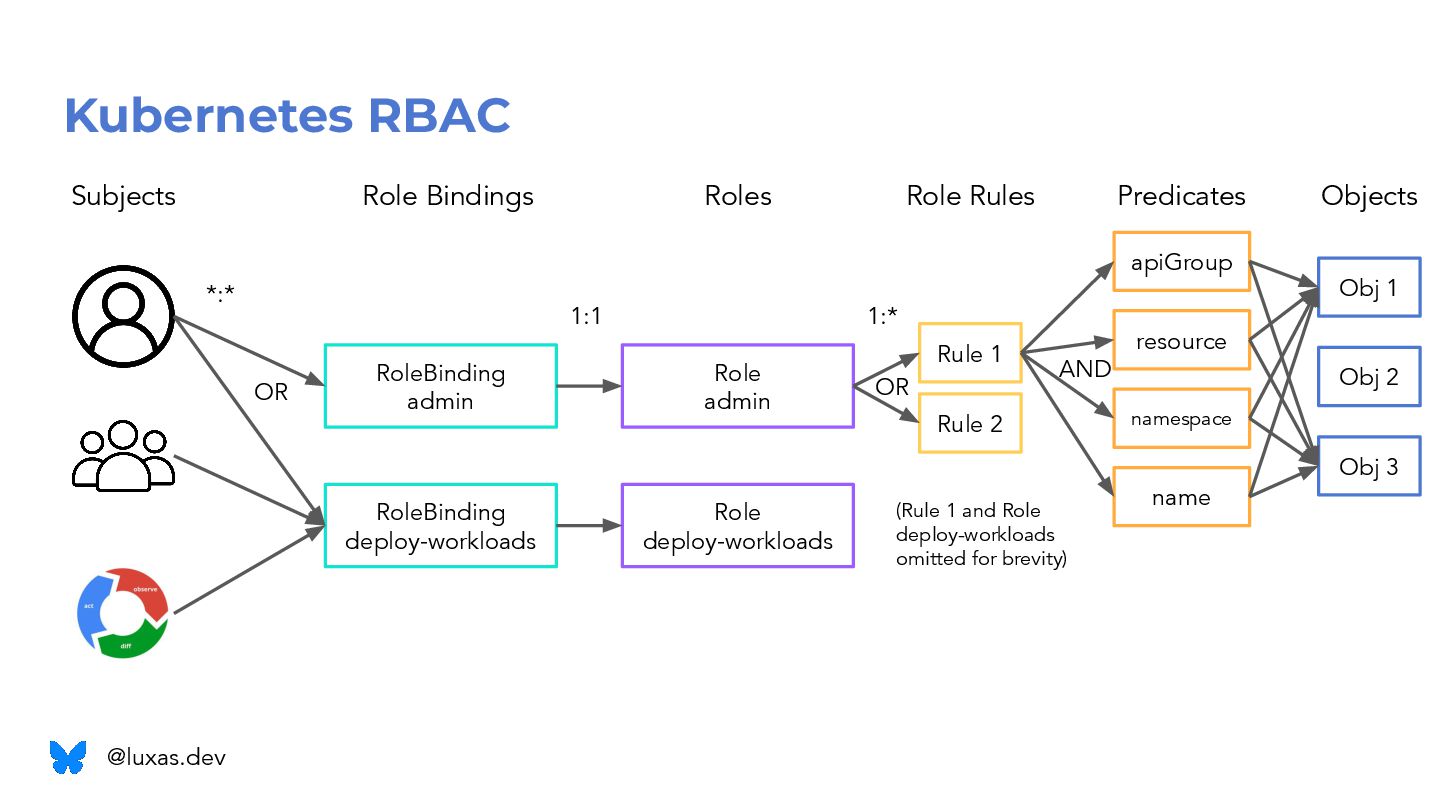
Kubernetes RBAC Subjects RoleBinding admin RoleBinding deploy-workloads Role admin Role
deploy-workloads 1:1 *:* OR Role Bindings Roles @luxas.dev -
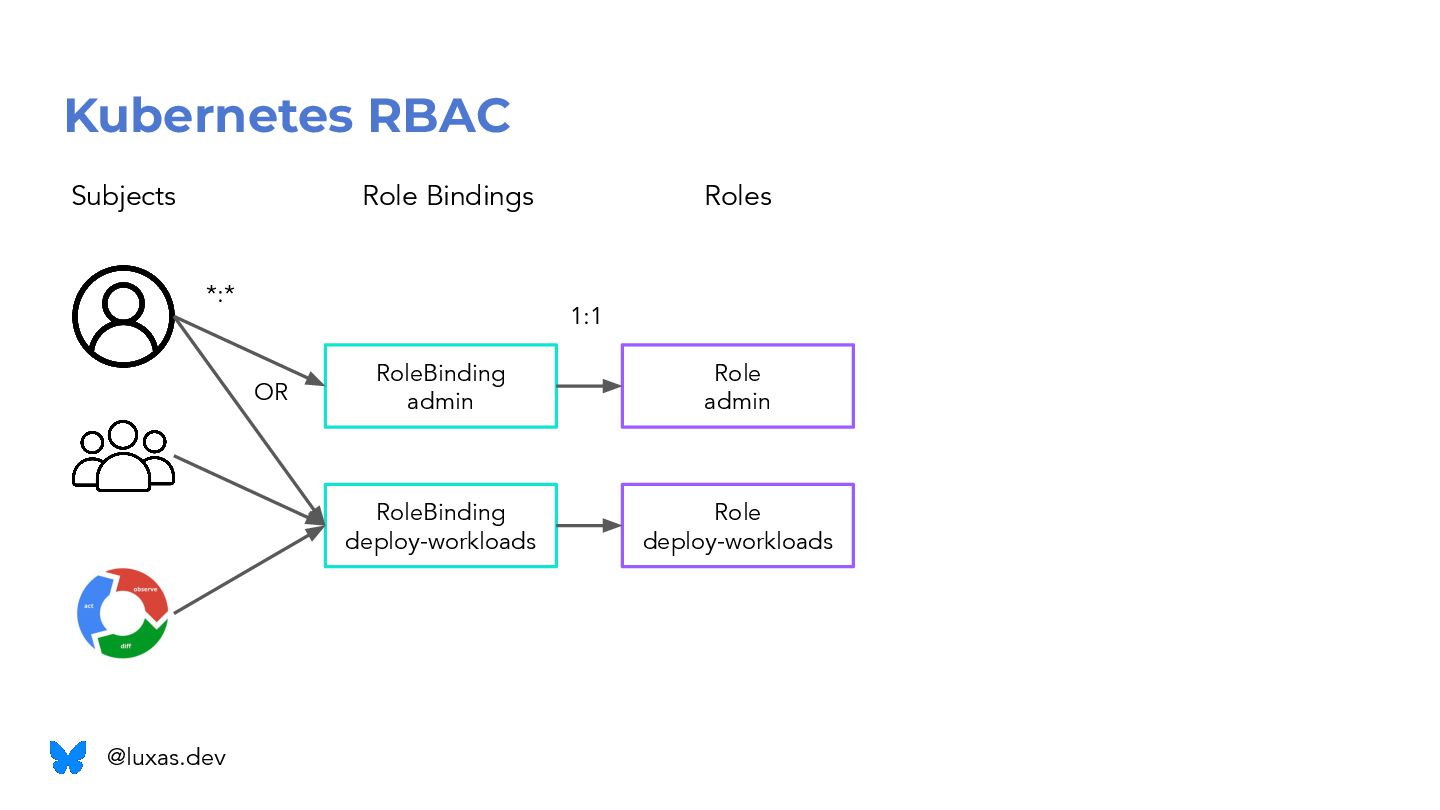
Kubernetes RBAC Subjects RoleBinding admin RoleBinding deploy-workloads Role admin Role
deploy-workloads 1:1 *:* Rule 1 Rule 2 OR OR (Rule 1 and Role deploy-workloads omitted for brevity) 1:* Role Bindings Roles Role Rules @luxas.dev -
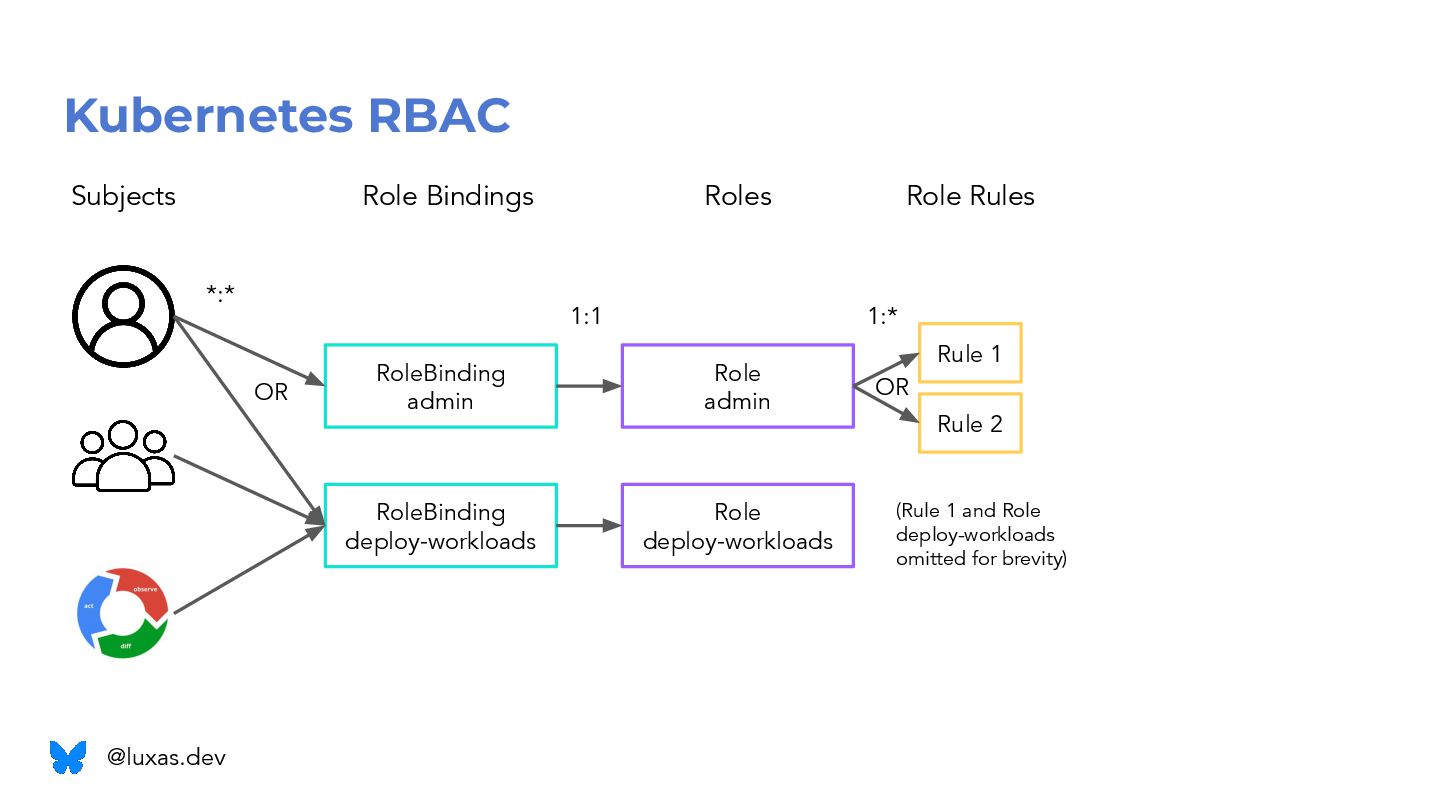
Kubernetes RBAC Subjects RoleBinding admin RoleBinding deploy-workloads Role admin Role
deploy-workloads 1:1 *:* Rule 1 Rule 2 OR OR (Rule 1 and Role deploy-workloads omitted for brevity) 1:* apiGroup resource namespace name AND Role Bindings Roles Role Rules Predicates @luxas.dev -
Kubernetes RBAC Subjects RoleBinding admin RoleBinding deploy-workloads Role admin Role
deploy-workloads 1:1 *:* Rule 1 Rule 2 OR OR (Rule 1 and Role deploy-workloads omitted for brevity) 1:* apiGroup Obj 1 resource namespace name Obj 2 Obj 3 AND Role Bindings Roles Role Rules Predicates Objects @luxas.dev -
Kubernetes RBAC Subjects RoleBinding admin RoleBinding deploy-workloads Role admin Role
deploy-workloads 1:1 *:* Rule 1 Rule 2 OR OR (Rule 1 and Role deploy-workloads omitted for brevity) 1:* apiGroup Obj 1 resource namespace name Obj 2 Obj 3 AND Role Bindings Roles Role Rules Predicates Objects “RBAC” “ABAC” @luxas.dev -
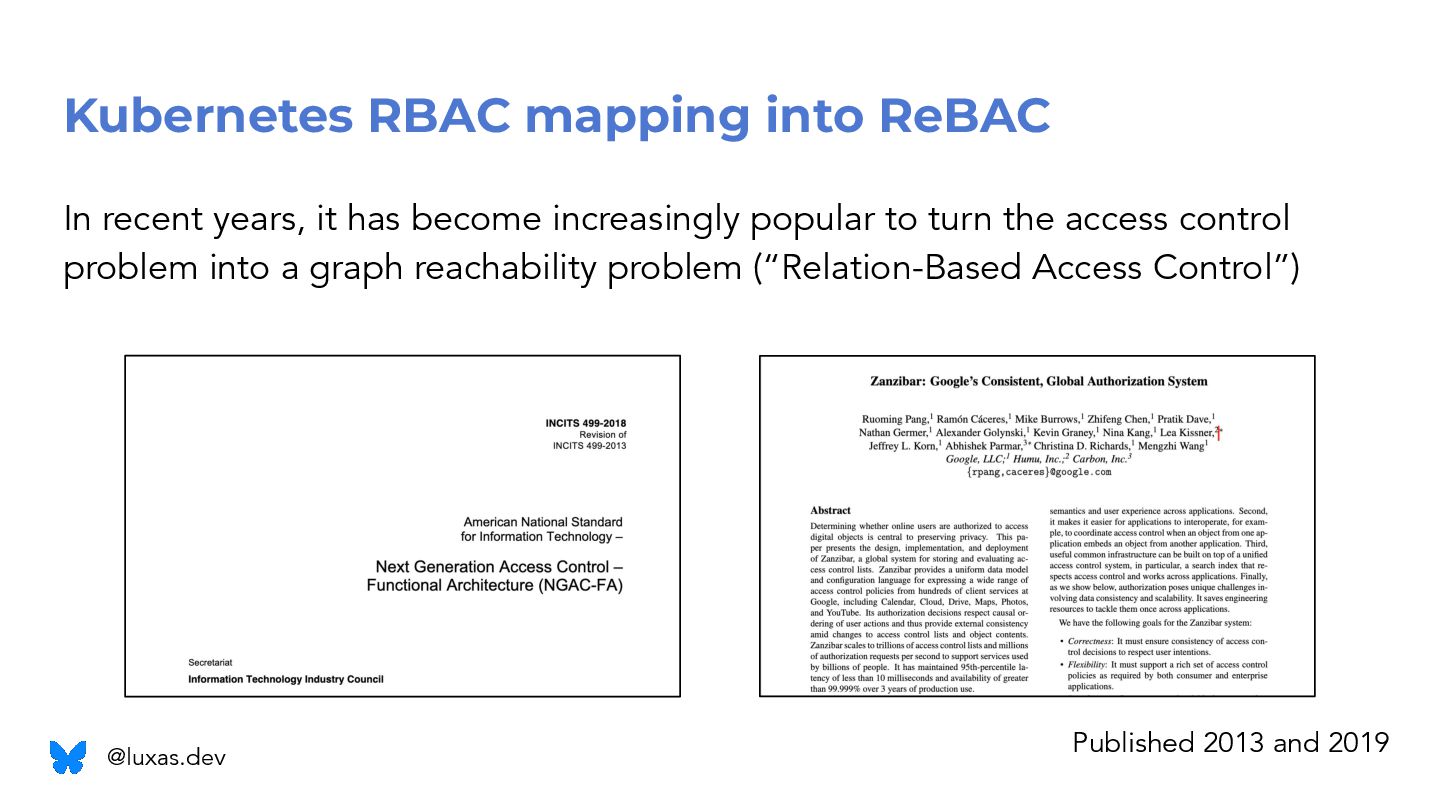
Kubernetes RBAC mapping into ReBAC In recent years, it has
become increasingly popular to turn the access control problem into a graph reachability problem (“Relation-Based Access Control”) @luxas.dev Published 2013 and 2019 -
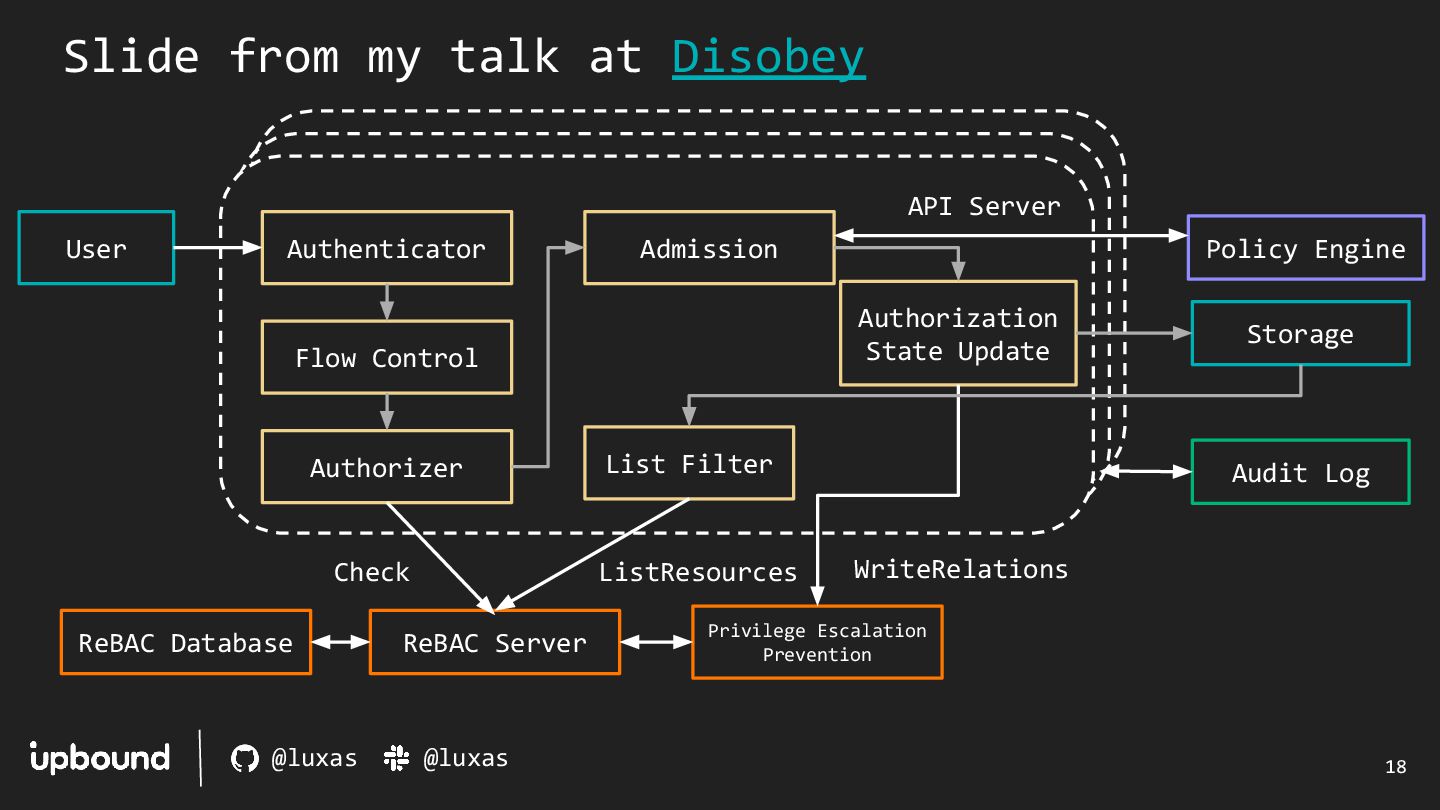
@luxas @luxas API Server Slide from my talk at Disobey
18 User Authenticator ReBAC Server Flow Control Authorizer Admission Privilege Escalation Prevention Authorization State Update List Filter ReBAC Database Storage Audit Log Policy Engine Check ListResources WriteRelations -
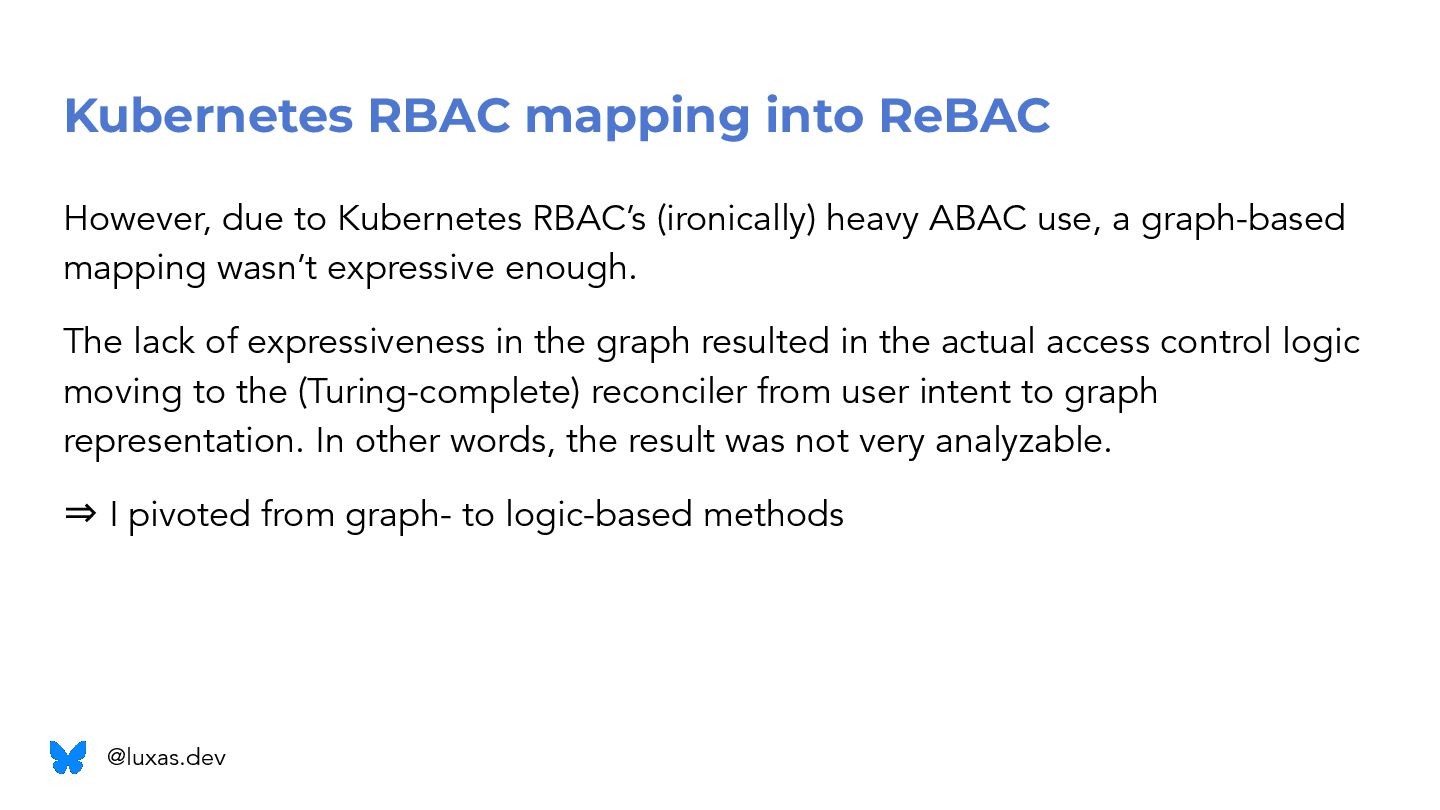
Kubernetes RBAC mapping into ReBAC However, due to Kubernetes RBAC’s
(ironically) heavy ABAC use, a graph-based mapping wasn’t expressive enough. The lack of expressiveness in the graph resulted in the actual access control logic moving to the (Turing-complete) reconciler from user intent to graph representation. In other words, the result was not very analyzable. ⇒ I pivoted from graph- to logic-based methods @luxas.dev -
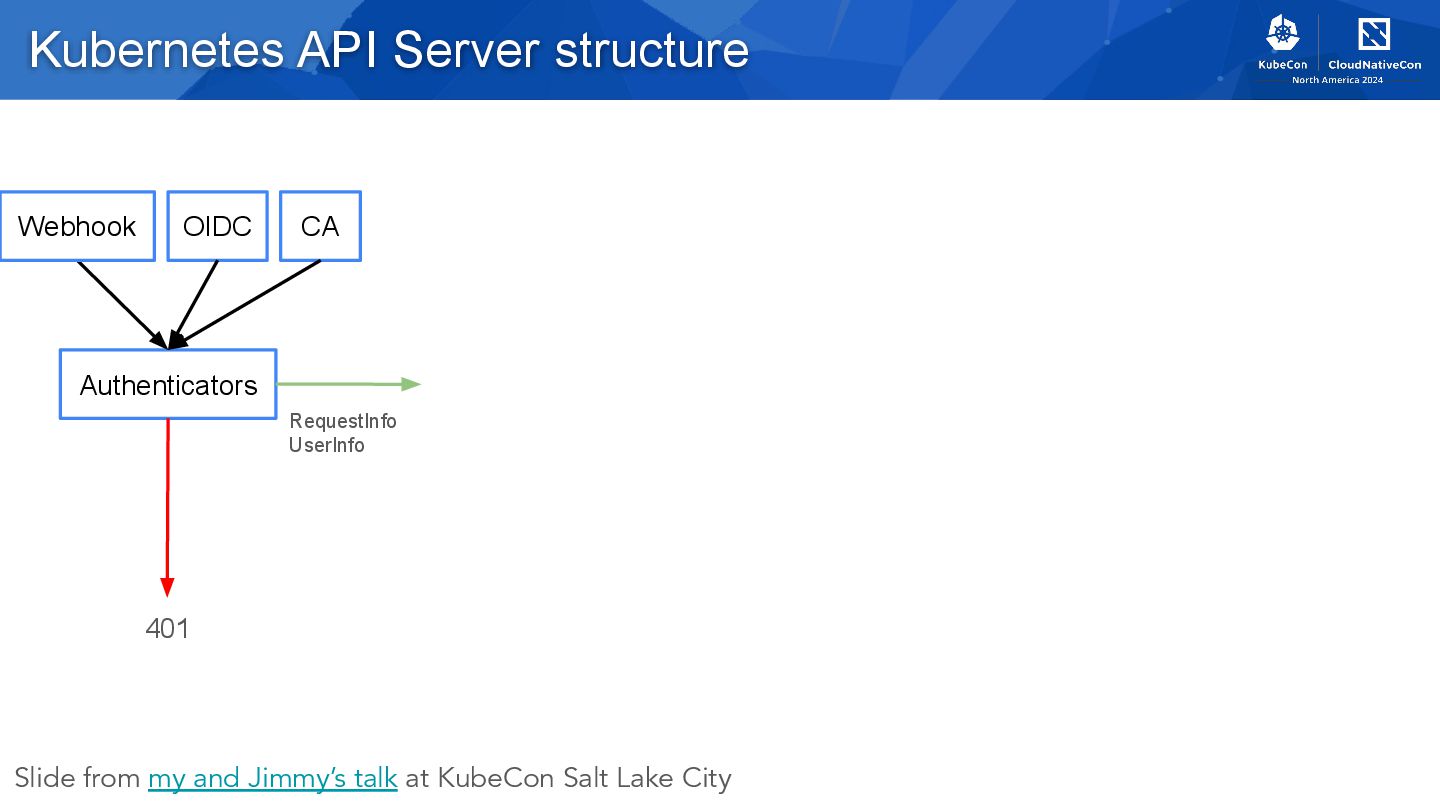
Kubernetes API Server structure Authenticators RequestInfo UserInfo 401 Webhook OIDC
CA Slide from my and Jimmy’s talk at KubeCon Salt Lake City -
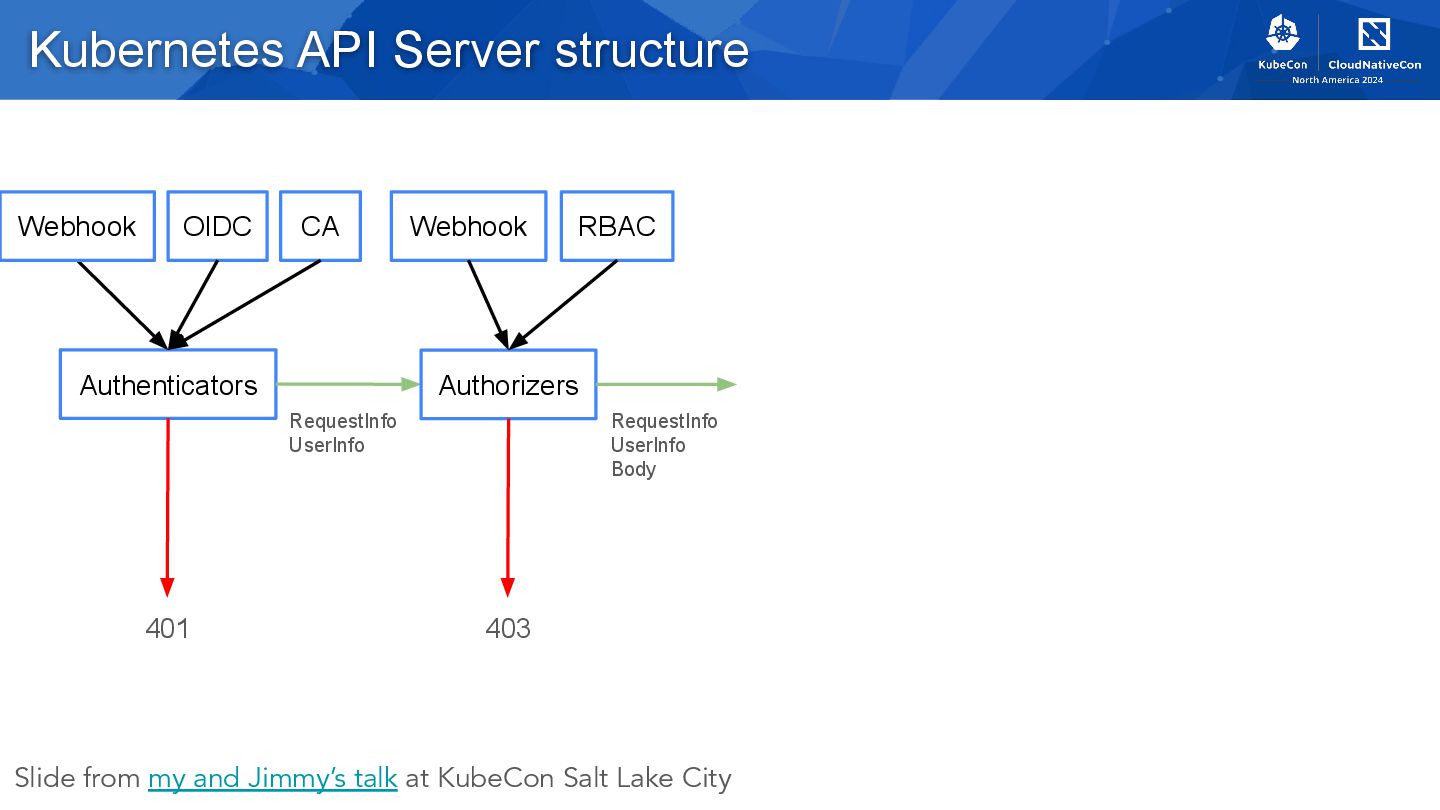
Kubernetes API Server structure Authenticators Authorizers RequestInfo UserInfo 401 403
RequestInfo UserInfo Body Webhook OIDC CA Webhook RBAC Slide from my and Jimmy’s talk at KubeCon Salt Lake City -
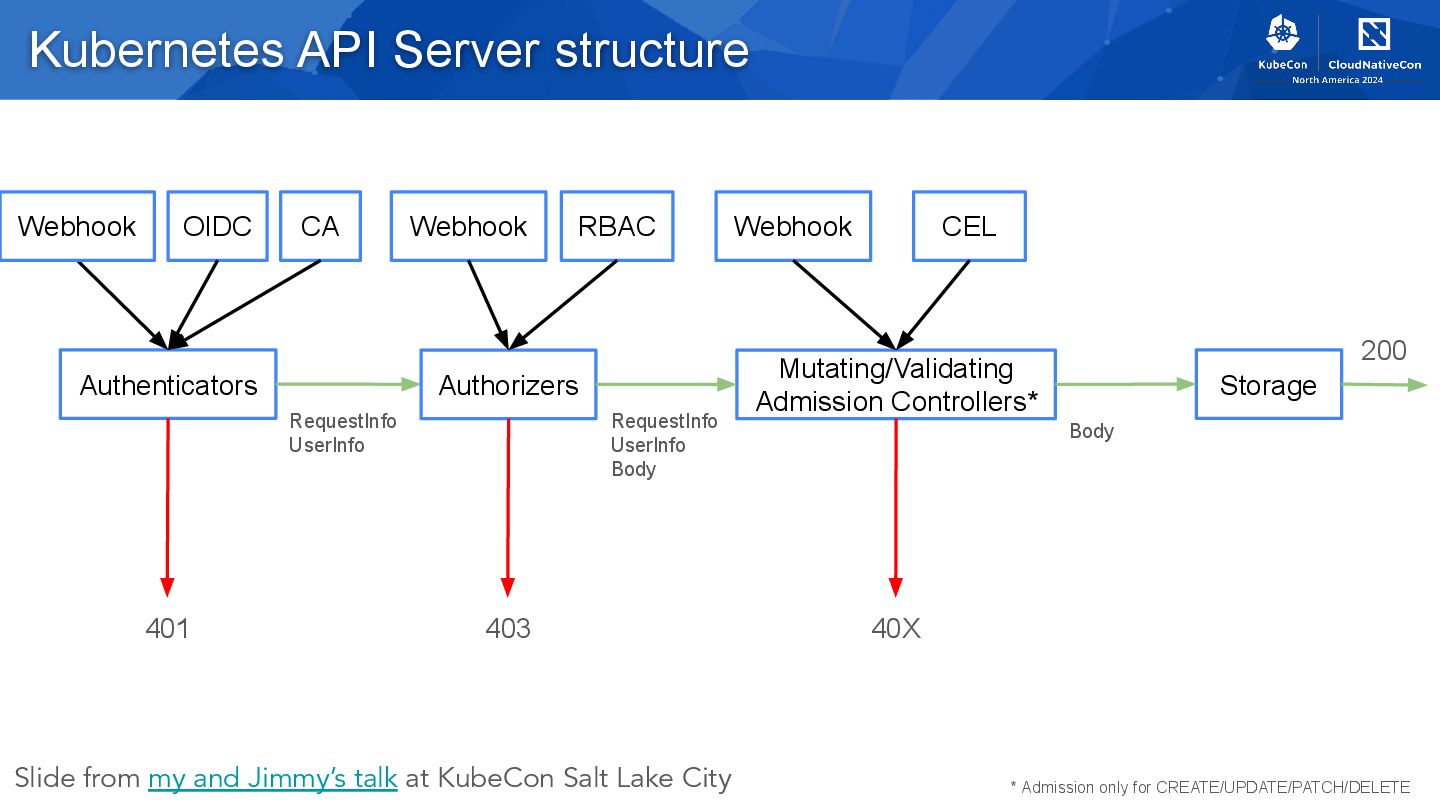
Kubernetes API Server structure Authenticators Authorizers RequestInfo UserInfo Mutating/Validating Admission
Controllers* Storage 401 403 40X RequestInfo UserInfo Body Body Webhook OIDC CA Webhook RBAC CEL Webhook 200 * Admission only for CREATE/UPDATE/PATCH/DELETE Slide from my and Jimmy’s talk at KubeCon Salt Lake City -
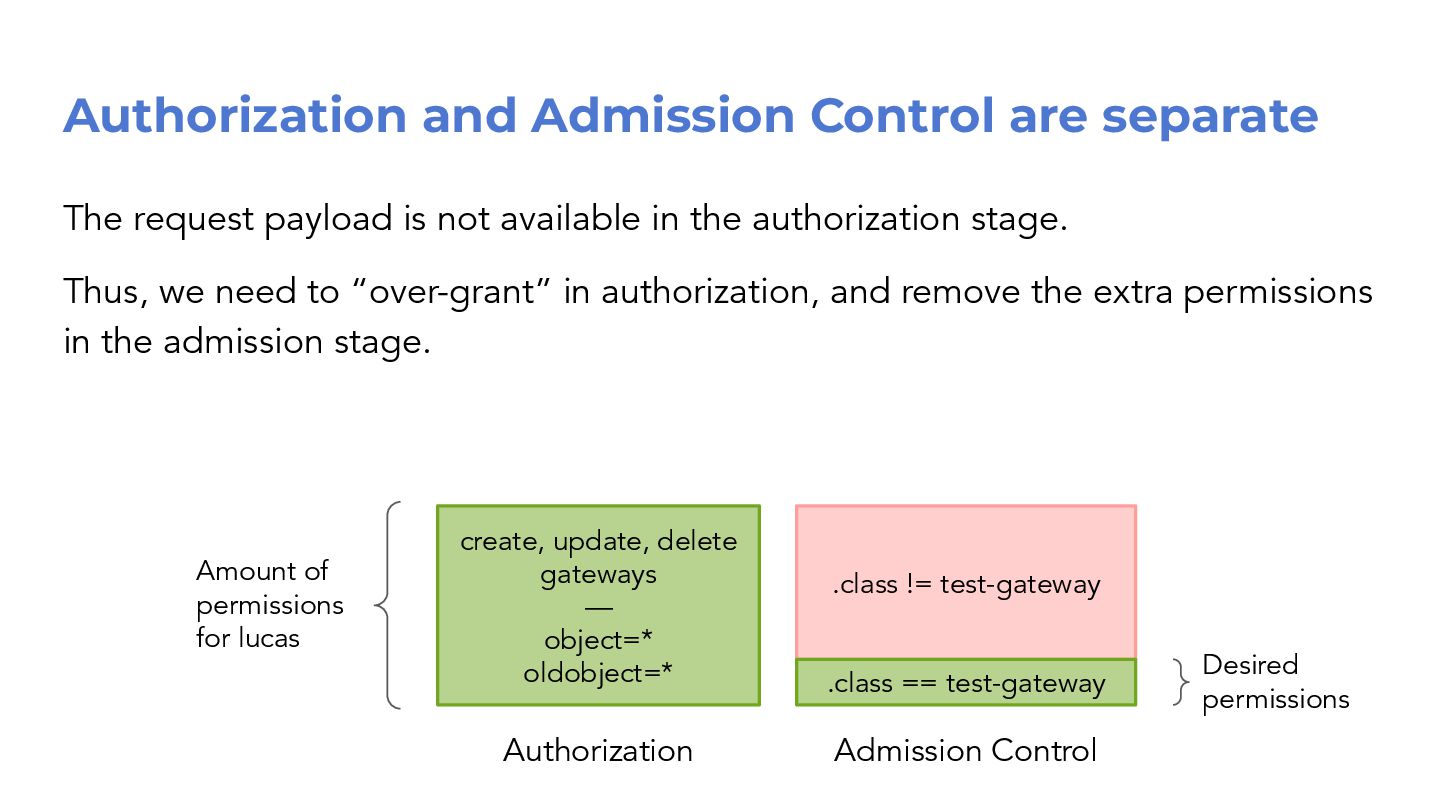
Authorization and Admission Control are separate The request payload is
not available in the authorization stage. Thus, we need to “over-grant” in authorization, and remove the extra permissions in the admission stage. create, update, delete gateways — object=* oldobject=* Authorization .class != test-gateway .class == test-gateway Admission Control Amount of permissions for lucas Desired permissions -
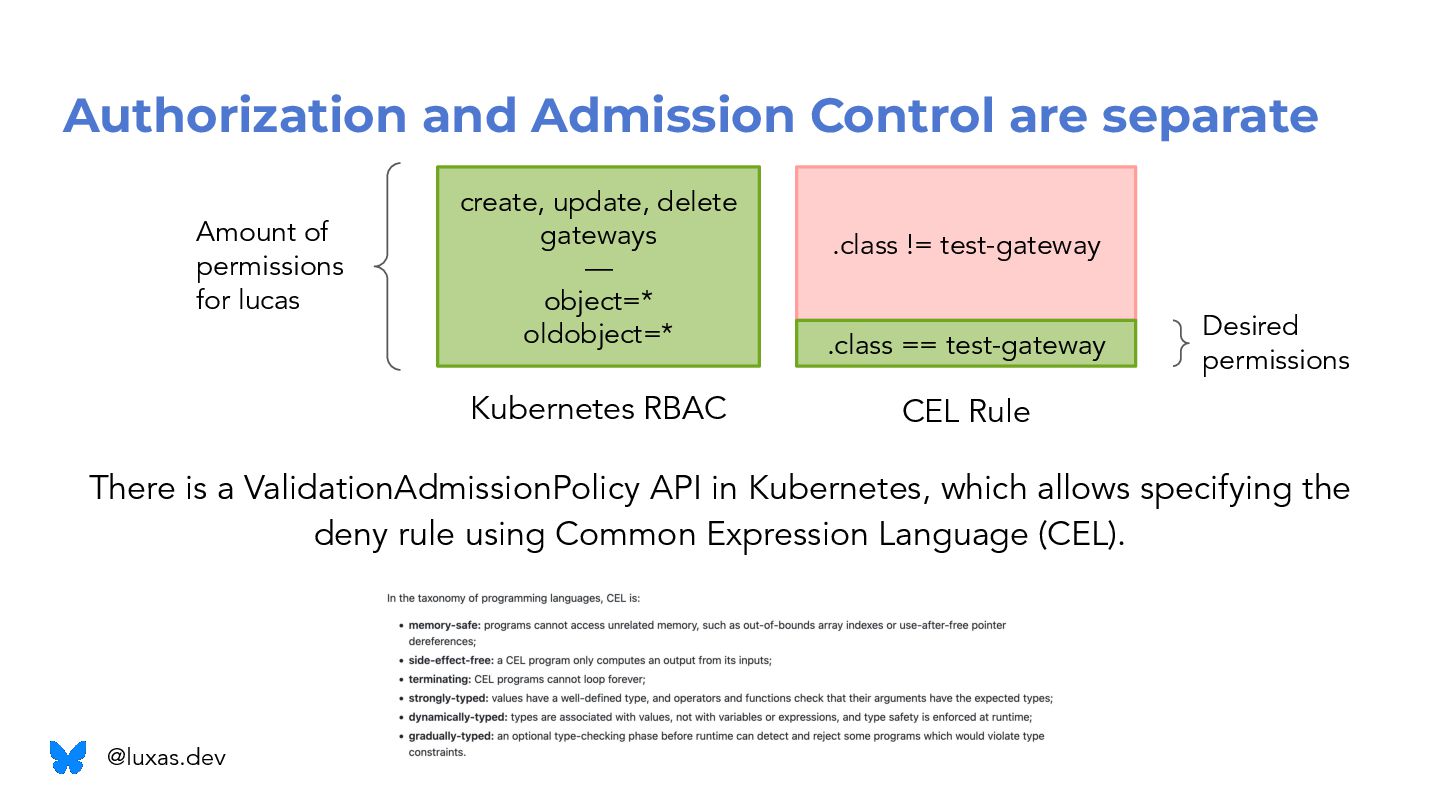
Authorization and Admission Control are separate There is a ValidationAdmissionPolicy
API in Kubernetes, which allows specifying the deny rule using Common Expression Language (CEL). @luxas.dev create, update, delete gateways — object=* oldobject=* Kubernetes RBAC .class != test-gateway .class == test-gateway CEL Rule Amount of permissions for lucas Desired permissions -
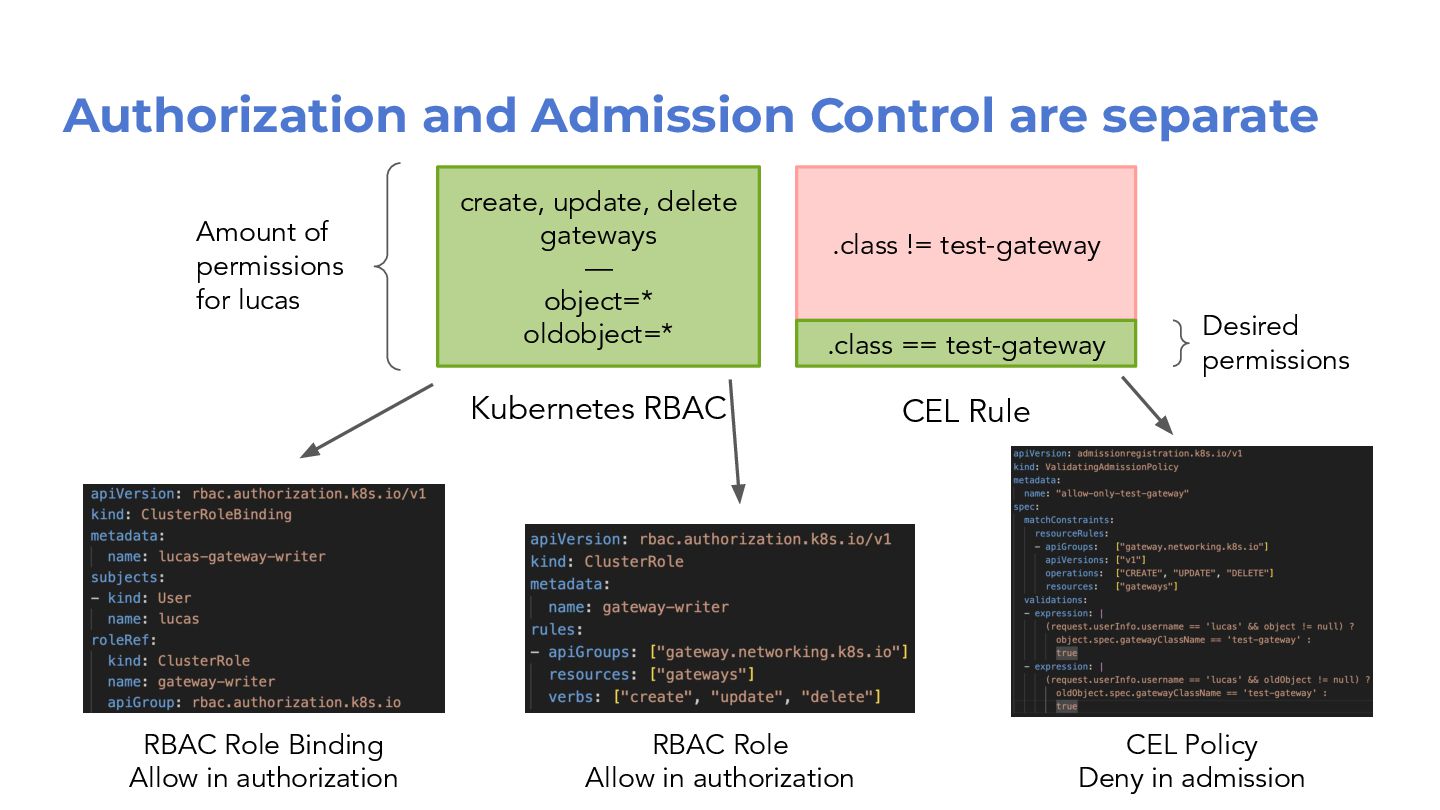
Authorization and Admission Control are separate RBAC Role Allow in
authorization RBAC Role Binding Allow in authorization CEL Policy Deny in admission create, update, delete gateways — object=* oldobject=* .class != test-gateway .class == test-gateway Kubernetes RBAC CEL Rule Amount of permissions for lucas Desired permissions -
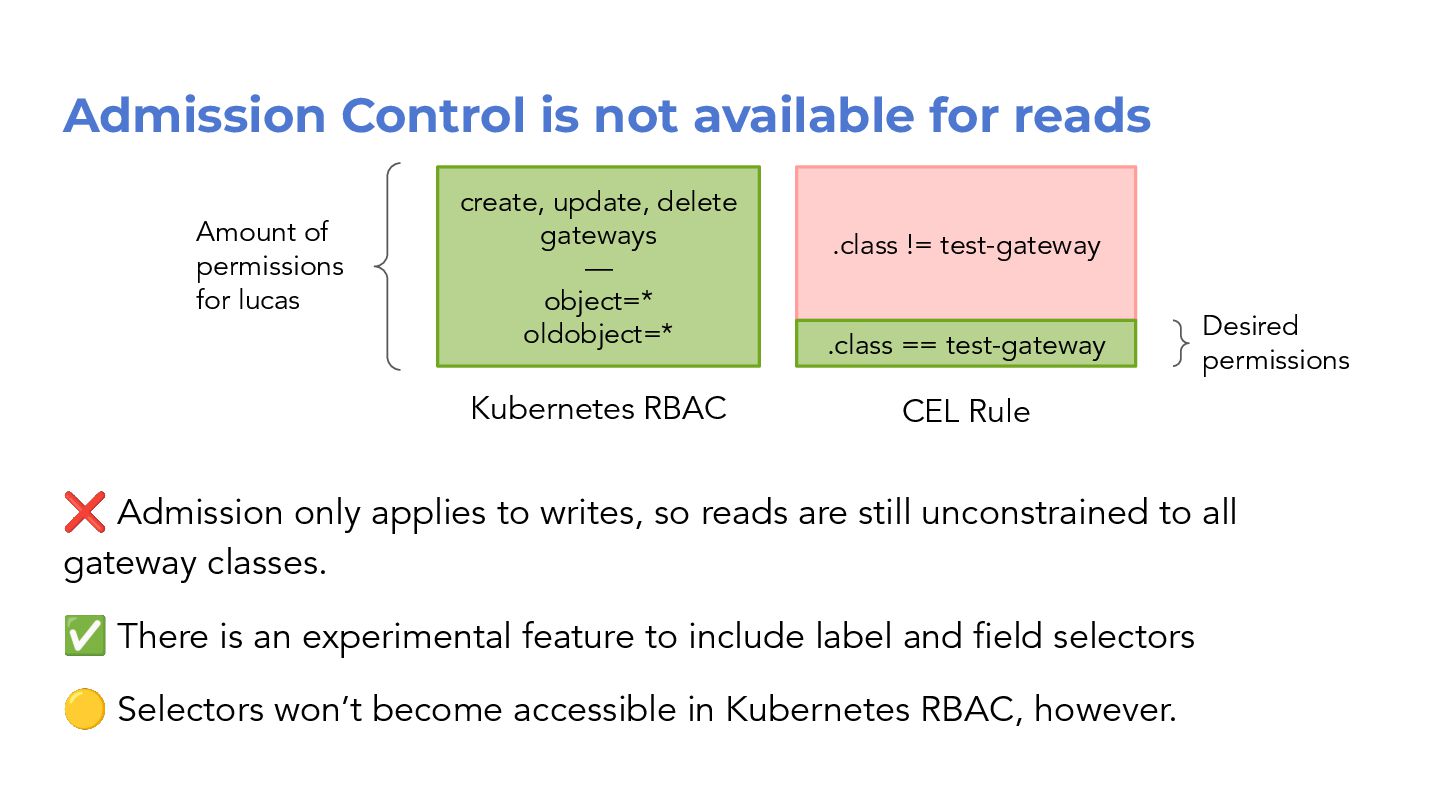
Admission Control is not available for reads ❌ Admission only
applies to writes, so reads are still unconstrained to all gateway classes. ✅ There is an experimental feature to include label and field selectors 🟡 Selectors won’t become accessible in Kubernetes RBAC, however. create, update, delete gateways — object=* oldobject=* .class != test-gateway .class == test-gateway Kubernetes RBAC CEL Rule Amount of permissions for lucas Desired permissions -
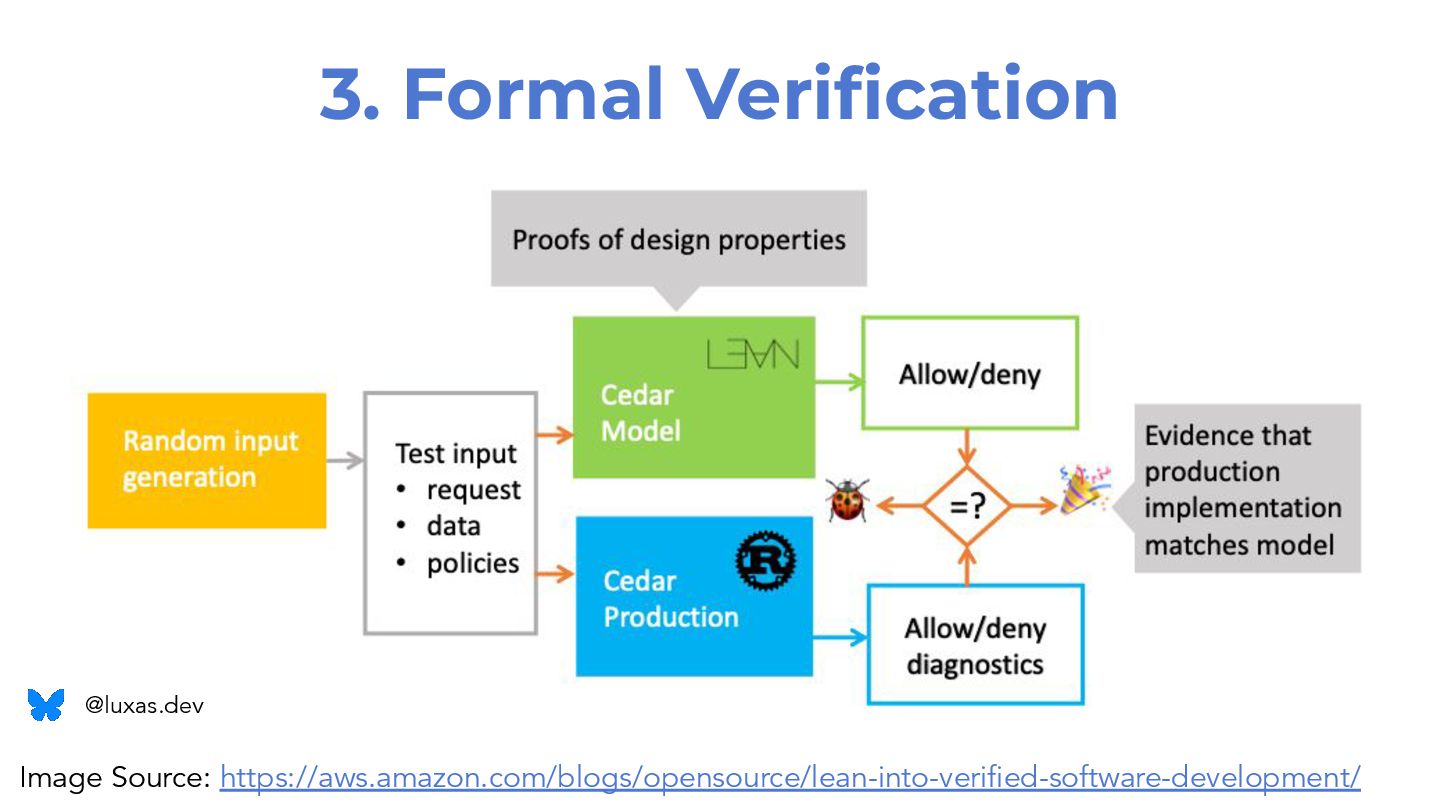
Open Source Authorization Engine @luxas.dev Aims to be expressive, fast,
safe, and analyzable -
Maintains a decidable encoding into Satisfiability Modulo Theories* Open Source
Authorization Engine @luxas.dev Aims to be expressive, fast, safe, and analyzable *Means in practice that the language does not have loops or ordered lists -
Maintains a decidable encoding into Satisfiability Modulo Theories* Open Source
Authorization Engine @luxas.dev Aims to be expressive, fast, safe, and analyzable *Means in practice that the language does not have loops or ordered lists Supports RBAC, ReBAC and ABAC paradigms -
Maintains a decidable encoding into Satisfiability Modulo Theories* Open Source
Authorization Engine @luxas.dev Aims to be expressive, fast, safe, and analyzable *Means in practice that the language does not have loops or ordered lists AWS is donating Cedar to the CNCF Supports RBAC, ReBAC and ABAC paradigms -
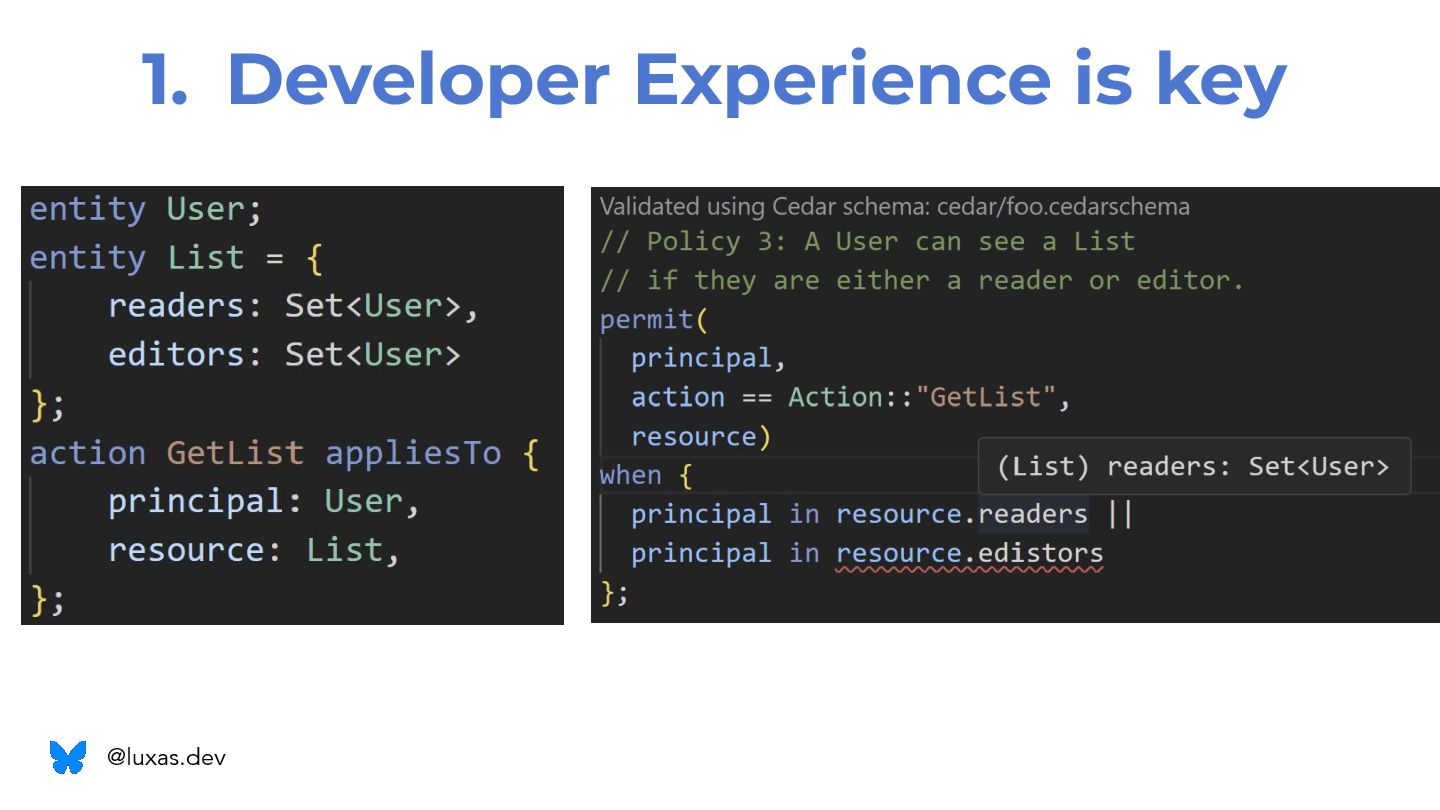
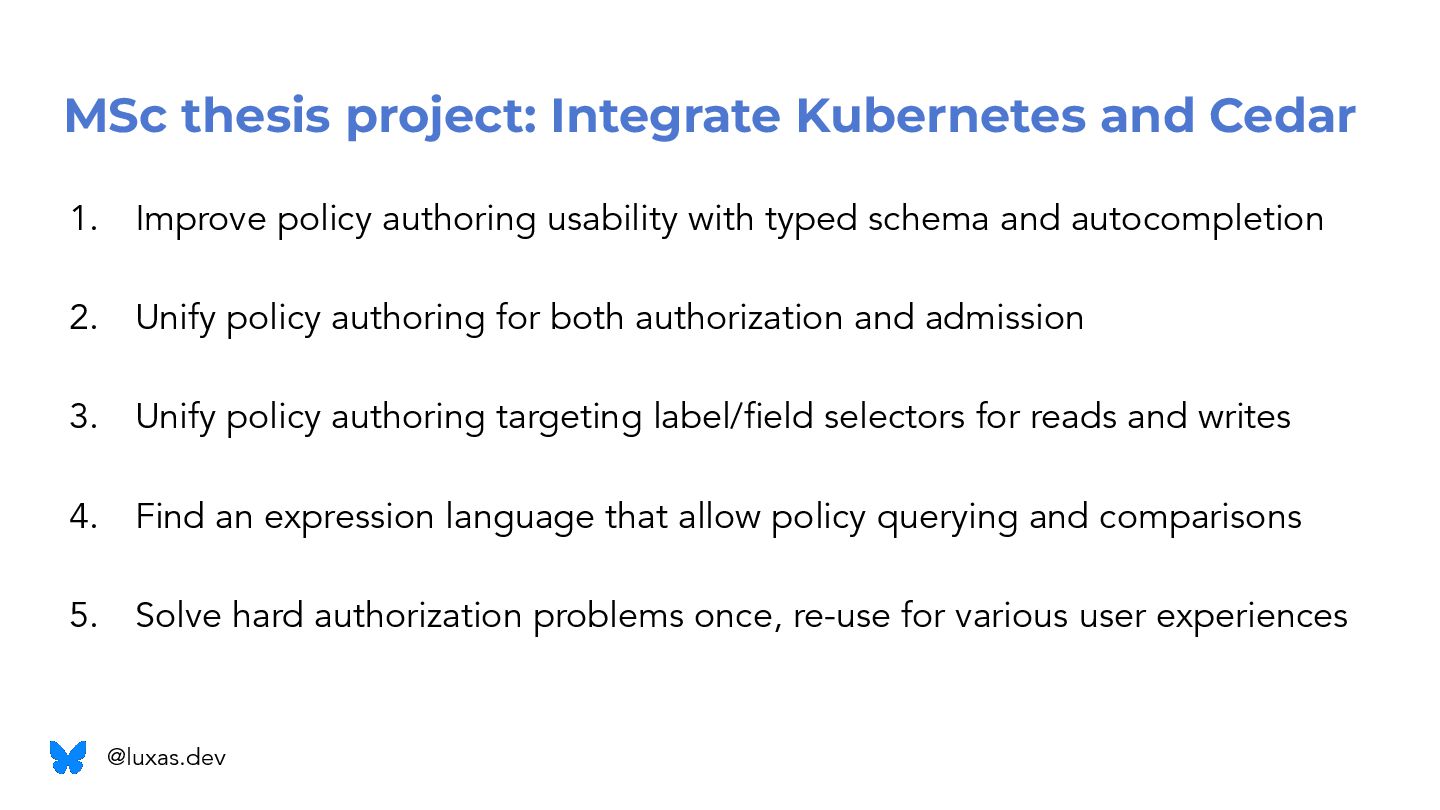
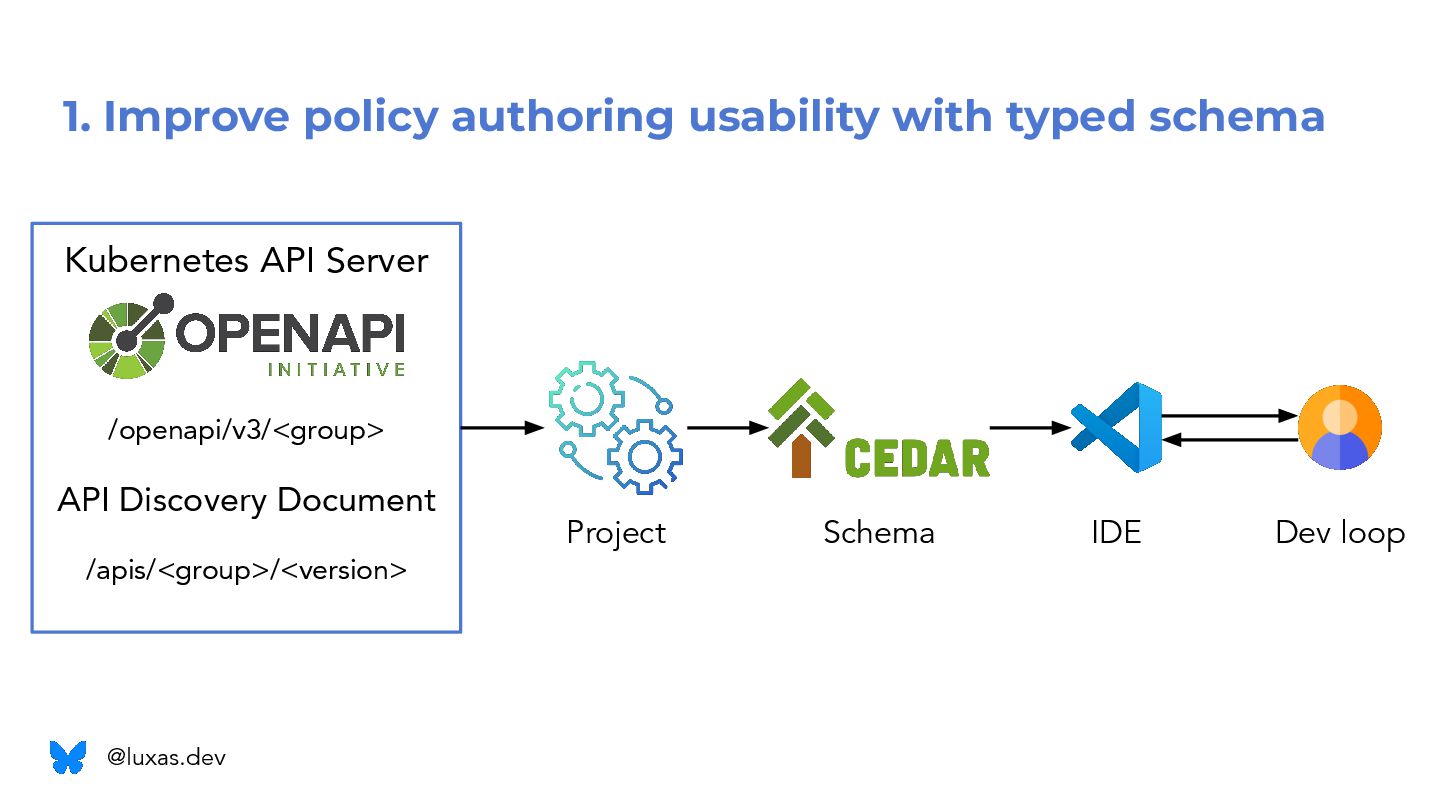
MSc thesis project: Integrate Kubernetes and Cedar 1. Improve policy
authoring usability with typed schema and autocompletion 2. Unify policy authoring for both authorization and admission 3. Unify policy authoring targeting label/field selectors for reads and writes 4. Find an expression language that allow policy querying and comparisons 5. Solve hard authorization problems once, re-use for various user experiences @luxas.dev -
Kubernetes API Server /openapi/v3/<group> API Discovery Document /apis/<group>/<version> 1. Improve
policy authoring usability with typed schema Project Schema IDE Dev loop @luxas.dev -
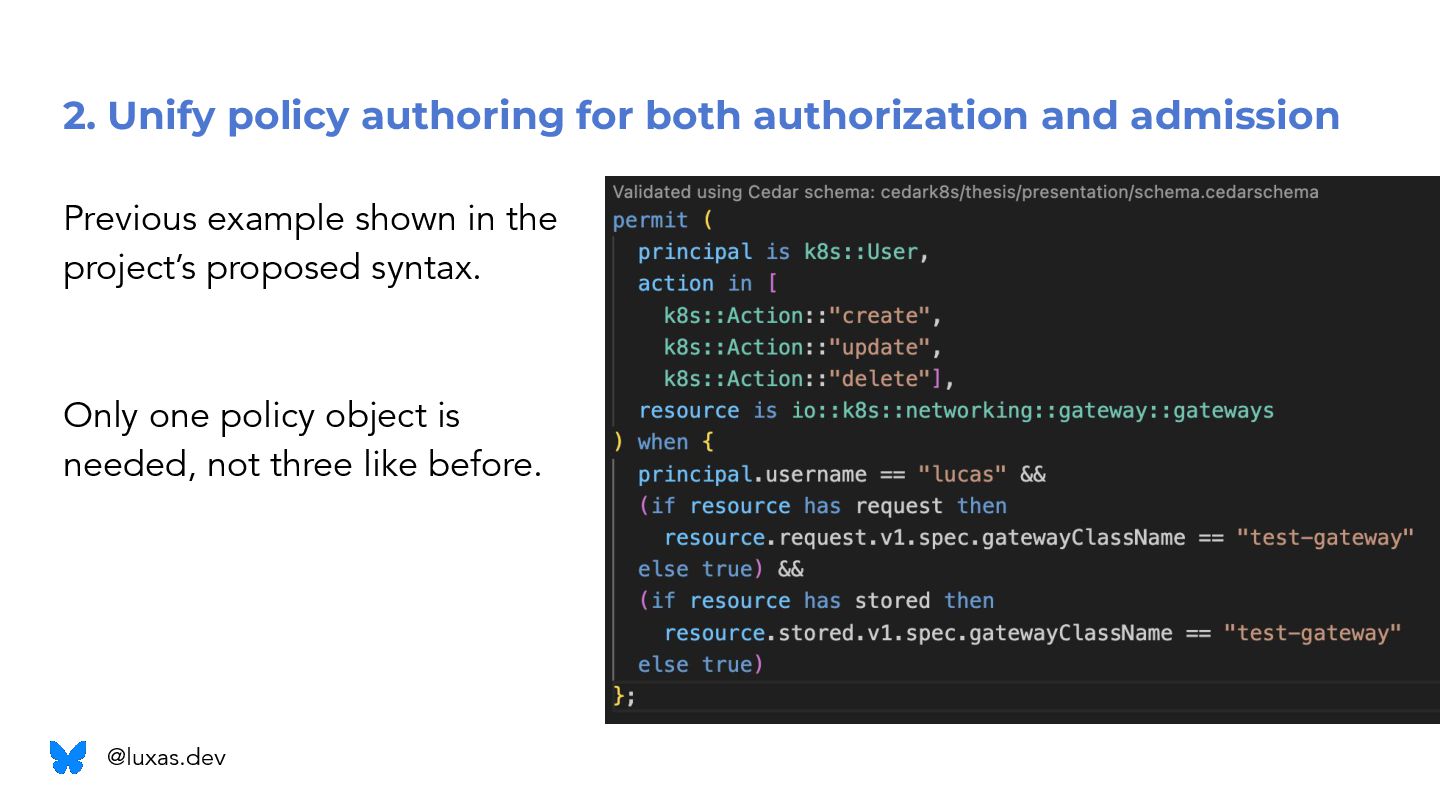
2. Unify policy authoring for both authorization and admission Previous
example shown in the project’s proposed syntax. Only one policy object is needed, not three like before. @luxas.dev -
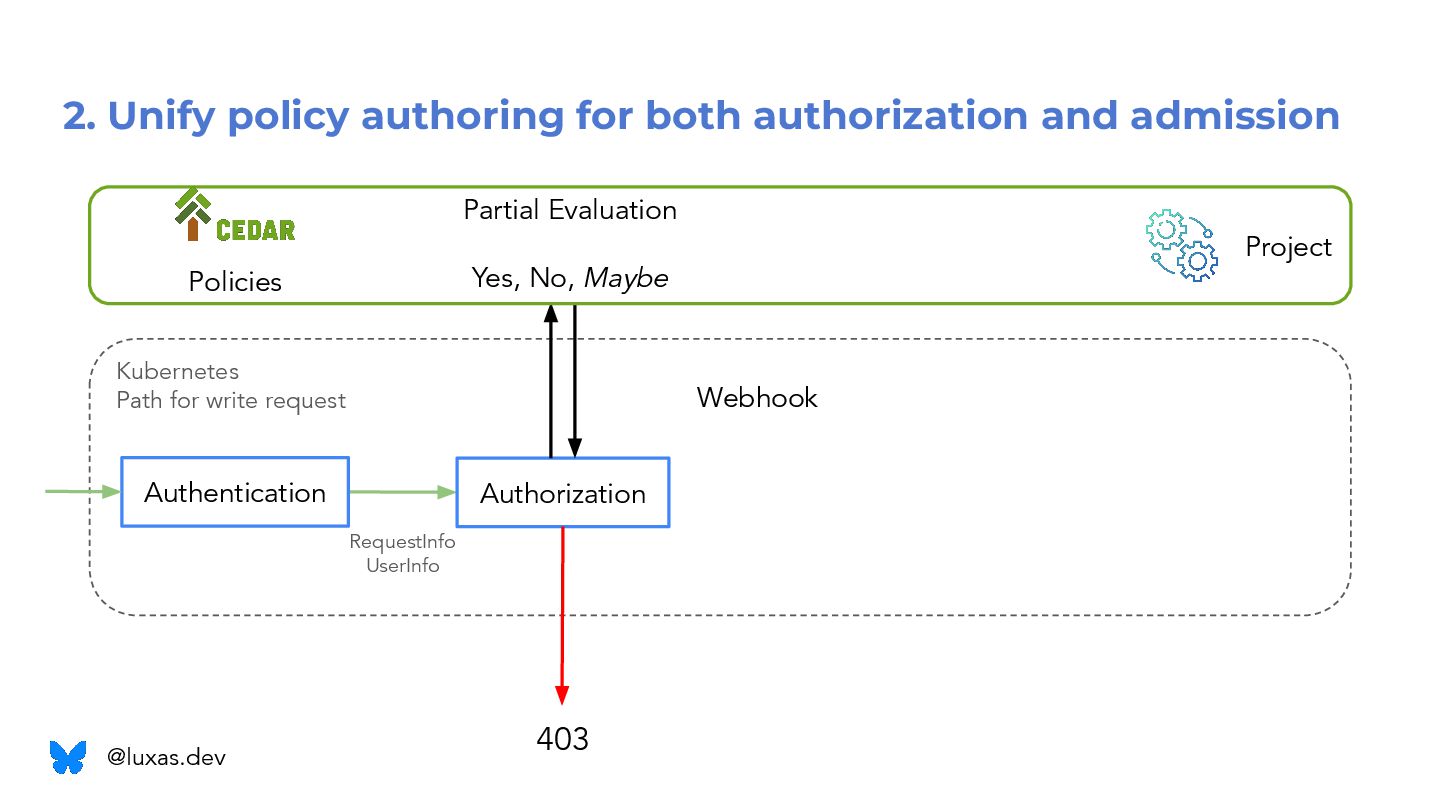
2. Unify policy authoring for both authorization and admission Authorization
RequestInfo UserInfo Kubernetes Path for write request Project Partial Evaluation Yes, No, Maybe 403 Policies Webhook Authentication @luxas.dev -
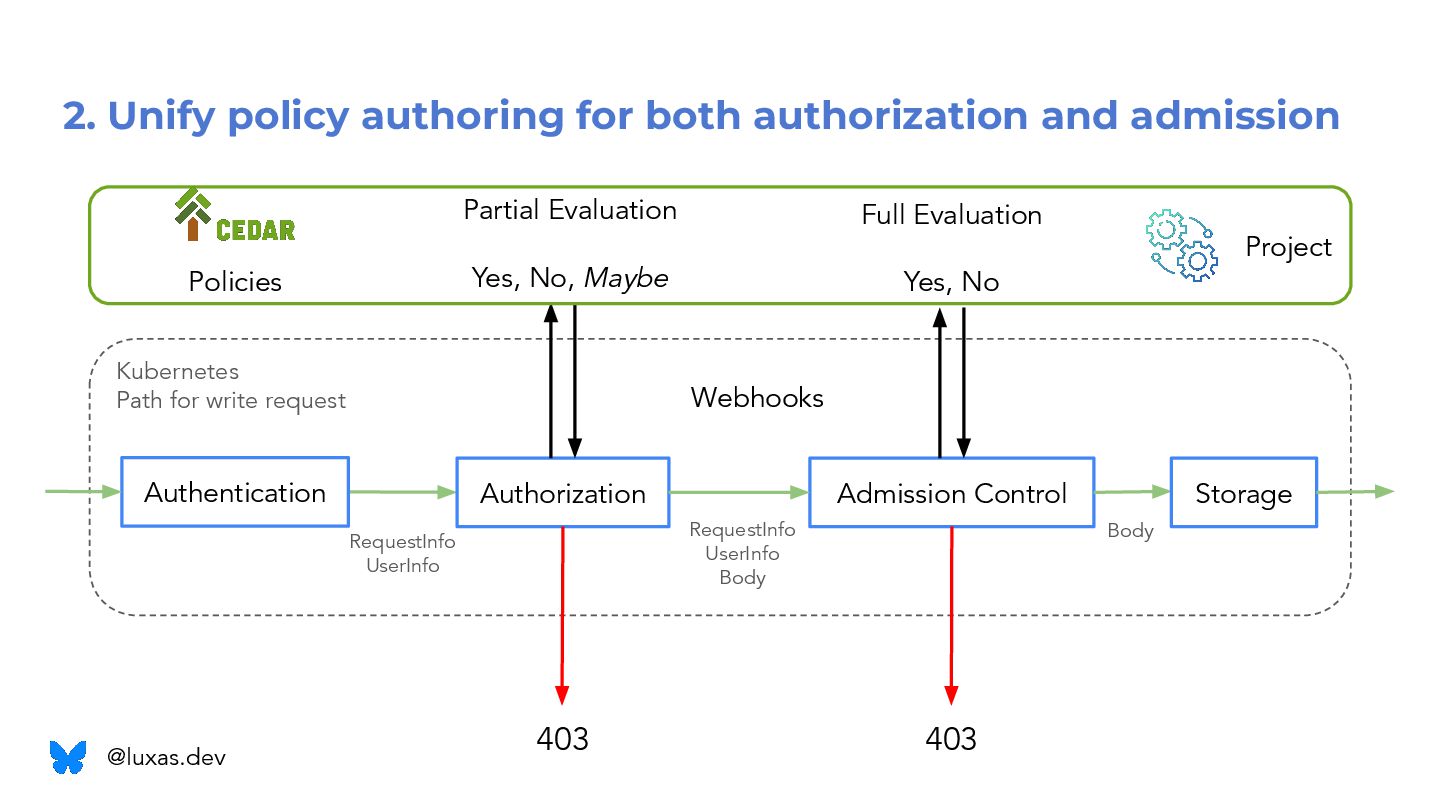
2. Unify policy authoring for both authorization and admission Authorization
RequestInfo UserInfo Admission Control RequestInfo UserInfo Body Body Kubernetes Path for write request Project Partial Evaluation Yes, No, Maybe Full Evaluation Yes, No 403 403 Policies Webhooks Authentication Storage @luxas.dev -
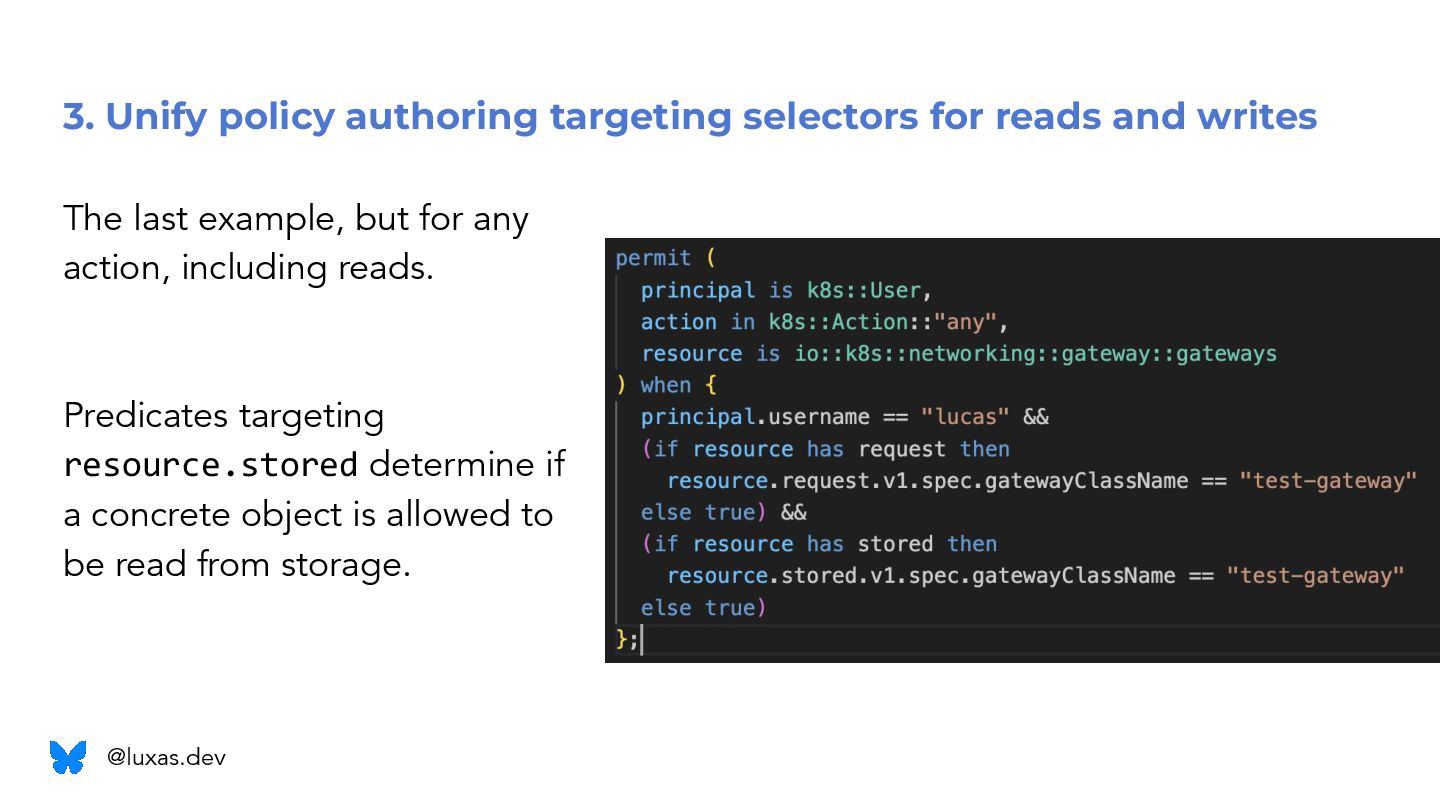
3. Unify policy authoring targeting selectors for reads and writes
The last example, but for any action, including reads. Predicates targeting resource.stored determine if a concrete object is allowed to be read from storage. @luxas.dev -
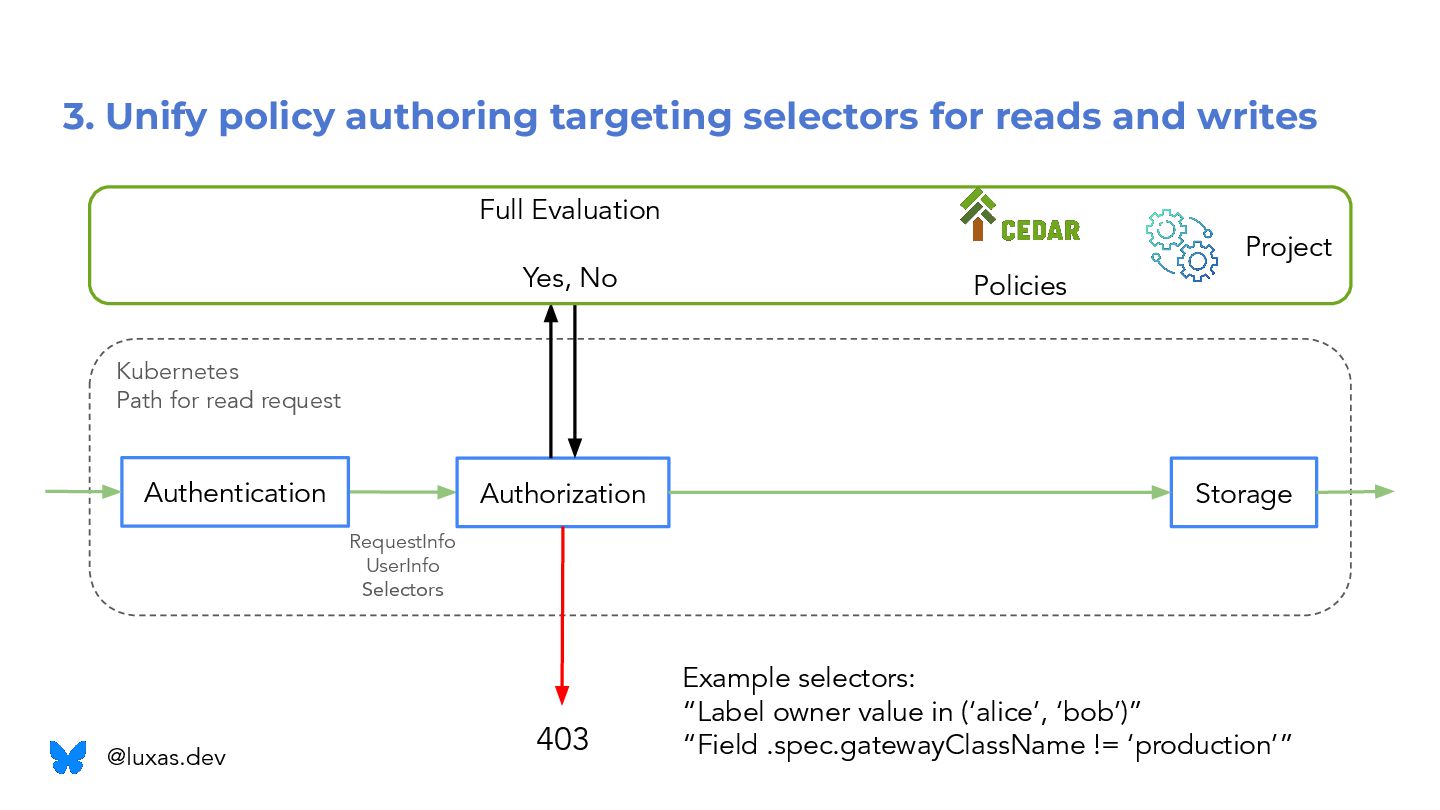
3. Unify policy authoring targeting selectors for reads and writes
Authorization Kubernetes Path for read request Project Full Evaluation Yes, No 403 Authentication Storage Example selectors: “Label owner value in (‘alice’, ‘bob’)” “Field .spec.gatewayClassName != ‘production’” @luxas.dev Policies RequestInfo UserInfo Selectors -
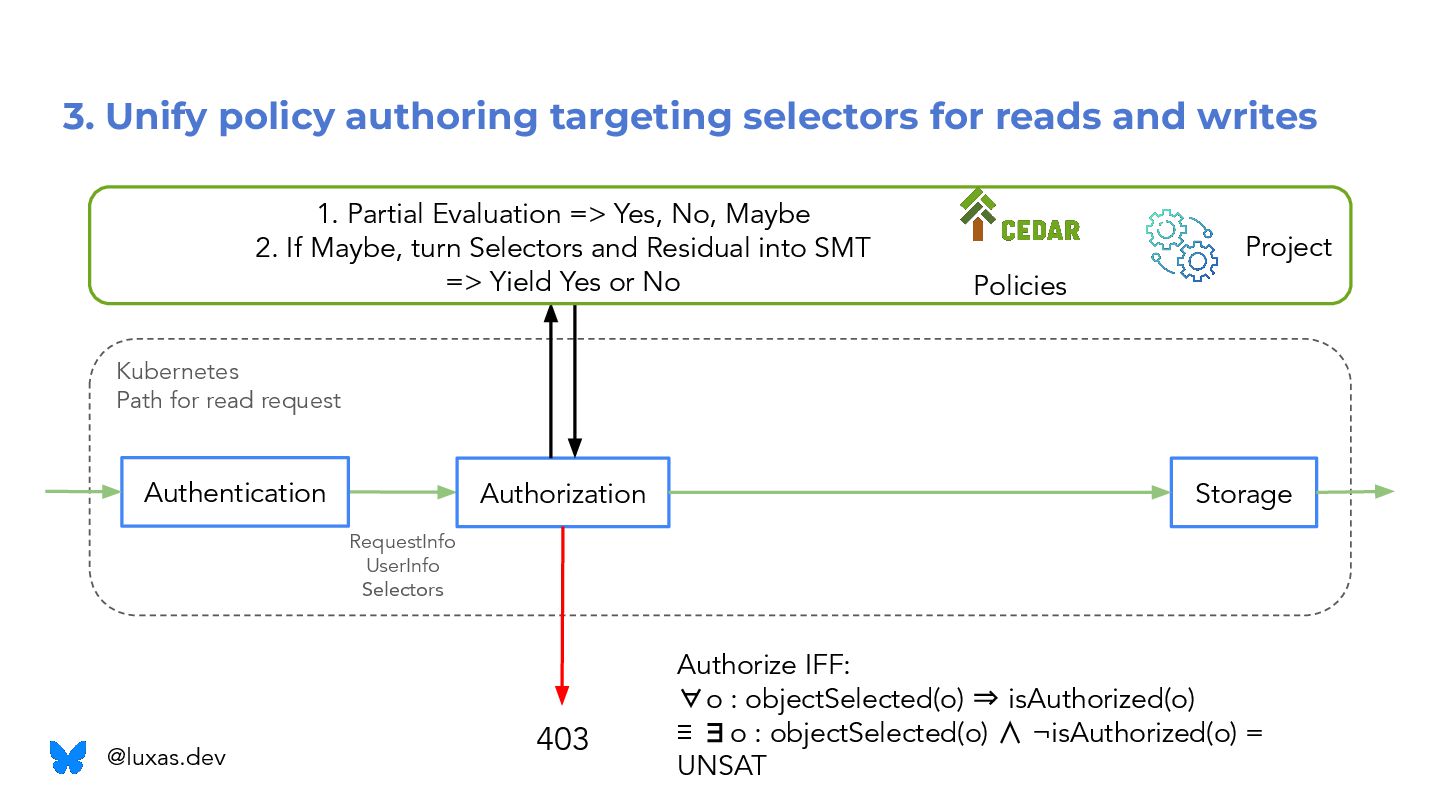
3. Unify policy authoring targeting selectors for reads and writes
Authorization RequestInfo UserInfo Selectors Kubernetes Path for read request Project 1. Partial Evaluation => Yes, No, Maybe 2. If Maybe, turn Selectors and Residual into SMT => Yield Yes or No 403 Policies Authentication Storage Authorize IFF: ∀o : objectSelected(o) ⇒ isAuthorized(o) ≡ ∃o : objectSelected(o) ∧ ¬isAuthorized(o) = UNSAT @luxas.dev -
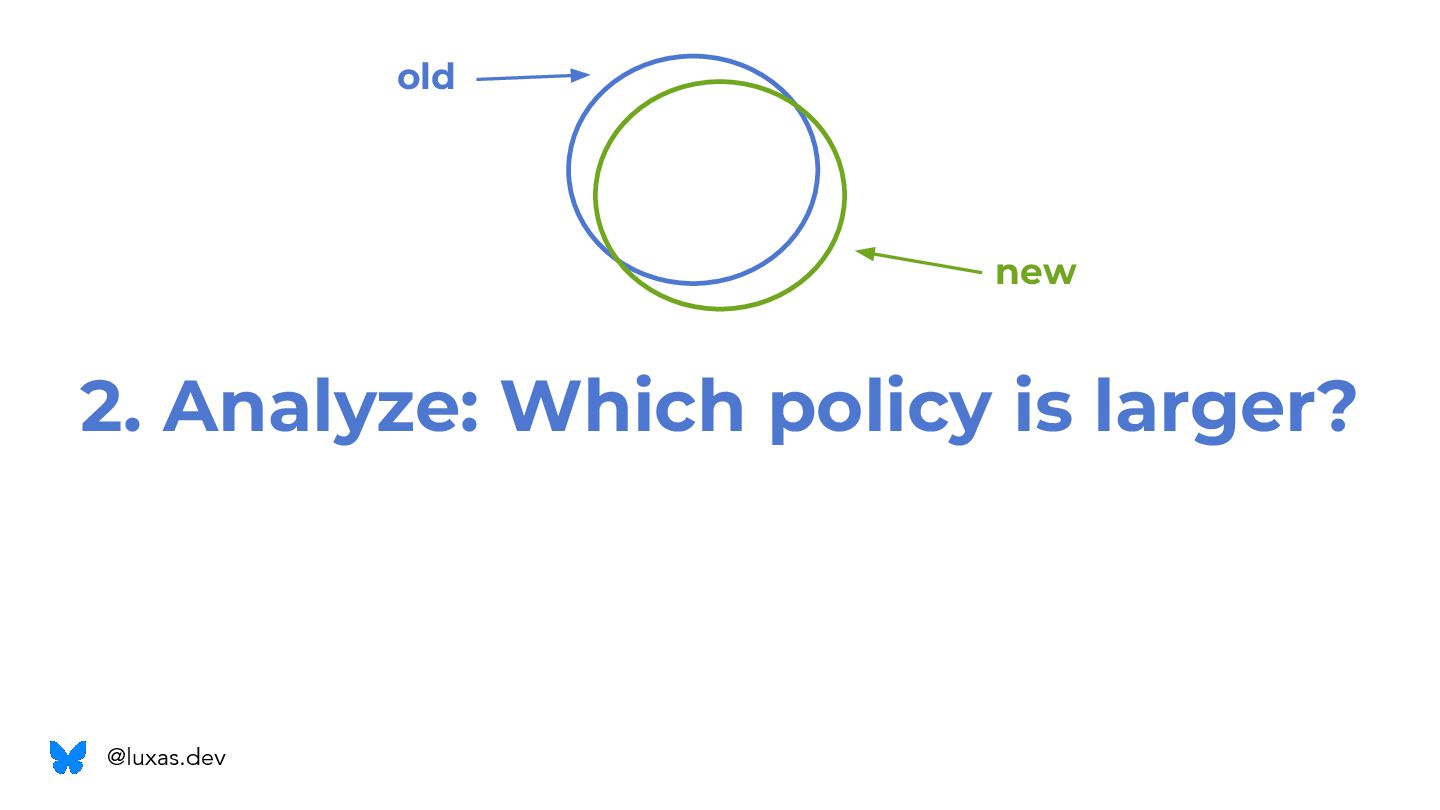
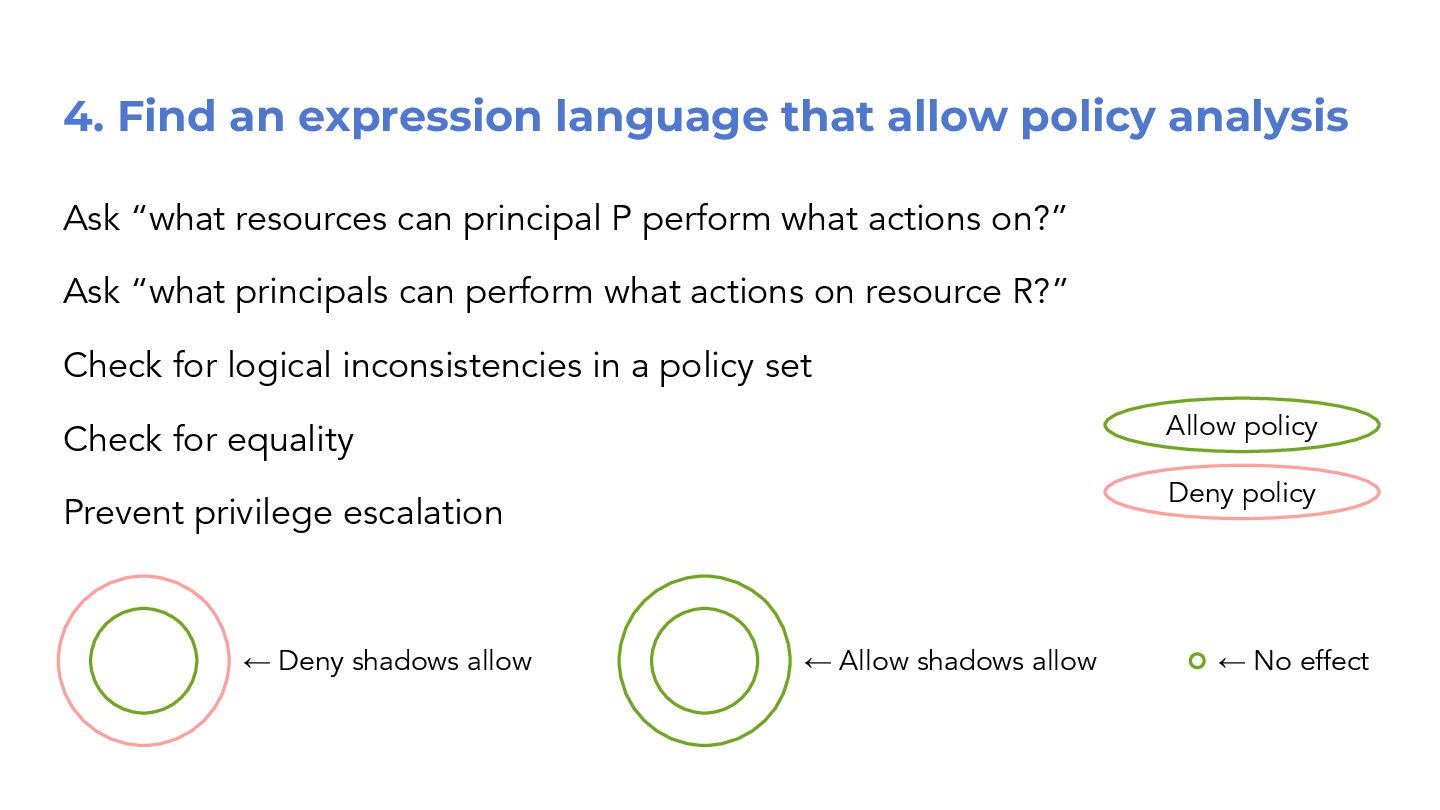
4. Find an expression language that allow policy analysis Ask
“what resources can principal P perform what actions on?” Ask “what principals can perform what actions on resource R?” -
4. Find an expression language that allow policy analysis Ask
“what resources can principal P perform what actions on?” Ask “what principals can perform what actions on resource R?” Check for logical inconsistencies in a policy set Check for equality Prevent privilege escalation ← No effect ← Allow shadows allow ← Deny shadows allow Allow policy Deny policy -
4. Find an expression language that allow policy analysis Queries
achievable through Partial Evaluation @luxas.dev -
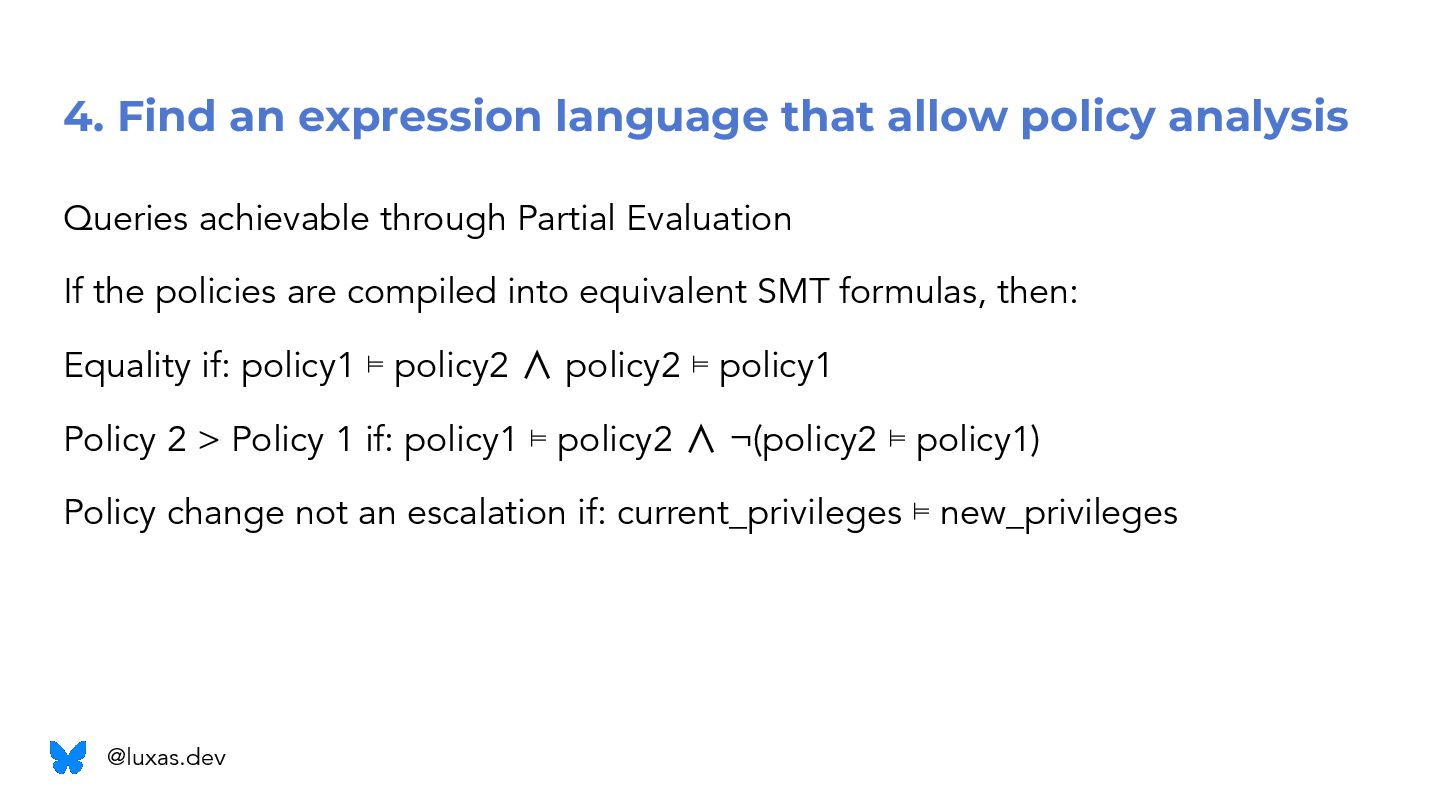
4. Find an expression language that allow policy analysis Queries
achievable through Partial Evaluation If the policies are compiled into equivalent SMT formulas, then: Equality if: policy1 ⊨ policy2 ∧ policy2 ⊨ policy1 Policy 2 > Policy 1 if: policy1 ⊨ policy2 ∧ ¬(policy2 ⊨ policy1) Policy change not an escalation if: current_privileges ⊨ new_privileges @luxas.dev -
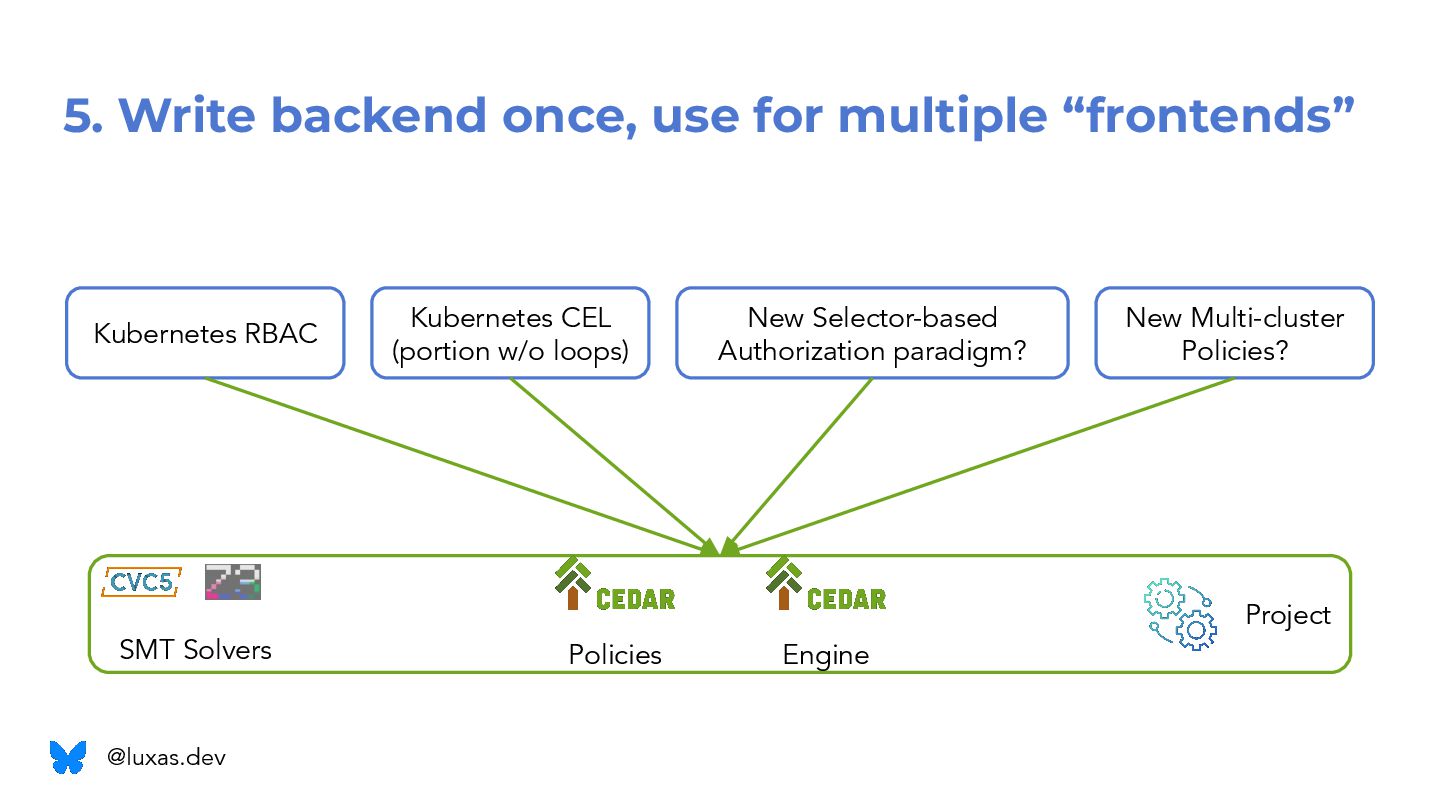
5. Write backend once, use for multiple “frontends” Kubernetes CEL
(portion w/o loops) Kubernetes RBAC New Selector-based Authorization paradigm? New Multi-cluster Policies? Project SMT Solvers @luxas.dev Policies Engine -
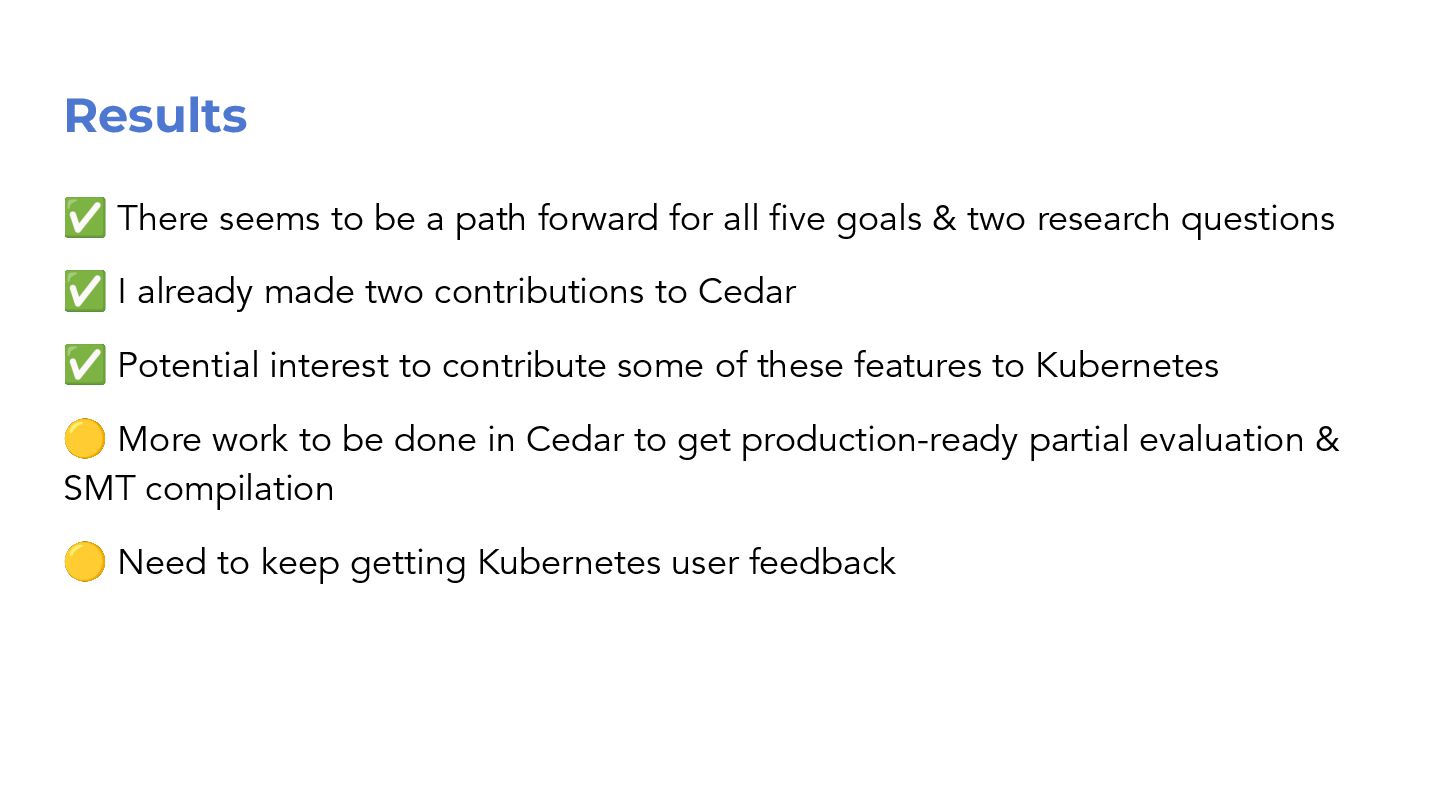
Results ✅ There seems to be a path forward for
all five goals & two research questions -
Results ✅ There seems to be a path forward for
all five goals & two research questions ✅ I already made two contributions to Cedar -
Results ✅ There seems to be a path forward for
all five goals & two research questions ✅ I already made two contributions to Cedar ✅ Potential interest to contribute some of these features to Kubernetes -
Results ✅ There seems to be a path forward for
all five goals & two research questions ✅ I already made two contributions to Cedar ✅ Potential interest to contribute some of these features to Kubernetes 🟡 More work to be done in Cedar to get production-ready partial evaluation & SMT compilation -
Results ✅ There seems to be a path forward for
all five goals & two research questions ✅ I already made two contributions to Cedar ✅ Potential interest to contribute some of these features to Kubernetes 🟡 More work to be done in Cedar to get production-ready partial evaluation & SMT compilation 🟡 Need to keep getting Kubernetes user feedback -
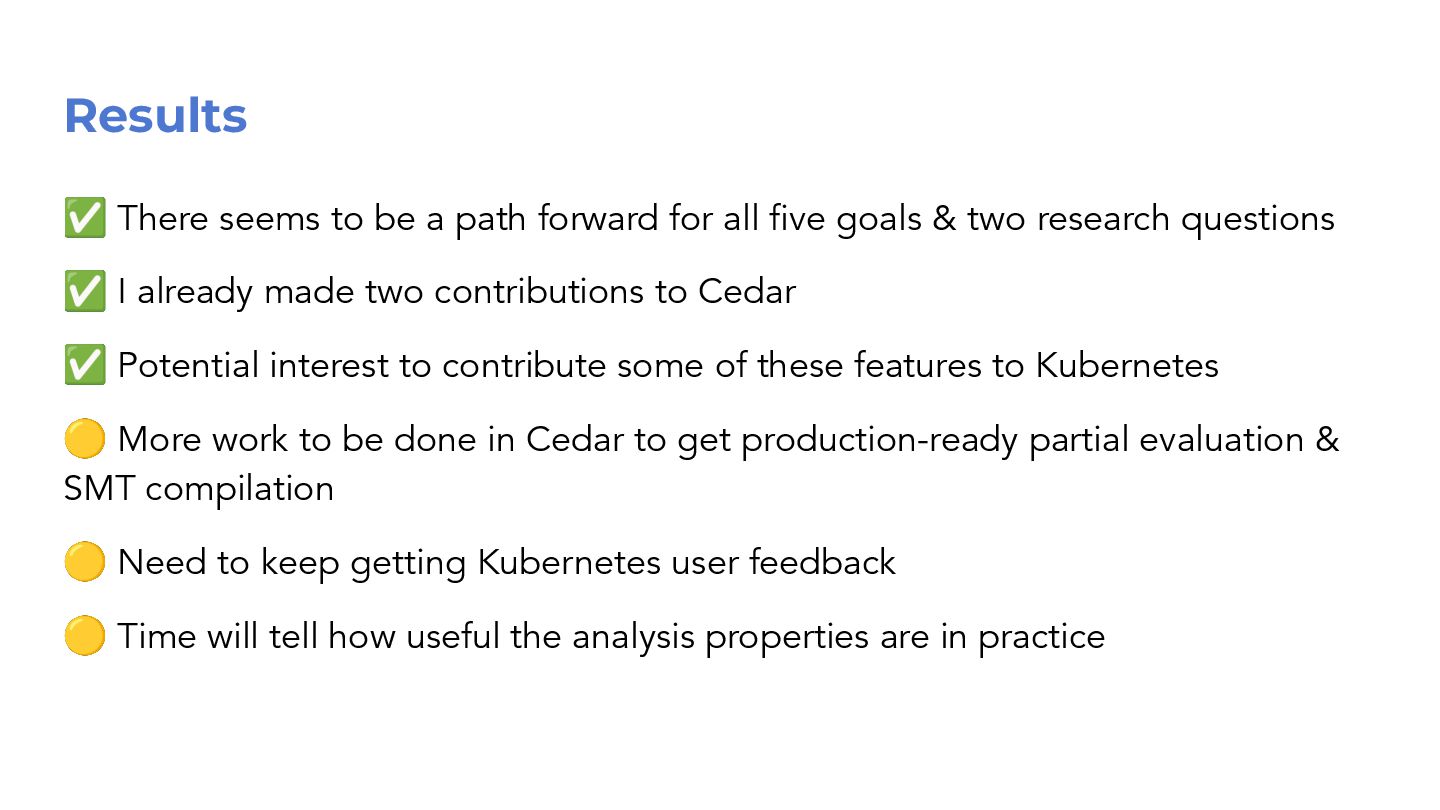
Results ✅ There seems to be a path forward for
all five goals & two research questions ✅ I already made two contributions to Cedar ✅ Potential interest to contribute some of these features to Kubernetes 🟡 More work to be done in Cedar to get production-ready partial evaluation & SMT compilation 🟡 Need to keep getting Kubernetes user feedback 🟡 Time will tell how useful the analysis properties are in practice -
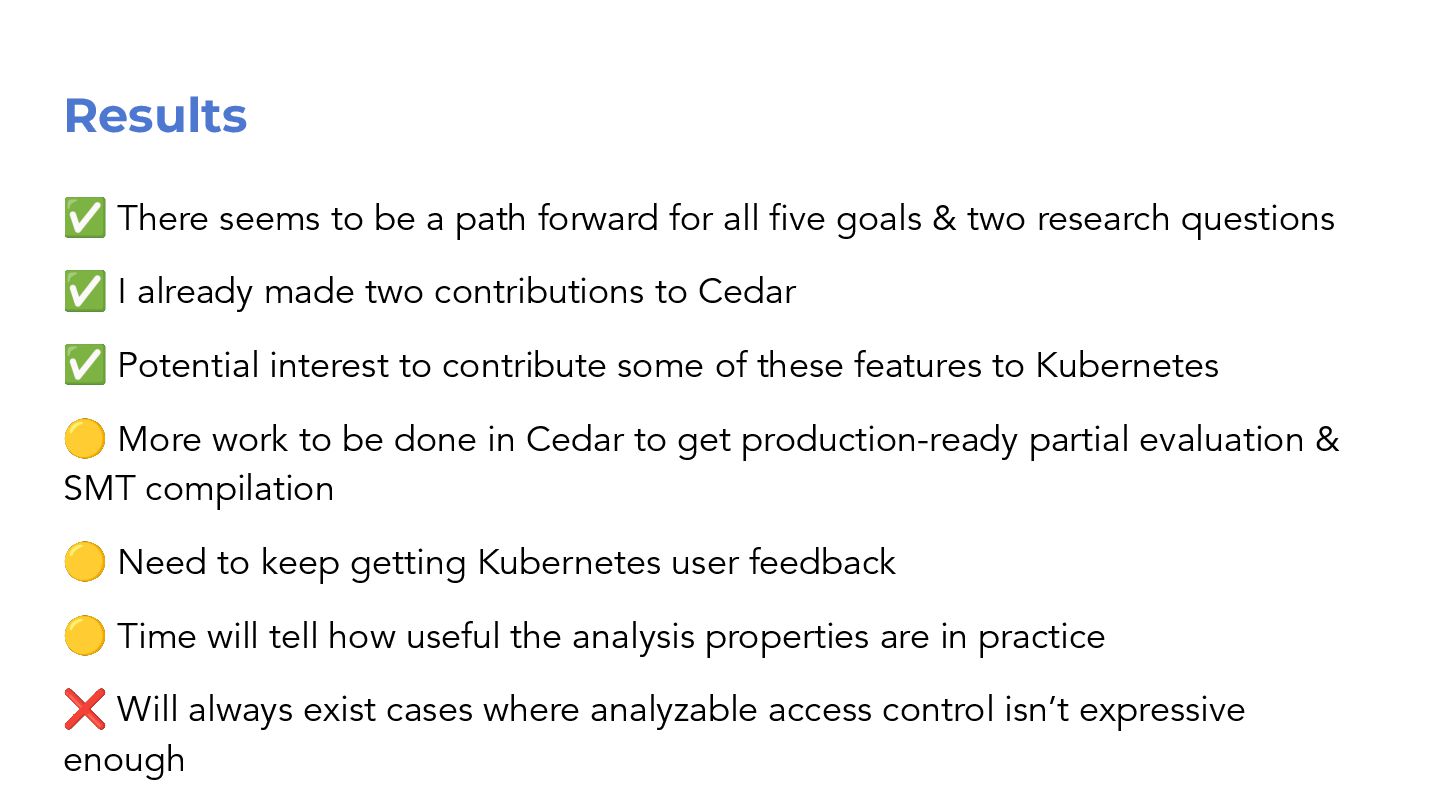
Results ✅ There seems to be a path forward for
all five goals & two research questions ✅ I already made two contributions to Cedar ✅ Potential interest to contribute some of these features to Kubernetes 🟡 More work to be done in Cedar to get production-ready partial evaluation & SMT compilation 🟡 Need to keep getting Kubernetes user feedback 🟡 Time will tell how useful the analysis properties are in practice ❌ Will always exist cases where analyzable access control isn’t expressive enough -
Thanks! Please give feedback! Email: [email protected] Bluesky: @luxas.dev LinkedIn: luxas
CNCF/Kubernetes Slack: luxas Credits: Icons by Flaticon