Upgrade to Pro — share decks privately, control downloads, hide ads and more …

CSC510 Lecture 21

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →

CSC510 Lecture 21

Cognito
(20261019)

Avatar for Javier Gonzalez-Sanchez

Javier Gonzalez-Sanchez PRO

October 26, 2026

More Decks by Javier Gonzalez-Sanchez

Other Decks in Programming

Transcript

  1. CSC 5100 Modern Software Engineering Lecture 21. Amazon Cognito Dr.

    Javier Gonzalez-Sanchez [email protected] www.javiergs.phd ffi o ce: 14 -227
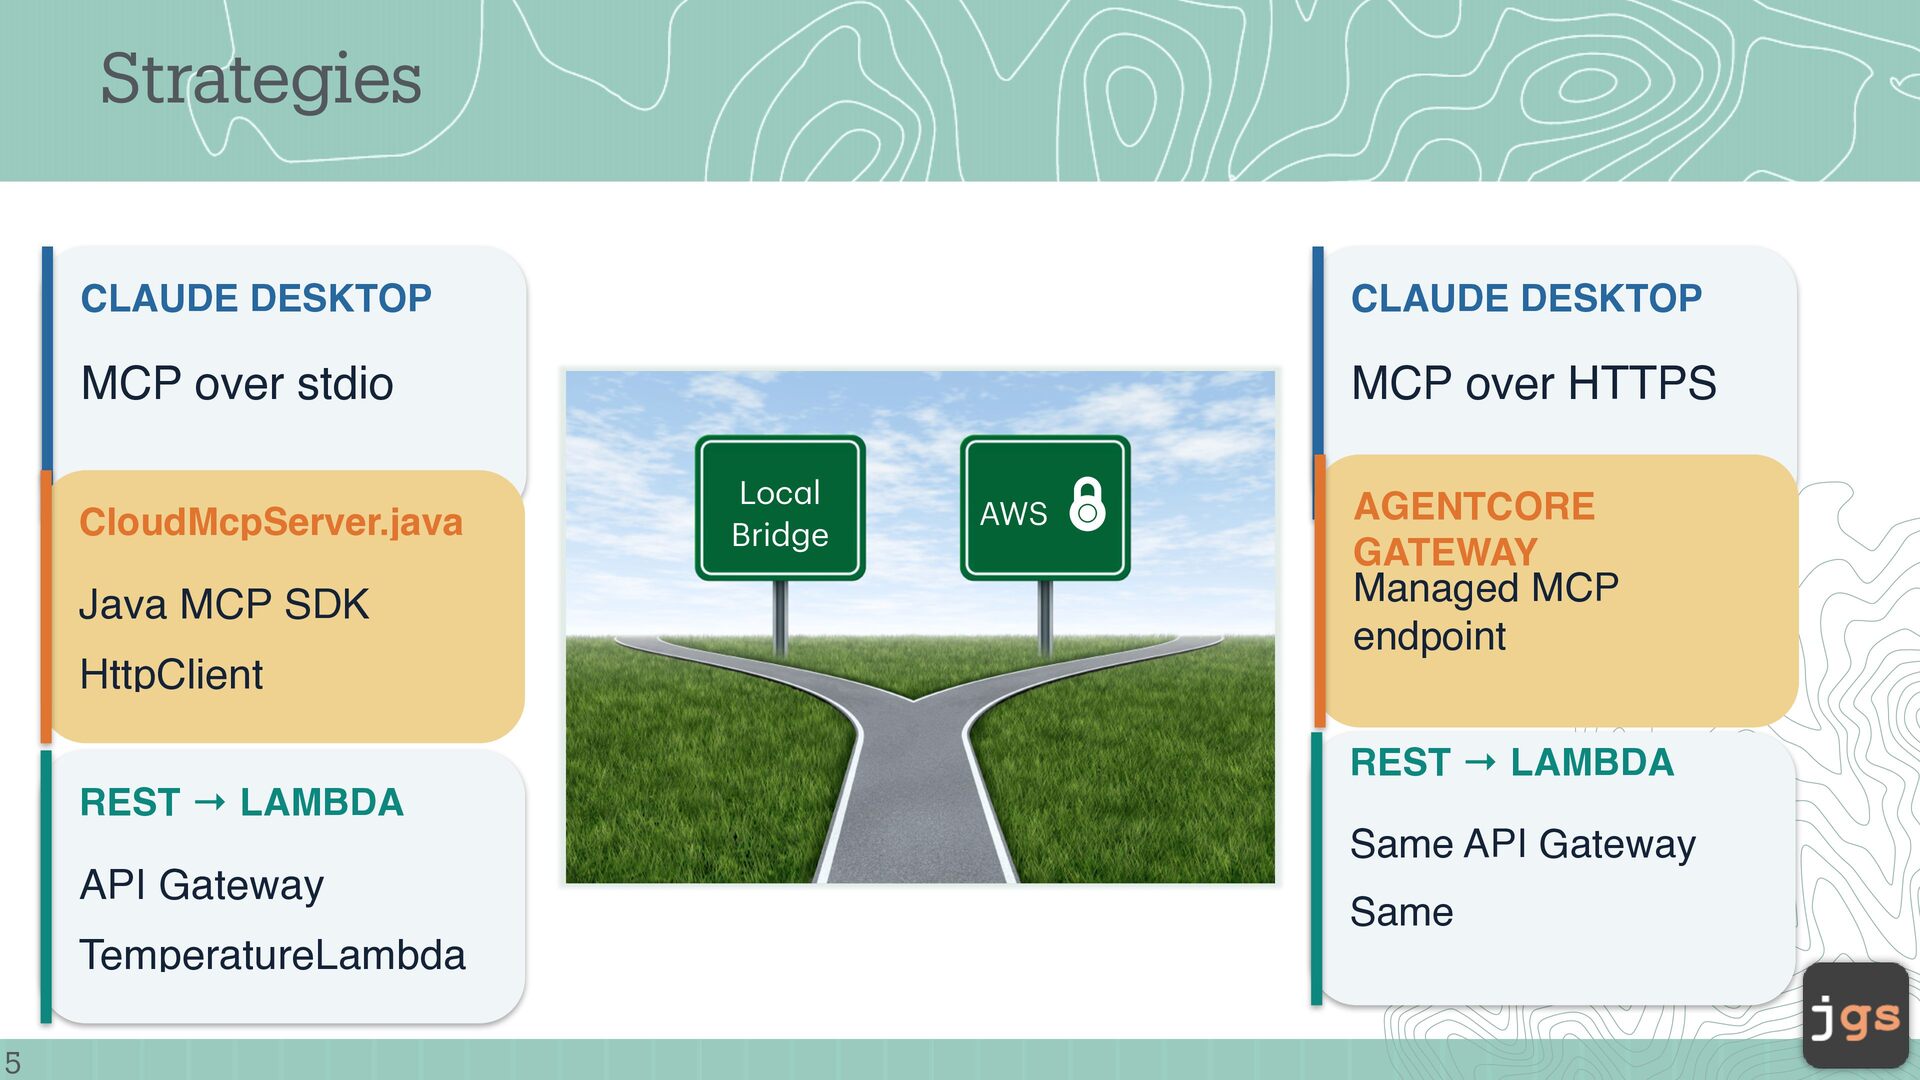
  2. Strategies CLAUDE DESKTOP CLAUDE DESKTOP MCP over stdio MCP over

    HTTPS CloudMcpServer.java Java MCP SDK HttpClient REST → LAMBDA API Gateway 5 a TemperatureLambda Loc l Bridge AWS AGENTCORE GATEWAY Managed MCP endpoint REST → LAMBDA Same API Gateway Same
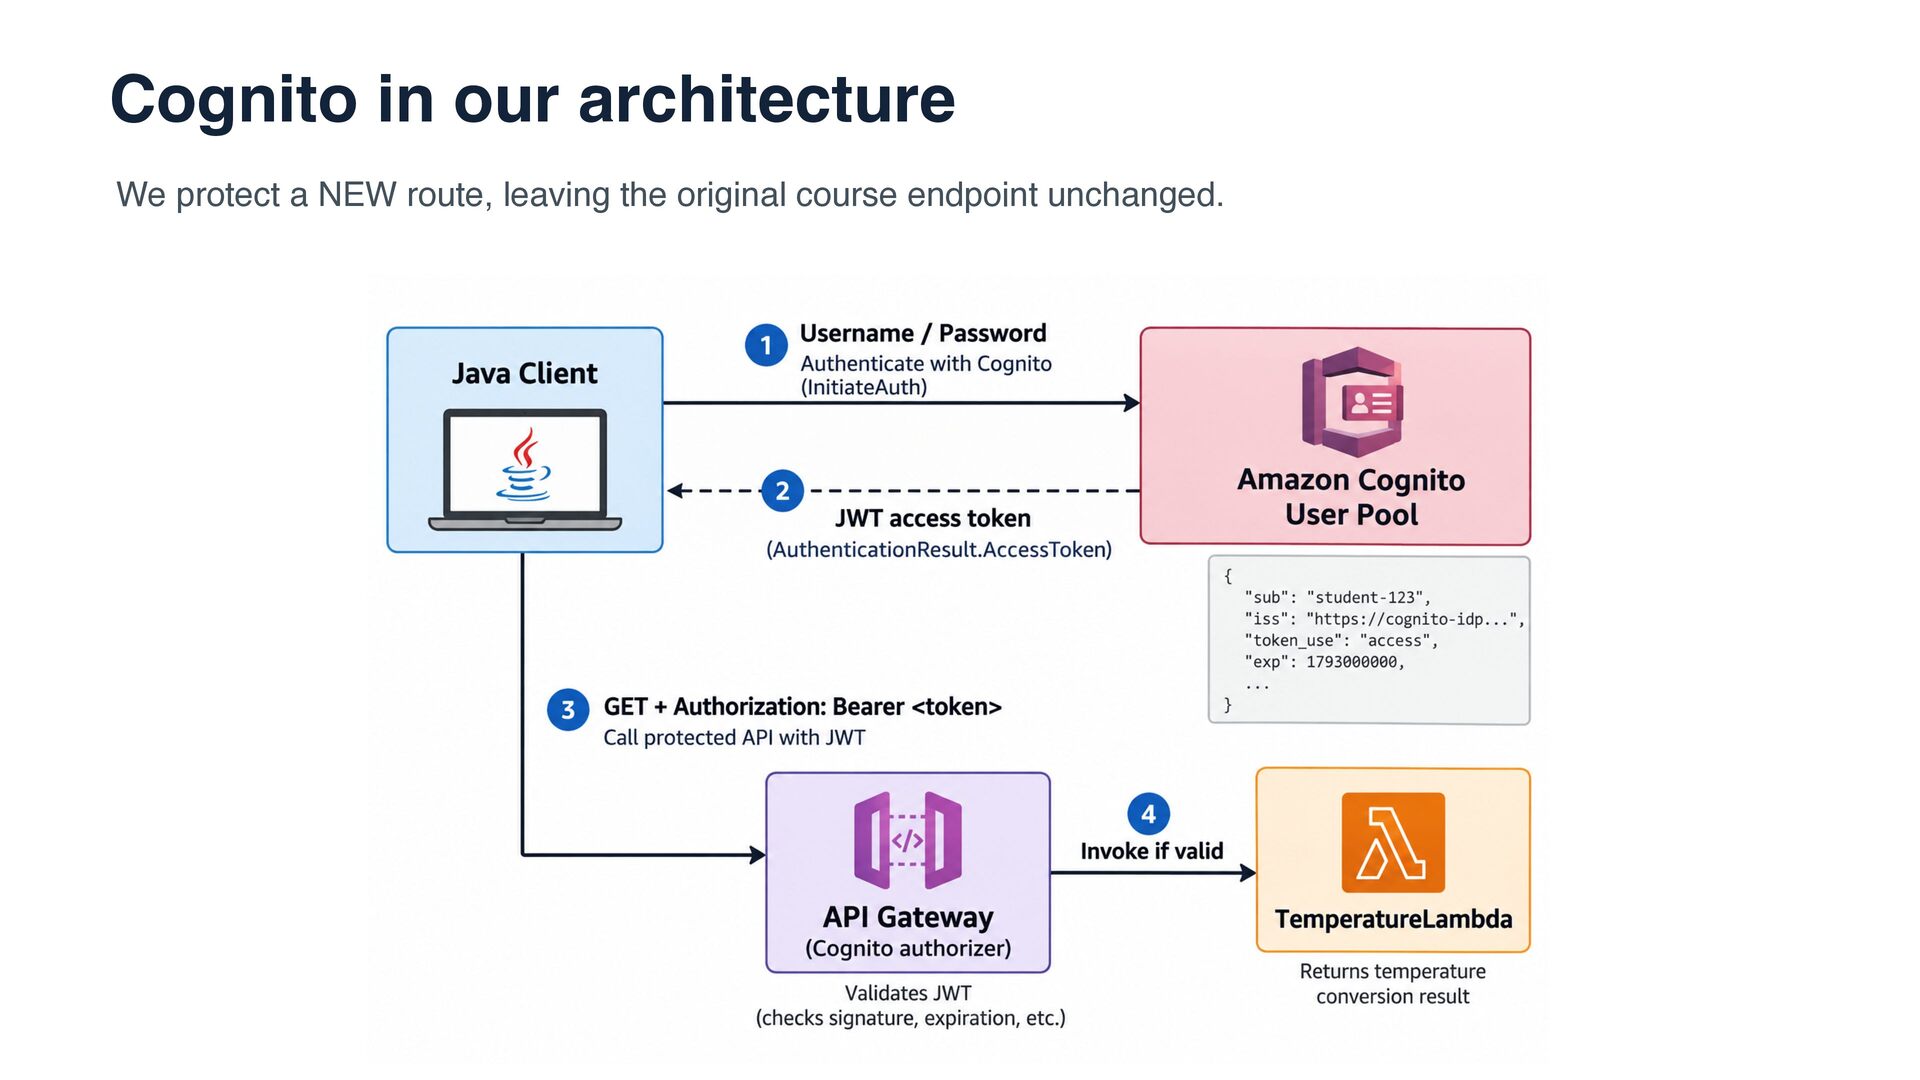
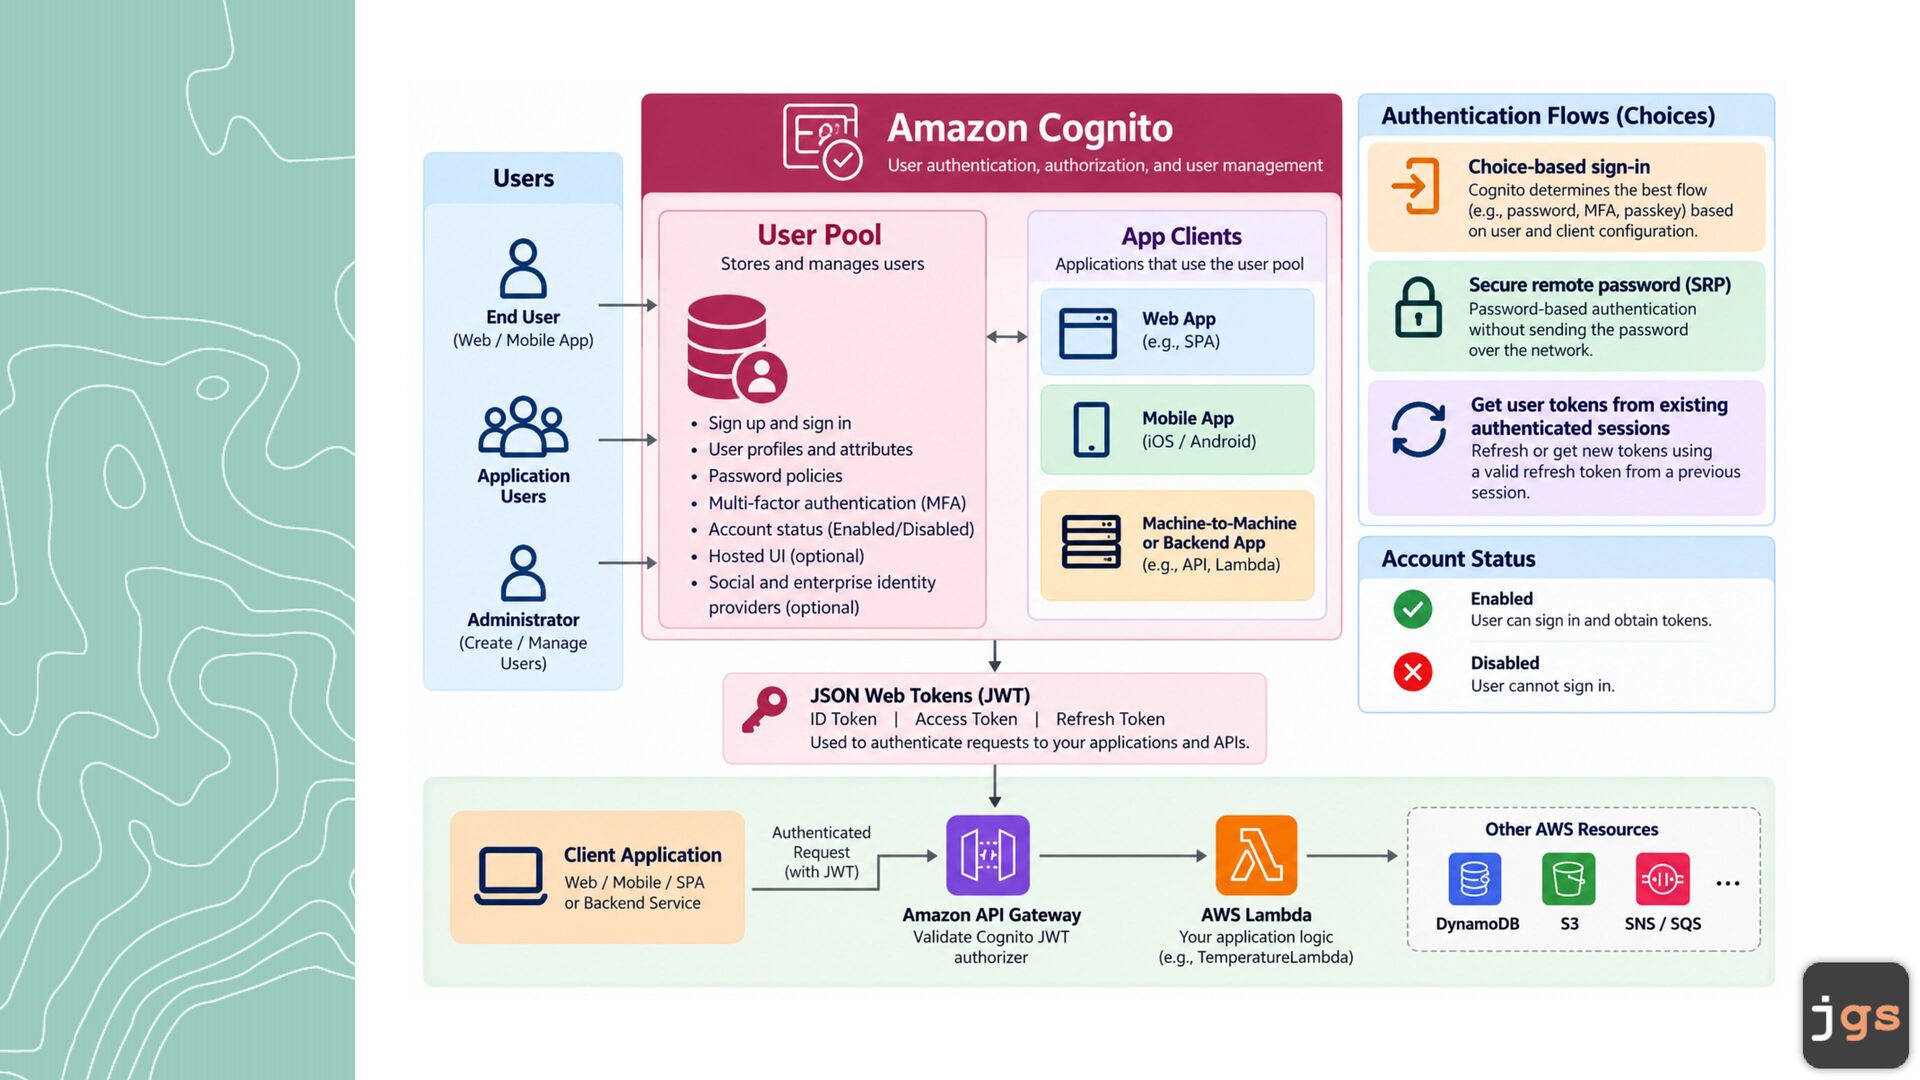
  3. Cognito in our architecture We protect a NEW route, leaving

    the original course endpoint unchanged.
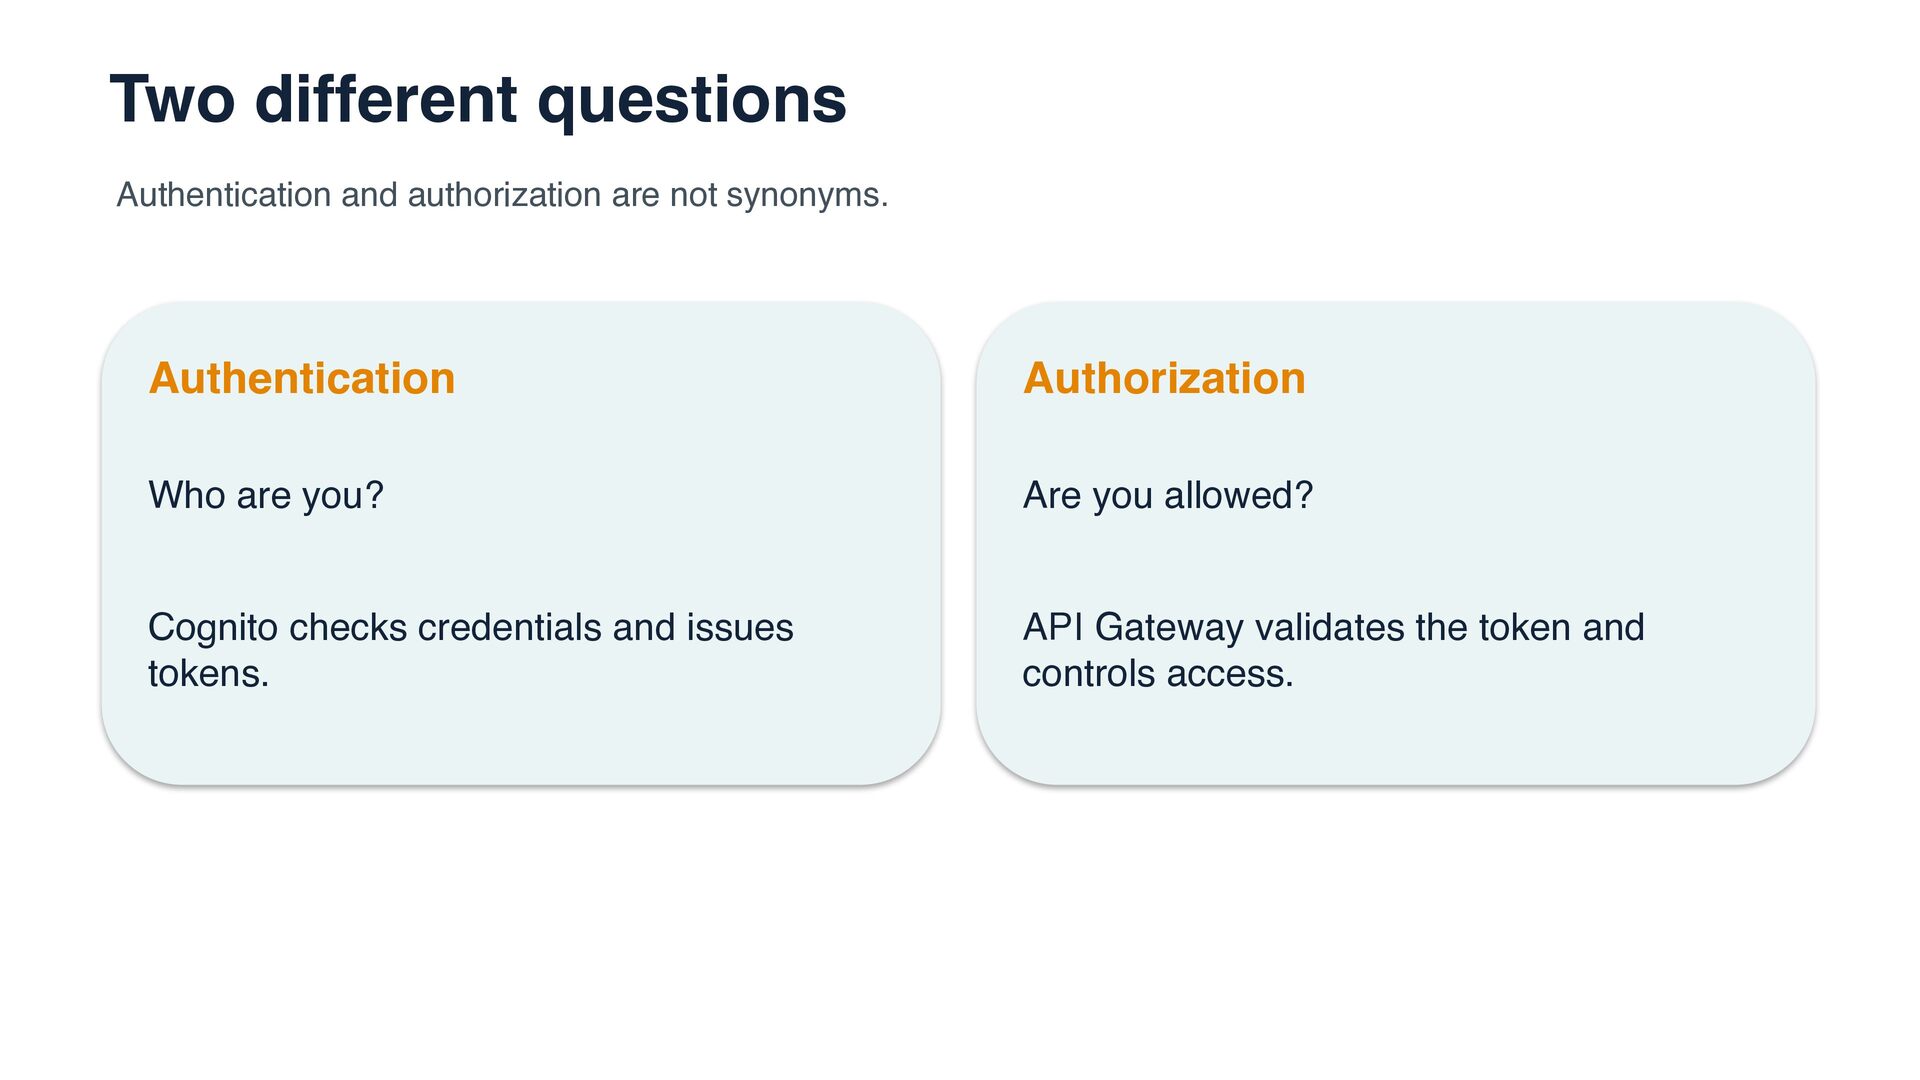
  4. Two different questions Authentication and authorization are not synonyms. Authentication

    Authorization Who are you? Are you allowed? Cognito checks credentials and issues tokens. API Gateway validates the token and controls access.
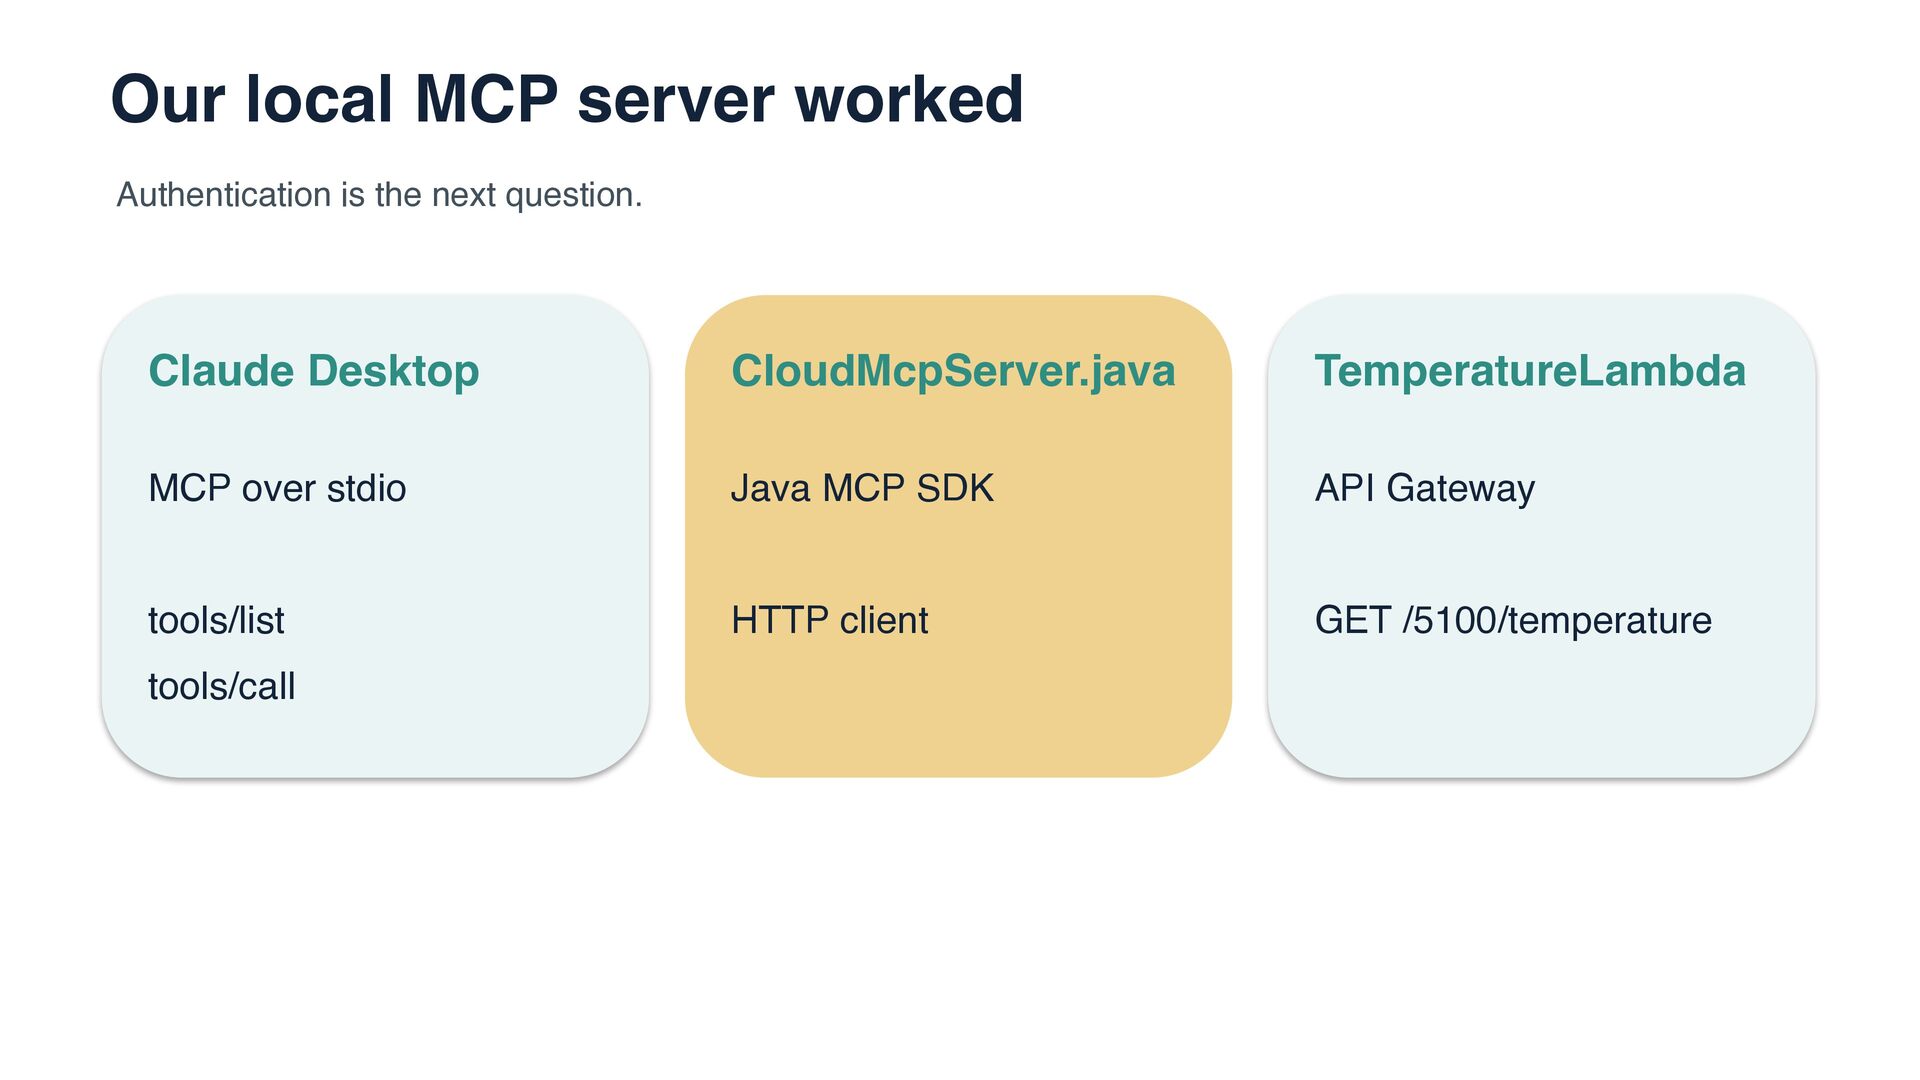
  5. Our local MCP server worked Authentication is the next question.

    Claude Desktop CloudMcpServer.java TemperatureLambda MCP over stdio Java MCP SDK API Gateway tools/list HTTP client GET /5100/temperature tools/call
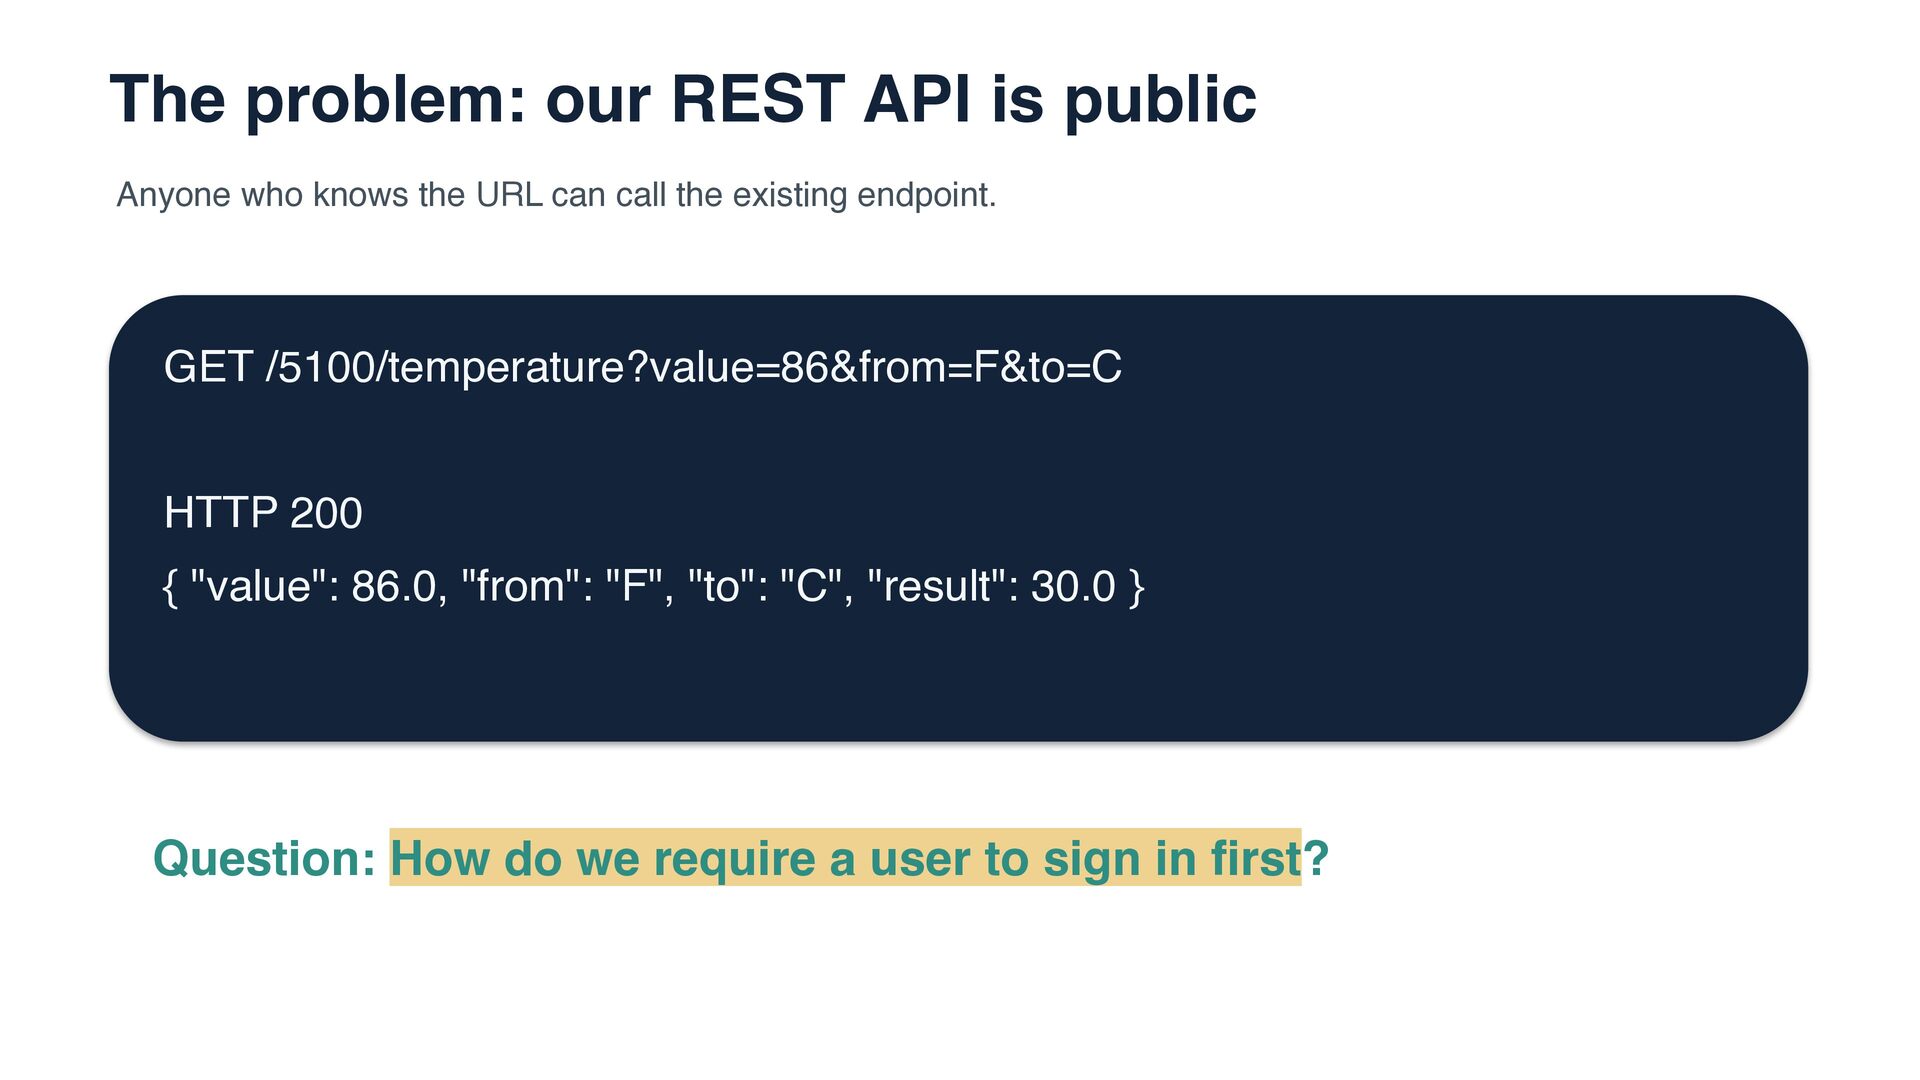
  6. The problem: our REST API is public Anyone who knows

    the URL can call the existing endpoint. GET /5100/temperature?value=86&from=F&to=C HTTP 200 { "value": 86.0, "from": "F", "to": "C", "result": 30.0 } Question: How do we require a user to sign in first?
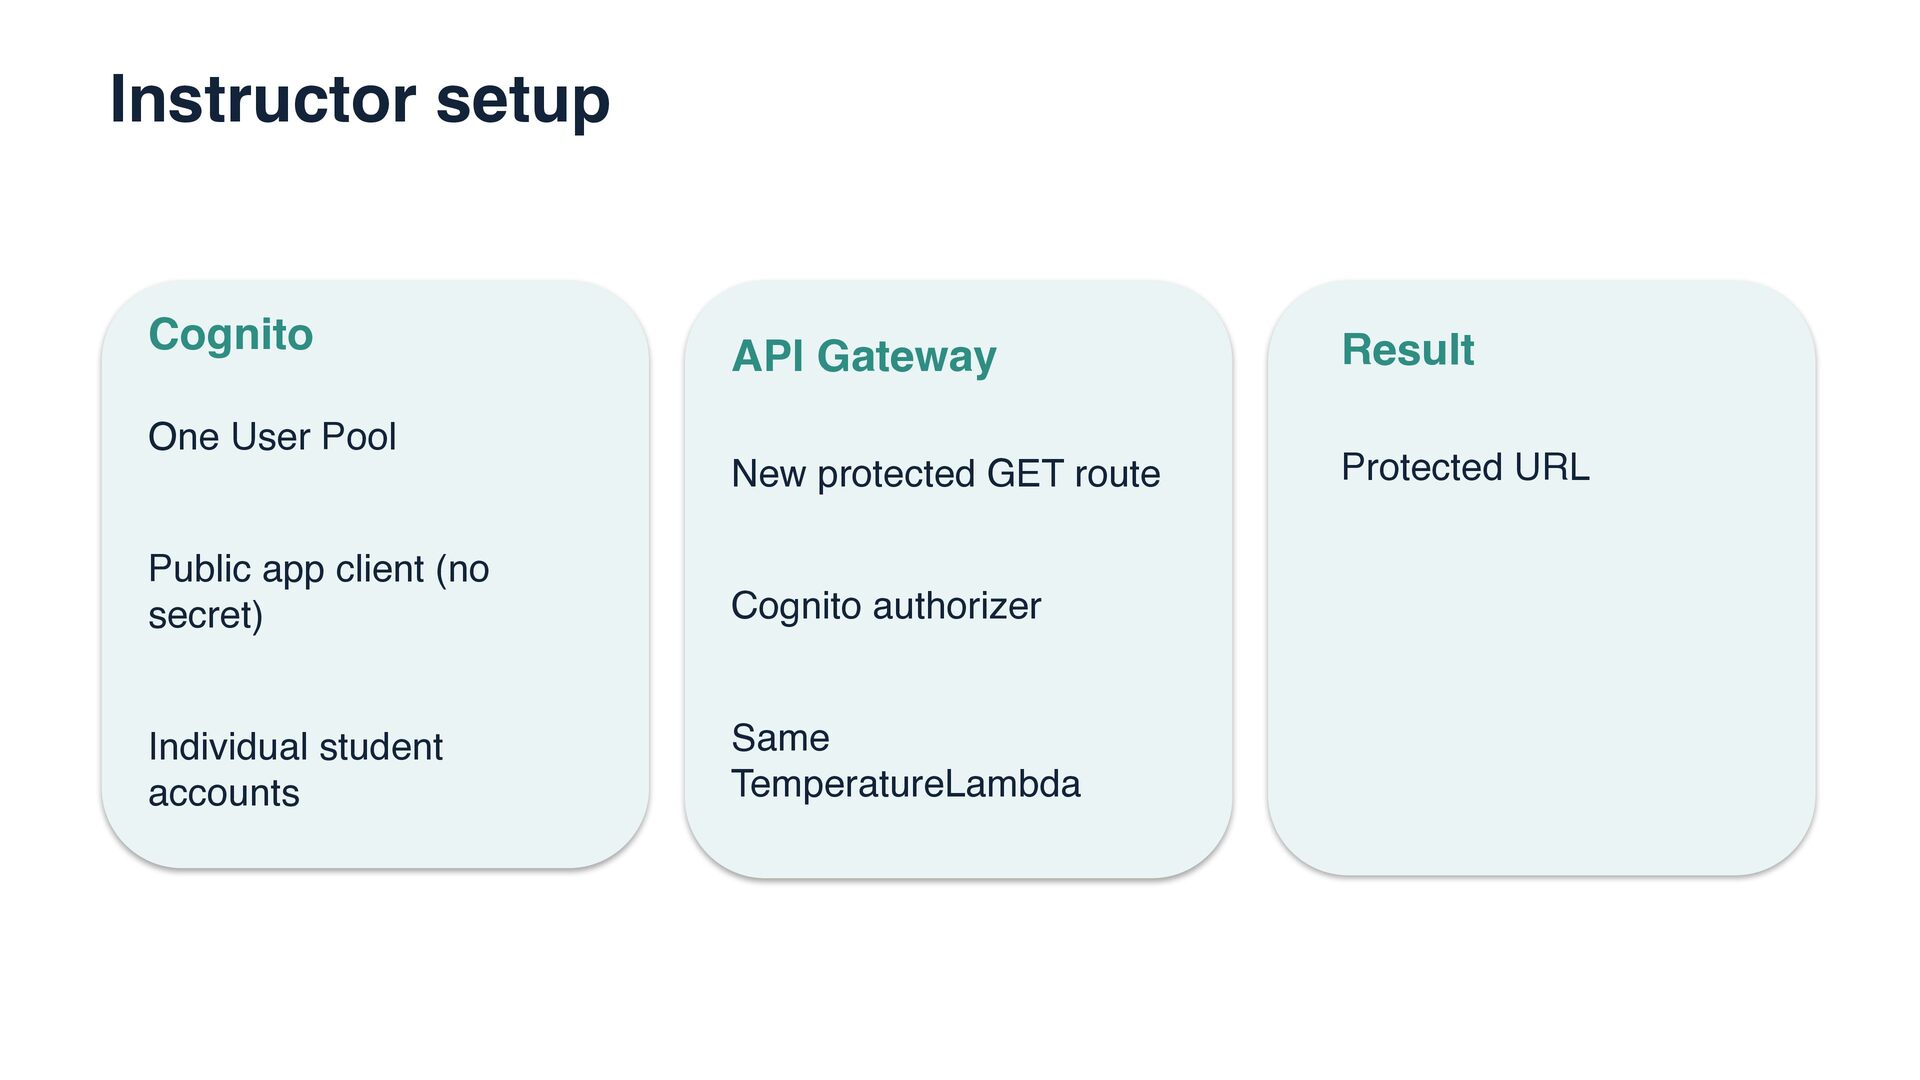
  7. Instructor setup Cognito One User Pool API Gateway Result New

    protected GET route Protected URL Public app client (no secret) Cognito authorizer Individual student accounts Same TemperatureLambda
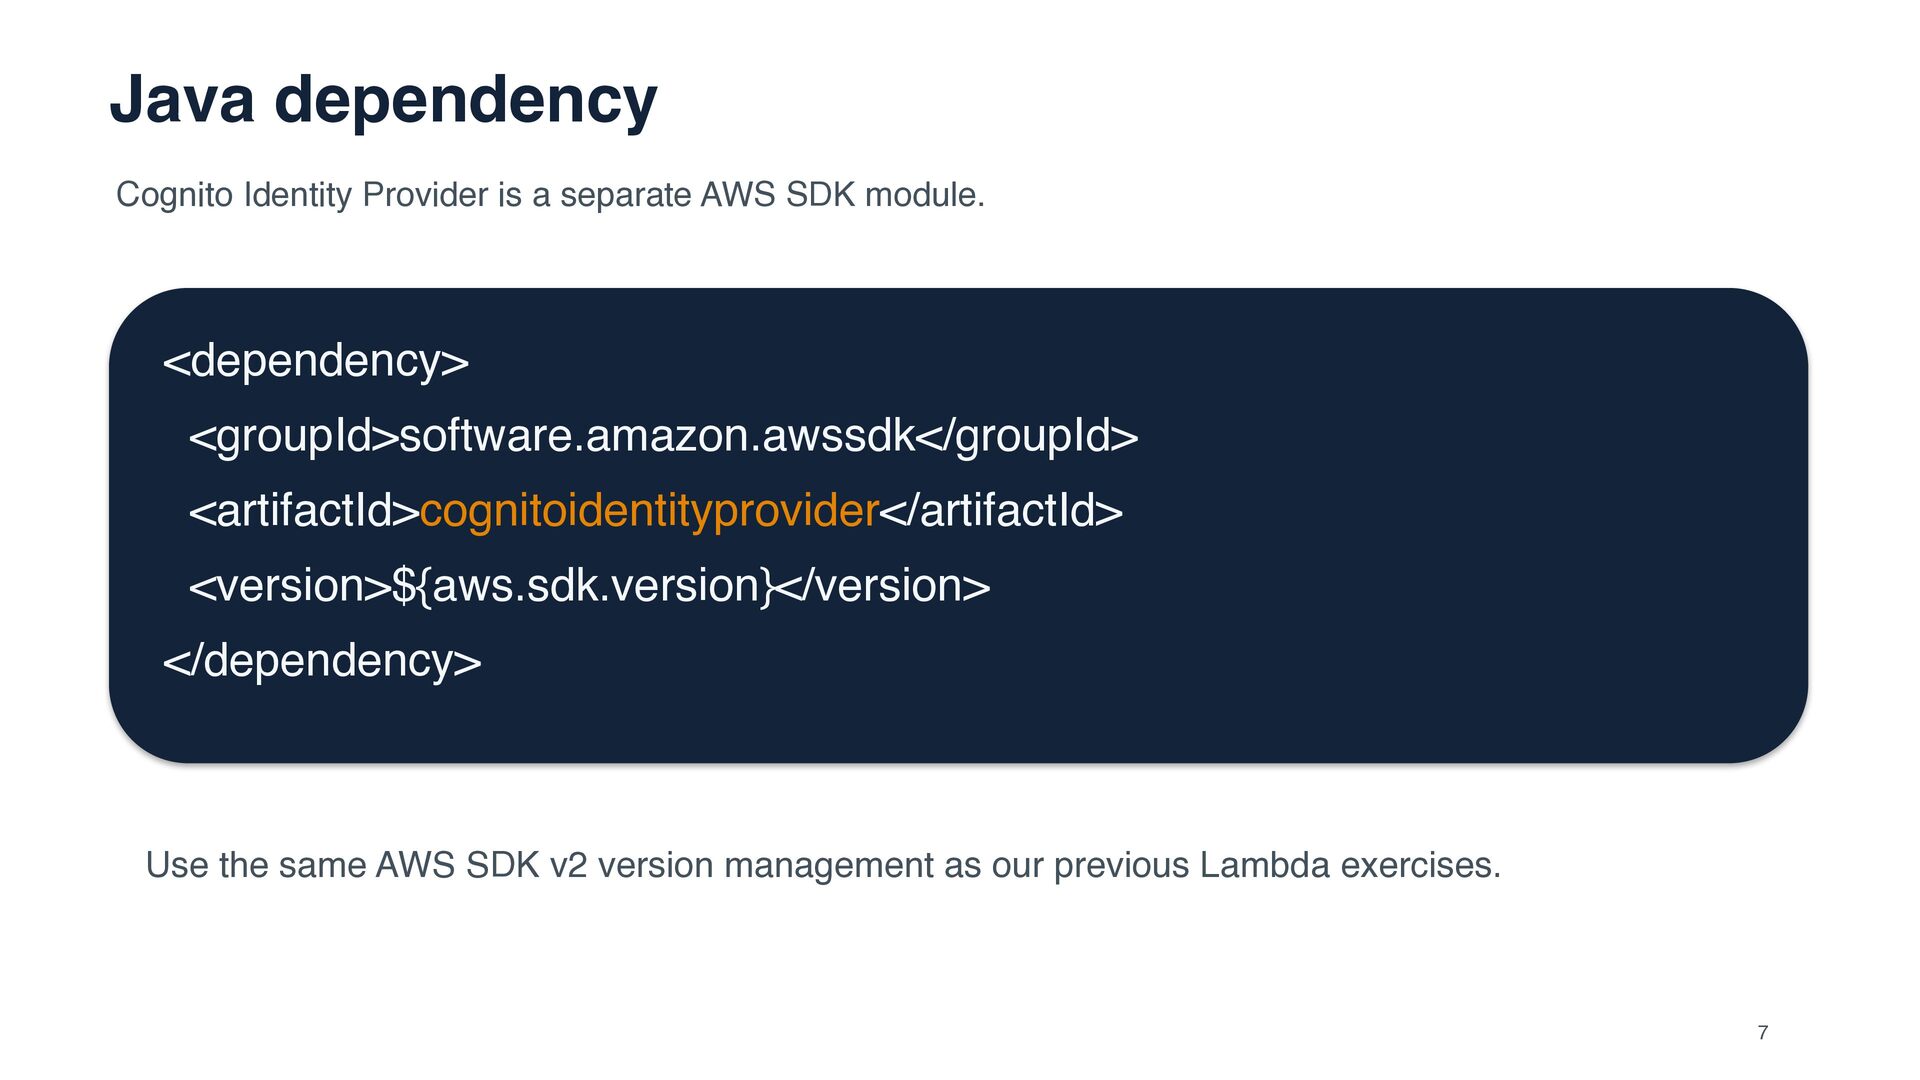
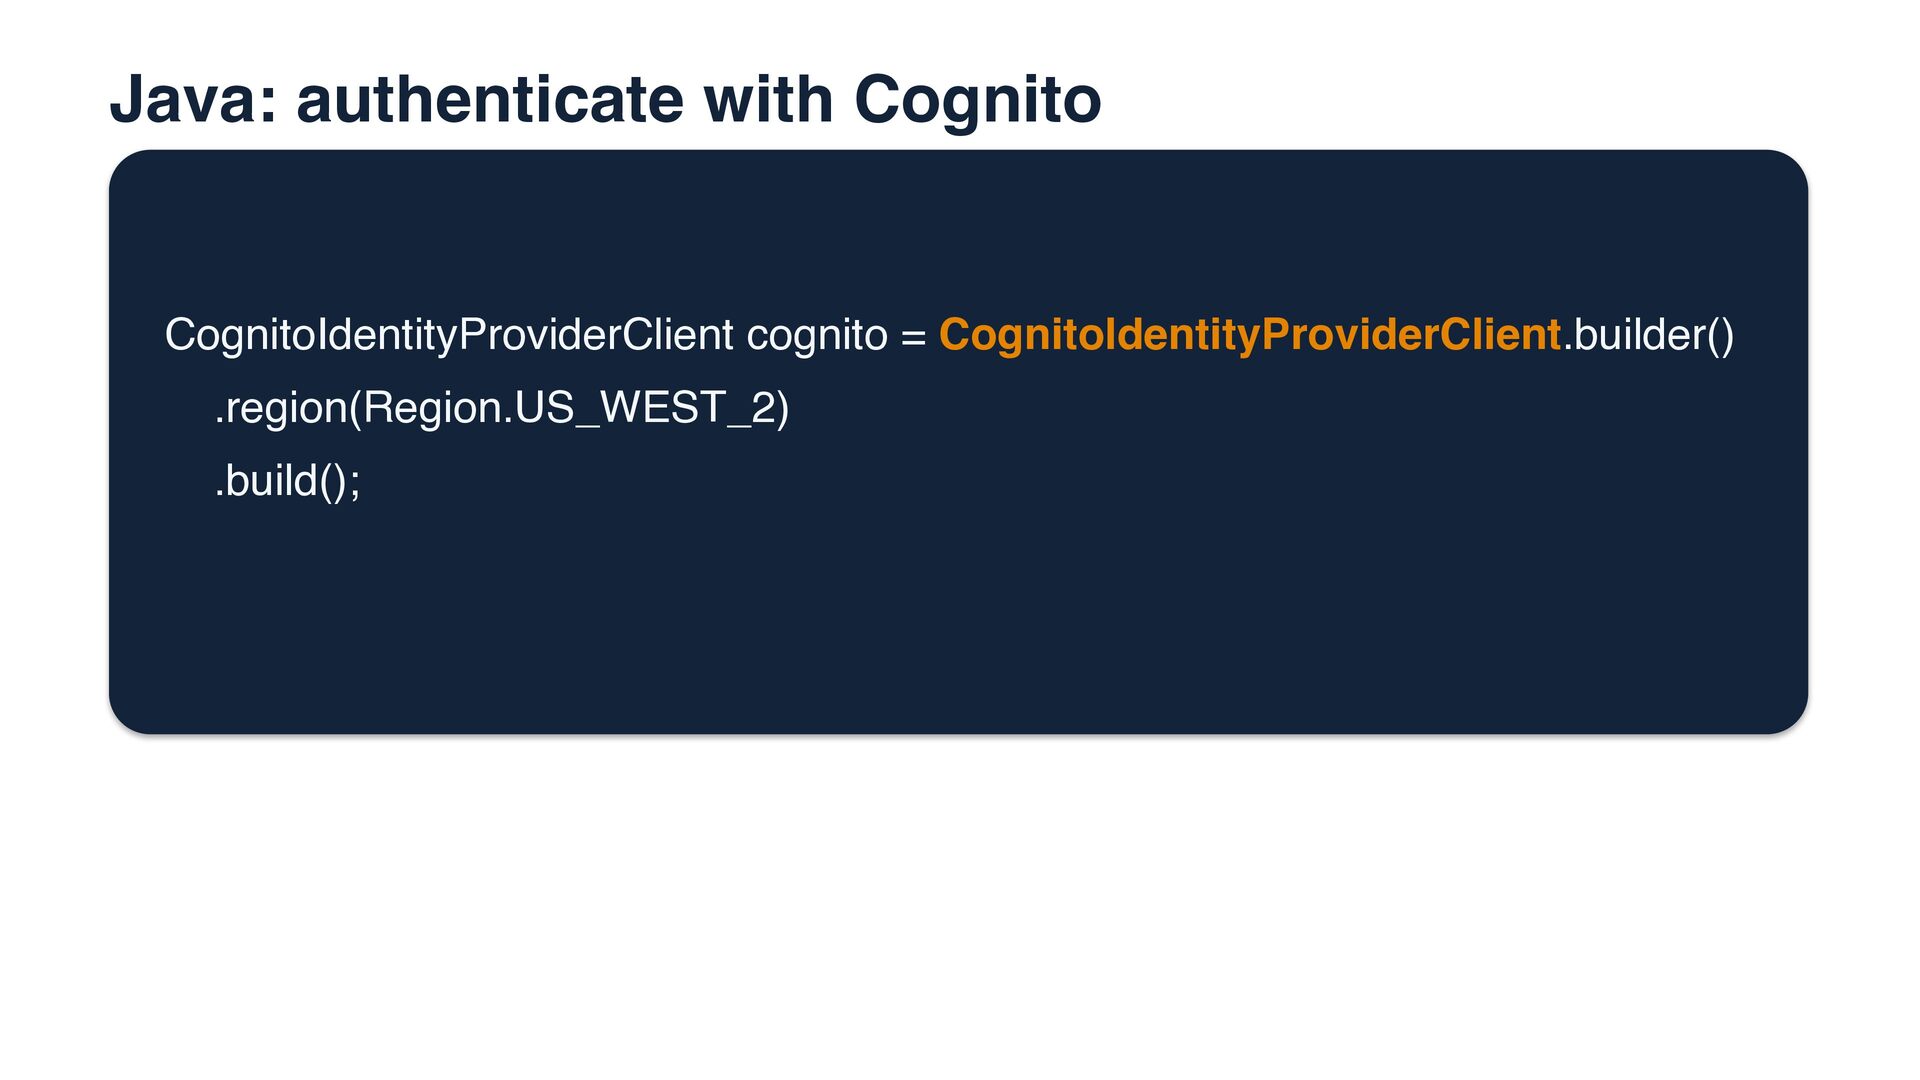
  8. Java dependency Cognito Identity Provider is a separate AWS SDK

    module. <dependency> <groupId>software.amazon.awssdk</groupId> <artifactId>cognitoidentityprovider</artifactId> <version>${aws.sdk.version}</version> </dependency> Use the same AWS SDK v2 version management as our previous Lambda exercises. 7
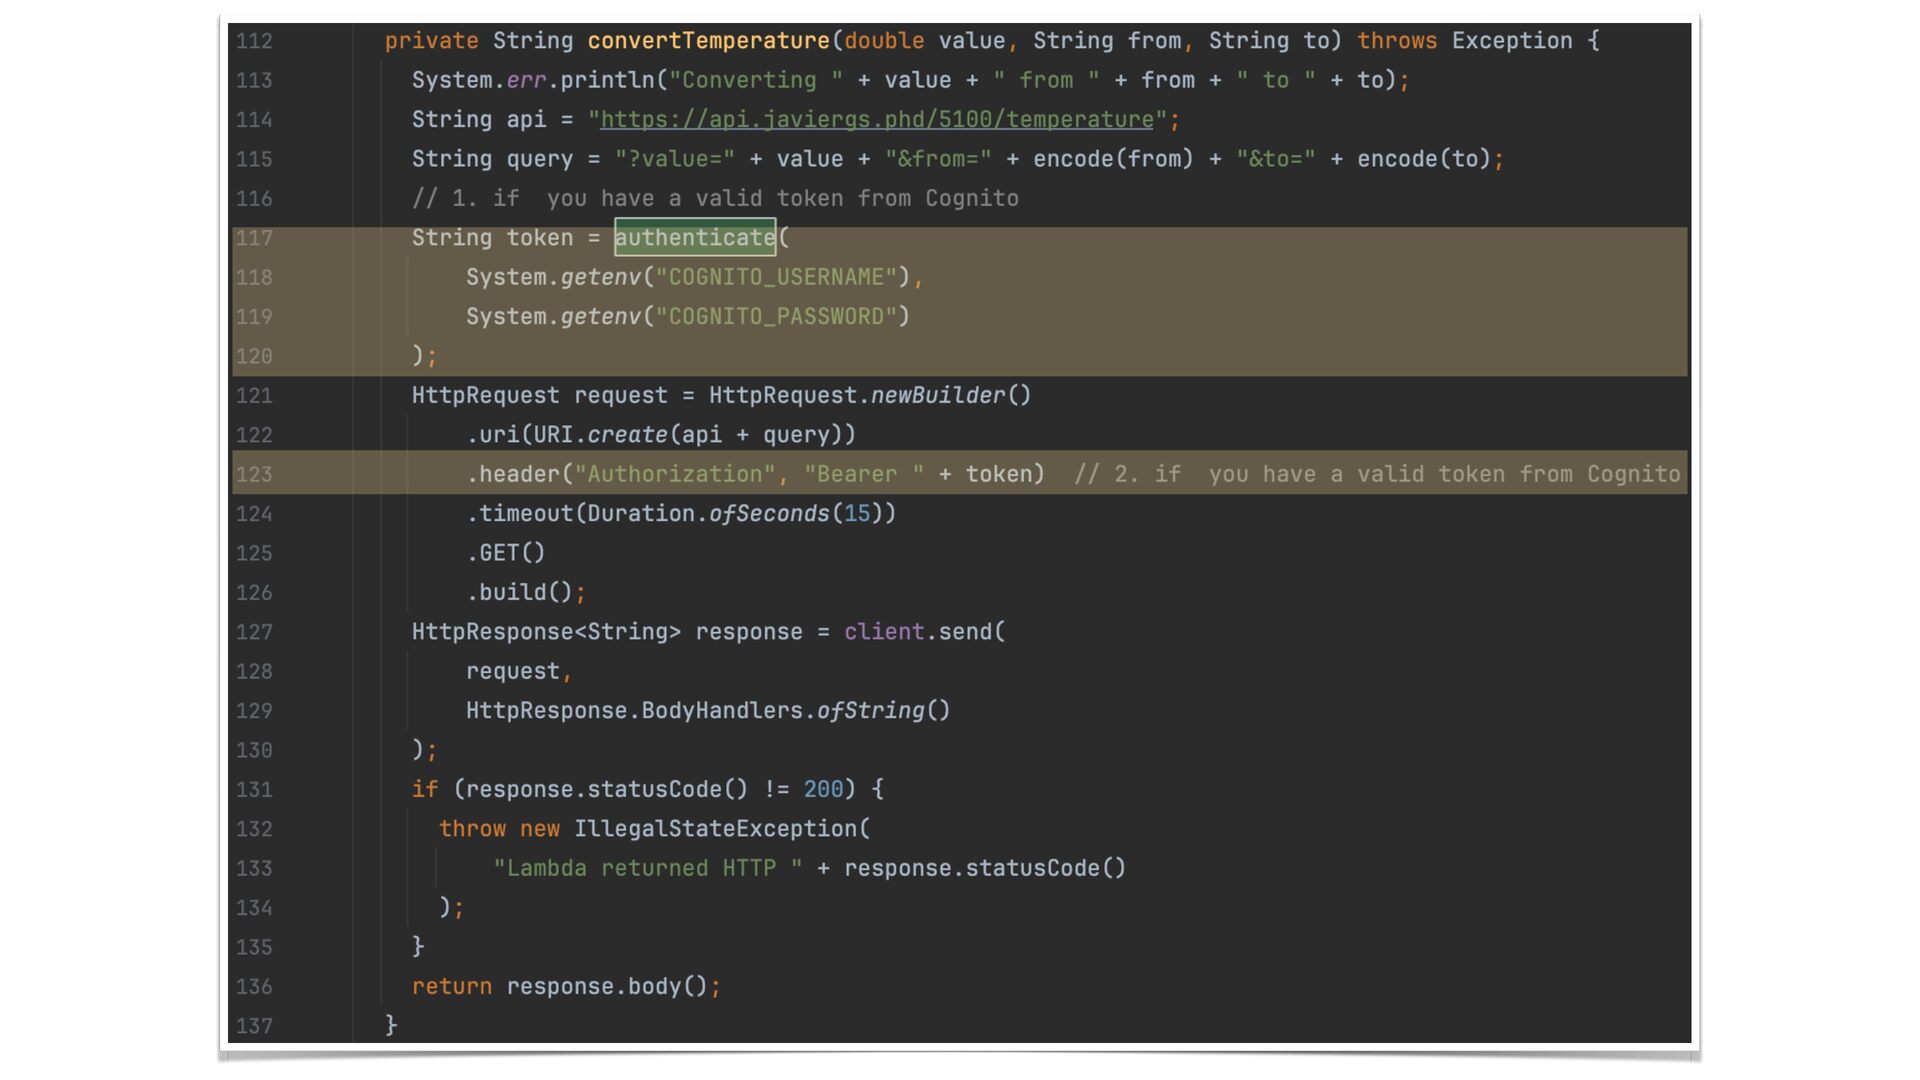
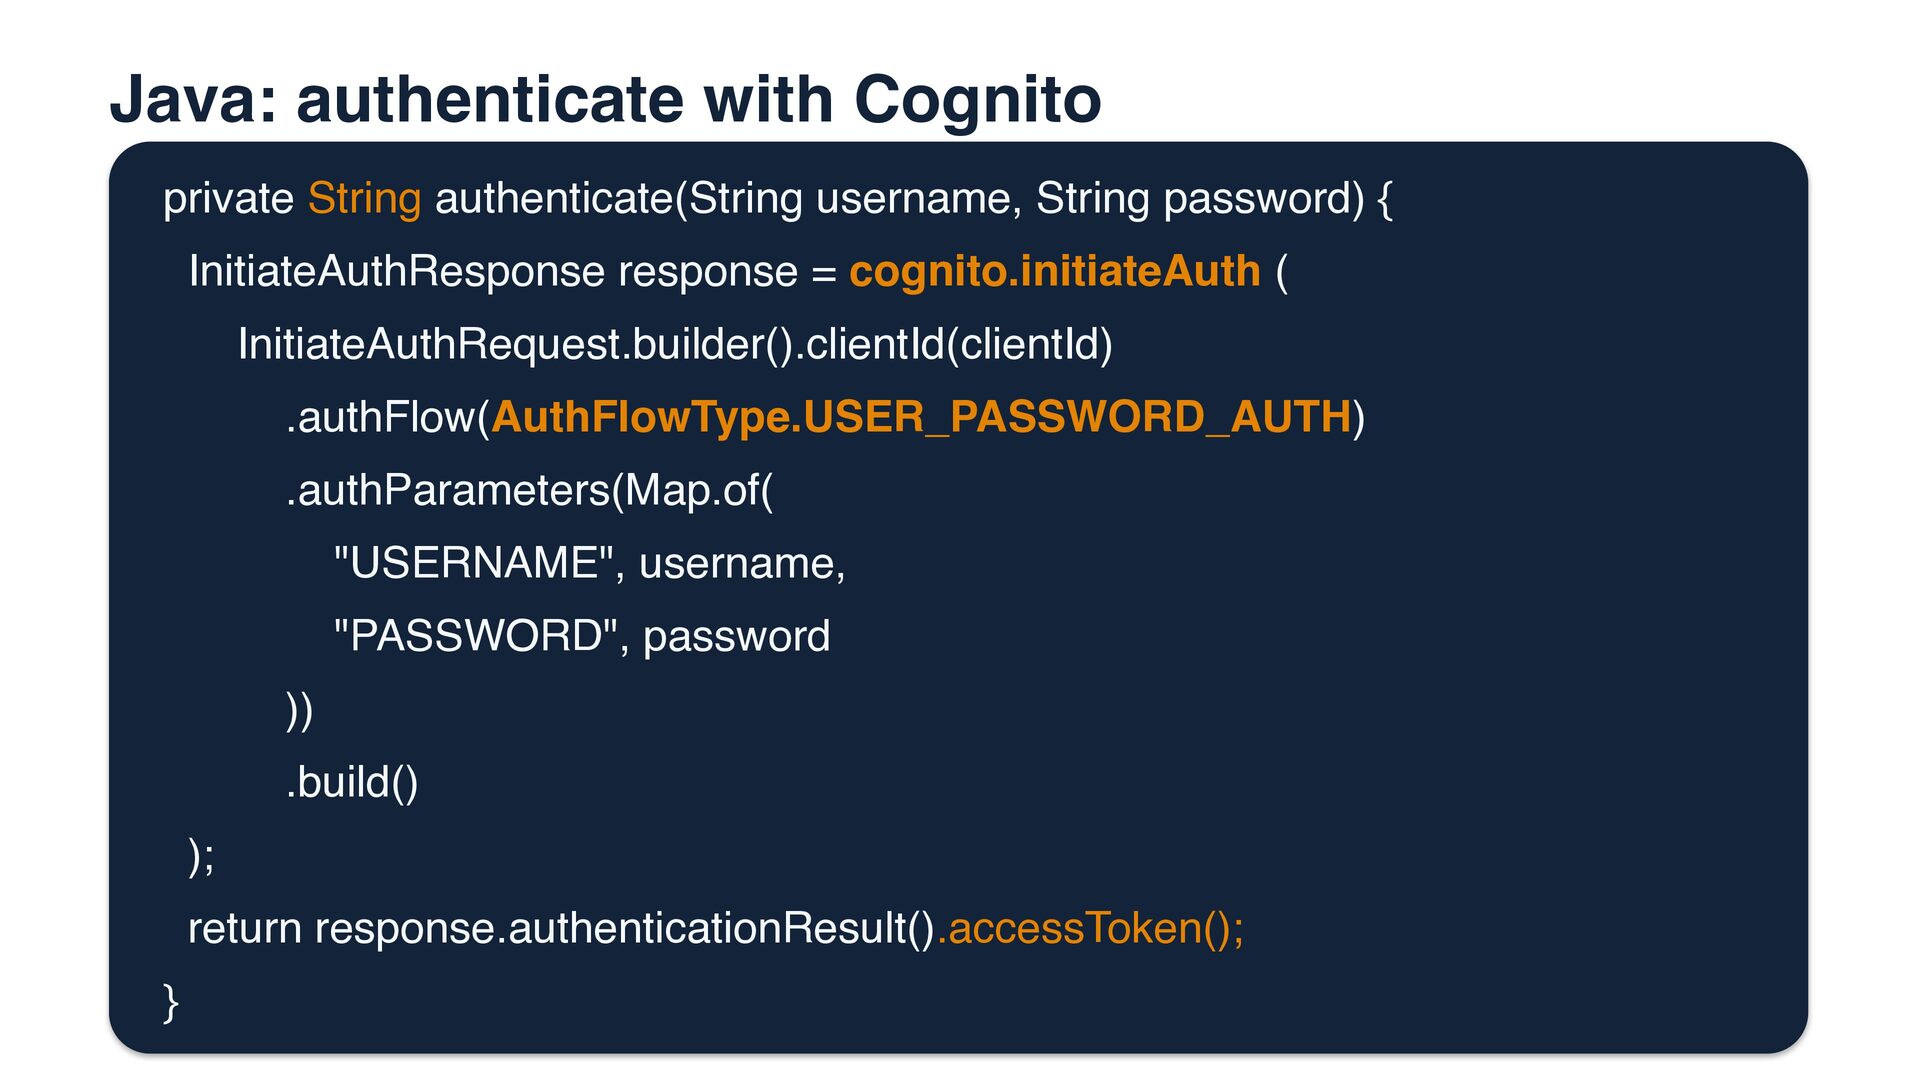
  9. Java: authenticate with Cognito private String authenticate(String username, String password)

    { InitiateAuthResponse response = cognito.initiateAuth ( InitiateAuthRequest.builder().clientId(clientId) .authFlow(AuthFlowType.USER_PASSWORD_AUTH) .authParameters(Map.of( "USERNAME", username, "PASSWORD", password )) .build() ); return response.authenticationResult().accessToken(); }
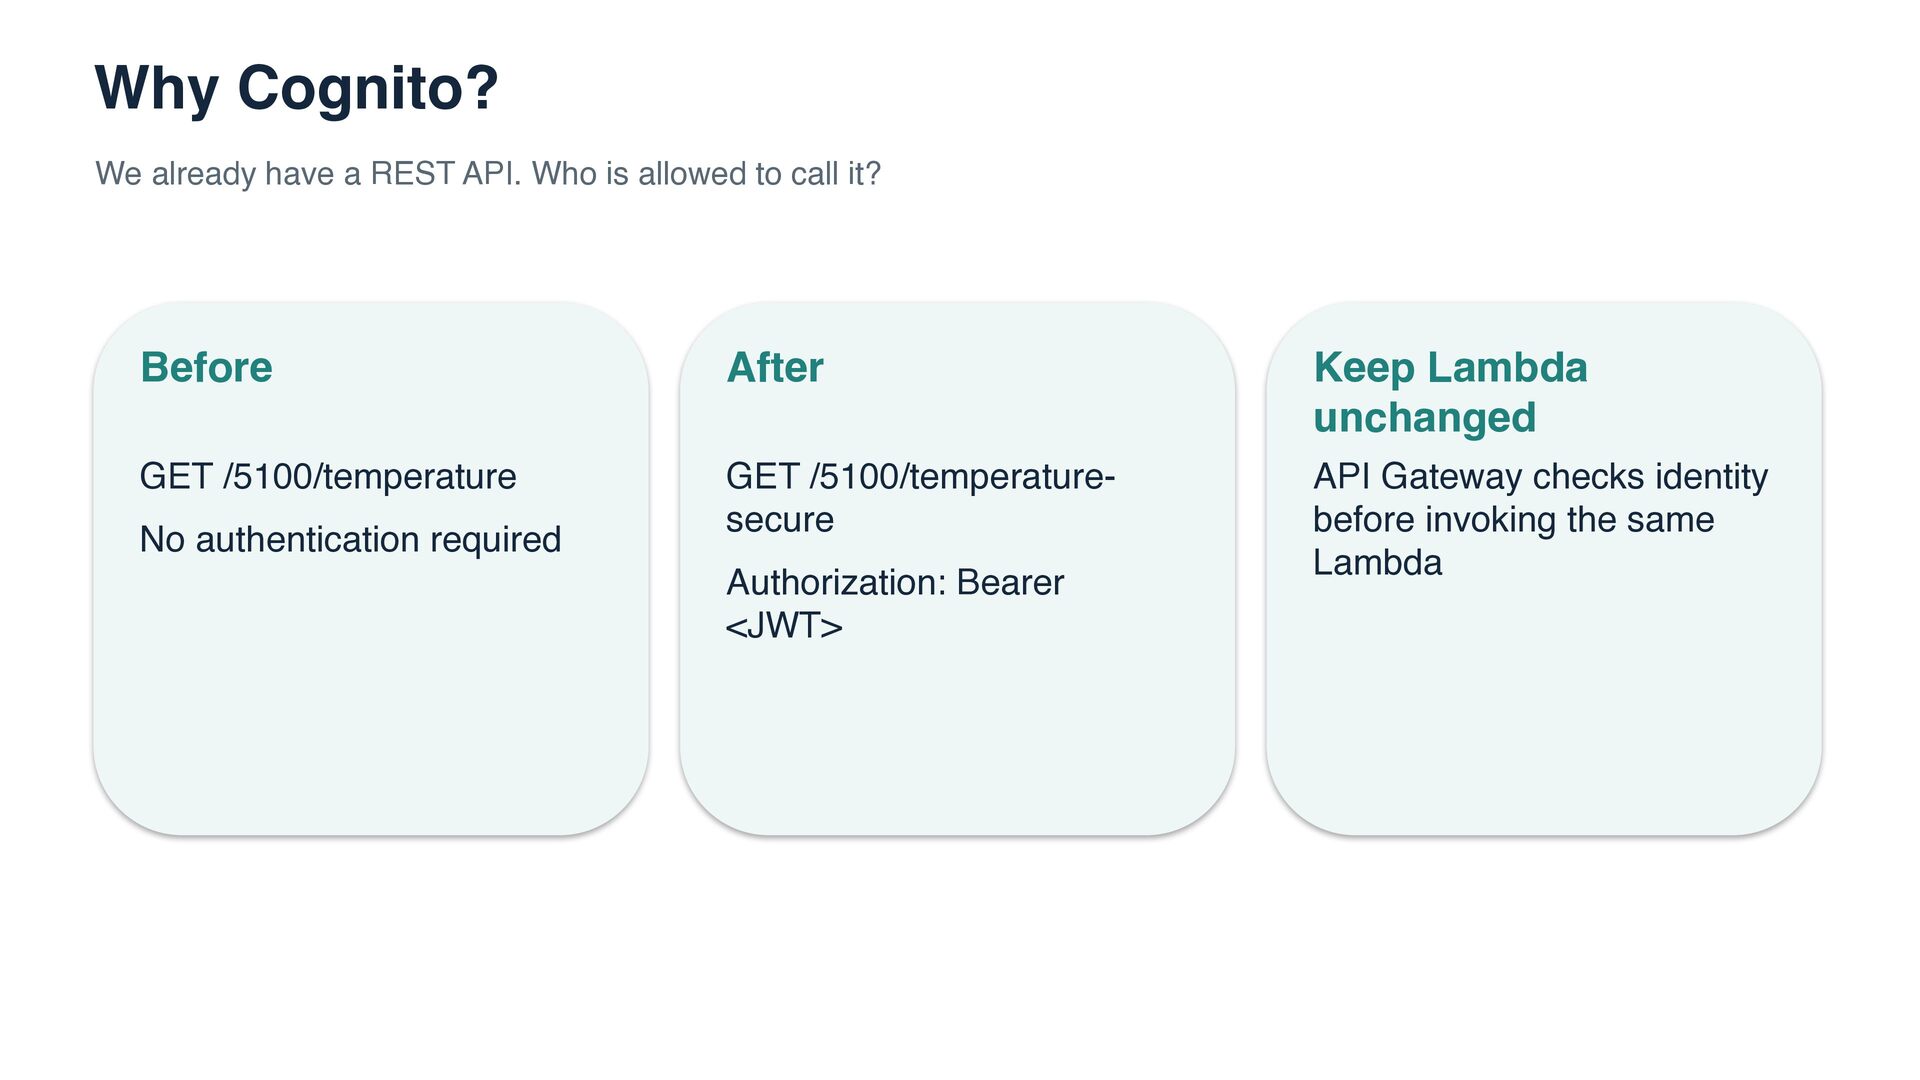
  10. Why Cognito? We already have a REST API. Who is

    allowed to call it? Before After Keep Lambda unchanged GET /5100/temperature GET /5100/temperaturesecure API Gateway checks identity before invoking the same Lambda No authentication required Authorization: Bearer <JWT>
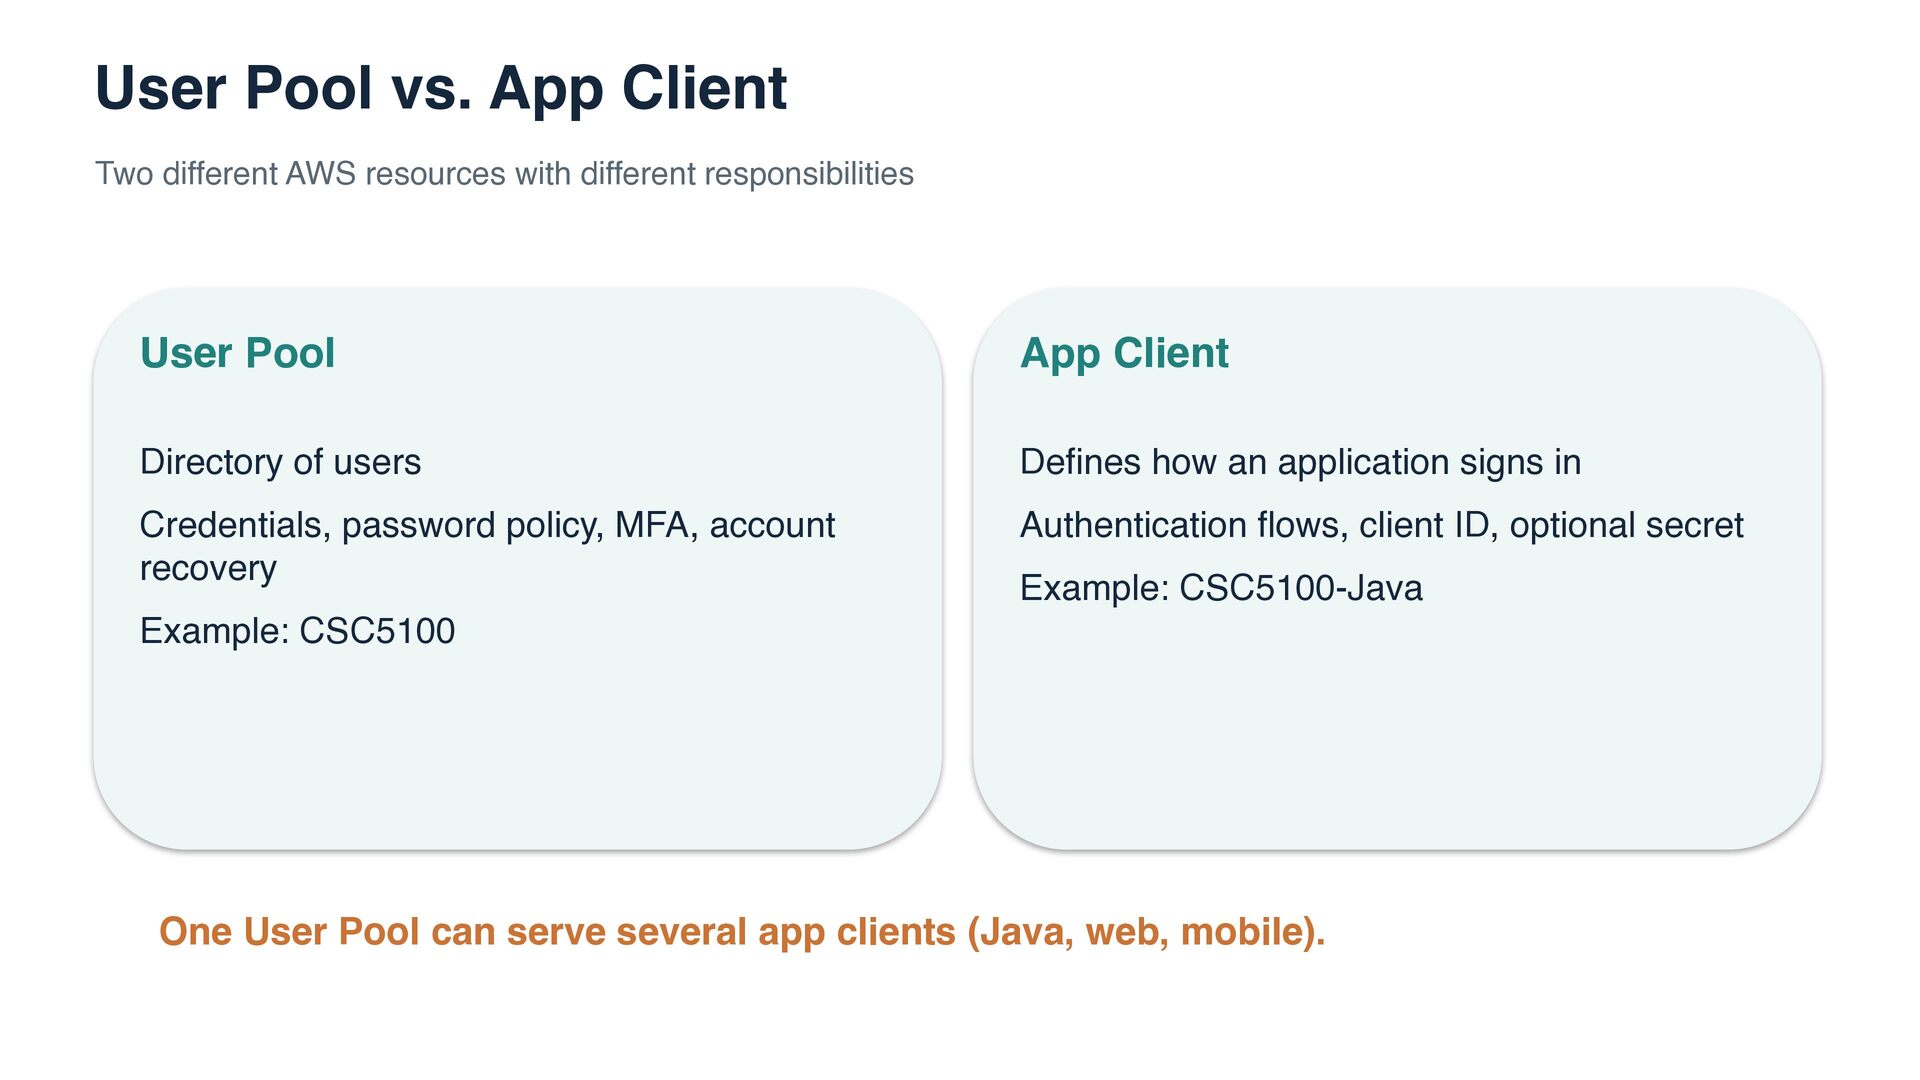
  11. User Pool vs. App Client Two different AWS resources with

    different responsibilities User Pool App Client Directory of users Defines how an application signs in Credentials, password policy, MFA, account recovery Authentication flows, client ID, optional secret Example: CSC5100-Java Example: CSC5100 One User Pool can serve several app clients (Java, web, mobile).
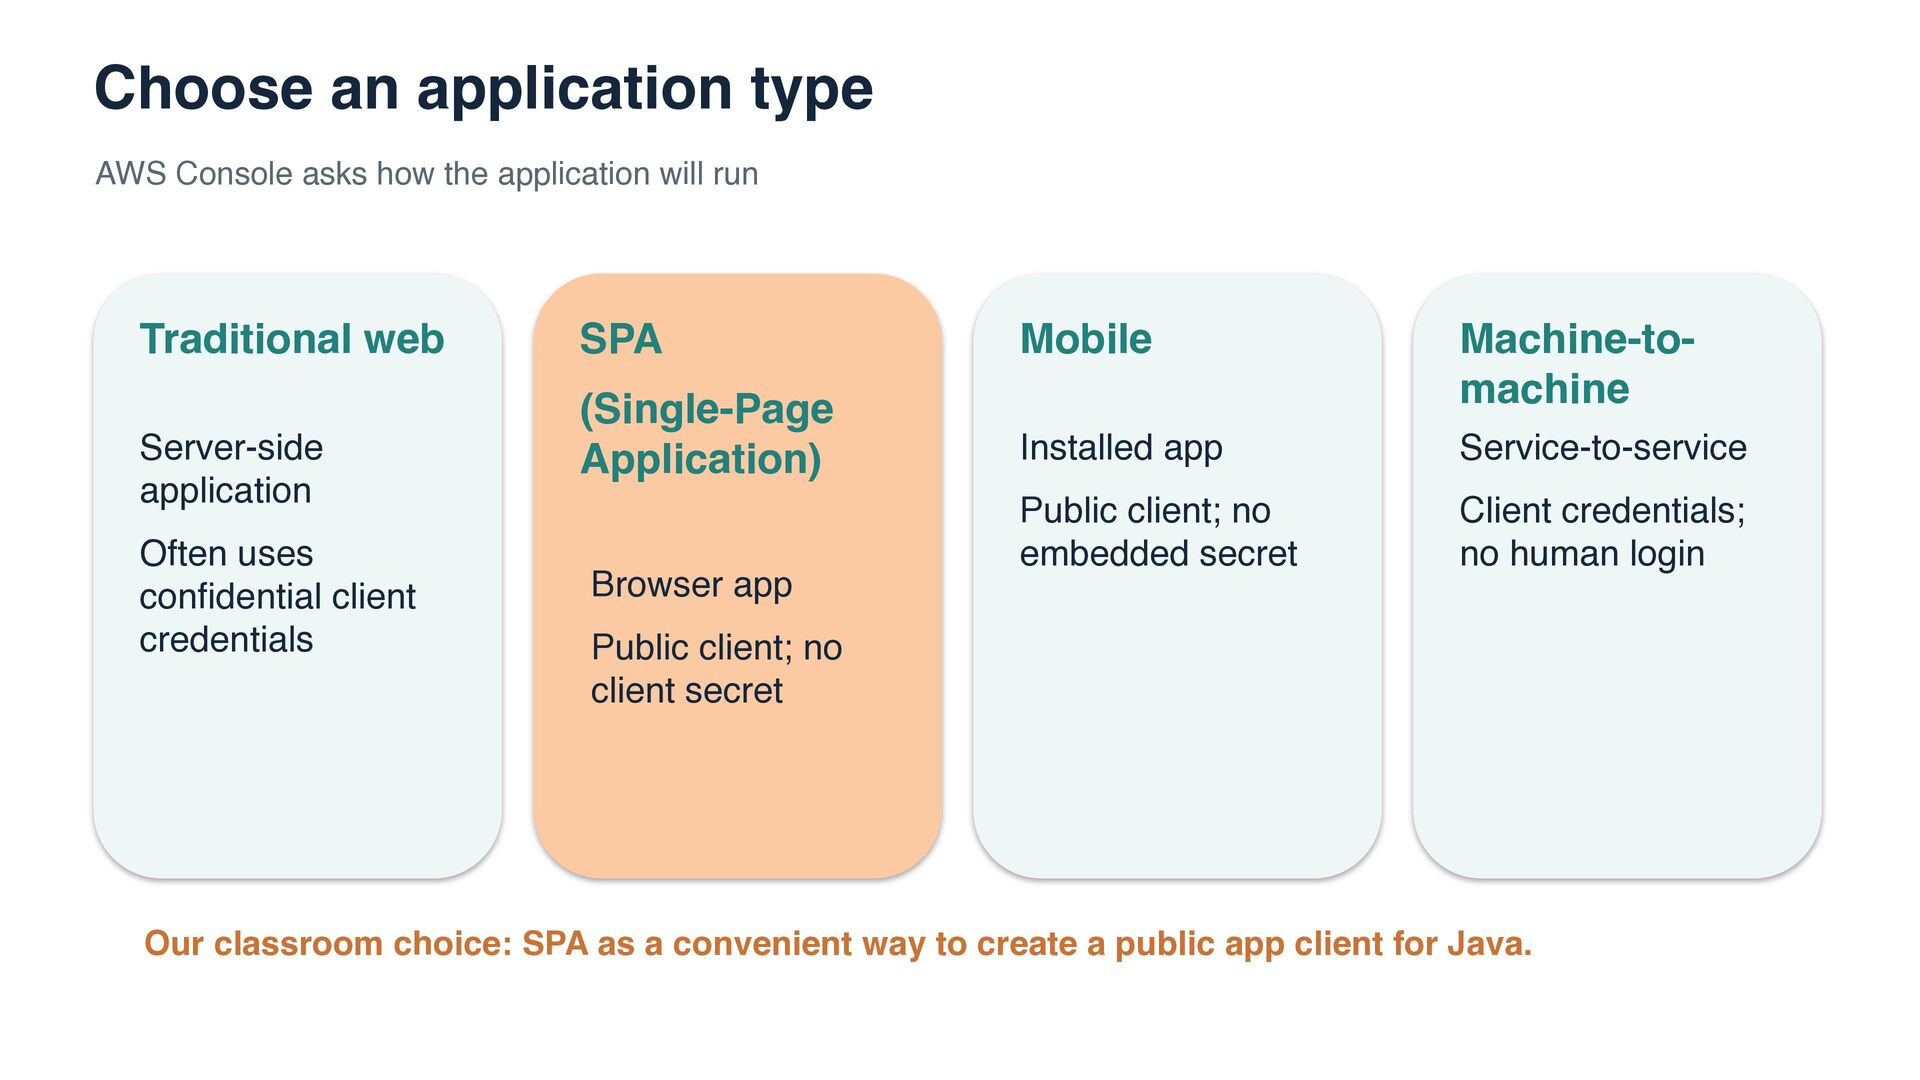
  12. Choose an application type AWS Console asks how the application

    will run Traditional web Server-side application Often uses confidential client credentials SPA Mobile (Single-Page Application) Machine-tomachine Installed app Service-to-service Public client; no embedded secret Client credentials; no human login Browser app Public client; no client secret Our classroom choice: SPA as a convenient way to create a public app client for Java.
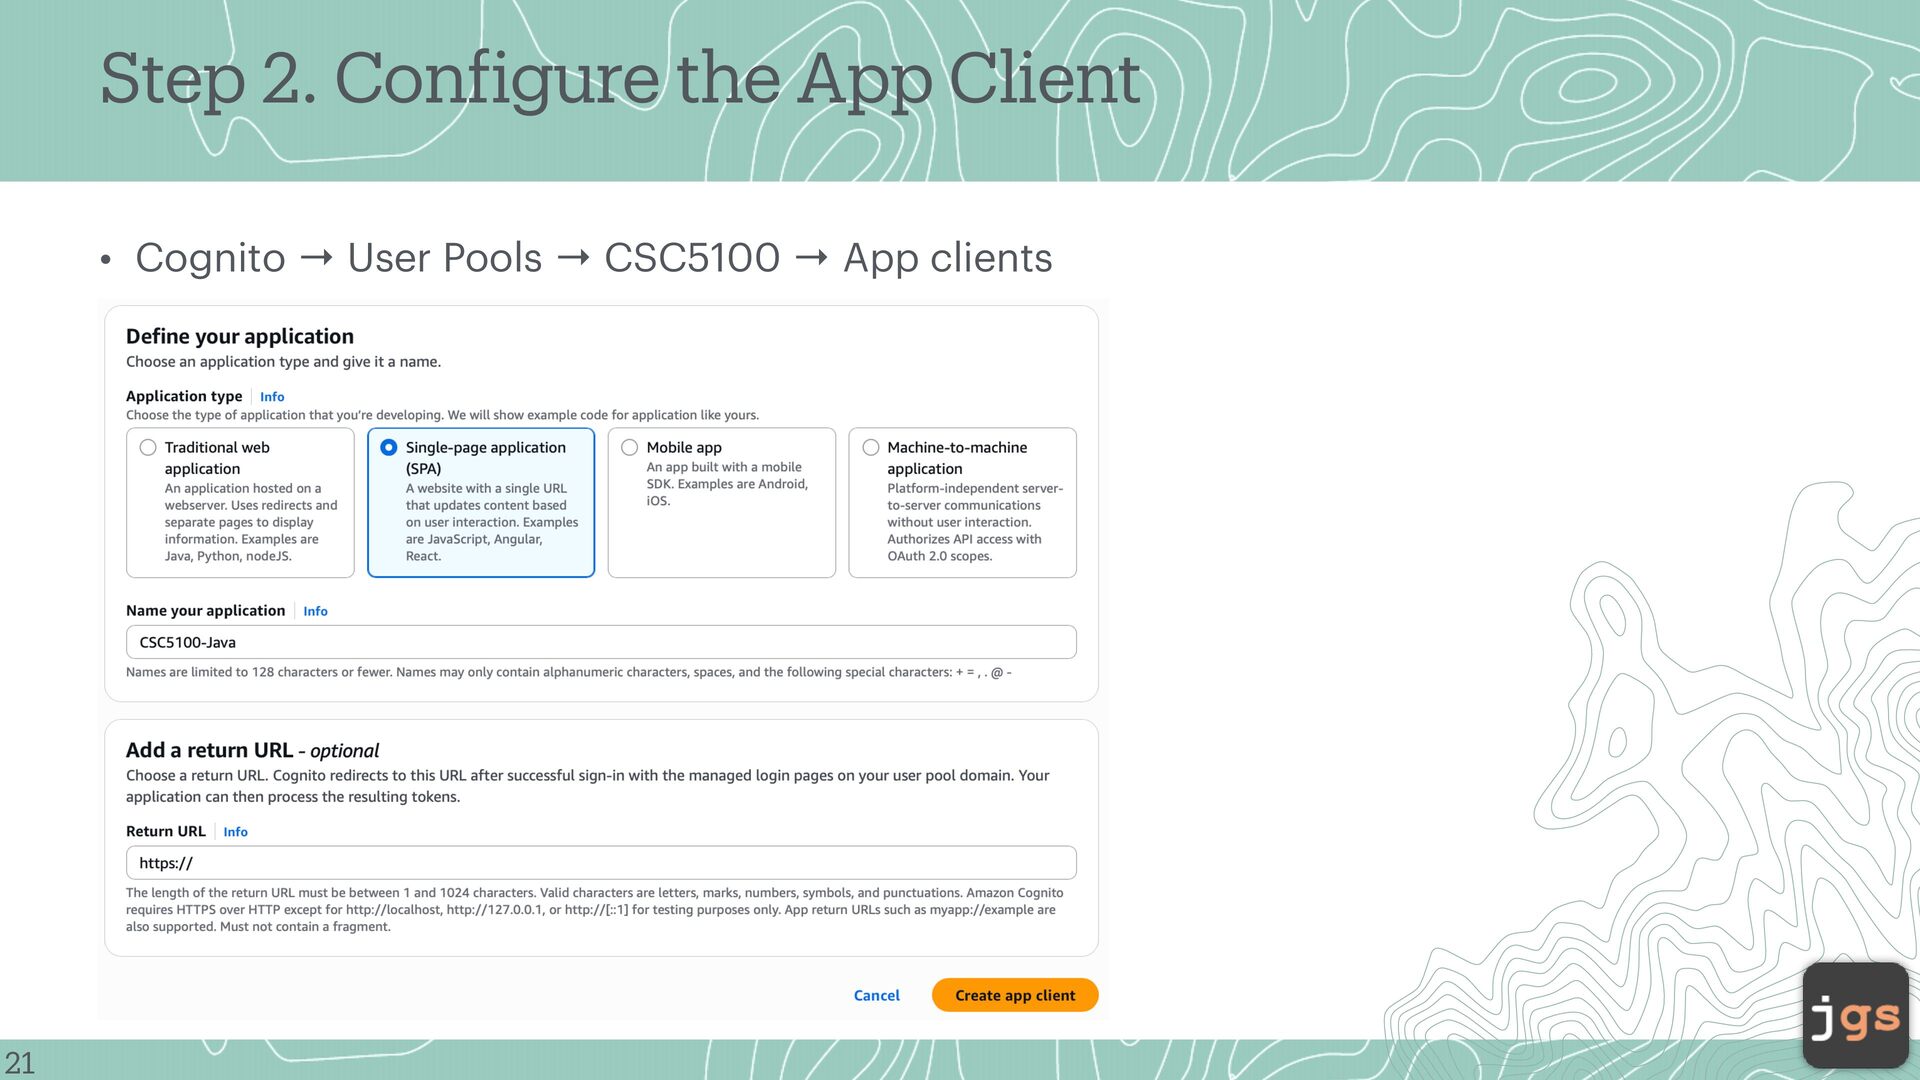
  13. Step 2. Con igure the App Client 21 f •

    Cognito → User Pools → CSC5100 → App clients
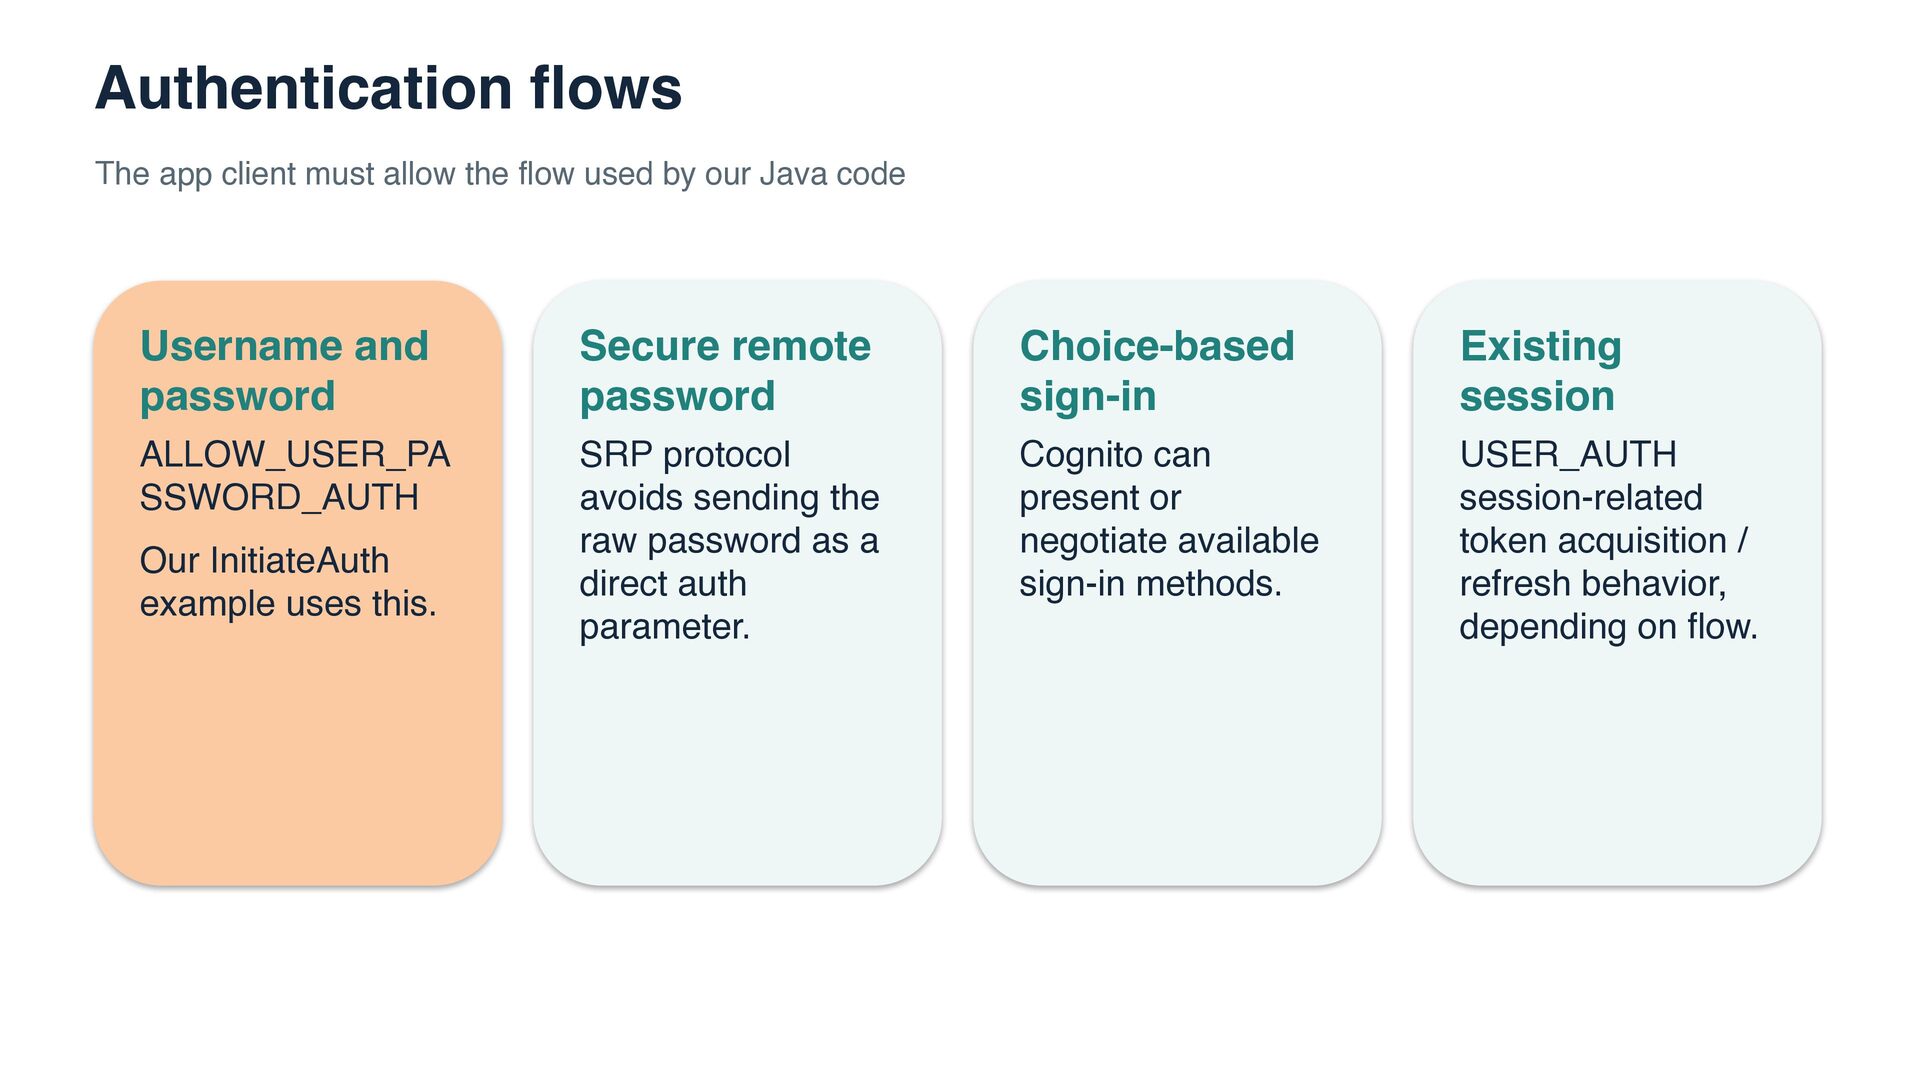
  14. Authentication flows The app client must allow the flow used

    by our Java code Username and password Secure remote password Choice-based sign-in Existing session ALLOW_USER_PA SSWORD_AUTH SRP protocol avoids sending the raw password as a direct auth parameter. Cognito can present or negotiate available sign-in methods. USER_AUTH session-related token acquisition / refresh behavior, depending on flow. Our InitiateAuth example uses this.
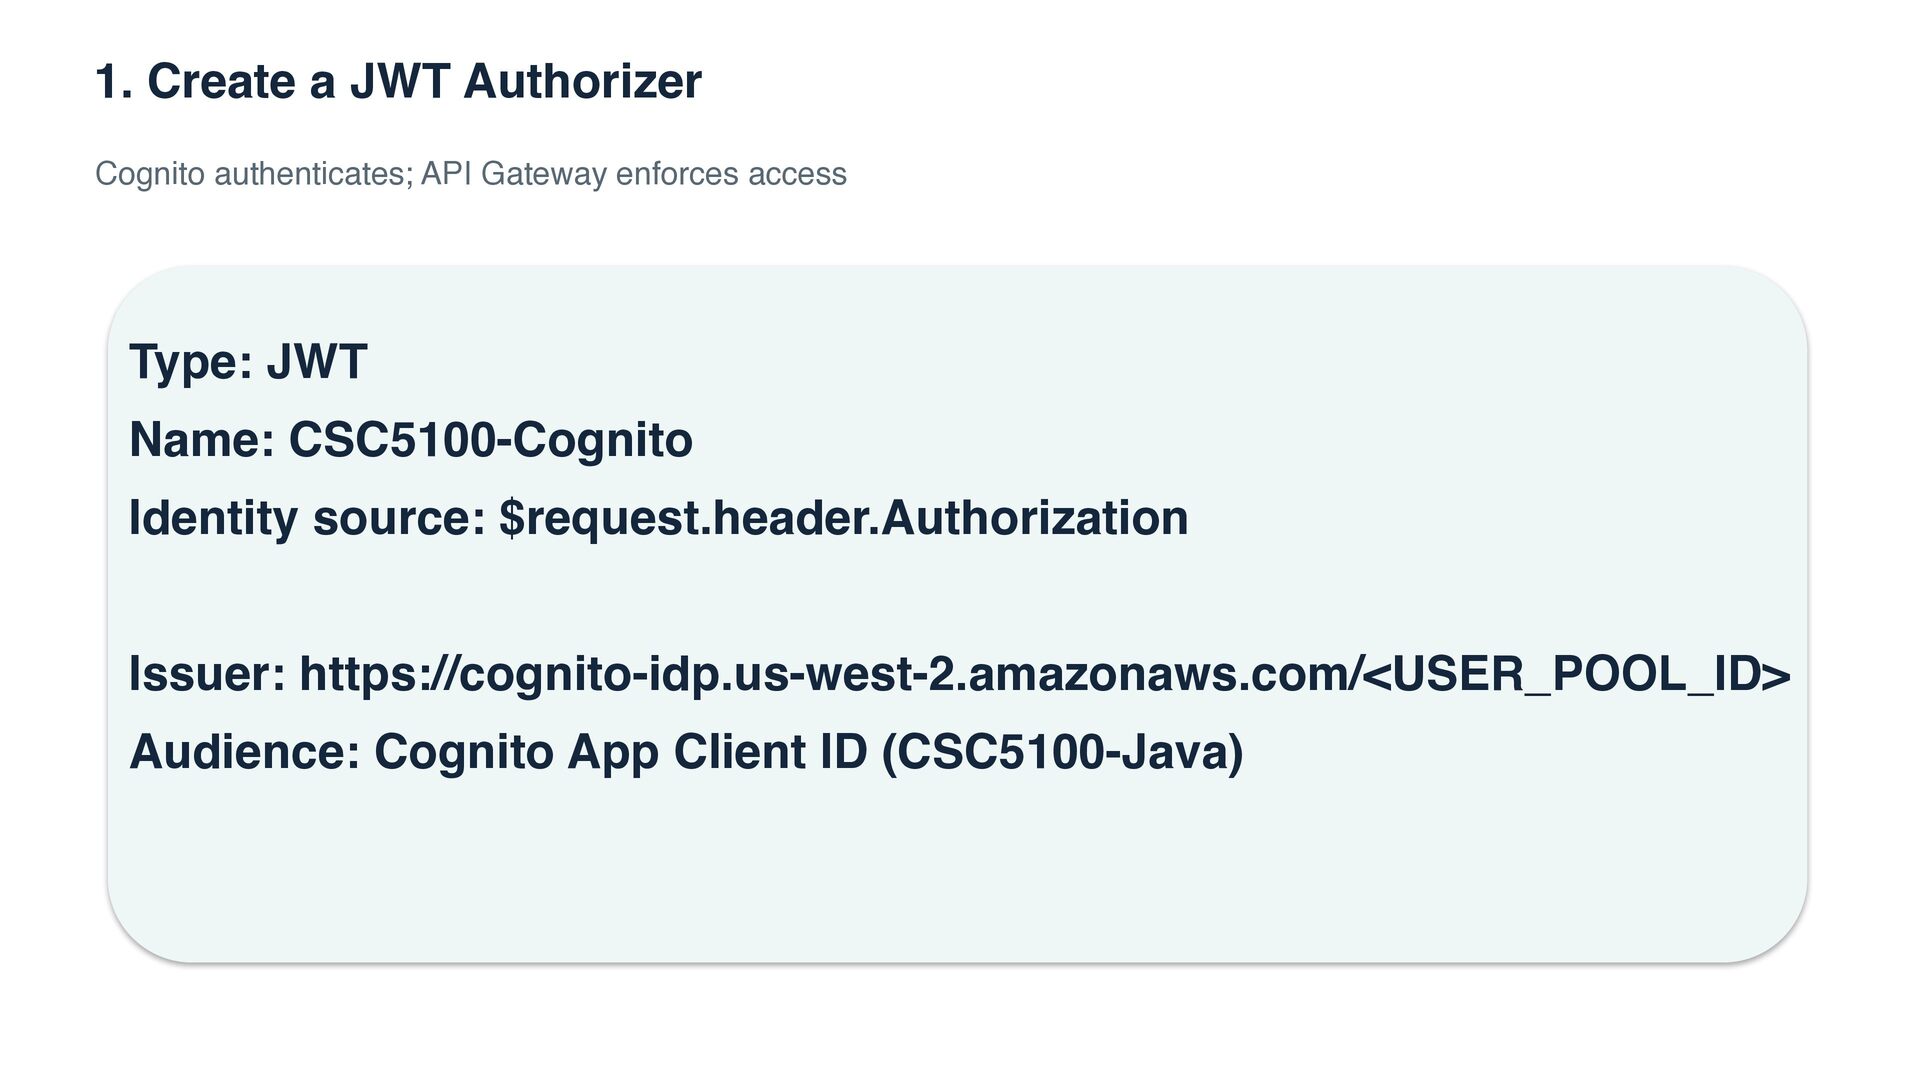
  15. 1. Create a JWT Authorizer Cognito authenticates; API Gateway enforces

    access Type: JWT Name: CSC5100-Cognito Identity source: $request.header.Authorization Issuer: https://cognito-idp.us-west-2.amazonaws.com/<USER_POOL_ID> Audience: Cognito App Client ID (CSC5100-Java)
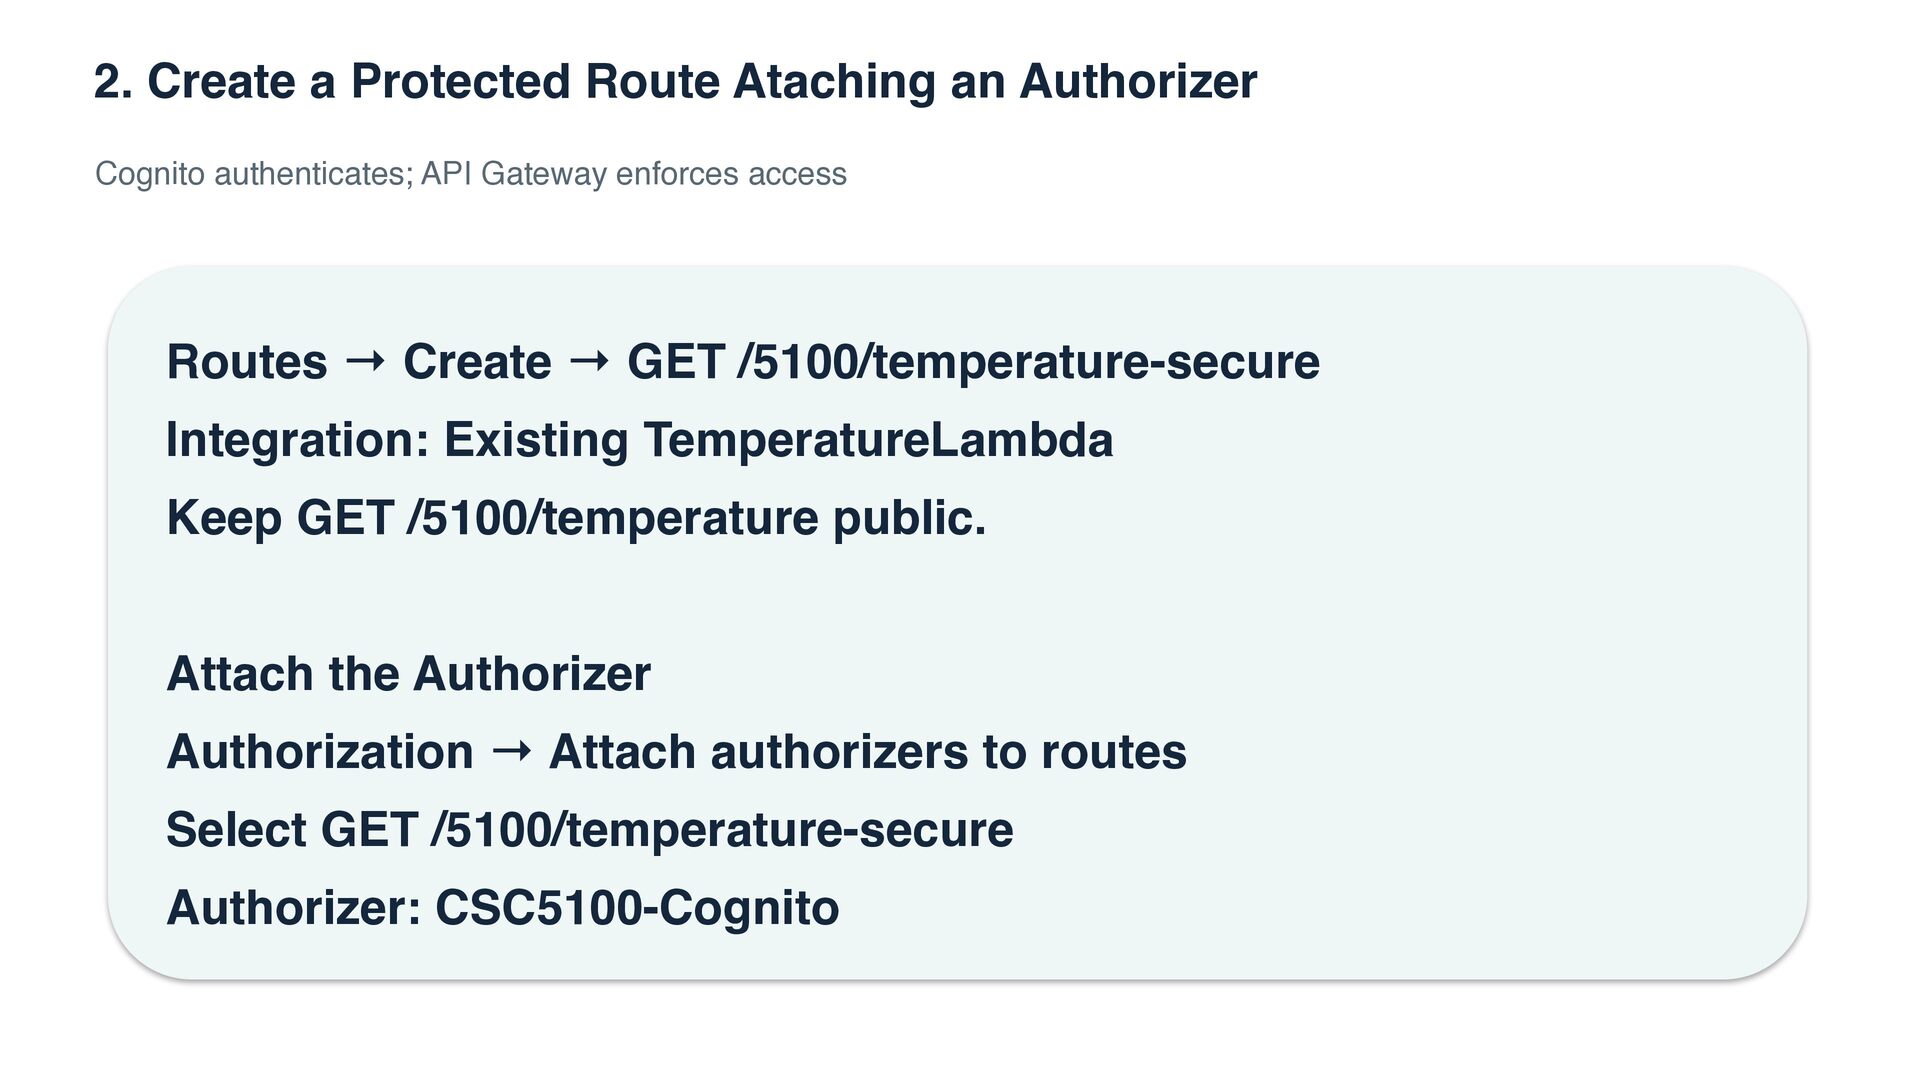
  16. 2. Create a Protected Route Ataching an Authorizer Cognito authenticates;

    API Gateway enforces access Routes → Create → GET /5100/temperature-secure Integration: Existing TemperatureLambda Keep GET /5100/temperature public. Attach the Authorizer Authorization → Attach authorizers to routes Select GET /5100/temperature-secure Authorizer: CSC5100-Cognito
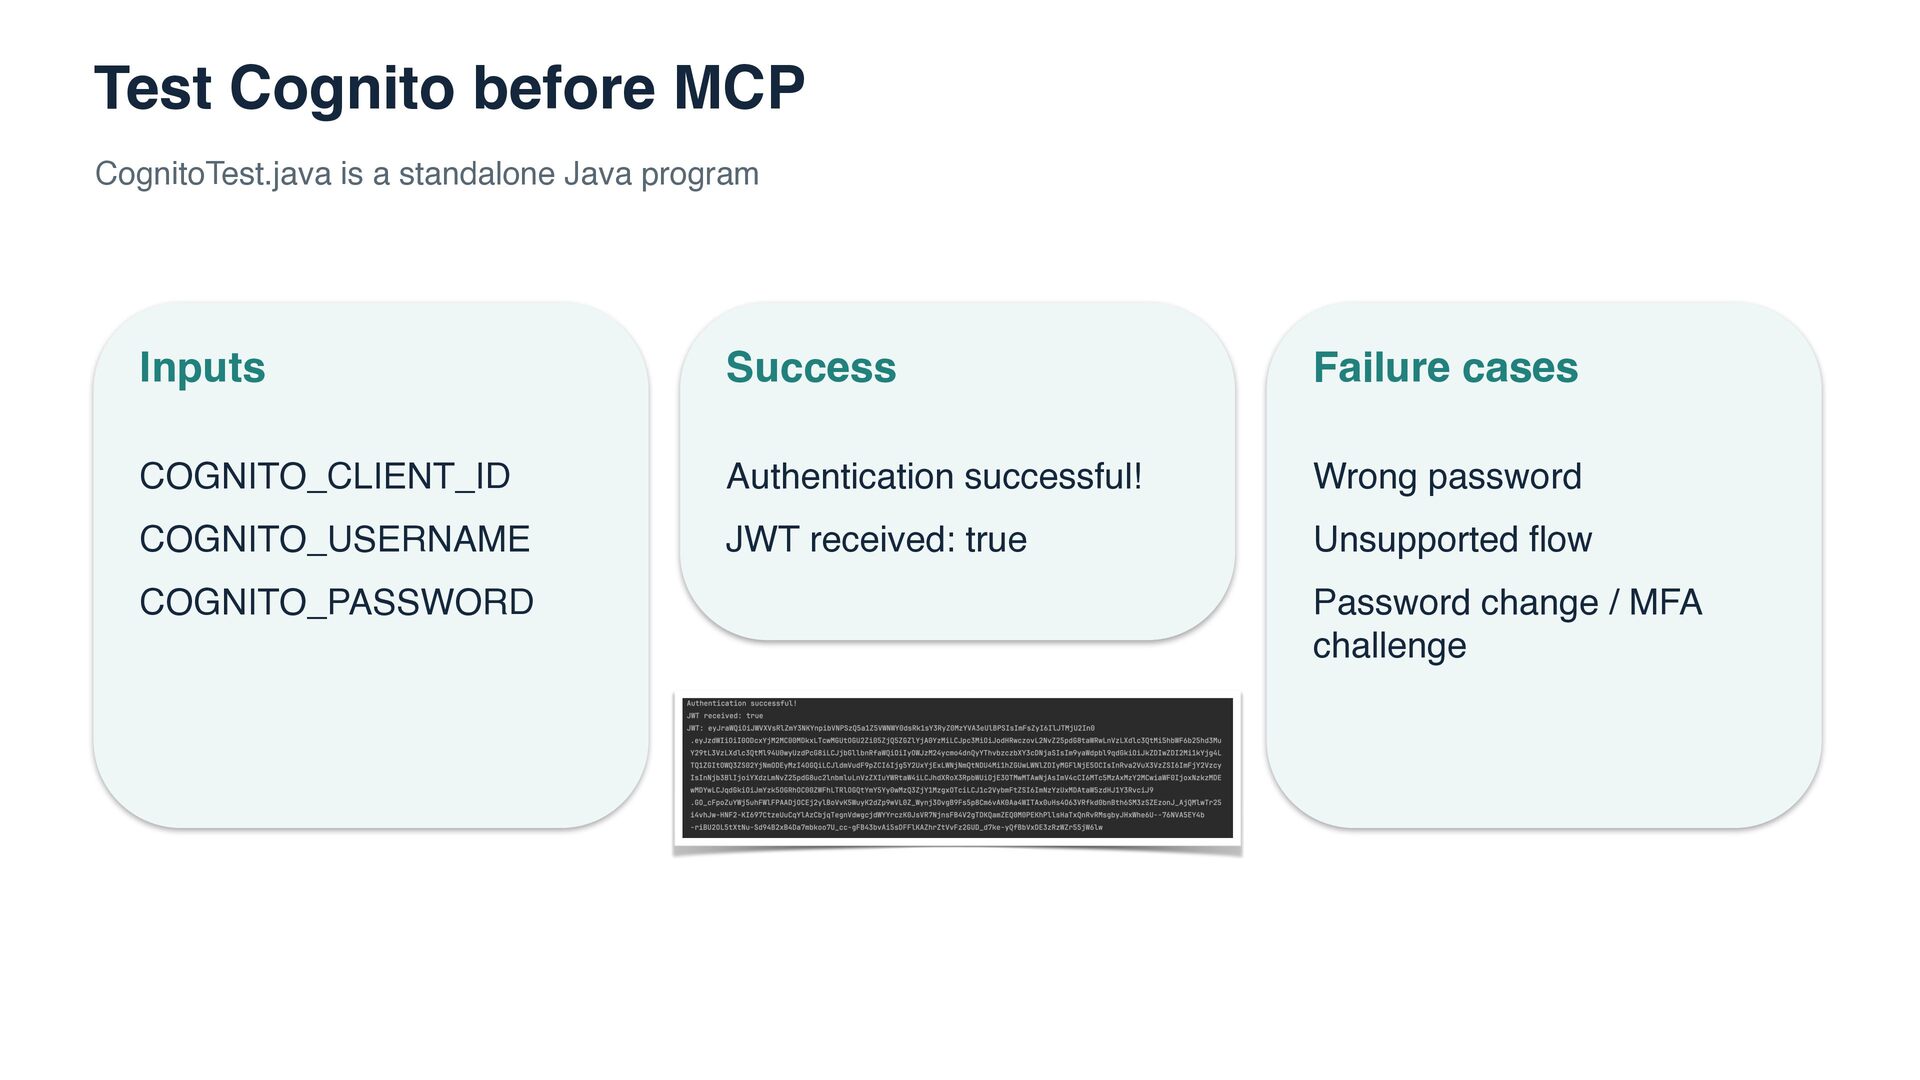
  17. Test Cognito before MCP CognitoTest.java is a standalone Java program

    Inputs Success Failure cases COGNITO_CLIENT_ID Authentication successful! Wrong password COGNITO_USERNAME JWT received: true Unsupported flow COGNITO_PASSWORD Password change / MFA challenge
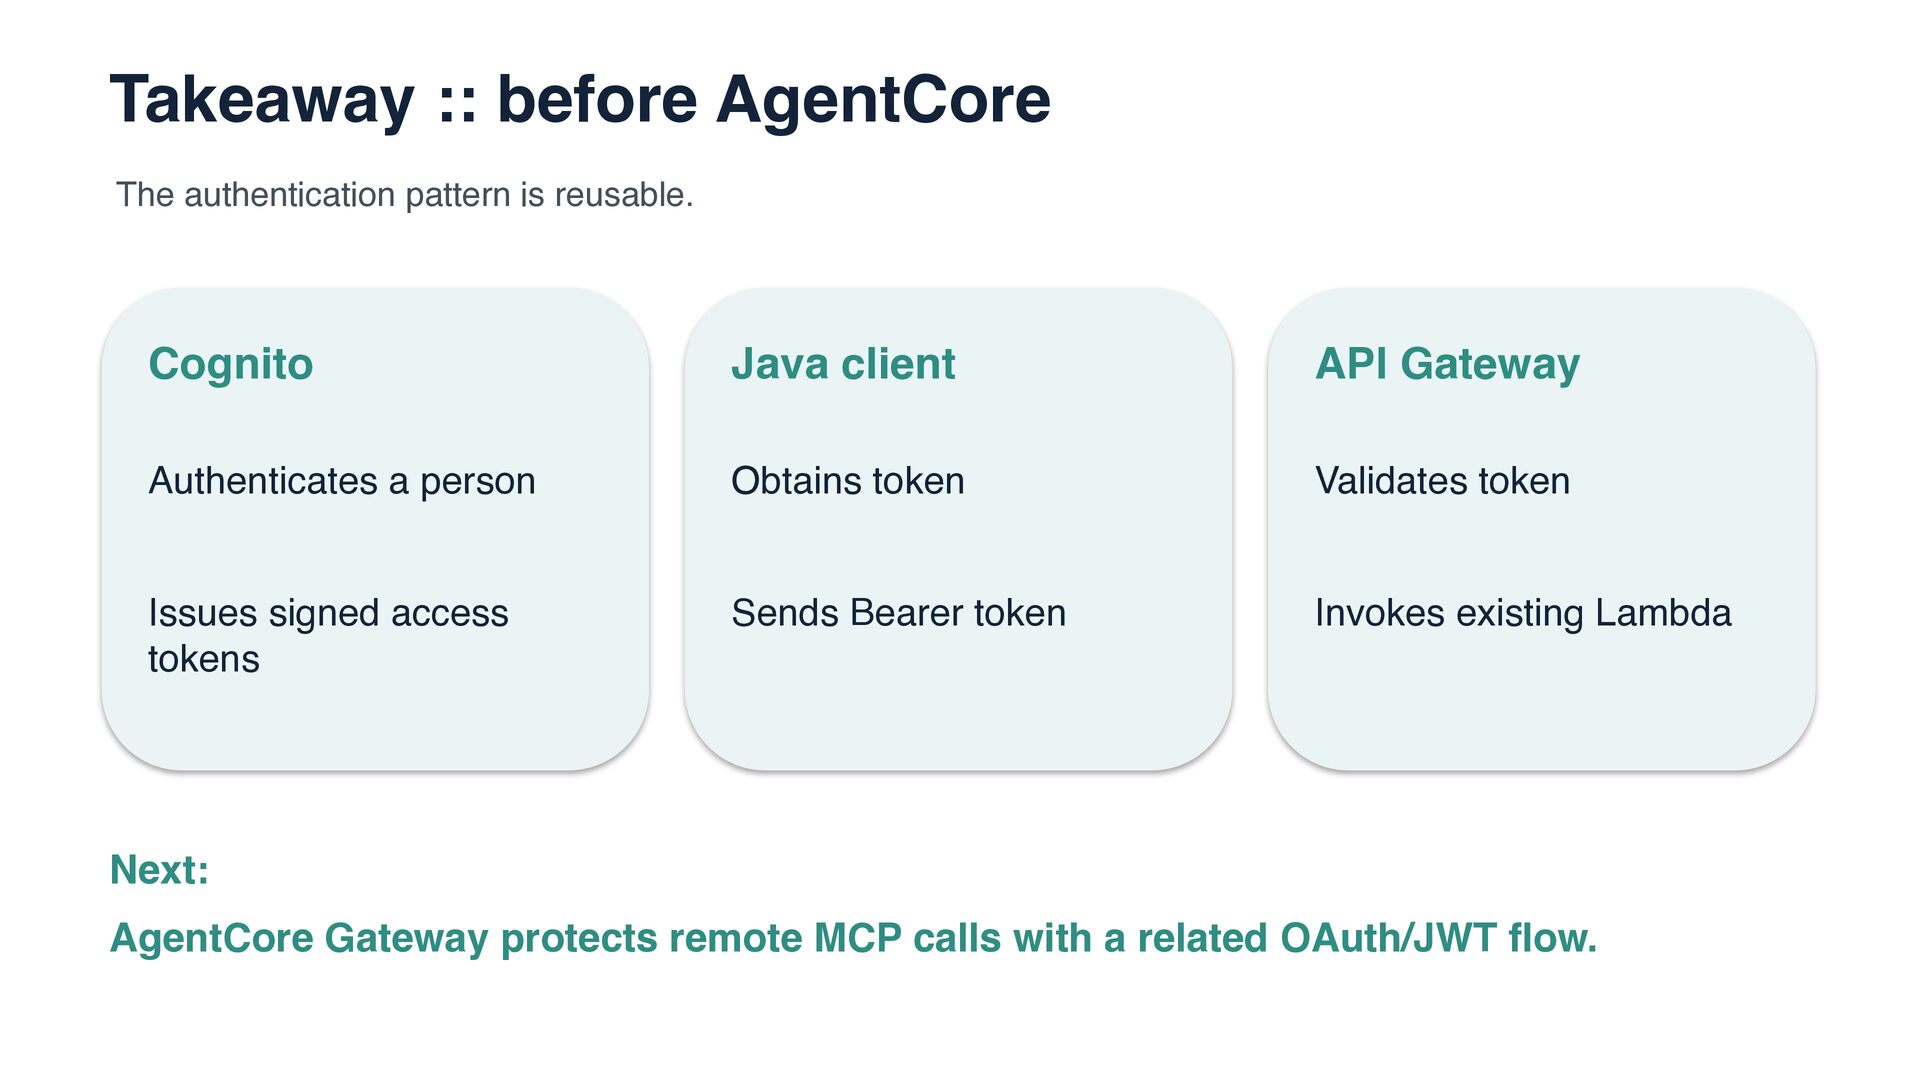
  18. Takeaway :: before AgentCore The authentication pattern is reusable. Cognito

    Java client API Gateway Authenticates a person Obtains token Validates token Issues signed access tokens Sends Bearer token Invokes existing Lambda Next: AgentCore Gateway protects remote MCP calls with a related OAuth/JWT flow.
  19. CSC 5100 Modern Software Engineering Javier Gonzalez-Sanchez, Ph.D. [email protected] Fall

    2026 Copyright. These slides may be used only as study material for CSC 5100 within the California State University system. They may not be distributed or used for any other purpose.