Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
The Most Dangerous Game
Search
Scott J. Roberts
February 03, 2015
Technology
5.4k
5
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
The Most Dangerous Game
A presentation about merging Threat Intelligence and DFIR by the team behind YoloThre.at.
Scott J. Roberts
February 03, 2015
More Decks by Scott J. Roberts
See All by Scott J. Roberts
LLM SATs FTW
sroberts
0
1.8k
STRAT - A System-Centric Approach to Cyber Resilience
sroberts
0
120
Tortured Responders Dept - Scott & Rebekah's Edition
sroberts
0
200
Skynet the CTI Intern: Building Effective Machine Augmented Intelligence
sroberts
0
230
DRIVING INTELLIGENCE WITH MITRE ATT&CK: LEVERAGING LIMITED RESOURCES TO BUILD AN EVOLVING THREAT REPOSITORY
sroberts
0
170
Exploring Threat Intelligence: Insights and Tools from Vertex Synapse
sroberts
0
170
Homemade Ramen & Threat Intelligence
sroberts
2
670
Introduction to Open Source Security Tools
sroberts
3
5.1k
Building Effective Threat Intelligence Sharing
sroberts
1
170
Other Decks in Technology
See All in Technology
reInvent2026stby LT00 "Change your life!"
shinichirokawano
1
530
Deep Data Security 機能解説
oracle4engineer
PRO
3
990
デザインレビューは自動化できるのか?─ Flutter × Figma で UI 品質保証を考える
techiro
2
720
素人でもできた!AIを使った短編小説創作入門
delhi09
PRO
0
280
自律的なチームを作るためにTechPMがやらないこと
ny7760
0
450
攻撃 3 時間 vs 復旧 10 時間。アクセスキー流出の非対称性を体感するために CTF を作った話
kazzpapa3
1
130
Claude Codeから見る、エンジニアの世界の変容とその先
oikon48
8
5.1k
AI時代、つくる力を自分たちの手に。 ──電通×KAG、アジャイルとAI駆動開発で挑む開発の変革
yuukiyo
3
450
AIがGISを代替する日:〜すべてをAIが創る時代に、私たちがFOSS4Gに関わる意味〜
lehupa
0
190
Patterns in AI Driven Software Development
akosma
PRO
0
430
[re:Invent2026事前勉強会(有志開催)]続きは、ラスベガスの廊下で / continue-in-the-vegas-hallway
sh_fk2
0
480
新卒エンジニア、 介護士になる
ryu1013
1
660
Featured
See All Featured
Let's Do A Bunch of Simple Stuff to Make Websites Faster
chriscoyier
508
140k
Are puppies a ranking factor?
jonoalderson
2
4.1k
How STYLIGHT went responsive
nonsquared
100
6.3k
Into the Great Unknown - MozCon
thekraken
41
2.8k
The State of eCommerce SEO: How to Win in Today's Products SERPs - #SEOweek
aleyda
2
12k
Abbi's Birthday
coloredviolet
4
11k
Design and Strategy: How to Deal with People Who Don’t "Get" Design
morganepeng
133
20k
For a Future-Friendly Web
brad_frost
184
11k
Evolution of real-time – Irina Nazarova, EuRuKo, 2024
irinanazarova
9
1.6k
Code Review Best Practice
trishagee
74
20k
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
520
16th Malabo Montpellier Forum Presentation
akademiya2063
PRO
0
440
Transcript
The Most Dangerous Game Hunting Adversaries Across the Internet
Kyle Maxwell Super Special Security Researcher @ iDefense
Scott J Roberts Advanced Persistent Incident Responder @ GitHub
How Kyle met Scott or How Scott met Kyle
If you are on the Twitter we’re @kylemaxwell & @sroberts
#YOLOTHREAT
Intelligence Concepts That everyone knows and already agrees on right…?
Data vs Intelligence Intelligence has gone through the intelligence process
Data is a raw piece of information without context
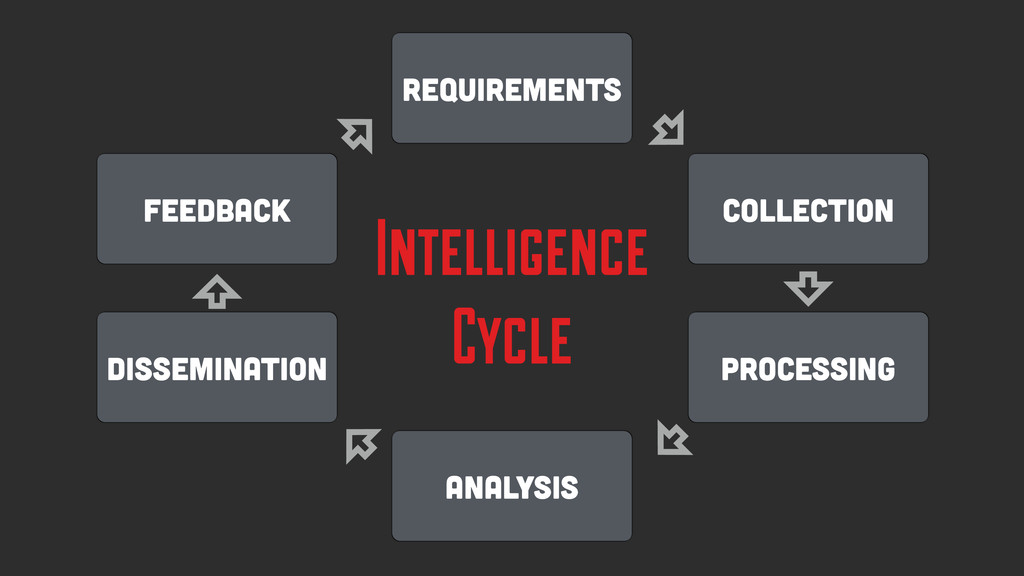
Feedback Analysis Processing Dissemination Collection Requirements Intelligence Cycle
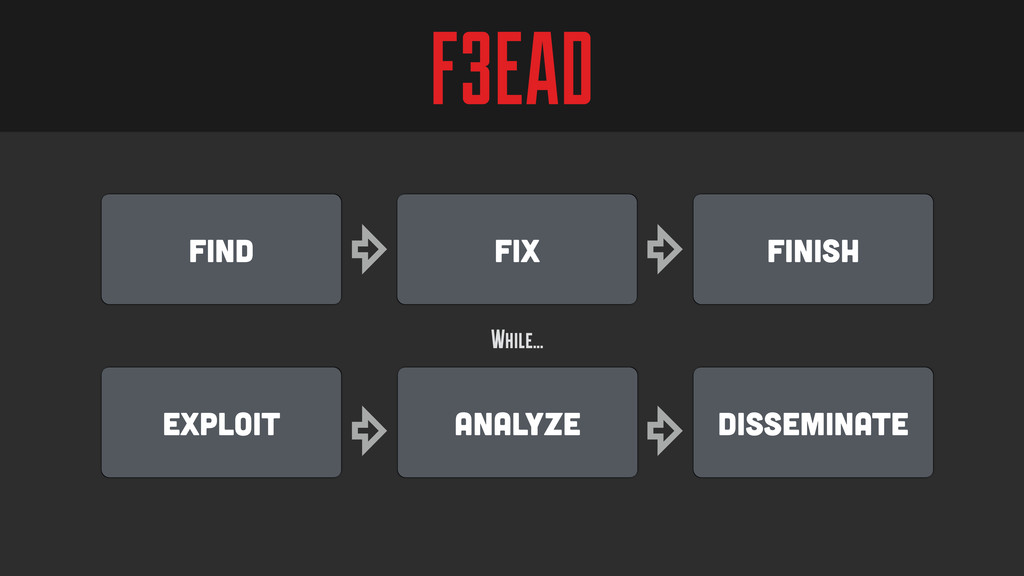
F3EAD While… Find Exploit Finish Disseminate Fix Analyze
The Target
What is Targeting? Making a plan for focusing threat research
& investigation
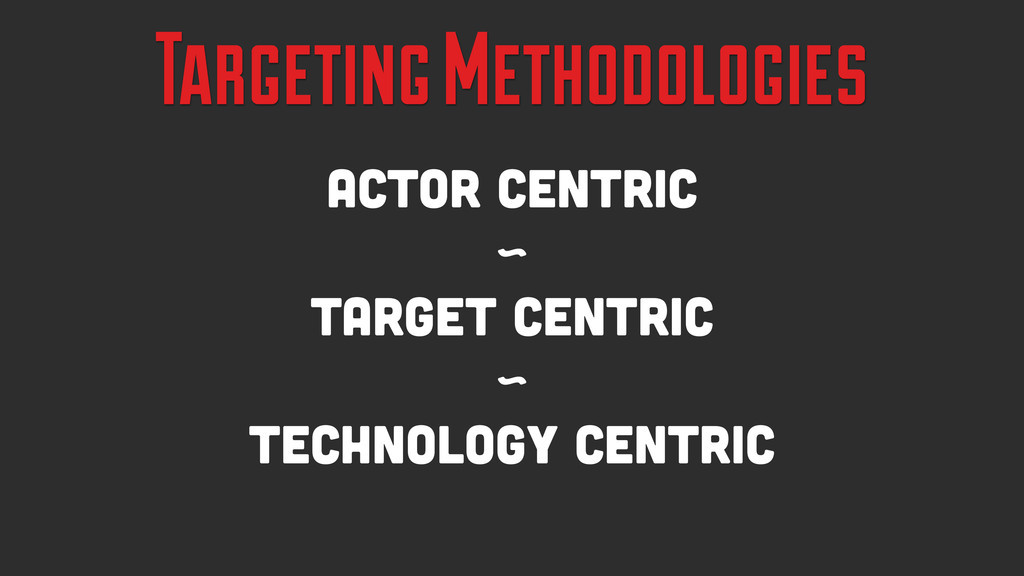
Targeting Methodologies Actor Centric ~ Target Centric ~ Technology centric
Feeds Needles in Haystacks
“My 5.4 gazillion indicators can beat up your threat indicators.
Garbage in garbage out #ThreatIntel ~ Rick Holland
Honeypots Bringing the Bad Guys to You
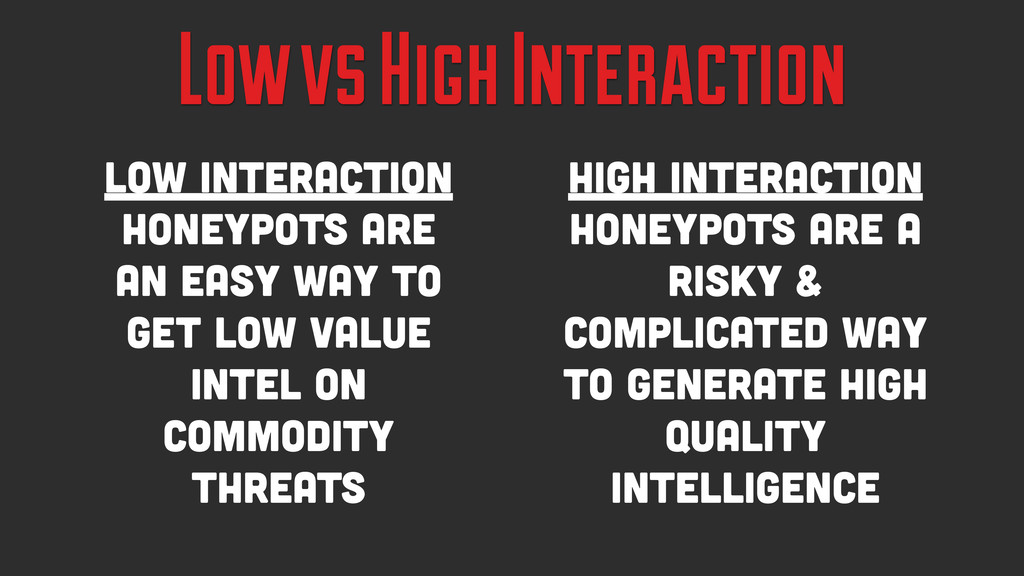
Low vs High Interaction High interaction honeypots are a risky
& complicated way to generate high quality intelligence Low interaction honeypots are an easy way to get low value intel on commodity threats
Software Old School: HoneyNet Project New Hotness: Modern Honey Network
by Threat Stream
Vulnerability Information Taking care of your Toys
“Structured vulnerability analysis is not threat intelligence it is requirements
gathering for threat intelligence. ~ @selil
Vendor Information Blogs ~ Reports ~ Services & APIs
Personal Aside to Vendors If you’re going to release a
report, blog post, etc: do not break the Cut and Copy Actions
None
Review Your Own Incidents Mine that fancy Incident Management System…
Review Your Others Incidents By sharing or News mining
The Hunt
What to Analyze Technical Sources
What to Analyze: Hashes Reversing: • C2 info • Developer
artifacts Sources: • VxShare • VirusTotal • malwr.com
What to Analyze: Passive DNS • Single most useful tool
for infrastructure research • What resolved to what, and when? • DNSDB (Farsight), PassiveTotal, VirusTotal
What to Analyze: Whois • Tougher to Acquire • WhoDat
etc for ongoing Tracking
What to Analyze Actors
What to Analyze: Criminal • Primary Weapon: Google • Social
Media (Twitter, Facebook) • Underground forums?
What to Analyze: Espionage • This is hard • Malware
& System artifacts • whois/registrar data • actions over target
How to Keep Tracking
Threat Library • CRITs is popular, MISP also • Lighter
solutions often work • Market hasn't fully addressed this
Web Monitoring Systems • Netflix Scumblr Meta SearcH (Works alongside
Sketchy) • Recorded Future • Lots of custom development
Malware Monitoring • VirusTotal is • Malware feeds with Lots
of custom internal solutions • Maltrieve, Viper, & Cuckoo
Internal Logging • Firewall, IDS, & Proxy • Web, mail,
& DNS • Authentication & Audit
The “Kill”
Incident Response The Entire Goal… Right?
The Imitation Game Don’t let them know that you know
that they know…
Attribution Probably doesn’t matter unless you can do this
Hand Cuffs or Cruise Missiles
KICK ‘EM OUT NOW! Sometimes it’s better to watch for
a while
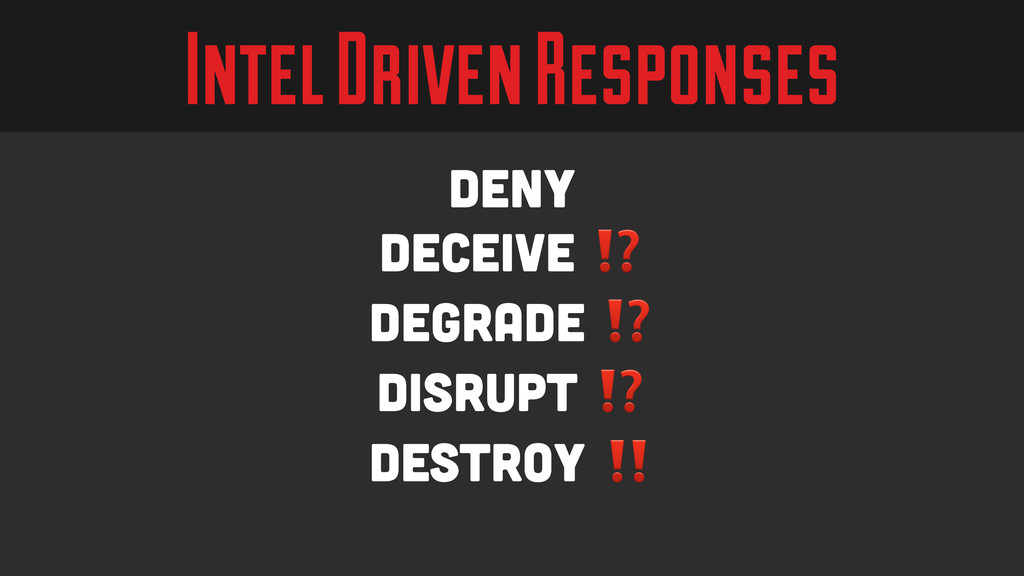
Intel Driven Responses deny Deceive ⁉️ degrade ⁉️ disrupt ⁉️
Destroy ‼️
Communication Who can make use of this information? ~ Who
might be able to provide additional intel?
The Hunting Stories
Products IOCs & RFIs ~ Short Form Products ~ Long
Form Products
Audience Internal - Team Internal - Organization External - Peers
External - Wide
IOCs - Generalized Stix & OpenIOC
“you pretty much need a PHD in XML to understand
either STIX or TAXII ~ Jeff Bryner
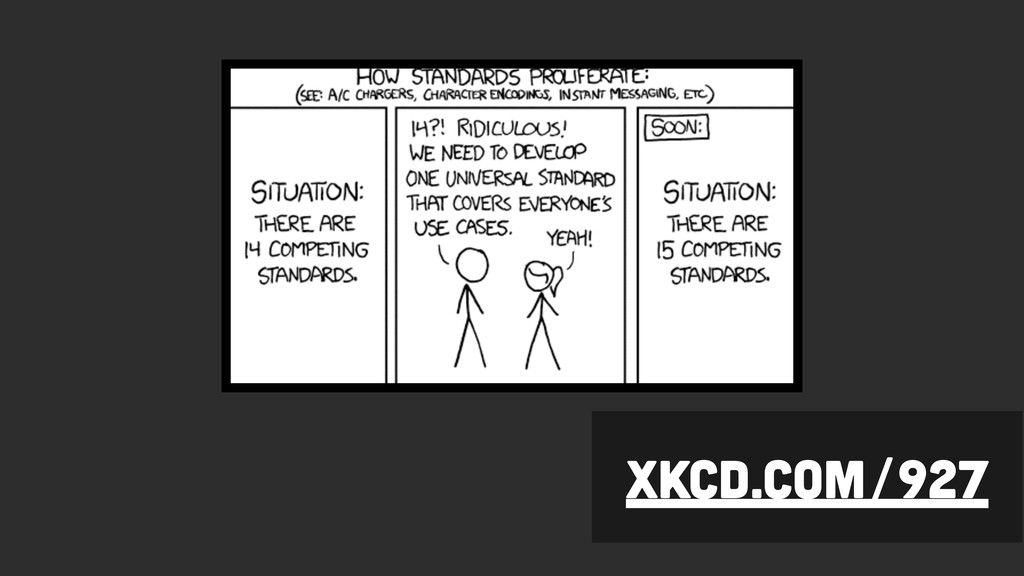
XKCD.com/927
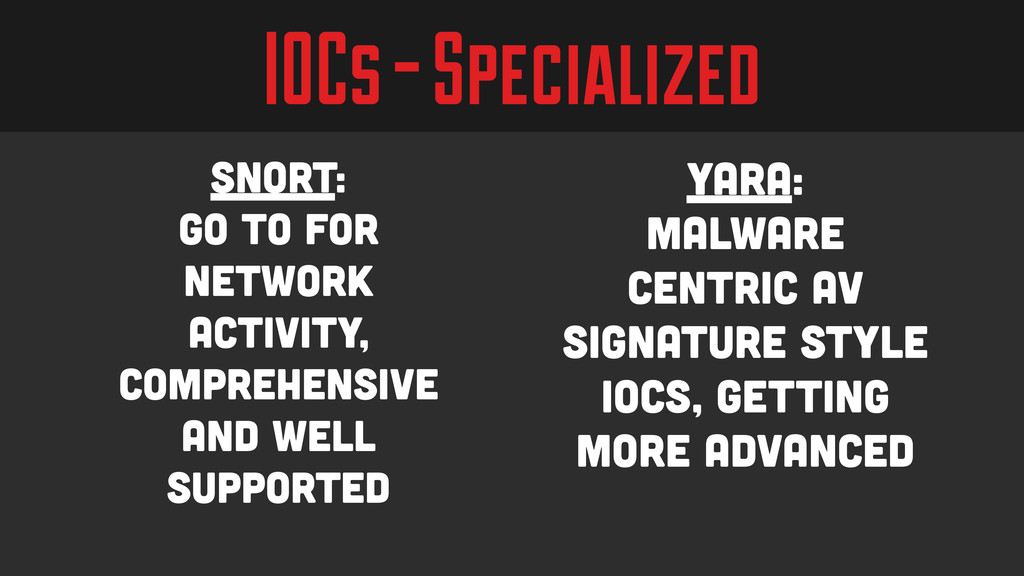
IOCs - Specialized Yara: Malware centric av signature style IOCs,
getting more advanced Snort: Go to for network activity, Comprehensive and well supported
“OH: "Yara is an antivirus that you update using git
pull" ~ @tomchop_
Requests For Intelligence A Q/A requesting very specific Intelligence ~
Shortest form Possible ~ Fastest turn around
Short Form Products Intermediate products to support incident response ~
Focus on actionable Information
Long Form Products Comprehensive “All Source” intelligence products ~ Requires
considerable Time & a well rounded team
The Surprise…
You Can’t Download a Threat Intelligence Until now….
The Surprise Coming out of Stealth Today, our new Startup…
YOLOTHRE.At
Announcement yolothre.at has run out of runway (We used up
our whole Starbucks Gift Card) SO we’re open sourcing everything and going back to our old jobs...
YoloThre.at A collection of open source docker containers for Threat
Intel
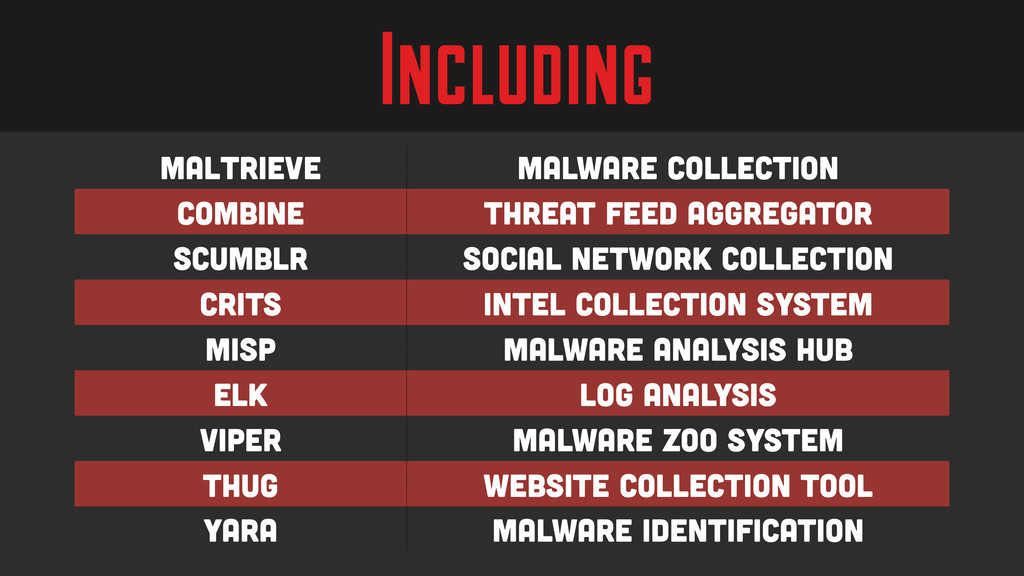
Including Maltrieve Malware Collection Combine Threat Feed Aggregator Scumblr Social
Network Collection CRITs Intel Collection System MISP Malware Analysis Hub ELK Log Analysis Viper Malware Zoo System Thug Website Collection Tool Yara Malware Identification
Review
Review The Target The Hunt The “Kill” The Hunting Stories
Questions?
Thanks
None


 sroberts
 shinichirokawano
 oracle4engineer
 techiro
 delhi09
 ny7760
 kazzpapa3
 oikon48
 yuukiyo
 lehupa
 akosma
 sh_fk2
 ryu1013
 chriscoyier
 jonoalderson
 nonsquared
 thekraken
 aleyda
 coloredviolet
 morganepeng
 brad_frost
 irinanazarova
 trishagee
 techseoconnect
 akademiya2063