Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Bitcoin Ops & Security Primer
Search
Russell Smith
April 07, 2014
Technology
190
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Bitcoin Ops & Security Primer
Russell Smith
April 07, 2014
More Decks by Russell Smith
See All by Russell Smith
Ops Skills and Tools for Beginners [MongoDB World 2014]
ukd1
0
150
3 Infrastructure + workflow lessons from an early stage startup
ukd1
0
140
Gearman & Kohana
ukd1
2
1k
Geo & capped collections with MongoDB
ukd1
1
170
Cassandra London UG July 2011 - Riak vs Cassandra
ukd1
1
340
MongoDB - Map Reduce
ukd1
2
270
MongoDB London UG, April 2011 - MongoDB Introduction
ukd1
1
140
MongoDB London 2011 - MongoDB Command Line Tools
ukd1
1
220
Seedhack 2011 - Introducing MongoDB
ukd1
1
160
Other Decks in Technology
See All in Technology
Benchmarking Disaggregated Serving on vLLM + Dynamo with a Real Coding-Agent Workload
nttcom
1
210
Code for Security プロジェクト紹介 2026年10月
yu23ki14
0
120
フロントエンドカンファレンス関西2026 - 速すぎるUIに、待ち時間を
teamlab
PRO
0
210
『SAR衛星データ解析入門』の ご紹介とその応用
syuchimu
0
130
野蛮なアジャイル [サイボウズ発!]組織の常識を覆した反骨のスクラム実践記 / Barbaric Agile - Enterprise Agile Study Group
ama_ch
0
120
Persisting Massive Data with Rails ~Designing for 60 billion rows, and fighting the bottlenecks~ Railsで挑む大量データ永続化 〜600億件を永続化するための設計とボトルネックとの戦い〜
occhi
0
750
Rustuna: Rustによる高速なOptuna実装
pfn
PRO
0
200
「エーアイ」をバズワードにしないために RPA 導入経験と Kiro 上での Claude モデル利用経験から
kazzpapa3
0
100
sue445's proposals 2026
sue445
0
120
トークン化預金DCJPYの取り組みと活用ユースケース
finengine
0
200
Refining Active Record
shugo
0
180
React改造してみた
tsukina_7mochi
0
140
Featured
See All Featured
Imperfection Machines: The Place of Print at Facebook
scottboms
270
14k
Ten Tips & Tricks for a 🌱 transition
stuffmc
1
270
B2B Lead Gen: Tactics, Traps & Triumph
marketingsoph
1
280
Thoughts on Productivity
jonyablonski
76
5.4k
Fashionably flexible responsive web design (full day workshop)
malarkey
409
67k
Code Review Best Practice
trishagee
74
20k
30 Presentation Tips
portentint
PRO
1
430
Redefining SEO in the New Era of Traffic Generation
szymonslowik
1
480
Primal Persuasion: How to Engage the Brain for Learning That Lasts
tmiket
0
500
StorybookのUI Testing Handbookを読んだ
zakiyama
31
7k
Tell your own story through comics
letsgokoyo
1
1.1k
Leadership Guide Workshop - DevTernity 2021
reverentgeek
1
400
Transcript
rainforest @rainforestqa Bitcoin + Ops Primer:! Understand your risk Manage
attacks
@rainforestqa rainforest Rainforest Human powered QA SaaS Designed for ‘Continuous
QA’ Built for PMs and Developers
@rainforestqa rainforest Us Team of 6 in SoMa All developers
YC S12
@rainforestqa rainforest Understanding risk
rainforest @rainforestqa Understand the trade off More secure generally means
more effort
@rainforestqa rainforest Risk vs Exposure
@rainforestqa rainforest High Risks Hot wallets / key storage Outgoing
payments Physically shipped items Reversible payments (e.g. chargebacks)
@rainforestqa rainforest …more risks Shared hosting / VPS / “physical”
security Staff
@rainforestqa rainforest Limiting Exposure Storing keys Hot wallets -> Cold
wallets, where poss Principle of least privilege
@rainforestqa rainforest What risks?
rainforest @rainforestqa Internet connected = hackable (Though, the NSA can
spy on you, even if you're not connected to the Internet)
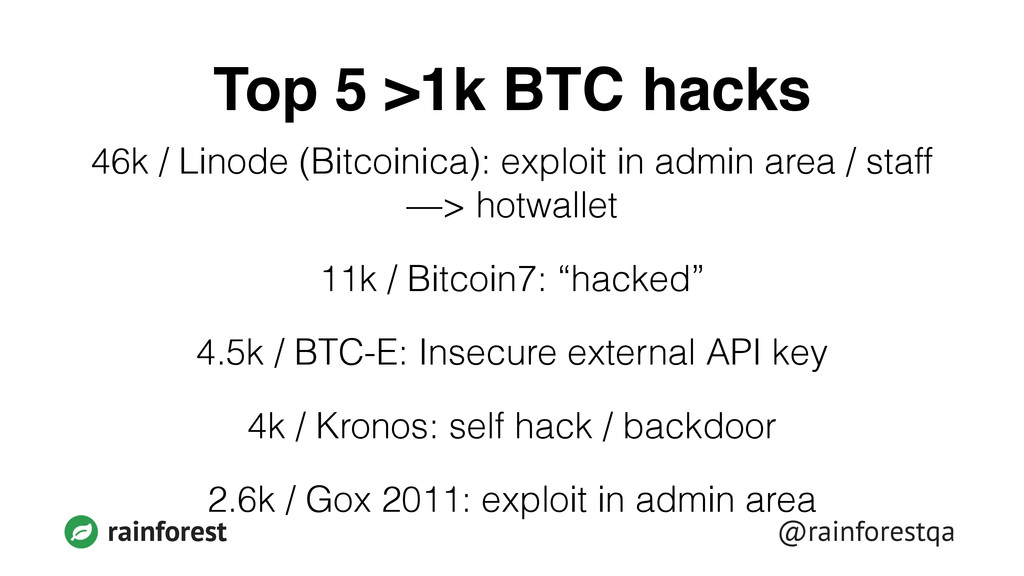
@rainforestqa rainforest Top 5 >1k BTC hacks 46k / Linode
(Bitcoinica): exploit in admin area / staff —> hotwallet 11k / Bitcoin7: “hacked” 4.5k / BTC-E: Insecure external API key 4k / Kronos: self hack / backdoor 2.6k / Gox 2011: exploit in admin area
@rainforestqa rainforest Top 3 reasons:
@rainforestqa rainforest Badly configured servers / services
@rainforestqa rainforest Poorly written software
@rainforestqa rainforest Exploits
@rainforestqa rainforest Attack vectors Your service Your customers You &
your team
@rainforestqa rainforest Your service Domain Email Servers (app, db, etc)
Network External services Backups
@rainforestqa rainforest Domain DNS hijacking MITM attacks Doppelganger domains /
Typo-squatting Renewals
@rainforestqa rainforest HSTS Pinning / force-ssl Cloudflare, imho Firewall +
IDS
@rainforestqa rainforest Email DKIM / SPF Account state Clear email
policies Lockout policy
@rainforestqa rainforest Servers Shared / VPS / AWS Dedicated Co-lo
>
@rainforestqa rainforest OS + software updates Automate provisioning Hire pen-testing
Have a security program
@rainforestqa rainforest Transactions & locking (see Flexcoin / Poloniex)
@rainforestqa rainforest Network IDS / IDPS / HIDS Firewall (both
ways) -complex-
@rainforestqa rainforest External services Verify SSL certs Limit IPs Work
out what + who you can trust
@rainforestqa rainforest Backups Major security issue Encrypt them Test them
@rainforestqa rainforest Your customers Understand their behavior (Progressive) Account limits
Policies KYC
@rainforestqa rainforest Primer
@rainforestqa rainforest Educate yourself
@rainforestqa rainforest Pick secure by default tech
@rainforestqa rainforest 2FA
@rainforestqa rainforest Avoid shared servers
@rainforestqa rainforest Honey pots
@rainforestqa rainforest Automate deployment
@rainforestqa rainforest Use SSH keys, rotate them
@rainforestqa rainforest Use a Firewall
@rainforestqa rainforest Use an IDS
@rainforestqa rainforest Encrypt (and take!) backups
@rainforestqa rainforest Subscribe to security lists
@rainforestqa rainforest Do as little as possible
@rainforestqa rainforest Staff opsec
@rainforestqa rainforest Principle of least privilege
@rainforestqa rainforest Split your servers
@rainforestqa rainforest Or consider LXC / KVM
@rainforestqa rainforest Split your app
@rainforestqa rainforest Server: partitions + noexec + nosuid split running
users disable root remove packages SELinux
@rainforestqa rainforest Starting points Figure out your risk + exposure
Implement low hanging fruit Reduce surface Plan the rest
@rainforestqa rainforest Conclusions Simpler = better Understand your exposure and
limit it
@rainforestqa rainforest Further reading Hacks: https://bitcointalk.org/index.php?topic=83794.0 Flexcoin: http://hackingdistributed.com/2014/04/06/another-one-bites-the-dust- flexcoin/ Docker:
http://www.slideshare.net/jpetazzo/linux-containers-lxc-docker-and- security CVE: http://web.nvd.nist.gov/view/vuln/search?execution=e2s1
rainforest @rainforestqa Questions? @rainforestqa @rhs


 ukd1
 nttcom
 yu23ki14
 teamlab
 syuchimu
 ama_ch
 occhi
 pfn
 kazzpapa3
 sue445
 finengine
 shugo
 tsukina_7mochi
 scottboms
 stuffmc
 marketingsoph
 jonyablonski
 malarkey
 trishagee
 portentint
 szymonslowik
 tmiket
 zakiyama
 letsgokoyo
 reverentgeek